Here s my 70th monthly but brief update about the activities I ve done in the F/L/OSS world.
Debian
This was my 79th month of actively contributing to Debian.
I became a DM in late March 2019 and a DD on Christmas 19! \o/
Debian was in freeze throughout so whilst I didn t do many uploads, there s a bunch of other things I did:
Attended DebConf25 in Brest, France.
Lead the bursary BOF and discussions.
Participated in other sessions, especially around the FTP masters.
I ve started to look at things with my trainee hat on.
Participated in the Debian Security Tracker sprints during DebCamp. More on that below.
Mentoring for newcomers.
Moderation of -project mailing list.
Ubuntu
This was my 54th month of actively contributing to Ubuntu.
I joined Canonical to work on Ubuntu full-time back in February 2021.
Whilst I can t give a full, detailed list of things I did (there s so much and some of it might not be public yet!), here s a quick TL;DR of what I did:
Got a recognition award for leading 24.04.2 LTS release and leading the Release Management team.
Preparing for the 24.04.3 LTS release early next month.
Debian (E)LTS
Debian Long Term Support (LTS) is a project to extend the lifetime of all Debian stable releases to (at least) 5 years. Debian LTS is not handled by the Debian security team, but by a separate group of volunteers and companies interested in making it a success.
And Debian Extended LTS (ELTS) is its sister project, extending support to the stretch and jessie release (+2 years after LTS support).
This was my 70th month as a Debian LTS and 57th month as a Debian ELTS paid contributor.
I only worked for 15.00 hours for LTS and 5.00 hours for ELTS and did the following things:
Coordinated with upstream due to lack of clarity on 1.11.4 being affected & not having a clear reproducer.
As 1.11.4 was still partially vulnerable and the backport was non-trivial, it was probably conveinent to bump the upstream version to 1.11.12 instead, fixing:
Helped Bastien with ca-certificates bit & coordinating with fellow Debian contributors.
Also triaged some newly supported packages for ELTS.
[LTS] Attended the monthly LTS meeting on IRC. Summary here.
Debian Security Tracker sprint 2025
Thanks to the LTS team for also organizing a security tracker sprint during DebCamp25. I attended the sprint and spent 10 hours working on the following tasks:
This includes some coordination with the web team and some back and forth with them to ensure both the Web team and the Security team would be happy with the fix. It also fixes more issues as mentioned in the description of the MR.
Show packages from next-point-release.txt in source package overview
If your bank is like mine, its website doesn t allow you to copy your password and paste it by performing a simple Ctrl+V. I tried the Don t Fuck With Paste extension in Firefox, which could paste my bank account s profile password but not the login password.
Therefore, I asked on Mastodon a couple of days ago and got some responses. The solution that worked for me was to use Shift+Insert to paste the password. It worked for me in LibreWolf and Firefox, and that s all I needed.
Furthermore, this behavior by bank websites leads to users choosing insecure and memorable passwords. Using this trick will help you choose strong passwords for your bank account.
I prefer to use random and strong passwords generated using the password manager pass. It is a freedom-respecting software, unlike popular proprietary password managers promoted by YouTubers. Feel free to check out their webpage here. The reason I use pass is that it stores all the passwords locally (and optionally in a remote Git repository) in encrypted form, which can only be decrypted using your private GPG keys.
It's Sunday and I'm now sitting in the train from Brest to Paris where I will be changing to Germany, on the way back from the annual Debian conference. A full week of presentations, discussions, talks and socializing is laying behind me and my head is still spinning from the intensity.
Pollito and the gang of DebConf mascots wearing their conference badges (photo: Christoph Berg)
Table of Contents
Sunday, July 13th
It started last Sunday with traveling to the conference. I got on the Eurostar in Duisburg and we left on time, but even before reaching Cologne, the train was already one hour delayed for external reasons, collecting yet another hour between Aachen and Liege for its own technical problems. "The train driver is working on trying to fix the problem." My original schedule had well over two hours for changing train stations in Paris, but being that late, I missed the connection to Brest in Montparnasse. At least in the end, the total delay was only one hour when finally arriving at the destination. Due to the French julliet quatorze fireworks approaching, buses in Brest were rerouted, but I managed to catch the right bus to the conference venue, already meeting a few Debian people on the way.
The conference was hosted at the IMT Atlantique Brest campus, giving the event a nice university touch. I arrived shortly after 10 in the evening and after settling down a bit, got on one of the "magic" buses for transportation to the camping site where half of the attendees where stationed. I shared a mobile home with three other Debianites, where I got a small room for myself.
Monday, July 14th
Next morning, we took the bus back to the venue with a small breakfast and the opening session where Enrico Zini invited me to come to his and Nicolas Dandrimont's session about Debian community governance and curation, which I gladly did. Many ideas about conflict moderation and community steering were floated around. I hope some of that can be put into effect to make flamewars on the mailing lists less heated and more directed. After that, I attended Olly Betts' "Stemming with Snowball" session, which is the stemmer used also in PostgreSQL. Text search is one of the areas in PostgreSQL that I never really looked closely at, including the integration into the postgresql-common package, so it was nice to get more information about that.
In preparation for the conference, a few of us Ham radio operators in Debian had decided to bring some radio gear to DebConf this year in order to perhaps spark more interest for our hobby among the fellow geeks. In the afternoon after the talks, I found a quieter spot just outside of the main hall and set up a shortwave antenna by attaching a 10m mast to one of the park benches there. The 40m band was still pretty much closed, but I could work a few stations from England, just across the channel from Bretagne, answering questions from interested passing-by Debian people between the contacts. Over time, the band opened and more European stations got into the log.
F/DF7CB in Brest (photo: Evangelos Ribeiro Tzaras)
Tuesday, July 15th
Tuesday started with Helmut Grohne's session about "Reviving (un)schroot". The schroot program has been Debian's standard way of managing build chroots for a long time, but it is more and more being regarded as obsolete with all kinds of newer containerization and virtualization technologies taking over. Since many bits of Debian infrastructure depend on schroot, and its user interface is still very useful, Helmut reimplemented it using Linux namespaces and the "unshare" systemcall. I had already worked with him at the Hamburg Minidebconf to replace the apt.postgresql.org buildd machinery with the new system, but we were not quite there yet (network isolation is nice, but we still sometimes need proper networking), so it was nice to see the effort is still progressing and I will give his new scripts a try when I'm back home.
Next, Stefano Rivera and Colin Watson presented Debusine, a new package repository and workflow management system. It looks very promising for anyone running their own repository, so perhaps yet another bit of apt.postgresql.org infrastructure to replace in the future. After that, I went to the Debian LTS BoF session by Santiago Ruano Rinc n and Bastien Roucari s - Debian releases plus LTS is what we are covering with apt.postgresql.org. Then there were bits from the DPL (Debian Project Leader), and a session moderated by Stefano Rivera interesting to me as a member of the Debian Technical Committee on the future structure of the packages required for cross-building in Debian, a topic which had been brought to TC a while ago. I am happy that we could resolve the issue without having to issue a formal TC ruling as the involved parties (kernel, glibc, gcc and the cross-build people) found a promising way forward themselves. DebConf is really a good way to get such issues unstuck.
Ten years ago at the 2015 Heidelberg DebConf, Enrico had given a seminal "Semi-serious stand-up comedy" talk, drawing parallels between the Debian Open Source community and the BDSM community - "People doing things consensually together". (Back then, the talk was announced as "probably unsuitable for people of all ages".) With his unique presentation style and witty insights, the session made a lasting impression on everyone attending. Now, ten years later (and he and many in the audience being ten years older), he gave an updated version of it. We are now looking forward to the sequel in 2035. The evening closed with the famous DebConf tradition of the Cheese & Wine party in a old fort next to the coast, just below the conference venue. Even when he's a fellow Debian Developer, Ham and also TC member, I had never met Paul Tagliamonte in person before, but we spent most of the evening together geeking out on all things Debian and Ham radio.
The northern coast of Ushant (photo: Christoph Berg)
Wednesday, July 16th
Wednesday already marked the end of the first half of the week, the day of the day trips. I had chosen to go to Ouessant island (Ushant in English) which marks the Western end of French mainland and hosts one of the lighthouses yielding the way into the English channel. The ferry trip included surprisingly big waves which left some participants seasick, but everyone recovered fast. After around one and a half hours we arrived, picked up the bicycles, and spent the rest of the day roaming the island. The weather forecast was originally very cloudy and 18 C, but over noon this turned into sunny and warm, so many got an unplanned sunburn. I enjoyed the trip very much - it made up for not having time visiting the city during the week. After returning, we spent the rest of the evening playing DebConf's standard game, Mao (spoiler alert: don't follow the link if you ever intend to play).
Having a nice day (photo: Christoph Berg)
Thursday, July 17th
The next day started with the traditional "Meet the Technical Committee" session. This year, we trimmed the usual slide deck down to remove the boring boilerplate parts, so after a very short introduction to the work of the committee by our chairman Matthew Vernon, we opened up the discussion with the audience, with seven (out of 8) TC members on stage. I think the format worked very well, with good input from attendees. Next up was "Don't fear the TPM" by Jonathan McDowell. A common misconception in the Free Software community is that the TPM is evil DRM hardware working against the user, but while it could be used in theory that way, the necessary TPM attestations seem to impossible to attain in practice, so that wouldn't happen anyway. Instead, it is a crypto coprocessor present in almost all modern computers that can be used to hold keys, for example to be used for SSH. It will also be interesting to research if we can make use of it for holding the Transparent Data Encryption keys for CYBERTEC's PostgreSQL Enterprise Edition.
Aigars Mahinovs then directed everyone in place for the DebConf group picture, and Lucas Nussbaum started a discussion about archive-wide QA tasks in Debian, an area where I did a lot of work in the past and that still interests me. Antonio Terceiro and Paul Gevers followed up with techniques to track archive-wide rebuilding and testing of packages and in turn filing a lot of bugs to track the problems. The evening ended with the conference dinner, again in the fort close by the coast. DebConf is good for meeting new people, and I incidentally ran into another Chris, who happened to be one of the original maintainers of pgaccess, the pre-predecessor of today's pgadmin. I admit still missing this PostgreSQL frontend for its simplicity and ability to easily edit table data, but it disappeared around 2004.
Friday, July 18th
On Friday, I participated in discussion sessions around contributors.debian.org (PostgreSQL is planning to set up something similar) and the New Member process which I had helped to run and reform a decade or two ago. Agathe Porte (also a Ham radio operator, like so many others at the conference I had no idea of) then shared her work on rust-rewriting the slower parts of Lintian, the Debian package linter. Craig Small talked about "Free as in Bytes", the evolution of the Linux procps free command. Over the time and many kernel versions, the summary numbers printed became better and better, but there will probably never be a version that suits all use cases alike. Later over dinner, Craig (who is also a TC member) and I shared our experiences with these numbers and customers (not) understanding them. He pointed out that for PostgreSQL and looking at used memory in the presence of large shared memory buffers, USS (unique set size) and PSS (proportional set size) should be more realistic numbers than the standard RSS (resident set size) that the top utility is showing by default.
Antonio Terceiro and Paul Gevers again joined to lead a session, now on ci.debian.net and autopkgtest, the test driver used for running tests on packages after then have been installed on a system. The PostgreSQL packages are heavily using this to make sure no regressions creep in even after builds have successfully completed and test re-runs are rescheduled periodically. The day ended with Bdale Garbee's electronics team BoF and Paul Tagliamonte and me setting up the radio station in the courtyard, again answering countless questions about ionospheric conditions and operating practice.
Saturday, July 19th
Saturday was the last conference day. In the first session, Nikos Tsipinakis and Federico Vaga from CERN announced that the LHC will be moving to Debian for the accelerator's frontend computers in their next "long shutdown" maintenance period in the next year. CentOS broke compatibility too often, and Debian trixie together with the extended LTS support will cover the time until the next long shutdown window in 2035, until when the computers should have all been replaced with newer processors covering higher x86_64 baseline versions. The audience was very delighted to hear that Debian is now also being used in this prestige project.
Ben Hutchings then presented new Linux kernel features. Particularly interesting for me was the support for atomic writes spanning more than one filesystem block. When configured correctly, this would mean PostgreSQL didn't have to record full-page images in the WAL anymore, increasing throughput and performance. After that, the Debian ftp team discussed ways to improve review of new packages in the archive, and which of their processes could be relaxed with new US laws around Open Source and cryptography algorithms export. Emmanuel Arias led a session on Salsa CI, Debian's Gitlab instance and standard CI pipeline. (I think it's too slow, but the runners are not under their control.) Julian Klode then presented new features in APT, Debian's package manager. I like the new display format (and a tiny bit of that is also from me sending in wishlist bugs).
In the last round of sessions this week, I then led the Ham radio BoF with an introduction into the hobby and how Debian can be used. Bdale mentioned that the sBitx family of SDR radios is natively running Debian, so stock packages can be used from the radio's touch display. We also briefly discussed his involvement in ARDC and the possibility to get grants from them for Ham radio projects. Finally, DebConf wrapped up with everyone gathering in the main auditorium and cheering the organizers for making the conference possible and passing Pollito, the DebConf mascot, to the next organizer team.
Pollito on stage (photo: Christoph Berg)
Sunday, July 20th
Zoom back to the train: I made it through the Paris metro and I'm now on the Eurostar back to Germany. It has been an intense week with all the conference sessions and meeting all the people I had not seen so long. There are a lot of new ideas to follow up on both for my Debian and PostgreSQL work. Next year's DebConf will take place in Santa Fe, Argentina. I haven't yet decided if I will be going, but I can recommend the experience to everyone!
The post The Debian Conference 2025 in Brest appeared first on CYBERTEC PostgreSQL Services & Support.
Dear friends, family, and community,
I m reaching out during a challenging time in my life to ask for your support. This year has been particularly difficult as I ve been out of work for most of it due to a broken arm and a serious MRSA infection that required extensive treatment and recovery time.
Current Situation
While I ve been recovering, I ve been actively working to maintain and improve my professional skills by contributing to open source software projects. These contributions help me stay current with industry trends and demonstrate my ongoing commitment to my field, but unfortunately, they don t provide the income I need to cover my basic living expenses.
Despite my efforts, I m still struggling to secure employment, and I m falling behind on essential bills including:
Rent/mortgage payments
Utilities
Medical expenses
Basic living costs
How You Can Help
Any financial assistance, no matter the amount, would make a meaningful difference in helping me stay afloat during this job search. Your support would allow me to:
Keep my housing stable
Maintain essential services
Focus fully on finding employment without the constant stress of unpaid bills
Continue contributing to the open source community
Moving Forward
I m actively job searching and interviewing, and I m confident that I ll be back on my feet soon. Your temporary support during this difficult period would mean the world to me and help bridge the gap until I can secure stable employment.
If you re able to contribute, GoFundMe . If you re unable to donate, I completely understand, and sharing this request with others who might be able to help would be greatly appreciated.
Thank you for taking the time to read this and for considering helping me during this challenging time.
With gratitude, Scarlett
Achieving full disk encryption using FIPS, TCG OPAL and LUKS to encrypt UEFI ESP on bare-metal and in VMs
Many security standards such as CIS and STIG require to protect information at rest. For example, NIST SP 800-53r5 SC-28 advocate to use cryptographic protection, offline storage and TPMs to enhance protection of information confidentiality and/or integrity.Traditionally to satisfy such controls on portable devices such as laptops one would utilize software based Full Disk Encryption - Mac OS X FileVault, Windows Bitlocker, Linux cryptsetup LUKS2. In cases when FIPS cryptography is required, additional burden would be placed onto these systems to operate their kernels in FIPS mode.Trusted Computing Group works on establishing many industry standards and specifications, which are widely adopted to improve safety and security of computing whilst keeping it easy to use. One of their most famous specifications them is TCG TPM 2.0 (Trusted Platform Module). TPMs are now widely available on most devices and help to protect secret keys and attest systems. For example, most software full disk encryption solutions can utilise TCG TPM to store full disk encryption keys providing passwordless, biometric or pin-base ways to unlock the drives as well as attesting that system have not been modified or compromised whilst offline.TCG Storage Security Subsystem Class: Opal Specification is a set of specifications for features of data storage devices. The authors and contributors to OPAL are leading and well trusted storage manufacturers such as Samsung, Western Digital, Seagate Technologies, Dell, Google, Lenovo, IBM, Kioxia, among others. One of the features that Opal Specification enables is self-encrypting drives which becomes very powerful when combined with pre-boot authentication. Out of the box, such drives always and transparently encrypt all disk data using hardware acceleration. To protect data one can enter UEFI firmware setup (BIOS) to set NVMe single user password (or user + administrator/recovery passwords) to encrypt the disk encryption key. If one's firmware didn't come with such features, one can also use SEDutil to inspect and configure all of this. Latest release of major Linux distributions have SEDutil already packaged.Once password is set, on startup, pre-boot authentication will request one to enter password - prior to booting any operating systems. It means that full disk is actually encrypted, including the UEFI ESP and all operating systems that are installed in case of dual or multi-boot installations. This also prevents tampering with ESP, UEFI bootloaders and kernels which with traditional software-based encryption often remain unencrypted and accessible. It also means one doesn't have to do special OS level repartitioning, or installation steps to ensure all data is encrypted at rest.What about FIPS compliance? Well, the good news is that majority of the OPAL compliant hard drives and/or security sub-chips do have FIPS 140-3 certification. Meaning they have been tested by independent laboratories to ensure they do in-fact encrypt data. On the CMVP website one can search for module name terms "OPAL" or "NVMe" or name of hardware vendor to locate FIPS certificates.Are such drives widely available? Yes. For example, a common Thinkpad X1 gen 11 has OPAL NVMe drives as standard, and they have FIPS certification too. Thus, it is likely in your hardware fleet these are already widely available. Use sedutil to check if MediaEncrypt and LockingSupported features are available.Well, this is great for laptops and physical servers, but you may ask - what about public or private cloud? Actually, more or less the same is already in-place in both. On CVMP website all major clouds have their disk encryption hardware certified, and all of them always encrypt all Virtual Machines with FIPS certified cryptography without an ability to opt-out. One is however in full control of how the encryption keys are managed: cloud-provider or self-managed (either with a cloud HSM or KMS or bring your own / external). See these relevant encryption options and key management docs for GCP, Azure, AWS. But the key takeaway without doing anything, at rest, VMs in public cloud are always encrypted and satisfy NIST SP 800-53 controls.What about private cloud? Most Linux based private clouds ultimately use qemu typically with qcow2 virtual disk images. Qemu supports user-space encryption of qcow2 disk, see this manpage. Such encryption encrypts the full virtual machine disk, including the bootloader and ESP. And it is handled entirely outside of the VM on the host - meaning the VM never has access to the disk encryption keys. Qemu implements this encryption entirely in userspace using gnutls, nettle, libgcrypt depending on how it was compiled. This also means one can satisfy FIPS requirements entirely in userspace without a Linux kernel in FIPS mode. Higher level APIs built on top of qemu also support qcow2 disk encryption, as in projects such as libvirt and OpenStack Cinder.If you carefully read the docs, you may notice that agent support is explicitly sometimes called out as not supported or not mentioned. Quite often agents running inside the OS may not have enough observability to them to assess if there is external encryption. It does mean that monitoring above encryption options require different approaches - for example monitor your cloud configuration using tools such as Wiz and Orca, rather than using agents inside individual VMs. For laptop / endpoint security agents, I do wish they would start gaining capability to report OPAL SED availability and status if it is active or not.What about using software encryption none-the-less on top of the above solutions? It is commonly referred to double or multiple encryption. There will be an additional performance impact, but it can be worthwhile. It really depends on what you define as data at rest for yourself and which controls you need. If one has a dual-boot laptop, and wants to keep one OS encrypted whilst booted into the other, it can perfectly reasonable to encrypted the two using separate software encryption keys. In addition to the OPAL encryption of the ESP. For more targeted per-file / per-folder encryption, one can look into using gocryptfs which is the best successor to the once popular, but now deprecated eCryptfs (amazing tool, but has fallen behind in development and can lead to data loss).All of the above mostly talks about cryptographic encryption, which only provides confidentially but not data integrity. To protect integrity, one needs to choose how to maintain that. dm-verity is a good choice for read-only and rigid installations. For read-write workloads, it may be easier to deploy ZFS or Btrfs instead. If one is using filesystems without a built-in integrity support such as XFS or Ext4, one can retrofit integrity layer to them by using dm-integrity (either standalone, or via dm-luks/cryptsetup --integrity option).
If one has a lot of estate and a lot of encryption keys to keep track off a key management solution is likely needed. The most popular solution is likely the one from Thales Group marketed under ChiperTrust Data Security Platform (previously Vormetric), but there are many others including OEM / Vendor / Hardware / Cloud specific or agnostic solutions.
I hope this crash course guide piques your interest to learn and discover modern confidentially and integrity solutions, and to re-affirm or change your existing controls w.r.t. to data protection at rest.
Full disk encryption, including UEFI ESP /boot/efi is now widely achievable by default on both baremetal machines and in VMs including with FIPS certification. To discuss more let's connect on Linkedin.
The main text below is an edited version of my original review of
Cyteen written on 2012-01-03. Additional comments
from my re-read are after the original review.
I've reviewed several other C.J. Cherryh books somewhat negatively, which
might give the impression I'm not a fan. That is an artifact of when I
started reviewing. I first discovered Cherryh with Cyteen some 20
years ago, and it remains one of my favorite SF novels of all time. After
finishing my reading for 2011, I was casting about for what to start next,
saw Cyteen on my parents' shelves, and decided it was past time for
my third reading, particularly given the recent release of a sequel,
Regenesis.
Cyteen is set in Cherryh's Alliance-Union universe following the
Company Wars. It references several other books in that universe, most
notably Forty Thousand in Gehenna but also
Downbelow Station and others. It also
has mentions of the Compact Space series (The Pride of Chanur and
sequels). More generally, almost all of Cherryh's writing is loosely tied
together by an overarching future history. One does not need to read any
of those other books before reading Cyteen; this book will fill you
in on all of the politics and history you need to know. I read
Cyteen first and have never felt the lack.
Cyteen was at one time split into three books for publishing
reasons: The Betrayal, The Rebirth, and The
Vindication. This is an awful way to think of the book. There are no
internal pauses or reasonable volume breaks; Cyteen is a single
coherent novel, and Cherryh has requested that it never be broken up that
way again. If you happen to find all three portions as your reading copy,
they contain all the same words and are serviceable if you remember it's a
single novel under three covers, but I recommend against reading the
portions in isolation.
Human colonization of the galaxy started with slower-than-light travel
sponsored by the private Sol Corporation. The inhabitants of the far-flung
stations and the crews of the merchant ships that supplied them have
formed their own separate cultures, but initially remained attached to
Earth. That changed with the discovery of FTL travel and a botched attempt
by Earth to reassert its authority. At the time of Cyteen, there
are three human powers: distant Earth (which plays little role in this
book), the merchanter Alliance, and Union.
The planet Cyteen is one of only a few Earth-like worlds discovered by
human expansion, and is the seat of government and the most powerful force
in Union. This is primarily because of Reseune: the Cyteen lab that
produces the azi.
If Cyteen is about any one thing, it's about azi: genetically
engineered human clones who are programmed via intensive psychological
conditioning starting before birth. The conditioning uses a combination of
drugs to make them receptive and "tape," specific patterns of instruction
and sensory stimulation. They are designed for specific jobs or roles,
they're conditioned to be obedient to regular humans, and they're not
citizens. They are, in short, slaves.
In a lot of books, that's as deep as the analysis would go. Azi are
slaves, and slavery is certainly bad, so there would probably be a plot
around azi overthrowing their conditioning, or around the protagonists
trying to free them from servitude. But Cyteen is not any SF novel,
and azi are considerably more complex and difficult than that analysis. We
learn over the course of the book that the immensely powerful head of
Reseune Labs, Ariane Emory, has a specific broader purpose in mind for the
azi. One of the reasons why Reseune fought for and gained the role of
legal protector of all azi in Union, regardless of where they were
birthed, is so that Reseune could act to break any permanent dependence on
azi as labor. And yet, they are slaves; one of the protagonists of
Cyteen is an experimental azi, which makes him the permanent
property of Reseune and puts him in constant jeopardy of being used as a
political prisoner and lever of manipulation against those who care about
him.
Cyteen is a book about manipulation, about programming people,
about what it means to have power over someone else's thoughts, and what
one can do with that power. But it's also a book about connection and
identity, about what makes up a personality, about what constitutes
identity and how people construct the moral codes and values that they
hold at their core. It's also a book about certainty. Azi are absolutely
certain, and are capable of absolute trust, because that's part of their
conditioning. Naturally-raised humans are not. This means humans can do
things that azi can't, but the reverse is also true. The azi are not
mindless slaves, nor are they mindlessly programmed, and several of the
characters, both human and azi, find a lot of appeal in the core of
certainty and deep self-knowledge of their own psychological rules that
azis can have. Cyteen is a book about emotions, and logic, and
where they come from and how to balance them. About whether emotional pain
and uncertainty is beneficial or damaging, and about how one's experiences
make up and alter one's identity.
This is also a book about politics, both institutional and personal. It
opens with Ariane Emory, Councilor for Science for five decades and the
head of the ruling Union Expansionist party. She's powerful, brilliant,
dangerously good at reading people, and dangerously willing to manipulate
and control people for her own ends. What she wants, at the start of the
book, is to completely clone a Special (the legal status given to the most
brilliant minds of Union). This was attempted before and failed, but
Ariane believes it's now possible, with a combination of tape, genetic
engineering, and environmental control, to reproduce the brilliance of the
original mind. To give Union another lifespan of work by their most
brilliant thinkers.
Jordan Warrick, another scientist at Reseune, has had a long-standing
professional and personal feud with Ariane Emory. As the book opens, he is
fighting to be transferred out from under her to the new research station
that would be part of the Special cloning project, and he wants to bring
his son Justin and Justin's companion azi Grant with them. Justin is a PR,
a parental replicate, meaning he shares Jordan's genetic makeup but was
not an attempt to reproduce the conditions of Jordan's rearing. Grant was
raised as his brother. And both have, for reasons that are initially
unclear, attracted the attention of Ariane, who may be using them as
pawns.
This is just the initial setup, and along with this should come a warning:
the first 150 pages set up a very complex and dangerous political
situation and build the tension that will carry the rest of the book, and
they do this by, largely, torturing Justin and Grant. The viewpoint jumps
around, but Justin and Grant are the primary protagonists for this first
section of the book. While one feels sympathy for both of them, I have
never, in my multiple readings of the book, particularly liked them.
They're hard to like, as opposed to pity, during this setup; they have
very little agency, are in way over their heads, are constantly making
mistakes, and are essentially having their lives destroyed.
Don't let this turn you off on the rest of the book. Cyteen takes a
dramatic shift about 150 pages in. A new set of protagonists are
introduced who are some of the most interesting, complex, and delightful
protagonists in any SF novel I have read, and who are very much worth
waiting for. While Justin has his moments later on (his life is so hard
that his courage can be profoundly moving), it's not necessary to like him
to love this book. That's one of the reasons why I so strongly dislike
breaking it into three sections; that first section, which is mostly
Justin and Grant, is not representative of the book.
I can't talk too much more about the plot without risking spoiling it, but
it's a beautiful, taut, and complex story that is full of my favorite
things in both settings and protagonists. Cyteen is a book about
brilliant people who think on their feet. Cherryh succeeds at showing this
through what they do, which is rarely done as well as it is here. It's a
book about remembering one's friends and remembering one's enemies, and
waiting for the most effective moment to act, but it also achieves some
remarkable transformations. About 150 pages in, you are likely to loathe
almost everyone in Reseune; by the end of the book, you find yourself
liking, or at least understanding, nearly everyone. This is extremely
hard, and Cherryh pulls it off in most cases without even giving the
people she's redeeming their own viewpoint sections. Other than perhaps
George R.R. Martin I've not seen another author do this as well.
And, more than anything else, Cyteen is a book with the most
wonderful feeling of catharsis. I think this is one of the reasons why I
adore this book and have difficulties with some of Cherryh's other works.
She's always good at ramping up the tension and putting her characters in
awful, untenable positions. Less frequently does she provide the emotional
payoff of turning the tables, where you get to watch a protagonist do
everything you've been wanting them to do for hundreds of pages, except
even better and more delightfully than you would have come up with.
Cyteen is one of the most emotionally satisfying books I've ever
read.
I could go on and on; there is just so much here that I love. Deep
questions of ethics and self-control, presented in a way that one can see
the consequences of both bad decisions and good ones and contrast them.
Some of the best political negotiations in fiction. A wonderful look at
friendship and loyalty from several directions. Two of the best semi-human
protagonists I've seen, who one can see simultaneously as both wonderful
friends and utterly non-human and who put nearly all of the androids in
fiction to shame by being something trickier and more complex. A wonderful
unfolding sense of power. A computer that can somewhat anticipate problems
and somewhat can't, and that encapsulates much of what I love about
semi-intelligent bases in science fiction. Cyteen has that rarest
of properties of SF novels: Both the characters and the technology meld in
a wonderful combination where neither could exist without the other, where
the character issues are illuminated by the technology and the technology
supports the characters.
I have, for this book, two warnings. The first, as previously mentioned,
is that the first 150 pages of setup is necessary but painful to read, and
I never fully warmed to Justin and Grant throughout. I would not be
surprised to hear that someone started this book but gave up on it after
50 or 100 pages. I do think it's worth sticking out the rocky beginning,
though. Justin and Grant continue to be a little annoying, but there's so
much other good stuff going on that it doesn't matter.
The other warning is that part of the setup of the story involves the rape
of an underage character. This is mostly off-camera, but the emotional
consequences are significant (as they should be) and are frequently
discussed throughout the book. There is also rather frank discussion of
adolescent sexuality later in the book. I think both of these are relevant
to the story and handled in a way that isn't gratuitous, but they made me
uncomfortable and I don't have any past history with those topics.
Those warnings notwithstanding, this is simply one of the best SF novels
ever written. It uses technology to pose deep questions about human
emotions, identity, and interactions, and it uses complex and interesting
characters to take a close look at the impact of technology on lives. And
it does this with a wonderfully taut, complicated plot that sustains its
tension through all 680 pages, and with characters whom I absolutely love.
I have no doubt that I'll be reading it for a fourth and fifth time some
years down the road.
Followed by Regenesis, although
Cyteen stands well entirely on its own and there's no pressing need
to read the sequel.
Rating: 10 out of 10
Some additional thoughts after re-reading Cyteen in
2025:
I touched on this briefly in my original review, but I was really struck
during this re-read how much the azi are a commentary on and a
complication of the role of androids in earlier science fiction. Asimov's
Three Laws of Robotics were an attempt to control the risks of robots, but
can also be read as turning robots into slaves. Azis make the slavery more
explicit and disturbing by running the programming on a human biological
platform, but they're more explicitly programmed and artificial than a lot
of science fiction androids.
Artificial beings and their relationship to humans have been a recurring
theme of SF since Frankenstein, but I can't remember a novel that
makes the comparison to humans this ambiguous and conflicted. The azi not
only like being azi, they can describe why they prefer it. It's clear that
Union made azi for many of the same reasons that humans enslave other
humans, and that Ariane Emory is using them as machinery in a larger (and
highly ethically questionable) plan, but Cherryh gets deeper into the
emergent social complications and societal impact than most SF novels
manage. Azi are apparently closer to humans than the famous SF examples
such as Commander Data, but the deep differences are both more subtle and
more profound.
I've seen some reviewers who are disturbed by the lack of a clear moral
stance by the protagonists against the creation of azi. I'm not sure what
to think about that. It's clear the characters mostly like the society
they've created, and the groups attempting to "free" azi from their
"captivity" are portrayed as idiots who have no understanding of azi
psychology. Emory says she doesn't want azi to be a permanent aspect of
society but clearly has no intention of ending production any time soon.
The book does seem oddly unaware that the production of azi is unethical
per se and, unlike androids, has an obvious exit ramp: Continue cloning
gene lines as needed to maintain a sufficient population for a growing
industrial civilization, but raise the children as children rather than
using azi programming. If Cherryh included some reason why that was
infeasible, I didn't see it, and I don't think the characters directly
confronted it.
I don't think societies in books need to be ethical, or that Cherryh
intended to defend this one. There are a lot of nasty moral traps that
civilizations can fall into that make for interesting stories. But the
lack of acknowledgment of the problem within the novel did seem odd this
time around.
The other part of this novel that was harder to read past in this re-read
is the sexual ethics. There's a lot of adolescent sexuality in this book,
and even apart from the rape scene which was more on-the-page than I had
remembered and which is quite (intentionally) disturbing there is a
whole lot of somewhat dubious consent. Maybe I've gotten older or just
more discriminating, but it felt weirdly voyeuristic to know this much
about the sex lives of characters who are, at several critical points in
the story, just a bunch of kids.
All that being said, and with the repeated warning that the first 150
pages of this novel are just not very good, there is still something magic
about the last two-thirds of this book. It has competence porn featuring a
precociously brilliant teenager who I really like, it has one of
the more interesting non-AI programmed computer systems that I've read in
SF, it has satisfying politics that feel like modern politics
(media strategy and relationships and negotiated alliances, rather than
brute force and ideology), and it has a truly excellent feeling of
catharsis. The plot resolution is a bit too abrupt and a bit
insufficiently explained (there's more in Regenesis), but even
though this was my fourth time through this book, the pacing grabbed me
again and I could barely put down the last part of the story.
Ethics aside (and I realize that's quite the way to start a sentence), I
find the azi stuff fascinating. I know the psychology in this book is not
real and is hopelessly simplified compared to real psychology, but there's
something in the discussions of value sets and flux and self-knowledge
that grabs my interest and makes me want to ponder. I think it's the
illusion of simplicity and control, the what-if premise of thought where
core motivations and moral rules could be knowable instead of endlessly
fluid the way they are in us humans. Cherryh's azi are some of the most
intriguing androids in science fiction to me precisely because they don't
start with computers and add the humanity in, but instead start with
humanity and overlay a computer-like certainty of purpose that's fully
self-aware. The result is more subtle and interesting than anything
Star Trek managed.
I was not quite as enamored with this book this time around, but it's
still excellent once the story gets properly started. I still would
recommend it, but I might add more warnings about the disturbing parts.
Introduction
Recently, I've got a chance to try AMDGPU.
I didn't have experience as a user with AMDGPU, but I felt it was very easy to switch.
How to switch from NVIDIAGPU to AMDGPU?
Here is the steps to migrate from NVIDIAGPU.
(I'm using Debian sid as a daily driver, but the following instructions are also applicable)
Not only nvidia-driver, but also need to say good-bye to CUDA related packages.
Anyway, it is important to clean it up.
Reboot it!
Ensure without nvidia-driver, it correctly boot with GUI desktop.
Now you can see driver was changed to nouveau module.
You can ensure it with lsmod command.
$ lsmod  grep nou
nouveau              3055616  16
mxm_wmi                12288  1 nouveau
drm_gpuvm              45056  1 nouveau
drm_exec               12288  2 drm_gpuvm,nouveau
gpu_sched              65536  1 nouveau
video                  81920  1 nouveau
i2c_algo_bit           16384  1 nouveau
drm_display_helper    274432  1 nouveau
drm_ttm_helper         16384  2 nouveau
ttm                   106496  2 drm_ttm_helper,nouveau
drm_kms_helper        253952  3 drm_display_helper,drm_ttm_helper,nouveau
drm                   774144  14 gpu_sched,drm_kms_helper,drm_exec,drm_gpuvm,drm_display_helper,drm_ttm_helper,ttm,nouveau
wmi                    28672  4 video,wmi_bmof,mxm_wmi,nouveau
button                 24576  1 nouveau
That's all.
Currently, I'm using it on linux-image-6.12.38+deb13-amd64 kernel.
It seems that there is more newer release for firmware-amd-graphics,
but no critical issue is found yet.
Conclusion
By switching from NVIDIAGPU, there were some disadvantage that
some application does not support AMDGPU yet.
On the positive side, no need to worry about nvidia-driver issues such as
#1089513
I just started using AMDGPU, I hope I could help to improve the AMDGPU experience on Debian.
This article was written with Ultimate Hacking Keyboard 60 v2 with Riser 60.
The Dragon's Banker is a self-published stand-alone fantasy novel,
set in a secondary world with roughly Renaissance levels of technology and
primarily alchemical magic. The version I read includes an unrelated
novelette, "Forego Quest." I have the vague impression that this novel
shares a world with other fantasy novels by the same author, but I have
not read them and never felt like I was missing something important.
Sailor Kelstern is a merchant banker. He earns his livelihood by financing
caravans and sea voyages and taking a cut of the profits. He is not part
of the primary banking houses of the city; instead, he has a small,
personal business with a loyal staff that looks for opportunities the
larger houses may have overlooked. As the story opens, he has fallen on
hard times due in part to a spectacular falling-out with a previous client
and is in desperate need of new opportunities. The jewel-bedecked Lady
Arkelai and her quest for private banking services for her father, Lord
Alkazarian, may be exactly what he needs. Or it may be a dangerous trap;
Sailor has had disastrous past experience with nobles attempting to
strong-arm him into their service.
Unbeknownst to Sailor, Lord Alkazarian is even more dangerous than he
first appears. He is sitting on a vast hoard of traditional riches whose
value is endangered by the rise of new-fangled paper money. He is not at
all happy about this development. He is also a dragon.
I, and probably many other people who read this book, picked it up because
it was recommended by Matt Levine as a fantasy about finance instead of
the normal magical adventuring. I knew it was self-published going in, so
I wasn't expecting polished writing. My hope was for interesting finance
problems in a fantasy context, similar to the kind of things Matt Levine's
newsletter is about: schemes for financing risky voyages, complications
around competing ideas of money, macroeconomic risks from dragon hoards,
complex derivatives, principal-agent problems, or something similar that
goes beyond the (annoyingly superficial) treatment of finance in most
fantasy novels.
Unfortunately, what I got was a rather standard fantasy setting and a plot
that revolves mostly around creative uses for magical devices, some
conventional political skulduggery, and a lot of energetic but rather
superficial business hustling. The protagonist is indeed a merchant banker
who is in no way a conventional fantasy hero (one of the most taxing parts
of Sailor's occasional visits to the dragon is the long hike down to the
hoard, or rather the long climb back out), but the most complex financial
instrument that appears in this book is straightforward short-selling.
Alas. I was looking forward to the book that I hoped this was.
Given my expectations, this was a disappointment. I kept waiting for the
finances to get more complicated and interesting, and that kept not
happening. Without that expectation, this is... okay, I guess. The writing
is adequate but kind of stilted, presumably in an effort to make it sound
slightly archaic, and has a strong self-published feel. Sailor is not a
bad protagonist, but neither is he all that memorable. I did like some of
the world-building, which has an attention to creative uses of bits of
magic that readers who like gadget fantasy may appreciate. There are a lot
of plot conveniences and coincidences, though, and very little of this is
going to feel original to a long-time fantasy reader.
Putting some of the complexity of real Renaissance banking and finance
systems into a fantasy world is a great idea, but I've yet to read one
that lived up to the potential of the premise. (Neal Stephenson's
Baroque Cycle comes the closest; unfortunately,
the non-economic parts of that over-long series are full of Stephenson's
worst writing habits.) Part of the problem is doubtless that I am
reasonably well-read in economics, so my standards are high. Maybe the
average reader would be content with a few bits on the perils of
investment, a simple treatment of trust in currency, and a mention or two
of short-selling, which is what you get in this book.
I am not altogether sorry that I read this, but I wouldn't recommend it. I
encourage Matt Levine to read more genre fiction and find some novels with
more interesting financial problems!
"Forego Quest": This included novelette, on the other hand, was
surprisingly good and raised my overall rating for the book by a full
point.
Arturus Kingson is the Chosen One. He is not the Chosen One of a single
prophecy or set of prophecies; no, he's the Chosen One of, apparently, all
of them, no matter how contradictory, and he wants absolutely nothing to
do with any of them. Magical swords litter his path. He has so many scars
and birthmarks that they look like a skin condition. Beautiful women
approach him in bars. Mysterious cloaked strangers die dramatically in
front of him. Owls try to get into his bedroom window. It's all very
exhausting, since the universe absolutely refuses to take no for an
answer.
There isn't much more to the story than this, but Warren writes it in the
first person with just the right tone of exasperated annoyance and gives
Arturus a real problem to solve and enough of a plot to provide some
structure. I'm usually not a fan of parody stories because too many of
them feel like juvenile slapstick. This one is sarcastic instead, which is
much more to my taste.
"Forego Quest" goes on perhaps a bit too long, and the ending was not as
successful as the rest of the book, but this was a lot of fun and made me
laugh. (7)
Rating: 6 out of 10
On Saturday 19 July 2025, the annual Debian Developers and Contributors
Conference came to a close.
Over 443 attendees representing 50 countries from around the world came
together for a combined 169 events (including some which took place during
the DebCamp) including more than 50 Talks, 39 Short Talks, 5 Discussions,
59 Birds of a Feather sessions ("BoF" informal meeting between developers
and users), 10 workshops, and activities in support of furthering our
distribution and free software,
learning from our mentors and peers, building our community, and having a bit
of fun.
The conference was preceded by the annual
DebCamp hacking session held 7
through 13 July where Debian Developers and Contributors convened to
focus on their individual Debian-related projects or work in team sprints
geared toward in-person collaboration in developing Debian.
This year, a session was dedicated to prepare the BoF "Dealing with
Dormant Packages: Ensuring Debian's High Standards"; another, at the
initiative of our DPL, to prepare suggestions for the BoF Package
Acceptance in Debian: Challenges and Opportunities"; and an afternoon around
Salsa-CI.
As has been the case for several years, a special effort has been made to
welcome newcomers and help them become familiar with Debian and DebConf
by organizing a sprint "New Contributors Onboarding" every day of Debcamp,
followed more informally by mentorship during DebConf.
The actual Debian Developers Conference started on Monday 14 July 2025.
In addition to the traditional "Bits from the DPL" talk, the continuous
key-signing party, lightning talks, and the announcement of next year's
DebConf26, there were several update sessions shared by internal projects
and teams.
Many of the hosted discussion sessions were presented by our technical
core teams with the usual and useful "Meet the Technical Committee", the
"What's New in the Linux Kernel" session, and a set of BoFs about Debian
packaging policy and Debian infrastructure. Thus, more than a quarter of the
discussions dealt with this theme, including talks about our tools and
Debian's archive processes. Internationalization and Localization have been
the subject of several talks. The Python, Perl, Ruby, Go, and Rust programming
language teams also shared updates on their work and efforts. Several talks
have covered Debian Blends and Debian-derived distributions and other talks
addressed the issue of Debian and AI.
More than 17 BoFs and talks about community, diversity, and local outreach
highlighted the work of various teams involved in not just the technical but
also the social aspect of our community; four women who have made
contributions to Debian through their artwork in recent years presented
their work.
The one-day session "DebConf 2025 Academic Track!", organized in collaboration
with the IRISA laboratory was the first session welcoming fellow academics
at DebConf, bringing together around ten presentations.
The schedule
was updated each day with planned and ad hoc activities introduced by
attendees over the course of the conference. Several traditional activities
took place: a job fair, a poetry performance, the traditional
Cheese and Wine party (this year with cider as well), the Group Photos, and the
Day Trips.
For those who were not able to attend, most of the talks and sessions were
broadcasted live and recorded; currently the videos are made available
through this
link.
Almost all of the sessions facilitated remote participation via IRC and Matrix
messaging apps or online collaborative text documents which allowed remote
attendees to "be in the room" to ask questions or share comments with the
speaker or assembled audience.
DebConf25 saw over 441 T-shirts, 3 day trips, and up to 315 meals planned per
day.
All of these events, activities, conversations, and streams coupled with our
love, interest, and participation in Debian and F/OSS certainly made this
conference an overall success both here in Brest, France and online
around the world.
The DebConf25 website
will remain active for archival purposes and will continue to offer
links to the presentations and videos of talks and events.
Next year, DebConf26 will be held
in Santa Fe, Argentina, likely in July. As tradition follows before
the next DebConf the local organizers in Argentina will start the
conference activities with DebCamp with a particular focus on
individual and team work towards improving the distribution.
DebConf is committed to a safe and welcome environment for all
participants. See the
web page about the Code of Conduct on the DebConf25 website
for more details on this.
Debian thanks the commitment of numerous
sponsors
to support DebConf25, particularly our Platinum Sponsors:
AMD,
EDF,
Infomaniak,
Proxmox, and
Viridien.
We also wish to thank our Video and Infrastructure teams, the DebConf25
and DebConf committees, our host nation of France, and each and every
person who helped contribute to this event and to Debian overall.
Thank you all for your work in helping Debian continue to be "The Universal
Operating System".
See you next year!
About Debian
The Debian Project was founded in 1993 by Ian Murdock to be a truly free
community project. Since then the project has grown to be one of the
largest and most influential Open Source projects. Thousands of
volunteers from all over the world work together to create and maintain
Debian software. Available in 70 languages, and supporting a huge range
of computer types, Debian calls itself the universal operating system.
About DebConf
DebConf is the Debian Project's developer conference. In addition to a
full schedule of technical, social and policy talks, DebConf provides an
opportunity for developers, contributors and other interested people to
meet in person and work together more closely. It has taken place
annually since 2000 in locations as varied as Scotland, Bosnia and Herzegovina,
India, Korea. More information about DebConf is available from
https://debconf.org/.
About AMD
The AMD ROCm platform includes programming models,
tools, compilers, libraries, and runtimes for AI and HPC solution development
on AMD GPUs. Debian is an officially supported platform for AMD ROCm and a
growing number of components are now included directly in the Debian
distribution. For more than 55 years AMD has driven innovation in
high-performance computing, graphics and visualization technologies. AMD is
deeply committed to supporting and contributing to open-source projects,
foundations, and open-standards organizations, taking pride in fostering
innovation and collaboration within the open-source community.
About EDF
EDF is a leading global utility company focused on
low-carbon power generation. The group uses advanced engineering and scientific
computing tools to drive innovation and efficiency in its operations,
especially in nuclear power plant design and safety assessment. Since 2003,
the EDF Group has been using Debian as its main scientific computing
environment. Debian's focus on stability and reproducibility ensures that
EDF's calculations and simulations produce consistent and accurate results.
About Infomaniak
Infomaniak is Switzerland's leading developer
of Web technologies. With operations all over Europe and based exclusively in
Switzerland, the company designs and manages its own data centers powered by
100% renewable energy, and develops all its solutions locally, without
outsourcing. With millions of users and the trust of public and private
organizations across Europe - such as RTBF, the United Nations, central banks,
over 3,000 radio and TV stations, as well as numerous cities and security
bodies - Infomaniak stands for sovereign, sustainable and independent digital
technology. The company offers a complete suite of collaborative tools, cloud
hosting, streaming, marketing and events solutions, while being owned by its
employees and self-financed exclusively by its customers.
About Proxmox
Proxmox develops powerful, yet easy-to-use Open
Source server software. The product portfolio from Proxmox, including server
virtualization, backup, and email security, helps companies of any size,
sector, or industry to simplify their IT infrastructures. The Proxmox solutions
are built on Debian, we are happy that they give back to the community by
sponsoring DebConf25.
About Viridien
Viridien is an advanced technology,
digital and Earth data company that pushes the boundaries of science for a more
prosperous and sustainable future. Viridien has been using Debian-based systems
to power most of its HPC infrastructure and its cloud platform since 2009 and
currently employs two active Debian Project Members.
Contact Information
For further information, please visit the DebConf25 web page at
https://debconf25.debconf.org/ or send
mail to press@debian.org.
DebConf 25 happened between 14th July and
19th July and I was there. It was my first DebConf (the big one, I was at a
Mini DebConf in Hamburg a
couple of years ago) and it was interesting. DebConf 25 happened at a Campus
University at the outskirts of Brest and I was rather reluctant to go at first
(EuroPython 25 was happening at the same time
in Prague), but I decided to use the chance of DebConf happening in Europe,
reachable by train from Vienna. We took the nighttrain to Paris, then found our
way through the maze that is the Paris underground system and then got to Brest
with the TGV. On our way to the Conference site we made a detour to a
supermarket, which wasn t that easy because is was a national holiday in France
and most of the shops were closed. But we weren t sure about the food situation
at DebConf and we also wanted to get some beer.
At the conference we were greeted by very friendly people at the badge station
and the front desk and got our badges, swag and most important the keys to
pretty nice rooms on the campus. Our rooms had a small private bathroom with a
toilet and a shower and between the two rooms was a shared kitchen with a
refrigerator and a microwave. All in all, the accommodation was simple but
provided everything we needed and especially a space to have some privacy.
During the next days I watched a lot of talks, met new people, caught up with
old friends and also had a nice time with my travel buddies. There was a beach
near the campus which I used nearly every day. It was mostly sunny except for
the last day of the conference, which apparently was not common for the Brest
area, so we got lucky regarding the weather.
Given that we only arrived in the evening of the first day of DebConf, I missed
the talk When Free Software Communities Unite: Tails, Tor, and the Fight for
Privacy
(recording),
but I watched it on the way home and it was also covered by
LWN.
On Tuesday I started the day by visiting a talk about
tag2upload
(recording).
The same day there was also an academic track and I watched the talk titled
Integrating Knowledge Graphs into the Debian
Ecosystem
(recording) which presented
a property graph showing relationships between various entities like packages,
maintainers or bugs (there is a
repository with parts of a paper,
but not much other information). The speaker also mentioned the graphcast
framework and the ontocast
framework which sound interesting - we
might have use for something liked this at $dayjob.
In the afternoon there was a talk about the
ArchWiki
(recording)
which gave a comprehensive insight in how the
ArchWiki and the community behind it works. Right
after that was a Debian Wiki BoF. There are various technical limitations with
the current wiki software and there are not enough helping hands to maintain
the service and do content curation. But the BoF had some nice results: there
is now a new debian-wiki mailinglist,
an IRC channel, a MediaWiki installation has been set up during DebConf, there
are efforts to migrate the data and most importantly: and handful of people who
want to maintain the service and organize the content of the wiki. I think the
input from the ArchWiki folks gave some ideas how that team could operate.
Wednesday was the day of the daytrip. I did not sign up for any of the trips
and used the time to try out
tag2upload, uploaded
the latest labwc release to
experimental
and spent the rest of the day at the beach.
Other noteworthy session I ve attended were the Don t fear the
TPM talk
(recording),
which showed me a lot of stuff to try out, the session about
lintian-ng (no
recording), which is an experimental approach to make lintian faster, the
review of the first year of wcurls
existence (no
recording yet) and the summary of Rust packaging in
Debian (no
recording yet). In between the sessions I started working on packaging
wlr-sunclock
(#1109230).
What did not work
Vegan food.
I might be spoiled by other conferences. Both at EuroPycon last year (definitely
bigger, a lot more commercial) and at PyCon CZ
23 (similar
in size, a lot more DIY) there was catering with explicitly vegan options.
As I ve mentioned in the beginning, we went to a supermarket before we went to
the conference and we had to go there one more time during the conference. I
think there was a mixture between a total lack of awareness and a LOT of
miscommunication. The breakfasts at the conference consisted of pastries and
baguettes - I asked at the first day what the vegan options were and the answer
was I don t know, maybe the baguette? and we were asked to only take as
much baguette as the people who also got pastries.
The lunch was prepared by the Restaurant associatif de Kern vent which is
a canteen at the university campus. When we asked if there is vegan food, the
people there said that there was only a vegetarian option so we only ate salad.
Only later we heard via word of mouth that one has to explicitly ask for a
vegan meal which was apparently prepared separatly and you had to find the
right person that knows about it (I think thats very Debian-like ). But even
then a person once got a vegetarian option offered as vegan food.
One problem was also the missing / confusing labeling of the food. At the
conference dinner there was apparently vegan food, but it was mixed with all
the other food. There were some labels but with hundreds of hungry people around
and caterers removing empty plates and dropping off plates with other stuff,
everything gets mixed up. In the end we ate bread soaked in olive oil, until the
olive oil got taken away by the catering people literally while we were dipping
the bread in it.
And when these issues were raised, some of the reactions can be summarized as
You re holding it wrong which was really frustrating.
The dinners at the conference hall were similar. At some point I had the
impression that vegan and vegetarian was simply seen as the same thing.
If the menus would be written like a debian/copyright file it would probably
have looked like this:
Food: *
Diet: Vegan or Vegetarian
But the thing is that Vegan and Vegetarian cannot be mixed. Its similar to non
compatible licenses. Once you mix vegan food with vegan food with vegetarian
food it s not vegan anymore.
Don t get me wrong, I know its hard to organize food for hundreds of people.
But if you don t know what it means to provide a vegan option, just communicate
the fact so people can look alternatives in advance. During the week some of
the vegan people shared food, which was really nice and there were also a lot
of non-vegan people who tried to help, organized extra food or simply listened
to the hangry rants. Thanks for that!
Paris
Saturday was the last day of DebConf and it was a rainy day. On Sunday morning
we took the TGV back to Paris and then stayed there for one night because the
next night train back to Vienna was on Monday. Luckily the weather was
better in Paris. The first thing we did was to look up a vegan burger place. In
the evening we strolled along the Seine and had a couple of beers at the
Jardins du Trocad ro. Monday the rain also arrived in Paris and we mostly went
from one cafe to the next, but also managed to visit Notre Dame.
Conclusio
The next DebConf will be in Argentina and I think its likely that DebConf 27
will also not happen anywhere in trainvelling distance. But even if, I think
the Mini DebConfs are more my style of happening (there is one planned in
Hamburg next spring, and a couple of days ago I learned that there will be a
Back to the Future musical show in Hamburg during that time). Nonetheless I had
a nice time and I stumbled over some projects I might get more involved in.
Thanks also to my travel buddies who put up with me
tl;dr: there is an attack in the wild which is triggering dangerous-but-seemingly-intended behaviour in the Oj JSON parser when used in the default and recommended manner, which can lead to everyone s favourite kind of security problem: object deserialization bugs!
If you have the oj gem anywhere in your Gemfile.lock, the quickest mitigation is to make sure you have Oj.default_options = mode: :strict somewhere, and that no library is overwriting that setting to something else.
Prologue
As a sensible sysadmin, all the sites I run send me a notification if any unhandled exception gets raised.
Mostly, what I get sent is error-handling corner cases I missed, but now and then things get more interesting.
In this case, it was a PG::UndefinedColumn exception, which looked something like this:
PG::UndefinedColumn: ERROR: column "xyzzydeadbeef" does not exist
This is weird on two fronts: firstly, this application has been running for a while, and if there was a schema problem, I d expect it to have made itself apparent long before now.
And secondly, while I don t profess to perfection in my programming, I m usually better at naming my database columns than that.
Something is definitely hinky here, so let s jump into the mystery mobile!
The column name is coming from outside the building!
The exception notifications I get sent include a whole lot of information about the request that caused the exception, including the request body.
In this case, the request body was JSON, and looked like this:
"name":":xyzzydeadbeef", ...
The leading colon looks an awful lot like the syntax for a Ruby symbol, but it s in a JSON string.
Surely there s no way a JSON parser would be turning that into a symbol, right?
Right?!?
Immediately, I thought that that possibly was what was happening, because I use Sequel for my SQL database access needs, and Sequel treats symbols as database column names.
It seemed like too much of a coincidence that a vaguely symbol-shaped string was being sent in, and the exact same name was showing up as a column name.
But how the flying fudgepickles was a JSON string being turned into a Ruby symbol, anyway?
Enter Oj.
Oj? I barely know aj
A long, long time ago, the standard Ruby JSON library had a reputation for being slow.
Thus did many competitors flourish, claiming more features and better performance.
Strong amongst the contenders was oj (for Optimized JSON ), touted as The fastest JSON parser and object serializer .
Given the history, it s not surprising that people who wanted the best possible performance turned to Oj, leading to it being found in a great many projects, often as a sub-dependency of a dependency of a dependency (which is how it ended up in my project).
You might have noticed in Oj s description that, in addition to claiming fastest , it also describes itself as an object serializer .
Anyone who has kept an eye on the security bug landscape will recall that object deserialization is a rich vein of vulnerabilities to mine.
Libraries that do object deserialization, especially ones with a history that goes back to before the vulnerability class was well-understood, are likely to be trouble magnets.
And thus, it turns out to be with Oj.
By default, Oj will happily turn any string that starts with a colon into a symbol:
How that gets exploited is only limited by the creativity of an attacker.
Which I ll talk about more shortly but first, a word from my rant cortex.
Insecure By Default is a Cancer
While the object of my ire today is Oj and its fast-and-loose approach to deserialization, it is just one example of a pervasive problem in software: insecurity by default.
Whether it s a database listening on 0.0.0.0 with no password as soon as its installed, or a library whose default behaviour is to permit arbitrary code execution, it all contributes to a software ecosystem that is an appalling security nightmare.
When a user (in this case, a developer who wants to parse JSON) comes across a new piece of software, they have by definition no idea what they re doing with that software.
They re going to use the defaults, and follow the most easily-available documentation, to achieve their goal.
It is unrealistic to assume that a new user of a piece of software is going to do things the right way , unless that right way is the only way, or at least the by-far-the-easiest way.
Conversely, the developer(s) of the software is/are the domain experts.
They have knowledge of the problem domain, through their exploration while building the software, and unrivalled expertise in the codebase.
Given this disparity in knowledge, it is tantamount to malpractice for the experts the developer(s) to off-load the responsibility for the safe and secure use of the software to the party that has the least knowledge of how to do that (the new user).
To apply this general principle to the specific case, take the Using section of the Oj README.
The example code there calls Oj.load, with no indication that this code will, in fact, parse specially-crafted JSON documents into Ruby objects.
The brand-user user of the library, no doubt being under pressure to Get Things Done, is almost certainly going to look at this Using example, get the apparent result they were after (a parsed JSON document), and call it a day.
It is unlikely that a brand-new user will, for instance, scroll down to the Further Reading section, find the second last (of ten) listed documents, Security.md , and carefully peruse it.
If they do, they ll find an oblique suggestion that parsing untrusted input is never a good idea .
While that s true, it s also rather unhelpful, because I d wager that by far the majority of JSON parsed in the world is untrusted , in one way or another, given the predominance of JSON as a format for serializing data passing over the Internet.
This guidance is roughly akin to putting a label on a car s airbags that driving at speed can be hazardous to your health : true, but unhelpful under the circumstances.
The solution is for default behaviours to be secure, and any deviation from that default that has the potential to degrade security must, at the very least, be clearly labelled as such.
For example, the Oj.load function should be named Oj.unsafe_load, and the Oj.load function should behave as the Oj.safe_load function does presently.
By naming the unsafe function as explicitly unsafe, developers (and reviewers) have at least a fighting chance of recognising they re doing something risky.
We put warning labels on just about everything in the real world; the same should be true of dangerous function calls.
OK, rant over.
Back to the story.
But how is this exploitable?
So far, I ve hopefully made it clear that Oj does some Weird Stuff with parsing certain JSON strings.
It caused an unhandled exception in a web application I run, which isn t cool, but apart from bombing me with exception notifications, what s the harm?
For starters, let s look at our original example: when presented with a symbol, Sequel will interpret that as a column name, rather than a string value.
Thus, if our save an update to the user code looked like this:
# request_body has the JSON representation of the form being submitted
body = Oj.load(request_body)
DB[:users].where(id: user_id).update(name: body["name"])
In normal operation, this will issue an SQL query along the lines of UPDATE users SET name='Jaime' WHERE id=42.
If the name given is Jaime O Dowd , all is still good, because Sequel quotes string values, etc etc.
All s well so far.
But, imagine there is a column in the users table that normally users cannot read, perhaps admin_notes.
Or perhaps an attacker has gotten temporary access to an account, and wants to dump the user s password hash for offline cracking.
So, they send an update claiming that their name is :admin_notes (or :password_hash).
In JSON, that ll look like "name":":admin_notes" , and Oj.load will happily turn that into a Ruby object of "name"=>:admin_notes .
When run through the above update the user code fragment, it ll produce the SQL UPDATE users SET name=admin_notes WHERE id=42.
In other words, it ll copy the contents of the admin_notes column into the name column which the attacker can then read out just by refreshing their profile page.
But Wait, There s More!
That an attacker can read other fields in the same table isn t great, but that s barely scratching the surface.
Remember before I said that Oj does object serialization ?
That means that, in general, you can create arbitrary Ruby objects from JSON.
Since objects contain code, it s entirely possible to trigger arbitrary code execution by instantiating an appropriate Ruby object.
I m not going to go into details about how to do this, because it s not really my area of expertise, and many others have covered it in detail.
But rest assured, if an attacker can feed input of their choosing into a default call to Oj.load, they ve been handed remote code execution on a platter.
Mitigations
As Oj s object deserialization is intended and documented behaviour, don t expect a future release to make any of this any safer.
Instead, we need to mitigate the risks.
Here are my recommended steps:
Look in your Gemfile.lock (or SBOM, if that s your thing) to see if the oj gem is anywhere in your codebase.
Remember that even if you don t use it directly, it s popular enough that it is used in a lot of places.
If you find it in your transitive dependency tree anywhere, there s a chance you re vulnerable, limited only by the ingenuity of attackers to feed crafted JSON into a deeply-hidden Oj.load call.
If you depend on oj directly and use it in your project, consider not doing that.
The json gem is acceptably fast, and JSON.parse won t create arbitrary Ruby objects.
If you really, really need to squeeze the last erg of performance out of your JSON parsing, and decide to use oj to do so, find all calls to Oj.load in your code and switch them to call Oj.safe_load.
It is a really, really bad idea to ever use Oj to deserialize JSON into objects, as it lacks the safety features needed to mitigate the worst of the risks of doing so (for example, restricting which classes can be instantiated, as is provided by the permitted_classes argument to Psych.load).
I d make it a priority to move away from using Oj for that, and switch to something somewhat safer (such as the aforementioned Psych).
At the very least, audit and comment heavily to minimise the risk of user-provided input sneaking into those calls somehow, and pass mode: :object as the second argument to Oj.load, to make it explicit that you are opting-in to this far more dangerous behaviour only when it s absolutely necessary.
To secure any unsafe uses of Oj.load in your dependencies, consider setting the default Oj parsing mode to :strict, by putting Oj.default_options = mode: :strict somewhere in your initialization code (and make sure no dependencies are setting it to something else later!).
There is a small chance that this change of default might break something, if a dependency is using Oj to deliberately create Ruby objects from JSON, but the overwhelming likelihood is that Oj s just being used to parse ordinary JSON, and these calls are just RCE vulnerabilities waiting to give you a bad time.
Is Your Bacon Saved?
If I ve helped you identify and fix potential RCE vulnerabilities in your software, or even just opened your eyes to the risks of object deserialization, please help me out by buying me a refreshing beverage.
I would really appreciate any support you can give.
Alternately, if you d like my help in fixing these (and many other) sorts of problems, I m looking for work, so email me.
Posted on July 25, 2025
Tags: madeof:atoms, craft:sewing, FreeSoftWear
I might be slightly insane? Or am I going to prove something about the
nature and accessibility of sewing and MYOG1 as a hobby?
I love my modular backpack, but it has a very modern look that is
maybe not the best thing when otherwise dressed in historybounding
dress, and it s also a bit bigger than I planned or needed it to be.
So, when one of the shops I buy from had some waterproof cotton
canvas on sale I failed my saving throw against temptations and bought
a few meters, with the intent to make myself a backpack in a different
style.
It needs to be a backpack, because my back doesn t like asymmetrical
bags2, and as far as I know 19th century backpacks
weren t the most comfortable things, so I decided to go for a vaguely
timeless roll top model that has the added advantage not to require a
lot of hardware for the closure, just a few D-rings.
Leather straps would look cool, but also require some tools that I still
don t have, so I decided to look for some cotton webbing, and when I
finally found some in 25 mm and 50 mm width I could finally start
on the project.
Except for one thing: thread. As much as I believe that regular n 50
cotton thread got a bad reputation from sellers who decided to cut
quality in favour of profit, it is not up to the task of sewing a
backpack. Nor that I d use regular sew-all poly thread either.
I do have some of the thread I used for my other backpack, which would
have been strong enough, but it s also in black, which isn t exactly the
look I was aiming for on the natural / ecru colour of both the canvas
and the webbing. I also misremembered it as only being available in that
colour (it isn t), so I wasn t tempted into doing a full online order of
technical materials just for that.
On the other hand, I did have in my stash some strong thread I could
trust for this job, in natural / ecru. There was only one problem: it
was 33 2 Tex linen, and not suitable for the sewing machine. You
can t handsew a backpack.
Or can you? Of course it s going to be much slower, but I m still in a
situation where I have more time and space for handsewing than I have
for machine sewing. And as for strength, my perception is that for the
same stitch length an handsewn backstitch is stronger than a machine
lockstitch, or at least it is more effort to unpick (and thus harder to
accidentally unravel if the thread breaks).
And so I tried.
And it worked.
Having to backstitch everything instead of being able to use a running
backstitch of course meant that it was slower than other sewing
projects, and any time there were more than two layers of fabric I had
to use the stabbing motion rather than the sewing one, which is even
slower, but other than a few places with many layers of both fabric and
webbing it wasn t hard.
And to be fair, the seams were fewer and shorter than other sewing
projects, and with the usual interruptions and uneven time availability
it was done in less than a month, which is somewhat typical for one of
my handsewn projects.
It may have been because of the pattern, but I think it s relevant that
it was also easier than other backpacks I ve made, with significantly
less cursing, even when doing seams that would have been quite fiddly
when sewn by machine.
I have to admit that now I m tempted to plan another backpack using the
same pattern or a slight variation, sewn by machine in a different
fabric, to see the difference in the time it takes and to check if the
changes I think would make it easier to sew by machine are actually
the right thing to do. But maybe I ll wait a bit, other projects are in
the queue.
The pattern is as usual online,
released as #FreeSoftWear.
Having used it for a while, I have to say that it is just the right size
to fit all the things I usually carry,
The fact that it only opens from the top means that finding things that
have fallen to the very bottom involves a bit of rummaging, but not
having to change a zipper every few years when (not if) it breaks is
also very nice, so I m not sure which shape of backpack I prefer.
The soft back of course is an issue when the backpack is filled with
small items, but the molle webbing is there exactly because I have plans
to solve it, beside the trivial put something flat towards the back .
As an object, I m happy with the result. As a project, it was way more
than successful, exceeding all expectations, especially for something
somewhat experimental like this one was.
Make Your Own Gear, i.e. sewing or otherwise constructing
outdoorish equipment.
at least not if I fill them with stuff as I usually
do with my backpack :D
The diffoscope maintainers are pleased to announce the release of diffoscope
version 302. This version includes the following changes:
[ Chris Lamb ]
* Mask stderr from the extract-vmlinux script.
* Make it much more explicit that we return 'success' from the
  extract-vmlinux script instead of just falling through to the bottom of the
  script.
* Use Difference.from_operation in an attempt to pipeline the output of
  extract-vmlinux, potentially avoiding it all residing in memory. This is an
  attempt to prevent out of memory issues on try.diffoscope.org.
[ Siva Mahadevan ]
* Use --print-armap long option with nm in the "ar" comparator for wider
  compatibility.
Posted on July 24, 2025
Tags: madeof:bits
An unsorted list, including some I already knew, but was reminded of.
dpkg-mergechangelogs exists.
Sewing your own shirt, posting it on planet and wearing it on the
first day of DebConf, is more effective than a badge for making people
recognise you.
I need to look into a number of tools for testings things (and try to
start using some of those at $DAYJOB).
Masks are good. masks protect you from debbugs. masks protect you from
ring cameras in the hotel you re staying on the day after debconf.
It s really nice to be chatting of random topics during lunch and
discover that you are talking to the maintainer of a package of which
you are one of the very few users! (the latter bit needs to be changed
:) ).
I need to look into sequoia and all of the modern OpenPGP stuff.
Even if I don t have a lot of money, apparently I have even less sense
(there will be blog posts on the topic in the mid-term future).
I can go to a talk about AI
and not hate the speaker (yeah, the bar is pretty low there :D ). The
automatic subtitles still failed in the same way as automatic
subtitles always fail.
Ringlet software updates (2025-03-23)Recent initial releases of [Ringlet software][r-site] (a fancy name for my pet projects):
[docker-scry][r-docker-scry] version [0.1.0][r-docker-scry-0.1.0] - examine Docker containers using host tools. Maybe the start of a set of tools that will allow system administrators to see what goes on in minimal containers that may not even have tools like ps or lsof installed.
[pshlex][r-pshlex] version [0.1.0][r-pshlex-0.1.0] - join various stringifiable objects and quote them for the shell. A trivial Python function that I've embedded in many of my projects over the years and I finally decided to release: a version of [shlex.join()][python-shlex-join] that also accepts [pathlib.Path][python-pathlib-path] objects.
[uvoxen][r-uvoxen] version [0.1.1][r-uvoxen-0.1.1] - generate test configuration files and run tests. A testing tool for Python projects that can either generate a [Tox configuration file][tox] or run the com...
mapec - my humble trivial tribute to Matt S TroutSo on Monday I learned from Perl Weekly that Matt S Trout ofPerl fame has passed away.I can't say I knew him, though I read a lot of his writings and discussions, andI used a lot of his software; I may have briefly met him at YAPC 2014 in Sofia,but that doesn't really count.So a silly little thing I did to honor his memory was to take a small program thatdoes one thing and does it well, polish it up a bit, and, I guess, try to preserve it fora little bit longer.So here is my version of mapec for what very little it's worth.
The sixteenth release of the qlcal package
arrivied at CRAN today, once
again following the QuantLib 1.39
release this morning.
qlcal
delivers the calendaring parts of QuantLib. It is provided (for the R
package) as a set of included files, so the package is self-contained
and does not depend on an external QuantLib library (which can be
demanding to build). qlcal covers
over sixty country / market calendars and can compute holiday lists, its
complement (i.e. business day lists) and much more. Examples
are in the README at the repository, the package page,
and course at the CRAN package
page.
This releases mainly synchronizes qlcal with
the QuantLib release 1.39.
Changes in version 0.0.16
(2025-07-23)
Synchronized with QuantLib 1.39 released today
Calendar updates for Israel, minor utility functions
update
Minor package maintenance updates
Courtesy of my CRANberries, there
is a diffstat report for this
release. See the project page
and package documentation for more details, and more examples.
How I finally
tracked my Debian uploads correctly
A long time ago, I became aware of UDD (Ultimate Debian Database), which
gathers various Debian data into a single SQL database.
At that time, we were trying to do something simple: list the
contributions (package uploads) of our local community, Debian Bras lia.
We ended up with a script
that counted uploads to unstable and experimental.
I was never satisfied with the final result because some uploads were
always missing. Here is an example:
I made changes in debci 3.0, but the upload was done by someone else.
This kind of contribution cannot be tracked by that script.
Then, a few years ago, I learned about Minechangelogs,
which allows us to search through the changelogs of all Debian packages
currently published.
Today, I decided to explore how this was done, since I couldn't find
anything useful for that kind of query in UDD's tables.
That's when I came across ProjectB. It was my first
time hearing about it. ProjectB is a database that stores all the
metadata about the packages in the Debian archive, including the
changelogs of those packages.
Now that I'm a Debian Developer, I have access to this database. If
you also have access and want to try some queries, you can do this:
I have been using Disroot as my primary email ever since
openmailbox.org stopped. I am very grateful for Disroot s service and
I occasionally donate to them.
Recently, my Disroot inbox has been flooded with spam. On an average
day, I used to receive around 90% spams on entire email
count. However, the situation has improved since then. I contacted the
Disroot team, and they informed me that they are aware of the
situation and planning to migrate to Rspamd from Spamassassin.
I don t know whether they deployed Rspamd, even if so that only going
to process incoming mails, I am looking for a way to identify spams
and purge that are already entered my Imap folders.
Later I found this script nh2/rspamd-move[1], which seems fit my need.
I made couple of trivial changes in the script for my use case. I
wasn t sure of directly running this on my Mail/ dir, so I cloned my
entire local mail directory to another directory and made available to
podman container where I script and rspamd instance exist. I trained
rspamd from the /Spam. Later, I manually moved couple of mails to
/spam folder/. I requested friends to share their spam folder in the
#debian-in channel, but that didn t happen :P
$podman run -it --mount
type=bind,source=/home/abhijith/$MAILS/,target=/container-mail-clone
id:latest
$script.py
(It took some time since I have around 10000+ emails)
Wow, it was quite a successful attempt, I was able to catch most of it
and move to spam/ and couple of false positive in a different
folder. Now I want to do the same in the actual maildir yet very
skeptical. While going through the cloned folder with mutt -f I
remembered that the mails are already indexed by notmuch.
So all I need to do is operate tagging and deletion with notmuch and
it will be synced back to the original mail dir. Ta-da. I cleaned by
Inbox.
[1] - https://github.com/nh2/rspamd-move
One thing that annoys me on TV shows and movies is getting the details wrong. Yes it s fiction and yes some things can t be done correctly and in some situations correctly portraying things goes against the plot. But otherwise I think they should try to make it accurate.
I was just watching The Americans (a generally good show that I recommend watching) and in Season 4 Episode 9 there s a close up of a glass of wine which clearly shows that the Tears of Wine effect is missing, the liquid in the glass obviously has the surface tension of water not of wine. When they run a show about spies then have to expect that the core audience will be the type of detail oriented people who notice these things. Having actors not actually drink alcohol on set is a standard practice, if they have to do 10 takes of someone drinking a glass of wine then that would be a problem if they actually drank real wine. But they could substitute real wine for the close up shots and of course just getting it right the first time is a good option.
Some ridiculous inaccuracy we just need to deal with, like knives making a schwing sound when pulled out of scabbards and silenced guns usually still being quite loud (so many people are used to it being wrong). Organisations like the KGB had guns that were actually silent, but they generally looked obviously different to regular guns and had a much lower effective range.
The gold coins shown on TV are another ridiculous thing. The sound of metal hitting something depends on how hard it is and how dense it is. Surely most people have heard the sounds of dropping steel nuts and ball bearings and the sound of dropping lead sinkers and knows that the sounds of items of similar size and shape differ greatly based on density and hardness. A modern coin made of copper, cupro-nickel (the current silver coins), or copper-aluminium (the current gold coins) sounds very different to a gold coin when dropped on a bench. For a show like The Witcher it wouldn t be difficult to make actual gold coins of a similar quality to iron age coin production, any jeweller could make the blanks and making stamps hard enough to press gold isn t an engineering challenge (stamping copper coins would be much more difficult). The coins used for the show could be sold to fans afterwards.
Once coins are made they can t be just heaped up. Even if you are a sorcerer you probably couldn t fill a barrel a meter high with gold coins and not have it break from the weight and/or have the coins at the bottom cold welded. Gold coins are supposed to have a precise amount of gold and if you pile them up too high then the cold welding process will transfer gold between coins changing the value. If someone was going to have a significant quantity of gold stored then it would be in gold ingots with separators between layers to prevent cold welding.
Movies tend not to show coins close up, I presume that s because they considered it too difficult to make coins and they just use some random coins from their own country.
Another annoying thing is shows that don t match up the build dates of objects used. It s nice when they get it right like the movie Titanic featuring a M1911 pistol which is something that a rich person in 1912 would likely have. The series Carnival Row (which I recommend) has weapons that mostly match our WW1 era, everything that doesn t involve magic seems legit. One of the worst examples of this is the movie Anna (by Luc Besson which is mostly a recreation of his film Nikita but in the early 90s and with the KGB). That film features laptops with color screens and USB ports before USB was invented and when color screens weren t common on laptops, as an aside military spec laptops tend to have older designs than consumer spec ones.
I ve mostly given up on hoping that movies will get hacking scenes that are any more accurate than knives making a schwing sound. But it shouldn t be that hard for them to find computer gear that was manufactured in the right year to use for the film.
Why can t they hire experts on technology to check everything?
Related posts:
ReWine I have just discovered an innovative Melbourne company that has...

 It's Sunday and I'm now sitting in the train from Brest to Paris where I will be changing to Germany, on the way back from the
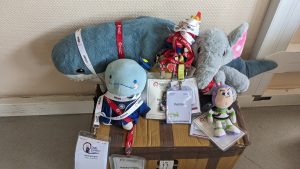 Pollito and the gang of DebConf mascots wearing their conference badges (photo: Christoph Berg)
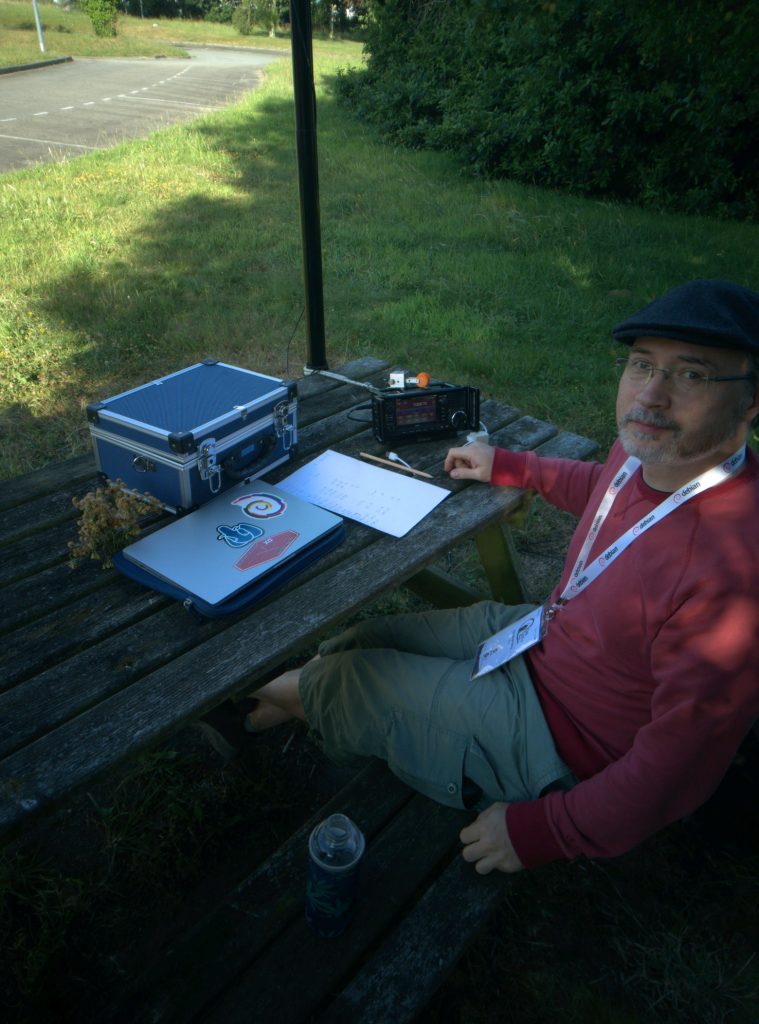 F/DF7CB in Brest (photo: Evangelos Ribeiro Tzaras)
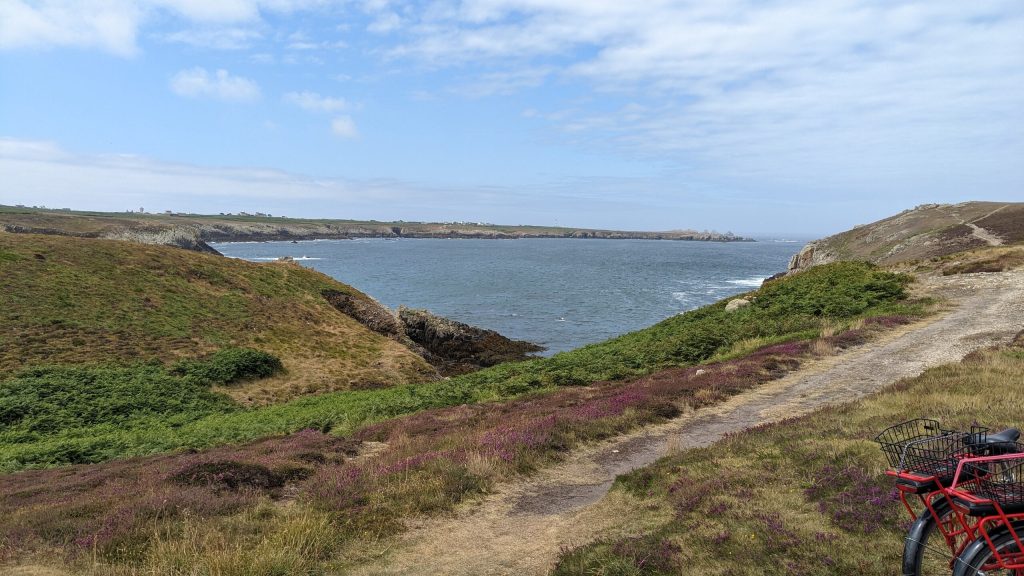 The northern coast of Ushant (photo: Christoph Berg)
 Having a nice day (photo: Christoph Berg)
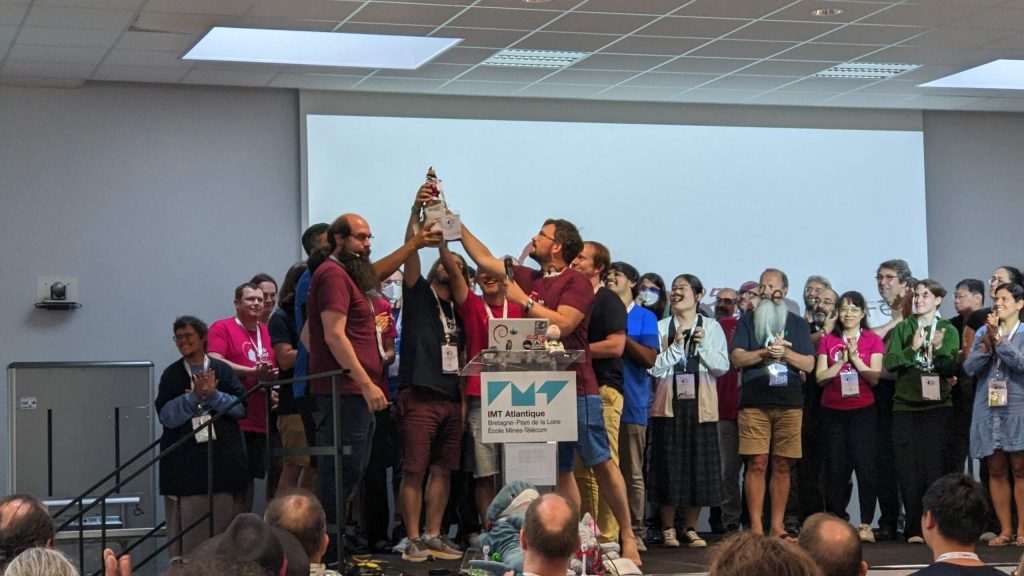 Pollito on stage (photo: Christoph Berg)


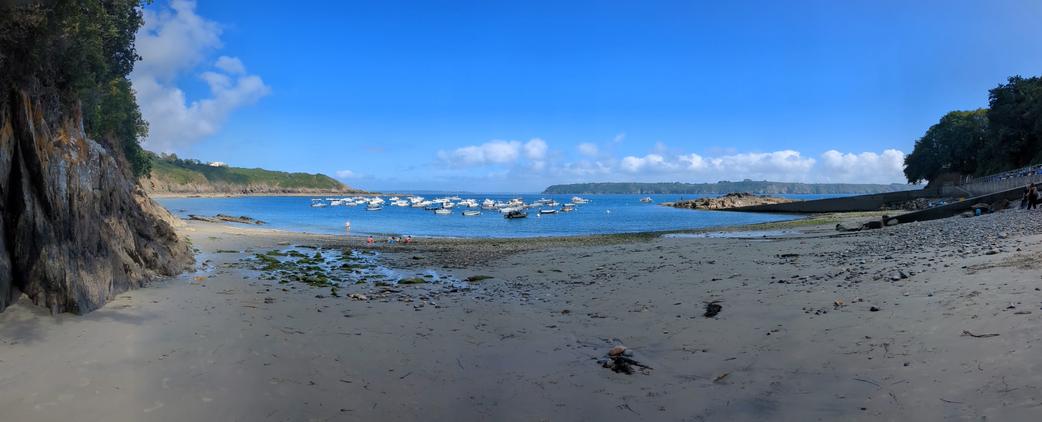 Given that we only arrived in the evening of the first day of DebConf, I missed
the talk
 Wednesday was the day of the daytrip. I did not sign up for any of the trips
and used the time to
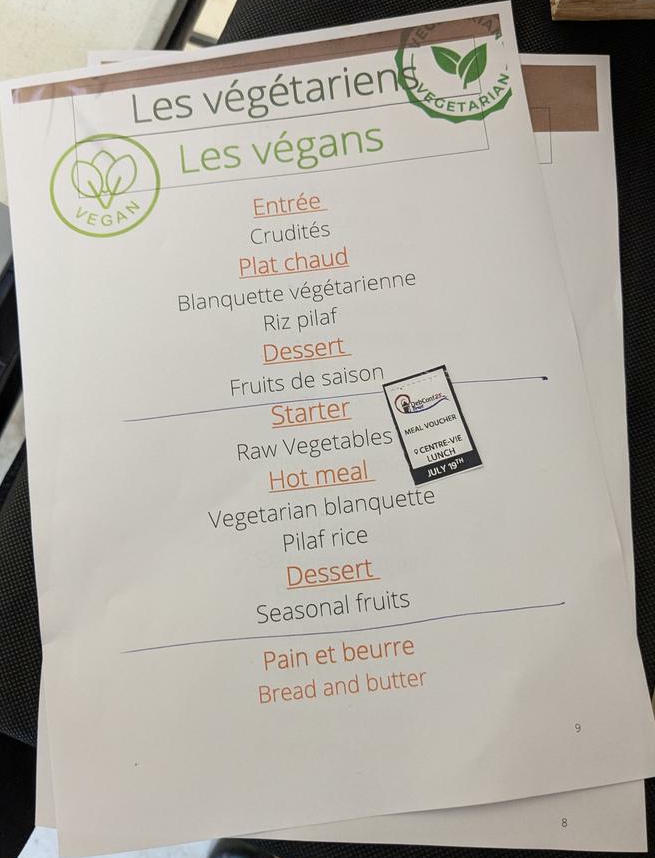 If the menus would be written like a

 I might be slightly insane? Or am I going to prove something about the
nature and accessibility of sewing and MYOG
 Having to backstitch everything instead of being able to use a running
backstitch of course meant that it was slower than other sewing
projects, and any time there were more than two layers of fabric I had
to use the stabbing motion rather than the sewing one, which is even
slower, but other than a few places with many layers of both fabric and
webbing it wasn t hard.
And to be fair, the seams were fewer and shorter than other sewing
projects, and with the usual interruptions and uneven time availability
it was done in less than a month, which is somewhat typical for one of
my handsewn projects.
 It may have been because of the pattern, but I think it s relevant that
it was also easier than other backpacks I ve made, with significantly
less cursing, even when doing seams that would have been quite fiddly
when sewn by machine.
I have to admit that now I m tempted to plan another backpack using the
same pattern or a slight variation, sewn by machine in a different
fabric, to see the difference in the time it takes and to check if the
changes I think would make it easier to sew by machine are actually
the right thing to do. But maybe I ll wait a bit, other projects are in
the queue.
The pattern is
 The soft back of course is an issue when the backpack is filled with
small items, but the molle webbing is there exactly because I have plans
to solve it, beside the trivial put something flat towards the back .
As an object, I m happy with the result. As a project, it was way more
than successful, exceeding all expectations, especially for something
somewhat experimental like this one was.
 The sixteenth release of the