Search Results: "will"

7 February 2011

Jonathan McDowell: Why Linux? (Part 6: Freedom)

(This is part of a series of posts on Why Linux?) I think of myself as reasonably pragmatic in my approach to Free/Open Source software. I don't get worked up over which set of language people want to use. I use devices that require binary firmware to be downloaded to them (because just because I can't see it doesn't mean it doesn't exist). I have non-free in my sources.list. And yet, talking to other Linux users these days, I realize I'm much more of a Freedom nut job than average. I want the source, be it for a driver, a minor widget, or a full app. I don't buy nVidia. I will sacrifice a degree of functionality in order to get Free. And while I think WINE is an excellent piece of software, I think the best end result is that it's no longer necessary, not that it's a perfect implementation of the ABI. How does any of this help justify my use of Linux in the work place? As previously mentioned, I'm a developer. Most developers don't operate in a vacuum; they have to inter-operate with other ecosystems. And usually somewhere along the line there's a failure to document exactly how something is handled, or an ambiguity about what exact choice might be taken. If I have access to the source then I can check that out for myself. If I don't, I have to guess. As an example, a long time ago I was involved in writing a serial console driver for QNX. There came a point where the behaviour wasn't quite as we'd expect. Although the organisation had a license for the source, I wasn't allowed to look at it. Instead I had to come up with a series of suitable questions that someone who could look at the source could answer without violating any NDAs. If I'd been able to look at the source directly we'd have all saved a lot of time. And that's an example where someone could look at the source, rather than having to make a bunch of guesses and instrument tests to see which was right. Access to the Linux source has helped me in other commercial contexts too. At Black Cat we were able to take advantage of patches like grsecurity in order to tighten up shell account boxes. I wrote the IPv6 support for l2tpns, because we had access to the source and could. I've been able to look at the source to understand exactly what SCSI responses are sent in certain circumstances too (or understand exactly what the error that a user land test program was getting back meant). Also I'm a big believe in Linus' Law. I do think that good Free software is much better than proprietary software (there's some really bad Free software out there though, I'm not disputing that). The fact that smart people can look at it and scratch whatever their itch is means that we get a gradual process of improvement that can't be ignored. Equally as long as someone has an interest in the software, end users can't be left high and dry by organisations abandoning still users applications. I think that should be a powerful driver to business to look towards Free software. (Before my more astute readers point it out; yes, I am employed writing non-free software. See the first sentence. One day I'll find a job working on Free software that ticks enough of the other boxes to be viable.)

6 February 2011

Matthew Palmer: My Goals for Wheezy

Inspired by some chatter in IRC, and encouraged to post by Paul Wise, here are my personal goals (in no particular order) during the Wheezy development cycle: So, I've shown you mine, will you show me yours?

David Paleino: Bash-Completion 1.3 released

After almost 8 months from the previous release, the Bash Completion Team is proud to announce the release of bash-completion 1.3! Nothing really innovative in this release. Just "boring" new completions, and bugfixes :) For some stats, this release features 184 completions, the previous (1.2) had 168. For more numbers, please read previous posts. New completions are obviously welcome! Apart from the usual team members (Ville Skytt , Freddy Vulto, Guillaume Rousse and me), we've had contributions from (in no particular order): Anton Khirnov, Paul Walmsley, Miklos Vajna, Andrej Gelenberg, Stephen Gildea and Andrey G. Grozin. Thank you people for helping us! The exciting things will arrive with 2.0. So stay tuned, and enjoy the new bash-completion! -- David

Martin Michlmayr: Upgrading to Debian 6.0 (squeeze) on ARM

Debian 6.0 (squeeze) has been released. Here are some notes if you're running Debian on an ARM-based NAS device or plug computer and are planning to upgrade. First of all, make sure to read the release notes for Debian 6.0 on ARM. This document contains a lot of information on performing a successful upgrade. Second, during the kernel upgrade, you'll get the following message about the boot loader configuration:
The boot loader configuration for this system was not recognized. These
settings in the configuration may need to be updated:
 * The root device ID passed as a kernel parameter;
 * The boot device ID used to install and update the boot loader.
On ARM-based NAS devices and plug computers, you can simply ignore this warning. We put the root device into the ramdisk so it will be updated automatically. Finally, after doing the upgrade and before rebooting your system, make sure to run flash-kernel to activate the new kernel.

Lars Wirzenius: Idea: addsysuser

Debian got squeeze released, and ideas are brewing for what to do during the next release cycle. Here's an idea I had lying around. I'm throwing it out there, since I won't have time to do anything about it for at least a little while, but perhaps someone else thinks it's a good idea? Or, better yet, you can all tell me in comments why this is a bad idea, or at least why it should be designed in a different way.
NAME
       addsysuser, delsysuser - create and remove systems user in Debian pack 
       ages
SYNOPSIS
       addsysuser [options] username
       delsysuser [options] username
DESCRIPTION
       addsysuser creates a system user, and delsysuser removes it.  The  pur 
       puse  of these tools is to make it easier for Debian packages to create
       and remove system users as  the  pacakges  are  installed  and  purged.
       These are wrappers around adduser(8) and deluser(8).
       addsysuser  will  create the system user, unless it already exists.  If
       the user already exists, it does nothing.
       delsysuser removes the user.  However,  the  system  administrator  may
       configure  it  to  never remove the user, or to remove only some users.
       Use the /etc/adduser.conf for the settings:
       DELETESYSTEMUSERS
          Set to true or false  depending  on  whether  delsysuser  should
          remove the system user or not.  Defaults to true.
OPTIONS
       -p, --packagePACKAGE
          Record the user as being used by a specific package.  Many pack 
          ages can use the same user.  delsysuser  will  only  remove  the
          user when no packages are using it anymore.
       --no-act
          Only  pretend  to call adduser or deluser without actually doing
          so.  This allows easier testing of command lines.
FILES
       /etc/adduser.conf
          Configuration file for addsysuser and delsysuser.
EXAMPLE
       In the postinst script:
          addsysuser --package hello hellouser
       In the postrm script:
          delsysuser --package hello hellouser
SEE ALSO
       adduser(8), deluser(8).

Erich Schubert: Debian Squeeze released!

Debian GNU/Linux 6.0 "squeeze" has been released today.
Congratulations to everyone involved in ironing the last few bugs out.
(My own involvement had been a bit limited recently, but I at least kept my few remaining packages in a ready-to-release state and helped with the occasional bug report and patch.)
Some people think that Ubuntu is the better Debian - I do NOT. Debian is a fun place, has great people working on it and is true to its aims at creating a truly free and high-quality distribution. The long release cycles of Debian are a feature, not a bug. Stable is for production systems, not toy projects.
The proper way of attributing Debian stable is conservative and sustainable, but not outdated. It actually can do everything you need - and will do so in 10 years.
If you have been using Open Source for as long as me (say 15+ years) you will probably have seen software hypes come and go. The one thing that has been always the same was Debian: dead reliable. There was a time when everyone was crazy about enlightement for it's shiny pretty UI. Almost like Compiz-Beryl just two years ago. It came, as a matter of fact Debian also had it, but it also went.
I also remember how people complained that Debian didn't ship Xgl back in 2006 when this was the latest hype (there was no Debian release in 2006). Well, Xgl died in 2008. The features remained, but done in a much nicer way, and also found their way into Debian. In fact, I also ran Xgl at least once, on Debian, but just not on "stable". One could say that Xgl never was quite "stable", was it?
Debian stable is good the way it is: an administrators choice. Of course, developers might have different needs, but there also is testing, unstable and experimental. Just make sure to align your choice with your needs. And sometimes, also rethink your needs: there is no "latest beta versions" and "stable platform" at the same time.

Charles Plessy: Long life to Squeeze !

Debian just published Squeeze today. It is an excellent release, that I hope I will keep for a long time on my machines. Among the improvements, boot has been accelerated. On my laptop with a second hand SSD, it only takes 20 seconds to see the login screen. I was amazed when I saw this for the first time. I was often upgrading from Stable to Testing quite quickly, to install more recent versions of desktop applications. But the backports change the game. I hope that I will not switch to Testing before one year or two. For Squeeze, I will also prepare backports for the packages I maintain. I hope that more people will enjoy them. Most of these packages are independant from the graphical system, and more in general from its core. The backports will allow to use recent version of these packages on top of a stable distribution. Since Lenny, Debian Med displays the contents of its metapackages with tasks pages, that include draft packages as well. Not all will make it in Debian, and I would like to have the feedback from our users to better chose our priorities. Contact us on the debian-med@lists.debian.org mailing list ! These new packages will also be distributed for Squeeze through the backports. Thanks again to everybody who contributed to the release of Squeeze !

Joey Hess: 12 hours of talking

I spent a solid 12 hours hosting the Debian Party Line chat today thru the Debian Squeeze release process. That's much much more time than I usually spend on the phone or talking. It went well. The mumble server peaked at 55 people connected, and 200 unique addresses connected to it over the course of the day. We had some good discussions, and a lot of lurkers too. And not too much bother with badly set up microphones. I hope that Debian will find uses for mumble going forward, some ideas I've heard are to use it for team meetings, or for remote audience feedback at DebConf talks. I plan to leave the server up as long as it is not abused.

5 February 2011

Tim Retout: Swirl

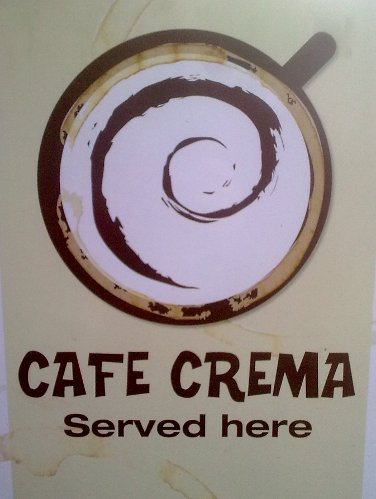
My employer moved offices to Park Gate about a year ago - there's a coffee/sandwich place just down the road, which I generally walk past to get my lunch. And it's got a sign outside: Cafe Crema served here I can't believe I didn't notice that swirl sooner. It will join my picture of the FreeBSD naughty toys machine from DebConf7. In other news, Debian squeeze is being released as I write this. It's been a fun two years. :) Also currently happening is FOSDEM - this is the second year I've missed it, so I reckon I'll make an effort for next year. Instead, today I was at a choral workshop with the Soton Phil, which was really good fun - especially when we danced (yes) through the Osanna from Mozart's Mass in C Minor.

Andrew Cater: Debian 6.0 release is happening now

Debian Squeeze 6.0

As predicted - the release is starting this weekend 5/6 February 2011. IRC channels are starting to buzz -- irc.debian.org #debian-release - and there's also a live commentary session at http://identi.ca/debian

For many people, this is yawn-worthy: Debian stable is seen as old, outdated, outmoded. This is the climax of two years work.

Debian 6.0 will be supported for the lifetime of this release + one year if the past few releases are a guide.

A wrap up release 5.0.9 is planned for the previous Debian 5.0 [Etch Lenny] which will be supported for another year.

Debian works on many machine architectures: it's the upstream for Ubuntu and many other Debian derivatives: it works in many languages, has 1034 developers and maintainers maintaining 28693 packages [last number may vary fractionally depending on machine/architecture].

This is big - and I'm pleased and proud to be part of it. Oh, and there's now over 80 parties worldwide to celebrate :)

[UPDATE - Thanks to my colleagues who pointed out my mistake - Debian 4.0 was Etch, 5.0 is Lenny, 6.0 is Squeeze and 7.x will be Wheezy. Developer/maintainer and party numbers also updated]

Julien Blache: pommed v1.36/v1.37: updates, fixes, MacBook7,1

pommed v1.36 is out and brings support for the MacBook7,1, along with a few fixes and updates. A typo in the pmac keyboard backlight has been fixed, so fading now works there too. Product IDs for the ANSI and JIS keyboard variants for pmac machines were also added. It s been like forever since I last touched that code; not a lot of people still use those (great) machines. This release also contains a small update that will make it compatible with future kernel releases as applesmc will no longer have a fixed a name and location in sysfs. Update: I just noticed a bug in 1.36, so 1.37 is out now. It also contains two patches that were submitted through Alioth.

Craig Small: Syntax Highlighting with Mid-Century themes

As a site that discusses a variety of programming languages, I thought it would be good to have syntax highlighting for the code snippets. This blog runs Movable Type so it had to fit in with the setup I have already. So I found the Syntax Highlighter module ok and the initial installation went fine, it was simply:
  1. Download the .zip archive
  2. Unzip the archive into a temporary directory
  3. Copy the plugins/SyntaxHighlighter directory to my plugins directory
  4. Copy the mt-static/plugins/SyntaxHighlighter directory to static/plugins
You then need to edit the HTML Head template and add to the bottom of it the following line:
<$MTSyntaxHighlighterInclude$>
Next, I like to use Markdown as my markup language. But you can only have one type text filter. Another plugin called FormatStack solves this. Create a new stack and put Syntax Highlighter before Markdown. You can then create documents with both sorts of tags and it works quite nicely, well almost. Mid Century Problems This is probably not a Mid-Century specific problem but the modern templates or styles may cause a problem. You ll find you switch styles and suddenly, no more syntax highlighting. The problem is the onLoad functions get overloaded. Some styles have an onload property on their body. You ll see lines similiar to
 <body id="blogbase" class="whatever" onload="mtEntryOnLoad">
This onload event stops other onload events, which means Syntax Highlighter cannot do its thing. The fix is rather simple, you just adjust the templates so they look like the following:
<body id="blogbase" class="mt-entry-archive layout-wtt">
<script type="text/javascript">
 mtAttachEvent("load", mtEntryOnLoad);
</script> 
After doing this and publishing it all worked! You may also see this sort of problem with other plugins that use the mtAttachEvent() Javascript call. Reducing Includes By default, the script includes all syntaxes it knows. If you want to only include some, you do this by specifying what brushes you want. For example if you only will highlight perl and python scripts then you can change the line to:
<$MTSyntaxHighlighterInclude brush="perl,python"$>
Syntax Themes The other attribute the Include line will take is theme. There are several themes but default is alternating white on grey with the rest being variations on light text on a dark background.

Ian Wienand: Comcast self-setup with Netgear routers

I just got a Zoom 5341 modem to replace a very sketchy old Motorola model and so far it seems to work fine. However, the Comcast self-install switch process was not seamless. After you plug your new modem in the process starts fine, capturing your session and prompting you for your account. However at the next step it prompts you to download the Windows or Mac only client, directing you to an address http://cdn/.... It is at this point you can get stuck if you're behind a Netgear router (I have a WNDR3700) and probably others. The simple problem is that, for whatever reason, the factory firmware in this router does not pass on the domain search suffix through its inbuilt DHCP client. Without that, cdn doesn't resolve to anything, so you can't download the self-help tool and you're effectively stuck at a "can not find this page" screen. If you google at this point you can find many people who have hit this problem, and various information from erroneous suggestions that you've been hacked (?) to most people just giving up and moving into Comcast phone support hell. Assuming you now don't have internet access, you can complete the process with a quick swizzle. Somebody might be able to correct me on this, but I don't think you want to run the self-install tool from an actual computer plugged directly into the modem if you have a router in the picture, because the wrong MAC address will get registered. So, your best solution is to turn everything off, plug your computer directly into the modem, turn it on, get an address, download the tool, turn everything off, plug the router back-in to the modem and then run the self install tool. At this point, everything just worked fine for me. Netgear should probably fix this by correctly passing through the domain search suffixes in their routers. Comcast should probably fix this by doing some sort of geo-ip lookup to give clients a fully-qualified address in that webpage to download the tool even if their router is broken (or really, does downloading that file really require a content-delivery network?). You can probably fix this by running Openwrt on your router before you start. Otherwise, the Zoom modem and the Netgear WNDR3700 seem to make a very nice combination which I would reccommend.

Meike Reichle: Squeeze Release Live Dent

The Debian Press Team will provide a live coverage of today's squeeze release (Yaaay!) via identi.ca. Follow us at http://identi.ca/debian.

Craig Small: JFFNMS and IPv6

ipv6-google-rrt.png One of the many Free Software projects I work on is JFFNMS, which is a network management system written in PHP. In light that the last IPv4 address blocks have now been allocated to APNIC it s probably timely to look at how to manage network devices in a new IPv6 world. First you need to get the basics sorted out and for that it is best to use the net-snmp command line utilities to check all is well. Then its onto what to do in JFFNMS itself. Now fixed with proper markup, I hope.
    strlcpy(hostname, a1, sizeof(hostname));
        if ((pptr = strchr (hostname, ':')))  
            remote_port = strtol (pptr + 1, NULL, 0);
         
Special Agent 6 All devices that are capable of being managed with SNMP have an agent. It s basically the SNMP server on the router, switch or server. The first step is to make sure it can accept and send traffic using IPv6. Depending on what the device is, it can be real simple. For example, my little Juniper router its a matter of setting the community and access control, just like IPv4 settings:
csmall@juniper1# set snmp community public clients 2001:db8:62:d0::/64
And then run snmpget on the command line to check
csmall@elmo$ snmpget -v 1 -c public udp6:2001:44b8:62:d0::4 system.sysObjectID.0
SNMPv2-MIB::sysObjectID.0 = OID: SNMPv2-SMI::enterprises.2636.1.1.1.2.41
We have success! For Linux systems that use net-snmp you will need to make the snmp daemon listen on UDPv6 ports as well as adjusting the access control. Access control is a matter of adding com2sec6 lines to /etc/snmp/snmpd.conf They are the same format as com2sec lines and are reasonably straight forward. Next, get the daemon to listen to requests on the IPv6 ports as well. The snmpd(8) man page says:
By default, snmpd listens for incoming SNMP requests on UDP port 161 on all IPv4 interfaces. However, it is possible to modify this behaviour by specifying one or more listening addresses as arguments to snmpd.
It wouldn t of killed them to put comma separated list somewhere, now would it? My /etc/default/snmpd file now looks like:
SNMPDOPTS= -Lf /dev/null -u snmp -g snmp -I -smux -p /var/run/snmpd.pid udp:127.0.0.1,udp6:[::1]:161
The bits in bold are the changes. Then its a quick check:
csmall@elmo$ snmpget -v 1 -c public udp6:[::1] system.sysObjectID.0
SNMPv2-MIB::sysObjectID.0 = OID: NET-SNMP-MIB::netSnmpAgentOIDs.10
And we have working agents! JFFNMS Changes OK, we have a working IPv6 network and snmp works across our network so we can query devices. JFFNMS uses PHP so all should be well, shouldn t it? Database Tables This is an almost classic problem with converting IPv4 to IPv6. You have 15 bytes for a IP address string 111.222.333.444 . Ipv6 can be much larger than that. JFFNMS has things like
  CREATE TABLE  hosts (
    [...]
   ip  char(20) NOT NULL default '',
A simple fix to use a char(39) or varchar(39) will do the trick. Fixing the JFFNMS code One of the most troubling problems with the host entries is that the values entered by a user can be a hostname, IP address or IP address and port separated by a colon. There are lots of bits of code that separate out the port or address by just finding the colon or use non-IPv6 aware functions like gethostbyname() that will need to be fixed. I ve got a function to check for an IPv6 address, using the inet_pton() function.
  function is_ipv6($addr)
 
  $net_addr = @inet_pton($addr);
  if ($net_addr === FALSE   strlen($net_addr) < 16)
    return FALSE;
  return TRUE;
 
PHP functions PHP still has the old IPv4 only functions, but unlike libc does not have the Address Family independent functions. The most significant absence is the replacement functions for gethostbyname(). There is dnsgetrecord() but it is quite low-level (it won t recurse lookups if you get alias or CNAME results). It s a little hit and miss in PHP-land with what functions work with IPv6 addresses and what ones do not. fsockopen() and file() do work with IPv6. PHP and SNMP To query remote devices using SNMP, JFFNMS uses the PHP SNMP functions. Unfortunately, while there is some IPv6 support in PHP, it doesn t extend to the SNMP functions. The library does it, as the net-snmp command lines use the same library, it is just that the small shim between the script and net-snmp that is PHP gets in the way. Looking at the PHP code itself you find things like
    strlcpy(hostname, a1, sizeof(hostname));
        if ((pptr = strchr (hostname, ':')))  
            remote_port = strtol (pptr + 1, NULL, 0);
         
which definitely need to be fixed for IPv6. There is also some simple address lookup going on somewhere as well which will also need to fixed. In short, JFFNMS won t be doing SNMP based queries over IPv6 until php5-snmp can do it. Reachability JFFNMS also has a different sort of query called a reachability type. It s essentially a ping from the server running JFFNMS out to the device being managed. It uses fping to do this work, but there is also a program called fping6. It s a simple matter of checking the address type and then selecting fping or fping6 to do the reachability work. The JFFNMS code soon to be pushed into git has this change in it now. Anything Else? The next stage is to find anything else that will work with IPv6. A likely candidate is the TCP and UDP port types as they use nmap to discover the ports and the fsockopen() function call to poll it. fsockopen() does handle IPv6 addresses if you escape them in square brackets.

Benjamin Mako Hill: Antifeatures at the Free Technology Academy

In addition to lecturing for two courses at MIT this term, I recently had the pleasure of giving a lecture on antifeatures at the Free Technology Academy -- a program which offers Masters courses over the Internet. Quite a few of the FTA courses are about free software, free knowledge, and related topics! It was my first time giving a lecture to microphone and an empty room. Although I found it a little tricky to adapt to the lack of any audience, the FTA folks put together a great video. I'm psyched that the course material will be available as open education resources for anyone who might want to incorporate it into another course. If you've seen my LCA keynote about antifeatures (which is also available online), there's not going to be a whole new in the lecture. If didn't see it, you might want to check out the lecture. I'll be in the online discussion group around the Lecture for the next couple weeks but you need to sign up to participate.

Craig Small: ncurses into experimental

Sven has been very busy getting a new Debian ncurses packages into order. With the multiple changes made and the fact that so many things depend on the shared libraries, we decided that it is best to put the first cut of these packages into experimental.

We're now using the Quilt 3.0 source format for our packages, which means that we should have a better handle on the patches, especially as they all now have Dep-3 patch tags .

So what has changed, why should you go over and try the experimental packages?

4 February 2011

Richard Darst: DebianNYC Squeeze release party

DebianNYC is having a Squeeze release/super bowl party this Sunday. It is in Park Slope, Brooklyn, and there will be both super bowl watchers and Debian installers/hackers who didn't know the super bowl was this weekend. For more information and to RSVP, see the wiki.Someone in IRC had the bright idea to have a "upgrade to half-broken testing" party in a few weeks. This sounds a lot more fun - and educational. We have been having so many events lately that I am a bit worried about having things too close together, so I guess we'll take it as it comes and people want to organize things. In the near future, we could have a Novice Night in Brooklyn, a Novice Night in the Bronx, a workshop on configuration management of clusters, and now this testing upgrade party.

Lars Wirzenius: Edinburgh squeeze release party

Moray and I decided to celebrate the Debian squeeze release in Edinburgh, Scotland. http://wiki.debian.org/ReleasePartySqueeze/Scotland/Edinburgh has the details, and will get updated as necessary, but here's a repeat: If you like Debian, please join us.

Robert Millan: Diskless Debian GNU/kFreeBSD HOWTO

It was completely non-obvious; In some cases I had to figure it out by reading kFreeBSD source code; I write it down here so it s not forgotten ;-) This is a short guide on how to boot Debian GNU/kFreeBSD via network on a diskless machine, using GRUB as the bootloader.
  • Step 1: Configure your DHCP/TFTP environment to load GRUB from network. See the PXE GRUB documentation for details.
  • Step 2: Rebuild kfreebsd-8 package with BOOTP and BOOTP_NFSROOT options, as described in upstream handbook. They need to be added to the debian/arch/*/*.config file for your architecture. This kernel can still be used for normal, disk-based boot, but it will issue DHCP requests to attempt network boot every time you start it.
  • Step 3: Put your kFreeBSD in TFTP directory and configure GRUB to load it. This requires only one command in grub.cfg. My setup:
    set timeout=1
    set default=0 menuentry Debian GNU/kFreeBSD
    echo Loading kFreeBSD
    kfreebsd /beastie/boot/kfreebsd-8.1-1-amd64.gz
    echo Booting
    boot
  • Step 4: Build a directory tree with your GNU/kFreeBSD userland, and export it via NFS. I copied it from an existing Debian GNU/kFreeBSD install, but I suppose debootstrap could do the job as well.
  • Step 5: kFreeBSD mounts root NFS in readonly mode initially, and Debian userland turns out to be very unhappy with that. If you want things to work you ll need to either setup tmpfs in a few places (e.g. /tmp) or adjust fstab so that / is remounted as writable by the INIT scripts. Example fstab line:
    192.168.1.3:/srv/netboot/beastie / nfs rw 0 0
    This, however, will only work if mount_nfs(8) is in your system. And (well, too bad) it hasn t been packaged yet. So you can copy it from a FreeBSD base tarball, along with its dependencies (/lib/libc.so.7, /libexec and /etc/netconfig).
  • Step 6: Finally the system boots, but you ll soon notice that file locks don t work. This breaks some daemons (rsyslog), dpkg, apt and possibly a lot other things. Actual (i.e. non-local) file locking on NFS requires a running lock daemon, both on client and on server. However, since FreeBSD lockd isn t packaged either, and you probably don t need global locks anyway, I suggest you disable it with nolockd mount option.
    The tricky part is that as explained in mount_nfs manpage, nolockd will only be honored when performing the initial mount, and it will be silently ignored if used while updating the mount options. So fstab is not an option.
    The only way I could find of telling the kernel to use arbitrary options when mounting / is by sending them via DHCP. Use the following options in your dhcpd.conf:
    option option-130 code 130 = text;
    option option-130 nolockd ;
  • Et voil . A Debian GNU/kFreeBSD system running completely in diskless mode. Enjoy!

    Next.

    Previous.