Search Results: "tar"

10 February 2011

Russell Coker: LCA2011, Harassment, etc

The conference LCA 2011 had an anti-harassment policy [1] which was violated by a keynote speech. The speaker and the conference organisers apologised, but of course the matter didn t end there.Discussion continued on the lca-chat list (for conference delegates) [2], on the Linux-aus list (for members of Linux Australia the parent body of the LCA conference) [3], and in some blog posts.There is also some discussion on an LWN article that is linked from an ITWire article [4].I think that the policy was reasonable and from all the descriptions it seems to have worked reasonably well. With such things there are always possibilities to tweak things, so probably there will be future policies which are better in some ways, but it seemed to do the job. The way that the LCA organisers handled the situation was appropriate. In the discussion there were some comments with logical failures that I think need further analysis, I ll summarise them one per paragraph with the heading being a para-phrase of the claim.Is it Offensive?A particularly relevant blog post is Skud s post about avoiding the use of the word offense [5]. In the various discussions about the speech in question most of the people who disapprove of the erotic images don t use the word offense , this is presumably due in part to the influence of Skud s post. This hasn t stopped people claiming that the debate is about whether the images are offensive, I m not sure if this is a deliberate straw-man attack or just cluelessness.The anti-harassment policy does use the word offensive in two places, I think that this was a mistake but it doesn t detract from the overall meaning of the document.Is it Harassment?There was some discussion about whether the actions in question were harassment. Wordnet s definition of harassment includes the act of tormenting by continued persistent attacks and criticism . It seems unlikely that any of the people in the audience who objected to the erotic content in the lecture slides had never seen unwanted erotic material before. So I think that it s worth considering this incident as just another entry in a list of similar incidents that some of the delegates have experienced, and thus as a continuation of persistent attacks IE harassment. Melissa McEwan s post about the variety of harassment that she has received from men is worth reading in this regard [6].I think that a reasonable analogy here is the school bullying campaigns that were experienced by many members of the Linux community when they were younger. School bullying in most cases is not about a small number of extreme incidents, but about a large number of small incidents each of which when considered independently can be rationalised as something that isn t significant (excusing such incidents independently is what allows bullying to be rife in most schools). In many cases of high school bullying the victim is blamed for supposedly over-reacting after a reaction is compared to some small incident at the end of a long harassment campaign, some of the criticism of the Geek Feminists seems to echo this pattern.It seems to me that some of the more dismissive comments which demonstrated a lack of regard for the experiences of other people can reasonably be considered as harassment too (which is also something that Melissa McEwan mentions). Note that I am specifically not advocating that the discussion be shut down, merely that the people who claim that it s only the (supposed) opinion of the majority that matters are part of the problem. However the fact that the apology for the talk received applause from the majority of the audience seems to indicate that the majority is in fact in favor of the anti-harassment policy.Derald Wing Sue, Ph.D. and David P. Rivera (a doctoral candidate in counseling psychology) have written a couple of interesting short articles about this for Psychology Today. Bullying and Microaggressions describes bullying as more than physical violence and also discusses adult bullies [7]. The Power to Define Reality describes the way that the experiences of people who lack power can have the reality of their experiences denied [8] this one really relates to some of the discussions about harassment.But it s Legal!It has been claimed that the legal system works well in Australia and that Australian law should be the only necessary guide to content. A trivial counter-case that was noted in the discussion is the fact that pure sales presentations are not accepted at LCA and such presentations are certainly legal! There is a good precedent for prohibiting things that are legal as part of the conference speaker agreement.More generally the legal system changes slowly and still infringes on what many people in our community regard as basic human rights. There is no reason why an Australian conference should have as it s standards the bare minimum that is required by Australian law.It was pointed out that workplace social norms translate well between cultures, they are usually more stringent than Australian law requires and Australian workplace law is a lot more stringent than the laws relating to conferences and other public events. It seems to me that a presentation which would result in a visit from HR if given at the office shouldn t be regarded as suitable for a conference such as LCA.But there is a Balance of Men and Women in Erotic Pictures!The complaints are not about a lack of balance in the erotic material, but it s presence there at all. Defending the slides on the basis that there was a supposed balance of male and female misses the point that most people just want no erotic material in presentations at conferences.Also it seems to me that if there are pictures which aren t offensive then the way to demonstrate this would be to publish them and say look, they aren t offensive . If it takes 600 words in a blog post to justify the use of some images then that alone seems to be evidence that the images were poorly chosen.But the talk was EffectiveSome of the people who have commented on this issue mentioned that they couldn t remember what was said when the images in question were displayed. When images from the talk are remembered and the main content of the talk isn t that seems to be a failure of the talk.When a major sponsor of the conference complains and requests that the talk video never be published that also seems like a major failure of the talk.I think that the effective talks are ones that educate people and inspire them to do something positive and useful. A talk that inspires a discussion about whether the speaker deserves censure doesn t seem effective.There are claims that there is no way the talk could have made the point as well if it wasn t for the images in question. But I can t believe that someone who is capable enough to get awarded a keynote speaking position at a conference such as LCA is incapable of finding other images to make the same point.But Similar Images are on MTVWhen people want MTV content they can watch MTV.Why Can t we just try Educating Men?It was claimed that education works in dealing with such issues in corporate environments and sporting clubs. My observation of the corporate environment is that such training must be extremely rare in Australia, the Netherlands, and probably the UK due to the fact that none of my employers have done it. I have heard first-hand reports of diversity training from people who work in the US. I expect that the fact that people who fail diversity training in a corporate environment get a meeting with HR is a major factor in it s effectiveness.The long email discussions and blog comment threads when these incidents happen could theoretically be used as training. But when you have some men using multiple mailing lists and dozens of posts arguing without appearing to learn it seems clear that they are not about to learn anything no matter what education is offered. It seems to me that you could broadly divide the free software community into two groups, those who want to learn how to do things better (but who are unlikely to make gross errors anyway), and those who won t learn.Besides, having a keynote speaker at a major conference apologise should be educational.But Clueless Nerds Hit on GirlsI don t know why every discussion about the treatment of women ends up getting a mention of this supposed issue.But Women Could make False AccusationsIn any classification system you have to make some sort of balance between false-positives and false-negatives. If the aim is to get zero false-positives then the incidence of false-negatives will increase. So if the aim was to never ever have a false accusation brought against a man for sexual harassment then the vast majority of real harassment cases would result in no action at all.I don t think it s reasonable to expect that most women who are mistreated should suffer in silence just to reduce the possibility that men might be falsely accused.The Rape Statistics cited in the discussion may be InaccurateThere is no possible way of interpreting rape statistics to make it not be a serious problem, now matter how you analyse the available information it happens far too often and has a significant impact on the victim. Also the suggested reinterpretation of the statistics didn t contradict the claim that it is likely that there are multiple rape victims attending LCA. So interpreting the statistics in a different way to get different numbers doesn t change anything. Trying to diminish the significance of rape generally doesn t support any other arguments that you might make.There are things that you can just discuss for the heck of it and things which should be discussed with care (if at all) to avoid needlessly hurting people. In these sorts of discussions the right thing to do is to avoid debating the numbers as much as possible.I think that the numbers produced by RAINN [9] are as good as we can get.But I am very supportive of women in our communityIf you spend all your time arguing with women and don t listen to what they have to say then you really aren t supporting them.ConclusionAfter publishing this post I ll email the URL to a few of the men who helped inspire it, I will explain how disappointed I am and how I expect better from them. I encourage others to do the same.Also when such discussions happen I encourage men to vote in favor of the positions advocated by women. Writing a message that addresses points in the debate can be difficult and if the debate is rapid then you may find that every point that you might make has been made by someone else. But in that case just posting to agree with the women can really mean a lot.

Charles Plessy: Chain reaction

Now that maintain several dozens of packages in Debian, I think twice before uploading a new one. Does it have a future, a public ? Some of the packages I prepare are available on git.debian.org, and are listed in Debian Med's tasks pages. It would not take me long to finish most of them, but that does not take into account the time others will spend on it. They will make our archive bigger and our quality tests longer to execute. Somebody will translate their description. Somebody else will perhaps write a security patch someday, or a patch to make the package compilable with a new version of GCC. All in all, each package has a footprint in Debian's ecosystem. That footprint starts early, as soon as the package is sent to the NEW queue. For instance, I kept by mistake some old content in the copyright file of clustalw, that was recently freed and has to go through the NEW queue to be transferred from the non-free to the main area of our archive. That costed a small of exchange of emails, that could have been avoided. Our packages should be perfect, but that is difficult to achieve alone. For that reason, I proposed two years ago a package review system, that functions like a chain reaction. The principle is simple. After uploading to the NEW queue, download two neighbor packages and check their copyright file. The errors found can be corrected by their maintainer before the the FTP team inspects it, which save their time. For instance, after uploading tabix, I found an error in mediathekview, that was corrected. That compensates for my mistake with clustalw. If each person receiving a package review does a review of two other packages, that will create a chain reaction that will clean the queue from the simplest mistakes, leaving only the really problematic cases. As Torsten noted recently, the NEW queue is getting long. So how about trying to help ?

9 February 2011

Jonathan Wiltshire: Point Release Security Co-ordinator

In Bits from the Security Team a few weeks ago, Thijs Kinkhorst wrote:
Since a couple of years we ve been handing off security issues of minor or
theoretical impact but for which a fix would be desirable at some point, like
certain classes of denial-of-service attacks, off to stable point updates.
We re looking for a person that wants to coordinate this: monitor the Security
Tracker for issues classified as such by the Security Team, converse with
maintainers to get such updates done and coordinate with the stable release
managers on this.
I m happy to confirm, now that it s been announced, that I am that person: point release security co-ordinator. Affected packages If your package fulfils these criteria: it is a candidate for updating in stable or oldstable, and you ll probably receive a mail from me at some point asking you to do so. You can pre-empt this mail of course, by backporting your fix to the affected versions and contacting the release team to get your fix into stable, without waiting for me. In such a case, please drop me a note with the details so I can tick your off on my hit^W candidate list. Making a stable/oldstable upload This is documented in the Developer s Reference, but to summarise:
  1. Prepare your fix, targetting stable or oldstable, and build it in an up-to-date chroot for that release
  2. Send a diff of the new package to the release team, asking for permission to upload
  3. Upload as normal, and wait for it to be included in the next point release. Meanwhile, notify the security team of your upload, if it fixes a CVE.
Tracking candidate packages I m going to start off tracking filed bugs for SPU candidates and OSPU candidates with usertags in the BTS, under my own address. In time that might be merged into an address used by the security team, but for now I m still finding a good workflow so it s much easier this way.
Comments
Point Release Security Co-ordinator is a post from: jwiltshire.org.uk Flattr

Alexander Wirt: squeeze-backports and lenny-backports-sloppy started

The backports team is proud to announce the next generation of backports:
squeeze-backports. From now on all contributors will be able to upload
backports of packages available in wheezy (testing) to squeeze-backports.
Additionally the previously announced lenny-backports-sloppy is now officially
open for uploads.

To ensure the basic principle that a system consisting of lenny plus
lenny-backports can be upgraded to squeeze proper, the handling of the
lenny-backports branch has changed. From now on uploads to lenny-backports
need manual approval from a backports team member similar to the handling of
the proposed-updates queue within the regular archive. Feel free to upload
packages here, especially security updates to previously backported versions,
but please ensure the versions are lower than those in stable /
stable-security.

If you feel the need of newer versions for lenny than which are available in
squeeze, please do upload them to lenny-backports-sloppy. The rules for this
suite are practically the same as for squeeze-backports: Do base your uploads
on packages available in testing (wheezy) and build them in the appropriate
environment.

Please remember when using lenny-backports-sloppy you can't easily upgrade to a
plain squeeze. This suite is specificly meant to contain newer versions than
squeeze. While the aim is to only carry packages that will also be provided in
squeeze-backports for upgrade possibilities, we can't guarantee that, so be
careful.

User visible change to squeeze-backports

As the apt maintainers had been so kind to introduce a new archive wide option
in squeeze, the usage of backports.debian.org is easier than ever before: In
the past you had to explicitly configure pinning for the backports repository
to enjoy the full feature set including upgrades to new versions of packages
you had installed from there. As this is cumbersome, errorprone and a nuisance
this new setting got introduced. With this feature backports get handled in a
way that updates for packages installed from squeeze-backports will happen out
of the box.

And last but definitely not least, let us send a big "thank you" to all
contributors that backports.debian.org enjoys to have - you made it possible to
serve more than 1400 binary packages through 837 source backports since
lenny-backports got kicked into life. Keep up the good work.

Thank you very much!

Richard Darst: whiteboard.debian.net

A while ago (early 2009), I created whiteboard.debian.net as a way to do real-time editing collaboration. While working for DebConf, I really wanted to be able to collaboratively edit text with people, and all of the web-based solutions I found at the time were non-free. Thus, I took mobwrite and wrote a very thin wrapper around it. Mobwrite is where all the cleverness is (and mobwrite is way beyond my expertise, by the way). Mobwrite is Apache licensed, so you can use it in other places, too.Thus, whiteboard.debian.net was begun. It was never publicized very much. It has no authentication required and no history (the "static link" does provide limited recovery for mistakes, though). Here is a test whiteboard; open it in two tabs and watch the text areas sync. Any whiteboard is created if you go to a valid URL.I just deployed a slightly newer version of whiteboard. You can now see an options page for each whiteboard, and it can render in several lightweight markup languages (good for drafting+previewing things). If you have other options to add there, let me know.If you are interested in collaborative text editing, there are some other options. There is a Debian titanpad, an "open" instance of now-open-sourced Etherpad, and it has history support. Use titanpad.com and you don't have to log in. Here is a test pad. For a non-web application, Gobby exists. Use gobby-0.5 for smart undo history if everyone uses squeeze or above.Is whiteboard still relevant in light of the options above that store history? I'm sure it depends, but for now, whiteboard works well for a low-overhead scratch space and for cases where you don't want to have a history trail. I also tend to use it as a simple pastebin or a personal notepad when I don't want to worry about having traces left behind. In short, it is so minimal you don't have to think about starting one up for something. I have found that collaborative writing really helps to get things done, thus, I hope that whiteboard (or a similar tool) can be useful to you.

8 February 2011

Joey Hess: mapping git repositories

Git has lots of tools to map the history of a git repository. But, I have not been able to find tools to map networks of git repositories. Possibly noone has done it because such networks tend to be pretty centralized really, with low levels of (visible) interconnection, and so not that interesting, like this network of all known branches of ikiwiki. Soon after I started using git-annex, I realized the repositories using it would tend to be more interconnected, and less centralized, and generally a more complex, rich fabric than I'd seen in my use of git before. So I've built "git annex map", which uses graphviz to spit out fun maps like this. (Green nodes are trusted drives; red nodes are not currently available.)
Previously: git tube map

Cyril Brulebois: Debian XSF News #4

Here comes the forth Debian XSF News issue! I usually try to keep the items sorted chronologically (but grouped by topic when possible), so if you re wondering about the current status of X in unstable, make sure you read the last entry.
Mike Hommey: Knowing how much disk seeks hurt

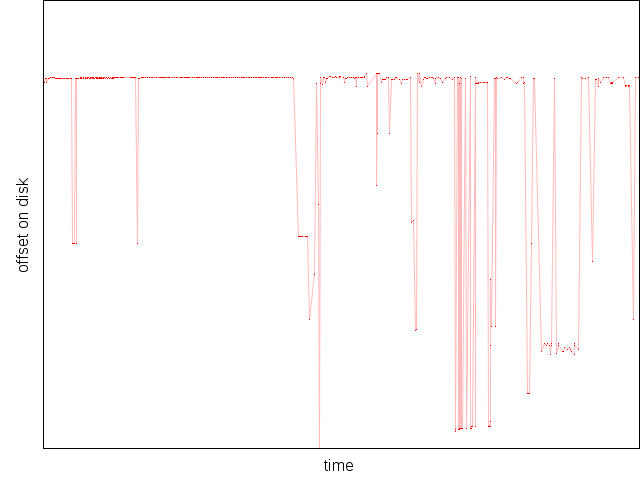
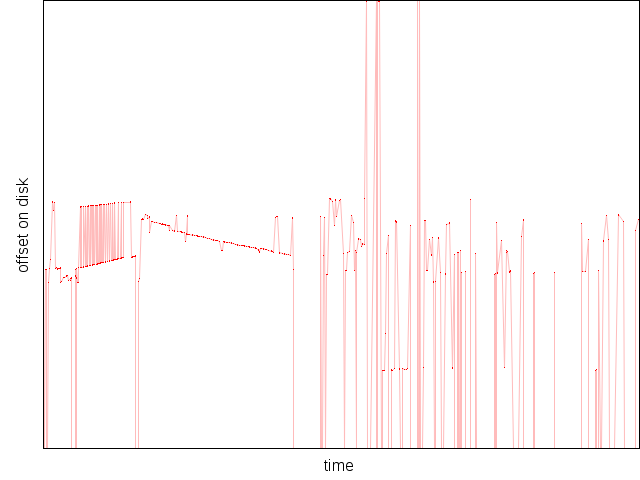
We all know disk seeks hurt. But we usually don t have a precise idea how much. How about getting that idea? Here is a little experiment I ran a few days ago. I took the output from the systemtap script tracking I/O I wrote, on a Firefox startup after boot. Each line of that output, which gives a timestamp (which we don t care about here), a file name, and an offset, represents a 4096 bytes read (one page). The first set of data points I got is how much time it takes to reproduce this read pattern after a reboot, and how that compares to Firefox startup time. For what it s worth, I did group following reads, to avoid doing too many system calls, and also avoided kernel readahead by using direct I/O, meaning I would only read exactly what the kernel reads when Firefox normally starts. All the following tests were done under the usual conditions (see previous posts), but I limited the tests to the x86-64 architecture, because all that really matters is the disk. I ll mention, however, that the amount of data read in these tests is 34,729,984 bytes, and that the original I/O pattern looks like this: Zooming around the main location where most I/O happen, we can see the pattern is still bumpy: This somehow looks familiar, doesn t it? We already know for a fact that even these patterns that, on the whole disk, look like pretty much insignificant, have an important impact on startup time. Try to imagine what kind of difference could be observed if we were reordering all these reads. Anyways, back to that I/O simulation, we first need to see how far it is from the actual Firefox startup. We would rather that simulated I/O + warm startup/hot cache end up close to the real thing. However, we need to keep in mind, as we saw in a previous post, that CPU scaling, when mixed with I/O, has an influence on startup time. Warm startup not involving I/O, the CPU can run at maximum speed the whole time. As such, for a fair comparison, we need to compare to cold startup time with the CPU forced at maximum speed, which we saw is faster than startup time with CPU scaling.
Average time (ms)
Simulated cold startup 2,764.26 0.42%
Warm startup 250.74 0.18%
Simulated cold + warm 3015
Real cold startup 3087.47 0.31%
Difference 72.47 (2.35%)
Close enough, I d say. The difference is most probably caused by metadata reads and a few other things, that isn t in the systemtap script scope. Now we know our simulated I/O is close to reality, what happens if we reorder all these reads according to the position on disk?
Average time (ms) Corresponding transfer rate
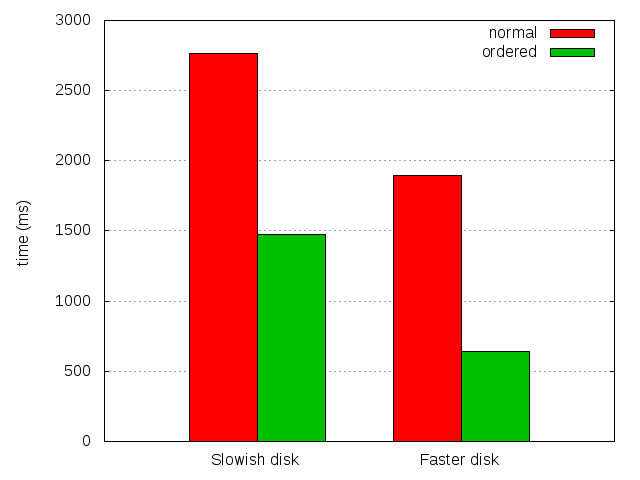
Simulated I/O 2,764.26 0.42% 12.56 MB/s
Reordered I/O 1,473.34 0.43% 23.57 MB/s
Difference 1,290.92 (46.7%) n/a
That s almost twice as fast ! And the disk doesn t even have a big throughput (around 30MB/s). Let s see what it does with a disk with a bigger throughput (85MB/s).
Average time (ms) Corresponding transfer rate
Simulated I/O 1,898.66 0.16% 18.29 MB/s
Reordered I/O 644.0 0.15% 53.93 MB/s
Difference 1,254.66 (66.08%) n/a
That s almost three times as fast ! The faster the disk, the bigger the improvement we can get by reordering and grouping I/O, which is not unexpected, but here we can see how much having to go back and forth on the disk hurt badly. Obviously, the numbers from the faster disk can t be directly compared to the ones from the slower disk, because the data was not arranged the same way on the disk, and file system fragmentation, as well as how the file system is filled also have their own share to add to the problem. And because it s more impressive to see on a graph than in a result table: Disks seeks hurt. Badly.

Julien Danjou: Announcing Org-contacts

When I started to use Emacs, I got hooked by many stuff like Gnus and Org-mode. One thing I quickly started to hate is how the Lisp code can be old and unmaintained. That especially applies to BBDB, which has been unmaintained for years, and has very very very old and obsolete code. Therefore I've decided to develop my own BBDB replacement based on my lovely Org-mode. It's called org-contacts, and it allows you to handle your contact like anything you would handle in Org. This way you can manage them the way you want, without any preset fields or any assumptions like BBDB has. I had the chance to present it at the Paris OrgCamp a couple of weeks ago, and due to the enthusiastic audience I had, I'm now releasing it to the wide Internet. Flattr this

Lars Wirzenius: Growing the Debian development community

In an article about gender issues among American atheists, Sharon Moss and Lyz Liddell give a list of things to consider to be better community, not just for women:
  • Be a leader. Take responsibility for the tone of your group. If potential new members are being made to feel uncomfortable and aren t coming back, you re doing it wrong. As a leader, it is your job to prioritize the comfort of your attendees in programs, group dynamics, and communications. Try to put yourself in other members shoes and also ask for feedback.
  • Promote a sense of community. Take the time to socialize and get to know each other. If you re group isn t primarily a social group, thinking about adding some social time. Go to breakfast before the protest, compose your letters to the editor over coffee, or grab a pizza and beer after that lecture. When you know each other, you have each others backs. Being a jerk isn t tolerated.
  • Moderate discussions. Make sure everyone has the opportunity to participate- new people, quiet people, etc. Don t let conversation be dominated by one or two people who must win.
  • Embrace and accept different ways of communicating. Whether someone is an aggressive debater or not, make sure they re still welcome. The other atheist in the room isn t your enemy.
  • Encourage subgroups. Every event your group hosts doesn t need to appeal to your entire membership. Many women appreciate women-only space to express their nonbelief and to connect with other atheist women. Here at the Humanist Community of Central Ohio, we started a subgroup book club called Reasonable Women. When it grew to have about 25 regular members and was beginning to be a little too large and unwieldy to function as a book club, we created a second group, Heathen Chicks, which is just a social group that meets at a local cafe. It isn t just about creating women only space, for us, this has been a way to draw more women into other events our group hosts.
  • Foster women in leadership. Groups with women in leadership positions tend to have more women. Encourage women in your group to be visible in leadership.
These should work pretty well for Debian as well. I mean for the project in general, for getting all kinds of new people in, and getting them to stay, not just women, even if the gender imbalance is perhaps the biggest glaring problem we have. As a concrete suggestion, maybe it would be a good idea to continue the Debian party line that Joey set up for the squeeze release. We already have IRC, but having an audio chat with your Debian peers might be a nice addition. Specifically a social one, instead of something intended to boost productivity.

Jonathan McDowell: My Squeeze upgrade notes

I did my first upgrade of a lenny box to squeeze today; a test server in work. All went pretty smoothly but I had a handful of things I had to frob manually that I thought I'd write up here: I think that's pretty smooth overall; kudos to all those involved. I've a few more boxes to upgrade, but they're all more likely to have people complaining at me if there are hiccups so they'll have to wait until I have a suitable block of time set aside.

7 February 2011

Vincent Sanders: It is a bit breezy

The weather has been a bit odd round here for a while now. The snow storms in December and early January were a mild inconvenience for me but as I work from home the advice not to travel was not too much of a problem.

It seems however that now February is here and the snow is gone we are in for some pretty strong storms. This actually affected me today when my neighbours garden wall was blown over!

As you can see my nice new IP camera captured the event, well OK the frame before and after but you get the idea. Unfortunately for my neighbour the wall collapsed onto his pickup causing extensive damage.

A short time later when my weather station was recording gusts well over 50mph nearby drains started flowing the wrong way and it became a case of water, water everywhere!

It seems that when the new buildings were erected a few years ago that the architect while maximising used space on the building plot may have inadvertently created something of a wind tunnel.

The Gap between our properties is on a parallel (north to south) to the valley below. The wind seems to travel along the crest of the valley and be funnelled through any spaces between the houses. Fortunately the rest of the properties on green lane are pretty old and the spacing between is very generous and the funnelling effect is minimal.

I wonder if we could fit a wind turbine in there? Alas it was too much for my secondary anemometer which is now smashed in three parts.

Also gaining access to the gable end wall of my property has become somewhat perilous (Hence the wonky APT antenna I cannot get fixed). Yes that really is a guy balancing on a ladder 10m high in a strong wind. And indeed the platform the ladder is resting on is built from scaffolding board wedged between the houses.

I guess the hospital emergency room being 300m away means medical assistance is on hand, even so he is braver than I am. So my weather satellite imagery will just have to come from the internet like everyone else's for a while.

Ana Beatriz Guerrero Lopez: post and pre-release fun

The last weeks before a Debian release are usually boring with respect to working on new stuff since unstable is pretty much closed to development. Now that the release is finished, this fun is back \o/ I have been in an upload frenzy since yesterday night and I have updated some packages in unstable: KOffice[1] and KOffice-l10n 2.3.1, yakuake, rsibreak and tintin++. Another of my packages, kid3, got magically updated itself in unstable before I had time to look at it, the magic of having active co-maintainers. [1] Thanks for the gentle push to update this, Pino :) I also emailed one of my upstream maintainers to ask him about the KDE 4 version of his application and he will likely make a release soon. One of the goals for wheezy is remove completely KDE 3 and Qt 3. If you are maintaining a KDE 3 or Qt 3 based application, we are about to start annoying you about this! See http://wiki.debian.org/kdelibs4c2aRemoval and http://wiki.debian.org/qt3-x11-freeRemoval The last 2 weeks before the release I had some fun watching how the Squeeze release countdown banner I published at http://news.debian.net spread to a lot of websites, personal blogs, community sites, forums to news portals.

The traffic has been increasing little by little through the 2 weeks the banner has been online and currently is still moderately high, since people keeps retweeting the news item about the Debian release. While writing these lines, the banner has been served 449575 times to a total of 244975 unique IP addresses!

Matthew Garrett: Hardware vexation

My laptop (an HP 2530p) gets quite a lot of abuse. It's been with me enough to have done the equivalent of going round the world 4 or 5 times, and it's typically just thrown in a bag without any particular care or attention being given to its care or wellbeing. It's been dropped a couple of times with the only damage being some corners that aren't really as even as they should be. All in all, it's survived amazingly well. But it recently started refusing to boot, merely flashing its LEDs. After finally finding a list of what these mean, I narrowed it down to the memory. Taking it apart and putting it back together again got things working for a while, but then it happened again. And again. So, since I have one memory module and two slots, I decided to just move the RAM in the hope that there's something physically wrong with the slot. It worked! Until I got to the BIOS splash and it informed me that Intel AMT requires that there be memory in slot 0. And didn't give me an opportunity to continue without AMT.

My hardware is conspiring against me.

Torsten Werner: You are uploading too fast

This is my first blog post on my new tarent blog which I am using as a replacement for blogspot. We had 451 new source packages in the NEW queue tonight. It is nice to know that Debian is the largest free software distribution but it will take some time until we (the ftp team) have processed all those new packages as we need the check every single package. I wanted to work on dak (the Debian archive kit) again after we have released Squeeze but I ll give NEW processing a higher priority. My next plan for dak is generating the contents files in dak directly instead of using apt-ftparchive. Contents generation is the slowest part of apt-ftparchive and having the package contents in dak s database is quite useful.

Michal Čihař: New phpMyAdmin themes

Today, I've made available two new themes for phpMyAdmin on our demo server. First one is Toba theme which was contributed by Azhari Harahap: Toba theme Second one is Graphite theme which I've started during Hackweek and finished during free time around FOSDEM: Graphite theme And we're still waiting for more contributions to our Theme contest. PS: Forgot to mention that new themes are only for 3.4 branch and won't work with others.

Filed under: English Phpmyadmin Suse 0 comments Flattr this!

Jonathan McDowell: Why Linux? (Part 6: Freedom)

(This is part of a series of posts on Why Linux?) I think of myself as reasonably pragmatic in my approach to Free/Open Source software. I don't get worked up over which set of language people want to use. I use devices that require binary firmware to be downloaded to them (because just because I can't see it doesn't mean it doesn't exist). I have non-free in my sources.list. And yet, talking to other Linux users these days, I realize I'm much more of a Freedom nut job than average. I want the source, be it for a driver, a minor widget, or a full app. I don't buy nVidia. I will sacrifice a degree of functionality in order to get Free. And while I think WINE is an excellent piece of software, I think the best end result is that it's no longer necessary, not that it's a perfect implementation of the ABI. How does any of this help justify my use of Linux in the work place? As previously mentioned, I'm a developer. Most developers don't operate in a vacuum; they have to inter-operate with other ecosystems. And usually somewhere along the line there's a failure to document exactly how something is handled, or an ambiguity about what exact choice might be taken. If I have access to the source then I can check that out for myself. If I don't, I have to guess. As an example, a long time ago I was involved in writing a serial console driver for QNX. There came a point where the behaviour wasn't quite as we'd expect. Although the organisation had a license for the source, I wasn't allowed to look at it. Instead I had to come up with a series of suitable questions that someone who could look at the source could answer without violating any NDAs. If I'd been able to look at the source directly we'd have all saved a lot of time. And that's an example where someone could look at the source, rather than having to make a bunch of guesses and instrument tests to see which was right. Access to the Linux source has helped me in other commercial contexts too. At Black Cat we were able to take advantage of patches like grsecurity in order to tighten up shell account boxes. I wrote the IPv6 support for l2tpns, because we had access to the source and could. I've been able to look at the source to understand exactly what SCSI responses are sent in certain circumstances too (or understand exactly what the error that a user land test program was getting back meant). Also I'm a big believe in Linus' Law. I do think that good Free software is much better than proprietary software (there's some really bad Free software out there though, I'm not disputing that). The fact that smart people can look at it and scratch whatever their itch is means that we get a gradual process of improvement that can't be ignored. Equally as long as someone has an interest in the software, end users can't be left high and dry by organisations abandoning still users applications. I think that should be a powerful driver to business to look towards Free software. (Before my more astute readers point it out; yes, I am employed writing non-free software. See the first sentence. One day I'll find a job working on Free software that ticks enough of the other boxes to be viable.)

6 February 2011

Christian Perrier: Squeeze released

This is the gazillionth entry on Planet Debian about Squeeze being released. If I had to say one thing about it, it would be that I think the way it was handled this time has been really great. The debian-publicity team, lead by the tireless Reichles, did great job in doing as many buzz as possible around that release....but managed to do it in the "spirit" of free software (pushing release parties, animating a feed on identi.ca, preparing press releases, etc.). The Release Team did a tremendous job during the 6 months of the freeze, by carefully balancing between conservatism and liberalism in accepting (or denying) our gazillion of request for freeze exceptions The FTP, CD, installer, website, documentation teams organized things really well for their respective fields of responsibility. A special mention to the tremendous effort done about the release notes, release announcements documents (and of course, their translators). I'm currently busy upgrading my servers (at home and at work) and things are going smoothly (except the first two I did without carefully reading warnings about missing firmwares...they're now waiting for me to provide them with the right non free firmware packages, 30km away from here). And, for myself, I celebrated the release this morning by squashing my personal best time on an half-marathon (officials races excepted) by nearly 7 minutes, bringing it just below 1h45 (PB in official races is 1h37). Release power! :) And, during that afternoon, I also had the please of having my pet package (geneweb) and my most important package (samba) having their first release in unstable, targeted for wheezy. Squeeeeeeze meeeeeeeeeeeee!

Raphaël Hertzog: Debian 6.0 is out, Wheezy kicks off

As you probably already know, Debian released Squeeze aka Debian 6.0 this week-end. It was a really great week-end. I saw quite a few release already, but none with so much online social activity. Alexander and Meike Schmehl live commented the release on the Debian identi.ca account and Joey Hess held his Debian Party Line. On top of this, the team in charge of the website rolled out a new design on quite a few online services during the week-end including www.debian.org, wiki.debian.org, planet.debian.org and more. Congratulations to all the people who made this happen (and the release team in particular). It s great to see Debian achieve all of this. Do you know that it s the third time in a row that we manage to release in the 18-24 months timeframe? 3.1: June 2005 4.0: April 2007 5.0: February 2009 6.0: February 2011. Yes, despite our size and the fact that we are all volunteers, we have managed to stick to a reasonable schedule for a stable distribution that is deployed on a large scale. Wheezy kicks off The best part of the release for us the developers is that wheezy is now open for development and we can work on new features for the next release. ;-) And it started quickly: according to UDD, wheezy already features 488 new source packages that are not in squeeze, 1713 updated source packages and among those 1246 are new upstream versions. I really look forward to the upcoming projects and related discussions.
Click here to subscribe to my free newsletter and get my monthly analysis on what s going on in Debian and Ubuntu. Or just follow along via the RSS feed, Identi.ca, Twitter or Facebook.

For the curious, here are the UDD queries I used:
# Updated packages in wheezy
select count(source) from sources_uniq as su where (select version from sources_uniq where release='squeeze' and distribution='debian' and source = su.source) < su.version and release='wheezy' and distribution='debian';
# Updated with a new upstream version
select count(source) from sources_uniq as su where debversion(regexp_replace((select version from sources_uniq where release='squeeze' and distribution='debian' and source = su.source), '-.*', '')) < debversion(regexp_replace(su.version, '-.*', '')) and release='wheezy' and distribution='debian';
# New package in wheezy
select count(source) from sources_uniq as su where source not in (select source from sources_uniq where release='squeeze' and distribution='debian' and source = su.source) and release='wheezy' and distribution='debian';

No comment Liked this article? Click here. My blog is Flattr-enabled.

Kees Cook: fun with game memory

So, I was testing a (closed source) single-player offline game recently and thought this exercise might be fun to document. I didn t want to spend any time actually earning in-game money since I d played it before and I wanted to just skip ahead to other aspects of the game. I was curious how straight-forward adjusting my cash might be. So, noting the in-game bank account number of 219393 and account balance of 3000, I dived right in. First up, what s the memory layout of the heap look like? I looked at the brk and the mmap regions without a mapped library or file, marked with w in the permissions column, from /proc/PID/maps:
0827e000-08282000 rw-p 00000000 00:00 0
0a22e000-0b08a000 rw-p 00000000 00:00 0 [heap]
efa59000-efd00000 rw-p 00000000 00:00 0
efd00000-efd21000 rw-p 00000000 00:00 0
Knowing these, I could use gdb s find command, after attaching to the process:
$ gdb /some/cool/game

(gdb) attach PID

(gdb) find /w 0 0827e000, 0 08282000, 219393
(gdb) find /w 0 0a22e000, 0 0b08a000, 219393
0xaf03d08
0xaf06ca8
No hits in the first region, but I see two hits for the account number value in the second region. Let s start there and see what s near them
(gdb) x/8x 0xaf03d08
0xaf03d08: 0 00035901 0 00000000 0 00000000 0 0af06ce0
0xaf03d18: 0 0af06be0 0 00000059 0 0af03d98 0 0af041e8
(gdb) x/8x 0xaf06ca8
0xaf06ca8: 0 00035901 0 00000bb8 0 00000bb8 0 0820b148
0xaf06cb8: 0 00000001 0 00000000 0 00000000 0 00000000
In that second hit, I see the value 0xBB8, which is 3000, and matches our account balance. Let s see what happens if we just change both of those to add a bit a few orders of magnitude above the current value
(gdb) set var *0xaf06cac = 0 00100bb8
(gdb) set var *0xaf06cb0 = 0 00100bb8
(gdb) x/32x 0xaf06cac
0xaf06cac: 0 00100bb8 0 00100bb8 0 0820b148 0 00000001
(gdb) continue
And presto, clicking on the bank account details in-game shows a huge account balance of 1051576 now. No need to reverse-engineer any saved games, whew.

Next.

Previous.

