Search Results: "ema"

24 July 2006

Bdale Garbee: Bad Caps

My wife couldn't read her email last night. Turns out the old Apple Airport wireless access point we still depend on had failed again. All lights blinking red, and a low buzzing sound in time with the blinking. Same symptoms as the other time it failed. Turned out to need the same fix again, too. Disassembled the flying saucer, and started wiggling parts on the board with the power applied until I found where the buzzing was coming from... one of the electrolytic caps in the power supply. Fortunately, I had a suitable replacement in my parts stock and we were back on the air ten or fifteen minutes later. One of these days, it'll fail during daylight hours and I'll just drive into town and buy an 802.11g hub to replace it... after all, my current laptop supports a/b/g, and the old hub is b-only. But, when it's night, it's snowing, and there's a hockey game on... having tools, parts, and experience troubleshooting recalcitrant widgets is good for family harmony!

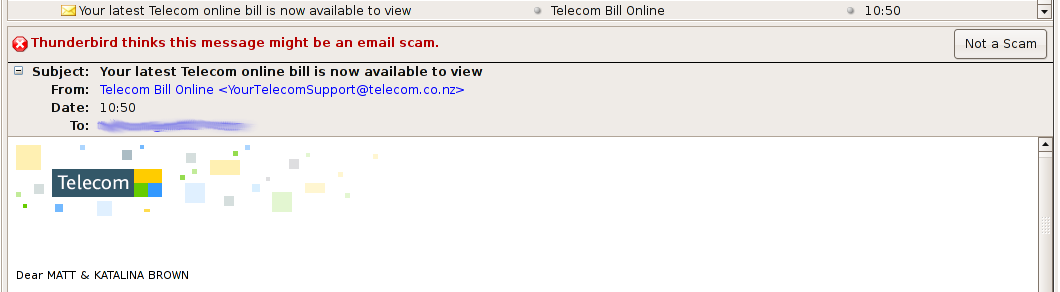
Matt Brown: Telecom Billing Scam!?

Is thunderbird smarter than it thinks? Thunderbird thinks this email is a scam!
Click image to enlarge.

23 July 2006

Amaya Rodrigo: The /usr/doc transition

Quote from Joey Hess: In 1999, Debian began moving /usr/doc to /usr/share/doc to comply with the FHS. Due to unfortunate dpkg issues at the time, we couldn t simply move the directory and be done with it, but decided to move things peicemeil by updating all packages. Due to some silly concerns about users having to look in two places during the transition, we decided to start by making /usr/doc/ -> /usr/share/doc/ symlinks. In 2001, putting any documentation in /usr/doc became a serious policy violation. The symlinks were still allowed. In 2002, we completed the first stage of the transition, released woody with complete /usr/share/doc and /usr/doc directories, and policy was changed to not require the /usr/doc symlinks. debhelper was changed to stop adding postinst and postrm fragments to manage the links, and so most packages only needed a recompile to finish the transition. As a result, More than 250 bugs were filed, blockers of #322762. Most of these bugs, rot in peace in the BTS for years, some maintainers fixed them themselves, some other maintainers NMUed and others did QA uploads to deal with this issue. But it was not enough. It looks like at a certain point I decided we would not ship Etch with a transition from 2002 still in progress, so I did approximately 114 NMUs between the 11th and the 18th of July, fixing 152 bugs, 46 of which were not related to the /usr/doc transition. I also closed the ones affecting packages not in testing or unstable, unblocked the ones for packages that would not ship with etch (as exim3, that will be replaced by exim4), and updated the MIA info for several of the maintainers. At the same time, I revamped packaging a bit if I felt inspired to do so. Sure, things went wrong at bits and places, which I later fixed the best I could, but inmense love was poured in these NMUs. Several maintainers thanked me and the most NMU-unfriendly people didn't even complain. Lars Wirzenius pointed me to other related bugs, found by upgrading from testing to unstable with piuparts, and added blocking relationships with #322762 where needed. At this stage, less than 5 open bugs remain. I suspect that more packages once created this link and don t remove it on upgrade. I would need some help to find them. All this NMU fever happened while Joey was away on holidays, and when he returned, he confirmed my fears, I had DoSed his email and bandwidth: <joeyh> amaya: did you have to fix all the /usr/doc bugs while I was on vacation?
* joeyh watches his inbox and BW groan at the seams :-)
There is still several important and minor issues that we should deal with before Etch is released, Release Goals or not, just because we are Debian, and just because we care about this sort of things: Some of you will argue that these might not be transitions per se, just mass-bugfilings. I don t really care how you d rather call it. If you are looking for easy ways to help Debian, or to fill your lazy summer afternoons with, provide a patch today and CC: me. I intend to group these bugs either using user-tags or blocking bugs in the BTS. Help locating them and grouping them will also be appreciated. [Updated entry to reflect more accurate NMU and bug totals]

Erich Schubert: No, 16:9 screens are not larger.

Dear Mark, why do you think you can get a bit more on with a 16:9 screen? Doesn't that depend on the actual number of pixels and the panel size, instead of the ratio? Mathematically speaking, a 16:9 screen is not larger than a 4:3 screen. And I'm not aware of any manufacturing reasons that allow you to make larger 16:9 screens (or larger 15" 16:9 screens ;-)) than you can do with 4:3. That doesn't mean there aren't - e.g. backlight might be easier with wide screens. As for "organizing your apps on your screen more efficiently", I don't see any reason why this should be easier with 16:9. Sure, you can now probably put your favourite IM window besides your word processor at the same time; but is that actually better? I prefer keeping stuff on different virtual screens anyway; and actually on my 4:3 screen I could already do that pretty well (it has 135 dpi; I can just read a typical A4 paper at this resolution, and I could have my IM window next to that of course. Having a wide screen just makes web pages look bad. ;-) Oh, and my glasses are pretty close to 4:3 ;-) but with round corners.

22 July 2006

Uwe Hermann: ScatterChat - secure, anonymous, free, cross-platform Instant Messaging client

ScatterChat is a new cross-platform IM client announced by the Cult of the Dead Cow / Hacktivismo (during the HOPE conference, it seems). From the website:
ScatterChat is a HACKTIVIST WEAPON designed to allow non-technical human rights activists and political dissidents to communicate securely and anonymously while operating in hostile territory. It is also useful in corporate settings, or in other situations where privacy is desired. It is a secure instant messaging client (based upon the Gaim software) that provides end-to-end encryption, integrated onion-routing with Tor, secure file transfers, and easy-to-read documentation. Its security features include resiliency against partial compromise through perfect forward secrecy, immunity from replay attacks, and limited resistance to traffic analysis... all reinforced through a pro-actively secure design.
So the client is a "friendly-fork" of Gaim, it uses Tor to achieve anonymity, and for the crypto parts (secure messaging, secure file transfer) ScatterChat uses libgcrypt. It's a cross-platform application available for Linux, Windows; support for other OSes is planned (Mac OS X, others). You can always download the source code, of course, as it's free software. Actually, not quite. While ScatterChat itself is based on the GPL'd Gaim, it has to be GPL'd, too. However, the scatterchat-module package, which seems to contain the crypto-parts, is licensed under a custom "Hacktivismo Enhanced-Source Software License Agreement" (HESSLA) right now, which is so horribly long I didn't even bother reading it. However, the README says:
I am open to the possibility of re-licensing parts of this library to GPL, BSD, public domain, or some other license. I cannot make any promises, but I will try to accomodate reasonable requests.
I'm going to do just that, email the author and ask him nicely to change the license to some sane, well-known free software license. If you feel similar, please let the author know (hint, hint). Depending on what the HESSLA really says, it might prevent ScatterChat from entering Debian, for example. I haven't yet tried to use the application, but it sure looks like it has a lot of potential. It also seems do most security-related things right: Of course that's no guarantee that it's secure; I hope some crypto-gurus look over it soon. But at least they didn't make obvious stupid mistakes we've all seen in many other pieces of software. Anyways, I feel this is a real important project which will help lots of people (activists, political dissidents, normal people like me and you who value their privacy). Go check it out! (via Boing Boing)

21 July 2006

Dirk Eddelbuettel: Undeleting from ext3

Kudos to Paul Wise who suggested late last night to try magicrescue to recover an OpenOffice file with meeting notes I had mistakenly deleted from the laptop before I even got to editing these very notes, or backing them up. And it worked -- despite the dire warnings from the ext3 FAQ about the near impossibility of undeleting from ext3 partitions. But a few things worked in my favour here: OpenOffice files are zip files 'under the hood', and magicrescue knows how to deal with certain file formats via its collection of 'recipes' (which one can extend), and zip is among the shipped recipes. Also, I still had the 'ls -l' session in one konsole tab so I knew the exact file size I was looking for. And I wasn't in a hurry. So this morning, after magicrescue had faithfully restored 4479 files in over four hours, its companion magicsort then filtered these into a handful of directories, one of which was 'OpenDocument Text' -- which contained a few files, including two versions of the desired file as well as copies of the version from the previous meeting. Nice. And OpenOffice gladly opened the file. Lastly, it cetainly helped that I happened to have a lurking debian-devel irc session open where --- where Paul not only caught my remark, but almost immediately suggested to try magicrescue. So here goes a well-earned Thank You to Paul!

20 July 2006

Biella Coleman: Debian History

I have made it to South Africa and the official part of the Law and Society conference has come, sadly, to an end. It has been an amazing experience for reasons that deserve a lot more attention than I have right now so I will wait to write some about it when I have more time. But before I forget, Lars has been thoughtful enough to put the Debian History Roundtable Discussion on the Debian Wiki. I organized this roundtable at Debconf4 and while there is a good chunk of information from the discussion, there is a lot missing and perhaps even wrong, so please make changes and additions.

Evan Prodromou: 2 Thermidor CCXIV

I talked with Raymond King and Mark Dilley at RecentChangesCamp in February (uh... I mean Pluvi se) about their plans to develop Mark's excellent SwitchWiki wiki directory into something... more. I'm glad to see that WikiIndex is really picking up steam. It's becoming my first-stop for getting information on what's wiki, what's not, and who's doing what. The site uses MediaWiki, but the principles and community are very much rooted in the traditions of Ward's Wiki, MeatballWiki and CommunityWiki. I really hope this site keeps up it's momentum and growth. tags:

CC Salon in Montreal Tonight is the first Creative Commons Salon in Montreal. The get-together is at Caf l tranger, 680 Sainte-Catherine Ouest (at Alymer) at 19h30. More details on the Creative Commons Canada blog: http://creativecommons.ca/blog/?p=185 . Maj and I are trying to get a sitter for the event -- Amita June is starting to get grumpier and grumpier about going to sleep after 8PM. But I'll be there regardless. tags:

Great camping Website So, maybe I just haven't been camping a lot in other places outside Quebec in a while, but I'm extremely impressed with the quality of the S paq Web site. You can search the entire network for available campsites based on various criteria (size of tent vs. RV, for example), and then use a map-based interface to browse possible sites. The maps go down to the individual site level, and have popup descriptions of each and every site -- how much sun, how close to water, how private, etc. It's really nice. I have my quibbles -- we tend to do road-trip camping, where we'll stay in a different campground each night for a few days. It'd be nice to do all those reservations at once, but the site doesn't support that. And there are some search criteria I'd like to be able to specify (number of neighbors, access by car) that aren't possible. But as far as it goes, this is a real good site. tags:

Wikispam lockdown I've been having a real problem with Wikispam on my site lately -- several of my pages have nothing-to-sniff-at wp:PageRank values of 6 or 7, and I think that attracts a certain spammity crowd. I think that dealing with Wikispam is something most wiki sites do very well-- an active community is the best counter-measure against spam. And there are lots of good tools, like regexp filters, per-page locking, email and IM notification, and ip blocking that make it easier to maintain a site. But I don't have an active community working on this site -- it's pretty much just me. And WiLiKi, as beautiful and Scheme-y as it is, doesn't have many of the anti-spam tools that users of other wiki engines take for granted. I plan on building more anti-spam tools into the site, but for now I've just been locking the site up when I'm not writing something. It's not as wiki-ish, but it does keep my writing up more often. I'd feel pretty bad about it, but it looks like Alex locks up CommunityWiki for days at a time. tags:

Amazon man at the door Just got an order from Amazon in... full of CDs and books. When I used to live in my car (long story, there), I had my 100 favorite CDs in a box in the back. It was safe there in tons of cities -- wt:Chicago, wt:Saint Louis, wt:New York City, even wt:Monterrey and wt:Guanajuato. But I parked it about a block from It's Tops in San Francisco one night while visiting home, and one of my windows was smashed and the discs were taken. Devastating. Slowly but surely I've been re-stocking my music collection, but it's painful to buy the same album twice (and, yes, I know... I shoulda made backups! I do that now). Today's shipment contained a lot of stuff I re-bought: ''wp:The Last Waltz'', a bunch of wp:Neil Young (including the DVD of wp:Greendale), and one of my favorite albums ever, the eponymous first album from Lamb. Also in the box were a bunch of Lost paperbacks ("inspired by the hit series") and the hardback copy of Bad Twin, the mystery novel supposedly written by one of the people who died in the crash of Flight 815. Yeah, I know -- but I like the show, dangit. tags:

Best thing ever Vaguely reminiscent of the very fine Good or Bad? feature from Brunching Shuttlecocks, bestthing.info, by the enigmatic but talented xkcd, is a good way to waste a few minutes. tags:

John Goerzen: Am I being scammed?

So today my auction for the tc1100 tablet PC ended. The winning bidder:


I replied to the buyer's e-mail giving shipping prices to Nigeria and Malaysia, and restating my policy of shipping to only PayPal Verified Addresses.

So what do you all think? Is this a scam?

I was shocked at the amount of scams that sellers on eBay are exposed to these days. I've never seen this before, even just a few months ago when I sold my last item on eBay. But with this one, spammers and scammers are using the "ask seller a question" interface. One person tried to get me to use an eBay phishing clone site. Quite a few tried to get me to sell to them off eBay, to people in China, using a non-reputable billpay service. And there was just some generic spam.

So all that, plus the fact that they want me to ship to Nigeria, plus the fact that the person just registered on eBay today, is making me nervous.

So it seems odd, but I can't quite work out how somebody would actually defraud me here. Also, I'm interested in what I should do if it is a scam.

19 July 2006

Erich Schubert: Google and the semantic web

Worth reading: article on Googles Peter Norvig and Tim Berners-Lee over the Semantic Web. While Google is obviously right about "millions of web masters" who will have trouble adopting to these new standards - thats why we're writing software. The days when you were hand-writing HTML code will be over some day. Already now - as Google acknowledged - many people fail to write proper HTML. But HTML isn't becoming easier to write. In fact, it gets much more complex with different character encodings, new CSS versions, raised bars for layouting, more dynamic web pages, Ajax, ... More and more people won't write HTML themselves anymore, but use some software. People used to write bad HTML; now people use tools such as Wordpress which are at least expected to produce valid markup. They start using visual editors, which will eventually stop using tags such as <i /> and use the "more semantic" <em /> instead. Without actually being aware of that. And their blog software also does generate RSS for them. How many people have ever written RSS by hand? So it's mostly a matter of the tools we offer them; with better tools we can push the use of better ("semantic") formats which then make data reuseable for others as well. For example, tons of people hope that friendster, openbc, linkedin and all these will help them in one way or another to keep contact with some people, sell some products, find new jobs. What these web pages basically collect is FOAF data. (And, btw, if any of these web sites were true Web 2.0, they would actually export FOAF files via some API!) They have a UI people understand; now all they would need to do is share their data, and we'd have a large body of "semantic web ready" FOAF data. Similar things apply to other "semantic" formats. Think calendards. Ical is pretty much the standard and widely used. Almost noone uses web pages which are only readable by humans. The semantic web isn't dead or anything. It just takes some time to be widely adopted, but that was to be expected. And having tools to generate semantic data that are maybe even easier to use than non-semantic tools - after all, the computer should be able to assist you more with semantic data - is the key thing to success. I'm also looking forward to Semantic wikis such as IkeWiki, that try hard to make entering semantic data as easy as editing a non-semantic wiki page. In large wikis such as Wikipedia, making useful links is not as easy as typing [MagicWord], because you first have to look up the magic word. A semantic wiki can assist you by suggesting appropriate links based on the information you've already entered. (e.g. if you mark a page as biology, it won't suggest you it might be a computer part).

Simon Richter: Fighting collateral damage from spam

One of the biggest problems in fighting spam is that of false positives. I regularly have to scan my Junk folder for legitimate mail, which takes a great amount of my time, but otherwise I'd miss important stuff, like my provider telling me about a network outage, or a message from eBay. Now what I'd like to see is a mechanism to hand those people legitimately sending bulk emails a token which allows them to go through my spam filters. Obviously, everyone would get a different token. The interesting bit about this is less of a technical thing though: having a token could be interpreted as a prior business relationship, which is a requirement for sending business email in most jurisdictions.

Erich Schubert: live.com is slooooow

live.com, Microsoft's latest branding experiment (read: their new Passport+MSN+whatever) features a new version of their search engine. Some time ago they promised they'll be the leading search engine this year... It's unuseable. They've packed it with so much AJAX that it's so slow I can't really use it on my computer (which has 1.8 GHz). I'll remain a Google user. Without even looking at your results, just because I can't really use your fancy schmansy scrolling CPU-eating thingy. Some fun from March, Reuters (original article no longer available):
"What we're saying is that in six months' time we'll be more relevant in the U.S. market place than Google," said Neil Holloway, Microsoft president for Europe, Middle East and Africa.
More relevant with Vista users that is, probably. ;-) If you want to see an AJAX-using search engine which is useable and useful, try Exalead. They have thumbnails, clustering, and still a pretty nice interface.

Erich Schubert: nofollow followup.

Micah Dubinko blogs on rel="nofollow" being a failure. I have to agree that this doesn't really stop comment spammers currently. I still believe that it will help on the long run, since most blog software will now use it by default. And people have to upgrade from time to time due to the lastest PHP security issue... However, I would like Google or other search engines to offer some "spam submission". It would be best if they had a common submission server. Then we could use the moderation tools of our blogs to submit these bad URLs to Google, who in turn could take measures to strip them off their index (e.g. by moderating indexing for these URLs, reducing their pagerank, freezing their ranking for some weeks etc.) I'm of course aware of abuse possibilities (e.g. spam with your competitors URL); but most comment spam I've seen so far uses new sites anyway. I think you can detect these by charcteristical URLs, site contents, incoming links etc. As for myself, I've never enabled comments on my blog for the very reason that I'm not willing to moderate all that spam. In my guestbook (which is mostly to reduce the number of emails I get because of certain popular contents of my german web page; people will happily post in my guestbook instead of sending me an email now), I've recently enabled a very simple filter. It will just reject any entry which contains http:// anywhere. My users don't need that, and it has reduced spam to 0 again. And I don't care for the entries there anyway. ;-)

18 July 2006

Jordi Mallach: Seventy years of the Spanish Civil War and the Spanish Revolution

A few months ago I wrote about the 75th anniversary of the proclamation of the Second Spanish Republic which was celebrated throughout the state. That weekend I visited a fantastic exposition of Republican and Revolutionary war propaganda posters, in Segorbe.

Today, Spain remembers the beginning of the end. During the evening of the 17th of July and morning of the 18th, a group of generals of the Spanish regular army raised against the democratically elected left-wing government of the Republic. History says that the murdering of Calvo-Sotelo, a right-wing leader, was what finally provoked the conflict. It was no secret that the same right-wing and some elements in the army had been conspiring for weeks about an uprise. The only question was when, but the government was fooled by general Mola and didn't take really effective measures to prevent it.


Warning from sanitary authorities against venereal diseases Mola and Sanjurjo planned to start taking over official buildings and army quarters and quickly seize control of the major cities. During the first hours of their rebelion, they managed to take over most of the southern regions in Andalusia, Extremadura and parts of the Northwest, plus most of the islands and the Moroccan protectorate area. Meanwhile, the Republic did not manage to react quickly due to the weakness of the government, and in the first days of the crisis, the government changed a few times. Finally, the Republican parties decided that to defend the state they should give arms to the unions, and soon after many militia groups were getting organised in the cities, and columns sent off to liberate other towns.


Solidarity of Catalunya to the Basque front The insurrection was suffocated in Barcelona after some heavy fighting against the military in the Montju c castle; the Anarchists of the CNT grew strong in Catalunya and Arag n, and offered good resistance in those fronts. After the first days of the coupe d'etat, it was clear neither the legitimate government or the rebels calculated how things would go after the first days. The government was confident in being able to end the rebelion as they did four years before; the fascists thought they would have quickly brought down the government with a successful coup. But after the first week, the country was divided in two halves, and both sides of the conflict were keen on fighting, due to the big social fracture during the last months of the government. The Republic asked for help to the League of Nations, but the United Kingdom and France decided not to intervene, scared about the conflict trespassing the Spanish borders and becoming another bloody war in European fields. The only official external aid came from the USSR and the International Brigades, formed by volunteers of more than 50 nations. Some well-known personalities like Ernest Hemingway or George Orwell came to aid as well. Orwell wrote about his life-changing experience in a Barcelona immerse in the social revolution, where he joined the anti-stalinist socialist party POUM. Badly wounded in the neck, he left the front and went back to Barcelona, and witnessed the assault of the Telef nica by the communists against the anarchists, during the fets de maig, after which the POUM was declared illegal. Orwell captured his experiences in the frontline and Barcelona in his book Homage to Catalonia.


To defend Madrid is to defend Catalunya Franco and Mola, aided by the Northafrican troops and soon after by their fascist allies of Italy and Germany, didn't have big problems seizing the Basque Country and Asturies in the North, but not before making the town of Gernika disappear below the nazi Condor Legion bombing, in what would be a test for the massive aereal bombings of Word War II. The battle for Madrid was fierce, and the city wasn't occupied until the very last days of the war. The long defence of the capital made was immortalised in the famous phrase No pasar n.


Madrid's No pasar n During the war, anarchist groups controlling fields and towns in Arag n and Catalunya managed to bring a Social Revolution to the area. The people collectivised the land and industries, administered by local assemblies. This experience is regarded as the time when Libertarian Communism has been successful. The experience ended dramatically when the anarchists were treasoned and blocked by the communists, and eventually defeated by Franco at the front.


Each bullet for a target After the first and a half years, the fronts had stabilised in Madrid and the East of Andalusia, until early in 1939, Barcelona fell in Franco's hands, after the bloody Batalla de l'Ebre, being followed by Girona and the rest of Catalunya. The fate of the democratic state was clear. Two months later, Madrid fell and Val ncia and the small area still under Republican control surrended.


Robert Capa's Muerte de un miliciano Franco declared a totalitarian regime to, according to the fascists, reconcile the two Spains. In the first five years of the regime, up to 100.000 were executed in the franquist repression, including the Catalan president, Llu s Companys and many intellectuals. The dictatorship continued executing people until two months before Franco's death, 36 years later. Hundreds of thousands also had to exile in M xico, France and other destinations, leaving Spain in ashes, road gutters full of scattered bodies and the population facing famine. The cultural elite left the country, making the state's clock go back at least a decade. Their reconciliation really meant humiliation and repression. Many people were also murdered during the war behind republican and rebel lines, but the genocide of the aftermath had was unmatchable.


The Republic promoted education among the troups It is a bit late to restore the dignity of the victims, but not too late. Some associations have been fighting since the end of Franco's regime to get some kind of public recognition for their suffering, for their priceless fight for the legal and democratically elected Republic, for the people who didn't make it.


Excellent anarchist poster rejecting the politisation
of children by any of the three loyal groups Other people reject these efforts banning them of "revisionism". Not too surprisingly, these are the sons or grandsons of the people who won the war. The current government is about to pass a Historic Memory law which aims to give recognition to all these people who gave their lives for an ideal and freedom. Unfortunately, due to pressures from the right, it is probable that the text will be ammended to make it more acceptable by them. I fear it will end up not pleasing the victims at all. I have a passion for Spanish Civil War related matters, and in the last years I tried to use any opportunity to listen to my Catalan grandmother talk about war affairs in Barcelona, and my grandfather, from a town in the middle of the Republican side of the Teruel front, but born in a very catholic family, about how the war went on in Vall and the nearby mountains.


From the defensive No pasar n to the encouraging Pasaremos! I know my grandfather only told me the less compromising stories, like how he was sent to dig refuges until he was 16 and apt to fight in the Front, or how he was put in charge of hiding the church's valuable relics in a few barns. He never told me about how life was after the war in the small town. It is dramatic to see that all the people who were old enough to have a sense of what was going on at the time are so old that these unvaluable memories and stories will be mostly gone in ten years. (Most of the pictures are taken from the Sociedad Ben fica de Historiadores Aficionados y Creadores' website, which has a huge documented catalog)
Ben Armstrong: XPilot change of upstream growing pains

XPilot development has changed hands over the past several years. While the original website at www.xpilot.org continues to be run by the original developers, XPilot-NG (xpilot.sf.net) is where all of the new development has been happening. But xpilot.org still performs an important function for the user community: they run the meta servers1 that list all public xpilot servers around the world. Recently, we (the XPilot-NG developers on #xpilot at irc.freenode.net) noticed quite a number of uncontactable servers popping up on the meta servers. This is annoying, to say the least. Users don’t know they can’t connect until they’ve tried (unless they’ve bothered to try pinging the server first) and besides which, having all those “junk” servers in the list makes it harder to locate contactable servers. Now, naturally, we wanted to know where all of those servers were coming from, and why now, at this particular time? I knew my Debian package (and presumably any derivatives) do not report to the metaserver by default. Any admin starting an XPilot server would have to explicitly configure it to do so, so the incidence of uncontactable Debian XPilot-NG servers should remain relatively low and have a constant growth rate. Then I found the Fedora package, and started poking around inside. After a shallow review of the package, I concluded there was a good chance it was the culprit2, especially since it recently (FC5) had an init script added. Such a bug, coupled with the relatively recent release of FC5, would account for the sudden spike in number of permanently running non-contactable XPilot-NG servers. Bingo! I found some helpful folks at #fedora-games at irc.freenode.net, including the XPilot NG maintainer, which led to filing this bug. I subsequently invited the maintainer over to #xpilot and had a nice time introducing him to the other upstream devs and chatting about our current issues. Ultimately, we know we need to fix the problem at the metas, but in the meantime, I am pleased to have established contact with my counterpart in the Fedora project, expanding the diminishingly small XPilot developer community by one.

1 They deliberately never released any source code for those metas to try to keep the user community unified at the centralized servers. While I see the reasoning behind the decision, given the problems we’re facing now, it’s clear the XPilot community would be better off with meta server source that is actively being maintained.

2 Admittedly two problems with the +reportMeta option upstream set us up for this problem. First, counterintuitively, +reportMeta disables reporting to the metaserver (following the rule ”+” negates the meaning of an option starting with ”-”). Second, -reportMeta is a stupid default. Most people starting servers are behind firewalls these days, so unless they consciously decide to make their server public, making the corresponding adjustments to their firewall, the option should not be set (not to mention the security implications of making a server public by default).

Ross Burton: EDS and Berkeley DB

Back in the good old days of Evolution 0.9, Evolution depended on Berkeley DB being installed. At the time Berkerley DB ("BDB") was undergoing a some major changes so it wasn't uncommon to upgrade your distribution and find that the new BDB can't read your addressbook. This was solved by Evolution embedding a copy of BDB into the source code. and statically linking it into the relevant addressbook backend. Problem solved. Over time Evolution was refactored, split into Evolution and Evolution Data Server, and so on. Then BDB was statically linked into not only the addressbook backend but also libedataserver, which contains some generic caches based on BDB. Now BDB isn't exactly a small library (it adds ~600K to a .so), so the second static linking started to irritate people. Not only does EDS have a private copy of a library, meaning extra work when BDB has security bugs, but there is 1.2M of code that could be shared. This led to various distributions patching EDS to use a system copy of BDB, a patch that has finally made it upstream, but not everyone is using it: by default EDS uses it's private copy. Now fast-forward to today. I did a full build of EDS from CVS using the system BDB (it's also a lot faster to build that way) and hit build failures from code demanding the static BDB to be built. Fixing these was trivial, but when I checked in the patch it worked fine... I investigated and discovered that BDB is now used in four places inside EDS: Now, BDB is approximately 600K when statically linked, and a typical EDS build statically links it four times. The server process will load both backends and both libraries, so it contains all four copies of BDB at once. This is getting silly. Please, all packagers, if you support multiple versions of BDB in your distribution, use --with-libdb=/usr to dynamically link to BDB. As a fallback I'm about to create a patch that installed the private BDB into a private library directory, to avoid all of this static linking. NP: Neighbour Radio, Last.fm (via Last Exit)

17 July 2006

David Welton: Oregon - OSCON

After more than three years away from home, we're going on vacation to Oregon this summer. Luckily, that will coincide with OSCON in Portland, so hopefully it will be possible to meet some people there that I ordinarly wouldn't get to see. Write me email if you'd like to get together for a beer or something! The rest of the time, we'll be in Eugene, or travelling around the state.

MJ Ray: HOWTO not melt - Summary

The main series has now finished. I've a few more emails to answer yet and a few more useful links that I've been sent. Someone suggested summarising the series and I think that's a good idea: 1. Switch off instead; 2. Understand your building; 3. Section your building; 4. Vent at night; 5. Close against the sun; 6. Use plants and fans; 7. Water the pavement and hang out the washing; 8. Don't use air-con, but if you must, use it wisely. If you can read French and would like to learn more, try Fra cheur sans clim' by Salomon and Aubert from Terre Vivante. Hope you enjoyed it and good luck not melting this summer!

16 July 2006

Daniel Burrows: Meeting the Wisconsin state bird in Washington

In Which our Intrepid Heroes Scale (or trudge along) Mountains While Defending Their Precious Bodily Fluids From The Local Fauna.

This is a continuation of my previous post about how I spent my holiday weekend. Yes, it took my a while to get around to it, why do you ask?

Day 1

On our second day in Leavenworth, we decided to hike up to Stuart Lake. This is a nine-mile round trip up the side of a mountain, culminating at an alpine lake; we figured it would make a nice site for a picnic.

The trip up was fairly smooth for about two-thirds of the way, at which point we discovered what we had forgotten in our preparations. Somehow, the fact that mosquitos can live on a mountain had escaped both of us, and we'd left the bug repellant at home!

The next couple hours were a nightmare of swatting, itching, and trying to move fast enough to leave the horde of bloodsuckers behind. We did make it to the lake, but only stayed long enough to take a picture and gobble down a sandwich while doing the Mosquito Dance (where you run in circles while flailing one arm wildly to repel the little nasties). As soon as we were done, we conceded the field and fled back down the mountain to less infested areas.

We got back at about 5, ate the remaining sandwich for dinner, and nursed our wounds until we fell asleep. The whole thing wasn't so bad for me, but Kate seems to be particularly sensitive to mosquitos, and by the time we made it back her whole arm looked like one big bite.

Erich Schubert: On programming contests (ACM ICPC etc.)

Bart Massey and Mike Vanier talk about programming contests such as the ACM International Collegiate Programming Competition. Well, since I'm being told that I love ranting, I have to join this one. ;-) I never participated in a contest except the Bundeswettbewerb Informatik back in (pre-university) school. In my opinion that contest was quite different for a number of reasons: most of the participants didn't have any IT classes at school. And noone "trained" for that contest. Also the contest isn't a speed contest, but you have a couple of months to solve a number of problems that most of us would find rather easy - for pupils aged 15-18 with no real CS classes they aren't that easy. Even in the later rounds, time isn't the main constriction - you have several weeks - and the programs are also judged by their code quality, documentation and design. I think you were allowed to participate in teams during the first and maybe second round. A friend of mine pointed out the ACM chellege to me; but we never really managed to form a team since everybody was too busy. We never actually did a training session (though I myself solved a couple of the valladoloid online judge problems), and we didn't submit our participitation. Though we would have automatically won our local contest, since I'm not aware of any teams by our universities here (despite them being top-ranked universities). In general, Germany isn't very much involved in this contest, despite being an "international" contest. This has various reasons. On one hand, CS teaching in germany is not much about just writing code. You'll of course learn the basics, but even when they've finished their degree, most will be really slow in writing code. Instead, the focus is on modeling and the theoretical background. In my opinion, that is very good. You'll always be able to improve your "basic" code writing skills later; that is mostly experience and routine. But you won't be learning much theoretical background in your job later on. Having worked on a number of the old, archived, training problem sets, I'm not convinced that this contest makes much sense. To succeed with the problem sets you need to be able to I agree with the others that I don't think team-play is of much value in this contest; nor will you be doing much creative work. In my opinion it's all about reducing the given problem to one of the known problems (e.g. longest common subsequence, shortest path, maximum flow), then adopting an algorithm to it. I'd call that reproductive work. In my opinion, they're rather boring. Basically you're expected to solve them using a certain algorithm. You aren't judged by good or smart solutions either. Just by speed. The (high-school) programming contest mentioned earlier was more interesting. For example there was the task of navigating a robot on a factory floor without any state information, and only a limited view. The robot was not allowed to keep any information. Such as "I need to go out of this dead end" or "that is a dead end". It would easily walk into a path just to notice after a few steps (it had a limited view!) that this is a dead end, then try to walk out - just to walk in again, having forgotten that it's a dead end. You of course can't judge solutions without inspecting the code. Smart programmers found a few ways to "cheat" here - and got extra credit here. For example one robot, when noticing that it's in a dead end it might forget, would step up to the wall. And whenever it was close to a wall, it would follow it, and thus walk out of the dead end. Some heuristics making it step away from the wall again made it much more successful than others. Another "cheat" involved calculating "remaining steps allowed - distance to destination mod 2". It then could be programmed with two alternating behaviours and switch between them by just not moving for one turn. I don't think there is any room for such great ideas in the ACM contest.

Next.

Previous.