Search Results: "ron"

6 November 2007

Manoj Srivastava: Manoj: Continuous Automated Build and Integration Environment

One of the things I have been tasked to do in my current assignment is to create a dashboard of the status of various software components created by different contractors (participating companies) in the program. These software components are built by different development groups, utilizing unlike toolsets, languages and tools though I was able to get an agreement on the VCS (subversion yuck). Specifically, one should be able to tell which components pass pre-build checks, compile, can be installed, and pass unit and functional tests. There should be nightly builds, as well as builds whenever someone checks in code on the release branches. And, of course, the dashboard should be HTTP accessible, and be bright and, of course, shiny. My requirements were that since the whole project is not Java, there should be no dependencies on maven or ant or eclipse projects (or make, for that matter); that it should be able to do builds on multiple machines (license constraints restrict some software to Solaris or Windows), not suck up too much time from my real job (this is a service, if it is working well, you get no credit, if it fails, you are on the hot seat). And it should be something I can easily debug, so no esoteric languages (APL, haskell and Python :P) So, using continuous integration as a google search term, I found the comparison matrix at Damage Control I looked at anthill, and cruisecontrol, and the major drawback people seemed to think it had was that configuration was done by editing an XML file, as opposed to a (by some accounts, buggy) UI is not much of a factor for me. (See this). I also like the fact that it seems easier to plug in other components. I am uncomfortable with free software that has a commercial sibling; we have been burned once by UML software with those characteristics. Cruisecontrol, Damagecontrol, Tinderbox1 & tinderbox2, Continuum, and Sin match. I tried to see the demo versions; Sin s link led me to a site selling Myrtle Beach condo s, never a good sign. Continuum and Damagecontrol were currently down, so I could not do an evaluation. So, here are the ones I could get to with working demo pages: http://cclive.thoughtworks.com/ and http://tinderbox.mozilla.org/showbuilds.cgi?tree=SeaMonkey Cruisecontrol takes full control, checking things out of source control; and running the tests; which implies that all the software does build and run on the same machine this is not the case for me. Also, CC needs to publish the results/logs in XML; which seems to be a good fit for the java world; but might be a constraint for my use case. I like the tinderbox dashboard better, based on the information presented; but that is not a major issue. It also might be better suited for a distributed, open source development model; cruisecontrol seems slightly more centralized more on this below. cruisecontrol is certainly more mature; and we have some experience with it. Tinderbox has a client/server model, and communicates via EMAIL to a number of machines where the actual build/testing is done. This seems good. Then there is flamebox nice dashboard, derivative of tinderbox2; and seems pretty simple (perhaps too simple); and easily modifiable. However, none of these seemed right. There was too much of an assumption of a build and test model and few of them seemed to be a good fit for a distributed, Grid-based software development; so I continued looking. Cabie screen shot. I finally decided CABIE
Continuous Automated Build and Integration Environment. Cabie is a multi-platform, multi-cm client/server based application providing both command line and web-based access to real time build monitoring and execution information. Cabie builds jobs based upon configuration information stored in MySQL and will support virtually any build that can be called from the command line. Cabie provides a centralized collection point for all builds providing web based dynamic access, the collector is SQL based and provides information for all projects under Cabie s control. Cabie can be integrated with bug tracking systems and test systems with some effort depending on the complexity of those systems. With the idea in mind that most companies create build systems from the ground up, Cabie was designed to not have to re-write scripted builds but instead to integrate existing build scripts into a smart collector. Cabie provides rapid email notification and RSS integration to quickly handle build issues. Cabie provides the ability to run builds in parallel, series, to poll jobs or to allow the use of scripted nightly builds. Cabie is perfect for agile development in an environment that requires multiple languages and tools. Cabie supports Perforce, Subversion and CVS. The use of a backend broker allows anyone with perl skills to write support for additional CM systems.
The nice people at Yo Linux have provided a Tutorial for the process. I did have to make some changes to get things working (mostly in line with the changes recommended in the tutorial, but not exactly the same. I have sent the patches upstream, but upstream is not sure how much of it they can use, since there has been major progress since the last release. The upstream is nice and responsive, and have added support in unreleased versions for using virtual machines to run the builds in (they use that to do the solaris/windows builds), improved the web interface using (shudder) PHP, and and all kinds of neat stuff.

5 November 2007

Daniel Burrows: Building rails

In the 1860s, in the middle of one of the largest wars America has ever been involved in, a 690-mile railroad was built in a period of seven to nine years (depending on how you count), a rate of about five days per mile of track. Now, it's certainly true that this was accomplished through labor practices that were, by today's standards, more than a little bit questionable. However, I still am amazed that it's apparently going to take us twenty years to construct fifty miles of track in the Seattle area. By my count, that's a hundred and forty six days per mile of track. And I haven't even mentioned the harsh environmental conditions the transcontinental line faced, which a line in the Seattle metro area by and large does not.

I haven't decided how or whether to vote in the election tomorrow, but the timescale they're projecting is ... astonishing.

Gunnar Wolf: Mini-post-mortem of a failed mini-Debconf

Over one year ago, still at DebConf 6, the Latin American Debian people (and by people I mean just interested people, regardless of whether they were/are official DDs or not) held a BoF session. One of the ideas we discussed there was that, in order to increase Debian presence in our region (which is by no means small - Let alone the geographical aspects, I'm guessing we are about 350 million people, roughly split in half between [officially] Spanish- and Portuguese- speaking countries). Yet, this is an area with very little involvement in Debian in particular, and with Free Software in general.One of our first issues seems to be language - Just by its scale and economic importance, we cannot even put in the same scale Brazil and the Spanish-speaking countries... So I'll focus on Spanish-speaking Latin America, as (I recall) we did in that session.So, we agree: We need more local involvement in each of our communities. And, so far, we have seen quite relevant results. The number of people directly involved in Debian in Argentina, Chile, Per , Colombia, Venezuela, El Salvador and Mexico (excuse me if I forget you in another country!) has notably risen since I brought this topic up, together with Christian Perrier, back in DebConf5, Helsinki. An undeniable fact is that distances in our continent, however, are huge. In the 2006 BoF, we agreed we should promote regional meetings, that would serve both for working focused on Debian topics (i.e. hack sessions, as we do in DebConf) and for spreading our work to the local population, to help them see that it is not needed to be super-skilled or anything like that to contribute to a real, important and large Free Software project such as ours. Of course, taking into account the distances in the continent, we thought it would be sensible to split it in two - and to try and hold regional mini-debconfs - One for the Northern half (i.e. Per , Ecuador, Colombia, Venezuela, Central America, Cuba and Mexico), and one for the Southern half (Bolivia, Chile, Argentina, Uruguay, Paraguay). And, for logistical reasons mainly, I strongly advocated having our first Northern meeting in Panam . Why Panam ? Because it is a place cheap and easy to get to. They have a very important international airport, connecting to most if not all countries in the region, and -as they have risen as a business center- have good connectivity. Visa is required for many of the interested countries, but trivial to get (as opposed to what happened here in Mexico :-( ). Of course, other countries also looked interesting (there was some argument pushing Venezuela, but in the end, we all conceded it would be in Panam .I have to strongly thank Guillermo Garc a - He is not (yet? :) I hope he still wants to get involved with this bunch of people) in Debian in any way, but after I contacted him, he agreed to start looking for a way to get us the right facilities in Panam . He coordinated with a team which did most of the organization - A very nice web site is still available so you can look at their work - Quite a good job, I must add.They contacted Universidad Tecnol gica de Panam , started talking with several potential sponsors, got information regarding hotels for us... But in the end, it flopped. Why? Because, although many of us were originally interested, in the end very few people (only three, none of them officially a Debian Developer, according to their last press release) confirmed their intention to attend.Which brings me again to the question: Why?First and foremost, I think it was lack of involvement. For one reason or another, all of the people that in the beginning pushed for this miniDebConf ended up busy doing other stuff, and didn't get at all involved in organization. It would have been a great present from our Panaman friends, yes, but quite unfair. And, of course, with no Debian people involved in organizing it, we got an chicken-and-eggesque situation... Where it didn't grab the attention of other Debian people.Second, what they offered us was quite different to what we intended in the first place - At least, to what I imagined. On my first messages both to debian-devel-spanish and to Guillermo, I tried to get something close to what we had in mind: Something as informal and as intimate as it could be. My original request to Guillermo was just to get us a room where we could hack and talk, and probably sleep with sleeping bags.Of course, I can perfectly imagine that when he requested the space to the university, on one hand, they didn't feel at ease having International Guests (with capital I and G - Very important for most Latin American universities!) sleeping on the floor. And, on the other hand, they would love to be able to show us around! Having an international project focus on a university in a non-technologically-well-known little country is quite something to show off!Anyway... What happened? I was among the instigators, but Real Life called me away (I've been mostly inactive in Debian since September! :-( ). The miniconf was scheduled for November 14-17. I also insisted originally on having the miniconf on a long weekend (say, Friday through Sunday), as -being a miniconf and not the Real Deal- it'd be much easier for most of us to rob one day off work than a full week. In the end, this was the most important point for my decision not to join: I cannot afford more time off my work, not at this time of year. About the other involved people? I do not want to speak for any other people.In the end, sadly, Guillermo had to inform us they cancelled - No, not postponed, but definitively cancelled. Why? Because -and I have to agree- next year we will have DebConf in Argentina... And many people in the region will focus our time and money on getting there. Ok, making this whole story short: I'm very, very ashamed and sorry, with you personally, Guillermo, and with your whole team. And I hope we can resurrect this idea - be it in Venezuela (as it was suggested once) or elsewhere.

Gerfried Fuchs: 1408, Chuck & Larry, Lissi

Some people say, write it right ahead or you won't write it at all. I fear the latter, thus I'm trying to catch up with things that happend in the last months. Not that I didn't mention some aspects, but I haven't written about some others and want to keep them at least for myself in good rememberance. There were some movies I went to, and some of them I totally enjoyed. First thing was "1408"—a horror shocker with John Cusack, and I really enjoyed it. I'm not a big fan of splatter horror, and this wasn't, it's a pretty nice done psycho shocker. If you still have the chance and like the genre, go and watch it. :) Then there was "I Now Pronounce You Chuck and Larry" which I watched even twice, with both my best friends. One would expect it being more cliche, more shallow—but it isn't. It really astonished me a fair bit how well it tackles the topic, and as an additional benefit the soundtrack of the movie is yet another must-have. Which brings me to "Lissi und der wilde Kaiser". Don't. Just... don't. This one is cliche, this one is shallow. Some small jokes, weakly connected to some story... Bully, you did way better before. Alright, first round of catching up, more to come. After all I'm syndicated on some Free Software related planets, and people might be interested in what's getting done in those parts, too. Not that I would do things in secret...

Eddy Petrișor: (debian) work and the silence

I've been really busy lately in RL and Debian work took the hit.

Some news:

Uwe Hermann: Recent LinuxBIOS progress

LinuxBIOS ROM Chip Logo Since the "World's First Motherboard Using LinuxBIOS Released" hype at the beginning of this year (which was incorrect btw; it was not the first supported desktop board, there were many others before), LinuxBIOS hasn't been in the news very much. That doesn't mean that there was no progress, however. We've been working hard behind the scenes to improve the LinuxBIOS code, add support for new chipsets and boards, and advance the upcoming next-generation LinuxBIOSv3 version which will brings lots of great improvements in various areas. Here's a random collection of stuff that happened in the last few months. New chipsets: New mainboards: Note that not all of these may be 100% supported, some may still be work in progress with some TODO items left... Check the LinuxBIOS wiki or ask on the mailing list for details. The future Most work will probably go into LinuxBIOSv3 in the future, in order to make it suitable for productive use.
Of course, work on new chipsets and boards will continue, too. For example the VIA CN700 chipset (plus Jetway J7F2WE board using it) is being worked on right now, probably also several others I don't know about. Call for board testers If you're interesting in trying out LinuxBIOS, please check the list of supported motherboards. If your board is not listed there, but the chipset is already supported we can probably add support for your board relatively easy with some testing help from you. Please contact us on IRC or preferrably on the mailing list if you want to help get your board supported! An (incomplete) list of good candidate boards for future support is available in the wiki. Thanks! We're very grateful for the many contributors who have helped us with testing and fixing existing code, or who even contributed code for new chipsets and motherboards. Thanks a lot! Many thanks especially to all hardware vendors who have been supporting us or even actively contributed by submitting code for their chipsets or boards (recently or in the past), including AMD, SiS, VIA, MSI, Tyan, Artec Group, and many others. Your efforts are very appreciated. Thanks!

Martin F. Krafft: How to ruin music, German-style

Solar Project are a German progressive band. I like most of their music, but they ruin it on almost every song by opening their mouths. The problem is not that they can't sing, the problem is that they sing ein English. Even zough zey doo not h ve i Dsch rm n ccent, they still can't pronunce their words, usually stressing the wrong syllables or resting too long on a vowel. For instance, they love the word "animals," but they always pronunce it aa-niiii-mals. As a result, I tend to think I am listening to some sort of "Learning English Special, First-Year Edition for German Folk Singers" CD, rather than progressive rock. What a shame. When The Beatles sing "O komm doch, komm zu mir" to the tune of "I Want to Hold Your Hand", I get the chills; when Peter Gabriel sings "Eindringling" instead of "Intruder", I turn off the stereo. But those experimented with their curiosity and translated their originals into German, which is applaudable even if horrific; well, it's "art", right? Solar Project seem to think English is so hip that they don't even bother with German. That's not uncommon either, many German bands sing English, but none have rubbed me so badly as Solar Project has. NP: Solar Project: Chromagnitude

Manoj Srivastava: Manoj: Filtering accuracy: Hard numbers

I have often posted on the accuracy of my mail filtering mechanisms on the mailing lists (I have not had a false positive in years, and I stash all discards/rejects locally, and do spot checks frequently; and I went through 6 months of exhaustive checks when I put this system in place). False negatives are down to about 3-4 a month (0.019%). Yes, that is right: I am claiming that my classification correctness record is 99.92 (99.98% accuracy for messages my classifiers are sure about). Incorrectly classified unsure ham is about 3-4(0.019%) a month; incorrectly classified unsure Spam is roughly the same, perhaps a little higher. Adding these to the incorrect classification, my best estimate of not confidently classified mail is 0.076%, based on the last 60 days of data (which is what gets you the 99.92%). I get unsure/retrain messages at the rate of about 20 a day (about 3.2% of non-spam email) about 2/3 rds of which are classified correctly; but either SA and crm114 disagree, or crm114 is unsure. So I have to look at about 20 messages a day to see if a ham message slipped in there; and train my filters based on these; and the process is highly automated (just uses my brain as a classifier). The mail statistics can be seen on my mail server. Oh, my filtering front end also switches between reject/discard and turns grey listing on and off based on whether or not the mail is coming from mailing lists/newsletters I have authorized; mimedefang-filter However, all these numbers are manually gathered, and I still have not gotten around to automating my setup s overall accuracy, but now I have some figures on one of the two classifies in my system. Here is the data from CRM114. I ll update the numbers below via cron. First, some context: when training CRM114 using the mailtrainer command, one can specify to leave out a certain percentage of the training set in the learn phase, and run a second pass over the mails so skipped to test the accuracy of the training. The way you do this is by specifying a regular expression to match the file names. Since my training set has message numbers, it was simple to use the least significant two digits as a regexp; but I did not like the idea of always leaving out the same messages. So I now generate two sets of numbers for every training run, and leave out messages with those two trailing digits, in effect reserving 2% of all mails for the accuracy run. An interesting thing to note is the assymetry in the accuracy: CRM114 has never identified a Spam message incorrectly. This is because the training mechanism is skewed towards letting a few spam messages slip through, rather than let a good message slip into the spam folder. I like that. So, here are the accuracy numbers for CRM114; adding in Spamassassin into the mix only improves the numbers. Also, I have always felt that a freshly learned css file is somewhat brittle in the sense that if one trains an unsure message, and then tried to TUNE (Train Until No Errors) the css file, a large number of runs through the training set are needed until the thing stabilizes. So it is as if the learning done initially was minimalistic, and adding the information for the new unsure message required all kinds of tweaking. After a while TOEing (Training on Errors) and TUNEing, this brittleness seems to get hammered out of the CSS files. I also expect to see accuracy rise as the css files get less brittle The table below starts with data from a newly minted .css file.
Accuracy number and validation regexp
Date Corpus Ham Spam Overall Validation
  Size Count Correct Accuracy Count Correct Accuracy Count Correct Accuracy Regexp
Wed Oct 31 10:22:23 UTC 2007 43319 492 482 97.967480 374 374 100.000000 866 856 98.845270 [1][6][_][_] [0][3][_][_]
Wed Oct 31 17:32:44 UTC 2007 43330 490 482 98.367350 378 378 100.000000 868 860 99.078340 [3][7][_][_] [2][3][_][_]
Thu Nov 1 03:01:35 UTC 2007 43334 491 483 98.370670 375 375 100.000000 866 858 99.076210 [2][0][_][_] [7][9][_][_]
Thu Nov 1 13:47:55 UTC 2007 43345 492 482 97.967480 376 376 100.000000 868 858 98.847930 [1][2][_][_] [0][2][_][_]
Sat Nov 3 18:27:00 UTC 2007 43390 490 480 97.959180 379 379 100.000000 869 859 98.849250 [4][1][_][_] [6][4][_][_]
Sat Nov 3 22:38:12 UTC 2007 43394 491 482 98.167010 375 375 100.000000 866 857 98.960740 [3][1][_][_] [7][8][_][_]
Sun Nov 4 05:49:45 UTC 2007 43400 490 483 98.571430 377 377 100.000000 867 860 99.192620 [4][6][_][_] [6][8][_][_]
Sun Nov 4 13:35:15 UTC 2007 43409 490 485 98.979590 377 377 100.000000 867 862 99.423300 [3][7][_][_] [7][9][_][_]
Sun Nov 4 19:22:02 UTC 2007 43421 490 486 99.183670 379 379 100.000000 869 865 99.539700 [7][2][_][_] [9][4][_][_]
Mon Nov 5 05:47:45 UTC 2007 43423 490 489 99.795920 378 378 100.000000 868 867 99.884790 [4][0][_][_] [8][3][_][_]
As you can see, the accuracy numbers are trending up, and already are nearly up to the values observed on my production system.

Kartik Mistry: GreenMirchi-IceCream-Meet

* On Saturday night, while watching some horror movie, I got SMS of Anurag (and Pradeepto already invited me/us on IRC!) that we are meeting Kishore tomorrow. Wanna come? It was undecided until 10:30 am, and suddenly, I took bath. Camera was ready. And, I reached and found dudes after some try. Chicken Salad Kishor looking for nice pose of outsiders * It was ‘Pizzeteria’ in front of ‘Hotel Ambassador’. Good Pizza. Roshan and me were veggie, others (Kishore, Anurag, Pradeepto) were only non-veggie! And, we talked lots of things. Mostly about upcoming events like Foss.in and Feb’s Freed.in. * We then walked to Chopati for having ‘Green Mirchi Ice Cream’, Kishore discovered this during his early visit to Mumbai and we were not knowing this wonderful stuff even being Mumbaikars! The Dudes Bachelorr's * Again, we had nice discussion and nice photography on ‘Pradeepto’ ;) And then ‘Orange Ginger’ and then ‘Orange Juice’. Kishore, we will love to meet you again :P

4 November 2007

Bernd Zeimetz: mod_wsgi 1.2 + 2.0~c1

mod_wsgi 1.2 + 2.0~c1 We had two mod_wsgi uploads a few days ago:

Marc 'HE' Brockschmidt: Still not campaigning for DPL

In my first post about my current problems with Debian, I noticed that there doesn't seem to be a common vision of Debian's future. My last post was about Debian's current state of moving from stable release to stable release without actual aims.

Today I would like to rant about our lack of enthusiasm. Could you name the biggest new feature of Debian Etch? I think the graphical installer is very cool, it made the installation look a lot friendlier and made translations to languages not based on the Latin alphabet easier. But what else happened in Etch? We added SecureApt, which might be cool if you are a hardcore hacker, but leaves most people bored. The same is true for using UTF8 for new installations and the addition of udev to the default install. If you don't know where I got this impressive list of thing - look at the Debian Wiki.

Most of the things listed on that page miss the bling we see in other distributions. Ubuntu 7.10 introduced Compiz bling while Fedora 7 had full NetworkManager support and tried to "just work" [tm]. Yeah, Debian isn't that far away from such things, whenever we release, such things are also picked up. But somehow it doesn't look like people would get out and party because we include the newest and coolest feature - no, Debian Developers prefer to discuss such things as the default MTA.

Of course, we need to discuss the default MTA - and exim4 might not be perfect for the job - but we should also start to think about advertising the features that impress non-geeks, so that we can go out and say "Hey, lenny came out and now we have a full dependency based init system and a smaller MTA and our kernel is now completely free of binary blobs" to our geek friends, while our non-geek friends can hear about the new easy-to-use and beautiful desktop environments and configuration applications that allow them to just install and use their Debian, without moving to a command line once.

We are half-way there. Debian is cool. Debian becomes better every day (*cough* please look away from the RC bug graph, thanks). We should start telling people about it and have fun doing so.

MJ Ray: Dear Blogger - the truth about your CAPTCHA

Dear Blogger, Your CAPTCHA (word verification or whatever) doesn't test whether someone is spamming. It tests whether someone has good eyesight, hearing, literacy, numeracy or browser-configuration, which is correlated in one way (few spambots include captcha-crackers yet, but there are some and they already have an 80% success rate IIRC) but it is not strongly correlated for humans (are blind people more likely to spam? I doubt it) and now some spammers are using porno-trojans to get humans to crack the eyetests for them - see http://www.schneier.com/blog/archives/2007/11/spammers_using.html http://news.bbc.co.uk/1/hi/technology/7067962.stm I block spam by premoderating all comments (they're well over 95% spam), but that does mean you need to check your site dashboard a lot to avoid cooling discussions too much. Other anti-spam tactics include OpenID, URL blacklists and so on - I don't use them because I've not added support for them to my site yet. I suspect Blogger.com users can't use them because Google hasn't added support for them. They've bought captcha's false sense of security. http://www.w3.org/TR/turingtest#security As for encouraging non-spam comments, I'll generally defer to this top 10 from Darren Rowse: http://www.problogger.net/archives/2006/10/12/10-techniques-to-get-more-comments-on-your-blog/ On my sites, I find that inviting questions doesn't make much difference, asking questions has limited use because readers are suffering from "question-fatigue" these days and I have difficulty appearing to be humble or gracious (people often read it as sarcasm! Hopefully that's just my audience), but the rest of the techniques seem to work for me and I use them when I can (not all of the sites I write are under my full control). Please let me know if you see other successful ways to reduce spam or encourage good comments. Hope that helps, MJR/slef

Andrew Pollock: [life] Solar power for Cloncurry

It's exciting to read that Cloncurry is going to get a solar power generation plant that sounds something similar to the honking great big one in Spain. All for only $7 million. Apparently the Spanish one cost 1,200 million, which by my calculations is something obscene like $1.8 billion. The Spanish one is going to produce 300 megawatts though, and the Cloncurry one is only producing something like 10. I'm mildly concerned about the other Australian solar tower project that I've been watching with interest. Their latest annual report doesn't offer a status update, and the last two news articles on their website aren't very promising. It'd be a shame to see this project only ever produce the wrong sort of hot air...

Marc 'Zugschlus' Haber: exim4 vs. OpenSSL vs. GnuTLS

Judging from the long list of exim4 bugs, especially #446036, I find myself between a rock and a hard place, and having to choose between staying with GnuTLS and accepting a probably continuing flow of technical issues, or moving over to OpenSSL, setting an example against GNU software, and probably generating a new flow of license issues. GnuTLS is the “clearer” solution from a license point of view: The client library is LGPL, and it can thus be safely linked to everything that is part of Debian main. This is the main reason why we decided to use GnuTLS for exim4 years ago, so that we do not need to worry about licensing issues when some other library is linked to by exim some time in the future. On the other hand, my impression gets stronger and stronger that GnuTLS is not ready for prime-time. There is a truckload of interoperability problems with a number of “remote sides”. The most prominent issues are TLS aborts when exim4 is SMTP server for some clients, most notably Incredimail and some mobile Phones from Nokia and other vendors. Most of them can be nailed down to misnegotiation of certain ciphers, but exim does currently not allow disabling of some ciphers at run-time, and - even worse - one would need to disable them completely since one cannot judge in advance whether we are facing a client with issues or one without. The GnuTLS maintainers of both Debian and upstream try being helpful, but I do not see a long-term solution here. Additionally, nobody upstream knows its way around the GnuTLS related code in exim, which was contributed by Nikos Mavroyanopoulos years ago. So, there is little chance to get GnuTLS-related bugs ironed out from exim. OpenSSL, on the other hand, does not have these interoperability issues. At least, I haven’t heard of any, and the recommended fix for the reporters of GnuTLS related bugs, “recompile exim with OpenSSL” (which the packaging has been supporting for nearly two years now), usually fixes their problems. I am not in a position to judge whether this is caused by people actually testing against OpenSSL, or OpenSSL generally being more tolerant towards strange implementations, or GnuTLS being buggy or poorly written. However, building exim4 again OpenSSL may post the license issues that convinced us to use GnuTLS in the first place. Exim itself has an OpenSSL exception, and from what I have been told, the MySQL FLOSS License Exception allows linkage to OpenSSL as well. At least, it does now, since historical evidence in the exim4 package either shows that it used to be a license violation to link MySQL and OpenSSL in the past, or that we (the Debian exim4 team) wrongly thought so. On the other hand, if it is illegal to have OpenSSL and “really” GPLled code in the same execution space, we already have that license violation today, brought to us by PostgreSQL, which links against OpenSSL. ftpmaster has already indicated that they won’t consider an exim4 linked against OpenSSL a license violation and that the packages would go through, the packaging can handle the change by virtue of flipping a switch and rebuilding, but I am still not fully convinced that doing so is the right thing from a political and license point of view. I might still need that final nudge by feedback to this blog article, or have my reluctance fed. Please comment. No, I do not plan to take this to debian-legal; I’d prefer exim4 staying in Debian main.

Daniel Burrows: Lessig at the University of Washington

On Friday 2007-11-02, I watched Larry Lessig give a presentation at the University of Washington entitled Is Google (2008) Microsoft (1998)? Since it was Lessig, the talk was articulate and thought-provoking, and he used his slides very well (unlike many presenters who just read bullet points).

The argument he made is that Google is like Microsoft in some ways (and so are other companies like Facebook). In his analysis, the problem with Microsoft was that so many companies made themselves Microsoft-dependent, which both forced other companies to follow suit (due to network effects) and gave Microsoft leverage they could use against everyone in their ecosystem (e.g., Netscape). According to Lessig, Microsoft was not evil to use this leverage, but you have to recognize that Microsoft will do what is best for Microsoft, and this may not be what is best for you. He then suggested that we should be aware of the potential for the same thing to happen; in support of this point, he quoted excerpts from the terms of service from the APIs of Google and Facebook, which contain typical statements like we reserve the right to terminate your use of this service for any reason or for no reason, and asked: What if Microsoft had written this license agreement?

But it seemed to me that this wasn't his main point. He was using this observation as a springboard to talk about issues revolving around competition and public policy. Specifically, he feels that we should work towards a more just model of interaction between companies and users whose work makes the company more valuable (by contributing to a software ecosystem, by posting content on the Web site, etc). But the correct way to do this (he says) is not via competition, after-the-fact litigation, or voluntary codes of conduct: competition may not be around to enforce good behavior (as we've seen with Microsoft), litigation may be too late and ineffective (again, see Microsoft), and voluntary codes of conduct will disappear as soon as they get in the way of the bottom line. The correct approach, he argued, is across-the-board regulation so that all the companies have to play by the same rules.

From there he went on to talk about governmental corruption. He said (quoting Robert Reich's book Supercapitalism) that the reason we consistently look for solutions in the market and in voluntary compliance is that our governmental system is broken and does not effectively regulate corporations in the public interest. But Lessig is optimistic that we can change things (he joked that his publisher was unhappy with this point of view, because his brand has been built on pessimism). In his view, the politicians in Washington, by and large, want to be honest and do good, but they aren't able to within the current political system. For instance, on the few occassions that he managed to get access to lawmakers to discuss copyright issues, it was often the first time they had heard that there was more than one side to the argument. He thinks we need a national political movement that will shame politicians into being less corrupt.

This is all a simplification of what he said, of course; unfortunately, I wasn't able to find a recording of this talk on Lessig's Web site, or I'd point you at primary source material. I don't know if this is because he chose not to post it, or because it just hasn't been made available yet.

My view

In general, I thought that the speech was very interesting and well thought out. But as much as I'd like to buy into his optimism that we can fix our system, I don't think it's well-founded, for two reasons.

First, he argued that competition will resolve some of these problems (that was before and after he said we can't rely on competition, which I found confusing and may indicate that I misunderstood something). His evidence for this seemed to be that when Microsoft was dominating the world, users responded by reducing their dependence on Microsoft products and by switching to alternatives such as Linux. But, in fact, although more people may be using Linux than in the past, virtually everyone is still only using Windows, it's still almost impossible to find a programming job that isn't Windows-only, and Microsoft is still raking in money hand over fist; indeed, they're doing so well that they're planning to expand their workforce by a third. To take just one data point of many: I ride the bus to Seattle and back, and I regularly see other people using laptops as they commute. Virtually all the laptops run Windows. Occasionally I'll see a Mac, and every few months I'll see a guy running Linux on his laptop; I say "a guy" because it's the same guy every single time. So by my estimation, use of Linux on laptops in buses on the 545 route from Redmond to Seattle is way below 1%, with Macintoshes somewhere around 5%.

To broaden my point, I think Lessig has fallen into a trap that highly intelligent people, particularly those in academia, tend to fall into. In academia, you are surrounded by people who value learning and thinking deeply about the world. These are people who will give serious and unbiased consideration to questions like what is the social effect of my acceptance of the Facebook Terms of Service? and If I become dependent on this service, will that possibly affect me in five years if the company decides to act against my interests? The problem with this is that these people are not representative of the population at large. The population at large thinks why is this check-box getting in the way of me sending pictures to my friends? And I have no doubt that any kid who, e.g., refuses to sign up for Facebook as a protest against their TOS will be roundly mocked in their social circles for being a weird antisocial nonconformist. (of course, this may not apply to the small minority of people like myself whose social circles consist of weird antisocial nonconformists)

Second, Lessig's optimism about the political system seemed to be based on his observation that the people in government are, by and large, not venally corrupt: they want to do good, but the system is constructed in a way that makes this impossible. To me, that's a tremendously disheartening statement. If our problem were simply a few, or even many, corrupt politicians, this would be a solvable problem: even nowadays, Americans have some ability to choose who gets elected, and I believe that a sufficiently well-coordinated campaign could replace bad politicians with good ones.

But if the problem is that the system is corrupt even when the individuals are honest, it's a much deeper problem and frankly one that I don't know how to solve. While individuals have some direct control over who gets elected, we have no way to directly change the system that produces the corruption; the levers to do this are in the hands of the politicians elected through that broken system. It's unlikely that the politicians themselves will fix the problem, because they've benefited deeply from it: if the system is left as it is, well over 90% of Congress members will keep
their jobs
in the next election cycle, and any effective change seems likely (by definition) to disrupt this cushy arrangement.

On the other hand, running new candidates for office will not fix the problem. After all, if the problem is that the system is corrupt even when the participants are honest, then putting more honest people into government will have no effect. In order to get elected, these new politicians will have to become just as corrupt as the old ones, because that's how the system is set up. So we might change the faces, but we'll have the same old problems.

I recall two specific concrete proposals that Lessig made to make the system more responsive. First, he suggested shaming politicians who engage in corrupt behavior -- presumably taking large donations from interested parties. I don't see how this will help. Americans generally have a very low regard for the political class as it is; will pointing out particular examples of politicians taking money really make a difference when it comes to votes? And if it doesn't, will it really produce any change in their behavior? Politicians are motivated by votes the same way corporations are motivated by money; unless they stand a chance of losing their job (which is virtually impossible in any event), there's no reason for them to change how they behave.

His second proposal was for a system of contributions where it's impossible for any individual to prove they had donated a particular amount of money to a particular candidate. Even assuming it could be implemented perfectly, I don't think this will really solve the problem, for two reasons. First, it's not generally a secret what moneyed interests want. Politicians who want to attract large donations can just take positions that they know will appeal to donors of that sort. The donors themselves can make this easier on the candidates by, e.g., posting public position statements on issues of the day. Secondly, and this is far more insidious, even if politicians honestly represent their positions, then because success in running for office is so tied to the amount of money the candidate can raise, only candidates who hold opinions favorable to large corporations and wealthy individuals will be able to get elected. In fact, for all I know this is what happens already!

But with all that said, it was a really interesting talk and Lessig tied together some things you might not think would go together. If a video or Flash presentation becomes available, I would recommend watching through it. And hopefully my pessimistic predictions will be wrong; it's certainly happened before.

3 November 2007

Raphaël Hertzog: Unexpected move on the DSA front

One should never loose hope apparently. After my previous posts on the topic, Sam put some more pressure and expressed strongly his disappointment in the lack of progress on the DSA front and warned that he might have to look for more radical solution. Phil Hands (who was really quiet in the discussions) decided that the situation had lasted long enough already and proposed to add Peter Palfrader (weasel@debian.org) to the team if nobody expressed any opposition in 24 hours. And this morning, Phil added weasel to the “adm” group… which make of Peter a full DSA member! :-) I really didn’t expect this outcome after so many months of negociations and discussions. But I’m really relieved to see some new blood in the DSA team. I wish him good luck and I’ll hope he will be able to foster cooperation with non-DSA people like I tried since the beginning of the year. Thank you Phil! Partagez cet article / Share This

Biella Coleman: On Bats, The Suckage of American Health Insurance and Paperwork Warfare

Two nights ago I was having dinner with a colleague who recounted a truly horrible experience he had with the modern-day American health care “system.” While in Montana over the summer, he got bit by a bat and well, as a result, he and his entire family had to get rabies shots. These shots are hard to get and priceeeeeeeeeeeeeeeeeeey. The final bill was $ 20,000 and his NYU based health insurance, United Health Care is claiming they are not responsible!### Like getting bit by a bat and the possibility of rabies are not bad enough. Isn’t the point of health insurance to take care of the unexpected?? Someone also pointed me to The Daily Kos’ wrangle with BCBS of California and well, they picked the wrong guy to mess with given there are so many many many many eyeballs tuned to his blog, everyday (just check out the number of comments). I wonder if the public relations director will contact him as they did with me after I blogged about my trials and tribulations. I certainly don’t have the audience and readers he does, so I am always surprised they ever contacted me in the first place. The Daily Kos also provided a link for a site that I was thinking of creating if my problems with BCBS were not solved (glad to see someone else has) called Sick of Blue Cross. I personally like the name I came up with a little better Blue Cross No Shield but the important thing is that a site like that exists and it is very good site, design and content wise. There should be a site created for every health insurance company and they should federate and pool resources to gain more visiblity. While I am not hopeful that the health insurance industry will change within, I think mounting and steady consumer pressure can do a lot to force the industry to change their awful ways. And while I think the bad publicity is a key part to putting pressure on the health insurance to change, I actually think that the power of the consumers also can come from elsewhere, and this elsewhere is overwhelming the administrative channels within and outside of the health insurance. The gist is if they send us a lot of (useless) paperwork, send them A LOT of paperwork back. On the Daily Kos, a lot of people noted that things got moving when they complained to the Department of Banking and Insurance. While my own complaint to that department did not produce any immediate fruit, it did get the ball moving for the appeal process, which eventually panned out for me. That is, I learned a lot and started to get decent customer service. Doors opened. Now, it took me weeks to find out that I could complain to the Department of Banking and Insurance and I am sure many find themselves in that situation of walking in a no man’s land of confusion and frustration. If more and more people know that you can file a complaint to these Departments (and why are doctor’s offices not relaying this information??!!), they and the health insurance companies will get inundated with that which they love to inflict on us, paperwork. This may slow things down for you but at a certain point, state governments will get the message that something is deeply wrong. So, people MUST use these channels and overwhelm these agencies with complaints, faxes, emails as this is a powerful and very material message that something is deeply wrong and broken and must be fixed. Also, send faxes and letters to various departments in your health insurance company (appeals, customer service, medical director’s office, public relations office…) get people’s email’s and send them emails. Inundate them with a barrage of administrative paperwork. If they are not being helpful, send a fax or two a day concerning your case until you get clear answers. While individual faxes won’t make much of a difference, imagine if there are 300 a day coming in or 3000…. This can work with the numbers are there and I have a feeling that the numbers Are There. So spread the word for housebreaking your health insurance and push the paperwork back on them.

Joerg Jaspert: Mouse onXclick selection in xterm

Switching from aterm to xterm I found it annoying that xterm didn’t select a full url when i did a double-click somewhere on it, like aterm did. Now, doing a little search on it I found something way stronger. Take a url like http://foo.bar/baz for the following example. If you now put something like the following into your .Xdefaults (and load it with xrdb -load .Xdefaults), you get xterms selection in a more useful way. A double click on foo will select foo.bar, clicking three times it selects the full url (well, better speak is to say it selects everything separated by whitespace). Click four times and it selects everything up to the start of the prompt (default prompt that is). 5 clicks selects the whole line.
XTerm*on2Clicks:  regex [^/@ \n]+
XTerm*on3Clicks:  regex [^ \n]+
XTerm*on4Clicks:  regex [^#$]+
XTerm*on5Clicks:  line

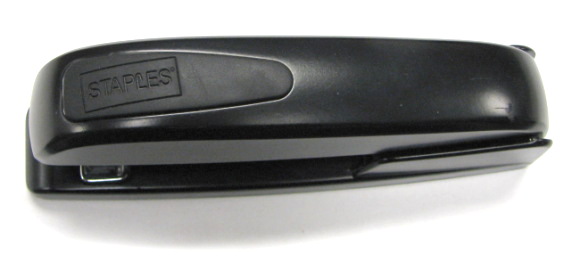
Benjamin Mako Hill: Accidentally Accurate

The label on this office product is correct, but for the wrong reason. /copyrighteous/images/stapler-small.jpg

2 November 2007

Wouter Verhelst: Beid updates

There've been some posts on Planet Grep about using the Belgian electronic ID card in Ubuntu, recently. As the one who's responsible for making that possible, I felt I had to comment. First, yes, it's possible to do crypto stuff with plain OpenSC rather than the belpic-patched versions; in fact, the tools required to sign plain text files aren't shipped anymore as part of belpic since (I believe) version 2.5.9, which is currently in Debian. However, if you're going to write your own software that somehow uses the eID, I strongly recommend you use the beid-patched versions, since they have support for a feature of which I can't remember the name currently but which means that you need to send your PIN to the card on every signature operation; plain OpenSC is not aware of this possiblity, so does not have support for it, may end up in a confused state when the card refuses to sign, and you may end up locking your card if you keep going on. You have been warned. Second, there is a README.Debian file in libbeidlibopensc2 which explains some of the idiosynchracies in the packaging, and tells you which packages you need and which ones you don't. If you're interested in using the eID, I suggest you read it. Finally, I'm currently working on packages of 2.6.0, which was released on 2007-08-30. They're mostly ready; I have a rather large changelog currently and a two-item TODO list—one of which reads "test&upload"; if all goes well, I should be able to upload them this weekend. Occasionally, this upload includes a small patch that was communicated to me through some mandriva developer which will make one of the aforementioned idiosynchracies—the fact that you have to install the -dev packages if you want to use the mozilla plugin—obsolete.

Next.

Previous.