Search Results: "ed"

28 August 2015

Ben Hutchings: Securing git imap-send in Debian

I usually send patches from git via git imap-send, which gives me a chance to edit and save them through my regular mail client. Obviously I want to make a secure connection to the IMAP server. The upstream code now supports doing this with OpenSSL, but git is under GPL and it seems that not all relevant contributors have given the extra permission to link with OpenSSL. So in Debian you still need to use an external program to provide a TLS tunnel. The commonly used TLS tunnelling programs, openssl s_client and stunnel, do not validate server certificates in a useful way - at least by default. Here's how I've configured git imap-send and stunnel to properly validate the server certificate. If you use the PLAIN or LOGIN authentication method with the server, you will still see the warning:
*** IMAP Warning *** Password is being sent in the clear
The server does see the clear-text password, but it is encrypted on the wire and git imap-send just doesn't know that. ~/.gitconfig
[imap]
	user = ben
	folder = "drafts"
	tunnel = "stunnel ~/.git-imap-send/stunnel.conf"
~/.git-imap-send/stunnel.conf
debug = 3
foreground = yes
client = yes
connect = mail.decadent.org.uk:993
sslVersion = TLSv1.2
renegotiation = no
verify = 2
; Current CA for the IMAP server.
; If you don't want to pin to a specific CA certificate, use
; /etc/ssl/certs/ca-certificates.crt instead.
CAfile = /etc/ssl/certs/StartCom_Certification_Authority.pem
checkHost = mail.decadent.org.uk
If stunnel chokes on the checkHost variable, it doesn't support certificate name validation. Unfortunately no Debian stable release has this feature - only testing/unstable. I'm wondering whether it would be worthwhile to backport it or even to make a stable update to add this important security feature.

Ben Hutchings: Securing git imap-send in Debian

I usually send patches from git via git imap-send, which gives me a chance to edit and save them through my regular mail client. Obviously I want to make a secure connection to the IMAP server. The upstream code now supports doing this with OpenSSL, but git is under GPL and it seems that not all relevant contributors have given the extra permission to link with OpenSSL. So in Debian you still need to use an external program to provide a TLS tunnel. The commonly used TLS tunnelling programs, openssl s_client and stunnel, do not validate server certificates in a useful way - at least by default. Here's how I've configured git imap-send and stunnel to properly validate the server certificate. If you use the PLAIN or LOGIN authentication method with the server, you will still see the warning:
*** IMAP Warning *** Password is being sent in the clear
The server does see the clear-text password, but it is encrypted on the wire and git imap-send just doesn't know that. ~/.gitconfig
[imap]
	user = ben
	folder = "drafts"
	tunnel = "stunnel ~/.git-imap-send/stunnel.conf"
~/.git-imap-send/stunnel.conf
debug = 3
foreground = yes
client = yes
connect = mail.decadent.org.uk:993
sslVersion = TLSv1.2
renegotiation = no
verify = 2
; Current CA for the IMAP server.
; If you don't want to pin to a specific CA certificate, use
; /etc/ssl/certs/ca-certificates.crt instead.
CAfile = /etc/ssl/certs/StartCom_Certification_Authority.pem
checkHost = mail.decadent.org.uk
If stunnel chokes on the checkHost variable, it doesn't support certificate name validation. Unfortunately no Debian stable release has this feature - only testing/unstable. I'm wondering whether it would be worthwhile to backport it or even to make a stable update to add this important security feature.

Ben Hutchings: Securing git imap-send in Debian

I usually send patches from git via git imap-send, which gives me a chance to edit and save them through my regular mail client. Obviously I want to make a secure connection to the IMAP server. The upstream code now supports doing this with OpenSSL, but git is under GPL and it seems that not all relevant contributors have given the extra permission to link with OpenSSL. So in Debian you still need to use an external program to provide a TLS tunnel. The commonly used TLS tunnelling programs, openssl s_client and stunnel, do not validate server certificates in a useful way - at least by default. Here's how I've configured git imap-send and stunnel to properly validate the server certificate. If you use the PLAIN or LOGIN authentication method with the server, you will still see the warning:
*** IMAP Warning *** Password is being sent in the clear
The server does see the clear-text password, but it is encrypted on the wire and git imap-send just doesn't know that. ~/.gitconfig
[imap]
	user = ben
	folder = "drafts"
	tunnel = "stunnel ~/.git-imap-send/stunnel.conf"
~/.git-imap-send/stunnel.conf
debug = 3
foreground = yes
client = yes
connect = mail.decadent.org.uk:993
sslVersion = TLSv1.2
renegotiation = no
verify = 2
; Current CA for the IMAP server.
; If you don't want to pin to a specific CA certificate, use
; /etc/ssl/certs/ca-certificates.crt instead.
CAfile = /etc/ssl/certs/StartCom_Certification_Authority.pem
checkHost = mail.decadent.org.uk
If stunnel chokes on the checkHost variable, it doesn't support certificate name validation. Unfortunately no Debian stable release has this feature - only testing/unstable. I'm wondering whether it would be worthwhile to backport it or even to make a stable update to add this important security feature.

27 August 2015

Norbert Preining: Kobo Japanese Dictionary Enhancer 1.1

Lots of releases in quick succession the new Kobo Japanese Dictionary Enhancer brings multi-dictionary support and merged translation support. Using the Wadoku project s edict2 database we can now add also German translations. kobo-japanese-dictionary-enhancer Looking at the numbers, we have now 326064 translated entries when using the English edict2, and 368943 translated entries when using the German Wadoku edict version. And more than that, as an extra feature it is now also possible to have merged translations, so to have both German and English translations added. kobo-dict-de-en Please head over to the main page of the project for details and download instructions. If you need my help in creating the updated dictionary, please feel free to contact me. Enjoy.

Ben Hutchings: Truncating a string in C

This version uses the proper APIs to work with the locale's multibyte encoding (with single-byte encodings being a trivial case of multibyte). It will fail if it encounters an invalid byte sequence (e.g. byte > 127 in the "C" locale), though it could be changed to treat each rejected byte as a single character.
#include <locale.h>
#include <stdio.h>
#include <stdlib.h>
#include <string.h>
#include <wchar.h>
int main(int argc, char **argv)
 
    size_t n = 12, totlen = 0, maxlen, chlen;
    setlocale(LC_ALL, "");
    if (argc != 2)
	return EXIT_FAILURE;
    maxlen = strlen(argv[1]);
    while (n--)  
	chlen = mbrlen(argv[1] + totlen, maxlen - totlen, NULL);
	if (chlen > MB_CUR_MAX)
	    return EXIT_FAILURE;
	totlen += chlen;
     
    printf("%.*s\n", (int)totlen, argv[1]);
    return 0;
 

Ben Hutchings: Truncating a string in C

This version uses the proper APIs to work with the locale's multibyte encoding (with single-byte encodings being a trivial case of multibyte). It will fail if it encounters an invalid byte sequence (e.g. byte > 127 in the "C" locale), though it could be changed to treat each rejected byte as a single character.
#include <locale.h>
#include <stdio.h>
#include <stdlib.h>
#include <string.h>
#include <wchar.h>
int main(int argc, char **argv)
 
    size_t n = 12, totlen = 0, maxlen, chlen;
    setlocale(LC_ALL, "");
    if (argc != 2)
	return EXIT_FAILURE;
    maxlen = strlen(argv[1]);
    while (n--)  
	chlen = mbrlen(argv[1] + totlen, maxlen - totlen, NULL);
	if (chlen > MB_CUR_MAX)
	    return EXIT_FAILURE;
	totlen += chlen;
     
    printf("%.*s\n", (int)totlen, argv[1]);
    return 0;
 

Ben Hutchings: Truncating a string in C

This version uses the proper APIs to work with the locale's multibyte encoding (with single-byte encodings being a trivial case of multibyte). It will fail if it encounters an invalid byte sequence (e.g. byte > 127 in the "C" locale), though it could be changed to treat each rejected byte as a single character.
#include <locale.h>
#include <stdio.h>
#include <stdlib.h>
#include <string.h>
#include <wchar.h>
int main(int argc, char **argv)
 
    size_t n = 12, totlen = 0, maxlen, chlen;
    setlocale(LC_ALL, "");
    if (argc != 2)
	return EXIT_FAILURE;
    maxlen = strlen(argv[1]);
    while (n--)  
	chlen = mbrlen(argv[1] + totlen, maxlen - totlen, NULL);
	if (chlen > MB_CUR_MAX)
	    return EXIT_FAILURE;
	totlen += chlen;
     
    printf("%.*s\n", (int)totlen, argv[1]);
    return 0;
 

Alexander Wirt: Basic support for SSO Client certificates on paste.debian.net

Sometimes waiting for a delayed flight helps to implement things. I added some basic support for the new Debian SSO Client Certificate feature to paste.debian.net. If you are using such a certificate most anti-spam restrictions, code limitations and so on won t count for you anymore.

Ritesh Raj Sarraf: Laptop Mode Tools - 1.68

I am please to announce the release of Laptop Mode Tools, version 1.68. This release is mainly focused on integration with the newer init system, systemd. Without the help from the awesome Debian systemd maintainers, this would not have been possible. Thank you folks. While the focus now is on systemd, LMT will still support the older SysV Init. With this new release, there are some new files: laptop-mode.service, laptop-mode.timer and lmt-poll.service. All the files should be documented well enough for users. lmt-poll.service is the equivalent of the module battery-level-polling, should you need it. Filtered git log:
1.68 - Thu Aug 27 22:36:43 IST 2015
    * Fix all instances for BATTERY_LEVEL_POLLING
    * Group kill the polling daemon so that its child process get the same signal
    * Release the descriptor explicitly
    * Add identifier about who's our parent
    * Narrow down our power_supply subsystem event check condition
    * Fine tune the .service file
    * On my ultrabook, AC as reported as ACAD
    * Enhance lmt-udev to better work with systemd
    * Add a timer based polling for LMT. It is the equivalent of battery-polling-daemon,
      using systemd
    * Disable battery level polling by default, because most systems will have systemd running
    * Add documentation reference in systemd files
The md5 checksum for the tarball is 15edf643990e08deaebebf66b128b270

Categories:

Keywords:

Like:

Thorsten Glaser: Go enjoy shell

Dimitri, I personally enjoy shell

tglase@tglase:~ $ x= 
tglase@tglase:~ $ echo $ x::12 
 
tglase@tglase:~ $ printf '%s\n' 'import sys' 'print(sys.argv[1][:12])' >x.py
tglase@tglase:~ $ python x.py $x


much more than Python, actually. (Python is the language in which you do not want to write code dealing with strings, due to UnicodeDecodeError and all; even py3k is not much better.) I would have commented on your post if it allowed doing so without getting a proprietary Google+ account.

Joey Hess: then and now

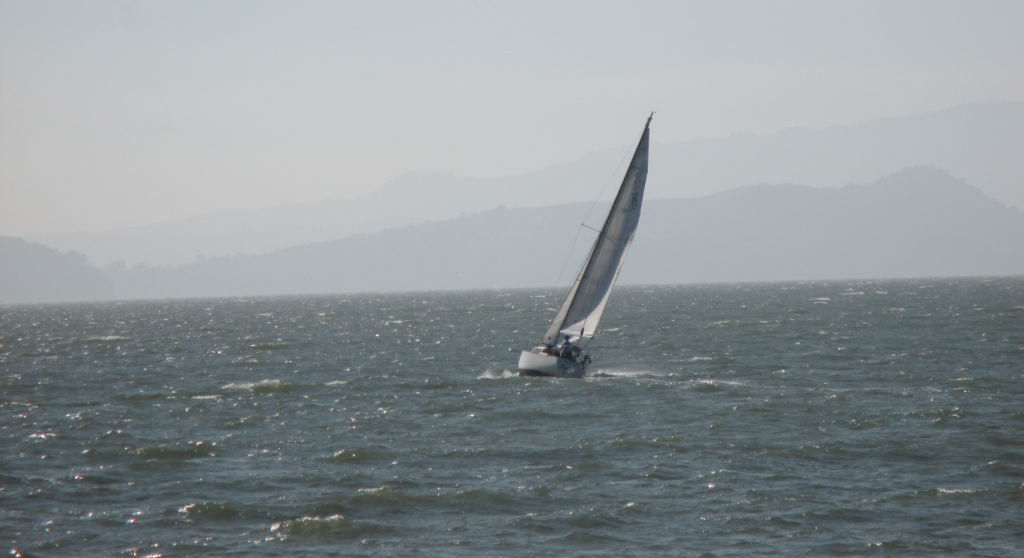
It's 2004 and I'm in Oldenburg DE, working on the Debian Installer. Colin and I pair program on partman, its new partitioner, to get it into shape. We've somewhat reluctantly decided to use it. Partman is in some ways a beautful piece of work, a mass of semi-object-oriented, super extensible shell code that sprang fully formed from the brow of Anton. And in many ways, it's mad, full of sector alignment twiddling math implemented in tens of thousands of lines of shell script scattered amoung hundreds of tiny files that are impossible to keep straight. In the tiny Oldenburg Developers Meeting, full of obscure hardware and crazy intensity of ideas like porting Debian to VAXen, we hack late into the night, night after night, and crash on the floor. sepia toned hackers round a table It's 2015 and I'm at a Chinese bakery, then at the Berkeley pier, then in a SF food truck lot, catching half an hour here and there in my vacation to add some features to Propellor. Mostly writing down data types for things like filesystem formats, partition layouts, and then some small amount of haskell code to use them in generic ways. Putting these peices together and reusing stuff already in Propellor (like chroot creation). Before long I have this, which is only 2 undefined functions away from (probably) working:
let chroot d = Chroot.debootstrapped (System (Debian Unstable) "amd64") mempty d
        & Apt.installed ["openssh-server"]
        & ...
    partitions = fitChrootSize MSDOS
        [ (Just "/boot", mkPartiton EXT2)
        , (Just "/", mkPartition EXT4)
        , (Nothing, const (mkPartition LinuxSwap (MegaBytes 256)))
        ]
 in Diskimage.built chroot partitions (grubBooted PC)
This is at least a replication of vmdebootstrap, generating a bootable disk image from that config and 400 lines of code, with enormous customizability of the disk image contents, using all the abilities of Propellor. But is also, effectively, a replication of everything partman is used for (aside from UI and RAID/LVM). sailboat on the SF bay What a difference a decade and better choices of architecture make! In many ways, this is the loosely coupled, extensible, highly configurable system partman aspired to be. Plus elegance. And I'm writing it on a lark, because I have some spare half hours in my vacation. Past Debian Installer team lead Tollef stops by for lunch, I show him the code, and we have the conversation old d-i developers always have about partman. I can't say that partman was a failure, because it's been used by millions to install Debian and Ubuntu and etc for a decade. Anything that deletes that many Windows partitions is a success. But it's been an unhappy success. Nobody has ever had a good time writing partman recipes; the code has grown duplication and unmaintainability. I can't say that these extensions to Propellor will be a success; there's no plan here to replace Debian Installer (although with a few hundred more lines of code, propellor is d-i 2.0); indeed I'm just adding generic useful stuff and building further stuff out of it without any particular end goal. Perhaps that's the real difference.

26 August 2015

Carl Chenet: Retweet 0.2 : bump to Python 3

Follow me on Identi.ca or Twitter or Diaspora*diaspora-banner Don t know Retweet? My last post about it introduced this small Twitter bot whichs just retweets (for now) every tweets from a Twitter account to another one. Retweet Retweet was created in order to improve the Journal du hacker Twitter account. The Journal du hacker is a Hacker News-like French-speaking website. logo-journal-du-hacker Especially useful to broadcast news through a network of Twitter accounts, Retweet was improved to bump Python version to 3.4 and to improve pep8 compliance (work in progress). The project is also well documented and should be quite simple to install, configure and use. After my first blog post about Retweet, new users gave me feedback about it and I now have great ideas for future features for the next release. Twitter_logo_blue What about you? If you try it, please tell me what you think about it, opening a bug request or ask for new features. Or just write your comment here ;)

Holger Levsen: 20150826-jenkins-fourth-state

jenkins has a fourth state So, at the jenkins.debian.org BOF (very short summary: j.d.o will be coming soonish, long summary thanks to the awesome video team) I shared a trick I discovered almost a year ago, but had never really announced anywhere yet, which enables one to programatically use a fourth state to the existing three jenkins job states ("success", "unstable" and "failed"), which is "aborted". Common knowledge is that it's only possible to abort jobs manually, but it's also possible to do that like this:
TMPFILE=$(mktemp)
curl https://jenkins.debian.net/jnlpJars/jenkins-cli.jar -o $TMPFILE
java -jar $TMPFILE -s http://localhost:8080/ set-build-result aborted
rm $TMPFILE
exit
The nice thing about aborted job runs is that these don't cause any notifications (neither mail nor IRC), so I intend to use this for several cases: I've no idea when I'll get along to actually implement that, so help doing this is very much welcome and I'd also be glad to help hooking this into the existing jenkins.debian.net.git codebase. In related news, I'm back home since Monday and am thankful for having shared a very nice and productive DebConf15 with many old and new friends in Heidelberg. Many thanks to everyone involved in making this happen!

NOKUBI Takatsugu: 1Gbps FTTH

This month, I changed FTTH Internet from 100Mbps to 1Gbps. The costs is almost same as the past line. To change the line, I had need to be witness in the construction, so I couldn t get time to attend DebConf 2015. According to Speedtest.net, I can get about 300 Mbps upstream bandwidth.

Rapha&#235;l Hertzog: Freexian s report about Debian Long Term Support, July 2015

A Debian LTS logoLike each month, here comes a report about the work of paid contributors to Debian LTS. Individual reports In July, 79.50 work hours have been dispatched among 7 paid contributors. Their reports are available: Evolution of the situation August has seen a small decrease in terms of sponsored hours (71.50 hours per month) because two sponsors did not pay their renewal invoice on time. That said they reconfirmed their willingness to support us and things should be fixed after the summer. And we should be able to reach our first milestone of funding the equivalent of a half-time position, in particular since a new platinum sponsor might join the project. DebConf 15 happened this month and Debian LTS was featured in a talk and in a work session. Have a look at the video recordings: In terms of security updates waiting to be handled, the situation is better than last month: the dla-needed.txt file lists 20 packages awaiting an update (4 less than last month), the list of open vulnerabilities in Squeeze shows about 22 affected packages in total (11 less than last month). The new LTS frontdesk ensures regular triage of CVE reports and the difference between both counts dropped significantly. That s good! Thanks to our sponsors Thanks to Sig-I/O, a new bronze sponsor, which joins our 35 other sponsors.

One comment Liked this article? Click here. My blog is Flattr-enabled.

Dirk Eddelbuettel: RProtoBuf 0.4.3

A new maintenance release 0.4.3 of RProtoBuf is now on CRAN. RProtoBuf provides R bindings for the Google Protocol Buffers ("Protobuf") data encoding library used and released by Google, and deployed as a language and operating-system agnostic protocol by numerous projects. This release comes upon the request of CRAN and adds additional import statements to the NAMESPACE file. While we were at it, a few more things got cleaned up and edited---but no new code was added. Full details are below.
Changes in RProtoBuf version 0.4.3 (2015-08-25)
  • Declare additional imports from methods in NAMESPACE.
  • Travis CI tests now run faster as all CRAN dependencies are installed as binaries.
  • The tools/winlibs.R script now tests for R (< 3.3.0) before calling the (soon-to-be phased out) setInternet2() function.
  • Several small edits were made to DESCRIPTION to clarify library dependencies, provide additonal references and conform to now-current R packaging standards.
CRANberries also provides a diff to the previous release. The RProtoBuf page has a package vignette, a a 'quick' overview vignette, and a unit test summary vignette. Questions, comments etc should go to the GitHub issue tracker off the GitHub repo.

This post by Dirk Eddelbuettel originated on his Thinking inside the box blog. Please report excessive re-aggregation in third-party for-profit settings.

25 August 2015

Norbert Preining: Plex Home Theater 1.4.1 updated for Debian/sid

Debian/sid is going through a big restructuring with the switch to a new gcc and libstc++. Furthermore, libcec3 is now the default. So I have updated my PHT builds for Debian/sid to build and install on the current status, both for amd64 and i386. plex-debian-new Add the following lines to your sources.list:
deb http://www.preining.info/debian/ sid pht
deb-src http://www.preining.info/debian/ sid pht
You can also grab the binary for amd64 directly here for amd64 and i386, you can get the source package with
dget http://www.preining.info/debian/pool/pht/p/plexhometheater/plexhometheater_1.4.1-2.dsc
The release file and changes file are signed with my official Debian key 0x860CDC13. For Debian/testing I am waiting until the transition has settled. Please wait a bit more. Now be ready for enjoying the next movie!

Richard Hartmann: Tor-enabled Debian mirror, part 2

Well, that was quite some feedback to my last post; via blog, email, irc, and in person. I actually think this may be the most feedback I ever got to any single blog post. If you are still waiting for a reply after this new post, I will get back to you. To handle common question/information at once: So this whole thing is a lot easier now:
# apt-get install torsocks apt-transport-tor
# mv /etc/apt/sources.list /etc/apt/sources.list--backup2
# > /etc/apt/sources.list << EOF
deb tor+http://vwakviie2ienjx6t.onion/debian/ unstable main contrib non-free
deb tor+http://earthqfvaeuv5bla.onion/debian/ unstable main contrib non-free
EOF
# apt-get update
# apt-get install vcsh

Lunar: Reproducible builds: week 17 in Stretch cycle

A good amount of the Debian reproducible builds team had the chance to enjoy face-to-face interactions during DebConf15.
Names in red and blue were all present at DebConf15
Picture of the  reproducible builds  talk during DebConf15
Hugging people with whom one has been working tirelessly for months gives a lot of warm-fuzzy feelings. Several recorded and hallway discussions paved the way to solve the remaining issues to get reproducible builds part of Debian proper. Both talks from the Debian Project Leader and the release team mentioned the effort as important for the future of Debian. A forty-five minutes talk presented the state of the reproducible builds effort. It was then followed by an hour long roundtable to discuss current blockers regarding dpkg, .buildinfo and their integration in the archive. Picture of the  reproducible builds  roundtable during DebConf15 Toolchain fixes Reiner Herrmann submitted a patch to make rdfind sort the processed files before doing any operation. Chris Lamb proposed a new patch for wheel implementing support for SOURCE_DATE_EPOCH instead of the custom WHEEL_FORCE_TIMESTAMP. akira sent one making man2html SOURCE_DATE_EPOCH aware. St phane Glondu reported that dpkg-source would not respect tarball permissions when unpacking under a umask of 002. After hours of iterative testing during the DebConf workshop, Sandro Knau created a test case showing how pdflatex output can be non-deterministic with some PNG files. Packages fixed The following 65 packages became reproducible due to changes in their build dependencies: alacarte, arbtt, bullet, ccfits, commons-daemon, crack-attack, d-conf, ejabberd-contrib, erlang-bear, erlang-cherly, erlang-cowlib, erlang-folsom, erlang-goldrush, erlang-ibrowse, erlang-jiffy, erlang-lager, erlang-lhttpc, erlang-meck, erlang-p1-cache-tab, erlang-p1-iconv, erlang-p1-logger, erlang-p1-mysql, erlang-p1-pam, erlang-p1-pgsql, erlang-p1-sip, erlang-p1-stringprep, erlang-p1-stun, erlang-p1-tls, erlang-p1-utils, erlang-p1-xml, erlang-p1-yaml, erlang-p1-zlib, erlang-ranch, erlang-redis-client, erlang-uuid, freecontact, givaro, glade, gnome-shell, gupnp, gvfs, htseq, jags, jana, knot, libconfig, libkolab, libmatio, libvsqlitepp, mpmath, octave-zenity, openigtlink, paman, pisa, pynifti, qof, ruby-blankslate, ruby-xml-simple, timingframework, trace-cmd, tsung, wings3d, xdg-user-dirs, xz-utils, zpspell. The following packages became reproducible after getting fixed: Uploads that might have fixed reproducibility issues: Some uploads fixed some reproducibility issues but not all of them: Patches submitted which have not made their way to the archive yet: St phane Glondu reported two issues regarding embedded build date in omake and cduce. Aur lien Jarno submitted a fix for the breakage of make-dfsg test suite. As binutils now creates deterministic libraries by default, Aur lien's patch makes use of a wrapper to give the U flag to ar. Reiner Herrmann reported an issue with pound which embeds random dhparams in its code during the build. Better solutions are yet to be found. reproducible.debian.net Package pages on reproducible.debian.net now have a new layout improving readability designed by Mattia Rizzolo, h01ger, and Ulrike. The navigation is now on the left as vertical space is more valuable nowadays. armhf is now enabled on all pages except the dashboard. Actual tests on armhf are expected to start shortly. (Mattia Rizzolo, h01ger) The limit on how many packages people can schedule using the reschedule script on Alioth has been bumped to 200. (h01ger) mod_rewrite is now used instead of JavaScript for the form in the dashboard. (h01ger) Following the rename of the software, debbindiff has mostly been replaced by either diffoscope or differences in generated HTML and IRC notification output. Connections to UDD have been made more robust. (Mattia Rizzolo) diffoscope development diffoscope version 31 was released on August 21st. This version improves fuzzy-matching by using the tlsh algorithm instead of ssdeep. New command line options are available: --max-diff-input-lines and --max-diff-block-lines to override limits on diff input and output (Reiner Herrmann), --debugger to dump the user into pdb in case of crashes (Mattia Rizzolo). jar archives should now be detected properly (Reiner Herrman). Several general code cleanups were also done by Chris Lamb. strip-nondeterminism development Andrew Ayer released strip-nondeterminism version 0.010-1. Java properties file in jar should now be detected more accurately. A missing dependency spotted by St phane Glondu has been added. Testing directory ordering issues: disorderfs During the reproducible builds workshop at DebConf, participants identified that we were still short of a good way to test variations on filesystem behaviors (e.g. file ordering or disk usage). Andrew Ayer took a couple of hours to create disorderfs. Based on FUSE, disorderfs in an overlay filesystem that will mount the content of a directory at another location. For this first version, it will make the order in which files appear in a directory random. Documentation update Dhole documented how to implement support for SOURCE_DATE_EPOCH in Python, bash, Makefiles, CMake, and C. Chris Lamb started to convert the wiki page describing SOURCE_DATE_EPOCH into a Freedesktop-like specification in the hope that it will convince more upstream to adopt it. Package reviews 44 reviews have been removed, 192 added and 77 updated this week. New issues identified this week: locale_dependent_order_in_devlibs_depends, randomness_in_ocaml_startup_files, randomness_in_ocaml_packed_libraries, randomness_in_ocaml_custom_executables, undeterministic_symlinking_by_rdfind, random_build_path_by_golang_compiler, and images_in_pdf_generated_by_latex. 117 new FTBFS bugs have been reported by Chris Lamb, Chris West (Faux), and Niko Tyni. Misc. Some reproducibility issues might face us very late. Chris Lamb noticed that the test suite for python-pykmip was now failing because its test certificates have expired. Let's hope no packages are hiding a certificate valid for 10 years somewhere in their source! Pictures courtesy and copyright of Debian's own paparazzi: Aigars Mahinovs.

Richard Hartmann: Tor-enabled Debian mirror

During Jacob Applebaum's talk at DebConf15, he noted that Debian should TLS-enable all services, especially the mirrors. His reasoning was that when a high-value target downloads a security update for package foo, an adversary knows that they are still using a vulnerable version of foo and try to attack before the security update has been installed. In this specific case, TLS is not of much use though. If the target downloads 4.7 MiB right after a security update with 4.7 MiB has been released, or downloads from security.debian.org, it's still obvious what's happening. Even padding won't help much as the 5 MiB download will also be suspicious. The mere act of downloading anything from the mirrors after an update has been released is reason enough to try an attack. The solution, is, of course, Tor. weasel was nice enough to set up a hidden service on Debian's infrastructure; initally we agreed that he would just give me a VM and I would do the actual work, but he went the full way on his own. Thanks :) This service is not redundant, it uses a key which is stored on the local drive, the .onion will change, and things are expected to break. But at least this service exists now and can be used, tested, and put under some load:
http://vwakviie2ienjx6t.onion/

I couldn't get apt-get to be content with a .onion in /etc/apt/sources.list and Acquire::socks::proxy "socks://127.0.0.1:9050"; in /etc/apt/apt.conf, but the torify wrapper worked like a charm. What follows is, to the best of my knowledge, the first ever download from Debian's "official" Tor-enabled mirror:
~ # apt-get install torsocks
~ # mv /etc/apt/sources.list /etc/apt/sources.list.backup
~ # echo 'deb http://vwakviie2ienjx6t.onion/debian/ unstable main non-free contrib' > /etc/apt/sources.list
~ # torify apt-get update
Get:1 http://vwakviie2ienjx6t.onion unstable InRelease [215 kB]
Get:2 http://vwakviie2ienjx6t.onion unstable/main amd64 Packages [7548 kB]
Get:3 http://vwakviie2ienjx6t.onion unstable/non-free amd64 Packages [91.9 kB]
Get:4 http://vwakviie2ienjx6t.onion unstable/contrib amd64 Packages [58.5 kB]
Get:5 http://vwakviie2ienjx6t.onion unstable/main i386 Packages [7541 kB]
Get:6 http://vwakviie2ienjx6t.onion unstable/non-free i386 Packages [85.4 kB]
Get:7 http://vwakviie2ienjx6t.onion unstable/contrib i386 Packages [58.1 kB]
Get:8 http://vwakviie2ienjx6t.onion unstable/contrib Translation-en [45.7 kB]
Get:9 http://vwakviie2ienjx6t.onion unstable/main Translation-en [5060 kB]
Get:10 http://vwakviie2ienjx6t.onion unstable/non-free Translation-en [80.8 kB]
Fetched 20.8 MB in 2min 0s (172 kB/s)
Reading package lists... Done
~ # torify apt-get install vim
Reading package lists... Done
Building dependency tree       
Reading state information... Done
The following extra packages will be installed:
  vim-common vim-nox vim-runtime vim-tiny
Suggested packages:
  ctags vim-doc vim-scripts cscope indent
The following packages will be upgraded:
  vim vim-common vim-nox vim-runtime vim-tiny
5 upgraded, 0 newly installed, 0 to remove and 661 not upgraded.
Need to get 0 B/7719 kB of archives.
After this operation, 2048 B disk space will be freed.
Do you want to continue? [Y/n] 
Retrieving bug reports... Done
Parsing Found/Fixed information... Done
Reading changelogs... Done
(Reading database ... 316427 files and directories currently installed.)
Preparing to unpack .../vim-nox_2%3a7.4.826-1_amd64.deb ...
Unpacking vim-nox (2:7.4.826-1) over (2:7.4.712-3) ...
Preparing to unpack .../vim_2%3a7.4.826-1_amd64.deb ...
Unpacking vim (2:7.4.826-1) over (2:7.4.712-3) ...
Preparing to unpack .../vim-tiny_2%3a7.4.826-1_amd64.deb ...
Unpacking vim-tiny (2:7.4.826-1) over (2:7.4.712-3) ...
Preparing to unpack .../vim-runtime_2%3a7.4.826-1_all.deb ...
Unpacking vim-runtime (2:7.4.826-1) over (2:7.4.712-3) ...
Preparing to unpack .../vim-common_2%3a7.4.826-1_amd64.deb ...
Unpacking vim-common (2:7.4.826-1) over (2:7.4.712-3) ...
Processing triggers for man-db (2.7.0.2-5) ...
Processing triggers for mime-support (3.58) ...
Processing triggers for desktop-file-utils (0.22-1) ...
Processing triggers for hicolor-icon-theme (0.13-1) ...
Setting up vim-common (2:7.4.826-1) ...
Setting up vim-runtime (2:7.4.826-1) ...
Processing /usr/share/vim/addons/doc
Setting up vim-nox (2:7.4.826-1) ...
Setting up vim (2:7.4.826-1) ...
Setting up vim-tiny (2:7.4.826-1) ...
~ # 

More services will follow. noodles, weasel, and me agreed that the project as a whole should aim to Tor-enable the complete package lifecycle, package information, and the website. Maybe a more secure install option on the official images which, amongst others, sets up apt, apt-listbugs, dput, reportbug, et al up to use Tor without further configuration could even be a realistic stretch goal.

Next.

Previous.