Search Results: "ron"

4 April 2008

MJ Ray: Tour of Britain launch notes

ToB Taunton Banner The Tour of Britain organisers emailed me to announce their launch. The race this year will be 7th - 14th September (starting stage 2 in my old stomping grounds of MK and finishing stage 3 in Burnham on Sea, the next town south from my home) and they announce daily coverage on itv4
on their front page. Well done ToB and itv! That should be a vast improvement on the 2 hours on the last day that BBC were giving it, although I expect it’s highlights rather than live.

Martin F. Krafft: Document management system sought

A client of mine seeks a document management system to be run on a Linux machine, and I have no experience in this domain. I am turning to you for help, dear lazyweb, my client will make a donation to a FLOSS project of your choosing in return. I define document management system as an online file storage for OpenOffice.org/Word documents, spreadsheets, PDFs, and pictures. Thus, this is less about content management than about file storage and organisation, aimed at collaboration. The following are the sought features: Do you know of any tool we could deploy? I did come across BFExplorer, but that seems to lack support for tags, direct data access, bulk uploads, multiuser environment, and it s not received updates in more than a year. Suggestions welcome! NP: Pulp: Freaks

3 April 2008

Steve Kemp: It's just a puzzle box!

Chronicle
I've made a new release of the chronicle blog compiler, primarily to allow the "Subject:" header to be used for new blog subjects. (That allows new entries to be automatically posted via email, with an appropriate procmail setup. I'll add one as an example shortly.)
RSS Utility
Whilst on the subject of RSS creation (huh?) I've written a tiny utility which will create an RSS feed from a list of text files. It will also create an index.html file to match. To see why this is useful you could view my recent changelog. I think there is a need for a small tool to read files and create feeds from them - like mod_index_rss does, but without messing with Apache. If there is any interest I'd be happy to release the code, as-is it doesn't use a template..
Anonymous Hosting?
Online privacy is important. Mostly when this is discussed it is in the context of client-side anonymity. Looking at it from the other side, though, How do you host a website anonymously? You could register the domain via a proxy, or with bogus details. But if you host the site yourself the IP address may be traced to the hosting provider, and that may be used to trace back to you. So, the alternatives? Well you could use a hosted site such as livejournal / wordpress / googlepages / etc. But pretty surely they'll be able to trace content back to you - and if you don't host it there's a high chance they'll just pull it if you talk about "bad things". (I guess you could use TOR for uploading / your connections there.) So, going back to the question. How can you host something, easily accessible to the world, without risk of your identity/association being discovered?
I'm, obviously, ignoring FreeNet. Two reasons for that:
  • It's slow, has no search-engine goodness, and is unproven.
  • It requires an atypical client. Aunt Milly won't be able to surf Freenet...
I almost think the best way forward would be to write a site which was a proxy for a file-sharing protocol, then link people to items that way. Relying on the swarm to host the files.. The downside is that you'd have to have a convincing argument for when RIAA comes calling, suggesting that you're sharing their stuff too. If it wasn't a general purpose proxy then the deniability is gone, and if it is you're at risk of general copyright infringement claims. Hard problem. Shame.
ObQuote: HellRaiser

Adrian von Bidder: OOXML

The thing to do: require Microsoft and its cronies to write a strict OOXML document parser/verifier and release it under the BSD license as a starting point for other companies' work with OOXML documents. And require them to offer free support to all companies wishing to publish OOXML compliant documents (without any vendor specific extensions) on how to do that with their M$ Office products.

2 April 2008

Lior Kaplan: Openoffice.org Issue #86811: Arabic numbers instead of decimal numbers


Issue #86811 is still of my top priorities this week, as it causes a major problem for Hebrew speaking users of Openoffice.org. As I can’t fix the code myself, I’m focusing on explaining that this is a major problem and it should be fixed in the 2.4.1 release. Before explaining more about the bug, let me clear a bit some terminologies: Arabic numbers are the numbers you know from English and most languages (including Hebrew). Hindu numbers are the one in use by the Arabic languages (Arabic, Persian, Urdu, etc). Notice that this is confusing as the numbers in the Arabic languages aren’t Arabic numbers but Hindu numbers. Issue #86811 is about how does OO.org handles numbers during import of Microsoft Word documents. The current problem is that during the import, the numbers change from Arabic to Hindu. This makes it impossible for Hebrew speaking users to read Microsoft Word documents which include numbers. See screenshots attached to issue #87625 (dup of #86811). As in Israel there is still a majority for Microsoft Office over Openoffice.org, this makes openoffice.org users isolated from getting documents from other people. This is the real reason for changing the bug priority to a higher one. Issue #86811 currently have 80 votes (and counting)… Some Linux users are even trying to convince their distributions to exclude version 2.4.0 from their coming release (See Ubuntu bug #210204 and Mandriva bug #38874). I personally think that this is wrong, as 2.4.0 should be included in the upcoming releases, but we should work hard to get 2.4.1 into those distributions when the fix for #86811 is ready. p.s. Hello planet openoffice.org (:

MJ Ray: Current Issues / Police chat logs

I couldn't get into the last police chat because it's Flash-only and I don't have it enabled, but they published a transcript on their site.  Nice to see Quadron being named and shamed for their mobile phoning drivers... and is the Ebdon Arms really rural?

What do you think of the other topics raised?

1 April 2008

MJ Ray: Blog Updates

First of all, you can't do All Fool's Day pranks on global web sites because of time zones: if you do, you'll be pranking either early or late somewhere and so you're the fool. Now, I've been a bit quiet recently because I've been moving dozens of Wordpress blogs over to one Wordpress MU install. Clearly the right way to do it. They're all on different domains and we want their names to have www, which needed the following small change...
 
--- wpmu-settings.php
+++ wpmu-settings.php
@@ -6,8 +6,8 @@ if( $current_site && $current_blog )
 $wpmuBaseTablePrefix = $table_prefix;
 $domain = addslashes( $_SERVER['HTTP_HOST'] );
-if( substr( $domain, 0, 4 ) == 'www.' )
-       $domain = substr( $domain, 4 );
+if( substr( $domain, 0, 4 ) != 'www.' )
+       $domain = 'www.'.$domain;
 if( strpos( $domain, ':' ) )  
        if( substr( $domain, -3 ) == ':80' )  
                $domain = substr( $domain, 0, -3 );
I could have sworn I changed something else in that file, but I don't see what. Oops. I guess I'll run a check against the release tarball before merging the next upgrade from upstream. If anyone wants to hire someone to move blogs to Wordpress MU, you how where to find me. It's pretty enjoyable once you get into the routine, even if this project overran. I'm looking at changing my own blogs too. I'm looking at Chronicle but maybe with more email-like input files.

31 March 2008

Benjamin Mako Hill: Proven Wrong!

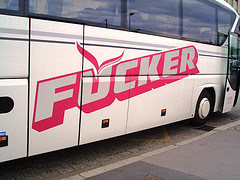
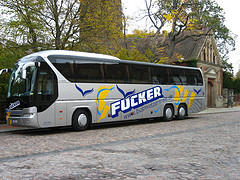
Yesterday I speculated that Lamers Bus Lines was the most disproportionately photographed, unintentionally insulting, bus line name on the Internet. Apparently not. Several readers pointed out that, while a Flickr search for lamers bus returns 81 photographs, a search for f cker bus and fucker bus return a combined 84 photos not unlike these. With Lamers, PUTA, F cker, SCAT, and the SLUT, I'm beginning to wonder if something very fundamentally wrong with the way human society is choosing the names for its mass transit systems.

Steve Kemp: I don't shut up, I grow up

Recently I took stock of my Javascript programming efforts, with the intention of simplifying things. To date I've put together three sites which make use of Javascript:
debian-administration.org
There isn't very much javascript in use upon this site, and you might be forgiven for thinking there was none at all if you don't have an account, or don't login. There's a tagging system which is starting to creak under the sheer number of different tags, and several back-end parts of the site make use of AJAX calls. Most of the script lives in a single file common.js which I cobbled via a process of trial and error, augmented with a little copy & paste coding. It works. But I knew I could do better ..
ctrl-alt-date
This was my first attempt to make a site be truely dynamic and "pretty". It has succeeded in that respect, although the lack of members makes the site itself essentially a failure. This time round I decided that I'd utterly refuse to write my own Javascript. So instead I used script.aculo.us (damn I hate those ugly URLS). This library made it almost too easy to add flash. I liked it a lot. Having said that though the sheer scope of the library and the way it didn't fit in the way that I coded made it painful to use at times. It works, and it works well. Like it? Yes. Love it no?
mail-scanning.com
This site has a fair amount of javascript upon it, but that isn't obvious unless you're actually a user. The only piece that I can recall is the real-time count of spam caught upon the front-page. (Realtime stats are cool!) Most of the code here is the simple kind, reverting back to the way I worked on the Debian Administration site; we're talking about basic effects such as:
  • show/hide a div
  • make an AJAX request every now and again.
  • Do a bit of auto-completion.
To get more of a feel for whats out there I wrote this initially with my own code, then later migrated it to jQuery. Quite frankly jQuery rocks. The way it works is a little strange at first, but it is so natural after a while. As an example:
// find the div called "foo" - hide it.
$("#foo").hide()
I'm liking this library a lot recently, but only time will tell if I use it more.
In conclusion I filed #473125: ITP jQuery failing to see the existing ITP already present. Once the package makes it through the NEW queue I will update it to follow the skeletal javascript-policy. I disagree about the naming scheme suggested by that policy primarily because we already have packages of several of the "big" javascript libraries, such as scriptalicious, and see no gain in renaming them. But otherwise the policy is sane enough; following it will cause no harm at the very least. ObQuote: Stand By Me

Eric Warmenhoven: Rewriting as a learning tool

So a year and a half ago, I mentioned I was trying to learn Haskell, and I still am. It’s been going much more slowly than I hoped, since I haven’t really spent any time on it. I never write anything new anymore! So I decided to rewrite something I had previously written myself, need be damned. So I chose the RSS aggregator I wrote, harsh. harsh hasn’t changed in eleven months (and that change was just about making the location of its configuration file configurable), but I still remembered how it worked pretty closely; at least enough that I didn’t have to really go searching through its code too much. That’s probably also a function of how small harsh is; in terms of lines of code (excluding blank lines):
  config.c: 139
  cookie.c: 221
 display.c: 709
    feed.c: 577
    list.c: 96
    list.h: 16
    main.c: 96
    main.h: 84
     md5.c: 360
     md5.h: 76
     rss.c: 120
     xml.c: 276
     xml.h: 17
     total: 2787
It uses expat to parse the HTML, libnbio for socket management (which is available in Debian), and ncurses for the UI. It doesn’t have any sort of threading (libnbio does a good job of making sure that, other than DNS lookups, there’s never anything going on long enough to prevent responsiveness). About its only feature is that it will use my cookies.txt file, so that I can see my LiveJournal friends’ protected entries. I originally wrote harsh in about a day or two. It was really easy because of the 2800 lines, about 850 of them had been written in some of my other projects (list.c/h and xml.c/h) or are standard (md5.c/h). I was also really familiar with the three helper libraries from writing grim (my IM client) and stark (a tool for viewing GnuCash data files). As a learning exercise, rewriting harsh in Haskell was excellent. It’s incredibly small, does a lot of standard things (like networking and console UI), and doesn’t do a lot of non-standard things (like an AIM client does). I got to play with the Haskell light-weight threads and STM; I learned how to create a Debian Haskell package; I learned how to use ghci as a debugger with breakpoints; and I’m much more comfortable with monads and with the language in general. It did take me significantly longer to write than the C version, though that’s more due to me having to learn not just the language but some libraries along the way (like HTTP, Vty, and HaXml). I still think that it would take me just as long to write the Haskell version as the C version, but I’m still much more comfortable with C, and imperative programming in general. From a code size perspective, the Haskell version is about one-sixth the size (excluding comments):
Config.lhs: 53
  Feed.lhs: 144
 Harsh.lhs: 272
  Util.lhs: 26
     total: 495
However, that’s not a very fair comparison. In the C version, md5.c/h are included in the total count, when really they should be considered a standard library (and on the Haskell side, I used Data.Hash.MD5 from MissingH). On the C side, I did all of the HTTP request and response processing myself (which is what more than half of feed.c is about), while on the Haskell side I left that to an HTTP client library. Excluding all those things though, the Haskell version is still about one-fourth the size. Anyway, I put the Haskell version of harsh up here. If any Haskell hackers out there could take a look at it and let me know what I’m doing wrong or oddly, I’d appreciate it.

Marc 'Zugschlus' Haber: Does Debian need the local host name in /etc/hosts for IPv6?

Exim has the habit of trying to find out about its host names and IP addresses when it starts up. This has, in the past, been an issue for the Debian packages, since a Debian system might be on a dial-on-demand modem line with expensive costs and thus should not do unnecessary DNS lookup when the MTA is started. This article tries to describe the issue and which countermeasures debian took, and asks for tips how to solve this in the case of IPv6, where our past measures unfortunately do not directly apply. I’d like to solicit opinions from people who are more experienced than me with Unix, the local resolver library including /etc/hosts and /etc/nsswitch.conf, DNS, and - especially - the customs that apply on a system running IPv6. To avoid the extra DNS lookups, the Exim packages have a Debconf option to configure exim for “minimal DNS usage”, which hardcodes the hostname into Exim’s configuration at package configuration time. This was necessary since - without this option - exim looks up its own host name in the DNS even when a completely local operation is invoked. In some cases, exim still looks up its IP address when a listening daemon starts up. This is why the Debian installer configures 127.0.1.1 (not 127.0.0.1) for the local hostname on installation, yielding /etc/hosts files like
127.0.0.1       localhost
127.0.1.1       myfoo.localdomain   myfoo
# The following lines are desirable for IPv6 capable hosts
::1     ip6-localhost ip6-loopback
fe00::0 ip6-localnet
ff00::0 ip6-mcastprefix
ff02::1 ip6-allnodes
ff02::2 ip6-allrouters
ff02::3 ip6-allhosts
However, in the last few weeks I have heard a few cases where exim does IPv6 AAAA lookups when a listening daemon starts up. An strace shows a gethostbyname2 call for AF_INET6, and if we want to continue the line we went in the past, we’d need an IPv6 address for myfoo.localdomain in /etc/hosts as well. I am now wondering how this could be implemented. In IPv4, we have 127.0.0.0/8 available for the local host and could arbitrarily choose 127.0.1.1 to configure the local host name on. In IPv6, there is only ::1, which is a single address. Would it be possible to choose an arbitrary “link local” address on lo, the loopback interface? Or is there any better way? This being said, I consider the entire 127.0.1.1 business a horrible hack which is one of the most ugly things I have ever seen. Do we have a chance to implement this in a more cleaner way, or is it still the way to go for the distribution, where we don’t know zilch about the environment where an installed system is going to be used? This issue leads to people adding their local host name to ::1 in /etc/hosts, which might re-introduce other issues that we experienced in a phase when we did the same for 127.0.0.1, eventually ending up with 127.0.1.1, or to disabling IPv6 altogether, which is a bad thing in a time where IPv6 should be enabled, not disabled. So I’d like to find a clean solution which could then be implemented in whatever part of Debian might be responsible. I tried asking this question in other places, including Usenet, before pestering my Blog to ask the Lazyweb, but obviously the people I asked before do not care for the special environment that a Linux distribution has to take care of. The only answers I got were like “that would be the local administrator’s task to fix” and “this should be taken care of in the local DNS server/setup (maybe even on the local box being installed)”. A quite frustrating experience.

David Pashley: Daylight Saving under Debian

Unfortunately I live in the UK, where 6 months of the year, the time is GMT. Now is the time of year when I discover which of my servers don't have the right timezone configuration and show the wrong time during daylight saving. For future reference, here's how to set the timezone to Europe/London rather than UTC.
root@cms01:/tmp/openssl-0.9.8g# date
Mon Mar 31 08:23:35 GMT 2008
root@cms01:/tmp/openssl-0.9.8g# tzconfig
Your current time zone is set to GMT
Do you want to change that? [n]: y
Please enter the number of the geographic area in which you live:
   1) Africa         7) Australia
   2) America        8) Europe
   3) US time zones     9) Indian Ocean
   4) Canada time zones    10) Pacific Ocean
   5) Asia           11) Use System V style time zones
   6) Atlantic Ocean    12) None of the above
Then you will be shown a list of cities which represent the time zone
in which they are located. You should choose a city in your time zone.
Number: 8
Amsterdam Andorra Athens Belfast Belgrade Berlin Bratislava Brussels
Bucharest Budapest Chisinau Copenhagen Dublin Gibraltar Guernsey Helsinki
Isle_of_Man Istanbul Jersey Kaliningrad Kiev Lisbon Ljubljana London
Luxembourg Madrid Malta Mariehamn Minsk Monaco Moscow Nicosia Oslo Paris
Podgorica Prague Riga Rome Samara San_Marino Sarajevo Simferopol Skopje
Sofia Stockholm Tallinn Tirane Tiraspol Uzhgorod Vaduz Vatican Vienna
Vilnius Volgograd Warsaw Zagreb Zaporozhye Zurich
Please enter the name of one of these cities or zones
You just need to type enough letters to resolve ambiguities
Press Enter to view all of them again
Name: [] London
Your default time zone is set to 'Europe/London'.
Local time is now:      Mon Mar 31 09:23:48 BST 2008.
Universal Time is now:  Mon Mar 31 08:23:48 UTC 2008.
More information is available in the Debian System Administrator Manual.
Read Comments (1)

Meike Reichle: Yay, I'm through

Since yesterday I am through with my NM procedure. Looking back I get to the same conclusion as probably most NMs have: not overly hard, but time-consuming and glad to have it over with. Anyway, so far so good, just waiting for DAM approval and my account now. There are still a couple of people in front of me but I hope for another processing before the elections close. (I guess it would at least be good for the turnout.) For now, many thanks to my Application Manager Andreas Barth who has been very responsive and always answered my mails quickly and thoroughly, and also to Martin Zobel-Helas for advocating me.

30 March 2008

Neil Williams: deb-gview, dpkg and emdebian-tools

OK, been quiet for a few days, at least on the blog, but in accordance with typical behaviour (for me at least) a quiet blog means a lot of things going on elsewhere. The smallest was a fix for deb-gview - combining a fix for opening files in the current working directory with a fix for the imminent dpkg 1.14.17 which modified the .changes file format a bit. That was relatively easy and I've uploaded 0.2.1 to unstable. gvfs hasn't made testing yet so there's no point in waiting for deb-gview to migrate before 0.2.1.
The largest change? Depends how you define large:
  1. Large number of changes to package files - emdebian-tools 1.0.0
  2. Large effect on Emdebian workload - dpkg 1.14.17

dpkg
dpkg bugs closed - emdebian-tools 1.0.0 pending - dpkg-shlibdeps is now able to look into directories containing libraries used by cross-built binaries provided that the right environment variable are set. Closes: #453267. dpkg-buildpackage will set PKG_CONFIG_LIBDIR (but not override an existing value) in case of cross-compilation so that pkgconfig finds .pc files in the directory specific to the target architecture. Closes: #439979.
These two changes will have a major effect on the overall workload required within Emdebian and give us a sane cross-building environment in Lenny which is ABSOLUTELY $^ @&*! FANTASTIC. :-) Currently, 1.14.17 is in experimental but I've installed it on my system for testing purposes so that I can complete emdebian-tools 1.0.0:
emdebian-tools 1.0.0
Now here, I'm making some progress. A bug has been bothering me for some time with how emdebian-tools needs a Debian primary mirror to calculate various dependency information and other apt cache stuff whilst taking into account the host architecture. Simon and I now think that we can do the dependency stuff with a continually updated dpkg-cross repository and I can use libcache-apt-perl for the rest. So whereas dpkg-cross might still exist into Lenny, it is looking like apt-cross might not - at least not as an application. However, I'm not taking that step with emdebian-tools just yet. In the meantime, I'm simply using debconf to replace the automated selection of a Debian Primary Mirror and passing that mirror to apt-cross - something I should probably have setup a while ago.
As well as that bug fix, I've added a check to emchain so that users are warned if they don't actually need to run it, added the mirror support to the various scripts and removed the workarounds now fixed by dpkg.
'dpkg-buildpackage -a' is usable for nearly all packages once you have dpkg-dev >= 1.14.7. emdebuild >= 1.0.0 is only necessary IF:
  1. You want to modify/update Emdebian patches (not just apply them) - i.e. if you have commit access to Emdebian SVN.

  2. You need the one remaining wrapper: 'X-Build-Cross-Libtool: yes' which is my next main target. This is a package-specific problem and each incidence needs a package-specific solution via an appropriate patch. As such, the wrapper is likely to stay in place in emdebuild for some considerable time - at least until someone can rebuild the entire archive with a test that can identify which packages are still affected.

  3. You want the build checks currently implemented by emdebuild but which I plan to spin out during the life of emdebian-tools 1.x. I want to standardise those build checks and abstract them into possibly a lintian-compatible check set.

Also, there should now be no need for any wrapper scripts that anyone may have devised to mangle LD_LIBRARY_PATH or PKG_CONFIG_LIBDIR - indeed,
explicit support for these within dpkg means that it is to be considered harmful from now on to touch these variables, except possibly in some specific corner cases.

29 March 2008

Enrico Zini: OpenStreetMap party at Kaohsiung, Taiwan

OpenStreetMap party at Kaohsiung, Taiwan Apparently, yesterday we had the first OpenStreetMap event in Taiwan! We met in a caf /restaurant equipped with power plug, wireless network and overhead projector and we had a bit of an introduction, chat and lunch. Then we split in groups and exploited the fact that the newly built underground (KMRT) system is still free of charge, to spread around and map around the stations. Finally, we reconvened at someone's house to see how to put the data together, draw roads, tag and upload. Highlights of the day: Technical bits: Issues to address:

28 March 2008

William Pitcock: New server :

If you noticed, a lot of services I run were offline last night. This is because either Supermicro or Micron sucks (I haven’t decided which), and the motherboard of that server got fried. Luckily, it’s nice replacement was also ready on the same evening. So, everything is restored from backups. If I missed something, please let me know about it. On another note, the replacement has AMD Opterons and a much larger RAM capacity. 16 slots!

John Goerzen: A Realistic View of the Economy

Yesterday, I read an article on CNN called From $70K to food bank.

It describes a woman who was laid off in February from a job paying $70,000 a year. "Weeks later", with bills "piling up and in need of food for her family", she went to a food bank.

The article proceeds to talk about the subprime lending situation at great length, which is largely irrelevant to this person's situation.

Then we learn she applied for food stamps, but was denied. There's a quote from this person about how frustrating that was, and general "tugging at the heartstrings" trying to make us feel sorry for this woman with two children whose mother moved in to help make the house payment. It seems to me that this is a correct decision; someone that can pay a $2500 mortgage each month ought to move into an apartment before trying to leech food or money from social service agencies.

And that's where this story gets interesting.

She has an interest-only mortgage, and is managing to pay the $2500 bill each month.

If you're not familiar with an interest-only mortgage, here's how it works. The bank loans you money to buy your house -- say, $200,000. This is a loan, and you have to pay interest on it each month, just like a regular mortgage. But with an interest-only mortgage, you never pay off the loan. You could be making monthly payments for 30 years and still owe $200,000. In general, the only ways to "pay off" this kind of loan is to sell your house, or get a conventional mortgage that pays off the interest-only loan.

Interest-only mortgages were largely banned after the Great Depression. Prior to that time, they were how mortgages normally worked. But there are several problems with them. One is that you have to pay on them forever, even after you retire. Another is that you can't move unless you can sell your house for at least as much as the bank financed, even if you've lived there for 20 years. In times of declining housing prices and unemployment, that really stinks. People often default on the loans, and from a bank's perspective, that really stinks, too.

Interest-only mortgages are usually used by banks financing construction (we had one for a few months when we renovated our farmhouse) or other short-term projects such as professional real-estate investors that buy old houses and fix them up to sell at a profit. Except for these things, in general, they should never be used for a primary house. It's not in the interest of the bank or the homeowner.

But since you never pay off the principal, the monthly payments can be lower. It seems likely that this woman took a knowing gamble, buying a home more expensive than she could afford, and somehow found a bank willing to finance this. Problem is, both she and the bank took a knowing risk. If she ever ran into financial difficulties, she'd have to sell the house quick. But now the house is probably worth less than the value of the mortgage, so selling it won't remove the loan -- BUT it would let her pay off a large part of the principal, reducing her monthly payments and giving her some wiggle-room to buy food and pay off the rest of it.

It seems to me that she is unwilling to own up to the calculated risk she took, and wants society to help bail her out. Don't get me wrong; I think we need to help people that run into hard times. We need to help make sure they still have the tools they need to find a job and a place to stay. But bailing out people that take huge financial risks shouldn't be the job of society. Let's help them land softly, but not be enablers keeping them in a home they never could -- and still can't -- afford. Fortunately, I don't think anyone in government (or running for president) is suggesting we should.

Not only that, but her bank shouldn't have ever made that loan. Banks should be held accountable to not sell unwise products to people that rely on them for their primary residences.

Here's another interesting point: in just a few weeks, she had burned through her entire savings.

This, unfortunately, is a quite typical situation for many Americans. My financial planner, and I think most experts, suggest that everyone ought to have 6 months of income in liquid non-retirement assets (savings accounts, investments, etc.) in case something like a layoff happens. Very few Americans have this.

And when it comes down to it, isn't that part of the problem? The economy thrives on consumer spending. Or, put more starkly, overconsumption. If people start saving like they ought to, and stop feeling like they're outcasts just for not keeping up with the Joneses and buying every last gadget or the biggest house, we'd all be in better shape -- but the economy wouldn't have grown as much.

The growth it would have seen, had we all been more responsible, would have been a lot more durable and recession-proof, I think.

Jos Parrella: No comments

Today we had the opportunity to be part of a very important event: Venezuela’s final meeting on DIS 29500 fast-tracking. Even though we’re working on this matter since 2007, and we weren’t approved official participation as a community, we managed to be there today. There was a strong discussion; and we had our chance to participate. I believe we were welcomed by the NB and hopefully we, as a community, can be part of future discussions in a very constructive way. Thanks again to all the committee members and our NB who made it possible for us to participate today.

From: "FONDONORMA" <...@fondonorma.org.ve>
To: <brannon@...>, <takahashi@...>, <gaillen@...>, <...@fondonorma.org.ve>
Subject: Modification to the vote on DIS 29500 - Venezuela (FONDONORMA)
Date: Fri, 28 Mar 2008 14:04:26 -0430
(snip) Venezuela wishes to modify its position on DIS 29500 (snip)
(snip) from Approval with comments to Disapproval with comments.

Decklin Foster: Section Twelve

Doing. It. Wrong.

Russell Coker: Debian SE Linux Status

At the moment I’ve got more time to work on these things than I have had for a while. I’ve got Etch support going quite well (see my post about my Etch repository [1]), the next step is to back-port some packages for AMD64 to get it working as well as i386. I’ve got an i386 Xen server for SE Linux development (which is also used for my Play Machine’s [2] DomU - so it’s definitely not for anything secret). I can give accounts and/or DomU’s to people who have a good use for them (the machine has 512M of RAM so could have 4-5 DomU’s). Currently it seems that the 2.6.24 kernel in Debian doesn’t work for Xen (at least on with an i686 CPU). I have filed bug report #472584 about it not working as a DomU [3]. This combined with the fact that according to bug report #466492 it doesn’t work as a Dom0 (which I have verified in my own tests) [4] makes the package linux-image-2.6.24-1-xen-686 unusable. Due to the inability to use 2.6.24 Xen I can’t do SE Linux development for Lenny in a DomU (Lenny tools build policy version 21 and the Etch kernel I’m using only supports policy version 20). So I have repurposed one of my servers for Lenny (unstable) development. I can give user accounts on that machine to anyone who has a good reason (and there are some people who I would give root access to if they need it). The current policy packages in Unstable are built without MCS support. This is a problem as converting between a policy which has MCS or MLS and one which doesn’t is rather painful (purge policy, reinstall policy, and reboot are all required steps). I have filed bug report #473048 with a patch for this - my patch may not actually be much good (I don’t understand some aspects of Manoj’s code) but it does achieve the desired result [5]. I won’t be making Apt repositories for such things as I expect that the changes will get into Debian fast enough. The next thing I am starting to work on is MLS support for Debian (currently it only supports the Strict and Targeted policies). See the Multilevel Security Wikipedia page for some background information on the technology [6]. I don’t expect that many people will use MLS on Debian in production environments, and it wouldn’t surprise me if no-one used it on a production server (although of course it would be impossible to prove this). But I still believe that it’s worth having for educational purposes. I am sure that there are packages in Debian of a similar size that will get less use so it’s not a waste of disk space on mirror servers! The only real down-side to adding MLS support is that it will increase the build time for the Debian SE Linux policy packages, currently they take 13 minutes to build on a 1.1GHz Celeron system (the Xen server I mentioned previously) and I expect that the machine in question will have build times greater than 20 minutes with MLS included. I will probably need to set up an Unstable DomU on a dual-core 64bit machine for the sole purpose of building policy packages. I will also have to investigate use of the “-j” option to make when building the policy to take advantage of the dual cores. I often do small tweaks to policy and it’s annoying to have to wait for any length of time for a result. The version of Coreutils that is currently in Unstable will have ls display a “+” character for every file when running SE Linux (I have filed bug report #472590) about this [7]. It is being actively discussed and at this stage it seems most likely that the functionality from Etch in this regard will be restored (which is using “+” to represent ACLs only not SE Linux contexts). It seems likely to me that I will find a few other issues of a similar nature now that I have started seriously working on Unstable. For the benefit of Debian and upstream developers who get involved in such discussions, please do not be put off if you join a discussion that is CC’d to the NSA SE Linux mailing list and have your message rejected by the list server. The code of conduct is much the same on most mailing lists, and the SE Linux list is not much different to others. The difference is that before your get your email address white-listed for posting you have to agree to the terms of service for the list. The people who run the list server appear to work more than 40 hours a week so there should not be a great delay. If anyone wants to get a message about Debian SE Linux development sent to the list without delay on a weekend then they can send it to me for forwarding. I am aware of some discussions about SE Linux and the Debian installer. I have not responded to them yet because I wanted to get some serious coding done first as an approach of “I haven’t done much coding recently but trust me I’ll fix the problems for you” might not be accepted well. I will start investigating these issues as soon as I have my Debian/Unstable server working well in enforcing mode. Update: I’ve just filed bug report #473067 with a patch to enable MLS policy builds [8].

Next.

Previous.