Search Results: "spa"

19 October 2007

Enrico Zini: filtering-planet

Filtering planet entries Here is how to setup liferea not to show me some entries in Planet Debian:
  1. Create a script that reads the rss from stdin, removes the entries you don't want and then writes the rss to stdout;
  2. From the feed properties in liferea, choose the source tab, enable the conversion filter and point that at your script.
Now you just need a simple script that filters the RSS. Here is mine:
#!/usr/bin/python
# Copyright (C) 2007 Enrico Zini <enrico@debian.org>
# This software is licensed under the therms of the GNU General Public
# License, version 2 or later.
import libxml2, re
# What links we should filter out
unwanted = re.compile(r"^(http://feed1.example.com http://feed2.example.com)")
doc = libxml2.parseFile("-")
root = doc.getRootElement()
# Create an xpath context and register the namespaces
xpc = doc.xpathNewContext()
for d in root.nsDefs():
    if d.name == None:
        xpc.xpathRegisterNs("rss", d.content)
    else:
        xpc.xpathRegisterNs(d.name, d.content)
# Remove unwanted items from the channel list
for x in xpc.xpathEval("/rdf:RDF/rss:channel/rss:items/rdf:Seq/rdf:li"):
    res = x.nsProp("resource", "http://www.w3.org/1999/02/22-rdf-syntax-ns#")
    if unwanted.match(res):
        x.unlinkNode()
        x.freeNode()
# Remove unwanted items from the item list
for x in xpc.xpathEval("/rdf:RDF/rss:item"):
    res = x.nsProp("about", "http://www.w3.org/1999/02/22-rdf-syntax-ns#")
    if unwanted.match(res):
        x.unlinkNode()
        x.freeNode()
# Serialize the result
print doc.saveFormatFile("-", True)
Now, getting to this simple script took some spitting blood. Basically, in Debian we seem to have lots of simple libraries for: I tried, in order:

Raphael Geissert: DeBaBaReTools: The de-what?

It's been a while since I wanted to post about a project I started.
But today when I read Russell Coker's post about his SE Linux repository I decided it was time to blog about DeBaBaReTools.


So, what is/are DeBaBaReTools?
is: a project which tries to unify different packages-building systems (pbuilder, buildd, etc) and different repository tools (debarchiver, reprepro, etc) in a single system by providing an incoming/ system.

are: Debian Bash-Based Repository Tools.

Or in other words:
DeBaBaReTools handles new packages by:


DeBaBaReTools is NOT a rewrite of a repository tool (like reprepro, debpool or debarchiver), neither yet an other building tool (like buildd or pbuilder). It is rather a glue between those two kind of tools.

So, how does DeBaBaReTools work?
As already said, they are a set of scripts which do all the work.
These are some of the scripts (more might be written later, they are under development):


Note that at the moment these are the only supported backends: gpgv, du, md5sums (all built in checkSums), pbuilder and reprepro.

Sounds interesting, doesn't it? :)

So, here's the magic:

The backends system
DeBaBaReTools doesn't try to re-invent the wheel, but it makes use of all the available tools so it works as less as possible.

This is where the backends take action. They are even more shell (even tough DeBaBaReTools clearly specifies they are Bash scripts they should work on any other POSIX-compatible shell) scripts which are loaded on demand and according to the user settings.

This opens a wide range of possible combinations of backends; making DeBaBaReTools work with almost anything.

The probe.sh script searches different directories for the specified backend (and will soon support user-hinted backends).

I think an example says more than a thousand words:
When needsBuild finds a package that needs to be built in a given architecture, the toBuild shell function is called. In order to provide the already said flexibility, needsBuild will at startup time call probeFile "buildQueue" which will then check several directories for the required backend (buildQueue in this case). Once it finds the given backend (backends/buildQueue/) it will check for any user hint (which will specify the real backend to be used) and then for a default one (default.sh which is a symlink to a real backend, plaintext.sh by default).

So, if somebody at some point wants to use a sqlite database to store all that information, that person would have to write a file called backends/buildQueue/sqlite.sh (or make it available in any of the include paths which can be extended via the EXTRA_PROBE_DIRS env variable) and either set a user hint or make default.sh point to it.
The sqlite.sh script can then call any external tools (or even more scripts) to insert the information in the database, read it and more.

I know this is a lot of blahblahblah but no single line of code is shown.
I've already requested an alioth project but it was denied because the package isn't already in the Debian archive.
If you are a DD and you think this sounds like a good project please contact the Alioth admins and convince them to create a project account for DeBaBaReTools.
Once created, many other people will be able to work on it and make it work with virtually any tool.

Any kind of feedback is very welcomed but I hope they are constructive ideas.

Why did I start this crazy project?
Because AFAIR only dak is able to do such job but I think dak is just too complex for a simple system to manage an a repository with an incoming system. And AFAIK there's no script which is able to do this job besides dak.

I hope this post makes sense because I don't want to review it again (I'm tired) :)

:bye: all

18 October 2007

Isaac Clerencia: aKademy-es

I love traveling but I have to concede that having aKademy-es in my own city (and five minutes away from my home) is quite convenient :) It will be great to meet again with the Spanish KDE crew. As Albert said, we’ll have talks, coding and party, and as a local I’ll try to make sure the latter is properly taken care of :P See you here!

17 October 2007

Russell Coker: Lazyweb Posts

A common practice in the blog space is to write posts that ask a question in the hope that someone else will answer it via a comment or a post. This is known as a “Lazyweb Post”. It seems to me that the way of managing such posts could be improved with a little informal cooperation. From now on I plan to tag each Lazyweb post with a Lazyweb Tag, now any reader of my blog can with a single click see all the unanswered lazyweb posts that I have written (I will remove the tag once an adequate answer has been provided or I have discovered and documented the solution myself). Almost all bloggers want to get more traffic to their blogs, the question is how to get traffic of the nature that you desire. Links from blogs that you like are a preferred source of traffic. If a blogger that you would like to receive a link from has a lazyweb tag or category then it provides a good list of ideas for post topics that will get you the links you desire. Such lists would also be good for determining what information is not generally available and which therefore can be used for the topics of original posts. Such tags or categories should also be good for getting answers to lazyweb posts. I’ll start doing this and see how well it takes off.

Adeodato Sim : The joy of libraries, and more

I’m reading Lo raro es vivir by Carmen Mart n Gaite, borrowed from the Library of my University. Somebody decided to amend this copy of the book with sundry fixes to the author’s grammar and spelling. Except that, of course, none are needed, and whoever made these changes can’t actually read (confusing unusual but valid constructs with not valid grammar), and doesn’t seem to have a clue of what an alternate spelling is, either. Joy. But maybe this post is only an excuse to recommend The Orphanage, this year’s Spain’s submission to the Best Foreign Language Film Category (which I really enjoyed!), and to point to Urban Dictionary re today’s xkcd.

Miriam Ruiz: OSI approves two Microsoft licenses as Open Source

The Open Source Iniciative (OSI) has approved two Microsoft license submissions: The Microsoft Public License (Ms-PL) and the Microsoft Reciprocal License (Ms-RL). The Open Source Definition was written after Debian Free Software Guidelines, also by Bruce Perens, and they have a lot in common. What is Hasefroch pretending with this movement? It’s not that I trust them too much, so I just don’t think they won’t have a hidden intention, but then again, they might not have it this time, who knows. It might be just a marketing show, having two OSI approved licenses, but not using them to release any significant code, or maybe they’re discovering that Open Source/Free and Proprietary Software are not exclusive and each of them might have its space. Or maybe… it was “Embrace, extend and extinguish“, wasn’t it? I’ve had a look at the licenses, and apart from some patent-related provisions, I don’t see anything in them that could make them non-DFSG-free, anyway. The difference between them is that the Microsoft Reciprocal License (Ms-RL) has a clause stating that you should release your modifications under the same license. Lets see what the future provides.

Frans Pop: Keeping threads

I currently follow a few Debian mailing lists by scanning the list archives instead of being subscribed. I find that makes it a lot easier to not read everything and to resist the temptation to reply. I've also started following the linux-kernel mailing list, which has anywhere between 100 and 600 posts per day (and next to no spam). First through the archives at lkml.org; later I tried subscribing but that resulted in drowning in mail and some issues with the "ignore/watch threads" option in kmail made me unsubscribe again after a few days. I ended up subscribing to the linux.kernel news group instead, which works well as it's quite easy to tag threads 'ignore' and filter out ignored threads. In both cases the problem was that sometimes you do want to reply to a post, but how to do that without breaking the thread? My news reader is not smart enough that I can tell it to use the original mail headers, and for the list archives a solution is even less obvious. So I wrote a little script that allows me to just paste the subject and headers of a post directly from the Debian list archives. For the kernel list I configured my news reader to display some of the original mail headers, so I can also just paste those. The script will then parse the pasted info and generate correct Subject, To, CC, In-reply-To and References headers. With a few extra lines of code it even generates correct replies to bug reports. After that the script just calls 'mail' with the correct options which asks me to type/paste the body of the mail. Problem solved. So, just in case D-I colleagues were wondering if maybe I'd resubscribed to the d-boot list, the answer is "no".

Russell Coker: Insider Threats and Small Storage Devices

Danny Angus writes about the potential threat posed by small storage devices with large capacity [1]. His post was prompted by a BBC article about Hitachi’s plans for new hard drives [2], they are aiming for 4TB of data on a single drive by 2011 and a 1TB laptop drive. One thing I noticed about the article is that they made the false claim that current drives are limited to 1TB, the storage capacity is determined by the total surface area which is proportional to the square of the radius and the height of the drive (AFAIK there are no practical limits to the number of platters apart from the height of the drive). So if a 5.25 inch hard drive was to be manufactured with today’s technology it should get a capacity equivalent to at least three times the capacity of the larger 3.5 inch drive. The reason that 5.25 inch drives are not manufactured is that for best performance you want multiple spindles so that multiple operations can be performed concurrently. Using 3.5 inch drives in servers allows the use of more disks for the same amount of space in the rack and the same amount of power. The latest trend is towards 2.5 inch (Small Form Factor AKA SFF) disks for servers to allow more drives for better performance. With 3.5 inch disks a 1U system was limited to 3 disks and a 2U system was often limited to 4 or 5 disks. But with 2.5 inch drives a 2U server can have 10 drives or more. I know of one hardware vendor that plans to entirely cease using 3.5 inch drives and claims that 2.5 inch disks will give better performance, capacity, and power use! In regard to Danny’s claim (which is entirely correct) about the threat posed by insiders. I don’t believe that a laptop with 1TB of capacity is the threat. In a server room people notice where laptops get connected and there are often strictly enforced policies about connecting machines that don’t belong to the company. I believe that the greatest threat is posed by USB flash devices. For example let’s consider a database with customer name (~20B), birth-date (10B), address (~80B), phone number (~12B), card type (1B), card number (16B), card expiry (5B), and card CVV code (3B). That’s ~155 bytes per record in CSV or TSV format. If you have data for a million customers that’s 155M uncompressed and probably about 50M when compressed with gzip or WinZip (depending on which platform is being ripped). No-one even sells a USB flash device that is smaller than 50M, I recently bought a 2G flash device that was physically very small and cheap (it was in the bargain bin). The next issue is, what data might be worth stealing that is large enough to not fit on a USB device? I guess that if you want to copy entire network file shares from a corporation then you would need more than the 16G that seems to be the maximum capacity of a USB device at the moment. Another theoretical possibility would be to copy the entire mail spool of a medium to large ISP. For the case of a corporate file server you could probably get the data at reasonable speed, 1TB of data would take 10,000 seconds or 2.8 hours to transfer at gigabit Ethernet speeds (if you max out a GigE link - it could be as much as five times that if the network is congested or if the server is slow). It’s doable, but it would be a rather tense three or more hours waiting by an illegally connected laptop. For the mail server of a large ISP there is often no chance of getting anywhere near line speed, it’s lots of small reads and seek performance is the bottleneck, such servers are usually running close to capacity (and trying to copy data fast would hurt performance and draw unwanted attention). Another possibility might be to copy the storage of an Intranet search device. If a company has a Google appliance or similar device indexing much of their secret data then copying the indexes would be very useful. It would allow offline searches of the corporate data to prepare a list of files to retrieve later. It would probably be more useful to get online access to the data from a remote site. I expect that an unethical person could sell remote access to someone who is out of range of extradition. All that would be required would be to intentionally leave a flaw in the security of the system. In most large corporations this could be done in a way that is impossible to prove. For example if management decrees that the Internet servers run some software that is known to be of low quality then a hostile insider could make configuration changes to increase the risk - it would look like an innocent mistake if the problem was ever discovered (the blame would entirely go to the buggy software and the person who recommended it). A large part of the solution to this problem is to hire good employees. The common checks performed grudgingly by financial companies are grossly inadequate for this. Checking whether a potential employee has a criminal record does not prevent hiring criminals, it merely prevents hiring unsuccessful criminals and people who have not yet been tempted enough! The best way to assess whether HR people are being smart about this is to ask them for an estimate of how many criminals are employed by the company. If you have a company that’s not incredibly small then it’s inevitable that some criminals will be employed. Anyone who thinks that it is possible to avoid hiring criminals simply isn’t thinking about the issues. I may write more about this issue in a future post. Another significant part of the solution to the problem is to grant minimum privileges to access data. Everyone should only be granted access to data that they need for their work so that the only people who can really compromise the company are senior managers and sys-admins, and for best security different departments or groups should have different sys-admin teams and separate server rooms. Of course this does increase the cost of doing business, and probably most managers would rather have it be cheap than secure.

16 October 2007

MJ Ray: Spam from Gofernet

Gofernet.net 466395 (or is it gofernet.co.uk? They seemed confused about that - maybe it's Jekyll and Hyde, one spammy, one not?) of Sutton Coldfield spammed an associate on 5 Oct 2007. The spam claimed it was sent to their client list. That associate is not and has never been a client of gofernet. The spam claimed to be "in full compliance with the Privacy and Electronic Commerce Statutory Instrument 2003, No 2426". I think they mean the the Privacy and Electronic Communications (EC Directive) Regulations 2003, which usually forbids
"unsolicited communications for the purposes of direct marketing by means of electronic mail unless the recipient of the electronic mail has previously notified the sender that he consents for the time being to such communications being sent by, or at the instigation of, the sender."
Gofernet don't have consent and none of the exceptions apply AFAICS. So it's spam, even by their standards.

Biella Coleman: Topics in Digital Media

Next semester I am teaching one (yay one) course and it is a graduate course on digital media. This is the description I have so far and I will post the tentative syllabus in the next few week.
Computers, especially in their networked dimension, have sparked a series of ethical, political, and social debates that often revolve around a series of stark and connected dualities: control and freedom; pleasure and exploitation; creativity and constraint. In this course we will approach topics in digital media via an historical angle that squarely addresses these dualities. To this end, we will often cross-cut readings on similar topics and material whose conclusion about the nature of computing will often vary considerably. The goal, however, is not to determine the correct or right side of these dualities but have students come away with a firm understanding of the following: 1) the history of computing and networking in light of the ways the authors as well as technologists/inventors construct or understand these dualities; 2) the various sources technological, social, and political that may shape or drive any of these elements; 3) unpack the political and social relationships, if any, between them and the stakes involved in how these authors represent the nature of computing and networking. The course primarily concentrates on computers and networks and is roughly chronological, starting with the first digital computers and ending with our digital present. Particular topics we address are: cybernetics and liberalism; networks and the cold war; personal computers and online communities; hackers, the free software movement and intellectual property; labor, development, and computers; peer-to-peer knowledge production; computer gaming; and counter-globalization and computer networking.

MJ Ray: the Cooperative Group Half-Yearly Meeting

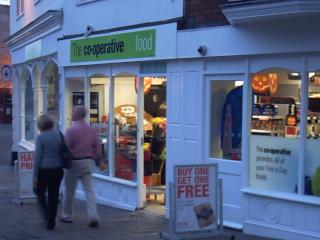
I attended my first half-yearly meeting as a member of the co-operative group yesterday evening at 7pm. The event for the strangely-named Kennet and Avon area was held at Jury's Hotel near Queen Square, which is a part of Bristol I've not visited for a while, so I got there a bit early to find it. the co-operative food, The Centre, Bristol I found it easily, which gave me a few minutes spare to visit the co-operative food store on the Centre (pictured), which is the first rebranded one I've seen. It looks light and airy and the staff were friendly. I didn't find everything I was looking for, but after exiting, I noticed I'd not seen around the corner of the L-shaped store! Anyway, the meeting itself was chaired by Peter Begley and was attended by six elected reps, three regional officers, four trading managers (all food?) and about 50 members by my reckoning. There was a comment later in the meeting about the low turnout from Bath - it seems that a meeting for each city had been requested and refused. There was also a comment about lack of transport from Weston-super-Mare, about which I'm not sure: trains between WsM and Bristol are at least hourly. Maybe there should be a shuttle between station and meeting for people who can't walk, but it seems nuts to run a bus from here when trains are faster and have space. Officer Chris Griffiths gave a presentation (with loud music!) about our community support, including windfarms on the co-operative farms, Farm to Fork, the Woodcraft Folk, the Queens Award for Sustainable Development, community chef visits to Ilfracombe and Bath, community challenge, Mukti Mitchell's Low Carbon Lifestyle Tour, Fairtrade fashion shows, Holyland Handicrafts Co-operative at Bath Christmas Market, BAND (D is for Daycare, but I missed the rest), Toy Box Library Bath, Avonmouth Community Centre Association and Oldfield Park Juniors. Frank Jones presented the business interim report, noting that the group has a 2.2% increase of revenue before reinsurance premiums, but the bad weather has hit the insurance arm, reducing the overall profit. Nevertheless, we still paid a total of 38 million pounds to and on behalf of members. The closure of WsM Dolphin Square and the gain of the co-operative pharmacy in Milton were mentioned in passing. There was a short presentation about the constitutional review. The first members' consultation ends on 26 October, so send in your comments soon. There was particular concern about some multi-thousand-pound payments to elected representatives who stand down. Then came member questions, which I'll describe in another post, approval of past minutes, reports of the local co-operative party (success in Bath+NES, 8 councillors in Bristol, loss of 2 councillors in N.Somerset) and presentations to Frank Jones and Simon Crew of 10-year elected service awards. The meeting closed at 9pm.

Neil Williams: A little humour from dpkg

This arises from upgrading a cross-built package where the prerm maintainer script wanted to use install-info and as Emdebian doesn't use info or man pages, the prerm script failed. I'd already removed the same from postinst but got this little comment from dpkg when I installed an upgraded package on the Balloon3 ARM board:
dpkg: warning - old pre-removal script returned error exit status 127
dpkg - trying script from the new package instead ...
dpkg: ... it looks like that went OK.

Nice trick!

Emdebian postinst patch.

This is the full apt output:

/ # apt-get upgrade
Reading package lists... Done
Building dependency tree
Reading state information... Done
The following packages have been kept back:
apt
The following packages will be upgraded:
busybox libreadline5 readline-common
3 upgraded, 0 newly installed, 0 to remove and 1 not upgraded.
Need to get 563kB of archives.
After unpacking 12.3kB disk space will be freed.
Do you want to continue [Y/n]?
Get:1 http://buildd.emdebian.org unstable/main readline-common 5.2-3em3 [1882B]
Get:2 http://buildd.emdebian.org unstable/main libreadline5 5.2-3em3 [249kB]
Get:3 http://buildd.emdebian.org unstable/main busybox 1:1.1.3-5em2 [312kB]
Fetched 563kB in 7s (70.5kB/s)
(Reading database ... 489 files and directories currently installed.)
Preparing to replace readline-common 5.2-3em2 (using .../readline-common_5.2-3em3_all.deb) ...
/var/lib/dpkg/info/readline-common.prerm: /var/lib/dpkg/info/readline-common.prerm: 3: install-info: not found
dpkg: warning - old pre-removal script returned error exit status 127
dpkg - trying script from the new package instead ...
dpkg: ... it looks like that went OK.
Unpacking replacement readline-common ...
Preparing to replace libreadline5 5.2-3em2 (using .../libreadline5_5.2-3em3_arm.deb) ...
Unpacking replacement libreadline5 ...
Preparing to replace busybox 1:1.1.3-5em1 (using .../busybox_1%3a1.1.3-5em2_arm.deb) ...
Unpacking replacement busybox ...
Setting up readline-common (5.2-3em3) ...
Setting up libreadline5 (5.2-3em3) ...
Setting up busybox (1:1.1.3-5em2) ...

This is inside a chroot on the Balloon3 board using cross-built packages from the Emdebian target repository. The chroot was created with the 'emsandbox' utility from emdebian-tools 0.4.1 (due for upload to Emdebian tonight) and a little manual help. A few more tweaks to the relevant packages are needed before the chroot (and therefore a root filesystem for Emdebian) can be installed without assistance.

MJ Ray: Stuttering through comment spam

I get too much spam and some of it isn't obvious from the subject line, particularly if it's a blog comment, so I use the following script to read the suspicious emails and pause at the bottom of each mail. It takes two optional parameters, explained in the comments below. Please comment on any obvious improvements to this quick hack.
#!/usr/bin/mzscheme -qr
(let ((c (or (and (> (vector-length argv) 0)
                  (string->number (vector-ref argv 0)))
             1)) ; first arg is how long to pause in seconds, default 1
      (re (or (and (> (vector-length argv) 1)
                   (regexp (vector-ref argv 1)))
              (regexp "^From [^ ]*@"))) ; second arg is regexp to pause at
      (i #f))
  (let loop ((l (read-line)))
    (if (regexp-match re l) (if i (sleep c) (set! i #t)))
    (write-string l) (newline)
    (if (not (eof-object? (peek-char))) (loop (read-line)))))
(exit)
;
#!/usr/bin/perl
# An earlier version in perl
$c = ($ARGV[0] 1); # How long to pause, in seconds
$re = ($ARGV[1] '^From [^ ]*@'); # What to pause on
$i = 0;
while (<STDIN>)  
  if (/$re/)   if ($i)   sleep ($c)   $i=1;  
  print $_;
 

Alastair McKinstry: The Curse of Oil

Jaldhar Vyas points to the rogues gallery of oil producing states and argues that Neoconservatism is good, well at least it gets rid of the dictators such as Saddam Hussein while it grabs the oil. As he ightly points out, we are researching new alternative energy sources, and just as importantly (or even more importantly) energy conservation. But we have been doing this for decades. Sooner or later we have to realize that the "Oil Crisis" isn't due to a shortage of energy sources: its due to deliberate politics to make us dependent on oil. Peak Oil is "only" a crisis for us consumers, dependent on oil to drive our cars, heat our houses, and supply our food. For oil companies, it means (1) they are shipping oil at a greater rate than ever before, (2) at higher demand than ever before, and (3) in circumstances where pesky politics like OPEC can't interfere and try and moderate the price down (I'm not arguing OPEC or cartels are good; its just that its long-term 'maximize the benefit for the oil producing nations' strategy interferes with oil companies shorter-term profit maximization). For the Oil Companies, its a good thing. In this context we have to see our current dependence on oil as the result of deliberate policy by the oil companies. The small filip that USanian governments have done towards alternative energy, such as funding Hydrogen fuel-cell research, nuclear power, etc. are so long-term, and so small in scale, that they have to be seen as deliberately not solving the problem. Thinking that research into alternative sources is good is gpoing to save us (disclaimer: as a scientist I think research is a good thing :-)) is missing the real problem. Its politics: the oil companies have simply been better at politics than the strugging alternatives; we need to recognize this, and fight for alternatives. When oil prices reach $100/barrel, and we struggle to pay rising food and energy bills, its because other have deliberately caused the crisis. Oil has often been called a Curse because of the effects 'Oil Wealth' have caused so many countries. They are not co-incidentally dictatorships; Saddam Hussein remained in power in Iraq for so long because it benefitted the West (see the weapons supplies to Iraq in the so-called "Iran-Contra" affair, for example). Ditto Saudi Arabia, remaining 'friends' of the USA despite its ties to 911. Overthrowing Saddam Hussein was about consolidating even more power in the Gulf than America had previously, not democracy. What was planned for Iraq was democracy in name only: all real power was already neutralised, with decisions to US benefit cemented in place before the parliament met: non-negotiable contracts already signed giving US companies control. This is straight imperialism, and cannot be considered democracy or a good thing. Tags , ,

Marc 'Zugschlus' Haber: A thousand things I never wanted to know about X

In the last few days, I have replaced the two 20 inch CRT monitors that I have hardly used the last years with two 20 inch TFT displays, and my company (finally) gave me a 19 inch TFT display to accompany my notebook display at work. Maybe I should take that as a hint that they want to see me in the office more frequently rather than in my home office which I generously use these days. At home, I built a “new” computer from mainly used parts to drive the two 20 inchers. I have learned a lot about X in the last days, but spent too much time with it. I have been running my Desktop with older X and two CRTs for quite some time, but I hardly ever used it due to the setup of my now ex-flat. Back then, I learned that the “two monitors, one display, one screen, one desktop” option of X was called Xinerama and statically configured: You write down your display layout in xorg.conf and it uses it. Configuration changes mean restarting the X server. KDE notices Xinerama automatically, designates one monitor the “main monitor” and displays its panel there. You can move windows from one monitor to the other one, but changing virtual desktops always changes what both monitors display. This is not really what I want, since I often have “static” contents (news reader, mail reader, chat windows, help screens etc) on one monitor while I do my normal work on the other monitor, which involves changing virtual desktops. So I was rather happy when I learned upon the arrival of the external TFT display for the notebook that you can work without Xinerama. In that case, the X server comes up with one display and two screens, which KDE uses to display two independent desktops which can be independently configured, but can both be accessed with one mouse and one keyboard. For me, this means that I finally can independently change virtual desktops on both monitors, but pay the price that I cannot display a certain virtual desktop on monitor 1 now, and on monitor 2 in five minutes, and that a window opened on monitor 1 is never going to be shown on monitor 2 without serious interference. This looked ok for me. Additionally, you can use different font sizes on the different monitors as defaults, which comes in handy if both monitors are blatantly different in size (which is the case with the notebook and its external monitor). However, with that setup, KDE seems to be challenged when it comes to saving the configuration. Some things (such as desktop background and panel config) seem to save fine, desktop independent, other things (such as open windows and their position) are lost when the session exitst. My daily visit to Kevin&Kell (which used to be in a browser window that was saved with my session) has badly suffered since then. Then, a few weeks ago, somebody talked me into trying the X server from experimental. Which is when my dual-desktop setup ceased working. The nice people on #debian-x told me that Xinerama is a thing of the past, and is currently in the process of being replaced by Xrandr 1.2. The removal of “my” two monitor, two screens, two desktop setup is collateral damage, and if I still want that behavior, the X.org upstream considers this an issue to be handled by the Window Manager / Desktop Environment now. Gee, thanks. That’s what I call a regression. After spending half a day cursing and ranting, and even considering to go back to lenny’s (or even etch’s) X.org, I finally settled on going with the “new” way as I was going to lose my independent desktops sooner or later anyway. Again, with the friendly help of the people on #debian-x, I found out about a lot of advantages of the latest X servers. In most basic cases, the latest X server does not need a configuration file any more. It autodetects your hardware and chooses whatever modes it finds optimal. It does a pretty decent job in doing so. If one wants to influence how the X system comes up, once can always write an Xorg.conf file - the configfileless server even writes the “virtual config file” it uses to the log as a starting point. Additionally, almost everything regarding screen layout can be reconfigured at run time using the xrandr binary from a command line. Even a hardware change (such a new monitor plugged into the powered on notebook) is correctly detected. Cute. This allows me to reconfigure my notebook depending on where it currently is and which external monitor (or projector) is connected. This can be perfected if I find out whether X offers a hook to plug a reconfiguration script into that is called when the X server starts or when the system is waking up from standby or hibernation with the X server running. A lot to do, and great potential for elegant stuff. However, while I am talking about hibernation, this is a downside of the new driver: When the system wakes up from hibernation, the X server sometimes confuses itself enough to become nearly unuseable: I had it become psychotic when plugging in the external monitor (which can do 1600x1200 points) after waking it up from hibernation at the office. The internal display can only do 1400x1050, and the box thought that the external monitor only had 1050 y axis pixels, displaying bit garbage in the lower part of the big monitor, and showing a useable, but unintelligible panel. When opening any browser or any other application with considerable text amounts in the window, all fonts become unreadable once one scrolls down. Restarting the X server helps and everyting is fine. But I do not use hibernation to force myself to log out of X after waking up. After going back to the “one monitor mode”, the X server now thinks that my virtual desktop is 1600x1200 and only shows 1400x1050, with dead space at the right and lower side of the virtual desktop. xrandr does not allow me to reisize the FB below 1600x1200. No idea what’s going on here. In most of the cases, calling xrandr --auto for each output will fix the issues at run time, but sometimes a session restart is needed. Code needs to stabilize quite a bit before becoming useable in production. There are a few disadvantages that will remain: Both monitors will change their contents when the virtual desktop is changed, and both displays will use the same default font size (which might be inappropriate if both displays are of different size). But I think, when the issues are cleared up, that I can live with these disadvantages. The “new” desktop system that I built has a Matrox G450 dual head graphics card, and unfortunately, the Xrandr 1.2 enabled X server from experiemental has shown to be unuseable: Upon some mode changes, the X server goes into an endless loop and proves itself to be unkillable short of SIGKILL. And if it dies, it sometimes pulls the entire system with it. There is a corresponding bug in the upstream BTS, but it hasn’t received any noticeable attention by the upstream developers. So I might find myself configuring one last Xinerama config before I can finally completly migrate to Xrandr 1.2 on the desktop as well. Then I’ll probably need to bug the KDE upstream people to implement a two-desktops-on-a-single-screen feature in one of their future versions so that I can get my independent-desktop-things back. But that’s a far far away future.

Ross Burton: Mr. Handy Man

On Saturday I turned into Mr. Handy Man. Our CD collection is getting rather large (~270 CDs), and the current CD rack is filled to capacity, with a 3 foot tall tower of CDs next to it. I decided to build a new one myself, there being no decent and cheap CD racks designed for this many CDs. I measured and planned and drew, and eventually had a design for a rack nearly 6 feet high, and more than a foot wide [1]. My Dad and me went down the local timber yard, bought the pine (which they cut for us) for a mere £10, and set about building it. The building went very well. My Dad is pretty damn good at DIY so we had all of the tools we needed, and a few hours later we had our new CD rack, and Vicky had caught the sun [2]. We did have a few minor problems -- one shelf was sticking slightly out (five minutes with a chisel sorted that), and the MDF back was put on backwards, showing the huge price sticker to the world, but on the whole its a damn fine and solid CD rack, which holds a grand total of 350 CDs, for £15. We have two and bit shelves free, so have space for another 80 or so CDs... shouldn't take long to fill that. Of course, we then spend much of Sunday afternoon filling the damn thing... To celebrate we bought Solid Bronze, the Best of Beautiful South, and a Black Sunday by Cyprus Hill. [1] The exact measurements for anyone wanting to build their own: 1700mm x 370mm x 150mm, in 15mm pine.
[2] That's a polite phrase for having a pink nose and arms.

Raphael Geissert: Print before you think!

What?! I mean... Think before you print!.

It's not very uncommon to see people who always print almost every single email they receive with information (and not just a notification), pdf's, and many other kind of documents.

I've never liked when people do that because they don't just print it, they sometimes even print the whole email conversation (usually gmail users). Some of them even dare to use non-recycled paper for printing some text and trashing it away after reading it!

Today is the Blog Action Day about the environment, so all I want to say is: reconsider, reuse and recycle (yes, in that specific order :D ). I know it's not the classic reduce, reuse, recycle message because I think people should better reconsider and not only reduce.

Here's a nice reminder you can, err, use on your computer's desktop (did you think I was going to say print??, I wasn't):


If you don't like that one, Google will point you to some others.

15 October 2007

Eddy Petri&#537;or: svn-buildpackage 0.6.22 released to experimental

Thanks to Damyan Ivanov for the upload, svn-buildpackage 0.6.22 is now in experimental. The upload was done to experimental due to the big number of changes affecting it and because I wanted to get a fairly significant amount of testing of the major fixes before propagating the code to unstable.

This release should fix 15 (yes, fifteen) bugs[0], most of which were important bugs or bugs affecting usability.

The major fixes are:
Installing the package on an etch, lenny or sid system should be straight forward: just get the deb from experimental and install it (no backporting is necessary).


If you usually use svn-buildpackage, please install the experimental version and report any bugs and/or success stories. I am particularly interested in feedback related to the behaviour around .svn/deb-layout and the other methods of specifying layout information.

Please send success stories to me directly eddy.petrisor @ gmail.com. Bugs should be directed to the BTS, but I hope there will be mail just directly to me :-) .


[0] I wonder, does the thickness of the yellow area on these graphs ever decreases?
[1] as soon as the breakage would have been visible in the past

Romain Francoise: In Rainbows

Once again, PopMatters is right on. I'm amazed that after all these years, international fame and millions of records sold, Radiohead can still get together and make an album such as In Rainbows, true to their sound, intricate and emotional, powerful. Wow.

Russell Coker: Blog Copyright Infringement

I have previously written about some of my efforts to counter sploggers [1]. Since then I have had a particularly brazen splogger copy one of my posts entirely and claim to have written it. The only reason I noticed the copyright violation (my blog license is on my About Page [2]) was because the post in question linked to other posts of mine and I saw the links. I was offended by the flagrant violation of all aspects of copyright law (breaking the license and infringing my moral rights by not attributing me as the author) and by the fact that the splog in question was hosted by Dreamhost (who have offended me by refusing a DMCA take-down request). So I decided that merely issuing a DMCA take-down was not enough. I went through the splog and identified content copied from several major journals (including by a journalist I regard as a friend) as well as by one multi-national corporation - and I notified all the relevant people. The splog in question deleted all it’s old content the next day, and immediately started copying new articles from other blogs. I have informed the people who appear to be copyright holders for some of the new articles… I recommend that other people who deal with sploggers also go to the extra effort of notifying other victims. It’s usually quite easy to do you just select a random bit of text from the copied article and paste it into your favourite search engine - usually you get only a single result. Some of the splog posts are edited in small ways so the first search may fail - if so then you merely need to search for a second piece of text. If you only request that your own illegally copied material be taken down then the splogger still has a good business model. They can keep copying content in violation of the license, occasionally take a post down when they get caught, and both the splogger and the ISP continue to make money. If you notify other victims (many of which won’t have the skills to find the content themselves or the background knowledge sufficient to recognise the benefits in having it removed unless you explain it to them) then the splogger loses a lot of content at one go and the ISP will have a more difficult time claiming to be innocent of the process. Also when you notify multi-national corporations you can expect that they have some decent lawyers and a budget assigned to such work. While I would be extremely unlikely to sue an ISP that repeatedly hosts unauthorised copies of my copyright materiel the same can’t be said for a corporation. For more information on splogging see the Wikipedia entry [3].

Next.

Previous.
