Search Results: "ag"

21 September 2015

Norbert Preining: International Sad Hits Volume 1

I stumbled over this CD a few weeks ago, and immediately ordered it from some second-hand dealer in the US: International Sad Hits Volume 1: Altaic Group. Four artists from different countries (2x Japan, Korea, Turkey) and very different music style, but connected in one thing: That they don t fit into the happy-peppy culture of AKB48, JPOP, KPOP and the like, but singers and songwriters that probe the depths of sadness. With two of my favorite Japanese appearing in the list (Tomokawa Kazuki and Mikami Kan), there was no way I could not buy this CD. international-sad-hits-volume-1 The four artist combined in this excellent CD are: Fikret K z lok, a Turkish musician, singer and songwriter. Quoting from the pamphlet:
However, in 1983 K z lok returned with one of his most important and best albums: Zaman Zaman (Time to time). [ ] These albums presented an alternative to the horrible pop scene emerging in Turkey they criticized the political situation, the so-called intellectuals, and the pop stars.
The Korean artist is (Kim Doo Soo), who was the great surprise of the CD for me. The sadness and beauty that is transmitted through is music is special. The pamphlet of the CD states:
The strictness of his home atmosphere suffocated him, and in defiance against his father he dropped out, and walked along the roads. He said later that, Hatred towards the world, and the emptiness of life overwhelmed me. I lived my life with alcohol every day.
After some problems due to political crisis, and fierce reactions to his song Bohemian (included) made him disappear into the mountains for 10 years, only to return with even better music. The third artist is one of my big favorites, Tomokawa Kazuki (Official site, Wikipedia) from Japan. I have written often about Tomokawa, but found a very fitting description in the booklet:
Author Tatematsu Wahei has described Tomokawa as a man standing naked, his sensibility utterly exposed and tingling. It s an accurate response to a creativity that seems unmediated by embarrassment, voraciously feeding off the artist s personal concern.
The forth artist is again from Japan, Mikami Kan, a well known wild man from the Japanese music scene. After is debut at the Nakatsugawa All-Japan Folk Jamboree in 1971, he was something like a star for some years, but without a record deal his popularity decreased steadily.
During this period his songwriting gradually altered, becoming more dense, surreal and uncompromisingly personal.
Every song on this CD is a masterpiece by itself, but despite me being a great fan of Tomokawa, my favorite is Kim Doo Soo here, with songs that grip your heart and soul, stunningly beauty and sad at the same time.

20 September 2015

Matthew Garrett: The Internet of Incompatible Things

I have an Amazon Echo. I also have a LIFX Smart Bulb. The Echo can integrate with Philips Hue devices, letting you control your lights by voice. It has no integration with LIFX. Worse, the Echo developer program is fairly limited - while the device's built in code supports communicating with devices on your local network, the third party developer interface only allows you to make calls to remote sites[1]. It seemed like I was going to have to put up with either controlling my bedroom light by phone or actually getting out of bed to hit the switch.

Then I found this article describing the implementation of a bridge between the Echo and Belkin Wemo switches, cunningly called Fauxmo. The Echo already supports controlling Wemo switches, and the code in question simply implements enough of the Wemo API to convince the Echo that there's a bunch of Wemo switches on your network. When the Echo sends a command to them asking them to turn on or off, the code executes an arbitrary callback that integrates with whatever API you want.

This seemed like a good starting point. There's a free implementation of the LIFX bulb API called Lazylights, and with a quick bit of hacking I could use the Echo to turn my bulb on or off. But the Echo's Hue support also allows dimming of lights, and that seemed like a nice feature to have. Tcpdump showed that asking the Echo to look for Hue devices resulted in similar UPnP discovery requests to it looking for Wemo devices, so extending the Fauxmo code seemed plausible. I signed up for the Philips developer program and then discovered that the terms and conditions explicitly forbade using any information on their site to implement any kind of Hue-compatible endpoint. So that was out. Thankfully enough people have written their own Hue code at various points that I could figure out enough of the protocol by searching Github instead, and now I have a branch of Fauxmo that supports searching for LIFX bulbs and presenting them as Hues[2].

Running this on a machine on my local network is enough to keep the Echo happy, and I can now dim my bedroom light in addition to turning it on or off. But it demonstrates a somewhat awkward situation. Right now vendors have no real incentive to offer any kind of compatibility with each other. Instead they're all trying to define their own ecosystems with their own incompatible protocols with the aim of forcing users to continue buying from them. Worse, they attempt to restrict developers from implementing any kind of compatibility layers. The inevitable outcome is going to be either stacks of discarded devices speaking abandoned protocols or a cottage industry of developers writing bridge code and trying to avoid DMCA takedowns.

The dystopian future we're heading towards isn't Gibsonian giant megacorporations engaging in physical warfare, it's one where buying a new toaster means replacing all your lightbulbs or discovering that the code making your home alarm system work is now considered a copyright infringement. Is there a market where I can invest in IP lawyers?

[1] It also requires an additional phrase at the beginning of a request to indicate which third party app you want your query to go to, so it's much more clumsy to make those requests compared to using a built-in app.
[2] I only have one bulb, so as yet I haven't added any support for groups.

comment count unavailable comments

Russ Allbery: Review: Shady Characters

Review: Shady Characters, by Keith Houston
Publisher: W.W. Norton
Copyright: 2013
ISBN: 0-393-34972-1
Format: Trade paperback
Pages: 250
Subtitled The Secret Life of Punctuation, Symbols & Other Typographical Marks, Shady Characters is one of those delightfully quirky books that examines the history of something you would not normally connect to history. It's an attempt to document, and in some cases reconstruct, the history of several specific punctuation marks. If you've read and enjoyed Lynn Truss's Eats, Shoots & Leaves, this is a near-perfect complement, focusing on more obscure marks and adding in a more detailed and coherent history. Houston has some interest in the common and quotidian punctuation marks, with chapters on the hyphen, dash, and quotation mark, but he avoids giving a full-chapter treatment to the most obvious periods and commas. (Although one learns quite a bit about them as asides in other histories.) The rest of the book focuses on the newly-popular (the at symbol), the recognizable but less common (the hash mark, the asterisk and dagger symbols used for footnotes, and the ampersand), and the historical but now obscure (the pilcrow or paragraph mark, and the manicule or pointing finger). He even devotes two chapters to unsuccessful invented punctuation: the interrobang and the long, failed history of irony and sarcasm punctuation. And this is an actual history, not just a collection of anecdotes and curious facts. Houston does a great job of keeping the text light, engaging, and readable, but he's serious about his topic. There are many reproductions of ancient documents showing early forms of punctuation, several serious attempts to adjudicate between competing theories of origin, a few well-marked and tentative forays into guesswork, and an open acknowledgment of several areas where we simply don't know. Along the way, the reader gets a deeper feel for the chaos and arbitrary personal stylistic choices of the days of hand-written manuscripts and the transformation of punctuation by technology. So much of what we now use in punctuation was shaped and narrowed by the practicalities of typesetting. And then modern technology revived some punctuation, such as the now-ubiquitous at sign, or the hash mark that graces every telephone touchpad. I think my favorite part of this history was using punctuation as perspective from which to track the changing relationship between people and written material. It's striking how much early punctuation was primarily used for annotations and commentary on the text, as opposed to making the text itself more readable. Much early punctuation was added after the fact, and then slowly was incorporated into the original manuscript, first via recopying and then via intentional authorial choice. Texts started including their own pre-emptive commentary, and brought the corresponding marks along with the notes. And then printing forced a vast simplification and standardization of punctuation conventions. Full compliments to W.W. Norton, as well, for putting the time and effort into making the paper version of this book a beautiful artifact. Punctuation is displayed in red throughout when it is the focus of the text. Endnotes are properly split from footnotes, with asides and digressions presented properly at the bottom of the page, and numbered endnotes properly reserved solely for citations. There is a comprehensive index, list of figures, and a short and curated list of further readings. I'm curious how much of the typesetting care was preserved in the ebook version, and dubious that all of it would have been possible given the current state of ebook formatting. Typesetting, obscure punctuation, and this sort of popular history of something quotidian are all personal interests of mine, so it's unsurprising I found this book delightful. But it's so well-written and engaging that I can recommend it even to people less interested in those topics. The next time you're in the mood for learning more about a corner of human history that few people consider, I recommend Shady Characters to your attention. Rating: 8 out of 10

Dirk Eddelbuettel: RcppArmadillo 0.5.600.2.0

armadillo image And yet another upstream Armadillo update -- version 5.600.2 was released yesterday by Conrad. So I pushed a new and matching RcppArmadillo release 0.5.600.2.0 to CRAN and to Debian. Armadillo is a powerful and expressive C++ template library for linear algebra aiming towards a good balance between speed and ease of use with a syntax deliberately close to a Matlab. This release contains small upstream improvements:
Changes in RcppArmadillo version 0.5.600.2.0 (2015-09-19)
  • Upgraded to Armadillo 5.600.2 ("Molotov Cocktail Deluxe")
    • expanded .each_col() and .each_row() to handle out-of-place operations
    • added .each_slice() for repeated matrix operations on each slice of a cube
    • faster handling of compound expressions by join_rows() and join_cols()
Courtesy of CRANberries, there is also a diffstat report for the most recent CRAN release. As always, more detailed information is on the RcppArmadillo page. Questions, comments etc should go to the rcpp-devel mailing list off the R-Forge page.

This post by Dirk Eddelbuettel originated on his Thinking inside the box blog. Please report excessive re-aggregation in third-party for-profit settings.

Dirk Eddelbuettel: RQuantLib 0.4.1

Right before heading off to last week's excellent EARL 2015 conference in London, a new minor release of RQuantLib was released onto CRAN and into Debian. The changes are detailed below.
Changes in RQuantLib version 0.4.1 (2015-09-11)
  • Changes in RQuantLib code:
    • A simple shiny application is now included in the directory shiny/DiscountCurve/ and accessible via the new demo function ShinyDiscountCurve.
    • The option surface plotting example in arrays.R now checks for rgl by using requireNamespace.
    • The files NAMESPACE and DESCRIPTION have been updated to reflect all the suggestions of R CMD check.
    • The Travis CI tests now use binary Debian packages for all package dependencies making the tests a little faster.
Courtesy of CRANberries, there is also a diffstat report for the this release. As always, more detailed information is on the RQuantLib page. Questions, comments etc should go to the rquantlib-devel mailing list off the R-Forge page. Issue tickets can be filed at the GitHub repo.

This post by Dirk Eddelbuettel originated on his Thinking inside the box blog. Please report excessive re-aggregation in third-party for-profit settings.

Thorsten Alteholz: Package of the Day: ansiweather

While looking at NEW I sometimes see a package and think wow this is great, you have to try this . One of these packages is ansiweather. It looks at the data at openweathermap and presents them on the console. So with

ansiweather -l chemnitz -u metric

I get something like:
Current weather in Chemnitz => 12 C Wind => 2.52 m/s WNW Humidity => 80 % Pressure => 1014 hPa
Now I see that I need a coat and an umbrella for my walk. Or better I don t go outside and continue looking at other stuff in NEW :-)

Michal Čihař: Weblate 2.4

Weblate 2.4 has been released today. It comes with extended support for various file formats, extended hook scripts, better keyboard shortcuts and dozen of bug fixes. Full list of changes for 2.4: If you are upgrading from older version, please follow our upgrading instructions. You can find more information about Weblate on http://weblate.org, the code is hosted on Github. If you are curious how it looks, you can try it out on demo server. You can login there with demo account using demo password or register your own user. Weblate is also being used https://hosted.weblate.org/ as official translating service for phpMyAdmin, Gammu, Weblate itself and other projects. If you are free software project which would like to use Weblate, I'm happy to help you with set up or even host Weblate for you. Further development of Weblate would not be possible without people providing donations, thanks to everybody who have helped so far! PS: The roadmap for next release is just being prepared, you can influence this by expressing support for individual issues either by comments or by providing bounty for them.

Filed under: English phpMyAdmin SUSE Weblate 0 comments

Jonathan Dowland: Kolo ep, Dubrovnik, Dalmatia

Trsteno Trsteno (near Botanical gardens)
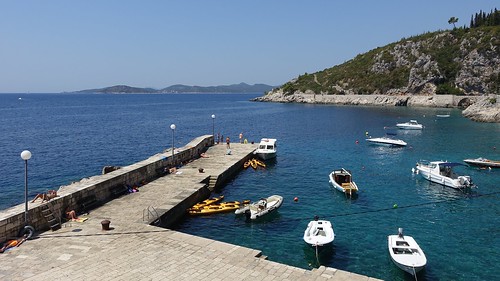
This year, Sarah and I spent two weeks off the coast of Dubrovnik, on Kolo ep island. We'd never been to Croatia before, and I was a little nervous that if there wasn't much to do on the island, we wouldn't be able to get elsewhere particularly easily. I needn't have worried: We thoroughly enjoyed our stay. It might even be my favourite holiday so far. We did travel around a bit: twice to Dubrovnik's old town and once to a botanical gardens in Trsteno but there was also loads to see on the island itself. One of our favourite trips was simply to a cave on the opposite side of the island known as a "blue cave" because you looked like a Smurf on the inside. We had to jump into the sea from the boat and swim into and out of the cave before continuing on our trip. Simply puttering about on the boat, either around the island or to Trsteno was a great experience in itself. Our guide Sammi was very friendly, the weather was great and swimming around or just enjoying the sun on the back of the boat was enough for me to want to check property prices out there. On Kolo ep island is a little restaurant called Villa Ruza. We managed to eat there twice during our stay. I think it is considered to be one of the top ten restaurants in Croatia. It's one of the best places I've ever eaten in my life. In terms of price, it was about half that of restaurants in Dubrovnik itself.
Kolo ep Kolo ep bay, from Villa Ruza
Dubrovnik itself was, quite predictably, much busier than Kolo ep. It is a stunningly attractive old town. On our second visit we took a tour. There are a variety of different themed tours that you can take, including Game Of Thrones sight-seeing tours, and there were Game Of Thrones tat shops all over the place. We opted for A Story About The War. One thing we love to do when visiting foreign places is to get an idea of what life is like for people there, and this war was not all that long ago - I can remember the news coverage from the time. We were the only two people on that particular tour, so we had a fairly tailored experience. I wish I could remember our guide's name. She was the same age as us and grew up as a child in the city when it was under siege. Her personal story included details about where her family stayed; what life was like for kids growing up at the time; how people got supplies; which areas were badly affected and much more. It was a very heartfelt tour and gave us an intimate and personal portrait of what life was like for people there at a time that most tour operators tend to prefer to ignore. This was exactly what we were looking for. Sarah and I were both a little teary at the end! We tried to do things a little different on this holiday. Normally we keep ourselves to ourselves and don't socialise much with other guests. We also rarely do trips and excursions, preferring to sort things out for ourselves. This time we made an effort to be more sociable and I'm glad we did because we met some really nice people. The trips we did were great fun and on the last day I blew through most of the rest of our currency by hiring a jet ski for half an hour. Those things are FUN. Top speed on the one I was using was 57 land mph. Every muscle in my body was screaming for a few days afterwards! Often on a two-week holiday we reach a point around 10 days where we've pretty much had enough. This time around I could have stayed for twice as long. This was the first proper test of my new camera and I've uploaded a set of photographs from our holiday to a Flickr gallery.

19 September 2015

Francois Marier: Hooking into docking and undocking events to run scripts

In order to automatically update my monitor setup and activate/deactivate my external monitor when plugging my ThinkPad into its dock, I found a way to hook into the ACPI events and run arbitrary scripts. This was tested on a T420 with a ThinkPad Dock Series 3 as well as a T440p with a ThinkPad Ultra Dock. The only requirement is the ThinkPad ACPI kernel module which you can find in the tp-smapi-dkms package in Debian. That's what generates the ibm/hotkey events we will listen for.

Hooking into the events Create the following ACPI event scripts as suggested in this guide. Firstly, /etc/acpi/events/thinkpad-dock:
event=ibm/hotkey LEN0068:00 00000080 00004010
action=su francois -c "/home/francois/bin/external-monitor dock"
Secondly, /etc/acpi/events/thinkpad-undock:
event=ibm/hotkey LEN0068:00 00000080 00004011
action=su francois -c "/home/francois/bin/external-monitor undock"
then restart udev:
sudo service udev restart

Finding the right events To make sure the events are the right ones, lift them off of:
sudo acpi_listen
and ensure that your script is actually running by adding:
logger "ACPI event: $*"
at the begininng of it and then looking in /var/log/syslog for this lines like:
logger: external-monitor undock
logger: external-monitor dock
If that doesn't work for some reason, try using an ACPI event script like this:
event=ibm/hotkey
action=logger %e
to see which event you should hook into.

Using xrandr inside an ACPI event script Because the script will be running outside of your user session, the xrandr calls must explicitly set the display variable (-d). This is what I used:
#!/bin/sh
logger "ACPI event: $*"
xrandr -d :0.0 --output DP2 --auto
xrandr -d :0.0 --output eDP1 --auto
xrandr -d :0.0 --output DP2 --left-of eDP1

Russ Allbery: Review: Magic's Promise

Review: Magic's Promise, by Mercedes Lackey
Series: Last Herald Mage #2
Publisher: DAW
Copyright: January 1990
ISBN: 0-88677-401-2
Format: Mass market
Pages: 320
Magic's Promise is the second book of the Last Herald Mage trilogy and a sequel to Magic's Pawn. As tempting as it is to skip the first book, which isn't very good, I think you'd miss a lot of the emotional dynamics between Vanyel and his family if you didn't read it. Magic's Promise opens years after the end of Magic's Pawn. Vanyel has become the most powerful Herald-mage of the kingdom, which is lucky for the kingdom because it's beset on all sides by magical attack. Heralds are being killed, countries on the border are looking for opportunities to spring, and Vanyel is being run ragged. Ragged enough that he's worried he's going to hurt someone by mistake when surprised. It's time for a desperately-needed vacation. Unfortunately for his ability to relax, that vacation means going home to visit his parents, who have never understood him and who disapprove strongly of his sexuality. (Not that he's actually had a lover in years.) It also means being in the same household as the armsmaster who broke his wrist as a child, and his father's deeply disapproving priest. And the border near his parents' lands may be heating up as well. Magic's Promise is the book where this trilogy hits its stride. After the events of the previous book, Vanyel is ridiculously overpowered and will be for the rest of the trilogy, but the problems in this book aren't the sort that raw power can fix. (That's a balance Lackey handles well in general.) There are a few places where Vanyel can simply overpower his problems, but the heart of the plot is a mystery that requires analysis, investigation, and a bit of undercover snooping. I enjoyed the defense of the kingdom plot (more than I had remembered, in fact), but the heart of this book is Vanyel and his family coming to terms with each other. Vanyel is a lot older and more confident than he was in the first book, and his service to the kingdom forces some grudging respect. But the way that grudging respect turns into real affection over the course of this book is a delight to read. This degree of reconciliation is wish-fulfillment most of the Valdemar series is heavy on wish-fulfillment but it's the sort of wish-fulfillment that matches the way that you wish the world would work. People figure out that they've been ignorant and cruel and actually change, and Vanyel learns some important lessons about giving people room to change. I particularly liked that the growth of respect wasn't one-sided. Most of the movement comes (and has to come) from Vanyel's family, but Vanyel gains some new-found appreciation and empathy for some strengths that he'd previously been blind to. Lackey's writing is still not the best here. There's something a bit awkward about the dialogue patterns in places, one gets a bit tired of the repetitive narrative focus on Vanyel's exhaustion, and the sentence-level construction of the story is more workable than delightful. You have to be invested in the characters; the beauty of the writing itself isn't going to win you over. As with a lot of Lackey's writing, I think your enjoyment will depend greatly on whether she happens to hit your emotional buttons. But the story she tells here, of people finding the inner goodness in each other and healing over past wounds, is one that I very much enjoy reading. I think this is the third time I read this book, and it's the first of the Valdemar series in this re-read that held up to my memory. So far, it's the best of the series. Followed by Magic's Price. Rating: 8 out of 10

Philipp Kern: Working with z/VM DIRMAINT as a mere user

Two helpful CMS commands to know if the users on the z/VM host you connect to are managed using DIRMAINT:

REVIEW is something I always expire from my mind after a few weeks of not using a mainframe. And then I do not usually find it quickly, even knowing where to look. (For some reason GET won't work unless you are a privileged user of the system.)

I guess by now most of the systems use DIRMAINT, but it's an IBM product that requires a separate license in addition to z/VM. Hence on some systems the user directory is still maintained by hand. In this case the password is written verbatim into the file and the administrator needs to change it manually for you.

Russ Allbery: pam-afs-session 2.6

I no longer use this PAM module, since I don't use AFS any more, and it's actually orphaned. But there was a bug report against the Debian package that was actually a PAM issue, not an AFS issue, so I went ahead and fixed that. The bug was that running sudo when you had the AFS PAM module enabled would delete your tokens. This was because sudo calls pam_setcred and pam_open_session in a somewhat strange way, leading the PAM module to think that sudo was taking ownership of the token but without putting the user in a new PAG. Then, when sudo closed its PAM session, the module would erroneously delete the token. The fix is to not set the flag to skip subsequent open_session and close_session handling when called with PAM_REINITIALIZE_CRED or PAM_REFRESH_CRED. This preserves correct session handling behavior and avoids this issue. Also with this release, I finally rewrote the test suite to use my generic PAM test suite code, and got rid of a bunch of old, legacy testing code. I lost one test for which the new test framework doesn't have enough hooks, but it wasn't particularly important, and the new code is much cleaner and more data-driven. There are also a few other, accumulated fixes, such as a compilation fix on Solaris 11, and a significant modernization of all of my common support libraries. (The last official release was in 2011!) You can get the latest version from the pam-afs-session distribution page.

Russ Allbery: Review: Magic's Pawn

Review: Magic's Pawn, by Mercedes Lackey
Series: Last Herald Mage #1
Publisher: DAW
Copyright: June 1989
ISBN: 0-88677-352-0
Format: Mass market
Pages: 349
Continuing my (very slow) re-read of Mercedes Lackey's Valdemar series. I've read all these books before (this series several times, in fact), but long before I started writing reviews. Vanyel is a legendary hero by the time of Talia (the hero of the first Valdemar series, starting with Arrows of the Queen). Talia was reading stories about him at the start of her story: the mage Herald who defended Valdemar against its enemies in the distant past. This is the first book of the trilogy that tells his story, starting (as Lackey's books often do) from rather inauspicious beginnings. Vanyel is the son of a border lord, and about as poorly suited for it as possible. He's small, pretty, entirely uninterested in the hammer-and-tongs sword fighting the arms master wants to teach him, and also gay, not that he has any idea that's even something that exists and has a name. His only ally was his sister, who is now off serving in Valdemar's military. Most of his life is spent hiding, feeling utterly lost and out of place, and wishing he could be a Bard. This is a Valdemar story, so if you're familiar with the series, you know what's coming next. What might come as a surprise is that "next" is quite some time into the story. Vanyel does not get rescued from his situation by a Companion. Instead, his father decides to exile him to the capital under the care of his aunt, who he's only met once and who didn't think highly of him. He expects to be even more miserable, and shuts emotionally down in anticipation. This is one of those books that I remembered as being better than it actually was, and one of the reasons why I enjoyed it less than I expected is that far too much of this book is devoted to describing Vanyel's mental state. This usually involves various elaborate emo analogies (which can be a failing of this series in general), and it's quite hard to maintain sympathy for Vanyel. Lackey gets us to feel for him at the start of the book, when he's really in a bad situation. But once he gets to the capital, he's his own worst enemy, and it's hard to avoid the desire to shake him. I also didn't remember just how much I disliked Tylendel. I'm sure it will come as a surprise to no one that Vanyel eventually meets someone who draws him out of his shell and gives him a reason to want to live. Unfortunately, that person, despite a positive surface impression, is self-obsessed, unstable, and not above manipulating Vanyel into actions that are so obviously catastrophic that it makes one want to yell at the book. I disliked this part of the book so much that even a Companion's choosing was overshadowed. The book does get a bit better after that truly awful middle, but it never hits the emotional stride that other Valdemar books hit. Lackey does introduce the Tayledras, which will be hugely important in later books in this series (and who are some of my favorite characters), but there too I prefer their later appearances. Vanyel's inability to see a good thing when it hits him in the face, punctuated by being occasionally cruel to the people who try to help him, makes it quite hard to enjoy his slow path to becoming a better person. I remember really liking this trilogy, so I think it gets better. But I also remembered liking Vanyel's claiming, and it didn't do much for me on a re-read. I can only recommend this one as a necessary preface to the later books in the trilogy, and expect to need a high tolerance for constant woe-is-me despair. Followed by Magic's Promise. Rating: 5 out of 10

Norbert Preining: Movie: Werner Herzog Fata Morgana

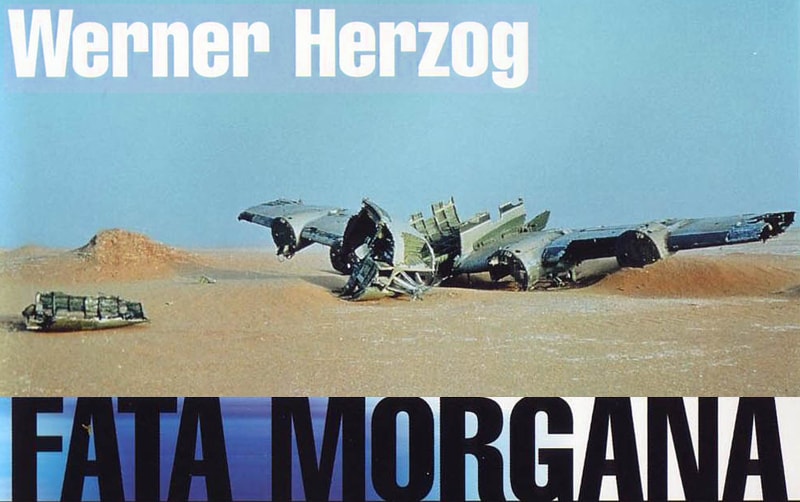
Finally I found the time and peace to watch one of the strangest movies that I have ever seen, Werner Herzog s (Offical Site, Wikipedia) Fata Morgana (Wikipedia, IMDb). Footage prepared for a SF movie that never realized, converted into an impressionistic allegory and movie full of phantasms.
Werner_Herzog-Fata_Morgana Fata Morgana is a movie that escapes every description. Having read several critics voices, as well as Herzog s comments in the excellent interview/(auto)biography book Werner Herzog A guide for the perplexed, I was eager to see this old and special movie. Having laid my hand on a collection of Werner Herzog s old movies recently, I prepared some good Japanese sake, and was ready to enjoy the move. The initial sequence of airplanes landing on a very hot day, again and again, sets the stage for a series of dream-like sequences in this movie. Divided into three parts, the movie tells its story only by visual impressions and the reading of the Mayan creation myth Popol Vuh, at times intermixed with some Leonard Cohen songs. Part One Creation introduces the desert as the origin of the world, accompanied by the initial creation myth before humans were formed. Part 2 Paradise is when humans enter into the desert. Full of ramshackle houses and rotten buildings, the contrast of the spoken words and imaginary cannot be more stunning. The final part 3 The Golden Age is full of absurdities and strange appearances, not surprisingly also most humans appear here. Watching this movie is more a visual experience for me than about seeing a story line. While there are many ways to interpret the relation between the Popol Vuh and the movie sequences, for me it is more a visual experiment that tries in some sense to hypnotize the audience. For those who love strange movies, an absolute must. For all others probably a torture.

18 September 2015

Dimitri John Ledkov: Clear Containers for Docker* Engine

Today at work, I announced something James Hunt, Ikey Doherty and myself have been working on. We integrated Clear Containers technology with Docker* Engine to create Clear Containers for Docker* Engine.

After following installation instructions, one can pull and run existing Docker* containers in the secure Clear Containers environment. This means that instead of namespaces, a fast virtual machine is started using the kvmtool hypervisor. This VM is running an optimised minimal Linux* kernel and the optimised Clear Linux* for Intel Architecture Project user-space, with the only goal to execute the Docker* workload and then shut down.

The net effect is almost indistinguishable from typical Docker* container usage:
$ docker run -ti ubuntu:vivid
root@d88a60502ed7:/# systemd-detect-virt
kvm
Apart from, as you see, it's running inside a kvm VM, and thus protected by Intel Virtualization Technology.

This is available on Clear Linux* as well as multiple other operating systems.

I hope this is exciting enough for people to try out, and if you have any feedback, feel free to leave comments or join our mailing list.

*Other names and brands may be claimed as the property of others

The postings on this site are my own and don't necessarily represent Intel s positions, strategies, or opinions.

Russ Allbery: Review: The Three-Body Problem

Review: The Three-Body Problem, by Cixin Liu & Ken Liu
Series: Three-Body Problem #1
Author: Liu Cixin ( )
Translator: Ken Liu
Publisher: Tor
Copyright: 2006, 2014
Printing: November 2014
ISBN: 1-4668-5344-1
Format: Kindle
Pages: 399
Liu Cixin ( ) is one of the best-known and most popular SF authors in China, but, due to the paucity of translated SF in the English-speaking world, was largely unknown to English-speaking SF readers. That made this translation by Ken Liu (no relation) highly anticipated: a window into a large world of SF by authors most of us have never read. And Ken Liu is an excellent writer in his own right (see, for instance, "The Literomancer" or "Altogether Elsewhere, Vast Herds of Reindeer"), which was a hopeful sign for a good translation. Indeed, the translation is very good. One can tell that the book comes from a different literary tradition, but primarily from unusual (to US readers, at least) emotional focal points for the characters and lots of Chinese history that the author feels little need to explain. (Ken Liu adds translator notes for the bits most likely to lose non-Chinese audiences.) I found the characters a bit odd and occasionally hard to identify with, but I didn't mind: it added to the feeling of exploring a slightly different literary tradition with different character conventions. Unfortunately, the end of the book went entirely off the rails, at least for me. The Three-Body Problem opens during the Cultural Revolution, with the murder of Ye Wenjie's father, a physics professor, and the suicide of her advisor and friend. Two years later, she's at a work camp in inner Mongolia, cutting trees, numb, keeping her head down. But a traveling journalist smuggles in a secret copy of Silent Spring and gives it to her. The book both hardens her own belief in the evil of humanity and gets her into deeper trouble when she agrees to recopy a draft of a letter to the central leadership about the environmental devastation caused by the logging. Ye Wenjie is forced to choose permanent exile to an experimental radar facility on a remote mountain in Mongolia. Ye Wenjie is vital to the slowly-developing plot of the book, but this is the last the reader sees of her for some time. Part II jumps to present time and to a different protagonist: Wang Miao, a distinguished nanotechnology researcher who is recruited by the PLA and the police into a secret war room. Distinguished scientists are killing themselves in frighteningly large numbers, including one that Wang Miao had a crush on. She left a suicide note before overdosing on sleeping pills, one that says only, cryptically, that physics doesn't exist. The government is desperate to figure out what's going on. The "radar" facility and the suicide of scientists are linked, of course, but it takes much of the book for Wang Miao and his colleagues to piece together how. Key clues come in the form of an odd puzzle virtual reality MMORPG that becomes a popular sensation. In it, players find themselves on an alien world whose suns rise and set at strange and unpredictable intervals: sometimes far too far away and horribly cold, sometimes far too close and destructively hot, and sometimes not seen for long periods of time. The players can somehow dehydrate themselves and the rest of the population to weather the worst seasons, but life is a constant struggle against apparently unpredictable elements. Despite that, players slowly find ways to build civilizations and attempt to predict the strange cycles of heat and cold. It takes the characters a long time to understand what's happening. Readers will probably be much faster, since they have out-of-band information the characters don't. At first, this game seems entirely unrelated to the suicides of the scientists or, for that matter, to Ye Wenjie, who is easy to almost forget. But they all weave together in a way that's almost compelling. I say almost because the motivations of the characters are quite tangled and interesting, but the science is... awful. Those who have read my other book reviews know that I don't insist on hard science in my SF. Usually I'm willing to roll with it, and I can read past even obvious scientific nonsense. But science is critical to the plot of this book; some very specific actions, with a detailed in-book scientific justifications, are the underpinning of the entire plot. And they make utter nonsense of physics. I've rarely had science in a novel destroy my suspension of disbelief this thoroughly. Physics isn't even alone: biology, chemistry, computing, and astronomy are all in for it as Liu reveals the causes of the book's events. I wanted to be engaged by the conflict of ethics and philosophy that drive the plot, and some of that conflict is quite interesting. But every other page would have another colossal pile of scientific nonsense that would throw me out of the book again, usually in the service of a set piece that missed grand and landed on absurdly silly. Be warned that this book also ends on a bit of a cliff-hanger, and there are two more books in the series. The second has been released in a translated edition, but with a different translator, which is disappointing (Ken Liu did an excellent job); the third isn't out yet. If you can get past the awful science, The Three-Body Problem is doing some interesting things. The characters are a bit wooden and forgettable, but the philosophical problems they encounter are ones I don't see often in western SF. This a refreshing change, and I'm interested enough that I'm still considering picking up the sequels. But the science hurts the book so badly. Followed by The Dark Forest. Rating: 6 out of 10

17 September 2015

Lunar: A key signing party keyserver as a Tor hidden service

Key signing parties are a pain and hopefully, one day, we will have better ways to authentication keys than reading hexadecimal strings out loud. The Zimmermann Sassaman key-signing protocol makes them much more bearable already by having only one single hexadecimal string read out loud. That string is the cryptographic hash of a document given to every participant listing all participants and their fingerprints. If everyone has the same hash, then we assume that everyone has the same document. Then, participants in turn will confirm that they fully recognize the fingerprint listed in the document. Alexander Wirt wrote a small key server dedicated to receive keys from the participants. There is also a script that will generate the document from the submitted keys and a ready-to-use keyring. The latter can be run automatically using inoticoming when a new key arrives. Finally, it would be nice if participants could confirm that their key has been properly added to the document, e.g. by making the list available on a web server. Setting all this up seemed like a good opportunity to play with Tor hidden services and systemd-nspawn. Here's the setup log with some comments. This was done on a small armhf device with Debian Jessie. Create a new hidden service Edit /etc/tor/torrc on the host to setup the hidden service:
HiddenServiceDir /var/lib/tor/ksp/
HiddenServicePort 80 10.0.0.2:80
HiddenServicePort 11371 10.0.0.2:11371
Run:
host# systemctl reload tor.service
Then, to learn the name of the newly created hidden service name:
host# cat /var/lib/tor/ksp/hostname
ksp123456789abcd.onion
Install the container debootstrap as always:
host# debootstrap --variant=minbase jessie /var/lib/container/ksp
Preliminary container configuration We do the following step simply using chroot as we are going to use the host network configuration for this stage. The container itself will not have access to the Internet.
host# chroot ksp
Let's set the hostname:
ksp-chroot# echo 'ksp' > /etc/hostname
Set up APT:
ksp-chroot# echo 'deb http://httpredir.debian.org/debian jessie main' > /etc/apt/sources.list
ksp-chroot# apt update
We need dbus to get systemd to work well:
ksp-chroot# apt-get install dbus
Make sure that we can resolve our own hostname:
ksp-chroot# apt-get install libnss-myhostname
ksp-chroot# sed -e '/^hosts:/s/files/myhostname \0/' -i /etc/nsswitch.conf
These are dependencies of the keyserver:
ksp-chroot# apt-get install --no-install-recommends libhttp-daemon-perl \
                liblog-loglite-perl libproc-reliable-perl
These ones are needed for the script generating the list:
ksp-chroot# apt-get install bzip2 inoticoming
And we will use the smallest HTTP server available:
ksp-chroot# apt-get install netcat-traditional micro-httpd
Finally, let's unconfigure all DNS resolvers:
ksp-chroot# echo > /etc/resolv.conf
And we are done with the chroot:
ksp-chroot# exit
Let's retrieve the ksp-tools repository now:
host# cd /var/lib/container/srv
host# git clone https://github.com/formorer/ksp-tools
Container setup We will now start the container with a shell to configure it:
host# systemd-nspawn -D ksp --network-veth
Let's ask systemd to configure the network for us:
ksp# systemctl enable systemd-networkd
Let's not forget to set a root password:
ksp# passwd
We add a dedicated user to run the keyserver and the list generation script:
ksp# adduser --system --group --disabled-password --disabled-login --home /var/lib/ksp ksp
Let's configure the keyserver:
ksp# cp /srv/ksp-tools/keyserver.conf /var/lib/ksp/keyserver.conf
Let's edit /var/lib/ksp/keyserver.conf:
homedir = /var/lib/ksp
Now create the GnuPG homedir for the keyserve:
ksp# mkdir /var/lib/ksp/keys
ksp# install -d -o ksp -g ksp -m 0700 /var/lib/ksp/keys/gpg
Copy the template list generator:
ksp# cp -r /srv/ksp-tools/example /var/lib/ksp/keys/ksp123456789abcd_onion
Create the key repository:
ksp# install -d -o ksp -g ksp -m 0700 /var/lib/ksp/keys/ksp123456789abcd_onion/keys
Create a directory accessible to the web server where the participant list will be generated:
ksp# mkdir -p /var/www
ksp# install -d -o ksp -g ksp -m 0755 /var/www/keys
Let's configure the list generation script by editing /var/lib/ksp/keys/ksp123456789abcd_onion/conf/vars:
KS=ksp123456789abcd.onion
export GNUPGHOME=/tmp/ksp-gpg
KSPFILE="/var/www/keys/ksp-event.txt"
Don't forget to adjust the header in /var/lib/ksp/keys/ksp123456789abcd_onion/conf/list-header. Now we create a unit file for the keyserver in /etc/systemd/system/keyserver.service:
[Unit]
Description=Key signing party keyserver
[Service]
Type=simple
Environment="KSP_HOMEDIR=/var/lib/ksp"
ExecStart=/srv/ksp-tools/bin/kspkeyserver.pl --nodaemonize
User=ksp
Group=ksp
PrivateTmp=yes
ProtectHome=yes
ProtectSystem=full
ReadOnlyDirectories=/
ReadWriteDirectories=-/var/lib/ksp
CapabilityBoundingSet=CAP_NET_BIND_SERVICE
[Install]
WantedBy=multi-user.target
Another unit for the list generator as /etc/systemd/system/ksp-list-generator.service:
[Unit]
Description=Key signing party list generator
[Service]
Type=simple
EnvironmentFile=/var/lib/ksp/keys/ksp123456789abcd_onion/conf/vars
ExecStart=/usr/bin/inoticoming --foreground /var/lib/ksp/keys/ksp123456789abcd_onion/keys --chdir /var/lib/ksp/keys/ksp123456789abcd_onion bin/generate-list \;
User=ksp
Group=ksp
PrivateTmp=yes
ProtectHome=yes
ProtectSystem=full
ReadOnlyDirectories=/
ReadWriteDirectories=/var/www/keys
CapabilityBoundingSet=
[Install]
WantedBy=multi-user.target
For the web server, we first configure a socket listening on port 80 in /etc/systemd/system/micro-httpd.socket:
[Unit]
Description=micro-httpd socket
[Socket]
ListenStream=80
Accept=yes
[Install]
WantedBy=sockets.target
And then the web server in /etc/systemd/system/micro-httpd@.service:
[Unit]
Description=micro-httpd server
[Service]
ExecStart=-/usr/sbin/micro-httpd /var/www/ksp
StandardInput=socket
PrivateTmp=yes
ProtectHome=yes
ProtectSystem=full
ReadOnlyDirectories=/
CapabilityBoundingSet=
Let's now ask systemd to start all of these at boot time:
ksp# systemctl daemon-reload
ksp# systemctl enable keyserver.service
ksp# systemctl enable ksp-list-generator.service
ksp# systemctl enable micro-httpd.socket
One way to kill the container is to type Control+] three times. Boot the container Let's get this party started!
host# systemd-nspawn -b -D /var/lib/container/ksp --network-veth
Hopefully, things should work now. Participants to the KSP should then be able to send their key with:
$ torsocks gpg --keyserver ksp123456789abcd.onion --send-key $KEYID
(Sadly, this is broken with GnuPG 2.1 at the moment.) The participant list should be available at http://ksp123456789abcd.onion/ksp-event.txt. Final steps We need to tell systemd to start the container started at boot time:
host# systemctl enable systemd-nspawn@ksp.service
But the default command-line will not use a dedicated network, so we need to override that part of the configuration. First create a directory:
host# mkdir /etc/systemd/system/systemd-nspawn@ksp.service.d
And edit /etc/systemd/system/systemd-nspawn@ksp.service.d/use-network-veth.conf:
[Service]
# The empty line because we want to override all previous ExecStart
# and not add an extra command
ExecStart=
ExecStart=/usr/bin/systemd-nspawn --quiet --keep-unit --boot --link-journal=try-guest --directory=/var/lib/container/%i --network-veth
Let's reload systemd and verify that our snippet is there:
host# systemctl daemon-reload
host# systemctl cat systemd-nspawn@ksp.service
All good? Let's start it:
host# systemctl start systemd-nspawn@ksp.service
One should also add a firewall to disallow any outgoing connections from the ve-ksp interface as an extra protection.

Julien Danjou: My interview in le Journal du Hacker

A few days ago, the French equivalent of Hacker News, called "Le Journal du Hacker", interviewed me about my work on OpenStack, my job at Red Hat and my self-published book The Hacker's Guide to Python. I've spent some time translating it into English so you can read it if you don't understand French! I hope you'll enjoy it.
Hi Julien, and thanks for participating in this interview for the Journal du Hacker. For our readers who don't know you, can you introduce you briefly?
You're welcome! My name is Julien, I'm 31 years old, and I live in Paris. I now have been developing free software for around fifteen years. I had the pleasure to work (among other things) on Debian, Emacs and awesome these last years, and more recently on OpenStack. Since a few months now, I work at Red Hat, as a Principal Software Engineer on OpenStack. I am in charge of doing upstream development for that cloud-computing platform, mainly around the Ceilometer, Aodh and Gnocchi projects.
Being myself a system architect, I follow your work in OpenStack since a while. It's uncommon to have the point of view of someone as implied as you are. Can you give us a summary of the state of the project, and then detail your activities in this project?
The OpenStack project has grown and changed a lot since I started 4 years ago. It started as a few projects providing the basics, like Nova (compute), Swift (object storage), Cinder (volume), Keystone (identity) or even Neutron (network) who are basis for a cloud-computing platform, and finally became composed of a lot more projects. For a while, the inclusion of projects was the subject of a strict review from the technical committee. But since a few months, the rules have been relaxed, and we see a lot more projects connected to cloud-computing joining us. As far as I'm concerned, I've started with a few others people the Ceilometer project in 2012, devoted to handling metrics of OpenStack platforms. Our goal is to be able to collect all the metrics and record them to analyze them later. We also have a module providing the ability to trigger actions on threshold crossing (alarm). The project grew in a monolithic way, and in a linear way for the number of contributors, during the first two years. I was the PTL (Project Technical Leader) for a year. This leader position asks for a lot of time for bureaucratic things and people management, so I decided to leave my spot in order to be able to spend more time solving the technical challenges that Ceilometer offered. I've started the Gnocchi project in 2014. The first stable version (1.0.0) was released a few months ago. It's a timeseries database offering a REST API and a strong ability to scale. It was a necessary development to solve the problems tied to the large amount of metrics created by a cloud-computing platform, where tens of thousands of virtual machines have to be metered as often as possible. This project works as a standalone deployment or with the rest of OpenStack. More recently, I've started Aodh, the result of moving out the code and features of Ceilometer related to threshold action triggering (alarming). That's the logical suite to what we started with Gnocchi. It means Ceilometer is to be split into independent modules that can work together with or without OpenStack. It seems to me that the features provided by Ceilometer, Aodh and Gnocchi can also be interesting for operators running more classical infrastructures. That's why I've pushed the projects into that direction, and also to have a more service-oriented architecture (SOA)
I'd like to stop for a moment on Ceilometer. I think that this solution was very expected, especially by the cloud-computing providers using OpenStack for billing resources sold to their customers. I remember reading a blog post where you were talking about the high-speed construction of this brick, and features that were not supposed to be there. Nowadays, with Gnocchi and Aodh, what is the quality of the brick Ceilometer and the programs it relies on?
Indeed, one of the first use-case for Ceilometer was tied to the ability to get metrics to feed a billing tool. That's now a reached goal since we have billing tools for OpenStack using Ceilometer, such as CloudKitty. However, other use-cases appeared rapidly, such as the ability to trigger alarms. This feature was necessary, for example, to implement the auto-scaling feature that Heat needed. At the time, for technical and political reasons, it was not possible to implement this feature in a new project, and the functionality ended up in Ceilometer, since it was using the metrics collected and stored by Ceilometer itself. Though, like I said, this feature is now in its own project, Aodh. The alarm feature is used since a few cycles in production, and the Aodh project brings new features on the table. It allows to trigger threshold actions and is one of the few solutions able to work at high scale with several thousands of alarms. It's impossible to make Nagios run with millions of instances to fetch metrics and triggers alarms. Ceilometer and Aodh can do that easily on a few tens of nodes automatically. On the other side, Ceilometer has been for a long time painted as slow and complicated to use, because its metrics storage system was by default using MongoDB. Clearly, the data structure model picked was not optimal for what the users were doing with the data. That's why I started Gnocchi last year, which is perfectly designed for this use case. It allows linear access time to metrics (O(1) complexity) and fast access time to the resources data via an index. Today, with 3 projects having their own perimeter of features defined and which can work together Ceilometer, Aodh and Gnocchi finally erased the biggest problems and defects of the initial project.
To end with OpenStack, one last question. You're a Python developer for a long time and a fervent user of software testing and test-driven development. Several of your blogs posts point how important their usage are. Can you tell us more about the usage of tests in OpenStack, and the test prerequisites to contribute to OpenStack?
I don't know any project that is as tested on every layer as OpenStack is. At the start of the project, there was a vague test coverage, made of a few unit tests. For each release, a bunch of new features were provided, and you had to keep your fingers crossed to have them working. That's already almost unacceptable. But the big issue was that there was also a lot of regressions, et things that were working were not anymore. It was often corner cases that developers forgot about that stopped working. Then the project decided to change its policy and started to refuse all patches new features or bug fix that would not implement a minimal set of unit tests, proving the patch would work. Quickly, regressions were history, and the number of bugs largely reduced months after months. Then came the functional tests, with the Tempest project, which runs a test battery on a complete OpenStack deployment. OpenStack now possesses a complete test infrastructure, with operators hired full-time to maintain them. The developers have to write the test, and the operators maintain an architecture based on Gerrit, Zuul, and Jenkins, which runs the test battery of each project for each patch sent. Indeed, for each version of a patch sent, a full OpenStack is deployed into a virtual machine, and a battery of thousands of unit and functional tests is run to check that no regressions are possible. To contribute to OpenStack, you need to know how to write a unit test the policy on functional tests is laxer. The tools used are standard Python tools, unittest for the framework and tox to run a virtual environment (venv) and run them. It's also possible to use DevStack to deploy an OpenStack platform on a virtual machine and run functional tests. However, since the project infrastructure also do that when a patch is submitted, it's not mandatory to do that yourself locally.
The tools and tests you write for OpenStack are written in Python, a language which is very popular today. You seem to like it more than you have to, since you wrote a book about it, The Hacker's Guide to Python, that I really enjoyed. Can you explain what brought you to Python, the main strong points you attribute to this language (quickly) and how you went from developer to author?
I stumbled upon Python by chance, around 2005. I don't remember how I hear about it, but I bought a first book to discover it and started toying with that language. At that time, I didn't find any project to contribute to or to start. My first project with Python was rebuildd for Debian in 2007, a bit later. I like Python for its simplicity, its object orientation rather clean, its easiness to be deployed and its rich open source ecosystem. Once you get the basics, it's very easy to evolve and to use it for anything, because the ecosystem makes it easy to find libraries to solve any kind of problem. I became an author by chance, writing blog posts from time to time about Python. I finally realized that after a few years studying Python internals (CPython), I learned a lot of things. While writing a post about the differences between method types in Python which is still one of the most read post on my blog I realized that a lot of things that seemed obvious to me where not for other developers. I wrote that initial post after thousands of hours spent doing code reviews on OpenStack. I, therefore, decided to note all the developers pain points and to write a book about that. A compilation of what years of experience taught me and taught to the other developers I decided to interview in the book.
I've been very interested by the publication of your book, for the subject itself, but also the process you chose. You self-published the book, which seems very relevant nowadays. Is that a choice from the start? Did you look for an editor? Can you tell use more about that?
I've been lucky to find out about others self-published authors, such as Nathan Barry who even wrote a book on that subject, called Authority. That's what convinced me it was possible and gave me hints for that project. I've started to write in August 2013, and I ran the firs interviews with other developers at that time. I started to write the table of contents and then filled the pages with what I knew and what I wanted to share. I manage to finish the book around January 2014. The proof-reading took more time than I expected, so the book was only released in March 2014. I wrote a complete report on that on my blog, where I explain the full process in detail, from writing to launching. I did not look for editors though I've been proposed some. The idea of self-publishing really convince me, so I decided to go on my own, and I have no regret. It's true that you have to wear two hats at the same time and handle a lot more things, but with a minimal audience and some help from the Internet, anything's possible! I've been reached by two editors since then, a Chinese and Korean one. I gave them rights to translate and publish the books in their countries, so you can buy the Chinese and Korean version of the first edition of the book out there. Seeing how successful it was, I decided to launch a second edition in Mai 2015, and it's likely that a third edition will be released in 2016.
Nowadays, you work for Red Hat, a company that represents the success of using Free Software as a commercial business model. This company fascinates a lot in our community. What can you say about your employer from your point of view?
It only has been a year since I joined Red Hat (when they bought eNovance), so my experience is quite recent. Though, Red Hat is really a special company on every level. It's hard to see from the outside how open it is, and how it works. It's really close to and it really looks like an open source project. For more details, you should read The Open Organization, a book wrote by Jim Whitehurst (CEO of Red Hat), which he just published. It describes perfectly how Red Hat works. To summarize, meritocracy and the lack of organization in silos is what makes Red Hat a strong organization and puts them as one of the most innovative company. In the end, I'm lucky enough to be autonomous for the project I work on with my team around OpenStack, and I can spend 100% working upstream and enhance the Python ecosystem.

Raphaël Hertzog: Freexian s report about Debian Long Term Support, August 2015

A Debian LTS logoLike each month, here comes a report about the work of paid contributors to Debian LTS. Individual reports In August, 71.50 work hours have been dispatched among 7 paid contributors. Their reports are available: Evolution of the situation September is stable compared to August (71.50 hours per month) and has not caught up back to the level of July as I hoped. Again it s because 2 sponsors were not able to pay their renewal invoice on time (one of last month paid, but another bigger sponsor failed this month). Those sponsors will continue to support us and I would like to be able to say that things will be back to normal next month, but I can t say it since we have also been informed of the (hopefully temporary) defection of another bronze sponsor that will affect us next month. Fortunately there are also good news, we have 3 new sponsors in the pipe (2 silver, 1 platinum) who shall join the project soon. And Blablacar increased their support from Silver to Gold (from 4h/month to 8h/month). But we still need more support in particular since we would like to commit to support virtualization related packages in Wheezy: that s clearly an objective for us. I recently published the summary of the work session held during DebConf 15 in Heidelberg (video recording). It would be really nice if we could get closer to the goal of funding a full-time position. In terms of security updates waiting to be handled, the situation is close to last month: the dla-needed.txt file lists 18 packages awaiting an update (2 less than last month), the list of open vulnerabilities in Squeeze shows about 30 affected packages in total (8 more than last month). Thanks to our sponsors

No comment Liked this article? Click here. My blog is Flattr-enabled.

NOKUBI Takatsugu: PIXELS (film)

I watched PIXELS in a theater. It subjects about video games, mostly retro 80 s arcade games. I love video games from childhood, my first game played would be Taito s Space Invaders, I was the 4 or 5 yeas old time. It had bring me to the computer world. Fortunately I am working at Akihabara area, so I can play the video games in the movie like Pac-man, Glaga, Cemtipede, Donkey Kong and so on in two gamecenters, Natsuge Museum and Hey (Hirose Entertainment Yard . Natsuge Museum is under private management so it closes week days. They focused to old games between 70 th to 90 th. Hey is a franchised shop ownd by TAITO. They covered almost video games except medal games. You can play old games like Paper-boy, The Tower of Druaga, and newest games like Left4Dead arcade. They correct many titles of the games in the movie, and be playable. They are my recommended place in Akihaba, if you like video games.

Next.

Previous.