Search Results: "ron"

13 October 2008

Ben Armstrong: Bits from the Debian Eee PC team, autumn 2008

Some brief highlights of the last three months of Debian Eee PC development. Thermal and ACPI breakage resolved in 2.6.26-7 We’re pleased to see that in the upload to Sid of linux-image-2.6.26-1-686 version 2.6.26-7, the pair of 2.6.26 bugs we’ve been tracking that have made it difficult for Eee users to upgrade their systems have been resolved. Since then 2.6.26-8 has been uploaded and is expected to enter Lenny this week due to a freeze exception. Once the new kernel has migrated we will move quickly to build and release a new installer that includes it. Ath5k wifi works on Eee PC in Linux 2.6.27 Jean-Christophe reports that ath5k works in Linux 2.6.27 on the Eee PC 701, and just needs a small patch to work with our eeepc-acpi-scripts package. This is good news for those of us with models 701, 900, 900A and 1000HD who have been wanting to get off of the non-free Madwifi drivers and onto DFSG free drivers. New Eee PC model 701SD wifi support in the works Users of the new Eee PC Model 701SD have just started showing up looking for support in mainstream Linux distros. Martin Filtenborg confirmed using our Eee PC Live image with the GPL’d rtl8187se driver from Realtek that we can at least use it to connect to an unencrypted AP, get an IP address and ping other hosts. Of course, it is one thing to have a working vendor-supplied driver and quite another to have mainstream support. We’ll make do with what we have now, but will be seeking a mainstream solution as soon as possible. We’re seeking more testers and developers to work on this. To date, an ITP has not been filed, as it is not yet clear who is going to carry this work forward. Chasing the 5 second boot An interesting discussion on Arjan van de Ven and Auke Kok’s work to get an Eee 901 to boot in 5 seconds took place this month. While the Debian Eee PC team is not making work on this a priority, we’ll keep an eye on it to see if Debian can incorporate some or all of the techniques they used so that our users can benefit without making radical changes to their systems. Working towards mainstream support for rt2860 Our filing of an ITP for rt2860 (the wifi driver for models 901, 1000 and 1000H) was followed by discussion about how to separate out the GPL’d driver from the embedded non-free firmware so that it can at least go into contrib. Glenn Saberton has been working on rewriting the build system around kbuild and separating out the firmware. Numerous improvements to ACPI scripts Since my last progress report, there have been numerous improvements to the eeepc-acpi-scripts package to deal with all of the various models we now support and make the scripts more robust and flexible. Check out the changelog for details.

Patrick Schoenfeld: Re: Gentoo destroying earth?

I fully agree that working with Gentoo is no fun at all, as Julian points out in his post
My impression, when I tried Gentoo for the first (and last) time is the same. Thats not because it is made bad. In fact things in Gentoo aren't made that bad. There is good documentation, portage is quiet nice (with its USE flags and alike), but in the end I'm not really satisfied.
After all Gentoo uses a copied concept, which itself is good. The concept is derived from the BSD-world and is just the concept of source-based systems. This concept has its advantages over binary distributions, because it allows a flexibility that is not really possible with a binary distribution. That really is the only appreciable advantage of these systems. Users of these systems (including FreeBSD and alike) tend to give other arguments as well: Newest Software, Highest Performance and even Security is a point they give.

Usually the "newest software" argument is brought up with a rant against Debian. I keep hearing statements like "Debian Etch is totally outdated and Testing is broken". That statement in itself is just wrong, but the important thing is: What do you need such new software for? On a server its preferrable not to upgrade to each and every major release, for certain reasons. Its also a bad thing to build on production systems, so you need to take further measures to administer systems like that. On a desktop I can understand the logic, but then again: No. Why would I want a system I have to compile from scratch and on each upgrade (wasting a lot of time, power etc.) which changes often?

The performance argument is the dumbest of all. Binary distributions usually build binaries for various platforms. And while they can't be optimized for a very specific processor or a very specific feature set (=reduces binary size) they usually perform well enough that a difference between the self-compiled Gentoo system and a foreign-compiled Debian is not noticed by the user and sometimes not even measurable. So the time you save during the lifetime of your builds (which is not very long on a Desktop, is it?) because of the enhanced performance is used up a hundred times, by the time you waste for compiling the whole software only for yourself. Even if some of the software performs noticable better (e.g. video processing is said to benefit a lot from an optimized platform).

What about the security argument? It has been said, that you get your updates earlier then users of binary distributions. That is partly true, because in a binary distribution the update needs to be built first, before it gets to the end user (however, everything before is the same for a binary or a source distribution). But do you really follow security issues that close, that you benefit a lot from this? If you do, indeed, you save some hours. If (and only if) both distributions have a solution for a security issue at the same time.

Anyway. The flexibility argument can't get discussed away. Its the argument that makes Ports in BSD-systems attractive. You can have exactly the features you want, with the build-time options you want. In a comfortable manner. That is in contrast to binary distributions where we package developers need to guess which features might be needed (/wanted) by the users with mixed results. Good if they can decide for themselves. Still, I don't see the reason for compiling the whole system, if I need one or two customized components. So I go with Debian and customize packages if I really need/want to. The only difference is that it takes a lot of more effort.

I would love to see something done in Debian to reach a compromise. Making rebuilding of packages with different options very comfortable. We have DEB_BUILD_OPTIONS, maybe we should enhance it to support a lot more options then noopt,nostrip or nodoc. Possibly it would be a good thing to standardize on some use flags (e.g. [no]ssl, [no]ldap, etc.) and support them in the debian/rules file. This way building customized packages would be as easy as setting sensible DEB_BUILD_OPTIONS and run dpkg-buildpackage on the source. This could be eased further by providing a tool to download the source and build a given package (IIRC such a tool already exists). How does that sound?

10 October 2008

Axel Beckert: water-proof mice

When I blogged about water-proof keyboards a few months ago I did not really expect that there will be water-proof mice (no IP classification though) so soon, too. (Found in an advertisment in the current issue of the German c’t magazine.) But the idea of water-proof mice in general doesn’t seem to be as new as I initially expected, at least the web design of http://www.waterproofmouse.co.uk/ is very nineties. ;-) RuggedTech even has washable, wireless, IP66 (protected against powerful water jets) mice with a scroll-wheel and completely silicone sealed IP68 mice (protected against immersion beyond 1m).

Julian Andres Klode: Gentoo destroying earth?


I worked a bit with some Gentoo systems the last days and it was no fun. The whole compiling thing is no fun. In fact, it is a danger for the environment. If every computer in the world run Gentoo, power consumption would increase dramatically. There would also be no netbooks, as they are almost unusable for running Gentoo on it, compiling software. The path chosen by binary distributions like Debian is much better. Packages are compiled centrally and users download and install these pre-compiled packages. But it is also much less flexible in terms of which functionality is supported. We, as package maintainers, have to decide which functionality is likely to be used by the users. In Contrast, Gentoo has USE flags, which allows the user to enable the specific functionality he/she wants. Should we combine the advantages of both technologies? Provide a normal binary distribution as we do now, but also provide a framework for users to easily recompile their packages, adding new functionality. Imagine a combination of all these technologies: User wants to install software X with feature F. The package maintainer has not enabled F in the binary. The user opens the website for his personal archive, selects the F flag and the software and clicks on build. The server builds the software and notifies the user once the binary is ready. At Ubuntu, the first step has been made into this direction. While the package format is still the same, Launchpad allows users to create so-called PPAs (Personal Package Archives), where users can upload their source packages, which are then compiled and made available to other users. Let’s say Project A releases version X of their software. They can create a source package for it, upload it to the PPA, and provide the binary packages to the users. Prior to PPAs, most users would have used an old version, compile their own version or use tarballs containing pre-compiled software (mozilla does this). And sorry for the title. I respect the Gentoo community and the Gentoo developers, they are doing great work there. And ebuilds and Gentoo’s boot system (with this runscript stuff) is really easy. BTW: I also like the way Gentoo displays its boot messages. It looks much more organized than Debian’s boot process. (In terms of the message logging, where Debian writes “done” when something is done, and Gentoo writes “[OK]” to the right side of the screen, in green letters. (This is partially possible in Debian using lsb-base-logging.sh, but not all init scripts use these functions, or they use the wrong ones.) Posted in Debian, General, Ubuntu      

9 October 2008

Felipe Augusto van de Wiel: 10 Oct 2008

Random news

/back
Yes, I was away... long and sad story involving health issues. :-( I'm trying to get back, hopefully everything will be fine. Let me publicly apologize to some people that was expecting some work from me and I postponed it, not because of slackness but because I was unable to do it. I'm catching up with a lot of tasks and trying to solve long standing issues, feel free to ping me to get some update on a specific matter. I am really sorry!


Slogan
Do you know about the poll to choose a slogan for the release of Debian 5.0, also known as "lenny"?

No!? Shame on you! :-)

People behind Debian Art started a discussion to get opinions! After some input they prepared a poll, maybe they should try to use a doodle. Right now, The Universal Operating System is quite popular, but a lot of people did some nice suggestions, and some of them would like to see a slogan some way related to the Toy Story (tm) character Lenny:


The discussion is distributed across three lists: Debian Desktop, Debian Publicity and Debian Curiosa, I would also point to the comments made by Gustavo Noronha da Silva (here) and Andre Felipe Machado (here).

If you didn't say anything so far, please do!

David Welton: Dynamic Languages in Desktop Applications

Ted Leung talks about the lack of dynamic languages in desktop applications. There's something ironic about that: Ted works for Sun Microsystems. Sun Microsystems, back in the day, was a big contributor to Tcl and Tk. Despite not being the "in thing", Tcl and Tk are used a lot more than people think. Not so much in the latest and greatest things being built now, due to the (undeservedly) "uncool" reputation, but in lots of products that are still chugging along, earning money and serving their users well, if not noisily so. Interestingly enough, my biggest client here in the Innsbruck area is one of these. They have offices worldwide, make a good living at what they do, and their user interface is mostly in Tk.

8 October 2008

Wouter Verhelst: Why I don't want an iSomething, part II

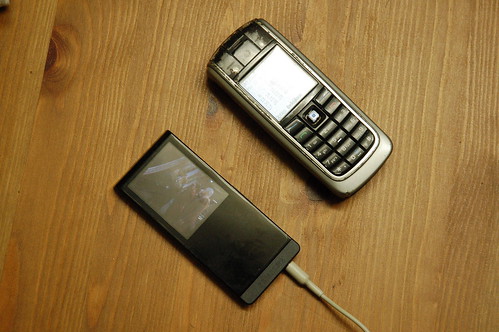
Bjorn mentions that he doesn't want the nokia internet tablet, because it doesn't have a phone and he doesn't want to carry two devices with him. portable media player Bottom left, my portable media player. 4G solid-state storage, plays movies (the display shows a scene from Star Trek: Deep Space Nine that I converted from DVD), audio, FM radio, and after a firmware update can do games and some random applications. Does bluetooth. Does not do phone calls. Upper right, my cell phone. A simple Nokia 6021. Does bluetooth, makes phone calls, and (as the display somewhat shows) can do calendaring, too. With SyncML, I can synchronize it with my laptop. Together, they perform anything I'd possibly want from a smartphone (and don't anyone tell me 'SSH', because doing ssh on any screen smaller than, 7" and without decent keyboard is laughable). Together, they're smaller and weigh less than a smartphone. Together, they're less expensive than a smartphone ( 125 for the phone, 85 for the portable media player). Why does anyone buy a smartphone?

Rob Taylor: Wizbit ars d

So it seems ars technica picked up on Codethink’s little pet project! Obviously the little amount of info on the wiki isn’t enough for everyone who’s interested and enough has changed since the GUADEC talk that I should write a bit here to clarify what’s going on and where we’re going. First off, we’re currently not using GVFS or FUSE - the core Wizbit component is simply a versioning, distributed object store. The current plan is to later hook up with a metadata service, maybe tracker, and use this to export a FUSE filesystem using the metadata. This core Wizbit service is just a library with its own api, maybe hooking up to gio streams for ease of use from GLib based applications. The current focus of our work is solidifying this store and the synchronization between multiple machines. We’re prototyping its use in Tomboy. Karl is also working on making some of these pretty widgets for navigating history work. We’re not actually using Git underneath, but using our own implementation of concepts from both Git and Bzr. This is for a number of reasons, partially that making a library from git’s code proved more trouble than just reimplementing the concepts (as things like JGit found). Also the nature of the problem is sufficiently different that things like the packed format don’t behave in a suitable way for general file system usage. The work on packing is yet to be started but we’ll probably use Robert Collin’s groupcompress idea from bzr. I promise we’ll make the wiki a bit better when the code’s stabilised a bit!

Steve Kemp: So cunning you could brush your teeth with it.

Lets take a look at a new tool available to Lenny & Sid:
apt-get source acon
int main(int argc,char **argv)
 
        int i,tty,useunicode=0;
        char *fontf=0,*translationf=0,*keymapf=0;
        get_ids();
        set_user_id();
        /*Read configure file if no input options*/
        if(argc<2)
         
                char *env;
                FILE *fp;
                char font[300],translation[300],keymap[300];
                char tmp[300];
                font[0]=translation[0]=keymap[0]=0;
                if((env=getenv("HOME")))
                        sprintf(tmp,"%s/.acon.conf",env);
                else
                        strcpy(tmp,"/etc/acon.conf");
Hmmm. Nice use of the environment there. I wonder what permissions the binary has:
skx@gold:~$ ls -l /usr/bin/acon
-rwsr-xr-x 1 root root 48672 2008-06-09 10:50 /usr/bin/acon
setuid(0) - just say no. ObTitle: Blackadder II

Russell Coker: Future Video Games

I just watched an interesting TED.com talk about video games [1]. The talk focussed to a large degree on emotional involvement in games, so it seems likely that there will be many more virtual girlfriend services [2] (I’m not sure that “game” is the correct term for such things) in the future. The only reference I could find to a virtual boyfriend was a deleted Wikipedia page for V-Boy, but I expect that they will be developed soon enough. I wonder if such a service could be used by astronauts on long missions. An advantage of a virtual SO would be that there is no need to have a partner who is qualified, and if a human couple got divorced on the way to Mars then it could be a really long journey for everyone on the mission. VR training has been used for a long time in the airline industry (if you have never visited an airline company and sat in a VR trainer for a heavy passenger jet then I strongly recommend that you do it). It seems that there are many other possible uses for this. The current prison system is widely regarded as a training ground for criminals, people who are sent to prison for minor crimes come out as hardened criminals. I wonder if a virtual environment for prisoners could do some good. Instead of prisoners having to deal with other prisoners they could deal with virtual characters who encourage normal social relationships, prisoners who didn’t want to meet other prisoners could be given the option of spending their entire sentence in “solitary confinement” with virtual characters, multi-player games, and Internet access if they behave well. Game systems such as the Nintendo Wii [3] would result in prisoners getting adequate exercise, so after being released from a VR prison it seems likely that the ex-con would be fitter, healthier, and better able to fit into normal society than most parolees. Finally it seems likely that someone who gets used to spending most all their spare time playing computer games will be less likely to commit crimes. It seems to me that the potential for the use of virtual environments in schools is very similar to that of prisons, for similar reasons. Update: Currently Google Adsense is showing picture adverts on this page for the “Shaiya” game, the pictures are of a female character wearing a bikini with the caption “your goddess awaits”. This might be evidence to support my point about virtual girlfriends.

7 October 2008

Alexander Reichle-Schmehl: What you can do for Lenny (Update #2)

You probably noticed by now, that Debian GNU/Linux 5.0 aka Lenny hasn't been released in September. Well, that's a shame, but very easy to explain: Too many release critical bugs. Well, it's pretty hard to estimate, how fast RC bugs will be fixed, and apparently our release team was a bit too optimistic :( The big question is: What can you do, to help release Lenny at least in this quarter? That's pretty easy: Fix rc-bugs, take care, that the fixed packages are migrated to Lenny, do upgrade tests, document problems in the release-notes. Pretty simple, isn't it? For users Even as a simple user (aren't we all just users?) you may help getting Lenny released. Some things you can do: See? Even as a simple user without deeper technical knowledge you can help us getting Lenny in shape to be released. If you have technical knowledge: Very good! You might want to read the next section, too, and see what applies to you, there :) For maintainers It basically boils down to two things: If your packages have RC bugs open in Lenny fix them and take care, that the fix will propagate to Lenny. If your packages don't have RC bugs open, fix someone else's RC bug. Surely you don't think, the release team will fix the remaining rc bugs, do you? And surely you understand, that your shiny rc bug free packages are kind of useless, if they aren't released? To search for bugs to be fixed, take a look at the unofficial rc bugs thingy. The URL lists RC bugs open in both Sid and Lenny. Obviously they should be fixed ASAP. If no one takes care about these packages, they might be removed from Lenny (if possible). Again: Try to reproduce the bug, try fix it, upload an NMU (or send your patch to the bug report and search for an sponsor). You'll notice, that some of these bugs already have a patch. In that case, your job would be to test the patch, report that to the bug report and offer to sponsor an NMU. Another interesting list is the list of rc bugs open only in Lenny. These bugs have been fixed, but the fix hasn't propagated to Lenny, yet. Normally, the release team will grant freeze exceptions for these packages if possible. However, if the changes to the fixed version are quite grave or the package in Sid depends on a newer package than in Lenny that's not possible. In these cases look out for packages marked as need tpu upload or similar. Oh, and if you could refrain from upload new upstream versions of packages to Sid, you would make all our lives easier. Some reasons: And of course you should spend your time fixing rc bugs anyway ;) Update: Rhonda pointed out, that running rc-alert -d TU -o and will limit the output to bugs open in both Sid and Lenny, which is the more interesting list of bugs.

6 October 2008

Jeff Bailey: ... when we last saw our intrepid explorers,

they were hanging out in California. Being warm. (That's Angie's comment. I'm still wearing sandals. Although I saw a Montrealer shudder at me today. That was worth it. I think I'll keep wearing them all week, even if it causes me to lose my toes)

but.. BUT! that's not the exciting part!

This is: http://www.realtor.ca/PropertyResults.aspx?Mode=5&id=1487634

This evening we accepted the counter-offer on the place.

The timeline so far: arrived Saturday, looked at places 10:30 Sunday morning. Made offer 7pm. They made a counter-office at 8:30pm. We accepted the counter-office at 6:30pm today.

Next up: Review property agreement. Find someone to sign all the paperwork for us when we're out of town. Pray that CMHC aren't rat bastards. Inspection on Saturday at 1pm.

Oh, and none of this includes going to the house party on Saturday night, the last minute finding of a hotel as our friend's place had a pipe burst where we were going to stay. Finding out that another friend had a place to stay. Me forgetting my laptop at the hotel. We saw the midwife this morning. And I went to work today.

Sometimes I think that Aikido Rondori has nothing on my life. =)

Russell Coker: RPC and SE Linux

One ongoing problem with TCP networking is the combination of RPC services and port based services on the same host. If you have an RPC service that uses a port less than 1024 then typically it will start at 1023 and try lower ports until it finds one that works. A problem that I have had in the past is that an RPC service used port 631 and I then couldn’t start CUPS (which uses that port). A similar problem can arise in a more insidious manner if you have strange networking devices such as a BMC [1] which uses the same IP address as the host and just snarfs connections for itself (as documented by pantz.org [2]), this means that according to the OS the port in question is not in use, but connections to that port will go to the hardware BMC and the OS won’t see them. Another solution is to give a SE Linux security context to the port which prevents the RPC service from binding to it. RPC applications seem to be happy to make as many bind attempts as necessary to get an available port (thousands of attempts if necessary) so reserving a few ports is not going to cause any problems. As far as I recall my problems with CUPS and RPC services was a motivating factor in some of my early work on writing SE Linux policy to restrict port access. Of course the best thing to do is to assign IP addresses for IPMI that are different from the OS IP addresses. This is easy to do and merely requires an extra IP address for each port. As a typical server will have two Ethernet ports on the baseboard (one for the front-end network and one for the private network) that means an extra two IP addresses (you want to use both interfaces for redundancy in case the problem which cripples a server is related to one of the Ethernet ports). But for people who don’t have spare IP addresses, SE Linux port labeling could really help.

Patrick Schoenfeld: Where do find help for commands?

Today an discussion rised up in #debian-devel on the OFTC IRC Network. It started because someone noted the bug report #501318 which is, to summarize it, just a user mistake, because someone obviously read the man page (time(1)) for the /usr/bin/time command, while time is also a shell builtin (which does not accept the same arguments as the time command. Certainly this bug reports appears to be funny at the first sight, but on the other hand, there is a suboptimal situation that leads to this.

  1. There are some builtin commands that also have binary equivalents (like time, printf, echo). Its quiet easy to tell weither the one or the other is used, by using the which command, but thats not really a realistic workflow, so its better to know this. The difference between these commands is often causing problems, which we have to cope with. For example bashs builtin echo behaves different as /bin/echo and people who use the bash as their default shell tend to use what bash provides, which in turn causes problems if other people who use a different default shell try to work with these scripts. But this is another problem, because...
  2. ... every program, utility and function in Debian has to provide a manpage, as said by our policy: "Each program, utility, and function should have an associated manual page included in the same package." I guess that the rationale behind that is that 'man' is a very common tool in the Un*x world, which is wide-spread and which usage is much recommended to find out how specific tools behave. It is always referred to in Documentation, weither it is Debian specific or not, e.g. in books.

    The time package, which is of priority Standard and which includes /usr/bin/time, does conform to that policy by providing a manpage for the time command. The various shells don't do that, because they usually don't have a man page for each and every command (usually they have a more generic manpage which includes the builtins or in some seldom cases a special manpage for such and similar things (as for zsh, which has zshmisc(1)) and because its not that easy, because the man command cannot (AFAIK) distinguish between the user joey_average calling 'man time' in a bash, while the user schoenfeld calls the command 'man time' in a zsh, or if joey_foobar calls 'man read' in a shell which does not have a builtin time command and uses /usr/bin/time instead.
So whats wrong about this situation? Would you say that users that expect 'man time' (or similar examples) to do the right thing are making wrong assumptions? I disagree. Its what they've always been told to do. And if it does not show anything eventually run info, or look at HTML documentation or what else. But they haven't been prepared for the case where the manpages does show something, something wrong. The good thing is that the manpage for time includes a sentence:

"Users of the bash shell need to use an explicit path in order to run the external time command and not the shell builtin variant."

The bad thing about it is, that it is at approx. 70-80% of the manpage.

Clint, the maintainer of zsh, mentioned run-help which seems to be a part of the zsh, but not of any other shell, and does more or less the right thing (at least for the builtins) but not for external commands and not even for itself (it opens the code of the function instead of something user-readable like a manpage). I guess "one tool for a specific need" is a good maxime, but is it really a good maxime for finding documentation?

But how could the situation be bettered? I could think of a wrapper for man, similar to run-help but as a more generic solution. Any ideas for it? Is it the right way at all to better the users experience? Any other ideas? Other opinions?

Chris Lawrence: Choosing the wrong denominator

Matthew Yglesias demonstrates innumeracy in action:
We got an interesting experiment this weekend as Bill Maher’s anti-religious screed Religulous and David Zucker’s right-wing satire An American Carol both opened. The two films were about tied in terms of total revenue but Carol was on three times as many screens, so basically Religulous was far more successful. I think this mostly reflects something I wrote about a couple of years ago — the moviegoing audience is very demographically similar to the Democratic Party voting audience. It’s disproportionately young, disproportionately childless, and tilted toward residents of big cities and away from residents of rural communities. Conversely, the audience for television news is demographically very conservative (older, white, and a bit more prosperous than average) which is one major reason TV news coverage tilts right. The big screen audience for what looks like a witless screed against God is just a lot bigger than the big screen audience for what looks like a witless screed against Michael Moore.
Actually, since total revenue for both movies was about the same, it would appear that the “big screen audience” for crappy polemical Bill Maher movies is about the same as the “big screen audience” for crappy polemical David Zucker movies. Further, since I’d guess Carol probably played in theaters with lower ticket prices on average than Religulous, the former probably did a little better in terms of the total audience. Yglesias also makes the rather faulty assumption that the per-screen average revenue would remain flat as screens increased. This result only obtains if moviegoers don’t select theaters based on what movies are playing at them or if screens are very distant from each other geographically; while surely there are some people who just go to the movies to see something without deciding beforehand which movie to see, I doubt there are enough of these people to ensure Maher’s movie would gain a substantially larger audience, except in the relatively uncommon cases where the film just isn’t on at any theater in a metropolitan area and there is a substantial number of people who want to see it. Besides, all the discerning moviegoers were at Nick and Norah’s Infinite Playlist this weekend anyway.

5 October 2008

Wouter Verhelst: Belgian electronic ID card and security

I received some feedback on my previous BeID post, where I explained how to log in to a remote system by use of your digital ID card. Philip and Guy both claim it possible or likely that the crypto keys on eID cards are stored on a system of the government somewhere and that you therefore should not be using them. I find this to be jumping the gun a little. Security is always a trade-off; indeed, if you want to hide stuff from the government, then using eID-based authentication might not be a very good idea. However, there are other cases where eID-based authentication really is the correct option; and it is nice to know that this kind of thing is possible. Security always is a trade-off; and if you make an informed choice, there's nothing wrong about giving someone else access to your server. The fun bit is that Philip actually advocates carrying a clear-text printout of a list of still-valid passwords. Now that, I feel, is unacceptable, security-wise. Personally, I'd rather use a smartcard that only some secret government agency might be keeping copies of rather than a list that any random thief might make use of. The question really boils down to this, I think: how likely do you think it is that someone else will be able to get at your password by guessing or stealing it? What I mean by that last bit is that you should always generate your passwords with a tool that generates fully-random passwords ('pwgen -s', for example), and never write them down in cleartext anywhere. That of course makes it slightly hardish to memorize them; what I do is to store the password encrypted to my GPG key on my laptop, and I memorize the password by changing it on a remote server that I need to access fairly often (Debian's systems will do), but leaving my GPG passphrase and laptop password as is for the time being. Every time I need to log in to the remote server, I first try to remember the passphrase. If I can't remember it, I look it up in the encrypted file (again taking care not to store the file on disk). Once I start being able to log in to the remote server without having to look it up in the file, I change all my other passwords. This process usually takes a few weeks. Then, the only way someone can get my password is either by coercing me or by killing me and disecting my brain. And then still. Unfortunately, in the real world, I realize that many people do not wish to go through all this trouble just to get a secure login, and instead just choose a weak password. I guess that's why I think the next best thing might be slightly better than using strong passwords...

James Morrison: Is your riding important?

It seems someone has figured out where in Canada it is worth strategically voting. So take a look to see if you live in an important riding.

I wonder if it is worth setting up a counter website that says if you live in a riding where the Tories, Grits or Bloc are almost certain to win, then you can vote to give the NDP or Greens money. Remember your vote is worth C$6.

4 October 2008

Dirk Eddelbuettel: World Marathon Majors

Last Sunday's Berlin Marathon was my fifth and final piece in completing the World Marathon Majors during 2007/2008: after running Boston, Chicago and New York in 2007, and then London and now Berlin in 2008, the set is complete. The idea was born after having run Chicago a few times, qualifying for Boston and winning a New York lottery entry. With friends to visit in New York, London and Berlin, it became feasible. It's been a great experience to run these famous courses in front of large crowds. Conditions ranged from cold, windy and rainy in Boston to way too hot in Chicago, had mixed conditions including a solid rain shower in London and were just perfect in both New York and Berlin. The crowds were awesome in all five places. All in all, these races were a blast -- if you're into long-distance running, give each or all of them a shot.

Erich Schubert: Debugging Windows with the help of Linux

On my parents' small laptop, Windows would just reboot. Even the repair functions of Windows would just reboot. No error message you could read, just reboot, repeat. Linux still worked fine (and my family is fine with using Linux, fortunately).Linux also allowed us to quickly find out what is wrong with Windows: the hard disk is damaged (I like operating systems that give you useful error messages such as "Unrecoverable Error" on your harddisk). And most likely the laptop is out of warrenty since a month ago, as usual.So I'm now investigating if the Linux partition also contains hardware errors, or if we might get away with just disabling Windows altogether for some time, until I get around to buy a replacement harddisk (and a replacement battery, too). So far, our experiences with Medion/Aldi/Tchibo have been rather bad. The TFT screen for the main computer is often flickering, but they failed to repair it in two attempts now. The MP3-CD-Player had stopped reading and the replacement didn't play MP3 at all. And the laptops batteries were crap (and why did they put in two small batterys instead of a reasonably sized one?), I know of a friend where the CD drive of that same model doesn't work anymore, and now our harddisk is dead with just some 11 days of use total (it was meant to be a portable system, and my parents have better computers for daily use at home).If we buy a replacement, it will most likely be a so called "Netbook" with Linux preinstalled. These tiny systems often come preinstalled with Linux (because a Windows licence would increase the price by like 50%) and would fit our requirements pretty well. Not sure which one, though. Maybe an EEE.

Russell Coker: Getting Started with Amazon EC2

The first thing you need to do to get started using the Amazon Elastic Compute Cloud (EC2) [1] is to install the tools to manage the service. The service is run in a client-server manner. You install the client software on your PC to manage the EC2 services that you use. There are the AMI tools to manage the machine images [2] and the API tools to launch and manage instances [3]. The AMI tools come as both a ZIP file and an RPM package and contain Ruby code, while the API tools are written in Java and only come as a ZIP file. There are no clear license documents that I have seen for any of the software in question, I recall seeing one mention on one of the many confusing web pages of the code being “proprietary” but nothing else. While it seems most likely (but far from certain) that Amazon owns the copyright to the code in question, there is no information on how the software may be used - apart from an implied license that if you are a paying EC2 customer then you can use the tools (as there is no other way to use EC2). If anyone can find a proper license agreement for this software then please let me know. To get software working in the most desirable manner it needs to be packaged for the distribution on which it is going to be used, as I prefer to use Debian that means packaging it for Debian. Also when packaging the software you can fix some of the silly things that get included in software that is designed for non-packaged release (such as demanding that environment variables be set to specify where the software is installed). So I have built packages for Debian/Lenny for the benefit of myself and some friends and colleagues who use Debian and EC2. As I can’t be sure of what Amazon would permit me to do with their code I have to assume that they don’t want me to publish Debian packages for the benefit of all Debian and Ubuntu users who are (or might become) EC2 customers. So instead I have published the .diff.gz files from my Debian/Lenny packages [4] to allow other people to build identical packages after downloading the source from Amazon. At the moment the packages are a little rough, and as I haven’t actually got an EC2 service running with them yet they may have some really bad bugs. But getting the software to basically work took more time than expected. So even if there happen to be some bugs that make it unusable in it’s current state (the code for determining where it looks for PEM files at best needs a feature enhancement and at worst may be broken at the moment) then it would still save people some time to use my packages and fix whatever needs fixing.

Next.

Previous.