Search Results: "blade"

25 August 2008

Steve Kemp: Who do you think God really favors in the web?

Steven Brust is a big tease. His most recent Vlad Taltos novel is full of tease for two reasons: It was a fun read though, and didn't make me as hungry as the previous volume did. (Mmmmmm pies food.) I always liked him as an author, and he rocks for publishing Dzur around the time I was telling local people "Too many people seem to write novels in which nobody really eats. Forget all that action, dialog, and exposition. Lets have a bunch of folk sit down and eat an exceptionally well described meal." (Many things that people do are never described in books. We all know why. Still on the same subject I love the scene in Terry Pratchetts Pyramids where Teppic puts his outfit on. "And slowly falls over". Nice) ObFilm: Blade

21 July 2008

Clint Adams:

This is the night of second-hand thoughts. Oh, the shame. I'm gonna do this in mostly-chronological order. Mostly. I vaguely remember the first great meal I had in Paris. I got off the plane, went through immigration and customs, hopped on the RER, got out and dragged my suitcase to Le Chat Gripp . I walked through the door in my T-shirt and jeans, and said well, I don't remember what I said, but I ended up getting a table and ordering the tasting menu. I don't remember very much about the food, but I remember that the waiter had to wake me up between courses. I've kinda had a thing for tasting menus ever since. Tonight I made a reservation at a fine dining establishment that was advertised as having a couple of tasting menus. I wasn't going to commit myself to a tasting menu, but there was a good chance I would find it irresistable. I timed my departure pretty well, and after walking the 2.5 miles to the restaurant, I was only a couple minutes early. Now the funny thing about this is I did not happen to notice that I had entered Molecular Gastronomy Hut. The signs outside did not say Molecular Gastronomy Hut, neither in cuneiform, hieroglyphs, nor any language I could read. The menu did not advertise the fact that this was Molecular Gastronomy Hut. Had I known that this was Molecular Gastronomy Hut, I would have not ordered the tasting menu, especially since I was not hungry and should probably have not even eaten a whole course. Had I known that the wine pairings would only include two reds, I wouldn't have ordered those either. Normally I expect wine pairings to include a white. It's the thing to do; it adds contrast. You drink it and get it over with and then you enjoy the rest of your meal. This had at least three whites and one ros . Mother of God. For the moment, though, I had no foreknowledge of the wines, and was was entranced by the knives, which were twisted such that if the handle was lying flat on the table, the blade stood vertically. Not only was this incredibly distracting, it seemed to have some practical value; if there were foodstuffs on your knife, they would remain elevated and not touch the tablecloth. Anyway, the food comes out, course by course, wine by wine. I wonder if Richard from Top Chef is hiding back in the kitchen. There are random foams and gastriques lying conspicuously on my plates. My second course had a lemon sorbet sitting on top of various types of vegetable matter. My third course involved arthropods. Ever wonder what to pair with fried arthropod? That's right, ros . My fourth course was actually tasty, much to my surprise. It was a pumpkin flower cappuccino. It is hubris to call it cappuccino, but they did and I am going to maintain the tradition. It tasted like warm infused buttery goodness, even though I was picking insect legs out of my mouth while drinking it. You may or may not be surprised to learn that the lemon sorbet made a reappearance in a later course. The waiter recommended mixing it with the other ingredients. Tom Colicchio was hiding in the back of my head asking why, if it was meant to be mixed, wouldn't they serve it mixed. I am forced to agree. The only other thing worth having was the cheese plate. It was populated with cheese I had never had before, and fruit concoctions to go with each. Most of the cheese were nothing special, but one was orgasmic. No, I'm not going to tell you what it was. Oh, all right, it was the middle one. One hundred fifty-six courses later, I was asked if I wanted any coffee. I didn't really want caffeine, but as I didn't want to sabotage the experience, I acquiesced and consented to an espresso. I'm not sure how I was understood, as by this time I had stopped speaking the local language and was presently shouting about bacon-burger dogs, the Huxtables, and Freebird. Then after coffee and being ignored, I asked for the check. Surprise, surprise: there was an additional dessert course to go. Didn't I look foolish? The bill came out to about half the country's GDP. The last time I had seen that many digits was when a bunch of hipsters tried to calculate while spaz-dancing to Fischerspooner and playing Space Channel Five. I wondered how it must feel for one of those guys who decides to order all kinds of extravagant room service in a luxury hotel right before committing suicide. After I paid, which seemed to confuse them a bit, they offered to call me a cab. I refused politely several times. I don't like cabs to begin with, aside from the whole plutocrat-fatcat I-might-as-well-get-a-maid-and-a-butler-and-a-valet feel to them, and the practical aspects of the drivers being douchebags. I had just spent a ridiculous amount of money on food that wasn't worth it, and I saw no reason to add insult to injury by paying for a taxi. It could probably have been $10 or $15 more. Mother of Christ. So I walked. It was only four or so miles to my bed, and I passed the time by singing songs of cormorants and racial disharmony and seventeen-year-old prostitutes and the time the Rescue Rangers got sentenced to maximum-security prison. All in all it was a terribly unpleasant contrast to the happy song about alfajores I was singing before dinner. Mmm alfajores.

8 July 2008

Russell Coker: Label vs UUID vs Device

Someone asked on a mailing list about the issues related to whether to use a label, UUID, or device name for /etc/fstab. The first thing to consider is where the names come from. The UUID is assigned automatically by mkfs or mkswap, so you have to discover it after the filesystem or swap space has been made (or note it during the mkfs/mkswap process). For the ext2/3 filesystems the command “tune2fs -l DEVICE” will display the UUID and label (strangely mke2fs uses the term “label” while the output of tune2fs uses the term “volume name“). For a swap space I don’t know of any tool that can extract the UUID and name. On Debian (Etch and Unstable) the file command does not display the UUID for swap spaces or ext2/3 filesystems and does not display the label for ext2/3 filesystems. After I complete this blog post I will file a bug report. If you are using a version of Debian earlier than Lenny (or a version of Unstable with this bug fixed) then you will be able to easily determine the label and UUID of a filesystem or swap space. Other than that the inconvenience of determining the UUID and label will be a reason for not using them in /etc/fstab (keep in mind that sys-admin work sometimes needs to be done at 3AM). One problem with mounting by UUID or label is that it doesn’t work well with snapshots and block device backups. If you have a live filesystem on /dev/sdc and an image from a backup on /dev/sdd then there is a lot of potential for excitement when mounting by UUID or label. Snapshots can be made by a volume manager (such as LVM), a SAN, or an iSCSI server. Another problem is that if a file-based backup is made (IE tar or cpio) then you lose the UUID and label. tune2fs allows setting the UUID, but that seems like a potential recipe for disaster. So this means that if mounting by UUID then you would potentially need to change /etc/fstab after doing a full filesystem restore from a file-based backup, this is not impossible but might not be what you desire. Setting the label is not difficult, but it may be inconvenient. When using old-style IDE disks the device names were of the form /dev/hda for the first disk on the first controller (cable) and /dev/hdd for the second disk on the second controller. This was quite unambiguous, adding an extra disk was never going to change the naming. With SCSI disks the naming issue has always been more complex, and which device gets the name /dev/sda was determined by the order in which the SCSI HAs were discovered. So if a SCSI HA which had no disks attached suddenly had a disk installed then the naming of all the other disks would change on the next boot! To make things more exciting Fedora 9 is using the same naming scheme for IDE devices as for SCSI devices, I expect that other distributions will follow soon and then even with IDE disks permanent names will not be available. In this situation the use of UUIDs or LABELS is required for the use of partitions. However a common trend is towards using LVM for all storage, in this case LVM manages labels and UUIDs internally (with some excitement if you do a block device backup of an LVM PV). So LV names such as /dev/vg0/root then become persistent and there is no need for mounting via UUID or label. The most difficult problem then becomes the situation where a FC SAN has the ability to create snapshots and make them visible to the same machine. UUID or label based mounting won’t work unless you can change them when creating the snapshot (which is not impossible but is rather difficult when you use a Windows GUI to create snapshots on a FC SAN for use by Linux systems). I have had some interesting challenges with this in the past when using a FC based SAN with Linux blade servers, and I never devised a good solution. When using iSCSI I expect that it would be possible to force an association between SCSI disk naming and names on the server, but I’ve never had time to test it out. Update: I have submitted Debian bug #489865 with a suggested change to the magic database. Below are /etc/magic entries for displaying the UUID and label on swap spaces and ext2/3 filesystems:
The following magic entry will display the UUID of a swap space as well as displaying the label in the same manner as the mkswap program:
# according to man page of mkswap (8) March 1999
# volume label and UUID Russell Coker
# http://etbe.coker.com.au/2008/07/08/label-vs-uuid-vs-device/
4086 string SWAPSPACE2 Linux/i386 swap file (new style),
>0×400 long x version %d (4K pages),
>0×404 long x size %d pages,
>1052 string \0 no label,
>1052 string >\0 LABEL=%s,
>0×40c belong x UUID=%x
>0×410 beshort x \b-%x
>0×412 beshort x \b-%x
>0×414 beshort x \b-%x
>0×416 belong x \b-%x
>0×41a beshort x \b%x The following magic entry will display the UUID and label (AKA volume name) of an ext2/3/4 filesystem:
# ext2/ext3 filesystems - Andreas Dilger <adilger@dilger.ca>
# ext4 filesystem - Eric Sandeen <sandeen@sandeen.net>
# volume label and UUID Russell Coker
# http://etbe.coker.com.au/2008/07/08/label-vs-uuid-vs-device/
0×438 leshort 0xEF53 Linux
>0×44c lelong x rev %d
>0×43e leshort x \b.%d
# No journal? ext2
>0×45c lelong ^0×0000004 ext2 filesystem data
>>0×43a leshort ^0×0000001 (mounted or unclean)
# Has a journal? ext3 or ext4
>0×45c lelong &0×0000004
# and small INCOMPAT?
>>0×460 lelong <0×0000040
# and small RO_COMPAT?
>>>0×464 lelong <0×0000008 ext3 filesystem data
# else large RO_COMPAT?
>>>0×464 lelong >0×0000007 ext4 filesystem data
# else large INCOMPAT?
>>0×460 lelong >0×000003f ext4 filesystem data
>0×468 belong x \b, UUID=%x
>0×46c beshort x \b-%x
>0×46e beshort x \b-%x
>0×470 beshort x \b-%x
>0×472 belong x \b-%x
>0×476 beshort x \b%x
>0×478 string >0 \b, volume name "%s"
# General flags for any ext* fs
>0×460 lelong &0×0000004 (needs journal recovery)
>0×43a leshort &0×0000002 (errors)
# INCOMPAT flags
>0×460 lelong &0×0000001 (compressed)
#>0×460 lelong &0×0000002 (filetype)
#>0×460 lelong &0×0000010 (meta bg)
>0×460 lelong &0×0000040 (extents)
>0×460 lelong &0×0000080 (64bit)
#>0×460 lelong &0×0000100 (mmp)
#>0×460 lelong &0×0000200 (flex bg)
# RO_INCOMPAT flags
#>0×464 lelong &0×0000001 (sparse super)
>0×464 lelong &0×0000002 (large files)
>0×464 lelong &0×0000008 (huge files)
#>0×464 lelong &0×0000010 (gdt checksum)
#>0×464 lelong &0×0000020 (many subdirs)
#>0×463 lelong &0×0000040 (extra isize)

24 June 2008

Pablo Lorenzzoni: Ruby security advisory and fix

Debian 4.0 version of Ruby is open to the, now widely known, Ruby security vulnerabilities. The bug is reported as 487238 in Debian s BTS, and is closed, since the version now in sid (version 1.8.7.22-1) is already fixed. Users of stable can apply the patch provided by Daniel Franke (it doesn t seem to fix all, but goes a long way). Apparently, this brought up (again) the rants over full disclosure. Indeed, what is vulnerable is not that hard to find, as Zed Shaw showed us, so, why not talk about it in a plain and bold form? Why just provide the CVE numbers and ask for everybody to upgrade? Zed goes more deep about the quality of C code, but that is not the issue I want to talk about As a Free and Open Source Software supporter (and developer), I can see the benefits of full disclosure. As a not-full-time webmaster, I can see the benefits of not having a proof-of-concept piece of code attached to the vulnerability report. Of course, there s a lot of things a webmaster can do to prevent having a machine completely compromised in case a security advisory is published with a proof-of-concept code in it (think about chrooting, randomized memory protection, security libraries, grsecurity, SELinux, etc) and my machines, although vulnerable to the bug, would not be fully compromised if exploited. I guess one should be prepared to whatever comes from the Internet Full disclosure, in this sense, have more pros than cons, IMHO. For instance it was not clear if Debian 4.0 were vulnerable There were no security advisory coming from Debian (and there s still not), and it is not promptly obvious if the version packaged is affected. I know that at least I wanted to run a proof-of-concept to check if my server is vulnerable or not before going all the way into packaging a fix (or backporting the sid version), and it was not until I read Matasano Chargen Blog that I could test older versions. But different people have different ideas

8 June 2008

Andrew Pollock: [life] And we're back

We actually got home last Sunday, but I've been too jetlagged, and then too busy with work to really have a chance to write anything... We got back in at around 2pm, but our bags fell victim to Heathrow's Terminal 5, and didn't arrive until around 11pm. I think I lasted until about 8pm, when I had to crash. Poor Sarah had to stay up until 11pm when they finally got around to delivering our suitcases. The week in Zurich was wonderful. The Zurich office is everything the photos make it out to be, and then some. One weird thing: apparently there's some Swiss regulation about how much you're allowed to cool a building in relation to the outdoor ambient temperature, so there's no air conditioning in the office. Instead, you can open the windows. Unfortunately, there's a fairly busy set of train tracks right beside the office, so it can get a tad noisy... It was a pretty warm week, I think around 30°C. I certainly prefer being colder rather than hotter when indoors, so found the lack of decent cooling to be a shame, given the rest of the building's features. That said, it was pretty amazing sweltering away in Zurich, and then looking up and seeing snow on the mountains. It was surprising how much of a temperature difference there was. On the last evening in Zurich, we went on a reconnoitre to try and find the river that we could hear (and see on the map) behind our apartment. We eventually found some street access to it, and it was another world back there. It was fairly thickly wooded, and the sunlight was heavily filtered through the trees, so it was cool and shady. The river was fairly fast flowing over some rocks in parts, which is what was making it so audible. The whole setting was absolutely beautiful. There were a couple of paths, and the whole thing felt like something out of a fairy tail. We think we stumbled onto a fox, but we're not sure. It's a shame we only discovered the place on the last day, as I'd have liked to have explored it further. I really liked Zurich. It was nice and flat, and had an excellent tram service. Monday Night Skate made me wish I'd packed my roller blades. We were wandering around on Monday night, and it felt like the entire city had donned skates and were going out. Apparently the authorities really get behind it, and close roads, and the police go along behind the pack and reopen the roads behind them and pick up the stragglers. Great way to encourage an active lifestyle. We've got all of our photos up now from the Europe trip, and they're here. This brings the total countries I've visited up to 10, excluding Hong Kong and Macau. I don't like selecting China when I generate this map, as I've never been to mainland China. Countries I've visited as of June 2008

6 June 2008

Dirk Eddelbuettel: Wayne Shorter at the CSO

Just got home from the 'An Evening with Wayne Shorter' concert at the CSO, part of this year's tour apropos his 75th birthday. The man is a legend and one my favourite musicians for both his own Blue Note work from the 60s and of course his participation in the legendary Miles Davis Quintet of the same period. Shorter (ts, as) was playing with his quartet of recent years: Danilo Perez (p), John Patitucci (b) and Brian Blade (dr). And playing they did. Shorter has such a soft lyrical tone, which accentuates both the rhythmic and harmonic quality of the side men. Very enjoyable concert, fairly 'modern' and free in style. And no standards or old material. Oddly enough, not one spoken word: neither greeting nor good byes or just an introduction of the band. Recommended.

21 March 2008

Steve Kemp: Don't you just hate loose ends?

Today I spent a while fixing some more segfault bugs. I guess that this work qualifies as either fixing RC bugs, or potential security bugs. Anyway I did an NMU of libpam-tmpdir a while back to fix all but one of the open bugs against it. I provided a patch for #461625 yelp: segfault while loading info documentation, which fixes the symptoms of bad info-parsing, and avoids the segfault. I also looked into the #466771 busybox cpio: double free or corruption during cpio extraction of hardlinks - but it turns out that was already fixed in Sid. Finally I found a segfault bug open against ftp: To reproduce this bug run:
skx@gold:~$ ftp ftp.debian.org
220 saens.debian.org FTP server (vsftpd)
Name (ftp.debian.org:skx): anonymous
331 Please specify the password
Password: foo@bar.com
ftp> cd debian/doc
250 Directory successfully changed.
ftp> get dedication-2.2.cn.txt dedication-2.2.de.txt dedication-2.2.es.txt ..
local: dedication-2.2.de.txt remote: dedication-2.2.cn.txt
Segmentation fault
You need to repeat the arguments about 50 times. But keep adding more and more copies of the three files to the line until you get the crash. It isn't interesting as a security issue as it is client side only; but as a trivially reproducable issue it becomes fun to solve. Click to read the rest of the entry I mailed the maintainer of FTP and said unless I heard differently I'd NMU and cleanup the package in a week. All being well this entry will be nicely truncated in the RSS feeds as support for the <cut> tag was the main new feature in my previous upload of chronicle - the blog compiler I use/wrote/maintain. ObQuote: Razor Blade Smile

6 March 2008

Filip Van Raemdonck: Bye bike...

Or, as it's said, history repeats itself. Today I sold my motorcycle (wait for the “blade” photograph).
Again it wasn't really old, just 4 years; but it too had over 54000 kilometres; time again to release it.

I didn't quite get the money of it that I wished for, but then again, for a bike with that mileage you can't really be picky about what people pay for it. And in hindsight the fireblade seems to have been a bad choice; there's a lot of them on sale at least over here right now.
Note to self: try to get a less popular bike next time, it pays off when trying to sell it.

Actually I've already made the choice for a new bike (though I do not know if my choice follows the rule I just laid out). But it's been a hard choice; which is a story in itself. And that story is for another time.

Again, I must say it feels strange. While this wasn't the first bike I sold off, I feel a little melancholious about it. I guess that's just part of selling any bike. Assuming you've build a bond with the machine. But then again, any real motor rider would build such bond. IMHO.

1 February 2008

Romain Francoise: Recent movies (5)

(Note: this post had been sitting in my drafts folder for some time so some of these are not so recent. I thought I'd mention them anyway.)

15 January 2008

Andrew Pollock: [tech] zomg Zonbu!

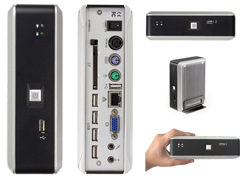
Zonbu I've been quietly coveting the Zonbu for a number of months now. I finally caved in and ordered one when we got back from Australia, with the intention of using it to replace minotaur, the computer that exports my RAID10 via ATA over Ethernet to my MythTV box. minotaur is the old daedalus, which I bought back around 2000. It's a VA Linux Pentium III. It's old, noisy, and has no idea what power management is. The Zonbu has more grunt than it (in terms of BogoMIPS), and it's a fraction of the size. Our linen cupboard is now significantly quieter (and hopefully cooler). Heck, hopefully the power bill will be lower as well. Anyway, I put the order in when we returned from Australia, with the expectation that it'd turn up some time while Sarah was in hospital, or shortly afterwards, and I could use the rest of the month that I was off work to play with it. Well, I got an email on the 31st of December, telling me they were out of stock, and unless I wanted to pay $29 more for one with built-in WiFi, I'd have to wait until mid-January. As I just couldn't see the point of having WiFi (or spending more money) and not needing the thing in a hurry anyway, because I had more important things to worry about in the meantime, I opted to wait. This morning, I emailed them to enquire about whether or not more stock had arrived, and they emailed back to say that they were still waiting, but they'd found one they could sell to me anyway. The company happens to be close by in Menlo Park, so I picked it up today in our travels. Let me just say that it is a very cool little computer, just if you use it for its intended purpose. It's running a customised Gentoo Linux, with a 2.6.22 kernel. I'm a bit surprised about their choice of Gentoo. I think they'd be better off partnering with Canonical, given that Mark Shuttleworth is trying to make a Linux distribution easy enough for his grandmother to use. That'd take the work of engineering the operating system out of the equation, then they could just focus on the hardware and a bit of integration with Amazon's S3. The thing I have to give them mad props for is documenting how to hack the tripe out of the box. They tell you how to enable root. They tell you how to enable PXE booting. So once I figured out that the front USB port seems to get treated slightly differently for a USB keyboard than the back ones, it was very easy to PXE boot it and install Debian. I initially started with trying to install Etch, but I kept getting missed interrupts on the CompactFlash device, which resulted in the filesystems panicking. So I gave up and went with Lenny, and presumably because it also uses 2.6.22, everything seemed to go fine. The box comes with a 4Gb CompactFlash card, which is ample for my needs. It's running the 686-optimised kernel, which is probably not ideal, but works. We'll see how things go. Interestingly, I blew another hard drive power supply, exactly like last time. I've no idea if it's the act of plugging everything back in again that's causing the problem, or they're generally flaky, and they don't fail until they're powered off and back on again. Maybe that IEC Y-cable wasn't such a good idea after all. I've now run out of spare power supplies, so I'm going to have to get some more for when these two inevitably fry themselves. Overall, I'm very pleased with this purchase, but it's a bit early to see how it's going to perform. I can't imagine it's going to perform worse than the computer it's replacing, but it was probably never intended for what I'm using it for either... Oh, and I discovered vblade-persist, which seems to be a very nice framework for managing ATA over Ethernet exports. Now I just need to get my hands on a big tub of Lego to build a nice chassis for the whole thing.

28 October 2007

Russell Coker: Xen and Security

I have previously posted about the difference between using a chroot and using SE Linux [1]. Theo de Raadt claims that virtualisation does not provide security benefits [2] based on the idea that the Xen hypervisor may have security related bugs. From my understanding of Xen a successful exploit of a Xen system with a Dom0 that is strictly used for running the DomU’s would usually start by gaining local root on one of the DomU instances. From there it is possible to launch an attack on the Xen Dom0. One example of this is the recent Xen exploit (CVE-2007-4993) [3] where hostile data in a grub.conf in a DomU could be used to execute privileged commands in the Dom0. Another possibility would be to gain root access to a DomU and then exploit a bug in the Xen API to take over the hypervisor (I am not aware of an example of this being implemented). A final possibility is available when using QEMU code to provide virtual hardware where an attacker could exploit QEMU bugs, an example of this is CVE-2007-0998 where a local user in a guest VM could read arbitrary files in the host [4] - it’s not clear from the advisory what level of access is required to exploit it (DomU-user, DomU-root, or remote VNC access). VNC is different from other virtual hardware in that the sys-admin of the virtual machine (who might be untrusted) needs to access it. Virtual block devices etc are only accessed by the DomU and Xen manages the back-end. The best reference in regard to these issues seems to be Tavis Ormandy’s paper about hostile virtualised environments [5]. Tavis found some vulnerabilities in the QEMU hardware emulation, and as QEMU code is used for a fully virtualised Xen installation it seems likely that Xen has some vulnerabilities in this regard. I think that it is generally recommended that for best security you don’t run fully virtualised systems. The remote-console type management tools are another potential avenue of attack for virtualised servers in the case where multiple users run virtual machines on the same host (hardware). I don’t think that this is an inherent weakness of virtualisation systems. When security is most important you have one sys-admin running all virtual machines - which incidentally seems to be the case for most implementations of Xen at the moment (although for management not security reasons). In ISP hosting type environments I doubt that a remote console system based on managing Xen DomU’s is going to be inherently any less secure than a typical remote console system for managing multiple discrete computers or blades. I have just scanned the Xen hypervisor source, the file include/asm-x86/hypercall.h has 18 entries for AMD64 and 17 for i386 while include/xen/hypercall.h has 18 entries. So it seems that there are 35 or 36 entry points to call the hypervisor, compared to 296 system calls on the i386 version of Linux (which includes the sys_socketcall system call which expands to many system calls). This seems to be one clear indication that the Linux kernel is inherently more complex (and therefore likely to have a higher incidence of security flaws) than the Xen hypervisor. Theo’s main claim seems to be that Xen is written by people who aren’t OpenBSD developers and who therefore aren’t able to write secure code. While I don’t agree with his strong position I have to note the fact that OpenBSD seems to have a better security history than any other multi-user kernel for which data is available. But consider a system running Xen with Linux in Dom0 and multiple para-virtualised OpenBSD DomU’s. If the Linux Dom0 has OpenSSH as the only service being run then the risk of compromise would be from OpenSSH, IP based bugs in the Linux kernel (either through the IP address used for SSH connections or for routing/bridging to the OpenBSD instances), and from someone who has cracked root on one of the OpenBSD instances and is attacking the hypervisor directly. Given that OpenSSH comes from the OpenBSD project it seems that the above scenario would only add the additional risk of an IP based Linux kernel attack. While a root compromise of an OpenBSD instance (consider that a typical OpenBSD system will run a lot of software that doesn’t come from the OpenBSD project - much of which won’t have a great security history) would only lose that instance unless the attacker can also exploit the hypervisor (which would be a much more difficult task than merely cracking some random daemon running as root that the sys-admin is forced to install). Is the benefit of having only one instance of OpenBSD cracked due to a bad daemon enough to outweigh the risk of a Linux IP stack? I’m sure that the OpenBSD people would consider that a better option would be OpenBSD in the Dom0 and in the DomU. In which case the risk of damage from a root compromise due to one badly written daemon that didn’t come from OpenBSD is limited to a single DomU unless the attacker also compromises the hypervisor. When working as a sys-admin I have been forced by management to install some daemons as root which were great risks to the security of the system, if I had the ability to install them in separate DomU’s I would have been able to significantly improve the security of the system. Another flaw in Theo’s position is that he seems to consider running a virtual machine as the replacement of multiple machines - which would be an obvious decrease in security. However in many cases the situation is that no more or less hardware is purchased, it is just used differently. If instead of a single server running several complex applications you have a Xen server running multiple DomU’s which each have a single application then things become much simpler and more secure. Upgrades can be performed on one DomU at a time which decreases the scope of failure (which often means that you only need one business unit to sign-off on the upgrade) and upgrades can be performed on an LVM snapshot (and rolled back with ease if they don’t succeed). A major problem with computer security is when managers fear problems caused by upgrades and prohibit their staff from applying security fixes. This combined with the fact that on a multiple DomU installation one application can be compromised without immediate loss of the others (which run in different DomU’s and require further effort by the attacker for a Xen compromise) provides a significant security benefit. It would be nice for security if every application could run on separate hardware, but even with blades this is not economically viable - not even for the biggest companies. I have converted several installations from a single overloaded and badly managed server to a Xen installation with multiple DomU’s. In all cases the DomU’s were easier to upgrade (and were upgraded more often) and the different applications and users were more isolated. Finally there is the possibility of using virtualisation to monitor the integrity of the system, Bill Broadley’s presentation from the 2007 IT Security Symposium [6] provides some interesting ideas about what can be done. It seems that having a single OpenBSD DomU running under a hypervisor (maybe Xen audited by the OpenBSD people) with an OpenBSD Dom0 would offer some significant benefits over a single OpenBSD instance.

18 October 2007

Romain Francoise: Shared links for 2007-10-18

2 October 2007

Simon Richter: New metric

My bug difficulty metric is "number of items I forgot while thinking about the problem". My not-entirely-obvious failure to tell COM that my objects are threadsafe ranks a measly 1 (umbrella). The only "3" so far (coat, mobile phone, rollerblades) involved template classes.

7 August 2007

Adrian von Bidder: Fun with virtualisation

Since I seem to be the last person these days who doesn't run his servers inside Xen, Vserver, kvm, lguest or whatever, I decided to finally evaluate Xen. Not having spare hardware and not wanting to really touch my main workhorse, I started with Qemu. Installing etch inside a Qemu (why can't qemu have working tun/tap setup scripts by default?), then xenifying this according to Ganneff's excellent slides, I was stopped while booting into the Xen kernel with a hard freeze in the boot process (Inside Qemu, so no harm done.) Talking to some people in #xen resulted in me disabling kqemu, and a few minutes later I had a working dom0. Debootstrap is slooooooowwww (well, inside a non-accelerated Qemu machine...)! So I decided to use cdebootstrap instead. Sadly, xen-create-image has debootstrap hardcoded, so I had to "ln -sf /usr/bin/cdebootstrap debootstrap". (I decided to do this when debootstrap was still calculating dependencies after several minutes.) After that, creating and booting a domU Just Worked(tm). Having a running Xen environment, I finally wanted to play around with live migration (mostly I was just curious how robust this Qemu + Xen setup is...) So, just clone the qemu disk and boot them both. Whereupon the two qemu machines have the same MAC address, hence networking is not reliable. Change the MAC of the second Xen dom0, curse udev for thinking that now the network interface should be eth1 (persistent device naming is a good thing, generally. I'm not sure there is a sane solution possible that can cover all/most cases. Computers with only one network interface might warrant some special logic ... Oh well.) Having restored the networking setup, enabling the relocation service in the Xen configuration is trivial. After thinking about using plain files on NFS and seeing a Novell tutorial which uses iSCSI, I decided that I should try AoE because it should be much simpler to set up. And by installing the 'vblade' package, it is indeed possible to have an AoE server running within a few minutes (the vbladed command doesn't take the -m option, though.) And the client side is just as simple, just install the aoetools package, and /dev/etherd is automagically created and lists all available devices. That's how SANs should work! (Note: I had the AoE devices in the dom0 and passed them to the domU. A next experiment would obviously be to pass AoE directly to the domU as root devices. Not sure what the implications would be, though.) Ok, after all this, I have two dom0 machines and a domU. Just for fun, I've installed xdaliclock inside the domU and started a live migration. Result: it works stable (modulo some scary kernel messages popping up when booting the domU. I didn't experience any crashes in this light test), xdaliclock stops for a mere 20s (yes, seconds, not milliseconds. Remember, this is two layers of virtualisation without hardware support.) Normal migration (pausing the domU), the migration takes roughly 2 min (both dom0 have 384M RAM assigned in Qemu, the domU has 128M in Xen, the host is a 3GHz P4 with 1G physical ram. There is some swapping going on (I use KDE, so some of the RAM is lost there. I also didn't stop beagle for this experiment.) The full live migration takes about twice as much time. But this said, if you're using Xen inside qemu, timing values are not what you're after... I was, frankly, astonished at how well this worked. Hmmm. I wonder, if I can stack some other virtualisation layer somewhere in there? Just to see how silly it might get.

27 July 2007

Gustavo Franco: Happy sysadmin day and AFD turns 20

Happy BOFH^W sysadmin day for you! For those who aren't sysadmins, don't ask stupid questions for him/her today. Come on, just give a gift and enjoy the reaction.

By the way, Guns N' Roses - Appetite for Destruction (AFD) turned 20, six days ago so real, raw, unique! Unlike autotuned crap all over the place that we hear today from non musicians... "But Appetite was also among the last classic rock records to be mastered with vinyl in mind, to be edited with a razor blade applied to two-inch tape, to be mixed by five people frantically pushing faders at a non-automated mixing board. "We used classic instruments and classic amps," says the album's producer and engineer, Mike Clink."

12 July 2007

Matthew Garrett

The Canonical offices are ridiculously swish, with the Dyson hand dryers providing literally seconds of entertainment (and providing something of an aircraft taking off atmosphere).

In other news, I'm now a cube. Since I'm forced to admit that I'm (at best) in my mid-to-late twenties, there will be boozing at my place tomorrow (Friday) from 9ish. It's possible that I won't get there until 10 or so, but I'm sure you'll manage to have fun anyway.

17 June 2007

Russell Coker: A Lack of Understanding of Nuclear Issues

Ben Fowler writes about the issues related to nuclear power in Australia. He spends 8 paragraphs discussing the issues on the “Right” side of politics - of which 6 concern the an Australian nuclear weapons capability and then spends 3 out of 5 paragraphs related to the “Left” side explaining that he thinks that everyone who opposes nuclear power is a Luddite. Ben didn’t bother providing any links or statistics to back up his claims, so I’ll assist him in analysing these issues by providing some facts that we can discuss. In March Spain had wind power provide 27% of all electricity (making wind power the main source of power for the country). I blogged about this at the time. While Spain has an ongoing program of building new wind power stations the majority of wind turbines in Spain are quite old (the Model T of wind power) and not nearly as efficient as modern turbines that would be installed for Australian power plants. The Danish government has announced plans to use wind power for 75% of their electricity. Denmark has a much smaller land area than Australia, which means that generating so much electricity from wind power is more technically challenging for them than it would be for us. A larger land area means that when one area has low wind speeds other areas can be used to provide power. For home electricity generation wind turbines have not yet been proven to be practical. The linear speed of the blade is determined by the wind speed and the rotational speed is therefore a factor of the wind speed divided by the radius of the blades. This means that smaller turbines have higher rotational speeds which causes more noise (bad for getting council approval), also to avoid turbulence a wind turbine will ideally be some distance above the ground (8 meters is good) which again gives problems when getting approval. The O’Connor Hush Turbine is supposed to solve the noise component of this problem. It will be interesting to see whether home based wind power becomes practical in future - if so I would like to get an O’Connor turbine on my house! Home solar power has been proven to work well, in the form of both solar-electric and solar hot water (I know several people who have been happily using them for years). You don’t get cold showers when the sun isn’t shining, you instead use gas or electricity to heat the water (it’s a standard feature in a solar hot water system). Also your home electricity doesn’t go off when the sun stops shining, you have batteries that are charged during sunny times to run things overnight, and when they get flat you pay for power from the grid. It is quite realistic to stick solar power systems on every roof in the country. The added cost to the process of building or purchasing a house is negligible and the benefits include having electricity when mains power is unavailable (NB water is used in generating electricity from coal or nuclear power plants so a bad drought will eventually become a time of limited mains power). Even the smallest home solar electric system will produce enough electricity to power a fridge and freezer 24*7 so it’s a very useful backup for essential power. The government is subsidising the installation of solar electric systems, so it seems that they expect everyone to get one eventually. Dr. Ziggy Switkowski (the main advocate of nuclear power in Australia) says “the introduction of a carbon tax could make nuclear power the cheapest option by the 2020s”. In consecutive paragraphs Ben derides “carbon trading” and claims that nuclear power is “practical”. Unfortunately the main advocate of nuclear power in Australia does not believe that it is practical without a carbon tax. Ziggy also states that it would take at least 15 years to complete a nuclear power plant, unfortunately we don’t have the luxury of waiting for 15 years before starting to try and reduce the damage that we are doing to the environment. The Stern report makes the economic consequences of inaction quite clear. I am not a Luddite. I oppose nuclear power because of the risks related to accidental release of radioactive material and the routine release of radioactive material as part of the uranium mining process, and the dangers related to long-term storage of nuclear waste (let’s not assume that Star Trek science can make it all non-radioactive). Nuclear power is not cost effective for Australia and will take so long to develop that it won’t save us from the serious economic damage predicted by the best scientific models as presented in the Stern report. For large scale power generation wind power works now, can be easily implemented and has no hidden costs or risks. There will never be a Chernobyl type accident with wind power, it is inherently a safe technology. For small scale power generation (something you can add to your home) solar power works well, is not expensive (when considering the price of a house and especially when the government subsidy is counted) and has the potential to seriously reduce the amount of carbon dioxide produced.

23 May 2007

Evan Prodromou: 3 Prairial CCXV

I just finished reading Ben Yoskowitz's Top 10 reasons to join a startup, and I feel like I have to say something. As an experienced programmer, I think of a startup as an abusive relationship. Most technology startups I've been in have been run by charismatic sociopaths with no actual management or technology experience. They make wild, ignorant, unfounded promises to employees, investors and potential customers, then get increasingly anxious and unpleasant as their unsupportable predictions of schedule and market share don't come through. Employees end up working 80-hour weeks, typically for low or no pay and worthless stock options that never pay out. Guilty that living the "startup lifestyle" (work from home, come in late, have fun) has caused schedule or feature slips, they push themselves too hard at work, to the detriment of their health and home life. It doesn't help you much get another job later. Most startups don't succeed, which means that you end up with 1, 2 or 3 years of space on your r sum consumed by a made-up company name that no one has ever heard of and whose phone line has been disconnected. If people have heard of the name, they'll associate it with failure ("Oh, yeah, wasn't that the company that spent all that money and went nowhere?"). On top of all that, the tech experience of working in a startup is usually pretty bad. The engineers are typically unexperienced -- just out of school, or close to it -- and they waste a lot of time and effort trying to reinvent the wheel. The idea that you're changing the world encourages this kind of bad engineering. You end up cutting a lot of corners and developing a lot of bad habits that you have to unlearn later on. Schedule pressures make you drop important engineering steps like analysis, design, unit tests, documentation. That is, if you even knew you were supposed to do them in the first place. It takes a lot of experience in this kind of pressure-cooker environment to come out of a startup sane, healthy, and wealthy. The vast majority of people end up with broken relationships, poor mental and physical health, and not much in the way of money to show for their efforts. tags:

Wikiclock in the news So, Niko, Hugh, Mike and Leoben Richardson all blogged about the Wikiclock. As far as I know, no MSM coverage yet, but it should be coming down the pipe any day. I talked to Niko tonight, and he said that he saw Hugh at La ka, and Hugh was updating the wikiclock. They traded off updating all afternoon. Sigh. It's actually quite addictive. tags:

Transit strike We've got a transit strike on in Montreal (see the CBC for deetz). It's a pretty heinous problem -- the maintenance workers are asking for X% pay increases over Y years with blah blah blah pension and fie fo fum and... Whatever. The city is refusing to budge, which makes our mayor, G rald Tremblay, officially a hypocritical idiot. Tremblay has been wagging fingers at provincial, federal and international figures for years about sticking to the Kyoto protocol, but when the hard decisions had to be made, he was willing to shut down Montr al's transit system... in summer... after one of the warmest winters in history. You can blame both sides on this issue, but when it comes down to it the union's job is to get the best deal it can for its workers, and Tremblay's job is to keep the Montreal M tro running. Someone's not doing his job. The city spends millions trying to get commuters out of their cars and into the public transit system. And all that work's out the window, now. Despite the public call for more people to rollerblade to work (riiiiiiiight), traffic is way up and auto use is way up. That means air quality is going to go down, and our city can go from being an environmental leader to an environmental mistake. I'm glad to hear that the Quebec government is stepping in to break up the fight, but I hope it doesn't take too long. tags:

Calling graphic designers: Universal edit button One of the interesting movements to come out of RoCoCoCamp this weekend is the idea of a universal wiki edit button. This would be an icon similar to the RSS radio-wave icon that's become ubiquitous for indicating an RSS feed. The UWEB would symbolize that the current page can be edited. Folks at AboutUs.org have taken the lead on this effort, which could be really interesting. Getting a universally-understood sign for "edit this page" would greatly help with acceptance of the wiki way by the general public. I don't think it'd have to be limited to wikis; any page that could be edited (e.g., on a CMS) could also have the UWEB. I highly encourage skilled graphic designers who want to take a crack at designing the Next Big Icon to look at the UWEB effort and give it a try. tags:

19 March 2007

Andrew Pollock: [life] New blades

Rollerblade Crossfire TFS As I'd semi-intended to after last week's renewal of hatred towards my current in-line skates, we popped into Skates on Haight yesterday while we were in San Francisco, and I acquired a pair of Rollerblade Crossfire TFS' The store was pretty nice. Small, but no other customers, so I got pretty good customer service. I have to wonder if I did the same level of due-diligence before purchasing as I did last time: I bought the first pair they recommended and I tried on. That said, they have a nicer closure system than the Bauers I had previously. They've got a ratchet-style strap at the top, a bit like some snowboard boots, and they've sort of got laces. They have some thin "string" and an interesting bit at the back that you grab and yank on to tighten the string, and there's a separate release catch to loosen it. A bit hard to describe. I've done a few test runs around the apartment complex today while I waited for the washing, and so far they seem not too bad. My biggest problem is I've got wide feet, so I have to find the happy medium between having the laces tight enough to have good ankle support, and not being too tight as to squish my feet. If the weather is good tomorrow and I can drag my arse out of bed at a reasonable time, I'll try skating to work.

10 March 2007

Andrew Pollock: [life] Busted out the rollerblades

When I first moved to Canberra to work at Asia Online, I was staying at the Waldorf, and working in Braddon, so it was a really nice short skate to work. I think skating around after work in the summer time (with daylight saving) was one of the things that made Canberra really grow on me. I managed to destroy the (fairly cheap) blades in an incident in Commonwealth Park, and then lashed out on a more expensive pair of Bauer skates, which I subsequently hated. The original pair were simple, had a good hard shell, and three ski-strap style buckles, so they provided pretty good ankle support. The Bauers, on the other hand, had to be bought in a women's size because apparently my feet were too small for the men's sizes, were lace up, and had two Velcro straps that went around the top of the laces. I really made a terrible purchasing decision in getting them, because I found I could never get them tight enough around my ankles, and they were too tight around my toes, and were generally quite uncomfortable. Anyway, fast forward something like seven years to today, and I've been meaning to try skating to work to see how long it took. This morning, Sarah felt like some Vegemite, and I've got two bottles at work, and we seem to have run out at home. Sarah proposed that we cycle into work to get one of the bottles, and I thought this would be the perfect time to try out the skates again with no time constraints. So, I pulled them out, got to try out the new safety gear that I think Sarah got me for my birthday 2 years ago, and we headed off down the Stevens Creek trail. Things started out okay (as they always tended to do) but by the time we got to the La Avenida exit from the trail, I was feeling like a quick break to give my feet a breather, and I realised that the back left wheel had pretty much shredded itself. Seems the wheels don't have a fantastic shelf life. So Sarah cycled back home and got the car, and we aborted that adventure. I think rather than persisting with a pair of skates that I totally hate, I'll replace the wheels and give them away to Good Will, and look at getting a new pair that suck less. I think after waiting six or seven years between pairs is long enough get over the few hundred I spent on this pair. We're going to stay in San Francisco next Friday night after a party, so I think I'll go check out this store on Saturday. Hopefully I can make a better purchasing decision this time around.

Next.

Previous.