Search Results: "tar"

30 August 2012

Axel Beckert: deepgrep: grep nested archives with one command

Several months ago, I wrote about grep everything and listed grep-like tools which can grep through compressed files or specific data formats. The blog posting sparked several magazine articles and talks by Frank Hofmann and me. Frank recently noticed that we though missed one more or less mighty tool so far. We missed it, because it s mostly unknown, undocumented and hidden behind a package name which doesn t suggest a real recursive grep everything : deepgrep deepgrep is part of the Debian package strigi-utils, a package which contains utilities related to the KDE desktop search Strigi. deepgrep especially eases the searching through tar balls, even nested ones, but can also search through zip files and OpenOffice.org/LibreOffice documents (which are actually zip files). deepgrep seems to support at least the following archive and compression formats: A search in an archive which is deeply nested looks like this:
$ deepgrep bar foo.ar
foo.ar/foo.tar/foo.tar.gz/foo.zip/foo.tar.bz2/foo.txt.gz/foo.txt:foobar
foo.ar/foo.tar/foo.tar.gz/foo.zip/foo.tar.bz2/foo.txt.gz/foo.txt:bar
deepgrep though neither seems to support any LZMA based compression (lzma, xz, lzip, 7z), nor does it support lzop, rzip, compress (.Z suffix), cab, cpio, xar, or rar. Further current drawbacks of deepgrep: deepfind If you just need the file names of the files in nested archives, the package also contains the tool deepfind which does nothing else than to list all files and directories in a given set of archives or directories:
$ deepfind foo.ar
foo.ar
foo.ar/foo.tar
foo.ar/foo.tar/foo.tar.gz
foo.ar/foo.tar/foo.tar.gz/foo.zip
foo.ar/foo.tar/foo.tar.gz/foo.zip/foo.tar.bz2
foo.ar/foo.tar/foo.tar.gz/foo.zip/foo.tar.bz2/foo.txt.gz
foo.ar/foo.tar/foo.tar.gz/foo.zip/foo.tar.bz2/foo.txt.gz/foo.txt
As with deepgrep, deepfind does not implement any common options of it s normal sister tool find. Dependencies The package strigi-utils doesn t pull in the complete Strigi framework (i.e. no daemon), just a few libraries (libstreams, libstreamanalyzer, and libclucene). On Wheezy it also pulls in some audio/video decoding libraries which may make some server administrators less happy. Conclusion Both tools are quite limited to some basic use cases, but can be worth a fortune if you have to work with nested archives. Nevertheless the claim in the Debian package description of strigi-utils that they re enhanced versions of their well known counterparts is IMHO disproportionate. Most of the missing features and documentation can be explained by the primary purpose of these tools: Being backend for desktop searches. I guess, there wasn t much need for proper commandline usage yet. Until now. ;-) 42.zip And yes, I was curious enough to let deepfind have a look at 42.zip (the one from SecurityFocus, unzip seems not able to unpack 42.zip from unforgettable.dk due a missing version compatibility) and since it just traverses the archive sequentially, it has no problem with that, needing just about 5 MB of RAM and a lot of time:
[ ]
42.zip/lib f.zip/book f.zip/chapter f.zip/doc f.zip/page e.zip
42.zip/lib f.zip/book f.zip/chapter f.zip/doc f.zip/page e.zip/0.dll
42.zip/lib f.zip/book f.zip/chapter f.zip/doc f.zip/page f.zip
42.zip/lib f.zip/book f.zip/chapter f.zip/doc f.zip/page f.zip/0.dll
deepfind 42.zip  11644.12s user 303.89s system 97% cpu 3:24:02.46 total
I though won t try deepgrep on 42.zip. ;-)

29 August 2012

Julien Danjou: Gnus notifications

Today, I've merged my Gnus notifications module inside Gnus git repository. This way, it will be available for everybody in Emacs 24.2. gnus-notifications example This module allows you to be notified via notifications-notify (the Emacs implementation of the Freedesktop desktop notifications) on new messages received in Gnus. It can also retrieves contacts photo via gravatar.el and google-contacts.el to include them in the notification. To enable it in Emacs > 24.1, you just have to add the following line to your Gnus configuration file:
(add-hook 'gnus-after-getting-new-news-hook 'gnus-notifications)
If you want to download it and use it stand-alone for a previous Emacs version, you can fetch the latest file revision and load it before adding the previously given line.

John Goerzen: Kindergarten Computer Class and Password Security

Jacob started Kindergarten last week. More on that in another post. He s been loving it, until yesterday. At least part of his disgruntlement was because it was his first visit to computer class. Putting together a few conversations, we learned this:
Jacob: Something was different about Kindergarten today. Us: Oh? What was it? Jacob: I had computer class today. Us: What did you do? Jacob, super frustrated: Nothing. NOTHING, NOTHING, NOOOO THIIING. Nothing. Us: You didn t get to use a computer? Jacob: All we did was log on and log off the whole time. Log on and log off. My username is Jacob and my password is Jacob. (annoyed and confused voice) Why are they the same??
I guess his teachers weren t used to children that had been logging on to computers for two years before Kindergarten. And probably also weren t expecting any of them to take some sort of offense at their password poicy. He probably couldn t appreciate how reasonable it was to tech Kindergarteners how to log in to a computer on the first day of computer class

28 August 2012

Russell Coker: SSD for a Workstation

SSDs have been dropping in price recently so I just bought four Intel 120G devices for $115 each. I installed the first one for my mother in law who had been complaining about system performance. Her system boot time went from 90 seconds to 20 seconds and a KDE login went from about 35 seconds to about 10 seconds. The real problem that she had reported was occasional excessive application delay, while it wasn t possible to diagnose that properly I think it was a combination of her MUA doing synchronous writes while other programs such as Chromium were doing things. To avoid the possibility of a CPU performance problem I replaced her 1.8GHz E4300 system with a 2.66GHz E7300 that I got from a junk pile (it s amazing what s discarded nowadays). I also installed a SSD in my own workstation (a 2.4GHz E4600). The boot time went down from 45s on Ext4 without an encrypted root to 27s with root on BTRFS including the time taken to enter the encryption password (maybe about 23s excluding my typing time). The improvement wasn t as great, but that s because my workstation does some things on bootup that aren t dependent on disk IO such as enabling a bridge with STP (making every workstation a bridge is quieter than using switches). KDE login went from about 27s to about 12s and the time taken to start Chromium and have it be usable (rather than blocking on disk IO) went from 30 seconds to an almost instant response (maybe a few seconds)! Tests on another system indicates that Chromium startup could be improved a lot by purging history, but I don t want to do that. It s unfortunate that Chromium only supports deleting recent history (to remove incriminating entries) but doesn t support deleting ancient history that just isn t useful. I didn t try to seriously benchmark the SSD (changing from Ext4 to BTRFS on my system would significantly reduce the accuracy of the results), I have plans for doing that on more important workloads in the near future. For the moment the most casual tests have shown a significant performance benefit so it s clear that an SSD is the correct storage option for any new workstation which doesn t need more than 120G of storage space. $115 for SSD vs $35 for HDD is a fairly easy choice for a new system. For larger storage the price of hard drives increases more slowly than that of SSD. In spite of the performance benefits I doubt that I will gain a real benefit from this in the next year. The time taken to install the SSD equates to dozens of boot cycles which given a typical workstation uptime in excess of a month is unlikely to happen soon. One minor benefit is that deleting messages in Kmail is an instant operation which saves a little annoyance and there will be other occasional benefits. One significant extra benefit is that an SSD is quiet and dissipates less heat which might allow the system cooling fans to run more slowly. As noisy computers annoy me an SSD is a luxury feature. Also it s good to test new technologies that my clients may need. The next thing on my todo list is to do some tests of ZFS with SSD for L2ARC and ZIL. Related posts:
  1. How I Partition Disks Having had a number of hard drives fail over the...
  2. Xen and Swap The way Xen works is that the RAM used by...
  3. big and cheap USB flash devices It s often the case with technology that serious changes occur...

Bdale Garbee: FreedomBox 0.1

FreedomBox 0.1 Ian Sullivan posted a release announcement today regarding the first FreedomBox public release, which we're calling 0.1. This release is, frankly, long overdue. Getting here has been harder and taken much longer than any of us intended. Fortunately, now that we've reached this milestone, I believe that making regular progress towards the vision we have for a "1.0" release will get easier. FreedomBox is far from the only thing that I'll be working on after my upcoming early retirement from HP, but hopefully I will succeed in putting far more time towards the project soon than I have been able to in the past.

27 August 2012

Simon Josefsson: Using OATH Toolkit with Dropbox

Today there was an announcement that Dropbox supports two-factor authentication. On their page with detailed instructions there is (at the bottom) a link to the man page of the OATH Toolkit command line utility oathtool. OATH Toolkit is available in Ubuntu 12.04 and Debian Wheezy. (Note that the 1.10.4 version in Ubuntu does not support the base32 features.) There is not a lot of details in the documentation on Dropbox s site on how to use oathtool, but I have experimented a bit with the setup and I d like to share my findings. I assume you are somewhat familiar with the OATH Toolkit; if not I suggest reading my earlier introduction to OATH Toolkit. To use OATH Toolkit s command line utility to generate OTPs that are accepted by Dropbox, here is how you proceed. When you enable two-factor authentication on Dropbox s site, you must select Use a mobile app and on the next screen with the QR code image, click the enter your secret key manually link. You will then be presented with a code that looks like this: gr6d 5br7 25s6 vnck v4vl hlao re Now this code is actually space-delimitted base32 encoded data, without any padding. Since version 1.12.0, oathtool can read base32 encoded keys. However, parsing the raw string fails, so to make it work, you need to remove the spaces and add padding characters. I have yet to see any documentation on the Dropbox implementation, but I assume they always generate 16 binary octets that are base32 encoded into 26 characters like the codes that I have seen. The code is the cryptographic key used for the HMAC-SHA1 computation described in the RFC 6238 that specify OATH TOTP. If you study the base32 encoding you discover that 26 characters needs six pad characters. So converted into proper base32, the string would be gr6d5br725s6vnckv4vlhlaore======. Now generating OTPs are easy, see below.
jas@latte:~$ oathtool --verbose --totp --base32 "gr6d5br725s6vnckv4vlhlaore======"
Hex secret: 347c3e863fd765eab44aaf2ab3ac0e89
Base32 secret: GR6D5BR725S6VNCKV4VLHLAORE======
Digits: 6
Window size: 0
Step size (seconds): 30
Start time: 1970-01-01 00:00:00 UTC (0)
Current time: 2012-08-27 21:22:54 UTC (1346102574)
Counter: 0x2ACA9C5 (44870085)
125860
jas@latte:~$
Dropbox s implementation is robust in that it requests a valid OTP from me, generated using the secret they just displayed, before proceeding. This verifies that the user was able to import the key correctly, and that the users OATH TOTP implementation appears to work. If I type in the OTP generated from oathtool this way, it allowed me to enable two-factor authentication and I agreed. From that point, signing into the Dropbox service will require an OTP. I invoke the tool, using the same arguments as above, and the tool will use the current time to compute a fresh OTP. Reflecting on how things could work smoother, I suppose oathtool could be more permissive when it performs the base32 decoding so that the user doesn t have to fix the base32 spacing/padding manually. I ll consider this for future releases.

flattr this!

Andrew Cater: Ken Starks - immediate need for help is over for the moment - but

From Ken Starks, of Helios Project / Reglue

From the desk of just-so-you-know.....

Thomas Knight and I have agreed that the fund drive to aid in paying for necessary surgery for me should be halted. I will do a full blog about this entire effort this Monday but suffice it to say, you have donated more than enough to take care of my immediate needs and those down the road. Asking for anything more would be taking advantage of a loving and generous community. While it is far from adequate, the only thing I can offer you is my eternal thanks. It just seems so....small of a thing to give in return.

They will not stop the Indiegogo campaign until it reaches its time limit unfortunately so that will remain in effect for the next 30-some hours. Please do not donate anything further as I have more than enough to cover my expenses. I will explain more about that on my blog Monday.

If you helped spread the word about this campaign, please pass this posting along with the same intensity. I would deeply appreciate it.

See also now: update from Ken:

http://linuxlock.blogspot.co.uk/2012/08/of-roller-coasters-cancer-and-linux.html
==

Donations for Ken himself may be over: the work of Helios/Reglue still remains good, important and useful - the world benefits for investment in education. I would urge that this is still a worthwhile charity to contribute to as you get Linux into the hands of young people and the disadvantaged who can then USE it.

Michael Prokop: jenkins-debian-glue: Continuous Integration for Debian and Ubuntu made easy

jenkins-debian-glue is an open source project of mine which recently celebrated its first birthday and it s time to finally write about it. jenkins-debian-glue allows you to build Debian and Ubuntu packages directly from the Jenkins continuous integration system. It retrieves package sources from a version control repository, adjusts debian/changelog (handle version number + mention changes that took place) and builds according source and binary packages out of it. Its lintitan integration provides Q/A reports about the resulting source and binary Debian packages. It started as a small pet project of mine to get integration of Debian packaging inside Jenkins. I mainly had the needs for the Grml project in mind and starting with Grml 2011.12 every release (including also all the daily builds) was built using Jenkins since then. It turned out that my project would also be a perfect match for one of my customers, Sipwise GmbH. In December 2011 the sip:provider 2.4 was the first stable release that was built 100% through Jenkins and featuring jenkins-debian-glue. Thanks to special needs and the open source friendliness of Sipwise I could invest further time into the project. Recently the project got even some further drive thanks to interest by some fellow Debian Developers, most notably are the icinga, nagios-plugins, packages and the PostgreSQL in Debian Hackathon. Now if you re also interested in it: there s an automated deployment procedure available for your service to get started with the whole jenkins-debian-glue and Jenkins stack in less than 10 minutes, working just fine on Debian as well as Ubuntu. For further details please head over to jenkins-debian-glue.org or check out this 6:36min screencast (safe for work, no audio :) ): <iframe allowfullscreen="allowfullscreen" frameborder="0" height="315" src="http://www.youtube.com/embed/9asp2ZvH90A?autohide=1&amp;showinfo=0" width="560"></iframe> This embedded video doesn t work for you? Try heading over to YouTube.

Robert Collins: Why platform specific package systems exist and won t go away

A while back mdz blogged about challenges facing Ubuntu and other Linux distributions. He raises the point that runtime libraries for Python / Ruby etc have a unique set of issues because they tend to have their own packaging systems. Merely a month later he attended Debconf 2010 where a presentation was given on the issues that Java packages have on Dpkg based systems. Since then the conversation seems to have dried up. I ve been reminded of it recently in discussions within Canonical looking at how we deploy web services. Matt suggested some ways forward, including: I think its time we revisit and expand on those points. Nothing much has changed in how Ubuntu or other distributions approach integration with other packaging systems but the world has kept evolving. Internet access is growing ever more ubiquitous, more platforms are building packaging systems clojure, scala, node.js, to name but three, and a substantial and ever growing number of products expect to operate in a hybrid fashion with an evolving web service plus a local client which is kept up to date via package updates. Twitter, Facebook and Google Plus are three such products. Android has demonstrated a large scale app store on top of Linux, with its own custom packaging format. In order to expand them, we need some background context on the use cases that these different packaging systems need to support. Platforms such as antivirus scanners, node.js, Python, Clojure and so forth care a great deal about getting their software out to their users. They care about making it extremely easy to get the latest and greatest versions of their libraries. I say this because the evidence is all around us: every successful development community / product has built a targeted package management system which layers on top of Windows, and Mac OSX, and *nux. The only rational explanation I can come up for this behaviour is that the lower level operating system package management tools don t deliver what they need. E.g. this isn t as shallow as wanting a packaging system written in their own language, which would be easy to write off as parochialism rather than a thoughtful solution to their problems. In general packaging systems provide a language for shipping source or binary form, from one or more repositories, to users machines. They may support replications, and they may support multiple operating systems. They generally end up as graph traversal engines, pulling in dependencies of various sorts you can see the DOAP specification for an attempt at generic modelling of this. One problem that turns up rapidly when dealing with Linux distribution package managers is that the versions upstream packages have, and the versions a package has in e.g. Debian, differ. They differ because at some stage, someone will need to do a new package for the distribution when no upstream change has been made. This might be to apply a local patch, or it might be to correct a defect caused by a broken build server. Whatever the cause, there is a many to one relationship between the package versions that end users see via dpkg / rpm etc, and those that upstream ship. It is a near certainty that once this happens to a library package, that comparing package versions across different distribution packages becomes hard. You cannot reliably infer whether a given package version is sufficient as a dependency or not, when comparing binary packages between Red Hat and Debian. Or Debian and Ubuntu. The result of this is that even when the software (e.g. rpm) is available on multiple distributions (say Ubuntu and RHEL), or even on multiple operating systems (say Ubuntu and Windows), that many packages will /have/ to be targeted specifically to build and execute properly. (Obviously, compilation has to proceed separately for different architectures, its more the depedency metadata that says and build with version X of dependency Y that has to be customised). The result of this is that there is to the best of my knowledge no distribution of binary packages that targets Debian/Ubuntu and RHEL and Suse and Windows and Mac OS X, although there are vibrant communities building distributions of and for each in isolation. Some of the ports systems come close, but they are still focused on delivering to a small number of platforms. There s nothing that gives 99% coverage of users. And that means that to reach all their users, they have to write or adopt a new system. For any platform X, there is a strong pressure to have the platform be maintainable by folk that primarily work with X itself, or with the language that X is written in. Consider Python there is strong pressure to use C, or Python, and nothing else, for any tools that is somewhat parochial, but also just good engineering reducing variables and making the system more likely to be well maintained. The closest system I know of Steam is just now porting to Ubuntu (and perhaps Linux in general), and has reached its massive popularity by focusing entirely on applications for Windows, with Mac OSX a recent addition. Systems like pypi which have multi platform eggs do target the wide range of platforms I listed above, but they do so both narrowly and haphazardly: whether a binary or source package is available for a given platform is up to the maintainer of the package, and the packages themselves are dealing with a very narrow subset of the platforms complexity: Python provides compilation logic, they don t create generic C libraries with stable ABI s for use by other programs, they don t have turing complete scripts for dealing with configuration file management and so forth. Anti virus updaters similarly narrow the problem they deal with, and add constraints on latency- updates of anti virus signatures are time sensitive when a new rapidly spreading threat is detected. A minor point, but it adds to the friction of considering a single packaging tool for all needs is the different use cases of low level package management tools like dpkg or rpm vs the use cases that e.g. pypi has. A primary use case for packages on pypi is for them to be used by people that are not machine administrators. They don t have root, and don t want it. Contrast that with dpkg or rpm where the primary use case (to date) is the installation of system wide libraries and tools. Things like man page installation don t make any sense for non-system-wide package systems, whereas they are a primary feature for e.g. dpkg. In short, the per-platform/language tools are (generally):
  1. Written in languages that are familiar to the consumers of the tools.
  2. Targeted at use on top of existing platforms, by non-privileged users, and where temporary breakage is fine.
  3. Intended to get the software packaged in them onto widely disparate operating systems.
  4. Very narrow they make huge assumptions about how things can fit together, which their specific language/toolchain permits, and don t generalise beyond that.
  5. Don t provide for security updates in any specific form: that is left up to folk that ship individual things within the manager.
operating system package managers:
  1. Are written in languages which are very easy to bootstrap onto an architecture, and to deploy onto bare metal (as part of installation).
  2. Designed for delivering system components, and to avoid be able to upgrade the toolchain itself safely.
  3. Originally built to install onto one operating system, ports to other operating systems are usually fragile and only adopted in niche.
  4. Are hugely broad they install data, scripts, binaries, and need to know about late binding, system caches etc for every binary and runtime format the operating system supports
  5. Make special provision to allow security updates to be installed in a low latency fashion, without requiring anything consuming the package that is updated to change [but usually force-uninstalling anything that is super-tightly coupled to a library version].
Anti virus package managers:
  1. Exist to update daemons that run with system wide escalated privileges, or even file system layer drivers.
  2. Update datasets in realtime.
  3. Without permitting updates that are produced by third parties.
Given that, lets look at the routes Matt suggested Decoupling applications from the core as a strategy makes an assumption that the core and applications are partitionable. If they are not, then applications and the core will share common elements that need to be updated together. Consider, for instance, a Python application. If you run with a system installed Python, and it is built without zlib for some reason, but the Python application requires zlib, you have a problem. A classic example of this problem is facing Ubuntu today, with all the system provided tools moving to Python 3, but vast swathes of Python applications still being unported to Python 3 at all. Currently, the Python packaging system virtualenv/buildout + distribute don t provide a way to install the Python runtime itself, but will happily install their own components for everything up the stack from the runtime. Ubuntu makes extensive use of Python for its own tools, so the system Python has a lot of packages installed which buildout etc cannot ignore this often leads to issues with e.g. buildout, when the bootstrap environment has (say) zope.interfaces, but its then not accessible from the built-out environment that disables the standard sys.path (to achieve more robust separation). If we want to pursue decoupling, whether we build a new package manager or use e.g. virtualenv (or gem or npm or ), we ll need to be aware of this issue and perhaps offer, for an extended time, a dedicated no-frills, no-distro-packages install, to avoid it, and to allow an extended supported period for application authors without committing to a massive, distro sponsored porting effort. While its tempting to say we should install pip/npm/lein/maven and other external package systems, this is actually risky: they often evolve sufficiently fast that Ubuntu will be delivering an old, incompatible version of the tool to users well before Ubuntu goes out of support, or even befor the next release of Ubuntu. Treating data as a service. All the cases I ve seen so far of applications grabbing datasets from the web have depended on web infrastructure for validating the dataset. E.g. SSL certificates, or SSL + content checksums. Basically, small self-rolled distribution systems. I m likely ignorant of details here, and I depend on you, dear reader, to edumacate me. There is potential value in having data repackaged, when our packaging system has behind-firewall support, and the adhoc system that (for instance) a virus scanner system has does not. In this case, I specifically mean the problem of updated a machine which has no internet access, not even via a proxy. The challenge I see it is again the cross platform issue: The vendor will be supporting Ubuntu + Debian + RHEL + Suse, and from their perspective its probably cheaper to roll their own solution than to directly support dpkg + rpm + whatever Apple offer + Windows the skills to roll an adhoc distribution tool are more common than the skills to integrate closely with dpkg or rpm What about creating a set of interfaces for talking to dpkg / rpm / the system packagers on Windows and Mac OSX ? Here I think there is some promise, but it needs as Matt said careful thought. PackageKit isn t sufficient, at least today. There are, I think, two specific cases to cater to:
  1. The anti-virus / fresh data set case.
  2. The egg/gem/npm/ specific case.
For the egg/gem/npm case, we would need to support a pretty large set of common functionality, on Windows/Mac OSX / *nux (because otherwise upstream won t adopt what we create: losing 90% of their users (windows) or 5% (mac) isn t going to be well accepted :) . We d need to support multiple installations (because of mutually incompatible dependencies between applications), and we d need to support multiple language bindings in some fashion some approachable fashion where the upstream will feel capable of fixing and tweaking what we offer. We re going to need to support offline updates, replication, local builds, local repositories, and various signing strategies to match the various tradeoffs made by the upstream tools. For the anti-virus / fresh data case, we d need to support a similar set of operating systems, though I strongly suspect that there would be more tolerance for limited support in that most things in that space either have very platform specific code, or they are just a large-scale form of the egg/gem/npm problem, which also wants easy updates. What next? We should validate this discussion with at least two or three upstreams. Find out whats missing I suspect a lot and whats wrong I hope not much :) . Then we ll be in a position to decide if there is a tractable, widespread solution *possible*. Separately, we should stop fighting with upstreams that have their own packaging systems. They are satisfying different use cases than our core distro packaging systems are designed to solve. We should stop mindlessly repackaging things from e.g. eggs to debs, unless we need that specific thing as part of the transitive runtime or buildtime dependencies for the distribution itself. In particular, if us folk that build system packaging tools adopt and use the upstream application packaging tools, we can learn in a deep way the (real) advantages they have, and become more able to reason about how to unify the various engineering efforts going into them and perhaps even eventually satisfy them using dpkg/rpm on our machines.

26 August 2012

Andrew Cater: Helios - Ken Starks - appeal for (time-critical) help

For anybody that doesn't know - Ken Starks is the man behind the Helios Project - recycling computers, putting Linux on them, donating them to youngsters and the needy in Austin Texas.

He has a cancer diagnosis but his disability pension is enough to defeat his state provided insurance. Now he himself needs the help of the community.

More details here: http://linuxlock.blogspot.co.uk/2012/08/something-ive-been-putting-off-all-day.html and his partner's post above.

and here: Thomas A. Knight, who is setting up donations.

http://thomasaknight.com/blog.php?id=71

UPDATE:

There is now also a donate button at the Blog of Helios (linuxlock.blogspot.com).

Enough has been raised so far to buy Ken an appropriate monitor - because of the effects of radiotherapy, he's been unable to tolerate using a monitor with backlighting.

One donor has also stepped in to buy a month's drug treatment.

The initial target -US $5000 - has been met but The cost of an operating theatre session is at least US $50,000. All donations continue to be gratefully received.

Should efforts for raising funds for Ken himself be unsuccessful, all surplus funds raised will be ploughed back into the Helios Project (now known as Reglue following a recent merger with another local computer charity).

The Helios Project has been associated with Software in the Public Interest [SPI - also the umbrella organisation supporting Debian] for some years.

UPDATE2 - From Thomas A. Knight's blog referenced above:

By Thomas A. Knight on Sun 19 Aug 2012 07:33:49 am $11,000 so far, and still going strong. The outpouring of support for this is amazing. My most humble thanks to all contributors.

Even though we are still far from our goal, this has been far more successful than I ever thought possible. Thank you.

UPDATE3 - From Ken Starks, Sunday 26 August 2012

The amount of money needed has been raised. Donations to Helios Project/Reglue are welcome, as ever - but Ken's immediate needs are satisfactorily met and he himself doesn't wish to profit further from the community's goodwill. As he says, he can't thank us enough
More news at http://linuxlock.blogspot.com is due on 27/08/2012

Gregor Herrmann: RC bugs 2012/34

good news: I'm seeing more & more people contributing to RC bugs in the BTS. here are my own contributions for the past week:

25 August 2012

John Goerzen: Voice Keying with bash, sox, and aplay

There are plenty of times where it is nice to have Linux transmit things out a radio. One obvious example is the digital communication modes, where software acts as a sort of modem. A prominent example of this in Debian is fldigi. Sometimes, it is nice to transmit voice instead of a digital signal. This is called voice keying. When operating a contest, for instance, a person might call CQ over and over, with just some brief gaps. Most people that interface a radio with a computer use a sound card interface of some sort. The more modern of these have a simple USB cable that connects to the computer and acts as a USB sound card. So, at a certain level, all that you have to do is play sound out a specific device. But it s not quite so easy, because there is one other wrinkle: you have to engage the radio s transmitter. This is obviously not something that is part of typical sound card APIs. There are all sorts of ways to do it, ranging from dedicated serial or parallel port circuits involving asserting voltage on certain pins, to voice-activated (VOX) circuits. I have used two of these interfaces: the basic Signalink USB and the more powerful RigExpert TI-5. The Signalink USB integrates a VOX circuit and provides cabling to engage the transmitter when VOX is tripped. The TI-5, on the other hand, emulates three USB serial ports, and if you raise RTS on one of them, it will keep the transmitter engaged as long as RTS is high. This is a more accurate and precise approach. VOX-based voice keying with the Signalink USB But let s first look at the Signalink USB case. The problem here is that its VOX circuit is really tuned for digital transmissions, which tend to be either really loud or completely silent. Human speech rises and falls in volume, and it tends to rapidly assert and drop PTT (Push-To-Talk, the name for the control that engages the radio s transmitter) when used with VOX. The solution I hit on was to add a constant, loud tone to the transmitted audio, but one which is outside the range of frequencies that the radio will transmit (which is usually no higher than 3kHz). This can be done using sox and aplay, the ALSA player. Here s my script to call cq with Signalink USB:
#!/bin/bash
# NOTE: use alsamixer and set playback gain to 99
set -e
playcmd ()  
        sox -V0 -m "$1" \
           "  sox -V0 -r 44100 $1 -t wav -c 1 -   synth sine 20000 gain -1" \
            -t wav -   \
           aplay -q  -D default:CARD=CODEC
 
DELAY=$ 1:-1.5 
echo -n "Started at: "
date
STARTTIME= date +%s 
while true; do
        printf "\r"
        echo -n $(( ( date +%s -$STARTTIME) / 60))
        printf "m/$ DELAY s: TRANSMIT"
        playcmd ~/audio/cq/cq.wav
        printf "\r"
        echo -n $(( ( date +%s -$STARTTIME) / 60))
        printf "m/$ DELAY s: off         "
        sleep $DELAY
done
Run this, and it will continuously play your message, with a 1.5s gap in between during which the transmitter is not keyed. The screen will look like this:
Started at: Fri Aug 24 21:17:47 CDT 2012
2m/1.5s: off
The 2m is how long it s been going this time, and the 1.5s shows the configured gap. The sox commands are really two nested ones. The -m causes sox to merge the .wav file in $1 with the 20kHz sine wave being generated, and the entire thing is piped to the ALSA player. Tweaks for RigExpert TI-5 This is actually a much simpler case. We just replace playcmd as follows:
playcmd ()  
        ~/bin/raiserts /dev/ttyUSB1 'aplay -q -D default:CARD=CODEC' < "$1"
 
Where raiserts is a program that simply keeps RTS asserted on the serial port while the given command executes. Here's its source, which I modified a bit from a program I found online:
/* modified from
 * https://www.linuxquestions.org/questions/programming-9/manually-controlling-rts-cts-326590/
 * */
#include <stdio.h>
#include <stdlib.h>
#include <termios.h>
#include <unistd.h>
#include <sys>ioctl.h>
#include <sys< sys="">types.h>
#include <sys>stat.h>
#include <fcntl.h>
static struct termios oldterminfo;
void closeserial(int fd)
 
    tcsetattr(fd, TCSANOW, &oldterminfo);
    if (close(fd) < 0)
        perror("closeserial()");
 
int openserial(char *devicename)
 
    int fd;
    struct termios attr;
    if ((fd = open(devicename, O_RDWR)) == -1)  
        perror("openserial(): open()");
        return 0;
     
    if (tcgetattr(fd, &oldterminfo) == -1)  
        perror("openserial(): tcgetattr()");
        return 0;
     
    attr = oldterminfo;
    attr.c_cflag  = CRTSCTS   CLOCAL;
    attr.c_oflag = 0;
    if (tcflush(fd, TCIOFLUSH) == -1)  
        perror("openserial(): tcflush()");
        return 0;
     
    if (tcsetattr(fd, TCSANOW, &attr) == -1)  
        perror("initserial(): tcsetattr()");
        return 0;
     
    return fd;
 
int setRTS(int fd, int level)
 
    int status;
    if (ioctl(fd, TIOCMGET, &status) == -1)  
        perror("setRTS(): TIOCMGET");
        return 0;
     
    status &= ~TIOCM_DTR;   </sys>* ALWAYS clear DTR */
    if (level)
        status  = TIOCM_RTS;
    else
        status &= ~TIOCM_RTS;
    if (ioctl(fd, TIOCMSET, &status) == -1)  
        perror("setRTS(): TIOCMSET");
        return 0;
     
    return 1;
 
int main(int argc, char *argv[])
 
    int fd, retval;
    char *serialdev;
    if (argc < 3)  
        printf("Syntax: raiserts /dev/ttyname 'command to run while RTS held'\n");
        return 5;
     
    serialdev = argv[1];
    fd = openserial(serialdev);
    if (!fd)  
        fprintf(stderr, "Error while initializing %s.\n", serialdev);
        return 1;
     
    setRTS(fd, 1);
    retval = system(argv[2]);
    setRTS(fd, 0);
    closeserial(fd);
    return retval;
 
This compiles to an executable less than 10K in size. I love it when that happens. So these examples support voice keying both with VOX circuits and with serial-controlled PTT. raiserts.c could be trivially modified to control other serial pins as well, should you have an interface which uses different ones.

24 August 2012

Olivier Berger: Generating RDF description of Debian package sources with ADMS.SW

Edit : I ve now managed to roll out my contribution which is now in production on packages.qa.debian.org. See a later post I ve made on the subject, and beware that the generated RDF has changed a bit also. ADMS.SW proposes specifications for description of software present in software catalogues. I ve tried and apply it to the contents of the Debian Package Tracking System (PTS), using transformation of the information known by the PTS to RDF+XML. The result is not yet in production, but here s an example of what can be done, using the Turtle syntax (more readable) :
<style type="text/css"> .T1 color:#000000; font-size:14pt; font-weight:bold; .T2 color:#000000; font-size:12pt; .T3 color:#000000; font-size:8.5pt; .T4 color:#0000ff; font-size:8.5pt; .T5 color:#a020f0; font-size:8.5pt; .T6 color:#228b22; font-size:8.5pt; .T7 color:#b22222; font-size:8.5pt; .T8 color:#008b8b; font-size:8.5pt; .T9 color:#8b2252; font-size:8.5pt; .dp1 .dp2 </style> @base <http://packages.qa.debian.org/> .
@prefix rdf: <http://www.w3.org/1999/02/22 rdf syntax ns#> .
@prefix admssw: <http://purl.org/adms/sw/> .
@prefix doap: <http://usefulinc.com/ns/doap#> .
@prefix dcterms: <http://purl.org/dc/terms/> .
@prefix rdfs: <http://www.w3.org/2000/01/rdf schema#> .
@prefix foaf: <http://xmlns.com/foaf/0.1/> .
@prefix schema: <http://schema.org/> .
@prefix spdx: <http://www.spdx.org/rdf/terms#> .
@prefix : <http://www.w3.org/1999/xhtml> .
@prefix str: <http://exslt.org/strings> . #
# First the packaging project for apache2 in Debian
#
# <http://packages.qa.debian.org/apache2> resource :
<apache2>
a admssw:SoftwareProject ;
doap:name "apache2" ;
doap:description "Debian apache2 source packaging" ;
doap:homepage "http://packages.debian.org/src:apache2" ;
schema:contributor [
a foaf:OnlineAccount ;
foaf:accountName "Debian Apache Maintainers" ;
foaf:accountServiceHomepage <http://qa.debian.org/developer.php?login=debian apache@lists.debian.org>
], [
a foaf:OnlineAccount ;
foaf:accountName "Stefan Fritsch" ;
foaf:accountServiceHomepage <http://qa.debian.org/developer.php?login=sf@debian.org>
], [
a foaf:OnlineAccount ;
foaf:accountName "Steinar H. Gunderson" ;
foaf:accountServiceHomepage <http://qa.debian.org/developer.php?login=sesse@debian.org>
], [
a foaf:OnlineAccount ;
foaf:accountName "Arno T ll" ;
foaf:accountServiceHomepage <http://qa.debian.org/developer.php?login=arno@debian.org>
] ;
# pointer to the release in the different suites :
doap:release <apache2_2.2.16 6+squeeze7>, <apache2_2.2.22 11>, <apache2_2.4.2 2>. #
# Now the different debian package source releases
#
# <http://packages.qa.debian.org/apache2_2.2.16 6+squeeze7> resource
<apache2_2.2.16 6+squeeze7>
a admssw:SoftwareRelease ;
rdfs:label "apache2 2.2.16 6+squeeze7" ;
admssw:project <apache2> ;
dcterms:description "Debian apache2 source package version 2.2.16 6+squeeze7" ;
doap:revision "2.2.16 6+squeeze7" . # This one is the reference version for the PTS as in unstable, so
# contains more details than the others
<apache2_2.2.22 11>
a admssw:SoftwareRelease ;
rdfs:label "apache2 2.2.22 11" ;
admssw:project <apache2> ;
dcterms:description "Debian apache2 source package version 2.2.22 11" ;
doap:revision "2.2.22 11" ;
# this release contains two components
admssw:includedAsset <apache2/apache2_2.2.22 11_debian>, <apache2/apache2_2.2.22_orig>
;
# this release can be downloaded as one package (with dget)
admssw:package <apache2/apache2_2.2.22 11.dsc> ;
# it also has a related release somewhere else
dcterms:relation <https://launchpad.net/ubuntu/+source/apache2/2.2.22 6ubuntu2> .
<apache2_2.4.2 2>
a admssw:SoftwareRelease ;
rdfs:label "apache2 2.4.2 2" ;
dcterms:description "Debian apache2 source package version 2.4.2 2" ; admssw:project <apache2> ;
doap:revision "2.4.2 2" . # Then the .dsc file for the current unstable version
<apache2/apache2_2.2.22 11.dsc>
a admssw:SoftwarePackage ;
dcterms:description "Debian source package descriptor file for apache2 version 2.2.22 11";
schema:downloadUrl "http://cdn.debian.net/debian/pool/main/a/apache2/apache2_2.2.22 11.dsc";
schema:fileSize "2885" ;
spdx:checksum [
a spdx:Checksum ;
spdx:algorithm <apache2#checksumAlgorithm_md5sum> ;
spdx:checksumValue "d7d03719b9f6432beeecd3aa04f7b22c"
] . #
# Then the upstream project
#
<apache2/apache2_orig>
a admssw:SoftwareProject ;
doap:description "The apache2 upstream project" ;
# either its name or homepage can be matched against other ADMS.SW
# or DOAP descriptors
doap:name "apache2" ;
doap:homepage "http://httpd.apache.org/" . # And a upstream release 2.2.22
<apache2/apache2_2.2.22_orig>
a admssw:SoftwareRelease ;
rdfs:label "Upstream apache2 release 2.2.22" ;
dcterms:description "Upstream source release for apache2 version 2.2.22" ;
doap:revision "2.2.22" ;
admssw:project <apache2/apache2_orig> ;
# and a link to the upstream source tarball s description
admssw:package <apache2/apache2_2.2.22.orig.tar.gz> . # now the (potentially re archived) upstream source archive for that release
<apache2/apache2_2.2.22.orig.tar.gz>
a admssw:SoftwarePackage ;
dcterms:description "Upstream source archive for apache2 version 2.2.22 11 (potentially re archived by Debian)";
schema:downloadUrl "http://cdn.debian.net/debian/pool/main/a/apache2/apache2_2.2.22.orig.tar.gz";
# Those 2 bits should help match packagings of the same tarball if needed
schema:fileSize "7200529" ;
spdx:checksum [
a spdx:Checksum ;
spdx:algorithm <apache2#checksumAlgorithm_md5sum> ;
spdx:checksumValue "d77fa5af23df96a8af68ea8114fa6ce1"
] . #
# Now, document specific details of the second component : Debian
# packaging files archive
#
<apache2/apache2_2.2.22 11_debian>
a admssw:SoftwareRelease ;
rdfs:label "Package sources apache2_2.2.22 11" ;
dcterms:description "Debian packaging sources for apache2 version 2.2.22 11" ;
doap:revision "2.2.22 11" ;
admssw:package <apache2/apache2_2.2.22 11.debian.tar.gz> . <apache2/apache2_2.2.22 11.debian.tar.gz>
a admssw:SoftwarePackage ;
dcterms:description "Debian source package files archive for apache2 version 2.2.22 11" ;
schema:downloadUrl "http://cdn.debian.net/debian/pool/main/a/apache2/apache2_2.2.22 11.debian.tar.gz";
schema:fileSize "195980" ;
spdx:checksum [
a spdx:Checksum ;
spdx:algorithm <apache2#checksumAlgorithm_md5sum> ;
spdx:checksumValue "d3d4146ccad51129636b7dbff284a110"
] . #
# Now, we also weave links with the Ubuntu counterparts
#
<https://launchpad.net/ubuntu/+source/apache2>
a admssw:SoftwareProject ;
doap:description "\"apache2\" source package in Ubuntu" ;
# this one promises some trolls and flames
admssw:forkOf <apache2> ;
doap:homepage "https://launchpad.net/ubuntu/+source/apache2" ;
doap:release <https://launchpad.net/ubuntu/+source/apache2/2.2.22 6ubuntu2> . # and its release known by the PTS
<https://launchpad.net/ubuntu/+source/apache2/2.2.22 6ubuntu2>
a admssw:SoftwareRelease ;
rdfs:label "apache2 2.2.22 6ubuntu2" ;
dcterms:description "\"apache2\" 2.2.22 6ubuntu2 source package in Ubuntu" ;
doap:revision "2.2.22 6ubuntu2" ;
admssw:project <https://launchpad.net/ubuntu/+source/apache2> .

Jonathan Carter: Wheezy Theme Updates


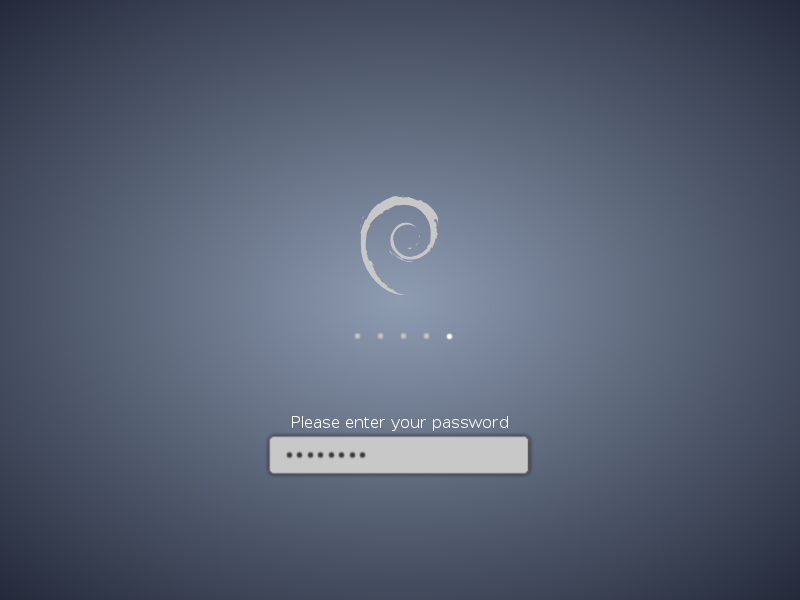
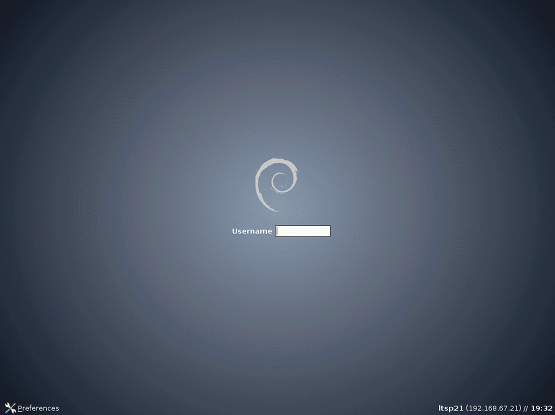
Joy Theme When the Joy theme was picked as the chosen theme for Debian 7.0 (Wheezy), I wanted to do what I could to get as much of it in the archive as possible before the freeze that occurred in June. I ve been working with Paul Tagliamonte and Vagrant Cascadian and I m glad that it resulted in some nice things! The Joy theme is modest and beautiful and I think Debian 7.0 is going to be one of the best looking Debian releases so far. Joy Plymouth Theme Plymouth is the part that provides the boot splash. It also takes care of a few other things, like showing prompts and progress indicators for filesystem checks, password prompts for encrypted devices and more so that the splash doesn t need to exit to show those. It s very scriptable, The installers for the Genesi Efika range of devices even use it for it s front-end. I needed to start with a Plymouth theme where I knew the prompts for all the things that happen during boot was at least more or less implemented, so I started off with one that I know works well, the Edubuntu one. So, fun fact: Debian 7.0 s Plymouth theme is actually based on the Edubuntu one. I had to play with the colours a bit to get it right, Edubuntu has a light background so I had to invert contrast for things like the input box, but I think it came out nicely. Splashy isn t in the archives anymore and it s not widely used anymore, so I cleaned it up from the desktop-base package so that there s less clutter shipped with it. Joy LTSP/LDM Theme This screenshot actually looks a bit uglier than it should because I took it on a VM that doesn t have 24bit colour, but we re looking into what we can do to make it look better on 16bit colour as well. During Debconf in Nigaragua, Vagrant and I worked on getting the LDM theme in shape. I have already done what I thought was most of the work by the time Debconf started, but it turns out there was a lot more to it to do it properly. We managed to get rid of the gtk2-engines-murrine dependency, which in itself is quite tiny, but it s a bit backwards in that it depends on the whole rest of the murrine-themes which brings in too much. We took the time to get the dependencies/recommends/etc right and to make it the default theme in Debian without messing it up for any Debian derivatives. It all came together and now when you install LTSP on Debian, you get the Joy theme by default! I m really glad about that because I didn t get the Spacefun LDM theme done in time for the Squeeze release. Enjoy!

23 August 2012

Neil McGovern: How not to be a jerk online chauvinism

Do you remember at school, when the teachers mentioned that something would be on your "permanent record"? The big secret is that there isn't one. Apologies to all teachers, but it's not likely this blog's demographic will reach your students. However, since the advent of the internet, a permanent record does exist. Everywhere from the Wayback Machine to Google's cache contains copies of all public activity you post online. At Collabora, we hire some of the best open source software engineers to work for our clients. It should be no surprise that a quick Ohloh and search for someone's name is a standard part of the hiring process. This normally comes up with all sorts of exciting things which people have done, both with software and further abroad. A tricky situation will occur if you have lost your temper online, as Patrick Ryan has done recently. He made a comment on #node.js on the Freenode network that:
[20.16.34] < TheEmpath> anyone else have a hot programmer girl in their office? o____O
This was quite rightly called out as being inappropriate for the channel, and quickly decided to have a large and abusive rant about this. This was then continued with him opening a number of bugs against the projects owned by the person who called him out, with titles such as "Hyperactive Leftist Power Trip not included" and "Not anti-Republican enough". This then gets worse. Once the log is posted (link above) there is yet more abuse and unfounded accusations by Mr Ryan in the comments. So, what happens when you search for his name? You get a log with someone being entirely inappropriate and then large rants. Not the best move for a software consultant.

Gunnar Wolf: Historic airplane found, cash spammed!

Sometimes, very rarely, I am happy that the spam filters in my personal mail server are so far from perfect. Many of us were amazed, some days ago, news broke that Amelia Earhart's plane was found in the Southwestern Pacific. The news is amazing and worthy in itself. But today, I got this mail, proof that Amelia lived through all those years: (all addresses obscured, of course)
Date: Wed, 22 Aug 2012 23:38:59 -0700
From: Amelia Earhart <some-mail@gmail.com>
To: undisclosed-recipients: ;
Subject: Hello
Reply-To: some-other-mail@live.com Hello friend, With due respect to humanity, i am compelled to write to you on a humanitarian ground, however, it has been my wish to execute in life. Please, I am contacting you based on my desire to create a charitable fund in your country with this sum of EURO 3.5 Million which I inherited from my late husband (Dr. Ahrens Earhart). It is my desire to see that this money is invested in any organization of your choice in your country and distributed each year among the charity organizations, the house mother of the child, mosques, churches, schools, support for disadvantaged older men and women or in whatever way you intend helping the less privileged. I took this decision because I was raised out of the house of mother and baby at the moment, i am admitted in a hospital in London were i am taking severe treatment to my cancer illness. Please answer as soon as possible to confirm your agreement with this proposal, so I ll give you all the necessary information that will enable you to have access to this funds my personal accountant will be aware of my arrangements with you. Thank you for your attention and I hope to hear from you soon. Please contact me through my this email- some-other-mail@live.com the nurse helping me will attend to you i have been restricted from touching the computer due to my illness i will direct you through her she is a nice person. Sincerely,
Ms. Amelia Earhart.

Paul Tagliamonte: dpu, debian.js and other random hax

In this choc-filled post, I ve got a few things I d love to share. debian.js First, a quick side-hack called debian.js. It s not entirely a serious project, but it s interesting. Here s some example code (and output from the terminal) Here s some of the client code (but slightly modified for clarity)
debian.on('bug', function(bug)  
    console.log(bug);
 );
which produces the following:
  sender: 'John Johansen <john.johansen@canonical.com>',
  package: 'vidalia',
  id: '<503577E5.2080502@canonical.com>',
  bugno: '682431',
  action: 'followup',
  class: 'bug',
  description: 'Bug#682431: [apparmor] Factorize Qt and GTK themes abstractions?'  
(and later, after I filed for unblock of desktop-base (more on that later))
  sender: 'Paul Tagliamonte <paultag@debian.org>',
  package: 'release.debian.org',
  id: '<20120823011639.GA8561@leliel.localdomain>',
  bugno: '685657',
  action: 'report',
  class: 'bug',
  description: 'Bug#685657: unblock: desktop-base/7.0.3'  
Legit. Anyway, hopefully more hax on this later. I d love to see Debian and Node.js get along better. dpu Nextly, I ve been working on something called dpu , with the (epic) Niels Thykier which will be a replacement for Lintian s test-runner. Progress is good, but not feature-complete yet. The end goal is to allow all projects which deal with the process of generating a debian package to start testing their code. If you have requirements, let me know! desktop-base I ve uploaded version 7.0.3, which features a switch to xz, and slight changes to existing theme elements. Mad props to Eshat Cakar for some slick KDE updates, and to Jo Carter for the Plymouth updates. Props!

22 August 2012

Gunnar Wolf: An industry commits suicide and blames us

[ once again, I am translating somebody else's material In this case, my good Costa Rican friend Carolina Flores. Please excuse my stylistic mistakes My English is far from native as you well know. But this material is worth sharing, and worth investing some tens of minutes doing a quick translation. If you can read Spanish, go read Caro's original entry ] Have you been to a music record store lately? I did so last Saturday, as a mere excercise. I was not planning on buying anything but I wanted to monitor things and confirm my suspicions. What was I suspicious of? First, that I would only find old records. And so it was: The only recent record I found was ...little broken hearts by Norah Jones. the second, that I would only find music for over 50 year old people. so it was: Were I there to look for a present for my father, I would have walked out with 10 good records. Third, that in the store nothing worth commenting would happen. About that last point, I should point out it was around 10 AM and the store had just opened its doors. Lets concede the benefit of doubt. I don't think many of you will remember, but in Barrio La California (where there is now a beauty parlour, almost in front of AM.PM) there was Auco Disco. In Auco Disco there was a guy specialized in rock (Mauricio Alice) and another one specialized in jazz (I don't remember his name). In that record you could always find rare records, but if they were not there, at least you were sure to find somebody to say: "No, we don't have that, but that's an excellent record, it's the best that [insert group here] have ever recorded because just afterwards they switched their guitar player, they had gone a bit south but with that record they are flying. But no, we don't have it; I can recommend you this record by [insert another group] because it has a guitar solo in track six that is amazing". It would happen more or less like that, which means, one would arrive to Auco Disco at 10 AM and leave around 5 PM with three new records, after having listened to a spectacular music selection. What happened to those stores? Were they killed by The Pirate Bay? That's the simplistic answer from the recording industry! The answer is that those stores never got anything from the industry but an invoice. The industry specially in prescindible markets such as ours was limited to hiring artists, taking care of them recording a sellable product, producing the object called record, and that's it. The more commercial radio stations were paid to program those songs as it cannot be casual that "Mosa, mosa" is the summer hit in all of Latin America, can it? but, record stores? Nothing. Lets carry on with that idea: Radio stations are paid to program said music. This idea should not lead us to believe that recording companies are to blame for bad taste. I won't reveal my sources, but I know the success of the "Locura autom tica" song by La Secta was a real example. Nobody paid for it. That song got to the number one because of its own merits(?) (you don't know the effort it took to find that thing, I cannot recommend it to you). Same thing happens with other stations that don't program reggaet n, that try to save the species, and where they play what we do like. But the thing is, everything we like is not available in any record store in this country. Then, even if we wanted to buy a record or give it as a gift to somebody, it is plain impossible. And don't tell me it's the same to present as a gift a link or a CD full of downloaded MP3 as it is to give a record with cover and booklet, wrapped in gift paper. I might be old-school, but the fetish object record still exists, not only because of its cover, but because of its sound. A 3MB MP3 is akin to drinking coffee dripping from a bag that has been used eight times with the same coffee beans. That format is the worst that has ever happened to music, and if we had any bit dignity we would never purchase digital files in Amazon or iTunes safe for MP3 with an acceptable compression level. That, if we could buy them, because not only that is allowed to us. As the musical industry has no interest in resolving ITS problem (that is not our problem, it is those companies') it has not even been resolved how to charge for a MP3 download that includes import fees (well, if downloading from here a MP3 from a USA-based file server can be considered importing goods into Costa Rica!!!) so we don't have to get dizzy entering into the nineties to Titi Online to discover there is nothing by Muse, Andrew Bird, The Killers, Death Cab for Cutie, Paramore, Bj rk... (believe me, I looked them all up, even Norah jones and La Secta. They also were not there). This all leads me to the question, which I present with all due respect (NOT): What the fuck do they expect us to do??? It is outrageous; above all because in the best case they will sell us a watery coffee download that won't allow us to get all the details a vinyl or less compression would give us. In the worst case, post-MP3 groups will end up recording music with no harmonics or hidden sounds, because, what for? Nobody will hear it. They even admit it: "Some musicians and audio engineers say the MP3 format is changing the way studios mix their recordings. They say the MP3 format "flattens" dynamics differences in tone and volume in a song. As a result, a great deal of new music sounds very much alike, and there is nothing as focusing to create a dynamic listening experience. Why working so hard in creating complex sound if nobody can detect it?" (Rolling Stone, The Death of High fidelity, December 26 2007, taken from here). That's why I am not surprised by Adri n's post regarding the sales of old records. The price has nothing to do with it. The causes are related to the fetish object record and what it means or does not mean for people that have never purchased one. Adri n also asks if somebody here keeps buying records. I answered that I would if the stores sold anything I like. I do it even after the nausea I feel while reading "This phonogram is an intellectual work protected in favor of its producer COPYING IT IN WHOLE OR PARTIALLY IS FORBIDDEN " (like that, uppercased, yelling to whoever is only guilty of having bought a record and defending the producer, not the artist). But I am sure that almost nobody buys records because doing so is no longer a gratifying experience; because if buying a record is clicking to wait 15 days for it to reach the mailbox, we prefer clicking on the download link. But there is another reason for people not to buy records anymore. In one of my talks regarding the dictatorship of the all rights reserved, I asked the 30 twenty-something-year-old students if any of them had ever bought a record. One answered he had, because he is an author and performer (cantautor in Spanish) and understands the effort that producing a record entails. The rest of them had never done so. Is it possible that said young people have never listened to real music? Is it possible that, were it not for concerts, what they consider music is a set of washed-out MP3 that are about to fill up 1TB of their computer? Does people no longer buy records because they cannot differentiate one sound from the other? It is not very clear for me where do I want to get to. The recording industry is despicable. An industry that instead of innovating sets its energy on suing adolescents for downloading songs, trying to pass laws restricting our freedoms in Internet, putting up DRMs making us hostages to our devices* and forcing us to listen just the aroma of music, deserves my whole contempt. If we add ot this that said industry won't allow us to legally download their breadcrumbs because it has not understood that Internet does not need a van crossing borders, besides my contempt they deserve my pity and my heartfelt condolence. But the condolence is also for music, real music, that which is not compressed under the shoe using a terrible format. It is also for independent musicians that have not realized that begging for a bit of space to that industry they just add to themselves the "despicable" tag, given they deserve the fruits of their work to enter their bank account. However, there are good things that have come out of this absurdity. Be it for those that have joined projects such as Aut mata (even if it is in MP3) and for dreams come true such as Musopen (that have achieved that the music that's in theory Public Domain becomes so in practice as well). Good for the Electronic Frontier Foundation and the list of lawyers willing to defend people accused of ilegally downloading music in the USA. Good for the Creative Commons licenses that allow free sharing. All those are growing solutions, although none of them allows me to buy the Panamanian Carlos M ndez's record. Thankfully, a friend of mine who knows I will never give a dime to Apple, bought the files for me in iTunes. I thank him deeply, although I would have prefered to go to Auco Disco and have Mauricio tell me that the 2007 EP I have from Carlos is better than the record he did on 2009. * My devices don't have DRM because I use free software. I also use the ogg file format. Image by verbeeldingskr8

Thomas Goirand: MiniUPnP now fully in Debian

IT S FINALLY IN! With this last upload of the MiniUPnP daemon 1.7-3, I ve reached a first milestone: all of the MiniUPnP libraries, daemons and clients are finally in Debian, in a shape which I am not ashamed anymore. What is UPnP for? Back in the days (around Linux 2.0.3x), the only way to share a single Internet connection was to run a Linux box as your gateway. These days are far gone, and nearly every home connection is done through a mini home router, which also often provides a small switch and a WiFi access point. Every computer on the LAN gets its connectivity through the router thanks to NAT, and to be more accurate, masquerading. That works very well for outbound connections (browse the web, send a mail, etc.), but it is then a lot harder that something connects to a server located in the LAN. If you run a permanent server with a fixed LAN IP address, that s fine, you just configure your router to do some port forwarding, so that any inbound connection will be forwarded to the computer of your choice in the LAN. But if one application needs to listen on the public IP address just for a while (for example, IRC using DCC connection), so that something can connect to it, it becomes a way more tricky. That s when UPnP comes into play. UPnP stands for Universal Plug and Play. It s a protocol so that any application on the LAN can open ports on the public IP address of the gateway. Note that an UPnP router is also often referenced as UPnP IGD (Internet Gateway Device). Why using MiniUPnP, don t we have already linux-igd? Before my packaging work, the only UPnP server that was available in Debian was linux-igd, which has a dependency on libupnpX. That library is quite big for what it does (about 500KiB, on top of which you have to install the 200KiB daemon itself), while MiniUPnP is designed to be lightweight (only 158K, with dependencies on iptables, iproute, uuid-runtime and libc6 only). That seems ridiculous, but when you have only 8MiB of flash in your old router, saving few hundreds KiB is really important, and here, we re saving more than 500 KiB, with a full implementation of the UPnP protocol, and the Microsoft NATPmP implemented as well (yes, Microsoft decided that one protocol wasn t enough, and that they should implement their own (sic!)). Who is using MiniUPNP? Probably, you already have the libminiupnpc installed in your SID/wheezy desktop, because the transmission bittorent client which is installed with Gnome by default, depends on it, and minissdpd might be in your desktop too, if you installed the Recommends: packages as well. Which is why these are scoring quite high already in popcon. Previously, transmission was embedding its own version of the MiniUPnP client library, so it s nice to have it as a standalone shared library now. Also, because of its very light weight, and the fact that UPnP is often needed for gaming (both XBOX 360 and PSP need, and can use, the MiniUPnP daemon that runs on your IGD), many ISP who ship a router to their customer, install MiniUPnP in it. For example, at least, the 2nd and 3rd largest Internet access provider in France (Free Telecom and SFR) are shipping MiniUPnPd in their box (one of them using OpenWRT on their router). So probably as well, you are also using MiniUPnP daemon without knowing it. But isn t UPnP unsafe? To this question, I d answer that connecting to Internet is unsafe. It isn t less safe than connecting to Internet on a WiFi hotspot for example. So adding UPnP support on your gateway doesn t make it less safe, especially since MiniUPnP has some features to help with security (like an ACL with IP and port lists, or a secure mode were the router will only open ports to the client requesting it). Also, we are running a distribution where dependencies are easy to check, so it s easy for you to check if a client uses UPnP or not, and decide to trust it (or not). I personally have no issue trusting transmission, x-chat or warzone2010 (more exactly: I don t trust that incoming connectivity will make it less safe for these applications, there are so many other things that could go wrong). MiniUPnP consists of what? MiniUPnP is a set of 4 source packages to handle all of your UPnP needs: - The client library, libminiupnpc (and the corresponding -dev package), with its sidekick miniupnpc client program (you can use it to check the public IP of your gateway, or manually open ports). - The UPnP IGD daemon, miniupnpd, which just reached Debian Experimental. The latest version, 1.7-3, also includes debconf configuration so that you can choose the NIC and IP address to bind on. If you installed previous version, I strongly recommend upgrading to fix previous problems. - The libnatpmp client library (and the -dev package) for implementing the Microsoft protocol as a client (it also has a client package binary for your tests). - The minissdpd daemon to keep memory of all UPnP devices that announced themselves, and speed-up using the UPnP protocol (used by the MiniUPnP client library). A long process to have MiniUPnP in Debian All these 4 pieces of the puzzle were not as easy as it seems to be packaged in Debian. Especially, the IGD daemon, MiniUPnPd, used to depend on some header files that were not packaged in Debian. This was a decision of the iptables maintainers, which even after a long discussion, refused to add the necessary headers because it wasn t supposed to be a kernel API. While this might really be truth, the issue was that there was no public API available in the Linux kernel at all, and other distributions (Fedora, Gentoo, etc.) really did supply these needed files. As a consequence, during a very long time (years literally), shamefully, it was impossible to build the MiniUPnP daemon in Debian, while it was no problem on other distributions. Note that I do not want to start a troll discussion here, I m just stating facts, both parties have very strong and respectable arguments. Anyway, this needed API was finally embedded in MiniUPnPd itself thanks to a contributor to the project, and now it builds on both the Squeeze and the Wheezy (that is Linux 3.2) kernel without any issue. Call for testing Unfortunately, I don t have a Linux box as my Internet gateway. So I did the tests that I could: I installed MiniUPnPd on one computer on my LAN, and checked that I could open ports from another computer. So it seems to work, but I had no way to really test it live , with some real clients. So if you have an Debian SID box as your Internet gateway, feedback would be highly appreciated. What is remaining to do? A transition from libminiupnpc5 to libminiupnpc8 has to happen. Of course, this is too late for Wheezy, so this will happen right after the release. There s not so many reverse dependencies, so it should be ok, but I (yet) have zero experience with transitions. BTW, I had hard time to find out what this transition process was, and maybe some more effort for documenting it would help others (I m thinking about adding some text in the Debian wiki for that). Also, I have called for help on debian-devel, because I m currently the only one maintaining all these 4 source packages, and I m trying to have all my packages checked by others, and team maintained. So if you want to give a hand, or just declare yourself as a backup if I m busy, please raise your hand! Upstream is a friend of mine, and is very reactive to any requests (it very rarely took more than 48 hours to get a reply). Enjoy MiniUPnP and report bugs! Again, feedback would be appreciated. :)

21 August 2012

Gunnar Wolf: Impromptu session on information freedom, network neutrality, etc. COSIT 2011, Mexico

TitleImpromptu session on information freedom, network neutrality, etc. COSIT 2011, Mexico
Publication TypeFilm
Year Released2011
AuthorsWolf G, Romo F, Miranda A, M ndez O, Hern ndez C, Araico S
Refereed DesignationNon-Refereed
Running Time0:56:00
Date Released2011-03-30
PublisherCongreso Mexicano de la Sociedad de la Informaci n y Conocimiento Libre (COSIT)
CountryMexico
Full TextDuring the COSIT 2011 conference, we held a very celebrated and fun impromptu talk. This was a very interesting session where many of the long-time Free Software activists in Mexico took the stage (we were waiting for a speaker who was late, so the audience was bored and waiting) and started talking in a completely irreverent, disorganized way about the status of network neutrality, ACTA, Free Software, Free Culture, legal issues regarding copyright and many other similar points.
At some point or another, we had on stage: Fernando Romo "el Pop", Alejandro Miranda "Pooka", Sandino Araico, Claudia Hern ndez, Octavio M ndez... Anybody else?
Regarding the quality of the recording: Regina just found this file in her cheap, aging hand-held, photo camera. Again, this was not a planned session, so don't expect a high quality recording. It is hard to follow the audio at points, and the video is not steady. Anyway, it's worth following!
Great thanks to Regina, and to her quick sense of opportunity, for reaching for her camera and filming this, as it would otherwise just get lost and stay only in our memory!
AttachmentSize
Full video (Ogg Vorbis+Theora encoded)81.19 MB

Next.

Previous.