Search Results: "will"

11 November 2012

Nathan Handler: Debian Developer

Today, I officially got approved by the Debian Account Managers as a Debian Developer (still waiting on keyring-maint and DSA). Over the years, I have seen many people complain about the New Member Process. The most common complaint was with regards to the (usually) long amount of time the process can take to complete. I am writing this blog post to provide one more perspective on this process. Hopefully, it will prove useful to people considering starting the New Member Process. The most difficult part about the New Member Process for me had to do with getting my GPG key signed by Debian Developers. I have not been able to attend any large conferences, which are great places to get your key signed. I also have not been able to meet up with the few Debian Developers living in/around Chicago. As a result, I was forced to patiently wait to start the NM process. This waiting period lasted a couple of years. It wasn't until this October, at the [Association for Computing Machinery at Urbana-Champaign's Reflections Projections Conference], that this changed. Stefano Zacchiroli was present to give a talk about Debian. Asheesh Laroia was also present to lead an OpenHatch Workshop about contributing to open source projects. Both of these Developers were more than willing to sign my key when I asked. If you look at my key, you will see that these signatures were made on October 7 and October 9, 2012. With the signatures out of the way, the next step in the process was to actually apply. Since I did not already have an account in the system, I had to send an email to the Front Desk and have them enter my information into the system. Details on this step, along with a sample email are available here. Once I was in the system, the next step was to get some Debian Developers to serve as my advocates. Advocates should be Debian Developers you have worked closely with, and usually include your sponsor(s). If these people believe you are ready to become a Debian Developer, they write a message describing the work you have been doing with them and why they feel you are ready. Paul Tagliamonte had helped review and sponsor a number of my uploads. I had been working with him for a number of years, and he really helped encourage and help me to reach this milestone. He served as my first advocate. Gregor Herrmann is responsible for getting me started in contributing to Debian. When I first tried to get involved, I had a hard time finding sponsors for my uploads and bugs to work on. Eventually, I discovered the Debian Perl Group. This team collectively maintains most of the Perl modules that are included in the Debian repositories. Gregor and the other Debian Developers on the team were really good about reviewing and sponsoring uploads in a very timely manner. This allowed me to learn quickly and make a number of contributions to Debian. He served as my second advocate. With my advocations taken care of, the next step in the process was for the Front Desk to assign me an Application Manager and for the Application Manager to accept the appointment. Thijs Kinkhorst was appointed as my Application Manager. He also agreed to take on this task. For those of you who might not know, the Application Manager is in charge of asking the applicant questions, collecting information, and ultimately making a recommendation to the Debian Account Managers about whether or not they should accept the applicant as a Developer. They can go about this in a variety of ways, but most choose to utilize a set of template questions that are adjusted slightly on a per-applicant basis. Remember that period of waiting to get my GPG key signed? I had used that time to go through and prepare answers to most of the template questions. This served two purposes. First, it allowed me to prove to myself that I had the knowledge to become a Debian Developer. Second, it helped to greatly speed up the New Member process once I actually applied. There were some questions that were added/removed/modified, but by answering the template questions befrehoand, I had become quite familiar with documents such as the Debian Policy and the Debian Developer's Rerference. These documents are the basis for almost all questions that are asked. After several rounds of questions, testing my knowledge of Debian's philosophy and procedures as well as my technical knowledge and skills, some of my uploads were reviewed. This is a pretty standard step. Be prepared to explain any changes you made (or chose not to make) in your uploads. If you have any outstanding bugs or issues with your packages, you might also be asked to resolve them. Eventually, once your Application Manager has collected enough information to ensure you are capable of becoming a Debian Developer, they will send their recommendation and a brief biography about you to the debian-newmaint mailing list and forward all information and emails from you to the Debian Account Managers (after the Front Desk checks and confirms that all of the important information is present). The Debian Account Managers have the actual authority to approve new Debian Developers. They will review all information sent to them and reach their own decision. If they approve your application, they will submit requests for your GPG key to be added to the Debian Keyring and for an account to be created for you in the Debian systems. At this point, the New Member process is complete. For me, it took exactly 1 month from the time I officially applied to become a Debian Developer until the time of my application being approved by the Debian Account Managers. Hopefully, it will not be long until my GPG key is added to the keyring and my account is created. I feel the entire process went by very quickly and was pain-free. Hopefully, this blog post will help to encourage more people to apply to become Debian Developers.

Vasudev Kamath: Weekly Log - 27/3 - 112012

OK I became again lazy to log my works and combined 2 weeks again :-). Most of my work is for Debian for this 2 weeks. This week was bit hectic I couldn't dedicate much time for any programming. This week I'm on vacation and will get more time to work on FLOSS and other coding stuffs. Only that I'm on slow network connection :-). Ok cya next week (hopefully) PS: My last weekly log never showed up in planet.d.o not sure what happened may be because I played with feed generating jekyll scripts. Hope this will show up in planet.d.o [1] http://code.metager.de/source/xref/linux/utils/util-linux/sys-utils/setsid.c
[2] http://vasudev.homelinux.net/display/copyninja/34241
[3] https://kakste.com/display/beardyunixer/974150
[4] anonscm.debian.org/gitweb/?p=collab-maint/friendica.git;a=summary

9 November 2012

Gunnar Wolf: Road trip to ECSL 2012 in Guatemala

Encuentro Centroamericano de Software Libre! Guatemala! During a national (for us) holiday, so it's easy to go without missing too much work time! How would I miss the opportunity? Several years ago, I started playing with the idea of having a road trip Probably this was first prompted with the UK crew and the Three Intrepid Motorcycle Riders arriving by land to DebConf 9 I don't know. Fact is, I wanted to go to DebConf10 in New York by land, as well as to DebConf12 in Nicaragua. Mostly due to a lack of time, I didn't Although we did start making some longish trips. Of course, my desire to show Regina what Mexico is like also helped! So, up until a week ago, our (according to my standards) long distance driving experience included:
  • M xico Guanajuato Puerto Vallarta Guanajuato M xico, in early November 2011, for Festival de Software Libre and with Regina and our Blender friends Octavio and Claudia. Totalling almost 1900Km, mostly consisting of wide, toll highway.
  • M xico Xilitla San Luis Potos M xico, in April 2012, just for fun and for a nice short vacation, alone with Regina. Totalling almost 1200Km, but through Sierra Gorda de Quer taro, a very tough stretch of about 250Km which we did at about 50Km/h on average. Beautiful route for sure! We didn't originally intend to go through San Luis Potos , and it does not appear to make much sense, as it adds ~350Km to the total, but it was even quicker than going back by the same route and according to those who now, even faster than our planned route, via Tamazunchale and Ixmiquilpan!
  • M xico San Luis Potos Zacatecas Aguascalientes Guanajuato M xico, in May 2012, for Congreso Internacional de Software Libre, again with Octavio and Claudia. Totalling 1250Km, and following very good roads, although most of them were toll-free.
But there is always a certain halo over crossing a border, maybe more so in countries as large as Mexico. We convinced Pooka and Moni, and granted, with some aprehension, as we knew of some important security risks in the more rural areas we wanted to go through we decided to go to Guatemala. And, although we wanted to go with a bit more time, Real Life took its toll: We could not take more time than the intersection of what our respective jobs offered. So, here goes a short(?) recap of our six day long, 3200Km trip. Of course, we have a map detailing this. Mexico Veracruz I came to my office early on Wednesday (31-oct), and left with Regina around 10AM towards Veracruz. We agreed to meet there with Moni and Pooka, who would take the night bus, and continue together. Crossing Mexico City proved to be the longest obstacle We arrived to Veracruz already past 3PM, and spent a nice evening walking down the center and port of the city. Veracruz port can still be seen as part of central Mexico; I knew the road quite well. Veracruz San Andr s Tuxtla Catemaco San Cristobal de las Casas We met with our friends at the iconic Gran Caf de la Parroquia at 6:30AM. Had a nice breakfast with coffee, and by 7:30 we were heading south-west. The reason to have a road trip was to get to know the route, to enjoy the countryside So, given we "only" had to make 650Km this day, we took the non-toll road A narrow path stretching along the coastal plains of Veracruz, until Acayucan. Doing so, we also saved some money, as the equivalent toll road is around MX$300 (~US$25)! Veracruz is a hot state. We ended up all sweaty and tired by 19:00, when we reached San Cristobal. We had agreed not to drive at night, due to security issues, but fortunately there was quite a bit of traffic both ways between Tuxtla Guti rrez (Chiapas State capital, around 1hr from San Cristobal, where darkness got us) and our destination, so we carried on. Now, San Cristobal is a high city, almost as high as Mexico City (2100m), and being more humid, it was quite chilly. We went for a walk, and were convinced that at a later time, we had to stay for several days there. The city is beautiful, the region is breath-taking, there is a lot of great handicrafts as well, and it's overall very cheap. Really lovely place. San Cristobal de las Casas Cd. Cuauht moc La Mesilla Guatemala Once again, this day started early. We woke up ready to leave at 7AM, and not earlier because the hotel's parking didn't open earlier. After a very quick visit to San Cristobal downtown, to take some photos that were not right the night before, we took the road to Comit n, stopping just for some tamales de bola y chipil n for breakfast. Central Chiapas is almost continuously populated, differing from most of my experience in Mexico. It is all humid, and has some very beautiful landscapes. We passed Comit n, which is a much larger city than what we expected, went downhill after La Trinitaria, crossed a plain, and continued until hills started taking over again. We stopped in a very chaotic, dirty place: Just accross the border, where Ciudad Cuauht moc becomes La Mesilla. This border was basically what we expected: There is no half-official place to exchange money, so we had to buy quetzales from somebody who offered them on the street, at MX$2 per Q1 (where the real exchange should be around 1.50 to 1). While on the road, I was half-looking for exchange posts in Comit n and onwards, and found none (and being a festive day, they would probably be closed anyway). But we were expecting this, after all, and exchanged just the basic minimum: MX$600 (US$50, which by magic became Q300, US$40). The tramit consists of:
  • Spraying the car against diseases (which has a cost of Q18)
  • Each of us has to go through migration. Note, in case you cross this border: We didn't expressly cross Mexican migration, so officially there was no record of us going out. Be sure to go through migration to avoid problems at re-entry!
    Migration has no cost.
  • Customs. As we were entering by car, I had to purchase a permit for circulation. I don't remember the exact quote, but it was around Q150, and the permit is valid for 90 days.
  • That's it! Welcome to Guatemala!
La Mesilla is in Guatemala's Huehuetenango Department, and from all of the Departments we crossed until Guatemala city (Huehuetenango, Quetzaltenango, Totonicap n, Solol , Chimaltenango, Sacatep quez and Guatemala), this is the largest one. Huehuetenango is home to the Cuchumatanes mountain ridge. We found beautiful, really steep, really fertile mountains. It is plainly amazing: Mountains over 60 , and quite often full with agricultural use Even at their steepest points! The CA-1 highway is, in general, in very good shape. There are however many (many, many) speed bumps (or topes, in Mexican terminology. Or t mulos in Guatemalan), at least a couple at every village we crossed, not always painted. The road is narrow and quite winding; it follows river streams for most of the way. We feared it would be in much worse shape, from what we have heard, but during the whole way we found only three points where the road was unusable due to landslides and an alternative road was always in place when we needed it. After Totonicap n, the narrow road becomes a wide (four lane) highway. Don't let that fool you! It still goes through the center of every village along the road, so it's really not meant for speeding. Also, even though the pavement is in very good condition, it is really steep quite often. It is not the easiest road to drive, but it's (again) by far not as bad as we expected. We arrived to Guatemala City as dawn was falling, and got promptly lost. Guatemala has a very strange organization scheme: The city is divided in several zones, laid out in a swirl-like fashion. East-west roads are called Calle and North-south roads are called Avenida (except for zona 4, I think, where they are diagonal, and some are Rutas while the others are V as). I won't go into too much detail). Thing is, many people told us it's a foolproof design, and people from different countries understand the system perfectly. We didn't... At least not when we arrived. We got quite lost, and it took us around one hour to arrive to our hotel, at almost 19:00 Almost 12 hours since we left San Cristobal. Went for a quick dinner, and then waited for our friends to arrive after the first day of work of ECSL, which we missed completely. And, of course, we were quite tired, so we didn't stay up much longer. Antigua Guatemala On Saturday, ECSL's activities started after 14:00 so we almost-kidnapped Wences, the local organization lead, and took him to show us around Antigua Guatemala. Antigua was the capital of Guatemala until an earthquake destroyed it in the 1770s; the capital was moved to present-day Guatemala city, but Antigua was never completely abandoned. Today, it is a world heritage site, a beautiful city, where we could/should have stayed for several days. But we were there for the conference, so we were in Antigua just a couple of hours, and headed back to Guatemala. Word of caution: Going from Guatemala to Antigua, we went down via the steepest road I have ever driven. Again, a real four-lane highway... but quite scary! The main focus for this post is to give some roadtrip advice to potential readers... So, this time around, I won't give much detail regarding ECSL. It was quite interesting, we had some very good discussions... but it would take me too much space to talk about it! The road back: Guatemala Tec n Um n; Cd. Hidalgo Arriaga So, about the road back: Yes, we just spent three days getting to Guatemala City. We were there only for ~36 hours. And... We needed to be here by Tuesday morning no matter what. So, Sunday at noon we said goodbye to our good friends in ECSL and started the long way back. To get to know more of Guatemala, we went back by the CA-2 highway, which goes via the coastal plains Not close to the Pacific ocean, which we didn't get to see at all, but not through the mountains. To get to CA-2, we took CA-9 from Guatemala. If I am not mistaken, this is the only toll road in Guatemala (at least, the only we used, and we used some pretty good highways!) It is not expensive; I don't remember right now, but must have been around Q20 (US$3). Went South past Palin and until CA-2, just outside Escuintla city, and headed West. All of Escuintla and Suchitep quez it is again a four lane highway; somewhere in Retalhueu it becomes a two lane highway. We were strongly advised not to take this road at night because, as the population density is significantly lower than in CA-1, it can get lonely at times And there are several reports of robberies. We did feel the place much less populated, but saw nothing suspicious in any way. Something important: There are almost no speedbumps in CA-2! The terrain stayed quite flat and easy as we crossed Quetzaltenango, and only in San Marcos we found some interesting hills and a very strong rain that would intermitetntly accompany us for the rest of the ride. So, we finally arrived to the border city of Tec n Um n at around 16:30 Approximately four hours after leaving the capital. The Tec n Um n Cd. Hidalgo cities and border pass are completely different from the disorderly and dirty Cd. Cuauht moc La Mesilla ones. The city of Tec n Um n could be just a nice town anywhere in the country, it does not feel aggressive as most border cities I have seen in our continent. We stopped to eat at El pollo campero and headed to the border. In the Mexican side, we also saw a very well consolidated, big and ordered migration area. Migration officers were very kind and helpful As we left Cd. Cuauht moc, Regina didn't get a stamp of leaving Mexico, so technically she was ilegally out of the country (as she is not a national... They didn't care about the rest of us). The tramit to fix this was easy, simple, straightforward. We only paid for the fumigation again (MX$60, US$5), and were allowed to leave. Anyway, we crossed the border. There is a ~30Km narrow road between Cd. Hidalgo and Tapachula, but starting in Tapachula we went on Northwards via a very good, four lane and very straight highway. Even though we had agreed not to drive at night... Well, we were quite hurried and still too far from Mexico City, so we decided to push it for three more hours, following the coastline until the city of Arriaga, almost at the border between Chiapas and Oaxaca. Found a little hotel to sleep some hours and collapsed. Word of warning: This road (from Tapachula to Arriaga) is also known for its robberies. We saw only one suspicious thing: Two guys were pushing up their motorcycle, from which they had apparently fallen. We didn't stop, as they looked healthy and not much in need of help, but later on talked about this Even though this was at night, they were not moving as if they had just crashed; nothing was scratched, not the motorcycle and not their clothes. That might have been an attempt to mug us (or whoever stopped by). This highway is very lonely, and the two directions are separated by a wall of vegetation, so nobody would have probably seen us were we to stop for some minutes. Be aware if you use this road! The trip comes to an end: Arriaga Niltepec Istmo C rdoba M xico The next (last, finally!) day, we left at 6:30AM. After driving somewhat over one hour, we arrived to Niltepec, where a group of taxi drivers had the highway closed as a protest against their local government's tolerance of mototaxis. We evaluated going back to Arriaga and continue via the Tuxtla Guti rrez highway, but that would have been too long. We had a nice breakfast of tlayudas (which resulted in Pooka getting an alergic reaction shortly afterwards) and, talking with people here and there, were told about an alternative route by an agricultural road that surrounds the blockade. So, we took this road the best way we could, and after probably 1hr of driving at 20Km/h, finally came back to the main road. We planned on crossing the isthmus using the Acayucan-Juchit n road We were amazed at the La Ventosa ("the windy") area, where we crossed a huge eolic plant for electricity generation, so of course we got our good share of photos. From then onwards, not much more worth mention. Crossed the isthmus via a quite secondary road in not too good shape (although there is a lot of machinery, and the road will much likely improve in the next few months/years), then took the toll freeway along Veracruz until C rdoba. We stopped for a (delilcious and revigorizing!) cup of coffee in Hotel Zeballos, where Agust n de Iturbide signed with Viceroy Juan O'Donoj the treaties that granted Mexico the independence. Traveller, beware: When crossing between Puebla and Veracruz, there is a steep slope of almost 1000m where , you will almost always (except if it's close to noon) find very thick fog; taking the highway from C rdoba, this is in the region known as Cumbres de Maltrata. We had the usual fog, and just as we left it, a thin but constant rain that went on with us up until we got home. Crossed Puebla state with no further eventualities, and arrived to Pooka and Moni's house by 22:00. Less than one hour later, Regina and me arrived home as well. This was four days ago... and I have finally finished writing it all down ;-) Hope you find this useful, or if not, at least entertaining! If you read this post in my blog, you will find many pictures taken along the trip below (Well, if you are reading the right page, not in the general blog index...). If you are reading from a planet or other syndication service... Well, come to the blog! Dreamhost woes Oh, and... Yes, it sometimes happens: My blog is hosted at Dreamhost. This means that usually it works correctly... But sometimes, specially when many people request many nontrivial pages, it just gives an error. If you get an error, reload once or twice... Or until your patience manages ;-)

Richard Hartmann: Release Critical Bug report for Week 45

Erratum Last week's posting had the wrong week. Turns out the script always outputs week 42. As the weeks were so close to each other, I didn't realize this at first. I fixed this by hand for this posting and will have it fixed upstream by next week. Timing I have put a lot of thought into when to publish this. Friday so it's before the weekend? Sat/Sun so it's during the weekend? Monday so it's at the actual start of the week (sorry, people from the U.S.)? Feedback welcome, assuming anyone cares. The actual gist The UDD bugs interface currently knows about the following release critical bugs: How do we compare to the squeeze cycle ?
Week Squeeze Wheezy Diff
43 284 (213+71) 468 (332+136) +184 (+119 ; +65)
44 261 (201+60)
45 261 (205+56)
46 271 (200+71)
47 283 (209+74)
48 256 (177+79)
49 256 (180+76)
50 204 (148+56)
51 124 (124+54)
52 115 (78+37)
1 93 (60+33)
2 82 (46+36)
3 25 (15+10)
4 14 (8+6)
5 2 (0+2)
6 release!

Olivier Berger: Using a DreamPlug with Debian as an IPv4/IPv6 router for a home LAN behind a FreeBox

The goal of this article is to describe the setup I've made for my home LAN behind a FreeBox (French ISP Free.fr).

1 Principles
The FreeBox is configured :
  • in router mode (with a local IPv4 network on 192.168.0.x/24)
  • with IPv6 support activated (by convention, we'll use the 2a01:e35:1234:5678::/64 prefix below, to represent the IPv6 prefix provided by the FreeBox)
Behind the FreeBox, I have connected a DreamPlug computer (running Debian wheezy with a dual-boot setup as sold by NewIT) on its eth0 etherlink port. Behind the DreamPlug, I have connected a switch (to its eth1 ethernet port), on which the LAN's machines will be connected, on a dual IPv4/IPv6 network. The IPv4 will be on 192.168.4.0/24 (addresses for machines connected to the switch will be static) while the IPv6 will use the addresses auto-generated on the FreeBox's prefix. The DreamPlug will also provide a wifi network (in master mode, through its uap0 interface), only IPv4 on 192.168.3.0/24. On the DreamPlug, the outgoing IPv4 traffic will be masqueraded, while the IPv6 traffic will be bridged so that machines on the LAN can be reached from the Internet directly, passing through the eth0 eth1 bridge. The DreamPlug will also act as a filter/firewall to only allow selected traffic to reach the LAN machines (in particular for the IPv6, since the machines may be reached directly from the Internet otherwise).

1.1 Alternatives
There are a lot of howtos describing the setup of FreeBox + IPv6, but I couldn't find one that was exactly reflecting the kind of setup I have. Some dealt with a FreeBox setup in bridge mode (i.e. not the router mode), but in case the DreamPlug isn't so much reliable, or I've messed with the config, I'm tempted to keep the possibility to connect directly to the FreeBox. Others didn't use the same setup with a router distributing both wired and wifi networks. And note described exactly the setup for a DreamPlug running Debian wheezy and using ferm as a firewall. No, there's no NIH syndrom here ;)

2 DreamPlug router configuration

2.1 Interfaces configuration
The /etc/network/interfaces on the DreamPlug looks like the following (kudos to Dag Bertelsen's Setting up Dreamplug as a router with Shorewall firewall for the wifi configuration bits):
# Note: Order of the interfaces declarations matters

auto lo
iface lo inet loopback

auto uap0
iface uap0 inet static
post-up /usr/bin/uaputl sys_cfg_ssid dream-uAP-XXXX
# Modus WPA2
post-up /usr/bin/uaputl sys_cfg_protocol 32
# WLAN password
post-up /usr/bin/uaputl sys_cfg_wpa_passphrase "WHATEVER PASSWORD"
# Set the Cipher
post-up /usr/bin/uaputl sys_cfg_cipher 8 8
# automatic channel
post-up /usr/bin/uaputl sys_cfg_channel 0 1
post-up /usr/bin/uaputl bss_start
# we deliver addresses for the Wifi with DHCP
post-up /usr/sbin/service udhcpd start
address 192.168.3.1
netmask 255.255.255.0

# Only IP6 traffic passes through the router between the Freebox on eth0 and the LAN on eth1
auto br0
iface br0 inet manual
bridge_ports eth0 eth1
bridge_maxwait 0
pre-up ebtables -t broute -A BROUTING -p ! ipv6 -j DROP
down ebtables -t broute -F

# Connected to the FreeBox, with DHCP in IPv4, masquerading outgoing IPv4 traffic
auto eth0
iface eth0 inet dhcp
up iptables -t nat -A POSTROUTING -o eth0 -j MASQUERADE
down iptables -t nat -F
post-up sysctl -q -w net.ipv4.ip_forward=1
iface eth0 inet6 auto

# Connected to the LAN with a static IPv4 address
auto eth1
iface eth1 inet static
address 192.168.4.1
netmask 255.255.255.0

2.2 DHCP server configuration
The DHCP config for udhcpd is as such (in /etc/udhcpd.conf):
start 192.168.3.100
end 192.168.3.200
interface uap0
opt lease 86400
opt router 192.168.3.1
opt subnet 255.255.255.0
opt dns 192.168.3.1
opt domain localdomain
max_leases 101
lease_file /var/lib/udhcpd.leases
auto_time 5

2.3 Firewall configuration
The firewall I use is ferm. Here's the /etc/ferm/ferm.conf configuration (YMMV). Thanks to Ren Garcia's R gles de firewall pour un pont IPv6 for inspiration :
## Interfaces of the router

# Our LAN on a switch
@def $DEV_PRIVATE = eth1;

# The ISP router
@def $DEV_WORLD = eth0;

# Our Wifi LAN
@def $DEV_WIFI = uap0;


## IP networks of our LAN

# IPv4 (includes ethernet switch and wifi)
@def $NET_PRIVATE = 192.168.0.0/16;

# IPv6 (the prefix granted by the ISP)
@def $NET6_PRIVATE = 2a01:e35:1234:5678::/64;

# IPv6 Local link
@def $LINK6 = fe80::/10;

# Specific machines on the LAN
@def $MACHINE_MYDESKTOP = 2a01:0e35:1234:5678:1234:5678:9abc:def0;

# Special function to log dropped packets
@def &DROP() =
mod limit limit 1/second limit-burst 10 LOG log-prefix "$DOMAIN-$CHAIN: ";
DROP;


# IPv4 iptables rules
table filter
chain INPUT
policy DROP;

# connection tracking
mod state state INVALID DROP;
mod state state (ESTABLISHED RELATED) ACCEPT;

# allow local packet
interface lo ACCEPT;

# respond to ping
#proto icmp ACCEPT;
proto icmp icmp-type echo-request ACCEPT;

# allow IPsec
proto udp dport 500 ACCEPT;
proto (esp ah) ACCEPT;

# allow SSH connections from the private network and from some
# well-known internet hosts
#saddr ($NET_PRIVATE 123.45.67.89) proto tcp dport ssh ACCEPT;
saddr $NET_PRIVATE proto tcp dport ssh ACCEPT;

# we provide DNS and SMTP services for the internal net
interface $DEV_PRIVATE saddr $NET_PRIVATE
proto (udp tcp) dport domain ACCEPT;
proto tcp dport smtp ACCEPT;


interface $DEV_WIFI
# DHCP
proto udp dport 67:68 ACCEPT;
proto (udp tcp) dport domain ACCEPT;

proto udp dport netbios-dgm DROP;


# LOG all dropped packets
proto (udp tcp) &DROP();


# outgoing connections are not limited
chain OUTPUT policy ACCEPT;

chain FORWARD
policy DROP;

# connection tracking
mod state state INVALID DROP;
mod state state (ESTABLISHED RELATED) ACCEPT;

# connections from the internal net to the internet or to other
# internal nets are allowed
interface $DEV_PRIVATE ACCEPT;
interface $DEV_WIFI ACCEPT;

# LOG all dropped packets
proto (udp tcp) &DROP();


# IPv4 masquerade / NAT support

table nat
chain POSTROUTING
# masquerade private IP addresses
saddr $NET_PRIVATE outerface $DEV_WORLD MASQUERADE;


## IPv6:

domain ip6
table filter

chain INPUT
policy DROP;

# Internal traffic authorized
saddr $NET6_PRIVATE ACCEPT;
saddr $LINK6 ACCEPT;

# accept multicast
daddr ff00::/8 ACCEPT;

interface lo ACCEPT;

# For public traffic
# Only DNS resolution + NTP acceped for UDP
interface br0
proto udp

sport domain ACCEPT;

dport ntp ACCEPT;

&DROP();


# TCP on ports < 1024 forbidden except for SSH
proto tcp

dport ssh ACCEPT;

dport 0:1023 DROP;


# Accepted established traffic
mod state state INVALID DROP;
mod state state (ESTABLISHED RELATED) ACCEPT;

# incoming connections forbidden
proto tcp syn DROP;

# Accept ping
proto icmpv6 ACCEPT;


proto (udp tcp) &DROP();

chain FORWARD
policy DROP;

# All local traffic accepted
saddr $LINK6 ACCEPT;

# All ping accepted unless coming from internet
saddr ! $NET6_PRIVATE proto icmpv6 icmp-type echo-request DROP;
proto icmpv6 ACCEPT;

# Allow SSH to specific machines
proto tcp daddr $MACHINE_MYDESKTOP dport ssh ACCEPT;

# Accept established traffic
mod state state INVALID DROP;
mod state state (ESTABLISHED RELATED) ACCEPT;

# Accept outgoing traffic
saddr $NET6_PRIVATE ACCEPT;

# Accept local outgoing traffic
saddr ::1 ACCEPT;

proto (udp tcp) &DROP();


# ebtables
domain eb chain FORWARD
policy DROP;

# Only accept bridged traffic for IPv6
logical-in br0 logical-out br0
#ebtables -t broute -A BROUTING -p ! ipv6 -j DROP
proto IPv6 ACCEPT;


2.4 DNS config

The DreamPlug will run bind9 to cache the DNS for the wifi network (default config is OK out of the box).

3 Configuration for the LAN machines

3.1 Connection with Wifi
Machines connected with the WPA wifi network should get an IPv4 only address via DHCP on the 192.168.3.0/24 network. There's nothing to be configured specifically.

3.2 Ethernet connection on the switch
Machines connected via ethernet cables to the switch can run either with IPv4 config, in which case they should be configured statically for the 192.168.4.0/24 network, using the router on 192.168.4.1 as a gateway, or with IPv6 auto config. On wheezy, the /etc/network/interfaces will look like :
auto eth1
iface eth1 inet static
address 192.168.4.42
netmask 255.255.255.0
gateway 192.168.4.1
dns-nameservers 212.27.40.241 212.27.40.240

iface eth1 inet6 auto

4 To do list

The setup works fine, but there are a few things I'd like to improve :
  • running a regular Debian distro on the DreamPlug (the kernel used at the moment is patched for the wifi driver in master mode support), possibly using only Free Software.
  • using subnets for the IPv6 machines (but that seems not exactly obvious, requiring NDP proxying and stuff), so that the privacy is improved (the IPv6 auto generated global addresses depend on the MAC addresses hmmm probably not optimal).
  • adding more stuff to the DreamPlug router so that it becomes a full fledged FreedomBox.

5 References

Date: 2012-11-09 16:30:34 CET

8 November 2012

Jo Shields: Evil, or why Douglas Crockford is harmful to Free Software

Yesterday I received a new serious bug report against Mono in Debian. For those not in the know, serious severity is release critical, and can trigger removal of a package from the distribution in order to make a shipping release (e.g. if Debian is in deep freeze, as is the case right now). Bug 692614 relates to a single source file, ./mcs/class/System.Web.Extensions/System.Web.Script.Serialization/JsonDeserializer.cs, which is part of the System.Web.Extensions assembly. This file was written in 2008 by an upstream Mono developer, and is based on some code from json.org specifically JSON_parser.c and JSON_checker.c json.org code carries a non-standard license. Specifically, it s MIT/X11 with an added clause: The Software shall be used for Good, not Evil. I ve had some discussions with Mono upstream, and they believe that they have resolved the matter to their satisfaction their solution will make its way into Debian soon. But in the meantime, let s talk about the clause. The Free Software Foundation s Freedom 0 reads:
A program is free software if the program s users have the four essential freedoms:
  • The freedom to run the program, for any purpose (freedom 0).
The Debian Free Software Guidelines and Open Source Initiative s Open Source Definition clause 6 reads:
No Discrimination Against Fields of Endeavor The license must not restrict anyone from making use of the program in a specific field of endeavor. For example, it may not restrict the program from being used in a business, or from being used for genetic research.
It s fairly clear that the JSON.org license clause goes against both of these, making any piece of software using that license neither Open Source nor Free Software. It is not distributable by any organization which mandates Freedom for its users not in Debian, not in Fedora, not on Google Code. Anybody who cares about their users will reject a clause like this, because it has awful chilling effects. Think it s funny? It really isn t. Who can use the code without being at risk of a lawyer knocking on their doors? Can the Catholic Church? The ACLU? Republicans? Democrats? Military contractors? Genetic engineers? Big pharma? Petrochemicals firms? Communists? Fascists? Mono developers? WikiLeaks? Without a clear definition of good and evil , people need to seriously consider whether they are safe to use the code because if the developer and users interpretations of the terms differ, there could be hell to pay. Would you want to ship a hardware device let s say you re making a smart TV and have some developer of a library send his lawyers around to tell you sorry, TV rots kids brains, it s clearly evil to get your entire distribution channel shut down by injunction? It s not an oversight, kids. Upstream are well aware of the pain this childishness causes anyone who takes software licenses seriously. They giggle about it at conferences, like tweenagers who think they ve one-upped the adults in the room. This non-Free license is intended to mock people who take licensing seriously. In fact, one could easily categorise efforts to pollute the Free Software ecosystem with fake, non-Free software as evil, which would mean all JSON.org code fails to comply with its own license, due to shipping with its license (Inception, anyone?). Before the jokers in the room claim that this kind of problem is deserved by Mono, let s take a look at all the software in Debian which Douglas Crockford endangers with his childishness. PHP? OwnCloud? jQuery? You think Debian serves its users well by pulling jQuery from the next release in order to serve the ego of a man behaving like an eleven year old? It is also interesting to note that the author of this do no evil clause works at PayPal. Read that twice, go and repair your irony meters, then come back. In conclusion: thank you so VERY much Doug Crockford for making the world of Free Software measurably worse.

Tanguy Ortolo: Licence to kill -9

The title of the next James Bond movie! Or will that be the next OpenBSD release song? ;-)
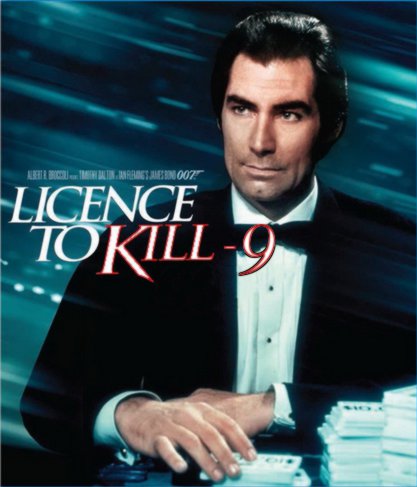
Parody of a James Bond movie poster: licence to kill -9

7 November 2012

Russell Coker: Rape Apology and LCA 2011

After a lecture at LCA 2011 included some inappropriate slides there was a long discussion on several mailing lists about the issues related to this. In February 2011 I wrote a blog post debunking some of the bogus arguments in question [1]. Of course the matter didn t end there, at LCA 2012 I was drawn into a few debates IRL about the issues, as long as there are more than a few men who want such porny pictures used in LCA talks the issue can t be properly resolved. The most serious aspect of the discussion in question is that of rape apology, the bad ideas that were presented have a real impact on the way people behave, merely making public statements saying that something is OK is going to increase the incidence of it happening. The Geek Feminism Wiki has a good page summarising the issue [2]. The Finally Feminism 101 post about Rape Culture is also worth reading in this context [3]. Recently Valeria Aurora wrote a post for the Ada Initiaive blog about the rape apology issue and how the community needs to act to prevent such behavior [4]. This inspired Matthew Garrett to write about the issue and state the position that In the absence of an apology and explanation from Ted, I ll be interacting with him to the bare minimum that I m compelled to as a result of my job [5]. I agree with Matthew s article, everything he writes is logical and I believe that it is all for the benefit of the FOSS community as a whole. I think that most guys have quietly defriended guys who are rape-positive in the past (for example when I was 12 I refused to play D&D with boys who were raping NPCs). But blogging about it, explaining the problem, and giving the offender the possibility to reform is a good idea and it s something that should be done more often. Sam Varghese has written about the issue for ITWire [6]. He has taken the wrong approach to this, he specifically claims that Matthew Garrett has kicked off what could be a damaging episode . I think that Matthew s approach is necessary and the situation demands it. If Matthew had been on holidays and I had read the TAI post earlier then I would probably have written a blog post which Sam could have described in a similar manner. So I don t think that Matthew kicked anything off (I think that someone had to do it). I also don t think that this has to be damaging it depends on how everyone reacts. On her personal blog Valerie says When I first read Ts o s comments, I couldn t sleep for two nights. I wanted to throw up every time I thought about it. I was furious and frightened at the same time. Every time I think about this, even now, I literally have nightmares. I can t bear the thought of working with him even over email, much less attending the same conferences [7]. I don t think that any of us who are seriously involved in the FOSS community have a way of avoiding this issue, allowing Valerie and other women who have the same understanding of the situation to go through that without any support is not a neutral action. I think we need to consider whether someone who gives other delegates and speakers nightmares should be welcome to attend a conference. Valerie s post makes sense to me and I can understand why she doesn t want to associated with Ted, my understanding of the issue isn t important or even required, I merely note this because I m sure that there are lots of readers who will ignore anything that a woman might say. ITWire has a follow-up article with Ted s response, Ted fails to address all the issues and seems to think that the people who disagree with him merely don t appreciate his nuance [8]. The thing is that the issue of the incidence of rape was raised in discussion to consider the probability that rape survivors would have been in the audience for the Mark Pesce talk in question. None of Ted s claims indicate that rape could be rare enough that a crowd of 500+ random people could be expected not to have multiple rape survivors so his comments weren t even relevant to the discussion. Ted seems unwilling to try to understand the position of all the people who disagree with him.

MJ Ray: Adrift @coopsutd in @coopParty workshop

image

Welney washes

Sometimes I felt at home at Cooperatives United, like at the wonderful fringe dinner at Eighth Day last Thursday night. Sometimes I felt overwhelmed by the flood, like at the cooperative party workshop on Friday morning. The workshop addressed the key questions: why do we want cooperative politicians, what could they do and what are the needs and challenges facing them? Personally, I felt the first is obvious and the answer is all the second. It s both frustrating (few ask why other movements want to influence politicians) and reassuring (no taboo topics) that the first question is asked. There were many fascinating answers to the other two questions from around the world. As so often with workshops, few hard conclusions were reached, but I think some interesting conversations were started there, which we might hear again in the future. What would I call the top challenge? Persuading open and transparent co-op members to join the party. I ve written about my difficulty with joining political parties in the past, as some forms of collective responsibility are against my beliefs and I m not sure that joining a small party will help anyone much, but I think I ll take another look at the cooperative party, all the same. The picture above is of the Welney washes, some miles south-west of Lynn. It s a stunning wetland environment, and it surprises me every time the train crosses the floods, as it did on the way to Manchester. And yes, I ve shoehorned a picture I liked into this article!

6 November 2012

Michael Stapelberg: Debian Code Search

I hereby announce a new Debian project: Debian Code Search. Debian Code Search is a search engine for program source code within Debian.
It allows you to search all 17000 source packages, containing 130 GiB of
FLOSS source code (including Debian packaging) with regular expressions. You can use the search engine at http://codesearch.debian.net/
Here are a few sample queries: The corresponding thesis (and source code, of course) will be released soon
(2013-01-15 being the deadline, but I hope I can do it earlier).

Stefano Zacchiroli: bits from the DPL for October 2012

Freshly baked, bits from the DPL for October 2012.
Dear Project Members,
another month, another periodic report of DPL-ish activities, this time for October 2012. Highlights Debian on public clouds I've spent quite some time to improve Debian presence on the so called "public clouds". Following up to an inquiry of a fellow developer, I've reached out to Microsoft to investigate the possibility of having Debian as an option on Windows Azure. Around the same time, I've been approached by Amazon to have Debian as an option on the AWS marketplace. In both cases, we will need to overcome challenges of various kinds, at the technical (e.g. image preparation), bureaucratic (e.g. terms of the agreements we'll need to accept to be present), and political (e.g. chain of trust, platform freedom) levels. Up to now, discussions have been going on mostly in private, simply because they started as 1-to-1 inquiries and continued from there, but there is no good reason they should remain so. Hence, thanks to the listmasters and in particular Alexander Wirt, we have setup the new debian-cloud mailing list. If you are interested in these topics please join the list. For both Azure and AWS there is good progress on the technical part already; summaries will soon be posted on the list so that we are all on the same page. Similarly, I'll post there status reports about the bureaucratic requirements. And of course there is no reason to focus on specific clouds, if you'd like to support others and are willing to put some work to that end, please join the list and let us know. DPL helpers meeting I've already bothered you at least in my last platform and DebConf13 talk with observations about how non-scalable the DPL job is. After having collected applications of DPL helpers for a while, I've finally sat down and tried to put those applications into good use. The idea is simple: to the extend of possible, we should shift from a one-man-band job to a more "board-like" job, with people sharing an agenda, a list of outstanding tasks, and public communication. We have started slowly, setting up the #debian-dpl IRC channel and running periodic bi-weekly meetings there. You can find the meeting minutes and full logs at the usual place. We are still ramping up, so we don't have yet "fancy" stuff like a mailing list or an issue tracker entry, but they're in the working. Some of the outcome are starting to show, too (e.g. as part of recent discussions on 3rd party orphaning, or on our inbound trademark policy, or even in the forthcoming DMCA policy to make mentors.d.n an official project service). It's an experiment and a big challenge. I'm, for one thing, not yet convinced there are enough people interested in sharing the load of DPL duties (that look boring, for many tech geeks) in the long run. But I'm also convinced that the sustainability of the Debian organization model depends on this, so it's worth trying. If you're interested in the challenge and willing to volunteer some of your time, please join us on #debian-dpl . I'll take care of keeping the project informed of further evolution, in particular about the communication channels we will pick for day to day activities and accountability. Events / public communication I've spent most of my remaining Debian time in October attending events on behalf of the Project, in particular: On the topic of public communication, I've also coordinated with the press team an answer to a press inquiry about Secure Boot (which has become part of this article), and happily vouched for the Ubuntu charity marathon, adding some Debian challenges to it. Delegations As largely overdue matters, I've finalized the delegations mentioned last month, namely: FTP masters, New Members Front Desk, and Policy editors. Assets and legal stuff Miscellanea Now let's all go back to RC Bug squashing to make Wheezy a reality. SPAM-my link of the month is http://udd.debian.org/bugs.cgi and its various "views" at the bottom of the page. Cheers.
PS the day-to-day activity log for October 2012 is available at the usual place master:/srv/leader/news/bits-from-the-DPL.txt.201210

Andrew Pollock: [life] On leasing a Leaf

Circumstances have required us to become a two-car family, and I've been very keen on the Nissan Leaf for some time. It's an excellent little car. A friend had leased one, and had positive things to say about the whole leasing process, so on Saturday we leased one ourselves. Now that we've been through the process, I'm not sure why you'd ever buy a car instead of lease. We paid $4,628 as a "down payment" (of which we'll get a $2,500 rebate) and it's going to cost I think $257 a month. Maintenance for the 3 years is included in those monthly payments as is any damage to the vehicle at the end of the lease. After the 3 years you hand the car back or pay out the residual. We plan on handing the car back. We get 12,000 miles a year, after which it's 15 cents a mile. There's no way in the world we'll do 12,000 miles a year in it. The last three cars I've owned I've just paid for in cash, because I generally don't like debt and like to minimise my monthly outlays, but in the case of cars, I also don't like forking out a large wad of cash for something that instantly loses value the moment it drives off the lot. I also think that given the pace of innovation in the electric vehicle space, the new hotness in three years time will be even more awesome than the Leaf is today. It gets delivered tomorrow.

Rapha&#235;l Hertzog: My Free Software Activities in October 2012

This is my monthly summary of my free software related activities. If you re among the people who made a donation to support my work (120.46 , thanks everybody!), then you can learn how I spent your money. Otherwise it s just an interesting status update on my various projects. Dpkg At the start of the month, I reconfigured dpkg s git repository to use KGB instead of the discontinued CIA to send out commit notices to IRC (on #debian-dpkg on OFTC, aka irc.debian.org). I didn t do anything else that affects dpkg and I must say that Guillem does not make it easy for others to get involved. He keeps all his work hidden in his private for 1.17.x branch and refuses to open an official jessie branch as can be seen from the lack of answer to this mail. On the bright side, he deals with almost all incoming bugs even before I have a chance to take care of them. But it s a pity that I can never review any of his fixes because they are usually pushed shortly before an upload. Misc packaging I helped to get #689336 fixed so that the initrd properly setups the keymap before asking for a passphrase for an encrypted partition. Related to this I filed #689722 so that cryptsetup gains a dependency ensuring that the required tools for keymap setup are available. I packaged a new upstream version of zim (0.57) and also a security update for python-django that affected both Squeeze and Wheezy. I uploaded an NMU of revelation (0.4.13-1.2) so that it doesn t get dropped from Wheezy (it was on the release team list of leaf packages that would be removed if unfixed) since my wife is using it to store her passwords. I sponsored a new upstream version of ledgersmb. Debian France We managed to elect new officers for Debian France. I m taking over the role of president, Sylveste Ledru is the new treasurer and Julien Danjou is the new secretary. Thank you very much to the former officers: Carl Chenet, Aur lien Jarno and Julien Cristau. We re in the process of managing this transition which will be completed during the next mini-Debconf in Paris so that we can exchange some papers and the like. In the first tasks that I have set myself, there s recruiting two new members for the boards of directors since we re only 7 and there are 9 seats. I made a call for volunteers and we have two volunteers. If you want to get involved and help Debian France, please candidate by answering that message as soon as possible. The Debian Handbook I merged the translations contributed on debian.weblate.org (which led me to file this wishlist bug on Weblate itself) and I fixed a number of small issues that had been reported. I made an upload to Debian to incorporate all those fixes But this is still the book covering Squeeze so I started to plan the work to update it for Wheezy and with Roland we have decided who is going to take care of updating each chapter. Librement Progress is annoyingly slow on this project. Handling money for others is highly regulated, at least in the EU apparently. I only wanted an escrow account to secure the money of users of the service but opening this account requires either to be certified as a payment institution by the Autorit de contr le prudentiel or to get an exemption from the same authority (covering only some special cases) or to sign a partnership with an established payment institution. Being certified is out of scope for now since it requires a minimum of 125000 EUR in capital (which I don t have). My bank can t sign the kind of partnership that I would need. So I have to investigate whether I can make it fit in the limited cases of exemption or I need to find another payment institution that is willing to work with me. Gittip uses Balanced a payment service specialized in market places but unfortunately it s US-only if you want to withdraw money from the system. I would love a similar service in Europe If I can t position Librement as a market place for the free software world (and save each contributor the hassle to open a merchant account), then I shall fallback to the solution where Librement only provides the infrastructure but no account, and developers who want to collect donations will have to use either Paypal or any other supported merchant account to collect funds. That s why my latest spec updates concerning the donation service and the payment service mentions Paypal and the possibility of choosing your payment service for your donation form. Thanks See you next month for a new summary of my activities.

5 comments Liked this article? Click here. My blog is Flattr-enabled.

Michal &#268;iha&#345;: Playing with HTML microdata

Since Google introduced support for "Rich snippets", I wanted to play with that technology a bit. I've already used microformats in the past, but today's preferred solution seems to be microdata, which plays nicely with HTML 5. To have some real data to show, I've chosen spolecneaktivity.cz, a community site for free time activities (sorry it is Czech only). It provides me XML export of some data to play with. After a little bit of hacking, I wrote a Python script to parse that and output HTML with all microdata details I've found in original XML. The output now lives at http://cihar.com/aktivity/ and Google's Structured Data Testing Tool seems to parse this just fine. The only question is whether it will show up in the results sometimes as it warns "urls are pointing to a different domain than the base url".

Filed under: English Website 0 comments Flattr this!

Russ Allbery: Review: Cerebus

Review: Cerebus, by Dave Sim
Series: Cerebus #1
Publisher: Aardvark-Vanaheim
Copyright: August 1987
Printing: July 2003
ISBN: 0-919359-08-6
Format: Graphic novel
Pages: 546
Cerebus is something of a legend in comics. Begun in December of 1977 by Dave Sim, it was one of the first entirely independent, self-published comics in a field dominated by the large work-for-hire companies like Marvel and DC. It ran for 300 issues and nearly 27 years and became one of the most influential independent comic books of all time, in part due to Sim's outspoken views in favor of creator rights and his regular use of the editorial pages in Cerebus issues to air those views. This collection (the first "phonebook") collects issues 1 through 25, with one of the amazing wrap-around covers that makes all of the phonebooks so beautiful (possibly partly by later Cerebus collaborator Gerhard, although if so it's uncredited so far as I can tell). Cerebus reliably has some of the best black-and-white art you will ever see in comics. There is some debate over where to start with Cerebus, and a faction that, for good reasons, argues for starting with the second phonebook (High Society). While these first twenty-five issues do introduce the reader to a bunch of important characters (Elrod, Lord Julius, Jaka, Artemis Roach, and Suenteus Po, for example), all those characters are later reintroduced and nothing that happens here is hugely vital for the overall story. It's also quite rough, starting as Conan parody with almost no depth. The first half or so of this collection features lots of short stories with little or no broader significance, and the early ones are about little other than Cerebus's skills and fighting abilities. That said, when reading the series, I like to start at the beginning. It is nice to follow the characters from their moment of first introduction, and it's delightful to watch Sim's ability grow (surprisingly quickly) through the first few issues. Cerebus #1 is bad: crude, simplistic artwork, almost nothing in the way of a story, and lots of purple narration. But flipping forward even to Cerebus #6 (the first appearance of Jaka), one sees a remarkable difference. By Cerebus #7, Cerebus looks like himself, the plot is getting more complex, and Sim is clearly hitting his stride. And, by the end of this collection, the art has moved from crude past competent and into truly beautiful in places. It's one of the few black-and-white comics where I never miss color. The detailed line work is more enjoyable than I think any coloring could be. The strength of Cerebus as an ongoing character slowly emerges from behind the parody. What I like the most about Cerebus is that he's neither a predestined victor (apart from the early issues that follow the Conan model most closely) nor a pure loner who stands apart from the world. He gets embroiled in political affairs, but almost always for his own reasons (primarily wealth). He has his own moral code, but it's fluid and situational; it's the realistic muddle of impulse and vague principle that most of us fall back on in our everyday life, which is remarkably unlike the typical moral code in comics (or even fiction in general). And while he is in one sense better and more powerful than anyone else in the story, that doesn't mean Cerebus gets what he wants. Most stories here end up going rather poorly for him, forcing daring escapes or frustrating cutting of losses. Sim quickly finds a voice for Cerebus that's irascible, wise, practical, and a bit world-weary, as well as remarkably unflappable. He's one of the best protagonists in comics, and that's already clear by the end of this collection. Parody is the focus of these first issues, which is a mixed bag. The early issues are fairly weak sword-and-sorcery parody (particularly Red Sonja, primarily a vehicle for some tired sexist jokes) and worth reading only for the development in Sim's art style and the growth of Cerebus as a unique voice. Sim gets away from straight parody for the middle of the collection, but then makes an unfortunate return for the final few issues, featuring parodies of Man-Thing and X-Men that I thought were more forced than funny. You have to have some tolerance for this, and (similar to early Pratchett) a lot of it isn't as funny as the author seems to think it is. That said, three of Sim's most brilliant ongoing characters are parodies, just ones that are mixed and inserted into the "wrong" genres in ways that bring them alive. Elrod of Melvinbone, a parody of Moorcock's Elric of Melnibone who speaks exactly like Foghorn Leghorn, should not work and yet does. He's the source of the funniest moments in this collection. His persistant treatment of Cerebus as a kid in a bunny suit shouldn't be as funny as it is, but it reliably makes me laugh each time I re-read this collection. Lord Julius is a straight insertion of Groucho Marx who really comes into his own in the next collection, High Society, but some of the hilarious High Society moments are foreshadowed here. And Artemis Roach, who starts as a parody of Batman and will later parody a huge variety of comic book characters, provides several delightful moments with Cerebus as straight man. I'm not much of a fan of parody, but I still think Cerebus is genuinely funny. High Society is definitely better, but I think one would miss some great bits by skipping over the first collection. Much of what makes it work is the character of Cerebus, who is in turn a wonderful straight man for Sim's wilder characters and an endless source of sharp one-liners. It's easy to really care about and root for Cerebus, even when he's being manipulative and amoral, because he's so straightforward and forthright about it. The world Sim puts him into is full of chaos, ridiculousness, and unfairness, and Cerebus is the sort of character to put his head down, make a few sarcastic comments, and then get on with it. It's fun to watch. One final note: I've always thought the "phonebook" collections were one of Sim's best ideas. Unlike nearly all comic book collections, a Cerebus phonebook provides enough material to be satisfying and has always felt like a good value for the money. I wish more comic book publishers would learn from Sim's example and produce larger collections that aren't hardcover deluxe editions (although Sim has an admitted advantage from not having to reproduce color). Followed by High Society. Rating: 7 out of 10

5 November 2012

Vincent Sanders: Another NetSurf Developer Workshop

The NetSurf Developers - Bringing you alternative internet meme delivery since 2002
The weekend saw some of the NetSurf developers gather once again to do battle against the Red Queen...no, wait. I mean plan and write code.

The successful event was once again kindly hosted by Collabora at their Cambridge office, the facilities remain as good as at the previous event and provided a comfortable environment in which to work.

Four developers managed to attend from around the UK John-Mark Bell, Vincent Sanders, Daniel Silverstone and Rob Kendrick. The turnout was a little lower than previous events, however Michael Drake managed to assist with some bug fixes remotely.

From Friday to Sunday afternoon we each managed to put in 24 hours of work consisting of almost 90 commits changing over 100 files and removing 10,000 lines of code.

Whiteboard with the 3.0 release tasks
The main theme of the event was consolidation ready for the 3.0 release. While not a glamorous target this is a major release for the project which we want to achieve soon, this requires the completion of numerous ongoing tasks (like finally removing the dependency of libxml) and fixing as many reported bugs as possible.

The Major things we achieved were:

Once the final usage of libXML is removed (from the hotlist code) NetSurf will become substantially smaller on several platforms as we will not have two separate parser implementations linked.

One big feature of the 3.0 release which was not originally on the roadmap is that of JavaScript. We initially intend to provide two builds of with and without the JavaScript interpreter compiled into NetSurf. This allows those on very small systems to continue to run NetSurf and those users who want a richer web experience to enjoy it.

Although JavaScript is a major new feature which is frequently requested the initial implementation will be incomplete. To complete the feature several thousand JavaScript to DOM interface binding functions must still be written. In addition it should be noted that we have yet to add dynamic layout or extensions such as Canvas or WebGL

We had a Raspberry Pi which was used to run RISC OS so we could examine the operation on this system.

The 2.9 edition as shipped works OK but is lacking the substantial progress made in the last six months.

The CI system build was run on the system and works well so we are reassured the 3.0 edition will provide an even better browsing experience.

The event was a great success overall and we are now very close to our 3.0 release which we hope to produce before Christmas.

Michal &#268;iha&#345;: Weblate 1.3 on l10n.cihar.com

As Weblate release is getting closer, I've decided to give new version more testing in real life and it got deployed at http://l10n.cihar.com/. This release brings quite a lot of new features, most interesting for users might be: You can see full list of changes in our documentation. As usual, I hope this upgrade will go smoothly and won't cause any big problems :-).

Filed under: English Phpmyadmin Website 0 comments Flattr this!

MJ Ray: Seize the Media! @theBoyler @coopsutd

image

1 Angel Square

So when I arrived on Thursday (ten minutes early despite a cancelled train, thanks to help from the cooperative fellow traveller mentioned last post), I was in time to go to a workshop on media cooperatives led by @theBoyler. It wasn t what I expected. It seemed to concentrate on the opportunity presented by the current awful state of news media companies in many countries and the technology-driven changes to their businesses. For example, WordPress is a viable way to start online first, then move into print later. There are already news co-ops in places where there would be no local news media. The challenge well be how to overcome what I d call spoiling or scorched earth tactics from departing media companies. Some local news media owners are looking for a way out. One obvious one is to turn a local title into a minor variation on a regional-or-worse service or publication, maybe by selling it to a bigger media business. That loses some audience but many will put up with it, so it avoids creating an obvious gap in the market for more truly local reporting. Much else was covered and the audience suggested tons of examples. I m not sure we reached many firm conclusions, but there seem quite a few examples to learn from (Morning Star, taz, ) and Dave Boyle s work is continuing

4 November 2012

Wouter Verhelst: Windows usability: followup.

Yesterday, I posted a blog post containing a list of issues with Windows, in response to a similar list for Linux, which has received quite some response; I've seen people +1 it on google+, and I've received a number of replies on the blog post itself. One of these replies was by the author of the original list; and as expected, he totally and utterly failed to see the point. He also has the audacity to claim I haven't installed Linux yet what?!? The last time I used anything other than Linux on my personal machine for any real work was on Windows 98. And no, that was not because I was too cheap to buy the latest and greatest. I have used Windows in some cases since then, but never on my own hardware. First of all, I should note that the list which I posted was only semi-serious (with tongue in cheek); the fact that it refers to Windows as the operating system which "attempts to replace Linux as the major operating system" should have been a pretty big clue to that effect. Like the original list that it was a reply to, my list contains things that are only true in a particular context (e.g., the one about requiring recent hardware), it contains things that don't matter for the large majority of Windows users (e.g., the point about focus-follows-mouse) but that are major arguments for why I don't use Windows, it contains things that are so alien to what most of us are used to that even most Linux users don't use it, while on the other hand some swear by it (like the SELinux argument), and it contains some things that a seasoned Windows user will call bullshit on but that are real actual problems for the non-seasoned Windows user that I am (such as the mouse argument). It also contains some actual facts, like the statement about most crashes being a direct result of faulty drivers that's pulled directly from a scientific study on the subject conducted by Microsoft, together with some independent researchers. Like the original list, I don't expect this list to change anything for the better, precisely because it is flawed in exactly the same way. But whether the items on that list were right or wrong isn't the point. This is: Nobody (except nutcases) ever said Linux is perfect, or that it's useful for everyone; and while the issues Artem lists may be bugs or may be design flaws or any of a number of other things that could be real problems, the fact is that creating a long "list of issues" isn't going to solve anything. If you find that there are problems with Linux, you basically have three options: fix the problem, get someone to fix it for you, or stop using Linux. Really. Rather than better or worse, Linux is different. It will have its own set of problems, and it will have its own set of advantages. Some of the design decisions cause problems, but also have serious advantages, and focussing on only these problems (the existence of which I'm not denying) isn't very helpful. A good example is the library model: under Linux, libraries are typically installed in a system-wide location, and use a SONAME which is (part of) the filename of that library and which defines the binary interface exported by that library. In contrary to the situation under Windows, Linux libraries also must use position-independent code. The result is a more robust library model. The downside to that model, however, is that when you install older applications that require older SONAME versions of a particular library, getting those older versions may be a challenge. While in theory, installing an older version of a library is not going to cause any problem if the SONAME is different, in practice you'll often find that you'll need to go to (unsupported) older packages from older versions of the distribution, which may not install due to missing or conflicting dependencies, or which may expect data files in a different format in the same location that newer versions of the same library do, or which may have any number of other issues. When that happens, the solution is to either use an older version of the distribution in a chroot or some such, or to patch and/or compile the needed libraries yourself, and install them alongside the newer version of the same library. That's perfectly possible, after all, precisely because of the SONAME. Another good example is the development model: where Windows has a central authority (Microsoft) which defines what it is to be "Windows" and what is and isn't part of that, the same simply isn't true about Linux. Yes, Linus defines what the official Linux kernel has, but he doesn't have any say about the user interface, the boot process, or any number of other things; other people make decisions there. As a result, in effect, who decides what it means to be a "Linux system" is, really, you, the user. If you believe that the Linux user space is completely wrong, you can just change it to something else entirely; and that's precisely what Google did when they created Android. Since there's no central authority making decisions about what will and won't go into the system, this means that inevitably, at any given time, there will be many competing options for many subsystems. Usually this will be an advantage; e.g., the competition between KDE and Gnome benefits both. Sometimes, however, the competing options are so confusingly interwoven that even those who should know the system inside out can't make heads or tails of it, and debugging issues then becomes quite a challenge. Unfortunately, the Linux sound subsystem is currently an example of the latter. I'm not saying that all the items in Artem's list are invalid; a minority are, in fact, actual problems for a majority of Linux users. Most however, are personal opinions, issues affecting only a small minority of Linux users, or, as above, things where he only talks about the downsides of a design decision that also has major advantages. As an example of something in the second category: it's easy, for example, to list hundreds if not thousands of issues relating to particular pieces of hardware that don't work under Linux, simply because the manufacturer doesn't provide any information, and the people developing drivers for Linux have to reverse engineer how everything works. If you're a bit careful in what you buy, however much like MacOS users need to be careful, too then using Linux isn't an issue. My Lenovo Thinkpad X220, for instance, has no parts that don't work; and this includes things like a docking station, and the fact that my (9-cell) battery life is over fourteen hours, which (I believe) is more than on the same laptop with the same battery under Windows. So how is making a list of issues useful? The answer to that is simply, not at all. If you want to help, don't look for other people's problems; we can all do that. Instead, try to look for solutions to these problems. That's not always easy, and in many cases requires that you first understand why something is done in a particular way. If you don't want to spend time doing that, that's perfectly fine; but then don't expect that open source developers (who are already strapped for time, usually) will suddenly jump up and fix the problems you think are most important, as opposed to what they think should be worked on most urgently. After all, most Open Source developers have their own sets of priorities what they think requires most work, and that's what they'll work on not what's shown in a particular list by someone they don't know and have no reason to respect, somewhere on the Internet. Finally, I'd like to note that any statement which claims that Linux isn't "ready" to be used on the desktop, when hundreds of thousands (if not millions) of people are using it in exactly that way for their day-to-day work, is insulting these people's intelligence. Since that includes me, it's also insulting my intelligence. And I don't like to have my intelligence insulted...

Petter Reinholdtsen: The European Central Bank (ECB) take a look at bitcoin

Slashdot just ran a story about the European Central Bank (ECB) releasing a report (PDF) about virtual currencies and bitcoin. It is interesting to see how a member of the bitcoin community receive the report. As for the future, I suspect the central banks and the governments will outlaw bitcoin if it gain any popularity, to avoid competition. My thoughts go to the W rgl experiment with negative inflation on cash which was such a success that it was terminated by the Austrian National Bank in 1933. A successful alternative would be a threat to the current money system and gain powerful forces to work against it. While checking out the current status of bitcoin, I also discovered that the community already seem to have experienced its first pyramid game / Ponzi scheme. Not very surprising, given how members of "small" communities tend to trust each other. I guess enterprising crocks will try again and again, as they do anywhere wealth is available.

Next.

Previous.