Search Results: "ed"

13 November 2016

Andrew Cater: Debian Miniconf, ARM Cambridge 10/11/16 - post 3

Quiet room with occasional outbursts of talking. One of my problems with radio gear down to broken cable so that's OK-ish - I have spares.

And suddenly it's 1720 and we need to leave at about 1730.

2 x radio receivers tried: 2 x transmitters working ready for talk on Saturday.

Spare huge bag of cables appreciated by others - it's amazing how often you find someone else needs stuff :)


Andrew Cater: Debian Miniconf ARM, Cambridge 10/11/16 - post 2

Now about 30 people here: the video team are chasing down power leads and cables in readiness for the weekend.

One large open plan room with about 30 small quadrilateral tables - two make a hexagon. Very quiet for open plan: periodically the room falls completely silent - lots of developers quietly coding / reading screens.

Lunch was very good curry: ARM caterers feed us very well indeed :D

The radio I'm trying to program refuses to play with the software: the maintainer is at the back of the room and has offered to sort out a backport to Debian stable. Debian can occasionally seem like a dysfunctional family but it's good to be a member.

The Cubietruck I bought last year is sitting with another developer as I speak - he's going to try adding multiple disks for a RAID array on a machine that only draws 5W or so.

Andrew Cater: Debian Miniconf, ARM, Cambridge 10/11/16 - Post 1

More or less just getting going: there are eight of us here.

Release team are round one desk and a couple of others of us are on adjacent tables. Coffee is good, as ever :)

ARM very helpful as ever: they have been able to provide a disabled space for me though parking here is really, really tight

Andrew Cater: MiniDebconf ARM Cambridge 13/11/16 - Day 4 post 4 - lightning talks

Ian Jackson - dgit in two slides with attitude :)

Mike Crowe - Code Club - volunteering to teach programming to school children in after school clubs. Scratch: version 1 is packaged for Debian and Raspberry Pi CSS HTML Python - all materials provided. Projects for Microbits as well. No slides.

Dimitri Ledkov - SPI board - explaining about SPI. SPI - US non-profit, also registered in Europe. Collects donations, can register trademarks, can hold assets on your project's behalf. Volunteer project: controlled by member orgs.

Guus Sliepen - ifupdown - dual protocol, bonding, VPNs, wireless,
- too many slides :)


Andrew Cater: MiniDebconf Cambridge, ARM, 13/11/16 - Day 4 post 3

Just about to watch Daniel Silverstone demonstrating his new FPGA board.

Mystorm - open hardware - growing out of Icestorm. Programmable hardware - toolchains - and showing the hardware.

The Debian video team have advised that they are about to start the transcoding process - videos will be available soonish :)

http://video.debconf.org/minidebconf-low.webm


Petter Reinholdtsen: Coz profiler for multi-threaded software is now in Debian

The Coz profiler, a nice profiler able to run benchmarking experiments on the instrumented multi-threaded program, finally made it into Debian unstable yesterday. Llu s Vilanova and I have spent many months since I blogged about the coz tool in August working with upstream to make it suitable for Debian. There are still issues with clang compatibility, inline assembly only working x86 and minimized JavaScript libraries. To test it, install 'coz-profiler' using apt and run it like this:
coz run --- /path/to/binary-with-debug-info
This will produce a profile.coz file in the current working directory with the profiling information. This is then given to a JavaScript application provided in the package and available from a project web page. To start the local copy, invoke it in a browser like this:
sensible-browser /usr/share/coz-profiler/viewer/index.htm
See the project home page and the USENIX ;login: article on Coz for more information on how it is working.

Andrew Cater: Debian MiniConf, ARM Cambridge, 13/11/12 - Day 4 post 2

Just watching Lars Wirzenius talking about Qvarn - identity and data protection management on large scale. Compliant with EC data/identity management regulations and concerns.

The room fell silent at 1100 for two minutes - as we did on Friday 11/11/12.
This is remembering the dead, wounded and those affected by the wars of the 20th and 21st centuries.

Inevitably, it also reminded me of friends and colleagues in Debian that are no longer with us: for Espy and so many others before and since, thanks from me - you are well remembered here.

Daniel Pocock: Are all victims of French terrorism equal?

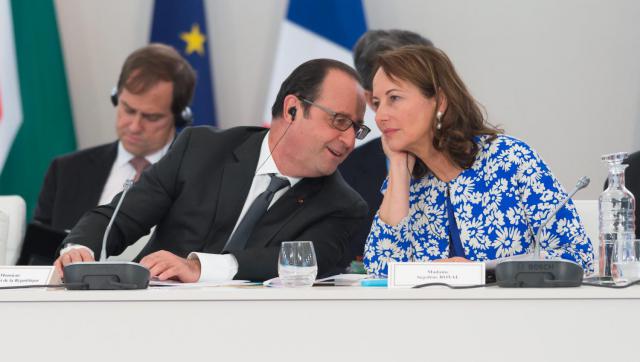
Some personal observations about the terrorist atrocities around the world based on evidence from Wikipedia and other sources The year 2015 saw a series of distressing terrorist attacks in France. 2015 was also the 30th anniversary of the French Government's bombing of a civilian ship at port in New Zealand, murdering a photographer who was on board at the time. This horrendous crime has been chronicled in various movies including The Rainbow Warrior Conspiracy (1989) and The Rainbow Warrior (1993). The Paris attacks are a source of great anxiety for the people of France but they are also an attack on Europe and all civilized humanity as well. Rather than using them to channel more anger towards Muslims and Arabs with another extended (yet ineffective) state of emergency, isn't it about time that France moved on from the evils of its colonial past and "drains the swamp" where unrepentant villains are thriving in its security services? Fran ois Hollande and S gol ne Royal. Royal's brother G rard Royal allegedly planted the bomb in the terrorist mission to New Zealand. It is ironic that Royal is now Minister for Ecology while her brother sank the Greenpeace flagship. If Fran ois and S gol ne had married (they have four children together), would G rard be the president's brother-in-law or terrorist-in-law? The question has to be asked: if it looks like terrorism, if it smells like terrorism, if the victim of that French Government attrocity is as dead as the victims of Islamic militants littered across the floor of the Bataclan, shouldn't it also be considered an act of terrorism? If it was not an act of terrorism, then what is it that makes it differ? Why do French officials refer to it as nothing more than "a serious error", the term used by Prime Minister Manuel Valls during a recent visit to New Zealand in 2016? Was it that the French officials felt it was necessary for Libert , galit , fraternit ? Or is it just a limitation of the English language that we only have one word for terrorism, while French officials have a different word for such acts carried out by those who serve their flag? If the French government are sincere in their apology, why have they avoided releasing key facts about the atrocity, like who thought up this plot and who gave the orders? Did the soldiers involved volunteer for a mission with the code name Op ration Satanique, or did any other members of their unit quit rather than have such a horrendous crime on their conscience? What does that say about the people who carried out the orders? If somebody apprehended one of these rogue employees of the French Government today, would they be rewarded with France's highest honour, like those tourists who recently apprehended an Islamic terrorist on a high-speed train? If terrorism is such an absolute evil, why was it so easy for the officials involved to progress with their careers? Would an ex-member of an Islamic terrorist group be able to subsequently obtain US residence and employment as easily as the French terror squad's commander Louis-Pierre Dillais? When you consider the comments made by Donald Trump recently, the threats of violence and physical aggression against just about anybody he doesn't agree with, is this the type of diplomacy that the US will practice under his rule commencing in 2017? Are people like this motivated by a genuine concern for peace and security, or are these simply criminal acts of vengence backed by political leaders with the maturity of schoolyard bullies?

Andrew Cater: Debian MiniConf, ARM Cambridge 13/11/16 - Day 4 post 1

Just got here, partway into Guus Sliepen's talk about issues with sourceless packages and the DFSG. Lots of problems with, for example, music for games and imagery and also areas where packages autobuild / use generated blobs which are not supplied or are not able to be regenerated.

Checked in by front desk - thanks again to Lisa, to Jo McIntyre and Lucy Wayland who have been very patient waiting for us, very helpful as ever, chasing us at the end of each day to reconcile badges and people and doing all the useful stuff that no one sees.

ARM security folk are still here, obviously, and the building work has stopped for the weekend so we can get in and out of the building more readily. Thanks once again to the ARM staffers who are also Debian-ites and to the ARM management who have to authorise all of this and allow us to use their facilities, buildings and guest WiFi. It's testament to a whole lot of hard work behind the scenes that this all seems seamless and (generally) works so well

Hideki Yamane: LTS for PowerPC?

Debian9 "Stretch" drops powerpc as release architecture, it means Debian based powerpc box would need more effort to maintain in the future.

If you use Debian for powerpc box in production environment, it maybe better to consider to join LTS funding and ask LTS team to add it to Jessie LTS architecture. I'm not sure they accept it or not, but if it's okay (as they did for armel and armhf), it may be worth to reduce your trouble.

12 November 2016

John Goerzen: Morning in the Skies

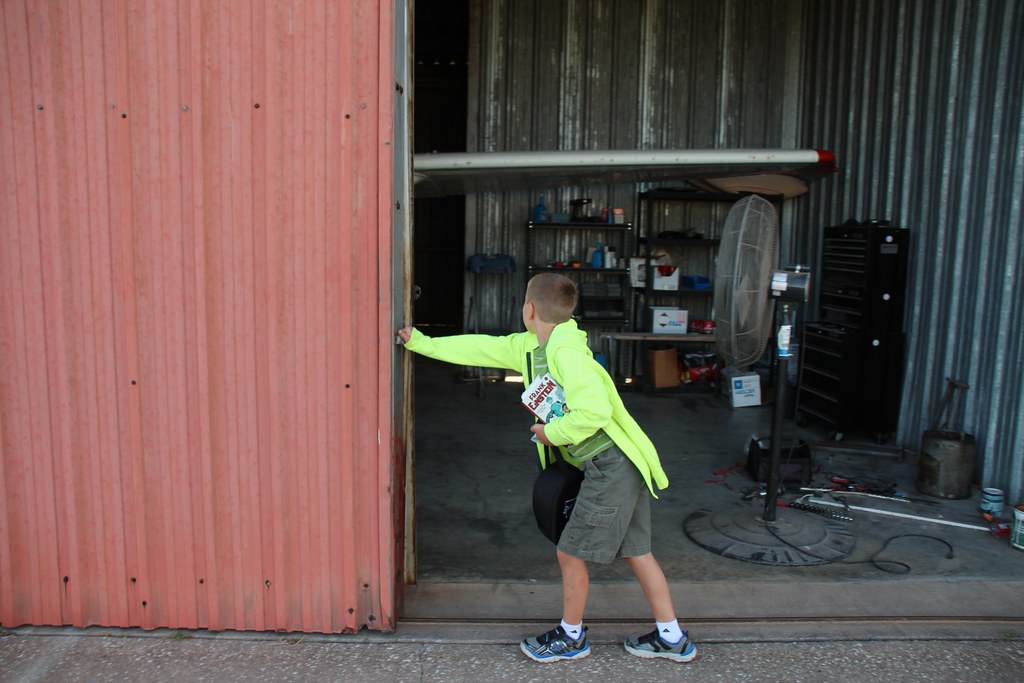
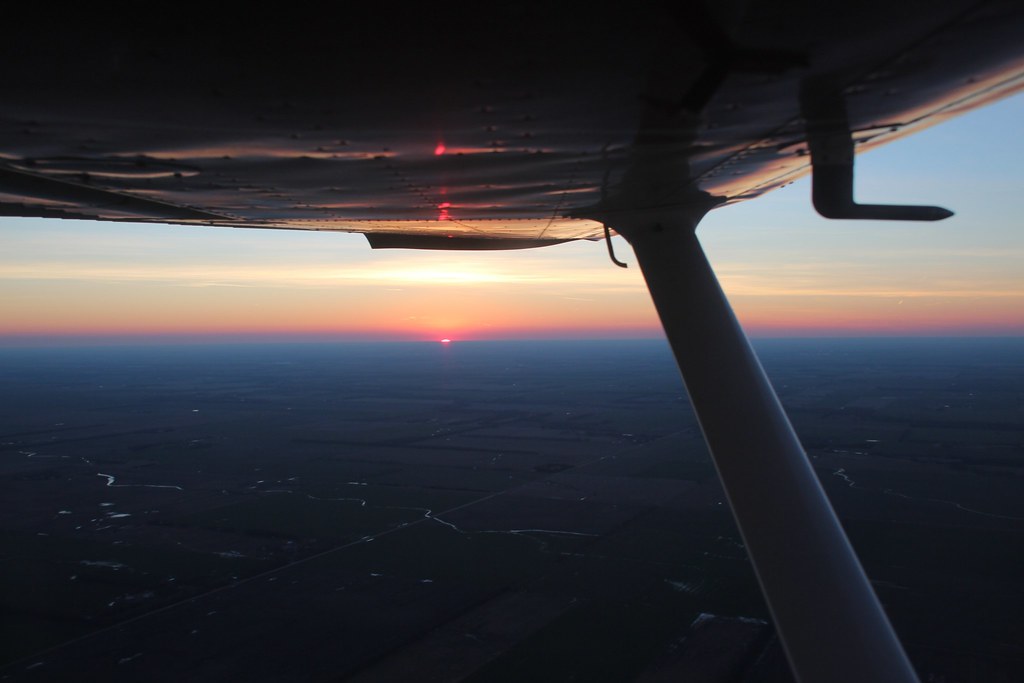
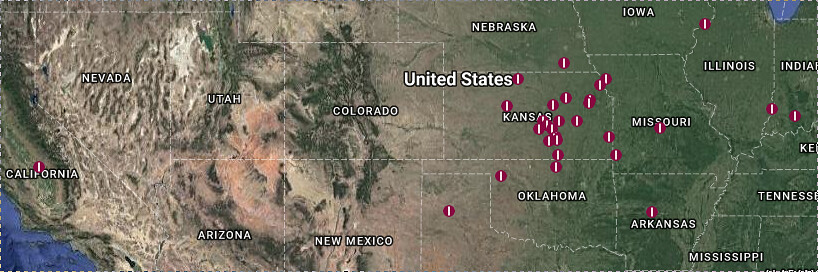
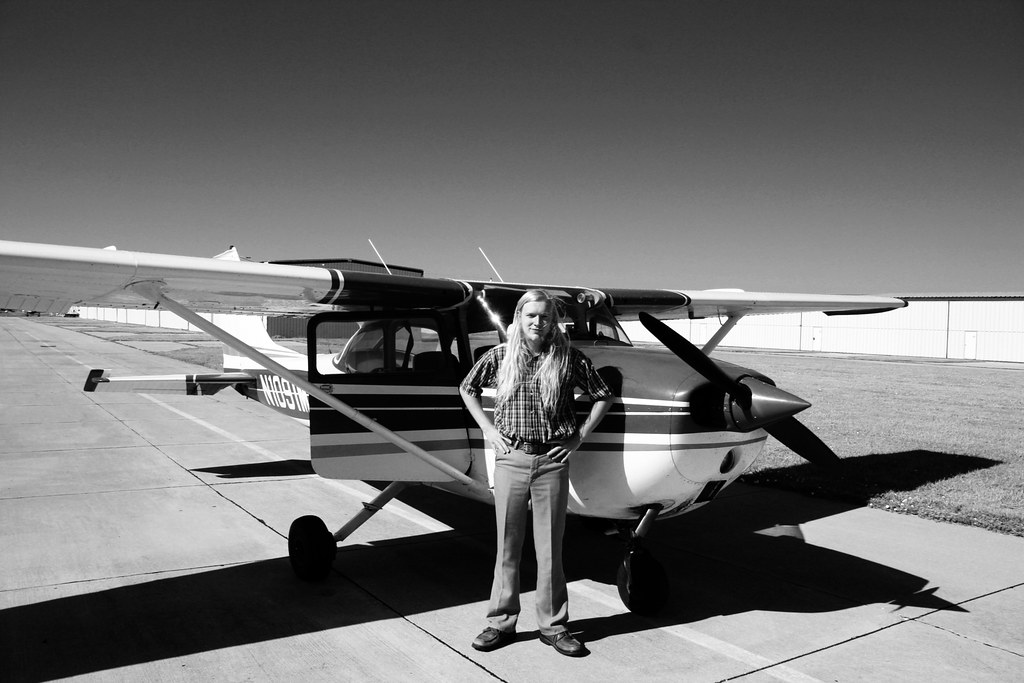
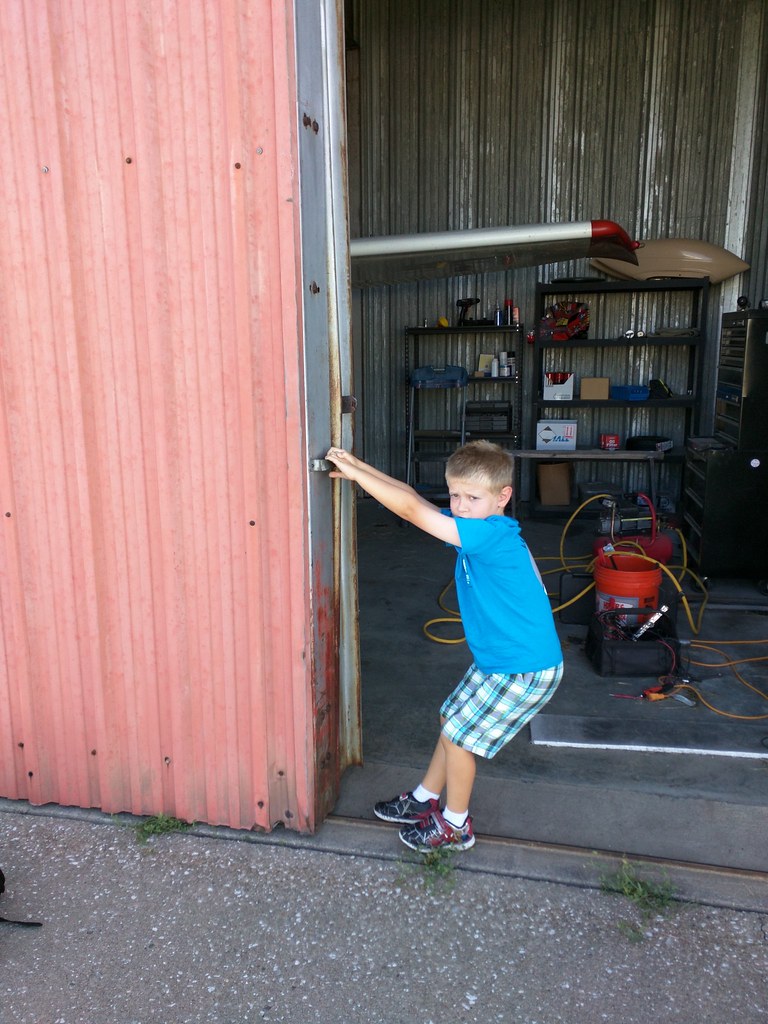
IMG_8515 This is morning. Time to fly. Two boys, happy to open the hangar door and get the plane ready. It s been a year since I passed the FAA exam and became a pilot. Memories like these are my favorite reminders why I did. It is such fun to see people s faces light up with the joy of flying a few thousand feet above ground, of the beauty and freedom and peace of the skies. I ve flown 14 different passengers in that time; almost every flight I ve taken has been with people, which I enjoy. I ve heard wow or beautiful so many times, and said it myself even more times. IMG_6083 I ve landed in two state parks, visited any number of wonderful small towns, seen historic sites and placid lakes, ascended magically over forests and plains. I ve landed at 31 airports in 10 states, flying over 13,000 miles. airports Not once have I encountered anyone other than friendly, kind, and outgoing. And why not? After all, we re working around magic flying carpet machines, right? IMG_7867_bw (That s my brother before a flight with me, by the way) Some weeks it is easy to be glum. This week has been that way for many, myself included. But then, whether you are in the air or on the ground, if you pay attention, you realize we still live in a beautiful world with many wonderful people. And, in fact, I got a reminder of that this week. Not long after the election, I got in a plane, pushed in the throttle, and started the takeoff roll down a runway in the midst of an Indiana forest. The skies were the best kind of clear blue, and pretty soon I lifted off and could see for miles. Off in the distance, I could see the last cottony remnants of the morning s fog, lying still in the valleys, surrounding the little farms and houses as if to give them a loving hug. Wow. Sometimes the flight is bumpy. Sometimes the weather doesn t cooperate, and it doesn t happen at all. Sometimes you can fly across four large states and it feels as smooth as glass the whole way. Whatever happens, at the end of the day, the magic flying carpet machine gets locked up again. We go home, rest our heads on our soft pillows, and if we so choose, remember the beauty we experienced that day. Really, this post is not about being a pilot. This post is a reminder to pay attention to all that is beautiful in this world. It surrounds us; the smell of pine trees in the forest, the delight in the faces of children, the gentle breeze in our hair, the kind word from a stranger, the very sunrise. I hope that more of us will pay attention to the moments of clear skies and wind at our back. Even at those moments when we pull the hangar door shut. IMG_20160716_093627

Lucy Wayland: Diversity and Inclusion, Debian Redux

So, today at Cambridge MiniDebConf, I was scheduled to do a Birds of a Feather (BoF) about Diversity and Inclusion within Debian. I was expecting a handful of people in the breakout room. Instead it was a full blown workshop in the lecture theatre with me nominally facilitating. It went far, far better than I hoped (although a couple of other and myself people had to wrench us back on topic a few times).
There were lots of good ideas, and productive friendly debate (although we were pretty much all coming from the same ball park). There are three points I have taken away from it (others may have different views):
  1. We are damned good at Inclusion, but have a long way to go on the Diversity (which is a problem of the entire tech sector).
  2. Debian is a social project as well as a technical one our immediately accessible documentation does not reflect this.
  3. We are currently too reactive and passive when it comes to social issues and getting people involved. It is essential that we become more proactive.
Combined with the recent Diversity drive from Debconf 2016, I really believe we can do this. Thank-you all you who attended, contributed, and approached me afterwards. Edit: Video here Debian Diversity and Inclusion Workshop Edit Edit: video link fixed.

Andrew Cater: Debian MiniConf ARM Cambridge - post 5

Daniel Pocock finally getting Jitsi to work - us talking to Berkeley, CA.

He's just given a talk on OpenPGP / Clean Room ISO creation for creating keys / CA certs appropriately offline and keeping everything secure.

It's been a good day, but I'm feeling pretty bushed :)

Andrew Cater: Debian MiniConf ARM Cambridge 12/11/16 - Post 4

Now Daniel Pocock on RTC. Again, a few technical issues :(

Big thanks to the video folks who have been working hard: they couldn't get into this room until 1800 last night and spent until about 2000 fixing the cameras etc. They must be shattered.

Thanks for front desk: who also pointed out that the security staff in over the weekend are also volunteers.

Andrew Cater: MiniDebconf ARM 12/11/12 - post 3

A crazy presentation on amateur radio and dongles for SDR for which I was at least partially responsible which may well have inspired others and piqued their interest - but, if nothing else, it was a lot of fun.

KiwiSDR - there should be anything up to 200 deployed in the end worldwide - look for them on sdr.hu - all done on top of a Beaglebone running Debian.
Four users independently tuning the receiver from 0-30MHz
Lunch was sandwiches in the kitchen - much hilarity as the door appeared locked, folk were shut outside - and the door was open all the time.

A presentation / group discussion on diversity and on ways that we can improve the understanding of Debian

Wouter Verhelst: New Toy: Nikon D7200

Last month, I was abroad with my trusty old camera, but without its SD cards. Since the old camera has an SD only slot, which does not accept SDHC (let alone SDXC) cards, I cannot use it with cards larger than 2GiB. Today, such cards are not being manufactured anymore. So, I found myself with a few options:
  1. Forget about the camera, just don't take any photos. Given the nature of the trip, I did not fancy this option.
  2. Go on eBay or some such, and find a second-hand 2GiB card.
  3. Find a local shop, and buy a new camera body.
While option 2 would have worked, the lack of certain features on my old camera had meant that I'd been wanting to buy a new camera body for a while, but it just hadn't happened yet; so I decided to go with option 3. The Nikon D7200 is the latest model in the Nikon D7xxx series of cameras, a DX-format ("APS-C") camera that is still fairly advanced. Slightly cheaper than the D610, the cheapest full-frame Nikon camera (which I considered for a moment until I realized that two of my three lenses are DX-only lenses), it is packed with a similar amount of features. It can shoot photos at shutter speeds of 1/8000th of a second (twice as fast as my old camera), and its sensor can be set to ISO speeds of up to 102400 (64 times as much as the old one) -- although for the two modes beyond 25600, the sensor is switched to black-and-white only, since the amount of color available in such lighting conditions is very very low already. A camera which is not only ten years more recent than the older one, but also is targeted at a more advanced user profile, took some getting used to at first. For instance, it took a few days until I had tamed the camera's autofocus system, which is much more advanced than the older one, so that it would focus on the things I wanted it to focus on, rather than just whatever object happens to be closest. The camera shoots photos at up to twice the resolution in both dimensions (which combines to it having four times the amount of megapixels as the old body), which is not something I'm unhappy about. Also, it does turn out that a DX camera with a 24 megapixel sensor ends up taking photos with a digital resolution that is much higher than the optical resolution of my lenses, so I don't think more than 24 megapixels is going to be all that useful. The builtin WiFi and NFC communication options are a nice touch, allowing me to use Nikon's app to take photos remotely, and see what's going through the lens while doing so. Additionally, the time-lapse functionality is something I've used already, and which I'm sure I'll be using again in the future. The new camera is definitely a huge step forward from the old one, and while the price over there was a few hundred euros higher than it would have been here, I don't regret buying the new camera. The result is nice, too: DSC_1012 All in all, I'm definitely happy with it.

11 November 2016

Jonathan Dowland: Vinyl is killing Vinyl (but that's ok)

I started buying vinyl records about 16 years ago, but recently I've become a bit uncomfortable being identified as a "vinyl lover". The market is ascendant, with vinyl album sales growing for 8 consecutive years, at least in the UK. So why am I uncomfortable about it? A quick word about audio fidelity/quality here. I don't subscribe to the school of thought that audio on vinyl is inherently better than digital audio, far from it. I'm aware of its limitations. For recordings that I love, I try to seek out the best quality version available, which is almost always digital. Some believe that vinyl is immune to the "loudness war" brickwall mastering plaguing some modern releases, but for some of the worst offenders (Depeche Mode's Playing The Angel; Red Hot Chili Pepper's Californication) I haven't found the vinyl masterings to sound any different. 16 years ago Let's go back to why I started buying vinyl. Back when I started, the world was a very different place to what it is today. You could not buy most music in a digital form: it was 3 more years before the iTunes Store was opened, and it was Mac-only at first, and the music it sold was DRM-crippled for the first 5 or so years afterwards. The iPod had not been invented yet and there was no real market for personal music players. Minidiscs were still around, but Net-MD (the only sanctioned way to get digital music onto them from a computer) was terrible.
old-ish LPs old-ish LPs
Buying vinyl 16 years ago was a way to access music that was otherwise much harder to reach. There were still plenty of albums, originally recorded and released before CDs, which either had not been re-issued digitally at all, or had been done so early, and badly. Since vinyl was not fashionable, the second hand market was pretty cheap. I bought quite a lot of stuff for pennies at markets and car boot sales. Some music such as b-sides and 12" mixes and other mixes prepared especially for the format remains unavailable and uncollected on CD. (I'm a big fan of the B-side culture that existed prior to CDs. I might write more about that one day.) 10 years ago
modern-ish 7 inches modern-ish 7 inches
Fast forward to around 10 years ago. Ephemeral digital music is now much more common, the iPod and PMPs are well established. High-street music stores start to close down, including large chains like MOS, Our Price, and Virgin. Streaming hasn't particularly taken off yet, attempts to set up digital radio stations are fought by the large copyright owners. Vinyl is still not particularly fashionable, but it is still being produced, in particular for singles for up-and-coming bands in 7" format. You can buy a 7" single for between 1 and 4, getting the b-side with it. The b-side is often exclusive to the 7" release as an incentive to collectors. I was very prepared to punt 1-2 on a single from a group I was not particularly familiar with just to see what they were like. I discovered quite a lot of artists this way. One of the songs we played at our wedding was such an exclusive: a recording of the Zutons' covering Jackie Wilson's "Higher and Higher", originally broadcast once on Colin Murray's Evening Session radio show. Now
Vangelis - Blade Runner OST An indulgence
So, where are we now? Vinyl album sales are a huge growth market. They are very fashionable. Many purchasers are younger people who are new to the format; it's believed many don't have the means to play the music on the discs. Many (most?) albums are now issued as 12" vinyl in parallel with digital releases. These are usually exactly the same product (track listing, mixes, etc.) and usually priced at exactly twice that of the CD (with digital prices normally a fraction under that). The second hand market for 12" albums has inflated enormously. Gone are the bargains that could be had, a typical second hand LP is now priced quite close to the digital price for a popular/common album in most places. The popularity of vinyl has caused a huge inflation in the price of most 7" singles, which average somewhere between 8- 10 each, often without any b-side whatsoever. The good news is from my observations the 2nd hand market for 7" singles hasn't been affected quite as much. I guess they are not as desirable to buyers. The less said about Record Store Day, the better. So, that's all quite frustrating. But most of the reasons I used to buy vinyl have gone away anyway. Many of the rushed-to-market CD masterings have been reworked and reissued, correcting the earlier problems. B-side compilations are much more common so there are far fewer obscure tracks or mixes, and when the transfer has been done right, you're getting those previously-obscure tracks in a much higher quality. Several businesses exist to sell 2nd hand CDs for rock bottom prices, so it's still possible to get popular music very cheaply. The next thing to worry about is probably streaming services.

Chris Lamb: Awarded Core Infrastructure Initiative grant for Reproducible Builds

I'm delighted to announce that I have been awarded a grant from the Core Infrastructure Initiative (CII) to fund my previously-voluntary work on Reproducible Builds. Whilst anyone can inspect the source code of free software for malicious flaws, most software is distributed pre-compiled to end users. The motivation behind the Reproducible Builds effort is to permit verification that no flaws have been introduced either maliciously or accidentally during this compilation process by promising identical results are always generated from a given source, thus allowing multiple third-parties to come to a consensus on whether a build was compromised. I'd like to sincerely thank the CII, not only for their material support but also for their recognition of my existing contributions. I am looking forward to working with my co-grantees towards fulfilling our shared goal. You can read the CII's press release here.

10 November 2016

Andrew Cater: Debian Miniconf ARM, Cambridge 10/11/16 - Post 4

As we left at about 1740, Wookey was still working on the Cubietruck I'd left him with but had made progress.

Dispersed to various pubs and eateries: we all ended up talking a great deal, much as last year. Tsk, tsk - you hardly see people for 20 years then you see the same people twice in two years :)

Though I didn't see that much of them through the day, thanks to Jo, Lucy and all who kept front desk running as ever and thanks to all the various ARM staff who were helpful with opening doors for the visitors and all the little things around administration - wifi access, badges and all that goes with hosting.

And why, O why, did I not notice that I'd subconsciously typed 10/11/12 not once but three times

Matthew Garrett: Tor, TPMs and service integrity attestation

One of the most powerful (and most scary) features of TPM-based measured boot is the ability for remote systems to request that clients attest to their boot state, allowing the remote system to determine whether the client has booted in the correct state. This involves each component in the boot process writing a hash of the next component into the TPM and logging it. When attestation is requested, the remote site gives the client a nonce and asks for an attestation, the client OS passes the nonce to the TPM and asks it to provide a signed copy of the hashes and the nonce and sends them (and the log) to the remote site. The remoteW site then replays the log to ensure it matches the signed hash values, and can examine the log to determine whether the system is trustworthy (whatever trustworthy means in this context).

When this was first proposed people were (justifiably!) scared that remote services would start refusing to work for users who weren't running (for instance) an approved version of Windows with a verifiable DRM stack. Various practical matters made this impossible. The first was that, until fairly recently, there was no way to demonstrate that the key used to sign the hashes actually came from a TPM[1], so anyone could simply generate a set of valid hashes, sign them with a random key and provide that. The second is that even if you have a signature from a TPM, you have no way of proving that it's from the TPM that the client booted with (you can MITM the request and either pass it to a client that did boot the appropriate OS or to an external TPM that you've plugged into your system after boot and then programmed appropriately). The third is that, well, systems and configurations vary so much that outside very controlled circumstances it's impossible to know what a "legitimate" set of hashes even is.

As a result, so far remote attestation has tended to be restricted to internal deployments. Some enterprises use it as part of their VPN login process, and we've been working on it at CoreOS to enable Kubernetes clusters to verify that workers are in a trustworthy state before running jobs on them. While useful, this isn't terribly exciting for most people. Can we do better?

Remote attestation has generally been thought of in terms of remote systems requiring that clients attest. But there's nothing that requires things to be done in that direction. There's nothing stopping clients from being able to request that a server attest to its state, allowing clients to make informed decisions about whether they should provide confidential data. But the problems that apply to clients apply equally well to servers. Let's work through them in reverse order.We have no idea what expected "good" values areYes, and this is a problem. CoreOS ships with an expected set of good values, and we had general agreement at the Linux Plumbers Conference that other distributions would start looking at what it would take to do the same. But how do we know that those values are themselves trustworthy? In an ideal world this would involve reproducible builds, allowing anybody to grab the source code for the OS, build it locally and verify that they have the same hashes.

Ok. So we're able to verify that the booted OS was good. But how about the services? The rkt container runtime supports measuring each container into the TPM, which means we can verify which container images were started. If container images are also built in such a way that they're reproducible, users can grab the source code, rebuild the container locally and again verify that it has the same hashes. Users can then be sure that the remote site is running the code they're looking at.

Or can they? Not really - a general purpose OS has all kinds of ways to inject code into containers, so an admin could simply replace the binaries inside the container after it's been measured, or ptrace() the server, or modify rkt so it generates correct measurements regardless of the image or, well, there's lots they could do. So a general purpose OS is probably a bad idea here. Instead, let's imagine an immutable OS that does nothing other than bring up networking and then reads a config file that tells it which container images to download and run. This reduces the amount of code that needs to support reproducible builds, making it easier for a client to verify that the source corresponds to the code the remote system is actually running.

Is this sufficient? Eh sadly no. Even if we know the valid values for the entire OS and every container, we don't know the legitimate values for the system firmware. Any modified firmware could tamper with the rest of the trust chain, making it possible for you to get valid OS values even if the OS has been subverted. This isn't a solved problem yet, and really requires hardware vendor support. Let's handwave this for now, or assert that we'll have some sidechannel for distributing valid firmware values.Avoiding TPM MITMingThis one's more interesting. If I ask the server to attest to its state, it can simply pass that through to a TPM running on another system that's running a trusted stack and happily serve me content from a compromised stack. Suboptimal. We need some way to tie the TPM identity and the service identity to each other.

Thankfully, we have one. Tor supports running services in the .onion TLD. The key used to identify the service to the Tor network is also used to create the "hostname" of the system. I wrote a pretty hacky implementation that generates that key on the TPM, tying the service identity to the TPM. You can ask the TPM to prove that it generated a key, and that allows you to tie both the key used to run the Tor service and the key used to sign the attestation hashes to the same TPM. You now know that the attestation values came from the same system that's running the service, and that means you know the TPM hasn't been MITMed.How do you know it's a TPM at all?This is much easier. See [1].


There's still various problems around this, including the fact that we don't have this immutable minimal container OS, that we don't have the infrastructure to ensure that container builds are reproducible, that we don't have any known good firmware values and that we don't have a mechanism for allowing a user to perform any of this validation. But these are all solvable, and it seems like an interesting project.

"Interesting" isn't necessarily the right metric, though. "Useful" is. And I think this is very useful. If I'm about to upload documents to a SecureDrop instance, it seems pretty important that I be able to verify that it is a SecureDrop instance rather than something pretending to be one. This gives us a mechanism.

The next few years seem likely to raise interest in ensuring that people have secure mechanisms to communicate. I'm not emotionally invested in this one, but if people have better ideas about how to solve this problem then this seems like a good time to talk about them.

[1] More modern TPMs have a certificate that chains from the TPM's root key back to the TPM manufacturer, so as long as you trust the TPM manufacturer to have kept control of that you can prove that the signature came from a real TPM

comment count unavailable comments

Next.

Previous.