Search Results: "Martin"

9 September 2008

Martin Michlmayr: More robust oldsys-preseed uploaded

To follow-up on my recent posting about oldsys-preseed: I uploaded a new version of netcfg yesterday that can be told via preseeding not to use a gateway. I also uploaded a new version of oldsys-preseed that will properly handle static IP configs without a netmask or gateway. Additionally, oldsys-preseed will now use DHCP when the static IP config is incomplete (i.e. when either the IP address or DNS are missing). This makes oldsys-preseed much more robust and will hopefully get rid of many problems users ran into with etch.

Martin F. Krafft: A mail header field to specify action deadlines

While drafting emails to be sent out as part of my research, I just had an idea about a new mail header field, let s call it X-Respond-By. This header field allows the sender to specify when s/he requests/requires/needs a response. The recipient could make use of this in multiple ways: Obviously, care would have to be taken to prevent abuse, e.g. by some senders who make all their messages require responses on the next day. One way to achieve this would be to give the recipient sender-specific policies to ignore the field, extend it by a fixed period, or simply reject messages with the field set. I already use a tickler system (which works locally as well as remotely) inspired by the GTD concept of a tickler file, which allows me to have email messages delayed to a given point in the future. I could very well imagine how such an approach could extend into a cooperative communication method. I am looking forward to your comments. Update: Jan Hudec wrote in to tell me about the Reply-By field used by Outlook, which sends messages with those headers:
X-Message-Flag: Follow up
Reply-By: Wed, 10 Sep 2008 12:00:00 +0200

According to Jan, this will
will mark the message with specific symbol,and at the time specified it will pop up a notification in the same way as it does for calendar events and after that it will show the mail in red in the index until it s marked completed .
He also notes that Reply-By stems from X.400 via RFC 2156 and has indeed been standardised by RFC 4021. I shall investigate this further when I have time. NP: Foo Fighters: Echos, Silence, Patience & Grace

8 September 2008

Martin F. Krafft: Tennis discrimination

Congratulations once again to Roger Federer, who didn t leave a doubt that he is a Great Player. Andy Murray, I tip my hat to you! You are someone to watch for: great ball control and you just hit it, as opposed to some other players slicing their way through the games. Keep it coming, I expect to see you more in the future! I was very pissed off by usopen.org and CBS sports, for their streaming was limited to US and territories . Since Eurosport and the like didn t get live coverage, I am assuming that there was shitloads of money involved (the US Open Finals, go figure ). Well, dear CBS and US Open folks, if you pocket shitloads of money, consider spending that tiny bit of a fraction in the future to make your international viewers happy. I assume you know that there s life outside of your country. Thanks to justin.tv for hooking me up with a stream that allowed me to follow, even though it was suboptimal. I wish I had been able to see this on a TV. Since we don t have one, and Irish pubs kick you out at half eleven, it was still the best option I had.

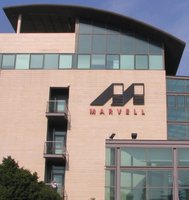
Martin Michlmayr: Visiting Marvell in Yoqne'am

Marvell in Yoqne'am Since I'm spending the summer in Israel, I used the opportunity yesterday to visit the Marvell site in Yoqne'am where the majority of the NAS software engineering team is located. They first gave me a tour through the hardware labs which I found incredibly interesting. It's amazing what equipment those folks use to perform QA tests of new chips, how they can reverse engineer chips and even make some modifications to test their theories about hardware bugs. I found it really amazing and at the same time felt glad that changing things in software is so easy. Later they showed me the software lab where they had an exhibition of various devices based on the Orion chip, including NAS devices, but also printers, wifi APs and game machines. They also told me some details of their product roadmap but unfortunately I cannot share that information. The only thing I can say is that we'll see a lot of new devices to which it would be cool to port Debian.

Ross Burton: Sound Juicer "Stab Stab Stab! This Is More Than A Message" 2.23.3

Sound Juicer "Stab Stab Stab! This Is More Than A Message" 2.23.3 has been released. Tarballs are available on burtonini.com, or from the GNOME FTP servers.

7 September 2008

Kyle McMartin: CONFIG_PRINTK_TIME, what is time?

GMsoft reported a few weeks ago, that kernels on his A500 were hanging on startup with CONFIG_PRINTK_TIME enabled. Knowing that all this does is prefix the kernel messages with a timestamp, I was interested to find out how this could possibly be causing a hard hang. Obviously, the first thing to do, is to try and reproduce the problem. But I was completely unable to reproduce it on my RP3440… How very strange. Ok, well, let’s poke at the A500 and see if it will happen there. It does! Spooky…[1] Well, now I was really interested. Let’s see what CONFIG_PRINTK_TIME actually does… In kernel/printk.c::vprintk, around the if (printk_time) section, we see that after printing the priority level tag, such as KERN_INFO, etc., we attempt to print a timestamp obtained with cpu_clock. The returned value from cpu_clock is in nanoseconds, so before it’s printed, it is munged into two smaller integers, the whole-seconds portion, and the decimal portion. Ok, this gives us a great place to start looking for ways PA-RISC could be tripping up on these codepaths. The first was a fairly fruitless search of the cpu_clock call chain, which turned up nothing suspicious, aside from a maze of CONFIG_ options. Turned out, on non-x86, this code reduced into some fairly trivial stuff, none of which could really have been causing a hang. However, we now had a basis for a fairly good hunch. If it wasn’t the cpu_clock going awry, the do_div routine, or sprintf must have been causing it. A quick boot-test to comment out the do_div routine and replace it will a fixed value resulted in a working system. Hooray. Then it hit me like a freight train, when I saw what was being printed. This was the banner line… the very first thing printed in init/main.c, right after jumping into the kernel in virtual mode at start_kernel.
Linux version 2.6.27-rc5-00283-g70bb089 (kyle@shortfin) (gcc version 4.3.1 (GCC) ) #2 SMP Sat Sep 6 19:45:05 PDT 2008
FP[0] enabled: Rev 1 Model 20
The 64-bit Kernel has started…
console [ttyB0] enabled
Initialized PDC Console for debugging.
Seeing the “FP[0] enabled” line immediately caused me to smack my head at the obviousness of the problem. We were attempting to do a division, which, because of how the kernel and libgcc are compiled, is attempting to use the fpu. However, this is faulting on the very first printk in the kernel, well before any of the architecture-specific initialization is done. A quick hack removing any printks before we initialized the fpu fixed the problem as well. But, dirty hacks are not appropriate for mainline. I thought long and hard about a nice way to fix this, but, really, open coding firmware calls in assembly didn’t strike my fancy. There is, however, another easy way to solve it. I ended up replacing the jump to start_kernel in head.S with my own function to turn on the fpu, and called start_kernel from there. Kind of ugly, but at least the fix is entirely contained to arch/parisc, instead of leaking all over the tree. The patch is available, but I’ve been too busy to push it this last release-cycle (and, didn’t really want to tempt fate at pushing a not-quite-actually-serious-fix outside of -rc1 time.) This has been another post brought to you by the maintainer of an inconsequential architecture. We do hope you enjoy it. 1. This ended up being due to either 1) the fpu being enabled by firmware on the PA8800, or 2) the fact that I was doing warm resets instead of cold starts.

5 September 2008

Martin F. Krafft: Swamp airports with trash

I am surely not the only one to complain about the ridiculous liquids restrictions for airplane travel. Since these new regulation are in place, I ve challenged them, found holes, and compiled tips for those trying to blow up planes. I wouldn t write another story if it weren t for an idea I ve had at Zurich airport on my last trip to London: let s swamp the airports with trash so that they ll be forced to deal with Brussels and IATA to return to normal. After checking in for my flight, I stopped by the supermarket to buy two containers of yoghurt that would make someone happy. The containers each said 150g (that s weight, not volume) on them, and I put them into a clear, resealable one-litre bag, placed them into a tray to be x-ray-scanned separately, only to have them confiscated. After discovering (not much to my surprise) that the security staff didn t know the difference between weight and volume, nor understood the concept of density, I got a chance to speak to the head security officer (surrounded by five police whose attention I d gotten), and learnt that Zurich airport has one ton of trash to discard every day, Frankfurt supposedly has to deal with four. As I was walking onto my plane, I tried to think of non-recyclable containers that we could fill with liquids to bring along to increase that amount. My theory was that once the trash problem became too massive, the airports would have to deal with the authorities to resolve this liquid restriction, because it seems quite clear that normal people have no way to influence choices made that affect our safety . Unfortunately, I see two problems: First, we d be dealing with trash and hence face all the environmental concerns. The airports do not recycle the millions of PET bottles they confiscate every day, so we shouldn t make that worse. Unfortunately, I cannot think of another liquid container that wouldn t come with similar concerns. Second, the airports might have the burden, but they won t carry the cost of all the trash. In fact, thanks to the security theatre related to liquids, we already pay higher airport taxes and charges. Surely it can t be in our interest to push that further up the scale. So in the end, swamping airports with trash doesn t seem like a viable way forward, unfortunately. I wish I knew what to do. I wish that the decision makers at IATA would finally admit that they overreacted and revert to normal, with sensible security measures, which focus on fending off the real threats, not fake ones. Unfortunately, nobody likes to admit that they were wrong, especially not when the decision is heavily backed up by the lobby of vending machine companies and restaurant owners, who benefit greatly from these ridiculous liquid safety measures. NP: Pulp: We Love Life

4 September 2008

Christian Perrier: What about translations other than German and French?

I recently announced that German and French reached 100% completion in unstable for po-debconf translations (by the way, both are now 100% in lenny as well). However, l10n efforts also happen for many languages in that area, so it's time to highlight them as well: Other translation efforts are more hectic. I'd like to point the slow decrease of the work on Catalan, probably due to low manpower and other areas of interest for the old timers. I'll try to soon make such report for other areas of translation effort in Debian.

Martin Michlmayr: The European Open Source Observatory and Repository (OSOR)

I attended the Open Nordic Conference in Norway in June, a conference that brought together people from Norway, Sweden, Finland and Denmark. Attending the conference allowed me to find out what's going on with FOSS in Northern Europe. What I found interesting is that there was a lot of talk about using FOSS in the public sector. A number of countries are working on repositories to exchange software, in particular for public administration. One example is the Software Exchange (softwareborsen.dk), a project by the Danish National Software Knowledge Centre to promote the use of FOSS in Danish public administration. The Norwegian software exchange (delingsbazaren.no) plays a similar role in Norway. It seems as if every country is working on their own software repository to share FOSS. As such, it's great to see that the European Commission is taking a step towards bringing everyone together by introducing the Open Source Observatory and Repository (OSOR) for European public administrations. The goal of OSOR is to provide a platform for the exchange of information, experiences and FOSS code for the use in public administrations. OSOR will officially launch at the Open Source World Conference in Malaga in October. I've always thought that there is not enough cooperation and communication between European countries, so I have high hopes for OSOR. (Originally published on FOSSBazaar)

Martin F. Krafft: New Zealand terrorism

Penny keeps me updated on New Zealand terrorism and it s depressing to hear about it: 18 people detained and tried as terrorists for peace activism, protesting against environmental issues, and fighting for M ori rights. I d like to help spread the word and hope that avaaz.org picks up this issue soon! If you would, please pass this on. NP: Stars: Set Yourself on Fire

3 September 2008

Martin Michlmayr: Starting to test GCC 4.4

I've been too busy to follow GCC development recently and haven't done any testing of development snapshots during the GCC 4.4 development phase so far. However, GCC 4.4 moved to stage 3 yesterday, the development stage dedicated to bug fixes and documentation. Given that GCC is now in stage 3 and that Debian unstable has fairly little churn because of the freeze, it's an ideal time to do some archive rebuilds. I started archive rebuilds on amd64 and powerpc last night and added ia64 today. I also tried to build GCC on armel, alpha and sparc but there are compiler errors during bootstrap. mips builds fine but I haven't started any archive rebuilds. I found and reported 9 compiler errors so far. Most of them have already received some attention and one of them has been fixed in the meantime. I'm not looking at build failures of packages at the moment since that's very time consuming and I'm not sure whether I'll find the time to report build failures later as GCC becomes more stable, but we'll see.

Martin-Éric Racine: another Tux bites the dust

At the dayjob, we've been evaluating various OS options for a customer project. Without going into details, it involves installing embedded software on a ThinCan for a special usage case. The basic needs are simple: graphic environment to run a custom application (OS neutral), plus a few drivers for hardware attached to the ThinCan. That's it. Nothing to excited about. Comparing various team members' proposals to implement the OS base was the real shocker: no matter how optimized the software base and compiler options, no matter which build environment was used (Thin Station, Open Embedded, Gentoo, etc.), we couldn't get a performance that was remotely usable: Then came the proposal from our team's lone Windows guy: XP Embedded. Booted in less than 10 seconds, has a graphical environment that is usable out of the box and integrating the customer's application was a breeze. Heck, the demo is practically a finished product already and took just a couple of hours to assemble! To make matters worse, the total we'd be paying in licensing fees, for all the Windows components we choose, would amount to far less than what it would cost to polish either of the Free Software -based proposals. Before anyone goes and puts on their asbestos suit, I'm already aware that the point of Free Software is to keep people employed and to make the community at large benefit from everyone's code improvements by contributing patches to upstream. Please keep in mind that, in contrast, business requirements are to get results at a reasonable cost, reasonably fast and to produce a well-polished product. The Free Software community has finally conquered the challenges of the desktop and was already on the server ages ago, but we ain't quite there yet on embedded devices, I'm afraid. While I personally refuse to run anything else than Ubuntu on my laptop, let's face it, in the above case, the savings in time=money were obvious and the resulting product quality, even at demo stage, spoke for itself. Thus, another Tux bit the dust.

2 September 2008

Russell Coker: Google Chrome - the Security Implications

Google have announced a new web browser - Chrome [1]. It is not available for download yet, currently there is only a comic book explaining how it will work [2]. The comic is of very high quality and will help in teaching novices about how computers work. I think it would be good if we had a set of comics that explained all the aspects of how computers work. One noteworthy feature is the process model of Chrome. Most browsers seem to aim to have all tabs and windows in the same process which means that they can all crash together. Chrome has a separate process for each tab so when a web site is a resource hog it will be apparent which tab is causing the performance problem. Also when you navigate from site A to site B they will apparently execute a new process (this will make the back-arrow a little more complex to implement). A stated aim of the process model is to execute a new process for each site to clear out the memory address space. This is similar to the design feature of SE Linux where a process execution is needed to change security context so that a clean address space is provided (preventing leaks of confidential data and attacks on process integrity). The use of multiple processes in Chrome is just begging to have SE Linux support added. Having tabs opened with different security contexts based on the contents of the site in question and also having multiple stores of cookie data and password caches labeled with different contexts is an obvious development. Without having seen the code I can’t guess at how difficult it will be to implement such features. But I hope that when a clean code base is provided by a group of good programmers (Google has hired some really good people) then the result would be a program that is extensible. They describe Chrome as having a sandbox based security model (as opposed to the Vista modem which is based on the Biba Integrity Model [3]). It’s yet to be determined whether Chrome will live up to the hype (although I think that Google has a good record of delivering what they promise). But even if Chrome isn’t as good as I hope, they have set new expectations of browser features and facilities that will drive the market. Update: Chrome is now released [4]! Thanks to Martin for pointing out that I had misread the security section. It’s Vista not Chrome that has the three-level Biba implementation.

Martin F. Krafft: Dear Firefox, you are unique

You are so unique! No other programme I know can suck up memory at such a steep rate as you. And not only that, you also keep it safe and secure, making sure never to release it. You re awesome! I wish there would be more like you. NOT. Update: sorry, Firefox, you re about to be degraded! NP: 65daysofstatic: The Destruction of Small Ideas

Martin F. Krafft: Does silence kill kids?

When Graham Bell invented the telephone in 1876, he probably didn t expect the rise of the cellphones we ve been seeing over the last 20 years. At first, there were C-net phone too huge to carry, but mobile still, as they communicated wireless. Then, devices became smaller, networks faster and ubiquitous, and today, the number of cellphones sold worldwide has exceeded the population. Much like everything else, it used to be better back then . When phone calls were still ridiculously expensive, people were able to enjoy their peace and life progressed slow for everyone to think enough, not do or say without engaging their brains. Then, when the first cellphones stuffed people s pockets, they did their job pretty much from the start: you could make phone calls. Some genius discovered SMS as a splendid tool to rip off customers, so phones grew pager abilities, but other than that, they just worked; I remember my first phone, which didn t break in years. Obviously, if you re a phone manufacturer, you don t like that, because once you sell a phone that works, the customer won t come back to give more monies in ten years. Clever as you are, you devised two schemes to ensure your cash flow: make phones more brittle and crap, so that they break within a year, at most two; and drag ever younger people into the debt trap. For the truly stupid, sites and services offer ring tones and games and what not, and the lesser challenged you keep close by the continuous addition of new features that noone needs. So these days, almost every phone can play music files, which is mighty convenient to spice up your work commute with some tunes, but our youngsters are overburdened by that, it seems. I almost soiled myself laughing at a group of five Italians at Ezeiza Airport in Buenos Aires, who were sitting around waiting for a bus, every one of them ear plugged and grooving to the beats (you know how dorky it looks when people silently sing along rap songs?). That s not the funny part. The funny part is that every minute, one of them would say something, which would cause the others to unplug one ear, and form their lips to bleat what (making sure to add just a little bit extra of the tone of general disinterest, which is cool ). This elicited one of two responses: either the original speaker would say oh, nothing and everyone nodded, or he d repeat his wisdom, causing everyone to laugh and nod before in both cases they replugged and returned to luff themselves. I wonder how they made it to the airport themselves, and why they travel as a group. Worse than that, however, is that cellphone manufacturers remembered that their phones had speakers (for fancy ringtones) and consequently added the ability to blast tunes through them. As a result, groups of kiddies walk around or sit in trains, with one (or more) of those cellphones blaring into the environment. Apart from being generally inconsiderate, what I don t understand is how they put up with the sound quality. It s mostly hip-hop music you know that genre that makes some homies out there install 5000 watt subwoofers into their cars so make sure the windows rattle with the base but these phones have a frequency spectrum comparable in width to that of your grandfather s, way further up the scale (meaning they just don t do base). Playing hip-hop through those is like putting a flute concerto on a subwoofer, just worse, because high-pitch tones are harder to filter by those who don t want to hear them. And yet, I see it all over the place, kiddies listening to music through cellphone speakers. Is it because silence would kill them? NP: 65daysofstatic: The Fall of Math

1 September 2008

Ingo Juergensmann: Initramfs problems with RAID setup

Yesterday a server at work needed some care - which was the reason why I had to leave the m68k porters meeting early. It was intented to migrate the filesystem to a RAID1 setup instead of using just a single disk.

Of course I tested everything in advance and it worked. Sadly Murphy did hit the scene as well and the previously tested upgrade path failed: somehow the RAID couldn't be started and the boot progress stopped.

Actually, the error was this one:


Failure: failed to load Module 1 no such module


Useless to say that the initrd was uptodate and included all necessary modules!

Luckily someone else happened to stumble upon the same problem last year and it was well documented on debian-user mailing list in a thread between Andrew Sackville-West and Martin F. Krafft , properly archieved by some mirrors.

So, the problem was in some mdadm script that was executed during boot process and which parsed the ARRAY definition in that way that the kernel modules couldn't get loaded.
If you follow the thread on that mailing list you'll come to the following hint:


Try the following patch agaist
/usr/share/initramfs-tools/hooks/mdadm. It ensures that RAID levels
include the word 'raid'. I think your mdadm.conf may say stuff like
level=5, when it should say level=raid5 or not specify level= at
all.


And yes, my ARRAY definition in mdadm.conf just stated level=1 as well. So after setting it to level=raid1 everything worked again.

Thanks, Andrew and Martin for solving that problem a year ago! :-)

31 August 2008

Michael Schutte: Perhaps if I eliminate no, wait, this won t work

In today s episode of Tatort, a German-language TV series Martin blogged about some time ago, I had to laugh at this line:
You are a computer scientist, aren t you? What we ve got here is an equation with two variables. You certainly know that this easy to solve.
Interestingly, the same mistake can be found in an older episode of another German TV series called Der Bulle von T lz. A part of a dialogue between a detective and a teacher went like this:
Detective: Was she a good student?
Teacher: Not at all. She even cannot solve a simple equation with two variables.
Dear screenwriters, when in doubt, please stay away from maths. And while we re at it, there is no need for fingerprint matching software to show every fingerprint from the database on the screen and emit lots of short beeps while doing that. Your programmes are more enjoyable without this stuff. Update: As this post has triggered responses: First, I do not deny the overall quality of Tatort it is a great series. Second, of course there are systems of equations with more variables than equations which can be solved. But these aren t straightforward and certainly not what the people I m talking about had in mind

Martin Michlmayr: Cannot connect to debian-installer via SSH: mystery solved?

I finally found the time today to dig into oldsys-preseed and what I found wasn't pleasant. In fact, I may have solved the mystery why some people trying to install Debian on their NSLU2 cannot connect to the installer via SSH. oldsys-preseed is used on certain NAS devices to read the network configuration from the original firmware and these values are used to bring up SSH in debian-installer. If you used DHCP in the original firmware to obtain an IP address, debian-installer will do the same. If you have a static IP config, debian-installer will use it. In theory, it's all pretty simple, but users often run into troubles when a static IP config is used (as is the case on the NSLU2). While you only need an IP address, netmask and gateway to bring up SSH (and then you could configure the rest, such as DNS and hostname), debian-installer expects everything at the same time. I've seen many cases where users couldn't connect to the installer because they forgot to configure their DNS in the original firmware or some other values they didn't think were important. Anyway, right now oldsys-preseed will use a static configuration if the firmware is configured this way even if it's clear that netcfg won't like this configuration because of missing values. The IP address and DNS are always required, but the netmask and gateway can be figured out automatically. I wanted to add a sanity check that would choose DHCP in case the IP address or DNS were not specified. While working on this sanity check, I noticed two things: First, the "empty" value oldsys-preseed preseeds when there's no netmask or gateway is not accepted by netcfg and leads to an error message (which the user cannot see because SSH is not up yet). I'm pretty sure I tested this scenario when I wrote oldsys-preseed but it clearly doesn't work today and I don't see how it could ever have worked. This is pretty significant because having an empty gateway is a valid configuration (if hopefully not too common). Second, it seems that it's impossible to create a preseed file that tells netcfg that no gateway should be used. If you preseed an empty value, netcfg will simple use .1 as the gateway. I've fixed the first problem and proposed a patch to put in a special case to allow preseeding of no gateway. The sanity check that chooses DHCP when the network configuration is incomplete is also there now.

Martin Michlmayr: Please test daily debian-installer images

debian-installer is now using the 2.6.26 kernel (the version the kernel team wants to release lenny with) and 2.6.26 has moved to testing a few days ago. As such, it's a great time to test the daily installer images to make sure our installer for lenny is in a good state. There's still time to fix bugs in the installer, but we need your feedback. Daily images can be obtained from the debian-installer web site which also contains instructions about how to submit installation reports. I'm particularly interested in reports about installations on ARM and MIPS. If you want to test debian-installer on these architectures, please read my messages on debian-arm and debian-mips.

30 August 2008

Martin F. Krafft: Recovering a lost default route

Tired and under the influence of beer, I tried to remove the currently broken IPv6 default route from my primary mailserver via an SSH connection and accidentally executed instead:
ip r d default
# I meant: ip -6 r d default

Unfortunately, I didn t immediately realise what I had done, and then it was too late. Robert Collins told me that I could have saved the session because even without a default route, packets still reach the machine. Unfortunately, due to Nagle s algorithm, you pretty much only have one shot, so the next time this happens to me (or you), quickly type
ip r a default via <gateway>

into a separate window, then copy and paste it into the SSH session and you may get lucky. Update: one lesson I learnt from this is to add specific routes for at least the IPv6 tunnel peer, and possibly another machine (or two) under my control out there. I now have that in place on all machines I own. NP: The Phoenix Foundation: Pegasus

Next.

Previous.