Search Results: "ema"

27 July 2008

Romain Francoise: emacs-snapshot 20080727-1

After two weeks of well-deserved vacation and other delays, I'm back to doing regular updates of emacs-snapshot. Here's a quick summary of the notable changes in Emacs CVS since my last post:

26 July 2008

Matthew Garrett: Further Foxconn fun

Ryan kindly sent me a copy of the ACPI tables for his motherboard, so I've had the opportunity to look at them in a little more detail. There's nothing especially surprising. The first method of interest is OSFL, which I've annotated below:
   Method (OSFL, 0, NotSerialized)
     
        If (LNotEqual (OSVR, Ones))
         
            Return (OSVR)
         
This block simply skips the checks if they've already been evaluated and returns the cached value
        If (LEqual (PICM, Zero))
         
            Store (0xAC, DBG8)
         
If the programmable interrupt controller has been set up in PIC mode rather than APIC mode, 0xAC is written to i/o port 0x80. This would then show up on a plug-in card if one were attached. Simply debug code
        Store (One, OSVR)
Set OSVR to 1, which in this case clearly means "Unknown OS"
        If (CondRefOf (_OSI, Local1))
This checks whether the OS supports the _OSI method. If it does, the following block is executed. If not, the older _OS method is used to detect the OS
         
            If (_OSI ("Windows 2000"))
             
                Store (0x04, OSVR)
             
Newer versions of Windows will also claim to support the interfaces defined in older versions, so this set of checks is done in release order
            If (_OSI ("Windows 2001"))
             
                Store (Zero, OSVR)
             
            If (_OSI ("Windows 2001 SP1"))
             
                Store (Zero, OSVR)
             
            If (_OSI ("Windows 2001 SP2"))
             
                Store (Zero, OSVR)
             
            If (_OSI ("Windows 2001.1"))
             
                Store (Zero, OSVR)
             
            If (_OSI ("Windows 2001.1 SP1"))
             
                Store (Zero, OSVR)
             
            If (_OSI ("Windows 2006"))
             
                Store (Zero, OSVR)
             
If we've got this far, OSVR is now set to 0. Linux will claim to support all of these interfaces, and so OSVR should be 0 on Linux systems. Note that there is no _OSI check for Linux - the 2.6.24 change to remove Linux from the set of claimed interfaces is therefore irrelevant
         
        Else
         
Linux supports _OSI, so we should never be here. But if we somehow are...
            If (MCTH (_OS, "Microsoft Windows NT"))
             
                Store (0x04, OSVR)
             
Linux has responded to _OS with "Microsoft Windows NT" since 2.6.9. MCTH is simply a string matching routine defined elsewhere in the DSDT. So, worst case here is that OSVR is 4
            Else
             
                If (MCTH (_OS, "Microsoft WindowsME: Millennium Edition"))
                 
                    Store (0x02, OSVR)
                 
                If (MCTH (_OS, "Linux"))
                 
                    Store (0x03, OSVR)
                 
..because this could never be true unless you're running 2.6.8.1 or earlier. But even so, getting here would still indicate failure - we've supported _OSI since before then, and so should never come anywhere near this code block.
             
         
        Return (OSVR)
     
In summary, we end up with the following values:
ValueOS
0Windows XP, 2003 or Vista. Linux (assuming absence of bugs)
1Unknown OS
2Windows ME
3A version of Linux that doesn't implement _OSI and is from before 2.6.9
4Windows NT 4 and 2000. A version of Linux that doesn't implement _OSI and is 2.6.9 or later (I don't believe any such version exists

Now, where is this used? The majority of the OSFL checks only check whether the return value is 1 or 2, which will only be true for an OS that (a) doesn't claim to be Windows or (b) is Windows ME. Linux doesn't fall into either of these categories, so we can ignore them. The first interesting hit we have is in the HPET code, where _STA will return 0xf (device present and working) if OSFL is 0 and 0xb (device present and working, but should not be shown in the UI) otherwise. This is just to keep the HPET from showing up in versions of Windows that don't know what it is. The only other interesting hit is the following code from the PCI bus initialisation pathway:
 
                               If (LEqual (OSFL (), Zero))
                                 
                                    Store (0x59, SMIC)
                                 
                                Else
                                 
                                    If (LEqual (OSFL (), 0x04))
                                     
                                        Store (0x5A, SMIC)
                                     
                                    Else
                                     
                                        Store (0x58, SMIC)
                                     
                                 
This writes different values to SMIC (which turns out to be i/o port 0xb2) depending on the OS. 0xb2 is the standard(ish) way to trigger a system management interrupt, which causes the CPU to execute some code from a memory region that can't be accessed by the OS. This isn't that unusual, but it's a little weird. In any case, note that there's no check for whether OSFL is 3 here (which would be true if the _OS call returned Linux), and so Linux is being treated identically to Windows ME and any unknown OS. In reality, Linux will be treated identically to either Vista or 2000. This block provides no evidence of conspiracy. Finally, the OS version flag is written to a region of memory before suspend and read back afterwards. Nothing appears to be done with this information - it's conceivable that the low-level resume code in the BIOS has conditionals based on this, but I suspect that it's just boilerplate code that's ignored.

To summarise:What's the problem, then? I've no idea. The only "significant" issue is that the OEMB table provided by the BIOS has an incorrect checksum. Given that the OEMB table is never used by Linux (it's a vendor extension of some kind, with the best hint I've been able to find being that it can be used to pass information from the BIOS to the OS - kind of like the rest of ACPI, then...), this is pretty unimportant. And given that the OEMB table isn't part of the ACPI spec, it's certainly entirely irrelevant when it comes to determining whether the system is ACPI compliant or not.

Are there ACPI issues with Ryan's system? It sounds like it. The "Error attaching device data" complaints indicate some kind of failure on the part of the kernel to work out how the devices correspond to the ACPI namespace, but I strongly suspect that this is a Linux bug. Failure to reboot after suspend? Could be anything (I'd need direct access to the hardware to figure it out properly), but again it's almost certainly a Linux bug. The standard way Linux reboots systems is to bang the keyboard controller, and it's conceivable that something we're doing on resume is leaving the keyboard controller in a slightly confused state. We're clearly doing something wrong there, given that my Dell comes up without a keyboard about one resume in twenty - I just haven't had time to look into it yet.

The only remaining thing is the mutex handwaving. I've got no clue what's going on there. Ryan's suggested change (from Acquire (MUTE, 0x03E8) to Acquire (MUTE, 0xFFFF)) simply means that the OS will wait forever until it acquires the mutex - in the past it would only wait a second. The reason the compiler generates a warning here is that the firmware never checks whether it acquired the mutex or not! Bumping the timeout to infinity obviously fixes this warning (there's no need to check the return code if you're happy to wait forever rather than failing), but the original code is merely stupid as opposed to a spec violation.

Take home messages? There's no evidence whatsoever that the BIOS is deliberately targeting Linux. There's also no obvious spec violations, but some further investigation would be required to determine for sure whether the runtime errors are due to a Linux bug or a firmware bug. Ryan's modifications should result in precisely no reasonable functional change to the firmware (if it's ever hitting the mutex timeout, something has already gone horribly wrong), and if they do then it's because Linux isn't working as it's intended to. I can't find any way in which the code Foxconn are shipping is worse than any other typical vendor. This entire controversy is entirely unjustified.

Adam Rosi-Kessel: EOM Is Clever

I’ve used the TLA EOM occasionally, but never considered the full scope of its utility. Lifehacker just made me a full convert:
EOM means much more than End of Message. It means “good use of time.” It means “concise.” It means “clarity.” But GUOTCC doesn’t have the same ring as EOM, so let’s stick with it. Here are eight great reasons for you to adopt EOM while crafting your email messages. (1) EOM saves your recipient’s time. Don’t you value your time? Isn’t it nice when others value your time too? By keeping your subject line short and using EOM you are showing the people you send to you value their time. They’ll thank you for it (when they know what it means). … (8) EOM guarantees 100% readership We’ve all had the frustrating experience of waiting on someone to read our important email and respond. Sometimes we wait a long time and follow up to find out they haven’t even read the message at all. Perhaps the most powerful advantage of EOM is 100% readership. Why? Because your entire message is in the subject line. Your message becomes impossible to ignore because it comes in front and center no need to double click.
In a job where I receive between 300-1000 emails on most weekdays, every little bit helps. The main drawback of excessive EOM’ing may be that it breaks threading for some mail readers, and may be incompatible with other email conventions. Technorati Tags: , , ,

25 July 2008

Jordi Mallach: Cinema de Barri in Benimaclet

Last summer we tried to organise a Cinema d'estiu movie projections in Benimaclet's Church Square, in an attempt to promote social activities in the street done by the neighbours, for the neighbours. The response was very positive, and the first two projections attracted many people, who would bring a chair and their dinner to the old town's square to watch a movie. Unfortunately, the authorities, who were completely out of the loop, weren't happy and on the 3rd week the Local police appeared and said that that kind of activities needed official permits, and disallowed the projection. For this year's summer, we decided we'd try to do the projections once again, and learned that only a legally-established organisation can do the paperwork to get an authorisation. In parallel, some neighbours of Benimaclet, who had liked last year's idea, were working on their own to repeat the experience, and somehow Clara was contacted by them, and we ended up collaborating. As these people are members of the Associaci de ve ns of Benimaclet, there were legally able to do the paperwork, and soon we agreed on the four movies for this year, to be played every Sunday of July at 22:00h. Our pick for Sunday 6th was Giuseppe Tornatore's Cinema Paradiso, followed on the 13th by Elling, a Norwegian comical drama by Petter N ss which I hadn't seen and I can totally recommend. Last week we saw Poniente, a Spanish film by Chus Guti rrez that focus on immigration issues in the South East of Spain, based on the racist happenings of El Ejido of 2000. Finally, next Sunday is the turn for some political action with V for Vendetta. A note for Benimaclet neighbours: if you don't come to see the movie, be aware that we plan to pump up the volume a lot for this one. You're definitely going to hear it from home. ;) We're very happy about the response of the neighbours this year. Not having done any effort to announce this around the city, except for a few posters around Benimaclet during the last week of June, people clearly remembered last year's experience and the pla a de Beni was full of chairs for all three weekends. It really helps to turn around during a projection and see so many people behind you participating in something you've invested some of your own time and money. It's probably too late now, but there's some talk of extending this to the Sundays in August, so we'll see. Also, we plan to do a picaeta for attendees as a small closing party for this year's cycle. See you on Sunday, and enjoy V!

24 July 2008

Christian Perrier: Holidays

Tomorrow, I'll leave /home for more than 3 weeks: For people who are not tired of this, I've had the great honor of being sollicited to hold a keynote lecture at Debconf. As you'd guess, that will be about i18n in Debian. I plan it to be a kinda general thing, giving the current rough picture of how things are going (or not going). No deep technical stuff (aha, how could *I* do that anyway?), just talking with hands. From informations I have, it should be on Aug. 14th, at the beginning of the talks schedule (9:30 or so, local time...check this when the official schedule is out). Apart from that, my personal schedule for DebConf is mostly working with the i18n folks who will be there (Felipe A. van de Wiel aka "faw", Nicolas Fran ois aka "nekral") on the i18n server. Work/talk with Neil Williams about tdebs stuff and all things related to i18n and embedded stuff is also planned as well as preparing the Extremadura meeting we need to have at the end of the year.

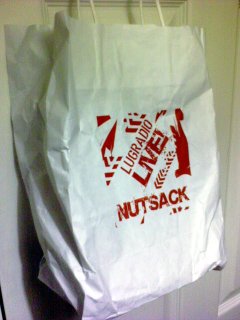
MJ Ray: What was in my Nutsack? (from Lug Radio Live)


The notorious nutsack (cc-by-2.0) The conference pack for LugRadioLive was called a “nutsack” for some reason (anyone know why?). It seems like a pretty good pack, as far as these things go. First of all, it’s a durable paper bag, so much greener than plastic. It contained: All in all, smarter than your average conference pack… or am I just thinking that because it looks a bit like a picnic?

23 July 2008

Pablo Lorenzzoni: The new Brazilian Internet surveillance

Here I am writing today to tell something that might not be known outside Brazil at least, I haven t read much in English about it the attempt to turn the Internet into a government surveillance device. This story goes back to 2006 (and even back), when we first successfully blocked the approval of a bill that would, in effect, turn the Brazilian Internet into a giant Big Brother. This bill was introduced by Senator Eduardo Azeredo as a replacement to a series of other similar bills that were attempted before and was followed by a strong resistance by civil organizations, one of those being ASL, of which I am proud of being one of the founders. By that time we ended having it postponed for more debate. It happened that the bill made a come back last weeks, and was pushed into approval by a subcommittee of the Senate (one that was suppose to deal with the constitutionality of bills) and now is heading to the Chamber of Deputies for appreciation. Apart from the first debates back in 2006, nothing happened between then and the approval. The bill have changed a little bit, but not much as to change its effects. In Brazil, we have two legislative houses, Federal Senate and Chamber of Deputies. If a Law Project is proposed by one, is revised by the other. So we have already lost 50% of the fight. Ronaldo Lemos, professor of Funda o Get lio Vargas (think about a Brazilian version of Harvard Law School ) have already stated how dangerous such a Law can be, once approved. In his own words: The wording of the law is too broad, and can be applied in several cases. The interpretation of what is a crime or not will be done by a criminal judge, who is used to deal with homicides and not with technology . Since its approval in Senate, several people have been putting together a resistance. Central to it is a Petition, hosted at Petition Online, that already holds 64-thousand signatures. One of the writers of that petition, Andr Lemos, a university professor and researcher, have said that the regular user will have the feeling of being watched, and not knowing if what he s doing in legal or not: For instance, if I disseminate a virus without knowing, will I be arrested? Can I exchange my files in P2P networks (my pictures, my musics, my text files) without asking for permission? How will the ISPs interpretate these exchanges? Can I copy a part of a text from a blog and paste it into mine? This law creates a feeling of insecurity and generalized fear . FGV s Center for Society and Technology have published an analysis of the Law Project, and have spotted a lot of problems in it. For instance: Thinking of how I can help, after sending an email to every Deputy whose email address I was able to get, I decided to translate the law into English (I also uploaded a version with indentation, since it s pretty hard to understand the whole law without it, if you re not used to), so the World can be made aware of what s going on in Brazil. I also just sent an email with it to EFF, asking for their help. Not that I think they can do much, but they surely will know one or two strings to pull in order to put more pressure on the Brazilian government. I also hope that, once this post reaches Planet Debian, even more people become aware of the issue. In a sense, this is an appeal for all the Freedom Culture lovers out there to take any actions they can to help us prevent this Law Project to become a Law. (In time, I d like to thank Alexandre Oliva, who revised the translation). Update (2008-07-23 11:50): Steve Langasek also revised the translation of the Law Project and I ve made a cherry-pick merge , which resulted in the version currently linked in the text above. Older version of the plain and the indented documents are still available. Thanks Steve!
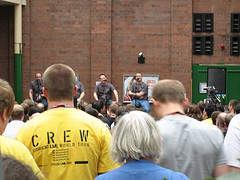
MJ Ray: LugRadio Live Event Review, Part Web2.0


LUGRadioLive 2008 by sheilaellen (cc-by-2.0) One aspect I didn’t mention in the LugRadio Live Event Review was how old-fashioned it seemed in some ways. I guess I’ve got used to seeing conferences experimenting with various web2.0 toys like live-blogging, feedback walls and so on, or the excellent live video streaming of DebConfs, but it was a bit of a surprise to find myself the only person in the audience who connected to the IRC channel from the event. One possible reason for that was that the wireless network was a bit difficult, or at least that was what I was told. I felt quite smug with my 3G smartphone IRC client (which I’ll blog about later) until Rufus Pollock mentioned the 800+ patents involved in 3G. Damn - I guess I hate freedom. In one way, I guess it’s appropriate if the network wasn’t up to the task. Broken networks were a regular feature of early ALUG meetings, as the end of this email hints. Web2.0 was there a little bit. There was a facebook page (which I accidentally spammed while travelling to the event), flickr:lugradiolive and a twitter link of #lugradiolive - but how does that work? There’s no user called lugradiolive and you can’t have usernames containing # Update: twitter:#lugradiolive (thanks to Dave Briggs for the explanation in a comment). Anyway, seeing as there will be another LUG Radio Live, maybe we can arrange something more interactive but free-software-friendly for 2009? More reviews I’ve read: davee: Lugradio-in makes me feel good , Peter Cannon: The party’s over for LugRadio Live and No’: Lugradio Undead - but why aren’t more people writing about this event? There seemed to be enough there. Or are they out there but I’m just not seeing them?

22 July 2008

MJ Ray: LugRadio Live Event Review


LUGRadioLive 2008 by sheilaellen (cc-by-2.0) This weekend, I learnt lots of things while at LugRadio Live in Wolverhampton. One thing was the surprising delay between posting something on this site and it actually appearing in the feed on my mobile phone. Another is that I can’t post to my new blog hosting from my mobile phone, which I’ll debug Real Soon Now. So, this is a bit later than when I first wrote it and it’s now one post instead of seven or so… Thanks to some unexplained delay travelling through Birmingham, I walked into LugRadio Live during the Introduction. The venue was generally pretty good, but the stage obstructed the entrance the acoustics in the atrium only seemed to work for the four gents. No idea what they said: I got past the stage into the audience and it finished almost immediately. For the first talk session, I went to see Rufus Pollock of Open Knowledge Foundation introduce a plan for the Comprehensive Knowledge Archive Network. Seems like a good idea. I’ve tons of questions, but I can’t quite get them into words, I don’t know when I’ll have time for this and I’m not sure they really matter anyway. I think I’ll mention CKAN to some librarians anyway and see what they make of it. I expected Emma Jane Hogbin’s “Form an orderly queue, ladies” to start an argument with the usual chix silliness but I was pleasantly surprised by how reasonable the advice was. In fact, the speaker also criticised the “chix” movements, although it appeared she participates in some women-only clubs, so not a 100% win for equality there. Sadly, much of the talk has been overshadowed in my mind by the memory of a giant furry racoon walking in unexpectedly, so I’ll probably grab the video of the LRL-USA version sometime soon. James Hooker’s talk titled “Taming the dragons — entrepreneurship and VCs” launched venturex as described on his own site already (along with more talk descriptions). It was an interesting demo, but it requires hackers to sell some votes in their companies to Venture Capitalists, which I believe is a bad thing for free software developers to do. We need to look more at a form of social entrepreneurism.</soapbox> I tried to ask a question, but the terrible atrium acoustics did funny things with my not-so-good hearing and I lost my way somewhat. At the end of that talk, I got chatting to an interesting web developer from Leicester who also forsook The Gong-a-Thong Lightbulb Talk Extravaganza and headed up to the Lightning Stage for Robert Collins and the Bzr talk. As well as some glimpses of how it’s changed since forking from tla, it was interesting to see a real (imperfect) demo and a non-Emacs version control GUI. The web interface for casual users to submit patches sounded very interesting and I also learned that some people pronounce “svn” like “Sven”. Most things that Robert thought were benefits sounded like drawbacks to me, so I’ll stay with git for now. Steve Lamb’s Green IT talk was the last presentation I saw. This talk really disappointed me because it seemed to be skewed towards the corporate governance nonsense instead of seeing Green IT as a vital pragmatic step, mentioning points I’d seen put more clearly elsewhere, as well as advertising Vista virtualisation and some panoramic webcam from Microsoft (who employ him) that doesn’t work with any free software, according to a deserved verbal shoe-ing in the Q+A. Only thing I remember that seems useful: charging from USB is more efficient than using wallwarts. Is that right? Finally, the main event: LugRadio Live and Unleashed. It opened with the shock announcement that LRL will continue into 2009, as announced elsewhere already. The rest of the madness will presumably appear online shortly and I don’t remember it well enough to do it justice… A tech conference crossed with a rocking gig by the strangest boyband ever, with a cheerleading racoon and some very cool people. I’ll try to be at LRL 2009. Will you be there? Were you at LRL this last weekend?

21 July 2008

Clint Adams:

This is the night of second-hand thoughts. Oh, the shame. I'm gonna do this in mostly-chronological order. Mostly. I vaguely remember the first great meal I had in Paris. I got off the plane, went through immigration and customs, hopped on the RER, got out and dragged my suitcase to Le Chat Gripp . I walked through the door in my T-shirt and jeans, and said well, I don't remember what I said, but I ended up getting a table and ordering the tasting menu. I don't remember very much about the food, but I remember that the waiter had to wake me up between courses. I've kinda had a thing for tasting menus ever since. Tonight I made a reservation at a fine dining establishment that was advertised as having a couple of tasting menus. I wasn't going to commit myself to a tasting menu, but there was a good chance I would find it irresistable. I timed my departure pretty well, and after walking the 2.5 miles to the restaurant, I was only a couple minutes early. Now the funny thing about this is I did not happen to notice that I had entered Molecular Gastronomy Hut. The signs outside did not say Molecular Gastronomy Hut, neither in cuneiform, hieroglyphs, nor any language I could read. The menu did not advertise the fact that this was Molecular Gastronomy Hut. Had I known that this was Molecular Gastronomy Hut, I would have not ordered the tasting menu, especially since I was not hungry and should probably have not even eaten a whole course. Had I known that the wine pairings would only include two reds, I wouldn't have ordered those either. Normally I expect wine pairings to include a white. It's the thing to do; it adds contrast. You drink it and get it over with and then you enjoy the rest of your meal. This had at least three whites and one ros . Mother of God. For the moment, though, I had no foreknowledge of the wines, and was was entranced by the knives, which were twisted such that if the handle was lying flat on the table, the blade stood vertically. Not only was this incredibly distracting, it seemed to have some practical value; if there were foodstuffs on your knife, they would remain elevated and not touch the tablecloth. Anyway, the food comes out, course by course, wine by wine. I wonder if Richard from Top Chef is hiding back in the kitchen. There are random foams and gastriques lying conspicuously on my plates. My second course had a lemon sorbet sitting on top of various types of vegetable matter. My third course involved arthropods. Ever wonder what to pair with fried arthropod? That's right, ros . My fourth course was actually tasty, much to my surprise. It was a pumpkin flower cappuccino. It is hubris to call it cappuccino, but they did and I am going to maintain the tradition. It tasted like warm infused buttery goodness, even though I was picking insect legs out of my mouth while drinking it. You may or may not be surprised to learn that the lemon sorbet made a reappearance in a later course. The waiter recommended mixing it with the other ingredients. Tom Colicchio was hiding in the back of my head asking why, if it was meant to be mixed, wouldn't they serve it mixed. I am forced to agree. The only other thing worth having was the cheese plate. It was populated with cheese I had never had before, and fruit concoctions to go with each. Most of the cheese were nothing special, but one was orgasmic. No, I'm not going to tell you what it was. Oh, all right, it was the middle one. One hundred fifty-six courses later, I was asked if I wanted any coffee. I didn't really want caffeine, but as I didn't want to sabotage the experience, I acquiesced and consented to an espresso. I'm not sure how I was understood, as by this time I had stopped speaking the local language and was presently shouting about bacon-burger dogs, the Huxtables, and Freebird. Then after coffee and being ignored, I asked for the check. Surprise, surprise: there was an additional dessert course to go. Didn't I look foolish? The bill came out to about half the country's GDP. The last time I had seen that many digits was when a bunch of hipsters tried to calculate while spaz-dancing to Fischerspooner and playing Space Channel Five. I wondered how it must feel for one of those guys who decides to order all kinds of extravagant room service in a luxury hotel right before committing suicide. After I paid, which seemed to confuse them a bit, they offered to call me a cab. I refused politely several times. I don't like cabs to begin with, aside from the whole plutocrat-fatcat I-might-as-well-get-a-maid-and-a-butler-and-a-valet feel to them, and the practical aspects of the drivers being douchebags. I had just spent a ridiculous amount of money on food that wasn't worth it, and I saw no reason to add insult to injury by paying for a taxi. It could probably have been $10 or $15 more. Mother of Christ. So I walked. It was only four or so miles to my bed, and I passed the time by singing songs of cormorants and racial disharmony and seventeen-year-old prostitutes and the time the Rescue Rangers got sentenced to maximum-security prison. All in all it was a terribly unpleasant contrast to the happy song about alfajores I was singing before dinner. Mmm alfajores.

Martin Michlmayr: Daily installer image available for QNAP TS-109, TS-209 and TS-409

Daily installer images are now available for the QNAP TS-109, TS-209 and TS-409. This means that complete installations of Debian testing are possible now. You can consider the daily image as a beta release of RC1 of the debian-installer for Debian lenny. It should only be used by experienced users and only if you can make a serial console in case something goes wrong. As the name suggests, the daily images change on a daily basis and they install Debian testing which also changes on a daily basis (although testing should be fairly stable since we're close to the freeze of testing in preparation for the release of Debian lenny). If you install Debian with these installer images, please send an installation report to debian-boot send an email to me so I can let you know in case there are any important news you should be aware of. There is a web site now with complete installation instructions and other information about Debian on QNAP Turbo Station. If you have any questions or suggestions, please let me know.

Biella Coleman: The BSA in Puerto Rico

Apparently there is enough of a pirate problem in PR that the BSA even has a special PR-only Website.

20 July 2008

Kartik Mistry: Quick visit to Mumbai and more..


* I visited /home (ie Mumbai) for one day. And, found that, 1. Kavin got 2 new teeth to accompany his rabbit like teeth on upper side! 2. Kavin can now walk (run) without support. 3. My broken camera can give very good results when needed. 4. I can stay without Internet for entire day! * Kavin and K will be here with me from next week, my hunt for home is still continue (hopefully, it will end this week). * Good news: Cleared FD and DAM Approval stages, now only one step remaining to get complete Nirvana. * I am bit upset about recent happenings in Gujarat and entire nation. Not writing much here, as My Gujarati blog is speaking better for such issues in my own language!

Russell Coker: Review of the EeePC 701

I have just bought a EeePC 701 [1], I chose the old model because it’s significantly smaller than the 90x series and a bit lighter too and it had Linux pre-loaded. Also it was going cheap, while I am not paying for it I give the same attention to saving my clients’ money as to saving my own. I ruled out everything that was heavier or larger than an EeePC 901 and everything that cost more than $700. That left only the Linux version of the EeePC 901 (which I couldn’t find on sale) and the EeePC 701 as my options. I also excluded the EeePC 900 because it is bigger and heavier than the 701 but has the same CPU (and therefore can’t run Xen). In terms of it’s prime purpose (a SSH client) 96*22 characters is the size of a konsole screen with the default (medium) font size when the window is maximised, that is 5% more characters than the standard terminal size of 80*25 but the smaller number of lines is a problem. When using the small font I can get 129*29 which I find quite comfortable to read (it would be impossible for me to read withut glasses - which means having almost average vision for someone in their 30’s). Then I can get 129*31 if I dismiss the tool bar at the bottom of the screen and could probably get another couple of rows if I removed the tabs that Konsole uses to switch between sessions. That would only be viable if using screen extensively as a single session without the ability to switch between programs is not particularly useful (I don’t think that ALT-TAB is adequate for switching between terminal sessions). When running Debian I can get 130*32 with the same font due to smaller window controls, but I’ll write more about converting to Debian in another post. Note that while the OS that ships with the Linux based EeePC machines is based on Debian, it is heavily customised and has some notable differences from a typical Debian install. It has some proprietary software, and uses unionfs for the root and /home filesystems. The first issue is that Console (the KDE terminal program) can only be accessed from the file manager (via the tools menu or ^t), the machine clearly doesn’t have defaults for someone like me. In principle it’s a multi-user system that can be fully customised, but in practice it’s configured as a single-user machine. Once you have a Console window open you can run “su -” and the root password is the password for the “user” account. I wonder whether I could get more than 42 rows or more than 140 columns of text that is readable. If so then I could have two console windows fully displayed on screen. The screen is bright and clear, this is essential as the number of pixels per character is going to be low for any reasonable amount of text to be displayed on screen. The password that you set when you first use the machine also works for “su -” (in fact that is the only real use as I expect that almost everyone will choose the automatic login option). The display comprises a significant portion of the weight, if the screen is fully open (about 150 degrees) then it will tip over. Even when the screen is not as far open it will tip due to bumps if resting on your lap on a tram. It’s a pity that the screen is connected at the very back of the base, if the attachment point was a bit closer then it would balance better and also be easy to hold with one hand. The depth of the machine combined with the angle at the back makes it impossible for me to get a good one-handed grip from the base, so typing while standing on a moving tram or bus will be extremely difficult (unlike my iPaQ which I can use at full speed on any form of public transport). Inidentally it would be good if there was an attachment point for a wrist-strap, every camera and most mobile phones have them so it would be good to have the same safety feature in a laptop to facilitate use on public transport. Another reason for not using it as a PDA is the fact that it takes about 7 seconds to resume after hibernating (when the lid is closed). The PSU is almost as small as that of a mobile phone! This is a major benefit as in the past I have often stored a Thinkpad PSU at a client site for 9-5 jobs as it is heavy enough that I didn’t want to carry it on public transport. The EeePC PSU is light enough that it won’t be unpleasant to carry, and small enough to fit easily into a jacket pocket. The OS installation is very well done for the basics. It’s easy to launch applications and there is a good selection of educational programs (including the periodic table, planetarium, typing, letters, and hangman, drawing, and a link to www.skoool.com). It’s a pity that they organised the folders according to the area rather than the age, but generally the OS is very well done. Most of the reviews focus on the speed of the CPU, the RAM expansion options, etc, but miss the fact that it is a really nice machine for using as-is. It is a much better machine for teaching children than any of the machines I’ve seen which are sold specifically for children (see my previous post about an awful computer for kids [2]). I believe that you could give an EeePC to any 3yo and have them doing something useful in a matter of minutes! The ability to freely install new software should not be overlooked when considering a computer for children to use. Someone who buys one now could use it for a few years as an ssh client and then reinstall the original OS and give it to a child as an educational toy. It has a program to create OGG video files from it’s built-in camera and mic, at this moment it’s the only device I own that can create OGG files (this is a good thing). OGG compression takes a really long time, the Atom CPU in the 901 and 1000x series would be good for this. It’s a pity that the microphone is directly below the mouse buttons, it clearly records the mouse click used to finish recording. The version of mplayer which is installed to play OGG files can also play FLV files downloaded from youtube with youtube-dl (althrough the file association is not set). When I tried to play a MP4 file from ted.com it only gave audio (the video works on a full Debian/Etch installation). There is a full set of office software, OpenOffice.org, Thunderbird email client, and all the other stuff you might expect. I find that the biggest problem for using it is the size of the keyboard, I don’t think I’ll ever be able to touch-type properly on it. Not only are the keys small but the positions of non-alphabetical keys are slightly different from most keyboards. Another problem is that the space-bar needs to be pressed near the centre, I usually like to press near the end but that doesn’t work. Those issues are all trade-offs of the small size. My T series Thinkpad is reasonably portable and has a great keyboard so I have the serious typing while travelling angle covered. One real mistake in the keyboard design is the lack of a LED to indicate whether caps-lock is enabled (there are four status LEDs, adding number five couldn’t be that expensive), this is a real problem when using the vi editor (which uses letters as editor commands and is case-sensitive). It will also occasionally cause problems when entering passwords. There is a caps-lock indicator on screen, but that is in the toolbar at the bottom of the scren (which I like to dismiss to gain an extra two lines of text). It would be good if I could display the status of the caps and num lock keys in the right side of the title-bar of the active window (the only bit of unused space on the screen). The cooling fan makes an annoying buzz. It’s significantly louder than Thinkpads which dissipate a lot more heat. The other problems are all software, which is OK as I plan to reinstall it. Firstly it is using Debian and shipped with the broken openssl library. There is a GUI for installing upgrades, but it recommends rebooting after installing each one! Naturally I didn’t choose to reboot, I installed the security update #1. Then I clicked on the button to install a BIOS update. It told me that it had to reboot to apply the update and gave only one button (OK), I tried closing the window but it rebooted anyway (fortunately the vi swap file allowed me to recover this post - which I am entirely writing on the EeePC). Aftere booting up again I discovered that the libssl bug still wasn’t fixed and that there was a second udate to apply! Why can’t they have a “apply all updates” button and also have it not automatically reboot? This must be the only Debian-based distribution that forces Windows-style reboots. But that said, while they made some mistakes in their software it generally provides a good user experience

19 July 2008

Luciano Bello: Exploiting DSA-1571: How to break PFS in SSL with EDH

( I love acronyms :-D )

At this point, all of you should know and see how the H D Moore s toys work. Those toys attack SSH public-key authentication using clone keys and online brute force.

Furthermore, many of you know that there are other effects produced by a biased PRNG besides this one.

Strangely, I could not find more of those toys exploiting these aspects. So, I would like to show you a Wireshark patch which attacks Perfect Forward Secrecy (PFS) provided by Ephemeral Diffie Hellman (EDH).
Introduction to EDHLet s put it in plain words (if you know what we are talking about, ignore this and jump to the next heading):
In an insecure communications channel the parties agree a common key to cipher their dialog. This is what happens in SSL (in most of the cases, depending on the cipher suite):
The exploit If an eavesdropper can explore the complete private key space (the all possible numbers for Xc or Xs), he/she will be able to get access to the shared secret. With it all the communication can be deciphered. That s what this patch can do.

A Wireshark with this patch and a list of possible private keys will try to brute force the share secret. If one of the parties is using the vulnerable OpenSSL package the communication is totally insecure and will be decrypted.


The patch was submitted in order to be committed on the Wireshark trunk. There you can find the patch against the on-develop source revision 25765.
Issues that can be improvedWe (the other developers and myself) detected few things to be improved. But we will do nothing for them. So, if you want to contribute with some code, start from these items and submit the patches to the Wireshark s bugzilla:CreditsPaolo Abeni <paolo.abeni at email.it>
Luciano Bello <luciano at debian.org>
Maximiliano Bertacchini <mbertacchini at citefa.gov.ar>

This work was partially supported by Si6 Labs at CITEFA, Argentina.

UPDATE Jul. 21st: See more and updated info here, especially this.

Luciano Bello: Exploiting DSA-1571: How to break PFS in SSL with EDH

( I love acronyms :-D )

At this point, all of you should know and see how the H D Moore s toys work. Those toys attack SSH public-key authentication using clone keys and online brute force.

Furthermore, many of you know that there are other effects produced by a biased PRNG besides this one.

Strangely, I could not find more of those toys exploiting these aspects. So, I would like to show you a Wireshark patch which attacks Perfect Forward Secrecy (PFS) provided by Ephemeral Diffie Hellman (EDH).
Introduction to EDHLet s put it in plain words (if you know what we are talking about, ignore this and jump to the next tittle):
In an insecure communications channel the parties agree a common key to cipher their dialog. This is what happens in SSL (in most of the cases, depending on the cipher suite):
The exploit If an eavesdropper can explore the complete private key space (the all possible numbers for Xc or Xs), he/she will be able to get access to the share secret. With it all the communication can be deciphered. That s what this patch can do.

A Wireshark with this patch and a list of possible private keys will try to brute force the share secret. If one of the parties is using the vulnerable OpenSSL package the communication is totally insecure and will be decrypted.


The patch was submitted in order to be committed on the Wireshark trunk. There you can find the patch against the on-develop source revision 25765.
Issues that can be improvedWe (the other developers and myself) detected few things to be improved. But we will do nothing for them. So, If you want to contribute with some code, start from these items and submit the patches to the Wireshark s bugzilla:CreditsPaolo Abeni <paolo.abeni at email.it>
Luciano Bello <luciano at debian.org>
Maximiliano Bertacchini <mbertacchini at citefa.gov.ar>

This work was partially supported by Si6 Labs at CITEFA, Argentina.

18 July 2008

Nicolas Valc rcel: Hello Planet Debian!

As it usual when someone gets in, this is my hello Planet Debian post. I’m Nicolas Valc rcel, i’m the maintainer of terminator and augeas and really interested on server and security topics. I’ve just started my New Maintainer process some weeks ago and hoping to put all my energies on making debian even better and easier! I Live in Lima, Per .

17 July 2008

Gunnar Wolf: Kept silent for a week...

Last week (July 7-13) was basically hell on Earth, for me and for the group that somehow got the name Cabras locas, of which I am part since I joined the National Pedagogical University, where I worked full-time 2003-2005.
It was, yes, the first of my officially three weeks of Summer holiday at IIEc-UNAM, so no problems here. So, why hell on Earth? Because we were in charge basically of anything related with information flow, retrieval and manipulation at the 11th International Congress on Mathematical Education, in Monterrey.
What we thought would basically be one or two days of hard work followed by six days of relaxed vacations (we had even planned to have an internal seminar, showing off the shiny stuff each of us is working on) became... A mind-boggling eight day experience where we worked over 12 hours a day on being human replacements for Google, SQL engines, full-text parsers, report generators, printer watchdogs, and in general lines, just a bunch of unhappy firemen, ready to be called off for whatever task was necessary.
We did have, of course, several calm periods every now and then. We even had to learn how to look busy while doing something compeltely unrelated (that would explain, for example, a couple of low-hanging bugs I fixed for Debian, or some dozens of lines of code I could get off my head).
But my advice for whoever reads this: Don't trust people with long database-handling experience. Specially when they insist that hand-capturing a thousand registers is preferrable (i.e. less error-prone) than parsing three separate databases and discarding duplicates. And, of course, specially when this person is your boss, which is enough of an argument to have it his way.

MJ Ray: Batting Against Three Strikes through the Back Door

One of the reasons that I didn’t post much last week was that I was contacting some of my MEPs as part of the Telecom Packet Action in order to help defend cooperative software distribution and use. This is a bit longer than my usual posts and no software is announced below, but I’m posting it here in the hope that more people will take part in this campaign that affects every EU internet user. In short, some MEPs that I remember from the Software Patent campaign proposed amendments that would enable the unpopular three-strikes regime, where internet users could be disconnected and fined if they had three allegations of copyright infringement made (not necessarily proved AIUI) against them, and ISPs could be required to block legal peer-to-peer cooperative distribution systems like BitTorrent. ISPs would also have to distribute official advice about proper internet use and I remember how good that often is. Note that three-strikes wasn’t explicit in the amendments, but there did appear to be loopholes which could be used to allow it, such as only prohibiting technical feature requirements. For longer descriptions, see articles by La Quadrature du Net (Squaring the Net) and The Open Rights Group. The UK Independence Party MEPs replied quickly that they would vote against, mainly because of the source of the legislation. I don’t completely agree with that, but at least UKIP does what it says on the tin. Neil Parish MEP of the Conservatives sent me back a reply which referred to unknown numbering (H1, K1 and so on) and generally seemed like a mish-mash of replies that other people had received. I replied with questions about several aspects, including asking where his numbering came from, and I’ve not seen an answer yet. I’ll email him again in a few days because it’s been over a week. I was really annoyed by the reported complaints by Malcolm Harbour (Conservatives lead MEP on this issue) about how voters have reacted to these amendments, where he called it “scaremongering” amongst other things. No mongering was required - those amendments are damn scary. See comments from a media solicitor at the end of a BBC report:-
“The amendment will cause several problems, firstly, many broadband users routinely transfer large files which are encrypted. “Many of these are acting quite legitimately and in order to determine whether or not such large files are or are not the produce of illicit file sharing the ISP will have to carry out an unprecedented degree of analysis of its customers’ traffic. “Furthermore, computers are frequently shared - within offices, within homes, within educational institutions and inadvertently, where wrong-doers “piggy back” on an inadequately secured Wi-Fi connection. “All this raises the spectre of people losing internet access - for reasons which are no fault of their own.”
The main thing that these actions over the last few years have taught me is the broken state of European Union decision-making. I know I’m sometimes dissatisfied with problems in local and civil democracy, but the EU is a good idea whose democracy and accountability seems broken on a massive scale. There are just too many disconnects, as far as the ordinary voter can see. We put things in to elections and consultations and get bizarre law-making like this. If we act to correct the bizarre law-making, some MEPs start criticising us quite severely. And what kind of stupid representative system allows the representatives to repeatedly blame the voters but still be safely elected because of their high position on their party’s list? I’d love a simple, reformist constitution that’s simple enough for people to actually understand, approve in referendums and participate in the EU effectively. I doubt it will happen in my lifetime, though.

16 July 2008

Stefano Zacchiroli: updating w3-recs

revamping w3-recs: new specs, misc improvements After quite a lot from my initial adoption, I've spent some time to update w3-recs. Beside the long overdue update of shipped recommendations (quite a few new specification was released, mostly related to SPARQL, but a few more have been edited, including CSS 1 and 2), I've also uploaded some pending improvements. A couple of bug fixes were about dangling links and registration of recommendations with the GNOME devhelp stuff. Additionally, I've also moved all the documents registered with doc-base under the new Help/Standards section of doc-base, which seems to be fit for W3C Recommendations. Apparently we have finally managed to have a proper section tree for doc-base, the decoupling of that tree from the Debian menu one will not be missed (at least not by me). During the process I've also discovered a (recent?) change in debhelper semantics. Thus far I used to have broken doc-base document IDs in w3-recs, as they contained uppercase letters, which are prohibited according to /usr/share/doc/doc-base/doc-base.txt.gz. My fault, I concur, but in the past the documents got installed anyhow without any problem. On the contrary, with the latest debhelper all documents got written to the very same file, apparently stripping away the part of their names which do not match the used lowercase regular expression. Well, not too bad, I fixed one more bug, but with a warning fixing that would have been quicker. Also, /me wonders, if everything (but package build :-) ) worked properly with uppercase document IDs, why the heck one should forbid them in the doc-base specification?

Next.

Previous.