Dear Debian community,
this are my bits from DPL written at my last day at another great
DebConf.
DebConf attendance
At the beginning of July, there was some discussion with the bursary and
content team about sponsoring attendees. The discussion continued at
DebConf.
I do not have much experience with these discussions. My summary is that
while there is an honest attempt to be fair to everyone, it did not seem to
work for all, and some critical points for future discussion remained. In
any case, I'm thankful to the bursary team for doing such a time-draining
and tedious job.
Popular packages not yet on Salsa at all
Otto Kek l inen did some interesting investigation about
Popular packages not yet on Salsa at all.
I think I might provide some more up to date list soon by some UDD query
which considers more recent uploads than the trends data soon. For
instance wget was meanwhile moved to Salsa (thanks to No l K the for this).
Keep on contacting more teams
I kept on contacting teams in July. Despite I managed to contact way
less teams than I was hoping I was able to present some conclusions in
the Debian Teams exchange BoF and Slide 16/23 of my
Bits from the DPL talk.
I intend to do further contacts next months.
Nominating Jeremy B cha for GNOME Advisory Board
I've nominated Jeremy B cha to
GNOME Advisory Board.
Jeremy has volunteered to represent Debian at
GUADEC in Denver.
DebCamp / DebConf
I attended DebCamp starting from 22 July evening and had a lot of fun with
other attendees. As always DebConf is some important event nearly
every year for me. I enjoyed Korean food, Korean bath, nature at the
costline and other things.
I had a small event without video coverage
Creating web galleries including maps from a geo-tagged photo collection.
At least two attendees of this workshop confirmed success in creating their
own web galleries.
I used DebCamp and DebConf for several discussions. My main focus was on
discussions with FTP master team members Luke Faraone, Sean Whitton, and
Utkarsh Gupta. I'm really happy that the four of us absolutely agree on
some proposed changes to the structure of the FTP master team, as well
as changes that might be fruitful for the work of the FTP master team
itself and for Debian developers regarding the processing of new
packages.
My explicit thanks go to Luke Faraone, who gave a great introduction to
FTP master work in their
BoF.
It was very instructive for the attending developers to understand how the
FTP master team checks licenses and copyright and what workflow is used
for accepting new packages.
In the first days of DebConf, I talked to representatives of DebConf
platinum sponsor WindRiver, who announced the derivative
eLxr. I warmly welcome
this new derivative and look forward to some great cooperation. I also
talked to the representative of our gold sponsor, Microsoft.
My first own event was the
Debian Med BoF.
I'd like to repeat that it might not only be interesting for people
working in medicine and microbiology but always contains some hints how
to work together in a team.
As said above I was trying to summarise some first results of my team
contacts and got some further input from other teams in the
Debian Teams exchange BoF.
Finally, I had my
Bits from DPL talk.
I received positive responses from attendees as well as from remote
participants, which makes me quite happy. For those who were not able to
join the events on-site or remotely, the videos of all events will be
available on the DebConf site soon. I'd like to repeat the explicit need
for some volunteers to join the Lintian team. I'd also like to point out
the "Tiny tasks" initiative I'd like to start (see below).
BTW, if someone might happen to solve my quiz for the background images
there is a
summary page
in my slides which might help to assign every slide to some DebConf. I
could assume that if you pool your knowledge you can solve more than just
the simple ones. Just let me know if you have some solution. You can add
numbers to the rows and letters to the columns and send me:
 2000/2001:  Uv + Wx
 2002: not attended
 2003: Yz
 2004: not attended
 2005:
 2006: not attended
 2007:
 ...
 2024: A1
This list provides some additional information for DebConfs I did not
attend and when no video stream was available. It also reminds you about
the one I uncovered this year and that I used two images from 2001 since
I did not have one from 2000. Have fun reassembling good memories.
Tiny tasks: Bug of the day
As I mentioned in my
Bits from DPL talk,
I'd like to start a "Tiny tasks" effort within Debian. The first type of
tasks will be the
Bug of the day
initiative. For those who would like to join, please join the corresponding
Matrix channel. I'm
curious to see how this might work out and am eager to gain some initial
experiences with newcomers. I won't be available until next Monday, as I'll
start traveling soon and have a family event (which is why I need to leave
DebConf today after the formal dinner).
Kind regards from DebConf in Busan
Andreas.
Debconf 24 is coming to a close in Busan, South Korea this year.
I thought that last year in India was hot. This year somehow managed to beat that. With 35C and high
humidity the 55 km that I managed to walk between the two conference buildings have really put the
pressure on. Thankfully the air conditioning in the talk rooms has been great and fresh water has been
plentiful. And the korean food has been excellent and very energetic.
Today I will share with you the main group photo:
You can also see it in:
The rest of my photos from the event will be published next week. That will give me a bit more time to process
them correctly and also give all of you a chance to see these pictures with fresh eyes and stir up new memories from
the event.
A new minor release 0.4.24 of RQuantLib
arrived on CRAN this afternoon
(just before the CRAN summer
break starting tomorrow), and has been uploaded to Debian too.
QuantLib is a rather
comprehensice free/open-source library for quantitative
finance. RQuantLib
connects (some parts of) it to the R environment and language, and has
been part of CRAN for more than
twenty-one years (!!) as it was one of the first packages I
uploaded.
This release of RQuantLib
follows the recent release from last
week which updated to QuantLib version 1.35 released that
week, and solidifies conditional code for older QuantLib versions in one source
file. We also updated and extended the configure source
file, and increased the mininum version of QuantLib to 1.25.
Changes in RQuantLib version 0.4.24 (2024-07-31)
Updated detection of QuantLib libraries in configure
The minimum version has been increased to QuantLib 1.25, and
DESCRIPTION has been updated to state it too
The dividend case for vanilla options still accommodates
deprecated older QuantLib versions if needed (up to QuantLib
1.25)
The configure script now uses PKG_CXXFLAGS and
PKG_LIBS internally, and shows the values it sets
The Combatants
In the red corner, weighing in at nah, I m not going to do that schtick.
The plaintiff in the case is Alegeus Technologies, LLC, a Delaware Corporation that, according to their filings, is a leading provider of a business-tobusiness, white-label funding and payment platform for healthcare carriers and third-party administrators to administer consumer-directed employee benefit programs .
Not being subject to the US bonkers health care system, I have only a passing familiarity with the sorts of things they do, but presumably it involves moving a lot of money around, which is sometimes important.
The defendant is DigiCert, a CA which, based on analysis I ve done previously, is the second-largest issuer of WebPKI certificates by volume.
The History
According to a recently opened Mozilla CA bug, DigiCert found an issue in their domain control validation workflow, that meant it may have been possible for a miscreant to have certificates issued to them that they weren t legitimately entitled to.
Given that validating domain names is basically the YOU HAD ONE JOB! of a CA, this is a big deal.
The CA/Browser Forum Baseline Requirements (BRs) (which all CAs are required to adhere to, by virtue of their being included in various browser and OS trust stores), say that revocation is required within 24 hours when [t]he CA obtains evidence that the validation of domain authorization or control for any Fully Qualified Domain Name or IP address in the Certificate should not be relied upon (section 4.9.1.1, point 5).
DigiCert appears to have at least tried to do the right thing, by opening the above Mozilla bug giving some details of the problem, and notifying their customers that their certificates were going to be revoked.
One may quibble about how fast they re doing it, but they re giving it a decent shot, at least.
A complicating factor in all this is that, only a touch over a month ago, Google Chrome announced the removal of another CA, Entrust, from its own trust store program, citing a pattern of compliance failures, unmet improvement commitments, and the absence of tangible, measurable progress in response to publicly disclosed incident reports .
Many of these compliance failures were failures to revoke certificates in a timely manner.
One imagines that DigiCert would not like to gain a reputation for tardy revocation, particularly at the moment.
The Legal Action
Now we come to Alegeus Technologies.
They ve opened a civil case whose first action is to request the issuance of a Temporary Restraining Order (TRO) that prevents DigiCert from revoking certificates issued to Alegeus (which the court has issued).
This is a big deal, because TROs are legal instruments that, if not obeyed, constitute contempt of court (or something similar) and courts do not like people who disregard their instructions.
That means that, in the short term, those certificates aren t getting revoked, despite the requirement imposed by root stores on DigiCert that the certificates must be revoked.
DigiCert is in a real rock / hard place situation here: revoke and get punished by the courts, or don t revoke and potentially (though almost certainly not, in the circumstances) face removal from trust stores (which would kill, or at least massively hurt, their business).
The reasons that Alegeus gives for requesting the restraining order is that [t]o
Reissue and Reinstall the Security Certificates, Alegeus must work with and
coordinate with its Clients, who are required to take steps to rectify the
certificates. Alegeus has hundreds of such Clients. Alegeus is generally
required by contract to give its clients much longer than 24 hours notice
before executing such a change regarding certification.
In the filing, Alegeus does acknowledge that DigiCert is a voluntary member of the Certification Authority Browser Forum (CABF), which has bylaws stating that certificates with an issue in their domain validation must be revoked within 24 hours.
This is a misstatement of the facts, though.
It is the BRs, not the CABF bylaws, that require revocation, and the BRs apply to all CAs that wish to be included in browser and OS trust stores, not just those that are members of the CABF.
In any event, given that Alegeus was aware that DigiCert is required to revoke certificates within 24 hours, one wonders why Alegeus went ahead and signed agreements with their customers that required a lengthy notice period before changing certificates.
What complicates the situation is that there is apparently a Master Services Agreement (MSA) that states that it constitutes the entire agreement between the parties and that MSA doesn t mention certificate revocation anywhere relevant.
That means that it s not quite so cut-and-dried that DigiCert does, in fact, have the right to revoke those certificates.
I d expect a lot of update to your Master Services Agreement emails to be going out from DigiCert (and other CAs) in the near future to clarify this point.
Not being a lawyer, I can t imagine which way this case might go, but there s one thing we can be sure of: some lawyers are going to able to afford that trip to a tropical paradise this year.
The Security Issues
The requirement for revocation within 24 hours is an important security control in the WebPKI ecosystem.
If a certificate is misissued to a malicious party, or is otherwise compromised, it needs to be marked as untrustworthy as soon as possible.
While revocation is far from perfect, it is the best tool we have.
In this court filing, Alegeus has claimed that they are unable to switch certificates with less than 24 hours notice (due to contractual SLAs ).
This is a pretty big problem, because there are lots of reasons why a certificate might need to be switched out Very Quickly.
As a practical example, someone with access to the private key for your SSL certificate might decide to use it in a blog post.
Letting that sort of problem linger for an extended period of time might end up being a Pretty Big Problem of its own.
An organisation that cannot respond within hours to a compromised certificate is playing chicken with their security.
The Takeaways
Contractual obligations that require you to notify anyone else of a certificate (or private key) changing are bonkers, and completely antithetical to the needs of the WebPKI.
If you have to have them, you re going to want to start transitioning to a private PKI, wherein you can do whatever you darn well please with revocation (or not).
As these sorts of problems keep happening, trust stores (and hence CAs) are going to crack down on this sort of thing, so you may as well move sooner rather than later.
If you are an organisation that uses WebPKI certificates, you ve got to be able to deal with any kind of certificate revocation event within hours, not days.
This basically boils down to automated issuance and lifecycle management, because having someone manually request and install certificates is terrible on many levels.
There isn t currently a completed standard for notifying subscribers if their certificates need premature renewal (say, due to needing to be revoked), but the ACME Renewal Information Extension is currently being developed to fill that need.
Ask your CA if they re tracking this standards development, and when they intend to have the extension available for use.
(Pro-tip: if they say we ll start doing development when the RFC is published , run for the hills; that s not how responsible organisations work on the Internet).
The Givings
If you ve found this helpful, consider shouting me a refreshing beverage.
Reading through legal filings is thirsty work!
With the work that has been done in the debian-installer/netcfg merge-proposal !9 it is possible to install a standard Debian system, using the normal Debian-Installer (d-i) mini.iso images, that will come pre-installed with Netplan and all network configuration structured in /etc/netplan/.
In this write-up, I d like to run you through a list of commands for experiencing the Netplan enabled installation process first-hand. Let s start with preparing a working directory and installing the software dependencies for our virtualized Debian system:
Next we ll prepare a VM, by copying the EFI firmware files, preparing some persistent EFIVARs file, to boot from FS0:\EFI\debian\grubx64.efi, and create a virtual disk for our machine:
Finally, let s launch the debian-installer using a preseed.cfg file, that will automatically install Netplan (netplan-generator) for us in the target system. A minimal preseed file could look like this:
For this demo, we re installing the full netplan.io package (incl. the interactive Python CLI), as well as the netplan-generator package and systemd-resolved, to show the full Netplan experience. You can choose the preseed file from a set of different variants to test the different configurations:
We re using the linux kernel and initrd.gz here to be able to pass the preseed URL as a parameter to the kernel s cmdline directly. Launching this VM should bring up the official debian-installer in its netboot/gtk form:
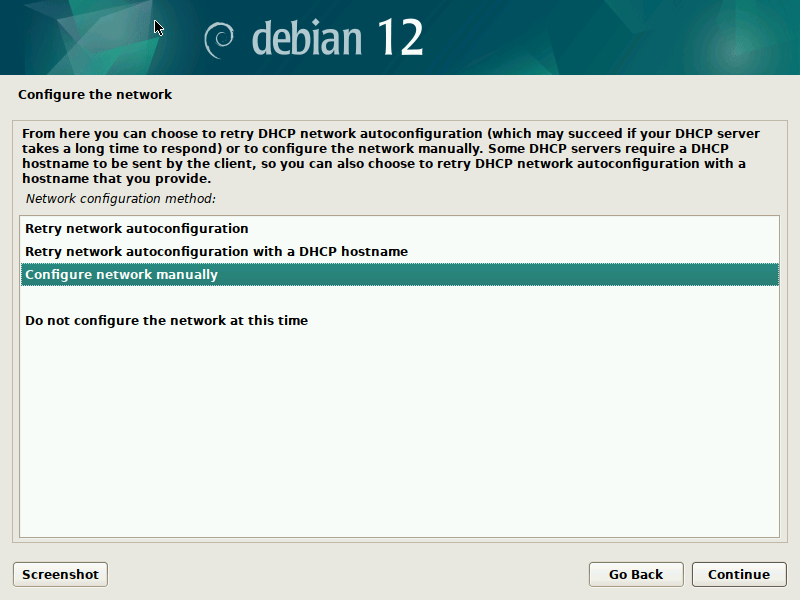
Now you can click through the normal Debian-Installer process, using mostly default settings. Optionally, you could play around with the networking settings, to see how those get translated to /etc/netplan/ in the target system.
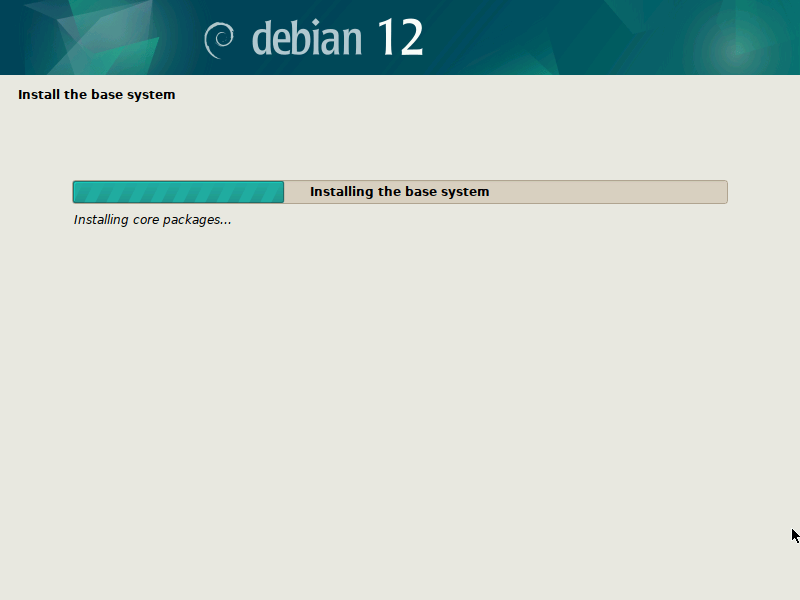
After you confirmed your partitioning changes, the base system gets installed. I suggest not to select any additional components, like desktop environments, to speed up the process.
During the final step of the installation (finish-install.d/55netcfg-copy-config) d-i will detect that Netplan was installed in the target system (due to the preseed file provided) and opt to write its network configuration to /etc/netplan/ instead of /etc/network/interfaces or /etc/NetworkManager/system-connections/.
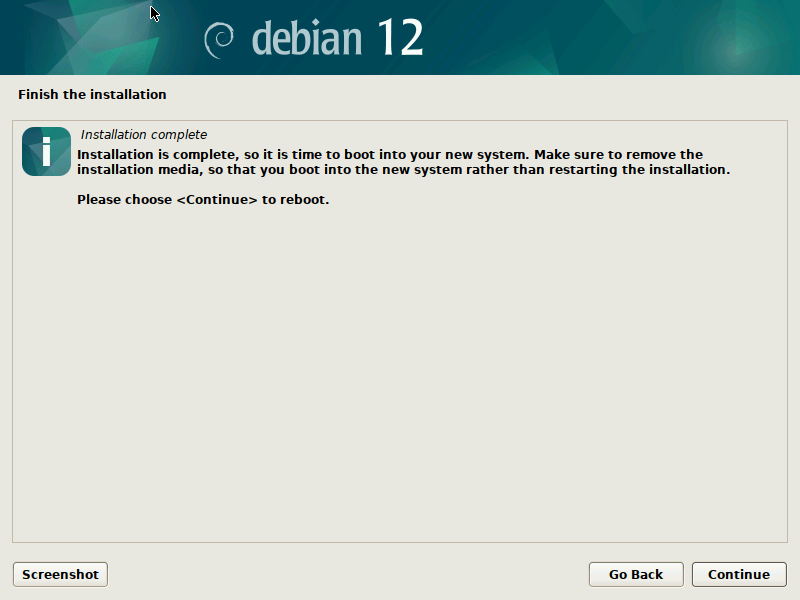
Done! After the installation finished, you can reboot into your virgin Debian Sid/Trixie system.
To do that, quit the current Qemu process, by pressing Ctrl+C and make sure to copy over the EFIVARS.fd file that was modified by grub during the installation, so Qemu can find the new system. Then reboot into the new system, not using the mini.iso image any more:
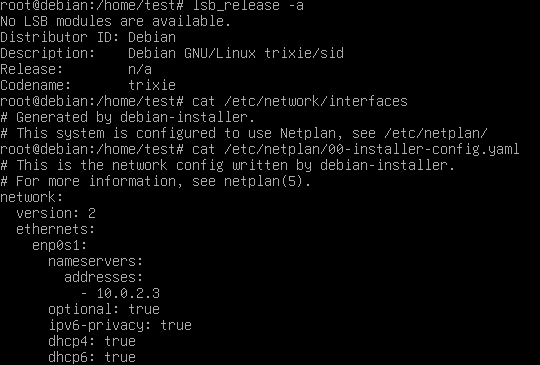
Finally, you can play around with your Netplan enabled Debian system! As you will find, /etc/network/interfaces exists but is empty, it could still be used (optionally/additionally). Netplan was configured in /etc/netplan/ according to the settings given during the d-i installation process.
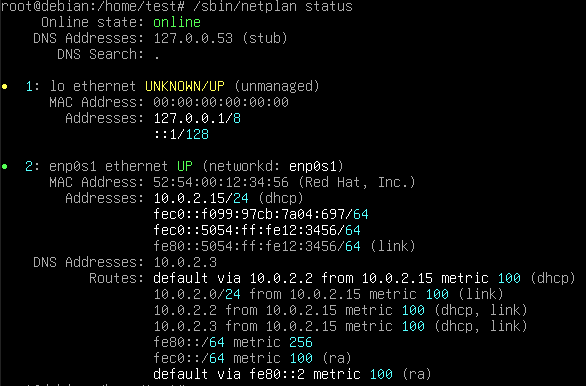
In our case, we also installed the Netplan CLI, so we can play around with some of its features, like netplan status:
Thank you for following along the Netplan enabled Debian installation process and happy hacking! If you want to learn more, find us at GitHub:netplan.
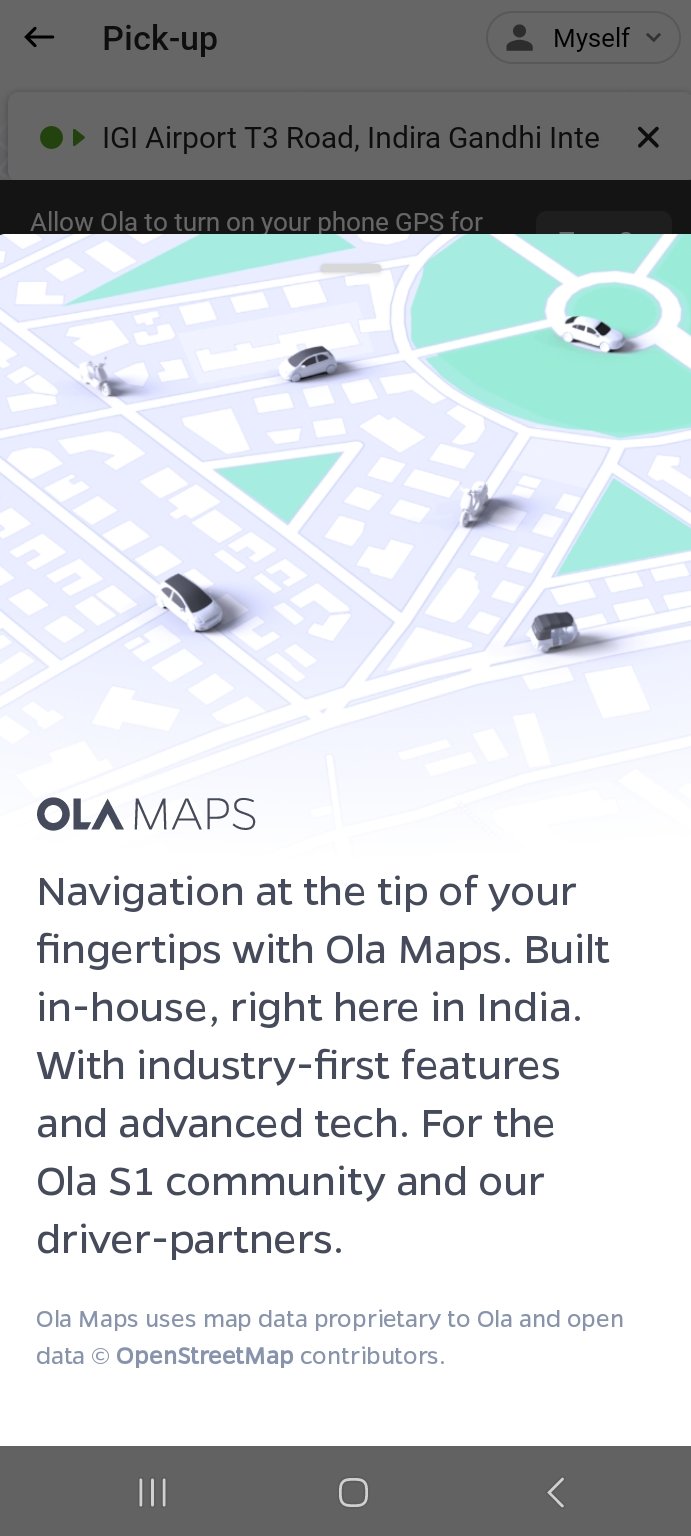
Recently, Ola started rolling out Ola Maps in their main mobile app, replacing Google Maps, while also offering maps as a service to other organizations. The interesting part for me was the usage of OpenStreetMap data as base map with Ola s proprietary data sources. I ll mostly about talk about map data part here.
Screenshot of Ola App. OpenStreetMap attribution is shown after clicking the Ola Map icon.
OpenStreetMap (OSM) for starters, is a community owned and edited map data resource which gives freedom to use map data for any purpose. This includes the condition that attribution is given back to OSM which in turn ideally would encourage other users to contribute, correct and edit, helping everyone in turn. Due to this, OSM is also regarded as Wikipedia of maps. OSM data is not just used by Ola. Many others use it for various purposes like Wikipedia Maps, Strava Maps, Snapchat Map, bus tracking in GoIbibo/Redbus.
OSM India community has been following Ola map endeavor to use and contribute to OSM since they went public. As required by OSM for organized mapping efforts, Ola created wiki entry with information regarding their editors, usage, policy and mentions following as their data usage case:
OSM data is used for the road network, traffic signs and signals, buildings, natural features, landuse polygons and some POIs.
Creating a map product is a task in itself, an engineering hurdle creating the tech stack for collection, validation, import and serving the map and the map data part. Ola has done a good job describing the development of tech stack in their blog post. Ola holds an enormous corpus of live and constantly updated GPS trace data. Their drivers, users, and delivery partners generate those, which they harness to validate, correct and add missing map data. Ola employees now regularly contribute new or missing roads (including adding dual carriageway to existing ones), fix road geometry, classification, road access type and restrictions pan India. They have been active and engaging in OSM India community channels, though community members have raised some concerns on their OSM edit practices.
Ola s venture into the map industry isn t something out of the ordinary. Grab, a South East Asian company which has business interests in food deliveries, ride hailing and a bunch of other services too switched to their in-house map based on OpenStreetMap, followed by launching of their map product. Grab too contributed back data like Ola. Both Ola and Grab heavily rely on map for their business operations and seem to chose to go independent for it, bootstrapping the products on OSM.
In India too, a bunch of organizations contribute to OSM like Swiggy, Stackbox, Amazon, Apple. Microsoft, Meta/Facebook and many others. Everyone wants a better map (data), so everyone works together.
Ola could have gone their own route, bootstrapping map data from scratch, which would have been a gargantuan task when you re competing against the likes of Google Maps and Bing Maps, which have been into this since many years. Deciding to use OSM and actively giving back to make data better for everyone deserves accolades. Now I m waiting to for their second blog post, which they mention would be on map data.
If you re an Ola map user through Ola Electric or Ola app, and find some road unmapped, you can always edit them in OSM. What I have heard from their employee, they import new OSM data weekly, which means your changes should start reflecting for you (and everyone else) by next week. If you re new, follow Beginners guide and join OSM India community community.osm.be/resources/asia/india/ for any doubts and participating in various mapping events.
PS You can see live OSM edits in India subcontinent here.
Combining BGP confederations and AS override can potentially
create a BGP routing loop, resulting in an indefinitely expanding AS path.
BGP confederation is a technique used to reduce the number of iBGP sessions
and improve scalability in large autonomous systems (AS). It divides an AS into
sub-ASes. Most eBGP rules apply between sub-ASes, except that next-hop, MED, and
local preferences remain unchanged. The AS path length ignores contributions
from confederation sub-ASes. BGP confederation is rarely used and BGP route
reflection is typically preferred for scaling.
AS override is a feature that allows a router to replace the ASN of a
neighbor in the AS path of outgoing BGP routes with its own. It s useful when
two distinct autonomous systems share the same ASN. However, it interferes with
BGP s loop prevention mechanism and should be used cautiously. A safer
alternative is the allowas-in directive.1
In the example below, we have four routers in a single confederation, each in
its own sub-AS. R0 originates the 2001:db8::1/128 prefix. R1, R2, and
R3 forward this prefix to the next router in the loop.
BGP routing loop using a confederation
The router configurations are available in a Git repository. They are
running Cisco IOS XR. R2 uses the following configuration for BGP:
The session with R3 uses both as-override and next-hop-self directives.
The latter is only necessary to make the announced prefix valid, as there is no
IGP in this example.2
Here s the sequence of events leading to an infinite AS path:
R1 selects it as the best path, forwarding it to R2 with AS
path (64501 64500).
R2 selects it as the best path, forwarding it to R3 with AS
path (64500 64501 64502).
R3 selects it as the best path. It would forward it to R1 with AS path
(64503 64502 64501 64500), but due to AS override, it substitutes R1 s
ASN with its own, forwarding it with AS path (64503 64502 64503 64500).
R1 accepts the prefix, as its own ASN is not in the AS path. It compares
this new prefix with the one from R0. Both (64500) and (64503 64502
64503 64500) have the same length because confederation sub-ASes don t
contribute to AS path length. The first tie-breaker is the router ID.
R0 s router ID (1.0.0.4) is higher than R3 s (1.0.0.3). The new
prefix becomes the best path and is forwarded to R2 with AS path (64501
64503 64501 64503 64500).
R2 receives the new prefix, replacing the old one. It selects it as the
best path and forwards it to R3 with AS path (64502 64501 64502 64501
64502 64500).
R3 receives the new prefix, replacing the old one. It selects it as the
best path and forwards it to R0 with AS path (64503 64502 64503 64502
64503 64502 64500).
R1 receives the new prefix, replacing the old one. Again, it competes with
the prefix from R0, and again the new prefix wins due to the lower router
ID. The prefix is forwarded to R2 with AS path (64501 64503 64501 64503
64501 64503 64501 64500).
A few iterations later, R1 views the looping prefix as follows:4
RP/0/RP0/CPU0:R1#showbgpipv6u2001:db8::1/128bestpath-compare
BGP routing table entry for 2001:db8::1/128Last Modified: Jul 28 10:23:05.560 for 00:00:00Paths: (2 available, best #2) Path #1: Received by speaker 0 Not advertised to any peer (64500) 2001:db8::1:0 from 2001:db8::1:0 (1.0.0.4), if-handle 0x00000000 Origin IGP, metric 0, localpref 100, valid, confed-external Received Path ID 0, Local Path ID 0, version 0 Higher router ID than best path (path #2) Path #2: Received by speaker 0 Advertised IPv6 Unicast paths to peers (in unique update groups): 2001:db8::2:1 (64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64503 64502 64500) 2001:db8::4:0 from 2001:db8::4:0 (1.0.0.3), if-handle 0x00000000 Origin IGP, metric 0, localpref 100, valid, confed-external, best, group-best Received Path ID 0, Local Path ID 1, version 37 best of AS 64503, Overall best
There s no upper bound for an AS path, but BGP messages have size limits (4096
bytes per RFC 4271 or 65535 bytes per RFC 8654). At some
point, BGP updates can t be generated. On Cisco IOS XR, the BGP process crashes
well before reaching this limit.5
The main lessons from this tale are:
never use BGP confederations under any circumstances, and
be cautious of features that weaken BGP routing loop detection.
When using BGP confederations with Cisco IOS XR, use
allowconfedas-in instead. It s available since IOS XR 7.11.
Using BGP confederations is already inadvisable. If you don t use the
same IGP for all sub-ASes, you re inviting trouble! However, the scenario
described here is also possible with an IGP.
When an AS path segment is composed of ASNs from a confederation, it
is displayed between parentheses.
By default, IOS XR paces eBGP updates. This is controlled by the
advertisement-interval directive. Its default value is 30 seconds for eBGP
peers (even in the same confederation). R1 and R2 set this value to 0,
while R3 sets it to 2 seconds. This gives some time to watch the AS path
grow.
This is CSCwk15887. It only happens when using as-override on an
AS path with a too long AS_CONFED_SEQUENCE. This should be fixed around
24.3.1.
More than two years after I last uploaded the purity-off Debian
package, its autopkgtest (the Debian distribution-wide continuous
integration system) started failing on arm64, and only on this architecture.
The failing test
is very simple: it prints a long stream of "y" or "n"
characters to purity(6)'s
standard input and then checks the output for the expected result.
While investigating the live autopkgtest system, I figured out that:
The paging function of purity(6) became enabled, but only
on arm64!
Paging consumed more "y" characters from standard input
than the 5000 provided by the test script.
The paging code does not consider EOF a valid input, so at that point
it would start asking again and printing "--- more ---" forever in
a tight loop.
And this output, being redirected to a file, would fill the file
system where the autopkgtest is running.
I did not have time to verify this, but I have noticed that the
25 years old purity(6) program calls TIOCGWINSZ
to determine the screen length, and then uses the results in the
answer buffer without checking if the
ioctl(2)
call returned an error.
Which it obviously does in this case, because standard input is not a
console but a pipe.
So my theory is that paging is enabled because the undefined result of
the ioctl has changed, and only on this architecture.
Since I do not want to fix purity(6) right now, I have
implemented the workaround of printing many more "y"
characters as input.
apt-upgrade-canary is a helper program to alert when upgrading
packages via apt.
If there are some packages which causes a critical or serious
bug, it shows warnings for terminal.
Then you can stay on current version of package by canceling
upgrades.
This program is aimed to help not to installing
problematic packages via manual upgrades.
Usually, you should delegate package upgrade to
unattended-upgrades and apt-listbugs.
apt-listbugs kindly warns if there are known bugs.
In most cases it is enough safer.
But there is one exception, it is not true that always apt-listbugs
can follow very latest critical or serious bugs in timely manner.
apt-upgrade-canary checks UDD mirror database (it take into account
to cache query not to throw redundant one frequently)
Getting started
Install required packages.
$ sudo apt install -y make ruby-pg ruby-json ruby-term-ansicolor
Use case in action
If there is no serious bugs which is reported against target packages,
apt-upgrade-canary reports no error.
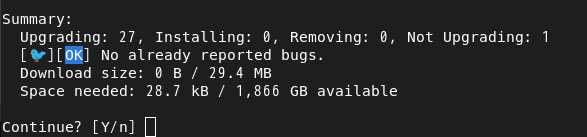
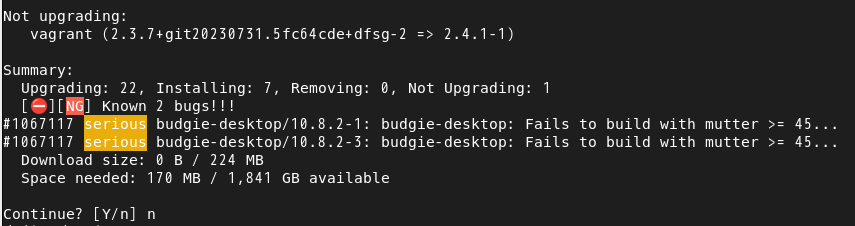
apt-upgrade-canary: no problem
If there are something weird happen, it reports matched bugs.
apt-upgrade-canary: serious case
So you can stay on.
A new minor release 0.4.23 of RQuantLib
just arrived at CRAN earlier
today, and will be uploaded to Debian in due course.
QuantLib is a rather
comprehensice free/open-source library for quantitative
finance. RQuantLib
connects (some parts of) it to the R environment and language, and has
been part of CRAN for more than
twenty-two years (!!) as it was one of the first packages I
uploaded.
This release of RQuantLib
updates to QuantLib version 1.35
released this morning. It accommodates some removals following earlier
deprecations, and also updates most of the code in the function for a
more readable and compact form of creating shared pointers via
make_shared() along with auto.
Changes in RQuantLib version 0.4.23 (2024-07-23)
Adjustments for QuantLib 1.35 and removal of deprecated code (in
utility functions and dividend case of vanilla options)
Adjustments for new changes in QuantLib 1.35
Refactoring most C++ files making more use of both
auto and make_shared to simplify and shorten
expressions
On the 18th of May I blogged about my new 5120*2160 monitor [1]. One thing I noted was that one Netflix movie had run in an aspect ratio that used all space on the monitor. I still don t know if the movie in question was cropped in a letterbox manner but other Netflix shows in full screen mode don t extend to both edges. Also one movie I downloaded as in 3840*1608 resolution which is almost exactly the same aspect ratio as my monitor. I wonder if some company is using 5120*2160 screens for TVs, 4K and FullHD are rumoured to be cheaper than most other resolutions partly due to TV technology being used for monitors. There is the Anamorphic Format of between 2.35:1 and 2.40:1 [2] which is a close match for the 2.37:1 of my new monitor.
I tried out the HDMI audio on a Dell laptop and my Thinkpad Yoga Gen3 and found it to be of poor quality, it seemed limited to 2560*1440, at this time I m not sure how much of the fault is due to the laptops and how much is due to the monitor. The monitor docs state that it needs HDMI version 2.1 which was released in 2017 and my Thinkpad Yoga Gen3 was released in 2018 so probably doesn t have that. The HDMI cable in question did 4K resolution on my previous monitor so it should all work at a minimum of 4K resolution.
The switching between inputs is a problem. If I switch between DisplayPort for my PC and HDMI for a laptop the monitor will usually timeout before the laptop establishes a connection and then switch back to the DisplayPort input. So far I have had to physically disconnect the input source I don t want to use. The DisplayPort switch that I ve used doesn t seem designed to work with resolutions higher than 4K.
I ve bought a new USB-C dock which is described as doing 8K which means that as my Thinkpad is described as supporting 5120 2880@60Hz over USB-C I should be able to get 5120*2160 without any problems, however for unknown reasons I only get 4K. For work I m using a Dell Latitude 7400 2in1 that s apparently only capable of 4096*2304 @24 Hz which is less pixels than 5120*2160 and it will also only do 4K resolution. But for both those cases it s still a significant improvement over 2560*1440. I tested with a Dell Latitude 7440 which gave the full 5120*2160 resolution, I was unable to find specs on what the maximum resolution of the 7440 is. I also have bought DisplayPort switch rated at 8K resolution. I got a switch that doesn t also do USB because the ones that do 8K resolution and USB are about $70. The only KVM switch I saw for 8K resolution at a reasonable price was one designed for switching between two laptops and there doesn t seem to be any adaptors to convert from regular DisplayPort to USB-C alternative mode so that wasn t viable. Currently I have the old KVM switch used for USB only (for keyboard and mouse) and the new switch which only does DisplayPort. So I have two buttons to push when switching between input sources which isn t too bad.
It seems that for PCs resolutions with more pixels than 4K are as difficult and inconvenient now as 4K was 6 years ago when I started doing it. If you want higher than 4K resolution to just work at this time then you need Apple hardware.
The monitor has a series of modes for different types of output, I ve found standard to be good for text and movie to be good for watching movies/TV and for playing RTS games. I previously wrote about how to use ddcutil to use a monitor as a KVM switch [3], unfortunately I can t do this with the new monitor as the time that the monitor waits for a good signal on a new input after changing is shorter than the time taken for Linux on the laptops I m using to enable HDMI output. I ve found the following commands to do the basics.
# get display mode
ddcutil getvcp DC
# set standard mode
ddcutil setvcp DC 0
# set movie mode
ddcutil setvcp DC 03
Now that I have that going the next thing I want to do is to have it switch between standard and movie modes when I switch keyboard focus.
The recent issue of Windows security software killing computers has reminded me about the issue of management software for Dell systems. I wrote policy for the Dell management programs that extract information from iDRAC and store it in Linux. After the break I ve pasted in the policy. It probably needs some changes for recent software, it was last tested on a PowerEdge T320 and prior to that was used on a PowerEdge R710 both of which are old hardware and use different management software to the recent hardware. One would hope that the recent software would be much better but usually such hope is in vain. I deliberately haven t submitted this for inclusion in the reference policy because it s for proprietary software and also it permits many operations that we would prefer not to permit.
The policy is after the break because it s larger than you want on a Planet feed. But first I ll give a few selected lines that are bad in a noteworthy way:
sys_admin means the ability to break everything
dac_override means break Unix permissions
mknod means a daemon creates devices due to a lack of udev configuration
sys_rawio means someone didn t feel like writing a device driver, maintaining a device driver for DKMS is hard and getting a driver accepted upstream requires writing quality code, in any case this is a bad sign.
self:lockdown is being phased out, but used to mean bypassing some integrity protections, that would usually be related to sys_rawio or similar.
dev_rx_raw_memory is bad, reading raw memory allows access to pretty much everything and execute of raw memory is something I can t imagine a good use for, the Reference Policy doesn t use this anywhere!
dev_rw_generic_chr_files usually means a lack of udev configuration as udev should do that.
storage_raw_write_fixed_disk shouldn t be needed for this sort of thing, it doesn t do anything that involves managing partitions.
Now without network access or other obvious ways of remote control this level of access while excessive isn t necessarily going to allow bad things to happen due to outside attack. But if there are bugs in the software there s nothing to stop it from giving the worst results.
The best thing that Dell could do for their customers is to make this free software and allow the community to fix some of these issues.
Here is dellsrvadmin.te:
Another thing to note is that include_directories adds both the source
directory and corresponding build directory to include path, so you don't
have to care.
It seems that I have to care after all.
Thankfully there is an implicit_include_directories setting
that can turn this off if needed.
Its documentation is not as easy to find as I'd like (kudos to Kangie on IRC),
and hopefully this blog post will make it easier for me to find it in the
future.
While I was living in Argentina, we (my family) found ourselves checking for
weather forecasts almost constantly weather there can be quite unexpected,
much more so that here in Mexico. So it took me a bit of tinkering to come up
with a couple of simple scripts to show the weather forecast as part of my
Waybar setup. I haven t cared to share
with anybody, as I believe them to be quite trivial and quite dirty.
But today, V ctor was asking for some slightly-related
things, so here I go. Please do
remember I warned: Dirty.
I am using OpenWeather s open
API. I had to register to get an APPID, and it
allows me for up to 1,000 API calls per day, more than plenty for my uses, even
if I am logged in at my desktops at three different computers (not an uncommon
situation). Having that, I set up a file named /etc/get_weather/, that
currently reads:
# Home, Mexico City
LAT=19.3364
LONG=-99.1819
# # Home, Paran , Argentina
# LAT=-31.7208
# LONG=-60.5317
# # PKNU, Busan, South Korea
# LAT=35.1339
#LONG=129.1055
APPID=SomeLongRandomStringIAmNotSharing
Then, I have a simple script, /usr/local/bin/get_weather, that fetches the
current weather and the forecast, and stores them as /run/weather.json and
/run/forecast.json:
#!/usr/bin/bashCONF_FILE=/etc/get_weather
if[-e"$CONF_FILE"];then."$CONF_FILE"else
echo"Configuration file $CONF_FILE not found"exit 1
fi
if[-z"$LAT"-o-z"$LONG"-o-z"$APPID"];then
echo"Configuration file must declare latitude (LAT), longitude (LONG) "echo"and app ID (APPID)."exit 1
fi
CURRENT=/run/weather.json
FORECAST=/run/forecast.json
wget -q"https://api.openweathermap.org/data/2.5/weather?lat=$ LAT&lon=$ LONG&units=metric&appid=$ APPID"-O"$ CURRENT"
wget -q"https://api.openweathermap.org/data/2.5/forecast?lat=$ LAT&lon=$ LONG&units=metric&appid=$ APPID"-O"$ FORECAST"
This script is called by the corresponding systemd service unit, found at
/etc/systemd/system/get_weather.service:
[Unit]
Description=Get the current weather
[Service]
Type=oneshot
ExecStart=/usr/local/bin/get_weather
And it is run every 15 minutes via the following systemd timer unit,
/etc/systemd/system/get_weather.timer:
[Unit]
Description=Get the current weather every 15 minutes
[Timer]
OnCalendar=*:00/15:00
Unit=get_weather.service
[Install]
WantedBy=multi-user.target
(yes, it runs even if I m not logged in, wasting some of my free API
calls but within reason)
Then, I declare a "custom/weather" module in the desired position of my
~/.config/waybar/waybar.config, and define it as:
This script basically morphs a generic weather JSON description into another set
of JSON bits that display my weather in the way I prefer to have it displayed
as:
#!/usr/bin/rubyrequire'json'Sources=:weather=>'/run/weather.json',:forecast=>'/run/forecast.json'Icons='01d'=>' ',# d day'01n'=>' ',# n night'02d'=>' ','02n'=>' ','03d'=>' ','03n'=>' ','04d'=>' ','04n'=>' ','09d'=>' ','10n'=>' ','10d'=>' ','13d'=>' ','50d'=>' 'ret='text':nil,'tooltip':nil,'class':'weather','percentage':100# Current weather report: Main text of the modulebeginweather=JSON.parse(open(Sources[:weather],'r').read)loc_name=weather['name']icon=Icons[weather['weather'][0]['icon']]' '+f['weather'][0]['icon']+f['weather'][0]['main']temp=weather['main']['temp']sens=weather['main']['feels_like']hum=weather['main']['humidity']wind_vel=weather['wind']['speed']wind_dir=weather['wind']['deg']portions=portions[:loc]=loc_nameportions[:temp]='%s %2.2f C (%2.2f)'%[icon,temp,sens]portions[:hum]=' %2d%%'%humportions[:wind]=' %2.2fm/s %d '%[wind_vel,wind_dir]ret['text']=[:loc,:temp,:hum,:wind].mappportions[p] .join(' ')rescue=>errret['text']='Could not process weather file (%s %s: %s)'%[Sources[:weather],err.class,err.to_s]end# Weather prevision for the following hours/daysbegincast=[]forecast=JSON.parse(open(Sources[:forecast],'r').read)min=''max=''day=Time.now.strftime('%Y.%m.%d')by_day=forecast['list'].each_with_indexdof,iby_day[day] =[]time=Time.at(f['dt'])time_lbl='%02d:%02d'%[time.hour,time.min]icon=Icons[f['weather'][0]['icon']]' '+f['weather'][0]['icon']+f['weather'][0]['main']by_day[day]<<f['main']['temp']iftime.hour==0min='%2.2f'%by_day[day].minmax='%2.2f'%by_day[day].maxcast<<' min: <b>%s C</b> max: <b>%s C</b>'%[min,max]day=time.strftime('%Y.%m.%d')cast<<' <b>%04d.%02d.%02d</b> '%[time.year,time.month,time.day]endcast<<'%s %2.2f C %2d%% %s %s'%[time_lbl,f['main']['temp'],f['main']['humidity'],icon,f['weather'][0]['description']]endcast<<' min: <b>%s</b> C max: <b>%s C</b>'%[min,max]ret['tooltip']=cast.join("\n")rescue=>errret['tooltip']='Could not process forecast file (%s %s)'%[Sources[:forecast],err.class,err.to_s]end# Print out the result for Waybar to processputsret.to_json
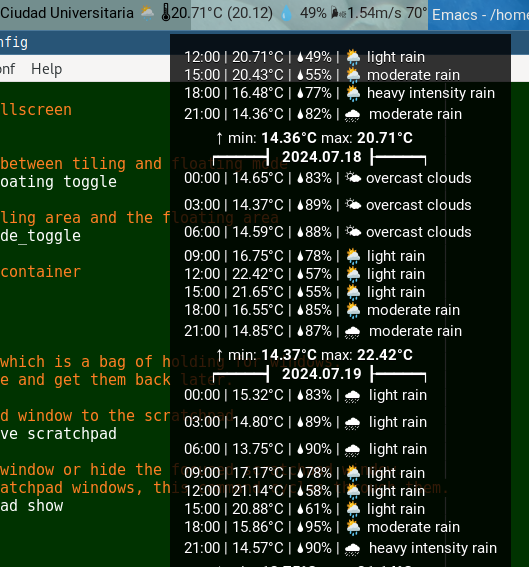
The end result? Nothing too stunning, but definitively something I find useful
and even nicely laid out:
Do note that it seems OpenWeather will return the name of the closest available
meteorology station with (most?) recent data for my home, I often get Ciudad
Universitaria, but sometimes Coyoac n or even San ngel Inn.
Lomiri Weather App goes Open Meteo
In Ubuntu Touch / Lomiri, Maciej Sopy o has updated Lomiri's Weather App to operate against a different weather forecast provider (Open Meteo). Additionally, the new implementation is generic and pluggable, so other weather data providers can be added-in later.
Big thanks to Maciej for working on this just in time (the previous implementation's API has recently been EOL'ed and is not available anymore to Ubuntu Touch / Lomiri users).
Lomiri Weather App - new Meteorological Terms part of the App now
While the old weather data provider implementation obtained all the meteorological information as already localized strings from the provider, the new implementation requires all sorts of weather conditions being translated within the Lomiri Weather App itself.
The meteorological terms are probably not easy to translate for the usual software translator, so special help might be required here.
Call for Translations: Lomiri Weather App
So, if you feel entitled to help here, please join the Hosted Weblate service [1] and start working on Lomiri Weather App.
Thanks a lot!
light+love
Mike Gabriel (aka sunweaver)
[1] https://hosted.weblate.org/
[2] https://hosted.weblate.org/projects/lomiri/lomiri-weather-app/
After the VoLTE saga [1] and the problems with battery life on the PinePhonePro [2] (which lasted 4 hours while idle with the screen off in my last test a few weeks ago) I m running a Galaxy Note 9 [3] with the default Samsung OS as my daily driver.
I don t think that many people will be rushing out to buy a 2018 phone regardless of my review. For someone who wants a phone of such age (which has decent hardware and a low price) then good options are the Pixel phones which are all supported by LineageOS.
I recommend not buying this phone due to the fact that it doesn t have support for VoLTE with LineageOS (and presumably any other non-Samsung Android build) and doesn t have support from any other OS. The One Plus 6/6T has Mobian support [4] as well as LineageOS support and is worth considering.
The Note 9 still has capable hardware by today s standards. A 6.4 display is about as big as most people want in their pocket and 2960 1440 resolution in that size (516dpi) is probably as high as most people can see without a magnifying glass. The model I m using has 8G of RAM which is as much as the laptop I was using at the start of this year. I don t think that many people will have things that they actually want to do on a phone which needs more hardware than this. The only hardware feature in new phones which beats this is the large folding screen in some recent phones, but $2500+ (the price of such phones in Australia) is too much IMHO and the second hand market for folding phones is poor due to the apparently high incidence of screens breaking.
The Note 9 has the Dex environment for running as a laptop if you connect it to a USB-C dock. It can run nicely with a 4K monitor with USB keyboard and mouse. The UI is very similar to that of older versions of Windows.
The Samsung version of Android seems mostly less useful than the stock Google version or the LineageOS version. The Samsung keyboard flags words such as gay as spelling errors and it can t be uninstalled even when you install a better keyboard app. There is a Bixby button on the side of the phone to launch the Bixby voice recognition app which can t be mapped to any useful purpose, The Google keyboard has a voice dictation option which I will try out some time but that s all I desire in terms of voice recognition. There are alerts about Samsung special deals and configuration options including something about signing in to some service and having it donate money to charity, I doubt that any users want such features. Apart from Dex the Samsung Android build is a good advert for LineageOS.
The screen has curved sides for no good reason. This makes it more difficult to make a protective phone case as a case can t extend beyond the screen at the sides and therefore if it s dropped and hits an edge (step, table, etc) then the glass can make direct contact with something. Also the curved sides reflect sunlight in all directions, this means that the user has to go to more effort to avoid reflecting the sun into their eyes and that a passenger can more easily reflect sunlight into the eyes of a car driver. It s an impressive engineering feat to make a curved touch-screen but it doesn t do any good for users.
The stylus is good as always and the screen is AMOLED so it doesn t waste much power when in dark mode. There is a configuration option to display a clock all the time when the screen is locked because that apparently doesn t use much power. I haven t felt inclined to enable the always on screen but it s a nice feature for those who like such things.
The VoLTE implementation is apparently a bit unusual so it s not supported by LineageOS and didn t work on Droidian for the small amount of time that Droidian supported it.
Generally this phone is quite nice hardware it s just a pity that it demonstrates all of the downsides to buying a non-Pixel phone.
I just got one of those utterly funny spam messages And yes, I recognize
everybody likes building a name for themselves. But some spammers are downright
silly.
I just got the following mail:
From: Hermine Wolf <hwolf850@gmail.com>
To: me, obviously
Date: Mon, 15 Jul 2024 22:18:58 -0700
Subject: Make sure that your manuscript gets indexed and showcased in the prestigious Scopus database soon.
Message-ID: <CAEZZb3XCXSc_YOeR7KtnoSK4i3OhD=FH7u+A5xSMsYvhQZojQA@mail.gmail.com>
This message has visual elements included. If they don't display, please
update your email preferences.
*Dear Esteemed Author,*
Upon careful examination of your recent research articles available online,
we are excited to invite you to submit your latest work to our esteemed
journal, '*WULFENIA*'. Renowned for upholding high standards of excellence
in peer-reviewed academic research spanning various fields, our journal is
committed to promoting innovative ideas and driving advancements in
theoretical and applied sciences, engineering, natural sciences, and social
sciences. 'WULFENIA' takes pride in its impressive 5-year impact factor of
*1.000* and is highly respected in prestigious databases including the
Science Citation Index Expanded (ISI Thomson Reuters), Index Copernicus,
Elsevier BIOBASE, and BIOSIS Previews.

*Wulfenia submission page:*
[image: research--check.png][image: scrutiny-table-chat.png][image:
exchange-check.png][image: interaction.png]
.
Please don't reply to this email

We sincerely value your consideration of 'WULFENIA' as a platform to
present your scholarly work. We eagerly anticipate receiving your valuable
contributions.
*Best regards,*
Professor Dr. Vienna S. Franz
Who cares what Wulfenia is about? It s about you, my stupid Wolf cousin!
Prior to arrival in Kenya, you need to apply for an Electronic Travel Authorization (eTA) on their website by uploading all the required documents. This system is in place since Jan 2024 after the country abolished the visa system, implementing the eTA portal. The required documents will depend on the purpose of your visit, which in my case, was to attend a conference.
Here is the list of documents I submitted for my eTA:
Scanned copy of my passport
Photograph with white background
Flight tickets (reservation)
Hotel bookings (reservation)
Invitation letter from the conference
Yellow Fever vaccination certificate (optional)
Job contract (optional)
Reservation means I didn t book the flights and hotels, but rather reserved them. Additionally, optional means that those documents were not mandatory to submit, but I submitted them in the Other Documents section in order to support my application. After submitting the eTA, I had to make a payment of around 35 US Dollars (approximately 3000 Indian Rupees).
It took 40 hours for me to receive an email from Kenya stating that my eTA has been approved, along with an attached PDF, making this one of my smoothest experiences of obtaining travel documents to travel to a country :). An eTA is technically not a visa, but I put the word visa in the title due to familiarity with the term.
Twenty years ago, it was easy to dislike Microsoft. It was the quintessential evil MegaCorp that was quick to squash competition, often ruthlessly, but in some cases slowly through a more insidious process of embracing, extending, and exterminating anything that got in the way. This was the signature personality of Ballmer-era Microsoft that also inspired and united the software freedom fighting forces that came together to safeguard things that mattered to them and were at risk.I remember the era when the Novell, SCO, and Microsoft saga cast fear, uncertainty, and doubt on the future of open Unix and Linux and on what would happen to the operating systems that we loved if the suits of Redmond prevailed. Looking back, I&aposm glad that the arc of this story has bent towards justice, and I shudder at the possibilities had it worked out differently.Looking at today&aposs Microsoft, I&aposm amazed at how much change a leader with the right vision can make to the trajectory of a company that even makes an old-school software freedom advocate as me admire and even applaud the strides it has taken in the last 10 or so years that has dramatically shifted the perception of Microsoft. The personality of the Satya-era Microsoft is one to behold. While it will take more time to win back the trust, we see the tides changing and the positivity is important for the entire industry.For Microsoft, it was TypeScript and VS Code that helped change the narrative internally which led to its internal resurgence and acceptance of open source. Its acquisition of GitHub propelled it forward within the community overnight. Its contributions to the Linux kernel and other major software projects have also been consequential in changing its public perceptions.It takes a while to claw back trust and is very easy to breach. This time, however, Microsoft seems to understand this dynamic more than it did 20 years ago. All it took was the right leadership.
Welcome to the June 2024 report from the Reproducible Builds project!
In our reports, we outline what we ve been up to over the past month and highlight news items in software supply-chain security more broadly. As always, if you are interested in contributing to the project, please visit our Contribute page on our website.
Table of contents:
Next Reproducible Builds Summit dates announced
We are very pleased to announce the upcoming Reproducible Builds Summit, set to take place from September 17th 19th 2024 in Hamburg, Germany.
We are thrilled to host the seventh edition of this exciting event, following the success of previous summits in various iconic locations around the world, including Venice, Marrakesh, Paris, Berlin and Athens. Our summits are a unique gathering that brings together attendees from diverse projects, united by a shared vision of advancing the Reproducible Builds effort. During this enriching event, participants will have the opportunity to engage in discussions, establish connections and exchange ideas to drive progress in this vital field. Our aim is to create an inclusive space that fosters collaboration, innovation and problem-solving.
If you re interesting in joining us this year, please make sure to read the event page which has more details about the event and location. We are very much looking forward to seeing many readers of these reports there.
GNU Guix patch review session for reproducibility
Vagrant Cascadian will be holding a Reproducible Builds session as part of the monthly Guix patch review series on July 11th at 17:00 UTC.
These online events are intended to encourage everyone everyone becoming a patch reviewer and the goal of reviewing patches is to help Guix project accept contributions while maintaining our quality standards and learning how to do patch reviews together in a friendly hacking session.
New reproducibility-related academic papers
Multiple scholarly papers related to Reproducible Builds were published this month:
An Industry Interview Study of Software Signing for Supply Chain Security was published by Kelechi G. Kalu, Tanmay Singla, Chinenye Okafor, Santiago Torres-Arias and James C. Davis of Electrical and Computer Engineering department of Purdue University, Indiana, USA, and is concerned with:
To understand software signing in practice, we interviewed 18 high-ranking industry practitioners across 13 organizations. We provide possible impacts of experienced software supply chain failures, security standards, and regulations on software signing adoption. We also study the challenges that affect an effective software signing implementation.
Code signing enables software developers to digitally sign their code using cryptographic keys, thereby associating the code to their identity. This allows users to verify the authenticity and integrity of the software, ensuring it has not been tampered with. Next-generation software signing such as Sigstore and OpenPubKey simplify code signing by providing streamlined mechanisms to verify and link signer identities to the public key. However, their designs have vulnerabilities: reliance on an identity provider introduces a single point of failure, and the failure to follow the principle of least privilege on the client side increases security risks. We introduce Diverse Identity Verification (DiVerify) scheme, which strengthens the security guarantees of next-generation software signing by leveraging threshold identity validations and scope mechanisms.
[ ] resulted in an extension of GNU make which is called rmake, where diffoscope a tool for detecting differences between a large number of file types was integrated into the workflow of make. rmake was later used to answer the posed research questions for this thesis. We found that different build paths and offsets are a big problem as three out of three tested Free and Open Source Software projects all contained these variations. The results also showed that gcc s optimisation levels did not affect reproducibility, but link-time optimisation embeds a lot of unreproducible information in build artefacts. Lastly, the results showed that build paths, build ID s and randomness are the three most common groups of variations encountered in the wild and potential solutions for some variations were proposed.
The thesis serves as an introduction to the concept of reproducibility in software engineering, offering a comprehensive overview of formalizations using mathematical notations for key concepts and an empirical evaluation of several key tools. By exploring various case studies, methodologies and tools, the research aims to provide actionable insights for practitioners and researchers alike.
Development news
In Debian this month, 4 reviews of Debian packages were added, 11 were updated and 14 were removed this month adding to our knowledge about identified issues. Only one issue types was updated, though, explaining that we don t vary the build path anymore.
On our mailing list this month, Bernhard M. Wiedemann wrote that whilst he had previously collected issues that introduce non-determinism he has now moved on to discuss about mitigations , in the sense of how can we avoid whole categories of problem without patching an infinite number of individual packages . In addition, Janneke Nieuwenhuizen announced the release of two versions of GNU Mes. [][]
In openSUSE news, Bernhard M. Wiedemann published another report for that distribution.
In NixOS, with the 24.05 release out, it was again validated that our minimal ISO is reproducible by building it on a virtual machine with no access to the binary cache.
What s more, we continued to write patches in order to fix specific reproducibility issues, including Bernhard M. Wiedemann writing three patches (for qutebrowser, samba and systemd), Chris Lamb filing Debian bug #1074214 against the fastfetch package and Arnout Engelen proposing fixes to refind and for the Scala compiler [.
Lastly, diffoscope is our in-depth and content-aware diff utility that can locate and diagnose reproducibility issues. This month, Chris Lamb uploaded two versions (270 and 271) to Debian, and made the following changes as well:
Drop Build-Depends on liblz4-tool in order to fix Debian bug #1072575. []
Update tests to support zipdetails version 4.004 that is shipped with Perl 5.40. []
Website updates
There were a number of improvements made to our website this month, including Akihiro Suda very helpfully making the <h4> elements more distinguishable from the <h3> level [][] as well as adding a guide for Dockerfile reproducibility []. In addition Fay Stegerman added two tools, apksigcopier and reproducible-apk-tools, to our Tools page.
Reproducibility testing framework
The Reproducible Builds project operates a comprehensive testing framework running primarily at tests.reproducible-builds.org in order to check packages and other artifacts for reproducibility. In June, a number of changes were made by Holger Levsen, including:
Marking the virt(32 64)c-armhf nodes as down. []
Granting a developer access to the osuosl4 node in order to debug a regression on the ppc64el architecture. []
Granting a developer access to the osuosl4 node. [][]
In addition, Mattia Rizzolo re-aligned the /etc/default/jenkins file with changes performed upstream [] and changed how configuration files are handled on the rb-mail1 host. [], whilst Vagrant Cascadian documented the failure of the virt32c and virt64c nodes after initial investigation [].
If you are interested in contributing to the Reproducible Builds project, please visit our Contribute page on our website. However, you can get in touch with us via:
 Dear Debian community,
this are my bits from DPL written at my last day at another great
DebConf.
DebConf attendance
At the beginning of July, there was some discussion with the bursary and
content team about sponsoring attendees. The discussion continued at
DebConf.
I do not have much experience with these discussions. My summary is that
while there is an honest attempt to be fair to everyone, it did not seem to
work for all, and some critical points for future discussion remained. In
any case, I'm thankful to the bursary team for doing such a time-draining
and tedious job.
Popular packages not yet on Salsa at all
Otto Kek l inen did some interesting investigation about
Popular packages not yet on Salsa at all.
I think I might provide some more up to date list soon by some UDD query
which considers more recent uploads than the trends data soon. For
instance wget was meanwhile moved to Salsa (thanks to No l K the for this).
Keep on contacting more teams
I kept on contacting teams in July. Despite I managed to contact way
less teams than I was hoping I was able to present some conclusions in
the Debian Teams exchange BoF and Slide 16/23 of my
Bits from the DPL talk.
I intend to do further contacts next months.
Nominating Jeremy B cha for GNOME Advisory Board
I've nominated Jeremy B cha to
GNOME Advisory Board.
Jeremy has volunteered to represent Debian at
GUADEC in Denver.
DebCamp / DebConf
I attended DebCamp starting from 22 July evening and had a lot of fun with
other attendees. As always DebConf is some important event nearly
every year for me. I enjoyed Korean food, Korean bath, nature at the
costline and other things.
I had a small event without video coverage
Creating web galleries including maps from a geo-tagged photo collection.
At least two attendees of this workshop confirmed success in creating their
own web galleries.
I used DebCamp and DebConf for several discussions. My main focus was on
discussions with FTP master team members Luke Faraone, Sean Whitton, and
Utkarsh Gupta. I'm really happy that the four of us absolutely agree on
some proposed changes to the structure of the FTP master team, as well
as changes that might be fruitful for the work of the FTP master team
itself and for Debian developers regarding the processing of new
packages.
My explicit thanks go to Luke Faraone, who gave a great introduction to
FTP master work in their
BoF.
It was very instructive for the attending developers to understand how the
FTP master team checks licenses and copyright and what workflow is used
for accepting new packages.
In the first days of DebConf, I talked to representatives of DebConf
platinum sponsor WindRiver, who announced the derivative
eLxr. I warmly welcome
this new derivative and look forward to some great cooperation. I also
talked to the representative of our gold sponsor, Microsoft.
My first own event was the
Debian Med BoF.
I'd like to repeat that it might not only be interesting for people
working in medicine and microbiology but always contains some hints how
to work together in a team.
As said above I was trying to summarise some first results of my team
contacts and got some further input from other teams in the
Debian Teams exchange BoF.
Finally, I had my
Bits from DPL talk.
I received positive responses from attendees as well as from remote
participants, which makes me quite happy. For those who were not able to
join the events on-site or remotely, the videos of all events will be
available on the DebConf site soon. I'd like to repeat the explicit need
for some volunteers to join the Lintian team. I'd also like to point out
the "Tiny tasks" initiative I'd like to start (see below).
BTW, if someone might happen to solve my quiz for the background images
there is a
summary page
in my slides which might help to assign every slide to some DebConf. I
could assume that if you pool your knowledge you can solve more than just
the simple ones. Just let me know if you have some solution. You can add
numbers to the rows and letters to the columns and send me:

 You can also see it in:
 A new minor release 0.4.24 of
 It s not often that a company is willing to make

 More than two years after I last uploaded the
 apt-upgrade-canary is a helper program to alert when upgrading
packages via apt.
If there are some packages which causes a critical or serious
bug, it shows warnings for terminal.
Then you can stay on current version of package by canceling
upgrades.
This program is aimed to help not to installing
problematic packages via manual upgrades.
Usually, you should

 While I was living in Argentina, we (my family) found ourselves checking for
weather forecasts almost constantly weather there can be quite unexpected,
much more so that here in Mexico. So it took me a bit of tinkering to come up
with a couple of simple scripts to show the weather forecast as part of my
 I am using
 Do note that it seems OpenWeather will return the name of the closest available
meteorology station with (most?) recent data for my home, I often get Ciudad
Universitaria, but sometimes Coyoac n or even San ngel Inn.
 Lomiri Weather App goes Open Meteo
In Ubuntu Touch / Lomiri, Maciej Sopy o has updated Lomiri's Weather App to operate against a different weather forecast provider (Open Meteo). Additionally, the new implementation is generic and pluggable, so other weather data providers can be added-in later.
Big thanks to Maciej for working on this just in time (the previous implementation's API has recently been EOL'ed and is not available anymore to Ubuntu Touch / Lomiri users).
Lomiri Weather App - new Meteorological Terms part of the App now
While the old weather data provider implementation obtained all the meteorological information as already localized strings from the provider, the new implementation requires all sorts of weather conditions being translated within the Lomiri Weather App itself.
The meteorological terms are probably not easy to translate for the usual software translator, so special help might be required here.
Call for Translations: Lomiri Weather App
So, if you feel entitled to help here, please join the Hosted Weblate service [1] and start working on Lomiri Weather App.
Thanks a lot!
light+love
 Who cares what Wulfenia is about? It s about you, my stupid Wolf cousin!
 Twenty years ago, it was easy to dislike Microsoft. It was the quintessential evil MegaCorp that was quick to squash competition, often ruthlessly, but in some cases slowly through a more insidious process of embracing, extending, and exterminating anything that got in the way. This was the signature personality of Ballmer-era Microsoft that also inspired and united the software freedom fighting forces that came together to safeguard things that mattered to them and were at risk.I remember the era when the Novell, SCO, and Microsoft saga cast fear, uncertainty, and doubt on the future of open Unix and Linux and on what would happen to the operating systems that we loved if the suits of Redmond prevailed. Looking back, I&aposm glad that the arc of this story has bent towards justice, and I shudder at the possibilities had it worked out differently.Looking at today&aposs Microsoft, I&aposm amazed at how much change a leader with the right vision can make to the trajectory of a company that even makes an old-school software freedom advocate as me admire and even applaud the strides it has taken in the last 10 or so years that has dramatically shifted the perception of Microsoft. The personality of the Satya-era Microsoft is one to behold. While it will take more time to win back the trust, we see the tides changing and the positivity is important for the entire industry.For Microsoft, it was TypeScript and VS Code that helped change the narrative internally which led to its internal resurgence and acceptance of open source. Its acquisition of GitHub propelled it forward within the community overnight. Its contributions to the Linux kernel and other major software projects have also been consequential in changing its public perceptions.It takes a while to claw back trust and is very easy to breach. This time, however, Microsoft seems to understand this dynamic more than it did 20 years ago. All it took was the right leadership.