Search Results: "xam"

5 March 2006

Uwe Hermann: HOWTO: Anonymous communication with Tor - some hints and some pitfalls [Update]

Warning: Very long post ahead. You have been warned! What? Tor is a Free Software project (revised BSD license), developed by Roger Dingledine and Nick Mathewson, which creates an infrastructure for anonymous TCP communication. From the project website:
Tor is a toolset for a wide range of organizations and people that want to improve their safety and security on the Internet. Using Tor can help you anonymize web browsing and publishing, instant messaging, IRC, SSH, and other applications that use the TCP protocol. Tor also provides a platform on which software developers can build new applications with built-in anonymity, safety, and privacy features. Tor aims to defend against traffic analysis, a form of network surveillance that threatens personal anonymity and privacy, confidential business activities and relationships, and state security. Communications are bounced around a distributed network of servers called onion routers, protecting you from websites that build profiles of your interests, local eavesdroppers that read your data or learn what sites you visit, and even the onion routers themselves.
Tor also allows you to set up and/or use a so-called Tor hidden service, i.e., a server which offers some service (a website, ssh access, or similar) without revealing its IP to its users. Why? Why would you want to use Tor? Well, because you probably don't want anybody (neither state agencies, nor companies, nor "hackers", nor any other individuals or groups) to be able to record, analyze, and (ab)use information about your web browsing habits, or any other communication habits. For instance, you don't want Google to have a complete search-profile of you, which — even worse — might some day get in the hands of other parties. In the days of massive data retention you don't want all your electronic traces to be recorded, stored for ages, analyzed, and data-mined for dubious reasons and with even more dubious results and false conclusions drawn which might negatively affect you. If you're a human rights activist in China, you want anonymous communication. If you're a whistleblower, you want anonymous communication. The list is endless. For securing your communications, so that nobody is able to sniff your emails, your chat messages, your passwords, your private documents and conversations, you use encryption. For communicating anonymously you can use Tor. Combine both, and you have secure and anonymous communication. In case you're wondering whether criminals might abuse Tor, read the Tor Abuse FAQ. Short answer: yes, but if you're willing to break the law, you already have anonymity (open access points, stolen/prepaid mobile phones, etc.). You don't need Tor to do bad things if you're a criminal. If you're one of those horrible "oh, but I don't have anything to hide" guys, consider this: Say you have a drug/alcohol problem and want to visit an anti-drugs/anti-alcohol website or forum for help. Would you want the whole world, your neighbors, your co-workers, your boss, to know that, or would you rather want to keep that a secret? Say you have AIDS and want to get information on the web? Or, to make the example even more dramatic: Would you want some random guys to be able to watch you while you fuck your wife? No? So you have something to hide after all, right? My point is: Everyone has something to hide, even more, it is a basic human right to have the ability to hide something. It's called privacy. How? Tor implements a form of onion routing to, basically, push encrypted data through multiple Tor nodes (servers), before it reaches the final destination (e.g. a website). The result is that neither the website owner, nor a local eavesdropper, nor any single Tor server knows who requested that specific website, hence you are communicating anonymously. For more technical details, read the Tor overview and the Tor documentation pages. In order to use Tor, you have to install and run a local Tor client/daemon (this is not necessarily a Tor server!). On Debian, type apt-get install tor, on other systems you can get the respective binary packages or download the sources and compile Tor yourself. Usually Tor is used together with Privoxy, a configurable HTTP proxy which sanitizes your web-browsing experience by removing nasty banner ads, pop-ups, JavaScript, webbugs, cookies etc. etc. So: apt-get install privoxy. After installing and starting Tor and Privoxy, you can now configure your webbrowser to use Privoxy as an HTTP proxy (see below), and Privoxy will in turn use Tor to anonymize your communication if you add "forward-socks4a / localhost:9050 ." to your /etc/privoxy/config. Anonymizing various applications Most (but not all) of the following information is also covered in the very useful Torify HOWTO in the Tor wiki (I will add the missing information there, ASAP). As I'm pretty paranoid, I have checked every single of these configurations with Ethereal to ensure that the traffic is really anonymized. However, if you are paranoid, you shouldn't trust me, but rather test this stuff for yourself! Warning: DNS Leaks:
The biggest problem with many applications is that they leak DNS requests. That is, although they use Tor to anonymize the traffic, they first send a DNS request untorified in order to get the IP address of the target system. Then they communicate "anonymously" with that target. The problem: any eavesdropper with more than three brain cells can conclude what website you visited, if they see that you send a DNS request for rsf.org, followed by some "anonymous" Tor traffic. The solution: use Tor together with Privoxy, that prevents DNS leaks. Many non-HTTP-based applications are usually torified using a small tool called torify (e.g. by typing torify fetchmail), but often this approach has DNS leaking problems, see below. You might also want to check out toraliases, a small shell script you can source from your ~/.bashrc file. It defines some functions and aliases which transparently direct the traffic of some (but not all!) programs through Tor. Applications which cannot easily be torified Anything not using TCP usually cannot be torified, as Tor only works for TCP. Pitfalls to be aware of More information More information is available in the Tor documentation, the Tor wiki, and especially in the Tor FAQ. In addition, there's an IRC channel on Freenode (#tor), some slides and a video (torrent) about Tor you might find interesting. If you would like to help, you can run a Tor server, donate some money, or volunteer to do other things (code, debug, document, translate, and more). That's it for now. I'm very grateful for comments and suggestions, especially for hints on how to anonymize more applications. Also, if you notice any dumb mistakes I made, please leave a comment. Update 2006-03-07: Fixed typos, added link to the toraliases project (thanks Benjamin Schieder).

David Nusinow: OMG Planet Conversation!

Josselin, I agree with you in theory, but the problem is that heated technical discussions quickly turn personal. debian-x is one shining example of this, where the previous fighting was over whether to polish and bring out the best possible packages we could or to push hard to get the newest releases in, which while not being as well done would get people support for new hardware. Fundamentally, this is a technical debate, but it turned very personal over time and the team still bears these scars. This has also happened in incredibly ugly ways on debian-devel, with vile threads from the past like "Serious Problems With Mr. Troup", which is about as personal as you can get. The Vancouver thread also took very serious personal turns as well, despite it beginning as a necessary discussion about the release process.

Momentum is critical for minimizing these kinds of debates, but it's not foolproof. I think a code of conduct along with people who are trusted and willing to enforce it will provide an extra layer of protection against this problem. Yes, I definitely agree with you that technical solutions and hard work are the critical things. It's critical to have technical solutions to technical problems, and these should always be the first priority for Debian. But a social layer of a mailing list code of conduct, much like our social contract and the DFSG, will provide a non-technical solution that can help guide us when things get ugly. I, for one, never want to see another "Serious Problems With Mr. Troup" thread.

4 March 2006

Josselin Mouette: Making fun of people is bad...

... but sometimes you just can't hold on.

Mike Hearn, author of the wonderful autopackage installation software - the one that's breaking your distribution by overwriting files installed by the package manager - has been entertaining me these days. After claiming to have "designed a versioning scheme" that he compared to ELF, he started a flamewar about how Debian likes to break upstream's software - without any relevant example so far. Interestingly, this thread also showed there are still some people to believe D.J. Bernstein's teachings can be useful.

His latest blog entry really made my day. After complaining about people not using autopackage enough (guess why), he started again to claim Debian is breaking upstream's software, with finally one example: the user-agent in Xulrunner being broken. A bug in the first public release of the package. Just like we didn't fix bugs...

1 March 2006

Clint Adams: Secret Changes to Blog Entry

It has come to my attention that AJ has made some updates. He says,
Of course, the two responses above are fundamentally contradictory: if Clint's right a ban (or similar) would've been appropriate, in spite of Joerg's claim. On the other hand, Google's sole definition of "snarky" seems to be "A colloquialism meaning short-tempered or snappish." which doesn't seem terribly applicable here -- however short tempered anyone was, anon left before anyone had a chance to lose theirs. Sadly, the rest of Clint's epithet assumes you've got some idea what the problem is in the first place.
Apparently I've been too cryptic, so I will attempt to rectify that slightly. The episode begins, I believe, with Anthony invoking a reference to secret changes . Ryan perpetuates the joking. Matt acknowledges the Sneakers reference, though it could have been interpreted as approval of the discourteous and disrespectful banter. anon expresses his confusion about this apparent disparity between the charter of the channel and what is occurring in practice. Ryan implies by inquiry that no such discrepancy exists. anon , clearly frustrated, storms off in a huff. Anthony cites this occurrence in his blog. As far as I am aware, none of the channel moderators listed on the Charter have made their opinions known publicly. In other examples, we see Anthony wielding the Charter as a threatening weapon. In this case, we see a failure to self-censor. It does not surprise me at all that someone would not want to put up with this. So I am not saying that either AJ or Ryan or Matt should have been banned for this; that would seem rather extreme and unproductive. I am saying that I have little faith in the #debian-tech team to enforce things fairly.

Anthony Towns: The Joy of Ranting

Joey replies to my post from yesterday with his own example of leaving:
The technical details remain as irrelivant today as they were at the time, the relevant problem being that developers who are not involved in the installer development rarely consider how their actions can affect it. When a policy gets int the way of solving a problem, it’s time to leave, that’s all.
His posted logs suffer from unescaped angle brackets so aren’t very easy to follow; and also from the fact that for rather obvious reasons they don’t include any of the conversation that took place after he left. Extended logs and the other side of that story below the fold: Read the rest ...

28 February 2006

Joey Hess: why I'm not on #debian-tech

So, I guess this is an example of the sort of self-recusement from debian-tech that aj is <a href="http://azure.humbug.org.au/~aj/blog/2006/02/28#2006-02-28-debiantech">referring to: @1130344829 <joeyh!joey@kitenet.net> aj: sigh, did you realy have to break d-i yet again right as we're trying ot release it?
@1130344847 <aj!aj-irc@azure.humbug.org.au> ?
@1130344881 <aj!aj-irc@azure.humbug.org.au> joeyh: (also, please try to avoid making things overly personal on this channel, cf the charter)
@1130344919 <joeyh!joey@kitenet.net> fine, did one have to ignore the d-i release and make a package upload with lots of changes that broke d-i internalls. Yes one did
@1130344928 <joeyh!joey@kitenet.net> for at least two values of one
@1130344967 <aj!aj-irc@azure.humbug.org.au> joeyh: please explain what you're talking about, in technical terms
@1130344989 <aj!aj-irc@azure.humbug.org.au> joeyh: if you do so, it might get fixed
@1130345337 <aj!aj-irc@azure.humbug.org.au> joeyh: hello?
@1130345448 <h01ger!~holger@bone.digitalis.org> joeyh, i guess you're referring to the debootstrap-upload of aj ?! /me wonders why an upload to unstable breaks the d-i beta, isnt that build+based on etch ?
@1130345451 <joeyh!joey@kitenet.net> sorry, busy fixing the beakage
@1130345474 <Sledge!steve@217.147.81.17> looks like a debootstrap change is causing problems in CD builds
@1130345481 <joeyh!joey@kitenet.net> well, there has not been a usable combination of apt, debootstrap, and d-i in testing for well over a week
@1130345634 <aj!aj-irc@azure.humbug.org.au> so you're saying i didn't break it just as you're trying to release?
@1130345720 <joeyh!joey@kitenet.net> no you broke it just as the fixed NMU was ready to go into testing
@1130345758 <h01ger!~holger@bone.digitalis.org> .oO( ah )
@1130345783 <aj!aj-irc@azure.humbug.org.au> sigh
@1130345792 <neuro!~rmurray@h24-80-164-222.sbm.shawcable.net> ...and we're still waiting for the technical details
@1130345813 <aj!aj-irc@azure.humbug.org.au> joeyh: second warning. this channel's for technical discussions, eg "here's what broke: ...", not accusations, eg "you broke it" "why'd you have to break it" "yes one did".
@1130345869 <aj!aj-irc@azure.humbug.org.au> joeyh: if you want, there's still time to put 0.3.1.9 into testing
* Logging finished Wed, 26 Oct 2005 12:58:19 -0400
It's worth noting that the d-i release in question was etch beta 1, which eventually released 2 weeks after the above conversation. Probably my fault for not being a big believer in ridigly defined topics for communications channels. After all, I still filter all of my 20-some Debian mailing lists into a single folder; I'll happily talk about anything on the one irc channel (typically #debian-boot) that I nowdadys limit myself to; and so #debian-tech seemed like the obvious place to bring up the issue since aj, sledge, and other relevant people were active on it at the time. The technical details remain as irrelivant today as they were at the time, the relevant problem being that developers who are not involved in the installer development rarely consider how their actions can affect it. When a policy gets int the way of solving a problem, it's time to leave, that's all.

Aigars Mahinovs: DPL platform runthrough

I think more people should just publish their thoughts about platforms of our DPL candidates so that we can have more visibility and insight (and a reason to actually read those platform statements). Thanks go to MJRay for the idea, however I will try to be a bit more biased so that this post conveys more of my opinions then just a plain summary of the platforms.
Jeroen van Wolffelaar
  • ftp-team for a year, looks good
  • dpl-team as a good idea, wants team decisions to take less responsibility on his own. Might be wise, but could be un-leaderish.
  • pushes for smooth communication, I am not sure how that will work out - smooth communication means sanding off the edges, but we all know that the best development is always on the edge.
  • pushes for code of conduct. While the idea might be quite popular it also states that bad behavior in our community is becoming so widespread that a special code is needed to compensate for that. I do not feel that we are at such a bad state now - more flamewars are raised about the code of conduct then about the conduct itself. I feel this is were simple and decisive action by the DPL should be done and not a birocratic procedure to spread the blame of failure.
  • "insider reports" - good idea, like an internal Debian News Station (see Howard 100 News)
  • encouraging wiki, forums and IRC as official channels of external communication. Several questions arise here: as a user with specific question - where must I go? to which media? to which list, channel or forum category? It must not be too complex. Also there is the question of spreading knowledgeable users and developers too thin across multiple channels of voluntary support.
  • infrastructure transparency - good, but how? even tiny bits of paperwork there can slow the whole project to a crawl.
  • mediator in flamewar situations - good, DPL should be doing that.
  • media coverage - does Debian need more media coverage? I do not think so. I do believe that we need more coverage in more professional circles (even if in circles of professional psychiatrists) to attract more developers and make them understand us better, but I do not feel that attracting huge crowds of general public would do much good for the project.
  • in my opinion team players make mediocre leaders
Five word summary: transparent, wide, smooth, mediative, consensus
Ari Pollak
  • whoa ... pictures, so sweet :)
  • humor, so much needed in our project
  • good point about half-DPL - it would be nice to have DPL delegate as much as they possibly can but be strict and easy with what is left
  • Debian Police - sounds like a good substitute for Project Scud and the Finnish Inquisition :D
  • good take on licences, however I would add to the Gnocchi licence the phrase "And you must remove any copies of this licence from your memory as soon as you have finished reading it." That will show them lawyers ...
Five word summary: humor, half-*, police, anti-legalese, illustrations
Steve McIntyre
  • got in cheap, but a long time ago
  • The CD dude!
  • not much new on internal communication, same old "will tell you even that I not doing anything"
  • same stuff about the code of conduct, see above.
  • social skill test within NM. Good idea, but not a good implementation - you will not get much social conditioning with mentoring inside teams. We need someone to get on the candidate and roast them good - test their asbestos suits. After he has made a package, schedule for time and either call the newbie or IRC with him. Grill him about his package. Must sure to slide into personal insults, religion bashing and political discourses. Watch the response. Evaluate. Post audio online :)
  • open cabalish developments - there is little to be done beyond talking to cabal and making sure all semi-private developments use public Debian infrastructure for communication - draft on wiki and develop in svn, so that everyone can see.
  • very good points about professionalism. we must be able to be proud about Debian and demand some level of standards from packages inside Debian. The idea of regular DD reexamination might be a very good fit here, see below.
  • Steve looks like a good organizer to me
  • however he might be a bit too soft on leadership or simply too diplomatically inclined in his platform statement
Five word summary: professionalism, standards, MIA, tests, communication
Anthony Towns
  • not wanting to win too much
  • speed up! - release early, release often. Sounds good for the everyday processes, but not for The Release. I still want to see Debian as The Most Stable thing ever.
  • recruiting - I would ask, recruit for what? People can not just get into the interesting parts of the project and recruiting for general run of the mill development does not sound too engaging to me. You'd better make a contest for new security team members or new ftp masters or any other position that one person or only a few persons hold now. Have clear requirements and tests and actually get those people into doing those critical jobs. After that we can think about ...
  • ... compulsory turnover. Now there is a good idea that I'd like other DPLs to consider, but only with in conjunction with the previous one. We might not need full rotation, but we could have a rotating ftp team leader post that would iterate among ftp team members. That would alleviate the "hit by a bus" problem a bit more.
  • DPL as a discussion and direction leader is quite a nice and needed idea in my opinion.
  • I do not agree with aj about compulsory kindness and the general idea of expulsion on social grounds. Currently it creates more problems then it could solve in a lifetime.
  • Congrats on declassification thing, historians will surely thank us for that.
  • nice legal disclaimer, I like those kind of things :)
Five word summary: continuity, tempo, newbies, direction, bling
Andreas Schuldei Not online, to be put here when it appears.
Jonathan (Ted) Walther
  • photo, nice touch.
  • speak your mind. sound essential to a DPL.
  • Ubuntu good. Good.
  • Make love (and code) and not Desktop. Let Ubuntu make Desktop if they want to.
  • We all are strange people, face it.
  • Kicking people out is more harm to the project then those people could ever do.
  • Kicking fun out of Debian.
  • Great points about improving NM process and worshiping James Troup - I fully agree.
  • The best idea here - recertification of all Debian Developers every X years (where X is proposed to be 3 currently). This will almost automatically solve many problems we have in Debian: NM frustration, MIA developers, standards of professionalism, reiteration of best practices, social reshuffling.
Five word summary: Here, goes, my, vote, period. Alternate summary: geek, love, tolerate, recertification, statue.
Bill Allombert
  • math Ph.D. and researcher.
  • wanted to vot for Lars, but as he stepped down saw no one else good enough, so put himself forward. brave words. I like Lars too, bet it's not like we do not have good candidates this year besides him.
  • summary on effect of voluntarism and respectful communication. Quite plain if you ask me. Got me a bit bored there. Not a good sign.
  • think globally
  • assist others
  • help Debian specific software
  • observers - sounds like that Debian Action News Team minus all the fun.
  • "I am very patient" - be patient when reading and enthusiastic while writing, otherwise people might not read patiently
Five word summary: filler, communicate, more filler, patience I hope this summary gave someone as much food for thought as it did for me. My favorite is very clear, but can you guess who is my second choice? Leave a comment and let me know what you think :)

Aigars Mahinovs: Migrating from Blogger to your own Mnemosyne blog

As I decided to migrate my blog from blogger.com to my own blogging software on my own domain, I did not want to leave my old posts behind. As I had more then 150 of them, I had to do some automation to do that within my lifetime. The first step is to get the data from Blogger.com database to somewhere where you can access it in full. You will need FTP or SFTP access to a computer with a real IP address. The idea is to go to blogger.com and specifiy that you want to switch storage of your blog pages from their blogspot.com service to your of FTP or SFTP server. You will have to provide server address, URL, folder, username and password. URL does not matter at this point, but other parameters define where your data will be dumped to. Save the changes and republish the blog. After a few dozens of minutes all your data will be at your server in a set of complete html files. Now we need something that will parse those html files and write out something that your blogging software can understand. As I use Mnemosyne, my format is a set of mail message files. To allow me to use HTML formatted messages in my blog (and not only reST) I added this to my config.py:
class EntryMixin:
   def _init_content(self):
       """Read in the message's body, strip any signature, and format using
       reStructedText unless X-Format=='html'."""
       s = self.msg.get_payload(decode=True)
       if not s: return ''
       try: s = s[:s.rindex('-- \n')]
       except ValueError: pass
       body=False
       try:
               if self.msg['X-Format'] == "html":
                       body = s.replace("&nbsp;", " ")
                       body = re.sub(r'&(?!\w 1,10 ;)',r'&amp;',body)
                       body = xml.dom.minidom.parseString("<div>"+body+"</div>").toxml()
       except KeyError:
               pass
       except xml.parsers.expat.ExpatError, e:
               print "W: Parse failed for "+self.msg['Subject']+" at "+self.msg['Date']+" from "+str(int(time.mktime(time.strptime(self.msg["Date"],"%a %b %d %H:%M:%S %Y"))))
               print xml.parsers.expat.ErrorString(e.code), e.lineno, e.offset
       if not body:
               parts = docutils.core.publish_parts(s, writer_name='html')
               body = parts['body']
       self.cache('content', body)
       return body
This will try to parse messages as pure xHTML if custom header "X-Format" is set to "html" in the blog entry. There is one problem with this approach - xHTML must be valid, otherwise XML parser in Kid templating engine will fail and there will be no end of trouble. That is why even in HTML mode we reparse the body to XML and back to string again. If we get a parsing error at that point, we fall back to reST parser. Now we need something that will analyse our Blogger.com generated HTML files and get our content from there. Here is the script that I used:
#!/usr/bin/python
import os, os.path, time, sys, glob, re, xml.dom.minidom
id = 1
host = "old"
mdate = re.compile( r'\">(\d+) (\D+) (\d+)<' )
mbody = re.compile( r'</div>(.+)<div style=' )
mfooter = re.compile( r'<a href=\"http://example.com/(.+)\" title=\"permanent link\">(\d+):(\d+)</a></em>' )
files = glob.glob("old/*/*/*.html")
for file in files:
       year = 0
       month = 0
       day = 0
       hour = 0
       minute = 0
       subject = ""
       oldurl = ""
       body = ""
       date = ""
       title = ""
       footer = ""
       f = open( file, "r" )
       status = 0
       for l in f:
               if status == 0:
                       if l.find('class="date-header"')>0:
                               date = l
                               status = 1
               elif status == 1:
                       if l.find('class="post-title"')>0:
                               status = 2
                       if l.find('class="post-body"')>0:
                               status = 4
               elif status == 2:
                       if len(l.strip()) > 0:
                               title = l
                               status = 3
               elif status == 3:
                       if l.find('class="post-body"')>0:
                               status = 4
               elif status == 4:
                       if len(l.strip()) > 5:
                               body += l
                       if l.find('padding-bottom: 0.25em;')>0:
                               status = 5
               elif status == 5:
                       if l.find('posted by ')>0:
                               footer = l
                               break
       f.close()
       rdate = mdate.search( date )
       rbody = mbody.search( body )
       rfooter = mfooter.search( footer )
       year = rdate.groups()[2].strip()
       month = rdate.groups()[1].strip()
       day = rdate.groups()[0].strip()
       subject = title.strip()
       body = rbody.groups()[0]
       body = "<p>"+body+" </p>"
       body = re.sub(r'<img([^>]*?[^/])>',r'<img\1/>',body)
       if subject == "":
               subject = re.sub(r'<br.*?>','\n', body)
               subject = re.sub(r'</p.*?>','\n', subject)
               subject = re.sub(r'<.*?>','', subject)
               subject = subject.strip()
               line = subject.find('\n')
               if line > 45:
                       subject = subject[:40]+"..."
               else:
                       subject = subject[:line]
       oldurl = "http://oldblog.blogspot.com/"+rfooter.groups()[0].strip()
       hour = rfooter.groups()[1].strip()
       minute = rfooter.groups()[2].strip()
       mtime = time.mktime(time.strptime(day+" "+month+" "+year+"  "+hour+":"+minute, "%d %B %Y %H:%M"))
       outname = str(int(mtime))
       while os.path.exists( outname+"."+str(id)+"."+host ):
               id += 1
       outname = outname+"."+str(id)+"."+host
       out = open( "entries/new/"+outname, "w" )
       out.write("Date: "+time.ctime(mtime))
       out.write("\nSubject: "+subject)
       out.write("\nX-URL: "+oldurl)
       out.write("\nX-Tags: untagged")
       out.write("\nX-Format: html")
       out.write("\n\n")
       out.write(body)
       out.close()
Here I parse the HTML files using a simple state automata and then assemble all the data that we need to have, like timestamp in filename and Date field. In this script it is assumed that in the current directory there is "old/" directory with subdirectories like "2005", "2006", ... which have subdirectories for months in which there are xHTML files for individual posts. The output is written to "entries/new/$timestamp.$id.$host" files. After running this script and then running mnemosyne you will see a bunch of messages about failed parsing of some messages. That shows you where your xHTML is not valid. The usual problems are html entities ( like &euro; ) that the parser does not recognise and lack of closure on img or br tags:
This will fail because of &euro;
<img src="smile.png"> will fail, it must be <img src"smile.png"/>
My import script fixes img and br tags, but for other problems there is not much choice but going trough the entries and fixing them up manually. Also later on, if you will want to paste some custom HTML into your post, you will have to mark the whole post as HTML mode post and also check if you pasted HTML is valid XML manually. There are some other fun things in this blog, but I will go into that in later posts.

Erich Schubert: On AppArmor vs. SELinux

Some might have read recent news such as Novell SELinux killer rattles Red Hat, or Dan Walsh's critique of Novells AppArmor release, concerned with "unix like fragmentation in the security sector". While I also do think that SELinux is both more mature in the core system and more powerful than AppArmor (with a big plus being that SELinux is in the vanilla kernel) - I do think that AppArmor can quickly become a true SELinux killer, by just being better documented and easier to use. SELinux has serious deficiencies in documentation and development community. Almost all the available SELinux documentation is based around the policy as published by the NSA, which is "superseded by the reference policy project". This is the policy currently in Debian and used in the Gentoo SELinux docs - which hasn't received any updates in months now. The newer "reference policy" is updated every few days, by exporting Tresys' internal SVN into a public CVS on sourceforge. Dan Walsh claimed "multiple distributions shipping with SELinux including Fedora Core (2,3,4 and soon 5), Red Hat Enterprise Linux 4, Gentoo, Debian, Ubuntu, Suse and Slackware. " Which is not entirely true. SuSE has AppArmor now, Fedora and RHEL are pretty much the same, and apparently neither Gentoo, Debian, Ubuntu or Slackware are up to date with SELinux. Or actually involved in the current development. So that basically makes 1 distribution using current SELinux and 1 distribution using AppArmor... Looks like a tie to me. Also with the development it's pretty much down. AppArmor was developed by a small company called Immunix, and is now backed by big Novell, owner of SuSE. Current SELinux is mostly developed by a small company called Tresys, and somewhat backed and used by RedHat. Both have the feeling of "closed door" commercial development, which may be the reason why it reminds some people of the old Unix wars. Both of course claim to do an open development, with for example the current SELinux Symposium. But if you look closely at the Agenda and the speakers, it's fairly obvious that this is pretty much a business meeting, with some university speakers talking about the security concepts used. Just one quote from the site:
Developer Summit
An invitation only meeting for the core developers of SELinux to discuss future plans for SELinux and upcoming technologies.
The winner of this "war" between AppArmor and SELinux will be whoever manages to incorporate community development best, and get the other distributions like Debian, Ubuntu and Slackware to support their efforts. Currently neither of them has the air of actively supporting them, which is really bad. Widespread adoption is also where grSecurity has failed before.

Lars Wirzenius: Random hacks: DVD ripping with .desktop files

I watch movies and other DVDs on a computer rather than by using a dedicated DVD player box. For various reasons, it is more comfortable to watch a movie by first copying it on a hard disk. For example, often vobcopy will be able to rip it even though there are scratches or other errors. Watching directly from the DVD will fail or be painful, because of frequent stops. The command to rip a DVD is vobcopy -m. I wrote a little script around that that also creates a .desktop file so that I can just double-click on it to start Totem. Double-clicking on the directory opens a new Nautilus window, which is not useful for viewing a movie.

27 February 2006

Anthony Towns: #debian-tech, Redux

Back in September last year I blogged on #debian-tech, a new IRC channel for discussing Debian, but with a charter and some ops with a mandate to enforce it. At the time I wrote:
It’ll probably be quite a bit different from #debian-devel on either OFTC or FreeNode; hopefully that’ll turn out to be in a good way. We’ve got (I think) a pretty good variety of ops, who have (I think) some pretty good ideas on encouraging good productive activities on Debian. We’ll see what happens!
Since then, we’ve had a couple of significant discussions on it, reflected on the wiki page; the multiarch discussion was interesting and spontaneous, and the release and archive qualification discussions were both potentially highly contentious discussions that seemed to end up being conducted really well, and have both had some pretty significant results. That’s pretty pleasing – this time last year, there wasn’t anywhere I’d’ve been comfortable having those sorts of discussions in public, now there’s somewhere that’s been demonstrated to work fairly well. A more surprising outcome is that we’ve never actually banned anyone from the channel. To some extent, this is to be expected since people who don’t like the concept just won’t join in the first place, and to the extent that’s true, it’s a good thing. And at least Wouter, who’d also objected in the past, was willing to join briefly for one of the discussions important to him and get along fine. Unfortunately that’s not the only reason for the total lack of bans. The other aspect is that people have turned out to be far more ready to ban themselves than the ops have been. To anonymise an example from November last year: Read the rest ...

Adam Rosi-Kessel: Low Blogging Frequency

I haven’t been blogging lately. I do have a running list of ideas and topics, but my blog is going through a bit of an identity crisis. When I was a law student, it was easy for this to be a ‘law student blog,’ but now that I’m practicing I haven’t figured out how to find a balance between the personal and professional (and, perhaps on a third axis, the technical). Also, since I had a daughter, my time has been pretty scarce and I’m not sure that blogging is the best use of it. I’ll probably pick up in frequency before too long, but in case anyone is wondering, I’m still here. In the meantime, my Webloyalty is a Scam entry continues to get more traffic than anything else on this blog—close to 31,000 hits at the time of this writing, and nearly 1,000 writebacks (plus nearly as many personal emails to me on the topic). See also this follow-up post. One guy has even started a blog dedicated solely to criticizing Reservation Rewards—but now the link seems to broken. When I write these consumer protection entries, I inevitably get comments from low-level company insiders defending their practices (see, e.g., U-Haul Responds). These writebacks are often a much better condemnation than I could ever come with. For example, the following was apparently written by a “WLI Call Center Rep.” The POST request came from the same area of Connecticut as where Webloyalty is located, and it seems pretty genuine:
I’m a rep in the call center at Webloyalty. I have no pity for any of you people. You’re all suckers, plain and simple. Didn’t anybody ever teach you that nothing is free? When all of you idiots made your purchases on whatever website you did business on at the end of your transaction there was an offer asking if you wanted to save $10, or get award miles, or whatever. When you clicked on that link you were not automatically signed up. What happens is that you’re brought to the Reservations Rewards website. On that website it tells you that you are on the website for Reservations Rewards. You see, you can tell that because the banner at the top of the site says “Reservations Rewards”. Unfortunately you were too stupid to notice or remember. It then gives you instructions on how to redeem your “reward”. At that point you are instructed to enter you email address in twice and click accept. Now you have to manually type in the email twice in those boxes. No cut and paste is allowed. Then it tells you to click accept. Now, if you had any fucking brains in your head you would have noticed that right above the box where you enter your email mail address its says, in regular sized type, in plain sight, right out in the open, that entering your email twice will act as an electronic signature and that by clicking accept you are accepting that the website you just made a purchase on can share the billing information with Reservation Rewards. Also in the big box next all of this it gives the exact details of what you are signing up for, again in regular sized print, in plain sight, right out in the open. If you are too stupid to take the time to notice all of that then you deserve what you got. which was a membership in a overpriced bullshit ptogram. Webloyalty depends on idiots like you to not notice this stuff. To be blinded by the idea that you are getting something for “free”. To not look at you credit card statement so charges go through every month. Its unbelievable the amount of dummies out there that fall for this stuff. Even if you do catch the charges eventually, and get a refund they still made money off of you by collecting interest on your money when they had possesion of it. Stay a member or cancel its win-win for webloyalty. So, anyway I hope all you dummies learned a valuable lesson and wont fall for this again. I’m sure many of you will, though. You’d be shocked at how many people are repeat members where they canceled the service a while back but fell for the scam again a few months later.

26 February 2006

Erich Schubert: SELinux policy a day

I've been writing SELinux policy these days. Again. This time for the Reference Policy. I didn't get any feedback back yet for my policy, which is quite disappointing. Still the number of violations on my systems has gone down a lot, so I might actually be able to run strict some time soon. Which would be a major step. Unfortunately, I still have a couple of things to sort out with the utilities. And every now and then there is a new violation - monthly cronjobs for example are not that easy to observe without playing around. ;-) The Debian/Ubuntu packaging group is growing, and that means it's bigger than the "pretty much nonexistant" it was just a short time ago. Recent policy files I've written (which of course still contain bugs): dpkg, apt, tor, amavis, clamav.

24 February 2006

Pierre Habouzit: back from the deads, screenrc, zshrc

Well, my DSL provider killed my connection for 10 days, and then I had some vacation ... Long time no see. Though, I've played with my dotfiles recently, and I set up some really nice things, picked from the web. Screen and zsh cooperation The one I find the best is the tight collaboration between screen and zsh to have nice labelled windows in the screen status line. You have to do this like that :
   # in your .zshrc, add the following code to you preexec :
   preexec ()  
       if [[ "$TERM" == "screen" ]]; then
           local CMD=$ 1[(wr)^(*=* sudo -*)] 
           echo -ne "\ek$CMD\e\\"
       fi
    
   # and this code in order to reset the title when zsh gets the hand back
   if [[ "$TERM" == "screen" ]]; then
       PROMPT="$ PROMPT % ^[kzsh^[\\% "
   fi
Then, you can have in your .screenrc some dark margic like :
   bind s select zsh
which make Ctrl-A s find your first available shell (really nice). Make Shift+PgUp/PgDown work in screen well, this is complete dark magic, but it works :
   # tell screen that you term can scroll
   termcapinfo xterm ti@:te@
   # bind Shift+PgUp/PgDn
   bindkey -m "^[[5;2~" stuff ^b
   bindkey -m "^[[6;2~" stuff ^f
And another great setting is altscreen :
   # Support alternate screens so that, for example, when you
   # quit out of vi, the display is redrawn as it was before vi
   # redrew the full screen.
   altscreen on
Though, now, Shift-Tab doesn't work anymore in screen, and since in vimrc I have things like :
   "   Tab Key magic ...
   vmap <tab> >gv
   vmap <bs> <gv
   function! CleverTab()
       if strpart( getline('.'), col('.')-2, 1 ) =~ '^\s*$'
           return "\<Tab>"
       else
           return "\<C-P>"
       endif
   endfunction
   inoremap <Tab> <C-R>=CleverTab()<CR>
   inoremap <S-Tab> <Tab>
   "  
it's quite important that Shift+Tab works ... zsh does not eat non "\n" terminated lines I don't like the option
   setopt no_prompt_cr
that tells zsh no to print a "\r" before each prompt : I have a rprompt, and if a command (e.g. echo -n "f*****g command") is performed just before a shell prompt display, then my rprompt is wrapped, it's ugly. but printing a "\r" each time eats the line if no "\n" was present, which happens sometime, and makes you think the command you launched failed. I found that jewel on the zsh-users MailList :
   precmd()  
       local escape colno lineno
       IFS='[;' read -s -d R escape\?$'\e[6n' lineno colno
       (( colno > 1 )) && echo ''
    
Basically, it checks before writing the prompt if the current column position is 0, and if not, it prints an "\n". I guess it may exists some races if you have a background job, but for alldays use, it's perfect.

23 February 2006

Erich Schubert: KDE never worked for me

KDE apps barely worked for me. For example konqueror crashes on every odd run (I guess it's more like: I need to start it twice). Skype, which also uses QT crashes in the current versions directly after showing it's main window, too (statically linked, so it can't be QT itself...) Sometimes it also crashes and it opens up the non-configured kMail to write an email with the backtrace. I think Gnomes bug-buddy does a better job on that, too, not popping up two overlapping windows... I was looking for a nice tool to organize my Ogg music collection, and amaroK was recommended to me. While amaroK started fine, it would stop updating it's screen when indexing my collection. And what I then hate most, is that I can't even type "killall amarok", because KDE applications seem to prefer chaning their name after start... Argh! I have to admit, that amaroks screen looks pretty. The player that impressed me most (both feature-wise and visually) was quodlibet, though, which suprised me with a nice fading current-track display including cover image. It used way to much memory for my liking though, so I'm back to using mpd with a tiny gnome app to display what is playing and access the playlists. So what I'd really need is probably a quodlibet-like frontend to mpd. ;-)

Simon Law: CodeCon 2006, Day 2


House
Originally uploaded by sfllaw.
I woke up to a breakfast of pancakes, cooked by the wonderful [info]riseorbleed. I don't know about you but waking up to a hot breakfast is heavenly. After some morning ablutions, we hailed a cab and along the way we chatted with the cabbie as I looked out the window. Luxor cabbies are really nice, every time I travelled with them, they had some interesting story to tell and big, broad smiles. Smiling is the way to fatter tips! The weather in San Francisco is supposed to be rather variable. You know how that is, rain one minute and then sun the next. Well, the entire time I was there, it was bright and sunny and gorgeous. San Francisco really put on her best to charm me and she really succeeded. I didn't think that postcard-perfect pictures were possible, but I saw them everywhere. I was happy to walk around without needing a winter coat. And everyone else smirked at how happy I was. Daniel seemed to have recovered from the previous night's revelry. His talk on delta was excellent because he's a very good public speaker. Which is good, because he gave two presentations at CodeCon. When I talked to him on Thursday night, he seemed a little embarassed at how successful delta had become since it such a simple piece of software. But people like GCC use it to fare down their bug reports to the lines of code that reproduce its bugs. Rob and Tristan sidled up to my bar and asked me if I could get them some juice. For their laptops. They were working on their presentation all the way until the last minute, which involved a drunken Tristan stumbling around on stage. Except that Tristan doesn't drink, so his imitation was quite poor. They were presenting Djinni, which is their implementation of a fast simulated-annealing algorithm that takes also pressure into account. Sadly, they didn't explain their algorithm but their talk was entertaining nevertheless.

Shoes
Originally uploaded by sfllaw.
At lunch, Spider snuck me out of the building and she showed me around San Francisco. She pointed out the Eagle Tavern with a glimmer in her eye. I think she's trying to corrupt me. Or she's trying to pimp me out. Then we went to Stompers where she tried on some boots. We were stymied, however, by the fact that a very annoying woman and her husband were trying on every single pair of boots in the entire store. iGlance is a real-world video-conferencing and screen-sharing application that has some fairly good usability built into it. It also has a fairly sensible privacy model and does some NAT punching to boot. Although it's only got a Win32 port for now, it's free software so someone will fix it up. Sometime in the afternoon, the beautiful and fair [info]wealhtheow came behind the bar and surprised me with a hug and a sandwich! I was happy with the random hug from a new friend, but the sandwich was wonderful. I had not eaten lunch on Friday so I was very grateful. She put a huge smile on my face. I munched on the sandwich while listening to the OASIS talk. This technology is a locality-aware server-selection resolver, which is pretty good for distributing servers around the world and finding the fastest one. They implement this as a DNS redirector so that lookups are transparent to normal Internet software. This made me feel a little bad for [info]holdenk, whose SelfDirectedProject happens to be on a very similar topic. It does, however, validate his approach. [info]maradydd's presentation about Query by Example was up next. She did a very good introduction to data-mining, which segued into her hack on PostgreSQL where you can specify examples of things you want to search for. That is not how SQL normally works, where you specify constraints. With QBE, you just specify things similiar to what you want, and things similar to what you don't want.

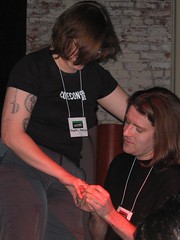
Proposal
Originally uploaded by sfllaw.
I was chatting with Rob Pascual when I noticed Len lining up in the Q&A; queue. Suddenly, my ears perked up as I sensed something important was going to happen. So I pulled out my camera, stepped on some toes, and got into position. When it was his turn at the microphone, he started saying random stuff that wasn't question at all! Something cheesy like how Meredith had changed his life and how he wanted to be with her. Then he got up on stage and asked The Question. It was beautiful. The audience broke out into cheers and applause, except for the heartless bastards beside me. But who cares about them? This was such an awesome occurance that an interview was taped. After teardown, some people were going to head to a franchise Mexican restaurant. Spider insisted that I get real food, so we walked down to the Mission. We made a detour to Good Vibrations which is a San Francisco landmark if ever there was one. I swear that she's trying to corrupt me. Anyway, as we were walking out, I must have mentioned that I was from Canada. Because Cohen, a Torontonian, came out of nowhere and introduced himself to us. Well, what was I to do but to invite my fellow countryman to dinner? So we set off to find a Taqueria that served nopales. This failed since Californians don't seem to like eating cactus. Instead, we went to Pancho Villa where I ate enchiladas and salsa verde and guacamole and churros and I was so very happy! We bid farewell to Cohen after exchanging contact information and tried to find everyone else. Unfortunately, we couldn't reach anyone by cellphone, so we sat around dejected for a while. Then we realised that we could go to Annie's Social Club where an event was happening. This turned out to be a good and a bad idea.

Taqueria
Originally uploaded by sfllaw.
It was a good idea because we found everyone at CodeCon. It was a bad idea because Annie's Social Club double-booked us with bad karaoke! And then were quite rude when we complained. And then kicked out John Gilmore. So I just want to say that Annie's Social Club hates geeks and freedom. So Len hailed a black stretch limousine, we all climbed into it, invited some reporters along and moved the entire party to the XYZ bar. The XYZ staff were very awesome, accommodating an extra hundred patrons and getting an extra bartender. And they were very nice about it. Unfortunately, the bar was full, so I had to lead a bunch of introverts in the fine art of taking over an establishment. We walked in, started talking, I encouraged people to sit down in empty spots on the couches. They did a very admirable job of taking over the back. I got the stunningly adorable [info]akashayi a seat and a drink, before I taked to the people sitting with us. They were a couple who had moved from Florida to San Francisco, and a man from New York who was quite the boor. The man in the couple knew the New Yorker and seemed quite embarassed about him. After twenty minutes of conversation, they excused themselves and bid us good night. This gave us plenty of seating space to talk about geeky things until the manager kindly kicked us out. I made sure Akasha got safely to her hostel and then took a taxi back to the guest room. It was quite the challenge to direct the cab driver, since I had lost the directions back, but I managed!

21 February 2006

Simon Law: CodeCon 2006, Day 1


SUV Taxi
Originally uploaded by sfllaw.
I woke up on Friday morning and wondered what breakfast would be. Then I remembered that I was staying at the W and decided to forage for food elsewhere. I took a taxicab with [info]spider88, [info]enochsmiles, [info]maradydd. It was a strange hybrid SUV cab that was painted all yellow, I would later learn that Yellow Cab drivers were scary and that I should avoid them. We got to StudioZ and discovered that we didn't know how to get inside. We figured that out eventually and took stock of the situation. I started moving tables about and setting up chairs, because I abhor standing about with my hands in my pockets. Then I helped hang banners from the rafters. After I did that, I tried to see if I could do anything else. Since CodeCon is run on the cheap so that anybody can attend, drinks like coffee are not included in the conference fee. And since the conference was being held in a night club, there was a convenient bar that would be a good place to setup a concessions stand. So I put things in order and stood behind the counter. I got to see people walk in the door and after registering with [info]wealhtheow or Spider, they'd stand in bewilderment in front of my bar. It was a lot of fun to watch all sorts of people come through. And then I'd smile at them and offer to get them something to drink. We started Lance's talk a little late in order to let everyone settle in their seats. I met him the night before where he talked about his Apache module that has heuristics for detecting when a phisher is trying to clone your website. Or when your website has been cloned and the phisher is passing login requests through to you. This kind of thing is totally what financial institutions have to start doing. We got coffee from this place called Cafe Organica, which seems to have some mixed online reviews. Or rather, Jonathan did, in a big messenger bag filled with carafes. Since Jonathan doesn't actually drink coffee, it was left to me to decide whether it was any good. It seemed to be drip coffee that was thick, dark and strong. Very decent for something that was brewed hours ago. The customers didn't seem to mind, as we ran out of coffee every day.

Couch
Originally uploaded by sfllaw.
The next presentation was SiteAdvisor which takes an interesting tack on safely surfing the web. Instead of building security features into your browser, there's a central server that stores information about sites that you're visiting. But what was really interesting was how they got this information. They had an automated tool that went in pretending to be a real person, signed up for some e-mails, downloaded some programs, and examined what happened afterward. I missed the majority of the VidTorrent presentation, because I was busy chatting with people and offering them refreshments. Also, their demo didn't work because the wireless setup at the conference kept on going down. People were abusing the free Wireless network that Cliff was trying to keep up and running. Which is sad, because Cliff had basically volunteered to set that up on his own time. Tom came up after that to present Localhost, which is a unimaginatively named piece of software, but is interesting because it lets you browse a world-wide filesystem of torrents. What's interesting about his filesystem is that it uses a distributed hash table, so that even if there are files with the same name, you'll be able to distinguish the distinct copies. Which is useful if you want to tell whether you're downloading a legitimate and popular file, or some malicious file that someone's injected. The last talk of the day was Truman, which not only demonstrated an interesting piece of technology, but also quite educational. The tool itself is a specialised Linux distribution that can capture what happens inside itself and simulate a public connexion to the Internet. This is advantages, Joe tells us, because modern pieces of malware are smart enough to disable themselves when they detect sandboxed environments. After people filed out, we packed away everything into storage as StudioZ is a nightclub, so it was setting up for its nightclub crowd. Everyone else went next door to Loft11 where a party was being held, sponsored by [info]bramcohen's awesome company I went inside and bumped into Graydon and we tried to go about finding fellow Canadians. This was not so successful on the crowded downstairs floor, so we went upstairs to chat and catch up. I met some people who were at the speaker's reception and successfully remembered their names. Then I met a guy who was at the night club just waiting for his buddy, and I explained CodeCon to him. He thought it was a great idea.

Stack of Macs
Originally uploaded by sfllaw.
Len Sassaman and Bram got up to give a little speech, which I tried to take photographs of. But failed. Instead, I noticed that they were on this awesome glass ceiling which made me want to dance. I didn't do that though, because my feet hurt from standing all day. I poked my head into a room upstairs that was all white, which was very cool. Some people were playing a game of Werewolf which finished with the villagers winning. I hung out with some people like Eric, Pete, and Kelsey who told the story of her pink Barbie backpack. I also met Chloe and her husband, whose name I have forgotten. But Chloe is awesome because she is now independently wealthy so that she can pursue her dream of studying the nitrogen cycle in soil using post-doc maths. Impressive! I also met [info]akashayi who is not a professional computer programmer at all. She teaches martial arts by day, and slings code by night. She drove all the way from Los Angeles to attend CodeCon and was having the time of her life. I wistfully remember when I was that excited about computing, so just hanging out with her was awesome. She promised me a Kempo lesson if I ever made my way to L.A., which is an offer I intend to collect. I found Spider downstairs, sitting on a couch with Daniel. The night was getting long and we were totally exhausted, so we took a taxicab to the W. There, we went up to Enoch's room party where he treated us to $17 cheeseburgers. Now, I didn't think that cheeseburgers that expensive were worth it, but boy oh boy were those good. Spider and I took a cab to [info]kineticphoenix and [info]riseorbleed's place sometime past midnight and we dragged our luggage into their guest room. Which was really more of an awesome guest apartment. Hurray for knowing people in foreign cities! I don't remember much after that. I think I turned on a space heater before passing out.

20 February 2006

Adeodato Sim : amaroK 1.4-beta1 packages

I’ve prepared amaroK 1.4-beta1 packages and uploaded them to experimental (a copy is available here). I recommend you to have a look at the changelog ; that way you’re more likely to discover the stuff that’s interesting to you. As an example: “Optionally update playcount for items played on iPod and submit them to last.fm and synchronize ratings between amaroK and iPod”. Note that you’ll need ruby installed to download lyrics now (feel free to reimplement the script in Python if you wish!), and that this version will rebuild your collection. If you can report bugs directly to upstream’s bugzilla, that’d be great (the packages are unstripped, btw). NP: Bergman, Enigmas in your hand

19 February 2006

Joey Hess: moreutils

Following up on my other posts about new unix tools, I've uploaded the moreutils package to Incoming and alioth. Currently it includes isutf8, sponge, vidir, ts (timestamps stdout) and vipe (discussed below). Hopefully this collection will grow to include other useful unix tools no-one thought to write 30 years ago.
vipe is my new personal best at writing a generic unix tool. It allows you to edit the contents of a pipe in a text editor. For example: find foo -type f vipe xargs rm Sorta handy as a way to make ad-hoc changes to data in a pipeline, or even just to examine it.

18 February 2006

MJ Ray: Uses and abuses of cookies

If you design your website so that it requires cookies, you ought to be punched [...] If you implement redirect chains [...] you ought to be kicked and battered, especially if those are implemented with meta refresh instead of HTTP redirect. - Madduck's pet peeves
I agree entirely. If you want to save data to my computer, ask me beforehand, else it will be refused. Particularly annoying are people using off-the-shelf applications which do the right thing and don't require cookies (OSCommerce, for example), but their idiot web developers have hacked it into requiring cookies by not thinking through the possibilities and ignoring library routines.

Next.

Previous.