Search Results: "spa"

20 May 2010

Dirk Eddelbuettel: RcppArmadillo 0.2.0 (and 0.2.1)

With the Rcpp 0.8.0 release on Monday, Romain, Doug and I were able to follow-up with a new RcppArmadillo release. RcppArmadillo uses Rcpp (and a few dozen lines of 'glue') to provide a transparent interface from R to Conrad Sanderson's impressive Armadillo library for linear algebra. This new release offers a number of key improvements: While we had tested this quite rigourously, the combination of some last minute changes that were meant to be stylistic-only, some troubles with the tests and builds at CRAN that were not apparent in all our tests (hint: do not yet use dynamic help features referencing other packages even if you have a Depends: on them) and an upcoming travel deadline meant that we missed a gotcha on Windows---so release 0.2.1 had to follow a few hours after the short-lived 0.2.0. More information is on the RcppArmadillo page. Questions, comments etc should go to the rcpp-devel mailing list off the R-Forge page.

19 May 2010

Russell Coker: Google Chrome and SE Linux

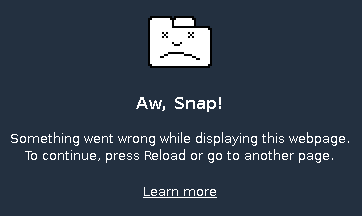
Google Chrome saying aw snap when it crashes [107108.433300] chrome[12262]: segfault at bbadbeef ip 0000000000fbea18 sp 00007fffcf348100 error 6 in chrome[400000+27ad000] When I first tried running the Google Chrome web browser [1] on SE Linux it recursively displayed the error message in the above picture, it first displayed the error and then displayed another error while trying to display a web page to describe the error. The kernel message log included messages such as the above message, it seems that some pointers are initialised to the value 0xbbadbeef to make debugging easier and more amusing. V8 error: V8 is no longer usable (v8::V8::AddMessageListener()) When I ran Chrome from the command-line it gave the above error message (which was presumably somewhere in the 8MB ~/.xsession-errors file generated from a few hours of running a KDE4 session). type=AVC msg=audit(1274070733.648:145): avc: denied execmem for pid=12833 comm= chrome scontext=unconfined_u:unconfined_r:unconfined_t:s0-s0:c0.c1023 tcontext=unconfined_u:unconfined_r:unconfined_t:s0-s0:c0.c1023 tclass=process
type=SYSCALL msg=audit(1274070733.648:145): arch=c000003e syscall=9 success=no exit=-131938567594024 a0=7fd863b41000 a1=40000 a2=7 a3=32 items=0 ppid=1 pid=12833 auid=4294967295 uid=1001 gid=1001 euid=1001 suid=1001 fsuid=1001 egid=1001 sgid=1001 fsgid=1001 tty=pts4 ses=4294967295 comm= chrome exe= /opt/google/chrome/chrome subj=unconfined_u:unconfined_r:unconfined_t:s0-s0:c0.c1023 key=(null)
type=ANOM_ABEND msg=audit(1274070733.648:146): auid=4294967295 uid=1001 gid=1001 ses=4294967295 subj=unconfined_u:unconfined_r:unconfined_t:s0-s0:c0.c1023 pid=12833 comm= chrome sig=11 V8 is the Google Javascript system which compiles JavaScript code and thus apparently needs read/write/execute access to memory [2]. In /var/log/audit/audit.log I saw the above messages (which would have been in the kernel message log as displayed by dmesg if I didn t have auditd running). The most relevant parts are that execmem access was requested and that it was by system call 9. From linux/x86_64/syscallent.h in the strace source I discovered that system call 9 on the AMD64 architecture is sys_mmap. Does anyone know a good way to discover which system call has a given number on a particular architecture without reading strace source code? Attempts to strace the Google Chrome process failed, Chrome gave the error Failed to move to new PID namespace after clone() failed. Clone was passed the flag 0 20000000 which according to /usr/include/linux/sched.h is CLONE_NEWPID. It seems that programs which create a new PID namespace (as Google Chrome does) can t be straced as the clone() call fails. It s a pity that Chrome doesn t have an option to run without using this feature, losing the ability to strace it really decreases my ability to find and report bugs in the program I m sure that the Google developers want people like me to be able to help them find bugs in their code without undue effort. Anyway the solution to this problem to allow it to run on the SE Linux Targeted configuration is to run the command chcon -t unconfined_execmem_exec_t /opt/google/chrome/chrome which causes the Chrome browser to run in the domain unconfined_execmem_t which is allowed to do such things. Of course we don t want Chrome processes to run unconfined, I think that the idea I had in 2008 for running Chrome processes in different SE Linux contexts is viable and should be implemented [3]. As a general rule if you are running a program from the command-line on SE Linux with the Targeted configuration (the default and most common configuration) then any time you see an execmem failure logged to the kernel message log or the audit subsystem then you can change the context of the program to unconfined_execmem_exec_t to make the problem go away. Note that this isn t necessarily a good thing to do, sometimes it s best to change the program to not require such access. But it seems that in this case the design of V8 requires write/execute memory access to pre-compile JavaScript code.

Bernd Zeimetz: new css for bzed.de

After more than a year of using ikiwiki to run bzed.de I thought it would be a good time replace the darkish-brown style by something bright. Also I wanted to get righ of the massive changes I had to do on the template files to make the old layout work. Unfortunately I hit one of the - in my opinion - major problems in the ikiwiki templates again: You can't rely on all <div>s being available on all pages, which is quite annoying when you need them to style the page with CSS. So I had to make a tiny change to page.tmpl:
diff --git a/templates/page.tmpl b/templates/page.tmpl
index 8a9911f..dbf78a0 100644
--- a/templates/page.tmpl
+++ b/templates/page.tmpl
@@ -111,8 +111,8 @@
 <TMPL_VAR CONTENT>
 <TMPL_IF HTML5></section><TMPL_ELSE></div></TMPL_IF>
-<TMPL_IF COMMENTS>
 <TMPL_IF HTML5><section id="comments"><TMPL_ELSE><div id="comments"></TMPL_IF>
+<TMPL_IF COMMENTS>
 <TMPL_VAR COMMENTS>
 <TMPL_IF ADDCOMMENTURL>
 <div class="addcomment">
@@ -121,8 +121,8 @@
 <TMPL_ELSE>
 <div class="addcomment">Comments on this page are closed.</div>
 </TMPL_IF>
-<TMPL_IF HTML5></section><TMPL_ELSE></div></TMPL_IF>
 </TMPL_IF>
+<TMPL_IF HTML5></section><TMPL_ELSE></div></TMPL_IF>
 <TMPL_IF HTML5><footer id="footer" class="pagefooter"><TMPL_ELSE><div id="footer" class="pagefooter"></TMPL_IF>
 <TMPL_IF HTML5><nav id="pageinfo"><TMPL_ELSE><div id="pageinfo"></TMPL_IF>
Everything else is a bit of CSS in local.css and some images. There are still various things which could be optimized, but there are more important things to do now :).

18 May 2010

Bernd Zeimetz: deb.li - the Debian ShortURL Service - beta test

After several other Debian developers convinced me that a ShortURL service, which is under control of a Debian Developer would be useful for them, I've spent some time to write the necessary code for it. And if it will be used regulary, I'll ask DSA if they want to host it on a proper machine. So I'm happy to announce the public beta test of deb.li (also available under go.debian.net)! Please note that neither the content of the pages nor the CSS is finished... :) As this should not become just another random, spammer-attracting ShortURL service, I will not provide a web based form to add new URLs. Instead new URLs have to be added via a simple JSON-RPC based interface. Other ways to add new URLs will be added on request (or by sending patches ;)), at least an email-gateway similar to db.debian.org is planned. The small piece of documentation which exists so far is available at wiki.debian.org/deb.li And if you want to give it a try now, log into alioth.debian.org and have a look into
/var/lib/gforge/chroot/home/users/bzed/godebian-client
- the usage is documented in the README file and should be pretty straight forward. I hope it will be useful - comments, bugreports and patches are welcome!

Sam Hartman: Moonshot: Federated Authentication Beyond the Web

Recently, I ve been working on an exciting project with JaNet(UK) on a project to bring federated authentication to non-web applications. I ve worked on authentication projects a lot, although this is the first federation project I ve worked on. The big difference appears to be an emphasis on credential independence: the subject (person trying to authenticate) and service will not share a common credential type. Within their organization, the subject and their identity provider share a credential. Then, the federation has some credential mechanism such that the user s organization and the service share some (probably completely different) type of credential. The other emphasis is on providing personalization. For web applications, there are a lot of options to achieve this: Information Card, Open ID, SAML, and OAuth all provide solutions in this space. However there are not good options for non-web applications. If you out-source your mail and chat infrastructure but want to use your own chat client or IMAP client, then you will not get the same federation benefits you can get with the web. If you re using usernames and passwords and don t mind the potential problems with your out-sourcing provider being able to impersonate all your users, you can simply synchronize usernames and passwords. Within an enterprise, you can do better using Kerberos. JaNet(UK) runs the UK Access Federation, which is a SAML-based web single-sign-on federation. In order to better meet the needs of their customers they d like to expand this offering to non-web applications. This demand is apparently shared across the European academic community. I suspect there is also some demand in the US academic community and in enterprise situations. With the web, it turns out that you have a convenient platform for interactions with the identity provider: you can simply direct a web browser to the identity provider and need not specify the user interaction with the web browser at all. This is seen as a significant branding and usability advantage. With other environments, it becomes necessary to specify the interaction with the identity provider. Consider an automated client that wishes to examine a mail box and provide advanced mail sorting or aggregation. That automated client cannot directly use a web browser. OAuth solves this issue with an enrollment step that does typically involve a web browser that produces a consumer key and an authentication step that does not. However for non-web clients it seems like avoiding reliance on the browser authentication will be important. It turns out we already have widely used technologies that do this: the Extensible Authentication Protocol (EAP) mediates the interaction between a subject and identity provider for obtaining network access. It also turns out that we have fairly good technologies for abstract security services within non-web applications: thanks to Kerberos and Active Director, many application protocols and a fair number of applications support GSS-API. JaNet(UK) proposes to combine these technologies with SAML in order to produce a solution for federation beyond the web. I prepared a feasibility analysis of this proposal. At a technical level, the proposal is sound. There s a lot of standardization and implementation work, but there appears to be sufficient motivation to form the seeds of a standards activity and put together a proof-of-concept implementation. However, the big question is Will anyone use it? In particular, to be useful beyond fairly small communities, support from client vendors and application framework vendors will be needed. It s taken massive money and around 20 years to get Kerberos support to a point where it is effective within an enterprise. Moonshot can leverage that work to a large extent, but moonshot may also have greater usability and penetration goals. It s interesting that I m advocating EAP for application layer authentication. When I was a Security AD, I made a strong statement that EAP must only be used for network access. I ve been fairly consistent about that since then. I think there are two huge problems with using EAP for application authentication. The first is that EAP only authenticates the home realm; it does not authenticate what service you re going to. So you might try to connect to your e-mail and end up giving something access to your stored files and pictures instead. That is, EAP has a phishing exposure in the federated context. If the only thing you can get by using EAP is network access, that exposure is only moderate. However in a fully federated environment that is a huge exposure. Moonshot will address this problem by using EAP channel binding and by doing the necessary work to make that a viable solution. The second concern is that interoperability is reduced when you have multiple authentication approaches for the same problem. If EAP is going to be used for application authentication, we need to understand how it relates to the rest of the application authentication metasystem. Moonshot proposes such a relationship, addressing my objection. Moonshot is designed to work well with the objectives of the Identity Metasystem and its laws of identity. It uses a different technology, but does have an approach for dealing with claims-based identity and hopefully will have a user experience very similar to the identity metasystem. It uses a different underlying technology. However one of the main beliefs behind the identity metasystem is that is the user experience and universal interoperability that is important, not any specific technology. In its domain, the technologies Moonshot selects will be a better fit than a web services stack. It s strange not to be working on Kerberos; Moonshot uses some Kerberos technology, but its core is definitely not today s Kerberos. In some ways it is fun to be working on something new. There s one aspect of Kerberos I really miss: Moonshot has nothing like tickets. There s no place to remember state or exchange to directly involve the client in what the server learns. My analysis talks about ways to make Moonshot more like Kerberos; there are some potential advantages, but so far, the tradeoffs do not justify changes. We re hoping to have a bar BOF at IETF 77 and a BOF in the summer at IETF 78.

Erich Schubert: Apple announces new iPad

In a surprise move Apple today announced a new product closely related to the behyped iPad. This move went completely unexpected with technology analysts, who were expecting a new iPhone dubbed "iPhone 4G" to be released next.The new product is called iPad mini, and features most of the iPad functionality in a lot smaller form factor, with extended battery life and without the overheating issues. It will focus on gamers, instead of the deprecated community of newspaper readers. The smaller form factor allows the users to bring the device along at any time.Get all the specifications of the new iPad mini here [www.apple.com]. There is also a special edition with voice-over-3G functionality [www.apple.com].Yes, I'm referring to the iPod touch and the iPhone. Just goofing around.

17 May 2010

Dirk Eddelbuettel: Rcpp 0.8.0

Romain and I are happy to announce the release of Rcpp version 0.8.0. It has been uploaded to CRAN. A Debian upload is delayed until the now-required inline package is accepted into Debian. The source package is also available from here. This release brings a number of changes that are detailed below. Of particular interest may be the much more robust treatment of exceptions, the new classes for data frames and formulae, and the availability of the new helper function cppfunction for use with inline. Also of note is the new support for the 'LinkingTo' directive with which packages using Rcpp will get automatic access to the header files. An announcement email went to the r-packages list (ETH Zuerich, Gmane); Romain also blogged about the release. The full NEWS entry for this release follows below:
0.8.0   2010-05-17
    o   All Rcpp headers have been moved to the inst/include directory,
	allowing use of 'LinkingTo: Rcpp'. But the Makevars and Makevars.win
	are still needed to link against the user library.
    o   Automatic exception forwarding has been withdrawn because of
	portability issues (as it did not work on the Windows platform).
	Exception forwarding is still possible but is now based on explicit
	code of the form:
	
	  try  
	    // user code
	    catch( std::exception& __ex__)  
	    forward_exception_to_r( __ex___ ) ;
	   
	
	Alternatively, the macro BEGIN_RCPP and END_RCPP can use used to enclose
	code so that it captures exceptions and forward them to R. 
	
	  BEGIN_RCPP
	  // user code
	  END_RCPP
	
    o   new __experimental__ macros 
	
	The macros RCPP_FUNCTION_0, ..., RCPP_FUNCTION_65 to help creating C++
	functions hiding some code repetition: 
	
	  RCPP_FUNCTION_2( int, foobar, int x, int y) 
	    return x + y ;
	   
	The first argument is the output type, the second argument is the 
	name of the function, and the other arguments are arguments of the C++ 
	function. Behind the scenes, the RCPP_FUNCTION_2 macro creates 
	an intermediate function compatible with the .Call interface and handles 
	exceptions
	
	Similarly, the macros RCPP_FUNCTION_VOID_0, ..., RCPP_FUNCTION_VOID_65 
	can be used when the C++ function to create returns void. The generated
	R function will return R_NilValue in this case.
	
	  RCPP_FUNCTION_VOID_2( foobar, std::string foo ) 
	    // do something with foo
	   
	  
	The macro RCPP_XP_FIELD_GET generates a .Call compatible function that
	can be used to access the value of a field of a class handled by an 
	external pointer. For example with a class like this: 
	
	  class Foo 
		public:
			int bar ;
	   
	
	  RCPP_XP_FIELD_GET( Foo_bar_get, Foo, bar ) ;
	  
	RCPP_XP_FIELD_GET will generate the .Call compatible function called
	Foo_bar_get that can be used to retrieved the value of bar.
	
	
	The macro RCPP_FIELD_SET generates a .Call compatible function that 
	can be used to set the value of a field. For example:
	
	  RCPP_XP_FIELD_SET( Foo_bar_set, Foo, bar ) ;
	
	generates the .Call compatible function called "Foo_bar_set" that 
	can be used to set the value of bar
	
	
	The macro RCPP_XP_FIELD generates both getter and setter. For example
	
	  RCPP_XP_FIELD( Foo_bar, Foo, bar )
	  
	generates the .Call compatible Foo_bar_get and Foo_bar_set using the 
	macros RCPP_XP_FIELD_GET and RCPP_XP_FIELD_SET previously described
	
	  
	The macros RCPP_XP_METHOD_0, ..., RCPP_XP_METHOD_65 faciliate 
	calling a method of an object that is stored in an external pointer. For 
	example: 
	
	  RCPP_XP_METHOD_0( foobar, std::vector<int> , size )
	
	creates the .Call compatible function called foobar that calls the
	size method of the std::vector<int> class. This uses the Rcpp::XPtr<
	std::vector<int> > class.
	
	The macros RCPP_XP_METHOD_CAST_0, ... is similar but the result of
	the method called is first passed to another function before being
	wrapped to a SEXP.  For example, if one wanted the result as a double
	
	   RCPP_XP_METHOD_CAST_0( foobar, std::vector<int> , size, double )
	
	The macros RCPP_XP_METHOD_VOID_0, ... are used when calling the
	method is only used for its side effect.
	
	  RCPP_XP_METHOD_VOID_1( foobar, std::vector<int>, push_back ) 
	
	Assuming xp is an external pointer to a std::vector<int>, this could
	be called like this :
	
	  .Call( "foobar", xp, 2L )
	
    o	Rcpp now depends on inline (>= 0.3.4)
	
    o   A new R function "cppfunction" was added which invokes cfunction from
	inline with focus on Rcpp usage (enforcing .Call, adding the Rcpp
	namespace, set up exception forwarding). cppfunction uses BEGIN_RCPP
	and END_RCPP macros to enclose the user code
    o	new class Rcpp::Formula to help building formulae in C++
    
    o   new class Rcpp::DataFrame to help building data frames in C++
	
    o   Rcpp.package.skeleton gains an argument "example_code" and can now be
	used with an empty list, so that only the skeleton is generated. It
	has also been reworked to show how to use LinkingTo: Rcpp
	
    o   wrap now supports containers of the following types: long, long double,
	unsigned long, short and unsigned short which are silently converted
	to the most acceptable R type.
	
    o	Revert to not double-quote protecting the path on Windows as this
	breaks backticks expansion used n Makevars.win etc
        
    o   Exceptions classes have been moved out of Rcpp classes,
	e.g. Rcpp::RObject::not_a_matrix is now Rcpp::not_a_matrix
As always, even fuller details are in Rcpp Changelog page and the Rcpp page which also leads to the downloads, the browseable doxygen docs and zip files of doxygen output for the standard formats. A local directory has source and documentation too. Questions, comments etc should go to the rcpp-devel mailing list off the R-Forge page

Kees Cook: yay for barriers

I find it surreal to have people guessing at my motivations when they could just ask me. On top of all that, I find it weird that people spend so much time with in-fighting. I just want my system not to suck. Some time ago (during in the Ubuntu Karmic development cycle maybe in September 2009), I started having giant problems with my build system. All I/O would start to stall, wait times would surge, and usually my entire system would just go unresponsive with the disk light on solid. This scared the crap out of me, and it wasn t entirely obvious what was triggering it. No one else seemed to be seeing it. I managed to start tracking things using latencytop , and saw stuff like liferea going crazy. As I eliminated more and more things, I eventually settled on it being a problem with umount, and I reported an Ubuntu bug. It seemed to look like an upstream bug that no one else but the reporter could reproduce either. Since no one else was seeing this issue, and it seemed related to LVM snapshots, I migrated off of snapshots, and started using aufs overlays for my builds. For a while, it seemed like things went away. It didn t, and I started hitting it again. I opened a new (now famous) bug in Ubuntu, since now snapshots weren t in the picture, and I didn t want to confuse the earlier history. I managed to find a relatively minimal test-case too. A few other people commenting on the bug were seeing the problem now too, but it was less pronounced for them. As an aside, this wasn t a just wait a few seconds longer kind of issue on my system. A single umount would last 30-40 minutes. And when I m doing parallel builds of security updates, this would turn into my system being unavailable for hours at a stretch. Since none of the kernel developers I was in contact with were able to track down the root cause, I asked Ted Ts o in email if he could just quickly peek in on this for me, since I figured he d be in a good position to confirm or deny it. I didn t want to start wasting upstream time with this if it wasn t reproducible (see earlier upstream kernel bug). To my great relief, Ted found a few minutes to check it, and was able to immediately confirm it and give me a viable work-around ( sync; umount ) for the time being. I confirmed the work-around, and went off to do other things. A while later, Ted came back to deliver a bit of a rant, the purpose of which was not clear to me, but I ultimately ignored it I didn t seem directed at me. I just wanted my system operating normally, and he d done me a favor to check in on it and got me a work-around. More time passes, and I eventually get caught in another I/O-wait melt-down. On investigation, it seemed that the in-kernel work-around in the Ubuntu kernel totally back-fired on me in some cases, rendering even the user-space work-around useless. After investigating the Ubuntu-specific work-around, I re-read Ted s rant in the course of researching what had happened during this bug s triage. It seemed that Ted was basically saying:
this is an upstream problem
RedHat hasn t run into it and he didn t know why I figured I should confirm for myself if Fedora was affected, so downloaded and installed Fedora to double-check there. Since I was able to reproduce it there, I opened an upstream bug, linking back to the original Ubuntu bug, and then went to open a bug in the Fedora tracker, linking back to upstream. And it seems to be these actions that everyone has jumped on. I will now bore you with the reality of my motivations: I wanted to fix the bug so no one would end up experiencing the same pain I d been through over the last 6 months. The bug was, from my perspective, a serious issue. Since I d managed to reproduce it in another distro, it was my duty as a Free Software developer to report it to them. And, in what I felt was an unambiguous gesture, I made sure to include the link to the upstream kernel bug. Reproducing it in Ubuntu, in Fedora, and with a stock kernel had me confident that it was an upstream issue. While Ted did correctly suspect the issue was upstream, I really didn t want to just open an upstream bug and have it be ignored. I wanted some additional proof of reproduction, which I got when I tested it on Fedora. So, I m rather saddened that so many people spent so much time questioning my motivations, making fun of Canonical, or doing anything other than trying to just simply solve this problem. I m totally disinterested in inter-distro fighting. Instead, I continue to assume we re all on the same team, fighting a philosophical battle against close-source software. And in that regard, I think it s still true. If I ignore the rants and jeering, I come away thankful for all the people that spent time trying reproduce the issue at Canonical, at RedHat, and in the larger community. I m hugely thankful that Ted made some time to let me know I wasn t crazy, and there was actually a problem. I m thankful for having some work-arounds, and I m thankful that the root cause was eventually ferreted out, with some possible solutions. I m even thankful that some people on the LWN thread saw that, far from malicious, I was trying to be helpful with the bug. I just wanted my filesystem not to eat my computer. And I was hoping other people could maybe help me, since I m not a filesystem expert. The drama around this bug is pathetic, and now by talking about it for almost 1000 words, I m just as guilty.

Mark Brown: ASoC updates in 2.6.34

Linux 2.6.34 was released today. This contains a fairly substantial batch of ASoC updates, including:

Rapha&#235;l Hertzog: Open money and Debian

I recently read an introductory article in an IT magazine on the increased usage of new currencies. It briefly mentioned the work of a researcher called Arthur Brock in using those currencies within open source communities. While I did not find more details on the research, it led me to think again about Debian s relation with money. The reason why we have troubles using money to pay the time spent by our developers is that money is scarce and it s thus next to impossible to be fair in the way money is spent among us. So why not invent a new currency that is not scarce and that would encourage the kind of work that we really value? Apparently there is free software out there to build new currencies: see metacurrency.org or openmoney.org. Let s call the new currency swirly/swirlies for the sake of the examples below. There are then multiple ways to create a small economy within the community and/or even create bridges with the national currencies: I m sure we can come up with many similar ideas. Feel free to share yours in the comments. Partagez cet article / Share This

Matt Zimmerman: Ubuntu 10.10 (Maverick) Developer Summit

I spent last week at the Ubuntu Developer Summit in Belgium, where we kicked off the 10.10 development cycle. Due to our time-boxed release cycle, not everything discussed here will necessarily appear in Ubuntu 10.10, but this should provide a reasonable overview of the direction we re taking. Presentations While most of our time at UDS is spent in small group meetings to discuss specific topics, there are also a handful of presentations to convey key information and stimulate creative thinking. A few of the more memorable ones for me were: The talks were all recorded, though they may not all be online yet. Foundations The Foundations team provides essential infrastructure, tools, packages and processes which are central to the development of all Ubuntu products. They make it possible for the desktop and server teams to focus on their areas of expertise, building on a common base system and development procedures. Highlights from their track: Desktop The desktop team manages both Desktop Edition and Netbook Edition, on a mission to provide a top-notch experience to users across a range of client computing devices. Highlights from their track: Server/Cloud The server team is charging ahead with making Ubuntu the premier server OS for cloud computing environments. Highlights from their track: ARM Kiko Reis gave a talk introducing ARM and the corresponding opportunity for Ubuntu. The ARM team ran a full track during the week on all aspects of their work, from the technical details of the kernel and toolchain, to the assembly of a complete port of Netbook Edition 10.10 for several ARM platforms. Kernel The kernel team provided essential input and support for the above efforts, and also held their own track where they selected 2.6.35 as their target version, agreed on a variety of changes to the Ubuntu kernel configuration, and created a plan for providing backports of newer kernels to LTS releases to support deployment on newer hardware. Security Like the kernel team, the security team provided valuable input into the technical plans being developed by other teams, and also organized a security track to tackle some key security topics such as clarifying the duration of maintenance for various collections of packages, and the ongoing development of AppArmor and Ubuntu s AppArmor profiles. QA The QA team focuses on testing, test automation and bug management throughout the project. While quality is everyone s responsibility, the QA team helps to coordinate these activities across different teams, establish common standards, and maintain shared infrastructure and tools. Highlights from their track include: Design The design team organized a track at UDS for the first time this cycle, and team manager Ivanka Majic gave a presentation to help explain its purpose and scope. Toward the end of the week, I joined in a round table discussion about some of the challenges faced by the team in engaging with the Ubuntu community and building support for their work. This is a landmark effort in mating professional design with free software community, and there is still much to learn about how to do this well. Community The community track discussed the usual line-up of events, outreach and advocacy programs, organizational tools, and governance housekeeping for the 10.10 cycle, as well as goals for improving the translation of Ubuntu and related resources into many languages. One notable project is an initiative to aggressively review patches submitted to the bug tracker, to show our appreciation for these contributions by processing them more quickly and completely.

Francois Marier: List of Open Source Conference Management Systems

Conference Management systems are web applications designed to make the lives of conference organisers easier. They usually include features such as registration, payment, paper submission and review, scheduling and publishing of announcements.

Since Wikipedia is apparently not a place for such a "spammy list," I figured I should at least post this here:
NameUsed byLicenseProgramming Language
A Conference ToolkitYAPC::EuArtistic LicensePerl
ConManUtah Open Source Conference, Texax Linux FestGPLPython (Django)
Open Conference Systemsvarious academic conferencesGPLPHP
OpenConferenceWareOpen Source BridgeMITRuby on Rails
PentabarfDebConf, FOSDEM, CCCGPLRuby on Rails
SCALEregSCALEGPLPython (Django)
Zookeeprlinux.conf.auGPLPython (Pylons)


If you know of any other Open Source systems, please leave a comment!

Marco T&uacute;lio Gontijo e Silva: Google Summer of Code weekly report #1

Some students of the Google Summer of Code are required to make a weekly report describing their activities. As far as I know, I m not, but I think it s a good idea in general, to comunicate to my mentor and other interested folks what I ve been doing. So I ll start to do them here. My project is Implementing the Immix Garbage Collector Algorithm on GHC. Last week I was most of the time involved in my school activities, so I didn t have much time to work on the project. I went to the bureaucratic services of my university to get a Proof of Enrollment in English, print/sign/scanned the Foreign Certification Form and sent them to Google on Friday afternoon. I asked them to confirm the receival, which they didn t. I m planning to ask again for a confirmal today in the afternoon, if I still get no reply. I also tried to build the current version of GHC, from the darcs repository. I was getting an error with my old (and updated) repository, so I donwnloaded a new one and could build nicely. Then I noticed that with make distclean I could also build with my older one, so I just removed the new. I downloaded the nofib benchmark suite and made an initial benchmark. While I was reading the documentation of the build process of GHC, I noticed a bug, and submitted a patch to the cvs-ghc mailing list. The patch was applied, with some changes. This week I plan to focus more on the project, and spend the weekly 36 hours working on it. I m planning to start reading the Immix Technical Report to see if there s anything new there with regard to the article. After that I ll read the wiki documentation on the GHC current GC, together with the GHC source code. I ll also experiment with Criterion. While I was writing this post I noticed that the GC benchmark in nofib is failing:
==nofib== fibheaps: time to run fibheaps follows...
/usr/bin/time ../../runstdtest/runstdtest ./fibheaps  -o1 fibheaps.stdout -o1 fibheaps.stdout  -ghc-timing     300000;  /usr/bin/time ../../runstdtest/runstdtest ./fibheaps  -o1 fibheaps.stdout -o1 fibheaps.stdout  -ghc-timing     300000;  /usr/bin/time ../../runstdtest/runstdtest ./fibheaps  -o1 fibheaps.stdout -o1 fibheaps.stdout  -ghc-timing     300000;  /usr/bin/time ../../runstdtest/runstdtest ./fibheaps  -o1 fibheaps.stdout -o1 fibheaps.stdout  -ghc-timing     300000;  /usr/bin/time ../../runstdtest/runstdtest ./fibheaps  -o1 fibheaps.stdout -o1 fibheaps.stdout  -ghc-timing     300000;
Command exited with non-zero status 2
0.72user 0.05system 0:00.77elapsed 99%CPU (0avgtext+0avgdata 277664maxresident)k
0inputs+32outputs (0major+17695minor)pagefaults 0swaps
././fibheaps 300000 < /dev/null
**** expected exit status 0 not seen ; got 2
././fibheaps 300000 < /dev/null
expected stderr not matched by reality
--- /tmp/no_stderr3559  2010-05-17 07:35:09.000000000 -0300
+++ /tmp/runtest3559.2  2010-05-17 07:35:10.000000000 -0300
@@ -0,0 +1,2 @@
+Stack space overflow: current size 8388608 bytes.
+Use  +RTS -Ksize -RTS' to increase it.
Command exited with non-zero status 1
0.72user 0.06system 0:00.85elapsed 92%CPU (0avgtext+0avgdata 277664maxresident)k
368inputs+48outputs (1major+22085minor)pagefaults 0swaps
Command exited with non-zero status 2
0.71user 0.04system 0:00.78elapsed 97%CPU (0avgtext+0avgdata 277664maxresident)k
0inputs+32outputs (0major+17694minor)pagefaults 0swaps
././fibheaps 300000 < /dev/null
**** expected exit status 0 not seen ; got 2
././fibheaps 300000 < /dev/null
expected stderr not matched by reality
--- /tmp/no_stderr3578  2010-05-17 07:35:10.000000000 -0300
+++ /tmp/runtest3578.2  2010-05-17 07:35:11.000000000 -0300
@@ -0,0 +1,2 @@
+Stack space overflow: current size 8388608 bytes.
+Use  +RTS -Ksize -RTS' to increase it.
Command exited with non-zero status 1
0.72user 0.06system 0:00.80elapsed 98%CPU (0avgtext+0avgdata 277664maxresident)k
0inputs+48outputs (0major+22093minor)pagefaults 0swaps
Command exited with non-zero status 2
0.72user 0.06system 0:00.80elapsed 98%CPU (0avgtext+0avgdata 277680maxresident)k
0inputs+32outputs (0major+17696minor)pagefaults 0swaps
././fibheaps 300000 < /dev/null
**** expected exit status 0 not seen ; got 2
././fibheaps 300000 < /dev/null
expected stderr not matched by reality
--- /tmp/no_stderr3597  2010-05-17 07:35:11.000000000 -0300
+++ /tmp/runtest3597.2  2010-05-17 07:35:12.000000000 -0300
@@ -0,0 +1,2 @@
+Stack space overflow: current size 8388608 bytes.
+Use  +RTS -Ksize -RTS' to increase it.
Command exited with non-zero status 1
0.72user 0.07system 0:00.83elapsed 96%CPU (0avgtext+0avgdata 277680maxresident)k
0inputs+48outputs (0major+22095minor)pagefaults 0swaps
Command exited with non-zero status 2
0.68user 0.08system 0:00.78elapsed 97%CPU (0avgtext+0avgdata 277680maxresident)k
0inputs+32outputs (0major+17695minor)pagefaults 0swaps
././fibheaps 300000 < /dev/null
**** expected exit status 0 not seen ; got 2
././fibheaps 300000 < /dev/null
expected stderr not matched by reality
--- /tmp/no_stderr3616  2010-05-17 07:35:12.000000000 -0300
+++ /tmp/runtest3616.2  2010-05-17 07:35:12.000000000 -0300
@@ -0,0 +1,2 @@
+Stack space overflow: current size 8388608 bytes.
+Use  +RTS -Ksize -RTS' to increase it.
Command exited with non-zero status 1
0.70user 0.09system 0:00.80elapsed 98%CPU (0avgtext+0avgdata 277680maxresident)k
0inputs+48outputs (0major+22089minor)pagefaults 0swaps
Command exited with non-zero status 2
0.71user 0.06system 0:00.93elapsed 82%CPU (0avgtext+0avgdata 277680maxresident)k
0inputs+32outputs (0major+17695minor)pagefaults 0swaps
././fibheaps 300000 < /dev/null
**** expected exit status 0 not seen ; got 2
././fibheaps 300000 < /dev/null
expected stderr not matched by reality
--- /tmp/no_stderr3635  2010-05-17 07:35:12.000000000 -0300
+++ /tmp/runtest3635.2  2010-05-17 07:35:13.000000000 -0300
@@ -0,0 +1,2 @@
+Stack space overflow: current size 8388608 bytes.
+Use  +RTS -Ksize -RTS' to increase it.
Command exited with non-zero status 1
0.73user 0.06system 0:00.95elapsed 83%CPU (0avgtext+0avgdata 277680maxresident)k
0inputs+48outputs (0major+22089minor)pagefaults 0swaps
make[1]: ** [runtests] Erro 1
Failed making all in fibheaps: 1
make: ** [all] Erro 1
Erro is error in Portuguese. I ll investigate on that.

14 May 2010

Petter Reinholdtsen: Sitesummary tip: Listing MAC address of all clients

In the recent Debian Edu versions, the sitesummary system is used to keep track of the machines in the school network. Each machine will automatically report its status to the central server after boot and once per night. The network setup is also reported, and using this information it is possible to get the MAC address of all network interfaces in the machines. This is useful to update the DHCP configuration. To give some idea how to use sitesummary, here is a one-liner to ist all MAC addresses of all machines reporting to sitesummary. Run this on the collector host:
perl -MSiteSummary -e 'for_all_hosts(sub   print join(" ", get_macaddresses(shift)), "\n";  );'
This will list all MAC addresses assosiated with all machine, one line per machine and with space between the MAC addresses. To allow system administrators easier job at adding static DHCP addresses for hosts, it would be possible to extend this to fetch machine information from sitesummary and update the DHCP and DNS tables in LDAP using this information. Such tool is unfortunately not written yet.

Matthew Garrett: Using qemu to instrument Windows

Part of the problem that we face in providing Linux hardware support is that we're lucky if there's a spec, and even if there's a spec there almost certainly isn't a test suite. Linux still isn't high on the list of things that vendors test with, so as a result hardware and firmware tend to be written to work with Windows rather than some more ideal notion of what a spec actually says.

This can lead to all kinds of problems. If the spec says we can do something and Windows never does that, we'll often find that there's at least one piece of hardware out there somewhere that breaks in response. But sometimes there'll be several different workarounds, and picking the wrong one may break some other system instead. It's helpful to know what Windows is actually doing, if only because that's the only configuration most systems have been tested with.

The problem is that doing this at the hardware level is next to impossible. I'm sure there are people out there who salivate at the possibility of working out i8042 initialisation sequences by hooking up oscilloscopes to their mouse, but I'm not one of them. There's a much easier alternative involving qemu.

The qemu source base is reasonably large and complex, but that's ok - we don't need to care about most of it. For our purposes we really only want to trace accesses to given bits of hardware. There's three main types of hardware access we're likely to care about: io ports, memory mapped io and pci configuration space. io ports are easy. Each piece of qemu that performs hardware emulation will call register_ioport_read or register_ioport_write. Just grep for those, find the ports that correspond to your hardware and then edit the functions to dump the information you want. PCI configuration space will be handled via pci_default_read_config or pci_default_write_config unless the driver overrides them. Finally, for PCI devices mmio will be handled via pci_register_bar - the last argument is the function called when the memory region is accessed.

All of which makes it pretty easy to watch register reads and writes performed by Windows when it's starting up. Suspend/resume is also an interesting problem, but sadly one that's harder to work with. First of all, you need at least version 0.6c of vgabios in order to indicate to Windows that it's possible to suspend at all. Secondly, for Vista or later you'll also need a WDDM driver for the graphics. Sadly there isn't one for the Cirrus that qemu emulates, which is unsurprising given how ancient it is. So I've had to perform my testing under XP, which was enough to give me an indication as to what Windows does with the SCI_EN bit on resume (answer: Ignores both the bit of the spec that says it should already be enabled and the bit of the spec that says it should never be written by hand). Nice, but if someone would like to write a WDDM driver for Cirrus it'd make my life easier.

The other thing I've been testing is keyboard controller probing. Some Macs deal badly with you banging on the keyboard controller, which is dumb but on the other hand they don't claim to have one. Linux will look at your ACPI tables and use any keyboard controllers it finds there, but if there isn't one it'll go on to try probing the legacy locations. Adding some debug code to the read and write functions of the keyboard driver in qemu and then editing the DSDT in Seabios to remove the declarations for the keyboard showed that Windows will only probe if there's a device with a recognised keyboard PNP ID. No keyboard for you if that's missing. So we probably need to emulate that behaviour as well.

The main reason to do this work is to try to reduce the number of DMI tables in the kernel. These are cases where we alter the kernel's behaviour based on the identity string of the hardware, allowing us to work around functional differences. The problem with this approach is that Windows generally works fine on these machines without knowing anything special about them, and chances are that the tables aren't exhaustive - there may well be some other piece of hardware that's also broken, but the user just gave up and went back to Windows instead of ever letting us know. Using qemu to work out how Windows actually behaves gives us the opportunity to fix things up in a way that will (with luck) work on all machines.

13 May 2010

Aigars Mahinovs: Hacker Neo caught in Latvia

A scandal has been brewing in Latvia over the last half year and yesterday the activity spiked shocking the media and some IT people in the country. I ll go back and explain what happened first, what is happening now and why this could have a heavy impact on IT and journalists in Latvia. At the end of last year, there were rumours that the IT system of Latvia s Internal Revenue System was hacked and millions of documents had been downloaded by multiple organizations. Shortly thereafter more details on the glaring security hole became public (after it was closed). There is a full electronic interface to give all reports to the IRS electronically (at http://eds.vid.gov.lv) and as part of that system you could also view and export monthly report summaries about your organization into XML and PDF files. After the system checked that you are authorized to access the report, you were redirected to the URL to actually download the report by report ID (as a single param in a GET request). Unfortunately, report IDs were predicable and the script that gave the reports for download did not check if you were authorized to get that report. It did not even check if were logged into the system. There were suspicions that the authorization was disabled on purpose to allow to leak data on purpose, but apparently it was an error of forgetting to disable debug code in production environment. The error was discovered only because the firewall administrator noticed an unexplained stable increase of traffic, especially during night hours when typically the traffic fully stopped. Apparently a single hacker (who later identified himself as Neo to the press) discovered the flaw and wrote a script to just try all possible report ids and get as much data out as possible. This had been going on for months, before someone noticed. After the flaw was discovered and a bit of time passed, Neo made his first move he published the list of top salaries in a governmental company, that clearly showed that the top leadership of this company failed to cut their salary by 40%, like everyone elses during harsh budget cuts of 2009. He stripped the names and ids of the specific employees, but named the company which made it pretty easy to figure out who was who. The society was outraged that the top managers in a government owned company failed to comply with the strict pay cut that everyone else in government had to endure. But after a few weeks the outrage subsided and no action followed from the government or law enforcement. Neo continued to release documents detailing salaries of top managers in different Latvian government companies. And each time after short outrage, nothing happened. Neo gave an interview where he said that he was disappointed in the passivity of the Latvian people in face of such blatant injustices. After a few month Neo went silent, promising to return before parliamentary elections this fall. However, this week a new development shocked everyone in the middle of the night two police SWAT teams went into action: one detained Ilm rs Poik ns, a researcher in artificial intelligence at the University of Latvia s Computer Science department and another raided the home of a Latvian TV journalist Ilze Nagle who interviewed Neo. Poik ns confessed of being Neo the next day and was released (with travel restrictions, pending trial) today. Politicians reacted immediately opposition demanded the resignation of the Interior Minister over such blatant disregard of freedom of press and another politician (who is also a famous lawyer) Aleksejs Loskutovs volunteered to defend Neo pro-bono (on Twitter, no less). Almost all Latvian online media have the arrest of Neo and the raid on the home of a journalist as main stories of the day. As a legal titbit, we also know that Neo is being charged with breaking statutes 145 and and 244p2 of the criminal law. Statute 145 is hard to find applicable in this situation as talks about actions done by people authorized (..) to access [private] information . Statute 244p2 will also be hard to pin down as it mentions influencing system resources of (an IT system) and if such action caused severe harm . It looks like the first part talks about at least a DoS attack (which did not happen in this case) and also there was no measurable harm from these leaks. Also Neo was careful to strip all personally identifying information (such as names, social security numbers and addresses of the employees in question), so it will be hard to pin him on that. Also no actual breaking or other modification of an IT system occurred. And no specialized software was used beyond a trivial script such as :

for i in range(0,7000000):
    wget('https://eds.vid.gov.lv/getRep.aspx?id='+str(i))
A lot of commentators on the Internet likened the situation to walking trough an unlocked door and stealing something. I think that analogy is very incorrect there was no door, and nothing went missing after the action. I came up with a different analogy there was this corridor with a lot of doors in IRS, locked steel doors. You were instructed to go to a room with a specified number and given a key to that room to unlock it and see your secret info. However, that corridor opened out to the street on one end, oh and also the walls of the rooms with all the secrets were transparent. So Neo walked into the corridor, looked at some of the secrets, wrote them down (to remember them better) and then went out and discussed the worst examples abuses of power he saw. In the end IRS had to learn their lesson if you have to put naked photos of yourself on the Internet (or something equally embarrassing), then make damn sure you password protect that, but if you don t then don t cry that someone hacked you and stole you pictures. What other people think:
http://freespeechlatvia.blogspot.com/2010/05/neo-released-under-restrictions.html We ll see how the story develops soon.

11 May 2010

Jonathan McDowell: Going to DebConf10


im_going_to_debconf10.pngNot that I ever thought I wasn't going, but due to some uncertainty about where I needed flights from I've only got round to booking things today - wish I'd gone ahead and done it last week!

Outbound:

2010-07-31 10:55 BHD -> 12:15 LHR BD85
2010-07-31 16:20 LHR -> 19:00 EWR VS001

Inbound:

2010-08-08 18:15 JFK -> 06:35 LHR VS004
2010-08-09 10:55 LHR -> 12:20 BHD BD84

See you all there!

Gunnar Wolf: e-voting seminar, Mexico City, tomorrow

If anybody is interested or can attend: Tomorrow and the day after (Wednesday and Thursday 12-13/05/2010) FLACSO (a leading Social Sciences faculty spanning countries all over Latin America) and IFE (Mexico's federal electoral authority) are presenting a seminar on e-voting: Electronic vote experiences in Mexico and around the world. Sadly, I will be unable to attend, as I will be on the road once again (Ecuador!). However, I hope those among my readers who are interested in the topic can attend or at least follow the audio and video transmission from the IFE website. The seminar will be held at IFE's auditorium Viaducto Tlalpan No. 100, Col. Arenal Tepepan, Delegaci n Tlalpan, c.p. 14610, M xico, DF. [update] If you don't know what is my stand on this topic (and can read Spanish), please read this short article. In short: I am against e-voting, and hope we are still in time (and can push at the right places) to avoid it becoming the rule in our country.

Ritesh Raj Sarraf: tomoyo for debian

Just uploaded tomoyo-tools and is waiting in the NEW queue.Thanks to Moritz Muehlenhoff, tomoyo kernel support should be available in Debian with kernel 2.6.32-13 and above.What is Tomoyo ?

Description: Lightweight and easy-use Mandatory Access Control for Linux
TOMOYO Linux is Lightweight and Usable Mandatory Access Control with
- "automatic policy configuring" feature by "LEARNING mode"
- administrators friendly policy language
- no need libselinux nor userland program modifications
.
TOMOYO Linux consists of patches to Linux kernel and administrative
utilities, and this package contains its audit daemon and tools.

Description: Lightweight and easy-use Mandatory Access Control for Linux

TOMOYO Linux is Lightweight and Usable Mandatory Access Control with

- "automatic policy configuring" feature by "LEARNING mode"

- administrators friendly policy language

- no need libselinux nor userland program modifications .

TOMOYO Linux consists of patches to Linux kernel and administrative utilities, and this package contains its audit daemon and tools.

9 May 2010

Craig Small: JFFNMS 0.8.5 released

After my usual battle with PHP and database exports, jffnms 0.8.5 is now released. This program is a network management system written in PHP. The worst part about the whole maintaining process for it would have to be is the release.

Why is it so difficult to track changes within a database and PHP code? You don't get that nice compile-time versus run-time error problems and the database is just diabolical to keep up to date with what you have changed. Someone needs to invent a git for database states!

Looking around other PHP based programs, I don't think anyone else has solved this issue. Well, its out there, enjoy it or not and if you have comments about the program let me know.
<script defer="defer" src="http://static.zemanta.com/readside/loader.js" type="text/javascript"></script>

Next.

Previous.