Search Results: "cas"

28 July 2010

Aigars Mahinovs: Debconf 10 arrival and first days

I had planned long for this Debconf and with the experience from the previous times I did all I could to reach one goal minimise stress. I think I got it right this time. First of all I got my company (Accenture) pay for the whole thing, so I did not have to worry about sponsorship queue (but instead I must gather and deliver them back some knowledge gained from the conference should be easy). I also managed to get a direct flight there is a weekly flight Tashkent-Riga-New York on Sundays and I got a ticket for that both ways. This took many hours off the travel time and reduced the stress a ton. Then I also did all the prudent travelling things: mostly reading the New York page on Wikitravel. This told me (among other things) what metro line to take to get the best view of the city. And for luggage I took a backpack (for the laptop and walking around) and a roller (for the clothes). I learned a lot from the Up in the air movie, it really teaches one how to take stress out of travel. This went very well in the beginning I took a bus to the airport early, checked in, breezed trough security and then waited and waited. The boarding only started half an hour after we were scheduled to depart. But I can not complain, because the flight attendant called my name (among a few others) just before boarding and changed my ticket I was bumped up to business class :) . It has been many years since I ve flown a regular (non-budget) airline and now first time ever in the business class! We got regular class meals, but at least we got to sit in the big chairs with lots of leg room. It was great! I bought a paper book (from Charles Stross) to read during the flight, because that is the only thing you can do during take-off and landing and I had some stuff to listen to in my iPhone. I tried sleeping and I think I managed to kill a couple hours that way too. It sure helped combat jet lag later on. When I arrived, I had my immigration and customs forms filled out. Latvia is on the USA Visa Waiver program, so I just had to fill out a form online prior to the trip to get a permission to enter USA. I only had one printout of the Waiver confirmation page and my airline took that before giving me a boarding pass, so I had no paper copy to give to the guy at the USA border, but he did not even ask for it he only took the two forms I filled out, scanned my passport, took my fingerprints (all fingers) and a photo. Then he gave me back the customs for (stamped) and I could go get my luggage. After that it was just a matter of walking trough customs and giving the customs official the pre-filled and stamped customs form. I was not stopped further. The AirTrain was a bit confusing you just get on the AirTrain and go where you need to go, you actually pay at the place where AirTrain connects to metro, so when you are coming from the airport you are actually paying ($5) when you are exiting the AirTrain system. There are plenty of AirTrain people that will give you an AirTrain ticked for $5 cash right there or you can use a machine to get it (where you can also pay with a card). The machines also take AmEx, but you must know the PIN code, if your don t know the PIN of you AmEx card (like I don t know the PIN of my corporate AmEx) you can only buy MetroCards at news stands, but there you will not find the unlimited ride tickets only 5 or 10 ride tickets are available. Next I screwed up a bit and thus got a bit lost in the New York metro system. The Wikitravel recommends to take the AirTrain to Jamaica station and from there take J or Z line into the city for the best views. I went to Jamaica and got into the first metro train that came on to the platform. Unfortunately, that was the E line train and it does not cross with J or Z lines after that, so I was stuck. To complicate the situation E line is under repair, so after a few stops the trains diverted to the F line and I had to scramble to figure out where to get out to get to the 1 line where Columbia University is. I ended up spending more than an hour in the metro, but I got there in the end. So I emerge from the 116th street metro station directly in front of the campus entrance gate and it starts raining. A thunderstorm swept across New York as soon as I stepped outside the metro station, so I took shelter a the side of the building. It kept raining. After a few minutes decided that I don t want to wait any more, so I put all my electronics into my backpack and went towards the dorm where my room was. The rain was warm, people around me were playing and running around in the wet grass, it was fun. The guard showed me where to go to check in. It was really simple sign here, here is you magnetic stripe key, have fun. And the room was just as spartan bed, desk, chair, closet, bathroom and a large fan under the window. The first night I did not know that I could actually turn that fan down, so I slept to the sound of full fan blasting, much like on the airplane. The dorm looks ancient it looks like it was build in the 60s and never changed since then. I mean, I ve lived in worse places, but people would at least change wall sockets or faucets or ceiling paint every other decade or so. The newest things here were the magnetic locks on the doors and a TV and a mini fridge in the hallway. After dropping my things I went off to the Mudd building across the campus to check in with people in the hacklab. It was just starting to take shape, but many great and familiar people were already there. It was like walking into a family home same warm welcome smiles and that great feel of belonging to the group. After I quick chat I went off downtown. The plan was that I left my old Canon 400D camera back at home and that I would buy a new Canon 550D here in New York on arrival. Unfortunately I underestimated the travel time on subway and by the time I got back downtown most shops where already closed. I got to checking out a Best Buy and was told there that they don t have 550D in stock. Next morning I went for a full scale search B&H Photo Video store, J&R Express, another BestBuy none of them had the Canon 550D (aka T2i) in stock in a body-only configuration. BestBuy had a few sets with the kit lens, but I did not want paying 100$ extra for something I already have. The last option was Adorama and I got lucky I nabbed the last 550D they had and it was body-only. Now I was back, with a camera in my hands and the Debconf10 could really begin!

27 July 2010

Daniel Baumann: The World's most powerful Wireless Network Card

About two weeks ago I got a Wifly-City G2000, the world's most powerful 802.11bg wireless network card. It features 2000mW which is 10 times more than the legally allowed limit of 200mW in Switzerland (or 2 times more than the allowed 1000mW in the USA, 5 times more than the allowed 400mW in Brazil, or 20 times more than the allowed 100mW in the EU). Contents The adapter is sold as a set named Wifly-City AVATAR-4PA with some accessories.
click on the images for full resolution The box prominelty lists Linux compatibility and contains the following part: The adapter has a Realtek 8187L chipset. This is particulary nice since there is no firmware needed for this chipset (therefore no questinable binary-only firmware blob). Also, it works out of the box with any Linux as of kernel version 2.6.30 and newer. I tested it on lenny with kernel backports, vanilla squeeze and vanilla sid. In all of these setups, it works out of the box without any configuration whatsoever - just plug it in and it works. I know that this is how it is supposed to be but still, I am always surprised again when things just work. For those who care, this is the output of dmesg when plugging in the card...
[...]
usb 1-1: new high speed USB device using ehci_hcd and address 6
usb 1-1: New USB device found, idVendor=0bda, idProduct=8187
usb 1-1: New USB device strings: Mfr=1, Product=2, SerialNumber=3
usb 1-1: Product: RTL8187_Wireless_LAN_Adapter
usb 1-1: Manufacturer: Manufacturer_Realtek_RTL8187_
usb 1-1: SerialNumber: xxxxxxxxxxxx
usb 1-1: configuration #1 chosen from 1 choice
phy1: Selected rate control algorithm 'minstrel'
phy1: hwaddr xx:xx:xx:xx:xx:xx, RTL8187vB (default) V1 + rtl8225z2, rfkill mask 2
rtl8187: Customer ID is 0xFF
Registered led device: rtl8187-phy1::tx
Registered led device: rtl8187-phy1::rx
rtl8187: wireless switch is on
usbcore: registered new interface driver rtl8187
ADDRCONF(NETDEV_UP): wlan1: link is not ready
wlan1: direct probe to AP xx:xx:xx:xx:xx:xx (try 1)
wlan1: direct probe responded
wlan1: authenticate with AP xx:xx:xx:xx:xx:xx (try 1)
wlan1: authenticated
wlan1: associate with AP xx:xx:xx:xx:xx:xx (try 1)
wlan1: RX AssocResp from xx:xx:xx:xx:xx:xx (capab=0x411 status=0 aid=5)
wlan1: associated
ADDRCONF(NETDEV_CHANGE): wlan1: link becomes ready
wlan1: no IPv6 routers present
[...]
...and this is the output of lsusb:
Bus 001 Device 006: ID 0bda:8187 Realtek Semiconductor Corp. RTL8187 Wireless Adapter
Special Offer I have played with the card for some time now and am really pleased with it. It works nicely with all the standard tools (aircrack-ng, kismet, etc.). The only bummer is that the card is quite expensive. Fortunately, we could arrange a good deal for Free Software people where the store selling it does not make any money on it: instead of 89 USD you can get it for 68 USD (including everything). If you are interested in getting one and you are comming to DebConf 10 in New York between 2010-07-25 and 2010-08-08, you can write an email to Ralph Amissah or speak to Ralph personally during the event. 1 I have no idea why they are shipping with a Y cable because the adapter does not need one. However, it does not disturb and in case I ever need an Y cable, I now have one :)

Wouter Verhelst: NBD: authentication and named exports

I just did some work on two NBD features: authentication and named exports. The first was written by Brad Allen back in 2008. I'd been thinking about an authentication scheme back at DebConf 8, and discussed it on the nbd-general mailinglist. Brad picked it up and ran with it, but it never got finished. Basically, what I did today was forward-port the code so that it would compile (and work) with today's version of the NBD utilities. I tested it and it works, but I'm not sure what to do with it. NBD is not encrypted; so there's no protection against TCP hijacking or some such. Oh well; I might still integrate it into nbd mainline. The second feature is something way more interesting. It had been on my long-term TODO list for quite a while, but I never sat down to implement it. Until today, that is. This patch has been compile-tested, but I haven't functionally tested it yet; I'll do that tomorrow. The main reason it took so long to implement, was that initial NBD handshake made that quite hard. Upon connecting, nbd-server as it currently exists will open the file or block device that it needs to export, and before nbd-client has sent anything sends information on that export (its size, whether or not it is read-only, etc) to the client. Unfortunately, this does mean that I cannot add new features to nbd-server while retaining full backwards compatibility if these features may involve changing what nbd-server sends during the initial handshake, as is the case here. This could be worked around by having the server first send information on a "default" export to the client, and then variate that if the client informs the server that it actually wants something else. But this would have been rather ugly, since it means that errors in open() or stat() calls for the initial "default" export would have to be non-fatal until the client actually tries to read or write to or from the device, at which point they would suddenly become fatal. This would open a can of worms near which I didn't want to tread. The way I fixed it in the end, however, is fairly simple. If names are used to specify an export, nbd-server can live with just one port to export all block devices that it supports, rather than needing many. As such, I can "reserve" one port for the new-style named exports. On this port, nbd-server would expect that clients send a name, and would not function correctly with clients that don't understand names. At the same time, nbd-server could still export the same block devices on other ports as well, using the old-style protocol, for clients that do not support named devices. This would of course require that both the client and the server know perfectly well what the port is, and that it does not change too easily. As such, I've just put in a request for an assigned port number over at IANA, so that I can be sure that the port will not change unexpectedly. This also means I won't make a public release with this change until the port number has been assigned, so that I don't need to support two 'default' nbd-server ports in the future (one "temporary" and one IANA-assigned port). For now, however, I think I'll go grab some food.

26 July 2010

Russell Coker: Creating a SE Linux Chroot environment

Why use a Chroot environment? A large part of the use of chroot environments is for the purpose of security, it used to be the only way of isolating a user from a section of the files on a server. In many of the cases where a chroot used to be used for security it is now common practice to use a virtual server. Also another thing to note is that SE Linux provides greater access restrictions to most daemons than a chroot environment would so in many case using SE Linux with a sensible policy is a better option than using a chroot environment to restrict a daemon. So it seems to me that the security benefits that can be obtained by using a chroot environment have been dramatically decreased over the last 5+ years. One significant benefit of a chroot environment is that of running multiple different versions of software on one system. If for example you have several daemons that won t run correctly on the same distribution and if you don t want to have separate virtual machines (either because you don t run a virtualisation technology or because the resources/expense of having multiple virtual servers is unacceptable) then running multiple chroot environments is a reasonable option. The Simplest Solution The simplest case is when all the chroot environments are equally trusted, that means among many other things that they all have the latest security patches applied. Then you can run them all with the same labels, so every file in the chroot environment will have the same label as it s counterpart in the real root this will mean that for example a user from the real root could run /chroot/bin/passwd and possibly get results you don t desire. But it s generally regarded that the correct thing to do is to have a chroot environment on a filesystem that s mounted nosuid which will deal with most instances of such problems. One thing to note however is that the nosuid mount option also prevents SE Linux domain transitions, so it s not such a good option when you use SE Linux as domain transitions are often used to reduce the privileges assigned to the process. There are two programs for labeling files in SE Linux, restorecon is the most commonly used one but there is also setfiles which although being the same executable (restorecon is a symlink to setfiles) has some different command-line options. The following command on a default configuration of a Debian/Lenny system will label a chroot environment under /chroot with the same labels as the main environment: setfiles -r /chroot /etc/selinux/default/contexts/files/file_contexts /chroot I am considering adding an option to support chroot environments to restorecon, if I do that then I will probably back-port it to Lenny, but that won t happen for a while. For a simple chroot once the filesystem is labelled it s ready to go, then you can start daemons in the chroot environment in the usual way. Less trusted Chroot environments A reasonably common case is where the chroot environment is not as trusted. One example is when you run an image of an old server in a chroot environment. A good way of dealing with this is to selectively label parts of the filesystem as required. The following shell code instructs semanage to add file contexts entries for a chroot environment that is used for the purpose of running Apache. Note that I have given specific labels to device nodes null and urandom and the socket file log in the /dev directory of the chroot environment (these are the only things that are really required under /dev), and I have also put in a rule to specify that no other files or devices under /dev should be labelled. If /dev is bind mounted to /chroot/dev then it s important to not relabel all the devices to avoid messing up the real root environment and it s impractical to put in a specific rule for every possible device node. Note that the following is for a RHEL4 chroot environment, other distributions will vary a little some of the file names. semanage -i << END
fcontext -a -t root_t -f -d /chroot
fcontext -a -t bin_t /chroot/bin.*
fcontext -a -t usr_t /chroot/usr.*
fcontext -a -t usr_t /chroot/opt.*
fcontext -a -f -d /chroot/dev
fcontext -a -f -s -t devlog_t /chroot/dev/log
fcontext -a -f -c -t null_device_t /chroot/dev/null
fcontext -a -f -c -t urandom_device_t /chroot/dev/urandom
fcontext -a -t "<<none>>" "/chroot/dev/.*"
fcontext -a -t "<<none>>" "/chroot/proc.*"
fcontext -a -t lib_t /chroot/lib.*
fcontext -a -t lib_t /chroot/usr/lib.*
fcontext -a -t bin_t /chroot/usr/bin.*
fcontext -a -t httpd_exec_t -d /chroot/usr/bin/httpd
fcontext -a -t var_t /chroot/var.*
fcontext -a -t var_lib_t /chroot/var/lib.*
fcontext -a -t httpd_var_lib_t /chroot/var/lib/php.*
fcontext -a -t var_log_t /chroot/var/log.*
fcontext -a -t var_log_t -f /chroot/var/log/horde.log.*
fcontext -a -t httpd_log_t /chroot/var/log/httpd.*
fcontext -a -t var_run_t /chroot/var/run.*
fcontext -a -t httpd_var_run_t -f /chroot/var/run/httpd.pid
fcontext -a -t httpd_sys_content_t /chroot/var/www.*
END
You could create a shell script to run the above commands multiple times for multiple separate Apache chroot environments. If there is a need to isolate the various Apache instances from each other (as opposed to just protecting the rest of the system from a rogue Apache process) then you could start each copy of Apache with a different MCS sensitivity label which will provide adequate isolation for most purposes as long as no sensitivity label dominates the low level of any of the others. If you do that then the semanage commands require the -r option to specify the range. You could have one chroot environment under /chroot-0 with the sensitivity label of s0:c0 for it s files and another under /chroot-1 with the sensitivity label of s0:c1 for it s files. To start one environment you would use a command such as the following: runcon -l s0:c0 setsid chroot /chroot-0 /usr/sbin/httpd

25 July 2010

Russell Coker: Links July 2010

David Byrne gave an interesting TED talk about how changes to architecture drove changes to musical styles [1]. I think he does stretch the point a little. To a certain extent people develop the most complex instruments and the largest music halls that can be supported by the level of technology in their society people with a hunter-gatherer civilisation play drums because they can build them and can carry them. The NY Times has an interesting article about paternity leave in Sweden [2]. The Swedish government pays for a total of 13 months leave that can be split between parents for every child. Of those 13 months 2 months can only be taken by the father and that is likely to increase to a minimum of 4 months of paternity leave after the next election. Dan Meyer gave an interesting TEDX talk about how the current math curriculum in the US (as well as Australia and lots of other countries that do the same thing) is totally wrong [3]. His main point is that maths problems should be based on real-world use cases where not all needed data is immediately available and there is also useless data that must be discarded. He believes that the most important thing is developing mathematical problem solving skills basically the things that I did for fun when I was in primary school are skills that need to be taught to high-school students The Atlantic magazine has an amusing article by Daniel Byman and Christine Fair about the incompetent Islamic terrorists [4]. In Afghanistan half the suicide bombers kill only themselves and the US government has a lot of evidence of Taliban soldiers practicing bestiality and collecting porn. Islamic extremist groups are staffed by people who are bad soldiers and bad Muslims. Jon Masters wrote an interesting post titled What Would Jesus Buy about ethical purchasing decisions [5]. Jon references The Church of Stop Shopping which isn t a real religious organisation but a street theatre activist group. ZeroHedga has an insightful article comparing corporations and the US government to street gangs [6]. The conclusion is that when gangs take over a neighbourhood everyone has to join a gang for their own protection. Hillel Cooperman gave an interesting TED talk about being obsessed with Lego [7]. He compares Lego fans to Furries and makes a good case for this comparison. Marian Bantjes gave an interesting TED talk about her graphic art / graphic design work [8]. I ve never seen anything quite like this. Business Insider has an interesting article about oil cleanup, it seems that most people who worked on the Exxon Valdez disaster are now dead [9], s opposed to most people who worked in almost every other occupation at that time who are either still working or enjoying their retirement. The current gulf disaster is bigger, will require more workers for the cleanup, and can be expected to have a higher death toll. Some people claim that measures to reduce oil efficiency will impact the economy, how will millions of people who are chronically ill for the rest of their lives impact the economy? The NY Times has an interesting article on circle lenses [10], contact lenses designed to make the eyes look larger. It s illegal to sell contact lenses in the US without a prescription, but the latest trend is for women to buy them online in a variety of colors. The FDA should probably approve them, it would be better to have the quality controls you expect from a medical supply company instead of having people rely on Malaysian mail-order companies for the safety of their eyes. Don Marti has written an interesting article about the economic decline in the US, he suggests making pension funds invest in local jobs [11]. Companies are supposed to act on behalf of their stock-holders, but US companies often have the majority of their stock owned by the pension funds of workers but they act on behalf of a small number of rich people who own a minority of the stock. Don s article was inspired by Andy Grove s article in Bloomberg about the stagnation in technological development that has been caused by off-shoring the manufacturing [12]. Neil Brown has completed a test release of a new Linux software RAID feature for arrays with multiple redundancy that have bad sectors [13]. When a disk gets a bad sector the current behavior is to kick it out of the array, if you have two such errors on a 3 disk RAID-1 or a RAID-6 array then you lose all redundancy and are at risk of catastrophic failure even though in most cases both disks will still mostly work. With this patch some regions of the disk may be excluded but it can provide redundancy for other stripes. Thanks Neil for your great work here, and all your previous work over the last 10+ years! The RSPCA has a new campaign titled Close the Puppy Factories [14]. Dogs are kept in very poor conditions and forced to churn out puppies for their entire lives to supply pet stores. The RSPCA recommends that people buy puppies from registered dog breeders (not registered dog breeding companies ) and ask to see the dog s parents. They also recommend not buying from classified adverts or pet stores. Animal shelters have to euthenise huge numbers of unwanted animals, you can buy a pet dog or cat from an animal shelter for a small fee that covers the expenses related to housing and spaying it and save that animal from being euthenised! Maureen Dowd criticises the Catholic Church properly in an article for the New York Times [15]. The Catholic Church officially regards ordaining a woman and raping a child to be equally bad offenses. Frank Rich wrote an interesting column for the New York Times about Mel Gibson [16]. He describes the destruction of Mel Gibson s reputation as a symptom of changes in the culture in the US and also links it to the fall of Ted Haggard (who supported Gibson s most notorious movie The Passion of the Christ).

Stefano Zacchiroli: RCBC - release critical bugs contest

Recipe for RCBC - Release Critical Bug squashing Contest:
squash RC bugs for 2 weeks , from July 25th to August 7th
help the release of Debian Squeeze
earn fame and glory (for sure)
win a GuruPlug and other geeky gadgets (maybe)
read on for more info ...
It has been a while since my last post in the RCBW tradition. Luckily, the tradition is in very good health of its own, thanks to many others that have picked up the habit of SPAM-ing planet with good news for Debian, encouraging others to do the same. With all that RC-obsessed people around and with the Squeeze release forthcoming, can DebConf10 be devoid of geeky RC-squashing activities? Of course not! Thanks to the orga team we expect the conference to contain a 2-week long RC bug squashing pride with tutorials, BoFs, a permanent bug squashing party, ... and a contest! I won't indulge much on the contest as the wiki page contains all rules and gory details. Obviously, all usual rules and best practices of bug squashing parties will apply; coordination will happen on #debian-bugs. Get involved, it starts today, and it's open to everyone (DebConf10 attendees as well as Debian enthusiasts abroad, regular RC squashers as well as casual bystanders, etc). All this wouldn't have been possible without the help of many people that love Debian, so many thanks to: PS a corresponding announcement is in the debconf-announce pipeline already

Russell Coker: SE Linux audit2allow -R and Milter policy

Since the earliest days there has been a command named audit2allow that takes audit messages of operations that SE Linux denied and produces policy that will permit those operations. A lesser known option for this program is the -R option to use the interfaces from the Reference Policy (the newer version of the policy that was introduced a few years ago). I have updated my SE Linux repository for Lenny [1] with new packages of policy and python-sepolgen that fix some bugs that stopped this from being usable. To use the -R option you have to install the selinux-policy-dev package and then run the command sepolgen-ifgen to generate the list of interfaces (for Squeeze I will probably make the postinst script of selinux-policy-dev do this). Doing this on Lenny requires selinux-policy-default version 0.0.20080702-20 or better and doing this on Debian/Unstable now requires selinux-policy-default version 0.2.20100524-2 (which is now in Testing) or better. Would it be useful if I maintained my own repository of SE Linux packages from Debian/Unstable that can be used with Debian/Testing? You can use preferences to get a few packages from Unstable with the majority from Testing, but that s inconvenient and anyone who wants to test the latest SE Linux stuff would need to include all SE Linux related packages to avoid missing an important update. If I was to use my own repository I would only include packages that provide a significant difference and let the trivial changes migrate through Testing in the normal way. The new Lenny policy includes a back-port of the new Milter policy from Unstable, this makes it a lot easier to write policy for milters. Here is an example of the basic policy for two milters, it allows the milters (with domains foo_milter_t and bar_milter_t) to start, to receive connections from mail servers, and to create PID files and Unix domain sockets. policy_module(localmilter,1.0.0)

milter_template(foo)
files_pid_filetrans(foo_milter_t, foo_milter_data_t, sock_file file )

milter_template(bar)
files_pid_filetrans(bar_milter_t, bar_milter_data_t, sock_file file )
allow bar_milter_t self:process signull;
type bar_milter_tmp_t;
files_tmp_file(bar_milter_tmp_t)
files_tmp_filetrans(bar_milter_t, bar_milter_tmp_t, file)
manage_files_pattern(bar_milter_t, tmp_t, bar_milter_tmp_t) After generating that policy I ran a test system in permissive mode and sent a test message. I ran audit2allow on the resulting AVC messages from /var/log/audit/audit.log and got the following output: #============= bar_milter_t ==============
allow bar_milter_t bin_t:dir search;
allow bar_milter_t bin_t:file getattr;
allow bar_milter_t home_root_t:dir search;
allow bar_milter_t ld_so_cache_t:file read getattr ;
allow bar_milter_t lib_t:file execute;
allow bar_milter_t mysqld_port_t:tcp_socket name_connect;
allow bar_milter_t net_conf_t:file read getattr ioctl ;
allow bar_milter_t self:process signal;
allow bar_milter_t self:tcp_socket read write create connect setopt ;
allow bar_milter_t unlabeled_t:association recvfrom sendto ;
allow bar_milter_t unlabeled_t:packet recv send ;
allow bar_milter_t urandom_device_t:chr_file read;
allow bar_milter_t usr_t:file read getattr ioctl ;
allow bar_milter_t usr_t:lnk_file read;
#============= foo_milter_t ==============
allow foo_milter_t ld_so_cache_t:file read getattr ;
allow foo_milter_t lib_t:file execute;
allow foo_milter_t mysqld_port_t:tcp_socket name_connect;
allow foo_milter_t net_conf_t:file read getattr ;
allow foo_milter_t self:capability setuid setgid ;
allow foo_milter_t self:tcp_socket write setopt shutdown read create connect ;
allow foo_milter_t unlabeled_t:association recvfrom sendto ;
allow foo_milter_t unlabeled_t:packet recv send ; Running the audit2allow command with the -R option gives the following output, it includes the require section that is needed for generating policy modules:
require
type sshd_t;
type ld_so_cache_t;
type bar_milter_t;
type foo_milter_t;
class process signal;
class tcp_socket setopt read create write connect shutdown ;
class capability setuid setgid ;
class fd use;
class file read getattr ;

#============= bar_milter_t ==============
allow bar_milter_t ld_so_cache_t:file read getattr ;
allow bar_milter_t self:process signal;
allow bar_milter_t self:tcp_socket read write create connect setopt ;
corecmd_getattr_sbin_files(bar_milter_t)
corecmd_search_sbin(bar_milter_t)
corenet_sendrecv_unlabeled_packets(bar_milter_t)
corenet_tcp_connect_mysqld_port(bar_milter_t)
dev_read_urand(bar_milter_t)
files_read_usr_files(bar_milter_t)
files_read_usr_symlinks(bar_milter_t)
files_search_home(bar_milter_t)
kernel_sendrecv_unlabeled_association(bar_milter_t)
libs_exec_lib_files(bar_milter_t)
sysnet_read_config(bar_milter_t)
#============= foo_milter_t ==============
allow foo_milter_t ld_so_cache_t:file read getattr ;
allow foo_milter_t self:capability setuid setgid ;
allow foo_milter_t self:tcp_socket write setopt shutdown read create connect ;
corenet_sendrecv_unlabeled_packets(foo_milter_t)
corenet_tcp_connect_mysqld_port(foo_milter_t)
kernel_sendrecv_unlabeled_association(foo_milter_t)
libs_exec_lib_files(foo_milter_t)
sysnet_read_config(foo_milter_t) To get this working I removed the require lines for foo_milter_t and bar_milter_t as it s not permitted to both define a type and require it in the same module. Then I replaced the set of tcp_socket operations write setopt shutdown read create connect with create_socket_perms as it s easiest to allow all the operations in that set and doesn t give any security risks. Finally I replaced the mysql lines such as corenet_tcp_connect_mysqld_port(foo_milter_t) with sections such as the following:
mysql_tcp_connect(foo_milter_t)
optional_policy(
mysql_stream_connect(foo_milter_t)
) This gives it all the access it needs and additionally the optional policy will allow Unix domain socket connections for the case where the mysqld is running on localhost.

22 July 2010

Erich Schubert: Dropbox revisited

Like one or two years ago, I got myself a free Dropbox account. I use it occasionally to exchange files with some friends. It does an excellent job at that. Basically, it works like any network folder. Except it is not within a local network, but over the internet.Dropbox serves me as an occasional replacement for both email and USB pen drive. Instead of sending a modified file by email or bringing around a dozen of photos on a USB stick, I just put them into the shared folder. This also very useful for files such as flyers, templates. They may easily grow to big to be sensibly sent by email.For all my use, a regular free Dropbox account is more than enough. As in, I have less than 1 GB in use, and I could easily free some of that space. You start at 2 GB, and can currently get up to 10 GB free (+250 MB for each referrer; if you use the link above you'll already start at 2.25 GB). But for my use, this is already a lot.Note that there are a couple of alternatives around. For Linux (only) there is Ubuntu One, and there is Zumo Drive and Box.net just to name a few. I havn't tried them, given that Dropbox works for me well enough.

Stefano Zacchiroli: debian podcast planning

This Week In Debian I've been contacted by Jonathan Nadeau of Frostbite Systems, a company selling computer hardware with pre-installed GNU/Linux distros, including Debian (of course!). (Usual disclaimer applies: I haven't tried their products, I've just skimmed through their website ...) Both for promotion and as a service to the communities, Jonathan has started various podcasts, such as This Week in Fedora. Jonathan has contacted me to check whether Debian is interested in having a This Week in Debian podcast, which will be discussing weekly Debian-related topics, interviewing at each episode someone from the community. So, folks, are you interested in seeing that happen?
Personally I like the idea, as I'm myself an eager podcast listener and I've always missed something Debian-specific. To make it a reality however we need to plan and record some episode in advance, to ensure the podcast will have enough "buffer" to start. That's why I've created the ThisWeekInDebian wiki page, where interested people should drop a line, proposing a topic and volunteering to speak about it. Any Debian-related topic is a good candidate: a team, an initiative, a general discussion about a relevant project aspect, etc. You don't even need any particular upfront preparation, as it'll be interview-like. So, what are you waiting for? Drop a line to the wiki page. Jonathan will attend DebConf10 so, in case you are attending, that can be a nice occasion to record some episode in person (otherwise recordings usually happen over the net).

John Goerzen: Once, We Were Makers

I saw an article on Wired today: The Lost Tribes of RadioShack. It is well worth the read even if you re not into electronics. A key quote:
[H]is shop is a lone outpost; in a single generation, the American who built, repaired, and tinkered with technology has evolved into an entirely new species: the American who prefers to slip that technology out of his pocket and show off its killer apps. Once, we were makers. Now most of us are users.
I remember as a kid eagerly awaiting each year s new RadioShack catalog. I d read them pretty much cover to cover for fun. And who wouldn t? The catalogs had fun things like radios, telephone gadgets, calculators, tape recorders, electronic lab kits , books, components, LEDs I loved the catalogs and loved the store. My parents bought me a electronic kit (if memory serves 20 years later, it s the deluxe 160-project electronic kit from page 156 of the 1988 catalog, though it may have been purchased a different year). I had endless fun with that thing. It had resistors, diode, capacitors, oscillator, speaker, LED, relay, etc plenty to make a bunch of kid-friendly projects. Just looking at the catalog makes me excited even today. On the next page from the kit I had is a $5 crystal radio kit which needs no power source Solderless. With earphone, instructions, theory. On page 28 there was a revolving red light, and some microcassette recorders on p. 36 (I had one of those for awhile). I had enthusiasm for building and figuring out things for a long time. My dad let me take apart an old lawn mower for fun once I m sure he knew ahead of time it would never be back together. One of his friends from work built homemade contraptions out of things like an old vacuum cleaner (attach a cardboard tube to the exhaust and you get a great tennis ball shooter). And there was always all sorts of fun junk to discover up in the barn. I eventually shifted to a different sort of making things : programming. It has kept me busy for quite a number of years. But the Wired article has a point. RadioShack is struggling. Many people have no interest in making or fixing things anymore. The best-selling smartphone in the world comes sealed in a metal case where not even the battery can be replaced, the software is dictated by a company in California, and good luck trying to program for it without signing your life away first. A far cry from the first computer I used, a TRS-80 Color Computer II, bought, yes, at RadioShack. Turn it on, and in a few seconds you get a BASIC prompt. Can t really use it without programming. Being able to read its manual was an early motivation for me to work at learning to read. It is sad that so many devices can t be worked on anymore, and that so many people don t care. It is difficult for me to give Jacob (and later, Oliver) the sort of experience I had as a child. Companies would love to sell us $50 DVD sets, $300 educational game systems, $40 educational games, and any number of $30 plastic toys (some of which we have and the boys enjoy). I d rather give him a $10 bag of resistors, capacitors, wire, battery holders, LEDs, and a book, and see what he can come up with (when he s a bit older, of course). And, in fact, he and I built his first computer together. We installed the ultimate in operating systems for tinkering: Linux. This all brings me back to RadioShack. I ve been working on ham radio lately, with an eye to that being a project for Jacob (age 3.5), Oliver (just turned 1), and me to enjoy in the future. I needed some cable, and had been told by many people to visit the RadioShack in Derby, KS. It s like the one mentioned in the Wired article: huge, selling everything from washing machines to bulk cable, except this one specializes in amateur radio. I asked Jacob if he would like to come with me to a radio store. Dad, I would LOVE that! He brought his little semi-broken walkie-talkies with him to use during the hour drive there. At one point, he was concerned that a radio store is like a library and he might have to leave them on a shelf. I assured him he could keep them. We got to the RadioShack and he loved it. He couldn t even really contain his excitement. He ran back and forth along the bright green stripe running down the middle of the carpet. He excitedly watched them measure out 60ft of RG-8 coax for me. He pushed buttons on the demo clothes dryer, looked at all the antennas, and just had a great time. And he s been interested in my radio, too. When I was talking to somebody on it the other day, he said, I think he is at the radio store. He is having fun there. Right now, everybody I talk to on the radio is at the radio store to him. Jacob loves the fact that the backlight on my FT-857D can change colors, and often comes into the office just so I can put it into setup mode and let him spin the big wheel to change the colors. He enjoys opening boxes of components, and came out to help (and run around) while I suspended a dipole from some trees last Friday. I had told Jacob when we got to the store that This radio store is called RadioShack. He obviously took that to heart, because now if he hears me talking about a radio store , he will say, Dad, actually it is radio SHACK. So I say thank you to the Derby RadioShack for keeping the magic of making things with your dad alive for another generation.

20 July 2010

Ond&#345;ej &#268;ert&iacute;k: Theoretical Physics Reference Book

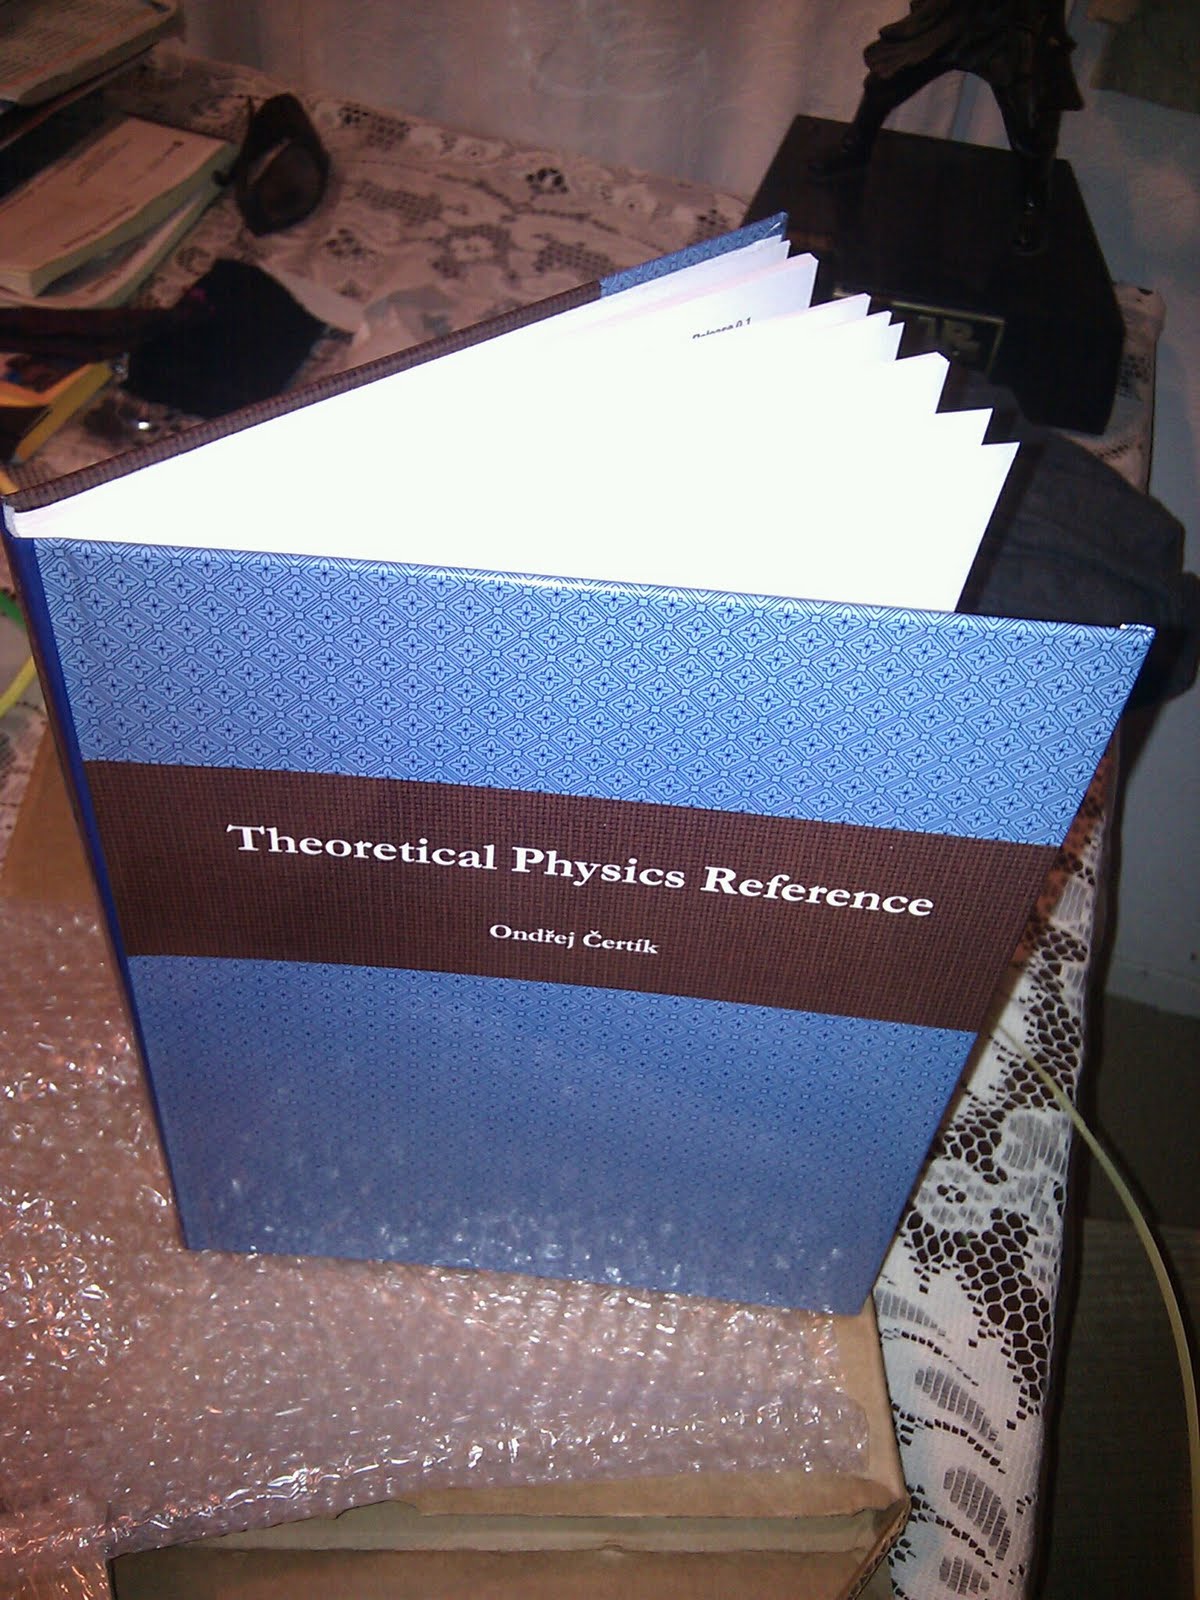
Today I fulfilled my old dream --- I just created my first book! Here is how it looks like:

More images
here.

Here is the source code of the book: http://github.com/certik/theoretical-physics, the repository contains a branch 'master' with the code and 'gh-pages' with the generated html pages, that are hosted at github, at the url theoretical-physics.net.

Then I published the book at Lulu: http://www.lulu.com/product/hardcover/theoretical-physics-reference/11612144, I wanted a hardcover book, so I setup a project at Lulu, used some Lulu templates for the cover and that was it. Lulu's price for the book is $19.20 (166 black & white pages, hardcover), then I can set my own price and the rest of the money probably goes to me. I set the price to $20, because Lulu has free shipping for orders $20 or more. You can also download the pdf (for free) at the above link (or just use my git repository). So far this didn't cost me anything.

I have then ordered the book myself (just like anybody else would, at the above address) and it arrived today. It's a regular hardcover book. Beautiful, you can browse the pictures above. It smells deliciously (that you have to believe me). And all that it cost me was $19.20.

As for the contents itself, you can browse it online at theoretical-physics.net, essentially it's most of my physics notes, that I collected over the years. I'd like to treat books like software --- release early release often. This is my first release and I would call it beta. The main purpose of it was to see if everything goes through, how long it takes (the date inside the book is July 4, 2010, I created and ordered it on July 5, got the physical book on July 19) and what the quality is (excellent). I also wanted to see how the pages correspond to the pdf (you can see for yourself on the photos, click on the picasa link above).

Now I need to improve the first pages a bit, as well as the last pages, improve the index, write some foreword and so on. I also need to think how to better organize the contents itself and generally improve it. I also need to figure out some versioning scheme, so far this is version 0.1. I think I'll do edition 1, edition 2, edition 3, and so on. And whenever I feel that I have added enough new content, I'll just publish it as a new edition. So if you want to buy it, I suggest to wait for my 1.0 version, that will have the mentioned improvements.

It'd be also cool to have all the editions online somehow and create nice webpages for it (currently theoretical-physics.net points directly to the book html itself).

So far the book is just text. I still need to figure out how to handle pictures and also whether or not to use program examples (in Python, using sympy, scipy, etc.). So far I am inclining not to put there any program codes, as then I don't need to maintain them.

Overall I am very pleased with the quality, up to some minor issues that I mentioned above, everything else end up just fine. I think we have come a long way from the discovery of the printing press. Anybody can now create a book for free, and if you want to hold the hardcopy in your hands, it costs around $20. You don't need to order certain amounts of books, nor partner with some publisher etc. I think that's just awesome.

19 July 2010

Andreas Barth: How to autorotate images?

I'm still receiving messages by fax. Sometimes pages get inserted wrong (head-down). To make my life easier, I'd like to execute code which automatically rotates the page if it was inserted with bottom first - any idea if there is free software suiteable to recognize if it's wrong (I won't mind if hand-written pages appear wrong - if it works in 90% of the cases, I'm entirely happy).

17 July 2010

Joachim Breitner: How forky may one maintain a Debian package?

I maintain most of my Debian packages because I use them myself. Sometimes, I have some needs that go slightly beyond what is currently offered by the software. This is not a problem: Debian ships Free Software and I can program, therefore I can patch the software to also do what I want it to do. Trying to be a good member of the Free Software community, I then submit the patch to the upstream author. If he accepts the patch (which is usually the case), everything is fine. But what if he does not reply to the report or rejects it because he does not want this feature (although the patch is technically fine)? I see two options:
  1. I could continue to use a privately patched and built version of the package, while separately building packages for Debian. This way, Debian ships the software as intended by the upstream maintainer while I can use the features I need. On the other hand, I would not be using the version that I upload to Debian, which is not good, and it causes double work when a a new version is released.
  2. I could upload a package to Debian that contains my patch. The technical infrastructure to add patch in Debian packages has always been there... I would actually use the package as it is in Debian and only manage one line of versions. But would I be abusing my powers as a Debian maintainer? If I were not the maintainer, I could not make this decision by myself (this happend with my patch to nagstamon). Plus it could have a negative effect on the Debian-upstream relationship.
How do other Debian Developers handle such issues? The actual case I m considering is a feature enhancement for link-monitor-applet (but I only just wrote the patch, so it does not yet fall in the category upstream does not reply ).

Petter Reinholdtsen: What are they searching for - PowerDNS and ISC DHCP in LDAP

This is a followup on my previous work on merging all the computer related LDAP objects in Debian Edu. As a step to try to see if it possible to merge the DNS and DHCP LDAP objects, I have had a look at how the packages pdns-backend-ldap and dhcp3-server-ldap in Debian use the LDAP server. The two implementations are quite different in how they use LDAP. To get this information, I started slapd with debugging enabled and dumped the debug output to a file to get the LDAP searches performed on a Debian Edu main-server. Here is a summary. powerdns Clues on how to set up PowerDNS to use a LDAP backend is available on the web. PowerDNS have two modes of operation using LDAP as its backend. One "strict" mode where the forward and reverse DNS lookups are done using the same LDAP objects, and a "tree" mode where the forward and reverse entries are in two different subtrees in LDAP with a structure based on the DNS names, as in tjener.intern and 2.2.0.10.in-addr.arpa. In tree mode, the server is set up to use a LDAP subtree as its base, and uses a "base" scoped search for the DNS name by adding "dc=tjener,dc=intern," to the base with a filter for "(associateddomain=tjener.intern)" for the forward entry and "dc=2,dc=2,dc=0,dc=10,dc=in-addr,dc=arpa," with a filter for "(associateddomain=2.2.0.10.in-addr.arpa)" for the reverse entry. For forward entries, it is looking for attributes named dnsttl, arecord, nsrecord, cnamerecord, soarecord, ptrrecord, hinforecord, mxrecord, txtrecord, rprecord, afsdbrecord, keyrecord, aaaarecord, locrecord, srvrecord, naptrrecord, kxrecord, certrecord, dsrecord, sshfprecord, ipseckeyrecord, rrsigrecord, nsecrecord, dnskeyrecord, dhcidrecord, spfrecord and modifytimestamp. For reverse entries it is looking for the attributes dnsttl, arecord, nsrecord, cnamerecord, soarecord, ptrrecord, hinforecord, mxrecord, txtrecord, rprecord, aaaarecord, locrecord, srvrecord, naptrrecord and modifytimestamp. The equivalent ldapsearch commands could look like this:
ldapsearch -h ldap \
  -b dc=tjener,dc=intern,ou=hosts,dc=skole,dc=skolelinux,dc=no \
  -s base -x '(associateddomain=tjener.intern)' dNSTTL aRecord nSRecord \
  cNAMERecord sOARecord pTRRecord hInfoRecord mXRecord tXTRecord \
  rPRecord aFSDBRecord KeyRecord aAAARecord lOCRecord sRVRecord \
  nAPTRRecord kXRecord certRecord dSRecord sSHFPRecord iPSecKeyRecord \
  rRSIGRecord nSECRecord dNSKeyRecord dHCIDRecord sPFRecord modifyTimestamp
ldapsearch -h ldap \
  -b dc=2,dc=2,dc=0,dc=10,dc=in-addr,dc=arpa,ou=hosts,dc=skole,dc=skolelinux,dc=no \
  -s base -x '(associateddomain=2.2.0.10.in-addr.arpa)'
  dnsttl, arecord, nsrecord, cnamerecord soarecord ptrrecord \
  hinforecord mxrecord txtrecord rprecord aaaarecord locrecord \
  srvrecord naptrrecord modifytimestamp
In Debian Edu/Lenny, the PowerDNS tree mode is used with ou=hosts,dc=skole,dc=skolelinux,dc=no as the base, and these are two example LDAP objects used there. In addition to these objects, the parent objects all th way up to ou=hosts,dc=skole,dc=skolelinux,dc=no also exist.
dn: dc=tjener,dc=intern,ou=hosts,dc=skole,dc=skolelinux,dc=no
objectclass: top
objectclass: dnsdomain
objectclass: domainrelatedobject
dc: tjener
arecord: 10.0.2.2
associateddomain: tjener.intern
dn: dc=2,dc=2,dc=0,dc=10,dc=in-addr,dc=arpa,ou=hosts,dc=skole,dc=skolelinux,dc=no
objectclass: top
objectclass: dnsdomain2
objectclass: domainrelatedobject
dc: 2
ptrrecord: tjener.intern
associateddomain: 2.2.0.10.in-addr.arpa
In strict mode, the server behaves differently. When looking for forward DNS entries, it is doing a "subtree" scoped search with the same base as in the tree mode for a object with filter "(associateddomain=tjener.intern)" and requests the attributes dnsttl, arecord, nsrecord, cnamerecord, soarecord, ptrrecord, hinforecord, mxrecord, txtrecord, rprecord, aaaarecord, locrecord, srvrecord, naptrrecord and modifytimestamp. For reverse entires it also do a subtree scoped search but this time the filter is "(arecord=10.0.2.2)" and the requested attributes are associateddomain, dnsttl and modifytimestamp. In short, in strict mode the objects with ptrrecord go away, and the arecord attribute in the forward object is used instead. The forward and reverse searches can be simulated using ldapsearch like this:
ldapsearch -h ldap -b ou=hosts,dc=skole,dc=skolelinux,dc=no -s sub -x \
  '(associateddomain=tjener.intern)' dNSTTL aRecord nSRecord \
  cNAMERecord sOARecord pTRRecord hInfoRecord mXRecord tXTRecord \
  rPRecord aFSDBRecord KeyRecord aAAARecord lOCRecord sRVRecord \
  nAPTRRecord kXRecord certRecord dSRecord sSHFPRecord iPSecKeyRecord \
  rRSIGRecord nSECRecord dNSKeyRecord dHCIDRecord sPFRecord modifyTimestamp
ldapsearch -h ldap -b ou=hosts,dc=skole,dc=skolelinux,dc=no -s sub -x \
  '(arecord=10.0.2.2)' associateddomain dnsttl modifytimestamp
In addition to the forward and reverse searches , there is also a search for SOA records, which behave similar to the forward and reverse lookups. A thing to note with the PowerDNS behaviour is that it do not specify any objectclass names, and instead look for the attributes it need to generate a DNS reply. This make it able to work with any objectclass that provide the needed attributes. The attributes are normally provided in the cosine (RFC 1274) and dnsdomain2 schemas. The latter is used for reverse entries like ptrrecord and recent DNS additions like aaaarecord and srvrecord. In Debian Edu, we have created DNS objects using the object classes dcobject (for dc), dnsdomain or dnsdomain2 (structural, for the DNS attributes) and domainrelatedobject (for associatedDomain). The use of structural object classes make it impossible to combine these classes with the object classes used by DHCP. There are other schemas that could be used too, for example the dnszone structural object class used by Gosa and bind-sdb for the DNS attributes combined with the domainrelatedobject object class, but in this case some unused attributes would have to be included as well (zonename and relativedomainname). My proposal for Debian Edu would be to switch PowerDNS to strict mode and not use any of the existing objectclasses (dnsdomain, dnsdomain2 and dnszone) when one want to combine the DNS information with DHCP information, and instead create a auxiliary object class defined something like this (using the attributes defined for dnsdomain and dnsdomain2 or dnszone):
objectclass ( some-oid NAME 'dnsDomainAux'
    SUP top
    AUXILIARY
    MAY ( ARecord $ MDRecord $ MXRecord $ NSRecord $ SOARecord $ CNAMERecord $
          DNSTTL $ DNSClass $ PTRRecord $ HINFORecord $ MINFORecord $
          TXTRecord $ SIGRecord $ KEYRecord $ AAAARecord $ LOCRecord $
          NXTRecord $ SRVRecord $ NAPTRRecord $ KXRecord $ CERTRecord $
          A6Record $ DNAMERecord
    ))
This will allow any object to become a DNS entry when combined with the domainrelatedobject object class, and allow any entity to include all the attributes PowerDNS wants. I've sent an email to the PowerDNS developers asking for their view on this schema and if they are interested in providing such schema with PowerDNS, and I hope my message will be accepted into their mailing list soon. ISC dhcp The DHCP server searches for specific objectclass and requests all the object attributes, and then uses the attributes it want. This make it harder to figure out exactly what attributes are used, but thanks to the working example in Debian Edu I can at least get an idea what is needed without having to read the source code. In the DHCP server configuration, the LDAP base to use and the search filter to use to locate the correct dhcpServer entity is stored. These are the relevant entries from /etc/dhcp3/dhcpd.conf:
ldap-base-dn "dc=skole,dc=skolelinux,dc=no";
ldap-dhcp-server-cn "dhcp";
The DHCP server uses this information to nest all the DHCP configuration it need. The cn "dhcp" is located using the given LDAP base and the filter "(&(objectClass=dhcpServer)(cn=dhcp))". The search result is this entry:
dn: cn=dhcp,dc=skole,dc=skolelinux,dc=no
cn: dhcp
objectClass: top
objectClass: dhcpServer
dhcpServiceDN: cn=DHCP Config,dc=skole,dc=skolelinux,dc=no
The content of the dhcpServiceDN attribute is next used to locate the subtree with DHCP configuration. The DHCP configuration subtree base is located using a base scope search with base "cn=DHCP Config,dc=skole,dc=skolelinux,dc=no" and filter "(&(objectClass=dhcpService)( (dhcpPrimaryDN=cn=dhcp,dc=skole,dc=skolelinux,dc=no)(dhcpSecondaryDN=cn=dhcp,dc=skole,dc=skolelinux,dc=no)))". The search result is this entry:
dn: cn=DHCP Config,dc=skole,dc=skolelinux,dc=no
cn: DHCP Config
objectClass: top
objectClass: dhcpService
objectClass: dhcpOptions
dhcpPrimaryDN: cn=dhcp, dc=skole,dc=skolelinux,dc=no
dhcpStatements: ddns-update-style none
dhcpStatements: authoritative
dhcpOption: smtp-server code 69 = array of ip-address
dhcpOption: www-server code 72 = array of ip-address
dhcpOption: wpad-url code 252 = text
Next, the entire subtree is processed, one level at the time. When all the DHCP configuration is loaded, it is ready to receive requests. The subtree in Debian Edu contain objects with object classes top/dhcpService/dhcpOptions, top/dhcpSharedNetwork/dhcpOptions, top/dhcpSubnet, top/dhcpGroup and top/dhcpHost. These provide options and information about netmasks, dynamic range etc. Leaving out the details here because it is not relevant for the focus of my investigation, which is to see if it is possible to merge dns and dhcp related computer objects. When a DHCP request come in, LDAP is searched for the MAC address of the client (00:00:00:00:00:00 in this example), using a subtree scoped search with "cn=DHCP Config,dc=skole,dc=skolelinux,dc=no" as the base and "(&(objectClass=dhcpHost)(dhcpHWAddress=ethernet 00:00:00:00:00:00))" as the filter. This is what a host object look like:
dn: cn=hostname,cn=group1,cn=THINCLIENTS,cn=DHCP Config,dc=skole,dc=skolelinux,dc=no
cn: hostname
objectClass: top
objectClass: dhcpHost
dhcpHWAddress: ethernet 00:00:00:00:00:00
dhcpStatements: fixed-address hostname
There is less flexiblity in the way LDAP searches are done here. The object classes need to have fixed names, and the configuration need to be stored in a fairly specific LDAP structure. On the positive side, the invidiual dhcpHost entires can be anywhere without the DN pointed to by the dhcpServer entries. The latter should make it possible to group all host entries in a subtree next to the configuration entries, and this subtree can also be shared with the DNS server if the schema proposed above is combined with the dhcpHost structural object class. Conclusion The PowerDNS implementation seem to be very flexible when it come to which LDAP schemas to use. While its "tree" mode is rigid when it come to the the LDAP structure, the "strict" mode is very flexible, allowing DNS objects to be stored anywhere under the base cn specified in the configuration. The DHCP implementation on the other hand is very inflexible, both regarding which LDAP schemas to use and which LDAP structure to use. I guess one could implement ones own schema, as long as the objectclasses and attributes have the names used, but this do not really help when the DHCP subtree need to have a fairly fixed structure. Based on the observed behaviour, I suspect a LDAP structure like this might work for Debian Edu:
ou=services
  cn=machine-info (dhcpService) - dhcpServiceDN points here
    cn=dhcp (dhcpServer)
    cn=dhcp-internal (dhcpSharedNetwork/dhcpOptions)
      cn=10.0.2.0 (dhcpSubnet)
        cn=group1 (dhcpGroup/dhcpOptions)
    cn=dhcp-thinclients (dhcpSharedNetwork/dhcpOptions)
      cn=192.168.0.0 (dhcpSubnet)
        cn=group1 (dhcpGroup/dhcpOptions)
    ou=machines - PowerDNS base points here
      cn=hostname (dhcpHost/domainrelatedobject/dnsDomainAux)
This is not tested yet. If the DHCP server require the dhcpHost entries to be in the dhcpGroup subtrees, the entries can be stored there instead of a common machines subtree, and the PowerDNS base would have to be moved one level up to the machine-info subtree. The combined object under the machines subtree would look something like this:
dn: dc=hostname,ou=machines,cn=machine-info,dc=skole,dc=skolelinux,dc=no
dc: hostname
objectClass: top
objectClass: dhcpHost
objectclass: domainrelatedobject
objectclass: dnsDomainAux
associateddomain: hostname.intern
arecord: 10.11.12.13
dhcpHWAddress: ethernet 00:00:00:00:00:00
dhcpStatements: fixed-address hostname.intern
One could even add the LTSP configuration associated with a given machine, as long as the required attributes are available in a auxiliary object class.

Gregory Colpart: Network connection with HTC Hero and Debian

I have an HTC Hero, an Android phone, for one year. But I never tried to share his network connection with my Debian laptop. To prepare my trip to Debconf10, I try it today and I m surprised because it s so easy! 1. Plug your phone on USB
2. Active Share your phone network on phone (in french: Partage du r seau mobile )
3. You see now an usb0 ethernet device:
usb0  Link encap:Ethernet  HWaddr a2:17:af:4f:fa:da
BROADCAST MULTICAST  MTU:1500  Metric:1
RX packets:0 errors:0 dropped:0 overruns:0 frame:0
TX packets:0 errors:0 dropped:0 overruns:0 carrier:0
collisions:0 lg file transmission:1000
RX bytes:0 (0.0 B)  TX bytes:0 (0.0 B)
4. Configure usb0 to have the network configuration 192.168.100.100/24 with your favorite tool (ifconfig for example).
5. Now you can ping your phone with 192.168.100.254. Use it as gateway and enjoy: your laptop is now connected with Wi-Fi, GPRS or 3G+! Note: I use HTC Hero with Android 1.5 (build number: 2.73.61.5) and the french mobile phone provider Orange.

John Goerzen: KD0MJT

Wow tonight was thrilling. It s hard to explain why, but it s pretty exciting to have a radio setup that is all wrong in so many ways work well enough for me to sit in my kitchen in Kansas and talk to someone in Indianapolis using only two-way HF radios. I recently passed my technician and general amateur radio exams. I ve been talking to some very nice people locally on the 2m band, which permits local (say, 100-200mi radius) communication. It s been fun, but Kansas is sparsely populated enough that sometimes there just isn t any activity. At all. Earlier this week, my Yaesu FT-857D and two antennas arrived. I tried it first on VHF, and had a nice chat with Kent (KB0RWI) a few miles away. But tonight was the big experiment. I bought a 20m dipole antenna. This is basically a 30-foot-long wire, connected to a balun and a coax feed line in the middle. You re supposed to put it at least 30 feet off the ground, and away from trees, houses, etc. You re supposed to have a nice RF ground for your transmitter, power supply, antenna tuner, and all that stuff. You re not supposed to just run the coax under that (until today, annoying) small hole in the seal under the kitchen storm door. You re supposed to have to have the correct connectors on your coax, instead of soldering an RG-8 PL-259 onto some RG-8X because you re new at this and didn t realize that you need to buy an adapter. And, I m really pretty sure that you re not supposed to have an aggressive outdoor cat complete with a full set of claws and teeth attack the coax RG-8X cable as it s being pulled through the grass. Fail to do any of these things, and the thing might not work well, or might not work at all, or for people that use old equipment, might burn out your radio or something. So anyway I got out the ladder today, and I got the antenna maybe 10-15 feet in the air. I have three trees in a row with the perfect separation to hang each end and the center balun from. So while Jacob went around playing with water and trying out the ladder on occasion (with my help), I used some string to hang the antenna. In the trees, not far from them. Near the house. Not 30ft off the ground. I strung the feed line into the house, set up all my equipment on our kitchen table, flipped the switch. And nothing. Just the occasional familiar whine while tuning. I tried the 20m band, then the 40m, then even 15, 12, and 10. No activity anywhere. So what was wrong? I improvised some grounding extracted the ground conductor from an old strip of AC house wiring, shoved it into the ground, and grounded the tuner and transmitter. No difference. I unplugged the coax, and tested it with my multimeter. It tested out OK. I plugged it back in and wiggled the connector. Turns out the connector isn t in great shape, but it had been working. I tried transmitting. The tuner made a whole bunch of alarming-sounding clicking noises (sounded like a symphony of relays), indicated SWR over 3, and the ammeter on my power supply went a bit nuts. Later I realized that I just wasn t giving the tuner enough time to tune up; with a few more seconds, it tuned up just fine on every frequency. (So yes, it was supposed to do that.) And, it turns out, that all I needed to do was wait a little while longer to hear some signals. Pretty soon I was finding stuff all over the 40m band. I heard a discussion from Chicago, another from Oklahoma City, some apparent broadcasters from Africa. I decided I would try and transmit. I was hearing one side of a discussion very clearly and decided I would wait for an opportunity to try to contact that person. I heard his callsign, K9RM. I looked it up, and realized he was near Indianapolis, where I had lived for awhile. Eventually he invited a station trying to get in to participate. And: KD0MJT (I announced my callsign, as a request to join the conversation) He said he only made out the 0, but eventually we were talking quite well. It was a brief conversation, but interesting; the person he was talking to was in Portland, and couldn t hear me (and I could barely hear him, but not loud enough to make out). That with no phone lines, no Internet provider needed, etc. And with a rig that is far from being at peak efficiency. I had no idea what to expect tonight and was surprised that just tossing an antenna up in a tree let me talk to someone in Indiana. That s 650 miles away. I wonder what I ll be able to do once I get things done the right way. This hobby is going to be fun. Many thanks to Mike_W for equipment suggestions, Kent and Dan from Newton ARC for encouragement and coming out to the house to test things, Kent for being my first ham radio contact ever (on 2m while I was using an old 1981 radio), Chuck (K9RM) for taking a few minutes to be my first HF contact, and my dad for helping plan out exterior wall penetration methods that will eliminate this coax under the kitchen door and lack of grounding business. Jacob, by the way, still loves his radios and is starting to take an interest in mine. It wouldn t shock me at all of he s one of these kids that gets his technician license in the 2nd grade or something. I think he and I can do this together for a long time.

16 July 2010

Patrick Schoenfeld: Facebook aggressively advertising dubious features

Yesterday some confusion arised on my side when I saw a new facebook advertising campaign in my facebook account (yes, I am a member of facebook, although I'm aware of the privacy concerns). Basically it was saying that I should try the friends finder and that some of my friends (showing and naming me three of them) would have used it already.

Some background:
The friends finder feature of facebook is a feature that asks for the password of your e-mail account. It will then crawl through your emails to find contacts that might already be on facebook but not connected to you (in a facebook sense).

My first feeling was: Oh my god. How can it be that friends (and family) of mine are so naive? Especially since there were people included which I consider to be quiet clever. But honestly: Who would be so naive to give an unknown company direct unsupervised (you can't tell what they really do) access to your mail account? Would you give it to your friend? Your husband? Your father? I guess the answer will be "No" in the most cases and these people are most likely people you trust. Well, I know, you could state similar things for Googlemail who crawl your mails to show you personalized advertising. And in fact you are right. But if one decides to use gmail for your email hosting you have to trust them anyway. Like you have to trust anybody else you retain to host your mails (who could do the same but just don't tell you). But in this case its a third party, Facebook.

But if you now think that this becomes a rant against my friends: You are wrong. Over the day I found out that it basically shows up all my friends in a rotation. Every time I open the start page it randomly picks three people from my friend list and shows them to me, telling the same lie to me all over again.

So what do we have here? Facebook tries to advertise the most dubious feature they have in the most aggressive way one could imagine. By pretending wrong facts. Wouldn't that even be an element of crime in Germany ("Irref hrung" 5 UWG or maybe also 4 UWG, "unsachliche Beeinflussung")?

Facebook, you can do better.

Update: Stefano raised a good point. I didn't actually make clear that it has been verified that those people actually did not use the "feature":

1. I asked some of them. They said, they didn't use it and were in fact surprised that I asked.
2. Others told me they saw that ad stating that I used the feature. I definitely did not use this "feature".
3. Probably weak: IMHO its highly unlikely that all of my friends used that feature and at the point I've written this it had already shown my whole friend list.

Dominique Dumont: Config::Model presentation done for Frankfurt Perl Mongers

Hello I was on business trip last week in Frankfurt. During the preparation of this trip, I had a sudden inspiration: why not benefit from this HP paid trip to meet other Perl or Debian guys. I googled for some Frankfurt am Main Perl or Debian group. (Please mind the am Main part, it s important as I ve learned there are several Frankfurt city in Germany ;-) ) I was lucky enough that Frankfurt-pm monthly meeting occurred on one free evening during my trip. So I looked for the agenda (good, they welcome presentations), subscribed to their mailing list (mostly German, but English is accepted) and proposed a presentation similar to the one I gave in Fosdem. So here I am, Tuesday evening, after a long meeting day for business, ready to give this presentation in a Japanese restaurant in Frankfurt. Since the audience was different from FOSDEM s, I offered to tune the presentation with more Perl related details. Thanks to LyX, Beamer and some evil red TeX, I quickly re-inserted some Perlish slides, and off we go. Well almost. Food came in just after the first slide. So we interrupted the session for excellent japanese plates :-p Among the audience, one guy was following the presentation with acute concentration. Max was already thinking on how to use Config::Model for Padre s configuration. After the presentations, We discussed a bit on the work needed to use Config::Model with Padre. Roughly and not necessarily in that order: Time will tell if this idea will be done or not, but I really enjoy the idea. This would be a great use case for Config::Model. All the best

15 July 2010

Enrico Zini: Released cfget 0.15

Released cfget 0.15 I have released version 0.15 of cfget. cfget is a tool to extract values from ini-style config files. A trivial thing, really. It is also simple to install: it is a single python executable and it has no dependencies besides the python standard library. It is trivial and simple, but because of the complex requirements (and sponsorship) of ISAC - CNR it has recently accumulated quite a set of features, and it manages to get a remarkable lot of things done. There are several news since 0.8, worth a rather major announcement: Added --dump=pickle Now all the contents of the configuration files, plus all the contents generated by cfget plugins, can be dumped in pickle format. This provides a quick and dirty way to load all cfget-generated data into a python dict:
data = pickle.loads(
    subprocess.Popen(
        ["cfget", "--dump=pickle"],
        stdout=subprocess.PIPE).communicate()[0])
It sounds like a rather complicated way to read a configuration file, but if you have various plugins that compute nontrivial derived configuration values, that quick&dirty hack could be quite useful. Curly brace expansion Suppose that you have a config file like this:
[general]
mode = show
[show]
command = display
[edit]
command = gimp
And you want to get the command from the section indicated by general/mode. Now you can, very easily: cfget ' general/mode /command' When it notices curly braces, cfget will literally replace them with the result of querying their contents, then parse the expression again. Simple expression support ISAC - CNR are using cfget to configure the run of a rather complicated physical model, and use plugins to derive all sorts of values form the base configuration. This works, but there are times when adding a function to a plugin sounds like overkill: for example, sometimes one needs foo/bar + 1, or just the hour of a timestamp. For those simple cases, I've added support for simple expressions: So to compute a middle point one can now do this:
cfget "round((pos/start + pos/end) / 2)"
It needs a space around arithmetic operators to avoid conflicts with characters used to refer to configuration values, but with the space the expressions look nicer, so the result is that it generally does the right thing. Just as a scary thought, curly braces work with and in expressions:
cfget "values/val round((pos/end - pos/start) / 2)  + 1"
Although if someone ends up having a hairy thing like that, it is worth considering to replace it with a dynamic value computed using a plugin.

Biella Coleman: A User s Guide to Lulzy Media, the Pleasure of Trickery, and the Politics of Spectacle: From the Luddities to Anonymous

One of my favorite conferences is HOPE, which I have missed the last 2 times as I was away from NYC, so I am glad I am around this year. I find it especially valuable when there is some controversy brewing in the air, as there is with Wikileaks, Adrian Lamo, and Manning. I am also giving a talk, description below, with a fabulous postdoctoral researcher, Finn Brunton, who works on spam! But we will be talking about pleasure, trickery, and exploitable media for activists. Our talk is late, like really late: 11:00 PM on Saturday night. At first I was a bit annoyed at the scheduling but then I figured, when will i ever give a talk at 11:00 PM?
Following a brief lecture on Project Chanology, the question will be posed: how can we harness the power of lulzy virality, of pleasure, of trickery, of spectacular trolling for purposes above and beyond sharing the wisdom of Advice Dog? It ll start with a brief look at great activist media in the past, from Guernica and the picture of the whole Earth to projects by the Yes Men - how they spread ideas and helped people get informed, organize, and act. What makes the creation of lulzy memes different? Learn about how to create exploitable forms and rapid variations, and mechanisms for bringing the best stuff forward. Can we make media memes with goals beyond lulz, and teach activists who ve never heard of 4chan to make them too? Part lecture, part workshop, this will feature cameos by Rageguy, Pablo Picasso, V, alt.pave.the.earth, Kathe Kollwitz, Courage Wolf, Stewart Brand, Sarah Palin, Batman, Goya, Philosoraptor, Adolf Hitler, Trollface, Shepard Fairey, Joseph Ducreux, David Cameron, lots of Spartan warriors, and lots and lots of (trollish) cats.

Next.

Previous.