Search Results: "cas"

5 September 2010

Jurij Smakov: Kernel config files

Long ago I've set up a small but occasionally useful service on merkel: Debian Official Kernel Configuration files. It extracts and stores the configuration files from all kernel packages ever uploaded to the archive (does not seem to work particularly well with stuff uploaded to experimental though). Now that merkel is going away, this service is likely going to die. If you care about things like that, and would like to see it continue beyond merkel's demise, feel free to grab the script code and historical config files, and set it up elsewhere (it's not likely that I'm going to bother).

Andrew McMillan: I guess I should have known better

Really, I should have known better than to buy myself a rather 'bleeding-edge' laptop. I suppose I've been lucky with my last couple of laptops and was thinking that pretty much everything works on Linux. Or maybe I'm being picky, because in fact pretty much everything does work on my new Dell Studio. I bought this laptop mainly because it has a 1920x1080 screen, without being a 17" monster. I had such a monster about four laptops ago (an enormous Sony Vaio weighing in at around 5kg and with a 1hr battery life) and it was an disaster: lots of weird proprietary stuff that never worked, like the external speakers in the docking station. But I loved that screen right up until the day Fraser threw a pair of scissors into it. With the advent of mass-market 1920x1080 screens I've been waiting for them to arrive in laptops at a reasonable price, and the availability of this screen in a few possible laptops seemed to me to be that point. It's a Dell Studio 15, and as well as the nice screen, it comes with a new Intel i7 Quad Core CPU, 6G RAM, 640G hard drive and a Blu-ray drive. While there are a few similar models around this one seemed to have the best mix of features-for-weight-and-price, so I bought my first Dell. I built a USB key with the latest Debian Installer from Squeeze and installed that and everything came up pretty well. I had to use the broadcom-sta driver for the wireless, since the BCM 43224 is not (yet) supported by the free b43 driver (though from looking the mailing list people seem to be working on it, and it looks like it might not be too far away). Everything seemed good. X came up on the (georgeous) screen. I don't care too much about 3D performance, but it was nice to note that the ATI 5000 series is expected to have full support as soon as it's integrated into the right places - it seems the code is written, and public, it just isn't incorporated into the 'radeon' driver quite yet. The fact that ATI is nowadays a free-software friendly company was one of the reasons for choosing this, in preference to an NVidia-based laptop. But it seems that it isn't all roses. The fan in the laptop seems permanently on, and not on, in a quiet-just-barely-audible way, but ON, in an 'IN UR LAPTOPZ KOOLIN UR P0RCESSAZ' kind of a way. Too damn noisy for me to concentrate in a quiet room. I've investigated what's going on, and it seems likely there are some ACPI misunderstandings happening. Some googling and some pecking around in /sys makes me wonder if the laptop expects some kind of configuration choice between favouring Active cooling and Passive cooling, and it's defaulted to the first one. Perhaps you get better benchmarks that way. Linux ACPI also seems to only half understand it, it has two thermal zones, and one of them always appears with 0 temperature. I can see set points for the fans, but have no control over them. In particular this got me out reading the ACPI 4.0 specification, and it explicitly mentions this choice of favouring 'Active' vs 'Passive' as being done by configuring the passive trip point setting to a higher value than the low & high active trip points. In the ACPI 4 spec (page 409) it says:
To implement a preference towards performance or energy conservation,
OSPM can request that the platform change the priority of active cooling
(performance) versus passive cooling (energy conservation/silence) by evaluating
the _SCP (Set Cooling Policy) object for the thermal zone or a corresponding
OS-specific interface to individual devices within a thermal zone.
This laptop is showing 'passive' at 95000 millidegrees celsius, and 'active' at 55000 / 75000 so right in line with the suggestion. However I don't see any way in Linux to change these trip point values, and in any case I'm not convinced the laptop is actually obeying them at all. It should be that if I do nothing on the laptop for a while the temperature would surely drop below 55 degrees celsius. Surely a modern laptop will sit at under 40 degrees when it's quiescent, and the temperature sensor that does show me something sits at around 30 degrees in this too, 26.8, to be overprecise. That one doesn't budge either. Looking in /sys/ I can't for the life of me find a way to set that cooling policy, and when I disassemble the DSDT it looks like a noop... Thinking that perhaps there was a newer BIOS, I looked at the Dell site and found there was one. Great! Investigating even further, it seems Dell hardware has some interesting capability via libsmbios and some utilities which will let me install my BIOS from a Linux system... even better! Linux is a second-class citizen though, and when I look for the Dell BIOS Hdr file I need there is no version of the file for this laptop - let alone the current BIOS version. And when I download the BIOS from Dell's website and unzip the first layer of packaging I find that both of the files inside will only run on Windows. I added a FreeDOS boot stanza to Grub 2 in order to discover this, also discovering in the process that this is not well explained, and I could not find how to do it on the FreeDOS or Grub2 websites, so in passing, here is what I added into /etc/grub/40_custom :
menuentry 'BIOS Flash 1558 A09' --class os  
        set root='(hd0,msdos1)'
        linux16 /boot/memdisk
        initrd16  /boot/1558_A09.img
 
Which certainly does boot FreeDOS from Grub2, into the image built from the 8M FreeDOS base image, and which I called '1558_A09.img' because that seems to be one of Dell's reference numbers for this model / BIOS version. So still no BIOS update for Andrew, it seems, and the laptop is probably going to continue to be noisy for some time. Possibly forever. Suspend/Resume works though. Kernel mode-setting for the ATI Radeon Mobility HD 5450 (or whatever it is) seems to work. Building kernels seems to work. The Blu-ray drive seems to work, at least as far as reading CDs - just because I got a laptop with a "Full HD" screen doesn't mean I watch movies on it: those pixels are for programming on! In any case, after reading the literature of pain about playing Blu-ray disks on Linux I'm convinced that we won't be shelling out to buy one any any time soon. After a bit more frustration I did manage to get the BIOS installed, using the hack I found here of running the Windows BIOS update under Wine and copying the BIOS file out of the temp directory while the error message is displayed. I could then download a random DOS-installable Phoenix BIOS to get copy of phlash16.exe and put those two files on the FreeDOS image I created earlier. Finally I was able to put that learning about how to boot FreeDOS from Grub2 to good use! Unfortunately, having jumped through all of those hoops (including the frustration of trying to build and use Dell's firmware-extract tools on a Debian system), the fan continues to grind away at annoying volume, with no way that I have been able to find to control it, and the temperature sensors also seem wrong, since one doesn't budge from 0 and the other doesn't budge from 26800. During boot I get a bunch of error messages, like:
[    1.049936] \_SB_.PCI0:_OSC invalid UUID
[    1.052202] pci 0000:00:1c.0: PME# supported from D0 D3hot D3cold
[    1.052210] pci 0000:00:1c.0: PME# disabled
[    1.065228] pci 0000:07:00.2: PME# supported from D0 D1 D2 D3hot D3cold
[    1.065237] pci 0000:07:00.2: PME# disabled
[    1.079086] Unable to assume PCIe control: Disabling ASPM
[    1.086412] HEST: Table is not found!
[    1.249906] ACPI: Fan [FAN0] (off)
[    1.249959] ACPI: Fan [FAN1] (off)
[    1.250093] [Firmware Bug]: ACPI: ACPI brightness control misses _BQC function
[    1.259118] acpi device:02: registered as cooling_device2
[    1.262132] thermal LNXTHERM:01: registered as thermal_zone0
[    1.262139] ACPI: Thermal Zone [TZ00] (27 C)
[    1.262561] thermal LNXTHERM:02: registered as thermal_zone1
[    1.262571] ACPI: Thermal Zone [TZ01] (0 C)
[    1.262598] ERST: Table is not found!
[    2.769664] i801_smbus 0000:00:1f.3: PCI INT C -> GSI 18 (level, low) -> IRQ 18
[    2.769670] ACPI: resource 0000:00:1f.3 [io  0x1840-0x185f] conflicts with ACPI
                         region SMBI [bus 1840-184f pref window disabled]
[    2.769672] ACPI: If an ACPI driver is available for this device, you should use it
                         instead of the native driver
I don't yet know what this all means, so I guess I'll be signing up for the linux-acpi mailing list to see if there's anything I can do to get things working better. Any pointers will be gratefully received :-) Right about now I wonder if maybe I should have gone for the HP or the Asus, even if they were a little heavier and a bit more expensive and next time I get a new laptop I must remember not to spend more than $900 (USD$600) on it. [Updated: 2010-09-08... Noise Problems Solved

Neil Williams: screen, irssi and page control

In case anyone else hasn't found these tweaks:
termcapinfo xterm xterms xs rxvt ti@:te@

In ~/.screenrc gives you Shift-PageUp and Shift-PageDown control again, without resorting to Ctrl-A Esc, inside screen. (Best to do
$ cp /etc/screen.rc ~/.screenrc
as a starting point first, if not done already.)

Also:
/set scroll_page_count /2
/save

In irssi itself (easier than editing the config) gives you internal PageUp, PageDown control within the irssi window.

In each case, the manpage is so long and impenetrable that these may be obvious to those with a special knowledge of terminals but mere mortals like me can't find it in / understand the docs.

3 September 2010

Alastair McKinstry: Building a statically-linked program

I'm currently working on a Fortran program at work: a post-processing tool that takes climate data, in NetCDF format, and outputs in CMOR2 format (a NetCDF variant with climate conventions). So, it links against netcdf and cmor. Now in HPC and climate in particular, codes are typically linked statically: partially for robustness, but mostly for speed (more on which later). So, I'd like to link this statically, as I have tens of terabytes of data to process. Now, mostly I've been linking using pkg-config:
  gfortran -o nemo-rewriter nemo-rewriter.f90  pkg-config --libs --cflags nemo cmor 
pkg-config assembles the libraries. For dynamic libraries, the netcdf and cmor libraries are themselves linked to dependencies. But in the static case, all dependencies need to be on the link line, which is more complex. Never mind, it should be possible with:
  gfortran -static -o nemo-rewriter nemo-rewriter.f90  pkg-config --static --libs --cflags nemo cmor 
This should work by assembling all the required static libraries, via pkg-config dependencies. Unfortunately not every package has a .pc file, and so this fails: As of version 4.1 NetCDF allows a URL instead of a file to read, and hence depends on curl to retrieve the file. Curl has no pkg-config .pc file describing its libraries, and it fails. Never mind, lets assemble the static libraries by hand. Debian provides static versions of libraries in the -dev packages. Can I assemble a statically-linked program ? For this I need: Now here it gets interesting. To handle secure communications and authentication, curl has some complex dependencies. It has two versions. Pick the gnutls one for example: I may have missed some out, having stopped because there is no static implementation of Kerberos on Debian. But still, the idea that a simple little fortran proggie will statically link in four database libraries is silly. It appears to be no longer possible to simply statically link a program in Debian, and definitely not via pkg-config, because so many dependencies do not yet have configuration files. Tags , , ,

Joerg Jaspert: Testing ChangeLog

I just merged a nice work from another ftpteam member, Luca Falavigna. He wrote dak make-changelog, which is intended for generating the changelogs for stable point releases. I took the chance and asked if he can extend it a bit, which he did, so today I could merge that work. Besides that we are able to generate ChangeLogs between all suites we have, we now generate a ChangeLog on every time we import a new set for testing, listing only the changes done in that run, by listing the changelog entries from the package, or in case of removed packages just listing their name with the removed version. We keep 4 rotations of that ChangeLog, you can find it (with the next mirror push) on all Debian mirrors in the dists/testing/ directory. This should be especially interesting for those people following testing on their systems, to easily see what got changed. :) Short update: We now keep the ChangeLog files with a date based name, deleting files which are older than 2880 minutes, so roughly keeping 2 days or 4 testing runs around, but in case we import more often (hey, possible short before a release), we keep more. There is a symlink ChangeLog always pointing to the latest file.

Richard Darst: DebConf Fundraising

The following post is the work of Pablo Duboue, the DebConf10 fundraising team leader.So you want to make DebConf, eh? You will need quite a bit of money then. That's when fundraising comes into play.There are traditionally two sources for funds for DebConf: government and businesses. A third one, micro-donors, has been mentioned, but haven't been explored yet. (Note, in this text I use the terms sponsors and donors interchangeably, as all sponsors are actually doing a donation to the Debian project earmarked for the use at a given DebConf.)Government funding has been key in a number of DebConfs. In DC10, though, by the time fundraising proper started, it was too late to secure it. Extrapolating from two DebConfs that had government funding, I would venture the following two pieces of advice: target a government level as local as possible (city, provincial level) and try to secure the funding at the time of the bid (which, by the way, can help you win the bid). A successful process will include government representatives aware of the bid status and the whole bidding process. This partnership can help unlock extra government resources such as housing or transportation. But to reiterate, if you haven't at least applied for government grants by the time the DebConf previous to yours is happening, then you have to plan to go along without government funding.Business funding for DebConf includes a significant amount of recurring donors. Keeping them happy is even more important than any money they will put forward for a given DebConf. Now, because of the high level of recurrence and the fact that government funding can cover easily one third of our costs, fundraising without government funding really means your projected funds are one third off. If that is the case, make sure to communicate that to the rest of debconf-team and even the larger Debian community (see below "asking for help").This entry has been truncated read the full entry.

2 September 2010

Russell Coker: Raw Satire Usually Fails on the Internet

Sarcasm and satire usually don t work on the Internet. One cause of this is the lack of out of band signalling via facial expression or tone of voice. Another issue is the fact that in real life people usually know something about the person who they listen to while on the Internet it s most common to read articles without knowing much about the author. So the reader can t use I know that the author isn t an asshole as a starting point to determine whether a message should be interpreted literally. This is really nothing new. The standard in printed communication for a long time has been to use Emoticons (Wikipedia) to indicate emotion and other interpretation that might not be deduced from a direct reading of the text. The Wikipedia page cites examples of emoticon use dating back to 1857 although the combinations of characters used for different emotions has changed significantly many times. The common uses that we now know on the Internet date back to 1982. In my experience the symbol :-# is commonly used to note sarcasm or satire. Unfortunately it seems that none of the Internet search engines allow searching for such strings so I couldn t find an early example of this being used. While I haven t found a reference describing this practice, I regularly receive messages annotated with it and find that people generally understand what I mean when I use it in my own email. But that is usually applied to a sentence or two. For a larger section of text a pseudo-HTML tag such as </satire> can be used to signal the end of satire. It seems that a matching start tag is optional as recognising the start of satire is a lot easier once the reader knows that some of the content is satirical. In spoken English a phrase such as but seriously may be used for the same purpose, but such a subtle signal may be missed on the Internet particularly by readers who don t use English as their first language. Another way of signaling a non-literal interpretation is by using Scare Quotes the deliberate usage of quotation symbols to indicate that the writer disagrees with the content that is written. That is common for the case of referencing a phrase or sentence that you disagree with, but doesn t work for a larger section of text. A final option is to make the satire or sarcasm so extreme that no-one can possibly mistake it for being literal. This is not always possible, Poe s Law holds that Without a winking smiley or other blatant display of humor, it is impossible to create a parody of Fundamentalism that SOMEONE won t mistake for the real thing [1]. I think that Poe was understating the case, it is impossible to create a parody of religion that most people won t mistake for the real thing without signals or context. For an example read LandOverBaptist.org and Chick.com, of course if you know those sites then you will know whether they are satirical or serious but I expect that most readers of my blog won t invest enough effort into either of those religious sites to determine whether they are serious or satire. But satire and sarcasm without signals or a reputation usually fails. One example of success is The Onion which is a long running and well known satirical news site [2]. But even The Onion it is regularly mistaken for being serious the number of occasions when people forward me Onion articles for amusement are vastly outnumbered by the number of occasions when I see people taking it seriously. Even when material is known to be satirical it can still fail grossly. An example is the Chaser s satire of the Make A Wish Foundation [3]. Even material that is well known to be satirical seems to fail when it attacks bad targets or attacks in a bad way. One difficulty is in satirising bigoted people, to effectively satirise them without attacking the minority groups that they dislike can be a difficult challenge. Finally, when you write some satire and members of your audience don t recognise it you should consider the possibility that you failed to do it properly. If you can t get a hit rate close to 100% for people with the same background as you then it s probably a serious failure.

31 August 2010

John Goerzen: Life snippets

#1: Dreams of a (almost) 4-year-old Yesterday, Terah had something going on in the evening, so it was just Jacob, Oliver, and me. Due to how the logistics worked out, she brought them to the office after work and I took them from there. We went to the post office, pharmacy, and a restaurant. Jacob and I had this conversation at the pharmacy. Jacob: Ooo! We are at the Goessel pharmacy! *claps happily* Me: Hmmm Actually Goessel doesn t have a pharmacy. This is the Hesston pharmacy. Jacob: *gets a serious look on his face* Dad, actually Goessel has a pharmacy . Look! A fire station! Me: That s right. And what can you see inside it? Jacob: FIRE TRUCKS! They are all still. Me: I guess there isn t a fire. Jacob: I think the Goessel pharmacy is on fire! Shall they go there now? Me: I hope it s not on fire. (what are you going to say to that?) Were you wanting to see a fire? Jacob: YEAH! I think it IS on fire. Shall we go see? So now he has an imaginary pharmacy with an imaginary fire and he wants to go see. Fortunately he was OK with just going inside Hesston Pharmacy instead. #2: The Songs on a Ceiling I read a book and sing a song to Jacob for bedtime every night. Over the weekends, sometimes I do that for him at nap time too. This weekend, he wanted us both to get on his bed, lie on our backs, and look at the imaginary songs on his ceiling. He gave me a whole tour, pointing to various (to me, nondescript) parts of the ceiling as he did so. Over there is a song about railroad tracks. There is one about trains. That train is upside down. That other one is stuck. There is a song about Word World. There is a song about preschool. There are the train tracks. There is a train on them. It might bump into the other train. Shall you sing a song about two trains on the tracks and they bump into the other train and go BLAM? He appeared to have a whole map in his head of his songs. The train songs were all at a specific place on the ceiling. #3: Younger Brother Oliver has really been changing lately. He occasionally will take a few steps by himself, and he has started to say a few parts of words. He communicates really well, though, especially with things he wants. He has a deep, vigorous nod to say yes, and sometimes it s accompanied by yesh for extra emphasis. His face is incredibly expressive too, and he has a distinctive Yoda-like expression at times. I almost expect to hear him say one day, Like that green bean I do not. Watermelon better is. Jacob, of course, is a lot bigger and sometimes is rough with Oliver. But they also have started to play together. Sometimes Jacob will put his head by Oliver s face. Oliver will grab fistfuls of Jacob s hair in both hands and pull. Both of them apparently find this hilarious and laugh on and on about it. #4: Viruses and Stomachs Sunday Jacob was complaining of a stomach ache. We were driving home, and shortly after we got home, he vomited on the driveway. Jacob really doesn t like throwing up. It s unpleasant and maybe a bit scary for him. He was about to start crying after vomiting, except One of our cats was hanging around. Claire came over, sniffed Jacob s vomit, and started eating it. Jacob was so fascinated by what was happening that he stopped sniffling and stood there staring at the cat, then gave an excited report of events to Terah and me. That evening, he was afraid he would throw up in bed. So we had a large bowl he held *directly* under his chin during story time. But then he didn t want to lie down, since he was afraid he d throw up in bed. Terah pointed out that he could have the bowl close while he slept. I went up and checked up on him an hour or two later, and he was sound asleep, face in the large bowl. #5: The Jukebox After the pharmacy, Jacob saw Skoops, a local 50s greasy spoon diner place across the street. He really wanted to eat there and get the birthday cake ice cream flavor. So we did. He was jabbering about getting a corn dog as we walked over, so that s what he had to eat. I don t know how he knew Skoops had them, as I don t think he s ever had a corn dog. Oh well. There s a jukebox inside Skoops, and every fifteen minutes or so, it ll spring to life and play a random song even if nobody put coins in it. This was very exciting for Oliver. He d twist all around in his highchair to watch it. And, most amusingly, he d start bopping his head. Not really in time with the music or anything, but it was cute to watch. Sometimes he d get really excited and pretty much his whole body was dancing. Well, as much dancing as you can do when you re 1 and strapped into a high chair, at any rate. One time, he heard the music, started dancing , and looked at me expectantly. So I started nodding in time with the music, and then Jacob saw us both and started sort of flailing about, somewhat in time with the music. All three of us wound up laughing after that.

Dominique Dumont: Improve config upgrade Ep 03 GSoC results

Hello Thanks to Google, Debian and more importantly Krzysztof Tyszecki, the accept feature discussed in episode 2 is now implemented and tested in Config::Model 1.206 and Config::Model::Itself 1.216. Next task is to create a minimal model to enable upgrades for cupsd.conf. This minimal model will heavily use the new accept feature coded during this GSoC. Cups configuration is an interesting use case because: Next episode should provide more details on the work required to provide this minimal model. All the best

Iustin Pop: Spooky harddrive

For a couple of weeks, one of the harddrives in my server has started to behave strangely. The RAID controller has started first reporting some drive timeouts (daily, when the drive runs a short or long smart test), and now it even kicks it out of the (RAID1) array. And yet, during normal operation, there's no read error or write error that I can trigger, and there are no reallocated sectors (according to smart). The only time when I can reproduce the error is: What happens when both these conditions are met? The the SMART query is taking ages (as in ~20-30 seconds). This might cause some such high delays that the drive itself will report a timeout error (if any I/O takes place at the same time), and log an error in its internal error log. Another harddrive (identical brand): ~3s for SMART query during selftest and I/O load, no issues whatsoever. For this harddrive, smartctl -a reads a while, and then:
Error SMART Error Self-Test Log Read failed: Input/output error
Smartctl: SMART Self Test Log Read Failed
 
real    0m39.029s
The timeout above also has generated lots of errors in the drive's error log. I don't know how to read these properly, but in any case they don't seem too scary:
Error 144 occurred at disk power-on lifetime: 13552 hours (564 days + 16 hours)
  When the command that caused the error occurred, the device was doing SMART Offline or Self-test.
  After command completion occurred, registers were:
  ER ST SC SN CL CH DH
  -- -- -- -- -- -- --
  10 51 00 80 ae 39 40
  Commands leading to the command that caused the error were:
  CR FR SC SN CL CH DH DC   Powered_Up_Time  Command/Feature_Name
  -- -- -- -- -- -- -- --  ----------------  --------------------
  61 80 70 80 ae 39 1c 08  41d+08:07:45.052  WRITE FPDMA QUEUED
  b0 d0 01 00 4f c2 00 08  41d+08:07:45.038  SMART READ DATA
  ec 00 01 00 00 00 00 08  41d+08:07:44.958  IDENTIFY DEVICE
  2f 00 01 10 00 00 00 08  41d+08:07:44.957  READ LOG EXT
  61 80 70 80 ae 39 1c 08  41d+08:07:37.960  WRITE FPDMA QUEUED
For some of the errors, all preceding commands are WRITE FPDMA QUEUED, but all are during a "SMART Offline or Self-test" phase. When a self-test is not being done, reading all the SMART data (smartctl -a) is very very quick, taking half a second. The only thing I can think of is that the drive's own area for storing SMART data is unhealthy, and reading it takes time, and a concurrent SMART test and I/O load makes it hard for the drive to do so. But again, I can't trigger any real I/O error, nor at the beginning of the drive neither at the end, so This also happens when the drives is connected to a plain SATA port, skipping the RAID controller, so it's not just the controller playing games on me. I'm really confused now. Given my previous experience, this drive will die, should already have died, and yet, no I/O errors, just some timeouts. Do I just need to wait a couple more weeks?

30 August 2010

Rapha&#235;l Hertzog: Understanding Membership Structures in Debian and Ubuntu

Debian and Ubuntu have a set of official membership roles that can be granted to regular contributors. Those roles come with rights that enable the contributors to do their work and to participate in the project governance (elections and other official decision-making processes). It s also a way for the distributions to acknowledge the work done: most contributors are proud of the status they reached. The membership structure plays an important role in the development of a distribution: it defines the kind of contributors that are welcome in the project, it sets expectations of the project towards its contributors and defines their rights. In the end, this shapes the project s ability to recruit new contributors to keep the project alive and kicking. This article introduces the existing statuses in Debian and Ubuntu, and defines the sometimes confusing jargon associated with them. The Debian Case Debian only has two types of official members: Debian Developers (DD) and Debian Maintainers (DM). The rights of the developers are codified in the Debian Constitution while those of the maintainers have been defined in a general resolution of 2007. The Debian Maintainer status is still mostly documented in a wiki page. The integration of this new status in Debian s official processes has been slow to come largely because it was introduced at that time without enough negotiation with the involved parties. Nowadays, it is preferred that people get the DM status before applying for DD. DM is a very limited role: maintainers can only upload packages that already have their name on them (either in the Maintainer or Uploaders field) and a specific flag (DM-Upload-Allowed: yes) that only Debian Developers can add. They have no other rights and limited access to Debian s resources. Besides those official roles, there are also maintainers of packages that have no official status within Debian except that they are listed in the Maintainer field of the package. They are doing the maintenance work but all uploads are done by a Debian Developer after verification of the work done (this is called sponsorship and is the only way to start with official packaging work). Once the DD trusts the maintainer, the developer will typically ask the maintainer to apply for DM status in order to be relieved from the sponsorship work. In the end, that makes three different kind of package maintainers and a lot of confusion when you discuss membership issues in particular when the New Maintainer process is the path that you follow to become a Debian Developer. Don t be fooled by the names when reading Debian s documentation! The Ubuntu Case Ubuntu had, from the start, an official Ubuntu Member status that includes all contributors: developers of course, but also documentation writers, artists, translators, etc. This status notably grants the right to vote in elections of the Community Council, the right to participate on Planet Ubuntu, and the @ubuntu.com email alias. For developers, the situation is more complicated: the wiki page lists no less than five different statuses. Initially, developers were split between Ubuntu Core Developers and the MOTU (Masters Of The Universe). The latter were responsible of the universe/multiverse sections of the archive while the former also had upload rights for the main/restricted sections. But, inspired by the Debian Maintainers concept and facing concrete problems in terms of archive management, they changed their infrastructure to offer more fine-grained control on package uploads. Ubuntu can now grant upload permissions on a package-per-package basis, but it can also delegate the right to grant upload permissions with the same granularity. This lead to the new Per-Package Uploader status which is simply an Ubuntu Member with upload rights on a limited set of packages where they have a specific expertise. The more generic Ubuntu Developers status now encompasses members of various development teams that have been delegated the right to manage upload permissions on a (usually large) package set (the current teams are Ubuntu Desktop, Mythubuntu, Kubuntu, and Edubuntu). Those teams can define their own policy to add new members provided they follow the basic rules defined by the Developer Membership Board (see this wiki page). Ubuntu Contributing Developer is an intermediate status for someone who is not yet ready for one of the other developer statuses but who has still shown enough commitment to be an Ubuntu Member. All those statuses can be obtained in a similar way: you prepare a wiki page listing your past contributions, you collect testimonials from existing members that you have worked with, you add yourself in the agenda of the next meeting of the board (or council) that grants the status that you seek, and you attend the meeting. The members of the board will decide whether you are ready for the status (or not) based on what you provided in the wiki, based on your answers during the meeting (and on a mailing-list for developers), and based on what others have to say about you. The most important boards are usually elected by the community while others are commonly appointed by the community council. Those governance bodies include Canonical employees but not as many as one would expect: two out of eight in the Developer Membership Board, two out of eight in the Community Council, but all six members of the Technical Board. The last figure, while not intended, is not surprising given the high expectations set on potential members of the technical board. Mark, as the founder, is the only person to have a permanent seat on both the Community Council and the Technical Board. Comparison of the Statuses Between Debian and Ubuntu The following table summarizes the rights given to each developer role in the two projects (Put the mouse over the abbreviations to know what they are referring to).
Rights Debian Ubuntu
DM DD UM PPU/UD MOTU UCD
Package maintenance via sponsorshipYN/AYYYN/A
Official email alias-YYYYY
Participate in votes for members-YYYYY
Participate in votes for developers-Y-YYY
Upload rights restricted to pre-approved packagesY--Y--
Upload rights restricted to a section of the archive----Y-
Unlimited upload rights-Y---Y
Number of contributors (as of 2010-07-27)117904462278563
Please note that the number of contributors are not 100% accurate for Ubuntu. A contributor can have multiple statuses (direct membership to a launchpad group) granted over time (while gaining experience). The problem has been mostly avoided by calculating differences between number of members of the various groups but it s not perfect and it can t be: some MOTU are also PPU for packages in main and it s legitimate (but I only counted them as MOTU and not as PPU). Another limitation is that members of some administrative teams are included indirectly in many teams and thus appear in the count while they should not. Anyway, this simple table makes it obvious that Ubuntu s structure offers a broader choice of statuses. They acknowledge the work of all contributors from the start while still giving the most critical rights only to those who have proven that they deserve them. Despite this difference, Debian still has a significant advantage in terms of number of developers. That number does not tell the whole story though: the Ubuntu contributors include many Canonical employees (e.g. 36 out of 63 core developers have a @canonical.com email registered on their launchpad account) that are likely to spend more time working on the distribution than the average Debian member. But even if comparing person-hours would be a challenging thought experiment, in practice it s of not much interest if both projects continue to cooperate and if more and more of the contributions flow in both directions. Debian is aware of the shortcomings of its structure. Changes to better accommodate non-packagers have been discussed several times already. The last efforts in that direction were unfortunately perceived as a solution ready to go rather than a proposal to be discussed, and the project got quickly buried by a general resolution (GR). Even if that resolution invited for further discussion and a new proposal, the truth is that when someone s initiative is corrected by way of GR, it usually kills any motivation to go forward. Possible Evolution? On the Ubuntu side, the infrastructural changes were completed recently and they don t expect any further change in the near future. They do plan, however, to expand usage of those new features so that more teams benefit from the possibility to control upload rights on packages that are relevant to them, and so that more individuals developers apply to become Per-Package Uploaders on packages that they know very well. On the Debian side, a recent discussion on the debian-project list brought back the topic of the bad terminology and it was agreed that the New Maintainer process should be renamed into something else ( New Developer process has been suggested). But Christoph Berg Debian Account Manager and hence heavily involved in the New Maintainer Team suggested that Debian would be better off implementing the long-awaited membership changes before trying to update all the documentation. It would certainly imply some more vocabulary updates. Later in the discussion, he confirmed that membership reform is on the top of the TODO list of the new maintainer team (just after the rewrite of the nm.debian.org website). What can be expected from this reform? The following answers are my own guesses based on my experience of Debian, but the project hasn t decided anything yet. Almost two years have elapsed since the previous efforts in that direction, the new maintainer team has recruited new members and is in a general better shape. Hopefully, the next episode of this saga will have a better outcome.
This article was first published in Linux Weekly News. In a comment, Mark Shuttleworth tried to explain how the Ubuntu community is being setup.
Flattr this Share/Bookmark 10 comments Support my work

Matt Zimmerman: Traveling at home

For me, the most enjoyable part of traveling is the inspiration that I derive from visiting different places, talking to people, and generally being outside of my normal environment. This bank holiday weekend, when so many Londoners visit faraway lands, my partner and I stayed in London instead, and my sought inspiration closer to home. The city has been delightfully quiet, and in contrast to the preceding week, the weather was mostly pleasant, apart from the sudden downpours the BBC described as squally showers .
Photo of deer in Richmond Park

Photo credit: M rcio Cabral de Moura


We spent Saturday afternoon in Richmond Park, a 2500-acre nature preserve easily accessible via public transport from London. The plentiful oak trees, fallow deer, and various species of water fowl made it easy to forget the city for a while. Having visited a few times on foot, I think it would be fun to cycle next time, and see different areas of the park. Afterward, we had dinner at a tapas restaurant in Parsons Green which offered notably excellent service as well as good food. By this time, it was nearly 7:00pm, and we took a chance on getting last-minute theatre tickets to see Jeff Goldblum and Mercedes Ruehl in Neil Simon s The Prisoner of Second Avenue. We arrived at the theatre just in time for the show, which was not sold out, and in fact had quite reasonable seats available. The show had several good laughs, holding up fairly well after nearly 40 years since the original Broadway production.
Photo of the exhibition at the Design Museum

Photo credit: Gary Bembridge


On Sunday, we visited the Design Museum for the first time. Having been disappointed by the nearby Fashion and Textile Museum, our expectations were not too high, but it turned out to be very worthwhile. The Brit Insurance Designs of the Year exhibition showcased designs from architecture, fashion, furniture, transport and more. Some of my favorites were: I was delighted to see that there were a half dozen or so exhibits which related to open source software. Even including the theatre tickets, it was a very inexpensive holiday compared to traveling overseas, and generated a lot less CO2. I was more than satisfied with the inspiration available within a relatively small radius. I don t think I ll give up traveling, as I really enjoy seeing friends who live far away, but I think I ll be more inclined to stay home during peak travel times and enjoy local activities.

29 August 2010

Steve Kemp: Proxies and Robots

I don't like repeating myself, but I'm very tempted to past my mini-review of the Roomba Vacuum Cleaner robot into this blog. Instead I will practise restraint and summerise: 250. Worth. Every. Penny. In more Debian-friendly news I've been fighting HTTP proxies today. I've noticed a lot of visitors to the various websites I host are logged as 127.0.0.1 - which is an irritation. My personal machine looks like this:

Internet -> Apache listening on *:80 -> thttpd on 127.0.0.1:xxxx
(This has been documented previously - primarily it is a security restriction. It means I can run per-UID web-servers.) I had previous added a patch to thttpd to honour the X-Forwarded-For: header - so that it would receive the correct remote address passed on from Apache. However the fact that so many visitors are logged as coming from 127.0.0.1 meant it wasn't working 100% correctly, and I wanted to understand why. Today I used ngrep to capture the incoming headers and the source of the problem became apparent:
skx:~# ngrep  -d lo  X-For ' port 1007'
..
T 127.0.0.1:41886 -> 127.0.0.1:1007 [AP]
  GET /about/ HTTP/1.1..Host: images.steve.org.uk..If-Modified-Since: Mon, 07
   Jun 2010 15:24:33 GMT..User-Agent: Mozilla/5.0 (X11; U; Linux x86_64; en-U
  S; rv:1.9.1.10) Gecko/20100701 Iceweasel/3.5.10 (like Firefox/3.5.10)..Acce
  pt: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8..Accept
  -Language: en-us,en;q=0.5..Accept-Encoding: gzip,deflate..Accept-Charset: I
  SO-8859-1,utf-8;q=0.7,*;q=0.7..Referer: http://images.steve.org.uk/2009/11/
  20/img_0471.html..X-Forwarded-For: 127.0.0.1, 11.22.33.123..Cache-Control:
  max-age=0..X-Forwarded-Host: images.steve.org.uk..X-Forwarded-Server: image
  s.steve.org.uk..Connection: Keep-Alive....
I bolded the important input; just in case that didn't jump out it was:
X-Forwarded-For: 127.0.0.1, 11.22.33.123
My patch to thttpd was making it read the first address, rather than the second - which meant that requests were being logged as coming from 127.0.0.1 and avoiding my efforts to track sources. Now I understand the problem - The X-Forwarded-Host header is being tweaked by a proxy server, such as Squid, upstream of my server. For the moment I've updated the thttpd patch to read:
        else if ( strncasecmp( buf, "X-Forwarded-For:", 16 ) == 0 )
            char *tmp = NULL;
            /* Jump to the header-value  */
            cp = &buf[16];
            cp += strspn( cp, " \t" );
            /*
             * If the first change is a 127.0.0.1, then we'll
             * jump over it.  Cope with Squid, et al.
             */
            if (  ( tmp = strstr( cp, "127.0.0.1, " ) ) != NULL )
              cp = tmp + strlen( "127.0.0.1, " );
            /* Parse the IP */
           inet_aton( cp, &(hc->client_addr.sa_in.sin_addr) );
         
That's not perfect, but the alternative would be: Or something equally hacky and security-by-obscurity-alike. Really I just want a simple way of always getting the correct remote IP. Shouldn't be so hard, should it? *pout*. ObQuote: "You don't mess with fate, Peanut. People die when they are meant to die. There's no discussion. There's no negotiation. When life's done, it's done." - Dead Like Me.

Bernd Zeimetz: the guruplug server plus - major design and qa fail

As a lot of people are coming to my blog to read the installing instructions for Debian on the GuruPlug Server Plus, I shall not hide my opinion about it: It is a major design and QA fail. Don't waste your money on it.
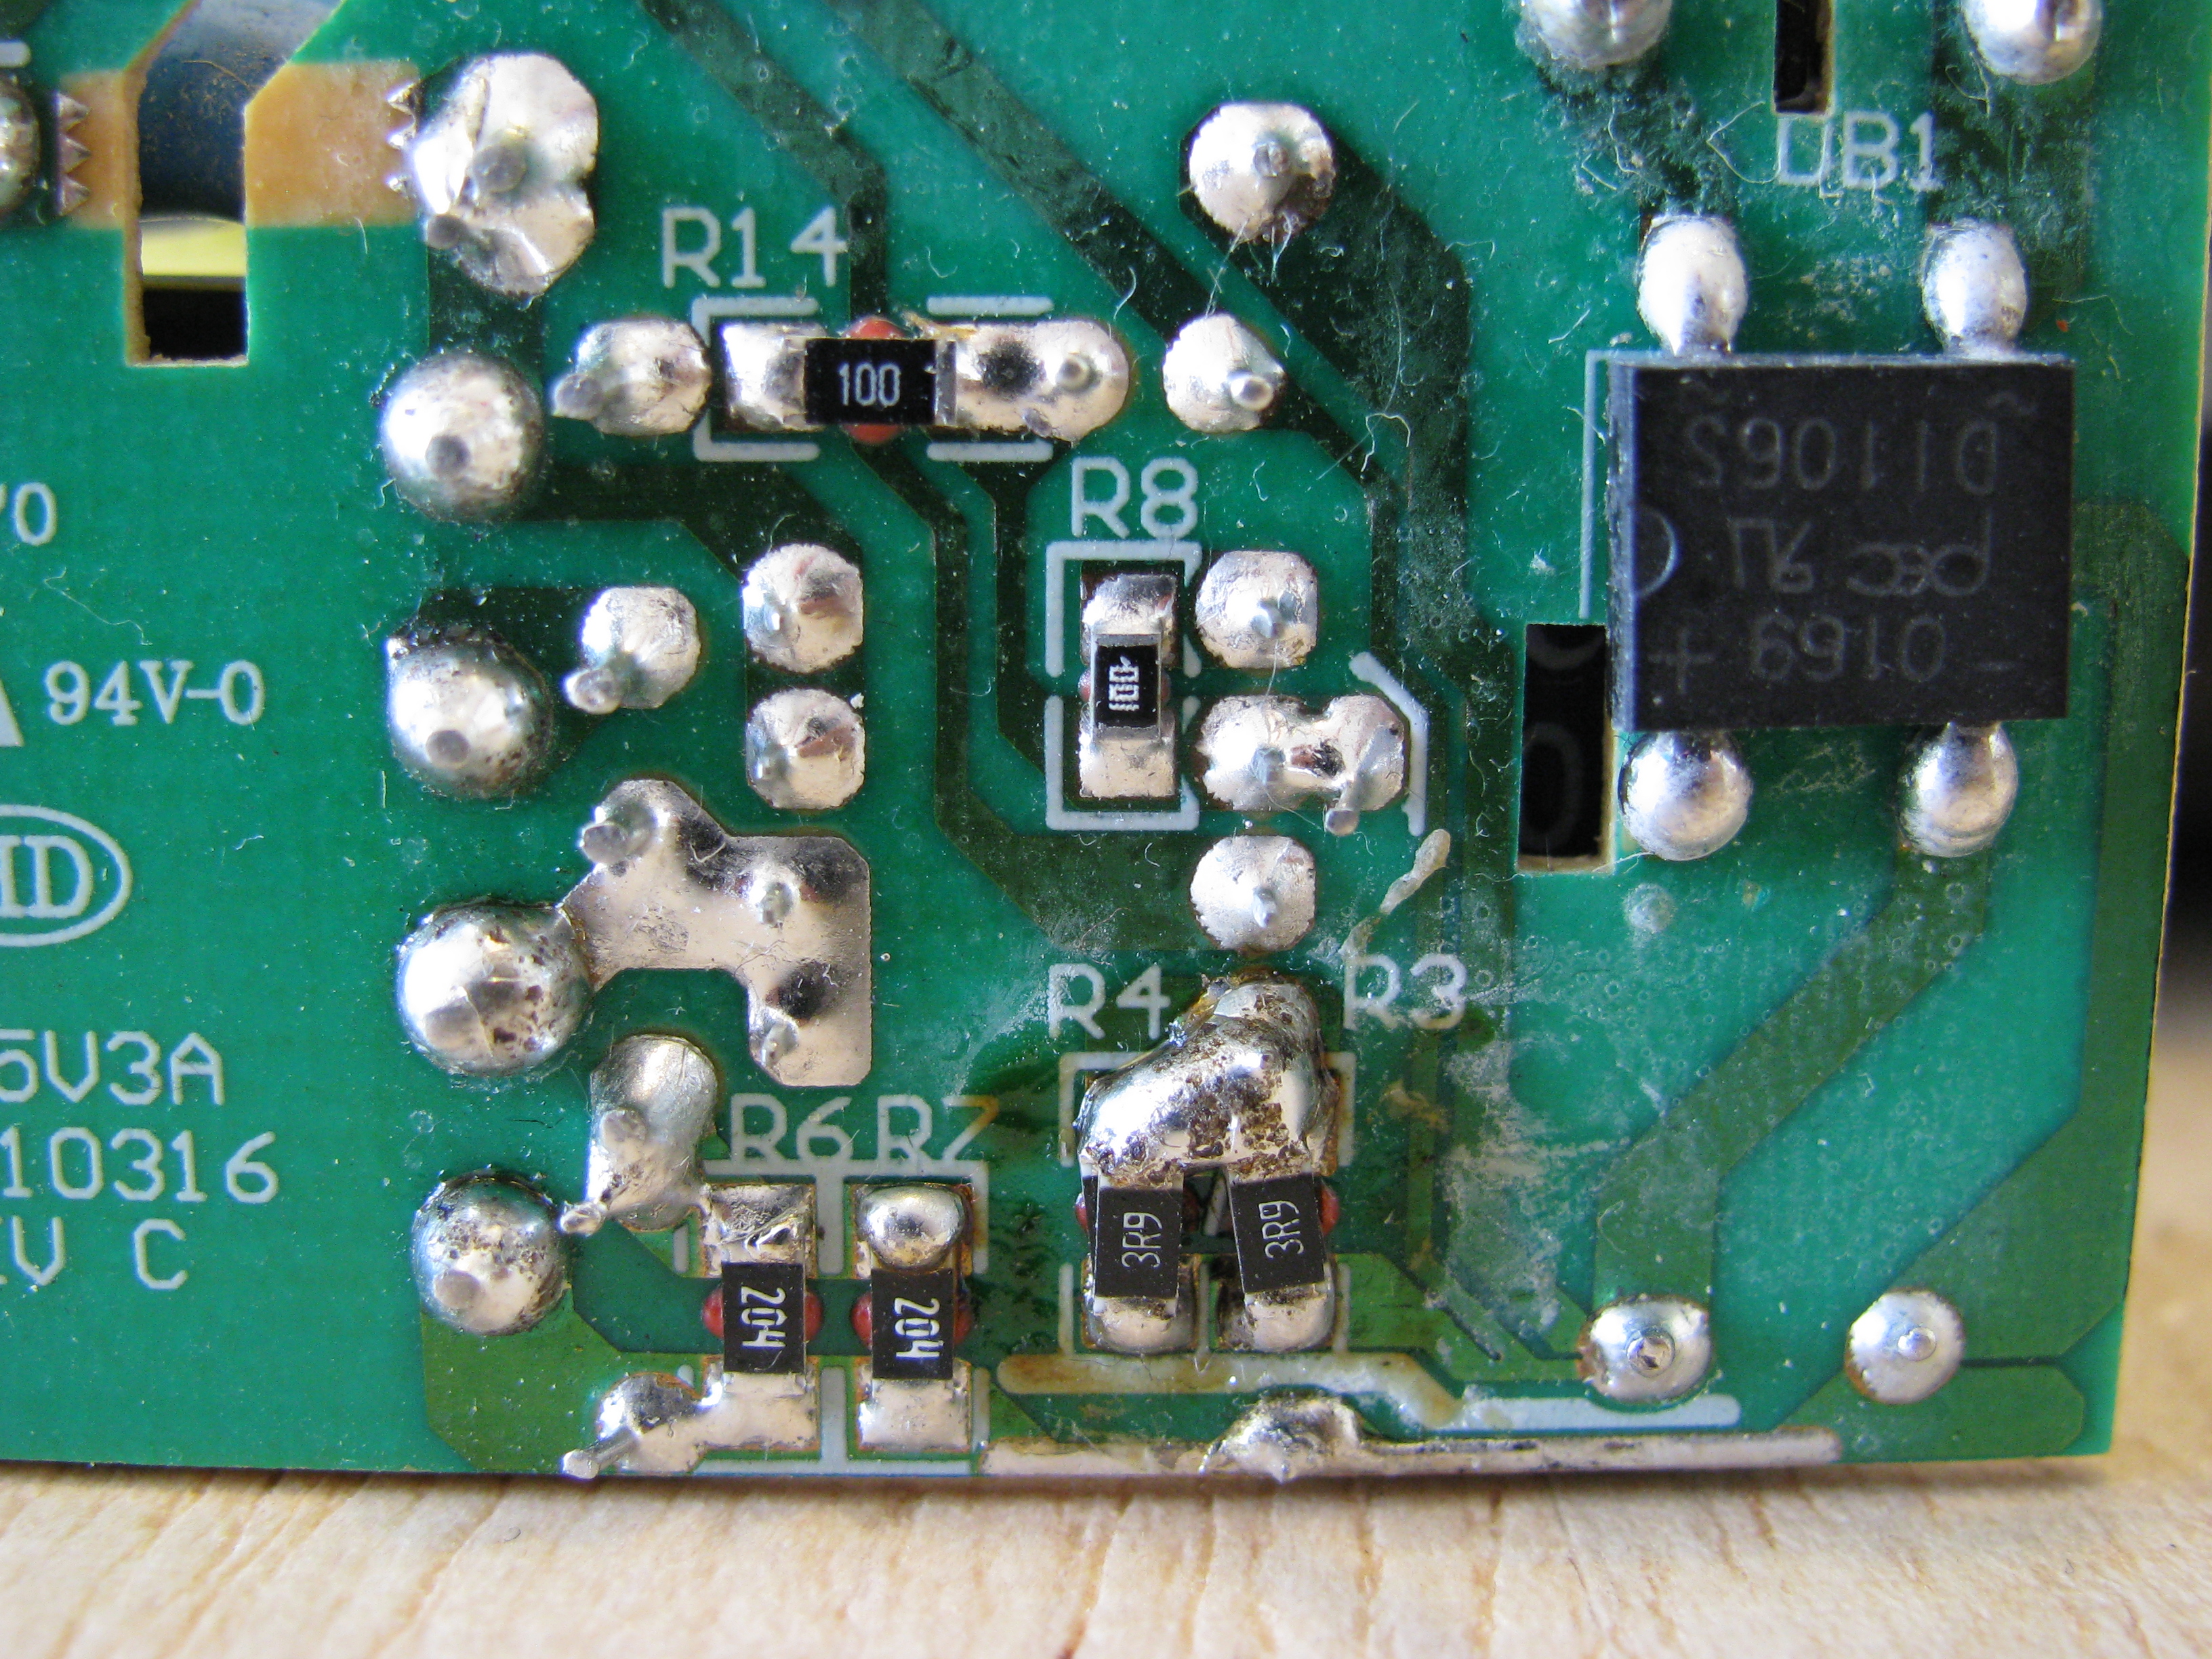
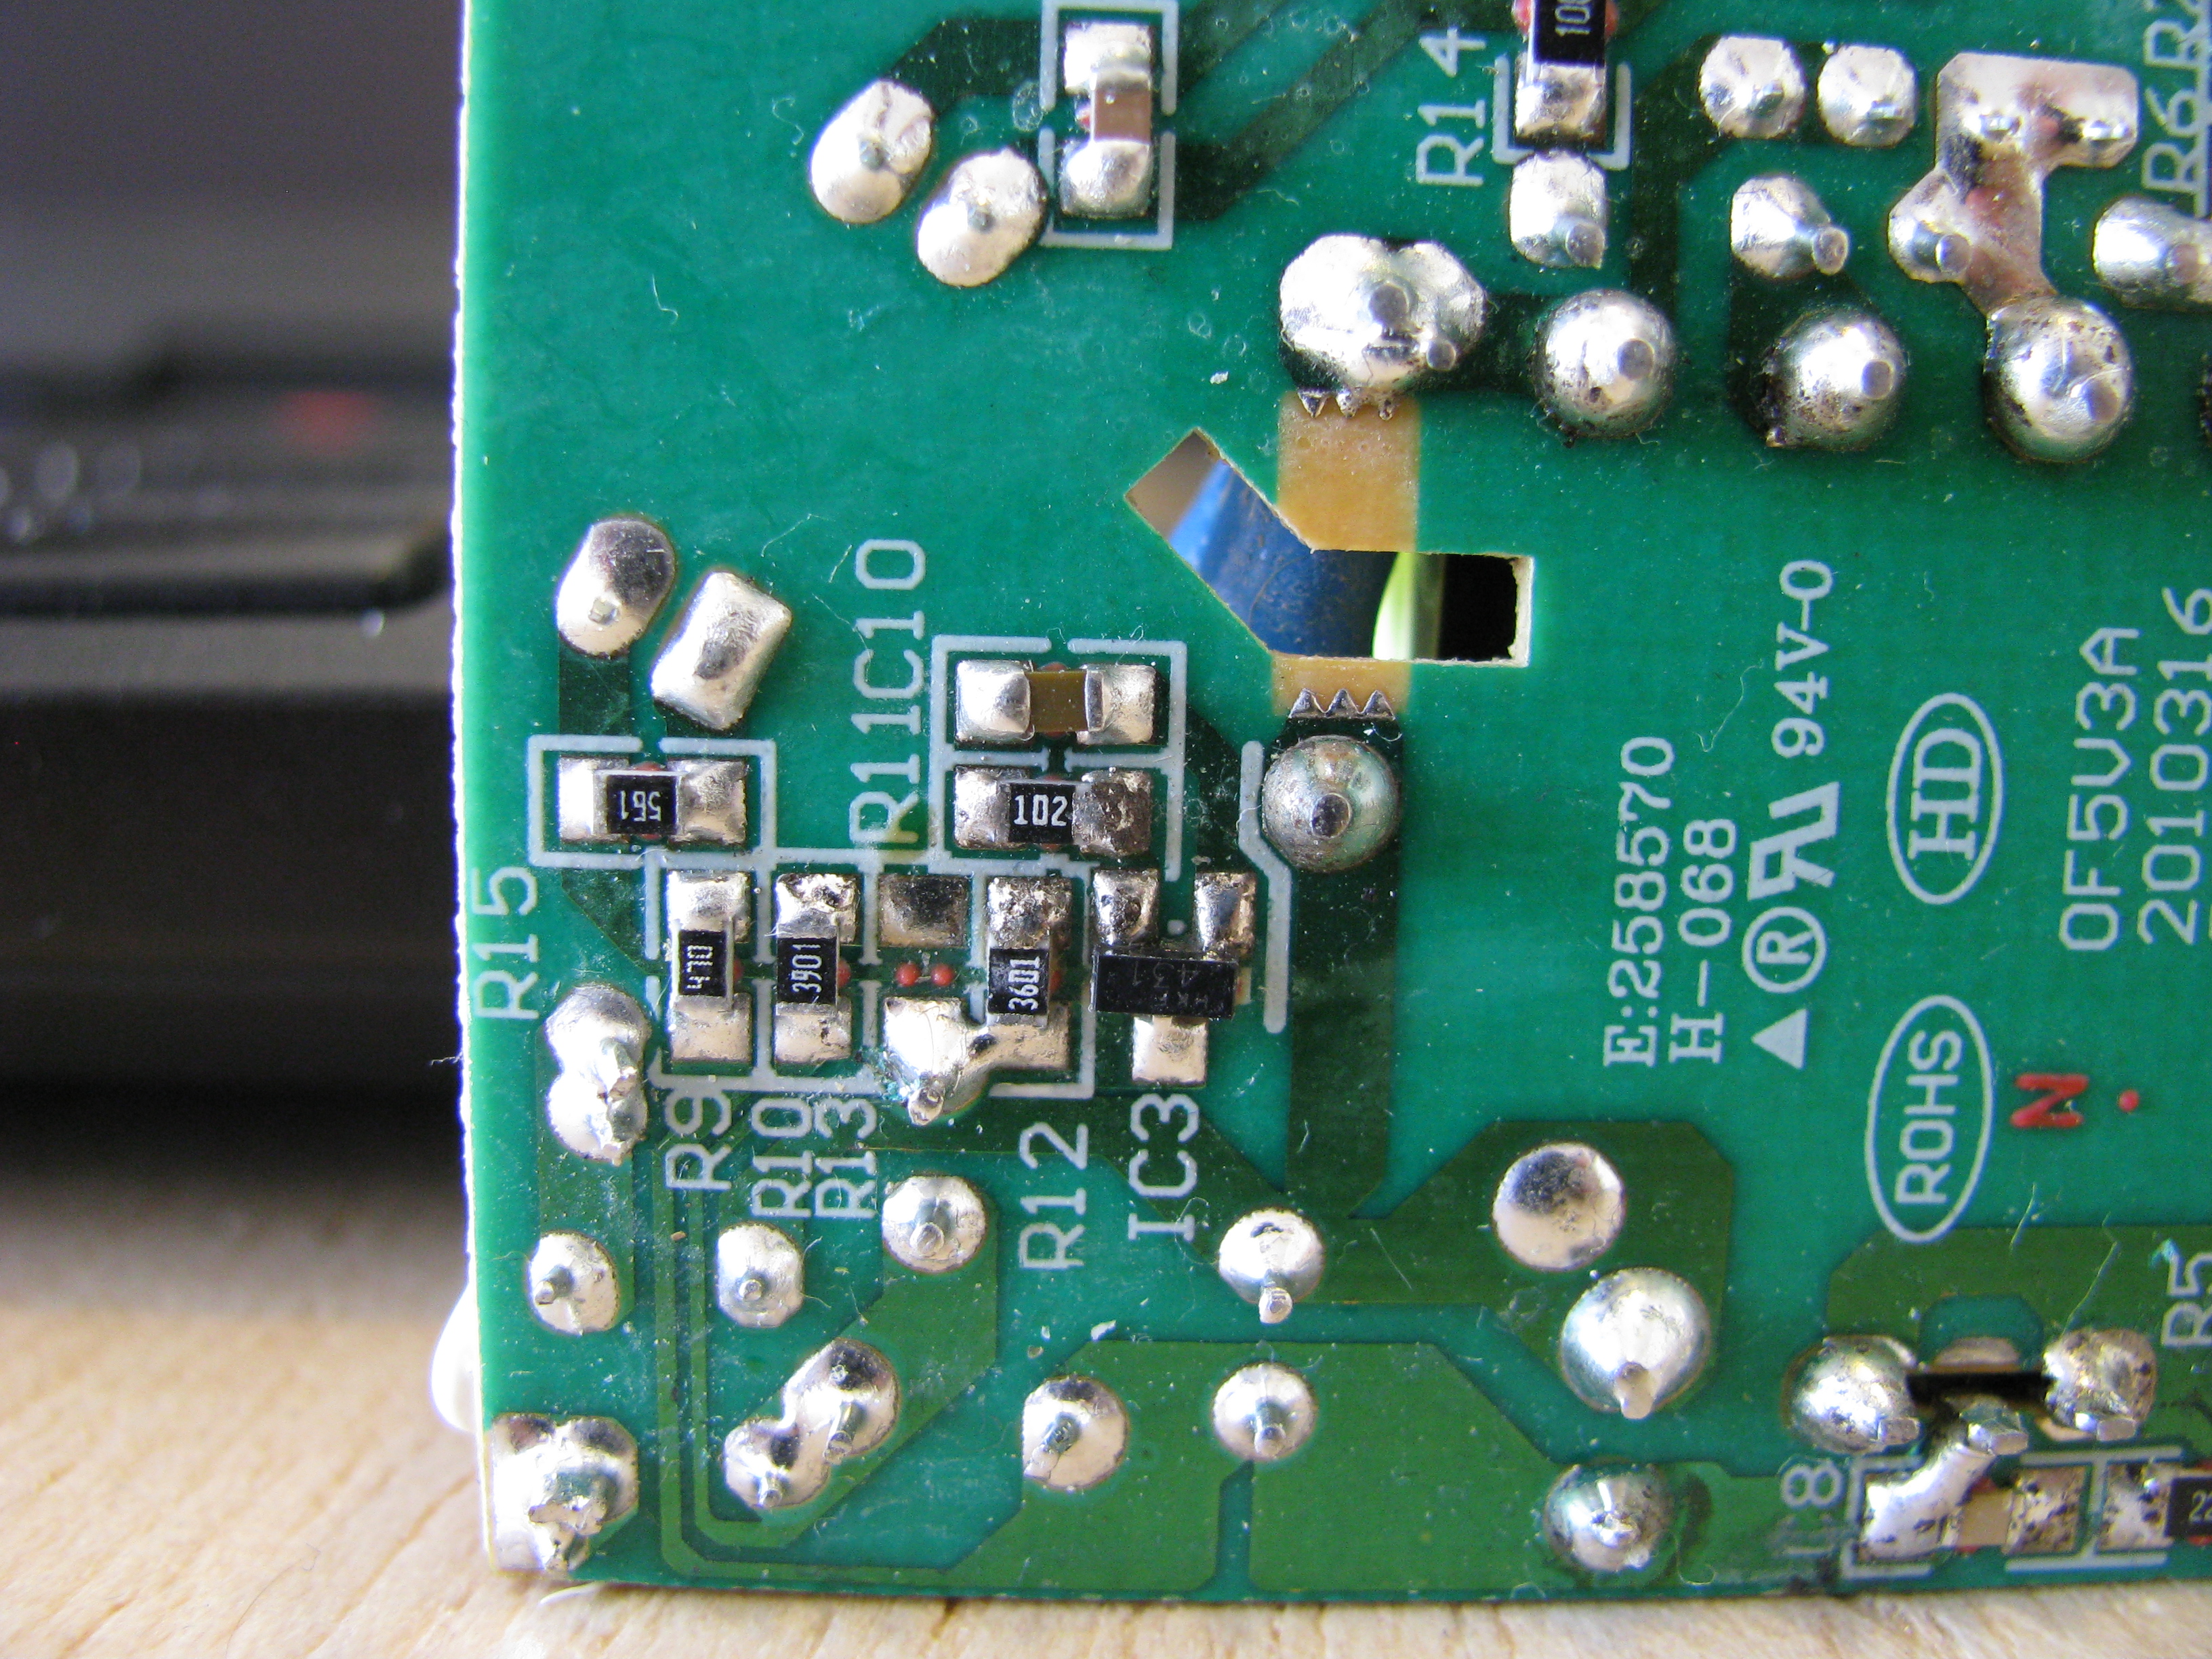
The power supply Although I've ordered the Guruplug pretty early with the promise, that I'd have it in April, it arrived at the end of May due to QA issues with the power supply. While I appreciate that they didn't deliver broken power supplies, I would have preferred not to receive one which was "fixed" by somebody who uses the soldering iron like an axe. Here are some macro photos to show the gory details: GuruPlug Server Plus PSU 1 GuruPlug Server Plus PSU 2 GuruPlug Server Plus PSU 3

Software issues The version of UBoot which shipped with the device was only able to boot from NAND and network. Booting from USB failed and ext2 support was missing, too. Didn't have a look if the community came up with a fixed UBoot version yet, but in my opinion a piece of hardware for >100 EUR should not have such flaws.

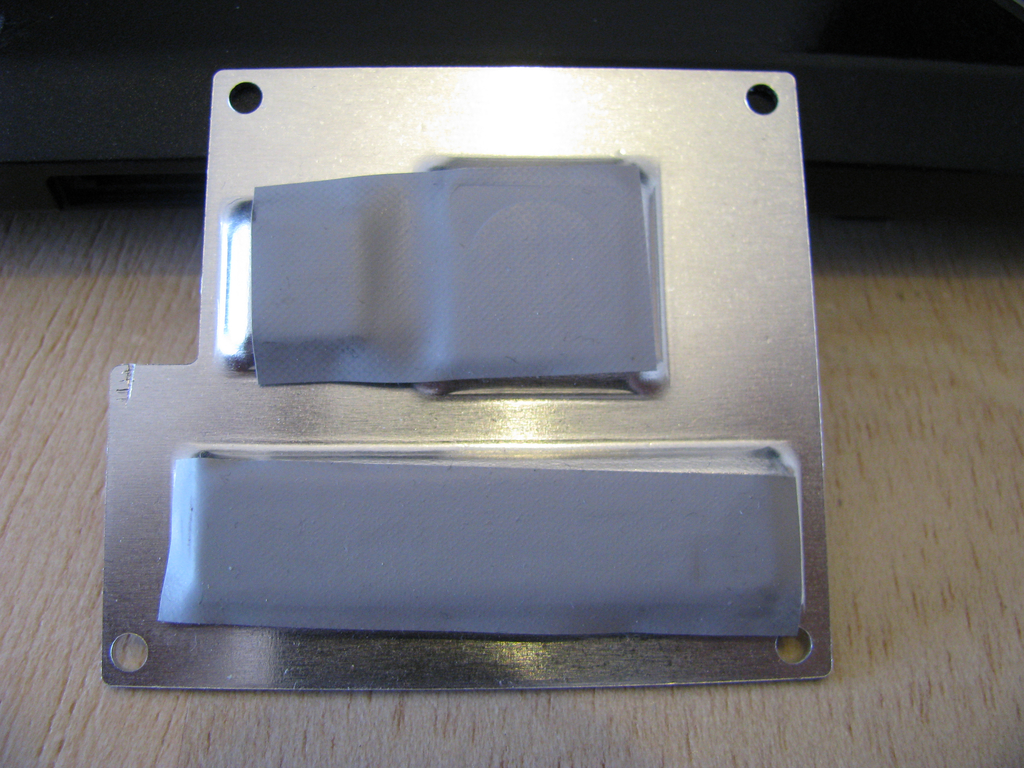
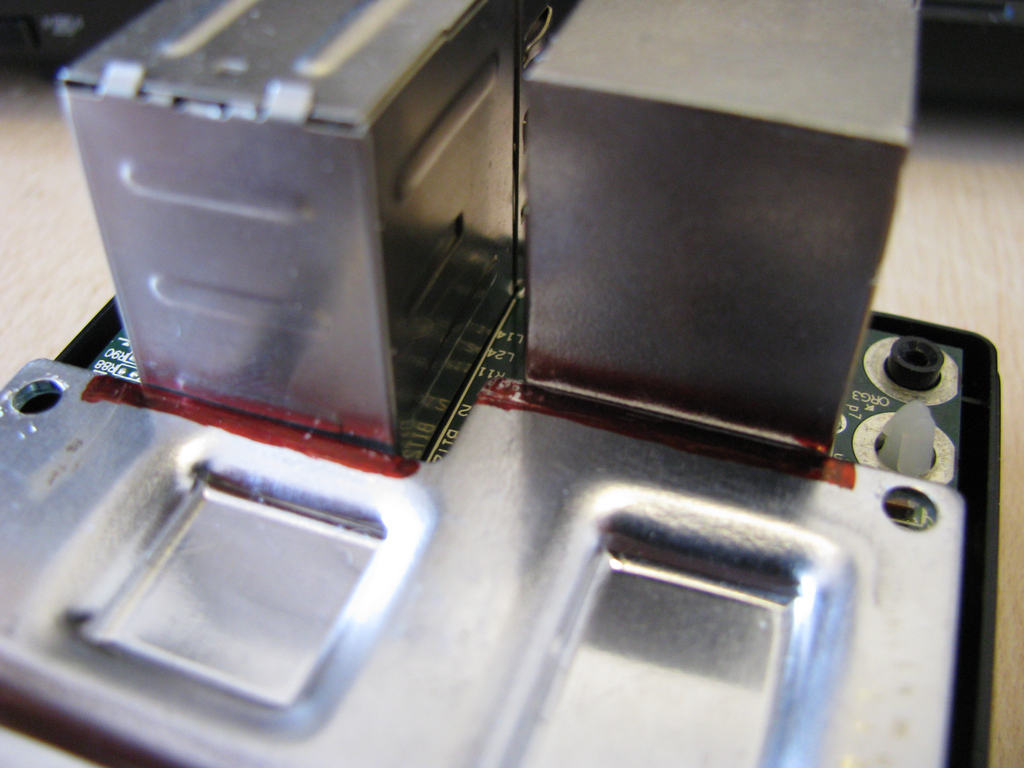
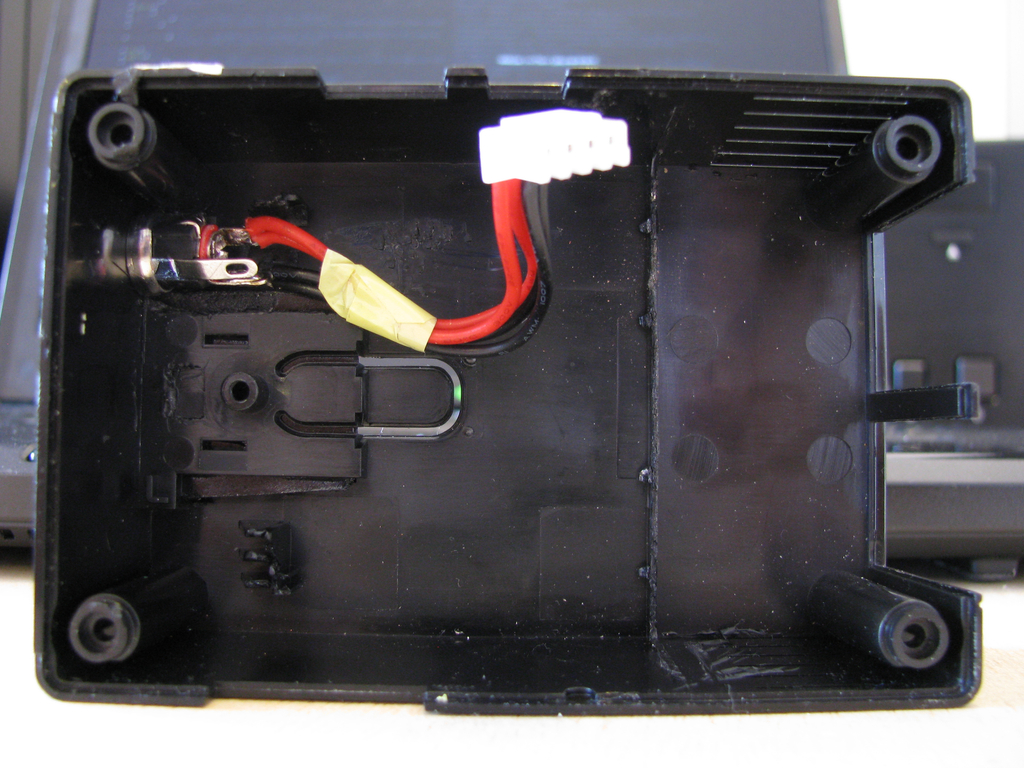
Thermal issues Using the Guruplug with more than one 100 MBit/s connection is just not possible, as it would toast itself to death. For the details have a look at this discussion in the NewIT forum, it links to a lot of interesting photos and postings. This issue is a major design and QA failure. Even without knowing what the datasheets say, it is easy to imagine that a thin piece of alloy is not the proper way to cool a CPU and network chip. Especially not when it is mounted with cheapish pads instead of a proper paste. GuruPlug Server Plus Cooling 1 As it seems the plan was to send the heat to the shielding of the network/USB/eSata ports (the area is marked red as my first plan was to remove that part of the alloy and reuse the heat-spreader), a strong indication for that is that this is the only area with holes for air circulation. I could imagine that it was not possible to have these holes next to the PSU, which was mounted above the heat-spreader, to avoid electrical shocks. GuruPlug Server Plus Cooling 2 As there was no other opening for the heat to leave the case, even the microSD card became pretty hot - I've measured temperatures around 60 deg. C next to the card - while CPU and 100MB/s network were idling. The official information from GlobalScale Technologies is that only 10/100MBit/s should be used as workaround to avoid overheating until a "Professional Upgrade Kit" is released. As mentioned here the upgrade kit announcement was removed silently from GST's website. To be honest, this doesn't make me wonder. There is no way to fix the Guruplug with an external fan or any other external magic as the only way to fix it is to cool the CPU and networking chip properly. There are various workarounds for the cooling issues posted to the forums. I've decided to rip out the power supply and heat spreader out of the case and get a nice external PSU. The new connector is mounted, ready to supply the GuruPlug's board with power. GuruPlug Server Plus power connector Currently I'm waiting for the new heat sinks and glue to arrive. Then I'll give it a try to mount eveything in the small case again, probably with some additional air holes. As soon as I have a workign solution, I'll blog about it again.

Bernd Zeimetz: the guruplug server plug - major design and qa fail

As a lot of people are coming to my blog to read the installing instructions for Debian on the GuruPlug Server Plus, I shall not hide my opinion about the Guruplug Server Plus: It is a major design and QA fail. Don't waste your money on it.
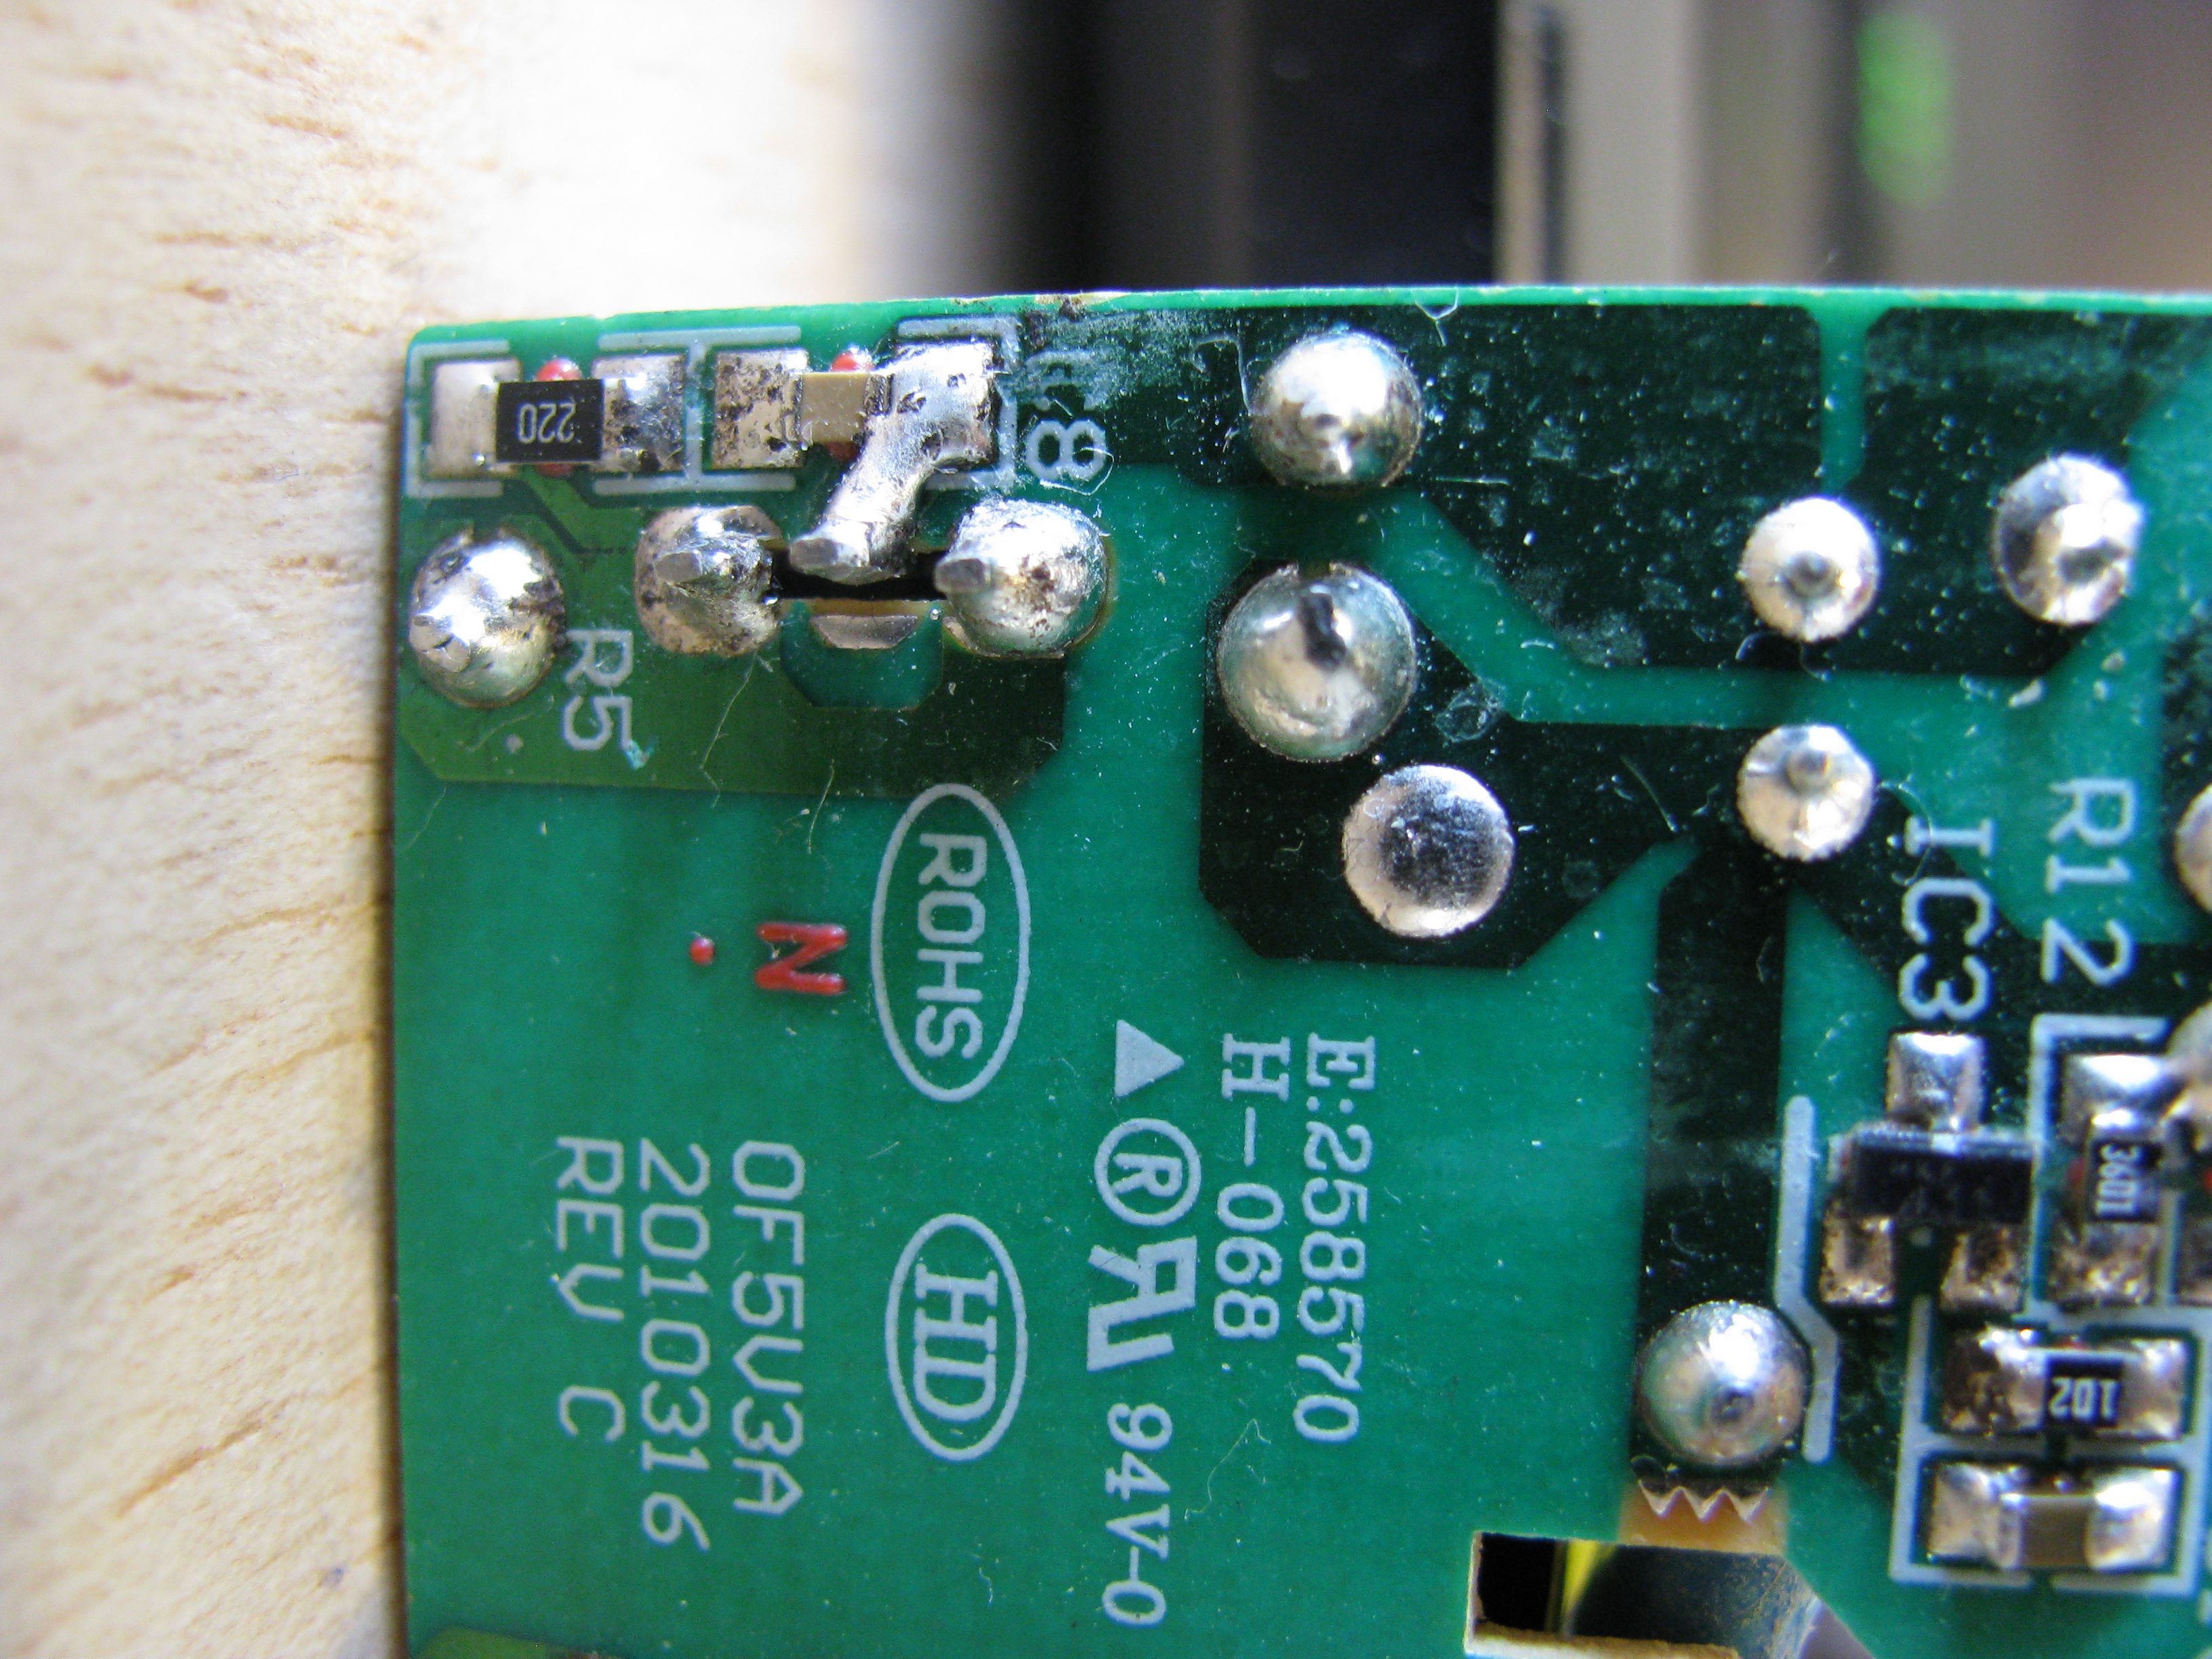
The power supply Although I've ordered the Guruplug pretty early with the promise, that I'd have it in April, it arrived at the end of March due to QA issues with the power supply. While I appreciate that they didn't deliver broken power supplies, I would have preferred not to receive one which was "fixed" by somebody who uses the soldering iron like an axe. Here are some macro photos to show the gory details: GuruPlug Server Plus PSU 1 GuruPlug Server Plus PSU 2 GuruPlug Server Plus PSU 3

Software issues The version of UBoot which shipped with the device was only able to boot from NAND and network. Booting from USB failed and ext2 support was missing, too. Didn't have a look if the community came up with a fixed UBoot version yet, but in my opinion a piece of hardware for >100 EUR should not have such flaws.

Thermal issues Using the Guruplug with more than one 100 MBit/s connection is just not possible, as it would toast itself to death. For the details have a look at this discussion in the NewIT forum, it links to a lot of interesting photos and postings. This issue is a major design and QA failure. Even without knowing what the datasheets say, it is easy to imagine that a thin piece of alloy is not the proper way to cool a CPU and network chip. Especially not when it is mounted with cheapish pads instead of a proper paste. GuruPlug Server Plus Cooling 1 As it seems the plan was to send the heat to the shielding of the network/USB/eSata ports (the area is marked red as my first plan was to remove that part of the alloy and reuse the heat-spreader), a strong indication for that is that this is the only area with holes for air circulation. I could imagine that it was not possible to have these holes next to the PSU, which was mounted above the heat-spreader, to avoid electrical shocks. GuruPlug Server Plus Cooling 2 As there was no other opening for the heat to leave the case, even the microSD card became pretty hot - I've measured temperatures around 60 deg. C next to the card - while CPU and 100MB/s network were idling. The official information from GlobalScale Technologies is that only 10/100MBit/s should be used as workaround to avoid overheating until a "Professional Upgrade Kit" is released. As mentioned here the upgrade kit announcement was removed silently from GST's website. To be honest, this doesn't make me wonder. There is no way to fix the Guruplug with an external fan or any other external magic as the only way to fix it is to cool the CPU and networking chip properly. There are various workarounds for the cooling issues posted to the forums. I've decided to rip out the power supply and heat spreader out of the case and get a nice external PSU. The new connector is mounted, ready to supply the GuruPlug's board with power. GuruPlug Server Plus power connector Currently I'm waiting for the new heat sinks and glue to arrive. Then I'll give it a try to mount eveything in the small case again, probably with some additional air holes. As soon as I have a workign solution, I'll blog about it again.

28 August 2010

Antti-Juhani Kaijanaho: Dear Lazyweb: Does this software exist?

I ve been wondering if the following kind of testing management software exists (preferably free software, of course). It would allow one to specify a number of test cases. For each, one should be able to describe preconditions, testing instructions and expected outcome. Also, file attachments should be supported in case a test case needs a particular data set. It would publish a web site describing each test case. A tester (who in the free software world could be anyone) would take a test case, follow the instructions given and observe whatever outcome occurs. The tester would then file a test report with this software, either a terse success report or a more verbose failure report. The software should maintain testing statistics so that testers could easily choose test cases that have a dearth of reports. As a bonus, it would be nice if the software could submit a failure report as a bug report . (Note that this would be useful for handling the sort of tests that cannot be automated. There are many good ways already to run automated test suites.)

Erich Schubert: Facebook closing up for third party developers?

It looks a lot as if Facebook is closing up on third party developers. Seems like they've cherry picked the features they want to copy, and now are no longer interested in third parties anymore:Expect once-famous Facebook applications such as SuperPoke to disappear on the long run - their integration hooks have been pulled. The API gets more and more limited for the cash cow use case: games. And of course marketing. Oh, I forgot one type of "applications". The one that basically embeds you regular web page within a Facebook tab. Wow. That's technology!If it was really about the users, Facebook would seriously fight Facebook spam, worms and fraud. They still don't have that under control (and none of them used either of the removed features!). They do even less to prevent users from clicking on such bad links such as the Free iPad scam, which has been around for at least a week now. Or the famous "dislike button" scam. They could not spell much more clearly that they do not care about their users - they just want your data to sell more directed advertising to you. Forget about privacy, too!Now that all my three Facebook applications are pretty much dead, this comes with a good side for me: I've been considering to disable/suspend/kill my Facebook account for quite some time. But I wasn't sure if that would also kill my applications for their users. Now that they're dead anyway, there is not much keeping me anymore.

27 August 2010

Colin Watson: Windows applications making GRUB 2 unbootable

If you find that running Windows makes a GRUB 2-based system unbootable (Debian bug, Ubuntu bug), then I'd like to hear from you. This is a bug in which some proprietary Windows-based software overwrites particular sectors in the gap between the master boot record and the first partition, sometimes called the "embedding area". GRUB Legacy and GRUB 2 both normally use this part of the disk to store one of their key components: GRUB Legacy calls this component Stage 1.5, while GRUB 2 calls it the core image (comparison). However, Stage 1.5 is less useful than the core image (for example, the latter provides a rescue shell which can be used to recover from some problems), and is therefore rather smaller: somewhere around 10KB vs. 24KB for the common case of ext[234] on plain block devices. It seems that the Windows-based software writes to a sector which is after the end of Stage 1.5, but before the end of the core image. This is why the problem appears to be new with GRUB 2. At least some occurrences of this are with software which writes a signature to the embedding area which hangs around even after uninstallation (even with one of those tools that tracks everything the installation process did and reverses it, I gather), so that you cannot uninstall and reinstall the application to defeat a trial period. This seems like a fine example of an antifeature, especially given its destructive consequences for free software, and is in general a poor piece of engineering; what happens if multiple such programs want to use the same sector, I wonder? They clearly aren't doing much checking that the sector is unused, not that that's really possible anyway. While I do not normally think that GRUB should go to any great lengths to accommodate proprietary software, this is a case where we need to defend ourselves against the predatory practices of some companies making us look bad: a relatively small number of people do enough detective work to realise that it's the fault of a particular Windows application, but many more simply blame our operating system because it won't start any more. I believe that it may be possible to assemble a collection of signatures of such software, and arrange to avoid the disk sectors they have stolen. Indeed, I have a first draft of the necessary code. This is not a particularly pleasant solution, but it seems to be the most practical way around the problem; I'm hoping that several of the programs at fault are using common "licence manager" code or something like that, so that we can address most of the problems with a relatively small number of signatures. In order to do this, I need to hear from as many people as possible who are affected by this problem. If you suffer from this problem, then please do the following: I hope that this will help me to assemble enough information to fix this bug at least for most people, and of course if you provide this information then I can make sure to fix your particular version of this problem. Thanks in advance!

Richard Darst: DebConf budgeting for a single conference

My last post discussed the year-to-year budgeting of DebConf. This post discusses what makes budgeting difficult within one particular DebConf. Since every DebConf is unique in its arrangements, the particular difficulties always vary year-to-year. For example, DebConf10 was easy in that Software in the Public Interest was in the same country so that we had easy access to bank accounts, but more difficult venue payment logistics. I'll use DebConf10 as an example below.
For DebConf10, we get our venue "for free" thanks to the support of the Columbia Computer Science department. However, we had to pay for guard costs after building hours, and custodial costs. For custodial costs at least, we had to go through many layers of bureaucracy, and people kept insisting it would be more than they quoted. (It ended up being about half, since DebConf attendees were so responsible!)DebConf sponsors many attendees. This means that all their food and accommodation costs are paid by us. We have sponsored registration and reconfirmation deadlines to set a maximum of the number of people we have to sponsor, but people are continually dropping out and it's hard to know just how many people to reserve for. Sponsored people won't always eat every meal with us, and usually won't decide until the day before - so figuring out food amounts is hard, too. Furthermore, we have unsponsored people who will want food and accommodations (paying themselves) which we must somehow plan for.Different venues operate on different payment rules. This year, CU Housing was fairly strict on asking for attendee counts and room assignments two weeks in advance. Then, as time gets closer, they got more flexible, and in the end told us that they will, in fact, only charge based on number of people actually attending - a huge win for us. Similarly with CU Dining, we had to go through great lengths to make sure that we would pay only for meals we ate. At CU, food had to be paid in advance, but accommodation and other costs are paid afterwards.We have to guess how much will be spent on miscellaneous supplies once DebConf starts. We have to then decide how much to spend on extras such as the day trip or conference dinner, and how to sponsor those, if possible.Debian (and thus DebConf) has money held in trust in many currencies in different accounts. Different sponsors will pay to different currencies, depending on what is convenient for them. This means that we need to consider fluctuating currency conversion rates, and decide if and when to transfer money. In general, DebConf hasn't transfer money just to make sure the DebConf-tagged money gets spent first. Some surpluses are best left in other countries to help pay future travel sponsorship since it is expensive to move money out of the country. Some conferences may result in a net movement of money from USA to Europe (more donors in one, more expenses in the other), some the other way around.Travel sponsorship is in the form of reimbursement. These can take many months to have the documentation received from attendees and the reimbursements all sent out, and thus finalizing the budget and surplus for next year.The overall principle we've tried to stick to is plan for a balanced budget in the worst case scenario, and then be happy when it ends up better than that.
At the DebConf&Debian BOF, someone mentioned how budgeting for any (free software) conference is hard. I think that's certainly true. Some of the registration fluctuations could be made easier by being less flexible, but DebConf wants to serve our attendees even if it is a bit of extra work for us. Each DebConf will have its own ways budgeting is difficult, but things have always work out, and usually with a bigger surplus than we were expecting.Tags: debconf

26 August 2010

Sylvain Le Gall: CentOS 5 chroot with schroot

OCaml compiles native executables in static mode. It allows to have a minimal set of dependencies when delivering an executable. It has also disadvantages like the size of the executable and problems arising when considering libraries update -- but this is another topic. There is still one strong dependency that you should not forget when you want to deliver a product for most of the Linux distributions: dependency on the glibc version. Trying to run OASIS compiled with Debian Lenny, on CentOS 5.5:
$ OASIS
.../OASIS: /lib64/libc.so.6: version  GLIBC_2.7' not found (required by .../OASIS)
So when compiling for delivery, one should choose the oldest distribution he targets. In my case, I choose CentOS 5 which comes with glibc v2.5. I usually choose Debian stable at the moment of writing Debian Lenny. But for now, the Debian Lenny's glibc is newer (v2.7) than the one coming from the CentOS 5.5 stable release. CentOS is a Red Hat like Linux distribution. I use a Debian Lenny amd64 host system and I decided to setup a chroot of CentOS 5 i386 and amd64. I also setup schroot to use my CentOS chroot. CentOS 5 amd64 setup First of all we use rinse, which can setup a RPM based distribution in a chroot. The version v1.3 shipped with Debian Lenny has some bugs: it doesn't install nss and other mandatory packages. So I downloaded v1.7 directly from Debian Sid. There is no dependencies problems and the package is arch:all, so it is straightforward to install:
$ wget http://ftp.de.debian.org/debian/pool/main/r/rinse/rinse_1.7-1_all.deb # Replace ftp.de.debian.org by your preferred Debian mirror
$ dpkg -i rinse_1.7-1_all.deb
Then I create the chroot directory and launch rinse:
$ mkdir /srv/chroot/centos5-amd64
$ rinse --arch amd64 --distribution centos-5 --directory /srv/chroot/centos5-amd64 # N.B. you must use --arch, the default is i386
Once installation is complete, you can add an entry for this distribution in /etc/schroot/schroot.conf:
[centos5-amd64]
description=Centos 5 (amd64)
location=/srv/chroot/centos5-amd64
priority=3
users=XXX
groups=
root-groups=root
type=directory
run-setup-scripts=true
run-exec-scripts=true
Replace XXX by your login. If you try to login directly, you will get warnings:
$ schroot -c centos5-i386
I : [chroot centos5-i386-a952de23-7f4b-4bae-a9b9-752ecee4a185] Ex cution de l'interpr teur de commandes initial :  /bin/bash 
-bash: /dev/null: Permission denied
This is a bit misleading because the real problem is that nothing is created in /dev/. CentOS delegates creating char/block devices to udev. You have two solutions to solve this issue:
$ MAKEDEV random
$ MAKEDEV console
$ MAKEDEV zero
$ MAKEDEV null
$ MAKEDEV stdout
$ MAKEDEV stdin
$ MAKEDEV stderr
$ rsync -av /srv/chroot/lenny-amd64/dev/* /srv/chroot/centos5-amd64/dev/
That's it, you now have a functional chrooted CentOS 5 environment:
$ schroot -c centos5-amd64 cat /etc/redhat-release
I : [chroot centos5-amd64-b9bae264-285b-4d17-a046-13386736cecd] Ex cution de la commande :   cat /etc/redhat-release  
CentOS release 5.5 (Final)
CentOS 5 i386 setup To setup an i386 environment, we follow almost the same scheme, except we need to fix a bug in rinse v1.7: we need to call linux32 before executing chroot. The problem is that the first stage installation of rinse install an i386/686 environment but as soon as you call chroot yum install ..., it will guess that the system is amd64 and will install missing packages. See the Debian bug report and the example patch attached to correct this behavior. WARNING: this patch is just an example, you can apply it for creating CentOS i386 chroot on Lenny amd64 host but you should remove the patch as soon as the installation is complete.
$ mkdir /srv/chroot/centos5-i386/
$ rinse --arch i386 --distribution centos-5 --directory /srv/chroot/centos5-i386 # With /usr/lib/rinse/centos-5/post-install.sh patched 
$ rsync -av /srv/chroot/lenny-i386/dev/* /srv/chroot/centos5-i386/dev/
Add this distribution to /etc/schroot/schroot.conf:
[centos5-i386]
description=Centos 5 (i386)
location=/srv/chroot/centos5-i386
priority=3
users=XXX
groups=
root-groups=root
type=directory
run-setup-scripts=true
run-exec-scripts=true
personality=linux32
You now have a schroot of CentOS 5 i386:
$ schroot -c centos5-i386 cat /etc/redhat-release
I : [chroot centos5-i386-9acafa91-9862-4488-aaef-4ab2a482771e] Ex cution de la commande :  cat /etc/redhat-release 
CentOS release 5.5 (Final)
Happy schroot hacking!

Next.

Previous.