Search Results: "will"

9 April 2014

Dirk Eddelbuettel: BH release 1.54.0-1

A new release of the BH package is now on CRAN and its mirrors. BH provides (a sizeable subset of) the Boost library for C++, particularly (large) parts delivered as pure template headers not requiring linking. See the BH page for more details. This release provides our first update relative to the Boost tarballs we started with. It moves us from 1.51.0 (which was getting a little long in the tooth) to 1.54.0. This is just about the first time ever that I didn't package something straight from the current release (now 1.55.0). My aim was to to balance the oh, shiny, new aspect with some stability. Comments welcome--maybe I will go to the bleeding edge next time. As before, the CRAN is created by running bcp over a number of selected components of Boost. If you'd like to see additional ones include, please do get in touch too. Before uploading, I also tested against all of these sixteen CRAN dependents I could quickly test on my server given the installed dependencies there. The complete list changes follows below.
Changes in version 1.54.0-1 (2014-04-07)
  • Upgraded to Boost 1.54.0
  • Adjust build script local/script/CreateBoost.sh accordingly
  • Renamed generation_runge_kutta_cash_karp54_classic.hpp to generation_runge_kutta_cash_karp54_cl.hpp to remain within 100-character limit for tar
Courtesy of CRANberries, there is also a diffstat report for the most recent release. Comments and suggestions are welcome via the mailing list or issue tracker at the GitHub repo.

This post by Dirk Eddelbuettel originated on his Thinking inside the box blog. Please report excessive re-aggregation in third-party for-profit settings.

8 April 2014

Tanguy Ortolo: Disable your spammed addresses with Postfix

Using address extension Postfix (and many other mail servers) offers one nice address extension feature: addresses like <user+whaterver@> are implicit aliases to <user@>. This allows users to implement a simple measure to fight spam:
  1. when SomeCompany or whatever asks for your email address, give them <user+somecompany@>;
  2. if you start receiving spam at that address, you know who sold or was stolen your address;
  3. finally, you will be able to disable that address so messages are simply refused with a permanent error code.
Road sign  you shall not pass  with Gandalf
Disabling an extended address So, here is how to implement that last step with Postfix, when you detect that your extended address <user+evilcorp@> is being spammed. In /etc/postfix/main.cf:
smtpd_recipient_restrictions =
    check_recipient_access hash:/etc/postfix/recipients,
    [ ]
Then, create /etc/postfix/recipients containing the addresses to disable:
user+evilcorp@example.com   553 5.7.1 I did not subscribe to receive spam, go away
Of course, the error codes and message can be freely configured, just make sure you are using a permanent error code so senders do not retry. Hash that table, reload Postfix and it is done:
# postmap /etc/postfix/recipients
# service postfix reload
After that, your mail server will reject messages sent to these addresses. And it will do so at the RCPT TO step, saving your bandwidth for more useful things.

Daniel Pocock: reConServer for easy SIP conferencing

In the lead up to the release of Debian wheezy, there was quite some debate about the Mumble conferencing software which uses the deprecated and unsupported CELT codec. Although Mumble has very recently added Opus support, it is still limited by the fact that it is a standalone solution without any support for distributed protocols like SIP or XMPP. Making SIP conferencing easy Of course, people could always set up SIP conferences by installing Asterisk but for many use cases that may be overkill and may simply introduce alternative security and administration overheads. Enter reConServer The popular reSIProcate SIP stack includes a high-level programming API, the Conversation Manager, dubbed librecon. It was developed and contributed to the open source project by Scott Godin of SIP Spectrum. In very simple terms, a Conversation object with two Participants is a phone call. A Conversation object with more than two Participants is a conference. The original librecon includes a fully functional demo app, testUA that allows you to control conferences from the command line. As part of Google Summer of Code 2013, Catalin Constantin Usurelu took the testUA.cxx code and converted it into a proper daemon process. It is now available as a ready-to-run SIP conferencing server package in Debian and Ubuntu. The quick and easy way to try it Normally, a SIP conferencing server will be linked to a SIP proxy and other infrastructure. For trying it out quickly, however, no SIP proxy is necessary. Simply install the package with the default settings and then configure a client to talk to the reConServer directly by dialing the IP address of the server. For example, set the following options in /etc/reConServer/reConServer.config:
UDPPort = 5062
EnableAutoAnswer = true
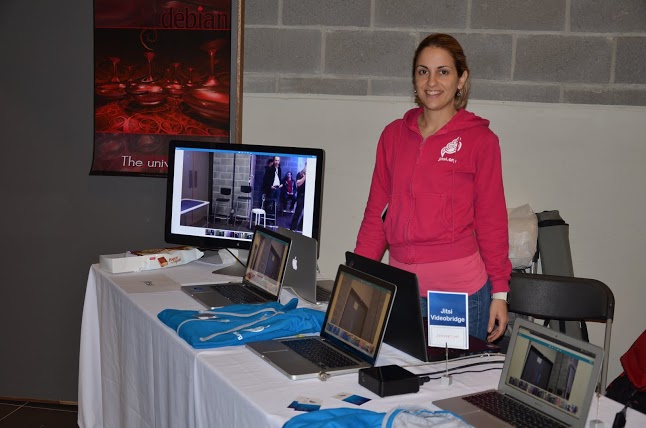
and it will happily accept all SIP calls sent to the IP address where it is running. Now configure Jitsi to talk to it directly in serverless SIP configuration: Notice here that we simply put a username without any domain part, this tells Jitsi to create an account that can operate without a SIP proxy or registration server: Calling in to the conference Notice in the screenshot below we simply dial the IP address and port number of the reConServer process, sip:192.168.1.100:5062. When the first call comes in, reConServer will answer and place the caller on hold. When the next caller arrives, the hold should automatically finish and audio will be heard. Next steps To make it run as part of a proper SIP deployment, set the necessary configuration options (username, password, proxy) to make reConServer register to the SIP proxy. Users can then call the conference through the proxy. To discuss any problems or questions, please come and join the recon-users mailing list or the Jitsi users list Consider using Wireshark to observe the SIP packets and learn more about the protocol.

7 April 2014

Holger Levsen: 20140407-some-jenkins-activities

Some jenkins.debian.net activities Yesterday and today I've spent some time time on jenkins.debian.net, so that it's finally only available via https, or so I thought. I quickly learned that it's better still serving via http, but only when queried from localhost :) Second, I've moved the git repo to QA group namespace on alioth and set up IRC notifications using the wonderful KGB client. There is no mailinglist which receives commit diffs yet, but thats also because it's mostly still me working on this. Though since yesterday there are now seven committers in the git history, which is two more than before: Niels Thykier submitted job configuratios for running the lintian testsuite on stable, testing and sid on every commit to the lintian git repo. The test suite passes nicely on testing and unstable but fails for stable as it needs backports and we need to make the job to install those. Gabriele Giacone submitted several patches so that soon hurd wgnu/hurd can be tested too. Currently this fails for two reasons, both of which are very temporarily: the hurd .iso image which was here this morning is gone now, and secondly I haven't installed (the locally build packages for) qemu and qemu-kvm packages with the fixes for #742386 as that .iso ain't there so this is pointless atm ;-) But I'm very happy to have a hopefully soon working job which will regularily test installation of Debian hurd and I do hope that some Debian kfreebsd enthusiasts will pick up and fix the existing jobs for kfreebsd tests. (Hint hint hint! I'm also totally happy to help with that!) This reminds me to mention one last bit: Thanks to Paul Wise, jenkins.d.n bugs are now tracked in the BTS among other Debian QA group bugs!

Vasudev Kamath: Loading Python modules/plug-ins at runtime

Some times it is desired to load arbitrary python files or pre- installed python modules during application run time.I had encountered 2 such usecases, one is in SILPA application and other is dictionary-bot which I was refactoring recently.
Case 1: Loading installed python module In case of SILPA I need to load pre-installed modules and here is the old code , that is a bit hacky code I copied from Active State Python recipies. I found a bit better way to do it using importlib module as shown below.
from __future__ import print_function
import sys
import importlib
def load_module(modulename):
    mod = None
    try:
        mod = importlib.import_module(modulename)
    except ImportError:
        print("Failed to load  module ".format(module=modulename),
                     file=sys.stderr)
    return mod
Here importlib itself takes care of checking if modulename is already loaded by checking sys.modules[modulename], if loaded it returns that value, otherwise it loads the module and sets it to sys.modules[modulename] before returning module itself.
Case 2: Loading python files from arbitrary location In case of dictionary bot my requirement was bit different, I had some python files lying around in a directory, which I wanted to plug into the bot during run time and use them depending on some conditions. So basic structure which I was looking was as follows.
      pluginloader.py
      plugins
       
       __ aplugin.py
       
       __ bplugin.py
pluginloader.py is the file which needs to load python files under plugins directory. This was again done using importlib module as shown below.
import os
import sys
import re
import importlib
def load_plugins():
    pysearchre = re.compile('.py$', re.IGNORECASE)
    pluginfiles = filter(pysearchre.search,
                           os.listdir(os.path.join(os.path.dirname(__file__),
                                                 'plugins')))
    form_module = lambda fp: '.' + os.path.splitext(fp)[0]
    plugins = map(form_module, pluginfiles)
    # import parent module / namespace
    importlib.import_module('plugins')
    modules = []
    for plugin in plugins:
             if not plugin.startswith('__'):
                 modules.append(importlib.import_module(plugin, package="plugins"))
    return modules
Above code first searches for all python file under specified directory and creates a relative module name from it. For eg. file aplugin.py will become .aplugin. Before loading modules itself we will load the parent module in our case plugins, this is because relative imports in python expects parent module to be already loaded. Finally for relative imports to work with importlib.import_module we need to specify parent module name in package argument. Note that we ignore files begining with __, or specifically we don't want to import __init__.py, this will be done when we import parent module. The above code was inspired from a answer on StackOverflow, which uses imp module, I avoided imp because its been deprecated from Python 3.4 in favor of importlib module.

Russ Allbery: Review: Fantasy & Science Fiction, September/October 2011

Review: Fantasy & Science Fiction, September/October 2011
Editor: Gordon van Gelder
Issue: Volume 121, No. 3 & 4
ISSN: 1095-8258
Pages: 258
Another review of a magazine that I finished quite some time ago. Apologies for any inaccuracies or lack of depth in the reviews. There wasn't much in Charles de Lint's reviews in this issue that interested me, but Michelle West covers a great selection of books. Two of them (The Wise Man's Fear and The Quantum Thief) are already on my to-read list; the third, The Postmortal, sounded interesting and would go on my list to purchase if I didn't already have so many good books I've not read. Otherwise, this issue is short on non-fiction. The only other essay entry is a film review from Kathi Maio, which is the typical whining about all things film that F&SF publishes. "Rutger and Baby Do Jotenheim" by Esther M. Friesner: Baby is a former pole dancer with a toy poodle named Mister Snickers, which warns you right away that this story is going to involve a few over-the-top caricatures and more use of the word "piddle" than one might ideally want. Rutger is a mythology professor who tolerates her for the standard reasons in this sort of pairing. They're travelling across country to Baby's sister's wedding when their car breaks down in Minnesota, prompting an encounter with frost giants. As you might expect, this is a sort of fractured fairy tale, except based on Norse mythology instead of the more typical Grimm fare. The fun is in watching these two apparent incompetents (but with enough knowledge of mythology to clue in the reader) reproduce the confrontation between Thor and Utgard-Loki. The fight with old age is particularly entertaining. If you've read any of Friesner's other stories, you know what to expect: not much in the way of deeper meaning, but lots of fun playing with stereotypes and an optimistic, funny outcome. Good stuff. (7) "The Man Inside Black Betty" by Sarah Langan: This story comes with a mouthful of a subtitle: "Is Nicholas Wellington the World's Best Hope?" It's also a story that purports to be written by a fictional character, in this case one Saurub Ramesh (with Langan credited as having done "research"). It's told in the style of first-person journalism, relating the thoughts and impressions of Ramesh as he interviews Nicholas Wellington. The topic is Black Betty: a black hole above Long Island Sound. Wellington is a scientific genius and iconoclast with radical theories of black holes that contradict how the government has been attempting to deal with Black Betty, unsuccessfully. The structure here was well-handled, reminding me a lot of a Michael Lewis article during the financial collapse. Langan has a good feel for how journalism of this type mixes personalities, politics, and facts. But it's all setup and no story. We get some world building, and then it's over, with no resolution except pessimism. Meh. (4) "A Borrowed Heart" by Deborah J. Ross: Ross starts with the trappings of urban fantasy transplanted into a Victorian world: supernatural creatures about, a protagonist who is a high-class prostitute, and sex and a sucubus by the second page. It evolves from there into a family drama and an investigation, always giving the reader the impression that a vampire will jump out at any moment. But the ending caught me entirely by surprise and was far more effective due to its departure from the expected path. Well done. (7) "Bright Moment" by Daniel Marcus: The conflict between terraforming and appreciation for the universe as we find it is an old story pattern in science fiction, and Marcus doesn't add much here. I think the story would have been stronger if he'd found a way to write the same plot with a pure appeal to environmental beauty without the typical stakes-raising. But he does sprinkle the story with a few interesting bits, including a pod marriage and a futuristic version of extreme sports as a way of communing with nature. (6) "The Corpse Painter's Masterpiece" by M. Rickert: This is typical of my reaction to a Rickert story: shading a bit too much towards horror for me, a bit too cryptic, well-written but not really my thing. It's about a corpse painter who does the work of an informal mortician, improving the appearance of bodies for their funerals, and the sheriff who brings him all the dead bodies. It takes an odd macabre twist, and I have no idea what to make of the ending. (4) "Aisle 1047" by Jon Armstrong: Armstrong is best known for a couple of novels, Grey and Yarn, which entangle their stories in the future of marketing and commerce. One may be unsurprised, then, that this short story is on similar themes, with the intensity turned up to the parody point. Tiffan3 is a department-store saleswoman, spouting corporate slogans and advertising copy while trying to push customers towards particular products. The story follows the escalation into an all-out brand war, fought with the bubbly short-cut propaganda of a thirty-second commercial. For me, it fell awkwardly between two stools: it's a little too over-the-top and in love with its own bizarre alternate world to be effective satire, but the world is more depressing than funny and the advertising copy is grating. More of a curiosity than a successful story, I think. (5) "Anise" by Chris DeVito: Stories that undermine body integrity and focus on the fascinated horror of violation of physical boundaries aren't generally my thing, so take that into account in this review. Anise's husband died, but that's not as much of a problem as it used to be. Medical science can resurrect people via a sort of permanent, full-body life support system, making them more cyborg than human. "Anise" is about the social consequences of this technology in a world where a growing number of people have a much different relationship with their body than the typical living person today. It's a disturbing story that is deeply concerned with the physical: sex, blood, physical intimacy in various different forms, and a twisted type of psychological abuse. I think fans of horror will like this more than I did, although it's not precisely horror. It looks at the way one's perception of self and others can change by passing through a profound physical transformation. (5) "Spider Hill" by Donald Mead: I liked this story a lot better. It's about witchcraft and farm magic, about family secrets, and a sort of coming-of-age story (for a girl rather than a boy, for once). The main character is resourceful, determined, but also empathetic and aware of the impact of her actions, which made her more fun to read about. I doubt I'll remember this for too long, but when skimming through it again for a review, I had fond memories of it. (6) "Where Have All the Young Men Gone?" by Albert E. Cowdrey: Cowdrey in his paranormal investigation mode, which I like better than his horror mode. For once, the protagonist isn't even a lower-class or backwoods character. Instead, he's a military historian travelling in Austria who runs across a local ghost story. This is a fairly straightforward ghost investigation that follows a familiar path (albeit to an unusual final destination), but Cowdrey is a good story-teller and I liked the protagonist. (7) "Overtaken" by Karl Bunker: This is the sort of story that delivers its moral with the force of a hammer. It's not subtle. But if you're in the right mood for that, it's one of the better stories of its type. It's about a long-journey starship, crew in hibernation, that's overtaken by a far newer and faster mechanized ship from Earth that's attempting to re-establish contact with the old ships. The story is a conversation between the ship AIs. Save this one until you're in the mood for an old-fashioned defense of humanity. (8) "Time and Tide" by Alan Peter Ryan: Another pseudo-horror story, although I think it's better classified as a haunting. A wardrobe recalls a traumatic drowning in the childhood of the protagonist. As these things tend to do in stories like this, reality and memory start blurring and the wardrobe takes on a malevolent role. Not my sort of thing. (3) "What We Found" by Geoff Ryman: Any new Geoff Ryman story is something to celebrate. This is a haunting story on the boundaries between the scientific method and tribal superstition, deeply entangled with the question of how one recovers from national and familial trauma. How can we avoid passing the evils and madness of one generation down to the next? Much of the story is about family trauma, told with Ryman's exceptional grasp of character, but the science is entangled in an ingenious way that I won't spoil. As with Air, this is in no way science fiction. The science here would have fascinating and rather scary implications for our world, but clearly is not how science actually works. But as an insight into politics, and into healing, I found it a startlingly effective metaphor. I loved every bit of this. By far the best story of the issue. (9) Rating: 7 out of 10

6 April 2014

Julien Danjou: Doing A/B testing with Apache httpd

When I started to write the landing page for The Hacker's Guide to Python, I wanted to try new things at the same time. I read about A/B testing a while ago, and I figured it was a good opportunity to test it out. A/B testing If you do not know what A/B testing is about, take a quick look at the Wikipedia page on that subject. Long story short, the idea is to serve two different version of a page to your visitors and check which one is getting the most success. When you found which version is better, you can definitely switch to it. In the case of my book, I used that technique on the pre-launch page where people were able to subscribe to the newsletter. I didn't have a lot of things I wanted to test out on that page, so I just used that approach on the subtitle, being either "Learn everything you need to build a successful Python project" or "It's time you make the most out of Python". Statistically, each version would be served half of the time, so both would get the same number of view. I then would build statistics about which page was attracting the most subscribers. With the results I would be able to switch definitively to that version of the landing page. Technical design My Web site, this Web site, is entirely static and served by Apache httpd. I didn't want to use any dynamic page, language or whatever. Mainly because I didn't want to have something else to install and maintain just for that on my server. It turns out that Apache httpd is powerful enough to implement such a feature. There are different ways to build it, and I'm going to describe my choices here. The first thing to pick is a way to balance the display of the page. You need to find a way so that if you get 100 visitors, around 50 will see the version A of your page, and around 50 will see the version B of the page. You could use a random number generator, pick a random number for each visitor, and decides which page he's going to see. But it turns out that I didn't find a way to do that with Apache httpd at first sight. My second thought was to pick the client IP address. But it's not such a good idea, because if you got visitors from, for example, people behind a company firewall, they are all going to be served the same page, so that kind of kills the statistics. Finally, I picked time based balancing: if you visit the page on a second that is even, you get version A of the page, and if you visit the page on a second that is odd, you get version B. Simple, and so far nothing proves there are more visitors on even than odd seconds, or vice-versa. The next thing is to always serve the same page to a returning visitor. I mean that if the visitor comes back later and get a different version, that's cheating. I decided the system should always serve the same page once a visitor "picked" a version. To do that, it's simple enough, you just have to use cookies to store the page the visitor has been attributed, and then use that cookie if he comes back. Implementation To do that in Apache httpd, I used the powerful mod_rewrite that is shipped with it. I put 2 files in the books directory, named either "the-hacker-guide-to-python-a.html" and "the-hacker-guide-to-python-b.html" that got served when you requested "/books/the-hacker-guide-to-python".
RewriteEngine On
RewriteBase /books

# If there's a cookie called thgtp-pre-version set,
# use its value and serve the page
RewriteCond % HTTP_COOKIE thgtp-pre-version=([^;])
RewriteRule ^the-hacker-guide-to-python$ % REQUEST_FILENAME -%1.html [L]

# No cookie yet and
RewriteCond % HTTP_COOKIE !thgtp-pre-version=([^;]+)
# the number of seconds of the time right now is even
RewriteCond % TIME_SEC [02468]$
# Then serve the page A and store "a" in a cookie
RewriteRule ^the-hacker-guide-to-python$ % REQUEST_FILENAME -a.html [cookie=thgtp-pre-version:a:julien.danjou.info,L]

# No cookie yet and
RewriteCond % HTTP_COOKIE !thgtp-pre-version=([^;]+)
# the number of seconds of the time right now is odd
RewriteCond % TIME_SEC [13579]$
# Then serve the page B and store "b" in a cookie
RewriteRule ^the-hacker-guide-to-python$ % REQUEST_FILENAME -b.html [cookie=thgtp-pre-version:b:julien.danjou.info,L]

With that few lines, it worked flawlessly. Results The results were very good, as it worked perfectly. Combined with Google Analytics, I was able to follow the score of each page. It turns out that testing this particular little piece of content of the page was, as expected, really useless. The final score didn't allow to pick any winner. Which also kind of proves that the system worked perfectly.
But it still was an interesting challenge!

4 April 2014

Daniel Pocock: Best real-time communication (RTC / VoIP) softphone on the Linux desktop?

The Debian community has recently started discussing the way to choose the real-time communications (RTC/VoIP) desktop client for Debian 8 (jessie) users. Debian 7 (wheezy), like Fedora, ships GNOME as the default desktop and the GNOME Empathy client is installed by default with it. Simon McVittie, Empathy package maintainer has provided a comprehensive response to the main discussion points indicating that the Empathy project comes from an Instant Messaging (IM) background (it is extremely easy to setup and use for XMPP chat) but is not a strong candidate for voice and video. Just how to choose an RTC/VoIP client then? One question that is not answered definitively is just who should choose the default RTC client. Some people have strongly argued that the maintainers of individual desktop meta-packages should choose as they see fit. Personally, I don't agree with this viewpoint and it is easy to explain why. Just imagine the maintainers of GNOME choose one RTC application and the maintainers of XFCE choose an alternative and these two RTC applications don't talk to each other. If a GNOME user wants to call an XFCE user, do they have to go to extra effort to get an extra package installed? Do they even have to change their desktop? For power users these questions seem trivial but for many of our friends and family who we would like to contact with free software, it is not amusing. When the goal of the user is to communicate freely and if they are to remain free to choose any of the desktops then a higher-level choice of RTC client (or at least a set of protocols that all default clients must support) becomes essential. Snail mail to the rescue? There are several friends and family I want to be able to call with free software. The only way I could make it accessible to them was to burn self-booting Debian Live desktop DVDs with an RTC client pre-configured. Once again, as a power-user maybe I have the capability to do this - but is this an efficient way to overcome those nasty proprietary RTC clients, burning one DVD at a time and waiting for it to be delivered by snail mail? A billion browsers can't be wrong WebRTC has been in the most recent stable releases of Firefox/Iceweasel and Chrome/Chromium for over a year now. Many users already have these browsers thanks to automatic updates. It is even working well on the mobile versions of these browsers. In principle, WebRTC relies on existing technologies such as the use of RTP as a transport for media streams. For reasons of security and call quality, the WebRTC standard mandates the use of several more recent standards and existing RTC clients simply do not interoperate with WebRTC browsers. It really is time for proponents of free software to decide if they want to sink or swim in this world of changing communications technology. Browsers will not dumb-down to support VoIP softphones that were never really finished in the first place. Comparing Empathy and Jitsi There are several compelling RTC clients to choose from and several of them are now being compared on the Debian wiki. Only Jitsi stands out offering the features needed for a world with a billion WebRTC browser users.
Feature Empathy WebRTC requirement? Comments
Internet Connectivity Establishment (ICE) and TURN (relay) Only for gmail XMPP accounts, and maybe not for much longer For all XMPP users with any standards-based TURN server, soon for SIP too Mandatory Enables effective discovery of NAT/firewall issues and refusal to place a call when there is a risk of one-way-audio. Some legacy softphones support STUN, which is only a subset of ICE/TURN.
AVPF X Mandatory Enables more rapid feedback about degrading network conditions, packet loss, etc to help variable bit rate codecs adapt and maximise call quality. Most legacy VoIP softphones support AVP rather than AVPF.
DTLS-SRTP X Mandatory for Firefox, soon for Chrome too DTLS-based peer-to-peer encryption of the media streams. Most legacy softphones support no encryption at all, some support the original SRTP mechanism based on SDES keys exchanged in the signalling path.
Opus audio codec X Strongly recommended. G.711 can also be used but does not perform well on low bandwidth/unreliable connections Opus is a variable bit rate codec the supercedes codecs like Speex, SILK, iLBC, GSM and CELT. It is the only advanced codec browsers are expected or likely to implement. Most of the legacy softphones support the earlier codec versions (such as GSM) and some are coded in such a way that they can't support any variable bit-rate codec at all.
Retrofitting legacy softphones with all of these features is no walk in the park. Some of them may be able to achieve compliance more easily by simply throwing away their existing media code and rebuilding on top of the WebRTC media stack used by the browsers However, the Jitsi community have already proven that their code can handle all of these requirements by using their media processing libraries to power their JitMeet WebRTC video conferencing server Dreams are great, results are better Several people have spoken out to say they want an RTC client that has good desktop integration (just like Empathy) but I'm yet to see any of them contribute any code to such an effort. Is this type of desktop integration the ultimate priority and stubbornly non-negotiable though? Is it more an example of zealous idealism that may snuff out hope of bringing the optimum communications tools into the hands of users? As for solving all the other problems facing free communications software, the Jitsi community have been at it for more than 10 years. Just have a look at their scorecard on Github to see what I mean. Jitsi lead developer Emil Ivov has a PhD in multimedia and is a regular participant in the IETF, taking on some of the toughest questions, like how to make a world with two protocols (SIP and XMPP) friendly for real users. A serious issue for all Linux distributions Communications technology is one of the most pervasive applications and also one of the least forgiving. Users have limited patience with phones that don't work, as the Australian Russell Crowe demonstrated in his infamous phone-throwing incident. Maximizing the number of possible users is the key factor that makes networks fail or succeed. It is a knife that cuts both ways: as the free software community struggles with this issue, it undermines our credibility on other issues and makes it harder to bring free desktops to our friends, families and workplaces. Do we really want to see the rest of our work in these areas undermined, especially when there is at least one extremely viable option knocking at the door?

Luciano Bello: Private folder in Dropbox

I wanted to have a directory in my Dropbox where every file placed get some sort of encryption. They might be personal pictures (if you know what I mean), finance notes, patent ideas, or the like. I create those files constantly, often with my phone. While I would like to back them up on the cloud, I don t need to access them regularly. The problem is that I don t want my phone to storage them (at least not plain) for obvious reasons. And, on top of this, Android s Dropbox app does not allow to disable synchronization by folder. So, here is the scheme I came up with. Maybe it is also useful for you or you get some idea how to improve it. You will need an always-on-line computer with Dropbox client (for Dropbox synchronization), GnuPG (for cipher the files), and a really nice tool called incron (which monitors a directory and trigger actions). The instructions: That s all, each time you put something in your private folder, incron will cipher it and leave it there.

Mario Lang: Accessible voting graphs

It is that time of the year again, Debian is electing the Project Leader for 2014/15. Whenever a Debian vote is in progress, I find myself rather happy to rediscover that Debian is providing text mode voting graphs. These are quite accessible to me as a braille user. It is rather unusual for me as a blind person to be able to access any graphs on the internet at all. All this has been made possible by gnuplots ability to generate text plots, and Manoj's willingness to implement it during his term as project secretary. Thanks to Gnuplot and Manoj, and thanks to the current secretary for keeping this feature, it is (at least to me) a very nice to have, and actually makes Debian rather unique. I personally don't know of any other major projects which provide text graphs. We are indeed setting a very good example here. It would be nice if other projects would adopt this as well. This is bridging the digital divide for me. For completeness sake I should probably mention that text graphs are not an universal solution for blind users. Those of us who do not use braille will probably have a very hard time extracting any meaningful information from this ASCII character salad. But to a braille user used to reading two dimensional information from the screen, it does actually work rather well. Some solutions from the 90s, when people didn't have graphical terminals readily available everywhere, are still very good accessibility workarounds. I am going to post another article about how I play chess on a computer, with newsgroup-style chessboard diagrams. Now that I think of it, these two topics are very related. There are some rather nifty solutions floating around from the good old text mode days which we need to revive before they finally get forgotten on the internet.

Gunnar Wolf: Mozilla: So our communitary echobox *does* resound with social issues

I woke up to the news that, after a very short tenure, Brendan Eich steps down as the Mozilla CEO. Why? Because of the community outcry. Because some years ago, Eich pubilcly supported (and donated funds) the ban of any kind of marriages in California that were not between a man and a woman. The world has advanced enormously in this regard in the last years/decades, and so many individuals and organizations opposed and announced they would boycott Mozilla that either him or Mozilla could not stand the pressure anymore. So, of course, it's sad the person had to resign. Many people talked about freedom of speech, freedom of harbouring his own personal opinion But when it comes to the rights of minorities, particularly of minorities that have suffered such hard prejudice and abuse as the gay, lesbian and all the other non-orthodox sexual- and gender- orientations, righting a wrong is much more important than preserving an individual's freedom of opinion. Besides, it's not just thinking or talking about something The concrete proposition Eich supported (and eventually made him resign) is about bringing the life of thousands of people to a hellish state of uncertainty, and going back to not having a way for the society to legally recognize their way of being, their love, their lifes. But anyway What prompts me into writing this is that, once again, the Free Software (and related denominations) community has shown that a set of core values, seemingly shared by a very large amount of our own people with no coordination or correlation with what conforms us as a community (and thus, being emergent traits), are strong enough to create a critical mass, to achieve cohesion. And that ours is not just a technical community of people writing software at all layers of the stack, but first and foremost is a group of social activists, committed to making the world better. I will quote from Matthew Garrett's post on this topic, clearly more contundent and thorough that what I'm trying to come up with:

The Mozilla Manifesto discusses individual liberty in the context of use of the internet, not in a wider social context. Brendan's appointment was very much in line with the explicit aims of both the Foundation and the Corporation - whatever his views on marriage equality, nobody has seriously argued about his commitment to improving internet freedom. So, from that perspective, he should have been a fine choice. But that ignores the effect on the wider community. People don't attach themselves to communities merely because of explicitly stated goals - they do so because they feel that the community is aligned with their overall aims. The Mozilla community is one of the most diverse in free software, at least in part because Mozilla's stated goals and behaviour are fairly inspirational. People who identify themselves with other movements backing individual liberties are likely to identify with Mozilla. So, unsurprisingly, there's a large number of socially progressive individuals (LGBT or otherwise) in the Mozilla community, both inside and outside the Corporation. A CEO who's donated money to strip rights from a set of humans will not be trusted by many who believe that all humans should have those rights. It's not just limited to individuals directly affected by his actions - if someone's shown that they're willing to strip rights from another minority for political or religious reasons, what's to stop them attempting to do the same to you? Even if you personally feel safe, do you trust someone who's willing to do that to your friends? In a community that's made up of many who are either LGBT or identify themselves as allies, that loss of trust is inevitably going to cause community discomfort.

3 April 2014

Matthew Garrett: Mozilla and leadership

A post I wrote back in 2012 got linked from a couple of the discussions relating to Brendan Eich being appointed Mozilla CEO. The tldr version is "If members of your community doesn't trust their leader socially, the leader's technical competence is irrelevant". That seems to have played out here.

In terms of background[1]: in 2008, Brendan donated money to the campaign for Proposition 8, a Californian constitutional amendment that expressly defined marriage as being between one man and one woman[2]. Both before and after that he had donated money to a variety of politicians who shared many political positions, including the definition of marriage as being between one man and one woman[3].

Mozilla is an interesting organisation. It consists of the for-profit Mozilla Corporation, which is wholly owned by the non-profit Mozilla Foundation. The Corporation's bylaws require it to work to further the Foundation's goals, and any profit is reinvested in Mozilla. Mozilla developers are employed by the Corporation rather than the Foundation, and as such the CEO is responsible for ensuring that those developers are able to achieve those goals.

The Mozilla Manifesto discusses individual liberty in the context of use of the internet, not in a wider social context. Brendan's appointment was very much in line with the explicit aims of both the Foundation and the Corporation - whatever his views on marriage equality, nobody has seriously argued about his commitment to improving internet freedom. So, from that perspective, he should have been a fine choice.

But that ignores the effect on the wider community. People don't attach themselves to communities merely because of explicitly stated goals - they do so because they feel that the community is aligned with their overall aims. The Mozilla community is one of the most diverse in free software, at least in part because Mozilla's stated goals and behaviour are fairly inspirational. People who identify themselves with other movements backing individual liberties are likely to identify with Mozilla. So, unsurprisingly, there's a large number of socially progressive individuals (LGBT or otherwise) in the Mozilla community, both inside and outside the Corporation.

A CEO who's donated money to strip rights[4] from a set of humans will not be trusted by many who believe that all humans should have those rights. It's not just limited to individuals directly affected by his actions - if someone's shown that they're willing to strip rights from another minority for political or religious reasons, what's to stop them attempting to do the same to you? Even if you personally feel safe, do you trust someone who's willing to do that to your friends? In a community that's made up of many who are either LGBT or identify themselves as allies, that loss of trust is inevitably going to cause community discomfort.

The first role of a leader should be to manage that. Instead, in the first few days of Brendan's leadership, we heard nothing of substance - at best, an apology for pain being caused rather than an apology for the act that caused the pain. And then there was an interview which demonstrated remarkable tone deafness. He made no attempt to alleviate the concerns of the community. There were repeated non-sequiturs about Indonesia. It sounded like he had no idea at all why the community that he was now leading was unhappy.

And, today, he resigned. It's easy to get into hypotheticals - could he have compromised his principles for the sake of Mozilla? Would an initial discussion of the distinction between the goals of members of the Mozilla community and the goals of Mozilla itself have made this more palatable? If the board had known this would happen, would they have made the same choice - and if they didn't know, why not?

But that's not the real point. The point is that the community didn't trust Brendan, and Brendan chose to leave rather than do further harm to the community. Trustworthy leadership is important. Communities should reflect on whether their leadership reflects not only their beliefs, but the beliefs of those that they would like to join the community. Fail to do so and you'll drive them away instead.

[1] For people who've been living under a rock
[2] Proposition 8 itself was a response to an ongoing court case that, at the point of Proposition 8 being proposed, appeared likely to support the overturning of Proposition 22, an earlier Californian ballot measure that legally (rather than constitutionally) defined marriage as being between one man and one woman. Proposition 22 was overturned, and for a few months before Proposition 8 passed, gay marriage was legal in California.
[3] http://www.theguardian.com/technology/2014/apr/02/controversial-mozilla-ceo-made-donations-right-wing-candidates-brendan-eich
[4] Brendan made a donation on October 25th, 2008. This postdates the overturning of Proposition 22, and as such gay marriage was legal in California at the time of this donation. Donating to Proposition 8 at that point was not about supporting the status quo, it was about changing the constitution to forbid something that courts had found was protected by the state constitution.

comment count unavailable comments

Daniel Pocock: LogAnalyzer and rsyslog MongoDB support now in wheezy-backports and Ubuntu

LogAnalyzer is a powerful but simple log file analysis tool. The upstream web site gives an online demo. It is developed in PHP, runs in Apache and has no other dependencies such as databases - it can read directly from the log files. For efficiency, however, it is now trivial to make it work with MongoDB on Debian. Using a database (including MongoDB and SQL backends) also means that severity codes (debug/info/notice/warn/error/...) are retained. These are not available from many log files. The UI can only colour-code and filter the messages by severity if it has a database backend. Package status The packages just entered Debian recently. It has now been migrated to wheezy-backports and Ubuntu so anybody on wheezy or Ubuntu can use it. Quick start with MongoDB The version of rsyslog in Debian wheezy does not support MongoDB output. It is necessary to grab 7.4.8 from backports. Some versions, up to 7.4.4 in backports, had bugs with MongoDB support - if you tried those, please try again now. The backported rsyslog is a drop-in replacement for the standard rsyslog package and for users with a default configuration it is unlikely you will notice any difference. For users who customized the configuration, as always, make a backup before trying the new version.
  • Install all the necessary packages: apt-get install rsyslog-mongodb php5-mongo mongodb-server
  • Add the following to /etc/rsyslog.conf:
    module (load="ommongodb")
    *.* action(type="ommongodb" server="127.0.0.1" db="logs" collection="syslog")
  • Look for the MongoDB settings in /etc/loganalyzer/config.php and uncomment them. Comment out the stuff for disk log access.
  • Restart rsyslog and then browse your logs at http://localhost/loganalyzer

Gunnar Wolf: DrupalCamp Mexico City: April 23-25

We are organizing a DrupalCamp in Mexico City! DrupalCamp Mexico City logo As a Drupal user, I have so far attended two DrupalCamps (one in Guadalajara, Mexico, and one in Guatemala, Guatemala). They are as Free Software conferences usually are great, informal settings where many like-minded users and developers meet and exchange all kinds of contacts, information, and have a good time. Torre de Ingenier a Torre de Ingenier a, UNAM This year, I am a (minor) part of the organizing team. DrupalCamp will be held in Torre de Ingenier a, UNAM Just by Facultad de Ingenier a, where I teach. A modern, beautiful building in Ciudad Universitaria. Talks, tracks So, who is this for? You can go look at the accepted sessions, you will find there is a lot of ground. Starting from the very introduction to how Drupal is structured and some tips on how to work with it (delivered by yours truly), through workflows for specific needs, to strong development-oriented talks. The talks are structured along four tracks: "Training", "Theming", "Development", "Business" and "SymfonyDay". "SymfonyDay"? Yes. Drupal is a fast-evolving Free Software project. Most users are currently using versions 6 and 7, which are as different between each other as day and night... But the upcoming Drupal 8 brings even greater changes. One of the most interesting changes I can see is that Drupal will now be based on a full MVC framework, Symfony. One of the days of our DrupalCamp will be devoted to Symfony (dubbed the Symfony Day). ...And... Again, just look at the list of talks. You will find a great amount of speakers interested in coming here. Not just from Mexico City. Not just from Mexico. Not just from Latin America. I must say I am personally impressed. Sponsors! Of course, as with any volunteer-run conferences: We are still looking for sponsors. We believe being a DrupalCamp sponsor will greatly increase your brand visibility in the community you want to work with. There are still a lot of expenses to cover to make this into all that we want. And surely, you want to be a part of this great project. There are many sponsor levels Surely you can be part of it!

AttachmentSize
drupalcampmx.png57.81 KB
torre_ing.jpg90.22 KB
torre_ing_mini.jpg21.64 KB

Aigars Mahinovs: Wireless photo workflow

For a while now I've been looking for ways to improve my photo workflow - to simplify and speed up the process. Now I've gotten a new toy to help that along - a Panasonic FlashAir SD card with WiFi connectivity. I was pretty sure that build-in workflows of some more automated solutions would not be a perfect fit for me, so I got this card which has a more manual workflow and a reasonable API, so I could write my own. Now I am trying to work out my requirements, the user stories if you will. I see two distinct workflows: live event and travel pictures. In both cases I want the images to retain the file names, Exif information and timing of the original photos and also have embedded GPS information from the phone synced to the time the photo was taken. And if I take a burst of very similar photos, I want the uploading process to only select and upload the "best" one (trivial heiristic being the file size) with an ability for me to later choose another one to replace it. There would need to be some way of syncing phone and camera time, especially considering that phones usually switch to local time zone when traveling and cameras do not, maybe the original time the photo was taken would need to be changed to local time zone, so that there are no photos that are taken during the day, but have a timestamp of 23:45 GMT. When I am in Live Event mode I would like the photos that I take to immediately start uploading to an event album that I create (or choose) at the start of the shoot with a preset privacy mode. This assumes that either I am willing to upload via 3G of my phone or that I have access to a stable WiFi network on-site. It might be good if I could upload a scaled down version of the pictures during the event and then later replace the image files with full-size images when the even is over and I am at home in my high-speed network. I probably don't need the full size files on my phone. When I am in Travel mode, I want to delay photo uploading until I am back at the hotel with its high speed Wifi, but also have an option to share some snapshots immediately over 3G or random cafe Wifi. I am likely to take more photos that there is memory in my phone, so I would like to clear original files from the phone while keeping them in the SD card and in the cloud, but still keeping enough metadata to allow re-uploading an image or choosing another image in a burst. Now I need to flesh out the technical requirements from the above and write an Android app to implement that. Or maybe start by writing this in Python as a cross-platform command-line/desktop app and only later porting it to Android when all the rought parts are ironed out. This will have an extra benefit of people being able to run the same workflow on a laptop instead of a phone or tablet. Let's assume that this is written in a pretty flexible way, allowing to plug in backends for different WiFi SD cards, cloud services, plug-in points for things like instant display of the latest photo on the laptop screen in full-screen mode and other custom actions, what else would people love to see in something like this? What other workflow am I completely overlooking?


2 April 2014

Joey Hess: propellor type-safe reversions

Propellor ensures that a list of properties about a system are satisfied. But requirements change, and so you might want to revert a property that had been set up before. For example, I had a system with a webserver container:
Docker.docked container hostname "webserver"
I don't want a web server there any more. Rather than having a separate property to stop it, wouldn't it be nice to be able to say:
revert (Docker.docked container hostname "webserver")
I've now gotten this working. The really fun part is, some properies support reversion, but other properties certianly do not. Maybe the code to revert them is not worth writing, or maybe the property does something that cannot be reverted. For example, Docker.garbageCollected is a property that makes sure there are no unused docker images wasting disk space. It can't be reverted. Nor can my personal standardSystem Unstable property, which amoung other things upgrades the system to unstable and sets up my home directory.. I found a way to make Propellor statically check if a property can be reverted at compile time. So revert Docker.garbageCollected will fail to type check! The tricky part about implementing this is that the user configures Propellor with a list of properties. But now there are two distinct types of properties, revertable ones and non-revertable ones. And Haskell does not support heterogeneous lists.. My solution to this is a typeclass and some syntactic sugar operators. To build a list of properties, with individual elements that might be revertable, and others not:
 props
        & standardSystem Unstable
        & revert (Docker.docked container hostname "webserver")
        & Docker.docked container hostname "amd64-git-annex-builder"
        & Docker.garbageCollected

Francesca Ciceri: On translations

"Take, for example, the opening to Eleanor Catton's The Luminaries: 'The twelve men congragated in the smoking room of the Crown Hotel gave the impression of a party accidentally met.' This is emphatically not the same as starting a novel with 'So there they were: a dozen men in the Crown Hotel, all together in the smoking-lounge, looking like they'd only met there by chance.' Yes, the explicit narrative data conveyed in the two are the same, but just as you wouldn't be happy with your publisher simply producing a sort of casual paraphrase of your writing and publishing that under your name, so your foreign-language publishers are hiring people to write exactly the same book as the one you've written. (Except for all the words, obviously.) Sound difficult? The reality is harder still. Every language is different. There's no single word in one language that maps perfectly onto a word in another - not one. And every language has things it can do, and things it can't."
[...]
"Once the contract is signed, the translator takes a deep breath and dives in. Their job is two-fold, and simple: they read you, then they write you.
They read you with more care than anybody else will, more demandigly, more inquiringly. Yes, your editor might take a moment to consider your punctuation if it doesn't work and needs rethinking, but translators have to think hard about it even - or especially - if it does."
A beautiful piece on translators: "The curious condition of being a translator" by Daniel Hahn via Paula G es on GV-Authors mailing list.

1 April 2014

Lars Wirzenius: Obnam 1.7.4 release (backup software)

I have just released version 1.7.4 of Obnam, my backup program. Actually, the release date was yesterday, but I had trouble building the binaries. Version 1.7.4, released 2014-03-31 Bug fixes:

Marco d'Itri: Real out of band connectivity with network namespaces

This post explains how to configure on a Linux server a second and totally independent network interface with its own connectivity. It can be useful to access the server when the regular connectivity is broken. This can happen thanks to network namespaces, a virtualization feature available in recent kernels. We need to create a simple script to be run at boot time which will create and configure the namespace. First, move in the new namespace the network interface which will be dedicated to it:
ip netns add oob
ip link set eth2 netns oob
And then configure it as usual with iproute, by executing it in the new namespace with ip netns exec:
ip netns exec oob ip link set lo up
ip netns exec oob ip link set eth2 up
ip netns exec oob ip addr add 192.168.1.2/24 dev eth2
ip netns exec oob ip route add default via 192.168.1.1
The interface must be configured manually because ifupdown does not support namespaces yet, and it would use the same /run/network/ifstate file which tracks the interfaces of the main namespace (this is also a good argument in favour of something persistent like Network Manager...). Now we can start any daemon in the namespace, just make sure that they will not interfere with the on-disk state of other instances:
ip netns exec oob /usr/sbin/sshd -o PidFile=/run/sshd-oob.pid
Netfilter is virtualized as well, so we can load a firewall configuration which will be applied only to the new namespace:
ip netns exec oob iptables-restore < /etc/network/firewall-oob-v4
As documented in ip-netns(8), iproute netns add will also create a mount namespace and bind mount in it the files in /etc/netns/$NAMESPACE/: this is very useful since some details of the configuration, like the name server IP, will be different in the new namespace:
mkdir -p /etc/netns/oob/
echo 'nameserver 8.8.8.8' > /etc/netns/oob/resolv.conf
If we connect to the second SSH daemon, it will create a shell in the second namespace. To enter the main one, i.e. the one used by PID 1, we can use a simple script like:
#!/bin/sh -e
exec nsenter --net --mount --target 1 "$@"
To reach the out of band namespace from the main one we can use instead:
#!/bin/sh -e
exec nsenter --net --mount --target $(cat /var/run/sshd-oob.pid) "$@"
Scripts like these can also be used in fun ssh configurations like:
Host 10.2.1.*
 ProxyCommand ssh -q -a -x -N -T server-oob.example.net 'nsenter-main nc %h %p'

Michal &#268;iha&#345;: New SSL certificates

Today, I've replaced server SSL certificates with new ones issues by GlobalSign. These should not suffer of same trust problems as CACert one used so far (especially after CACert root certificate being removed from Debian). While doing this, I had to use SNI on server to be able to decide which SSL certificate it should use. This should work for any decent browser, but I guess your scripts might have problems, but I hope this will be rare. Anyway if you will face some issues because of this, please let me know. Other than that I've also tweaked SSL setup to follow current best practice, what could also cause troubles to some ancient clients, but I hope these are non existing in this case :-). See Qualys SSL report for more details. Anyway thanks to GlobalSign free SSL certificates for open source projects you can use hosted Weblate without any SSL warnings. PS: Similar change (just without SNI) has happened last week on phpMyAdmin web servers as well.

Filed under: English phpMyAdmin Weblate 3 comments Flattr this!

Next.

Previous.