Search Results: "Martin"

6 June 2009

Martin-Éric Racine: Killing the console bell on Jaunty?

Every once in a while, rewrites in ALSA drivers or in desktop audio components (GNOME mixer or Gstreamer) result in an impossibility to completely mute the console bell. Until recently, ALSA offered a separate channel to control this. Since Jaunty (kernel 2.6.28, ALSA 1.0.18r3) came out, not anymore. As such, I was wondering how else could I mute the console bell? Some people on Ubuntu Forum suggested blacklisting the pc-spkr kernel module, but this is entirely the wrong approach, as it completely kills sound output on this laptop's built-in speakers. I don't wanna completely lose sound support, I just wanna get rid of that annoying console bell! Others recommended setting set bell-style none in /etc/inputrc but that only works for interactive shells. The console bell still rings e.g. whenever rebooting, probably because bash gets called as a non-interactive shell by init scripts. Actually, since Jaunty, restarting the system makes the bell ring not just once, but twice! Can anyone think of any more permanent way of disabling the console bell in some global system setting?

5 June 2009

Martin Michlmayr: Corporate participation in open source communities

Someone recently asked me a few question about corporate participation in open source communities and I thought I'd share my thoughts on this topic here. Are there differences between an open source project done for a corporation and one done for personal reasons? There are many different ways to run an open source project, led by a corporation or by someone else. Some projects that are run by corporations have few outside contributors. This is often the case with projects that require copyright assignment (i.e. contributors have to assign their copyright to the corporation). These projects may not gain all the benefits of a true open source community, such as outside contributions or high levels of peer review. However, they may still be very successful projects and may have high levels of quality. Projects done by a corporation may have better planning and may have more resources than other projects. When a corporation, especially a large one, starts or becomes involves in a project it can also give credibility to the project and attract a lot of interest to the project. This means that projects done by corporations may have a bigger impact and might also be more visible in terms of publicity. How do corporations successfully utilize an open source community? Corporations can benefit from an open source community in many ways. For example, they can often find people who will review their code or make code contributions. If people become excited about what the corporation does, they might also spread the word and create viral marketing for the corporation. Establishing a community around one's project is often also a good way to identify people to hire since you already have experience working with them and know their capabilities. How do open source communities successfully utilize their corporate relationships? Corporations can make several unique contributions. For example, large corporations can use their name to attract attention to a project and give it credibility. Furthermore, corporations have some capabilities that personal contributors often don't have access. They may have special testing equipment (such as servers with thousands of CPUs or hard drives) or access to a testing lab where a professional usability test can be done. Finally, corporations can sponsor developer conferences, which are typically very effective means for the community to come together and work on activities together. It is important for projects to remember that corporations are not charities and that they will invest in an open source project for a reason. Therefore, they have to ensure that the corporation will get tangible outcomes from their involvement or sponsorship, otherwise they may not stay involved in the long run. What are the risks for a corporation when working with an open source community? One risk is that the code (or other form of contribution) is not accepted. However, this is a risk any contributor to a project faces. Before making any sort of contribution, it is therefore important to become familiar with the project and its culture. Every project has their own "do's" and "don'ts" that have to be followed. Another risk is that a corporation will invest in a community project that later on is abandoned by the community. However, in this case, the corporation could take the lead and continue to maintain the project. What are the risks for an open source community when working with a corporation? One potential risk is that the corporation will assert too much control over the project. It's important for projects to ensure that the community as a whole has influence over the direction of a project rather than one particular player. Are certain certifications needed in order for someone to participate in open source projects for a corporation? Certifications are not needed to get involved in or start a project. However, it is important to become familiar with the open source community and the project one wants to contribute to. A good first step is to read the book Producing Open Source Software by Karl Fogel which is available online. As a next step, the community in which someone wants to get involved in should be studied, for example by reading the mailing list archives. This will help to become familiar with the culture of a project as well as the mechanisms to contribute to the project. How do open source communities communicate and collaborate with corporations? In the best case, employees from corporations would interact in the project like any other contributor. That is, they should use the existing communication channels, such as mailing lists, IRC or developer gatherings. Many companies are good at working "with the community" but the ideal scenario is for a company to be part of the community and to work "in the community", just like other contributors. This is the most effective way for them to make changes to the code and project. Of course, not every corporation will get involved in a project directly. That's why it makes sense for projects to collaborate with corporations in other ways. For example, projects can talk directly to companies to get samples of their hardware in order to add support for them in their software. Projects can also work directly with corporations to find out how their project can better meet the needs of enterprise users.

31 May 2009

Martin Michlmayr: Initial thoughts on the new QNAP TS-219P

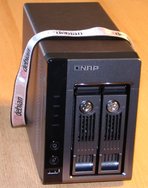
QNAP TS-219P QNAP has announced a new device earlier this month, the QNAP TS-219P. The specs are very similar to the TS-219 (1.2 GHz Kirkwood CPU, 512 MB RAM and 16 MB flash) but the device is smaller and has some other advantages. What I like about the new TS-219P: What I don't like so much: Since the TS-219 and TS-219P are quite similar, Debian and the installer will work without any problems. I updated my QNAP page to document the QNAP TS-219P, including some pictures of the new device.

24 May 2009

Martin-Éric Racine: Atom feeds per-topic

Just a quick note for those interested in subscribing only to my blog articles pertaining to a specific topic that the following Atom feeds are available:

22 May 2009

Martin F. Krafft: Swiss army knives for SMTP

If you deal with SMTP servers, you probably know swaks, the Swiss Army Knife for SMTP . Great tool for anything related to sending mails. Today, I found its counterpart for receiving mails:
python -m smtpd -n -c DebuggingServer localhost:1025

that binds a no-frills SMTP server to the specified socket which does nothing but talk SMTP to connecting clients and print received messages to stdout, e.g.:
---------- MESSAGE FOLLOWS ----------
Date: Fri, 22 May 2009 21:21:40 +0200
To: madduck@madduck.net
From: madduck@lotus.madduck.net
Subject: test Fri, 22 May 2009 21:21:40 +0200
X-Mailer: swaks v20061116.0 jetmore.org/john/code/#swaks
X-Peer: 127.0.0.1
This is a test mailing
------------ END MESSAGE ------------

Sweet, very sweet! NP: Porcupine Tree: Signify

Martin F. Krafft: Django: a beautiful and truly thin web development framework

Take the following URL:
http://my.server.tld/wow/summary/2009/05/21/?style=boxed

and imagine the following Python function:
def summary(request, year, month, day):
    response = HttpResponse()
    // do something
    return response

If you see a relation between the two, then Django is for you. The missing part is a URL mapping, a list of regular expressions, which transforms a URL into a keyword list, and maps it to a function (a HTTP view, as it s called):
(r'^wow/summary/(?P<year>\d 4 )/(?P<month>\d 2 )/(?P<day>\d 2 )/$',
    mysite.wow.summary,  'additional':'information' )

You do not have to use keyword arguments, positional parameters will work as well, and you can do anything you like within the powers of regular expressions, but the result is always along the same lines: When someone visits the above URL, Django calls the above summary( ) function (defined in the modules mysite/wow.py) and passes an object encapsulating the request, along with the components from the URL as parameters:
summary(request, 2009, 05, 21,  'additional':'information' )

It then renders the return value. The function can also throw an exception if it need to communicate e.g. a 404 error. Very clean, and there are even generic views if your data doesn t need any massaging, of if you just want to do standard things like generate PDFs. This is the core idea of Django, which I ve gathered from one talk and four hours of invested time. It s a truly thin layer, and its elegance made me bouncey. The QUERY STRING of the request will be passed in the request object, along with all the other CGI variables you re familiar with. Django provides a large number of helpers and shortcuts to save you from having to do the ugly work, including topics such as internationalisation, syndication, authentication, file uploads, and caching. In addition, Django gives you an object-relational_mapper to map the data into, and manage the data definition within your favourite RDBMS, a templating language designed to fit in with the whole philosophy, and widgets to work with forms. You do not have to use any of those. You are free to use any other Python module for the task, just as you can use all of the other features of and modules written for Python. This is particularly powerful in the context of the middleware layer. There s also a large number of pluggable applications and snippets for re-use. The only concern I have at this point is whether features like tagging are going to find their way into the framework, because tracking numerous external plugins for a site and keeping them working across versions reminds me of the nightmares I had with Zope and Plone (I stopped working with (and on) those before I had a chance to dive into version 3 of each). The fact that Django leaves data storage to other tools (in fact, it s entirely up to you) makes those nightmares seem further distant. All in all, I am excited to have had a chance to take a brief glance at the software, and I am looking forward to doing more with it. Unfortunately, it looks like it will take quite some time to wade through existing plugins and design the rest of an application that can finally replace the horrific dung-pile that is my homepage.

20 May 2009

Gustavo Noronha Silva: GMail and threads

Martin blogged about Microsoft pushing proprietary extensions instead of using long existing standards for email replies. I think it is worth pointing out that Google s GMail does not respect In-Reply-To for displaying threads, which causes people who are on groups where most use GMail to complain about people who use some other client and create sub-threads with different subjects. This is one of the reasons why I sometimes see GMail as the IE6 of email - the net effect is also in motion here.

Martin F. Krafft: Five days to free Aung San Suu Kyi

In Myanmar, Aung San Suu Kyi and 2 000 monks and activists are being detained, as the miltary junta in the country presses new, ridiculous charges against Suu Kyi a few days before the end of her house arrest. Suu Kyi, recipient of the Nobel Peace Prize and proponent of democracy, is leader of the opposition and the greatest threat to the junta s grasp on power. Given the inhumane conditions imposed upon the Burmese, and the ruthless slaughter of those who do not play by the military s rules, it is not hard to imagine that she would win any fair election, as soon as she would get a chance to run. However, if the junta are successful in pushing charges Suu Kyi is accused of breaching the house arrest after an American man sneaked into her house uninvitedly she could be locked up until after the elections in 2010, effectively disarming the threat she poses to the military regime. She is threatened to be kept in the notorious Insein Prison without medical care. As she is suffering from serious illness, this puts her life at risk. I do not usually campaign for political topics, but I ve been to Myanmar and this issue touches me deeply. The people in Myanmar need our support. Even though the 2007 Burmese anti-government protests seriously weakened the military and brought hope to the lives of millions that have been oppressed for years, the events quickly vanished from the media and allowed the junta to regain control. We must not let that happen again. It is of utmost importance to show our support and not look away. One way of doing so is by increasing visibility. If you care, please write to your newspapers, publish on your blog, and do everything else you can to raise awareness. Another way to help the Burmese people is through signing the avaaz.org petition to UN Secretary General Ban Ki-moon. Best to do all of the above! Unfortunately, avaaz.org force-subscribes everyone who signs a petition to their newsletter, which may well not be what you want. However, please do not let it stop you from signing the petition. You can later unsubscribe from the (infrequent) newsletter. I have informed the staff members of this concern. If you would like to voice your opinion too, write to info t avaaz dot org and encourage them to make the newsletter subscription optional. But make sure to also sign the petition, please.

Martin F. Krafft: Read notifications, standards, and Microsoft

Some might dread the feature of read notifications supported by certain MUAs; some call it an invasion of privacy ; and yet, it can also be useful in certain situations: When a message is read or seen in a MUA supporting this extension, the programme emits a notification back to the sender saying something along the lines of your message was read on . This is good to know, especially in times when you cannot wait for the failed-delivery-notification that follows four to five days of unsuccessful (but furious) attempts of some delivery agent, assuming it doesn t get trashed as spam. Such a read notification is logically a reply to the original message, isn t it? The RFC 680 proposed in April 1975 defines the header References as a way to point to other correspondence which this message references . This header, along with In-Reply-To (defined in the same RFC), is commonly used in every-day mail traffic to refer to previously exchanged messages, and enables mail readers to thread separate messages together into coherent conversations (it takes a human to remove the coherence, the technical aspect is infallible). Cut. Microsoft was also founded in April 1975, and it took them 20 years to barely manage to squeeze through the Internet door without the proverbial foot in it. They published a browser and several e-mail programmes, and it always appeared as if they tiredlessly tried to be different from the rest, attempting to form a clique of users, a Microsoft league in which to increase their revenue through network effects. Sounds bad, is bad, but yet again, they managed, through unimaginable feats of entrepreneurial genius and ruthless behaviour. Cut. In 1982, STD11 declared the aforementioned In-Reply-To and References headers as standards. At that time, Microsoft software didn t even know what a computer network was. Cut. Does it come as a surprise that read notifications sent by Microsoft e-mail programmes, such as Microsoft Outlook do not make use of either of these standard headers to tag read notifications they send? Instead, Microsoft pushes Thread-Topic and Thread-Index, which are undocumented and thus probably only work in a Microsoft-only context. How am I supposed to assume anything else than Microsoft actively trying to oppose standards. Anyone who boycotts standards is hindering progress and should be left behind. It s good to see that the Internet society seems to follow that trend more and more. Update: I found a way to extract the data to recreate the In-Reply-To with procmail. I don t see a way to do the same for the References header. Also, I ve only verified that this works for message disposition notifications from Outlook 2003, although I expect it to work for other, similarly crippled MUAs too.

Martin F. Krafft: Sardines in Zurich's public transport

Yesterday was my first appearance as a sardine in Zurich s public transport vehicles, as part of a campaign by the Swiss group for sustainable mobility, umverkehR, which I support: Martin and Sandro as sardines at Z rich Stadelhofen We handed out flyers and answered questions, and the general reaction was very positive. The fact that we got covered in Switzerland s most popular newspaper, 20 Minuten will add greatly to the reconnaisance factor, so that in the months to come, us sardines will be immediately recognised, hopefully provoking thought and chat over the roots of the campaign. Most of us know the sardine as a dead fish perched into a can with many others in a way to minimise space. Human-sized, walking sardines are a great way to increase awareness of the issue of over-crowded public transport. It was fun to see even the Really Serious Newspaper Readers unable to suppress a smile. Talking to friends about the campaign, I ve often been met with expressions of how absurd such a campaign is in Switzerland, possibly the country with the best public transport system world-wide. I agree, but that doesn t mean that we should not keep working on further improving it. If you ve ever been stuck in a commuter train during rush-hour, standing around in stifling heat and jealously eyed those that managed to grab a seat before you, you ll probably agree that even in Switzerland, we could be doing it better. These days, with the financial crisis weighing heavy on everyone s budgets, and with environmental concerns on the rise, we are witnessing a never-before level of readiness of the public to make sustainable choices. Confronting those people with stuffed trains doesn t reconfirm those decision. Instead, it will make those people crave their air-conditioned cars and possibly switch back to polluting the air with exhaust and noise, because it surely is more comfortable to sit in your own cool car than it is to be perched in public transport like a sardine. Thus, umverkehR s message goes mainly to the politicians: prioritise public transport in your future mobility plans, keep the prices affordable, and help get people off the road in the interest of our environment. You can see more pictures in the gallery and a short film on Youtube. We have a separate sardine blog, a Facebook account and there s even a chance for you to win travel coupons: all you have to do is submit an original photo of anything to do with over-crowded public transport by e-mail or MMS to sardine t umverkehr.ch by October 2009. You can browse all submissions on Flickr. I hope that we can spread the idea as far as New Zealand and the countries between. There are always chances in any crisis. NP: Porcupine Tree: Stupid Dream

19 May 2009

Martin-&#201;ric Racine: Invandringskonsult

In close to 11 years of living in Europe, I've accomplished plenty beyond working in the high-tech sector: I've also been fairly active in Immigration Policy, especially on aspects that affect migrant labor. Because of this, I keep on getting more and more requests to produce statements or to appear on panels to discuss issues pertaining to migrant labor and to immigrants' integration. The hot topic of last week was Swedish language for immigrants, the crux of the issue being that even though Swedish has an official language status in Finland, in practice, it is pretty much impossibly for immigrants to register their kids at the Swedish language school, to claim public services in Swedish or, even more so, to request labor training in the Swedish language at the Employment Office. The weekly newspaper Helsinki Times, in collaboration with the media think tank Magma, recently conduced a survey of the immigrant population, to find out how much they know about Swedish culture in Finland and about the Swedish language. It was in this context that the Helsinki Times and the national television's Swedish programming (FST) asked for an interview with yours truly, because I have recently visited the Ministry of Employment and Economics with a concrete proposal to facilitate the availability of labor training in the Swedish language. This FST webcast, starting at 16:03 minutes into the show, and the above Helsinki Times article provide more details about the context and about my proposal to the Ministry.

Martin Michlmayr: SheevaPlug lenny tar ball and SD cards

I updated my SheevaPlug installation instructions today to document how to boot from an SD card. The u-boot boot loader shipped with the SheevaPlug doesn't have SD/MMC card support, but PlugComputer forum user kwonsk created one that does (and which works pretty well, except for not working with some SD cards).

Martin Michlmayr: First successful installation on QNAP TS-219

I performed the first successful installation of Debian on the QNAP TS-219 using the Debian installer today. Everything is in place now but the Linux 2.6.29 kernel has to move to testing so installations will work.

Obey Arthur Liu: PGP/GPG transition 8CA99047 -> 29C0FFEE *

Here comes the new 4096 bit RSA key, replacing the old (2002) 8CA99047 1024 bit DSA key:
pub  4096R/29C0FFEE 2009-05-18
  Key fingerprint = 9590 8AA6 E4F7 BAA7 8BD6  C148 F1A6 9BE4 29C0 FFEE
uid  Obey Arthur Liu <arthur@milliways.fr>
uid  Obey Arthur Liu <obey.liu@ensimag.imag.fr>
uid  Obey Arthur Liu <graffit@graffit.net>
uid  Obey Arthur Liu <obey.liu@lzb.fr>
uid  Obey Arthur Liu <arthur.randolph@gmail.com>
sub  4096R/15D7FD9B 2009-05-18
In other news, I found a great flatshare on Riedmattstrasse in Kreis 3 in Z rich with a fellow Google summer intern. Thanks to all (Jeroen, Martin, Jaroslavs, Giacomo..) who gave me pointers about finding accomodation in Z rich. I m looking forward to a great summer there. coffee * It did involve generating about 40 millions gpg keys on a few tr s badass computing clusters UPDATE: Come on guys. Of course I followed basic key management rules. The clusters which generated the actual final keys were under my direct control and the particular slice which generated this published key is on my desk.

17 May 2009

Martin F. Krafft: Switzerland opts for biometric passports

Switzerland voted today for the introduction of biometric passports, with 50.1% for and 49.9% against, one of the closest votes since 1848 (according to NZZ). While the news don t fill me with glee there are too many unanswered questions around the digital passports one aspect of the decision surprised and even shocked me. I do not like biometric passports, because I like to know when my data are consumed, and by whom. The German government assures that only authorised parties can access those data, and published information about the security features of the German biometric passports, but I am unconvinced that those are adequate to protection for the 10 years of validity of the passport. Furthermore, I could find absolutely no information on who the authorised parties are, or which regulations cover who will become authorised in the near future. If that was properly addressed, e.g. by leaving it up to me and only me to decide who gets access, then the digital passport could actually be a good step forward, streamlining border control and making travel easier. But there is a completely different avenue of concern, no matter who gives permission to whom to consume whose data: how are they used, and where, and how long are they stored, and for what? Again, I cannot find any regulations. Instead, my question to the German Department of the Interior was answered (!) along the lines of it being up to each country to decide themselves over the use and storage of the data. In this light, it makes little difference that the German procedure for the digital passport does not permit the issuing bureau to store the data, while Switzerland s strategy is to build a central database of all these personal details (this is what shocked me). It might make you wonder what use the Swiss government is hoping for, and you might feel uncomfortable with your government building up an even tighter database of its people. But I d much rather have my data stored in Switzerland than consumed and stored every time I enter another country, because when I compare the style of governance of Switzerland to pretty much anything else out there, I am glad I get to live here (even though I am not Swiss and cannot vote). Yet, it s a worrying step in a direction of the glass human , of a society in which personal privacy is unknown and everything is part of the system. These are totalitarian visions, and it s doubtful whether we ll ever actually get there (so far, I don t think any state has come up with the information management strategies required to properly store, make use, and read sense out of the massive amounts of information), but the trend is clearly visible. In the end, however, what worries me the most is how relaxed people treat their personal information these days. Look at the infamous social networking sites, or other Web 2.0 gimmicks and you really start to wonder how headless people can be these days. I cannot immediately paint a scenario where it might be dangerous to push all kinds of information about yourself to the masses, but the mere idea of that is scary in and of itself. I d prefer to have the choice with whom to share what data. The biometric passports, despite the advantages they might bring, are one step away from that, because they empower the government to make that choice for you. I don t consider that progress at all. Update: NZZ reports that the issue is not closed. In the cantons of Grishuna and Lucerne, people are challenging the vote and a recount or even re-vote seems possible. I will post an update as soon as I know more. Then, I would also like to address some replies I ve received over the real problems behind the digital passports, because it cannot be just the central data storage it s not like your government doesn t already have all that, and I can t imagine how your fingerprint could be used against you.

16 May 2009

Martin Michlmayr: Automatic power on QNAP Turbo Station devices

All ARM based QNAP machines can turn on automatically when power is applied if the device was not powered down correctly. This is helpful when your power goes down. Follow the instructions below if you want to turn automatic power on using Debian on a QNAP TS-109, TS-119, TS-209, TS-219, TS-409 or TS-409U. Edit the file /etc/apt/sources.list and add the following line:
deb http://people.debian.org/~tbm/orion lenny main
Now install a new version of qcontrol:
apt-get update
apt-get install qcontrol
Finally, turn the automatic power feature on:
qcontrol -d &
qcontrol autopower on
kill %1
rm /var/run/qcontrol.sock

13 May 2009

Martin Michlmayr: Update on QNAP TS-119/TS-219 kernel support

I mentioned a few weeks ago that initial kernel support for the QNAP TS-119 and TS-219 Turbo NAS got accepted for 2.6.30 but that there were some issues left. Here's an update: The SATA and flash fixes are already in our 2.6.29 kernel.

11 May 2009

Martin F. Krafft: GPG-key mania

Would all the paranoid crypto-users please stop flooding Planet Debian with GPG output? And if you just cannot avoid it, please tag those posts meme, because that s what they are. If you really think there s a need for a new key, you re one step ahead of me, because so far, there s only a theoretical attack and the valid question of whether this is actually something to worry about in the context of GPG (or in the context of Git, for that matter). There is no practical exploit out there, and I don t expect one that would endanger your use of GPG any time soon. Of course, we ought to replace the current crypto infrastructure with a new one before the current one is compromised, but that should really be motivated by careful consideration and planning, not by lemming-like behaviour and the infamous tipping point. I ve long been meaning to clean up my key and may also switch to using a new one in the near future. However, I don t think there is an immediate need and I ll take time first to investigate the options RSA is hardly free from problems or an optimal choice. For instance, why would I want to use an RSA key, which is limited in GPG to 4096 bit keys? Do we really want to deal with signatures that are 4-10 times longer than their DSA counterparts? When RSA is broken, will we see a replay of this whole key-replacing frenzy? Wouldn t it make more sense to leverage the current situation and work on pushing/improving the DSA algorithm with larger keys, and to strive towards better algorithms in general, e.g. through SHA-3. If you still need to replace your key, revoke the old one, point at the new one in the revocation reason, and please refrain from abusing feed aggregators from letting the world know. If gpg cannot follow the trust chain after the revocation, please fix it. In the mean time, it is a good idea to use RIPEMD160 instead of SHA-1 for signing, with the following lines in ~/.gnupg/gpg.conf:
personal-digest-preferences SHA512 SHA384 SHA256 SHA224 RIPEMD160
default-preference-list [ ] H10 H9 H8 H11 H3 [ ]

and to set the preferences on your key accordingly:
% gpg --edit-key $KEYID
> setpref [ ] H10 H9 H8 H11 H3 [ ]
> save
% gpg --send-key

Then, make sure RIPEMD160 is being used:
% gpg --clearsign -a </dev/null   grep '^Hash:'

I ll end with a link to a decent write-up on the cryptographic basics of GPG.

10 May 2009

Martin Meredith: This whole GPG/PGP thing

So, SHA-1 has potential exploits, but you know what? I only use it for signing plain text things. Email, change files I ve no reason to use it for encryption, as I don t encrypt things Surely, if anyone is going to make something that collides with a valid signature of mine, it s going to either a) be noticable to the person reading it (random characters in an email?) or b) not be processable by whatever automated sytem is using it. I ve yet to hear of any exploit that could affect the way I use SHA-1 in a meaningful way. Ok, yes, I m not going to be using it to hash passwords in future (well, GPG uses it to hash passwords, but generally, to be able to crack that, someone would have to have my secret key anyway, which I would count as being compromised!) If someone can give me a real world example of how this can be used against me, I might go out of my way to replace my key, but for now, I don t see the need. Ok, I might take the next time I meet up with a fellow Debian Developer as a chance to replace my key, but I m not going to go out of my way to do so (as I had to for getting my key signed by my first Debian/Ubuntu Developer in the first place)

5 May 2009

Martin-&#201;ric Racine: Debian CUPS transition in progress

Since Lenny was the first Debian release to feature CUPS under its new package naming strategy, I started going through 'rdepends' results to see which packages in Squeeze still present dependencies for *cupsys* packages. Much to my amazement, there's quite many. If you are the maintainer of a package that still has those dependencies, please fix them ASAP. Alternately, if you're aware of any favorite package that does, please do not hesitate at filing a patch to help the maintainer update their debian/control. Comes June 2009, transitional CUPS packages will be removed from our debian/control.

Next.

Previous.