Search Results: "ron"

29 February 2012

Amaya Rodrigo: Why "Colussion" is brilliantly named

Collusion is "an experimental add-on for Firefox and allows you to see all the third parties that are tracking your movements across the Web."
If you are not paying for something... you, the customer, are the product being sold.
-- Andrew Lewis , Mozilla.
I am very eager to see how this evolves given that things like Adsense, no less, belong to Google, and Google (i believe, and please correct me if I am wrong), is one of Mozilla's biggest, erm, how to put it, "sponsors". Will Chrome get a similar feature? I am very veruy curious. This might be the biggest White Rabbit I've seen in a long time.

Andrew Cater: Raspberry Pi - announcement

_Something_ is going to happen at 06:00 GMT on 29th February. I predict a server meltdown ..

==

Product available from RS Components and Farnell.com - both servers not responding. Effectively a worldwide DDOS because of demand 29/2/2012

== 07:20 or so ==

Farnell sold out almost immediately: now taking pre-orders for the next batch
RS may be taking orders later in the week. [Per RaspberryPi Twitter feed]

Update: RS are also taking pre-orders and expressions of interest. Both companies will do their best to get stock to all ASAP.

Please don't blame Eben, Liz or the other RaspberryPi folks for this - they've worked miracles to get this far.

To negotiate proper licensing agreements with the two largest UK electronics distributors and get them to undertake manufacturing and distribution is, actually, a masterstroke for a small non-profit organisation.

Kartik Mistry: Updates

* In case of you ve noticed, this blog has new URL: http://0x1f1f.wordpress.com, reading from Planet Debian doesn t harm your feed reader (if any readers left ;) ). * On Debian front, I m mostly helping Debian-IN-Workers team to finish ttf->fonts naming transition and moving rest of packages to Git. Vasudev and Muneeb has done most of these work, well done! Rest of my time with Debian goes to usual updates of packages and in reading debian-devel during weekends. It is still fun, yeah. * And, illumian is born. * On personal side, life is great as usual. It looks that couple of dentist visit is coming soon. I also started jogging/running regularly since couple of months. In case you re interested, I m on dailymile too.

28 February 2012

Andreas Barth: Traveling to DebConf 11 - Zagreb to Split

On the second day, I entered the train to Split early in the morning. The train was a bit crowded, but having a seat reserved helped. Unfortunatly I knew that kind of train already from home (here known as 612), and changing colours didn't make it a better train.
Train from Zagreb to Split in Gra ac After leaving Zagreb, the train went through nice countryside. After some time hills started - with given-up houses, walls, areas. As I learned in the meantime, this track used to be not the main line to Split but a backland-line. However, since the last war (the one from 1991-1995), the shorter and faster direct line is still cut. In Knin one could still see the reminders of the direct line which was electrified.
Landscape from within the train The railway was a mixture of historic operations (with many people, changing switches by going there and by hand and using flags instead of signals) and directly into the 21nd century with electronic signal boxes just being built.
train junction in Perkovi In spite of "the train should be an alternative to cars and busses"-speeches, as there was only one (and overcrowded) train suiteable for going to Split, priorities seem to be elsewhere (not too uncommon for politics on public transport in Europe). Also, there was obviously much more money put into the streets than into the trains. The journey to Split should have taken about 6 hours, but the train in the opposite direction was a bit late, so I arrived late about 30 minutes. Directly on the platform there was a crowd of people trying to let appartments to tourists etc. Ignoring that, I first got rid of my luggage in the train station, bought the bus ticket for the next leg, and as having planned for late trains still had ample of time to see Split. This was my first "southern" target on this journey, so I could say Hi to fig trees (and their smell as they were blooming at that time). Split itself has an historic center (being dated back to the Romans). One could also go up a hill and have an overview over both Split and the Adria. All in all I found Hrvatska being compareable to other nice parts of Europe: Many tourists, overcrowded, and prices similar to Germany. Usage of public transport by tourists seems strange, and mostly only done by interrailers.

Paul Wise: Debian/Ubuntu games screenshot party results

The Debian/Ubuntu games team recently organised a half-day screenshots party for creating screenshots for all the games that are available in Debian/Ubuntu. Unfortunately, only 5 people participated in the screenshots party, I had hoped that we would get more folks turn up. Only one of those was not already involved in the games team and that one person found out via our spam on the #debian-mentors IRC channel. This means that most of our promotion of the event was ineffective. Hopefully for future games parties we can improve this, please let us know if you have any ideas about that. We also had 7 other people on the channel during the party lurking, discussing and or working on other things, in particular Ben Armstrong was working on a games live CD. Over the 7 hours of the party, we uploaded 100 screenshots for 40 different packages. Of the packages, 2 are available only in Debian (auralquiz, cutechess), one is available only in Ubuntu (plasma-widget-tictactoe) and the rest are available in both. I think we got quite a bit done for such a small group. Some of us could not resist filing some bugs on packages that had issues preventing or delaying us from taking screenshots. I also suggested to one maintainer that his package (acm4) be removed from Debian, since it is obsoleted by acm and unusable. If you want to play some games, check out goplay, which is a tool for browsing available games using debtags that displays screenshots from the games-thumbnails package, which has just been updated with the screenshots created during the party. goplay needs some more development, if you would like to help out with that, you would be most welcome. If you are interested to see our screenshots, they are all on the screenshots.debian.net website and the packages are auralquiz, cardstories, londonlaw, cube2font, ardentryst, cutechess, pianobooster, emacs-chess, xye, flare, tmw, garden-of-coloured-lights, flight-of-the-amazon-queen, geekcode, glpeces, fofix, unknown-horizons, klickety, polygen, tictactoe, xscreensaver-screensaver-dizzy, goban-original-games, xjokes, mudlet, xabacus, xtux-client, connectagram, crystalspace, pescetti, purity-ng, qstat, slashem, sudoku, minetest, xscavenger, plasma-widget-tictactoe, xbomb, xfrisk, xpilot-ng and xsok.

27 February 2012

Mark Brown: Yahoo! Groups spam

Yahoo! Groups have for a long time had big problems with allowing people to create obvious spam groups (randomly generated names, no meaningful description and so on) and then add people without any confirmation. This was annoying but at least they have an obvious abuse reporting link in the subscription mails. Sadly rather than improve the situation they appear to have just changed the link to not be a direct link to the reporting form but instead to be a generic help page. The link didn t change, the content just got even less useful. I m strongly tempted to just block all of Yahoo! from the mail systems I control.

Leandro Gómez: DebConf needs you!

The 13th Debian Conference is just around the corner. DebConf12 will be held in Managua, Nicaragua, July 8-14, 2012, and we need your help! Why should I care? DebConf is the annual conference for Debian contributors and interested users. Previous Debian Conferences have featured speakers and attendees from around the world (DebConf11 had attendees from 46 different countries). DebConf helps share the knowledge and experiences of individual developers with the entire community. It also helps promote enthusiasm for specialized areas of development and encourages discussions about Debian s future. The benefits that DebConf brings to the Debian project as a whole, and the larger Free Software community, will improve Debian and by extension will help improve GNU/Linux for everyone, whether they use Debian (or a Debian derivative), or any other distribution. How can I help? DebConf is a lot to organize and pay for. We invite you to help that this is going to be a successfull event.

23 February 2012

Jordi Mallach: alsaconf

Removing alsaconf was one of the very few rewarding moments of these ten years of taking care of ALSA in Debian. Not everyone agreed back then, and we still get some retaliation. :)
Date: Thu, 23 Feb 2012 02:59:31 +0100
From: <CENSORED>
To: jordi@debian.org
Subject: sabotage!
the removing of alsaconf without working(!) alternatives  was (AND IS!)  an
act of sabotage against millions of debian/alsa - users who needs stable
productive systems
you and all those proponents of removing this still needed alsaconf - program
will have to take the responsibility in front of an (us-) court for damages in
millions of dollars - amounts (lost man hours) all over the world
only a short while and we will have enough sponsors and witnesses around the
globe (and a very specialised, international labouring bureau of advocates) to
go to the court for prosecution.
we will not tolerate such an betray ("stable"? - do you believe, we're
fools??!!) against broad sections of the population and against the spirit of
free software!
it will be intresting to investigate, in whoms interests you've done so and
who the beneficiaries are ...
L.B.
conductor, publicist, whistleblower

Russ Allbery: Debian Policy 3.9.3.0

I've just uploaded version 3.9.3.0 of Debian Policy. The really big change in this version is the 1.0 version of the copyright format specification, but that will get a separate announcement once the www team has had a chance to put it in place on the web site. There are a bunch of other fixes, though, including some normative changes. Here's the upgrading checklist (duplicated from my announcement, but formatted a bit prettier):
2.4
New archive sections education, introspection, and metapackages added.
5.6.8
The Architecture field in *.dsc files may now contain the value any all for source packages building both architecture-independent and architecture-dependent packages.
7.1
If a dependency is restricted to particular architectures, the list of architectures must be non-empty.
9.1.1
/run is allowed as an exception to the FHS and replaces /var/run. /run/lock replaces /var/lock. The FHS requirements for the older directories apply to these directories as well. Backward compatibility links will be maintained and packages need not switch to referencing /run directly yet. Files in /run should be stored in a temporary file system.
9.1.4
New section spelling out the requirements for packages that use files in /run, /var/run, or /var/lock. This generalizes information previously only in 9.3.2.
9.5
Cron job file names must not contain "." or "+" or they will be ignored by cron. They should replace those characters with "_". If a package provides multiple cron job files in the same directory, they should each start with the package name (possibly modified as above), "-", and then some suitable suffix.
9.10
Packages using doc-base do not need to call install-docs anymore.
10.7.4
Packages that declare the same conffile may see left-over configuration files from each other even if they conflict.
11.8
The Policy rules around Motif libraries were just a special case of normal rules for non-free dependencies and were largely obsolete, so they have been removed.
12.5
debian/copyright is no longer required to list the Debian maintainers involved in the creation of the package (although note that the requirement to list copyright information is unchanged).
copyright-format
Version 1.0 of the "Machine-readable debian/copyright file" specification is included.
mime
This separate document has been retired and and its (short) contents merged into Policy section 9.7. There are no changes to the requirements.
perl
Packages may declare an interest in the <perl-major-upgrade> trigger to be notified of major upgrades of perl.
virtual
ttf-japanese- mincho,gothic have been renamed to fonts-japanese- mincho,gothic .
Please review and update your packages as necessary the next time you make an upload.

22 February 2012

Michal &#268;iha&#345;: Secure your phpMyAdmin

phpMyAdmin is quite popular software (to give some numbers let's mention 10000 downloads daily on SourceForge.net or 122685 reports in Debian's popcon) and as such is quite attractive target for various scripted attacks. If you run phpMyAdmin installation somewhere you should really make sure it is enough secured, so that these script kiddies don't get through. In past month I've looked at what kind of attacks are these guys trying and in all cases these are pretty old vulnerabilities, some of them fixed years ago. So the first thing you should do is to update. It is always good to run latest stable version, but in case you can not for whatever reason, try at least taking the most important fixes and using them. In ideal world your distribution would do this job for you, but in case it did not, you can for example take patches from Debian, which is pretty good at taking our patches (surprisingly it is not much related to my involvement there). To check which patches they have applied you can use excellent patch-tracker tool, which exposes patches from all released packages. To give you overview of which issues are mostly being attempted to exploit by script kiddies right now, here is the list: If you have fixed these, you should be pretty safe for now, but follow our security announcements for possible future issues (you can use RSS feed or subscribe to news mailing list, where all security issues are announced as well). However there are more things you can do to keep you safer: So these are the basic steps which will help you against possible compromise, I might return to some of these in more details in future posts.

Filed under: Debian English Phpmyadmin Suse 0 comments Flattr this!

19 February 2012

Richard Hartmann: RAID sucks

Intro RAID sucks, and so do all other Free alternatives in the Linux world. Having been in exactly the same situation several times in the past, I have been following Russell Coker's posts regarding data integrity with interest. FWIW, the correct answer to "BTRFS (sic) and Xen" is: subvolumes. Now that Fedora has, once again, decided to postpone their switch to Btrfs as default file system, I decided to write up my own take on this topic. Any and all my considerations are made under the assumption that important data is backed up while semi-important data is at least living on two different machines. Beware, this is a long post, but I do like to think it's well worth reading. RAID Disk failures Let's recap the current situation for "traditional" file systems like xfs, ext 2..4 , etc. In case you need to freshen up on the technical details go here. Silent corruption All the RAID levels with redundancy are fine and dandy if you lose a whole disk and put in a new one. Of course, that does not help you the tiniest bit once you get read errors. Controllers which manage RAID 1 or 10 may or may not compare the data while it's being read and may or may not tell you about discrepancies. They can then toss a coin and give you either result. There is no way to determine which is correct. RAID 2, 3, 4, 5, and 6 could, in theory, verify the data as it's being read, but that would limit your read rate to that of a single disk so no one does that. We actually had a massive web presence fail over night, once. No one knew what the cause was as there hadn't been any kind of access logged. As that particular deployment is done directly from a VCS, we simply ran a diff and found one change. We traced the failure down to a syntax error; a one character change made everything fail. Looking at the ASCII table, it was clear that one single bit had flipped. This sucked. A lot. Mitigation So you end up scrubbing your RAID sets on a weekly basis, recovering from silent corruption with the help of your RAID 6's two parity stripes. And even though you schedule the scrubbings with the least priority, you still take a performance hit when randomly seeking a lot. ZFS Some smart people at Sun set out to fix these problems and more, and fix it they did. The "Z" in ZFS is meant to imply that this is the last file system you will ever need and if not for its license, this might have worked. Of course, "last" and "forever" mean "not now" and "10 years" respectively, in computer terms. The limits within ZFS have been chosen so that the entropy needed to create a disk able to max out a ZFS volume would, literally, require our oceans to boil. Let's just say that you won't encounter these limits any time soon. While that is a nice thing to know, it does not say anything about data integrity. There are several mechanisms ensuring data integrity built in ZFS, the most fundamental being extensive checksumming. Checksums are vastly superior to live comparisions which RAID would have to perform as it does not need to sacrifice any significant i/o reading checksum data. With HDD access, you are i/o-bound, and not CPU-bound, anyway, so performing the checksum calculations is laughably cheap when factoring in the added safety. Everything, be data, metadata, inodes, you name it, is checksummed. Every read operation must go through the checksumming functions, ensuring that all data which reaches your user space is correct. If ZFS can't verify the checksum, it will not deliver any data at all, ensuring noticeable, as opposed to silent, corruption. So how does ZFS recover when the checksum does not match the data? copies= 1..3 The easy way is to store several copies of your data within your volume. Mount a ZFS volume or subvolume with copies=2 or 3 and all data that is being written from then on will be copied twice or three times. Trivial in principle, but powerful when built into a file system. RAIDz 1..3 This is where things start to get interesting. RAIDz1, 2, and 3 will allow you to lose 1, 2, or 3 disks respectively while still retaining your data; at the obvious expense of the storage capacity of as many disks. Basically, RAIDz2 is ZFS' variant of RAID 6, but it's so much better than mere RAID 6. Moo! RAIDz will not assign fixed slices and fill them up like RAID does. It will look at the current write speeds and use appropriate slice sizes dynamically. As a direct result, data which has been written at roughly the same time will always be near other data written at the same time. This is very nice for functionality like snapshots, writeable subvolumes and other things and is called COW, ZFS' variant of super cow powers. This also enables ZFS to write data, read it back and verify the checksum and only then point to the new data. Atomic commits done right. Keep rollin' As ZFS has to keep track of what data is still in use in which volumes and subvolumes anyway, it knows which regions are free to be reclaimed. Instead of filling up random places, ZFS will roll over your disks, overwriting unused data on the fly. This bears repeating: Contrary to RAID 5 and 6, ZFS will never need to read old data in order to write new data. Write performance galore and anyone still stuck on RAID 10 can finally enjoy the increased data security. Btrfs To be completely honest, I do not know Btrfs as well as I know ZFS. If I get anything wrong, correct me. If I offend anyone with my outsider's interpretation, that is not my intention. Btrfs has been initiated by Oracle way before it ever even thought about buying Sun or history might have run a different course, for worse or a lot worse. The closing of Java, Solaris, ZFS, Hudson, OpenOffice (since then "gifted" aka thrown away), and others makes me think the latter. As there are few technological developments which caused me as much stress, overtime and pain as OCFS2, I am naturally wary of file systems sponsored by Oracle and their data focus integrity/availability. The fact that there's still no way to fsck a Btrfs volume could be birthing pain or yet another facet of Oracle's stance on this topic, I honestly don't know. Either way, it's a good idea to be wary for now. I can't say too much on Btrfs' technical underpinnings, but I know it uses COW and that it has its own variant of RAID. Toss in snapshots (writeable?), subvolumes and integrated block device management, and you have the building blocks of a decent file system. Still, Btrfs is not ready for prime time. Btrfs has been "one or two years in the future" for a few years now so I will not be holding my breath. And once the first distributions are starting to use Btrfs by default, people will lose data. A year or three after that, I will feel comfortable to use it myself and in production. Commercial solutions You can either hand a lot of money to proprietary vendors who will not tell you a thing about how things work internally (and no way to fix things directly) or you can buy solutions that employ ZFS in the back-end. I prefer my storage hardware to be relatively dumb while keeping the intelligent bits where I can see and poke them so this is not really part of these considerations. So what can you do? Test your disks before deploying them Easy, but vitally important:
disk=/dev/foo
smartctl -a $disk
smartctl -t long $disk
badblocks -swo $vendor_$model_$serial_$timestamp.badblocks.swo $disk
smartctl -a $disk

If you are lazy, get a copy of disktest, a tool I wrote to do exactly this. It should wait for the long self-test to finish, can not read out all vendor names, and does not have a way to document who ran the test, but it's a start. Patches and feedback are, obviously, welcome. And yes, I will package this soonish. Using your disks This list is surprisingly short. You can use And that's it. At work, I prefer small RAID 6 volume sets. It sucks, but there is nothing better. For personal use, I have a machine with a FUSE-based RAIDz2 mounted with copies=2. Three disks can fail and my data is still secure. While this setup is slow as molasses due to FUSE, speed is not a consideration for me here; data safety is. A migration to Debian/kFreeBSD in the medium term is still likely. If you have things to add or disagree with me, I would love to hear from you. Update: Jan Christian Kaessens pointed out that, contrary to my experience, zfsonlinux did not bring down his sytem in flames. As zfsonlinux is a kernel module, potential performance is a lot better. Also, it supports ZFS Pool Version 28 as opposed to FUSE-ZFS' 23. While the really nice features are in v 29 and 30 (which are closed thanks to Oracle) v 28 still has some nice changes.

Russ Allbery: Debian, licenses, and license-count

A few people have been using the license-count tool that I wrote to analyze the breakdown of licenses in Debian and draw some conclusions. Unfortunately, some of those conclusions can't be drawn from the output of this specific tool (which doesn't make them wrong, just unproven). So here are a few cautions. license-count was written for a specific purpose: to see how many references there are to a particular license in Debian so that we had some facts behind our discussion of whether to include it in common-licenses. It was not written to classify packages into particular categories, only to find out how many copies of a license we could save by adding it to common-licenses. This means that using it to determine how much software in Debian is covered by a particular license fails in the following ways:
  1. license-count numbers cannot be added. Since the goal is to find every reference to a given license, each package is not classified as under one and only one license. If a package has material under the GPL, the LGPL, and the GFDL, it will add one to each of those counts. This means that you cannot determine, from its output, questions like "how many packages are covered under one of the GPL family of licenses?" You will double- or treble-count packages when you add the numbers together.
  2. license-count counts any reference, not just "important" ones. If the license is referenced in debian/copyright, that counts, since the goal is to see how many packages might benefit from being able to reference it in common-licenses. This may not be the license that the package is under, just some small portion of the package. For example, all of my packages that use Autotools add to the GPL count because I include all the source code licensing statements, including the statements for libtool and the Automake helper scripts, which say that the files can be released under either the GPL or the license of the including package. These packages are generally under a BSD-style license (or in some cases the Apache 2.0 license), not under the GPL, but since the reproduced license text has a reference to the GPL, license-count adds one to the GPL column for each of those binary packages. For most purposes for counting GPL-covered software, these are false positives. I don't know how many people are as complete in documenting license statements as I am, but just the binary packages that I maintain probably count for at least 50 false positives because of this alone.
  3. license-count numbers include dual-licensing. Whether this matters for your analysis or not depends on what question you're asking, of course. If you're asking whether the package is covered under a copyleft license, including the thousands of packages that are dual-licensed under the Artistic license and the GPL may be okay, since the Artistic license is a sort of copyleft (although it allows you to avoid the copyleft requirement by renaming executables, providing the originals, and documenting your changes). But, for example, one of my packages is dual-licensed under a BSD-style license and the GPL (for reasons that aren't worth getting into). This package is not covered by copyleft under any reasonable definition of the term, but license-count will count it as a package using the GPL.
In order to draw interesting conclusions like "how much software in Debian is protected by copyleft," I'm afraid that you'd have to write a much more sophisticated tool than license-count.

18 February 2012

Biella Coleman: Montreal, first impressions

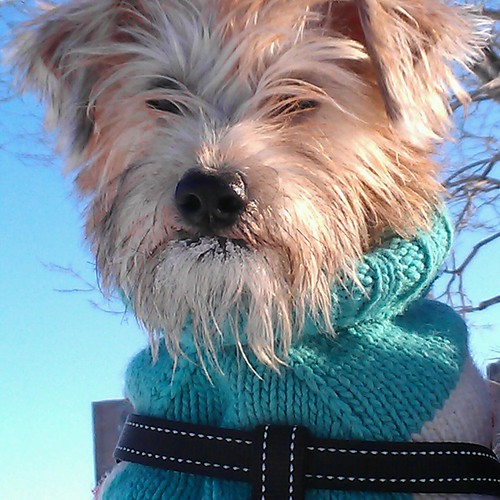
frozenlights When I told people of my plans to move to Montreal, it usually prompted one of two reactions: one was some version of joyful envy, many people exclaiming breathlessly Montreal is one of my favorite cities, one person once even clutching my arm and told me as he looked me straight in the eye: you are so lucky, there is no city quite like Montreal in North America. The second reaction came off as a thinly veiled mixture of disdain and disbelief usually peppered with many reallys: oh wow, really, really you would really leave NYC? I am pretty certain they really were thinking something along the lines of what a fool, how dare she leave a great job, a great university, a world class city (the only city to live) for some Canadian mid-sized city, which is like tundra for a good chunk of the year? The decision to move weighed heavily on me, if for no other reason I had a choice to stay or to go and I honestly have not had a choice, a decision to make about where to go since I got accepted to graduate school (and even then the choice was more obvious than this one). So over a month into my move what is my verdict? In a word, win. I don t miss NYC at all though I get why some people cannot leave the place and know that despite some oddities and difficulties of living in Montreal, it fits my tastes and needs much better than NYC which dwarfed me in so many ways. I never felt I could enjoy it, I grew tired of the cramped living quarters, the noise ate at my soul, and I simply felt more overwhelmed by the fact that I could not even get a handle on the neighborhoods in my vicinity, much less all the other hoods in the area. Instead of dogging NYC anymore, I think I will spend a little time on first impressions, as they will soon be lost to the familiarity borne with time and experience. In essence Montreal is chock full of life but rather intimate, a quirky city with lots of charm but some grit and lacking the way over designed and done feel of cities like Portland. Here are some of quirks: 1. The Hawt Metro: I fell in love with the Metro when I first rode it a few years ago. I just love the powder blue color of the cars and the super sweet 1960s aesthetic of many stations. Even better and unlike NYC, they are just clean and quiet. The downside? The temperatures approximates a sauna during the winter and while you would think this is a good thing, when you are layered with the clothing necessary to survive outside (re: long underwear along with Canada-coat, gloves, hat, and scarf), it is hooooooot down there and you feel like you need to pass out. 2. Spend money, get free stuff: In many establishments you get free stuff (like blueberries or some like sports bar) when you spend over a certain amount of money, like 70 bucks. Quirky local tradition. 3. The culture of negotiation and the kick ass standard lease: Housing is amazing here. There is plenty of it, there are many different styles, and it is rather fun exploring all the different hoods that make up the city. Problem is too that lots of apartments have weird problems and issues and I had to steer clear of anything that could even possibly have mold. I spent weeks day in day out looking for a place, desperate to move out of my corporate apartment very nicely provided by the university but still not my ideal living situation. Finally found a place that fit all my needs in the perfect location and I took it to only find out that places are priced to negotiate and I was faced with the decision to negotiate or not. Sort of did, was not thrilled about it (thinking that I might lose the place) but it sort of worked and I scored the place. If price is up to haggling, the lease on the other hand, is standard (you can buy one at your local bodega ). It is the law to use it and it is like a no nonsense, straightforward lease, which is very protective of renters. 4. Montreal is known for its exceptional food but you know Poutine is just plain gross: Food here is good and I can tell that I will get a handle of restaurants in a way that felt impossible in NYC. The gluten free religion seems to be spreading, thankfully. There are many little Fruiterias! to get your fruits veggies which I am still exploring and right around my house is a crazy supermarket that is so cheap, which is weird because consumer goods generally ain t cheap in Montreal like they are in the states but this place is a gem and everyone agrees (and almost impossible to notice from the street!). Now Poutine is disgusting. Ok it did not help that the first night I went out to eat it, I was still under the clutches of Noro virus, and I think it re-activated the nausea that had been zapped by some strong medicine and the hospital, the day before, which brings me to the next point, the health care system. 5. Healthcare, I had to use it way too early: So last week I came down with the Noro virus and you usually wait it out as it runs through you quickly but I was dehydrated before I even started to vomit to for 8 hours straight, at which point severely tired and so nauseous (I was yelling to make it stop), I went to the hospital. Now I had talked to lot of people about the healthcare system in Montreal as it seems good, really great but a bit over taxed, especially compared to where I had lived in Edmonton where it was like a magic fairy tale dream. I had heard of two things: the care is excellent but the facilities are shocking and the wait times unless dire can be atrociously long. So facilities, yea they are kinda shocking, somewhat shabby but who cares, so long as the care is good, no? Packaging is irrelevant so long as the goods are derived. Before going I was scared of the long wait times (and also the taxi took me by mistake to Montreal General Hospital was looked too much like a HUGE version of the creepy buildings in The Shining for me, and I was supposed to go to Jewish General so left for there). The wait time: nearly none, somewhat as shocking as the facilities first looked to me. I think it was a combination of the time I arrived, with the fact that my lounge was parched and yellowish-gross (sorry, it was gross), indicating I was dehydrated, oh and I was crying bit hysterically, for despite my high threshold for pain, nausea terrorizes me. I was covered by insurance and since I did not yet have my McGill health cards (it takes three months to qualify for the local stuff), I did pay and the price was laughably cheap compared to what I would pay in NYC for the same treatment. 6. Now for my favorite, snow so nice, ice oh Christ: Well this winter has been, by all accounts, weak and warm, the spirit of winter barely making its way from the underworld to the outerworld. But even though it is has been more idle than full throttle, I still got a pretty accurate taste of what winter is like, with a few days of 20- c temps, and having to walk a number of times on a layer of frozen ice that makes it feel like a very dangerous mini-ice age in the making. IMAG0028-1 I do rather love the quiet snow falling and just love love sprinting through the snow with my dog, Roscoe, who has taken a liking for prancing in the white stuff and looks awful cute with his winter man s ice beard. After a sizable snowfall, it is clear they city does not toy with the snow removal although the sidewalk snow plows do look somewhat like very large and dangerous but kinda cute toys. But let s be frank, winters are hard, so hard that I think I would go mad if I had to stay through the entire thing, being born and raised in the tropics So the fact that I am writing this from the southern hemisphere in the height of summer gives me the assurance I can handle the rest of the snow, ice, ice and snow upon my return.

Stefano Zacchiroli: GPL-d Debian software skew (?)

At FOSDEM, John Sullivan delivered an interesting talk titled Is copyleft being framed? to verify alleged claims on the decline of GPL-d software. (Slides are available.) The crux of the talk is the analysis he performed on the Debian archive to discover the amount of software we distribute that is covered by GPL, LGPL, or AGPL ("GPL-d" for short in the remainder). John's talk steps in an interesting and long running debate (a recent summary of which is available in this ITWire article). The most interesting part is the discrepancy among John's results and Blackduck's, which are often used to argue how the popularity of the GPL license is declining. That might be the case. Or not. The more analyses we do to find it out, the better. The underlying assumption on John's work is that Debian is a representative sample of the Free Software out there, which I think is a reasonable assumption. I find the analysis presented in the talk completely satisfactorily from a purely scientific point of view. The same cannot be said about Blackduck's result: both their methods and data are secret, making it impossible to reproduce their experiments. Highly unscientific. Still, John's results are surprising: as much as 87 percent of Lenny's packages and 93 percent of Squeeze's are GPL-d. That seems a lot. Puzzled about that, John discussed with me the issue before his talk, in search for pitfalls in his methods or data. Finding none, I pointed him to the almighty DktrKranz for some extra review; who found nothing either. To stay on the safe side, even during his talk John called for independent reviews of his results. What could be wrong? The tool used to gather the data is license-count from the debian-policy package. Input data are the debian/copyright files of all Debian source packages. If license-count is not bugged, our debian/copyright files might be. One thing that occurred to me only a few days ago is the habit of declaring a different license for Debian packaging (the files under debian/) than the software being packaged itself. That's a bad habit because it might cause unwanted license mixtures via patches that live under debian/ but I've seen several occurrences of it in the Debian archive. For name and (self-)shame: I've also been guilty of it in the past, when I was young . Is that reason enough to skew results and overestimate GPL-d software? I don't think so, I hope not, but ultimately I don't know. It'd be nice to rule out the possibility entirely. So if anyone is willing to do some sampling of affected debian/copyright files and propose patches for license-count to exclude those "false positives", please shout. (As a bonus point: that would also help to take more sound decision for the typical use case of license-count, i.e. deciding when a license should be added to /usr/share/common-licenses.) Other independent reviews of the results are equally welcome. Note: the above, as well as John's analysis, would be a trivial exercise if DEP-5 were already widely deployed in the Debian archive.
Update: add link to John's slides
Update 19/02/2012: Russ Allbery, author of license-count, posted a way more likely cause of data skew in John's analysis: double counting among the different types of copyleft licenses

Andrea Veri: Nagios XMPP Notifications for GTalk

While improving GNOME s servers Nagios Notifications, I ended up working on a nice way to notify the relevant folks through GTalk in case something could go wrong on any of the hosted services. Looking around on the web, I found Seth Vidal s script, modified it to suit my needs and made it working with GTalk, here s the result:
#!/usr/bin/python -tt
import warnings
warnings.simplefilter("ignore")
import xmpp
from xmpp.protocol import Message
from optparse import OptionParser
import ConfigParser
import sys
import os
parser = OptionParser()
opts, args = parser.parse_args()
if len(args) < 1:
    print "xmppsend message [to whom, multiple args]"
    sys.exit(1)
msg = args[0]
msg = msg.replace('\\n', '\n')
# Connect to the server
c  =  xmpp.Client('gmail.com')
c.connect( ( 'talk.google.com', 5223 ) )
# Authenticate to the server
jid  =  xmpp.protocol.JID( 'example@gmail.com' )
c.auth( jid.getNode( ), 'yourgmailpassword' )
if len(args) < 2:
    r = c.getRoster()
    for user in r.keys():
        if user == username:
            continue
        c.send(Message(user, '%s' % msg))
else:
    for user in args[1:]:
        c.send(Message(user, '%s' % msg))
I, then, added the command definitions on the relevant Nagios configuration file:
define command 
        command_name    host-notify-by-xmpp
        command_line    /home/user/bin/xmppsend "Host '$HOSTALIAS$' is $HOSTSTATE$ - Info : $HOSTOUTPUT$" $CONTACTPAGER$
         
define command 
        command_name    notify-by-xmpp
        command_line    /home/user/bin/xmppsend "$NOTIFICATIONTYPE$ $HOSTNAME$ $SERVICEDESC$ $SERVICESTATE$ $SERVICEOUTPUT$ $LONGDATETIME$" $CONTACTPAGER$
         
And in the end on contacts.cfg:
define contact  
        contact_name    admin
        use             generic-contact
        alias           Full Name
        email           example@gmail.com
        pager           example@gmail.com
        service_notification_commands   notify-by-xmpp
        host_notification_commands      host-notify-by-xmpp
 
When done just reload the configuration files with:
sudo /etc/init.d/nagios3 reload
Enjoy your new XMPP Nagios notifications! Update: if you don t want the script to store your username or password, you can use the following modified script together with a nice config file like this one:
[xmpp_nagios]
username=example@gmail.com
password=yourgmailpassword
Then you can invoke xmppsend this way:
xmppsend -a config.ini

Mike Hommey: How to waste a lot of space without knowing

const char *foo = "foo";
This was recently mentioned on bugzilla, and the problem is usually underestimated, so I thought I would give some details about what is wrong with the code above. The first common mistake here is to believe foo is a constant. It is a pointer to a constant. In practical ELF terms, this means the pointer lives in the .data section, and the string constant in .rodata. The following code defines a constant pointer to a constant:
const char * const foo = "foo";
The above code will put both the pointer and the string constant in .rodata. But keeping a constant pointer to a constant string is pointless. In the above examples, the string itself is 4 bytes (3 characters and a zero termination). On 32-bits architectures, a pointer is 4 bytes, so storing the pointer and the string takes 8 bytes. A 100% overhead. On 64-bits architectures, a pointer is 8 bytes, putting the total weight at 12 bytes, a 200% overhead. The overhead is always the same size, though, so the longer the string, the smaller the overhead, relatively to the string size. But there is another, not well known, hidden overhead: relocations. When loading a library in memory, its base address varies depending on how many other libraries were loaded beforehand, or depending on the use of address space layout randomization (ASLR). This also applies to programs built as position independent executables (PIE). For pointers embedded in the library or program image to point to the appropriate place, they need to be adjusted to the base address where the program or library is loaded. This process is called relocation. The relocation process requires information which is stored in .rel.* or .rela.* ELF sections. Each pointer needs one relocation. The relocation overhead varies depending on the relocation type and the architecture. REL relocations use 2 words, and RELA relocations use 3 words, where a word is 4 bytes on 32-bits architectures and 8 bytes on 64-bits architectures. On x86 and ARM, to mention the most popular 32-bits architectures nowadays, REL relocations are used, which makes a relocation weigh 8 bytes. This puts the pointer overhead for our example string to 12 bytes, or 300% of the string size. On x86-64, RELA relocations are used, making a relocation weigh 24 bytes! This puts the pointer overhead for our example string to 32 bytes, or 800% of the string size! Another hidden cost of using a pointer to a constant is that every time it is used in the code, there will be pointer dereference. A function as simple as
int bar() return foo;
weighs one instruction more when foo is defined const char *. On x86, that instruction weighs 2 bytes. On x86-64, 3 bytes. On ARM, 4 bytes (or 2 in Thumb). That weight can vary depending on the additional instructions required, but you get the idea: using a pointer to a constant also adds overhead to the code, both in time and space. Also, if the string is defined as a constant instead of being used as a literal in the code, chances are it s used several times, multiplying the number of such instructions. Update: Note that in the case of const char * const, the compiler will optimize these instruction and avoid reading the pointer, since it s never going to change. The symbol for foo is also exported, making it available from other libraries or programs, which might not be required, but also adds its own overhead: an entry in the symbols table (5 words), an entry in the string table for the symbol name (strlen("foo") + 1) and an entry in the symbols hash chain table (4 bytes if only one type of hash table (sysv or GNU) is present, 8 if both are present), and possibly an entry in the symbols hash bucket table, depending on the other exported symbols (4 or 8 bytes, as chain table). It can also affect the size of the bloom filter table in the GNU symbol hash table. So here we are, with a seemingly tiny 3 character string possibly taking 64 bytes or more! Now imagine what happens when you have an array of such tiny strings. This also doesn t only apply to strings, it applies to any kind of global pointer to constants. In conclusion, using a definition like
const char *foo = "foo";
is almost never what you want. Instead, you want to use one of the following forms:

15 February 2012

Russell Coker: Links February 2012

Sociological Images has an interesting article about the attempts to apply the word Camping to OWS and framing the issues [1]. Lester Macgurdy wrote an insightful article about the snake , a new technique for OWS protesters to beat riot police [2]. Ron Barassi suggests that Australia Day be celebrated on the 27th of May to commemorate the day in 1967 when the Australian constitution was amended to not be racist [3]. The current Australia Day is often referred to as Invasion Day . IMHO Ron deserves another Best and Fairest award. Stefon Harris gave an entertaining TED talk about improv Jazz music titled There Are No Mistakes on the Bandstand [4]. It seems that his concepts can apply to some extent to many collaborative projects. John Robb wrote an interesting article about the future of drone (UAV) warfare [5]. He suggests that having one person control each drone is a temporary thing and that the future is to have a cloud of cheap autonomous drones taking strategic control from one person. His comparison of Starcraft players to future drone fighters is interesting. The OWS movement is branching out into other related areas, OccupyYourHomes.org is one of the latest ones [6]. When banks try to forclose on homes without good cause the OWS people are protesting. Cory Doctorow wrote an important article for The Guardian about corporations using the Youtube ContentID system to pirate works that other people have uploaded [7]. Matt Taibbi s description of Goldman Sachs as a great vampire squid wrapped around the face of humanity, relentlessly jamming its blood funnel into anything that smells like money will never die [8]. It has spawned many other creative descriptions of the evil and greed of Goldman Sachs and even Lloyd Blankfein of Goldman Sachs describes his company as having burned down the Reichstag, shot the Archduke Ferdinand and fired on Fort Sumter he was trying to use satire, but I don t think that Goldman Sachs people would act differently to Fritz Thyssen. Keith Packard wrote an interesting article about the Calypso CalDAV system which he uses with Android [9]. He makes lots of good points about how to improve calendaring and contacts on Android, unfortunately I lack time to fiddle with such things at the moment so I ll stick with Google in spite of the risks. Asheesh Laroia wrote a great article about the problems with short (32bit) GPG keys [10]. It seems that creating keys with matching ID numbers isn t particularly difficult and that GPG doesn t handle them as well as we would like giving the possibility of at best annoying DoS attacks and at worse security problems due to using the wrong key. Sociological Images has an interesting article about when game show audiences are trustworthy [11]. It seems that French people don t want an undeserving person to win so they will intentionally advocate the wrong answer if the contestant should know it. Paul Wayper gave a great lecture titled SE Linux for Everyone [12]. He covers the basics of SE Linux in a user-friendly way and explains some simple solutions to common problems which don t involve compromising system security. Paul Tassi wrote an insightful article for Forbes about piracy [13]. His conclusion is that the media companies should make it cheaper and easier to be a customer and not spend insane amounts of money on low quality products. The Reid Report has an interesting article about Ron Paul s racism [14]. Ron Paul is generally well regarded outside the US because he wants the US government to stop meddling in the affairs of other countries, but while he s less bad than other US politicians in terms of foreign policy that doesn t make him a good person. Anonymous hacked some mailboxes belonging to a neo-Nazi group and found links to Ron Paul [15]. I ve always been suspicious of the way Ron Paul wanted to avoid anti-racism legislation on supposed Libertarian principles. The Reid Report has an interesting summary of Ron Paul news plus some criticism of Glenn Greenwald and others who associate with him [16]. Related posts:
  1. Links February 2011 Australia s Department of Finance has mandated that the MS-Office document...
  2. Links January 2012 Cops in Tennessee routinely steal cash from citizens [1]. They...
  3. Links February 2009 Michael Anissimov writes about the theft of computers from the...

Joachim Breitner: Including full LaTeX documents in another LaTeX document

Assume the following situation: You set problem sheets for a class, and at the end of the semester, you have 13 individual LaTeX files, including the preamble (the stuff from \documentclass to \begin document ). Now you want to provide a file that contains all problems, followed by all problems with solutions. You could just concatenate the resulting PDFs, but that would waste quite a bit of paper, as most problem sheets do not fill the whole page. You could just copy n paste the LaTeX code, but that is not neat either. So you want to include the 13 individual documents in one LaTeX document. LaTeX provides \include and \input commands, but these would require that the content of the individual files, i.e. the stuff between \begin document and \end document , is put in a file of its own. You cannot just \input the full problem sheet document, as there must be only one \documentclass command, and a few preamble commands are invalid within the document. There are various solutions suggested, e.g. on Wikibooks and StackOverflow, and there are packages helping with that functionality, such as combine or subfiles. I chose a rather rough, hands-on solution that worked great in my case: The idea is to simply re-define all commands that you have in your preamble to do nothing, including the document environment, before including the other files and constraint to a group. In my case, the preambles were relatively small, as the common definitions of the problem sheets were in a file of their own. I am also using the \foreach command provided by the TikZ package for a convenient loop over all problem sheets:
\foreach \x in  0,...,13   
   
    \excludecomment solution 
    
    \DeclareDocumentCommand \documentclass om 
    \DeclareDocumentCommand \usepackage om 
    \newcommand \Blattnummer [1] 
    \DeclareDocumentCommand \FirstDueDate mmm 
    \DeclareDocumentCommand \ThisDueDate mmm 
    \newcommand \SkippedWeeks [1] 
    \renewenvironment document 
    \section* Problem Sheet \x 
    \setcounter problem 0 
    \input GraphTheoryProblems\x 
   
 
\clearpage
\label sols 
\foreach \x in  0,...,13   
   
    \newenvironment solution 
      \par\addvspace 1em 
     
     
    \DeclareDocumentCommand \documentclass om 
    \DeclareDocumentCommand \usepackage om 
    \newcommand \Blattnummer [1] 
    \DeclareDocumentCommand \FirstDueDate mmm 
    \DeclareDocumentCommand \ThisDueDate mmm 
    \newcommand \SkippedWeeks [1] 
    \renewenvironment document 
    \section* Solution Sheet \x 
    \setcounter problem 0 
    \input GraphTheoryProblems\x 
   
 
To redefine commands taking optional arguments, using the xparse package is convenient. You can see how I include every file twice, first with the solution environment turned into a comment and then again with the solution environment actually showing its content. I create a section header based on the counter of the foreach loop, but I could have easily redefined \title and use that for a header, if my problem sheets had used that command (They don t, as they calculate the problem sheet number and the due date based on the number in the filename very convenient, and maybe worth a blog post of its own). The problem counter is reset for each file, so that the problems are numbered individually. I could have left this out, then the problems would be numbered consecutively across all included problem sheets. The individual and resulting files can be found on the Graph Theory course website.
Flattr this post

13 February 2012

Petter Reinholdtsen: Automatic proxy configuration with Debian Edu / Skolelinux

New in the Squeeze version of Debian Edu / Skolelinux is the ability for clients to automatically configure their proxy settings based on their environment. We want all systems on the client to use the WPAD based proxy definition fetched from http://wpad/wpad.dat, to allow sites to control the proxy setting from a central place and make sure clients do not have hard coded proxy settings. The schools can change the global proxy setting by editing tjener:/etc/debian-edu/www/wpad.dat and the change propagate to all Debian Edu clients in the network. The problem is that some systems do not understand the WPAD system. In other words, how do one get from a WPAD file like this (this is a simple one, they can run arbitrary code):
function FindProxyForURL(url, host)
 
   if (!isResolvable(host)  
       isPlainHostName(host)  
       dnsDomainIs(host, ".intern"))
      return "DIRECT";
   else
      return "PROXY webcache:3128; DIRECT";
 
to a proxy setting in the process environment looking like this:
http_proxy=http://webcache:3128/
ftp_proxy=http://webcache:3128/
To do this conversion I developed a perl script that will execute the javascript fragment in the WPAD file and return the proxy that would be used for http://www.debian.org/, and insert this extracted proxy URL in /etc/environment and /etc/apt/apt.conf. The perl script wpad-extract work just fine in Squeeze, but in Wheezy the library it need to run the javascript code is no longer able to build because the C library it depended on is now a C++ library. I hope someone find a solution to that problem before Wheezy is frozen. An alternative would be for us to rewrite wpad-extract to use some other javascript library currently working in Wheezy, but no known alternative is known at the moment. This automatic proxy system allow the roaming workstation (aka laptop) setup in Debian Edu/Squeeze to use the proxy when the laptop is connected to the backbone network in a Debian Edu setup, and to automatically use any proxy present and announced using the WPAD feature when it is connected to other networks. And if no proxy is announced, direct connections will be used instead. Silently using a proxy announced on the network might be a privacy or security problem. But those controlling DHCP and DNS on a network could just as easily set up a transparent proxy, and force all HTTP and FTP connections to use a proxy anyway, so I consider that distinction to be academic. If you are afraid of using the wrong proxy, you should avoid connecting to the network in question in the first place. In Debian Edu, the proxy setup is updated using dhcp and ifupdown hooks, to make sure the configuration is updated every time the network setup changes. The WPAD system is documented in a IETF draft and a Wikipedia page for those that want to learn more.

Gunnar Wolf: Mexico City Metro project

Some days ago, reading my local Couchsurfing groups, I stumbled across an announcement by Australian Peter Davies to go to each of the 148 stations in the Mexico City Metro system, take some photos of the environment, and document on his impressions. I have followed and enjoyed the Mexico City Metro blog since I learnt of it, and have grown used to looking forward to the daily post-or-two. Peter writes each of his entries both in English and Spanish (you can tell it's not a native Spanish, but it's a good effort). He has been doing the stations in a very well distributed order (I cannot say it's completely random, but it's surely not lineal or methodical). I connected wiht his project as I love discovering the city more or less the same way, but with a different system: I try to have at least one long bike ride every two weeks (being "long" something over 40Km). I usually go either to the North or to downtown and to the East by the good old route I always take, and on my way back, at some point I decide just to turn right or left and discover yet another village slurped by the city. I don't usually take pictures, as I'm too much into the cycling thrill, left-right-left-right... But cycling has led me to appropriate my city (I don't know if that's proper English), to make my city really mine, to get to know parts of it I'd never otherwise go to. Anyway, Peter's is a great way to document urban life. I'm in love with my city, and with expressions of urban appropriation. I loved his project, and if you are interested by what I say, go take a look at his wanderings in the city. I have suggested him two bits to check, but the work is very much an artist's He accepts my input, but quite probably he will do whatever he pleases ;-) In case any of you is interested in contacting him, I can tell you for a fact he replies :-) [*] And what is CouchSurfing? Oh, a great community where you can offer a space to crash at your house for unknown people from all around the world. I have never requested a couch, as the Free Software community is much more tightly knit, but I have offered it to several interesting people.

Next.

Previous.