Search Results: "spa"

22 September 2012

Jonas Smedegaard: Muziik!

Hi there! I'm sittin' here listening to Rickie Lee Jones. Just bought the CD today :-) Simply wanted you to know, that's all! Best regards
Jonas Smedegaard BTW Welcome aboard this pseudo-list (actually I'm doin' it directly from my e-mail client!) If you don't know who I am, or why you got this letter, then please contact me - there might be an error somewhere (and we might get to know each other ;-) I'm just an ordinary guy with an ordinary mail program, not a spammer
This text is part of my friends scriblings.

21 September 2012

Philipp Kern: IPv6 support in debian-installer, take 2

The IPv6 patch set for netcfg (part of debian-installer) has landed in Debian unstable. In follow-up uploads I diverged from the Ubuntu patch set a little bit:
Thanks to Michael Tokarev's recent upload of busybox, we now also have a more featureful ping and ping6 in debian-installer's environment.

Known bugs:
If you could take another look at a current d-i daily, install a system with it and look if the installed system has a correct network configuration, that would still be appreciated. I also need somebody to test the GNU/kFreeBSD image. I fixed it up to build there but the result might be entirely wrong.

My sincere thanks go to Bernhard Schmidt and Karsten Merker, who successfully completed installations over IPv6 in various environments!

19 September 2012

Stefano Zacchiroli: bits from the DPL for August 2012

DPL August report, posted on d-d-a a while ago (yep, I forgot to blog it up to now!, sorry for the oldies).
Dear project members, August has been a month with a good deal of vacations for many of us, including yours truly. Therefore the monthly report of DPL activities will be briefer than usual. Which is good, as it'll leave all my readers more time to do NMUs and fix RC bugs! Ongoing discussions Assets Core teams Legal and RC fun Hardware See? It's been quick(er)! Talk to you here next month, with a much lower count of Wheezy RC Bugs on the horizon, hopefully.
Cheers.
PS the boring day-to-day activity log for August 2012 is available at master:/srv/leader/news/bits-from-the-DPL.txt.201208

18 September 2012

Dirk Eddelbuettel: RcppArmadillo 0.3.4.1

Conrad released the bug-fix release 3.4.1 of Armadillo earlier today, and the corresponding RcppArmadillo package 0.3.4.1 is already on CRAN. No R level or interface changes were, the upstream changes are summarized below.
Changes in RcppArmadillo version 0.3.4.1 (2012-09-18)
  • Upgraded to Armadillo release 3.4.1
    • workaround for a bug in the Mac OS X accelerate framework
    • fixes for handling empty sparse matrices
    • added documentation for saving & loading matrices in HDF5 format
    • faster dot() and cdot() for complex numbers
Courtesy of CRANberries, there is also a diffstat report for 0.3.4.1 relative to 0.3.4.0 As always, more detailed information is on the RcppArmadillo page. Questions, comments etc should go to the rcpp-devel mailing list off the R-Forge page.

Evgeni Golov: sorry for the spam

This especially goes to planet.debian.org: SORRY! My WordPress thought it is a great idea to deliver empty (no date, no link, no content) posts, randomly, and planet started to post everything as new as it took the feed. I still haven t reenabled all the plugins, but it runs stable for several hours now and I ll try not to break it again.

Patrick Matth i: Playing with Apache mod_geoip

If you want to add some rules to your Apache based on the clients country, mod_geoip is perfect for it. Installation On Squeeze following is enough: # apt-get install libapache2-mod-geoip geoip-database/squeeze-backports Note that you should use the geoip-database version from squeeze-backports to have got the most up to date database version, I am updating it every month. Configuration You can add the rules to your VirtualHost, Directory, Location directives and also to your apache2.conf ( serverwide ). So you are flexible with where to use it. Blocking countries On some servers I have got more than 90 percent of spam requests only from three countries, so I blocked them with: <DirectoryMatch ^/var/www/.*/html >
SetEnvIf GEOIP_COUNTRY_CODE RU BlockCountry
SetEnvIf GEOIP_COUNTRY_CODE CN BlockCountry
SetEnvIf GEOIP_COUNTRY_CODE UA BlockCountry
Deny from env=BlockCountry
</DirectoryMatch> Allow only specific countries In the other way you also can allow specific countries to have got access to your website, this also may be a good idea for extranets, where you know from where your customers are: <Directory /var/www/my.site.com/html/login >
SetEnvIf GEOIP_COUNTRY_CODE DE AllowCountry
SetEnvIf GEOIP_COUNTRY_CODE CH AllowCountry
Deny from all
Allow from env=AllowCountry
</Directory> Very easy! Rewrite Rules You can also use it for mod_rewrite. Within a project, customers from CN and TW should be redirected to the chinese page: RewriteCond % ENV:GEOIP_COUNTRY_CODE ^(CN TW)$
RewriteRule ^(.*)$ http://some.example.cn/site.php [L] mod_geoip with proxy frontends Normaly mod_geoip works behinds load balancers and proxy servers, since it also take care of the HTTP_X_FORWARDED_FOR header. But with haproxy it looks problematic, since it does not add the HTTP_X_FORWARDED_FOR header to KeepAlive d requests :( Disabling KeepAlive is a bad idea on this cluster, so we decided to also use php5-geoip in our application, so everything is working nice now.. What mod_geoip is NOT is mod_geoip helps you to block/allow specific countries, but it does not protect you from them.
Also keep in mind that the database is only ~ 99,8% accurate, so you may have got false positives/negatives. If you only allow german users, a german IP could be listed as russian.
This is much more problematic with mobile/satellite connections and surely you can also not access your page, if you are on vacation in another country. ;)

17 September 2012

M nica Ram rez Arceda: Debconf12: Debian QA, una puerta de entrada al proyecto Debian

I wanted to write this post a lot of days ago, but it's better late than never :-) Last July, I had the pleasure to be at Debconf12, in Managua. On Debian Day, I gave a talk about getting involved in Debian through Debian QA Team. I hope everybody who was there enjoyed the talk! The talk was in Spanish and here you have all the produced material (slides and video): Talk: Debian QA, una puerta de entrada al proyecto Debian.

Andrea Veri: Building Debian packages with Deb-o-Matic

Today I ll be telling you about an interesting way to build your Debian packages using Deb-o-Matic, a tool developed and maintained by Luca Falavigna. Some more details about this tool from the package s description:
Deb-o-Matic is an easy to use build machine for Debian source packages based on pbuilder, written in Python. It provides a simple tool to automate build of source packages with limited user interaction and a simple configuration. It has some useful features such as automatic update of pbuilder, automatic scan and selection of source packages to build and modules support.
The setup. 1. Download the package.
apt-get install debomatic
2. Modify the main configuration file as follows:
[default]
builder: pbuilder
packagedir: /home/john/debomatic # Take note of the following path since we'll need it for later use.
configdir: /etc/debomatic/distributions
pbuilderhooks: /usr/share/debomatic/pbuilderhooks
maxbuilds: 3 # The number of builds you can perform at the same time.
inotify: 1
sleep: 60 # The sleep time between one build and another.
logfile: /var/log/debomatic.log
[gpg]
gpg: 0 # Change to 1 if you want Deb-O-Matic to check the GPG signature of the uploaded packages.
keyring: /etc/debomatic/debomatic.gpg # Add the GPG Keys you want Deb-O-Matic to accept in this keyring.
[modules]
modules: 1 # A list of all the available modules will follow right after.
modulespath: /usr/share/debomatic/modules
[runtime]
alwaysupdate: unstable experimental precise
distblacklist:
modulesblacklist: Lintian Mailer
mapper:  'sid': 'unstable',
'wheezy': 'testing',
'squeeze': 'stable' 
[lintian]
lintopts: -i -I -E --pedantic # Run Lintian in Pedantic mode.
[mailer] # You need an SMTP server running on your machine for the mailer to work. You can have a look at the 'Ssmtp' daemon which is a one-minute-setup MTA, check an example over here.
fromaddr: debomatic@localhost
smtphost: localhost
smtpport: 25
authrequired: 0
smtpuser: user
smtppass: pass
success: /etc/debomatic/mailer/build_success.mail-template # Update the build success or failure mails as you wish by modifying the relevant files.
failure: /etc/debomatic/mailer/build_failure.mail-template
[internals]
configversion = 010a
The available modules are:
  1. Contents , which acts as a dpkg -c over the built packages.
  2. DateStamp , which displays build start and finish times into a file in the build directory.
  3. Lintian , which stores Lintian output on top of the built package in the pool directory.
  4. Mailer , which sends a reply to the uploader once the build has finished.
  5. PrevBuildCleaner , which deletes all files generated by the previous build.
  6. Repository , which generates a local repository of built packages.
2. Configure dput to upload package s sources to your local repository, edit the /etc/dput.cf file and add this entry:
[debomatic]
method = local
incoming = /home/john/debomatic
or the following if you are going to upload the files to a different machine through SSH:
[debomatic]
login = john
fqdn = debomatic.example.net
method = scp
incoming = /debomatic
3. Add a new Virtual Host on Apache and access the repository / built packages directly through your browser:
<VirtualHost *:80>
ServerAdmin john@example.net
ServerName debomatic.example.net
DocumentRoot /home/john/debomatic
<Directory /home/john/debomatic>
Options Indexes FollowSymLinks MultiViews
AllowOverride None
Order allow,deny
allow from all
</Directory>
</VirtualHost>
4. Start the daemon:
sudo /etc/init.d/debomatic start
5. (Optional) Add your repository to APT s sources.list:
deb http://debomatic.example.net/ unstable main contrib non-free
6. (Optional) Start Deb-O-Matic at system s startup by modifying the /etc/init.d/debomatic file at line 21:
- [ -x "$DAEMON" ]   exit 0
- [ "$DEBOMATIC_AUTOSTART" = 0 ] && exit 0
+ [ -x "$DAEMON" ]   exit 0
+ [ "$DEBOMATIC_AUTOSTART" = 1 ] && exit 0
and finally add it to the desired runlevels:
update-rc.d debomatic defaults
Enjoy!

16 September 2012

Russell Coker: Servers in the Office

I just had a conversation with someone who thinks that their office should have no servers. The office in question has four servers, an Internet gateway/firewall system, the old file server (and also Xen server), the new file server, and the VOIP server. The Internet gateway system could possibly be replaced by a suitably smart ADSL modem type device, but that would reduce the control over the network and wouldn t provide much of a benefit. The VOIP server has to be a separate system for low latency IMHO. In theory you could use a Xen DomU for running Asterisk or you could run Asterisk on the Dom0 of the file/Xen server. But that just makes things difficult. A VOIP server needs to be reliable and is something that you typically don t want to touch once it s working, in this case the Asterisk server has been a few more years without upgrades than the Xen server. An Asterisk system could be replaced by a dedicated telephony device which some people might consider to be removing a server, but really a dedicated VOIP server device is just as much of a server as a P4 running Asterisk but with greater expense. A major advantage of a P4 running Asterisk is that you can easily replace the system at no cost if there is a hardware problem. Having two file servers is excessive for a relatively small office. But running two servers is the common practice when one server is being replaced. The alternative is to just immediately cut things over which has the potential for a lot of people to arrive at work on Monday and find multiple things not working as desired. Having two file servers is a temporary problem. File Servers The first real problem when trying to remove servers from an office is the file server. ADSL links with Annex M can theoretically upload data at 3Mb/s which means almost 400KB/s. So if you have an office with a theoretically perfect ADSL2+ Annex M installation then you could save a 4MB file to a file server on the Internet in not much more than 10 seconds if no-one else is using the Internet connection. Note that 4MB isn t THAT big by today s standards, the organisation in question has many files which are considerably bigger than that. Large files include TIFF and RAW files used for high quality image processing, MS-Office documents, and data files for most accounting programs. Saving a 65MB quick-books file in 3 minutes (assuming that your Annex M connection is perfect and no-one else is using the Internet) would have to suck. Then there s the issue of reading files, video files (which are often used for training and promotion) are generally larger than 100MB which would be more than 30 seconds of download time at ADSL2+ speed but if someone sends an email to everyone in the office saying please watch this video then the average time to load it would be a lot more. Through quickly examining my collection of Youtube downloads I found a video which averaged 590KB/s, if an office using a theoretically perfect ADSL2+ connection giving 24Mb/s (3MB/s) download speed had such a file on a remote file server then a maximum of five people could view it at one time if no-one else in the office was using the Internet. Now when the NBN is connected (which won t happen in areas like the Melbourne CBD for at least another 3 years) it will be possible to get speeds like 100Mb/s download and 25Mb/s upload. That would allow up to 20 people to view videos at once and a 65MB quick-books file could be saved in a mere 22 seconds if everyone else was idle. Of course that relies on the size of data files remaining the same for another 3 years which seems unlikely, currently no Youtube videos use resolutions higher than 1920*1080 (so they don t take full advantage of a $400 Dell monitor) and there s always potential for storing more financial data. I expect that by the time we all have 100Mb/25Mb speeds on the NBN it will be as useful to us as 24Mb/3Mb ADSL2+ Annex M speeds are today (great for home use but limited for an office full of people). There are of course various ways of caching data, but all of them involve something which would be considered to be a server and I expect that all of them are more difficult to install and manage than just having a local file server. Of course instead of crunching the numbers for ADSL speeds etc you could just think for a moment about the way that 100baseT networking to the desktop has been replaced by Gigabit networking. When people expect each workstation to have 1000Mb/s send and receive speed it seems quite obvious that one ADSL connection shared by an entire office isn t going to work well if all the work that is done depends on it. Management could dictate that there is to be no server in the office, but if that was to happen then the users would create file shares on their workstations so you would end up with ad-hoc servers which aren t correctly managed or backed up. That wouldn t be an improvement and technically wouldn t achieve the goal of not having servers. Home Networking Without Servers It is becoming increasingly common to have various servers in a home network. Due to a lack of space and power and the low requirements a home file server will usually be a workstation with some big disks, but there are cheap NAS devices which some people are installing at home. I don t recommend the cheap NAS devices, I m merely noting that they are being used. Home entertainment is also something that can benefit from a server. A MythTV system for recording TV and playing music has more features than a dedicated PVR box. But even the most basic PVR ($169 for a 1TB device in Aldi now) is still a fairly complex computer which would probably conflict with any aim to have a house free of servers. The home network design of having a workstation run as a file and print server can work reasonably well as long as the desktop tasks aren t particularly demanding (IE no games) and the system doesn t change much (IE don t track Debian/Testing or otherwise have new versions of software). But this is really something that only works if you only have a few workstations. Running an office without servers seems rather silly as it seems that none of my friends are able to have a home without a server. Running Internet Services Hypothetically speaking if one was to run an office without servers then that would require running all the servers in question on the Internet somewhere. For some things this can work better than a local server, for example most of my clients who insist on running a mail server in their office would probably get a better result if they had a mail server running on Linode or Hetzner or one of the Hosted Exchange offerings if they want a Windows mail sever. But for a file server if you were to get around the issue of bandwidth required to access the files in normal use there s the issue of managing a server (which is going to take more effort and expense than for a server on the LAN). Then there s the issue of backups. In my previous post about Hard Drives for Backup [1] I considered some of the issues related to backing data up over the Internet. The big problem however is a complete restore, if you have even a few dozen gigs of data that you want to transfer to a remote server in a hurry it can be a difficult problem. If you have hundreds of gigs then it becomes a very difficult problem. I m sure that I could find a Melbourne based Data Center (DC) that gives the option of bringing a USB attached SATA disk for a restore but even that case would give a significant delay when compared to backing things up on a LAN. If a server on the office LAN breaks in the afternoon my client can make arrangements to let me work in their office in the evening to fix it, but sometimes DCs don t allow 24*7 access and sometimes when they do allow access there are organisational problems that make it impossible when you want it (EG the people at the client company who are authorised become unavailable). The Growth of Servers Generally it s a really bad idea to build a server that has exactly the hardware you need. The smart thing to do is to install more of every resource (disk, RAM, CPU, etc) than is needed and to allow expansion when possible (EG have some RAM slots and drive bays free). No matter how well you know your environment and it s users you can get surprised by the way that requirements change. Buying a slightly bigger server at the start costs hardly any money but upgrading a server will cost a lot. Once you have a server that s somewhat over-specced you will always find other things to run on it. Many things could be run elsewhere at some cost, but if you have unused hardware then you may as well use it. Xen and other virtualisation systems are really good in this regard as they allow you to add more services without making upgrades difficult. This means that it s quite common to have a server that is purchased for one task but which ends up being used for many tasks. Anyone who would aspire to an office without servers would probably regard adding extra features in such a manner to be a problem. But really if you want to allow the workers to do their jobs then it s best to be able to add new services as needed without going through a budget approval process for each one. Conclusion There probably are some offices where no-one does any serious file access and everyone s work is based around a web browser or some client software that is suited to storing data on the Internet. But for an office where the workers use traditional Office software such as MS-Office or Libre-Office a file server is necessary. Some sort of telephony server is necessary no matter how you do things. If you have a traditional telephone system then you might try not to call the PABX a server , but really that s what it is. Then when the traditional phone service becomes too expensive you have to consider whether to use Asterisk or a proprietary system, in either case it s really a server. In almost every case the issue isn t whether to have a server in the office, but how many servers to have and how to manage them. Related posts:
  1. Planning Servers for Failure Sometimes computers fail. If you run enough computers then you...
  2. a good security design for an office One issue that is rarely considered is how to...
  3. Efficiency of Cooling Servers One thing I had wondered was why home air-conditioning systems...

15 September 2012

Martin-&#201;ric Racine: HTML5: Firefox without Flash

Over the past few days, I decided to purge Gnash and LightSpark from my laptop to see whether my Internet experience would be affected in any dramatic way. Amazingly, a number of sites seem to offer video content encoded in Theora (VP3) or WebM (VP8). Sadly, a handful of popular sites such as Vimeo insist upon using the H.264 (MPEG-4) CODEC, which cannot be safely supported on Free Software because of unclear licensing issues that might impose an ulterior usage fee onto the end-users.

The good news is that the Mozilla Foundation has decided to avoid the issue together: starting with the most recent release of the mobile version of Firefox, content decoding is offloaded to the platform's native media CODEC library. On most Free Software platforms, this means that Gstreamer will handle the content and, in turn, use gstreamer-plugins-bad to perform the decoding. However, Gstreamer support is still rather sketchy, as attested by this Debian bug report and thus disabled by default. This leaves me wondering how little is missing for this to properly work. Would either Canonical or Red Hat perhaps be interested in funding this?

Eddy Petri&#537;or: Why a lack of skepticism is dangerous...

Some of my Romanian readers might know that for the last two years I've got involved in the skeptical movement to such a degree that I am a co-producer of a bi-weekly podcast on science and skepticism (in Romanian) called Skeptics in Romania . Some might even be regular listeners of the show.

(There isn't much to see now visually on the site, but me and the other people behind the project have some ongoing plans to change that.)

In spite of our modest site, up until now we had some successes, one of them being the publication of an article on us in a known Romanian printed publication and another being the invitation to a live show face to face with Oreste Teodorescu, a well known Romanian mysticist and woo promoter.

During that live show we managed to show a demonstration (video below, in Romanian) of how astrology gives the impression of working, without actually working, and, taking into account we had no prior TV camera experience and that it was a live show, I think we managed an honourable presence.


<iframe allowfullscreen="allowfullscreen" frameborder="0" height="315" src="http://www.youtube.com/embed/y5OG1q8_3Ro" width="420"></iframe>

We also have a series of interviews in English with some really interesting people: Dr. Eugenie Scott, Prof. Christopher French, Prof. Edzard Ernst, Samantha Stein and others. We did these interviews at Denkfest 2011, in Zurich, and we integrated the translated (voice over) interviews in our podcast. The conlusion is that most of our activities revolve around the podcast, so let me tell you more about that.

The podcast has a somewhat fixed structure, it starts with a conversation between ourselves, then we have a segment on the history of science, technology, skepticism and woo, and then we have a segment called The dangers of not being skeptical . In this segment we present cases of people who lost their lives, their health, their money or any combination of the former because they were duped into some scam, science-y sounding non-science, unfounded claim or some other woo.

Having lost recently my brother-in-law to a form of cancer known as Hodgkin lymphoma, I became especially sensitive about miracle-cure claims for cancer, and this section of the show has lately seen its fair share of such cases. Honestly, if there could be a way to prosecute the irresponsible, ignorant and/or cynical people promoting all sorts of quack "therapies", especially for cancer*, I would really like to see it happen. But there isn't, and we're trying the best accessible approach, informing the public.

During my brother-in-law's last two years of his life, he went through lots of chemotherapy and radiotherapy sessions, repeated periods of hospitalisation, and lots of drugs. This is the best of what we currently have for treating and curing most forms of cancer, and too many times this isn't enough. I can't even imagine how stressful and discouraging it must feel when the best of what we have doesn't help.

Here is where the desperation and hopes of patients and their families meet the purely irresponsible cynical or ignorant promoters of woo and quack therapies. Because it takes either an ignorant or a really cynical (I really feel this word isn't enough) person to prey on the suffering of other people to make easy money under the false pretence of offering a cure.

It almost happened to my brother-in-law and his family, because they almost went for some herbal concoction promoted as a cancer cure on some forum, blog or page of a seller of this fake therapy. It was really hard for me to make them understand why using such a product it not advisable, not even in parallel with the medical treatment due its possible counter effect or interactions with the real medical treatment, without them getting the wrong idea that I wasn't trying to help. While trying to be brief and informative not to lose their attention, I told them how "natural" doesn't necessarily mean "good" (uranium, lead and Irukandji's venom are all natural), and how plants are drugs because they all contain chemical substances (and no, "chemical" does not mean "human made" or "artificial") which could interact with the medical treatment.


But most people don't even have the chance of having close by a person with a more science-leaning thought process and a skeptical mind. Those unfortunate people are the most vulnerable people and constitute the biggest chunk of the victims of baseless pseudo-cures or pseudo-treatments.

On our last show, I presented the case of Yvonne Main, a cancer suffering patient who mistook an invasive carcinoma for a cyst, and irdologist Ruth Nelson for a real healthcare giver.

Yvonne Main, died from an invasive carcinoma
after seeking help from a iridologist,
and delaying real medical treament for 18 months


Yvonne, after seeking medical advice from a person that essentially promotes the dead idea of guessing diseases by looking at the eyes**, used natural treatments for about 18 months and, after all this time, her carcinoma grew to a size of 10 to 11 cm, eating through her skull and causing damage which was later attempted to be countered through bone transplant from her ribs.

Ruth Nelson wasn't prosecuted in any way and continues her practice of quackery unharmed.

This is not the only case, nor even one case from a select few where woo and quackery lead to grave consequences for patients. There are many, many more; they're so many that even after splitting them in categories they seem too many per category, especially when you realise these are only the findings of, essentially, a single man:


http://www.whatstheharm.net/


This is part of what I have been doing in the last few years, instead of working on Debian. Is it a good thing? Is it a bad thing? Maybe it's good. I want to know what do you think?


* you will, most likely, never hear such a promoter of non-therapies say that there isn't just one cancer, and that, in fact, cancer is a name for a certain family of diseases which are all called cancer - that's a first sign that you might be dealing with quack
** probably in the line of thought that the eyes are the gates to the soul so they must tell something significant about health

14 September 2012

Christian Perrier: Two more languages reach 100% translation for po-debconf in wheezy (fr,pt)

I recently blogged about 3 languages reaching 100% translation for debconf templates in wheezy. Today, two more languages joined the club: French and Portuguese. We're still on our way to get seven or even eight complete translations in wheezy. Czech is now only missing "linux-latest" and Spanish waits for sysvinit (which I just NMU'ed) and nova (unfortunately an error in former translation was unnoticed and I discovered it quite late). David Pr vot is still trying to get Danish complete, by doing many fast update rounds and NMUs. I hope he succeeds in this.

13 September 2012

Tim Retout: Inbox zero

My email's been out of control for a while now. I've noticed a correlation between the state of my email and my state of mind - I don't know which way the causation flows, if any. At the weekend (after assembling the shelves), I archived my entire inbox. Again. But I find the hard part with email bankruptcy is preventing the entire cycle recurring. This time, I was more drastic. I deleted all my labels, and all but three of my filters. I removed the Smart Labels, the chat widget, the calendar integration, the Google+ circles (more on that soon). There are no distractions in my inbox any more. I'm forcing myself to process every non-spam email that comes to my address. (Yes, I'm embarassed to say that I use Gmail - it seemed like a good idea at the time, because of the spam filtering. I occasionally notice bugs with ancient emails becoming unarchived or unread, and wonder if Google uses a probabilistic data structure to access all those attributes quickly enough. Can't investigate, though, because it's Gmail. Consider this the first step towards moving away.) So rather than hiding the deluge in the background, I'm unsubscribing from a lot of mailing lists, and informing marketers that I don't want their communications. It turns out that I get a lot less email than I feared - and processing them this way means that high-traffic sources get removed first. My remaining problem is what to do with email from mailing lists like debian-private - I don't really care enough to read everyone's vacation plans, but unsubscribing doesn't seem like the right thing either - there's (obviously) no online archive for this type of mailing list. For the moment, I've added a filter back to hide just vacation messages, but there's a more general problem lurking here.

MJ Ray: Business As Mutual conference, Anglia Ruskin Uni, 12 Sep

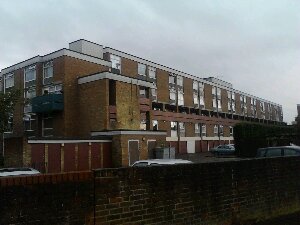
image Here s a summary of what happened at this conference. Opening address. Keynote from Nick Hurd MP, @minforcivsoc. Lot less money around. Called canals and rivers trust the biggest social enterprise. Blames lack of large social enterprises on culture, leadership and access to capital. First Big Society Capital investments announced tomorrow. Questions (and responses) about what had changed in commissioning (determination?), something about accountability in health I think but I didn t hear (more public scrutiny), other models besides worker-led (gov is agnostic, but that s just the type of mutuals so far), and capital renewal (gov is challenging the banks with Big Society Bank). This is going to get a bit long, so click through to our site to read what the other the speakers had to say and what that block of flats in the picture has to do with it Still here? Good! Harriet Hounsell from John Lewis Partnership was next. What s the Right level of profit? Structure of the partnership. The registry seems like the member services function and a bit more. Partner suggestions make a real difference. Beliefs have been tested. Recession hit us. Vivian Woodall, the co-operative phone, back to how it started. He knew people working for NGOs with high international phone bills. Bulk buy. Solid steady growth. Paid all tax. Living our cooperative values. Employee council and profit-shared. Adoption of new brand. Questions to both on redundancies (debate openly, try to redeploy, ultimately division of responsibilities: managers manage staff levels, not members), and being rejected as too small to help other social enterprises (ask why? Try local level instead of head office?), plus praise for John Lewis. Then there was coffee, workshops, lunch, workshops and coffee. I don t think I should report all of that, so a quick comment on the venue at Anglia Ruskin Uni Cambridge: is the Lord Ashcroft it s named after the same one who said it was legal to attack Iraq? Anyway Based on the workshops, I don t think our co-op will do SROI accounting any time soon (needs too much people time) and I m little the wiser on leadership. Some people are intrigued by collective management and cooperative working, though. The closing keynote was Wayne Hemingway, formerly of Red or Dead and now of Hemingway Design. He gave a quick history of himself and of those two enterprises and a bit of an entertaining ramble around. He seemed very much from the business end and how to use business to benefit society, but I ve not really looked at his companies before. I probably should do, as they ve a regeneration project in Lynn (pictured: before Wayne). Then it was the closing address, the thanks (yes, thanks to the workers and sponsors) and then time to head for the exit. It s a shame that some people who made good points during the keynotes (coop party!) left quickly instead of staying to chat.

12 September 2012

Patrick Matth i: Recent packaging updates 2012/09

What I have done (on my packages for Wheezy) in the last weeks? imvirt 0.9.4-3 and 0.9.4-4 adds two upstream patches to remove an applicable use of /proc in Perls procfs_read() method, which fixes LXC detection and another patch to not count the dmesg lines twice within the KVM detection module.
Much thanks to Thomas Liske! mlt The 0.8.0-4 upload also adds two upstream patches to fix an major memory leak in the mlt_cache function and a crash with LADSPA plugins on dlclose().
And here much thanks to Dan Dennedy!
I have also uploaded 0.8.2-1 to experimental. roaraudio 1.0~beta2-2 and 1.0~beta2-3 added a few upstream patches to fix security and major use problems. The debdiff was a bit huge so it took a bit more time to unblock/migrate.
1.0~beta5-1 is also available in experimental.
Much thanks for the patch support to Philipp Schafft! otrs2 With the 2.4.9+dfsg1-3+squeeze3 upload (DSA-2536-1) there was an security update for otrs2 on Squeeze which fixes a cross-site scripting issue and improved the e-mail filter to detect nested tags. Those with a few other fixes migrated with 3.1.7+dfsg1-5 to testing, while I also uploaded 3.1.10+dfsg1-1 to experimental.
Now I can focus on the upcoming 3.2.x packaging. :)

Martin F. Krafft: A black day for democracy

Today was a black day for democracy in Germany. The German constitutional court ruled in favour of the European Stability Mechanism. In combination with last week s announcement by the European Central Bank to purchase government bonds without limits (breaking the No-Bail-Out clause at the core of their mandate more obviously and irreversably than ever before), the German people have lost a good deal of democracy today. Why? you may ask because from now on, fiscal and financial policy will be made in Brussels, by people enjoying full immunity, but who are not elected democratically by the European people, let alone the Germans, and they will freely decide over who has to pay and be liable for whom. I am talking about people like Klaus Regling, who was already involved the very first time the Maastricht Criteria were violated. He is now at the front of the largest and most powerful financial weapon ever conceived. With immunity. And people like Mario Draghi, whom I would possibly call the most corrupt person I know. His announcement to save the Euro at whatever cost accidentally came only a day before his motherland Italy had to go to the market for more money and was able to place a bond at such ridiculously low interest rates that anyone who s kept up to speed with Italy s development had to rightfully ask how that was possible. While in the past, for whatever reason, the European people have let the ECB get by saying that they are not bailing out countries when they buy bonds on the secondary market (wtf!), they have finally dropped that restriction (the law). And as of today, the ESM is ready to go, along with the fiscal pact. Germany is now liable for more than quarter of all of the Eurozone s past and future debts. And no citizen will be able to have any more influence in this, or reverse it. Budget, fiscal policy and currency control are forever gone. Not that parliamentarian democracies were ever direct. Yet, in the past, one could at least vote for those people whose promises one was inclined to believe the most. You can still do that in the future, but those people won t be able to influence fiscal or financial policy anymore. There is no way back. The ESM and its employees enjoy full immunity, and the ESM is forever-binding. There is no exit clause. Thanks to the ECB s law breaking and the ESM, which I consider highly unconstitutional, at least in Germany, Eurozone-countries may refinance their debts at interest rates that are in no way related to their ability to pay back loans. All other countries foremost Germany are henceforth liable for others debts. The fundamental rule of the EU that no country would have to stand up for another country, is gone with the wind. Within an hour, the markets reacted. Germany, which previously had to pay negative interest (a sign of stability) saw interests on its bond shoot up. And Spain, Portugal, Greece and others who couldn t previously refinance their old debts, are now getting fresh money cheaper than ever. Spain s president Rajoy today didn t even bother beating around the bush anymore, he s now going to apply for fresh money but won t bother with any saving schemes or other restructurings. Monti in Italy has suggested the same. Wouldn t you take money if you were offered it for free, without the need to pay it back? This is more than inflation, in my opinion. What is currently happening in Europe is active depreciation of individual wealth. Our heads of state are actively working against the people. The Euro has lost all credibility and everyone knows it. It is only a question of time until it will tremble and fall. Meanwhile, the market celebrates and continues their gambles while they still can, on the backs of our currency and our wealth. Most affected are the people who have savings in Euros, whose life insurances are decreasing in worth and who cannot afford to diversify into other asset classes or currencies. On the other hand, those who let their money do the work are being saved. Whoever previously invested into bonds of struggling states, hoping to reap massive interest gains, is now proven right. Brussels has eliminated the risk factor. What kind of message does this send??? Hands up if you thought that our politicians are even interested in closing the rapidly widening gap between rich and poor. Really? That s naive. The Eurozone is corrupt, and our currency has never been as virtual as today. Nobody can say whether saving the Euro at all cost is the right thing and noone knows whether what s currently happening is just bad. I would have wished that our politicians had taken the crisis as an incentive to fix the system in the interest of the people and with a long-term focus: But on the contrary! Europe s policiticans are making it crystal clear that the foundation upon which it was built, the laws and rules, the promises and guarantees, no longer apply. The people were not asked. The promises once made were broken. Our politicians have ruled over our heads. More debts are being made, and more debts to pay off debts, and so on. It s long gotten out of control, now the process is institutionalised. I feel sorry for our kids. I find it irresponsible what is being done to them (in addition to the way we rape the environment). I also feel deeply with the people in the struggling countries who are being screwed by the crisis and are not at fault. What our politicians are doing is unfortunately not going to help long term. The problems are just postponed, and with every day, the inevitable crash will be more painful. I am sorry. Today is a black day for democracy. We have lost souvereignity. We have lost control over our currency. We have lost our budget rights. And I have lost my faith in the last instance of the German government that I trusted. As of today, I know that the German constitutional court is nothing more than a puppet in the hands of the politicians (who are themselves puppets of Brussels and the banks). The limit they imposed (Germany s liability must not increase beyond 190 billion Euros without the federal parliament s consent) is worthless. Soon the politicians will explain to us why it s inevitable that we must raise this limit. Not that the people could prevent it, but still I had hoped for a fundamental ruling. They should not have touched numbers. The EU had a no-bailout-clause from day one. It was conditional from the start. If one of the fundamental principles of a contract is broken, the contract becomes invalid. Not only did I expect the court to rule against socialised debt, I would have wished them to go a step further. The German national bank gave up control over the currency to the ECB only because the ECB incorporated the principles of the German national bank. Once the ECB overturned those principles, Germany should have reclaimed their souvereignity. But noone else in Europe would have wanted that. Merkel became a puppet herself. I am grateful that our daughter has dual citizenship. NP: Porcupine Tree: Live at Atlanta 2010

11 September 2012

Russell Coker: Back to the Xperia X10

10 months ago I was given a Samsung Galaxy S Android phone [1] to replace my Sony Ericsson Xperia X10. I also installed Cyanogenmod on it (here is a more detailed comparison of the phones with a focus on liberty [2]). But now I m using the Xperia X10 again. Hardware Reliability Some time ago a friend told me that he bought a Sony phone in preference to a Samsung phone because he didn t think that Samsung phones were reliable enough. I assured him that Samsung phones would be fine if you used a gel-case, but now I m not so sure. My mother in law has a Samsung Galaxy S which now has a single crack across the face, it doesn t appear that her phone was dropped, maybe it just bent a bit it s a fairly thin phone. My Galaxy S started crashing over the last few months and now many applications will crash any time I use 3G networking. Currently my Galaxy S is working well as a small Wifi tablet and hasn t crashed since I replaced the SIM with one that has expired. I wish that phone designers would make mode solid products with bigger batteries. The fact that the Xperia X10 weighs maybe 20g more than the Galaxy S (according to Wikipedia) isn t a problem for me. Even with the Mugen Power 1800mah battery [4] to replace the original 1500mah battery it s still nowhere near the limit of the phone mass that I m prepared to carry. Sony Upgrades Some time ago Sony released an Android 2.3.3 image for the Xperia X10. There is no Cyanogenmod image for the Xperia X10 because it has been locked down which greatly limits what can be done. Also Sony has a proprietary backup program on their Android 2.1 image which isn t supported on Android 2.3.3 this inspired my post about 5 principles of backup software [3]. Due to this pain I didn t even try to upgrade the Xperia X10 phones for me and my wife until recently. Before upgrading the Xperia X10 phones I was unable to use my wife s phone. The phone didn t seem to like recognising my touch so long touch actions (such as unlocking the phone) were almost impossible for me. I think that this is due to the fact that I have fairly dry skin which presumably gives me a higher capacitance. After the upgrade both phones are usable for me, so presumably either Sony or Google upgraded the algorithms for recognising touch to work better with varying screen quality. Comparing the Galaxy S and the Xperia X10 When I first started running Cyanogenmod on the Galaxy S I noticed that it was a lot faster than the Xperia X10 but I didn t know why. It was documented that there had been performance improvements in Android 2.2. Now that I m running Android 2.3.3 on the Xperia X10 I know that the performance difference is not due to the Android version. It could be due to Cyanogenmod optimisations or Sony stupidity, but it s most likely due to hardware differences. The Galaxy S has more RAM and storage which allows installing and running more applications. Now that I m using the Xperia X10 for the bare minimum applications (phone calls, SMS, camera, email, ssh, and web browsing) it works quite well. I still play games on the Galaxy S and use it for more serious web browsing via Wifi. I think that the value I m getting from the Galaxy S as a tiny wifi tablet is greater than the money I might get from selling a partially broken phone that s been obsoleted by two significantly better models. Conclusion The camera on the Xperia X10 is significantly better than the one on the Galaxy S, so going back to a phone that has a great camera is a real benefit. But being slow and locked down is a real drag. I was tempted to buy a Samsung Galaxy Note or Galaxy S3, but it seemed like a bad idea to buy a phone given that my contract comes up for renewal in about 6 months which means I ll be offered a free phone which while not really free is still going to be cheaper than buying a phone outright. Also in future given the low opinion I m now getting of smart phone reliability I ll try and keep a small stock of spare Android phones to cover the case of broken phones. Related posts:
  1. Galaxy S vs Xperia X10 and Android Network Access Galaxy S Review I ve just been given an indefinite loan...
  2. CyanogenMod and the Galaxy S Thanks to some advice from Philipp Kern I have now...
  3. Liberty and Mobile Phones I own two mobile phones at the moment, I use...

10 September 2012

Tim Retout: Shelves

Bookshelves are a wonderful thing. Kate and I have been living without enough book space since we moved in together - all our shelves have been double-stacked. Finding anything is a pain, because it's impossible to tell if you still own the book you're looking for. No longer. One short visit to Ikea (plus delivery and assembly), and we have a huge 5x5 Expedit bookshelf dividing our living area. It has comfortably absorbed our entire collection (plus boxes) - we have double-stacked it, but can access both sides. Books are grouped by subject matter, so can actually be found. (We have a huge O'Reilly collection, but gave up sorting by publisher when we discovered various non-computing books in there...) Now I can sit on the sofa, and have (paper) reading material within arm's reach. It's good to have something more to our living space than a television and a pair of laptops. As an added bonus, you can't see the washing up from the living room any more. Screw e-books.

Christian Perrier: Three languages reach 100% translation for po-debconf in wheezy (de,ru,sv)

After several months of effort by the i18n team (and quite a bit from /me), some NMUs, a lot of help by the release team to accept many unblocks, we finally reached 100% translation for debconf screens, in wheezy, for three languages. And, no, French is not among them (yet). The first to reach this heaven are Russian, German and Swedish with translations for all translatable debconf screens for packages in Debian testing (which will become the next Debian release). Three more languages (French, Czech and Portuguese) are waiting for one package to reach testing and another (Spanish) is waiting for three packages. We should then soon reach 7 complete languages. David Pr vot is even trying to get Danish as complete as possible, but it requires pushing for about 15 packages, with many NMUs and unblocks to ask. I started this work in early April, so it took about SIX months to reach this and be ableto happily make a lot of noise about such achievement. You have no idea how it is appreciated by translators....so you maybe have a better idea why I can be so noisy when some uncoordinated upload (for instance with modified localized material) breaks this... We'll have much more news about achievements in l10n for wheezy in the upcoming weeks. We had a lot of things that deserve some trumpets, bells or whistles..:-)

Craig Sanders: openstack, bridging, netfilter and dnat

I just posted the following question to ServerFault .and then realised there might be people out there in magical internetland who know the answer but never visit any of the SO sites, so i ve posted it here too. Feel free to respond here on on serverfault.
In a recent upgrade (from Openstack Diablo on Ubuntu Lucid to Openstack Essex on Ubuntu Precise), we found that DNS packets were frequently (almost always) dropped on the bridge interface (br100). For our compute-node hosts, that s a Mellanox MT26428 using the mlx4_en driver module.
We ve found two workarounds for this:
1. Use an old lucid kernel (e.g. 2.6.32-41-generic). This causes other problems, in particular the lack of cgroups and the old version of the kvm and kvm_amd modules (we suspect the kvm module version is the source of a bug we re seeing where occasionally a VM will use 100% CPU). We ve been running with this for the last few months, but can t stay here forever.
2. With the newer Ubuntu Precise kernels (3.2.x), we ve found that if we use sysctl to disable netfilter on bridge (see sysctl settings below) that DNS started working perfectly again. We thought this was the solution to our problem until we realised that turning off netfilter on the bridge interface will, of course, mean that the DNAT rule to redirect VM requests for the nova-api-metadata server (i.e. redirect packets destined for 169.254.169.254:80 to compute-node s-IP:8775) will be completely bypassed.
Long-story short: with 3.x kernels, we can have reliable networking and broken metadata service or we can have broken networking and a metadata service that would work fine if there were any VMs to service. We haven t yet found a way to have both.
Anyone seen this problem or anything like it before? got a fix? or a pointer in the right direction?
Our suspicion is that it s specific to the Mellanox driver, but we re not sure of that (we ve tried several different versions of the mlx4_en driver, starting with the version built-in to the 3.2.x kernels all the way up to the latest 1.5.8.3 driver from the mellanox web site. The mlx4_en driver in the 3.5.x kernel from Quantal doesn t work at all)
BTW, our compute nodes have supermicro H8DGT motherboards with built-in mellanox NIC:
02:00.0 InfiniBand: Mellanox Technologies MT26428 [ConnectX VPI PCIe 2.0 5GT/s - IB QDR / 10GigE] (rev b0)
We re not using the other two NICs in the system, only the Mellanox and the IPMI card are connected.
Bridge netfilter sysctl settings:
net.bridge.bridge-nf-call-arptables = 0
net.bridge.bridge-nf-call-iptables = 0
net.bridge.bridge-nf-call-ip6tables = 0
Since discovering this bridge-nf sysctl workaround, we ve found a few pages on the net recommending exactly this (including Openstack s latest network troubleshooting page and a launchpad bug report that linked to this blog-post that has a great description of the problem and the solution) .it s easier to find stuff when you know what to search for :), but we haven t found anything on the DNAT issue that it causes.

Update 2012-09-12: Something I should have mentioned earlier this happens even on machines that don t have any openstack or even libvirt packages installed. Same hardware, same everything, but with not much more than the Ubuntu 12.04 base system installed. On kernel 2.6.32-41-generic, the bridge works as expected. On kernel 3.2.0-29-generic, using the ethernet interface, it works perfectly.
Using a bridge on that same NIC fails unless net.bridge.bridge-nf-call-iptables=0 So, it seems pretty clear that the problem is either in the mellanox driver, the updated kernel s bridging code, netfilter code. or some interaction between them. Interestingly, I have other machines (without a mellanox card) with a bridge interface that don t exhibit this problem. with NICs ranging from cheap r8169 cards to better quality broadcom tg3 Gbit cards in some Sun Fire X2200 M2 servers and intel gb cards in supermicro motherboards. Like our openstack compute nodes, they all use the bridge interfaces as their primary (or sometimes only) interface with an IP address they re configured that way so we can run VMs using libvirt & kvm with real IP addresses rather than NAT. So, that indicates that the problem is specific to the mellanox driver, although the blog post I mentioned above had a similar problem with some broadcom NICs that used the bnx2 driver. openstack, bridging, netfilter and dnat is a post from: Errata

Next.

Previous.