Search Results: "reg"

22 March 2012

Richard Hartmann: Svalbard

Svalbard The things you find when cleaning out a disk; preparing for re-installation of your laptop on a larger disk once the laptop comes back from repair... I thought I had posted this in early January, but apparently not. As it would be a shame to just throw this away, here goes: I am sitting in the Oslo airport, waiting for boarding back home to start. Seeing the sun after a week of darkness still feels strange. Inital trouble It's been a very interesting week, starting with our trip to Oslo in the other direction. We spent New Year's Eve in Oslo, timing our forced overnight stay before reaching Svalbard to coincide with something interesting. The close timing of our travel meant that there was exactly one flight to Oslo we could take. Never having heard of Air Baltic before and finding out that they are a discount airline, my gut feeling told me to be be wary. I refuse to fly with those airlines on principle, not wanting to support their business model while hurting airlines with decent treatment of customers. Unfortunately, I was forced to book with them in this case. As it turns out, my gut was right. More on that below. Our plane was late in landing and my luggage was lost. As it was New Year's Eve, the staff at Oslo airport understandably wanted to be home, not at work. Still, getting them to file a report was tedious and finding out days later that the report was incomplete was, well, not good. The express train from the airport to Oslo central station had closed early without any advance notice or local signs, presumably because of NYE. The gates were simply closed and that's that. We figured out how the bus system worked, got our tickets from a vending machine, saw the one bus to central station drive away, and proceeded to wait in the outside waiting area; at least we had a front spot in the queue. While we don't get cold easily, it was funny to see Norwegians in thin clothes stand around in the biting wind, apparently being comfortable. A young mother with a baby, who didn't anticipate being forced to wait outside at -15C, as opposed to just sitting down in a train, had no warm clothes for her son; something that was fixed by wrapping him in spare clothes from Ilona's luggage. After waiting for about thirty minutes for the next bus to appear, it parked twenty or thirty meters away from the designated parking spot. The rough queue disintegrated and if not for Ilona's leaving me with luggage and backpacks and storming off to fight the masses, said mother with baby and ourselves would have waited for another thirty minutes. More than hundred people were left stranded at the airport to celebrate there or on the bus. Meh. We hurried, by taxi, from central station to hotel to harbour and arrived about five minutes to twelve. NYE itself was nice. We stood on top of the opera house and watched a rather impressive show of fireworks through the thickening mists. Norwegian fireworks pack lot more punch than German ones; you actually feel your clothes shake when they go off. Getting to Longyearbyen The flight from Troms to Longyearbyen had free in-flight Wi-Fi and flying over the edge of satellite coverage demonstrated how far we were from everywhere else rather impressively. Arriving at Longyearbyen, I fixed the lost luggage claim with the help of an extremely nice woman working at the airport. She confirmed that Air Baltic is legally required to reimburse me after an arcane system based on a virtual IMF currency to the tune of about 1.500. That may sound like a lot, but seeing as I had most of my scuba gear with me, that's not even half of what my luggage was worth. I was forced to get by New Years with what I had on my body and went shopping the next day when I could buy at least a few things. I got by with spending about 180 by going for non-fitting bargain bin clothes, wanting to reduce impact on Air Baltic. Shortly after that, my luggage arrived, unannounced. Air Baltic refused to reimburse me even though they are legally required to, again the airport staff confirmed this. But unless I sue in the country of destination, Norway, I won't see any money. Long story short: Avoid Air Baltic if possible. They will break the law to cheat you out of money when they have a reasonable expectation of getting away with it. Update: Yep, seems they got away with it unless I take legal measures. You have been warned. Longyearbyen itself was very nice. We started off with a short, guided taxi tour around the city, seeing literally everything of it as there's not a lot of Longyearbyen to start with. Dogsledding Next day, as noted earlier, we went shopping and spent the "evening" with dogsledding which turned out to be tons of fun. We helped with harnessing the dogs which is somewhat cumbersome as the dogs are so eager to burn off their energy that they want to run all over the place, not being put into a harness and snapped onto the pull-line. Never having been dogsledding before I was a bit wary, but riding over not too rough terrain is almost trivial once you get the hang of it; listen to what the musher in front of you yells and emulate the same shouts with your own dogs. If the dogs become too fast, step onto the brake pad which simply drives spikes into the snow. If the dogs slow down while going uphill, skate with one foot to help them. That's it for speed. As the dogs are following the musher's sled anyway, steering the dogs was not a concern. Fun fact: The musher used a laser pointer to steer his dogs; simple, efficient, and presumably fun. We learned, by demonstration, that sledding dogs can eat snow, take a leak, and take a dump while running at full speed and pretty much all at the same time. The dogs are left either in cages or on long chains far away from the city as they tend to bark and howl a lot. We were surprised to learn that, even when there are seals left to hang dry as dog food nearby, there are no problems with bear attacks. Apparently even the extremely aggressive and hungry one year old males will not go near dogs. Still, while out in the ice and snow, our guide carefully flooded all crevices and cliff bases to root out female bears with young ones early. They hide their children from the wind and they will attack, dogs and all, if we get too close. That's why our musher carried rifle in his sled and flare gun on his body. Snowmobile The next "morning", we drove around by snowmobile. This turned out to be extremely boring as it was a curated trip with over half a dozen snowmobiles in our group; a stark contrast to our two-sled tour the day before. The last time I went snowmobiling, we raced each other up and down a two-star black (i.e. steep, bumpy, and curvy) ski slope, jumping several meters when racing over larger bumps and crossing streets, so riding single file at 30 km/h was... anticlimatic. Again, the guide had rifle and flare gun with him. We spent the afternoon and evening walking around the city. Ice bears, part I As the ice caves and the glacier were still closed, we decided to have another walk around the city. Having planned make it a quick tour, we lost track of time due to lack of sun and ended up walking around for seven hours. A note about that trip.. If you are alone with your wife, unarmed, climbing up a very steep and slippery mountainside over a sheet of ice with deep snow underneath and loose rocks in between, and then start shining around with your flashlight under the stilts of an abandoned mine that looks like in a horror movie, the correct answer to "What are you doing?" is never ever "Looking for ice bears". Even if it's the truth, this is not an acceptable answer. I crawled up the last part on all fours, camera and tripod in hand while Ilona stayed about two dozen meters below the mines' entrance, refusing to go another step towards the mine. As soon I made it up the creaky and shaky, for a lack of a better word, let's call it ladder, she forced me to come down again. Bleh, but I guess I deserved that. Armed photographer Next day, we got final confirmation that we would not be allowed to rent snowmobiles to explore the hinterland on our own and that other for some, and I quote, "crazy Russians", no one would even attempt to cross over to Barentsburg. Thus, we ended up renting a car for the ~20 kilometers of total road length. That turned out to be a great idea as it allowed us to get away from the light and take some very nice long exposures. It was then that I got a rental rifle, as well. There is a law against leaving the town unarmed and I was not about to test my luck too much. Turns out that, as part of Germany's WWII reparations, Norway received our all hand guns and as they still function perfectly when dirty and in cold climate which makes them still popular in Svalbard, today. The Karabiner 98 Kurz which I received is built incredibly well. It's somewhat scary inasmuch every detail is designed to make this weapon ready to fire. If you hurry or are inexperienced, you will end up with an unlocked and loaded rifle after putting in the bolt. Putting the safety in and not chambering a bullet takes conscious effort and knowledge of the weapon. This is in stark contrast to other weapons I had the chance to dissect, which all defaulted to being safe. Even other military weapons such as the AK74 and the M4A1 are inherently more secure, designed to be locked and safe. The Mauser K98... not so much. As an aside, they didn't bother to remove the Reichsadler and Swastika from the rifle, contending themselves with striking out the German registration number and stamping the rifle with a Norwegian one. I guess Norwegians don't really "care" about these signs as much as we Germans do. In a way, that's a good thing I guess, at least as long as it's an indication of indifference towards the sign, not one of forgetting or ignoring the underlying issues. Still, I was very glad to have rented the rifle. While Ilona tended to stay in the running car with heat and lights on, I went out and away from the car. Even when standing near a street, a medium snow storm will make you appreciate the four powerful arguments against being eaten by a random bear which are at the ready over your shoulder. We even went to the shooting range so I could get some practice. The procedure is very trusting, as is anything in Longyearbyen. After accessing the interior of one of the houses in a particular way which I won't specify here, you simply switch on the floodlights, put up the red flag, position a target and write your name into the guest book. Once you're done shooting, toss a few coins into the bowl next to the guest book, remove the targets and flag, turn off the lights, close the door and that's that. Unfortunately, the way in was under a few meters of snow so I couldn't get in any practice shots. Ice bears, part II Later, as I was standing on a wind-polished slate of ice taking pictures of the Seed Vault (located here), I heard an ice bear roar behind (i.e. to the north of) me. I consciously remember hearing the bear, I consciously remember facing the other way around, half-crouched, rifle raised in the direction of the roar. I also consciously remember smacking the safety off and chambering a bullet after having regained control of my body. I do not remember spinning around on a wind-polished slate of ice, so treacherous I hand to balance with my arms and didn't even lift my feet when walking over it, without losing balance or footing, nor do I remember crouching and raising the gun. Evolution really is amazing; no matter what primal chord that roar struck, it certainly saved a ton of people over the years. In my case, thankfully, there was no bear to be seen down the slope. There may be no sun or anything, but the snow reflects the starlight so you tend to see surprisingly far and as I was on on the mountainside and the roar came from down from the coast, and as I had my rifle, I decided to finish the photo session while keeping the slope in close view. In hindsight, I am still glad I decided to do that as the shots came out rather nice. Next day, we drove out to Mine 12, the farthest you can away from Longyearbyen. The dump truck transporting coal alternated between driving a full load of coal back to the city and being its own snowplow. One quick trip to get coal, one slow and empty trip to plow away snow, rinse, repeat. If not for that, our 4WD would never have made it all the way up to the mine. Neither snow storms in North America nor around the Alps prepared me for what people on Longyearbyen consider normal wind in their backyard. This is where the word wind-swept was invented. The main reason that Svalbard is inhabited at all, other than the Gulf Stream, is coal. We have been told that the coal up there is of extremely high quality and while I can't say much about that, I can say that it's hard as stone. This is nice as it does not smear when you get coal all over yourself. Just shake out your jacket and pants and you are good as new. On our way back, we met two locals who had just prepared the glacier and ice caves for tourists. Had I known that in advance, I would have tried to go with them to take pictures completely away from all artificial light. Oh well, can't have everything. Speaking of not being able to have everything, the outdoor hot tub in our hotel which integrated ice bar and BBQ grill was still under several meters of snow so we couldn't use that, either. Finally, the few divers who are in Longyearbyen didn't have time to take me onto a trip while I was there. As I already missed my opportunity to dive the Arctic circle when the one diver on Gr msey happened to be on the mainland and barely missing it by diving Str tan instead, this was kind of a bummer. On the plus side, this has given me a goal to pursue and achieve. Random notes For the rest of my notes, I will resort to a largely unsorted list of bullet points as there's just too much to talk about in prose. All in all, it was well worth it. PS: If you know anyone working with Google Maps, ask them to consider improving their coverage of the Arctic. This is a real pity. As is the rest of the Arctic and the fact that Google Earth cheats you out of the North and South Pole by stretching adjacent tiles into and over them.

Richard Hartmann: Lenovo service quality

As there has been a lot of feedback to my post regarding Lenovo's hardware quality, I thought it would only be fair to follow this up now that my laptop returned from Lenovo. After waiting about 15 minutes on the phone, I got to speak to an actual human. While I really do not have a problem with foreigners and love to talk to people from other cultures, I do firmly believe that someone working in a telephone support position should have at least basic language skills, both spoken and written. This was not the case and communicating my issues, and making sure that they would be written down correctly, took a long time and was generally frustrating. I put four things into the returns package: In said letter, I specified all my issues with the laptop, how removing the UMTS card will improve, but not fix the situation, and that the power brick will deliver power for a split second and then go off for a second; rinse repeat. Not having heard from them for a week, I decided to follow up on the status. As Lenovo's web interface claimed my ticket number did not exist, I spent a total of 1 hour 47 minutes in the waiting loop, not counting the menu selections. I never even managed to even reach a human. The day before I left for Open Source Days, the laptop arrived. The ticket number still did not exist according to the web interface and they never sent email even though they had my address, but at least my issue was fixed. Or so I thought. The repair slip claimed they switched out the mainboard, a claim I can not prove/disprove. It's OK not to find a bug in the first try, especially when it's not as simple as "display cracked". It's not quite as OK to not properly test a machine before sending it back. It's definitely not OK to not care in the least and just send back a machine which you obviously did not even try to debug. How they could not replace the power brick is beyond me. Thankfully, I ordered three separate ones and that was just my on-desk one so I have two others. Still. Overall, I am not impressed.

21 March 2012

Axel Beckert: Tools for CLI Road Warriors: Remote Shells

Most of my private online life happens on netbooks and besides the web browser, SSH is my most used program especially on netbooks. Accordingly I also have hosts on the net to which I connect via SSH. My most used program there is GNU Screen. So yes, for things like e-mail, IRC, and Jabber I connect to a running screen session on some host with a permanent internet connection. On those hosts there is usually one GNU Screen instance running permanently with either mutt or irssi (which is also my Jabber client via a Bitlbee gateway). But there are some other less well-known tools which I regard as useful in such a setup. The following two tools can both be seen as SSH for special occassions. autossh I already blogged about autossh, even twice, so I ll just recap the most important features here: autossh is a wrapper around SSH which regularily checks via two tunnels connect to each other on the remote side if the connection is still alive, and if not, it kills the ssh and starts a new one with the same parameters (i.e. tunnels, port forwardings, commands to call, etc.). It s quite obvious that this is perfect to be combined with screen s -R and -d options. I use autossh so often that I even adopted its Debian package. mosh Since last week there s a new kid in town^WDebian Unstable: mosh targets the same problems as autossh (unreliable networks, roaming, suspending the computer, etc.) just with a completely different approach which partially even obsoletes the usage of GNU Screen or tmux: While mosh uses plain SSH for authentication, authorization and key exchange the final connection is an AES-128 encrypted UDP connection on a random port and is independent of the client s IP address. This allows mosh to have the following advantages: The connection stays even if you re switching networks or suspending your netbook. So if you re just running a single text-mode application you don t even need GNU Screen or tmux. (You still do if you want the terminal multiplexing feature of GNU Screen or tmux.) Another nice feature, especially on unreliable WLAN connections or laggy GSM or UMTS connections is mosh s output prediction based on its input (i.e. what is typed). Per line it tries to guess which server reaction a key press would cause and if it detects a lagging connection, it shows the predicted result underlined until it gets the real result from the server. This eases writing mails in a remote mutt or chatting in a remote irssi, especially if you noticed that you made a typo, but can t remember how many backspaces you would have to type to fix it. Mosh needs to be installed on both, client and server, but the server is only activated via SSH, so it has no port open unless a connection is started. And despite that (in Debian) mosh is currently just available in Unstable, the package builds fine on Squeeze, too. There s also an PPA for Ubuntu and of course you can also get the source code, e.g. as git checkout from GitHub. mosh is still under heavy development and new features and bug fixes get added nearly every day. Thanks to Christine Spang for sponsoring and mentoring Keith s mosh package in Debian.

Steve Kemp: My code makes it into GNU Screen, and now you can use it. Possibly.

Via Axel Beckert I learned today that GNU Screen is 25 years old, and although development is slow it has not ceased. Back in 2008 I started to post about some annoyances with GNU Screen. At the time I posted a simple patch to implement the unbindall primitive. I posted some other patches and fixed a couple of bugs, but although there was some positive feedback initially over time that ceased completely. Regretably I didn't have the feeling there was the need to maintain a fork properly, so I quietly sighed, cried, and ceased. In 2009 my code was moved upstream into the GNU Screen repository (+documentation update). We're now in 2012. It looks like there might be a stable release of GNU Screen in the near future, which makes my code live "for real", but in the meantime the recent snapshot upload to Debian Experimental makes it available to the brave. 2008 - 2012. Four years to make my change visible to end-users. If I didn't use screen every day, and still have my own local version, I'd have forgotten about that entirely. Still I guess this makes today a happy day! Wheee! ObQuote: "Thanks. For a while there I thought you were keeping it a secret. " - Escape To Victory

20 March 2012

Russell Coker: An Introduction to Android

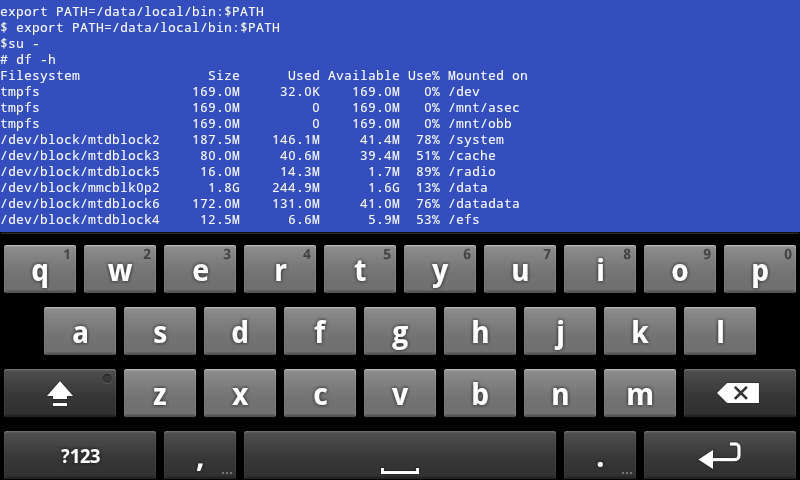
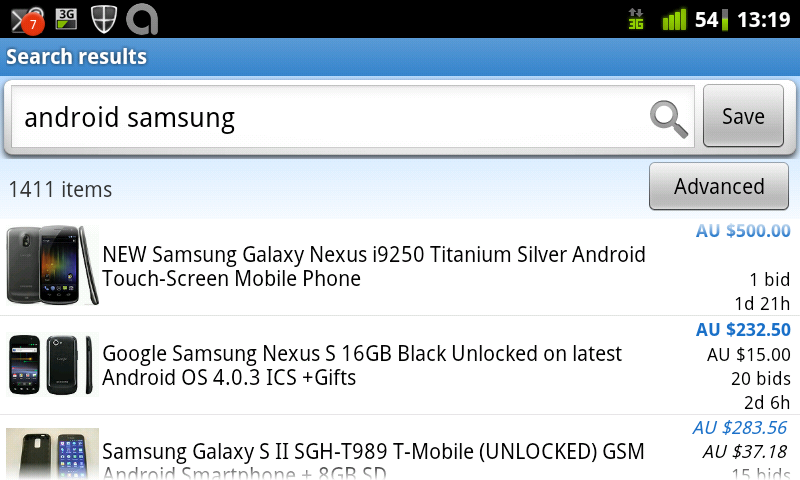
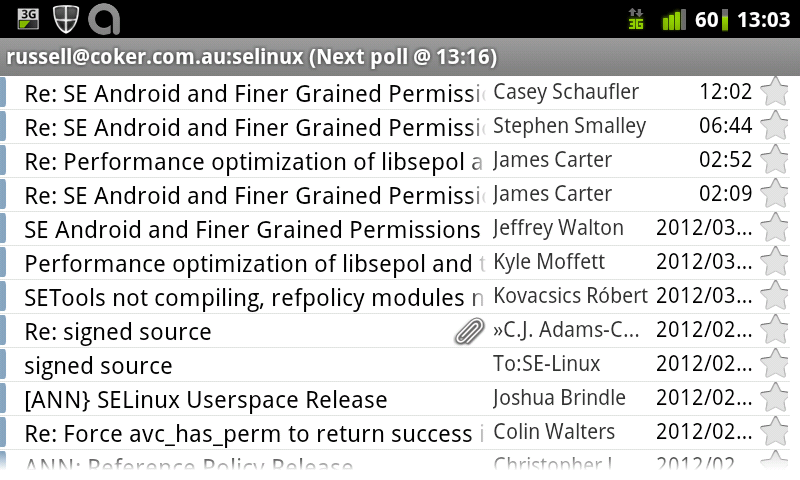
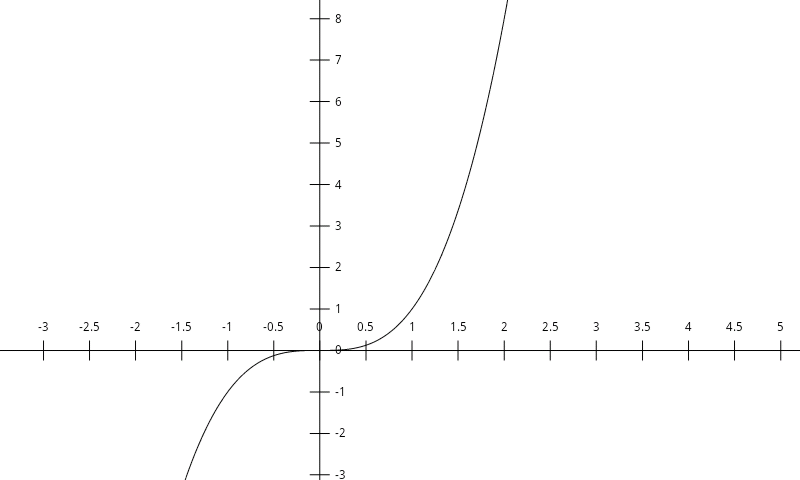
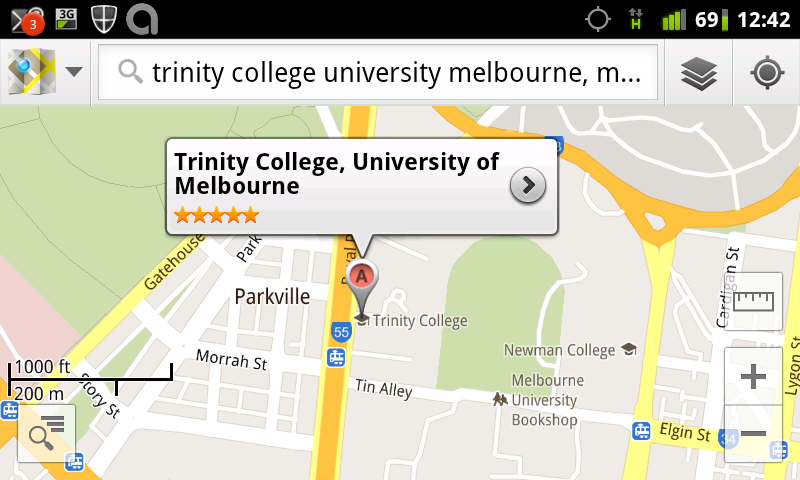
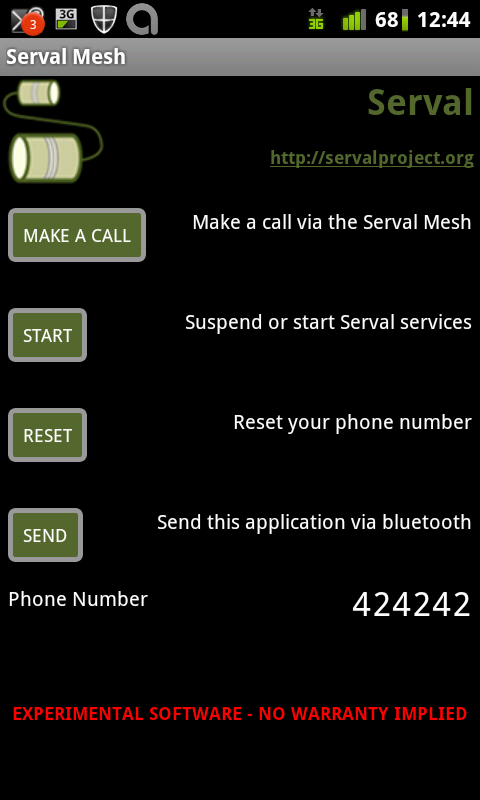
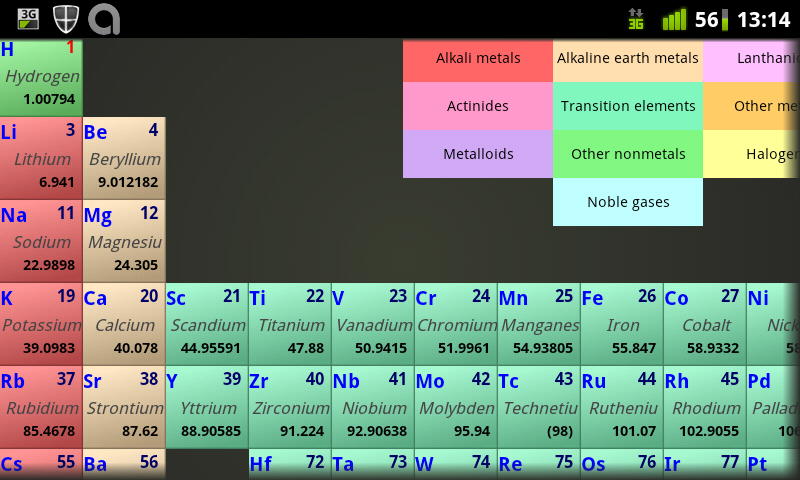
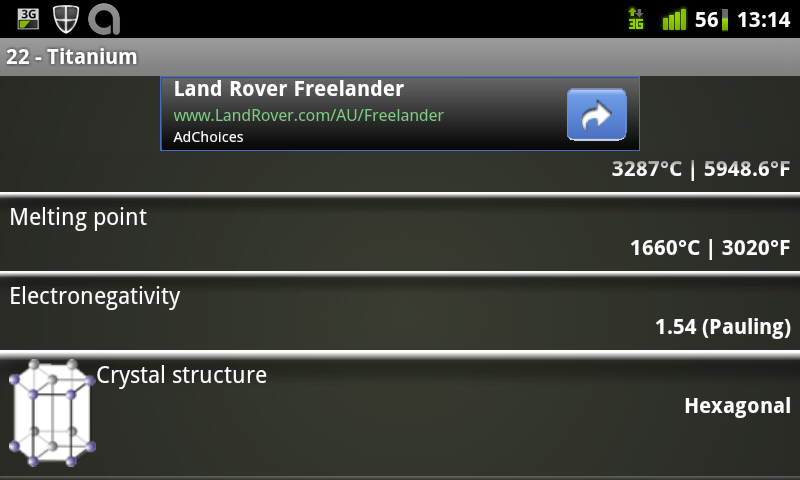
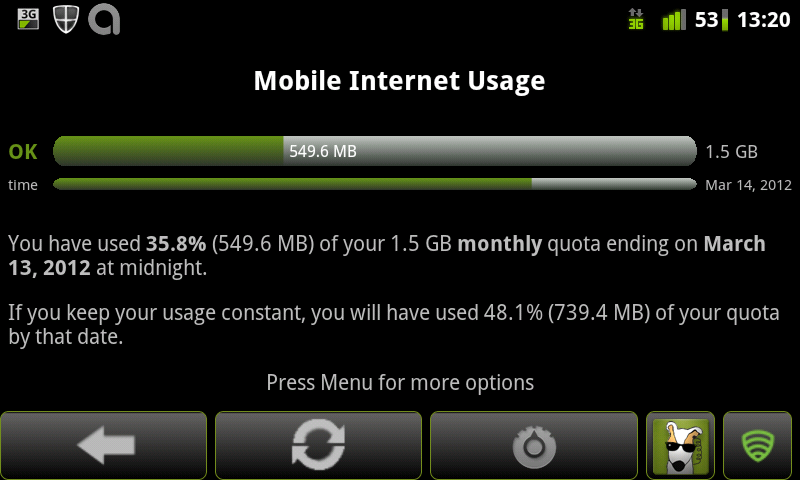
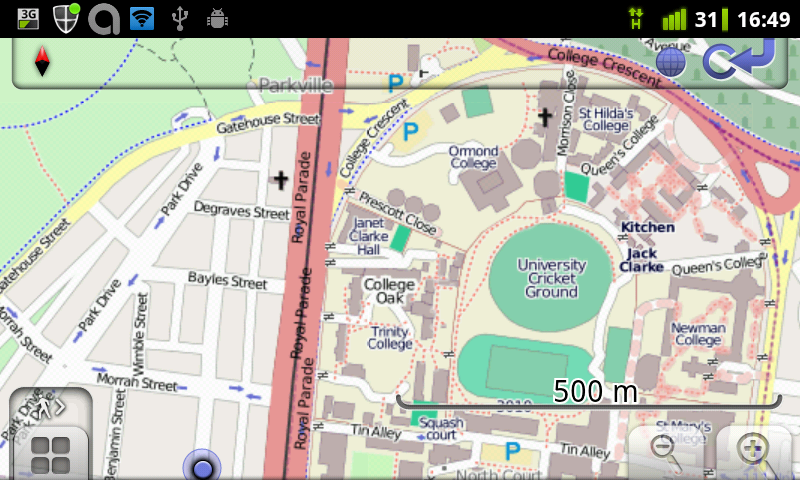
I gave a brief introductory talk about Android at this month s LUV meeting. Here are the slides with a brief description. All the screen-shots were made on a Samsung Galaxy S running Cyanogenmod version 7.1 [1] (Android version 2.3.7). With that build of Cyanogenmod you can press the power button for about 1.5 seconds to get a menu which gives an option to take a screen shot. The aim of the talk was to give an overview of what Android can do. I also gave some random commentary about Android such as explaining why it doesn t make a good phone. Most of the pictures in this post have links to the Android applications in question. Essential and Important Apps picture of root shell access running df I started by explaining why having root access to your system is really important, including the issue of backing up an Android phone [2]. Cyanogenmod includes a terminal program which allows you to run su - . Running a shell as root isn t generally that useful, what you really want is to be able to run programs such as Titanium Backup which can only work properly if given root access. When you run an OS that allows root access you can run su - at a terminal prompt and you can also have an application use a GUI to request root access. I recommend rooting and modding an Android phone immediately after buying it. However that takes some time which is somewhat equivalent to money and is a significant hidden cost to purchasing an Android phone. picture of 3g watchdog bandwidth monitor The business models of telephone companies seem to involve hidding users for unexpected fees and extra fees for excess bandwidth can be really expensive. 3G Watchdog is one app that can monitor bandwidth and disable data transfers if too much is used. Onavo is an alternative that allows tracking data use on a per-application basis, but it only runs on Android 2.3.x while 3G Watchdog works on Android 2.1. Official EBay app searching for Samsung Android phones EBay has an official app which is handy for searching for items. So far I ve only used it to get price estimates and have used a PC for buying. K9 viewing my SE Linux mailing list email K9 seems to be the best MUA for Android. The MUA that ships with Android 2.1 isn t nearly as good and K9 is good enough that I didn t even bother testing the MUA from Cyanogenmod. The above picture shows a list of mail in my SE Linux folder. graph by opticron grapher The Opticron Grapher is a good graphing calculator. I won t claim it s the best because I didn t seriously test such programs, but for the basic tests I ve done it has worked well. Google map of LUV location The Google Maps client comes with every Android system, the above shows the location of the LUV meeting. Open Street Map location of the LUV meeting Osmand is an Android client for the Open Street Map project. Here is the web site for the Open Street Map project [3]. One significant advantage of OSM over the Google Maps is that OSM is free, the data is all contributed by users like Wikipedia. Another significant advantage is that you can download as much data as you need to your phone, for example the entire dataset for Australia is about 200M. Storing 200M of data on your phone is no big deal when you consider the availability of phones with more than 16G of storage and the ability to use a map when offline is a real benefit. So far I ve used Osmand while waiting for a train at an underground station and I plan to use it to track my progress the next time I m on a cruise. serval mesh networking and VOIP Serval is a mesh networking application for Android that supports VOIP phone calls and distributing messages and files. It s designed to be used in disaster areas, but there are lots of other potential uses of the technology. The Serval Project blog has an article about the presentation they gave at LCA 2012 [4]. periodic table
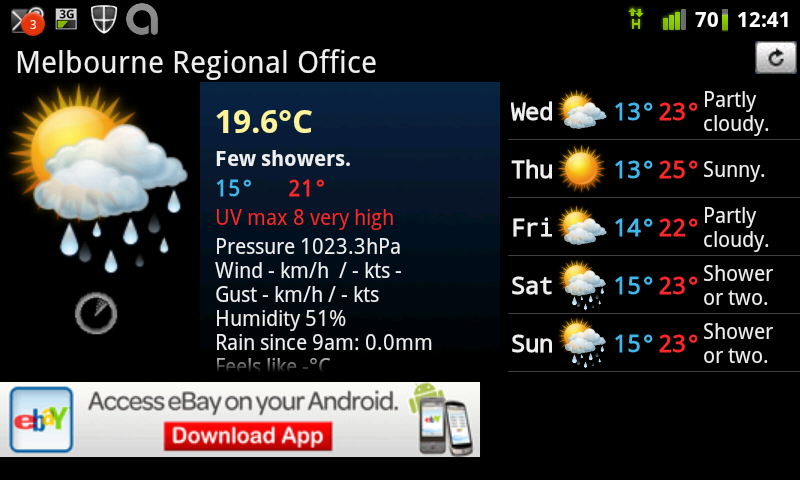
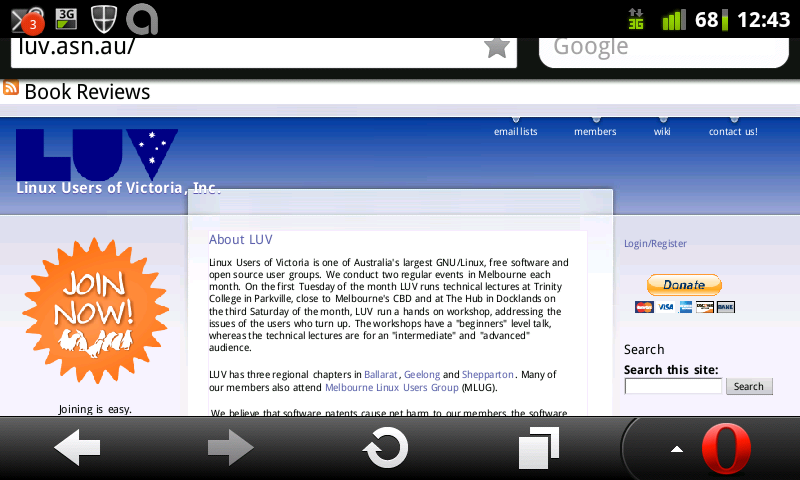
details about Titanium Periodic Droid is my favorite Periodic Table viewing program. tomfusion Au Weather forecast app The Tomfusion AU Weather forecast app seemed to be better than the one from the BoM last time I checked. It s probably the best weather app for Australia. screen-shot of LUV web site
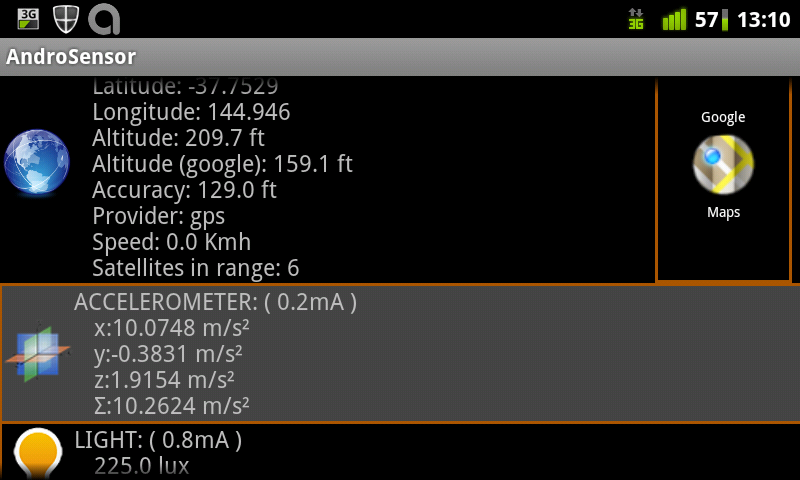
LUV web site zoomed in The Opera Mini browser is often faster than other browsers because it uses a compressing proxy run by Opera. It s not so good for privacy though LUV page on Wikipedia I have been using Wapedia for browsing Wikipedia. Since giving the talk I discovered the Official Wikipedia browser from the Wikimedia foundation [5] which is a better fit for my needs and I ve uninstalled Wapedia. As an aside modern phones have 16G of storage or more and could easily have a copy of the entire English text of Wikipedia on internal storage. It would be good if someone like Jason King (who is known for work on stand-alone DVD images for Wikipedia) was to write an Android program to do this. Handy Apps Androsensor showing GPS, accelleration, and light intensity
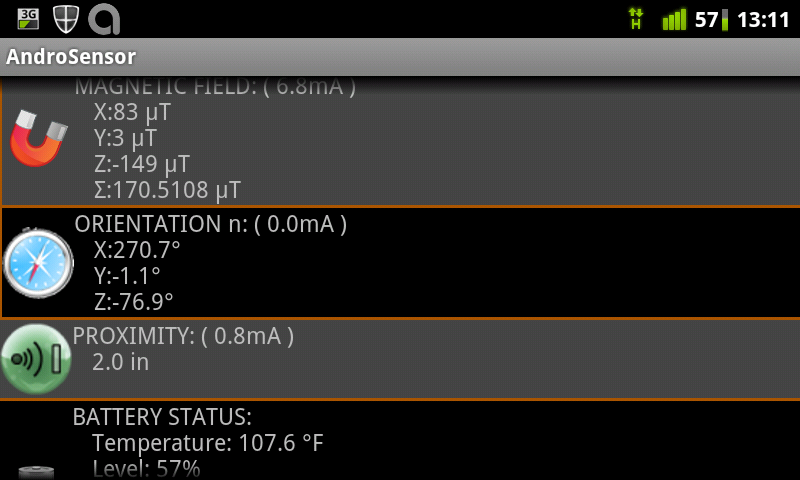
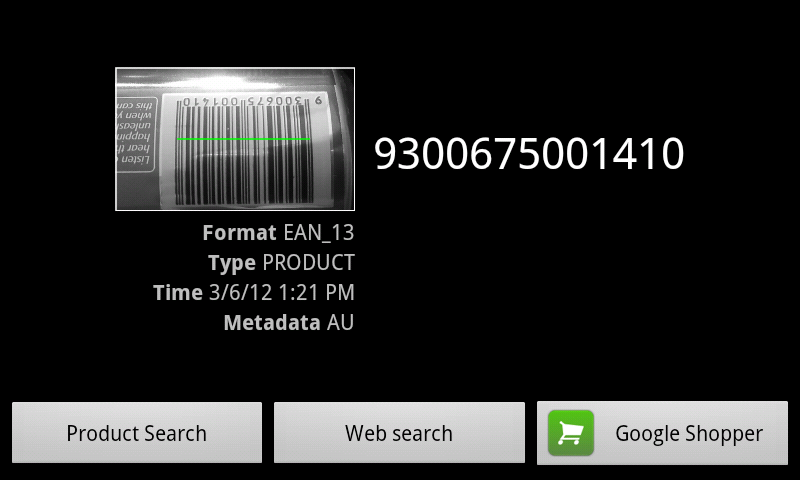
Androsensor showing magnetic field, orientation, and battery Androsensor is a program to display output from most (all?) of the sensors on your phone. The results aren t as accurate as one would hope, for example Earth s gravity is 9.81m/s^2 not the 10.26m/s^2 my phone registered. But they are a useful indication. picture of Coke can, scanning the barcode
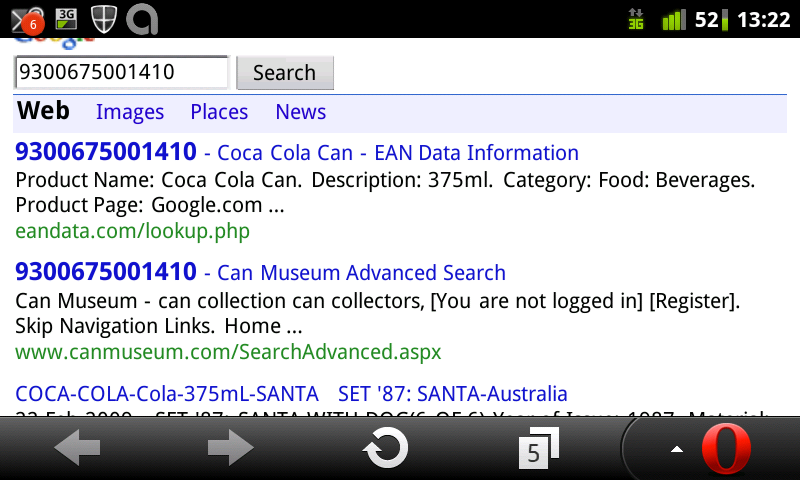
Google search on Coke can barcode
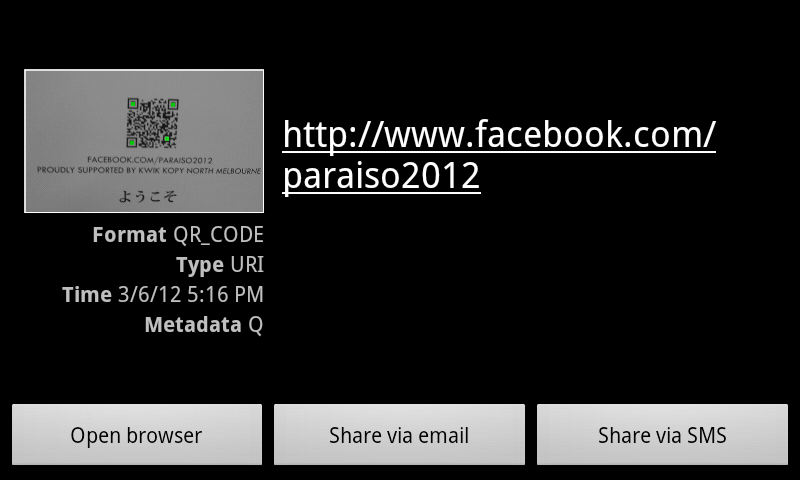
QR Code lookup of Facebook page The Zxing Barcode scanner is one of many programs that will scan barcodes with the camera in an Android phone. It can launch a Google search on a product code or open a URL from a
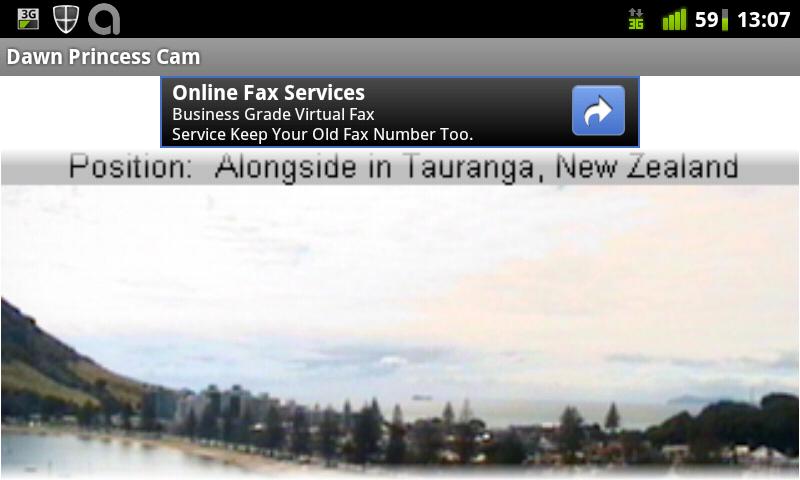
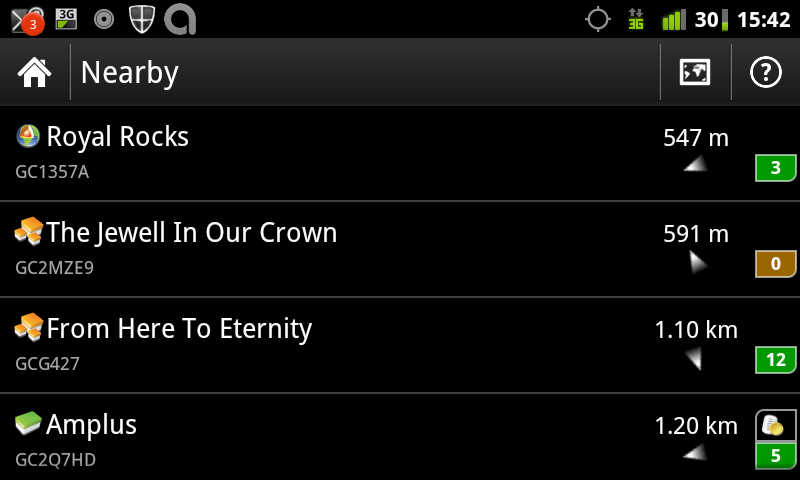
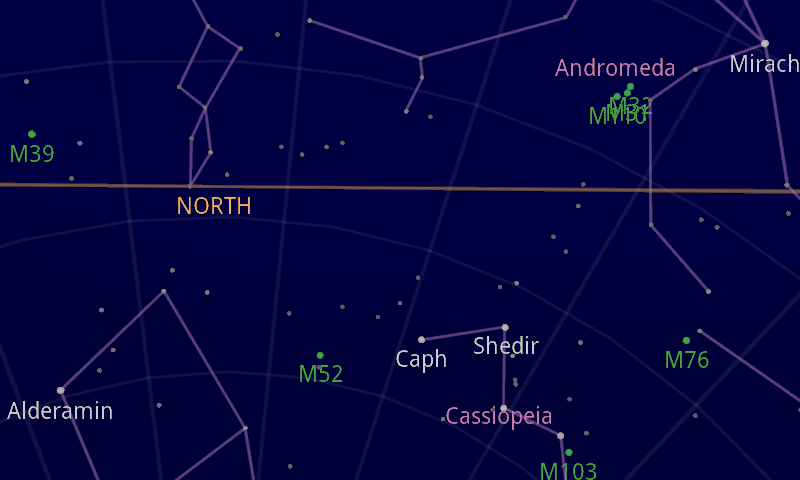
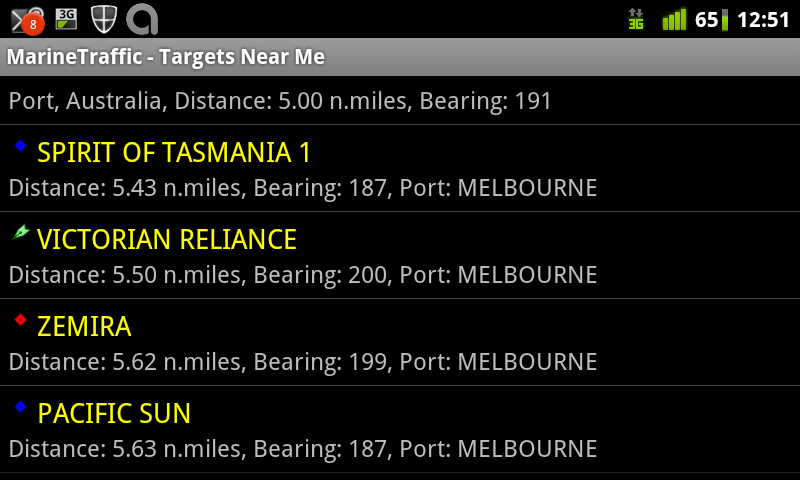
QR Code. The above pictures show it scanning a Coke can (the can and other background was displayed on the full screen before the screen capture program activated), doing a Google search on the can barcode, and looking up a QR code that was on an advertisment outside the LUV venue. picture from the bridge of the Dawn Princess in Tauranga NZ Cruise Cams allows you to download pictures from cruise ships. Some cruise ships have several cameras on different parts of the ship uploading pictures regularly so that people around the world can see what s happening. list of geo-caches near the park where I prepared most of my notes The c:geo opensource program allows you to get information on Geocaches and see a compass or map showing the location. This program has been getting an increasing number of features to do everything you might want to do related to Geocaching. The above picture shows some caches that are close to where I made the screen-shot, in a park a couple of Km from the meeting location. picture of Google Sky Map in the direction of Andromeda The Google Sky map uses augmented reality techniques to display stars in the direction that your phone is pointing along with their names and the names of the constellations. Marine Traffic showing ships near me
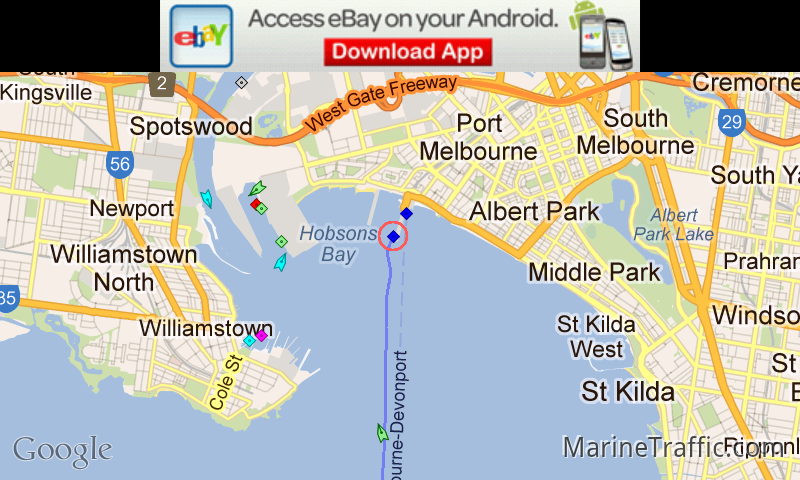
Marine Traffic showing the Pacific Sun highlighted on a Google Map
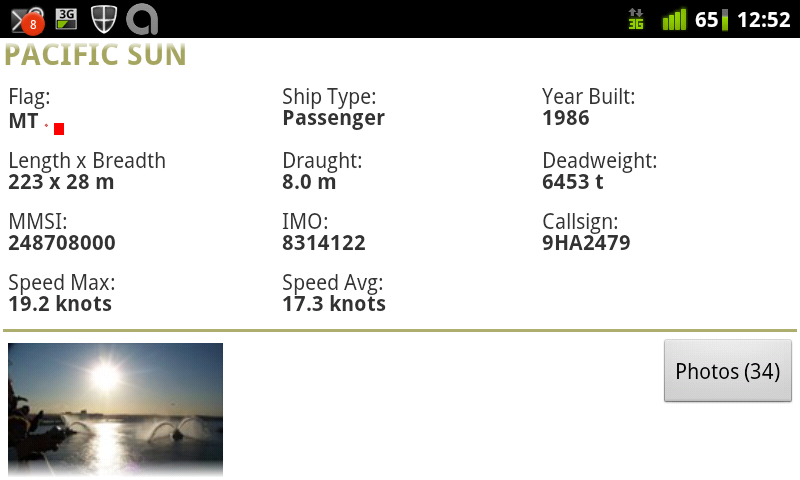
Marine Traffic showing details of the Pacific Sun
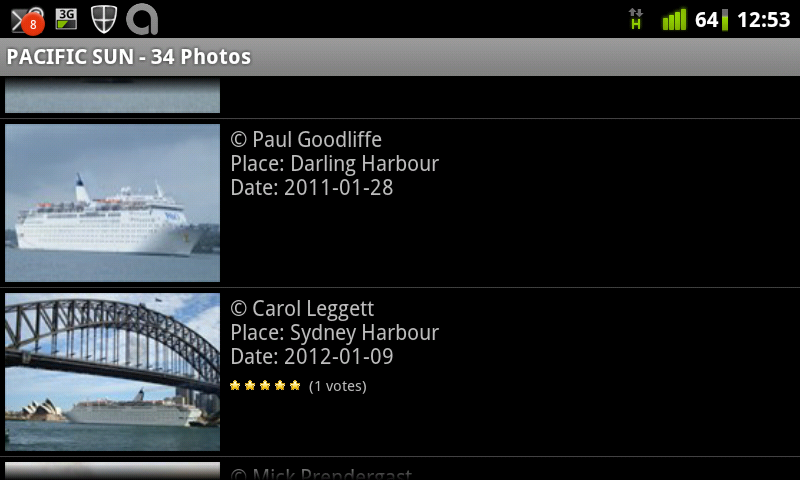
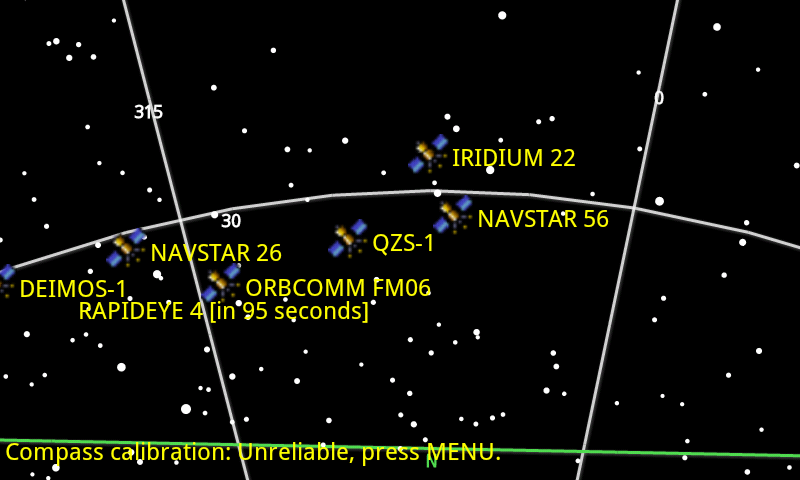
Photos of the Pacific sun taken by fans and shown by Marine Traffic The Marine Traffic program shows the locations of ships as well as lots of information about them. The above pictures show me discovering that the Pacific Sun was nearby, viewing it s location on Google Maps, seeing the details, and then viewing fan pictures. The developer s web site allows viewing all the same data without an Android phone [6]. Anyone can join the project by buying an Automatic Identification System (AIS) receiver and configuring a PC to take data from AIS and send it to the MarineTraffic.com servers. As an aside they seem to be missing coverage in western Victoria, so it would be good if someone near Apollo Bay or Warrnambool could install an AIS receiver and help out. Satellite map from Satellite AR Satellite AR uses augmented reality to show the location of satellites and other things in spare. Unfortunately the screen capture process turned off the camera as I had a sign advertising fast food positioned in an amusing location in the background. Shipmate overview of Dawn Princess
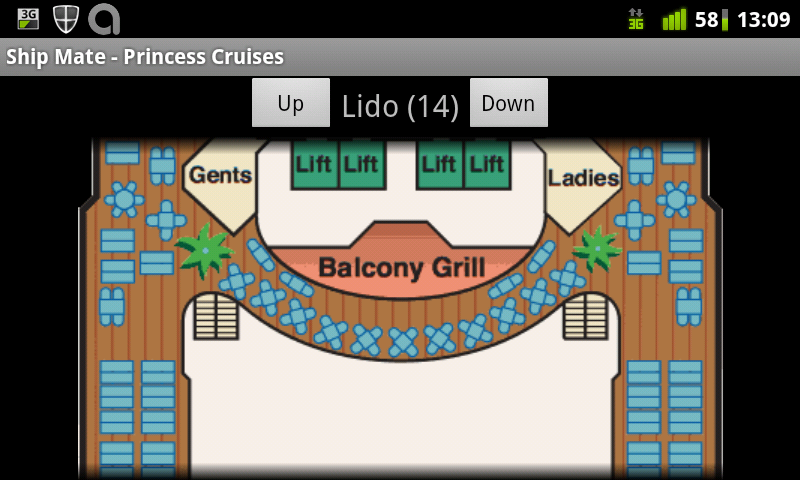
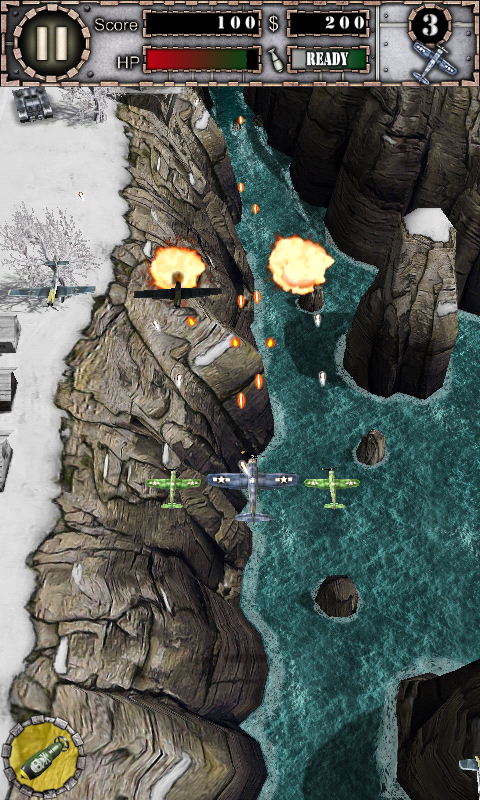
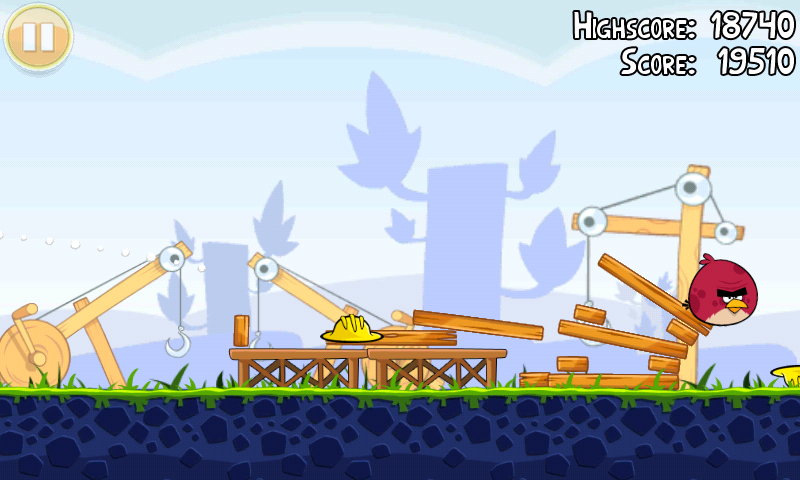
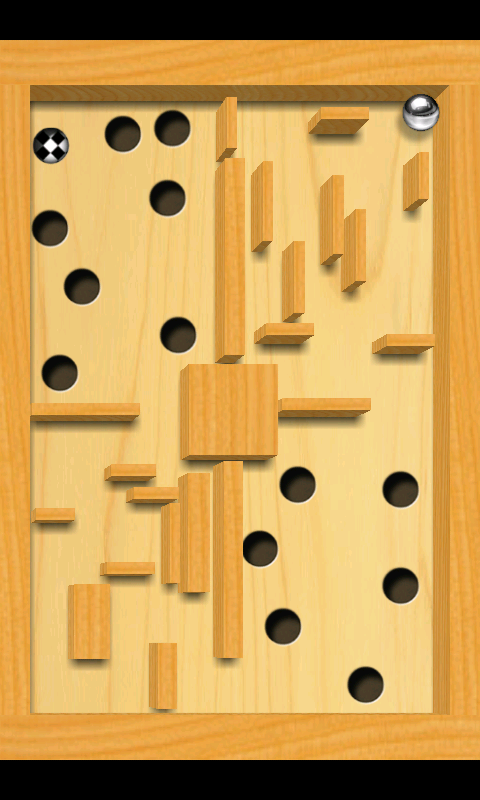
Shipmate map of Dawn Princess Shipmate publishes a set of programs giving information on cruise ships, they have one program for each cruise line. Above is the program for the Princess cruise line, the above pictures give information on the Dawn Princess. Unfortunately the program wasn t usable without net access when I tried to use it on a cruise ship. Games Air Attack HD game, clone of 1942 Air Attack HD is an entertaining game that demonstrates the capability of Android phones to run action games. Like many Android games it has a free version and paid versions if you want more. picture of Angry Birds Angry Birds is one of the most well known games for touch-screen devices. It has also spawned a huge line of merchandise. Labyrinth Lite
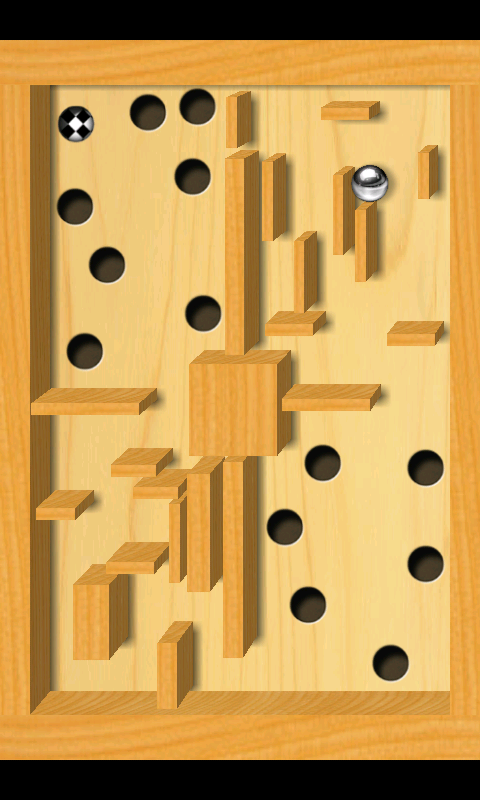
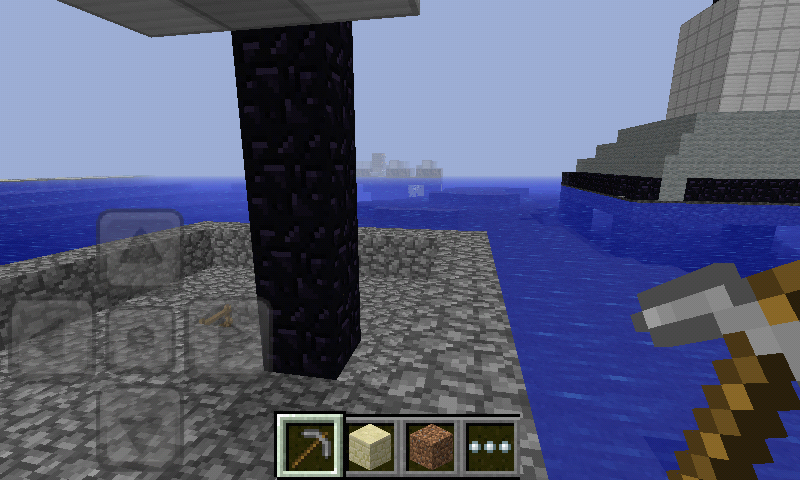
Labyrinth Lite from a different angle Labyrinth Lite is one of the many Android games based on the old mechanical game where you tilt a toy to roll a ball-bearing through a maze. It s free and is better than most of the free games in that genre. Minecraft Pocket Edtion Minecraft Pocket Edition allows you to play Minecraft on your phone. The demo version doesn t allow saving the game, you have to buy the game for about $5 if you want to do that. It also lacked the full features of the game last time I checked, it didn t have monsters. Paradise Island overview
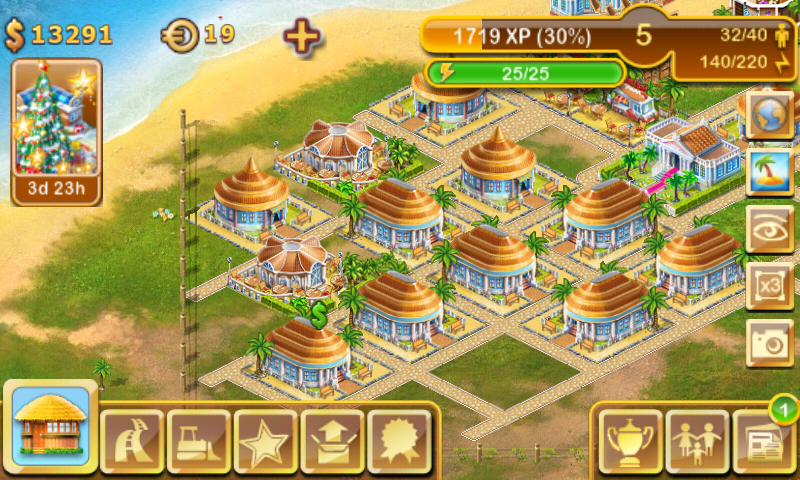
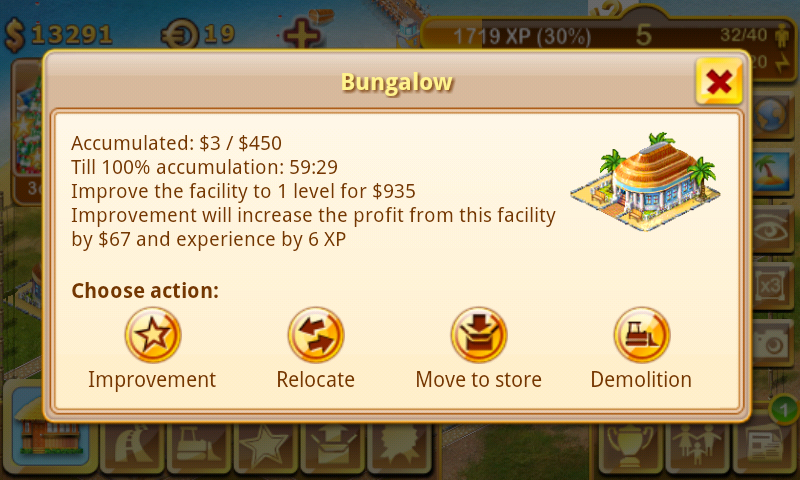
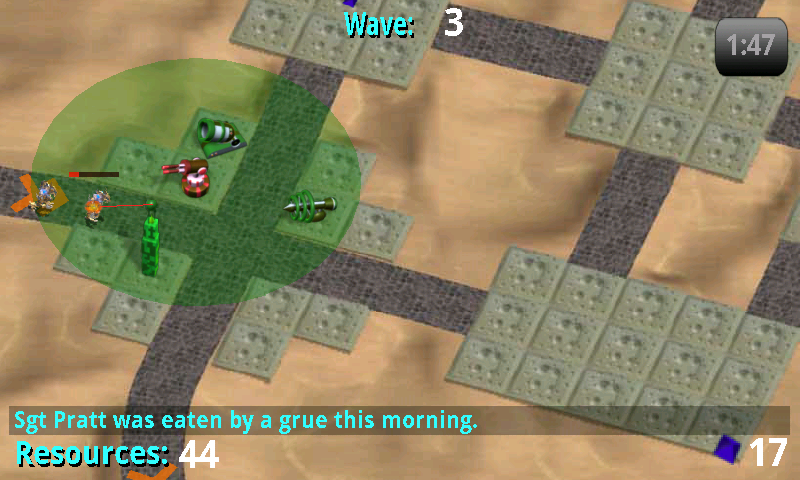
Paradise Island details of Bungalow Paradise Island is one of many business simulation games for Android. It s more playable than most and has very detailed graphics, but the down-side is that it s a memory hog and will crash if you don t have enough RAM. It s one of the games that are free to download but encourage you to pay money to level up, for some players it s probably a very expensive game. Tower Raiders 2, Pratt was eaten by a Grue Tower Raiders 2 is one of the better tower defense games for Android. Related posts:
  1. Choosing an Android Phone My phone contract ends in a few months, so I m...
  2. Galaxy S vs Xperia X10 and Android Network Access Galaxy S Review I ve just been given an indefinite loan...
  3. Standardising Android Don Marti wrote an amusing post about the lack of...

Dirk Eddelbuettel: R / Finance 2012 Open for Registration

The annoucement below just went to the R-SIG-Finance list. More information is as usual the the R / Finance page:
Now open for registrations: R / Finance 2012: Applied Finance with R
May 11 and 12, 2012
Chicago, IL, USA
The registration for R/Finance 2012 -- which will take place May 11 and 12 in Chicago -- is NOW OPEN! Building on the success of the three previous conferences in 2009, 2010, and 2011, we expect more than 250 attendees from around the world. R users from industry, academia, and government will join 40+ presenters covering all areas of finance with R. This year's conference will start earlier in the day on Friday, to accommodate the tremendous line up of speakers for 2012, as well as to provide more time between talks for networking. We are very excited about the four keynotes by Paul Gilbert, Blair Hull, Rob McCulloch, and Simon Urbanek. The main agenda includes nineteen full presentations and eighteen shorter "lightning talks". We are also excited to offer six optional pre-conference seminars on Friday morning. Once again, we are hosting the R/Finance conference dinner on Friday evening, where you can continue conversations while dining and drinking atop a West Loop restaurant overlooking the Chicago skyline. More details of the agenda are available at:
http://www.RinFinance.com/agenda/
Registration information is available at
http://www.RinFinance.com/register/
and can also be directly accessed by going to
http://www.regonline.com/RFinance2012
On behalf of the committee and sponsors, we look forward to seeing you in Chicago!
Gib Bassett, Peter Carl, Dirk Eddelbuettel, Brian Peterson,
Dale Rosenthal, Jeffrey Ryan, Joshua Ulrich
Our 2012 Sponsors:
International Center for Futures and Derivatives at UIC Revolution Analytics
Sybase
MS-Computational Finance at University of Washington Google
lemnica
OpenGamma
OneTick
RStudio
Tick Data
See you in Chicago in May!!

19 March 2012

Mark Brown: regulator updates in 3.3

Linux 3.3 was released today. This was the biggest release for the regulator API for quite some time thanks to the contribution of device tree bindings for the API by Rajendra Nayak, the first substantial framework update for a long time, but otherwise was fairly quiet:

Mark Brown: regmap updates in 3.3

After the rush of new features in version 3.2 this has been a fairly quiet cycle for the regmap API, the main change being the wider usage by drivers. In terms of development of the subsystem itself this release sees:
  • Introduction of a generic interrupt controller for regmap based devices, this is already used by a few drivers with more coming.
  • Support for 10 bit register 14 bit value devices.
  • Removal of the indexed cache type devices which would have used it should use rbtree instead. If anything the rbtree cache is expected to be faster for small devices as where registers are grouped together into blocks it will usually be cheaper to search the rbtree.
  • Some improvements to the coverage of the tracepoints..
  • Diagnostics showing the number and size of nodes in an rbtree cache.

18 March 2012

Aurelien Jarno: 10 years ago

Date: Mon, 18 Mar 2002 18:22:10 +0000
From: James Troup <troup@samosa.debian.org>
To: Aurelien Jarno <aurelien@aurel32.net>
Cc: da-manager@debian.org
Subject: New Debian maintainer Aurelien Jarno [ This is a long (automatically-generated) mail, but it contains
important information, please read it all carefully. ] Dear Aurelien Jarno! An account has been created for you on developer-accessible machines with username aurel32 . The password for this account can be found encrypted with your PGP or GPG key and appended to this message. A list of machines available to Debian developers can be found at <URL:http://db.debian.org/machines.cgi>. Please take a minute now to familiarize yourself with the Debian Machine Usage Policy, available at <URL:http://www.debian.org/devel/dmup> You have been subscribed to the debian-private mailing list as <aurel32@debian.org>. Please respect the privacy of that list and don t forward mail from it elsewhere. E-mail to <aurel32@debian.org> will be forwarded to <aurelien@aurel32.net>. To change this, please see <URL:http://db.debian.org/forward.html> Also, please subscribe to debian-devel-announce, if you haven t done so already. We strongly suggest that you use your aurel32@debian.org address for the maintainer field in your packages, because that one will be valid as long as you are a Debian developer, even if you change jobs, leave university or change Internet Service providers. If you do so, please add that address to your PGP/GPG key(s) (using gpg edit-key YOUR USER ID ) and send it to the keyring server at keyring.debian.org with gpg keyserver keyring.debian.org send-keys YOUR USER ID . You can find more information useful to developers at <URL:http://www.debian.org/devel/> (in particular, see the subsection titled Debian Developer s reference ). We suggest that you subscribe to debian-mentors@lists.debian.org. This list is for new maintainers who seek help with initial packaging and other developer-related issues. Those who prefer one-on-one help can also post to the list, and an experienced developer may volunteer to help you. You can get online help on IRC, too, if you join the channel #debian-devel on irc.debian.org. Take a look at the support section on www.debian.org in order to find out more information. You should have read these documents before working on your packages. o The Debian Social Contract
<URL:http://www.debian.org/social_contract.html> o The Debian Policy Manual
<URL:http://www.debian.org/doc/debian-policy/> If you have some spare time and want to contribute it to Debian you may wish to take a look at the Work-Needing and Prospective Packages for Debian GNU/Linux also known as WNPP that can be found at <URL:http://www.debian.org/devel/wnpp/> If you plan to make a Debian package from a not yet packaged piece of software you *must* announce your intention on the debian-devel mailing list to make sure nobody else is working on them. The machine ftp-master.debian.org is our main archive server. Every uploaded package finds it s way there (except for Packages covered by US crypto laws which go to non-us.debian.org) eventually. master.debian.org is the home of our bug tracking system. Project web pages and CVS archives are hosted on klecker.debian.org (aka cvs/www.debian.org), klecker is also our general shell server. Web pages should be placed in public_html on klecker and refered to by http://people.debian.org/~aurel32 You should use ssh to log into the machines instead of regular telnet or rlogin. Our LDAP directory is able to share ssh RSA keys among machines, please see <URL:http://db.debian.org/doc-mail.html> Otherwise when you first login a ~/.ssh directory will be created with the appropriate permissions. Please be aware of the security implications of using RSA authentication and ssh agents. Finally, please take a minute to visit <URL:http://db.debian.org/>.
Login using the password information appended to this email, and update your personal information. The information is used to maintain your accounts on various Debian machines, and also to allow other developers and general users to find out more about you. Many of the fields are only visible to other registered Debian developers. This is also the only way to change your password. The passwd program does not yet work. Welcome to the project!
The Debian New Maintainer Team

Gustavo Franco: Debian testing (wheezy) keyboardless install

I couldn't find an end-to-end document online about this just bits and pieces here and there. Let me describe how to install Debian testing (wheezy) without a keyboard using an USB flash drive and ssh.


I've got an HP Microserver a month or so ago and this is the step by step of my second install. The first one was also keyboardless but didn't involve an USB flash drive to bootstrap. I've used tftpd and dhcp from my laptop, but forgot to capture the notes to make a blog post. Shame on me.

Here's what you need:
The last two requirements are optional for hardcore preseeders. If you don't know what I mean. You aren't one of them. :)

Here's the step by step to install using SSH:
At this point you have all that you need to do a regular install using an USB flash drive and it's kinda of well documented. Well, we still need to change it to make it work without a keyboard and give you the ability to ssh into the installer.

Create a preseed.cfg in the root directory of the USB flash drive containing the following:
d-i netcfg/get_hostname string HOSTNAME
d-i netcfg/get_domain string DOMAIN
d-i anna/choose_modules string network-console
d-i network-console/password password INSERT_A_PASSWORD_HERE
d-i network-console/password-again password INSERT_A_PASSWORD_HERE

Edit syslinux.cfg in the root directory of the USB flash drive to look like this:
default netinst
prompt 0
timeout 5
label netinst
menu label netinst
 kernel linux
 append auto=true vga=normal file=/preseed.cfg initrd=initrd.gz priority=critical
My wishlist to the d-i hackers out there:
  • A boot-ssh.img.gz with the syslinux.cfg and preeseed.cfg above. In this case, it would be much more trivial to document in the installer manual how to use such a great feature.

Andrew Pollock: [life] Guantanamo: My Journey

I first learned that David Hicks had written an autobiography when I saw some press coverage of there being an attempt by the Australian Government to ban the sale of it, so I asked my sister if she could get me a copy for my birthday before any ban happened. The book doesn't appear to be available on Amazon. I sat down and tried to read it almost immediately, but at the time found his writing style to be rather inarticulate, so I put the book down for a month or so. When I next had a platelet donation to make, I took it along with me, and forced myself to read it for duration of the donation. On the second reading, I managed to engage with the book, and from that point on, once I made it through his early years in that initial forced reading session, it ended up being quite enthralling. I plugged my way through the 456 pages in a bit over a month I guess. We'll never truly know the full story of David Hicks, because I'm sure that unless there's some sort of inquiry (and even then, there's multiple country's governments involved), the full story won't come out. I was always sympathetic to Hicks' plight, since I don't believe that anyone should be held without due process let alone for anywhere near as long as he was. Certainly, the way the book reads, Hicks comes across as a very young, naive, but principled individual. Like many Australians, he got the travel bug, and by way of it, got to interact with some different cultures, which awakened a hunger for social justice in him (at least that's my interpretation of his portrayal). I guess I have a different mental image of torture than Hicks did, because I didn't really find any incidences of what I'd consider torture in his story. There was plenty of despicable, inhumane treatment though, so I can see how the line might get blurry, particularly if you're the one experiencing it. Specifically on the (mis)treatment of the detainees: it was pretty bad, based on the book. I'm surprised there haven't been more whistle blowers that have come out. I can't believe that the many soldiers who were stationed there could treat detainees the way Hicks says they were treated and then can look themselves in the mirror. The ICRC seemed well apprised of the detainees conditions (since they seemed to have the most access to them of any non-military people). I don't know what confidentiality is imposed on them in return for that access, though. The fact that he's able to string a sentence together at all after the treatment he describes for the length of time he received it, I think is pretty amazing. I couldn't imagine having to endure what he says he went through. I did feel quite appalled by my own country's complete disregard for his plight, and similarly in the way the US Government treated these detainees for as long as they did. Given there are still 171 detainees in Guantanamo today, it makes me wonder what the conditions and treatment are like there now. It certainly seems to have fallen out of the mainstream press. Overall, not the most well written book, but a fascinating and shocking account of what happened to one person. I think Hicks should be congratulated for the courage to relive his experiences to get them down on paper, and Random House should also be congratulated for publishing his work, which I'm sure put them under some political pressure. I have no idea how well the book has sold, or how widely it has been read, but I certainly recommend it.

Gregor Herrmann: RC bugs 2012/10-11

since I was travelling in the pre-ultimate week for a few days, there was no report about my RC bugs fixing activities. so here we go with an overview covering two weeks:

Soeren Sonnenburg: Shogun got accepted at Google Summer of Code 2012

SHOGUN has been accepted for Google Summer of Code 2012. SHOGUN is a machine learning toolbox, which is designed for unified large-scale learning for a broad range of feature types and learning settings. It offers a considerable number of machine learning models such as support vector machines for classification and regression, hidden Markov models, multiple kernel learning, linear discriminant analysis, linear programming machines, and perceptrons. Most of the specific algorithms are able to deal with several different data classes, including dense and sparse vectors and sequences using floating point or discrete data types. We have used this toolbox in several applications from computational biology, some of them coming with no less than 10 million training examples and others with 7 billion test examples. With more than a thousand installations worldwide, SHOGUN is already widely adopted in the machine learning community and beyond. SHOGUN is implemented in C++ and interfaces to all important languages like MATLAB, R, Octave, Python, Lua, Java, C#, Ruby and has a stand-alone command line interface. The source code is freely available under the GNU General Public License, Version 3 at http://www.shogun-toolbox.org. During Summer of Code 2012 we are looking to extend the library in three different ways:
  1. Improving accessibility to shogun by developing improving i/o support (more file formats) and mloss.org/mldata.org integration.
  2. Framework improvements (frameworks for regression, multiclass, structured output problems, quadratic progamming solvers).
  3. Integration of existing and new machine algorithms.
Check out our ideas list and if you are a talented student, consider applying!

17 March 2012

Matthew Garrett: More ways for firmware to screw you

Some of my recent time has been devoted to making our boot media more Mac friendly, which has entailed rather a lot of rebooting. This would have been fine, if tedious, except that some number of boots would fall over with either a clearly impossible kernel panic or userspace segfaulting in places that made no sense. Something was clearly wrong. Crashes that shouldn't happen are generally an indication of memory corruption. The question is how that corruption is being triggered. Hunting that down wasn't terribly easy.

My first thought was that we were possibly managing to load the kernel over a region used by UEFI code. UEFI defines two types of code - boot services and runtime services. While runtime services code and data must be preserved by the OS, in theory boot services code and data is available to the OS once the firmware has exited. In practice, that's not true. It seemed entirely possible that the kernel might be ending up on top of some of that boot services code or data and getting trodden on. Grub now has code to avoid putting the kernel on boot services, so testing the latest code seemed like a good plan. But no, crashes still happened.

That pretty much ruled out the bootloader. My next thought was that executing some of the firmware code was triggering a write to some other memory that contained the kernel. Josh Boyer suggested the next trick, which was to try marking the kernel read-only to see whether anything was hitting it. x86 lets you mark pages as read-only - any attempt to write to them should take a fault. UEFI functions are executed in the context of the kernel, so share the same page tables. That let me rule this out, since everything still went just as wrong and I wasn't taking an extra fault first.

However, at this point I was reasonably happy that it wasn't the kernel itself being overwritten - faults were occurring in userspace code as well. That was a pretty strong indication that what was happening was continuing to happen once userspace had started, so it wasn't a direct response to a firmware call. I made sure of that by stubbing out all the calls that could be triggered after kernel initialisation, and saw the same failures. Once all attempts to be clever have failed, it's time to just start using brute force. The kernel lets you reserve areas of RAM by passing arguments like memmap=0xlength$0xstart to block length bytes starting at start from being used. It took a while, but I finally found a 256MB range that made a difference - reserving it resulted in the machine booting reliably, letting the OS use it resulted in occasional crashes.

Definite progress. Comparing that memory range to the EFI memory map was helpful. There were several blocks of UEFI boot services data present there, which really seemed like too much of a coincidence. By reserving each of them in turn, I'd traced it down to a single 31MB region of boot service data - that is, memory reserved by the firmware for use by the UEFI boot services. Per spec, this is available to the OS once the boot environment has been exited. Nothing other than the OS should be touching this after boot, but something clearly was. Tracking down what was far easier than I expected, although the first attempt was a failure. Setting it read-only should have triggered a fault, but didn't. That was rather confusing. But, rather than give up, I patched the kernel to fill the region with 0xff at kernel init. Then I booted the system, read it back and looked for values that weren't 0xff. I got this:
00000000  ff ff ff ff ff ff ff ff  ff ff ff ff ff ff ff ff   ................ 
*
001568a0  ff ff ff ff ff ff ff ff  ff ff ff ff 84 00 00 00   ................ 
001568b0  00 20 a7 ac 46 00 00 00  00 00 00 00 00 00 06 01   . ..F........... 
001568c0  c2 0b 0c 00 ff ff ff ff  ff ff ff ff ff ff ff ff   ................ 
001568d0  ff ff 0a 04 f0 03 82 0d  40 00 00 00 ff ff ff ff   ........@....... 
001568e0  ff ff 00 21 00 36 9a 80  ff ff ff ff ff ff 00 7e   ...!.6.........~ 
001568f0  00 09 43 48 41 2d 47 75  65 73 74 01 04 02 04 0b   ..CHA-Guest..... 
00156900  16 32 08 0c 12 18 24 30  48 60 6c 2d 1a 0e 18 1a   .2....$0H l-.... 
00156910  ff ff 00 00 00 00 00 00  00 00 00 00 00 00 00 00   ................ 
00156920  00 00 00 00 00 00 00 dd  09 00 10 18 02 00 10 01   ................ 
00156930  00 00 dd 1e 00 90 4c 33  0e 18 1a ff ff 00 00 00   ......L3........ 
00156940  00 00 00 00 00 00 00 00  00 00 00 00 00 00 00 00   ................ 
00156950  00 00 bd ea f8 b3 ff ff  ff ff ff ff ff ff ff ff   ................ 
00156960  ff ff ff ff ff ff ff ff  ff ff ff ff ff ff ff ff   ................ 
*
022fb000
That's a lot of 0xffs (around 31MB of them) with one small section that contains an 802.11 probe packet with the SSID of the hospital across the road from my house. Apple support network booting off wireless networks. It seems that the firmware brought up the wireless card, associated with this network (it's the only public one nearby) and then left the card DMAing packets into RAM. The read-only page attribute only applies to CPU-initiated accesses, so it could do this without triggering a page fault. It also explained why it was so random - whether memory corruption occurred would depend on whether a packet appeared between that memory being used by the OS and the kernel reinitialising the wireless card. It certainly explains why I couldn't reproduce it when I left the machine repeatedly rebooting on the bus home.

How do we fix this? Unsure. With luck disconnecting the UEFI driver in the bootloader should quiesce the hardware, but without testing I'm not sure of that yet. For now it's just another example of firmware managing to break expectations in deeply strange ways.

comment count unavailable comments

16 March 2012

Matt Brown: Kindle Reading Stats

I ve written before about my initial investigations into the Kindle, and I ve learnt much more about the software and how it communicates with the Amazon servers since then, but it all requires detailed technical explanation which I can never seem to find the motivation to write down. Extracting reading data out of the system log files is however comparatively simple. I m a big fan of measurement and data so my motivation and goal for the Kindle log files was to see if I could extract some useful information about my Kindle use and reading patterns. In particular, I m interested in tracking my pace of reading, and how much time I spend reading over time. You ll recall from the previous post that the Kindle keeps a fairly detailed syslog containing many events, including power state changes, and changes in the Booklet software system including opening and closing books and position information. You can eyeball any one of those logfiles and understand what is going on fairly quickly, so the analysis scripts are at the core just a set of regexps to extract the relevant lines and a small bit of logic to link them together and calculate time spent in each state/book. You can find the scripts on Github: https://github.com/mattbnz/kindle-utils Of course, they re not quite that simple. The Kindle doesn t seem to have a proper hardware clock (or mine has a broken hardware clock). My Kindle comes back from every reboot thinking it s either at the epoch or somewhere in the middle of 2010, the time doesn t get corrected until it can find a network connection and ping an Amazon server for an update, so if you have the network disabled it might be many days or weeks of reading before the system time is updated to reality. Once it has a network connection it uses the MCC reported by the 3G modem to infer what timezone it should be in, and switches the system clock to local time. Unfortunately the log entries all look like this:
110703:193542 cvm[7908]: I TimezoneService:MCCChanged:mcc=310,old=GB,new=US:
110703:193542 cvm[7908]: I TimezoneService:TimeZoneChange:offset=-25200,zone=America/Los_Angeles,country=US:
110703:193542 cvm[7908]: I LipcService:EventArrived:source=com.lab126.wan,name=localTimeOffsetChanged,arg0=-25200,arg1=1309689302:
110703:193542 cvm[7908]: I TimezoneService:LTOChanged:time=1309689302000,lto=-25200000:
110703:183542 system: I wancontrol:pc:processing "pppstart"
110703:193542 cvm[7908]: I LipcService:EventArrived:source=com.lab126.wan,name=dataStateChanged,arg0=2,arg1=:
110703:183542 cvm[7908]: I ConnectionService:LipcEventArrived:source=com.lab126.cmd,name=intfPropertiesChanged,arg0=
,arg1=wan:
110703:183542 cvm[7908]: W ConnectionService:UnhandledLipcEvent:event=intfPropertiesChanged:
110703:193542 wifid[2486]: I wmgr:event:handleWpasupNotify(<2>CTRL-EVENT-DISCONNECTED), state=Searching:
110703:113542 wifid[2486]: I spectator:conn-assoc-fail:t=374931.469106, bssid=00:00:00:00:00:00:
110703:113542 wifid[2486]: I sysev:dispatch:code=Conn failed:
110703:183542 cvm[7908]: I LipcService:EventArrived:source=com.lab126.wifid,name=cmConnectionFailed,arg0=Failed to connect to WiFi network,arg1=
:
Notice how there is no timezone information associated with the date/time information on each line. Worse still the different daemons are logging in at least 3 different timezones/DST offsets all interspersed within the same logfile. Argh!! So our simple script that just extracts a few regexps and links them together nearly doubles in size to handle the various time and date convolutions that the logs present. Really, the world should just use UTC everywhere. Life would be so much simpler. The end result is a script that spits out information like:

B000FC1PJI: Quicksilver: Read 1 times. Last Finished: Fri Mar 16 18:30:57 2012
- Tue Feb 21 11:06:24 2012 => Fri Mar 16 18:30:57 2012. Reading time 19 hours, 29 mins (p9 => p914)
... Read 51 books in total. 9 days, 2 hours, 29 mins of reading time
I haven t got to the point of actually calculating reading pace yet, but the necessary data is all there and I find the overall reading time stats interesting enough for now. If you have a jailbroken Kindle, I d love for you to have a play and let me know what you think. You ll probably find logs going back at least 2-3 weeks still on your Kindle to start with, and you can use the fetch-logs script to regularly pull them down to more permanent storage if you desire.

Michal &#268;iha&#345;: Weblate 0.7

Continuing at same pace (one release every two days), I can announce Weblate 0.7. The major change is built in full text search and displaying of context for currently translated message (either based on location in po file or by string similarity based on full text data). Full list of changes for 0.7: You can find more information about Weblate on it's website, the code is hosted on Github. If you are curious how it looks, you can try it out on demo server. You can login there with demo account using demo password or register your own user. Weblate is now also being used https://l10n.cihar.com/ as official translating service for phpMyAdmin, Gammu, Weblate itself and others.

Filed under: English Weblate 0 comments Flattr this!

Pablo Lorenzzoni: Windows Laptop with Debian Recovery Partition

I was playing with my new Laptop (a Philco 14E-P686WP) that comes with (argh!) Windows 7. I was gathering information in order to avoid surprises with regards to drivers and hardware-compatibility so I can proceed with the Debian installation By doing that with a new machine, I, usually, peek and poke everywhere, including the Recovery System. I was shocked to find out that this (argh) Windows 7 laptop has a bootable recovery partition loaded with a customized Debian just to run Partclone which installs a Windows factory image. I was about to take some pictures of the process, but I managed to find some in a forum post. Debian is being used to re-install (argh) Windows How sad is that! ;-)

15 March 2012

Debian Med: Bits from Debian Med team (Posted by Andreas Tille)

Hi,

in this bits:
  1. Debian Med Bug Squashing Advent Calendar 2011
  2. Anniversary of Debian Med
  3. Second Debian Med sprint (Southport, 27th-29th January 2012)
  4. Mentoring of Month (MoM)
  5. DDs who came to Debian because of Debian Med
  6. Future plans
  7. General lessons learned

Debian Med Bug Squashing Advent Calendar 2011In December last year Thorsten Alteholz has started a nice QA initiative which might be interesting for other teams next Advent. The Debian Med team was able to fix about 70 bugs in this time. Thanks to Thorsten for this nice piece of motivation and thanks to everybody who took part in the bug squashing.

Anniversary of Debian MedOn Mon, 7 Jan 2002 the Debian Med project was first officially announced. I submitted a short blog posting about this and perhaps you might like to see a long sequence of talks about this topic.

Second Debian Med sprint (Southport, 27th-29th January 2012)In end of January 2012 the Debian Med team has met to the second sprint. As last year I would call this a very successfull event and I would recommend other teams to instanciate such meetings as well. Feel free to read my more verbose report.

Mentoring of Month (MoM)I have started this project for the following reasons:
I made a short summary how the first MoM project worked (see at bottom).

DDs who came to Debian because of Debian MedAfter realising that several members of the Debian Med team finally became DDs I made a little survey to find out about their reasons to become DD / DM. I came to the conclusion that a Blend could be a nice entry point for people to join Debian because newcomers can identify themselves with a known topic (the scope of the Blend - in this case medicine and bioinformatics) first and learn Debian rules in a team with common interest. This perfectly fits my expectation which I had from the beginning 10 years ago and I would be very happy if other Blends would follow this example to be nice, inviting and try to *actively* ask people for cooperation (see some simple rules which I learned in this process below). In the teammetrics GSOC project some graphs were created where you can see the level of contribution of these people (and other team members).

Future plansCurrently some heavy work regarding bringing bibliographic references about packages straight into package information is going on. This topic is specifically interesting in Biology because programs are frequently connected to some publication about the methods used inside the code. This topic is as well relevant to Debian Science and DebiChem. Thanks to the patient work done by Charles Plessy we now have about 70 packages featuring debian/upstream files featuring bibliographic references and there is ongoing work to move these data to UDD to enable further usage. We are in the process of final polishing the format and finishing scripts for the import. If people are interested to join this effort this would be the right moment to raise their hand.

General lessons learned
  1. Do not let wait anybody who wants to do work.
  2. Newcomers are frequently shy - try to invite them kindly and patiently.
  3. Tell people verbosely about your project - it is astonishing how less people know and what wrong assumptions they make about your project.

Kind regards
Andreas.

14 March 2012

Michal &#268;iha&#345;: Weblate 0.6

Continuing with fast release pace for Weblate, I've just released version 0.6. It brings few bug fixes adds quality checks for translations and configurable access control. Full list of changes for 0.6: You can find more information about Weblate on it's website, the code is hosted on Github. If you are curious how it looks, you can try it out on demo server. You can login there with demo account using demo password or register your own user. Weblate is now also being used https://l10n.cihar.com/ as official translating service for phpMyAdmin, Gammu, Weblate itself and others.

Filed under: English Weblate 3 comments Flattr this!

Richard Hartmann: Open Source Days 2012, the aftermath

Open Source Days Open Source Days were nice, especially the meating(sic) of and talking to old friends and new people. I got to discuss Mercurial with two of its developers which was very interesting indeed. It's funny how similar git and Mercurial are in some regards and how different in others. Overall, it feels a bit as if Mercurial is not quite as distributed as git. Its local, sliding revision index feels like disaster waiting to happen, to me. On the other hand, Mercurials ability to not check out large files to your local repository sounds very git-annex-ish, which is nice. Choice is good :) My talk about how to gitify your life (slides, no video) went extremely well. Within my time-slot, there were a total of six talks, and lunch(!), in parallel. About 300 people attended OSD on Sunday and of those, many were at booths, stands, eating, etc. My personal turnout was 50-70 listeners so I was well above mathematical average and from what I heard, my talk was the most-visited one during that time. Add the fact that several people asked me to put up the resource links up again after the talk so they could take pictures and I would say this talk really was a success. Ego-stroking? Yes. Vanity? Most likely. Being able to see that people can really want to learn about what you have to say? Priceless. It's a real pity that there was no video recording, but it's obviously too late to do anything about that. Joey Hess asked me to at least make an audio recording on my laptop, but that turned out to be a lot of useless white noise with faint mumbling in between. Maybe I should at least get a small microphone or recorder so I will always have an audio copy. I already did order a presentation clickie with built-in laser pointer so I won't have to rely on possibly non-existent conference infra, any more. If there's any interest, I may re-record the talk as audio, else I will just try to get another speaker slot at another conference, with video recording, and link that. Denmark Barring the airport, central station, bus, hotel, venue, and metro, I did not see anything of Copenhagen. That's a pity, but I didn't want to leave the conference early. To continue my recent tradition of dumping random observations about places I visit onto my blog, here goes:

Next.

Previous.