Search Results: "reg"

22 May 2012

Gunnar Wolf: e-voting: Bad when it's near, worse when it's far.

Note: All of the information linked to from this post is in Spanish and related to Mexico Part of it will be translatable via automated means, some will not. Sorry, that's what I have, and it's too much text to invest the effort to hand-translate
I have been following the development of the different e-vote modalities in Mexico for several years already, although I have only managed to do so methodically in the last half year or so. If you are interested in my line of reasoning as to why I completely oppose e-voting, you can look at the short article I published in 2010 or the slightly longer and more updated version published in our book in 2011. Currently, in Mexico there are two different venues of e-vote that are being pushed: Bad and worse. The bad one will be carried out for about 10% of the population of the state of Jalisco and somewhat less for the state of Coahuila (Distrito Federal was also to be in this list, but the contract was cancelled due to the provider company delivering booths with too many problems and unable to deliver in the due time). The worse one is, fortunately, likely to have the least impact. Why? Because it regards votes cast by Distrito Federal residents (the capital entity, where part of Mexico City is located) living abroad. And it will have less impact because of the amount of the population registered for it: We are about 9 million residents in DF, and in the last election (first time IIRC there was the right to vote from abroad) there were only about 10,000 people registered for casting a (enveloped and sent by post) vote. Even if this year we the campaign for this was better (and I'm not yet sure about it), the number of voters will not be enough to make a dent on the results. I'm not going into details as to why it is bad in this post I requested information from the DF Electoral Institute (IEDF) with academic interest, to try to find more information about it, and I want to share my results with you and, of course, to request for your input on how to continue with this. On May 3rd, I sent the following request (this I am translating to English :) You can look at the receipt for the request for the original redaction) to the official contact address, oficinadeinformacionpublica@iedf.org.mx: Of course, I wasn't very optimistic when receiving this information. Still, I have to share my results: My information request was largely denied:
( )
III. The divulgation of this information harms the interest it protects
Given that, were it to be divulged it would affect the informatic security of the refered system. Anyway, we have to point out that said systems have enough measures and security provisions, so that the citizen can emit his vote in a universal, free, secret and direct way.
IV. The damage that can be produced by making this information public is larger than the public interest to know it
This is so because making this information public puts at risk the correct development of the Internet-based voting, because were the technical, purpose-specific information be made public, it could be misused to carry out informatic attacks.
It is also important to mention that a confidentiality agreement was signed with the company that developed said systems.
( )
VI. The time for the information to be reserved
It will be seven years starting at the present resolution, this information will be made public when the reserve period is over or when the target is reached, except for the confidemtial information that it could contain. ( )
In case some other person is interested in following this information, the other two points were answered, and I'll try to get some relevant information from it: So, I don't have any real conclusions yet. I'm just reporting how work is unfolding. Tomorrow evening (Wednesday May 23) I'll give a talk on the "e-voting in Mexico 2012" subject in Congreso Internacional de Software Libre in Zacatecas, Mexico. I'll talk on the situation on this and the other topics I have been able to work on.
AttachmentSize
Receipt of my information request11.64 KB
Transparency Committee resolution354.66 KB
Information request answered by UTCSTyPDP (IEDF)85.75 KB

21 May 2012

Thomas Goirand: Unit tests for PHP: PHPUnit

PHPUnit, according to its PTS, has been in Debian since 2009. But it was orphaned, and nobody took care of it for a while. That is until few weeks ago, Luis Uribe started to work on it. Since he isn t a DD, and that I take care of, I believe, about half of the all the PHP PEAR packages in Debian, I started working with him on re-doing the work of packaging PHPUnit for Debian. Previously, the old version was quite wrong, with missing dependencies, and not really working, what a shame PHPUnit 3.6 has been in Debian SID for 3 days now. And it s working well. I m now adding runs of unit testings from upstream packages at build time (of course, only if DEB_BUILD_OPTIONS doesn t contains nocheck , as per the policy). All together, it s been quite some fun to hack this, and I m quite happy of the results, even though there s still a lot of work remaining. PHP itself is running unit tests at build time. And not just a few: more than 11000 of them. The only small issue, is that they are totally outdated. Over the time, the vardump() function has evolved, and doesn t print things the same way. One may say that it prints things in a nicer way, but as a result, many of the tests that were suppose to work, actually fails because of these differences in vardump() over time. So I started working on fixing some of the tests. It s most of the time very easy to fix, but it takes a long time to fix all these small unit tests. So far, I ve been able to fix most of what s in the tests/, Zend/tests (more than 161 tests fixed), and the beginning of ext/*/tests: for the moment: bcmath, bz2, calendar, curl, date, dba, dom, ereg, and a part of exif, which for the moment represent 214 fixed tests, and I ll try to do more fixes when I have time. I hope to send the patches upstream soon. The final goal is of course to have the build of PHP to fail if unit tests are failing as well. For the moment, unit tests do run at build time, but the build don t care of the results, which I think is stupid (it s wasting CPU cycles for no reasons, IMO). If you maintain some PEAR packages, I would welcome you to first join the PKG-PEAR team on Alioth, and team maintain your packages, switch over to pkg-php-tools and dh 8 auto-sequencer, and to follow the PKG-PHP-PEAR packaging guide lines so that we have consistency in the archive. And of course, run unit testings, by doing a build-depends on phpunit (>= 3.6). Note that unit testings in PEAR packages are tracked on the Debian wiki. This post is also a call for help, because I feel quite alone doing this work of packaging PEAR packages, which many PHP applications depend on (think about roundcube, horde, extplorer, and many more). Other teams are doing very well, like the Perl team, and there s no reason why Debian wouldn t maintain PHP libraries as well as the ones for Perl.

20 May 2012

Gregor Herrmann: RC bugs 2012/20

I was on vacations for a few days last week, therefor my list of RC bugs is a bit shorter this time. thanks again to everyone who sent patches to the BTS that I could just use.

19 May 2012

Richard Hartmann: Motherland's bosom

I read a translated poem about Russia being "the Motherland" and its vast bosom years ago. Having driven through a significant part of it, I can agree on the "vast" part... Also, as I am on a train and without access to the Internet, I will refrain from linking to a lot of pages; sorry. (Turns out I am posting this a week later, but I will still not link to stuff now; no time). Russia in general Moscow Sights Kreml Our remaining time in Moscow was spent with touring the usual suspects; the Kreml is a lot less impressive in real life, the Red Square is tiny when compared to the stories I heard about it and the Chapel ofi St. Basil is even more colorful and impressive in real life. Lenin's body was inaccessible because workers built seats for the May 9th parade to the left and the right of it and they apparently thought it would be a good idea to block access to one of the main tourist attractions while doing so. A river tour of Moscow was a nice cool-off and we got to see quite a few things. We managed to see the weekly military parade within the Kreml grounds, but it was mostly pomp and little substance. The National Treasure which you can access with an extra ticket within the Kreml grounds is nice, but less impressive than the tourist guides would make you believe. That being said... There's another museum within the museum and.... Whoah... Tourists pay extra, visitors go through the only non-security-theater check I encountered in Russia, guards are armed, people can only enter and leave in batches, and the stuff which is presented is mind-boggling. Disregarding the fist-to-calf-sized chunks of gold and platinum which are still in their original form directly from the mine, there is real, actual treasure galore. Little heaps of uncut and cut diamonds, an outline of Russia filled with cut diamonds and other random "we have this stuff" displays can be found as well. Then, you have various tiaras and other jewellery made from various gems. Not incorporating, but largely made of. All that pales in comparison to the crown, royal apple, scepter, etc. It's hard to put the amount of tiny multi-colored light points that shine at you into words. I was just standing there, swaying back and forth to catch the moving pattern of pinpoints. It's said that this collection is equalled only by the ones in the Tower of London and the one Shaw of Iran had and boy do I believe it. TV Tower Getting up there was funny. The old-style Soviet queuing system was used: "Security" for approaching the tower was multi-level, the guards see you approach along a long walkway way in advance and the main guard shed had several small cabins separated by thick glass. So good so menacing. But in a twist that would make Bizarro and Garry Larson proud, I was required, by means of metal detector gate, metal detector wand and even an x-ray machine to remove every shred of metal and other hard objects from myself and the camera bag and put them onto a table. Once I was without anything except my clothes and the bag was completely empty, I could pass. Everything I had had to remove was just laying there, not inspected in the least, for me to stuff back into pockets and bag and to take with me. This "everything" included a Spot Messenger 2 with lots of green and red blinky lights. The guard did not even glance and it. Security theater? Security theater. The view from 364 meters down on Moscow was nice, but there was a lot of Smog so I couldn't see very far. Jumping on the glass floor while looking down was a lot of fun, though. Subway to Thiefing I bet Christopher Nolan rode the subway in Moscow at least once. That unnerving sound you hear during several key scenes in "The Dark Knight"? Two thirds of all subways make the same sound while moving. Also, I had an encounter with a pickpocket down there; very classical, too. Guy approaches quickly, talks loudly and sounds as if it's really important (in Russian... duh... that's sure to keep me interested). His approach made me turn and protect my left leg pocket automatically, most likely marking the target for the tiny woman standing behind me. Now, I have to tell you something about my usual travel layout. As my normal pockets are very deep, it looks as if their content was in the leg pocket. Plus, there's an extra, hidden leg pocket where I keep the passports and train tickets. The outermost leg pocket is protected by a velcro flap, but it contains nothing of value; usually the appropriate phrasebook, local map, maybe a tissue or chewing gum. Due to this layering, the outermost pocket looks as if it's full to the brim with stuff. Also, I took pains to make it a habit to protect said leg pocket with my hand, nothing else. This looks as if that's the target, but what I am actually doing is protect my normal pocket with my forearm. The right side is different, but the most easily accessibly pocket always holds some small change. I pay from that stash but my actual wallet is well out of reach. Anyway, once the guy ran off, talking to several others, most likely marking all them for the actual pickpockets, I wanted to enter the subway. While the Russian-style queuing took place, I felt an unusual tug at the velcro flap. I looked down and saw a tiny woman to the left of me with a jacket held over her right side with the left arm; I look up to check no one is trying to steal from my permanently assigned female, feel another tug, look the woman into the eyes, look up again and around me, look down again and she is gone. All that took maybe three seconds and I had boarded the subway after an additional two. In hindsight, it makes sense to choose the time of entry for attack. It's crowded, you are being pushed around, and once you are in the subway, it will start moving more or less immediately while the thief remains in the station. In this case, she would only have gotten a grubby map of Moscow's subway and an English-Russian phrasebook, but she got nothing at all. Moscow-Novosibirsk Where to begin... If you think a few hours on a train are a long time, try over fifty hours. Things get so bad, you start getting land-sick while not in a moving train. You even start missing the familiar tunk-cachunk, tunk-cachunk, tunk-cachunk... of driving over rails with gaps in them when you are not moving. The defining element of the Trans-Siberian Railway are birch trees. And birch trees. And then more birch trees. You would not believe how many birch trees there are. This is made "worse" by the way the Russian Railway protects their rails. Left and right of the track, there's a cleared area of maybe ten to twenty meters, sometimes as little as three. Outside of that, they plant ten to twenty meters of birch trees, presumably to catch snow during winter. Beyond that protective perimeter, there's the normal landscape.As a result, on top of the near endless stretches of birch woods, you see most if not all scenery through a layer of birch trees. You get sick sick of birch trees after a few hours and you see them for days on end. Bullet points to save myself some typing and you some reading... Novosibirsk The non-existent hostel We arrived at ~0200 local and made our way to the hostel we had booked a room with. Walking to the correct address, we saw several signs but they all turned out to be for a police station and some other state agency. We walked back, forth, double-checked, triple-checked: no hostel. We then walked around the building through some not-quite-nice back alleys, but other than a few entries to private flats, there was nothing. Thankfully, the booking slip included a number which we called and after at least twenty rings (no kidding), when I had given up and wanted to hang up, it stopped ringing. Dead silence. After maybe ten seconds, someone started talking in Russian. I asked him if he spoke English and told him that we could not find the hostel. He mumbled something about being sorry and that we should wait, he would come down. Fast forward a minute or two and someone walked towards us. Again, he mumbled about being sorry, that the hostel "did not work" at the moment and that we would need to sleep in his private apartment. He ushered us into some back alley entrance, into his flat, and proceeded to remove the sheets from the couch on which he had slept; after putting on new sheets, we had our "hostel" bed, ready to sleep on. We briefly considered if he would murder us in our sleep, but him and me even got to talking a bit. Over cheese, sausage and rum (at 0300), he admitted that the hostel did not exist and he merely planned to turn his flat into a hostel for the summer while he and his family moved into their summer house (the Russian term of which escapes me, at the moment) in the countryside. He had accepted our reservation as he thought he would be finished by that time. He did not even get started, though. While he sent us an overbooking notice through booking.com two days before, we were on the train at that time, so... booking.com even called him to check what happenend to us as we did not book another place through them. Good customer service/protection, that. Next morning, he didn't even want to take our money (we paid anyway) and, as a means of compensation, drove us into the city in the morning and to a train museum well outside the city limits, one of the fabled scientist cities, and a large lake which everyone in Novosibirsk claims is an ocean, in the afternoon. Foreigners, foreigners! All in all, Novosibirsk was relatively uneventful, safe for one bizarre episode. We took our lunch in a local fast food joint (why do all the good stories happen there, and not at the various truly local places?) and threw the cashier our well-rehearsed "Niet Russkie; anglisky?" with phrasebook in hand and he actually understood a few words of English (beef, chicken, fries). We told him, in our worst Russian, that we are from Germany wished him a nice day and went to sit down. A few minutes later, a girl approached us, literally hopping from one foot to the other and wringing her hands. She told us that the cashier had told her that we spoke English and if it would be OK if she talked to us. We suspected some sort of elaborate ruse, but went with it. Turns out, she had English at school and really wanted someone to practice English on. Two young men passed our table and exchanged a few words with her, sitting down out of sight. When she told us that she had to leave now but if it would be OK if the two boys joined us we suspected a ruse yet again. But those two were law students, one with a minor in English and one with a minor in German; both of them also extremely nervous, asking us if we would talk to them. When they had to leave, they told us that the three of them worked at the burger joint and that their shift was just about to start when the news that foreigners were here spread amongst staff like wildfire. The girl stopped by several times in between cleaning tables, getting in a sentence or two before being cussed at by her supervisor. All in all, this took about twenty minutes and seeing three people so nervous and grateful to talk with us felt beyond absurd. On the other hand, not a single traveller we met even considered stopping in Novosibirsk during their transit so there really does seem to be a shortage of non-Russians there. Weird, and memorable. Novosibirsk-Irkutsk Irkutsk / Listvianka / Lake Baikal Listvianka Aah, lake Baikal... the oldest and deepest lake on Earth which holds a fifth of the global non-salt water reserves; a must-see in my book. Quad tours at break-neck speeds, dry-suit diving with Russian regulators, walking barefoot in between and across drift ice that made its way onto the shorei, and extended hiking around the lake's coast... All of which I could not do because I was ill and had to spend two solid days in bed. The draft from the open window in between Novosibirsk and Irkutsk was enough to give me a rather bad cold which peaked at Lake Baikal. Still, the area was lovely and we were glad to be out of a train and able to unpack our stuff without having to repack immediately for once. I am not sure where my current losing streak with regards to diving is coming from (Grimsey, diving north of the Arctic circle with birds that plummet into the water and hunt fish: Only guy who does this is on the Icelandic mainland that day; Svalbard, diving north of the Arctic circle in permanent darkness: The few people who do this privately did not reply while I was there; Baikal, oldest, deepest, largest lake on Earth: ill), but I will most likely return to Russia for a week of ice diving in Lake Baikal next winter or the one after that. As an aside, I saw several people walking to Lake Baikal with buckets to get their water. Other people got it from a well which was still half frozen. If you have running water consider yourself lucky... Irkutsk Nice city, largely uneventful. The farther east you get within Russia, the more normal women look. In Moscow, just as in Paris, they are way over-dressed and even service personnel will walk with high heels. Thankfully, I don't have to wear heels, but for the other males out there: Walking and standing in these things hurts and thus most if not all people who stand and walk for a living have flat shoes. We happened upon preparations for a military parade, complete with cordon, viewing podests, at least half a dozen TV cameras etc, but were not sure if it would start soon enough for us to catch our train.We asked someone who told us it would start at 2100 local, at 1945 local it seemed about to start, and sure enough at 1955 sharp, the whole thing went under way. About a dozen groups of 50-100 people each, all in their own, respective uniforms stood against one side of a cordoned-off street and several higher-ups on the other side. Two highest-ups shouted into microphones and the throng of people on the other side shouted back answers. Then, the two highest-ups stood in the back of a jeep each and drove past said throng, stopping in front of each group, shouting into microphones mounted in the back of the jeeps and the groups shouted back once again. After that, all groups marched around the make-shift plaza once, saluting the higher ups. Once they were done, and they took ages, two trucks drove by with soldiers jumping out of the moving trucks and moving into crouching positions. They ran around in a circle a few times and engaged in pretend hand-to-hand combat. I am sure they are skilled at whatever style they wanted to show, but they were overdoing things so badly, they were funny, not imposing. When they jumped over some barriers, the barriers fell to pieces and everyone scrambled to make it look as if that was part of the show. While carrying off the gear, it fell into further pieces which was even more funny. An armoured personnel carrier ended the show; several tougher looking guys jumped off of that one and their mock combat involved fully automatic fire (of blanks), several flashbangs, smoke grenades and, to top things off, the machine gun mounted on the APC moving down the opposing team with blanks. I never witnessed a "real" military parade in person but this one was somewhat disappointing. On the one hand, there was a distinct lack of ballistic missile carriers and tanks like you see in movies, documentaries and games, on the other hand, the whole thing had a make-do feeling to it. The cordoning police had designated spots to stand on, yet walked around. They were standing to attention, yet checking their cell phones. Several people in one uniformed group were wearing track suits and jeans. Another uniformed guy had a grocery bag with him; yet another one was carrying a huge water bottle. Bikers zig-zagged through the cordon and when the whole show was just about to wrap up the police finally started putting up barriers around the unmoving pedestrians, not blocking the bikers. One little girl was standing well within the cordoned area, watching with big eyes and after she did not react to the police talking to her, they just built the barriers in a curve around her. And to top it all off, some guy with a cane walked all through the parade with his personal camcorder, trying to direct the whole show while being ignored by everyone. Still, I am sure he managed to mess up some otherwise perfectly good TV scenes. Irkutsk-Russian border TL;DR 3000 kilometers of birch trees

18 May 2012

Johannes Schauer: a periodic counter

tldr: counting without cumulative timing errors Sometimes I want just a small counter, incrementing an integer each second running somewhere in a terminal. Maybe it is because my wristwatch is in the bathroom or because I want to do more rewarding things than counting seconds manually. Maybe I want not only to know how long something takes but also for how long it already ran in the middle of its execution? There are many reason why I would want some script that does nothing else than simply counting upward or downward with some specific frequency. Some bonuses: Now this can not be hard, right? One would probably write this line and be done with it:
while sleep 1; do echo $i; i=$((i+1)); done
or to count for a certain number of steps:
for i in  seq 1 100 ; do echo $i; sleep 1; done
This would roughly do the job but in each iteration some small offset would be added and though small, this offset would quickly accumulate. Sure that cumulative error is tiny but given that this task seems to be so damn trivial I couldn't bear anymore with running any of the above but started looking into a solution. Sure I could just quickly hack a small C script that would check gettimeofday(2) at each iteration and would adjust the time to usleep(3) accordinly but there HAD to be people before me with the same problem who already came up with a solution. And there was! The solution is the sleepenh(1) program which, when given the timestamp of its last invocation and the sleep time in floating point seconds, will sleep for just the right amount to keep the overall frequency stable. The author suggests, that sleepenh is to be used in shell scripts that need to repeat an action in a regular time interval and that is just what I did. The result is trivial and simple but does just what I want: You can check it out and read how to use and what to do with it on github: https://github.com/josch/periodic Now lets compare the periodic script with the second example from above:
$ time sh -c 'for i in  seq 1 1000 ; do echo $i; sleep 1; done'
0.08s user 0.12s system 0% cpu 16:41.55 total
So after only 1000 iterations, the counter is already off by 1.55 seconds. This means that instead of having run with a frequency of 1.0 Hz, the actual frequency was 1.00155 Hz. Is it too much to not want this 0.155% of error?
$ time ./periodic -c 1000
0.32s user 0.00s system 0% cpu 16:40.00 total
1000 iterations took exactly 1000 seconds. Cool.

16 May 2012

David Welton: Up for Auction: LinuxSi.com

A number of years back, I read yet another complaint about someone having trouble finding a computer with Linux preinstalled. So I did something about it: I created LinuxSi.com, where it is possible to register computer stores in Italy (this was an Italian Linux mailing list) that are helpful towards people wishing to buy a Linux machine. Fast forward past getting married, having kids and buying a house, and LinuxSi.com is not something I have much time to run any more. I still think it's a useful service, even if the site itself is a bit creaky. In any event, I've put it up for auction with Flippa.com, and there's one week left on the auction. Right now, it's going for just $10, which even with the low amounts of adsense income it brings in, you'd make back pretty quickly. I hope that it goes to someone who cares about promoting Linux in Italy - if nothing else, the domain name is a good one that could be employed for many things.

Christian Perrier: Bug #1000000 in Launchpad

Way before Debian, Launchpad bug tracking system just reached 1 million bugs reported with one "bug" reported against Edubuntu basically mentioning it should invade schools. What to say about this? Hard without being harsh towards my friends working in the Ubuntu "world", indeed. Still, I really think that here, too much noise kills signal and the LP BTS is often hardly usable. I counted up to 217 bugs reported against samba4 (which is, after all, not so widely used yet) just because it apparently has upgrading issues between pre 12.04 versions of Ubuntu and Oneiric. It indeed seems that some automated bug reporting is now active and whenever a user encouters an upgrade issue with a package, a bug is being reported. I guess this is somehow an opt-in system (I hope so..:-)) but the default is very clearly using it. This feature is apparently what caused the recent bump in number of bugs reported in LP, making them even less useful, particularly to Debian package maintainers. I'm sure there are tools to help dealing with that and I was already answered that work is in progress to change this (and use a dedicated website for such reports or something like this). But, still, that seems to be the scary side of popularity...the very same popularity that is slowly but constantly hiding the work we're doing in Debian to indirectly make Ubuntu popular. (moving to more general concerns) I know that things are not all black or all white, but it always saddens me to feel that slowly....but, again, constantly, more and more people tend to forget that Debian is behind Ubuntu, is the ground on which it is built and Ubuntu wouldn't exist without it. When doing work, a human need is to get reward for it...and we are getting less of it...slowly, but constantly. Don't take me wrong. I have many friends working directly for Ubuntu. Some paid by Canonical for this. Some really involved up to "top level" (yes, including the very very top level even if I killed him once). I don't want to throw offense on them. I don't even know if they can do something about what I'm expressing below. I would just have them (and others) know. Let's take an example. I recently activated a few languages in D-I (Burmese, Tibetan, Uyghur). I'm happy with that, this is something I'm doing for 8 years now. But all these new translators were indeed only interested in one thing : "have Ubuntu translated in their language". No offense intended, but they didn't really care about *Debian* being translated in their language. I think that some didn't even know what Debian is. In the same field, I am more and more "fighting" to keep the level of translation completeness in Debian (see my regular spa^W reports). In some way, I still succeed, but the price to pay is more and more and more personal investment and work. That's still working for the strong set of languages we support. That works much less for most others. When someone "disappears" (or just switches to some other priorities), it's more and more difficult to find someone else popping up. And, for the "strong set", something else is happening : work duplication. There are "strong" French, German, Italian, whatever, l10n teams in Debian.....and there are similar teams for Ubuntu. And, mostly, those do not really work together. And sometimes, this is kinda discouraging. So, seeing the explosion happening on what is, whatever we think or write, the "other side", is not somethnig that can make one entirely happy. And this is why I won't celebrate Launchpad's millionth bug report. Particularly when I see that millionth bug report not even ack'ing that this Edubuntu marvel is based on the grounds set by some pionneers many years ago in a few schools in Norway (hello, Petter and others). Yeah, sometimes sad. To balance this, let's release wheezy and have millions of people benefit from it without even knowing.

15 May 2012

Martin Pitt: Debian/Ubuntu Packages for PostgreSQL 9.2 Beta 1

The first Beta of the upcoming PostgreSQL 9.2 was released yesterday (see announcement). Your humble maintainer has now created packages for you to test. Please give them a whirl, and report any problems/regressions that you may see to the PostgreSQL developers, so that we can have a rock solid 9.2 release. Remember, with the postgresql-common infrastructure you can use pg_upgradecluster to create a 9.2 cluster from your existing 8.4/9.1 cluster and run them both in parallel without endangering your data. For Debian the package is currently waiting in the NEW queue, I expect them to go into experimental in a day or two. For Ubuntu 12.04 LTS you can get packages from my usual PostgreSQL backports PPA. Note that you need at least postgresql-common version 0.130, which is available in Debian unstable and the PPA now. I (or rather, the postgresql-common test suite) found one regression: Upgrades do not keep the current value of sequences, but reset them to their default value. I reported this upstream and will provide updated packages as soon as this is fixed.

13 May 2012

Jamie McClelland: Sparkleshare

Sparkleshare is a file sharing utility that keeps folders in sync on multiple computers in a similar fashion to the commercial and proprietary Dropbox. Sparkleshare recently released a Windows client, finally allowing me to start switching my co-workers at the Progressive Technology Project away from Dropbox. Overall, I'm very impressed. In particular, I appreciate the Sparkleshare authors' decision to build on top of existing tools (git for storage and revision control, ssh for transport, and ssh public key infrastructure for authorization and authentication). That means I don't have to learn new tools and protocols to debug and it means Sparkleshare can focus on the file sharing pieces. Despite my overall enthusiasm, I do have some serious concerns. Protecting your credentials A researcher found a startling security flaw in Dropbox - if you can copy a particular file from a user's computer to your own computer, you can impersonate them flawlessly, accessing all their Dropbox files without having to know the user's password. Unfortunately, Sparkleshare suffers from this same vulnerability if you use the default configuration. When you first install Sparkleshare, it creates a password-less ssh private/public key pair and then makes the public part easily accessible to you so you can add it to your server (or gitorious account, etc). Very convenient. But it also means that all an attacker needs to do is copy your private key (and your Sparkleshare configuration file) and they get complete control over your files. This problem is easily avoided. If you are running Linux or Mac OS X and you have your own key loaded in your ssh agent, Sparkleshare will happily use that key. So - simply by using your existing (presumably password-protected key) on your remote Sparkleshare servers, you can mitigate this problem. Sparkleshare will still load your Sparkleshare generated key, but if you don't provide that key with access to anything, no harm is done. Confirming each use of your key However... that leads to a new problem. If you are like me, your ssh agent is configured to ask for a confirmation every time your key is used. And, Sparkleshare regularly polls the remote git repository for changes. At best repeatedly clicking to confirm is tedious. At worst, it prevents you from intelligently rejecting malicious requests, thus defeating the whole purpose of the check. It is possible to launch Sparkleshare via ssh-agent in an environment in which you are not requiring the confirmation when Sparkleshare uses your key, but still requiring it for all other uses. However, given the trade offs, I've decided to add a password to my Sparkleshare provided ssh key rather than using my existing key: ssh-keygen -p -f ~/.config/sparkleshare/sparkleshare.jamie@progressivetech.org.key Now, I am prompted to enter my passphrase when I start Sparkleshare and don't have to confirm every use of the key. And, I continue to confirm each use of my main key. git was designed to store code, not documents Just because something is designed for one purpose doesn't mean it can't be used for another. However, there are a few limitations. Large files are one. git can handle files over 100MB, but may run into memory problems. I had to alter the git windowMemory setting, raising it higher than the size of the largest file. Another problem is disk space. Since git keeps full revision history on every machine, you have to download more data than just the files that are checked out. The more edits you make to a repository, the more disk space beyond what is checked out is needed (and deleting files won't help). Lastly, you can't use file modification times. With git, the file modification time will depend on when you checkout the files. With some fancy hook writing, you could tweak things so that the file modification date is the same as the commit date, but that still won't help you if you add an existing directory to Sparkleshare because all the files will have the same commit time. This "bug" has been reported to git and it has been rejected because mucking with the modification time of files can have bad results when you are using make to compile code. As Linus colorfully put it:
I'm sorry. If you don't see how it's WRONG to set a datestamp back to something that will make a simple "make" miscompile your source tree, 
I don't know what definition of "wrong" you are talking about.
It's WRONG.
It's STUPID.
And it's totally INFEASIBLE to implement.
Well, did I mention that git was designed for source code? No server validation Of all the problems I encountered, this one is by far the most serious. Perusing ~/.config/sparkleshare/debug.log is very informative. On a default installation, after you have added a project, you'll see:
19:32:27 [Fetcher][/home/jamie/SparkleShare/.tmp/bar] Fetching folder: ssh://foo@bar.org/foo/bar
19:32:27 [Fetcher] Disabled host key checking for bar.org
Wah. Once the project is added, whatever key fingerprint is given is stuffed into your ~/.ssh/known_hosts file. Host key checking is only disabled when you initially create the project, so if you connect to the proper server the first time, you are protected from subsequent man-in-the-middle attacks. However... if the initial fingerprint is wrong, your personal ssh configuration is now poisoned. This seems like a very bad idea. I've opened a debian bug to address it.

Gregor Herrmann: RC bugs 2012/19

like in the last two weeks, this week's bug squashing was mostly related to the gcc 4.7 FTBFS bugs:

12 May 2012

DebConf team: Report from our visit to Managua, Nicaragua (Posted by Holger Levsen)

I ve send a mail today with a summary of some of my experiences in Managua and tiny bits of Nicaragua late April / early May 2012. If you are considering going to DebConf12 (which you obviously should do as you are reading this!) go and read this mail, as it includes a thematically sorted list of impressions and advice written by Gunnar, Norman, Leo, Felix and myself, which should give you some better idea about DebConf12 in Managua! While I spent 14 days in Nicaragua in total, for the last three days I was joined by Gunnar Wolf, to make sure my impressions about the local team, the status of the preparations and everything were correct. Our visit also seems to have been very motivating to local team members, whom I ve seen really enthusiastic to welcome a huge Debian crowd for the first DebConf in Central America in just a few weeks! At the last DebConf12 IRC meeting I summarized it like this: in very short: my two weeks were great, I had a great vacation, met many members of the localteam, which is way bigger then it seems on irc, saw and liked UCA (Universidad Centroamericana, the DebConf12 venue), had zillions of reunions (meetings, see schedule wiki page) and met many nice people and a very hot & interesting country+capital with great countryside. The deadline for sponsored accomodation ends in three days - so if you haven t registered yet, hurry up, DebCamp starts in 49 days! :-) (After that registration is still possible, but you will need to pay for your costs yourself.) We re looking forward to see you there and have a great DebConf together! Hopefully we sweat together while Wheezy is frozen :-D

Tanguy Ortolo: Signing-party and crypto conference in Paris

Statue of Saint Peter holding the heaven's key Monday 21st during at 18:45, in Paris, there will be a conference organized by Parinux, where I will explain the principles of cryptography and their application in the SSL and PGP systems. This conference will be followed at 20:30 by a signing-party PGP et CAcert. For the signing-party, I will ask participants to:
  1. generate a key pair if you do not already have one;
  2. send me you public key and register;
  3. print some copies of your key fingerprint;
  4. print the list of participants I will send you;
  5. come with all that stuff and one or two identity documents.
This is a partial translation of the full article I wrote in French, in case foreigners could attend. Sorry for the very late notice

Joachim Breitner: 10 years of using Debian

Today, it must have been exactly 10 years that I started using Debian. The story of how I came to Debian shows some of its strengths, so I ll use this occasion to share it. I spent the first half of 2002 as an high-school exchange student in Wenatchee, USA. I was already a user of Linux at that time: I made my first contact roughly in 1996 and did my first installation at home two years later, but all that time I was dual-booting and my main system was a well-arranged Windows 98. The machine was a regular tower PC, but nevertheless I put the computer into my trunk when I flew to the US. It took away most of the space, and I had to put some of my cloths inside the case. So I was there, happily using my Windows and my manually set up Linux From Scratch until one day the inevitable happened; inevitable at least until you start doing backups: On April 30th, my hard drive crashed, and took the two systems together with 4 years of personal data with it. Two weeks later I had a new hard drive and was pondering my options. I did plan to install Windows again; at that time Windows XP was just released. But I wanted a German version of Windows, which would be hard to get there. Also, I did not want to use Linux from Scratch any more, and wanted to make a well-founded choice of a distribution. On the other hand, I really wanted to get my machine up and running quickly, to be able to read my mail more comfortably. I had heard that Debian had good support for network installations (downloading a full 700MB CD was something to avoid at that time), so I grabbed some netinst images, burned a CD, and quickly installed Debian. I was planning to use the system for about two weeks. I did not pay any particular attention to the setup. Heck, I even picked from my Simpsons sidekick machine naming scheme one that I would not miss being used up ( barney ). Nevertheless, I was using this installation for many years (and many upgrades), until I eventually switched to using laptops. In fact, that very installation is still on the machine somewhere and works. I did install Windows XP a few weeks later as well, but hardly used it. So May 12th of 2002 was when I turned into a full-time Linux and Debian user. I soon became interested in Debian the project and started to contribute. But that is another story for another ten year anniversary blog post, most likely on October 21, 2013...

Flattr this post

Steve Kemp: On working from home

Recently an ex-colleague of mine changed jobs and suggested that I write something about the pros and cons of working from home. I've thought about this subject, off and on, for a few years and frustratingly I think most of the pros and the cons are the same: I live in a two-bedroom flat in Edinburgh. (Having just spent thousands on a new bathroom I don't expect I'll be moving any time soon. A rough budget of 40-50,000 would let me convert my attic into two/three rooms. So there is growth potential!) In my flat I have made one of the bedrooms an office. The office contains: One PC is for work. One PC is for me. One phone is for work. One phone is my own. Every working day I switch on the work router, the work phone, the work PC around 09:30. I then work, taking a lunch-break between either 12:00-13:00 or 13:00-14:00, until 18:00 at which point I switch off the work toys. I ignore my personal PC during the working day with the exception that it is the source of my music. I can reach across and hit the appropriate multi-media keys to select Play/Pause/Next Track/Previous Track/Volume Up/Volume Down. (When thenever the work-phone rings the first ring is ignored as I scramble to hit "Mute" or "Pause"..!) So what are some of the advantages/drawbacks? Well I'm at home. So the environment is one that I've made myself, and enjoy. The music is mine. The colour-scheme is mine. The pictures on the walls are mine. I have a Steve-loving chair. There is no soulless air-conditioning, no horrible cubicles, and no noisy people talking. The downside? No people talking. If I didn't leave my house at lunchtime I'd speak to zero people face to face in an average working day. That took a while for me to notice, but it is not nice. Since I work from home "the commute" takes seconds. I tend to get out of bed and wander straight to the desk. I'll work non-stop, then get dressed around lunchtime so that I can go out for lunch. Hail, Rain, Snow, or Sunshine I leave the house for lunch every single day (unless waiting for an atypical delivery). Because if I didn't I'd have no human contact. In the afternoon if it is a nice day I'll get undressed again, because I can, so why the hell not? Providing you're focussed working from home has several advantages that I can think of - I've no qualms about setting the washing machine going before I start work knowing that I can "spare" five minutes to empty it later in the day. Similarly I've no concern about ordering (even large) items, because I know what time the postman comes, and I know I'm never going to be out and miss a delivery. When I first started working from home I had a laptop instead of a PC and there were mornings when I worked, lazily, from my bed, or from my sofa whilst watching TV. That didn't last for long because I just didn't do a good job. I think I got away with it in the sense that I don't think people noticed, but I expect if it had lasted for longer it would have been quickly apparent. I stopped because the line was blurring between "home life" and "work life". Having a dedicated working area is essential in keeping me focussed. I don't do "home things" when I'm in "work time" - with very rare exceptions. Yes I wander around and pace if I'm thinking, yes I make more tea and coffee than I would in a real office, and yes I might open windows, phone a friend, read my gas meter, washup dishes, or similar as I'm "making coffee". But on the whole it only works if I work when I'm working. I could save money by using my work-internet instead of paying for personal-internet, but keeping the two links separate is another way of being focussed. I don't do "dodgy" things on the internet, on the whole (haha), but if I do I'd want to be damn sure that that was via my link and not the work-link - and having two PCs and two network links I know that is the case. There have been times when the work link has broken and I've used my personal link + openvpn to continue working, or at the very least re-join our internal chatroom and say "Internet down, brb". As a system administrator there are times when I have to do things either early in the morning, late at night, or even during a weekend. I guess a final advantage is that this is not a struggle - providing I don't schedule such operations at times when I'm in the pub, meeting friends, or taking pictures of cute strangers, it isn't a struggle to say "I'll do this after 8pm tonight", or set the alarm early. No long walk to an office, and if I've already got food cooking for my tea I can eat it nearby whilst still configuring things and testing sites/services/machines. So pros: I'm in my own environment, I don't worry about receiving parcels, meter-readings, and have wonderfully pleasant music all day. Ancillory bonuses are really side-effects of being in my environment: I have my good coffee, my nice cups, I can eat food I enjoy. etc, etc. Cons: You must be dedicated. You must be focussed lest you give in to temptation and cease working for minutes/hours at a time. You lose part of your home space - I can't turn this room into a childrens bedroom, for example. Nothing earth-shattering. I've done this for five years now, and although I was a little skeptical initially I thought "Why not?" It has worked out well and I think if I ever did need to leave my current position I'd have no hesitation about working from home in the future. Finally it has to be said that when I've had partners in my life they've traditionally been the type to wake up later than me. I get significant brownie points for being able to wake them up around 10/11AM with a cup of hot coffee & breakfast in bed every morning. By virtue of having a separate space I can close the door and not be disturbed by them walking around. I'm sure I've forgotten things - but as an initial pass the benefits and disadvantages of working from home are the same: You're in your own house. ObQuote: "Explorers in the further regions of experience." - HellRaiser

11 May 2012

Andrew Pollock: [life] Zoe at 24 months

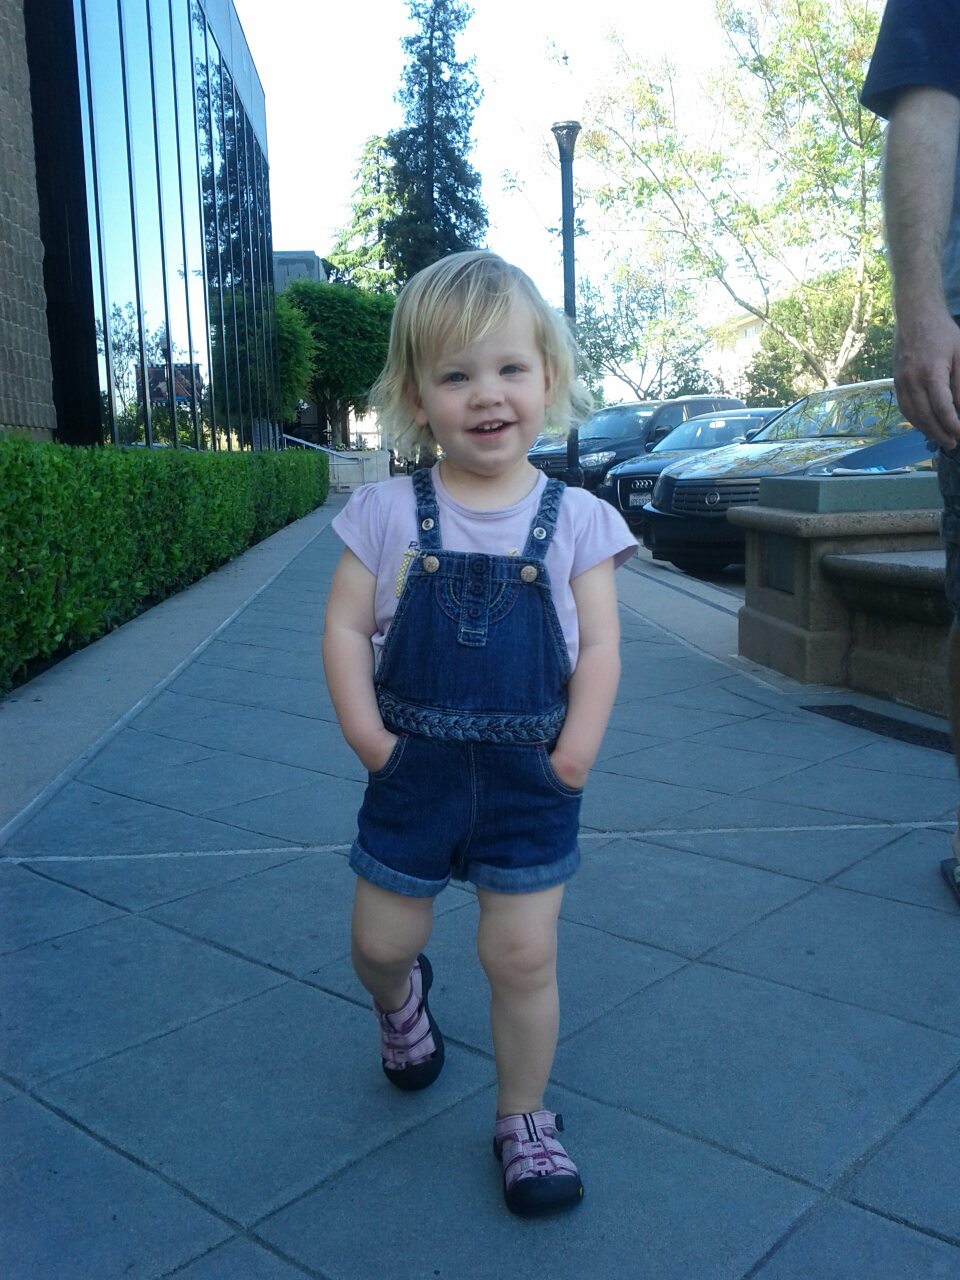
Once again, another 3 months have flown by. Honestly, it's been a total blur. What on earth has happened since February? Well, heaps more travel of course. There was the trip to New Orleans, which I already wrote about. The other big trip we did was to Washington D.C. for a week, which I'm yet to write up. We stayed with friends in Alexandria for the week. Unfortunately, Zoe came down with conjunctivitis before Sarah's very eyes on the flight over (I'd been in North Carolina for work the week before, so they flew without me and I flew up to D.C. to meet them). She also developed an ear infection and a general cough/cold. Fortunately, we caught it all pretty much as soon as it happened, and spent Easter Sunday at an Urgent Care in Virginia getting antibiotics for her, but her sleep was not so great the whole time we were in D.C. Other than that, we've just been doing the normal stuff. Swimming classes have continued (she's very confident in the water now). Her speech continues developing well. Toilet training is continuing to go very well. There haven't been very many accidents at all. She's really loving the "new" day care. It was definitely the right thing to do to move her. Physically, she's in the 80th percentile for height and the 50th percentile for weight, so I guess she's currently tracking to be on the tall and thin side of things. We had another birthday party in the park behind our home, and this year the weather was much nicer, so we had people hanging around until about 7pm, and a good time was had by all. Zoe even successfully blew out her candle on the first attempt. Her two-year molars still haven't come through. They seem to go through various stages of giving her a lot of grief, and then they stop messing with her sleep. I was beginning to think we'd never get back to an uninterrupted night's sleep ever again. It's still a bit hit and miss, but she usually settles down again fairly quickly if she does wake up, and doesn't always require intervention from us. I've arrived at the theory that the "terrible twos" are largely the fault of trying to cut these two year molars. Her tantrums are so much worse when her teeth are actively giving her trouble. If she's had a good night's sleep and her teeth aren't driving her crazy, she's still pretty well behaved. If she's been awake half the night and her teeth are hurting during the day, she can be quite difficult. We seem to be currently at a point where they're not causing too much trouble at night, but she'll chew on her fingers like crazy if given the chance during the day. I think seasonal allergies are also messing with her a bit. After she got over the cold she came down with in Washington D.C., she's still had a runny nose and a bit of a cough, but I don't think she's actually "sick" I think it's more related to allergies. She passed on whatever she had to me, and since I've recovered from it I'm also not feeling quite right. I read somewhere that pollen counts are off the charts this year due to the weird weather, and Sarah's having a bit of a hard time as well, so I think we're all going to just have to ride it out with the judicious use of antihistamines. Speaking of allergies, it's about time to re-test her for her egg allergy. We'll have to try that at a point when she's not regularly taking antihistamines for seasonal allergies, so it might be a while yet before we can do that. I guess the next big development will be graduating from the crib to a toddler bed. I'm not in any hurry to do that though, so as long as she's not escaping the crib, her sleeping arrangements can stay the way they are. It'd be nice if she can cut her teeth first and then once she's sleeping properly, we can try converting the crib into a toddler bed. Zoe walking down Castro Street in Mountain View
10 May 2012

Jo Shields: Sleeping with the enemy: my life with Windows Phone

In my last blog post about smartphones, I urged the universe at large to help maintain a variety of ecosystems, to help foster competition and originality amongst vendors and the same day I hit publish, WebOS was killed. Apparently the universe hates me. Since then, a few things have changed. My main phone since the day of its release was the HP Pre 3, running WebOS and whilst I still have a soft spot for the OS, the Pre 3 was simply too buggy for me to use full time. The main issue is that I use my phone as an MP3 player in the car but the Pre 3 would pause playback at the end of a track every half dozen tracks or so making it impossible to drive the 85 miles to work without needing to root around in the armrest and poke a touchscreen. Not something I really want to do whilst moving and ultimately too big a papercut to deal with. So, come the new year, I moved on to my next device, a Nokia N9 running MeeGo Harmattan. Ultimately, this was an even bigger failure for me than the Pre 3 was, and I lasted maybe two weeks with it before giving up and going back to the HP. Beyond massive usability errors in the software (especially the braindead unkillable pop-up demanding Internet access, even when none is available), the worst for me was how it handled the MP3 player task. My usual way of working is to have the phone hooked up to the stereo with a 3.5mm jack, and the car switches to headset Bluetooth profile to handle calls this is pretty common on cars too old to support A2DP profile (Stereo music-capable headphones). WebOS and Android are fine with this but not the N9. The N9, instead, will output all audio through the last connected audio device, regardless of how much that might not be helpful. Get in car, start music playing, plug in cable, start engine and it plays audio for about three seconds before the Bluetooth connects, and it switches to outputting music via the Headset bluetooth profile (not something that my car can do). Unplug and replug the cable, and music works but incoming calls are silent until I disconnect the 3.5mm jack, as it outputs the headset audio through the headphone socket. I just couldn t deal with this big a step back from WebOS as far as my workflow goes, and gave up. So, where next? Well, a funny thing happened a co-worker with generally very good instincts regarding consumer electronics usability told me that his housemate had just bought a Nokia Lumia 800 Windows phone (the WP7-based cousin to the N9) and loved it. Enough that said co-worker was considering getting one himself. This was a very strange thing to hear, especially from an iPhone owner, about a Microsoft product. I d been generally interested in WP7 on an academic level for a while, but to hear that degree of praise of the actual product was interesting. Also interesting, and roughly simultaneous, was seeing Sajid Anwar s reverse engineering of the proprietary Zune file transfer protocol go from theory into an actual set of libmtp patches. So if the capability to use Banshee to transfer music on is here or near and it can t be as braindead as Harmattan when it comes to headphone/bluetooth behaviour, then why not jump ship and squeeze a handset out of Orange? About a week after my co-worker replaced his iPhone with a Lumia 800, I bought one too. So where to begin? Well, I ll begin at the start: WP7 is a joy to use. It really just is. It s the first mobile OS to try something radically different in the UI department for years. Everyone else these days (especially Android) builds iPhone rip-offs to varying degrees, and even the iPhone interface has a lot in common with the old old OLD interfaces found on the dumb Nokia phones of the 1990s. WP7 has an interface which provides just the right level of passively visible information and interactivity, and manages to do it with an elegance that no Android home screen filled with widgets will ever manage. The uncluttered screens are easy to read, and the Metro usability paradigms are trivial to pick up and learn. Without a doubt I d recommend WP7 to friends and family from a usability perspective, and the Microsoft engineers and designers responsible for cooking up the WP7 interface are worthy of praise. And I m not the only one saying this Apple co-founder Steve Woz Wozniak recently came out with a similar line. That s the good. There s also some bad, make no mistake. I m going to cover all the reasons WP7 sucks over several paragraphs. But overall, a smartphone is a device which I expect to suck the question is how bad the suck is, and whether it gets in the way of me using the device for what I need at the time. Moreso than MeeGo, moreso than Android, and even WebOS (and I m still a big WebOS fan), WP7 has more good points than bad points. But there s still some room for improvement, and some room for caution and since I know there are a few Microsoft folks following me on Twitter, I m going to go over my prescription for continued platform success. Oh, one more thing before I start: I know WP7 isn t Free Software. As an end user, I really don t care about that. I just want something that works something I didn t get from WebOS and Harmattan, both of which are primarily Free Software stacks. I m not saying there s a causal relationship there, or that a mobile OS can t be both Free Software and good just that as an end user, my favourite platform right now is non-Free. Take from that whatever you like. It s also vitally important, as Free Software folks, never to lose sight of what the other players in the market are up to. If you can t objectively assess why people are using a proprietary option by using it & recognising its good points (i.e. what to steal & what to improve) then you can t hope to win over users. So. WP7 s downsides in detail. In-place updates. Seriously guys, even Apple can manage this now. Why can t Windows Phone? I understand that making backups is smart and all updates come with a mandatory backup but I really shouldn t be tied to a PC to update a post-PC device. Also, those backups are useless, since they cannot be restored onto replacement devices in the case of failure or theft, so fix that too. Update all the things. An iPhone sold in June 2009 still has access to the latest iOS releases. Android phones are notorious for shipping with an outdated version of the OS, then getting at most one major update over the phone s lifetime (usually the device is abandoned by its manufacturer within months of release). Which camp does Microsoft want to align with, there? Every Windows phone 7 device released should receive Windows Phone 8, even with some features disabled. Anything less is punishing every existing customer, in the hope that you ll attract new ones not a winning strategy for a fringe platform whose biggest evangelists are its users. Fix IMAP. IMAP isn t hard. Yet WP7 never seems to work properly with a subset of my mail, never showing the message body & just saying Downloading forever. Fix it. Bing sucks. Bing s search results are terrible. Either do something to make them bearable, or allow me to pick which search engine I get when I hit the search button. A Google live tile isn t the same thing. Make killing apps easier. I know you stole the WebOS card view for multitasking (hold the back button) please also steal the WebOS ability to close apps. I don t want to have to go into an app and bash back repeatedly until it quits. This is particularly annoying for Internet Explorer. Make reinstalling apps easier. If I want to install every app I previously had installed on a new device, without restoring a backup, this should be easy. There are third party apps which try to plug this gap. Find a way to support copyleft. I d like to port a few C# apps to WP7, but because they re LGPL, I can t. The code s copyright holders would have no issue with their code being on WP7, as long as end users have a mechanism to replace the libraries, so why not find a way to allow this? e.g. when compiling an app, let me mark a library as user-replaceable , then allow for some mechanism where an end user can replace those assemblies with their own version. Let me use multiple Google calendars. WP7 only lets me add/see appointments on my default Google calendar. I want to add/see things on my wife s calendar, which is shared with me. WebOS can do this. MTP-Z is the devil. I do not need or want encrypted end to end communication between my PC and my camera device, to transfer a photo off. I do not need or want encrypted end to end communication between my PC and my MP3 player to transfer a photo on. Let s be honest, the only reason for MTP-Z is to enforce DRM on Zune-rented music tracks and honestly, there s no good reason to require MTP-Z for *all* communications if all you want to do is protect one folder or file extension. Now, since MTP-Z theoretically forces me to use Zune for many tasks better handled by other apps, now I get to write multiple criticisms of Zune s desktop app and as long as MTP-Z is enforced, every Zune failing is a Windows Phone failing too. Zune: Support Windows codec infrastructure, and transcode where needed. Windows Media Player can play Ogg Vorbis files. No, not out of the box, but if one installs the required codecs. Zune should support the same files as WMP if you want to ensure people don t try to copy files to a portable device which are not supported on that device, then you should have an API in place to allow for pluggable seamless transcoding of files as required Banshee allows me to do this (e.g. to copy files I have as .flac to devices which do not support it). Zune: Search my tracks, not the web. Zune s searching is terrible it doesn t do as-you-type searches, and when I hit enter, matches from my collection are given a tiny little space compared to matches from the Zune music store. Let me easily pick the track I feel like listening to, don t make it a chore Zune: Let s solve metadata together. I absolutely love how nicely the Zune app on desktop and on phone shifts as appropriate to the currently playing artist (e.g. changing the lock screen to an image of the artist in question). However, Zune doesn t make it obvious how to set an album s metadata to support this, and it s particularly frustrating when it s a minor difference of spelling causing a track not to get the nice treatment e.g. UNKLE versus U.N.K.L.E. . Either start making heavy use of audio fingerprinting services like MusicBrainz to fill in metadata, or allow me to search for fully supported artists when filling in track metadata Zune: Random playlists are useless on devices. I like smart playlists. In Banshee, I have one to pick 12GB of random tracks, which I can sync to my phone. I can t do this with Zune. If I try to just sync all my random music to my phone, it errors out due to lack of space. If I have a random playlist, the random selection changes multiple times during a sync resetting the sync, wiping out half the tracks that were transferred on, and starting again. As a result, the sync goes on for literally hours, never ending up with more than a gig or so of tracks on the phone. Random playlists should be freezable, so I can transfer them to my device in peace, then get a new random selection when I want. So, that s my list of miserable failure and it s still a less painful list than any other mobile OS I ve used. Perhaps one day Android will approach being usable, perhaps Blackberry s BBX will actually appeal to human beings rather than corporate IT managers, and perhaps Mozilla s delightfully named Boot to Gecko will get some traction. Who knows. All I know is, My Lumia 800 is the best phone I think I ve ever owned, and it s important for anyone working in the mobile space to understand why.

Michal Čihař: Weblate 1.0

After few weeks of heavy testing, Weblate 1.0 has been released today. Compared to 0.9 there are just minor changes and bug fixes. The most important thing is that Weblate should be now really ready to use :-). Full list of changes for 1.0: You can find more information about Weblate on it's website, the code is hosted on Github. If you are curious how it looks, you can try it out on demo server. You can login there with demo account using demo password or register your own user. Ready to run appliances can be found in SUSE Studio Gallery. Weblate is also being used https://l10n.cihar.com/ as official translating service for phpMyAdmin, Gammu, Weblate itself and others. If you are free software project which would like to use Weblate, I'm happy to help you with set up or even host Weblate for you (this will be decided case by case as my hosting space is limited).

Filed under: English Phpmyadmin Suse Weblate 0 comments Flattr this!

Raphaël Hertzog: The Debian Administrator s Handbook is available

The Debian Administrator's Handbook CoverI am so glad that we managed to complete this project. Roland and I have spent countless hours on this book since December, both for the translation itself and also for all the things that we tend to forget: a nice book cover, a great book layout for the print version, coordinating the work of reviewers, registering as an editor to get an ISBN, etc. I think I will come back to this in a future article because some parts of the story are interesting. In the mean time, enjoy the DFSG-free Debian Administrator s Handbook: Check out the official announce (there s a discount for early buyers of the paperback).

12 comments Liked this article? Click here. My blog is Flattr-enabled.

DebConf team: Submit your greatest ideas as a DebConf12 talk (read: Call for Papers reminder) (Posted by Gunnar Wolf)

DebConf12 is drawing closer and closer! Have you ever been to a DebConf? You will surely agree with us: It s a life-changing event! It s one of the greatest geek gatherings in the world! It s something you can t afford on missing out! It s wait.. Oh, sorry, I had my spam mode set to highest. But still, that does not make it any less true. And one third of May has already passed. This means that the first deadlines are just around the corner: next Tuesday (15-may), sponsored registration will close, so make sure to register before it s too late. But wait wasn t this about the call for papers? Right, that s not the point of my post, I wandered off again. I m sorry, I just visited Managua last weekend (Holger will soon tell you about our visit), and it s impossible to keep the mind off the excitement. I wanted to ask you to share your greatest, latest ideas or projects. DebConf is about many things But one of its most important features is its rich set of talks, usually with very high and interesting contents in the technical, social, organizational levels Or several of them at once. As always, you will be able to submit talks until a day before you present it. However, it s best for your intended audience to know bits about your proposed topic, possibly even to share some information beforehand, so that the exposition can be as smooth as possible and the interaction during the talk even more And this is specially true for BoF sessions. However, we do have one advertised deadline: Talks submitted up to June 1st will be considered to be pre-scheduled. This means, to be part of the officially announced program, and have guaranteed coverage of our (always great) video team. DebConf Tracks But maybe you don t feel comfortable presenting a topic. Or you are, but you think it would be important to have several thematically related talks be grouped together. And if you are interested in this group of talks, you will probably know who would be more interesting to invite to present the topics - And will be able to prod them to do so. You can request to coordinate a track. That will ensure you get a contiguous block of timeslots for the talks you schedule, and do a great contribution to DebConf. To add your track, please mail talks@debconf.org. Please, specially if you do so in the few days following May 9, send me a copy to gwolf@gwolf.org, as it seems the alias is not yet set up. Tutorials and mentoring This year, we will have a high number of very motivated attendees from the many countries in the Central American region who want to get started in helping Debian, but have not yet found how to do it. Usually we would see local communities as prime material for DebianDay However, many of them are more interested in getting hands-on tutorials and be mentored into contributing to Debian. So, if you are part of a team working on a given aspect of Debian, or want to get people involved into your project, register it in the Tutorials and mentoring track. See you all soon, very soon, in tropical Managua for the hottest DebConf ever! (oh For those who remember days long past in Helsinki: There is even a sauna! ;-) And it s GREAT)

9 May 2012

Leandro Gómez: Are you going to DebConf12?

There s only a few days left before the sponsored registration for DebConf12 closes. If you haven t registered yet, please do it before May 15th and consider submitting a talk. We re looking forward to see you in Managua in July!

Next.

Previous.