Search Results: "pm"

12 August 2008

MJ Ray: Don t Attack Your Users

It seems to me like basic business common sense not to attack your software’s users, because they’re people who might fund your future development work, when they want some new feature adding or some adaptation making. We should hope that this audience will become co-promoters, co-developers or co-producers of free and open source software in the future. Indeed, one of the basic lessons at our webmaster cooperative is to try to direct enquiries about software we’ve co-produced to somewhere useful, even if the question isn’t really much to do with us (because it’s about some part we didn’t produce or it’s something we’re no longer funded to work on), or even if we suspect the questioner has done something very silly. This approach has worked well so far. So, just don’t attack your users. It’s not on. Don’t do it. This basic lesson of not attacking users doesn’t seem to have been learned in software industries in general. Most software comes with a very restrictive “End User License Agreement” that seems to treat the user as if they are a potential criminal and grabs as many rights as possible for the software producer. I expect that Microsoft’s new post-Windows operating system will continue this approach and that the user-tracking possibilities of internet-centred operation will be exploited as far as legally possible. Hopefully, we’ll continue to see pre-installed Linux growing strongly in UK as Bristol Wireless describe. However, this pales into insignificance compared to many media companies. One of the worst offenders is Bristol-based TV Licensing who send us a “pay up or else, you potential criminal”-style letter each year. If there’s ever a reform that makes BBC subscription voluntary, they will probably reap the seeds of hatred that TVL have sown by attacking their audience. I have quite a lot of admiration for people like Martyn Drake who are fighting a noble fight in things like TV Licensing - the war begins! but I wonder whether media companies will learn not to attack their users before they cease to exist.

11 August 2008

Michael Banck: 11 Aug 2008

OpenSync update To give some update on the state of OpenSync in Debian, I have uploaded libsycml-0.4.7 to experimental a couple of days ago. This is significant in sofar as a lot of development and bug-fixing (mostly by Michael Bell) happened for this release, as well as some committment to maintaining an API and at least responsively versioning the library. In order to use libsyncml-0.4.7 with OpenSync, a newer libopensync than 0.36 is needed; however, current OpenSync trunk has seen a lot of changes in plugin handling and plugins need to get ported to the new API. So I uploaded the last known-working revision of OpenSync along with corresponing revisions of the file-sync and syncml plugins, the vformat module and a rebuild of msynctool to experimental for now. I did not have the time or energy to migrate/upload the other plugins yet, and as it seems that OpenSync-0.37 will only ship with ported file-sync and syncml plugins, it might not make much sense. I also took over maintainership of the related wbxml2 package, and upload a patch by Michael Bell which seem to fix a lot issues people are having with SyncML. The good news is that it seems all of the new features for a 0.40 stable OpenSync release have been finished according to the roadmap , most notably a common plugin configuration system and the machinery for a migration path from 0.22 to 0.40 configurations (plugins still need to support/implement that I believe), so no more big API changes are expected and the focus will be on bugfixing and plugin discovery from now on. This means developers will be able to start porting their plugins to the 0.40 API once 0.37 is out and front-end authors can start to take a look at the architectural changes which were made to facilitate their jobs. My hope is that conduit will be able to leverage the OpenSync technology and introduce a solid GUI for this (as kitchensync does for KDE), making syncronization finally work on the desktops. From the Debian packaging point of view, I have been mostly on my own now for the last couple of months. However, I recently registered an Alioth project in order to maintain the packages in a subversion repository (I have not yet decided whether it is worth importing the 0.22 packages targetted at lenny), and people who are interested in helping should contact me.

8 August 2008

Martin-Éric Racine: brainstorm: new LPC dongle design

One of our most popular products at the dayjob has been our Programmable LPC Dongle. It has seen widespread use as an embedded hardware development and debugging tool and is particularly popular among Coreboot developers as a ROM emulator, because of its low price and because we publish the FPGA code under the LGPL. Unfortunately, our current LPC Dongle product is nearing end of life, because some components are no longer available. We're currently designing a brand new Programmable LPC Dongle and, noticing the plethora of improvement ideas we already received from the Coreboot community, we decided to widen the scope and invite a larger group of hardware developers to tell us what features they want to see in our next-generation Programmable LPC Dongle. Anyone interested in participating in this brainstorm is welcome to send me their ideas to first-middle.lastname@artecgroup.com by September 1st 2008. While we cannot guarantee that every idea submitted will be used, we will definitely be reading all the feedback we receive.

6 August 2008

Matthew Garrett

Testing 2.6.27-rc2 with the current released (not development) BIOS on the Foxconn G33M reveals the following:Summary: Almost all problems caused by bugs in Linux, one problem caused by BIOS vendors interpreting the ACPI specification differently to the Linux implementation and trivially worked around. No sabotage.

Thanks very much to Carl at Foxconn for being able to get me information about what was causing the reboot issue - I spent significantly longer putting the system together than I did fixing it.

5 August 2008

William Pitcock: LSB 4 doesn t fix things any better than LSB 1, 2 or 3 did.

As mentioned elsewhere, LSB 4 is due out soon, and won’t really make a lick of difference when it comes to improving compatibility with non RPM/redhat-like systems. With software appliances and software as a service becoming more relevant, and appliance-oriented non-RPM distributions like rPath, Ubuntu JeOS and Defusion coming around that offer equal (or arguably better) value to customized Fedora/RHEL/CentOS and improved administrative ability due to using tools not stuck in the 1990s (RPM, I am looking at you here), one would think that the LSB working group might actually want to make LSB not suck. Right now, Debian derivitives like Ubuntu JeOS and Defusion can compete by using alien, and rPath has the RPMPackageRecipe for conary, but these are kludges and carry their own share of problems. So, why does the LSB require a specific format? There’s no reason for them to. Really, LSB compliance is a redhat-only club. Not just an RPM-only club… last time I checked, SuSE is in the same boat as everyone else and they use RPMs. A lot of the LSB needs to simply be ripped out in order to do any good. Until the LSB working group is willing to drop a lot of the RedHat-isms they have had, non-RedHat distros will always have problems complying. What about source-based distros like Gentoo for example? There is really no easy way they can comply by default (on the other hand, do they care to?). To put things simply, the LSB sucks. Here’s why: Ideally, the LSB spec would define a config format capable of describing how the system worked, and all of that, but it doesn’t. Until it does, then the LSB spec is worthless, because it can’t handle all distributions (even the common ones).

Kartik Mistry: BarCampAhmedabad2


* On Sunday, I attended BarCamp and gave small talk on GujaratiLexicon.com. Session was well received and there were number of good questions and feedback from people. Apart from learning something new and meeting new people, nice campus of IIM-A was attraction for me. Some bits from event, 1. IIMA campus is running Windows network, No wifi was provided during camp (bah!) 2. Came to know about osx86 project 3. Food was good, specially: Samosa! 4. CMS was hot topic during camp 5. Discussion kind of session were on top rather than showing slides (and, I had to use Windows machine as projector cable was glued with monitor there!) 6. Met Harit and friends and had nice discussion from how to configure GPRS connection in Linux to how to bundle Java application on Windows :) I left event around 4 PM after Tea break. Pictures

4 August 2008

Russell Coker: Lenny SE Linux on the Desktop

I have been asked about the current status of Lenny SE Linux on the Desktop. The first thing to consider is the combinations of policies and configurations. I will number them if only for the purpose of this post, if the numbering is considered generally helpful it could be more widely adopted to describe configurations.

  1. Default configuration. This has the default policy and is configured with all users having the domain unconfined_t and daemons such as POP servers are allowed to access home directories of type unconfined_home_dir_t. This allows such daemons to attack privileged user accounts.

  2. Some restricted users. This is the same as above but with some users restricted. Daemons such as POP servers are only allowed to access the home directories of restricted users. This means that if a user is to have an unconfined account and receive email they must have two Unix accounts or receive their mail under /var/spool/mail. This is one setsebool command and one (or maybe a few) “semanage login -m” commands from the default configuration.

  3. All users restricted. The system administrator has the domain sysadm_t and users have domains such as user_t. This requires a few more semanage commands. It is equivalent to the old strict policy.

  4. MLS. This is anything that is based around the MLS policy.

Currently I have two Desktop machines running Lenny (a test machine and my EeePC) and one server. I have only just switched my test machine to enforcing mode so have no good data on it (apart from the fact that I can boot it up and login - which is always a good start). The server is running in permissive mode because I have not yet written the policy to allow the POP server to read from unconfined_home_dir_t. I could get it working by switching from level 1 to level 2 or 3, but I want to get level 1 server policy working for the benefit of others else first. My EeePC however is fully functional, I have been doing some work on it - that mostly means running a ssh client under GNOME but that’s OK (desktop environments such as GNOME and KDE are quite complex and demanding, getting a machine to boot and run such a desktop environment tests out many parts of the system). It’s only at level 1 for the moment because I want to get level 1 working everywhere before moving to the higher levels. I want to get things ready for real users ASAP. With the way the policy is managed now it will be possible to move from level 1 to 2 or 3 without rebooting or interrupting running services. So once users have systems running well at level 1 they can easily increase the security at a later date. The problems that I have had are due to text relocations in libraries (see my previous post about execmod permission [1]). I’ve filed bug report #493678 against libtheora0 [2] in regard to this issue and included a patch from Fedora (which disables the non-relocatable assembly code in question). It seems that upstream have some new assembler code to try and fix this issue, so hopefully we’ll have something that can make it into Lenny! I’ve filed bug report #493705 against libswscale0 for the same issue [3]. I included a patch to turn off the assembler code in question but that was not well received. If anyone has some i386 assembler skill and some spare time I would appreciate it if you could try and find a way to make the code position independent while losing little or no performance. One thing to note is that I am now using an Opteron 1212 (2.0GHz dual-core) system for compiling, I run the i386 DomU with a 64bit kernel (I expect that 32bit user-space runs faster with a 64bit kernel than a 32bit kernel), and the disks are reasonably fast. Even so it takes about 15 minutes to build libswscale0 and the other packages from the same source tree. Previously I was using a 1.0GHz Pentium-3 for my Lenny i386 development until I had the libswscale0 build process go for more than 90 minutes before running out of disk space! If your build machine is old enough to only be 32bit then you should probably plan on watching a movie or going to bed while the build is in progress. I have built packages that work around the above bugs and included them in my Lenny repository [4]. If you take the packages from that repository plus the Lenny packages then you should have a functional desktop system at level 1. I would appreciate it if people would start testing that and providing feedback. One important issue is the discovery of libraries that want shared stacks, text relocations, and executable memory. The deadline for fixing them properly is even more of a problem due to the number of people who have to be involved in a solution (as compared to the policy where I can do it on my own). One finally problem is a bug in xdm which causes it to give the wrong context for login sessions due to having an old version of the SE Linux related code [5]. Due to a combination of this and some policy bugs you can not login with xdm. This is not a hugely important issue as most people will use gdm (which has the newer patch) or kdm (which has no SE Linux patch but can use pam_selinux.so). Also another option is wdm which works with pam_selinux.so. I’ve had a response to my bug report suggesting that there’s a bug in the patch (which was taken from gdm so maybe there’s a bug in gdm code too). I haven’t responded to that yet as I’ve been concentrating on the things that will make the most impact for Lenny. At this stage I’m still unsure of when the release team will cut me off and prevent further SE Linux related fixes from going in Lenny. I need at least one more update to the policy packages before Lenny is released. I could release one right now with some useful improvements over what is currently in unstable, but am waiting until I get some other things fixed. If I get everything fully working at level 1 (both client and server) before Lenny then I will provide a similar status report for users and testers of levels 2 and 3. I don’t expect that I will even get a chance to test level 4 (MLS) properly before Lenny releases.

Marcela Tiznado: When did we start attacking each other?

So, I should be at DebCamp, but I'm back home after driving 800km in one day.  
Why? I still don't know.

The main reason for this post is the irrational and unilateral response I got
from the DebConf Orga Team, with no right to replica of any kind, and with
the violence and humiliation we were treated with. I've helped to make
3 DebConf's possible, and have been involved in many ways for the past years
in Debian, so this shocked me deeply.

The short story is that there was an extra bed in the room I was staying in, the
person who was suppose to be in that bed is a close friend of mine, so I asked
if someone else could use it while they weren't, since that meant I could take
the necessary equipment that I managed to get for DebConf, and also introduce
to Debian someone who is very active and well known in our local community
(and also part of the umbrella foundation used for local finance issues).
I was excited about getting there, like every year. Just to make this extra
clear, this person had already booked the full week of DebConf, just not
DebCamp, as he previously thought he couldn't attend. When he found out he
could, he was thrilled to be able to go and help setup. So, I made the mistake
of not notifying the Orga team about the switch. I did this because it truly
was harmless action, where a bed which would otherwise be wasted would get
used, and, I did not notify the Orga team because they've been very
aggressive, inflexible and unhelpful throughout the planning of the
conference. This doesn't justify it, just explains why someone who generally
is helpful decides to take the wrong path to solve something.

Up to here, nothing very exciting. What made this special, is that when one
of the organizers, Margarita Manterola, found out about the switch, instead
of coming to talk to me, even though she's known me for *years*, she went
and informed the hotel that somebody had committed a crime, and checked in
under a different name, as if me or the person that came with me where
some random stranger. All I can say is, WTF?

Let me stress this, the email that was sent out[1] twisted the facts, to the
extent that some of them are a lie, like the problem arrived at check-in,
when it actually happened while we where napping a few hours after we had
arrived, and any effort made by the Orga team with the hotel where wasted,
as it was one of them who had originally created the problem.

Instead of solving this among us as a group, and, again, "solve" is a
bureaucratic thing, because no one was being harmed, Marga decided to
actually *harm* me personally, the person who I had brought, and DebConf
as a group. What got solved? Nothing. I left, along with someone who
would of otherwise been helping out build DebConf, while the Orga team
demanded a ridiculous fee for me to stay in the hotel.
Rules are rules, I understand, but I also understand everybody listens to
downloaded music, people in Germany install[2] nmap, and a very long list
of rules that we tend not to follow because they're unreasonable or
unnecessarily complicated.
Is this really what DebConf is turning into?

All I can say is I'm very sad and shocked that the people I've worked with
for so many years decided to condemn me over such a meaningless issue, and
especially that the local team, Martin Ferrari, Damian Viano, Maximiliano
Curia and Margarita Manterola would do such thing to "one of there own",
and that the international Orga team would mindlessly follow through with it.

I apologized to the hotel, I do want to apologize to the innocent people who
had to deal with this, and, even though my intentions where good and unselfish,
I regret what happened.

Despite all of this, I'm still deeply committed to Debian, have worked during
the year and deserve to relax and enjoy it, so I will be there for DebConf
as a regular attendee.

See you there!

[1] http://lists.debconf.org/lurker/message/20080802.231856.66c7d3fd.en.html
[2] http://it.slashdot.org/article.pl?sid=07/05/31/1629259&from=rss

2 August 2008

Ben Armstrong: Bits from the Debian Eee PC team, summer 2008

As always, we’re doing lots of interesting and significant things and have more good ideas than we have people to do the work.  If you have an Eee PC or are planning to get one, or are otherwise interested in our work, some of which has uses beyond just the Eee, here are some highlights: Earliest Eee models supported in Lenny Lenny will release with the atl2 ethernet driver and the non-free madwifi-source now works with the earliest Eee models as well, so our patched version is no longer needed.  This means Lenny will work with all of the earliest models of the Eee PC: 701 (2G and 4G surf, 4G, 8G) and 900! All we need now for full support in Lenny is to replace the non-free wireless driver with the free ath5k driver when it is ready. Free drivers Nick Kossifidis has submitted patches on linux-wireless supporting the Eee models currently supported only by the non-free madwifi in ath5k.  This means we’ll soon realize our goal of a completely DFSG free system for the earliest models of the Eee.  By 2.6.27, or at the latest 2.6.28, these models will be supported.  Then we will see about making a patch to support whichever kernel makes it into Lenny. New models Model 901, 1000 and 1000H users are now able to install using the atl1e ethernet driver from eeepc.debian.net.  Support for wireless and other aspects of the new hardware will follow soon.  The debian-kernel team was prompt to add atl1e to 2.6.26 which has just been uploaded to sid.  We hope 2.6.26 makes it into Lenny. Wireless installer Glenn Saberton has been doing an upstanding job adding wireless support to our custom Debian-installer.  We have supported WEP authentication for several releases, now, and a beta version supports WPA.  Glenn is also making progress with these patches upstream so that non-Eee Debian users will benefit from our work. LXDE is in Lenny LXDE has entered Lenny, thanks to Andrew Lee.  It is a quite lightweight desktop environment that is made with the Eee PC in mind. Live images Two flavours of Debian-live USB images are available: a demo of the LXDE desktop and a minimal console-only image for rescue/backup.  The images are still in alpha stage of development.  If you’d like to help, give us a shout.

More interesting things are planned for the future that benefit Debian as a whole.  With a small amount of work patching live-helper, anyone will be able to make a live image that includes a customized Debian-installer. Mobile device initiative This month on debian-devel, there was some interesting discussion about Debian support for the Intel Atom processor and a possible mobile net device initiative.  That’s something we could get behind, if anything comes of it. Wiki translation Robert Epprecht has been keeping the German wiki translation in good shape, but we could always use some more help with any of the translations. New members welcome If you’d like to join us, check out our site at http://wiki.debian.org/DebianEeePC and drop us a note on our list or join our irc channel and talk to us about what you’d like to do.    

30 July 2008

Matthew Garrett

The Linux Plumbers Call for Papers is open for another day or so. It's looking like we'll have an excellent spread of interesting power management topics, but if you've got anything interesting to say then throw it forward. We're looking for kernel issues that have an impact on userspace, userspace issues that need kernel support and anything else that involves the interesting interactions between the two.


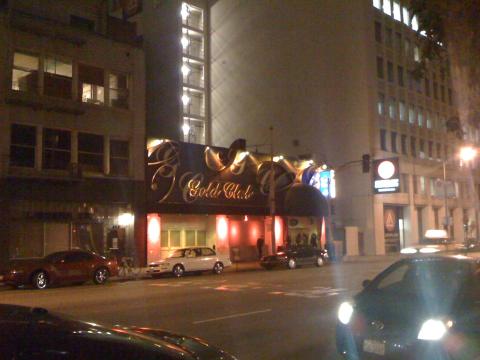
Hats for everyone and cab it to the Gold Club

San Francisco has been somewhat hectic, but yesterday included a quick trip to the office to discuss community involvement in improving power management. Look forward to developments there. Independently, I now join Brian the guy who had been clean too long to get onto the drugs rehab program (hurrah voicemail) in being an ex-owner of my US phone number. Probably best to delete it if you have it.

In other news, Foxconn are sending me a board with the "controversial" AMI BIOS in order to figure out what's going on. Progress by this time next week, with luck.

29 July 2008

Wouter Verhelst: Debian testing

Martijn isn't too sure about Debian testing, though he doesn't go into much detail about the "not sure" bits. Well, Martijn, even though I could really use some more detail, let me make an attempt:
  • Debian Testing isn't the perfect thing to use at all times. Especially right after a release, when people start uploading all kinds of crap to Debian unstable, it's probably better to stick with Debian Stable for a while. Right before a release (such as the time we're in right now), however, using testing on a laptop is probably a much better choice if you want reasonable up-to-dateness of the software on your system.
  • In case you didn't know, testing does get security updates these days (since quite a few years already, actually).
  • In the pre-sarge days, installing Debian almost required some magician to do it for you. These days, however, installing Debian is much easier, so if you're afraid of that, don't be. Also, the default "desktop" installation can compete with Ubuntu in many areas already, although there surely is some more work to be done.
  • Debian is a bit more conservative with updates than is Ubuntu, even in the development distributions ('testing' and 'unstable'). This is generally a good thing if you don't want your system to break in all kinds of "interesting" ways right when you don't have the time (although that might still happen, though more so with unstable than with testing).
  • Most of the bits that are available in Ubuntu are also available in Debian; and in Debian, in most cases they're done more thorough, because of the difference between Debian's and Ubuntu's approach to package maintenance: in Debian, every package has its own maintainer who is solely responsible for the package; in Ubuntu, maintainers are responsible for a whole lot more packages, which improves their view on the distribution as a whole, but makes it more difficult for them to follow up on the state of individual packages.
In all, I still prefer Debian over Ubuntu, mostly because of the higher attention to detail you'll find in Debian; I find that ubuntu developers usually don't have the time to pay too much attention to pesky details. This makes the system work slightly better. But, of course, YMMV, and if you decide to stay with Ubuntu because you think it works better in your particular use cases, more power to you!

MJ Ray: How to Install Koha 3.0.0 on MacOS X 10.5

This is a pretty technical note, which I’m posting here for review and hopefully to help other people. The reinstall I mentioned last week was a MacOS X 10.5 server, so this time I installed Koha more simply and took more notes. I don’t want to put this in the distribution as INSTALL.osx, for reasons mentioned below. Also, I’d be very happy if people replaced all osx servers with debian ones, or at least some sort of tidy GNU/Linux. The sysadmin installed XCode and fink for me and I ran
fink install apache2 apache2-dev mysql mysql15-dev
without any great event. I also re-used an old, imperfect, local finkinfo/idzebra.info to
fink install idzebra idzebra-shlibs
Next, I used the extremely horrible command
fink list $(sed -n -e “/PREREQ_PM =/,/ / ;s/^[ ']*//;s/::/-/g;s/’.*\$/-pm588/;/-.*-pm588/p; ” Makefile.PL tr A-Z a-z)
inside an unpacked koha-3.00.00.094 folder to find out which modules fink had packaged already. Something similar can be done for debian and ubuntu, using apt-search or dpkg instead of fink and a libperl- prefix instead of a -pm588 suffix. (I think all systems should do something like that. Then we could merge the INSTALL.*s into the main INSTALL because they lag behind.) Three of those, I copied to /sw/fink/10.5/local/main/finkinfo and edited slightly (usually to increase the version: dbd-mysql-pm, html-template-pm, xml-libxml-common-pm, xml-libxml-pm.info and xml-simple-pm.info… also in my fink-10.5 folder) and then ran
fink install dbd-mysql-pm588 text-iconv-pm588 xml-simple-pm588 data-dumper-pm588 digest-md5-pm588 file-temp-pm588 getopt-long-pm588 html-scrubber-pm588 list-util-pm588 list-moreutils-pm588 mime-base64-pm588 net-ldap-pm588 test-harness-pm588 text-wrap-pm588 time-hires-pm588 unicode-normalize-pm588 xml-dumper-pm588 xml-libxslt-pm588 xml-rss-pm588 yaml-syck-pm588
to install those modules. For the remaining modules from CPAN, I set PERL5LIB to my new Koha folder (export PERL5LIB=/Library/WebServer/Koha/lib:/Library/WebServer/Koha/System/Library/Perl/5.8.8/:/Library/WebServer/Koha/lib/perl5/site_perl/:$PERL5LIB) and ran perl -MCPAN -e shell, telling the configuration screens to use PREFIX=/Library/WebServer/Koha (so install into the Koha folder instead of splattering across /System/Library). Then the command
install Bundle::KohaSupport
just worked, thanks to excellent work by Mike Mylonas and others. Finally, all that was left was to run the normal installation in the koha-3.00.00.094 folder, picking the “single” configuration and ignoring “make test” failure (because it’s a work in progress and this is RC1), edit the /Library/WebServer/Koha/etc/zebra/*cfg to point at /sw instead of /usr, symlink koha-httpd.conf into /sw/etc/apache2/sites-available and run the a2ensite commands, copy the service plist files into /Library/LaunchDaemons and load them into launchctl, browse koha and start testing it. Simple(!) It only took me a full day of work to figure that out and do the reinstall… compared to under 2 hours from scratch on debian at the moment. Maybe it’s faster if you know the OS better and/or aren’t trying so hard not to splatter stuff across the base system. Did I do anything wrong above?

28 July 2008

Russell Coker: Biba and BLP for Network Services

Michael Janke has written an interesting article about data flows in networks [1], he describes how data from the Internet should be considered to have low integrity (he refers to it as “untrusted”) and that as you get closer to the more important parts of the system it needs to be of higher integrity. It seems to me that his ideas are very similar in concept to the Biba Integrity Model [2]. The Biba model is based around the idea that a process can only write data to a resource that is of equal or lower integrity and only read data from a resource that is of equal or higher integrity, this is often summarised as “no read-down and no write-up“. In a full implementation of Biba the OS would label all data (including network data) as to it’s integrity level and prevent any communication that violates the model (except of course for certain privileged programs - for example the file or database that stores user passwords must have high integrity but any user can run the program to change their password). A full Biba implementation would not work for a typical Internet service, but considering some of the concepts of Biba while designing an Internet service should lead to a much better design (as demonstrated in Michael’s post). While considering the application of Biba to network design it makes sense to also consider consider the Bell LaPadula model (BLP) [3]. In computer systems designed for military use a combination of Biba and BLP is not uncommon, while a strict combination of those technologies would be an almost insurmountable obstacle to development of Internet services I think it’s worth considering the concepts. BLP is a system that is primarily designed around the goal of protecting data confidentiality. Every process (subject) has a sensitivity label (often called a “clearance”) which is comprised of a sensitivity level and a set of categories and every resource that a process might access (object) also has a sensitivity label (often called a “classification”). If the clearance of the subject dominates the classification of the object (IE the level is equal or greater and the set of categories is a super-set) then read access is permitted, if the clearance of the subject is dominated by the classification of the object then write access is permitted, and the clearance and classification have to be equal for read/write access to be permitted. This is often summarised as “no write-down and no read-up“. SGI has published a lot of documentation for their Trusted Irix (TRIX) product on the net, the section about mandatory access control covers Biba and BBLP [4]. I recommend that most people who read my blog not read the description of how Biba and BLP works, it will just give you nightmares. The complexity of either Biba or BLP (including categories) is probably too great for consideration when designing network services which have much lower confidentiality requirements (even the loss of a few million credit card numbers is trivial compared to some of the potential results of leaks of confidential military data). But a simpler case of BLP with only levels is worth considering. You might have credit card numbers stored in a database classified as “Top Secret” and not allow less privileged processes to read from it. The data about customers addresses and phone numbers might be classified as “Secret” and all the other data might merely be “Classified”. One way of using the concepts of Biba and BLP in the design of a complex system would be to label every process and data store in the system according to it’s integrity and classification/clearance. Then for the situations where data flows to processes with lower clearance the code could be well designed and audited to ensure that it does not leak data. For situations where data of low integrity (EG data from a web browser) is received by a process of high integrity (EG the login screen) the code would have to be designed and audited to ensure that it correctly parsed the data and didn’t allow SQL injection or other potential attacks. I expect that many people who have experience with Biba and BLP will be rolling their eyes while reading this. The situation that we are dealing with in regard to PHP and SQL attacks over the Internet is quite different to the environments where proper implementations of Biba and BLP are deployed. We need to do what we can to try and improve things, and I think that the best way of improving things in terms of web application security would involve thinking about clearance and integrity as separate issues in the design phase.

25 July 2008

Jordi Mallach: GNOME-Mud 0.11

GNOME-Mud 0.11 was released yesterday. This was probably something unexpected to those who follow the mailing list, as it's the first release in over three years. Back in 2006, Les Harris started contributing to the project and started a major rewrite of the program. Things looked very promising, with the program being ported to newer GNOME technologies and standards and being basically rewritten from ground up. However, Les got hit by Real Life and being the project's only real hacker, development basically stopped for nearly two years. On June, I was tempted to remove my irssi subscription to #gnome-mud; all I did was idling or telling people who popped by that nothing was being done and that wouldn't change unless someone rolled up their sleeves and finished up the nearly ready 0.11 release. A few days after considering declaring GNOME-Mud dead, Les joined IRC after more than a year of no contact, recovered his GNOME account password and started to commit the missing bits at an awesome pace. A few weeks later, 0.11 was done, with even more features than originally planned (support for more advanced MUD protocols like MSP or ZMP, for example) and I finally found the time to make a tarball and publish it. Les has lots of plans for the next release, and I hope my old wish of seeing GNOME-Mud becoming a MUD client that is comparable to the classic zMud will soon be a lot closer. The foundation set by this release certainly will make it easier to accomplish. As always, if you want to contribute, we'll be happy to help you out on #gnome-mud at GIMPnet, or in gnome-mud-list@gnome.org.

22 July 2008

Russell Coker: Bad Telstra

77020 packets transmitted, 18029 received, 76% packet loss, time 77049435ms
rtt min/avg/max/mdev = 20.026/130.848/2245.752/287.550 ms, pipe 3 Above are the ping results from pinging my server (hosted on a business DSL connection). Telstra stuffed up and appear to have entirely disconnected DSL for a few suburbs (based on reports from a client who has several clients in that region that all went offline simultaneously). It’s affected at least two ISPs (every DSL service uses Telstra’s backbone). The above ping results show almost 17 hours of outage, but it was really more like 18 (I didn’t start pinging until I realised it was down). Telstra’s response to the problem reports (which my client raised via two ISPs) was that it would take until the end of the next business day. The problem was reported at 10AM, so Telstra was apparently happy with two entire business days of outage. I think that the root cause of such problems is the terrible performance of Sol Trujillo [1] (or “Telstra’s Sole True Hero” as suggested in Crikey [2]). Under Sol’s leadership Telstra stock has not performed well (it’s a monopoly - it’s supposed to reap money), it’s lost market share in every area where competition is permitted and it hasn’t made it’s customers happy. Sol is taking an approach to business that works well for some big companies in the US (and for the mining and automative industries in Australia). He has been trying to force the government to extend the Telstra monopoly with the Fibre To The Node (FTTN) plan [3]. His idea was to have small Telstra boxes (nodes) spread around the suburbs with short copper runs to each home, each node would have absolutely no spare space for other ISP equipment and therefore the other ISPs would not be able to provide a service. The claim was that FTTN was needed for decent performance but ADSL2+ has been shown to work well in the areas where FTTN was proposed. Telstra even sent out brochures to stock-holders encouraging them to lobby members of Parliament on behalf of Telstra’s rent seeking [4]. However Australia is not like the US and this didn’t work, they couldn’t even get Telstra stock holders to support such plans. Speaking for myself, my interests as a Telstra stock-holder (and I own more Telstra shares than the median stock holder) are vastly outweighed by my interests as a consumer of telecommunications services. I would like to see the government nationalise the local loop and the exchange buildings and then provide fair and equal access to all telephone companies and ISPs (including Telstra). Then we can have true competition in this market and the companies that provide the best services will win. Currently Telstra resembles one of those inefficient Soviet monopolies. We need some capitalism in the telco industry!

Axel Beckert: Blosxom 2.1.0 released

Today I had the honour to prepare and announce the first Blosxom release after exactly two years and six days. The primary cause for the Blosxom 2.1.0 release date this week was to get our development efforts of the last two year into Debian Lenny with a nice version number (i.e. one without snapshot dates in the package version ;-). The second biggest cause was that it just was time. But Debian Freezes always give you a good kick in the ass. ;-) Rhonda plans to prepare an updated blosxom package for Debian during the day. (Update 25-Jul-2008: Packages are available.) So if Planet Debian is broken in a few days, you know whom to blame: Me and my last minute bug fixes. ;-) But since you seem to be able to read this, the release shouldn’t be too broken – because of course my blog already runs the very fresh Blosxom 2.1.0 release. ;-)

21 July 2008

Joachim Breitner: One Week with an OpenMoko Freerunner

About one week ago, I received my OpenMoko Freerunner. This is an openly developed mobile phone that runs purely on Free Software. So this is what I have to tell about it.The hardwareIt was smaller than I thought, and is quite light. My girlfriend says it s ugly, but I m fine with the look of it. Besides being a GSM-phone, it comes with some nice gimmics: GPS, accelerometer, WLAN. The touchscreen works fine, although I don t have anything to compare it with.The softwareThe system it comes with, even after upgrading, is still very rough. It mostly works for doing phone calls and SMSs, but there are a number of unsolved quirks that prevent me from using the Freerunner as my sole phone for now. The suspend mode is left too often, resulting in a battery life of about eight hours, and there are issues with the audio for the conversation partners, who will hear static and echoes. But, as this is free software, there is hope that this will be fixed eventually.DevelopmentThe OpenMoko distribution is based on Openembedded, which uses bitbake for building software. So if I got it right, and this is not sure, because documentation is rare and spread, there is the git repository at git.openmoko.org, which is a copy of the openembedded git repository. This contains bitbake recipies for all the packages, which includes where they can be downloaded, the package metadata (such as dependencies and version numbers) and sometimes patches. These recipies reference upstream tarballs or subversion URLs. For the native OpenMoko applications, the source is in the OpenMoko subversion repository.One of the suggested ways of compiling software for the FreeRunner is by using a toolchain tarball, that can easily be extracted somewhere and used to build the software from the subversion repository, or other (hopefully autoconf ed) software. This builds the binaries, but does not produce proper .ipk files, so no version number or dependencies.The other way is the full openembedded setup, made easy using the MokoMakefile. This, automatically, fetches and builds everything needed for the cross compiliation and all available packages, producing the same output as can be found on the openmoko servers. Setting this up requires about 6 gigabytes of storage and takes over a day the first time, but then hacking the phone is relatively painless, as it resolves dependencies and is self-contained.The communityFor a free software project, the state of the community is very important. The OpenMoko seems to suffer from a rush of interested people on the mailing lists, so it s hard to follow real development in a mass of frequently asked questions and nice ideas from people who have neither an OpenMoko phone nor wil do any coding.On the other hand, it s not easy for new contributers. I have written some code that make sure the phone can handle numbers such as 0172/123 456 instead of the official +49172123456 in the phonebook and the SMS app, something that other users have complained about as well. But no one could tell me where and how I should submit my patches, and the mail to the mailing list with the patches and the bug report is unanswered. It is not clear, at least to me, who is responsible for what part of the project quite different to what I m used to from Debian, where there is a clear list of maintainers for each package, and a well known way of submitting patches (by going through bugs.debian.org).For interested users, I have published my branch of the git repository at git.nomeata.de, and I will hopefully add more features and bugfixes later at least when I find out how to properly contribute to OpenMoko.

Benjamin Mako Hill: OSCON and More

I'm in Portland, Oregon for the week where I'll be at OSCON. I'll be giving two talks on the final day of the conference (July 25): the first will be a 15 minute keynote on Revealing Errors at 8:45 in the Portland Ballroom; the second is a full-length normal talk on Selectricity at 11:35AM in Portland 255. It will be my first long-form talk about Selectricity and I'm looking forward to it. Because myself, a few Free Software Foundation staff members including Campaign Manager Joshua Gay, and quite a few FSF associate members will be in town, we're going to hold a small FSF Associate Members event in Portland (the first outside Boston!). It's going to be in the form of a pizza party with a few small talks from FSF folk including myself. Here are the details:

FSF Associate Members (& friends!) Event
July 22nd 6:30-9:00PM
Old Town Pizza
226 NW Davis St
Portland, OR 97209
It's free and open to all but is designed to provide a forum for members and friends. If you are an FSF member, please consider coming. If you're not a member yet, please don't let it keep you away; staff will be able to sign up new members there. RSVPs to Deborah Nicholson aren't necessary to attend but would be welcome. I'll be heading to Seattle right after the conference for a few days. If you would like to meet up in Seattle or Portland this week, please don't hesitate to get in contact.

20 July 2008

Mirco Bauer: At The End Was The Beginning: Smuxi 0.6.0 Released!

Just in time, at the end of my 3 week vacation, I released the first public version of smuxi! For people who don't know smuxi yet: I have been developing over the last 3 years an IRC client that fits the needs I could not satisfy with irssi. I was using irssi over 4 years and it's the best the IRC client I used so far. Most annoying was that it didn't integrate at all into my desktop experience (such as mouse / clipboard / theming / highlight handling). Thus irssi inspired lots of features and commands seen in smuxi. So here it comes, a flexible cross-platform open-source IRC client for the GNOME desktop, in action:
    Smuxi is built using a great software development stack, composed of: C# / Mono, GTK +,# / GNOME(#) and MonoDevelop. Interested in using or contributing to smuxi?
Head over to the official release announcement on the smuxi project website. For the Debian users and developers among us:
Debian packages for smuxi are not available yet, but will be very soon.

19 July 2008

William Pitcock: PGSQL support in dsyslog? It s more likely than you think.

dsyslog 0.3 has been released, with support for postgresql logging targets, and much more. The development of postgresql support, and extensive documentation, has been made possible by Google’s summer of code program sponsorship of Jeff Katz, who intends to contribute even more code to 0.4. It’s presently sitting in NEW, but if you want it now, you can grab it from the dsyslog website.

Next.

Previous.