Search Results: "ema"

5 March 2012

Russell Coker: LUV Hardware Library

What is it? Last month I started what I am calling the LUV Hardware Library. It s a briefcase full of computer parts that are free to LUV members which I plan to bring to all LUV meetings [1]. The issue is that there is a lot of hardware which has no great value to people and is often excess to requirements but which is still somewhat expensive or difficult to obtain and thus transferring it from the people who don t need it to people who do provides a significant benefit to the recipient but no real cost to the donor. Currently my briefcase has a range of different types of DIMM, some PCI cards, some assorted cables, a laptop SATA disk, and a bunch of other random things. Most of the stuff has been in my spare parts pile for a year or two, but some of it has been donated by other people. What we Need The next thing we need is more packaging, anti-static bags for RAM and PCI cards, sealable bags for screws, and some way of storing motherboard batteries. In terms of hardware that can be donated one thing that would be really useful is SATA disks. I m sure that there are lots of people who have upgraded the storage of their computer and kept the old drive with no real chance of using it. But there are lots of people who need such disks, for example I ve been giving away a bunch of P4 systems which lack disks and are not cabled for IDE disks a supply of SATA disks would make them a lot more usable. Also any other random electronic stuff is of interest, including non-Linux things such as mobile phones (but only if not network locked). If you have something that s big or heavy to donate then contact me via email first. Other Options Computerbank does great work in rebuilding old PCs and selling them cheaply to worthy people [2], but most of the spare hardware I get is below the minimum specs that they will accept. I m not planning to compete with Computerbank in any way, I just want to provide a useful service to LUV members who want to upgrade their PC for free. I encourage other people to do the same at other LUG meetings! Related posts:
  1. Donating old Hardware On a recent visit to my local e-waste disposal place...
  2. Giving Away Hardware For the last few years I have been actively seeking...
  3. Shelf-life of Hardware Recently I ve been having some problems with hardware dying. Having...

Benjamin Mako Hill: Unhappy Birthday Hall of Shame

/copyrighteous/images/no_happy_bday.png I roll my eyes a little when I think that Unhappy Birthday is the document I have written that has been read by the most people. The page -- basically a website encouraging people to rat on their friends for copyright violation for singing Happy Birthday in public -- has received millions of page views and has generated tons of its own media (including a rather memorable interview of CBC's WireTap). At the bottom of the page I am listed, by name and email, as the "copyrighteous spokesman" for the initiative. And since the page has been online, I have received hate mail about it. Constantly. Since the email only goes to me, I thought it might be fun to share some of these publicly. All these messages are quoted verbatim but I have not included the senders' names. Be warned: the language is often salty. This email is years old now but it is probably still my favorite:
Atrocity and strife run rampant in this world. Babies are abandoned in dumpsters. Teachers molest students. Impoverished Indonesians make sneakers for pennies while the spoiled jackhole in the 30-second commercial makes millions for sinking a three-pointer and smirking at the camera. Forms of religion are interpreted as to compel people to strap explosives to their chest and board buses full of innocents. Boss Tweeds embezzle and get severance pay while John Q. Workingman gets put out on the street when the corporation goes belly up. Out of all these indignities and countless others I haven't the time to mention, why do you make it your personal crusade to assist in the flagrant persecution of family restaurants for partaking in the time-honored tradition of singing "Happy Birthday"? God forbid these foul brigands bend copyright law in order to bring a smile to somebody's face. Food for thought...without the accompanying song.
Many others strike a defiant, if less poetic, tone:
Good luck! There are millions of us who refuse to accept the ridiculous "copyright" on Happy Birthday. If Time Warner were an ethical company rather than a greedy megacorp they would do something truly special and release it into the public domain. There are some things in this world more important than money.
Quite a few people notice that my last name is Hill and suspect that I must be related to the Hill sisters who originally penned the song. I'm not, to my knowledge, although since Time Warner bought the rights, it's not clear it would matter:
I am writing to just let you know how disappointed I am that a large corporation and others (like the HILL family) are making $2 million plus for a song that was created over 100 years ago with noone knowing who created the lyrics! None of us at our place of employment could believe this and we certainly won't encourage people to send money to ASCAP. It is a shame that ASCAP license fees aren't used to pay more to up-and-coming artists who I'm sure need this money alot more than Time Warner. We all plan to sing Happy Birthday MORE now in public places and if anyone asks if it is copyrighted we will say "of course not". Maybe this way the song will not die out completely as more and more other "birthday" songs are being sung. It would also be nice if your website cited whose opinion is writing the piece and your obvious conflict of interest.
Or another:
Is it a coincidence that your last name is the same as the last name of the authors of the song "Happy Birthday?" You seem to have a personal monetary motive for your work with the "grassroots project" you call Unhappy Birthday, and if you do not, your concern is misplaced all the same. Whom do you imagine your campaign serves? And do you realize whom it harms? I do not question the illegality of performing the copyrighted song publicly. And you are correct that most of the public is not even aware that the song is under copyright. I think the harm done to Time Warner and its associates by such public performances is far outweighed by the joy created when the much-loved happy tune is shared. I urge you to ask yourself why you think the immortal Hill sisters wrote the song in the first place. It was not to put more money Time Warner's pocket. It was, I would argue, for the sake of the song itself and the happiness it brings when performed (publicly or otherwise). Please consider siding with the children and the artists; let the lawsuits alone.
Some people suspect the site may be satire, but include insults and and attacks just in case it isn't:
I'm trying to figure out if your Unhappy Birthday site is meant to be in jest. If so Rofl, and congrats on a hilarious site. If you're actually serious, then fuck you Nazi cunts and your corporate butt buddies. Thank you for your time.
Or these two alternatives (each were separate emails):
If this is a joke then it's rather funny. However if this website is serious then you're a fucking idiot. Get a life!!!! if it is a form of protest, then THANK YOU! if it is not, then screw you all!
One memorable piece of mail was from someone who knew of me from my activities in the free software and free culture communities and had a hard time reconciling my work there with the high protectionist website:
I was quiet surprised to see your name and email address at the bottom of the home page of the site Unhappy Birthday. The site claims that you are their spokesman. Is this correct? I do not understand... You have all this Open Source/ Free Software background and then this site that defends one of the most controversial copyright issues??? Do you really mean this? Do you want to help Time Warner?
I've also received probably half a dozen mails that offer some sort of support! For example, this person liked the website -- and even wanted to buy one of our t-shirts -- but objected to our logo:
I was going to buy one of your products from your Unhappy Birthday Shop at CafePress but there's a problem. I hate emblems that uses human skulls in them. Being a member of ASCAP I really do support your cause but I can't buy a product that I would never wear.
And many people are simply confused asking something like this one:
So I saw the unhappy birthday site and I'm just a little confused. Is this a joke or a serious thing?
I usually reply and explain that I have tried to ensure that the site describes the legal situation around Happy Birthday honestly and correctly. That said, the vast majority of messages I receive are unequivocal. Like this email that I received last week addressed to "you anti-free speech fascists":
         __
        /  \


 __  __      __
/  \/  \    /  \
                \
                  
                 /
                 \
                  /
\                /
                 
                 
Half an hour later, the author followed up with a English version of the same message, set to the tune of happy birthday. You might think that getting insulted and flipped off by confused people on the Internet might get me down. It doesn't! I made Unhappy Birthday because I thought that the fact that something as important to our culture as Happy Birthday could be owned was outrageous. Every piece of hate mail means that somebody else -- almost always somebody who isn't a "copyfighter" or a free culture geek -- is now upset about the current state of copyright too. Sure, Unhappy Birthday makes me a tiny bit sad about people's ability to recognize satire. But it makes me really happy about people's ability to get very annoyed at what they think is the outrageous control of our culture through copyright. When more people are as mad as the the people I've quoted above, we will be able to change copyright into something less outrageous to all of us.

4 March 2012

Jamie McClelland: Managing KVM instances

At May First/People Link we have been using KVM for several years now and recently I have been running KVM instances on my local laptop. I'm pleased to see all the work that has gone into libvirt, which seems like a robust and full-featured suite of tools for managing many virtualization technologies, including KVM. However, we don't use it at May First/People Link for a number of reasons. The most pressing is that it runs all virtual guests as the same user, but also because it offers far more features than we need (such as graphical access to virtual server, which we don't need since none of our guest servers run X). On May First/People Link hosts, we are using a relatively simple set of bash scripts (accessible via git at git://lair.fifthhorseman.net/~dkg/kvm-manager). These scripts re-use many tools we are already familiar with to build and launch kvm guests. Each guests runs as a dedicated non-provileged user, with a console available using screen, and the kvm process is managed using runit. Since our admins are familiar with these tools already, the learning curve involved is much less steep. Despite the relative simplicity of kvm-manager, it was still more complicated and involved than I wanted on my laptop. Additionally, I wanted to fully understand every piece of the puzzle and separating out user privileges wasn't important to me. So - I wrote the following bash script to launch virtual servers. It assumes you are using logical volume manager. Some editing required if you want to re-use it.
#!/bin/bash
# manage a virtual server
# add /etc/udev/rules.d/92-kvm.rules with the following line (change "jamie" 
# to the group you are running as and vg_animal0 to the name of your volume 
# group):
# ACTION=="change", SUBSYSTEM=="block", ATTR dm/name =="vg_animal0-*_root", GROUP="jamie"
#
# install a new server by:
# * create logical volume with the name: servername_root
# * $0 servername start /usr/local/share/ISOs/default.iso
bridge=virbr0
user=jamie
base=/home/jamie
server="$1"
vg=vg_animal0
# modify server memory here
mem=768
command="$2"
[ -z "$command" ] && command=start
die ()  
  printf "$1\n"
  exit 1
 
cdarg=
if [ -n "$3" ]; then
  [ ! -f "$3" ] && die "Third argument should be path to cd iso. Can't find that path."
  cdarg="-cdrom $3"
fi
function start()  
  lvname="$ vg -$ server _root"
  # trigger udev to ensure we have proper ownership of the block device
  sudo udevadm trigger --subsystem-match=block --attr-match=dm/name="$lvname"
  lv="/dev/mapper/$lvname"
  [ ! -e "$lv" ] && die "Can't find $lv"
  sudo modprobe -v tun   die "Failed to modprobe tun module"
  # create network device if it doesn't already exist
  ip tuntap   grep "$tap"   sudo ip tuntap add dev "$tap" mode tap user "$user"   die "Failed to create device $tap"
  # bring up device if it's not already up
  ip link   grep " $tap "   sudo ip link set "$tap" up   die "Failed to set $tap to up"
  # add the device to the bridge so it get use the upstream network connections
  /sbin/brctl show   grep "$tap"   sudo brctl addif "$bridge" "$tap"   die "Failed to add tap to bridge"
  # launch kvm in a screen session
  screen -S "$server" kvm -drive "file=$lv,if=virtio,id=hda,format=raw" -m "$mem" -device "virtio-net-pci,vlan=1,id=net0,mac=$mac,bus=pci.0" -net "tap,ifname=$tap,script=no,downscript=no,vlan=1,name=hostnet0" $cdarg -nographic   die "Failed to start kvm" 
 
function cleanup()  
  read -p "Please shutdown the host first then hit any key to continue..."
  sudo brctl delif "$bridge" "$tap"
  sudo ip link set "$tap" down
  sudo ip tuntap del mode tap dev "$tap"
 
# generate reproducible mac address
mac="$(printf "02:%s" "$(printf "%s\0%s" "$(hostname)" "$ server "   sha256sum   sed 's/\(..\)/\1:/g'   cut -f1-5 -d:)" )"
tap="$ server 0"
case "$command" in
  start)
    start
    ;;
  cleanup)
    cleanup
    ;;
  *)
    die "Please pass start or cleanup as first argument"
esac

Stefano Zacchiroli: bits from the DPL for February 2012

Released a few hours ago, here is the monthly report of DPL activities for February 2012.
Howdy, dear Project Members,
here's another round of updates about what has happened in DPL land, this time during February 2012. Highlights Quit a bit of highlights for this month: Talks, interviews, and the like Sprints Plenty of sprints related news! It would be amazing to have an average of one sprint per month for 2012, and we're on good track for it. If you want to help, organize one for your team as documented on the wiki. Legal stuff Appointments In addition to the GSoC admins delegation (see above), I've agreed with former secretary Kurt Roeckx to reappoint him as a secretary for another year. Many thanks, Kurt! Miscellaneous Happy Debian hacking.
PS as usual, the boring day-to-day activity log is available at master:/srv/leader/news/bits-from-the-DPL.*

Steve Kemp: Symbiosis is wonderful

Symbiosis
Symbiosis is the collective name given to a group of Debian GNU/Linux packages which implement simple virtual hosting. It is developed by my employers Bytemark. Symbiosis is basically a collection of configuration snippets, code, and libraries which works to offer virtual hosting in a reliable consistent and easy to understand fashion. You implement hosting for a new domain by merely creating a directory tree. So for example you might configure the hosting for the domain example.com by running:
mkdir -p /srv/example.com/public/htdocs
echo "hello, world" >> /srv/example.com/public/htdocs/index.html
mkdir -p /srv/example.com/mailboxes/webmaster
echo "super-secret" > /srv/example.com/mailboxes/webmaster/password
mkdir -p /srv/example.com/config
echo "3l33t" > /srv/example.com/mailboxes/config/ftp-password
There you are, now http://www.example.com/ and http://example.com/ will work, and you may login to check mail with the email address webmaster@example.com via POP3, IMAP, IMAPS, or POP3S. Finally you can FTP with username example.com and be dropped into the public directory. The mail handling is very flexible, and the webhosting supports wonderful things. I don't generally talk about work-stuff explicitly, but we've just made a major new release of the Symbiosis system such that it works upon Squeeze and has lots of IPv6 support out of the box. (Email, DNS, HTTP, Firewalling, FTP etc.) All in all it is simple, well-documented, and open-source with a reasonably large user-base. More external testers, users, and developers would be a wonderful thing..
Mutt Mailboxes & Idle Hooks?
Mutt is wonderful but I'm starting to get annoyed by its lack of auto-mailbox discovery. Assuming you use procmail you might deliver mail to ~/Maildir/.foo/ and mutt won't notice that if the directory is created once it starts. (This is because generally mailboxes are defined via "mailboxes =one =two ..", even if you use a shell snippet it won't get updated unless you re-read configuration, or re-exec mutt). I wish it were possible to use inotify/dnotify/something magic such that everything beneath ~/Maildir would just work. (Re-reading mailboxes manually is one solution but it is .. nasty?) I'm thinking that of all the possible solutions one of the most potentially interesting would be to define a new hook: "idle-hook command .." That way "command" would be executed every time the client is idle. (This is a distinct state unrelated to IMAP IDLE times.) Nopte: There is already "mail_check" & "timeout" options. Even running a defined command immediately following the code for mail_check would be reasonable.
Reverse Proxy
I continue to use, love, and enjoy my node.js-based reverse HTTP proxy, and pub discussions seemed to suggest it is a great idea (due to flexibility) but it will never take on because people don't trust node. I'm almost tempted to re-code it in LUA & C. But I can't help but think that would be a waste of time which would not increase adoption - after all most people use "simple" reverse proxies, and they are well suited by Apache, nginx, or even varnish. Still no rush I suppose.
In more personal news after living in this flat for 7 years, or so, I'm getting a new bathroom designed and deployed. Good times. In the meantime I've been steadily watching Stargate SG-1 having recently purchased a box-set of series 1-10. I've just started series six this evening, and I'm enjoying it a lot. ObQuote: "You have been recruited by the Star League to defend the frontier against Xur and the Ko-Dan armada. " - The Last Starfighter (1984). First film I ever saw at a cinema as a child.

Craig Small: JFFNMS 0.9.2 Released

JFFNMS version 0.9.2 was released today both as an upstream tar.gz file and a new debian package. This version fixes some bugs including making sure it works with PHP5.4. The biggest change in PHP 5.4 is that you can no longer call by reference. Previously you could call a function like myfunc(&blah); which would send a pointer to blah and not the item itself. Now the function definition needs to define what it wants rather than change it each time.

3 March 2012

Andrew Cater: Raspberry Pi - order

Farnell did take note of the pre-order: I've just had an email asking me to confirm an order. I've just put one in for 30 days delivery ...

A work colleague has also added me to a list he's putting together - this means I might get two :(

Torrent was running at 5.90 sharing ratio a couple of days ago when I stopped it. It's now running at 1.4 share ratio - there's a lot of interest

I put up most of the Debian AMD64 DVDs plus a couple of netinsts at the same time - only a couple of those have reached 1.0 share ratio or better and been deleted.

UPDATE - Using instructions on how to run the image in QEMU, I have managed to get the basic Debian image meant for the RaspberryPI to run on my small i686 laptop.

Well done to the folks at the University of Cambridge who've been using this as a development distribution: Fedora from University of Toronto will follow.
LXDE, compilers - and all running in 256M :)

Ingo Juergensmann: Goodbye Google, hello Diaspora!

Well, at least in Germany there was lot of press coverage about Google changing its data protection policies and joining the user profiles of their services like Youtube, GMail, Google+ and so on. There were even HowTos to delete some tracking relevant data and history before of March 1st. like on German Spiegel Online news magazine. Because I'm no big fan of Google and being a strong privacy advocate, I tried to follow the steps mentioned there and got some surprises. First of all I discovered in Googles Dashboard that Google already joined my private account or email address with the one I used at work when I was testing some Android phones for some reasons. The mail address from work was considered as primary address and I couldn't change this. I could delete my private mail address from that account, but not the primary address from work. So, time was pressing because 1st of March was coming near, only one hour left, but what to do know? I'm already using plugins like Ghostery and AdBlockPlus for some time now to minimize the chance of being tracked and such. I registered with Google+ to have a look onto it and to reserve my name and account there, but I was not actively using it for privacy reasons nor do I use Facebook. Therefor the decision was simple and easy: deleting my Google account was probably the best idea I got on that day. That was easy and a quick win for my privacy concerns! On the other hand having some sort of a social network can be nice. And I'm a fan of decentralized solutions like Jabber, which I prefer over AIM/ICQ. I'm running my own Jabber server for some years now, so it was a natural thought to me to make this step for a social network as well. Diaspora* started as a distributed social network in 2010 after some students listened to a speech by Eben Moglen about "Freedom in the Cloud" and is currently still in Alpha stage of development. But it is working and it is running on free software. That's a fairly good reason alone to prefer, support and use Diaspora* over other proprietary social networks like G+ or Facebook, isn't it? So, give it a try! Everyone can run a Diaspora* node, called "pod", on their own server. There are some good installation guides available at Github.com Wiki even covering installation on Debian! Although these installation HowTo is quite good there are some pitfalls left. For example you'll need good SSL cert from an CA authority that is wildly installed on all systems. CAcert seems not to be supported and self-signed certs and CAs doesn't work either. Without a good SSL cert you won't be able to interconnect with other Diaspora* pods. Another pitfall for Debian seems to be the installation of Ruby. First I used the Debian Ruby packages, but got some errors when starting the server that some CSS files couldn't be found. After using the RVM installation metioned in the installation guide these problems were solved (please note that the described way of using RVM didn't work for me either and I got help from some really helpful people on #diaspora-de@freenode). But anyway, I managed to get Diaspora* up and running on my own server and get it to interconnect with other pods. Although installing Diaspora* from source is currently a little pain compared with the ease and comfort of pre-built Debian packages, it's worth the effort! Everyone who consider Google evil and Facebook bad should consider switching to Diaspora*! The more people join, the better the social network will get! Help to fight against the AOL-ism of the Internet by using open and non-proprietary APIs and software like Jabber and Diaspora*! You can find my Diaspora* pod at: http://nerdwind.de/ where my account is "ij".
Kategorie:
File attachments:

1 March 2012

Mike Hommey: Introducing faulty.lib

TL;DR link: faulty.lib is on github. Android applications are essentially zip archives, with the APK extension instead of ZIP. While most of Android is java, and java classes are usually loaded from a ZIP archive (usually with the JAR extension), Android applications using native code need to have native libraries on the file system. These native libraries are found under /data/data/$appid/lib, where $appid is the package name, as defined in the AndroidManifest.xml file. So, when Android installs an application, it puts that APK file under /data/app. Then, if the APK contains native libraries under a lib/$ABI subdirectory (where $ABI is armeabi, armeabi-v7a or x86), it also decompresses the files and places them under /data/data/$appid/lib. This means native libraries are actually stored twice on internal flash: once compressed and once decompressed. This is why Chrome for Android takes almost 50MB of internal flash space after installation. Firefox for Android used to have that problem, and we decided we should stop doing that. Michael Wu thus implemented a custom dynamic linker, which would load most of Firefox libraries directly off the APK. This involves decompressing the zipped data somewhere in memory, and doing ld.so s job to make the library usable (please note that on Android, ld.so is actually named linker). There were initially circumstances under which we would decompress into a file and reuse it the next time Firefox starts, but we subsequently removed that possibility (except for debugging purpose) because it ended up being slower than decompressing each time (thanks to internal flash being so slow). Anyways, in order to do ld.so s job, our custom linker was directly derived from Android s system linker, with many tweaks. This custom linker has done its job quite well for some time, now, but has been recently replaced, see further below. Considering Firefox can t do anything useful involving Gecko until its libraries are loaded, in practice, this means Firefox can t display a web page faster than completely decompressing the libraries. Or can it? Just don t sit down cause I ve moved your chair We know that a lot of code and data is not used during Firefox startup. Based on that knowledge, we started working on only loading the necessary bits. The core of the idea is, when a library is requested to be loaded, to reserve anonymous memory for its decompressed size, and that s all. That memory is protected such that any access to it triggers a segmentation fault. When a segmentation fault happens, the required bits are decompressed, and execution is resumed where it was before the segmentation fault. The original prototype was decompressing from a normal zip deflated stream, which means it was impossible to seek in it. So, if an access was made at the end of the library, it was necessary to decompress the whole library. With some nasty binary reordering, and some difficulty, it was possible to avoid accessing the end of the library, but the approach is very much fragile. It only takes an unexpected code path to make things much slower than they should be. Consequently, for the past months, I ve been working on improving the original idea and, with some assistance from Julian Seward, implemented the scheme with seekable compressed streams. Instead of letting the zip archive creation tool deflate libraries, we store specially crafted files. Essentially, files are cut in small chunks, and each chunk is compressed individually. This means a less efficient compression, but it also means random access to chunks is possible. However, instead of stacking on top of our existing custom linker, I started over, from the ground up. First, because it needed a serious clean up (a good part of linker.c is leftovers from the Android linker that we don t use, and APKOpen.cpp is a messy mix of JNI stubs, library decompression handling (which in itself was also a mess) and Gecko initialization code) and most importantly, because it relied on some Android system linker internals and thus required binary compatibility with the system linker. Which, according to Google engineers that contacted us a few months ago, was going to break in what we now know will be called Android Jelly Bean. The benefit of the clean slate approach is that the new code is not tied to Gecko at all and was designed to work on Android as well as on desktop Linux systems (which made debugging much much easier). We re thus releasing the code as a separate project: faulty.lib. It is licensed under the Mozilla Public License version 2.0. Please feel free to try, contribute, and/or fork it. This dynamic linker is not meant to completely follow standard ELF rules (most notably for symbol resolution), and as a result does some assumptions. It s also still work in progress, with some obvious optimizations pending (like, avoiding to resolve the same symbols again and again during relocations), and some features missing (for example, symbol versioning). The next blog post will give some information about how to build Firefox for Android to benefit from on-demand decompression. I will also detail a few of the tricks involved in this dynamic linker in subsequent blog posts.

Roland Mas: Looking for the ultimate distributed filesystem, take 2

This follows up on a previous post, and tries to summarize the corrections and suggestions I received. First, a reminder: yes, I'm really looking for a filesystem, not a storage system. Even if I only consider the music files use case, there are just too many things that want to access the files, and there's no way I'm going to port these things to use the storage system's API instead of plain old file access. Examples? The Rhythmbox player. The XMMS2 player. The mt-daapd/forked-daapd DAAP server. My script to backup or restore metadata (tags). Ex-Falso, to do mass edits on these tags. abcde, to add new files when I buy a new CD. Any kind of shell one-liners I currently do without thinking because find, xargs, cp, ln, and so on all operate on files. I understand that providing filesystem semantics on top of a storage system is hard, but that doesn't change my requirements, and saying otherwise is patronising. So, on to the meat of the matter. Apparently my understanding of Tahoe-LAFS was mostly correct. It seems that multiple introducers are on their way to become a reality, which would mean the one remaining central point would go away. Most of my other complaints seem to be on their way to be resolved, too, except that it's still targeted as a storage system, and the FUSE/sshfs layer on top still has its drawbacks (quoting from the wiki, Before uploading a file to a Tahoe filesystem, the whole file has to be available , mutable parts of a filesystem should only be accessed via a single sshfs mount [...] data loss may result for concurrently accessed files if this restriction is not followed and so on). From what I read, the position is that nobody publicly uses Tahoe's filesystem integration, therefore there's no need to fix its shortcomings; my understanding is that nobody uses it precisely because of its shortcomings. Ceph: apparently does repair/rebalance automatically contrary to what I thought. However, two persons told me that it's really expecting all nodes on the same LAN, and geographically distributed setups aren't really targeted. XtreemFS: I don't think I got any comments on my evaluation, so I'll assume it still stands. git-annex: storage system, not a filesystem. Yes, the files can be made available in the filesystem, but if I need to manually retrieve them before accessing them, this doesn't work. GlusterFS: I'd like to read more docs on how it works, but I haven't been able to find them. Apart from the installation manuals, the only documentation I found was a very short Concepts page, which described some of the concepts but didn't give me the big picture on how the who thing works. (I'm turning a blind eye on the Red Had advertisements and the requiremets that everything be installed on RH machines; the hardware requirements are also quite out of line with what I want to do.) HekaFS (aka CloudFS): I found even fewer docs about this one than about GlusterFS, and apparently HekaFS is on its way to being merged into GlusterFS anyway. PlasmaFS: I didn't know about this one previously, but the one email I got about it was mainly full of this won't work and this won't work either . I didn't feel inclined to read further docs after that. In summary, I guess the replies I got didn't cause me to change my mind too much. Tahoe-LAFS still seems to be, if not the best solution, then at least the least bad . Hopefully the drawbacks will be fixed soonish; the main sticking point (at least from my point of view) still seems to be the lack of focus on proper filesystem integration. I'll try setting it all up at some point; I may report further if I end up finding interesting things. Thanks to all who responded!

Raphaël Hertzog: My Debian Activities in February 2012

This is my monthly summary of my Debian related activities. If you re among the people who made a donation to support my work (384.14 , thanks everybody!), then you can learn how I spent your money. Otherwise it s just an interesting status update on my various projects. Dpkg and multiarch The month started with a decision of the technical committee which allowed me to proceed with an upload of a multiarch dpkg even if Guillem had not yet finished his review (and related changes). Given this decision, Guillem made the experimental upload himself. I announced the availability of this test version and invited people to test it. This lead to new discussions on debian-devel. We learned in those discussions that Guillem changed his mind about the possibility of sharing (identical) files between multiple Multi-Arch: same packages, and that he dropped that feature. But if this point of the multiarch design had been reverted, it would mean that we had to update again all library packages which had already been updated for multi-arch. The discussions mostly stalled at this point with a final note of Guillem explaining that there was a tension between convenience and doing the right things every time that we discuss far-reaching changes. After a few weeks (and a helpful summary from Russ Allbery), Guillem said that he remained unconvinced but that he put back the feature. He also announced that he s close to having completed the work and that he would push the remaining parts of the multiarch branch to master this week (with the 1.16.2 upload planned next week). That s it for the summary. Obviously I participated in the discussions but I didn t do much besides this I have a mandate to upload a multiarch dpkg to sid but I did not want to make use of it while those discussions remained pretty unconclusive. Also Guillem made it pretty clear that the multiarch implementation was buggy , not right and not finished and that he had reworked code fixing at least some of the issues since he never shared that work in progress, I also had no way to help even just by reviewing what he s doing. We also got a few multiarch bug reports, but I couldn t care to get them fixed since Guillem clearly held a lock on the codebase having done many private changes it s not quite like this that I expect to collaborate on a free software project but life is full of surprises! I ll be relieved once this story is over. In the mean time, I have added one new thing on my TODO list since I made a proposal to handle bin-nmu changelogs and it s something that could also fix #440094. Misc dpkg stuff After a discussion with Guillem, we agreed that copyright notices should only appear in the sources and not in manual pages or --version output, both of which are translated and cause useless work to translators when updated. Guillem already had some code to do it for --version strings, and I took care of the changes for the manual pages. I merged some minor documentation updates, fixed a bug with a missing manpage. Later I discovered that some recent changes lead to the loss of all the translated manual pages. I suggested an improvement to dh_installman to fix this (and even prepared a patch). In the end, Guillem opted for another way of installing translated manual pages. Triggered by a discussion on debian-devel, I added a new entry to my TODO list: implementing dpkg-maintscript-helper rm_conffile_if_owner to deal with the case where a conffile is taken over by another package which might (or might not) be installed. Misc packaging At the start of the month, I packaged quilt 0.51. The number of Debian specific patches is slowly getting down. With version 0.51, we dropped 5 patches and introduced a new one. Later in the month I submitted 4 supplementary patches upstream which have been accepted for version 0.60. This new version (just released, I will package it soon) is an important milestone since it s the first version without any C code (Debian had this for a long time but we were carrying an intrusive patch for this). Upstream developer Jean Delvare worked on this and based his work on our patch, but he went further to make it much more efficient. Besides quilt, I also uploaded dh-linktree 0.2 (minor doc update), sql-ledger 2.8.36 (new upstream version), logidee-tools 1.2.12 (minor fixes) and publican 2.8-2 (to fix release critical bug #660795). Debian Consultants The Debian Project Leader is working on federating Debian Companies. As the owner of Freexian SARL, I was highly interested in it since Freexian contributes to Debian, offers support for Debian and has a strategic interest in Debian . There s only one problem, you need to have at least 2 Debian developers on staff but I have no employees (it s me only). I tried to argue that I have already worked with multiple Debian developers (as contractors) when projects were too big for me alone (or when I did not have enough time). Alas this argument was not accepted. Instead, and since our fearless leader is never afraid to propose compromises, he suggested me (and MJ Ray who argued something similar than me) to try to bring life to the Debian Consultants list which (in his mind) would be more appropriate for one-man companies like mine. I accepted to help animate the list, and on his side, he s going to promote both the Debian Companies and the Debian Consultants lists. In any case, the list has seen some traffic lately and you re encouraged to join if you re a freelancer offering services around Debian. The most promising thing is that James Bromberger offered to implement a real database of consultants instead of the current static page. Book update We made quite some progress this month. There s only one chapter left to translate. I thus decided to start with proofreading. I made a call for volunteers and I submitted one (different) chapter to 5 proofreaders. The liberation campaign made a nice leap forwards thanks to good coverage on barrapunto.com. We have reached 80% while we were only at 72% at the start of the month (thanks to the 113 new supporters!). There s thus less than 5000 EUR to raise before the book gets published under a free license. Looking at the progression in the past months, this is unlikely to be completed on time for the release of the book in April. It would be nice though so please share the news around you. Speaking of the book s release, I m slowly preparing it. Translating docbook files is not enough, I must be able to generate HTML, ePub and PDF versions of the book. I m using Publican for most formats, but for the PDF version Publican is moving away of fop and the replacement (webkit-based) is far from being satisfactory to generate a book ready for print. So I plan to use dblatex and get Publican to support dblatex as a backend. I have hired Beno t Guillon, the upstream author of dblatex, to fix some annoying bugs and to improve it to suit my needs for the book (some results are already in the upstream CVS repository). I m also working with a professional book designer to get a nice design. I have also started to look for a Python Django developer to build the website that I will use to commercialize the book. The website will have a larger goal than just this though ( helping to fund free software developers ) but in free software it s always good to start with your own case. :-) Hopefully everything will be ready in April. I m working hard to meet that deadline (you might have noticed that my blog has been relatively quiet in the last month ). Thanks See you next month for a new summary of my activities.

No comment Liked this article? Click here. My blog is Flattr-enabled.

29 February 2012

Andrew Cater: Raspberry Pi - announcement

_Something_ is going to happen at 06:00 GMT on 29th February. I predict a server meltdown ..

==

Product available from RS Components and Farnell.com - both servers not responding. Effectively a worldwide DDOS because of demand 29/2/2012

== 07:20 or so ==

Farnell sold out almost immediately: now taking pre-orders for the next batch
RS may be taking orders later in the week. [Per RaspberryPi Twitter feed]

Update: RS are also taking pre-orders and expressions of interest. Both companies will do their best to get stock to all ASAP.

Please don't blame Eben, Liz or the other RaspberryPi folks for this - they've worked miracles to get this far.

To negotiate proper licensing agreements with the two largest UK electronics distributors and get them to undertake manufacturing and distribution is, actually, a masterstroke for a small non-profit organisation.

28 February 2012

Paul Wise: Debian/Ubuntu games screenshot party results

The Debian/Ubuntu games team recently organised a half-day screenshots party for creating screenshots for all the games that are available in Debian/Ubuntu. Unfortunately, only 5 people participated in the screenshots party, I had hoped that we would get more folks turn up. Only one of those was not already involved in the games team and that one person found out via our spam on the #debian-mentors IRC channel. This means that most of our promotion of the event was ineffective. Hopefully for future games parties we can improve this, please let us know if you have any ideas about that. We also had 7 other people on the channel during the party lurking, discussing and or working on other things, in particular Ben Armstrong was working on a games live CD. Over the 7 hours of the party, we uploaded 100 screenshots for 40 different packages. Of the packages, 2 are available only in Debian (auralquiz, cutechess), one is available only in Ubuntu (plasma-widget-tictactoe) and the rest are available in both. I think we got quite a bit done for such a small group. Some of us could not resist filing some bugs on packages that had issues preventing or delaying us from taking screenshots. I also suggested to one maintainer that his package (acm4) be removed from Debian, since it is obsoleted by acm and unusable. If you want to play some games, check out goplay, which is a tool for browsing available games using debtags that displays screenshots from the games-thumbnails package, which has just been updated with the screenshots created during the party. goplay needs some more development, if you would like to help out with that, you would be most welcome. If you are interested to see our screenshots, they are all on the screenshots.debian.net website and the packages are auralquiz, cardstories, londonlaw, cube2font, ardentryst, cutechess, pianobooster, emacs-chess, xye, flare, tmw, garden-of-coloured-lights, flight-of-the-amazon-queen, geekcode, glpeces, fofix, unknown-horizons, klickety, polygen, tictactoe, xscreensaver-screensaver-dizzy, goban-original-games, xjokes, mudlet, xabacus, xtux-client, connectagram, crystalspace, pescetti, purity-ng, qstat, slashem, sudoku, minetest, xscavenger, plasma-widget-tictactoe, xbomb, xfrisk, xpilot-ng and xsok.

27 February 2012

Jon Dowland: American Psycho

American Psycho is a novel by Bret Easton Ellis. It's a first person stream-of-consciousness novel about a mid-to-late twenties Wall Street banker during the late-eighties-early-nineties. Patrick Bateman is a vain, self-obsessed pleasure-seeker, surrounded by a gaggle of similarly self-obsessed bankers and socialites. Bateman and his friends idle away their days thinking about what restaurants to secure dinner bookings; which nightclubs to be seen at; where to score cocaine and pick up women. They compete with one another on points of dress etiquette, and the relative degree of luxury demonstrated by their attire. They are all relatively interchangeable: the reader could be excused for mixing the identi-kit bankers up, and indeed they are frequently confused for each other, and other people, throughout the novel. Bateman describes in vivid detail nearly every item of clothing worn by both his male and female associates, describing both their cut and which fashion house they have come from, occasionally passing judgement. The murders are typically described with the same vivid detail as his more public activities. As well as a yuppie, Bateman is a psychotic, and probably a serial killer: there is a small amount of ambiguity, partially due to the frequent confusions of identity between the various male banker characters in the book. It's possible that Bateman has fantasised his killer side, or embellished it. He's clearly an unreliable narrator. It takes a relatively long time before this aspect of his personality emerges. It's also possible that he is a killer, but the people he kills are so interchangeable that nobody notices, or cares. There is a passage towards the end of the book that strays into Hollywood action-thriller levels of absurdity, possibly the only moment in the book where you have difficulty believing that the events could have occurred as described. Bateman tries repeatedly to talk to people about his crimes, but never succeeds in holding people's attention, or being taken seriously. This particular theme reaches a particularly amusing climax. Reportedly Ellis wrote the novel without the violent scenes and later added them in. I can believe that. The novel is carefully constructed to manipulate the reader in a way I've never been aware of before. The everyday and the horrific mesh to make the whole seem very consistent and lucid. There is a small surreal element woven into the story which is so subtle and downplayed that you can't withdraw into the safety of "this is a fantasy". Similar scenes recur over and over: heading to a restaurant. Heading to a club. Sex. Murder. Ellis uses repetition to lull you into a false sense of security before hitting you hard with an about-face, mid-sentence, like a movie jump-cut. This book has the dubious distinction of being the second novel ever to have made me feel physically queezy after reading a passage (and I was reading the other book in a car, which may have been a contributing factor). The book has been criticised for the level of violence meted out against women. Numerically, Bateman describes a roughly even number of male and female murders. However his female victims are dispatched with a shockingly higher level of planned sadism: most of his male victims are opportunistic rather than planned. Some critics theorise that the even male/female victim count is a deliberate pre-emption on the part of the author from criticism for the violence against women. I don't quite see the argument, here: Bateman is not a sympathetic character. He's a monster, and the fact he's a sexist monster is only one unpleasant facet of many. To me, the disdain and hatred shown towards homeless people was a far more prevalent problem, not least because it wasn't limited to murders, or even Bateman: many of the other characters are cruel towards them. What would this book be, without the murder? Quite similar to a number of Ellis' other stories, if their blurbs are anything to go by: explorations of the emptiness of the lives of privileged, upper class contemporary Americans. Is the psychopathy central to the story? I think so. The contrast between the corporate and the murderous is at the core. Would I recommend this novel? I'd hesitate to do so to anyone with a nervous disposition: otherwise, it has left a lasting impression and a desire to discuss it further, which you can take as praise. There's a good critical review at the M/C Journal.

26 February 2012

Craig Small: psmisc 22.16 Released

psmisc version 22.16 was released today. It is a bugfix release that bascially fixes a problem around strings in C. Process name lengths are only supposed to be 16 characters long, so a 17 bye buffer is ok; until you have processes with brackets which means the string is 18 characters. The next wrinkle is that at times the brackets are stripped out so matches fail because the lengths don t quite line up. You ll see this with the debian 22.15-2 version of psmisc where killall won t find long-named processes. So, 22.16 fixes all that. Test Processes It really shows that psmisc needs a set of tests like procps has already. The difficulty with both is that its not simple in the DejaGNU framework to make test processes. These are not the programs within the package but other processes that the programs can work on. There really needs to be an equivalent to touch for processes just for this sort of thing. Creating processes is rather simple, but ensuring they go away is the tricky part, or they die with certain signals.

24 February 2012

Richard Hartmann: zsh pound-insert

Ben Hutchings writes:
There is an alternative to using C-c, and that is M-#. This adds a '#' to the start of the line, commenting it out, and then behaves as if you pressed Return. The result is that the command is cancelled but still remains on-screen and in your history. You can then copy the command later using the mouse or keyboard.
Naturally, there is a zsh equivalent for this (there always is...): pound-insert. Quoth the manpage:
pound-insert
If there is no # character at the beginning of the buffer, add one to the beginning of each line. If there is one, remove a # from each line that has one. In either case, accept the current line. The INTERACTIVE_COMMENTS option must be set for this to have any usefulness.
So if you want the same for zsh, a simple
bindkey '^[#' pound-insert

is all you need. Update: Clint Adams noted another way to do (almost) the same.

Richard Hartmann: apt-get install vcsh

apt-get install vcsh I finally got around to package vcsh and David Bremner was kind enough to sponsor it. vcsh is available in testing, unstable, and squeeze-backports. Also, Ubuntu seems to have copied it over into their repositories automagically. As you probably don't know, vcsh is a tool to manage config files in git. Say you want to maintain one repository for zsh, one for vim, one for ssh, one for mplayer, and one for mr, but obviously there can only be one .git in $HOME. vcsh helps by moving $GIT_DIR into $XDG_CONFIG_HOME/vcsh/repo.d/ but keeping $GIT_WORK_TREE in $HOME. The splitting of configuration sets into separate repositories allows you avoid checking out, say, mplayer's config on your servers, or checking out your ssh config at work. If this sounds complicated, it's not; vcsh hides all of the dirty details from you. vcsh integrates nicely with mr by means of a plugin, making handling your configurations even more trivial. If you do get stuck along the way, simply drop into #vcs-home on irc.oftc.net or send email to the vcs-home mailing list. popcon tells me that there are more users than I know about directly, so pipe up if you're one of them. And if you are one of the people who have it installed but don't use it, I am even more interested. I would love to know why so I can improve it. Long story short, if you care about the integrity and/or history of your configuration, or if you use one or more computers, you should definitely give vcsh a try. Any kind of feedback appreciated :)

Julien Danjou: 10 years as a Debian developer

Ten years ago, I joined the Debian project as a developer. At that time, I was 18 and in my first year at university, hanging out with the TuxFamily system administrators, which included 3 french Debian developers (sjg, igenibel and creis). I was learning Debian packaging while working on VHFFS, and decided to package one or two non-yet-packaged software for Debian. My friends pushed me into the NM process, and less than 2 months later I was a Debian developer. One have to admit that back in the days, the NM process was really fast if you were able to reply to the questions quickly. :-) I think I became the youngest developer among Debian's ones. That was my first steps in a Free Software project, and it was really exciting. In 10 years, I've been doing a lot of different things for Debian. Sure, I've been using it all the years long, but let's recap a bit what I did, from what I recall. My first Debian only project was apt-build around 2003, and later rebuildd in 2007. I built the Xen packaging team in 2005, I've been a Stable Release Manager for a year in 2006, and did heavy bug squashing to release Etch that same year. I also was an Application Manager in 2006 and managed the application of 2 Debian developers (Jose Parrella and Dami n Viano). I admit I've been less active in Debian after 2007, mainly because I was busy working on awesome, GNU Emacs and others software. Since 2011, I joined the OpenStack packaging team and I'm working on OpenStack on a (almost) daily basis. I don't know how many packages I touched, managed or updated, but that should be one or two hundreds. I still maintain 53 of them. After all, the adventure has been really pleasant, and I had the chance to work with and meet fabulous and smart people. I always liked this project and what it's trying to do. After all these years, I'm definitively staying! See you in another 10 years, folks! :)

23 February 2012

Tanguy Ortolo: Who gave my address to spammers?

For hurried readers: do not give your main email address to Moneybookers or to deviantART, since they may give it (unintentionally, I hope) to spammers.Dedicated addresses Since I have set up my own email server, when a company or an unknown individual asks for an address I give it a dedicated one. For instance, to make a payment I had to give an address to Moneybookers: instead of giving them my main address <tanguy@>, I used <tanguy+moneybookers@>. Thanks to Postfix's address extension feature (look for recipient_delimiter in postconf(5) manpage), these <tanguy+whatever@> are all implicit aliases to my main address. This practice has several benefits, since it allows me to: Working around lamers Some systems are coded by lamers that think the + sign is forbidden for email addresses, so I have to work around that. My current solution it to use a static alias <tanguy-2012@>, which I simply drop after a year to replace it by a new one. Two years report After two years collecting spam, the first noticeable thing is that, among 5.5k spams I received, only 78 are the result of an information leak from an organization. I excluded from that count the addresses I use in public mailing-lists, for instance <tanguy+debian@>. So, after some fine exclusion and checking of messages, these are the only two organizations that somehow gave my address to spammers:

  1. Moneybookers: 43 spam messages received;
  2. deviantArt: 35 spam messages received.

22 February 2012

Bernd Zeimetz: nagios-plugins-contrib released

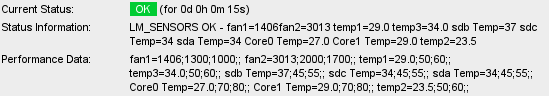
Nagios or Icinga users probably know the problem that neither the default plugin packages (nagios-plugins-basic and -standard) nor the few other plugin packages ship all the plugins you need to monitor your hardware and software properly. And unless you have puppet, cfengine or some other automation software, you probably just start searching plugins on Nagios Exchange, MonitoringExchange or some other machines you are monitoring already. Your problem shall be solved! nagios-plugins-contrib passed NEW today. It is a collection of various useful plugins, maintained within the Debian Nagios Maintainer Group. So far it contains only 6 plugins (check_email_delivery, check_ipmi_sensor, check_lm_sensors, check_memcached, check_raid, check_rbl), but more are going to come. check_lm_sensors in action To have your favorite plugins added to the package we would like to encourage you to send pull requests, either using github, alioth or your personal repository. Please keep in mind that you'll be added to the Uploaders of the package automatically to ensure that you keep your plugin updated and in a good shape. See debian/README.source for some instructions on adding new plugins. Unmaintained plugins will be removed! Of course you can also submit bug reports to have a new plugin added, but you have to convince somebody to maintain it for you (or that he wants to use the plugin and needs to maintain it therefore :) ). We might also also have a similar package in contrib as a lot of commonly used plugins require non-free software, so don't hesitate to prepare plugins for inclusion in such a package and let us know! Suggestions and ideas for improvement are always welcome. And so is help to maintain the packages!
Next.

Previous.