Search Results: "cas"

17 August 2013

Daniel Leidert: Create a KNOPPIX USB (boot-)stick from a running Linux system

I was recently examining, how to boot a (live) KNOPPIX from an USB stick. It turns out I did not find a manual about how to create a bootable USB stick containing KNOPPIX without burning KNOPPIX to a CD/DVD first?! So this is a short howto without burning anything. I'm showing how to put a KNOPPIX ISO image to an USB stick. I need an ISO image of KNOPPIX, an USB stick and syslinux installed. I've chosen to put the 4GB DVD image KNOPPIX_V7.2.0DVD-2013-06-16-EN.iso onto a 16GB USB stick. The place left on the USB device should be available to the user as NTFS partition. I'll use the term /dev/sdX to refer to the stick (where X is a lowercase character, e.g. /dev/sdb) and completely empty it first (THIS WILL DELETE ALL DATA INCLUDING THE PARTITION TABLE!):
shred -z /dev/sdX
Now after the ISO image has been downloaded, we need to alter it a bit. For this some information about the USB stick is required. The relevant bits heads and sectors/track are highlighted below:

fdisk -l /dev/sdX

Disk /dev/sdX: 16.0 GB, 16008609792 bytes
64 heads, 32 sectors/track, 15267 cylinders, total 31266816 sectors
Units = sectors of 1 * 512 = 512 bytes
Sector size (logical/physical): 512 bytes / 512 bytes
I/O size (minimum/optimal): 512 bytes / 512 bytes
Disk identifier: 0x0000

Device Boot Start End Blocks Id System
Now we change the ISO image for hybrid mode:
isohybrid -o 1 -h 64 -s 32 -e 1 KNOPPIX_V7.2.0DVD-2013-06-16-EN.iso
and copy the ISO image to the USB stick:
cat KNOPPIX_V7.2.0DVD-2013-06-16-EN.iso > /dev/sdX
After the command has succeeded, the partition table will show a bootable "Hidden HPFS/NTFS" partition. Note that you can adjust the partition type by using the -t, --type switch of isohybrid.

fdisk -l /dev/sdX

Disk /dev/sdX: 16.0 GB, 16008609792 bytes
64 heads, 32 sectors/track, 15267 cylinders, total 31266816 sectors
Units = sectors of 1 * 512 = 512 bytes
Sector size (logical/physical): 512 bytes / 512 bytes
I/O size (minimum/optimal): 512 bytes / 512 bytes
Disk identifier: 0x0000

Device Boot Start End Blocks Id System
/dev/sdX * 1 8032255 4016127+ 17 Hidden HPFS/NTFS
Now we can create one or more partitions on the stick for shipping data or $whatever by using fdisk, e.g. create a new primary partition and set the type to HPFS/NTFS/exFAT:

fdisk /dev/sdX

Command (m for help): p

Disk /dev/sdX: 16.0 GB, 16008609792 bytes
64 heads, 32 sectors/track, 15267 cylinders, total 31266816 sectors
Units = sectors of 1 * 512 = 512 bytes
Sector size (logical/physical): 512 bytes / 512 bytes
I/O size (minimum/optimal): 512 bytes / 512 bytes
Disk identifier: 0x12345678

Device Boot Start End Blocks Id System
/dev/sdX * 1 8032255 4016127+ 17 Hidden HPFS/NTFS

Command (m for help): n
Partition type:
p primary (1 primary, 0 extended, 3 free)
e extended
Select (default p): p
Partition number (1-4, default 2): 2
First sector (8032256-31266815, default 8032256):
Using default value 8032256
Last sector, +sectors or +size K,M,G (8032256-31266815, default 31266815):
Using default value 31266815

Command (m for help): t
Partition number (1-4): 2
Hex code (type L to list codes): 7
Changed system type of partition 2 to 7 (HPFS/NTFS/exFAT)

Command (m for help): p

Disk /dev/sdX: 16.0 GB, 16008609792 bytes
64 heads, 32 sectors/track, 15267 cylinders, total 31266816 sectors
Units = sectors of 1 * 512 = 512 bytes
Sector size (logical/physical): 512 bytes / 512 bytes
I/O size (minimum/optimal): 512 bytes / 512 bytes
Disk identifier: 0x12345678

Device Boot Start End Blocks Id System
/dev/sdX1 * 1 8032255 4016127+ 17 Hidden HPFS/NTFS
/dev/sdX2 8032256 31266815 11617280 7 HPFS/NTFS/exFAT

Command (m for help): w

[..]

Run mkfs.ntfs on /dev/sdX2 to create the NTFS file system there. The USB stick is ready now. Connected to the system where one wants to start a live KNOPPIX and chosen to boot this system from USB will result in a running KNOPPIX system.The same should also work for creating a Debian live system USB stick. Thanks to the author of this article.

Steve Kemp: Soon it will be time for something different

This weekend I'm mostly alternating between reading, writing, and trying to avoid death by the plague.[*] I've switched Lumail to using a UTF-8 aware string library, which means we can now handle the obvious case:
--
-- Prove keybindings work.
--
keymap['global'][' '] = 'msg("UTF-8 rocks!")'
Similarly we can stuff input into the buffer:
--
-- Pretend the user typed ":msg ...\n"
--
stuff( ":msg('  is pie')\n" );
This transition was annoying to handle, but wasn't too difficult. There is only one more major update required, according to the development roadmap, which is to double check that UTF-8 output is correct. Otherwise I think I'm almost done. In the sense that I don't see anything obvious missing, barring things that won't ever happen such as mutt-style "tag" support. I've updated the online examples to include some nice code: I can't claim to have many users, so far the development has been carried out by myself and approximately four other people. But that matters not. I genuinely believe this is a good client and it really suits the way that I handle (large volumes of) email: Allowing you to open multiple folders at once means you get a great view into your currently-unread mail, regardless of where procmail has placed it. The overriding feeling having "completed" the client is that Lua rocks. I'm torn between wanting to sleep some more, and wondering what other system/package/tool can be extended by Lua. As epiphanies go my on_idle() update takes some beating.
* - I do not have the black death, but I'm not well.

Russ Allbery: WebAuth 4.5.4

WebAuth is the site-wide centralized web authentication system that we use at Stanford. This release is a bug-fix release for the central login server, mostly focused on multifactor authentication but also featuring a wide variety of random bug fixes. Going into this release, I filtered the Apache error logs on all of our production servers for a period of a month and then set out to fix every log anomaly or odd behavior pattern that I detected. The most significant bug fix is to support for requiring non-password session factors. The code handled this entirely incorrectly, resulting in the user being stuck at the password authentication prompt and never able to proceed. It also cleans up several corner cases involving REMOTE_USER authentication to sites that require a Kerberos authenticator (such as for delegated credentials). This release downgrades a mismatch of login credentials and a webkdc-proxy token (single sign-on credentials) to a log warning rather than a fatal error and just discards the non-matching single sign-on credentials. This case ideally shouldn't happen, but sometimes users share devices, and if they hit a site with forced login or session factors, it's easy for this case to arise. WebLogin now retries the WebKDC POST once and ignores SIGPIPE errors to work around problems with signals from the FastCGI process manager. It also rewrites non-ASCII characters in XML from the WebKDC to work around XML validation errors created by non-ASCII characters in Kerberos error messages, pending a better fix on the WebKDC side. Password changes no longer go through the replay detection logic, which should not apply to them. Several error messages in WebLogin are now clearer. The WebKDC now requires that the return URL in a WebAuth request be an absolute URL and not contain any non-ASCII characters. A bug in the way that errors during the authentication process were reported has been fixed and should produce better error output for the user. There are also a few other, more minor bug fixes, particularly to logging and error reporting. You can get the latest release from the official WebAuth distribution site or from my WebAuth distribution pages.

16 August 2013

Sylvain Le Gall: Augeas tips and tricks for Puppet user: edit a complex node.

I have a recurring problem when trying to use augeas on a complex node: trying to edit a specific entry in a list which is uniquely defined by many attributes. You probably don't know that you have this problem, but it is easy to spot it into your augeas/puppet resource. Here are some symptoms of this problem:
 
 augeas  
   "setup-shorewall":
     changes =>
       [
         "set entry[last() + 1]/source 'all'",
         "set entry[last()]/dest 'all'",
         "set entry[last()]/policy 'REJECT'",
         "set entry[last()]/log_level 'info'",
       ],
     onlyif => "match entry[source = 'all'][dest = 'all'][policy = 'REJECT'] size == 0";
For a long time, I thought it was the only solution. But last week, I read again the documentation and found another solution. My main concerns are the onlyif and last() parts, it doesn't look clean to me. The problem is that I cannot define the entry all at once and if I use a value that will be set late, the node cannot be targeted in between. The clean way to do this was to define first the target attribute. Typically, in augeas changes:
 set spec[user = '$name']/user '$name'
This way if the node doesn't exist it is created and you can then use it directly:
 set spec[user = '$name']/host_group/host 'ALL'
 set spec[user = '$name']/host_group/command1 'ALL'
 set spec[user = '$name']/host_group/command1/tag 'PASSWD'
But sometimes it is not possible to set the attribute directly -- typically when you need to use multiple attribute. The solution in this case is to use defnode:
 defnode target entry[#comment = 'puppet: <%= name %>']/ "<%= name %>"
 set $target/action '<%= action %>'
 set $target/source '<%= source %>'
 set $target/#comment 'puppet: <%= name %>'
 clear $target
The big trick here is that defnode needs a value, but most of the time you cannot set a value for the node -- because it has none. To solve this, you set a value with defnode, process with your change and you clear the node at the end. This recent discovery has simplify a lot some augeas changes I use. Feel free to leave comment on your personal technique to deal with augeas and puppet.

Daniel Leidert: N54L LCD-Mod with U204FR-A3 (LCDModkit) and lcdproc (II)

Here it goes. I was looking for an LCD display for my microservers 5,25'' bay and found this neat post. The manufacturer of the LCD display used there provides different displays for this purpose. I've decided for an U204FR-A2 in black with a red backlight. It left Hongkong around five days later and arrived here another 6 days later. All in all: I got it after 11 days. I unpacked the LCD device. It comes with an internal USB connector and is driven by an Hitachi HD44780 LCD controller. The connection wasn't a problem at all. I've already put a Silverstone SST-EC04-P PCIe card with two USB 3.0 external ports and an internal 19pin dual port connector into the systems PCIe 1x slot. Now to connect the LCD with this card I've bought an Inline 19pin USB 3.0 header to 8pin double USB 2.0 header adapter and connected the card with the LCD display. Easy, right?
To make the display "attached" to the case - it comes with two steel sheets and two screw holes each, that cannot be attached to anything in the microserver case - I've used a small workaround: double-faced adhesive tape and two halfs of a matchbox - one can also use small scantlings - and created a bonding between the steel sheets and the case.
That's it. I put the cover plate carefully back - the steels sheets of the LCD display and the LED of the server will bump to each other!
There are two programs to output information to the LCD display. These are lcdproc and lcd4linux. I started with the first one which only provides pre-defined screens. Seems with the latter one can create own screens. This is an option for the future. lcdproc consists of two programs. First there is a daemon called LCDd. It controls the driver, contrast etc.pp. The relevant parts of its configuration file /etc/LCDd.conf look like as shown below. Note that I did not change the default values for contrast or brightness.

[server]
Driver=hd44780
WaitTime=25

[hd44780]
ConnectionType=lcd2usb
Size=20x4
To print something to the screen one can use the lcdproc command, which is configured via /etc/lcdproc.conf. I've enabled the Iface, TimeDate, SMP-CPU, and MiniClock screens. The program is started during startup via cron. The file /etc/cron.d/lcdproc simply contains this:

@reboot root lcdproc
The following pictures show the resulting screens, which change every 25 seconds. That's it.

Justus Winter: All the important bits are there - please test and review :)

Finally, more bootlog-pr0n:
start ext2fs: Hurd server bootstrap: ext2fs[device:hd0s1] exec init proc auth
INIT: version 2.88 booting
Using makefile-style concurrent boot in runlevel S.
Activating swap...done.
Checking root file system...fsck from util-linux 2.20.1
hd2 : tray open or drive not ready
end_request: I/O error, dev 02:00, sector 0
/dev/hd0s1: clean, 44680/181056 files, 292234/723200 blocks
done.
Activating lvm and md swap...(default pager): Already paging to partition hd0s5!
done.
Checking file systems...fsck from util-linux 2.20.1
hd2 : tray open or drive not ready
end_request: I/O error, dev 02:00, sector 0
done.
Cleaning up temporary files... /tmp.
Mounting local filesystems...done.
Activating swapfile swap...(default pager): Already paging to partition hd0s5!
done.
df: Warning: cannot read table of mounted file systems: No such file or directory
Cleaning up temporary files....
Configuring network interfaces...inetutils-ifconfig: invalid arguments
ifup: failed to open pid file /run/network/ifup-/dev/eth0.pid: No such file or directory
Internet Systems Consortium DHCP Client 4.2.2
Copyright 2004-2011 Internet Systems Consortium.
All rights reserved.
For info, please visit https://www.isc.org/software/dhcp/
can't create /var/lib/dhcp/dhclient./dev/eth0.leases: No such file or directory
Listening on Socket//dev/eth0
Sending on   Socket//dev/eth0
DHCPDISCOVER on /dev/eth0 to 255.255.255.255 port 67 interval 8
DHCPREQUEST on /dev/eth0 to 255.255.255.255 port 67
DHCPOFFER from 10.0.2.2
DHCPACK from 10.0.2.2
can't create /var/lib/dhcp/dhclient./dev/eth0.leases: No such file or directory
bound to 10.0.2.15 -- renewal in 34744 seconds.
done.
Cleaning up temporary files....
Setting up X socket directories... /tmp/.X11-unix /tmp/.ICE-unix.
INIT: Entering runlevel: 2
Using makefile-style concurrent boot in runlevel 2.
Starting enhanced syslogd: rsyslogd.
Starting deferred execution scheduler: atd.
Starting periodic command scheduler: cron.
Starting system message bus: dbusFailed to set socket option"/var/run/dbus/system_bus_socket": Protocol not available.
Starting OpenBSD Secure Shell server: sshd.
unexpected ACK from keyboard
GNU 0.3 (debian) (console)
login: root
root@debian:~# shutdown -h now
Broadcast message from root@debian (console) (Fri Aug 16 20:02:47 2013):
The system is going down for system halt NOW!
INIT: Switching to runlevel: 0root@debian:~#
INIT: Sending processes the TERM signal
INIT: Sending processes the KILL signal
Using makefile-style concurrent boot in runlevel 0.
Stopping deferred execution scheduler: atd.
task c10f72a8 deallocating an invalid port 2098928, most probably a bug.
Asking all remaining processes to terminate...done.
All processes ended within 1 seconds...done.
Stopping enhanced syslogd: rsyslogd.
Deconfiguring network interfaces...ifdown: failed to open pid file /run/network/ifdown-/dev/eth0.pid: No such file or directory
Internet Systems Consortium DHCP Client 4.2.2
Copyright 2004-2011 Internet Systems Consortium.
All rights reserved.
For info, please visit https://www.isc.org/software/dhcp/
can't create /var/lib/dhcp/dhclient./dev/eth0.leases: No such file or directory
Listening on Socket//dev/eth0
Sending on   Socket//dev/eth0
/bin/sh: 1: ifconfig: not found
done.
Deactivating swap...swapoff: /dev/hd0s5: 177152k swap space
done.
Unmounting weak filesystems...umount: /etc/mtab: Warning: duplicate entry for device /dev/hd0s1 (/dev/cons)
umount: could not find entry for: /dev/cons
done.
Unmounting local filesystems...done.
mount: cannot remount /: Device or resource busy
Will now halt.
init: notifying pfinet of shutdown...init: notifying tmpfs swap of shutdown...init: notifying tmpfs swap of shutdown...init: notifying tmpfs swap of shutdown...init: notifying ext2fs device:hd0s1 of shutdown...init: halting Mach (flags 0x8)...
In tight loop: hit ctl-alt-del to reboot
(You might note that df complains about not being able to read the mtab file. That is because it has been built with _PATH_MOUNTED being /var/run/mtab. This will correct itself when the coreutils package is being rebuilt against a patched libc.) I spent my last two weeks with polishing my patch series, that meant a lot of package rebuilds and that means a lot of waiting (even more so on the Hurd, short version: fakeroot-hurd could be fast but is not yet working properly, fakeroot-tcp is slow) and thus some frustration ;) Also I had to pay special attention so that the upgraded packages could be installed without accidentally breaking anything in the process. Making sysvinit pid 1 is surprisingly tricky in this regard since it breaks the ABI and requires a libc fix that also worked with the current Hurd servers. Here are the patches: So I had some spare time on my hand while waiting for numerous package rebuilds and I took this as an opportunity to read papers about Mach and to familiarize myself with mig, the Mach Interface Generator. While I have used it in the past, I had not yet looked at its implementation. And I had to patch the exec server, and there was both code implementing a questionable feature (on-demand unzipping of binaries) and code that was not even compiled (courtesy of the preprocessor) and had probably bit-rot by now. So I figured I could spend my time doing some cleanups: I have rebuild all the necessary packages and uploaded them into an apt repository:
deb http://teythoon.cryptobitch.de/gsoc/heap/debian unstable main
Please use unstable for now. Also make sure that you have a recovery plan for your Debian/Hurd installation if anything goes wrong. For your convenience there's a seed tarball containing packages with the appropriate sources.list.d snippets and the repository key: https://teythoon.cryptobitch.de/gsoc/heap/debian/seed.tar If you want to switch to the new runsystem.sysv, do:
# update-alternatives --config runsystem
Whenever you switch runsystems, please use reboot-hurd to reboot the system. This is the most robust way. Known issues: Next week I will address the network related issues. By now they are the source of most of the error messages in the bootlog.

Lucas Nussbaum: Debian birthday

This upload was the first one of my very first package in Debian. It was sponsored by Dafydd Harries, who I ve finally met at DebConf13, and got out of NEW on 2005-08-16. Exactly 8 years ago today. I only realized that yesterday evening, and Debian s birthday feels even more special to me now. Dafydd, it looks like I owe you a lot! :)

Lucas Nussbaum: DebConf

This DebConf is obviously quite special for me, being the DPL. It has really been great so far to talk to meet so many people, and especially to meet so many new Debian contributors or Developers. I m really happy to see that the next generation is ready! :) On Sunday, I delivered my Bits from the DPL talk. The video is available, and I ve finally uploaded the slides (working link here, it seems that Penta ate my slides). I hope you enjoyed it/will enjoy it!

15 August 2013

Daniel Leidert: HP N54L Microserver - energy efficiency and power management

I recently worked on activating power management functions, reduce energy consumption and noise of my little HP N54L "toy". During this process I tried to avoid the usage of /etc/rc.local and set things by udev, hdparm and friends. Below are my results. Actual resultsWith the following steps my system (N54L + 3xWD20EFRX HDD +1xWD5003AZEX HDD + LCD-mod + case fan mod + Debian Wheezy) uses 27W in idle mode. The USB W-LAN card uses another 10W. In active mode, e.g. compiling source code, the system runs (and boots) with around 57W. The highest power consumption observed is during startup phase with 88W. First things firstFor the following steps it might be necessary to have some packages installed, that maybe do not occur in this post. If I missed something, I appreciate a hint. Further the following steps might produce even better results with a custom kernel. I'm using the stock linux-image-3.2.0-4-amd64 kernel image as the time of writing and I have these packages installed: amd64-microcode, firmware-linux, firmware-linux-free, firmware-linux-nonfree and firmware-atheros (the latter for my WLAN card). ASPM and ACPIFirst I enabled PCIE ASPM in my (non-modded) BIOS and forced it together with ACPI via grub by changing GRUB_CMDLINE_LINUX_DEFAULT in /etc/default/grub so it looks like this:

GRUB_CMDLINE_LINUX_DEFAULT="quiet splash acpi=force pcie_aspm=force nmi_watchdog=0"
ASPM has now been enabled as lspci prooves:

00:04.0 PCI bridge: Advanced Micro Devices, Inc. [AMD] RS780/RS880 PCI to PCI bridge (PCIE port 0) (prog-if 00 [Normal decode])
[..]
LnkCap: Port #1, Speed 5GT/s, Width x1, ASPM L0s L1, Latency L0 <64ns, L1 <1us
ClockPM- Surprise- LLActRep+ BwNot+
LnkCtl: ASPM L0s L1 Enabled; RCB 64 bytes Disabled- Retrain- CommClk+
ExtSynch- ClockPM- AutWidDis- BWInt- AutBWInt-
[..]
00:06.0 PCI bridge: Advanced Micro Devices, Inc. [AMD] RS780 PCI to PCI bridge (PCIE port 2) (prog-if 00 [Normal decode])
[..]
LnkCap: Port #3, Speed 5GT/s, Width x1, ASPM L0s L1, Latency L0 <64ns, L1 <1us
ClockPM- Surprise- LLActRep+ BwNot+
LnkCtl: ASPM L0s L1 Enabled; RCB 64 bytes Disabled- Retrain- CommClk+
ExtSynch- ClockPM- AutWidDis- BWInt- AutBWInt-
02:00.0 USB controller: Renesas Technology Corp. uPD720201 USB 3.0 Host Controller (rev 03) (prog-if 30 [XHCI])
[..]
LnkCap: Port #0, Speed 5GT/s, Width x1, ASPM L0s L1, Latency L0 <4us, L1 unlimited
ClockPM+ Surprise- LLActRep- BwNot-
LnkCtl: ASPM L0s L1 Enabled; RCB 64 bytes Disabled- Retrain- CommClk+
ExtSynch- ClockPM- AutWidDis- BWInt- AutBWInt-
[..]
03:00.0 Ethernet controller: Broadcom Corporation NetXtreme BCM5723 Gigabit Ethernet PCIe (rev 10)
[..]
LnkCap: Port #0, Speed 2.5GT/s, Width x1, ASPM L0s L1, Latency L0 <1us, L1 <64us
ClockPM+ Surprise- LLActRep- BwNot-
LnkCtl: ASPM L0s L1 Enabled; RCB 64 bytes Disabled- Retrain- CommClk+
ExtSynch- ClockPM- AutWidDis- BWInt- AutBWInt-
[..]
Even so /sys/module/pcie_aspm/parameters/policy will still show as below:

[default] performance powersave
I'll show how to set the powersave value in /sys/module/pcie_aspm/parameters/policy in the next section.JFTR: These are my ACPI related packages installed: acpi, acpid, acpi-support and acpi-support-base. Enable powersaving via UDEVThe following rules file /etc/udev/rules.d/90-local-n54l.rules has been inspired by a blog post. It enables powersaving modes for all PCI, SCSI and USB devices and ASPM. Further the internal RADEON cards power profile is set to the low value. There is no monitor connected usually. The file contains these rules:

SUBSYSTEM=="module", KERNEL=="pcie_aspm", ACTION=="add", TEST=="parameters/policy", ATTR parameters/policy ="powersave"

SUBSYSTEM=="i2c", ACTION=="add", TEST=="power/control", ATTR power/control ="auto"
SUBSYSTEM=="pci", ACTION=="add", TEST=="power/control", ATTR power/control ="auto"
SUBSYSTEM=="usb", ACTION=="add", TEST=="power/control", ATTR power/control ="auto"
SUBSYSTEM=="usb", ACTION=="add", TEST=="power/autosuspend", ATTR power/autosuspend ="2"
SUBSYSTEM=="scsi", ACTION=="add", TEST=="power/control", ATTR power/control ="auto"
SUBSYSTEM=="spi", ACTION=="add", TEST=="power/control", ATTR power/control ="auto"

SUBSYSTEM=="drm", KERNEL=="card*", ACTION=="add", DRIVERS=="radeon", TEST=="power/control", TEST=="device/power_method", ATTR device/power_method ="profile", ATTR device/power_profile ="low"

SUBSYSTEM=="scsi_host", KERNEL=="host*", ACTION=="add", TEST=="link_power_management_policy", ATTR link_power_management_policy ="min_power"
Set harddrives spindown timeoutI decided to sent my system drive to standby after 20 minutes and the RAID drives after 15 minutes. This is usually ok, because the RAID isn't always used. hdparm is the right tool to realize this. Many people use the /dev/disk/by-uuid/... syntax here, to avoid having to touch the configuration file if some system configuration changes. Because I'm running a RAID, I couldn't use this syntax, although it might be possible to use /dev/disk/by-id/... instead. Well for the moment I stay with the configuration below. The relevant part of /etc/hdparm.conf is:

[..]

# system harddrive
/dev/sda
spindown_time = 240


# below are the WD20EFRX drives
/dev/sdb
spindown_time = 180


/dev/sdc
spindown_time = 180


/dev/sdd
spindown_time = 180

Idle modeWhen there is nothing to do for the system, all I hear is the (still a bit noisy) fan of the power supply, which I might replace in the future too. Either by testing a different fan or by replacing the whole power supply unit by the fanless FORTRON FSP150-50TNF or (even better) a picoPSU.The system currently shows a power consumption of around 37W in idle mode whereas the USB W-LAN card itself needs around 10W. There is a possibility to enable power savings mode for this card too. I could add this entry to /etc/udev/rules.d/90-local-n54l.rules:

SUBSYSTEM=="net", ACTION=="add", KERNEL=="wlan*" RUN+="/usr/bin/iw dev %k set power_save on"
But it turned out that the connection became a bit unstable after it. So I don't use this rule. More on the roadThere are a lot more options one can easily find via $search_engine. The N54L system could be brought to sleep and woken up by LAN via Wake-on-LAN (WOL). This is a feature I don't use. I've also read rumors about enabling different sleep/suspend states of the system, which seems to require to install a modded BIOS. Well, I'll post news and changes if they happen to come;)

Russell Coker: Google web sites and Chromium CPU Use

Chromium is the free software build of the Google Chrome web browser. It s essentially the same as the Google code but will often be an older version, particularly when you get Chromium from Debian/Stable (or any other Linux distribution that doesn t track the latest versions all the time) and compare it to getting Chrome straight from Google. My wife is using Chromium on an AMD Opteron 1212 for all the usual web browsing tasks. Recently I ve noticed that it takes a lot of CPU time whenever she leaves a Google web site open, that can be Google+, Gmail, or Youtube. Web standards are complex and it s difficult to do everything the way that one might desire. Making a web browser that doesn t take 100% CPU time when the user is away from their desk may be a difficult technical challenge. Designing a web site that doesn t trigger such unwanted behavior in common web browsers might also be a challenge. But when one company produces both a web browser and some web sites that get a lot of traffic it s rather disappointing that they don t get this right. It could be that Google have fixed this in a more recent version of the Chrome source tree, and it could be that they fixed the browser code before rolling out a new version of Google+ etc which causes problems with the old version (which might explain why I ve never seen this problem). But even if that is the case it s still disappointing that they aren t supporting older versions. There is a real need for computers that don t need to be updated all the time, running a 3 month old Linux distribution such as Debian/Wheezy shouldn t be a problem. There s also a possibility that part of the cause of the problem is that an Opteron 1212 is a relatively slow CPU by today s standards and it s the slowest system I m currently supporting for serious desktop use. I don t even think it was one of the fastest CPUs available when it was released 4 years ago. But I think we should be able to expect systems to remain usable for more than 4 years. The Opteron 1212 system is a Dell PowerEdge tower server that is used as a workstation and a file server, so while I get desktop systems with faster CPUs for free I want to keep using the old PowerEdge server to avoid data corruption. As an aside I ve been storing important data on BTRFS for a year now and the only data loss I ve suffered has been due to a faulty DIMM. The filesystem checksums built in to modern filesystems such as BTRFS and ZFS mean that RAM corruption covers a greater portion of the risk to data integrity and the greater complexity of the data structures in such filesystems gives the possibility of corruption that can t be fixed without mkfs (as happened to me twice on the system with a bad DIMM). The consequences of such wasted CPU use are reduced CPU time for other programs which might be doing something useful, extra electricity use, and more noise from CPU cooling fans (which is particularly annoying for me in this case). Any suggesstions for reducing the CPU use of web browsers, particularly when idle?

Daniel Pocock: Free software for free markets

Co-inciding with the first DebConf in Switzerland, one of the world's leading financial centers, the first official packaging of open messaging and market data distribution framework OpenMAMA for a Linux distribution has just been uploaded. The packages, along with the Avis low-latency event-router middleware/transport were uploaded to the Debian unstable catalog this week and will soon be available conveniently to install with apt-get. OpenMAMA was developed by NYSE Technologies and includes code originally developed under their previous brand Wombat Financial Software. The project was recently placed under the strategic umbrella of the Linux Foundation. Packages for Fedora and EPEL The initial packaging effort has identified a number of build system bugs, patches have been contributed upstream. The resolution of these issues and the experience gained with the Debian package will make it relatively easy to package for RPM-based platforms in the near future. Not just for finance While it is clear that OpenMAMA's designers had financial services in mind (and the low-latency, high throughput transport of market price data in particular), the solution is generalised and likely to be useful in other domains where asynchronous messaging and inter-process communication is required. In fact, this distinction is made particularly clear by the division of OpenMAMA into two subprojects:
  • OpenMAMA itself is a general-purpose programming API for asynchronous messaging. It hides the details of various low-level transports, including the open source Avis event router and popular proprietary solutions like Tibco Rendezvous. Java programmers have had such a generalised API for many years (JMS), whereas OpenMAMA brings a similar paradigm to the C/C++ developer.
  • OpenMAMDA is a further layer on top of OpenMAMA designed to encapsulate market data. It competes directly with proprietary solutions such as those from Reuters and Bloomberg. OpenMAMDA comes with specific APIs for news, order books and options and could be extended for other markets.
Commercial background Reuters and Bloomberg are well known as two of the main vendors in the market data industry. Both of them (and other competitors) provide a range of data services and related software. Buying a data feed doesn't automatically give access to the software from the same franchise: the software and APIs are promoted as a valuable product in their own right. It is actually quite possible (and not unheard of) for an institution to run a Reuters Market Data System (RMDS) software stack fed by a data feed from Bloomberg or vice-versa. When an IT department or third-party vendor of trading systems wants to transport data between applications (or between multiple users of a single application) they will not typically do it themselves and one of these APIs is usually chosen. OpenMAMA appears to be a strong contender for such use cases. Bloomberg has recently made their API public, although OpenMAMA goes much further by making their source code public too. Development samples with the OpenMAMA API Programming the OpenMAMA API appears to be relatively consistent with the event-loop model that many developers are already comfortable with. For a very fast start, two compelling examples are the basic publisher and basic subscriber. Here is a sample of the code from the basic subscriber, demonstrating how to start the event loop and receive event notifications in a callback class:
static void createSubscriber (void)
 
    try
     
        gSubscription = new MamaBasicSubscription;
        gSubscription->createBasic (gTransport,
                                    gDefaultQueue,
                                    new SubscriptionCallback (),
                                    gTopic);
        gSubscription->setDebugLevel (gSubscLogLevel);
     
    catch (MamaStatus &status)
     
        cerr << "Error creating subscription: " 
             << status.toString () << endl;
        exit (1);
     
 
and here is some basic code that processes messages asynchronously:
class SubscriptionCallback : public MamaBasicSubscriptionCallback
 
public:
    virtual ~SubscriptionCallback ()  
    virtual void onCreate (MamaBasicSubscription*  subscription)
     
        if (gQuietLevel < 2)
         
            printf ("Created inbound subscription.\n");
         
     
    virtual void onError (MamaBasicSubscription*  subscription,
                          const MamaStatus&       status,
                          const char*             subject) 
     
        printf ("Error creating subscription: %s\n", 
                status.toString ());
        exit (1);
     
    virtual void onMsg (MamaBasicSubscription* subscription, 
                        MamaMsg&               msg)
     
        if (gQuietLevel < 2)
         
            printf ("Recieved msg.\n");
         
        DisplayIterator it;
        msg.iterateFields (it, NULL, NULL);
     
    //JG: need to add in onDestroy as this is abstract and must be implemented
    virtual void onDestroy (MamaBasicSubscription*  subscription, void * closure)
     
        if (gQuietLevel < 2)
         
            printf ("Destroyed subscription.\n");
         
     
 ;
Practical uses outside financial services Some people may feel that having a low-latency market-data system is overkill for anybody not running a trading desk. Not so. OpenMAMA may well prove useful and convenient as a one-stop-shop API for multi-currency accounting software (Postbooks, GnuCash, etc), for multi-currency web sites (e.g. UberCart) and many other applications.

14 August 2013

Joey Hess: words fail me


Russ Allbery: C TAP Harness 2.2

I've been incredibly, overwhelmingly busy lately, and I'm still fairly consumed by things other than writing journal posts (or reviews, sigh), but hopefully it's letting up a bit now. At the least, I'm back to writing code instead of doing other things, which is quite a relief. There's nothing particularly exciting in this release of my C test harness software, but since I'm doing some general releases anyway, it seemed like a good time to flush out pending changes. This release changes the exit status of the bail and sysbail functions to 255 to more closely match the BAIL_OUT function in Perl's Test::More, and documents why the runtests test harness does not match Test::More's handling of a bailing test case. You can get the latest version from the C TAP Harness distribution page.

13 August 2013

R&#233;mi Vanicat: Git annex and Calibre

The debconf BoF about gitify all things make we to want to report some of my git-annex use cases. The problem Calibre is a ebook manager that is available in debian. I use it to maintain my library, but also to dowload every day an epub version of a French newspaper and then put it on my kobo. Configuring git annex for this I wanted to use git-annex, so
    $ git init
    $ git annex init "some useful name"
But I don't want every thing in annex, because Calibre use some text file to save some metadata, so I used:
    $ git config annex.largefiles "include=* exclude=*.opf exclude=*.json"
then lets add everything
    $ git annex add *
    $ git add *
    $ git commit -m "first commit"
Calibre need read and write access on the its database, so let unlock it:
    $ git annex unlock metadata.db
On my other computer I only need to do
    $ git clone $user@$host:Calibre\ library
    $ cd Calibre\ library
    $ git annex init "another useful name"
    $ git annex get .
    $ git annex unlock metadata.db
The problem is that every time you will git annex sync, git annex will lock again the metadata.db, so lets unlock it automatically. I use git hooks, in .git/hooks/post-commit I have
    #!/bin/bash
    git annex edit metadata.db
don't forget to make this file executable
    $ chmod a+x .git/hooks/post-commit
Day to day operation
    $ git annex add .
Will put new file into the annex
    $ git add .
Will take care of the files that should no go into annex
    $ git annex sync
Will make the repositories exchange informations about all this, and make remote change local
    $ git annex get .
Will make remote book locally available Merge conflict You should not run calibre on the two computer simultaneously, or without syncing before it. If you do, you will have a conflict that git-annex will automatically solve by rename both of the file. You can then either: Checking the library You can use calibredb check_library to check you library is correct. If you use git for it, it will always tell you that it is not correct: there is this author ".git" it doesn't know about. Just don't care about it. Maybe this can be solved by using vcsh but apparently vcsh+git annex it not well tested yet. Automatic stuff I use mr to automatically run all this, but some config could be done (I believe) to have git annex copy --auto do what it should. There are also the git annex assistant for this kind of automatic synchronizations of contents, but I don't know if my automatic unlocking of one file will break this. It might be interesting to find someway to unlock and lock the library only when running calibre, a simple script to launch calibre will do that. Note that each time you will lock and unlock, you will have a new commit in git.

Russell Coker: Nexus 4 Ringke Fusion Case

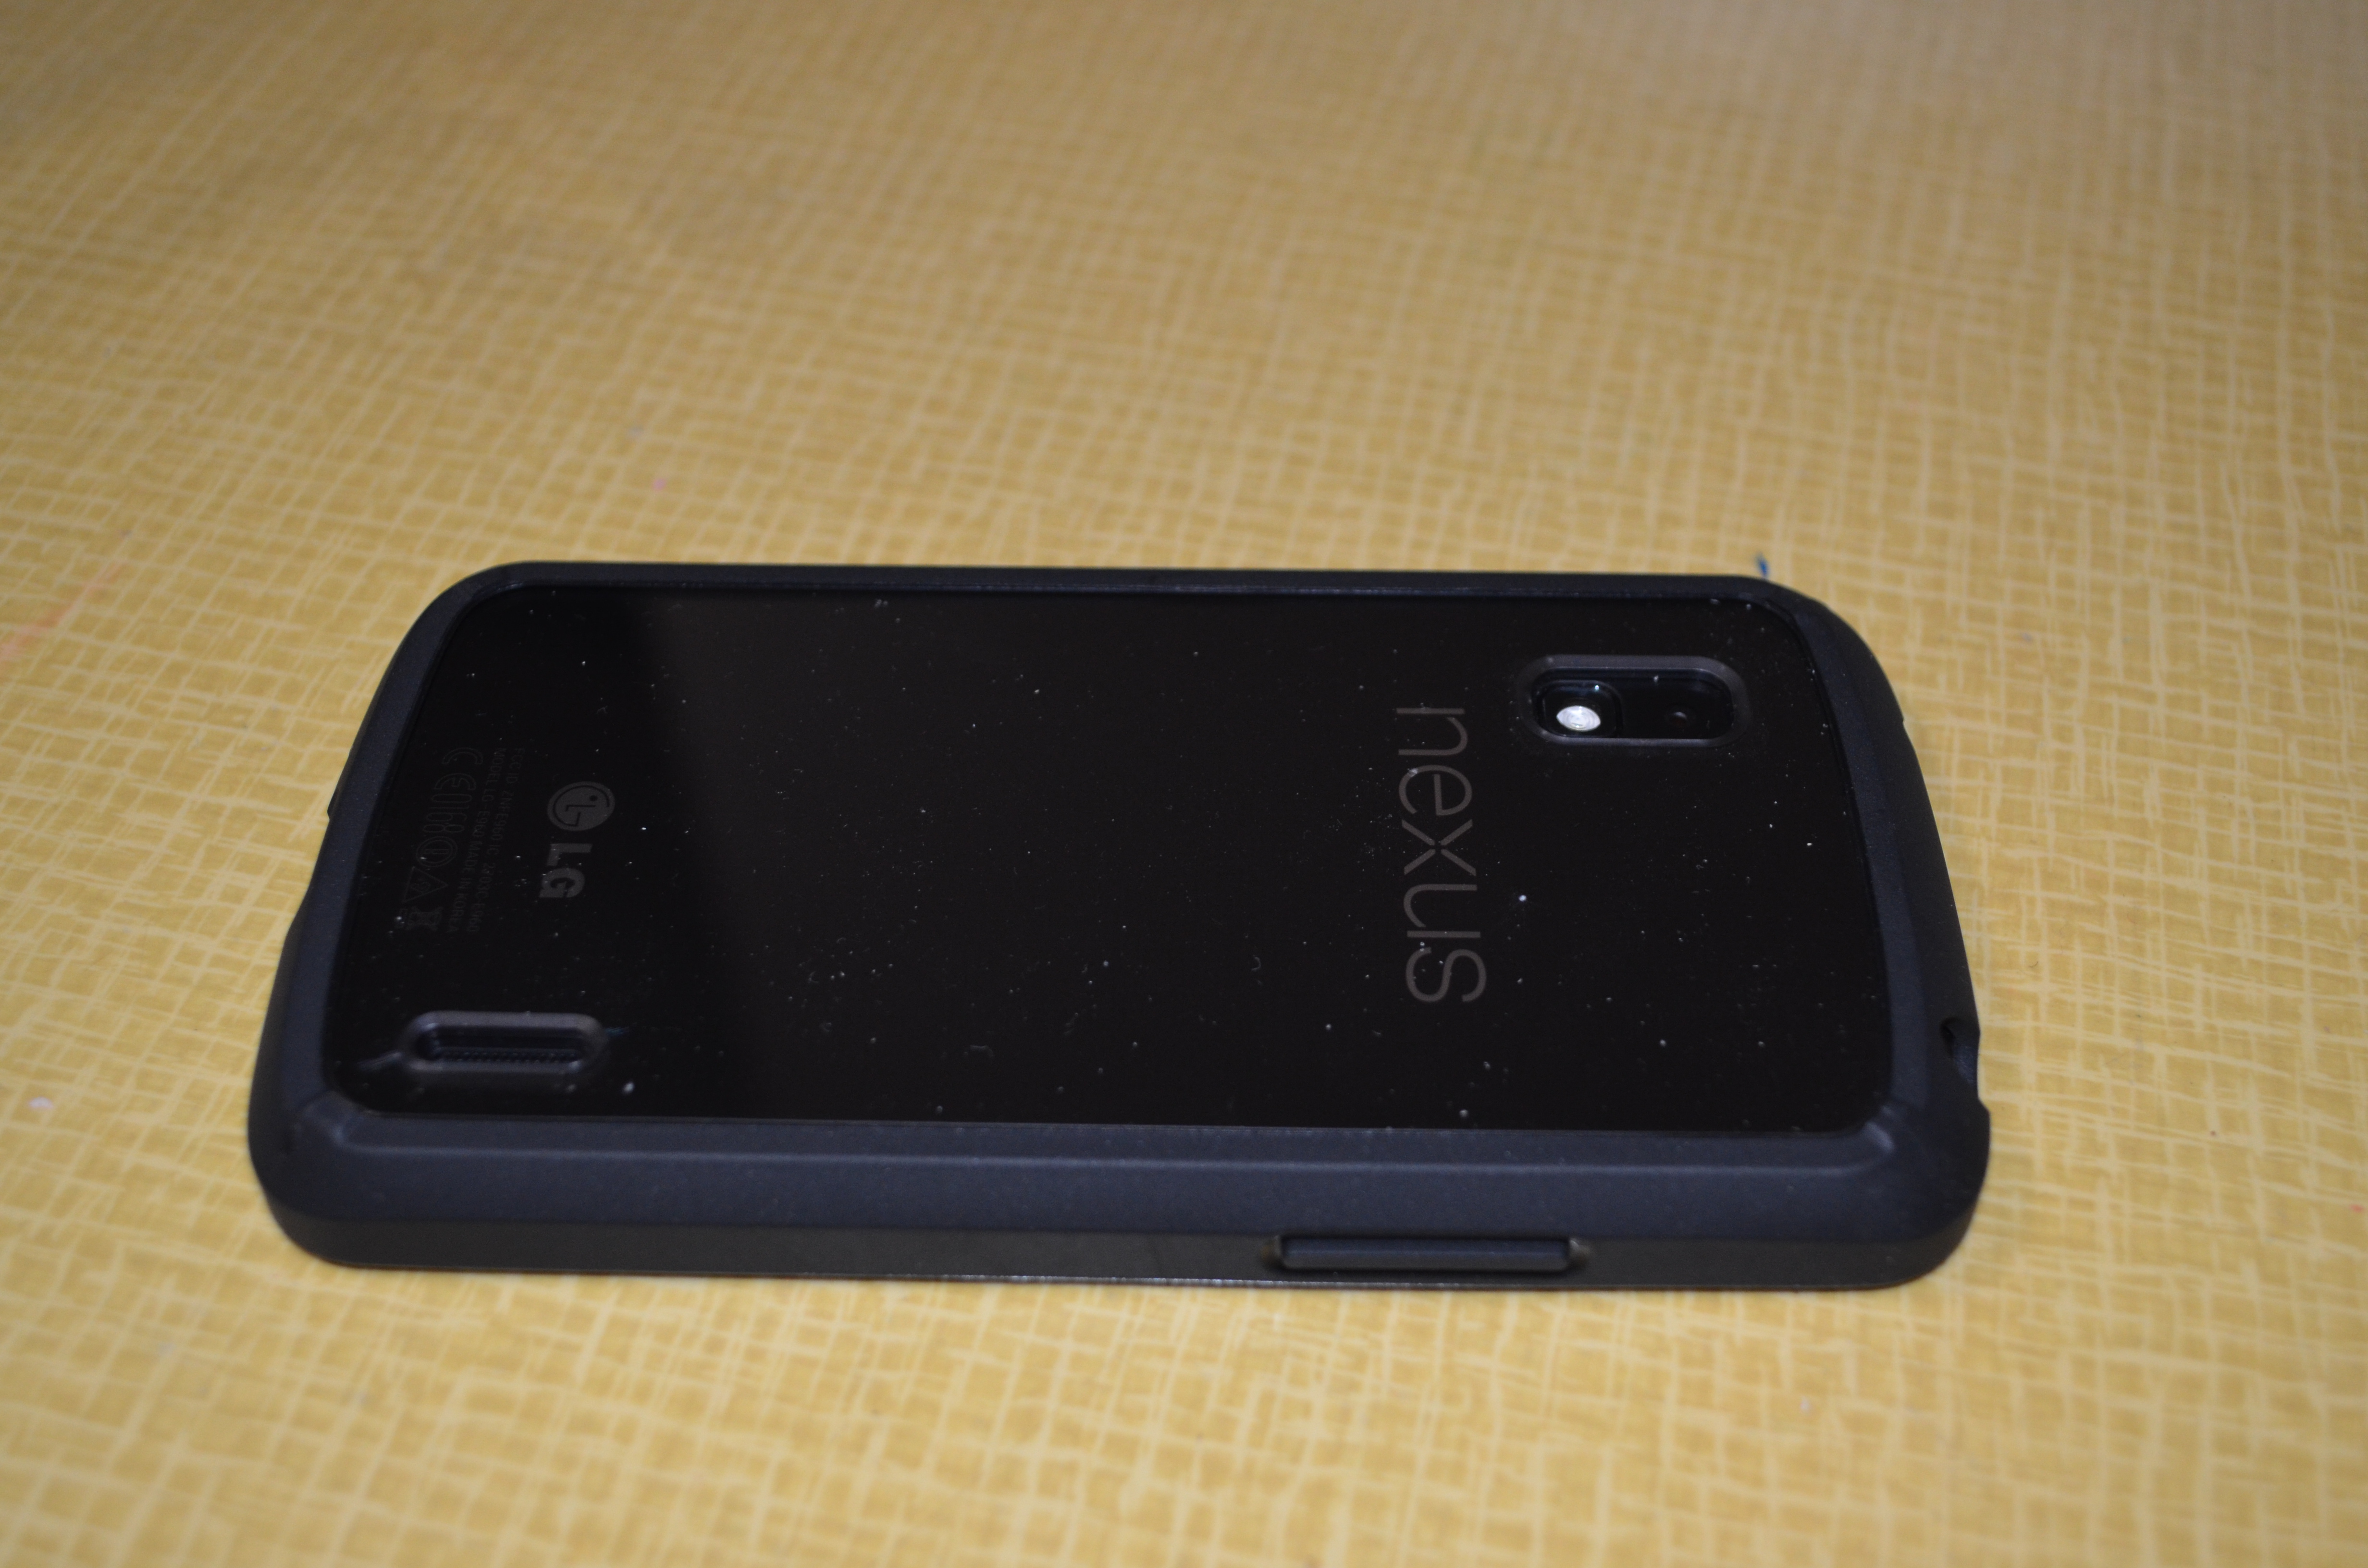
LG Nexus 4 phone with Ringke Fusion case I ve been using Android phones for 2.5 years and for all my phones (Sony-Ericsson Xperia X10, Samsung Galaxy S, Samsung Galaxy S3, and LG Nexus 4) I ve bought gel cases. The gel cases are made of soft rubber which allows phones to bounce rather than break if dropped and also provide better grip (both for holding the phone and for resting it on a vibrating surface such as a tray in a car or plane). The cases have cost me between $12.50 and $15, I haven t felt inclined to pay any more because a case has always seemed like a needless expense, something that merely compensates for deficiencies in phone design. There are some problems with the gel cases, the first one is that they are rather ugly, while I m not really interested in decorating my phones it seems a waste to have a nice phone like the Nexus 4 which has a neat sparkling pattern on the back and then use a case that entirely covers it. The next problem is the fact that the gel cases tend to restrict access to the buttons on the outside of the case. I have been given a Rearth Ringke Fusion case for my Nexus 4 by MobileZap (this is a link for the Nexus 4 cases they sell) [1]. The case features a transparent layer of plastic at the back which protects the phone against having the rear glass of the case break (a known risk with the Nexus 4) while still allowing the user to admire it. With good lighting the sparkling pattern on the back of the phone can still be enjoyed, unfortunately this doesn t show up at all in my photo. It s impossible for a photo to capture a shimmering effect although other photographers have done a better job at showing off a Nexus 4. Also the transparent back to the case gives the option of putting any form of decoration between the phone and the case, for example one could print the logo of their Ingress team and put it between the phone and the case. One thing that is visible in the photo is the feet on the back of the case. With small feet at the corners the transparent back usually won t touch a surface that it rests on, this should prevent unsightly scratches to the back of the case. Also the feet can get some grip on the surface that it rests on, my car has a tray suitable for resting a phone which has a pattern of dimples that catch the feet of the Ringke case and prevent it from sliding. Finally the external buttons for power and volume control are not obstructed in any way. After using 7 phones of 4 different models with gel cases I ve become accustomed to buttons either being difficult to press or easy to press accidentally. The Ringke case allows the buttons to be pressed easily when needed but doesn t seem prone to accidental presses. I m not about to buy a new case for my Galaxy Note 2 (my main phone at the moment) because I don t like paying to replace something that works. But next time I buy a case I ll look for something better than a plain gel case, it s worth paying an extra $9 to get a good case for a phone that costs $350 (the current discount rate for a Nexus 4) or more. I definitely recommend the Ringke case for a Nexus 4.

12 August 2013

Sylvain Le Gall: Migrating a puppet maintained computer from Squeeze to Wheezy

This blog post is a little recipe to do a Debian migration for a node using Puppet and some other good practices. We do all the following commands as root, which on of the exceptional situation where you should have a real root session (login through console, or su -). I tend to avoid using the X server while doing an upgrade, so my 'best' setup is to have a laptop to take note and check things on the internet and a session to the computer to upgrade (ssh + su - or login as root into console). In both case, I use screen during the upgrade so that I can handle disconnection. Create or update your admin-syscheck script First of all, a good practice is to have a script that runs various test on the system that checks everything is ok. This is not only for upgrade but in general. But in the case of upgrade, it can be particularly useful. I call this script admin-syscheck. This is a simple bash script. This script check various aspect of the system and serve me as my external worker to check the most advanced knowledge I have gathered about setting up a service. For example, I know that having *.bak or *.dpkg-dist in /etc/ means that something needs to be merged and a file should be deleted. Another example is about setting up the right alias for 127.0.0.1 and ::1 (which you can differentiate using getent ahostsv4 and getent ahostsv6). I have packaged this script and distributed it using a specific apt-get repository. You can just distribute it using puppet. I recommend to run it daily to track changes (e.g. after an apt-get dist-upgrade) and to check that my setup is aligned with my most up-to-date knowledge about setting up a service (i.e. this is my external worker). In our case we are interested in checking presence of old and new configuration files, before and after upgrading. Here is this specific section of my script:
if ! $IS_ROOT; then
  warning "Not trying to detect dpkg leftover file in /etc/."
else
  LEFTOVER_FILES=( $(find /etc/ \
      -name "*.dpkg-dist" -o \
      -name "*.dpkg-old" -o \
      -name "*.ucf-old" -o \
      -name "*.ucf-dist" -o \
      -name "*.bak") )
  for i in "$ LEFTOVER_FILES[@] "; do
    if [ "$i" = "/etc/hosts.deny.purge.bak" ]; then
      continue
    fi
    if $fix; then
      BASE=$ i%.* 
      cond_exec vim -d $BASE $i
      read -p "Delete $i (y/N)? " ans
      if [ "$ans" = "y" ]; then
        cond_exec rm $i
      fi
    else
       report_error "dpkg leftover file: '$i'."
    fi
  done
fi
(cond_exec allows to do a dry run, you can just remove it). Setting $fix to true will spawn a vim -d old new command where you can edit and then delete the leftover file. This is extremly handy. Upgrading to Wheezy I strongly recommend to read first the upgrade chapter of the release notes. This gives you a more complete overview of the upgrade procedure. I just go through the basic step here. 1. Update everything on the system:
$> apt-get update 
$> apt-get dist-upgrade
2. Check that the current configuration apply cleanly:
$> puppet agent --test
3. Run admin-syscheck:
$> admin-syscheck
And fix all the problems. 4. Disable puppet: I use a cronjob to run puppet, so I just comment the line for the job (/etc/cron.d/puppet-custom). You should disable puppet by stopping the daemon and preventing it to run by editing /etc/default/puppet and set START=no. 4. Fix your sources and pinning: Change squeeze to wheezy in /etc/apt/sources.list and remove useless files in /etc/apt/sources.lists.d/. (You may keep certain sources that refers to stable, like google-chrome.list).
$> rm /etc/apt/sources.list.d/* # Check if this ok to do this with your system.
Although, I tend to fully purge /etc/apt/sources.list expect for the main line (removing backports and security is fine for a short time). The first run of puppet after upgrade will anyway reset this file.
$> rm /etc/apt/preferences.d/* # (at least the ones that do pin some version)
You can although remove all pinning from /etc/apt/preferences. 5. Now you start the real upgrade:
$> apt-get update 
$> apt-get dist-upgrade
6. During the upgrade you will be asked if you want to keep old configuration files or install the newer one from the maintainer. I have always wondered what to answer to this. But here is the answer after a few major upgrade: always install configuration files from maintainer if the service has no ultra-specific settings that could break during the upgrade. The only file, that I should not upgrade on my system, is /etc/sudoers. In this very specific case, you need to make sure before the upgrade that the old and new configuration can coexist. In the squeeze to wheezy case, I have just setup a few extra augeas rules to set the secure_path before the upgrade and it was fine. This is typically the kind of situation where you are thankful to have a real root session. 7. The upgrade can be long and require various fixing to remove/re-add packages to circumvent problems. At the end you will have a set of file *.dpkg-old and *.ucf-old (and some *.dpkg-dist and *.ucf-dist). The *-old files are your old version of the file, while the corresponding files match the maintainer version of it. The *-dist files are the maintainer version of the file and the corresponding files match your old version of it. Starting from here you have 2 options: First upgrade This is the tricky part, you'll have to spend a little time on it: 1. Go over all *. ucf,dpkg - old,dist and merge them with the corresponding configuration file. Use admin-syscheck with fix=true 2. Make a copy of your /etc directory into /etc.new:
$> cp -rp /etc /etc.new
3. Run puppet again:
$> puppet agent --test
4. Disable again the automatic run of puppet, if the previous command has re-enabled it. 5. Make a diff between /etc and /etc.new. Since you have a run of puppet, you know what has changed and should not have changed.
$> diff -Nurd /etc.new /etc
Everytime you find some files that doesn't match your expectation for the upgrade with puppet, change the corresponding puppet manifest to have what you expect. For example, if this is a file:
if ($lsbdistcodename == 'wheezy')  
  file  
    "/etc/foo":
        source => "puppet:///files/foo.wheezy"
    
  else  
  file  
    "/etc/foo":
        source => "puppet:///files/foo.squeeze"
    
 
People working with augeas and puppet, will appreciate the fact that they probably have 0 changes to make for this to work (since it only does a few replacement in configuration files). 6. Once you are happy with the changes, copy back /etc.new to /etc and go to step 3 until the difference is almost 0. 7. Re-enable automatic run of puppet. Do this procedure for a least each computer category you have (e.g. Desktop and Server nodes). Once you are fully confident your new puppet setup works, you will be able to use 'further upgrade' for the other nodes. Further upgrade. This one is super easy compare to a first upgrade: 1. Re-enable puppet and have it run at least once:
$> puppet agent --test
2. Merge *. dpkg,ucf - dist,old with corresponding files (you can run admin-syscheck with fix=true). This is mostly a sanity check since you should have already solved most problem with the 'first upgrade' procedure. That's it. Enjoy your upgrade to Wheezy with puppet.

Richard Hartmann: DebConf13 I

DebConf! The venue here at Le Camp is pretty much perfect. Short walking distances, organic layout of the buildings, and a stunning view of the lake. I would be hard pressed to think of other venues which could be as nice... After arriving Fri/Sat night at 0330, Saturday was spent setting up the Access points: Me prior to pull-ups on the roof beams Access Point in pillow cases This little green valve caused a power outage in the server room, messing with servers, and resetting several switches to old configs. Xtaran had a lot of fun as a result of this. The valve of evil. And water. The ikiwiki BoF on sunday was rather interesting. I will try to publish some notes from this BoF and the other Git-related ones towards the end of the week. The Gitify ALL the things BoF managed to fill the room from "full-ish" over "good thing we don't need the beamer and can use the space in front of the whitescreen" over "out of chairs" over "the chairs from other rooms won't fit any more" to the final state of "people stand around near the walls and in the doors". At a total of 54 people, turnout has been... unexpectedly high.. The BoF started at 1130 and usually, slots are 45 minutes long. We extended our BoF into lunch time (I chose the slot just prior to lunch for precisely that reason) and finally finished at around 1245, i.e. 30 minutes late. After a quick show of hands on if there's interest in another BoF, I applied for and got the next slot, tomorrow at 11:30, once again in BoF room 1 and just before lunch. It's called Gitify EVEN MORE of the things and will expand on use cases and best practices. At a guess, we will focus on managing configurations and photos in default and complex situations. Sadly, neither of those BoF are taped. Afterwards, I had a chance to sit down with Lucas Nussbaum to talk over some points regarding the Debian Trademark Team. Finally, during Why Debian should (or should not) make systemd the default (it probably should not, but that's a different story), my kernel panicked. 3.9 and 3.10 have been less than ideal on my new X1 Carbon, but this was the first panic. I was not even done cussing and Ben Hutchings suddenly appeared on my side, telling me that yes, this particular module (mei) has been causing issues recently. Kernel panic As a closing note, I am really enjoying my first DebConf. Great venue, great people, great content, winebeer and cheese party tonight, and I found out that we have a fire place and fire wood...

11 August 2013

Lisandro Dami&aacute;n Nicanor P&eacute;rez Meyer: Qt in Debian: using Qt4 and/or Qt5 in your packages

Hi everyone! We now have both Qt4 and Qt5 in the archive. Those using Qt4 should not need to make any changes in their packages, although you can be extra-safe with a few steps. Don't rush, just read below.
Some backgroundSune took the time some months ago to consult upstream for a sane way to allow both SDKs to coexist without us distros having to reinvent the wheel choosing which tools have to be in use in each case.

After a long discussion, upstream decided to write qtchooser (already in the archive) to be able to select between Qt4, Qt5 and even special user's cases like cross-platform builds.

So instead of going trough Debian's alternatives as we did with Qt3/Qt4, we will make use of this new tool.
My package uses Qt, how should I proceed?There are many ways of choosing either of the versions of Qt:

- Using any qtchooser method (preferred):

* Exporting QT_SELECT with 4, qt4, 5 or qt5 as a value in debian/rules.
* Call the tool using the '-qtx' parameter, where x can be replaced with any of the options above.

- Build-depending on qt4-default or qt5-default. You can't B-D on both of them, as they can't coexist.

It is good to notice that:

- any qtchooser method will take precedence over build depending on qtX-default.
- If you export XDG_CONFIG_DIRS it will ignore the default paths to qtchooser's configs we setted up in the packages.

We have also provided qt4-[arch-triplet] and qt5-[arch-triplet] options for special cases.

Once again, if you are already using Qt4, there is no need to rush. See below.

Can is use both Qt4 and Qt5 in my package?You can't mix Qt4 and Qt5 in the same binary, but you may provide libraries compiled against one or the other. For example, your source package foo could provide both libqt4foo1 and libqt5foo1. You need to mangle your debian/rules and/or build system accordingly to achieve this. At the time of this writing I don't know of any examples yet.

So are you going to break the archive with a big transition?No, we have done our best to avoid having to make any changes to existing Qt4 packages. Qt tools should default to Qt4 except if overriden by any method described above.

My package uses Qt4, can I leave it as it is?While there is no need to apply the changes in this case, explicitly setting the Qt version will surely not hurt at all. But don't rush ;-)

Gregor Herrmann: DebCamp 2013

[no pictures here, just a short report]. Today DebConf, this year's edition of the annual Debian developer conference, started with two inspiring talks about Debian proper, one by Lucas Nussbaum, the other by Joey Hess. This also means that yesterday DebCamp ended, the period preceeding DebConf and dedicated to working on Debian together with others. Here's a short report from my point of view: I arrived here on Tuesday, the first day of DebCamp. I immediately fell in love with the venue, & despite the early stage of setup, everything I needed was working fine for me from the very start. Like in previous years, I used the time to do work in the Debian Perl Group, especially taking advantage of the presence of other team members. That's the great thing about DebCamp & DebConf: collaborating in real-life & real-time, from quickly asking a question over sitting together to think about solutions for a problem to "just" chatting & thereby developping ideas for the future. In the previous days I I really enjoy my time here, & I'm especially happy to meet some people for the first time in meat space. This is only possible due to the generous support of the DebConf sponsors & the immense efforts of the DebConf team. Thank you!

Michal &#268;iha&#345;: Good morning DebConf

Yesterday evening I've arrived at DebConf 13. I was quite tired after traveling so I just had few beers and went to bed. The travel went quite well besides somebody else broke wine and my suitcase was all wet from it. Fortunately almost nothing got inside so I have some clean clothes for next week :-). As I went to bed quite early, I woke up early as well so I went to short walk to see what is nearby: Sunrise at Lake Neuch tel Castle Vaumarcus Castle Vaumarcus

Filed under: English Debian Photography 0 comments Flattr this!

Next.

Previous.