Search Results: "reg"

13 October 2013

Francesca Ciceri: MissRepresentation: discussing gender stereotypes in Moldova

Recently, I've been attending a training course in Moldova about the representation of gender in the media and the influence on society of gender stereotypes.
The course was organized by Inesa Lupu, of Invento and financed by the UE as part of the Youth in Action program. It was the first time, for me, in this kind of international project and it was, in a word, fantastic.
Among the participants, there were people from Azerbaijan, Georgia, Italy, Latvia, Moldova and Slovenia.
That meant a great mix of cultures, languages and experiences.
And that was the key, in my opinion, of the success: coming from different countries and different social and cultural contexts meant that we were able to have a very broad and diverse point of view on the problem of gender stereotypes. So, here's some highlights on what we discussed. The media representation of gender (aka: gender issues are not only women issues) Tough Guise by Jackson Katz is a interesting documentary about the way the modern society - particularly in the US - defines masculinity as intrinsically tied to violence, aggressivity and "toughness" and on the consequences of this on the society as a whole. The author's theory is "that male violence, misogyny, and homophobia are inextricably linked to how we define manhood as a culture. The film gives special attention to how American media have glamorized increasingly regressive and violence masculine ideals in the face of mounting social and economic threats to traditional white male heterosexual authority". It then results clear that we cannot avoid to think about gender issues as women and men issues, because after all is the cultural definition of both femininity and masculinity that heavily influences the behaviour of men and women and their interaction.
In particular, I liked Katz's analysis of media's use of victim blaming speech while reporting of violences against women which tend to shift the focus from the violence perpetrated by men as part of definition of masculinity. Another documentary we watched, more focused on women representation, is MissRepresentation by Jennifer Siebel Newsom.
The film analyses the under representation of women in position of power, and the issue of women and leadership, especially in politics, in the US. Nothing too new, if you are interested in gender issues, as it is a widely discussed and studied topic, but still worth watching. After watching them, we formed little groups of three-four persons from different countries to discuss them, and it was even more interesting to listen the opinion of the guys (we had four male participants). The guys talking about Tough Guise Photography and Phototherapy As a workshop on media representation of gender, photography and advertisement were two of the main argument we spoke about. We focused on it for two days: our trainer, Lietta Granato - photographer and phototherapist - first gave us a lesson on photography, making us experimenting a bit with exposure times and diaphragm's aperture. a lesson on photography Then she presented the evolution in the last 50 year or so, of the depiction of women in the ads.
And that, to be honest, was a bit upsetting.
I've already had seen one of the most important and widely known films on this theme, the Killing Us Softly series by Jean Kilbourne, but some of the ads Lietta showed to us were really really horrible. Actually, most of them were horrible. Commenting and deconstructing these ads would take a separate blogpost, probably, and there are many people more competent than me on the topic, so I've decided to simply share some of the worst ads in a collage, without much commenting. These are vintage, from the fifties to the seventies. a collage of vintage sexist ads Do you think we got better? Pff. a collage of recent sexist ads They go from promoting violence and rape to heavily objectifying women. Special mention for the Compaq ad: as a geek woman I feel particularly insulted by the idea that I'm supposed to use a "pocket pc" as "pocket mirror". Because I wouldn't be able, obviously, to use it as a computer. Lietta also introduced us to photographic therapy and particularly the work of Jo Spence and Rosy Martin. If you browse Jo Spence's site, please be aware that there is a series of pics documenting all the stages of her illness (she died of breast cancer) and they are pretty intense. "In 1984, alongside Rosy Martin, Spence developed Photo-Therapy , adopting techniques from co-counselling. The considerable achievement of Photo-Therapy was to invert the traditional relationship between the photographer and the subject. If historically the subject had little control over their own representation, Photo-Therapy shifts this dynamic. The subject was able to act out personal narratives and claim agency for their own biography." (source: http://www.jospence.org/biography.html)
I love this concept and I really really love Spence's photos. To close on a happier note, I really suggest you to allocate 20 minutes of your time to watch this great talk by Nigerian novelist Chimamanda Ngozi Adichie, about the role of "single story" in shaping stereotypes and misunderstandings.

12 October 2013

Michael Vogt: apt 0.9.12

The recently released apt 0.9.12 contains a bunch of good stuff, bugfixes and cleanups. But there are two new feature I particularly like. The first is the new parameter with-new-pkgs for the upgrade
command:
# apt-get upgrade --with-new-pkgs
that will install new dependencies on the upgrade but never remove
packages. A typical use-case is a stable system that gets a kernel
with a new kernel ABI package. The second is show-progress for
install/remove/upgrade/dist-upgrade which will show inline progress
when dpkg is running to indicate the global progress.
# apt-get install --show-progress tea
...
Selecting previously unselected package tea-data.
(Reading database ... 380116 files and directories currently installed.)
Unpacking tea-data (from .../tea-data_33.1.0-1_all.deb) ...
Progress: [ 10%]
Progress: [ 20%]
Progress: [ 30%]
Selecting previously unselected package tea.
Unpacking tea (from .../tea_33.1.0-1_amd64.deb) ...
Progress: [ 40%]
Progress: [ 50%]
Progress: [ 60%]
Processing triggers for doc-base ...
Processing 2 added doc-base files...
Registering documents with scrollkeeper...
...
Processing triggers for man-db ...
Setting up tea-data (33.1.0-1) ...
Progress: [ 70%]
Progress: [ 80%]
Setting up tea (33.1.0-1) ...
Progress: [ 90%]
Progress: [100%]
For the install progress, there is also a new experimental option
Dpkg::Progress-Fancy . It will display a persistent progress status bar in the last terminal line. This works like this:
# apt-get -o Dpkg::Progress-Fancy=true install tea
apt-install-fancy-progress This kind of information is obviously most useful on complex operations like big installs or (release) upgrades.

11 October 2013

Michal Čihař: Hackweek is over

10th hackweek is over and I think it has been again great chance to hack on something. This year we even had better food supplies so interruptions from hacking were even less frequent. As you've might have already noticed, I was working on Weblate whole week and I think it worked pretty well and I've implemented all what I wanted. First of all, Weblate now supports login using lot of third party services (like GitHub, Facebook, Google, ...). This was achieved by using python-social-auth for that. It is quite new module for this, so hopefully it's API will stay stable enough to be usable in the long term. It was surprisingly easy to implement, though I've spent quite a lot of tweaking of the login and registration process to make it work according to my expectations. After doing this quite big change, I thought it's about time to restructure the documentation and document new features in it. I think it now covers all important things, but if you can't find something or some parts are hard to understand, just let me know, I'll fix it. Another quite big feature (though it won't be much visible in upcoming 1.8 release) is source string tracking. This is prerequisite for many features people have requested in Weblate's issue tracker, but these will have to wait for next releases. If you want to see some feature earlier, you can support it by money on Bountysource :-). Weblate can now also search in all strings, which might become handy if grepping over dozen of Git repositories is not your favorite game. And last but not least, I've implemented simple Captcha protection for new registrations as the demo server is full of bots who register there and do nothing afterward. Basically I think this makes Weblate 1.8 feature complete and I'd like to stabilize it in upcoming weeks to release. Right now it is deployed on the demo server, where you can play with it and discover bugs :-). Also it's now time to work on Weblate translations!

Filed under: English SUSE Weblate 0 comments Flattr this!

Petter Reinholdtsen: Oslo community mesh network - with NUUG and Hackeriet at Hausmania

Wireless mesh networks are self organising and self healing networks that can be used to connect computers across small and large areas, depending on the radio technology used. Normal wifi equipment can be used to create home made radio networks, and there are several successful examples like Freifunk and Athens Wireless Metropolitan Network (see wikipedia for a large list) around the globe. To give you an idea how it work, check out the nice overview of the Kiel Freifunk community which can be seen from their dynamically updated node graph and map, where one can see how the mesh nodes automatically handle routing and recover from nodes disappearing. There is also a small community mesh network group in Oslo, Norway, and that is the main topic of this blog post. I've wanted to check out mesh networks for a while now, and hoped to do it as part of my involvement with the NUUG member organisation community, and my recent involvement in the Freedombox project finally lead me to give mesh networks some priority, as I suspect a Freedombox should use mesh networks to connect neighbours and family when possible, given that most communication between people are between those nearby (as shown for example by research on Facebook communication patterns). It also allow people to communicate without any central hub to tap into for those that want to listen in on the private communication of citizens, which have become more and more important over the years. So far I have only been able to find one group of people in Oslo working on community mesh networks, over at the hack space Hackeriet at Husmania. They seem to have started with some Freifunk based effort using OLSR, called the Oslo Freifunk project, but that effort is now dead and the people behind it have moved on to a batman-adv based system called meshfx. Unfortunately the wiki site for the Oslo Freifunk project is no longer possible to update to reflect this fact, so the old project page can't be updated to point to the new project. A while back, the people at Hackeriet invited people from the Freifunk community to Oslo to talk about mesh networks. I came across this video where Hans J rgen Lysglimt interview the speakers about this talk (from youtube): I mentioned OLSR and batman-adv, which are mesh routing protocols. There are heaps of different protocols, and I am still struggling to figure out which one would be "best" for some definitions of best, but given that the community mesh group in Oslo is so small, I believe it is best to hook up with the existing one instead of trying to create a completely different setup, and thus I have decided to focus on batman-adv for now. It sure help me to know that the very cool Serval project in Australia is using batman-adv as their meshing technology when it create a self organizing and self healing telephony system for disaster areas and less industrialized communities. Check out this cool video presenting that project (from youtube): According to the wikipedia page on Wireless mesh network there are around 70 competing schemes for routing packets across mesh networks, and OLSR, B.A.T.M.A.N. and B.A.T.M.A.N. advanced are protocols used by several free software based community mesh networks. The batman-adv protocol is a bit special, as it provide layer 2 (as in ethernet ) routing, allowing ipv4 and ipv6 to work on the same network. One way to think about it is that it provide a mesh based vlan you can bridge to or handle like any other vlan connected to your computer. The required drivers are already in the Linux kernel at least since Debian Wheezy, and it is fairly easy to set up. A good introduction is available from the Open Mesh project. These are the key settings needed to join the Oslo meshfx network:
SettingValue
Protocol / kernel modulebatman-adv
ESSIDmeshfx@hackeriet
Channel / Frequency11 / 2462
Cell ID02:BA:00:00:00:01
The reason for setting ad-hoc wifi Cell ID is to work around bugs in firmware used in wifi card and wifi drivers. (See a nice post from VillageTelco about "Information about cell-id splitting, stuck beacons, and failed IBSS merges! for details.) When these settings are activated and you have some other mesh node nearby, your computer will be connected to the mesh network and can communicate with any mesh node that is connected to any of the nodes in your network of nodes. :) My initial plan was to reuse my old Linksys WRT54GL as a mesh node, but that seem to be very hard, as I have not been able to locate a firmware supporting batman-adv. If anyone know how to use that old wifi access point with batman-adv these days, please let me know. If you find this project interesting and want to join, please join us on IRC, either channel #oslohackerspace or #nuug on irc.freenode.net. While investigating mesh networks in Oslo, I came across an old research paper from the university of Stavanger and Telenor Research and Innovation called The reliability of wireless backhaul mesh networks and elsewhere learned that Telenor have been experimenting with mesh networks at Gr nerl kka in Oslo. So mesh networks are also interesting for commercial companies, even though Telenor discovered that it was hard to figure out a good business plan for mesh networking and as far as I know have closed down the experiment. Perhaps Telenor or others would be interested in a cooperation? Update 2013-10-12: I was just told by the Serval project developers that they no longer use batman-adv (but are compatible with it), but their own crypto based mesh system.

8 October 2013

Daniel Kahn Gillmor: Unaccountable surveillance is wrong

As I mentioned earlier, the information in the documents released by Edward Snowden show a clear pattern of corporate and government abuse of the information networks that are now deeply intertwined with the lives of many people all over the world. Surveillance is a power dynamic where the party doing the spying has power over the party being surveilled. The surveillance state that results when one party has "Global Cryptologic Dominance" is a seriously bad outcome. The old saw goes "power corrupts, and absolute power corrupts absolutely". In this case, the stated goal of my government appears to be absolute power in this domain, with no constraint on the inevitable corruption. If you are a supporter of any sort of a just social contract (e.g. International Principles on the Application of Human Rights to Communications Surveillance), the situation should be deeply disturbing. One of the major sub-threads in this discussion is how the NSA and their allies have actively tampered with and weakened the cryptographic infrastructure that everyone relies on for authenticated and confidential communications on the 'net. This kind of malicious work puts everyone's communication at risk, not only those people who the NSA counts among their "targets" (and the NSA's "target" selection methods are themselves fraught with serious problems). The US government is supposed to take pride in the checks and balances that keep absolute power out of any one particular branch. One of the latest attempts to simulate "checks and balances" was the President's creation of a "Review Group" to oversee the current malefactors. The review group then asked for public comment. A group of technologists (including myself) submitted a comment demanding that the review group provide concrete technical details to independent technologists. Without knowing the specifics of how the various surveillance mechanisms operate, the public in general can't make informed assessments about what they should consider to be personally safe. And lack of detailed technical knowledge also makes it much harder to mount an effective political or legal opposition to the global surveillance state (e.g. consider the terrible Clapper v. Amnesty International decision, where plaintiffs were denied standing to sue the Director of National Intelligence because they could not demonstrate that they were being surveilled). It's also worth noting that the advocates for global surveillance do not themselves want to be surveilled, and that (for example) the NSA has tried to obscure as much of their operations as possible, by over-classifying documents, and making spurious claims of "national security". This is where the surveillance power dynamic is most baldly in play, and many parts of the US government intelligence and military apparatus has a long history of acting in bad faith to obscure its activities. The people who have been operating these surveillance systems should be ashamed of their work, and those who have been overseeing the operation of these systems should be ashamed of themselves. We need to better understand the scope of the damage done to our global infrastructure so we can repair it if we have any hope of avoiding a complete surveillance state in the future. Getting the technical details of these compromises in the hands of the public is one step on the path toward a healthier society. PostscriptLest I be accused of optimism, let me make clear that fixing the technical harms is necessary, but not sufficient; even if our technical infrastructure had not been deliberately damaged, or if we manage to repair it and stop people from damaging it again, far too many people still regularly accept ubiquitous private (corporate) surveillance. Private surveillance organizations (like Facebook and Google) are too often in a position where their business interests are at odds with their users' interests, and powerful adversaries can use a surveillance organization as a lever against weaker parties. But helping people to improve their own data sovereignty and to avoid subjecting their friends and allies to private surveillance is a discussion for a separate post, i think.Tags: cryptography, nsa

Russ Allbery: krb5-strength 2.0

This is a rather huge release of my password strength checking package for Heimdal and MIT Kerberos KDCs, incorporating quite a bit of new work as well as some substantial restructuring. The largest change is that MIT Kerberos is now fully supported, not just with provided patches, thanks to work by Greg Hudson and MIT. The package can now build plugins for either MIT or Heimdal, as well as an external password quality program for Heimdal (the preferred method for that implementation). Alongside that change, the plugin installation path has changed to fit the layout of MIT plugins (as well as I understand it). This version also now supports password dictionaries other than CrackLib. You can generate a CDB dictionary from a wordlist using a utility included in the package and use it instead of or as a supplement to CrackLib. This dictionary lookup uses a much simpler set of permutations (the password as given plus removing some leading and trailing characters), providing a simpler approach suitable for much larger dictionaries. (CrackLib does a lot of transformations before dictionary lookup that are dubious, such as ignoring case and punctuation.) Also in this release are new configuration options to control additional checks: minimum password length (independent of whatever length CrackLib requires), requiring at least one non-alphabetic character, and rejecting non-ASCII or non-printable characters. The latter isn't to make the password stronger, but to prevent user frustration since those characters often can't be reliably entered in different situations and can result in an unreproducible password, particularly since Kerberos doesn't define a password normalization. In support of these changes, and to make testing easier, the plugin can be configured without a dictionary of any kind, or with any combination of CDB and CrackLib dictionaries. The checks for passwords based on principals are now more comprehensive, checking not only the local part but also each component of the principal with leading or trailing digits. Since many sites put their institution name in the Kerberos realm, this will also check for passwords based on the institution name. There are also some fixes to the internal CrackLib implementation, in case it is used instead of the system CrackLib, to better handle long passwords by scaling the test for simplistic passwords. You can get the latest release from the krb5-strength distribution page.

7 October 2013

Gregor Herrmann: using lintian profiles for fun & profit

since lintian gained support for vendor profiles, or at least since it has a nice documentation about writing checks & even a tutorial (the latter only local/in the package), I thought about writing some checks in a specific 'pkg-perl' profile. after talking to niels at debconf13, I tried in late august, & realized that at least simple checks are fun to write & really not difficult; luckily niels also reviewed my first attempts. & axel soon joined the fun & added some more checks. so here we are: the new pkg-perl-tools package also ships a lintian vendor profile 'pkg-perl' with a couple of simple but still useful checks that help to enforce our group policy. if you want to use them, install the package and check /usr/share/doc/pkg-perl-tools/README.lintian, if you want to look at the checks, you can also clone the git repo or inspect it in gitweb (directory lintian).

Michal Čihař: Weblate 1.7

Weblate 1.7 has been released today. It comes with lot of improvements, especially in translation speed and many new features. Full list of changes for 1.7: You can find more information about Weblate on it's website, the code is hosted on Github. If you are curious how it looks, you can try it out on demo server. You can login there with demo account using demo password or register your own user. Ready to run appliances will be soon available in SUSE Studio Gallery. Weblate is also being used https://l10n.cihar.com/ as official translating service for phpMyAdmin, Gammu, Weblate itself and others. If you are free software project which would like to use Weblate, I'm happy to help you with set up or even host Weblate for you. Further development of Weblate would not be possible without people providing donations, thanks to everybody who have helped so far!

Filed under: English SUSE Weblate 1 comments Flattr this!

6 October 2013

Gregor Herrmann: RC bugs 2013/37-40

not much activity around RC bugs on my side in the last weeks; & the ones I worked on were all in the Debian Perl Group: on an unrelated note: following the discussion on debian-project, I finally revoked my old opengpg key 0x00F3CFE4 which served me well from 1998 until 2009. since then, I've only been using 0x8649AA06 anyway ...

5 October 2013

Vincent Sanders: If I have a style, I am not aware of it.

I wish I had known about that quote from Michael Graves before now. I would have perhaps had an answer to some recent visitors to makespace.

There are regular scheduled visits to makespace where people can come and view our facilities, and perhaps start the process of becoming a member if they decide they like what they see.

Varnishing a folding chair using a stool as a stand
However, we sometimes get people who just turn up at the door. If a member feels charitable they may choose to give a short tour rather than just turn the person away. I happened to be in one Friday afternoon recently varnishing a folding chair when two such people rang the doorbell. There were few other members about and because watching varnish dry was dull I decided to be helpful and do a quick tour.

I explained that they really ought to return for a scheduled event for a proper tour, gave the obligatory minimal safety briefing, and showed them the workshops and tools. During the tour it was mentioned they were attending a certain local higher education establishment and were interested in makespace as an inexpensive studio.

Before they left I was asked what I was working on. I explained that I had been creating stools and chairs from plywood. At this point the conversation took a somewhat surreal turn, one of them asked, well more demanded, who my principle influence had been in designing with plywood.

When I said that I had mainly worked from a couple of Google image searches they were aghast and became quite belligerent. They both insisted I must have done proper research and my work was obviously influenced by Charles and Ray Eames and Arne Jacobsen and surely I intended to cite my influences in my design documents.

My admission that I had never even heard the names before and had no design documents seemed to lead to a distinctly condescending tone as they explained that all modern plywood design stemmed from a small number of early 20th century designers and any competent designers research would have revealed that.

At this point in proceedings I was becoming a bit put out that my good deed of showing off the workshop had not gone unpunished. I politely explained that I designed simply by generating a requirement in my head, maybe an internet search to see what others had done, measuring real things to get dimensions and then a great deal of trial and error.

I was then abruptly informed that my "design process was completely invalid and there were well established ways to design furniture correctly and therefore my entire design was invalid" and that I was wasting time and material. I thanked them for their opinion and showed them out, safe and well before anyone gets any ideas.

I put the whole incident out of my mind until I finished writing up the final folding chair post the other day. It struck me that perhaps I had been unknowingly influenced by these designers. It was certainly true I had generated ideas from the hundreds of images my searches had revealed.

I did some research and it turns out that from the 1930s to the 1950s there were a string of designers using plywood in novel ways from the butterfly stool by Sori Yanagi through formed curvy chairs by Alvar Aalto and eero saarinen.

While these designers produced some wonderfully iconic and contemporary furniture I think that after reviewing my initial notes that two more modern designers Christian Desile and Leo Salom probably influenced me more directly. Though I did not reference their designs beyond seeing the images along with hundreds of others, certainly nothing was directly copied.

And there in lies an often repeated observation: no one creates anything without being influenced by their environment. The entire creative process of several billion ape descendants (or Golgafrincham telephone sanitisers if you prefer) is based on the simple process of copying, combining and transforming what is around us.

Isaac Newton by Sir Godfrey Kneller [Public domain], via Wikimedia Commons
I must accept that certain individuals at points in history have introduced radical improvements in their field, people like Socrates Galileo Leonardo Newton Einstein. However, even these outstanding examples were enlightened enough to acknowledge those that came before. Newtons quotation "If I have seen further it is by standing on the shoulders of giants" pretty much sums it up.

In my case I am privileged enough to live in a time where my environment has grown to the size of the world thanks to the internet. My influences, and therefore what I create, is that much richer but at the same time it means that my influence on others is similarly diminished.

I have joined the maker community because I want to create. The act of creation teaches me new skills in a physical, practical way and additionally I get to exercise my mind using new techniques or sometimes things I had forgotten I already knew. I view this as an extension of my previous Open Source software work, adding a physical component to a previously purely mental pursuit.

But importantly I like that my creations might provide inspiration for someone else. To improve those chances in the wider world I force myself to follow a few basic rules:
Release
Possibly one of the hardest things for any project. I carefully avoided the word finish here because my experience leads me to the conclusion that I always want to improve my designs.

But it is important to get to a point in a project where you can say "that is good enough to share", this is more common in software but it really applies to any project.

Share
If your aim here is to improve your society with your contribution sharing your designs and information is important. I think there is nothing better than someone else taking one of your designs and using it and perhaps improving on it, remember that is what you probably did in one way or another better to make it less hard for that to happen.

Ensure your design files are appropriately licensed and they are readily accessible. I personally lean towards the more generally accessible open source licences like MIT but the decision is ultimately yours.

Licencing is important, especially in the current copyright happy society. I know it sounds dull and no one takes that seriously, right? Sorry, but yes they do and it is better for you to be clear from the start, especially if there is a software component to your project. Oh one personal plea, use an existing well known licence, the world simply does not need another one!

Write about it
The blog posts about the things I have made sometimes take almost as much time as the creation. The clear recording on my thoughts in written and photographic form often gives me more inspiration for improvements or other projects.

If someone else gets pleasure from the telling then that can only be good. If you do not do this then your voice cannot be heard and you wasted an opportunity to motivate others.

Feedback
If you do manage to get feedback on your creation, read it. You may disagree or not be interested for the current project but the feedback process is important. In software this often manifests as bug reports, in more physical projects this often becomes forum or blog comments.

Just remember that you need a thick skin for this, the most vocal members of any society are the minority with inflammatory opinion, the silent majority are by definition absent but there is still useful feedback out there.

Create again
By this I simply mean that once you are satisfied yourself on a project move on to the next. This may sound a little obvious but once you have some creative momentum it is much easier to keep going project to project than in you leave time between.

Also do not have too many projects ongoing, by all means have a couple so you do not get stuck waiting for materials or workshop time but more than three and four and you will never be able to release any of them.
Those students were perhaps somewhat misguided in how they stated their opinions, but they are correct that in the world in which we find ourselves we are all influenced. Though contrary to received wisdom those influences are more likely to be from the internet and our peers in the global maker society than historical artists.

3 October 2013

Joachim Breitner: Experimenting with the TI eZ430 Chronos

For a while I have been eyeing with the TI eZ430 Chronos watch, a slightly bulky sports watch that not only comes with a built-in thermometer, barometer and accelerometer, but also a freely programmable micro controller (from the TI MSP430 family hence the name). In addition it has a small radio chip included and can communicate wirelessly with the computer, or possibly other devices. All in all, a very geeky toy. A week ago I managed to buy one quite cheaply via eBay (30 including shipping). It took me a while to get an overview of the various resources about the device. Here is what I have learned. After I found that out, I tried to hack a bit on the various software. The first issue I had (and still have) is that I cannot use the buttons of the device while it is attached to the debug board. They do work if forget to take out the battery, but supposedly that is bad for the battery. So my compile-upload-test-cycle becomes a compile-upload-detach-insert-battery-test-remove-battery-attach-cycle. I could not find out how to emulate button presses using mspdebug. Any suggestions are welcome. The other problem was the new altimeter hardware: Neither OpenChronos nor openchronos-ng support that yet. I originally planned to port the driver from the official software to a random OpenChronos fork when I read that Richard Rondu did that to openchronos-ng yet. I found the code in a month-old merge-request. I tried it, it worked, and I started to clean up the code a bit and add a variometer mode to it, e.g. displaying the current rate of climb my ultimate goal is to use this as a surprisingly cheap variometer for paragliding. After a day of hacking and quickly lifting the watch from the room floor to the room ceiling and back I believe that it works okish, although quite a few parameter can benefit from more tweaking: sample rate (currently 20Hz), length of history (currently 2s) and the linear regression method (currently simply the difference between the average of the samples of the current second with the samples of the last second). As always, patches welcome, the code is in my fork on sf.net.
Next to do would be to enable some buzzing noise depending on the rate of change; during flight I don t want to decipher a low-contract LCD screen. But it is questionable whether the buzzer is loud enough we ll see. I was also happy to hear that there are other zE430-hackers in Karlsruhe, one of them for example tries to make the alarm clock sleep-cycle-aware.

MJ Ray: The 2012 Update to the Worker Co-op Code

We like guidelines. In our work, things like the Debian Free Software Guidelines, pep8 and Koha Coding Guidelines are quite useful. I follow guidelines for how I work, too. In addition to the financial reports required by government, our co-op produces an annual social report which we share with our members and other key stakeholders. Since 2007, the backbone of it is The Worker Co operative Code of Governance published by our national federation. In 2012, the Worker Co-op Council updated the code. I don t remember why an update was felt necessary, but as a side-effect of producing of our 2013 social report, I ve made a list of the changes:
  1. Principle 1 is reordered, with information becoming the first point and membership offered to all becoming the last item.
  2. Principle 2 sees democratic processes drop down the order, plus it loses the item on long-term planning.
  3. Principle 3 has the point about reserves clarified and gains a last item about distributing surplus fairly.
  4. Principle 4 loses its first item about regular reviews, the skills assessment point moves to principle 5 and it gains a build capability point.
  5. Principle 5 gains items on replacing key members and skills assessment (from the previous section), while most points seem rephrased.
  6. Principle 6 is reordered, active co-operation is split into distinct points about referring and collaborating and the point about actively sharing good practice is deleted.
  7. Principle 7 is unchanged.
Are these good changes? Much of it seems like tinkering and maybe shifting emphasis the reorderings add little and make it harder to spot the changes while the lost points on long-term planning and sharing good practice are surprising. I would have preferred to see the items that seem mainly to promote the code itself and its publisher Co-operatives UK deleted instead. The additions and clarifications about surplus are good, though, and there s nothing new that I think should stop us adopting it. What do you think? Should all business behave this way?

2 October 2013

Joey Hess: insured

Here in the US, the Affordable Care Act is finally going into effect, with accompanying drama. I managed to get signed up today at healthcare.gov. After not having health insurance since 2000, I will finally be covered starting January 1 2014. Since my income is mosty publically known anyway, I thought it might be helpful to blog about some details. I was uninsured for 14 years due to a combination of three factors:

  1. Initially, youthful stupidity and/or a perfectly resonable cost/benefit analysis. (Take your pick.)
  2. Due to the US health insurance system being obviously broken, and my preference to avoid things that are broken. Especially when the breakage involved insurers refusing to cover me at any sane level due to a minor and easily controlled pre-existing condition.
  3. Since I'm not much motivated by income levels, and am very motivated to have time to work on things that are important to me, my income has been on average pretty low, and perhaps more importantly, I have intentionally avoided being a full-time employee of anyone at any point in the past 14 years (have rejected job offers), and so was not eligible for any employee plans which were the only reasonable way to be covered in the US. (See point #2.)
So, if you're stuck waiting in line on healthcare.gov (is this an entirely new online experience brought to us by the US government?), or have seen any of the dozen or so failure modes that I saw just trying to register for a login to the site, yeah, it's massively overloaded right now, and it's also quite broken on a number of technical levels. But you can eventually get though it. Based on some of the bugs I saw, it may help to have an large number of email addresses and use a different one for each application attempt. It also wouldn't hurt to write some programs to automate the attempts, because otherwise you may have to fill out the same form dozens of times. And no, you can't use "you+foo@bar.com" for your email; despite funding the development of RFC-822 in the 80's, the US government is clueless about what consititutes a valid email address. But my "favorite" misfeature of the site is that it refuses to let you enter any accented characters, or characters not in the latin alphabet when signing up. Even if they're, you know, part of your name. (Welcome back to Ellis Island..) I want to check the git repository to see if I can find the backstory for these and other interesting technical decisions, but they have forgotten to push anything to it for over 3 months. The good news is that once you get past the initial signup process, and assuming you get the confirmation mail before the really short expiration period of apparently less than 1 hour (another interesting technical choice, given things like greylisting), the actual exchange is not badly overloaded, and nor is it very buggy (comparatively). I was able to complete an application in about an hour. The irony is that after all that, I was only able to choose from one health insurer covering my area on the so-called "exchange". (Blue Cross/Blue Shield) I also signed up for dental insurance (it was a welcome surprise that the site offers this at all) and had a choice of two insurers for that. The application process was made more uncertian for me since I have no idea what I'll end up doing for money once my current crowdsourced year of work is done. The site wants you to know how much income you'll have in 2014, and my guess is anywhere between $6000 (from a rental property) and about what I made this year (approx $25000 before taxes). Or up, if I say, answered the Google pings. The best choice seemed to be to answer what I made this year, which is also close to what I made last year. So, I'll be paying around $200/month for a combination of not very good health insurance, and not very good dental insurance. There is around $750/year of financial aid to people at my guesstimated 2014 income level, which would drop that to $140/month, but I will let them refund me whatever that turns out to be in a lump sum later instead. For comparison, I am lucky to spend rather less renting a three bedroom house situated in 25 acres of woods.. It's strange to think that all of this is an improvement to the system here in the US, especially given all the better options that could have been passed instead, but it seems that it probably is. Especially when I consider the many people around me who are less fortunate than myself. If you'd like a broader perspective on this, see Tobias Buckell's "American healthcare was already socialized by Reagan, we re just fighting about how to pay for it".

Axel Beckert: How to make wget honour Content-Disposition headers

Download links often point to CGI scripts which actually generate (or just fetch, i.e. proxy) the actual file to be downloaded, e.g. URLs like http://www.example.com/download.cgi?file=foobar.txt. Most of such CGI scripts send the real file name in the Content-Disposition header as specified in the MIME Specification. All browsers I know (well, at least those I use regularily :-) handle that perfectly and propose the file name sent in the Content-Disposition header as file name for saving the downloaded name which is usually exactly what I want. All browsers do that, , just not my favourite commandline download tool GNU Wget Downloading the above URL with wget would look like this with default settings:
$ wget 'http://www.example.com/download.cgi?file=foobar.txt'
--2013-10-02 16:04:16--  http://www.example.com/download.cgi?file=foobar
Resolving www.example.com (www.example.com)... 93.184.216.119, 2606:2800:220:6d:26bf:1447:1097:aa7
Connecting to www.switch.ch (www.example.com) 2606:2800:220:6d:26bf:1447:1097:aa7 :80... connected.
HTTP request sent, awaiting response... 200 OK
Length: 2020 (2.0K) [text/plain]
Saving to:  download.cgi?file=foobar.txt'
100%[============================================>] 2,020       --.-K/s   in 0s
2013-10-02 16:04:24 (12.5 MB/s) -  download.cgi?file=foobar.txt' saved [2020/2020]
Meh! But luckily Wget can do that, it s just not enabled by default because it s an experimental and possibly buggy feature, at least according to the man page. Well, works for me! :-) You can easily enabled it by default for either your user or the whole system by placing the following line in your ~/.wgetrc or /etc/wgetrc:
content-disposition = on
Given the CGI script sends an appropriate Content-Disposition header, the above output now looks like this:
$ wget 'http://www.example.com/download.cgi?file=foobar.txt'
--2013-10-02 16:04:16--  http://www.example.com/download.cgi?file=foobar
Resolving www.example.com (www.example.com)... 93.184.216.119, 2606:2800:220:6d:26bf:1447:1097:aa7
Connecting to www.switch.ch (www.example.com) 2606:2800:220:6d:26bf:1447:1097:aa7 :80... connected.
HTTP request sent, awaiting response... 200 OK
Length: 2020 (2.0K) [text/plain]
Saving to:  foobar.txt'
100%[============================================>] 2,020       --.-K/s   in 0s
2013-10-02 16:04:24 (12.5 MB/s) -  foobar.txt' saved [2020/2020]
Now Wget does what I mean! You can also set this as flag on the commandline, but typing wget --content-disposition everytime is surely not what I want. ;-)

30 September 2013

Sylvain Le Gall: OUnit 2.0, official release

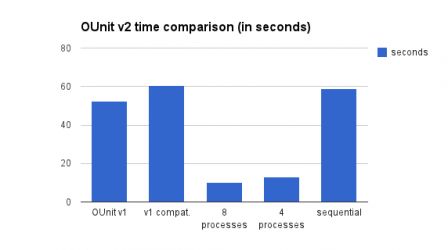
After 1.5 month of work, I am proud to officialy release OUnit 2.0.0. This is a major rewrite of OUnit to include various feature that I think was missing from OUnit1. The very good news is that the port of the OASIS test suite has proven that this new version of OUnit can drastically improve the running time of a test suite. OUnit is a unit test framework for OCaml. It allows one to easily create unit-tests for OCaml code. It is based on HUnit, a unit testing framework for Haskell. It is similar to JUnit, and other XUnit testing frameworks. Download OUnit v2.0.0 Documentation of v2.0.0 Website The basic features: Migration path OUnit 2.0.0 still provides the OUnit module which is exactly the same as the last OUnit 1.X version. This way, you are not forced to migrate. However, this means that you will gain no advantage of the new release and even some slowdown due to increase complexity of the code. Though, I strongly recommend to upgrade to OUnit2. Here is a checklist to do the migration: The OASIS test suite migration In order to check that everything was working correctly, I have migrated the OASIS test suite to OUnit2. This is a big test suite (210 test cases) and it includes quite big sequences of tests (end to end tests from calling oasis setup to compiling and installing the results). This was really time consuming and I wish to see a significant speedup for the tests with OUnit2. You can see the result in term of code of the full migration here. Here are the results on my Intel Core i7 920/SSD: OUnit v2 benchmark The migration was quite heavy because this test suite had a big design problem. It uses in-place modification of the test data. I think I pick this design because I thought this was a good idea to decrease the running time. As a matter of fact, this was a huge mistake, that keeps popping failed test cases because one of the previous tests was failing. I have refactored all this and now we start by copying the test data into a temporary directory, which ensure that everything is always starting from pristine test data. During the redesign, I have decided to reduce the number of tests by merging some of them. This should have no big impact on the running time, although this is not as pure 1:1 comparison with OUnit v1. Although it is still testing exactly the same thing. This explain the loss of ~50 tests, which in fact has been merged in other tests. The overall speedup is 4x compared to OUnit v1, when using processes. However there is a 12% increase compared to OUnit v1 for sequential and a 15% increase when using OUnit v1 compatibility layer. While this is not very good score, I hope this is small enough to compensate the huge win of being able to run tests in parallel with processes. And now the magic ! At this point, if you read carefully the numbers, you would have noticed that there is a 4.5x decrease in speed when you compare sequential and 4 processes for OUnit2. Since we are only actively testing in 4 shards, it looks strange. I don't expect a super-linear speedup due to the use of processes. I have checked that every tests was indeed running and found no solutions to this mystery. Right now, I think this is due to the fact that we are running less tests in more processes which should lighten the load of the GC (which may not trigger at all). I am not sure about this explanation and will welcome any bug report which shows a problem in the implementation of either sequential or processes runner. Although, this is great. Help still wanted If you find any bugs with OUnit v2, this is the time to submit a bug. OUnit BTS If you want to try to fix bugs by yourself, please checkout the latest version of OUnit:
 $> darcs get http://forge.ocamlcore.org/anonscm/darcs/ounit/ounit
Patches always welcome.

Russell Coker: Links September 2013

Matt Palmer wrote an insightful post about the use of the word professional [1]. It s one factor that makes me less inclined to be a member of professional societies. The TED blog has an interesting article about Wikihouse which is a project to create a set of free designs for houses to be cut out of plywood with a CNC milling machine [2]. The article also links to a TED talk by Alastair Parvin of the Wikihouse project which covers many interesting things other than designing houses. An XKCD comic has one of the best explanations of bullying I ve ever seen [3]. If you aren t familiar with XKCD then make sure you hover your mouse over it to read the hidden text. The Fair Phone is a project to develop a smart phone starting with conflict-free resources and with fully free software (not like a typical Android build) [4]. It s an interesting project and the price and specs seem within the normal range so you re not paying a huge premium for a conflict-free phone. Unfortunately they only have one model with a 4.3 display, if they had a competitor for the Galaxy Note then I d be interested. Patrick Stokes wrote an insightful article about why I m entitled to my opinion is a bogus argument [5]. Jim Daly wrote an interesting TED blog post interviewing Rishi Manchanda about Upstream Doctors who look for the root causes of medical problems rather than just treating the symptoms [6]. Brian Krebs wrote an insightful article about the value of a hacked email account [7]. If you are trying to convince your users to use better passwords then this should help. Ron Garrett wrote an insightful series or articles on morality hooked on the premise of whether it s wrong to torture kittens [8]. Part of his conclusion is that people who believe it s wrong to do such things tend to be more capable of working in large groups and forming a productive and efficient society. The TED blog has an interesting post by Karen Eng summarising Andreas Raptopoulos talk about using autonomous drones to deliver parcels in parts of the world that don t have usable roads [9]. Delivering parcels (which would start with medical supplies but would presumably move on to commercial transport) by drone is apparently really cheap. Being cheaper than building roads isn t going to be difficult but it seems that they are going to make it cheaper than paying people to deliver parcels even if the roads were built. The main web site about this project is www.matternet.us, they are hiring electrical engineers. Here is the link for Andreas TED talk [10]. The TOR blog has an interesting article by Emily Asher-Perrin comparing the different houses of Hogwarts [11]. It s an insightful article about personality attributes and gives more information than is available in the movies (I d read the books if I had time).

28 September 2013

Daniel Kahn Gillmor: RIP Cookiepuss

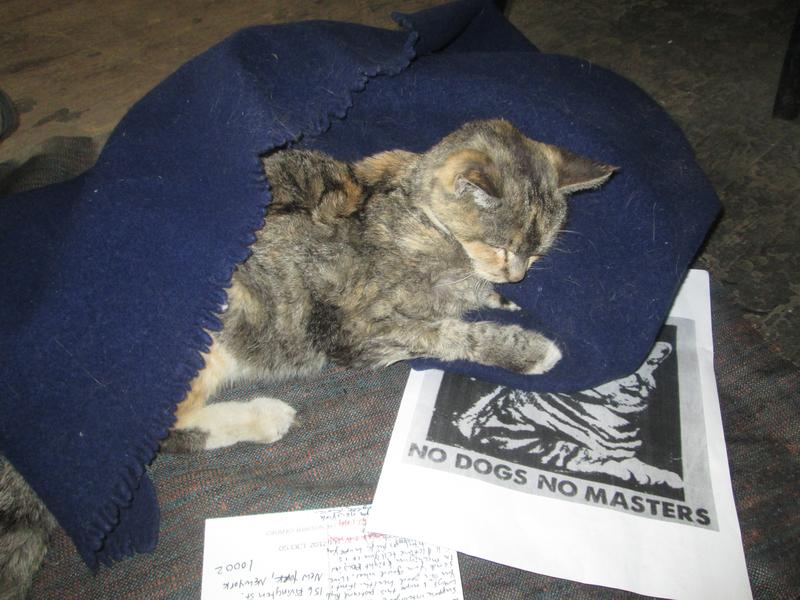
Yesterday, i said a sad goodbye to an old friend at ABC No Rio. Cookiepuss was a steadfast companion in my volunteer shifts at the No Rio computer center, a cranky yet gregarious presence. I met her soon after moving to New York, and have hung out with her nearly every week for years. [Cookiepuss -- No Dogs No Masters] She had the run of the building at ABC No Rio, and was friends with all sorts of people. She was known and loved by punks and fine artists, by experimental musicians and bike mechanics, computer geeks and librarians, travelers and homebodies, photographers, screenprinters, anarchists, community organizers, zinesters, activists, performers, and weirdos of all stripes. For years, she received postcards from all over the world, including several from people who had never even met her in person. In her younger days, she was a ferocious mouser, and even as she shrank with age and lost some of her teeth she remained excited about food. She was an inveterate complainer; a pants-shredder; a cat remarkably comfortable with dirt; a welcoming presence to newcomers and a friendly old curmudgeon who never seemed to really hold a grudge even when i had to do horrible things like help her trim her nails. After a long life, she died having said her goodbyes, and surrounded by people who loved her. I couldn't have asked for better, but I miss her fiercely.

25 September 2013

Jon Dowland: Married

Jon and Sarah
I got married! Sarah and I tied the knot on the 10th August this year. We married in a registry office where we live and had an evening reception on Tynemouth beach. A fantastic time was had by all. We honeymooned in Sorrento, Italy, which was fantastic. We spent one day visiting Pompeii (my fourth visit: about 6 hours on our feet this time, and we walked from one side right to the other); another day in Herculaneum (my second visit); one day visiting the village near where we were staying, where we visited a local food festival and bought the nicest Marmelade I've ever tasted; a few day and evenings in Sorrento town itself; but most of the time we just relaxed, swam, snoozed, read.

Sylvain Le Gall: OUnit 2.0 progress, September 2013

Continuing last month progress report onOUnit2. The release is just a few days away, I am testing real life application and the core of the work is already in the VCS. The basic features: Still remaining to do, but quite straightforward: Some things that I decided not to do for OUnit 2.0 release: The main development is now done, but before releasing I decided to test it first on a real scale application. The first big migration to OUnit2, will be the OASIS test suite. This is a pretty big test suite (100+ tests) that takes a fair amount of time to run. I hope that during the next week I will be able to port the whole test suite and come back with some timing results. You can follow my progress on porting OASIS to OUnit 2.0, in github. Help wanted If you have a long standing issue with OUnit, this is the time to submit a bug. OUnit BTS If you want to try the dev version of OUnit:
 $> darcs get http://forge.ocamlcore.org/anonscm/darcs/ounit/ounit
Patches always welcome. You can read the documentation of the devel version the website.

23 September 2013

Ben Hutchings: Linux kernel update for wheezy (3.2.51-1)

The upcoming stable update for Debian (7.2) should have a new Linux kernel version, fixing various bugs. I have uploaded version 3.2.51-1 which is now available in wheezy-proposed-updates. I would appreciate any regression testing people can do before this is released. Also, this fixes one of the causes of lock-ups currently seen with newer Intel GPUs, though we don't know exactly which bug reports were due to this. If you've reported this kind of problem, please test whether this version fixes it. Updated 2013-09-23: KiBi reminded me to link to the page about proposed-updates. And the update is now available for all architectures.

Next.

Previous.