Search Results: "ema"

26 June 2013

Russ Allbery: Review: River of Stars

Review: River of Stars, by Guy Gavriel Kay
Publisher: Roc
Copyright: April 2013
ISBN: 0-451-46497-4
Format: Hardcover
Pages: 639
In Under Heaven, Guy Gavriel Kay applied his style of slightly fantastic alternate history to Tang Dynasty China and wrote possibly the best book of his career. In River of Stars, he takes the unusual step of revisiting one of his historical worlds, something I don't think he's done explicitly apart from the Sarantime Mosaic duology. River of Stars is set in the same land of Kitai, Kay's alternate China, four centuries later. It's a stand-alone novel, not a sequel, but the effects of the events of the earlier book are deeply felt on the structure of society. Under Heaven was one of my favorite books of all time, so you can imagine how eagerly I've been awaiting this book ever since it was announced. It starts, once again, in the distant regions of Kitai, this time with a boy. Ren Daiyan is the second son of a minor clerk in a backwater town with a very atypical dream for someone of his social rank: to win back the lost provinces of Kitai from the Xiaolu and restore the glory of the empire as the center of the world. One sees little hope for this dream in a world where no one with any choice in the matter would let their sons join the discredited and suspected army. And, as River of Stars opens, it's become much less likely since the town's only teacher has closed his school and left. As with Under Heaven, the unfolding of Daiyan's life is full of surprises, all of which should be enjoyed in the flow of the story. Here, I think the cover flap even gives away too much information, despite only mentioning events at the start of the book, since the incident that it recounts has much more impact without being spoiled. I recommend avoiding any plot summary and just reading, and therefore will avoid giving any more details. River of Stars, in another echo of its predecessor novel, has a second, female protagonist. Lin Shan is the daughter of a scholar on the edges of imperial court life, a man who has quietly but persistently refused to educate her differently than he would have educated a son. This matters in the time of this novel. Kitai has turned more conservative, turned away from the roles of women in public life seen (in their limited ways) in Under Heaven, and has pressed women into new roles of formal modesty. Shan has been set up for a difficult life. But she's also brilliant, careful, and canny, making use of opportunties, and manages to make several extraordinary friends within the power structures of the court. It's impossible not to compare this novel to Under Heaven, but that's an unfair standard to which to hold any novel. So I will say up front that, at least for me, River of Stars does not capture quite the same magic. Shen Tai was a brilliant protagonist, and his unwanted journey into the circles of power was the perfect palette on which to mix personal integrity with sweeping politics. It used history as a backdrop for a novel that was always grounded in Shen Tai's modest ambitions and quiet integrity. Neither Daiyan nor Shen are that character, nor is River of Stars that book. This novel is far more political from the start, concerned directly with issues of governance, court intrigue, and military maneuvers. Even with Shen to ground the story, the personal is the political and the events of history have been moved to center stage. I've seen Kay approach a history both ways, and I prefer when he uses history as backdrop rather than focus. I find it easier to identify and celebrate with the protagonists when their journies are less caught up in grand events. When, as here, the personal becomes the political, it creates a darker tone. The stakes are higher, and there is little separable individual triumph to blunt the tragic moments. That said, Kay remains at the height of his form. Once again, this novel contains some of the best conversations I have ever read. I'm not sure what Kay is doing that other novelists aren't. It may be that he is discarding some realism in favor of presenting the purified essence of sharp and dangerous exchanges (more on that in a bit). But there are several conversations here that read like the distilled essence of a high-stakes, insightful exchange between fearsomely intelligent adversaries: steeped in strategy, carefully managed for effect, and full of thrilling rhetorical tightropes. There are also moments that literally sent shivers up my spine: moments when the story changes, and lives change, in ways that I was not expecting at all. The story is beautifully stage-managed, imbuing every moment with a feeling of a broader resonance. I do have to warn, as with all Kay but particularly recent writing, that this is done openly and explicitly via an omniscient and very obvious narrative voice. Kay writes in the style of high fantasy in which the narrator is nearly a character in the story, one who foreshadows events and shares observations directly with the reader. Some people dislike that style inherently, and if so, Kay may not be for you. I love it when it's done well, and I don't think anyone does it better than Kay. I feel like I'm in the hands of a master storyteller who is carefully crafting the story to preserve surprise and suspense and who knows exactly where he wants the story to go. That's fitting, since one of the major themes of this book is stories and legends, and how they are shaped by events but then come to shape events in turn. River of Stars is partly about the construction of stories in the way that Under Heaven was partly about poetry. Some of the characters try to control the setting and subject matter, some use stories as a way to focus their personal motivation, and some use them to define their lives. But stories also shape politics because they can define popular reaction and the limits of the possible. This theme is subtle through much of the book, but the more I thought about it the more I noticed it woven through the story. Unfortunately, and very unusually for one of Kay's novels, the journey was intense but the destination was mildly unsatisfying. I don't want to give away any detail of the plot, so this is necessarily vague, but while I intellectually appreciate the themes that I think Kay was exploring, I think River of Stars lacks the powerful catharsis that I normally get from his novels. This for me returns to the focus on the politics over the personal (which is in some ways another of the themes of the novel). The catharsis in a novel for me begins and ends with the characters, and these characters didn't have quite enough independence from the broader sweep of events. Another theme of the novel is the degree to which every character is operating within tight constraints. This also showed up in Under Heaven, but Under Heaven was full of characters who subverted and manipulated those constraints. In River of Stars, they are more often suffocating. Shen is my favorite character, and I think the strongest character in the novel, because she manages to work around the most constraints and has the most personal story. But the roles into which she's forced remain smothering and push her out of the center of the action. Her life is full of lovely details (I particularly liked her domestic situation, which shows a family model that I think was far more common in reality than it has been in fiction and one that I would like to see portrayed far more often), but she simply doesn't have realistic room, within the society portrayed here, to maneuver to the catharsis I was looking for. One other, minor note: as in Tigana, but more blatantly, unusual sexual desires make an appearance linked with the closest thing this story has to a villain. (In this case, femdom BDSM, although shown so glancingly that I suspect some readers will not pick up on what's being described.) It was neither unrealistic nor out of character, but there is a moment of nastiness that caught me by surprise and bothered me. I hope eventually to see alternative sexuality show up in a Kay novel without the negative linkages. It's not quite characterization by stereotype (I think Kay was going for a deeper point about the constrained roles available to women), but it's close enough to not work for me. I'm spending a lot of words on what didn't quite work for me, but that's because it's complex to explain, not because this is a bad story. Rather the opposite: it's an excellent novel that I didn't enjoy quite as much as its predecessor for reasons that are very individual to me. It's quite likely that those with different narrative preferences or different tolerances for certain emotional tones in novels will have a far different reaction. The quality of the writing is quite high, provided that you don't mind Kay's intrusive narrator, and several moments in this novel made me catch my breath in wonder. If you like Kay, read this; it's very much worth your time. If you're new to Kay, I would start with Under Heaven, which is near the top of my list of novels to recommend to anyone. Then read this, since seeing how the world develops and how the events of the previous novel change and shape subsequent politics is fascinating. It's not quite at the same level, but it's very much worth reading on its own terms. Rating: 9 out of 10

25 June 2013

Dirk Eddelbuettel: Rcpp 0.10.4

A new version of Rcpp is now on the CRAN network for GNU R; binaries for Debian have been uploaded as well. This release brings a fairly large number of fixes and improvements across a number of Rcpp features, see below for the detailed list. We are also announcing with this release that we plan to phase out the RCPP_FUNCTION_* macros. Not only have they been superceded by Rcpp Modules and Rcpp Atributes (each of which has its own pdf vignette in the Rcpp package), but they also appear to be at best lightly used. We are for example not aware of any CRAN packages deploying them. To provide a smooth transition, we are aiming to keep them around for another twelve months, but plan to remove them with the first release after that time window has passed. As before, we tested the release rather rigorously by checking against all packages I could (relatively easily) built on my server: this time it covered 91 of the 124 CRAN packages depending on Rcpp. As all of these 91 packages passed their checks, we do not expect any issues with dependent packages. The complete NEWS entry for 0.10.4 is below; more details are in the ChangeLog file in the package and on the Rcpp Changelog page.
Changes in Rcpp version 0.10.4 (2013-06-23)
  • Changes in R code: None beyond those detailed for Rcpp Attributes
  • Changes in Rcpp attributes:
    • Fixed problem whereby the interaction between the gc and the RNGScope destructor could cause a crash.
    • Don't include package header file in generated C++ interface header files.
    • Lookup plugins in inline package if they aren't found within the Rcpp package.
    • Disallow compilation for files that don't have extensions supported by R CMD SHLIB
  • Changes in Rcpp API:
    • The DataFrame::create set of functions has been reworked to just use List::create and feed to the DataFrame constructor
    • The operator-() semantics for Date and Datetime are now more inline with standard C++ behaviour; with thanks to Robin Girard for the report.
    • RNGScope counter now uses unsigned long rather than int.
    • Vector<*>::erase(iterator, iterator) was fixed. Now it does not remove the element pointed by last (similar to what is done on stl types and what was intended initially). Reported on Rcpp-devel by Toni Giorgino.
    • Added equality operator between elements of CharacterVectors.
  • Changes in Rcpp sugar:
  • Changes in Rcpp build tools:
    • Fix by Martyn Plummer for Solaris in handling of SingleLogicalResult.
    • The src/Makevars file can now optionally override the path for /usr/bin/install_name_tool which is used on OS X.
    • Vignettes are trying harder not to be built in parallel.
  • Changes in Rcpp documentation:
    • Updated the bibliography in Rcpp.bib (which is also sourced by packages using Rcpp).
    • Updated the THANKS file.
  • Planned Deprecation of RCPP_FUNCTION_*:
    • The set of macros RCPP_FUNCTION_ etc ... from the preprocessor_generated.h file will be deprecated in the next version of Rcpp, i.e they will still be available but will generate some warning in addition to their expected behavior.
    • In the first release that is at least 12 months after this announcement, the macros will be removed from Rcpp.
    • Users of these macros (if there are any) should start replacing them with more up to date code, such as using Rcpp attributes or Rcpp modules.
Thanks to CRANberries, you can also look at a diff to the previous release 0.10.3. As always, even fuller details are on the Rcpp Changelog page and the Rcpp page which also leads to the downloads, the browseable doxygen docs and zip files of doxygen output for the standard formats. A local directory has source and documentation too. Questions, comments etc should go to the rcpp-devel mailing list off the R-Forge page

24 June 2013

Vincent Sanders: A picture is worth a thousand words

When Sir Tim made a band the first image on the web back in 1992, I do not imagine for a moment he understood the full scope of what was to follow. I also do not imagine Marc Andreessen understood the technical debt he was about to introduce and that fateful day in 1993 when he proposed the img tag allowing inline images.

Many will argue of course that the old adage of my title may not apply to the web, where if it were true, every page view would be like reading a novel! and many of those novels would involve cats or one pixel tall colour gradients.

Leaving aside the philosophical arguments for a moment it takes web browser author a great deal of effort to quickly and efficiently put those cat pictures in front of your eyeballs.
NavigatingImages are navigated by a user in a selection of ways, including:
Whatever the method, the resulting object is subject to the same caching operations as any content object within a browser. These caching and storage operations are not specific to images however images are one of the most resource intensive objects a browser must regularly deal with (though javascript and stylesheet sources are starting to rival it at times) because they are relatively large and numerous.
Pre render processing
When the image object fetch is completed the browser must process the image for rendering which is where this gets even more complicated. I shall use how this works in NetSurf as I know that browsers internals best, but operation is pretty similar in many browsers.

The content fetch will have performed basic content sniffing to determine the received objects mime type. This is necessary because a great number of servers are misconfigured and a disturbingly large number of images served as png are really jpegs etc. Indeed sometimes you even get files served which are not images!

Upon receipt of enough data to decode the image header, for the detected mime type, the images metadata is extracted. This metadata usually includes things like size and colour depth.

If the img tag in the original source document omitted the width or height of the image the entire document render may have to be reflowed at this point to allow the correct spacing. The reflow process is often unsightly and should be avoided. Additionally at this stage if the image is too large to handle or an unhandled format the object will be replaced with the "broken" image icon.

Often that will be everything that is done with the image, when I added "lazy" image conversion to NetSurf we performed extensive profiling and discovered well over 40% of images on visited pages are simply never viewed by the user but that small (100 pixel on a side) images were almost always displayed.

This odd distribution comes down to how images are used in modern web pages, they broadly fall into two categories of "decoration" and "content" for example all the background gradients and sidebar images etc. are generally small images used as decoration whereas the cat picture above is part of the "content". A user may not scroll down a page to see content but almost always gets to "view" the decoration.
Rendering
Created by Andrea R used under CC Attribution-NonCommercial-ShareAlike 2.0 licence
The exact browser heuristics used differ as to when the render operation is performed but they all have a similar job to perform. When i say render here this may be possibly as an "off screen" view if they are actually on another tab etc. Regardless the image data must be converted from the source data (a PNG, JPEG etc.) into a format suitable for the browsers display plotting routines.

The browser will create a render bitmap in whatever format the plotting routines require (for example the GTK plotters use a Cairo image surface) , use an image library to unpack the source image data (PNG) into the render bitmap (possibly performing transforms such as scaling and rotation) and then use that bitmap to update the pixels on screen.

The most common transform at render time is that of scaling, this can be problematic as not all image libraries have output scaling capabilities which results in having to decode the entire source image and then scaling from that bitmap.

This is especially egregious if the source image is large (perhaps a multi megabyte jpeg) but the width and height are set to produce a thumbnail. The effect is amplified if the user has set the image cache size limit to a small value like 8 Megabytes (yes some users do this apparently their machines have 32MB of RAM and they browse the web)

In addition the image may well require tiling (for background gradients) and quite complex transforms (including rotation) thanks to CSS 3. Add in that javascript can alter the css style and hence the transform and you can imagine quite how complex the renderers can become.
CachingThe keen reader might spot that repeated renderings of the source image (e.g. because window is scrolled or clipped) result in this computationally expensive operation also being repeated. We solve this by interposing a render image cache between the source data and the render bitmaps.

By keeping the data in the preferred format, image rendering performance can be greatly increased. It should be noted that this cache is completely distinct from the source object cache and relates only to the rendered images.

Originally NetSurf used to perform the render conversion for every image as it was received without exception, rather than at render time, resulting in a great deal of unnecessary processing and memory usage. This was originally done for simplicity and optimising for "decoration" images.

The rules for determining what gets cached and for how long are somewhat involved and the majority of the code within the current implementation NetSurf uses is metrics and statistic generation to produce better decisions.

There comes a time at which this cache is no longer sufficient and rendering performance becomes unacceptable. The NetSurf renderer errs on the side of reducing resource usage (clearing the cache) at the expense of increased render times. Other browsers make different compromises based on the expected resources of the user base.
FinallyHopefully that gives a reasonable overview to the operations a browser performs just to put that cat picture in front of your eyeballs.

And maybe next time your browser is guzzling RAM to plot thousands of images you might have a bit more appreciation to exactly what it is up to.

Daniel Pocock: Private WANs may be less secure than VPNs

The latest round of Snowden revelations concern a British GCHQ program dubbed "Mastering the Internet (MTI)". The program involves, among other things, tapping the world's under-sea fibre-optic cables and systematically monitoring all communications. One of the most significant facts that appears is the benefit of using IPsec and VPNs over the public Internet instead of trusting un-encrypted traffic to pass over private WAN connections. The definition of a private WAN connection is quite broad: many ISPs in the UK, for example, use the British Telecom OpenReach platform to tunnel DSL connections back to their data centers and offer virtual WANs to their business customers. Can any wifi be trusted? It should be assumed that all Wifi networks can be compromised at-will by a sophisticated attacker. This is another situation where VPNs may be part of the solution: even WPA2 secured wifi segments should be treated as untrusted public Internet networks and not bridged or routed onto any private subnets. Users with devices on a wifi network should be forced to use a VPN over wifi connection, even when the wifi is within the same building as the private network. Tor may be compromised by an attacker with this much data As I've mentioned in previous blogs with a focus on real-time communications there is no such thing as perfect privacy. Simply encrypting data with IPsec does not prevent the attacker knowing the volume of data transmitted or the time it was transmitted. Using a service like Tor for onion-routing provides some benefit. However, an attacker with sufficient infiltration of many points in the network may be able to deduce the real origins of a data transfer over Tor using some combination of packet sizes and timestamps. "Mastering the Internet (MTI)" may have sufficient coverage to achieve that. Tor could overcome this by putting dummy data into the network and adding fragmentation, but such schemes may add latency, reduce throughput and require significant effort to upgrade existing users. Gaining intelligence from encrypted data VoIP signals are typically compressed using some type of codec. These are dedicated, lossy compression schemes optimised for voice signals. Some codecs use a fixed compression ratio. Other codecs use a variable compression ratio (VBR): a simple example involves sending shorter packets to indicate a period of silence. Encrypting these packets prevents an attacker seeing what is inside them but the attacker can easily detect the lengths of the packets. Researchers have demonstrated that statistical techniques can be applied to VBR dataflows to identify syllables used in speech and then make a hypothesis about what has been said. (This would be an interesting hack to try and reproduce by collecting data with tcpdump and analysing it with R) Identifying phrases in encrypted VoIP using statistical analysis In many cases like those described, it is necessary to go beyond default encryption settings and put extra dummy data or frame padding into the data flow to gain a more fool-proof level of privacy. Simply connecting VoIP phones to an IPsec network doesn't automatically make them secure. The rise of the free-software VPN Even if the default configurations are not always universally resilient to every type of attack, many free software prodcuts provide an excellent building block for VPNs. Having the source code and specifications on hand, free software developers can then innovate to mix-and-match different technologies or add random data flows to mask the real activity on the network. In a recent hosting migration project, I successfully used the rather trivial VPN package tinc to bridge the ethernet segments between virtual machines in the old and new networks. This allowed virtual machines to be moved one-by-one over a period of a week. This is a remarkably simple solution that can protect the integrity of communications on a private subnet. A more comprehensive solution is strongSwan which provides support for industry-standard IPsec in various topologies. They now offer a full IPsec client for Android phones (hopefully it will be made available on f-droid: using a Google account to access Google Play may result in Google accidentally helping you "back up" your settings, including credentials, to their cloud, undermining the privacy of the system) An IPsec VPN can be deployed to all hosts on a network: then they can use opportunistic encryption for any type of communication without needing to worry about the underlying network. Furthermore, it is possible to add smart cards to further boost VPN security while using free software for the whole solution. For those interested in looking beyond Linux solutions, the *BSD range of operating systems, particularly OpenBSD provide a compelling alternative. This paper about OpenBSD's iked, which is also available on other platforms as OpenIKEd is very recent and provides a thorough overview of it's current status. One notable limitation is that their MOBIKE support is not yet complete. Many older VPNs likely to need an ugprade When I first started deploying Linux VPNs in the 90s the market was favourable for any type of Linux VPN. In extreme cases (which were surprisingly common at the time) companies accustomed to paying $20,000 per month for a leased line would happily pay a flat fee of $100,000 to purchase a VPN that was cobbled together using less than $10,000 of commodity hardware and some free software. Many of the first generation of these VPNs were built using RSA key lengths and algorithms no longer considered secure, such as DES. Some of these solutions (or products derived from them) may still remain in use today: managers may be slightly embarrassed to put aside their $100,000 VPN and replace it with a $50 router that is more secure. While that is the more extreme example, there are many intermediate solutions out there in the field. There are clear opportunities here to upgrade users to free software solutions.

23 June 2013

Marko Lalic: Google Summer of Code - Debian Package Tracking System

Introduction
Every May for the last three or four years, I contemplated applying for the Google Summer of Code program. I was never quite sure I would be up for the challenge, though, but this year I finally took the plunge.

Since Python is my favorite language, I was looking to take up a project which could use it. When I saw that one of the possible projects which the Debian Project was offering was a rewrite of the Package Tracking System using Django, my choice became pretty clear. Not only would I use my favorite programming language, I could get a chance to interact with one of the largest and best established open source communities in the world. Moreover, the Package Tracking System is one of the most important parts of Debian's infrastructure and working on making it even better seemed like a perfect way to get into the open source world. The fact that I also had prior experience using Django on a Web project was an additional factor which pushed me to go for it.

Two programming tasks, meant to evaluate the students' knowledge and also give them a chance to get acquainted with the current implementation of the PTS, were given to prospective applicants by the Debian Google Summer of Code team. Neither was particularly challenging in and of itself, but since I had to attend the annual Congress of the Electrical Engineering Students' European Association in Munich during the week the applications were open, I was quite pressed for time. In the end, I managed to complete the application in a timely fashion and I submitted it being pleased that I at least made an attempt to get in the Summer of Code program.

Truthfully, when I got an email from Google on a Monday night congratulating me on being selected for the project, I could not believe my eyes. I needed to take about an hour to read the email again and make sure there wasn't some sort of mistake, but, as it turns out, there really was not. This is when excitement kicked in and I started to draft an email to my mentor for the project, Rapha l Hertzog, to start on the official planning for the summer.

PTS Rewrite in Django
The Package Tracking System is currently made up from a variety of different scripts, ranging from Bash, through Perl, to Python, which are used to pull all information about packages and generate a static HTML page for each of them. This process is repeated as a cron-job a few times each day meaning that the information presented on the pages could easily be outdated. So, a requirement for the new system is that the pages need to be as dynamic as possible.

Consolidating the code into a well thought out Django project hopes to make it easier for other developers to contribute to the project.

Finally, decoupling the application itself from Debian-specific resources, along with making it easy to customize or extend any logic, aims to allow derivatives to deploy their own Package Tracking System by simply making a few modifications to the configuration.

This is quite an ambitious set of goals, but I believe it should be attainable.

Community Bonding Period and the First Week
As I was already quite familiar with the existing codebase and PTS documentation by completing the tasks for the application, I did not need to use the community bonding period to get to know the project itself, but I did use the first few days to read up about using agile methods (particularly Scrum) and Test-Driven Development, since this was what my mentor, Rapha l Hertzog, and co-mentor, Stefano Zacchiroli, saw us using. Naturally, these were not new terms for me, but never having applied either an agile or a test-driven approach on a large scale project, I wanted to be as prepared as I could for the coming weeks.

I was quite eager to start working, though, and as it turns out, so were my mentors. When Rapha l made the suggestion to begin even before the official first week, I accepted and from there, my first "real" work on the project came: trying to define as many of the core stories to describe the system. This was followed by writing exhaustive acceptance tests and giving a rough time estimate on the stories relating to the email interface of the PTS. We are using a Trello board to document and track all this.

As we were planning on applying a Scrum-inspired agile approach, this meant having fixed-duration sprints/iterations which produce a working part of the system. Using a week long iteration seemed like a perfect fit for the situation. The other part, a working deployment, was handled by me setting up an Amazon Web Services EC2 instance where the application is deployed upon completing the week's work.

After all this, I started the coding work, trying to follow a Test-Driven Development approach. Properly applying it is sometimes a challenge, never having used it before, but its usefulness is definitely obvious. Being able to rely on this harness makes refactoring work painless and stress-free. Rapha l's constant feedback on this part is really helping me get into the flow of things and I hope that I will be quite proficient in it in a few weeks' time.

In summation, at the end of the first official week, on Friday, June 21 (during the third week since I started), a large chunk of the PTS's existing email functionality has been reimplemented and deployed. Some kinks and wrinkles are left to iron out, as well as add some long desired improvements to it, but, all in all, I would say that the two iterations produced a nice and usable result.

Anyone interested can already test this out... The email address control@pts.debian.net is used to access the control bot and the different commands. You can send it an email message containing the help command (the word help on a single line) to see the list of the currently implemented commands, along with their description. Currently, though, only a few packages are available to be subscribed to, imaginatively named "dummy-package", "second-package", "third-package" (quotes for clarity). The address for the package-specific messages to be forwarded to subscribers is <package-name>@pts.debian.net.

Conclusion
As the summer and my GSoC work is settling into a stable weekly-iteration rhythm, I have decided to set this blog up where I plan on writing a weekly update about the work being done for the PTS to complement my weekly status reports sent to the Debian GSoC coordination mailing list.

Again, I invite anyone who is interested in contributing to the future of the PTS in some way to test out the weekly deployments, contact me with any questions, feedback or advice, or simply follow the status updates on the blog, the Trello board or the project's Git repository.

Finally, I would like to give a great thank you to the Debian Project community, with the aforementioned mentors, Rapha l Hertzog and Stefano Zacchiroli, at the top, for giving me the vote of confidence to work on this project. The experience and knowledge I will get from it is immeasurable. Special thanks to Rapha l for putting a lot of effort and time into his feedback and advice; it really means a lot to me and I hope I use it in a way which will bring this project to a successful ending.

Gregor Herrmann: RC bugs 2013/24-25

thanks to lucas & his trainees, we're seeing archive rebuilds & tons of new RC bugs again. besides that, there are still some patches in the BTS. here goes my list of recently worked on bugs; most of them in the pkg-perl group

Paul Tagliamonte: Hacking a Computer from Scratch

I ve decided that I d rather like to hack an entire working (ok, not working", but programmable) computer (except for ROM and perhaps I/O) from scratch (just wires, perfboard, transistors (and friends) and solder). It sounds insane, but a simple ALU seems easy enough. Anyone do this before? Anyone have tips? Schematics of similar projects?

I ll be sure to blog my progress if / when I get around to starting it.

Ben Armstrong: Tutorial: wheezy live iso-hybrid with persistence on USB

As of wheezy, Debian no longer offers for download any prebuilt hdd (formerly known as usb-hdd) live images, which, in squeeze, were necessary if you wanted to use persistence. The good news is, since the new wheezy iso-hybrid images use xorisso, you can copy an image to a USB key and repartition it to add a persistence partition. Unfortunately, the filesystem itself is read-only, so you have to manually append the persistence boot parameter each time you boot the image. If that doesn t bother you, you can skip this whole tutorial and just follow the instructions in live-manual for adding a persistence partition and you re all set. This tutorial explains how to extract the contents of a wheezy iso-hybrid live image to a USB key and modify it to boot with this parameter permanently enabled. I am writing it solely as a workaround and do not endorse this as a means to customize Debian Live images in general. I would love to help make a more convenient, supported way to accomplish the same thing for a future release. Meanwhile, the supported and recommended way to make any change to a Debian Live image is to build it from scratch using live-build, as described in live-manual. A simplified Debian Live Images Autobuilder web service is available that works well for many common customizations, if you prefer. Please use one of these methods if you want to do this, or other customizations in the supported way. Otherwise, read on. Prerequisites Identify the USB key device Caution: Always double-check the device you are writing to is the correct one to avoid losing precious data. There are two things to do to protect yourself. The first is, don t write the USB key as root. The second is, first use ls -l /dev/disk/by-id to identify which device is the target USB key.
lrwxrwxrwx 1 root root  9 Jun 22 11:58 
usb-SanDisk_Cruzer_Contour_0000184CA87406BC-0:0 -> ../../sdb
As you can see, my SanDisk Cruzer Countour is /dev/sdb. For the rest of the tutorial, I ll be referring to this device as /dev/sdX to avoid unfortunate cut-and-paste disasters. When you follow along, make sure you substitute the correct device for your USB key on your system. Initialize the USB key Start by plugging in the key and unmounting any automounted partitions to ensure nothing is accessing the device, e.g.
$ umount /dev/sdX1
Now make changes to the partition table. Use parted because it may be run as an ordinary user and has some advanced capabilities beyond more basic tools like fdisk.
$ /sbin/parted
WARNING: You are not superuser.  Watch out for permissions.
GNU Parted 2.3
Using /dev/sdX
Welcome to GNU Parted! Type 'help' to view a list of commands.
(parted) print devices
/dev/sdX (8221MB)
(parted) select                                                           
New device?  [/dev/sdX]?                                                  
Using /dev/sdX
(parted)
Note that when run as an ordinary user, if you only have one removable drive (which may include mp3 players, cameras, e-readers) plugged in, parted immediately selects that device. But just to be sure, use print devices to list the devices and select to if you need to select a different one, as shown above. Repartition the USB key Once you ve verified you have the correct device, start repartitioning. Write a new partition table with mklabel msdos to wipe out all of the old partitions on it. You may skip this step and adapt the remaining instructions if there are partitions you need to keep. This is your last chance to bail if the device is wrong, so make sure it is the correct one before proceeding.
(parted) mklabel msdos
Warning: The existing disk label on /dev/sdX will be destroyed and all data
on this disk will be lost. Do you want to continue?
Yes/No? y
Error: Partition(s) 1, 2, 3, 4, 5, 6, 7, 8, 9, 10, 11, 12, 13, 14, 15, 16 on
/dev/sdX have been written, but we have been unable to inform the kernel of
the change, probably because it/they are in use.  As a result, the old
partition(s) will remain in use.  You should reboot now before making further
changes.
Ignore/Cancel? i
(parted)
The error is normal, and appears when you run parted as an ordinary user, so it is OK each time it appears to press i to ignore it. For the rest of this tutorial I will omit these errors from the output for brevity. Make three partitions, a fat32 partition for the image itself that is 5% larger than the size of the ISO, a 1G ext4 partition for persistence, and an extra fat32 partition for the rest of the space. Put the extra partition first so that other OSes you might use the key with will be able to use it. Use relative positioning from the end of the device to make it easy to put all of the rest of the space in the first partition. Finally, flag the live image partition bootable.
(parted) mkpart primary fat32 1 -1897M
(parted) mkpart primary ext4 -1897M -897M
(parted) mkpart primary fat32 -897M -0
(parted) set 3 boot on
(parted) quit
Information: You may need to update /etc/fstab.
Unplug the USB key and plug it in again so that the kernel will re-read the updated partition table. If there were old filesystems on the key that were automounted, unmount them again. Now we re ready to make the new filesystems.
$ umount /dev/sdX1
$ /sbin/mkdosfs -nEXTRA /dev/sdX1
mkdosfs 3.0.16 (01 Mar 2013)
$ /sbin/mkfs.ext4 -q -Lpersistence /dev/sdX2
$ /sbin/mkdosfs -nLXDE /dev/sdX3
mkdosfs 3.0.16 (01 Mar 2013)
Make the USB key bootable Use install-mbr to install an MBR on the key and syslinux to install the bootloader to boot into your live image partition.
$ /sbin/install-mbr /dev/sdX
$ syslinux -i /dev/sdX3
Mount the partitions Unplug the key and plug it in again so the new partitions will be automounted. Observe where the partitions are mounted with df.
$ df
...
/dev/sdX1        6204568         4   6204564   1% /media/EXTRA
/dev/sdX3         831888         4    831884   1% /media/LXDE
/dev/sdX2         944120      1204    894124   1% /media/persistence
Extract the ISO contents to the key To continue preparing this key as an unprivileged user, use p7zip to extract the ISO. You may alternatively mount the ISO loopback and extract it that way, but you must be root to do that.
$ cd /media/LXDE
$ 7z x ~/debian-live-7.0.0-amd64-lxde-desktop.iso
...
Extracting  live/filesystem.packages-remove
...
When live/filesystem.squashfs is extracted (right after live/filesystem.packages-remove) it will take the longest time of all of the files to extract, as it contains the whole live filesystem. Be patient and eventually it and all other files on the image will finish extracting.
...
Everything is Ok
Folders: 245
Files: 370
Size:       892183367
Compressed: 895483904
Modify the bootloader configuration files The syslinux bootloader configuration directory and files within it are named isolinux when installed on an ISO. You need to rename the directory and two files changing isolinux to syslinux so the bootloader will find them on your fat32 live image partition.
$ mv isolinux syslinux
$ mv syslinux/isolinux.cfg syslinux/syslinux.cfg
$ mv syslinux/isolinux.bin syslinux/syslinux.bin
Enable full persistence Next, append persistence to the live boot parameters and turn on full persistence by putting / union in a persistence.conf file in the persistence partition.
$ sed -i 's/\(append boot=.*\)$/\1 persistence/' syslinux/live.cfg
$ cd /media/persistence
$ echo / union > persistence.conf
Reboot into the live system Now your USB key is ready to boot with full persistence enabled. Have fun!

22 June 2013

Justus Winter: My first week and some promising though hacky results

Hi Planet Debian :) my name is Justus Winter, I'm a computer science student at the University of Hamburg. I'm participating in the GSOC 2013, my task is to make Debian/Hurd systems boot using the same initialization scripts Debian/Linux uses. I spent the community bonding period with some gsoc related administrative tasks, updating my development machine and getting reacquainted with the Hurd system. It was nice to see how far Debian/Hurd has come since my last "serious" encounter with it. I've setup a continuous build solution on one of my Hurd VMs and prepared a package repository. I'll post details once I have some packages to share. I built the hurd, sysvinit and ifupdown packages and dived into the interesting world of literate programming. I'm going to write about that when I start looking into the ifupdown related issues. But most importantly I started writing a tool to automate all the tasks I would do during my work that could possibly be automated. As I'm working on the boot process, it makes sense to use some kind of virtualization software so I can work in the comfort of my usual development environment. My virtualization solution of choice is qemu and I actually wrote a qemu based black-box test solution for a former employer once, so I already was familiar with qemu and wrapping my own code around it. Without further ado, here it is: https://bitbucket.org/teythoon/hurdtest Provided that you have golang installed, you can compile it easily:
teythoon@europa /tmp % export GOPATH= pwd 
teythoon@europa /tmp % go get bitbucket.org/teythoon/hurdtest
teythoon@europa /tmp % bin/hurdtest
Usage: hurdtest [options] <command> [<arguments...>]
Currently it has the following subcommands:
test
Starts a VM, logs in as root, tests the interaction with the VM, verifies that certain VFS locations are writable, tests the network connectivity, the DNS resolution and installs and runs the hello package.
update
Executes aptitude update && aptitude full-upgrade, reboots the system and runs the test subcommand. If successful, it commits the changes to the virtual disk and creates a snapshot.
overlay
Takes as argument the path to a directory that is copied to the VM, reboots the machine and runs the test subcommand.
The update command is nice because it allows me to keep the VM up to date while ensuring that the image remains usable, with respect to what the test command considers a usable state of a Debian system. I'd really like to get some suggestions on how to test the "health" of a Debian system. You can look at how the tests are implemented in test.go, it's quite easy to add more and more interesting tests, and you don't even have to clean up after them or worry about any side-effects as the changes are not committed to the virtual disk. This is hurdtest doing an update:
teythoon@europa ~/repos/hurd/hurd-tests % bin/hurdtest update
2013/06/22 19:59:45 starting kvm [-drives file=image.qcow2,cache=writeback,snapshot=on -serial unix:/tmp/285813369/serial -monitor unix:/tmp/285813369/monitor -nographic -m 512]
2013/06/22 19:59:45 Waiting for grub...
2013/06/22 19:59:46 Waiting for login prompt...
2013/06/22 20:00:05 Updating system
2013/06/22 20:02:52 Get: 1 http://www.local unstable InRelease [8279 B]
Get: 2 http://http.debian.net sid InRelease [205 kB]
Get: 3 http://ftp.debian-ports.org unreleased InRelease [23.9 kB]
[...]
Setting up perl (5.14.2-21) ...
Reading package lists...
Building dependency tree...
Reading state information...
Reading extended state information...
Initializing package states...
Reading task descriptions...
2013/06/22 20:02:52 Update successful. Snapshotting system...
2013/06/22 20:02:53 Rebooting system...
2013/06/22 20:02:54 Waiting for grub...
2013/06/22 20:02:59 Waiting for login prompt...
2013/06/22 20:03:16 Running main.testTrue...
2013/06/22 20:03:16 Running main.testFalse...
2013/06/22 20:03:17 Running main.testClean...
[...]
2013/06/22 20:03:18 Running main.testNetwork...
2013/06/22 20:03:18 Running main.testResolver...
2013/06/22 20:03:20 Running main.testAptitudeInstall...
2013/06/22 20:03:46 Test successful. Reverting system...
2013/06/22 20:03:48 Halting system...
2013/06/22 20:03:53 Committing changes...
2013/06/22 20:03:57 Creating snapshot...
2013/06/22 20:04:04 All done.
bin/hurdtest update  157.31s user 69.71s system 87% cpu 4:18.94 total
The overlay command implements my work flow. I can edit scripts or drop hacked up executables onto my VM and see the results without any manual intervention. There's the -interactive flag that does this in a loop, avoiding the VM startup time using qemu snapshots. With this I can apply an overlay and see the results of the test suite in about a minute on my system. From early experiments I knew that simply running /etc/rcS.d/S* prevented the system from booting correctly, so I figured my first task should be to figure out what went wrong there. Using my tool (and developing it in that process) and many iterations later I came up with a surprisingly small diff of scripts in the initscripts and utilities shipped with the hurd package. For your convenience here is a tarball that you can extract to the root of your Debian/Hurd installation to reproduce my results (of course I invite you to use my tool for that purpose):
% bin/hurdtest overlay test
2013/06/22 21:35:31 starting kvm [-drive file=image.qcow2,cache=writeback,snapshot=on -serial unix:/tmp/345188134/serial -monitor unix:/tmp/345188134/monitor -nographic -m 512]
2013/06/22 21:35:31 Waiting for grub...
2013/06/22 21:35:31 Waiting for login prompt...
2013/06/22 21:35:48 Creating tarball...
./
./etc/
./etc/hurd/
./etc/hurd/rc
./etc/init.d/
./etc/init.d/checkroot.sh
./etc/init.d/mountall.sh
./runme
./lib/
./lib/init/
./lib/init/mount-functions.sh
./sbin/
./sbin/swapon
./bin/
./bin/mount
2013/06/22 21:35:48 Extracting overlay...
2013/06/22 21:35:49 Rebooting system...
2013/06/22 21:35:49 Waiting for grub...
2013/06/22 21:35:55 Writing log to /tmp/bootlog-802006344
2013/06/22 21:35:55 Waiting for login prompt...
2013/06/22 21:36:20 Booting successful.
2013/06/22 21:36:20 Running main.testTrue...
2013/06/22 21:36:21 Running main.testFalse...
2013/06/22 21:36:21 Running main.testClean...
2013/06/22 21:36:21 Running anonymous function...
2013/06/22 21:36:22 Running anonymous function...
2013/06/22 21:36:22 Running main.testUname...
2013/06/22 21:36:22 Running main.testNetwork...
2013/06/22 21:36:22 Running main.testResolver...
2013/06/22 21:36:23 Running main.testAptitudeInstall...
bin/hurdtest overlay ../hurd-tests-old/test  44.20s user 20.01s system 82% cpu 1:17.94 total
And here is the boot log:
Loading GNU Mach ...
Loading the Hurd ...
GNU Mach 1.3.99-486
AT386 boot: physical memory map from 0x0 to 0x9f400
AT386 boot: physical memory map from 0x100000 to 0x1fffe000
AT386 boot: physical memory from 0x0 to 0x1fffe000
Enabling FXSR
pcibios_init : BIOS32 Service Directory structure at 0xfcff0
pcibios_init : BIOS32 Service Directory entry at 0xfc7ba
pcibios_init : PCI BIOS revision 2.10 entry at 0xfc78c
Probing PCI hardware.
ide: Intel 82371 PIIX3 (dual FIFO) DMA Bus Mastering IDE
    Controller on PCI bus 0 function 9
ide: BM-DMA feature is not enabled (BIOS), enabling
    ide0: BM-DMA at 0xc100-0xc107
    ide1: BM-DMA at 0xc108-0xc10f
hd0: got CHS=762/128/63 CTL=c8 from BIOS
hd0: QEMU HARDDISK, 3001MB w/256kB Cache, CHS=762/128/63, DMA
hd2: QEMU DVD-ROM, ATAPI CDROM drive
ide0 at 0x1f0-0x1f7,0x3f6 on irq 14
ide1 at 0x170-0x177,0x376 on irq 15
Floppy drive(s): fd0 is 1.44M
FDC 0 is a S82078B
probing scsi 0/22: advansys probing scsi 1/22: BusLogic probing scsi 2/22: UltraStor 14F/34F rev. 4.33.00  probing scsi 3/22: UltraStor 14F/24F/34F probing scsi 4/22: Adaptec 152x SCSI driver; $Revision: 1.1 $ probing scsi 5/22: Adaptec 1542 Invalid address for shpnt with 1542.
Invalid address for shpnt with 1542.
probing scsi 6/22: Adaptec 174x (EISA) probing scsi 7/22:  probing scsi 8/22: Always IN2000 probing scsi 9/22:  probing scsi 10/22:  probing scsi 11/22:  probing scsi 12/22: Trantor T128/T128F/T228 probing scsi 13/22: DTC 3180/3280  probing scsi 14/22: Tekram DC390(T) V1.11 Feb-05-1997 probing scsi 15/22:  probing scsi 16/22: ncr53c8xx - revision 2.5f.1 probing scsi 17/22: EATA (Extended Attachment) PIO driver probing scsi 18/22: Western Digital WD-7000 Failed initialization of WD-7000 SCSI card!
probing scsi 19/22: EATA/DMA 2.0x rev. 4.33.00  probing eata on 1f0EATA0: address 0x1f0 in use, skipping probe.
probing eata on 1c88probing eata on 2c88probing eata on 3c88probing eata on 4c88probing eata on 5c88probing eata on 6c88probing eata on 7c88probing eata on 8c88probing eata on 9c88probing eata on ac88probing eata on bc88probing eata on cc88probing eata on dc88probing eata on ec88probing eata on fc88probing eata on 170EATA0: address 0x170 in use, skipping probe.
probing eata on 230probing eata on 330probing scsi 20/22: AM53C974 probing scsi 21/22: Iomega parport ZIP drive ppa: Version 1.42
ppa: Probing port 03bc
ppa: Probing port 0378
ppa:     SPP port present
ppa:     PS/2 bidirectional port present
ppa: Probing port 0278
done
scsi : 0 hosts.
scsi : detected total.
Partition check (DOS partitions):
 hd0: hd0s1 hd0s2 < hd0s5 >
lpr0: at atbus0, port = 378, spl = 6, pic = 7.
module 0: ext2fs --readonly --multiboot-command-line=$ kernel-command-line  --host-priv-port=$ host-port  --device-master-port=$ device-port  --exec-server-task=$ exec-task  -T typed $ root  $(task-create) $(task-resume) module 1: exec /hurd/exec $(exec-task=task-create)                                                                                                                                                                           2 multiboot modules                                                                                                                                                                                                                    task loaded: ext2fs --readonly --multiboot-command-line=root=device:hd0s1 console=com0 --host-priv-port=1 --device-master-port=2 --exec-server-task=3 -T typed device:hd0s1
task loaded: exec /hurd/exec
start ext2fs: Hurd server bootstrap: ext2fs[device:hd0s1] exec init proc auth
Using makefile-style concurrent boot in runlevel S.
ERROR: could not open /proc/stat: No such file or directory
Activating swap...done.
Checking root file system...fsck from util-linux 2.20.1
hd2 : tray open or drive not ready
end_request: I/O error, dev 02:00, sector 0
ext2fs_check_if_mount: Can't check if filesystem is mounted due to missing mtab file while determining whether /dev/hd0s1 is mounted.
/dev/hd0s1: clean, 44328/181056 files, 288266/723200 blocks
done.
Cleaning up temporary files... /tmp.
mount: /run: Unknown device or filesystem
mount: /run/lock: Unknown device or filesystem
mount: /proc: Unknown device or filesystem
mount: /run/shm: Unknown device or filesystem
/etc/rcS.d/S06mtab.sh: 48: /etc/rcS.d/S06mtab.sh: cannot open /proc/mounts: No such file
Activating lvm and md swap...(default pager): Already paging to partition hd0s5!
done.
Checking file systems...fsck from util-linux 2.20.1
hd2 : tray open or drive not ready
end_request: I/O error, dev 02:00, sector 0
done.
Mounting local filesystems...mount: invalid option -- 'O'
Try  mount --help' or  mount --usage' for more information.
failed.
Activating swapfile swap...(default pager): Already paging to partition hd0s5!
done.
df: Warning: cannot read table of mounted file systems: No such file or directory
Cleaning up temporary files....
Configuring network interfaces...inetutils-ifconfig: invalid arguments
ifup: failed to open pid file /run/network/ifup-/dev/eth0.pid: No such file or directory
Internet Systems Consortium DHCP Client 4.2.2
Copyright 2004-2011 Internet Systems Consortium.
All rights reserved.
For info, please visit https://www.isc.org/software/dhcp/
can't create /var/lib/dhcp/dhclient./dev/eth0.leases: No such file or directory
Listening on Socket//dev/eth0
Sending on   Socket//dev/eth0
DHCPDISCOVER on /dev/eth0 to 255.255.255.255 port 67 interval 5
DHCPREQUEST on /dev/eth0 to 255.255.255.255 port 67
DHCPOFFER from 10.0.2.2
DHCPACK from 10.0.2.2
can't create /var/lib/dhcp/dhclient./dev/eth0.leases: No such file or directory
bound to 10.0.2.15 -- renewal in 36884 seconds.
done.
Cleaning up temporary files....
Setting up X socket directories... /tmp/.X11-unix /tmp/.ICE-unix.
Using makefile-style concurrent boot in runlevel 2.
Starting enhanced syslogd: rsyslogd.
Starting deferred execution scheduler: atd.
Starting periodic command scheduler: cron.
Starting system message bus: dbusFailed to set socket option"/var/run/dbus/system_bus_socket": Protocol not available.
Starting OpenBSD Secure Shell server: sshd.
GNU 0.3 (debian) (console)
login:
I know it isn't that pretty, but it yields a working Debian/Hurd system that is more like a Debian/Linux system. For example /dev/shm and /run ,/* are connected to a tmpfs translator. I think this is a rather encouraging first result. I added my findings to the list of open issues. Another nice thing about hurdtest is that it is not even Hurd specific (only a tiny bit GNU Mach specific). I'm going to make it work nicely with Debian/Linux and Debian/kFreeBSD, since this is a very handy tool for anyone hacking on the Debian boot process (and with some changes for any OS). If anyone tries it out, I'd love to get feedback and patches. The tool requires the guest to be configured to use the first serial console for grub, the kernel and the userspace. The password for the user root must be empty. The guest has to have a working network connection setup at boot time. I will provide a suitable image as soon as I devise a good way to zero-fill the free space on the virtual disk. Is there any better way than to fill the disk with a huge file containing zeros? Without doing that the image is too large even compressed with xz. So this was my first week working for Debian. Next week I will focus on getting patches for the hurd and initscripts package in shape, I need to add some functionality to the mount utility shipped with the hurd package. It provides a mount-like experience on the Hurd, on which binding a translator (e. g. /hurd/ext2fs) to a filesystem node is an operation that does not involve the kernel (GNU Mach) at all, and is in fact a operation that any unprivileged user may perform. That is one of the nice features the Hurd has, it empowers its users.

21 June 2013

Daniel Pocock: Practical challenges for interrupt-free computing

My previous blog on interrupt-free computing has been very well read. I've had a look at some practical implementation possibilities and can share some more details about how to go about it and potential problems. No perfect solution They say that a certain billionaire is so rich that he would not spend 5 seconds bending over to pick up a $100 banknote on the ground because he makes $500 in 5 seconds anyway. A man from Ethiopia may well run a marathon for the same $100. This little anecdote underlines the point that no two people have exactly the same priorities and it is hard to provide a one-size-fits-all solution. A good technical solution needs to let the user have some control over their own priorities as that will go a lot further in respecting their preferences, their objectives and their environment. A practical example: some users may not want to be disturbed by a VoIP call while watching a movie with their PC. Other users may be quite happy to receive these interruptions. Some users may want to only allow this interruption from a subset of possible callers. Building blocks In the original blog on this subject I suggested that Thunderbird and it's popular plugin, Mozilla Lightning calendar would provide one useful framework for integrating events, alerts and to-do items of various grades of importance. I already use these applications myself, from the re-branded icedove and iceowl-extension packages on Debian. They are also available in Fedora and many other distributions. Priority with Lightning An initial look at Lightning reveals a Priority attribute for tasks. It can be set to the values High, Medium or Low. These don't map to the concepts of Urgency and Importance from the Eisenhower method discussed in the original blog. Potential hacks: there are two ideas that come to mind, with no coding changes:
  • One possibility is to set Due dates for any item that has the Urgent characteristic and no date for items without the characteristic. In this case, the Priority attribute can then be used to distinguish Important and non-Important tasks.
  • The other possibility is to use the Categories feature to define four categories: Urgent-Important, non-Urgent-but-Important, Urgent-non-Important and neither-Urgent-Important.
A more elegant solution would be to develop an additional plugin that provides new attributes for the Urgency and Importance characteristics. For server-side storage of these attributes, it would be feasible to use extension properties as defined in RFC 2445, for example, X-urgency and X-importance This approach would make it easier to view a large range of tasks across multiple domains with the most urgent and important tasks at the top. Ideally, the Categories attribute of tasks can be used to distinguish tasks that relate to work (or project/client) from personal tasks (such as planning a holiday) Challenges with Lightning Some of the challenges that I've identified after reviewing this solution:
  • the Categories in Lightning don't appear to be synchronized with the Tags used in Thunderbird for email.
  • Furthermore, the Tags are not synchronized automatically with the list of server-side IMAP keywords and somebody having multiple Thunderbird profiles (e.g. on both a desktop and a laptop) needs to manually synchronize the lists of tags and categories between all their devices.
  • Many people use mobile devices such as smartphones and tablets to access their email, calendar and tasks. The lightweight mail/calendar clients on these devices don't support the full range of features for classification of content. Furthermore, their low-resolution user interfaces may even make it difficult to replicate the same experience on a mobile device. There is some hope, for example, rooting a tablet device and installing Linux would allow it to run a proper installation of Thunderbird with the various plugins described above.
Feeding system events and other data into the pipeline Given the text-based nature of the iCalendar format, it should be easy enough for any application that is capable of generating mail to generate these iCal events with X-Urgency and X-importance properties. These events - such as alerts about security updates - could then be dispatched through the system's mailer. Some additional effort may be needed to avoid duplication. The notification system in the desktop UI may then prioritize events from the mailbox rather than showing all alerts in real-time. Only applications that implicitly need to do so (such as VoIP/chat clients) would display notifications to the user directly. Conclusion: Interrupting the user Finally, after gathering all the events for the user in a mailbox like this, it would be possible for the plugin to be configured to interrupt the user only when some event reaches the user's own urgency/importance threshold. For example:
  • The user may want to be interrupted for Urgent items with a deadline in less than 24 hours, but if the task has a work' category, only interrupt during business hours
  • For all other items, the user only sees them when they open Lightning or some other calendar/task management application to explicitly review things that they need to do.

Craig Sanders: backup-mysql.sh

A bash script to backup mysql databases, with separate schema and plain-text dump files (INSERT commands) for each database. Makes it easy to restore individual databases or copy them into dev/test servers. Keeps 30 days worth of backups in separate YYYY-MM-DD directories. Also dumps the mysql grants to a separate file mysql-grants.txt , and creates a sometimes conveniently useful mysql-create-databases.txt containing CREATE DATABASE commands. Based on my similar backup script for postgresql databases.
#! /bin/bash
# mysql backup script
#
# $Id: backup-mysql.sh,v 1.8 2013/06/21 02:20:39 cas Exp $
#
# by Craig Sanders <cas@taz.net.au>
# this script is public domain.  do whatever you want with it.
# set user/password here, or leave undefined to rely on ~/.my.cnf
#MYSQL_USER="root"
#MYSQL_PWD="SECRET"
[ -n "$MYSQL_USER" ] && ARGS="$ARGS -u$MYSQL_USER"
[ -n "$MYSQL_PWD" ] && ARGS="$ARGS -p$MYSQL_PWD"
DATABASES=$(mysql $ARGS -D mysql --skip-column-names -B -e 'show databases;'   egrep -v 'information_schema' );
BACKUPDIR=/var/backups/mysql
YEAR=$(date +"%Y")
MONTH=$(date +"%m")
DAY=$(date +"%d")
DATE="$YEAR-$MONTH/$YEAR-$MONTH-$DAY"
# make sure that perms on all created files/dirs are rwxr-x---
umask 0027
mkdir -p "$BACKUPDIR/$DATE"
cd "$BACKUPDIR/$DATE"
mysql $ARGS -Bse "SELECT CONCAT('SHOW GRANTS FOR \'', user ,'\'@\'', host, '\';') FROM mysql.user"   \
    mysql $ARGS -Bs   \
    sed 's/$/;/g'  > mysql-grants.txt
# "create database" lines, for easy cut-and-paste
> mysql-create-databases.txt
for i in $DATABASES ; do
  echo "CREATE DATABASE $i;" >> mysql-create-databases.txt
done
ARGS2="--skip-opt --no-create-db --no-create-info --single-transaction --flush-logs"
for db in $DATABASES ; do 
    echo -n "backing up $db: schema..."
    mysqldump $ARGS --no-data $db > $db.schema.sql
    echo -n "extended..."
    mysqldump $ARGS $ARGS2 --extended-insert $db > $db.data.extended.sql
    # uncomment if you want complete-insert dumps too.
    #echo -n "data...complete..."
    #mysqldump $ARGS $ARGS2 --complete-insert $db > $db.data.complete.sql
    echo -n "compressing..."
    gzip -9fq $db.schema.sql $db.data.extended.sql #$db.data.complete.sql
    echo "done."
done
echo deleting backups older than 30 days:
find "$BACKUPDIR" -mindepth 1 -a -type d -mtime +30 -print0   xargs -0r rm -rfv
backup-mysql.sh is a post from: Errata

20 June 2013

Craig Small: jqplot in Turbogears

I ve been working on the Rosenberg jqPlot GraphsNMS graphs slowly migrating them from using rrdtool graph and using jqplot. While there have been many false-starts and re-works, I now have a working set of graphs, two of which are shown on the page. The graphs look a lot slicker and I have also simplified the admin screens. I found I kept having to type the same thing in over and over for the rrdgraphs and have narrowed down the type of graphs to approximately 5. They re certainly not bulletproof and need more testing but they re a good start. The graphs are based upon the ToscaWidgets2 series of widgets that then provide a nice handle for the jqPlot code. My graphs even have some hand-coded Javascript to give nice units on the Y axis.

MJ Ray: What s the current state of Windows Anti-Virus?

One of our co-op s clients asked me what I use for anti-virus at the moment and tips for what they should use on their Windows system. Well, flame me now, but I don t actually use any anti-virus at the moment: I rely on system security, firewalling and intrusion detection. The diversity of GNU/Linux software and I use some pretty odd stuff probably helps too. Even if I did want to run antivirus software, most of what s available for GNU is actually aimed at detecting and preventing transmission of Windows viruses. There are few real-world GNU viruses and fewer attack opportunities left open. Also, I prefer firewalling and fairly paranoid security settings because, like an antibiotic, an antivirus is only effective once the virus is already on your system somehow hopefully held in quarantine by the browser or email client and not actively malignant in the processor. There s quite a list at http://en.wikipedia.org/wiki/Comparison_of_antivirus_software#Microsoft_Windows but I expect most of the purchase-free proprietary ones (labelled as Free or Freemium but you usually pay by watching adverts) will try to sell you upgrades, as that s how their production is funded. If you don t mind doing such things, you can disable the ads in at least one of them The only very free ones I found were Immunet (also funded by upgrades not sure if it s actually Free and Open Source Software) and ClamWin (donation-funded) which both use the same scanning engine. If I had to use Microsoft Windows, I think I d probably use and donate to ClamWin, install the (altruism-funded I think) Clam Sentinel alongside it and be rather cautious about what I downloaded or used online. I m a bit worried that it doesn t do great in reviews, though. What do/would you do? I don t really know about paying for security. The only paid product I ve really seen has been Norton and that seemed no better than the ad-funded ones, still getting in the way and always trying to sell upgrades. It also irks me that there s this huge market just to fix fundamental defects in Microsoft s product. There s a Microsoft Security Essentials add-on listed on Wikipedia, but it does fairly badly in this PC Magazine review and do any of them do intrusion detection? And finally, if you do decide to download something new, I strongly suggest getting it from a trusted source and/or triple-checking the link with wikipedia, a magazine review like CNET and a search engine. Don t just trust a search engine, because fake antivirus software is a big way of getting viruses and worse onto computers: there s even one calling itself Microsoft Security Essentials 2011 !

19 June 2013

Daniel Pocock: Australia's war on brains (and immigration)

Some weeks ago, our Prime Minister was slashdotted when she suspended her usual racist attacks on refugees to attack foreign IT workers and the companies that employ them with absurd accusations of "rorts" and "stealing" jobs. Today, she's introduced new laws in the parliament aiming to further bastardization of intelligent, skilled and educated workers and anybody who associates with them, including Australian employers. Unwarranted attention on a minority of IT workers This is not just some random bill before the parliament. There are just two weeks left before the parliament concludes and an election campaign begins. It is clear that what we are seeing now is the Real Julia coming though, choosing to make the small minority of foreign workers in our country at the center of people's thoughts as they go to vote in September. A debt of gratitude to foreign workers These verses from our national anthem, Advance Australia Fair say a lot about how Australia became what it is today:
For those who've come across the seas

We've boundless plains to share;

With courage let us all combine

To Advance Australia Fair.
The last 200 years of Australia's history has been a story of immigration. It is not something to be afraid of: our forefathers celebrated it. Foreign workers: why Australia needs you Australia has had some appalling flops in IT and engineering: There is no doubt in my mind that additional foreign workers would have made a positive contribution to all of these problems or can do so in the future. The sun never sets on IT Every day, I collaborate with dozens of IT specialists all over the world through the virtual workplace that is the Internet, particularly in the free and open source software community. Many of these people, I've never even met and in most cases I don't even know where they are, where they were born or what is the colour of their skin. Those details wouldn't make any difference to the way that we work in IT today. How many IT managers have time to waste dealing with more real world bureaucracy when they've experienced online, global productivity? How many IT workers feel demotivated by having to explain trivial details about their personal life to a Government bureaucrat who doesn't understand their skills and just looks at their colour? If you think about it, any immigration officer who really understands IT wouldn't be an immigration officer. They would be working in IT themselves. Immigration officers, who don't understand IT, are now going to be further empowered to bully companies away from employing some talented workers on the basis of race or nationality. Hiring managers will be intimidated into these prejudiced and biased decisions by delays, processing fees and invasive demands for sensitive documents about business planning and recruitment strategies. Australia's immigration system already has a horrendous reputation. Any visa application seems to take more than a year: no small company can keep a job position vacant that long. Families can't plan their children's schooling. Other life events come and go. There are exhorbitant fees, 1000% higher than in other western countries. Fewer and fewer self-respecting skilled workers are willing to put their spouses and children through the degrading medical examinations. Judging the impact of poor immigration policy While the economic impact of this immigration mess on industry is hard to quantify with an exact figure, we can take some insight from the education system. As the visa system has been hijacked by racists over the last 10 years, there has been a dramatic fall in participation (and revenues) from foreign students. In one year, enrolments (and revenue) fell 30%. This is not just bad for the balance sheets of the universities, it also means that in a future where commerce is global, Australians are more and more isolated and inexperienced culturally. IT workers and their employers have plenty of choices: Australia's close neighbor, Singapore, is one of them. Visas are granted in 2 weeks, no degrading medical exam required, low taxes and tropical sunshine all year round. Many companies that find it impractical to deal with Australia's bureaucracy end up moving their best Australian workers to places like Singapore to be part of a global team. This can't be good for the workforce that is left behind without jobs. The training delusion Government officials continue to rant and rave about companies failing to train Australian workers. The new laws supposedly force companies to "fix" this problem and train Australian workers. This, too, is a delusion: employers are not to blame. Some of the best Australian workers are already long gone to places like Singapore, London and the US. With talented foreign workers denied the opportunity to come and fill the void, there is less opportunity for skills to be acquired by more junior workers in Australian workplaces. It is also extremely difficult for more junior workers to get a foot in the door in the international job market and the primary reason for this is the Australian Government's failure to fund university programs beyond a bachelor's degree. Compare this to Europe and the US where all competent graduates are funded through to a Masters or PhD program. The bottom line is that more junior workers are denied the opportunity to get the best training either at home or abroad and in both cases it's not the foreign workers that can be blamed: it's the Government's own fault. Why do we need skilled foreign workers when Australians can win Nobel Prizes? The Australian press recently went into a frenzy when an Australian won the Nobel Prize for physics. There was a catch though: he's a migrant from the United States (just don't tell the Prime Minister). Dr. Schmidt migrated to Australia 20 years ago when the immigration system was not the same as today. Today, future Nobel Prize winners are being shown a brick wall - maybe we even have one of them rotting away in our death camps or left in the sea for sharks to eat. The BBC recently revealed that Britain's successor to Stephen Hawking may be a young girl who migrated from India - it is chilling to imagine where a child like this may be hidden away under Australia's immigration system. Bureaucracy leads to fraud and exploitation It's been clearly demonstrated that wherever you have elaborate, artificial systems of bureaucracy it leads to inefficiency, it suppresses innovation and in the worst cases it enables fraud and exploitation. The typical examples usually involve police in some third-world African nation setting up road blocks and collecting fees from travellers who want to pass the queues. This type of opportunism has also been found in Australia's immigration system, with one Federal politician already directly implicated and jailed for his role in a visa racket. Gillard's own bullet man A Queensland pensioner made international headlines recently when he was caught sending bullets in the mail to the Prime Minister. His demands were clear: stop immigration. While most world leaders refuse to let nutcases like this dictate their actions, Gillard appears to have been transcribing his racist letters directly into these newest immigration laws. It is a sad reality that Australian politics regularly seeks to appeal to the worst instincts in people like bullet man. The ultimate political failure When politicians stoop to the level of demonizing immigrants it is usually a clue that the politicians themselves are past their use-by dates and out of fresh policy ideas. When former French president Sarkozy tried to play the racist card in his campaign for re-election, it bit him in the bum and he was swept from power by the socialists. As always in politics, there is an element of hypocrisy at work: neither our Head of Government (the Prime Minister) nor our Head of State (the Queen) was born in Australia. Gillard was born in Wales and migrated to Australia as a child. If Australians don't vote for her in September, will she be given 28 days notice to pack her bags and go back home'? From the frying pan and into the fire Tony Abbott, Australia's would-be Prime Minister contemplating his colleague's statements on bestiality The scariest thing is that if Australians see through this racist charade and refuse to vote for it, we could end up with something equally obnoxious: the other major political party is now gaining worldwide attention for their campaign linking gay marriage and homosexuals to bestiality. Which prejudice is the lesser evil: racism or homophobia?
18 June 2013

Daniel Pocock: RSA Key Sizes: 2048 or 4096 bits?

Many people are taking a fresh look at IT security strategies in the wake of the NSA revelations. One of the issues that comes up is the need for stronger encryption, using public key cryptography instead of just passwords. This is sometimes referred to as certificate authentication, but certificates are just one of many ways to use public key technology. One of the core decisions in this field is the key size. Most people have heard that 1024 bit RSA keys have been cracked and are not used any more for web sites or PGP. The next most fashionable number after 1024 appears to be 2048, but a lot of people have also been skipping that and moving to 4096 bit keys. This has lead to some confusion as people try to make decisions about which smartcards to use, which type of CA certificate to use, etc. The discussion here is exclusively about RSA key pairs, although the concepts are similar for other algorithms (although key lengths are not equivalent) The case for using 2048 bits instead of 4096 bits
  • Some hardware (many smart cards, some card readers, and some other devices such as Polycom phones) don't support anything bigger than 2048 bits.
  • Uses less CPU than a longer key during encryption and authentication
  • Using less CPU means using less battery power (important for mobile devices)
  • Uses less storage space: while not an issue on disk, this can be an issue in small devices like smart cards that measure their RAM in kilobytes rather than gigabytes
So there are some clear benefits of using 2048 bit keys and not just jumping on the 4096 bit key bandwagon The case for using 4096 bits
  • For some types of attack, security is not just double, it is exponential. 4096 is significantly more secure in this scenario. If an attack is found that allows a 2048 bit key to be hacked in 100 hours, that does not imply that a 4096 bit key can be hacked in 200 hours. The hack that breaks a 2048 bit key in 100 hours may still need many years to crack a single 4096 bit key
  • Some types of key (e.g. an OpenPGP primary key which is signed by many other people) are desirable to keep for an extended period of time, perhaps 10 years or more. In this context, the hassle of replacing all those signatures may be quite high and it is more desirable to have a long-term future-proof key length.
The myth of certificate expiration Many types of public key cryptography, such as X.509, offer an expiry feature. This is not just a scheme to force you to go back to the certificate authority and pay more money every 12 months. It provides a kind of weak safety net in the case where somebody is secretly using an unauthorised copy of the key or a certificate that the CA issued to an imposter. However, the expiry doesn't eliminate future algorithmic compromises. If, in the future, an attacker succeeds in finding a shortcut to break 2048 bit keys, then they would presumably crack the root certificate as easily as they crack the server certificates and then, using their shiny new root key, they would be in a position to issue new server certificates with extended expiry dates. Therefore, the expiry feature alone doesn't protect against abuse of the key in the distant future. It does provide some value though: forcing people to renew certificates periodically allows the industry to bring in new minimum key length standards from time to time. In practical terms, content signed with a 2048 bit key today will not be valid indefinitely. Imagine in the year 2040 you want to try out a copy of some code you released with a digital signature in 2013. In 2040, that signature may not be trustworthy: most software in that era would probably see the key and tell you there is no way you can trust it. The NIST speculates that 2048 bit keys will be valid up to about the year 2030, so that implies that any code you sign with a 2048 bit key today will have to be resigned with a longer key in the year 2029. You would do that re-signing in the 2048 bit twilight period while you still trust the old signature. Fortunately, there are likely to be few projects where such old code will be in demand. 4096 in practice One of the reasons I decided to write this blog is the fact that some organisations have made the 4096 bit keys very prominent (although nobody has made them mandatory as far as I am aware). Debian's guide to key creation currently recommends 4096 bit keys (although it doesn't explicitly mandate their use) Fedora's archive keys are all 4096 bit keys. The CACert.org project has developed a 4096 bit root These developments may leave people feeling a little bit naked if they have to use a shorter 2048 bit key for any of the reasons suggested above (e.g. for wider choice of smart cards and compatibility with readers). It has also resulted in some people spending time looking for 4096 bit smart cards and compatible readers when they may be better off just using 2048 bits and investing their time in other security improvements. In fact, the "risk" of using only 2048 rather than 4096 bits in the smartcard may well be far outweighed by the benefits of hardware security (especially if a smartcard reader with pin-pad is used) My own conclusion is that 2048 is not a dead duck and using this key length remains a valid decision and is very likely to remain so for the next 5 years at least. The US NIST makes a similar recommendation and suggests it will be safe until 2030, although it is the minimum key length they have recommended. My feeling is that the Debian preference for 4096 bit PGP keys is not based solely on security, rather, it is also influenced by the fact that Debian is a project run by volunteers. Given this background, there is a perception that if everybody migrates from 1024 to 2048, then there would be another big migration effort to move all users from 2048 to 4096 and that those two migrations could be combined into a single effort going directly from 1024 to 4096, reducing the future workload of the volunteers who maintain the keyrings. This is a completely rational decision for administrative reasons, but it is not a decision that questions the security of using 2048 bit keys today. Therefore, people should not see Debian's preference to use 4096 bit keys as a hint that 2048 bit keys are fundamentally flawed. Unlike the Debian keys (which are user keys), the CACert.org roots and Fedora archive signing keys are centrally managed keys with a long lifetime and none of the benefits of using 2048 bit keys is a compelling factor in those use cases. Practical issues to consider when choosing key-length Therefore, the choice of using 2048 or 4096 is not pre-determined, and it can be balanced with a range of other decisions:
  • Key lifetime: is it a long life key, such as an X.509 root for an in-house CA or an OpenPGP primary key? Or is it just for a HTTPS web server or some other TLS server that can be replaced every two years?
  • Is it for a dedicated application (e.g. a closed user group all using the same software supporting 4096 bit) or is it for a widespread user base where some users need to use 2048 bit due to old software/hardware?
  • Is it necessary to use the key(s) in a wide variety of smartcard readers?
  • Is it a mobile application (where battery must be conserved) or a server that is likely to experience heavy load?

Tollef Fog Heen: An otter, please (or, a better notification system)

Recently, there's been discussions on IRC and the debian-devel mailing list about how to notify users, typically from a cron script or a system daemon needing to tell the user their hard drive is about to expire. The current way is generally "send email to root" and for some bits "pop up a notification bubble, hoping the user will see it". Emailing me means I get far too many notifications. They're often not actionable (apt-get update failed two days ago) and they're not aggregated. I think we need a system that at its core has level and edge triggers and some way of doing flap detection. Level interrupts means "tell me if a disk is full right now". Edge means "tell me if the checksums have changed, even if they now look ok". Flap detection means "tell me if the nightly apt-get update fails more often than once a week". It would be useful if it could extrapolate some notifications too, so it could tell me "your disk is going to be full in $period unless you add more space". The system needs to be able to take in input in a variety of formats: syslog, unstructured output from cron scripts (including their exit codes), snmp, nagios notifications, sockets and fifos and so on. Based on those inputs and any correlations it can pull out of it, it should try to reason about what's happening on the system. If the conclusion there is "something is broken", it should see if it's something that it can reasonably fix by itself. If so, fix it and record it (so it can be used for notification if appropriate: I want to be told if you restart apache every two minutes). If it can't fix it, notify the admin. It should also group similar messages so a single important message doesn't drown in a million unimportant ones. Ideally, this should be cross-host aggregation. The notifications should be possible to escalate if they're not handled within some time period. I'm not aware of such a tool. Maybe one could be rigged together by careful application of logstash, nagios, munin/ganglia/something and sentry. If anybody knows of such a tool, let me know, or if you're working on one, also please let me know.

17 June 2013

Tanguy Ortolo: Encryption without a certification layer is (partly) useless

With the PRISM scandal, there has been some talk about encrypted communication systems. For instance, BitMessage is often introduced as an easy and secure message system, that would allow you to communicate with no possible eavesdropping. Apple is also making similar claims about their systems iMessage and FaceTime. This is a good time to remind this: without direct contact or a certification layer, encryption systems are not secure! Or at least, not as secure as you would expect, as they do allow some kind of eavesdropping.Let us take the example of BitMessage:
  1. Alice sends her BitMessage address to Bob by email, an insecure channel;
  2. Mallory catches that email message and changes Alice's BitMessage address with his own;
  3. Bob sends a BitMessage for Alice to the address he received, which he thinks is Alice's, but is in fact Mallory's;
  4. Mallory receives the message, reads it, modifies it if he wants, and sends it to Alice.
This is a man-in-the-middle attack, a kind of active eavesdropping technique that requires read-modify access to a communication line. Without a specific way to ensure that a cryptographic key really belongs to its alleged owner, a cryptographic system is vulnerable to such attacks, even if it does protect against simpler attacks (like passive eavesdropping or introduction of MiTM after the introduction sequence). When you read that a cryptographic system provides end-to-end security and is impervious to eavesdropping, while it provides no mean to make sure you are in contact to the right person, remember to consider this affirmation as what it is: a lie.

John Sullivan: M-x spook

In light of the recent leaks about the NSA's illegal spying, I've decided to go back to using M-x spook output in my email signatures. cypherpunk anthrax John Kerry rail gun security plutonium Guantanamo wire transfer JPL number key military MD5 SRI FIPS140 Uzbekistan

Gunnar Wolf: Cultural objects/goods: When a superhero is too famous for his own good

I found the following news item; if you can read Spanish, you will most probably prefer the original version in the Proceso magazine's site. The subject? The federal police (PGR) and army arrest 17 artisans for making money out of Spiderman. The following translation is mine. Done past midnight, and being quite tired, and translated so this news item can reach a broader audience. All errors are mine (except those carried out by the security forces, that is).
June 13, 2013 Cuernavaca, Morelos. Policement from the General Republic Attorney (Procuradur a General de la Rep blica, PGR) and the Army entered and searched the "3 de mayo" neighbourhood, in the municipality of Emiliano Zapata, detaining 17 ceramist artisans that sold candies, dolls and pi atas shaped like Spiderman. This search was done on the evening of last Wednesday, around 16:00. Federal ministerial policement and army soldiers closed a street with several informal stores and detained workers taht were selling this Marvel Comics character, following said company's denounce. As a result for this operation, 17 artisants were detained, although the same day five of them were freed. The policemen also seized 12 bags of candies, pi atas, ceramics and wooden figures of the superhero. PGR closed down 11 stores where ceramics with this same figure was being sold, accusing the detainees of plagiarizing Spiderman's image, protected under the copyright law. The 12 that remained under detention were put at the Federal Justice's disposal, which prompted that this Thursday, around 10AM, hundreds of sellers of "3 de mayo" went out to PGR's building to demand their friends' freedom, who are facing a bail of up to 200,000 pesos (~USD$18,000). Outraged because they said they were treated as if they were part of a drug ring, hundreds of artisans closed intermitently Avenida Cuauhn huac, where the PGR representation in Morelos state is located. The artisans' pressure helped for the amount of the bail to be lowered from MX$200,000 to MX$16,000, and so they were set free. Francisco Fern ndez Flores, president of the Ceramists Association, criticized the operation because, he said, it was as strong as if they were "drug dealers". The artisans explained that they don't even make the Spiderman figures, they are made by the interns of the Centro Estatal de Reinserci n Social de Atlacholoaya (prision), located in the Xochitepec municipality, who offered them to the ceramists so they could be sold. "The Atlacholoaya inmates do them, we buy them to support them, and turns out we are the delinquents now", said Miriam Monroy, sister of one of the detainees. This information was contradicted by Jes s Valencia Valencia, responsible for Morelos' state prision system, who assured that in said prision no ceramics are done. Fern ndez Flores insisted though that from within the prision they are being offered pi atas, candies and "piggy banks" with Spiderman's shape. Jos Luis Pozo, vicepresident of the Ceramists Union, said that to avoid more such federal operations for copyright breaches, they have committed not to produce or commercialize Marvel superhero figures, and any other characters the authority demands. "We do commit to, from now on, those products singled out to us will not be commercialized", he said. Pozo said that the PGR operation caused losses not just to the detained producers and salesmen, but to over 200 ceramists that had to close their stores in solidarity with their friends. Acording to the artisans, the products were a success until the PGR came, seized the products and detained the salesmen.
And yes, the copyright insanity does not stop. Spiderman is by today a clear part of popular culture. Marvel brilliantly succeeded in creating such a popular icon that everybody recognizes, that everybody identifies with And that everybody should be able to recreate. We are not talking about brand protection. Marvel does not, and will never, commercialize pi atas, ceramics or wooden toys. And even if they were plastic-cast While Spiderman is still under the protection of copyright, as the Berne Convention defines it (and of course, as the much stricter Mexican laws agree), that does not mean that any and every product resembling a Spiderman should be protected. Many ceramists and pi ata makers will create unique pieces of art Ok, handicraft. But reading the copyright law more strictly, Spiderman is more treated as a trademark than as a copyright. And it is a trademark that should be declared as having passed on to the public domain.

15 June 2013

Daniel Pocock: Girls Around Me and the NSA

When the Girls Around Me app was released in 2012, it received massive criticism on the basis that it could enable stalking and undermine privacy. Nonetheless, the existence of this app may well be an even bigger problem for the NSA right now than it is for single women. US Government officials in damage control mode over the NSA surveillance leaks have sought to deny that it is even possible to monitor people in the way that The Guardian reported the matter. Leaders of Internet giants such as Google and Facebook have also tried to deny and downplay the possibilities of PRISM. In my view, a company like Google is no more likely to admit hiving off customer data than a bank is likely to admit a liquidity crisis, for fear of starting a self-fulfulling bank run. User trust is as existential with data as it is with bank deposits. So my question is, if the NSA with an $8 billion annual budget can't track people in real-time, how come a small team of app developers could do much the same thing so easily in Girls Around Me? One possibility is that some companies may be accurate in what they have reported: they are not letting data out the back door. The scary thing is, they are letting it out the front door and it is just as possible for third-party commercial operators and foreign powers to harvest a lot of this data in the same way as Girls Around Me In one of the most remarkable cases, the chief of British MI6 (the team that James Bond plays for) may have been compromised by his wife's Facebook posts - if Facebook really is an outsourced NSA operation, then that is a remarkable case of friendly fire Both the scandals around Girls Around Me and the NSA spying leaks only serve to confirm one thing: that people need to think twice every time they fill in some form or submit some data that could be used to identify or track them.
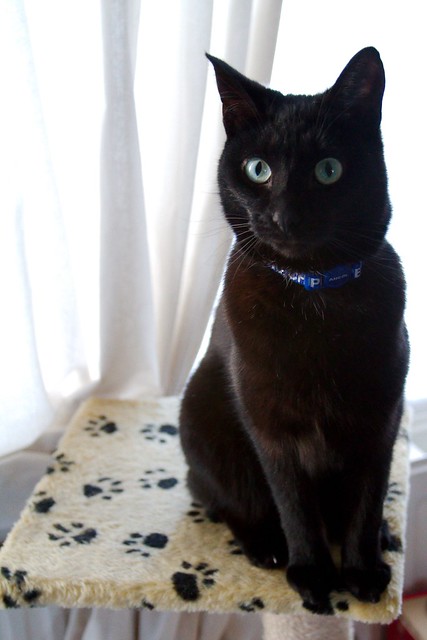
Next.

Previous.