Search Results: "tar"

29 January 2017

Sam Hartman: Network Audio Visualization: Network Modeling

Previously, I wrote about my project to create an audio depiction of network traffic. In this second post, I explore how I model aspects of the network that will be captured in the audio representation. Before getting started, I'll pass along a link. This is not the first time someone has tried to put sound to packets flying through the ether: I was pointed at Peep. I haven't looked at Peep, but will do so after I finish my own write up. Not being an academic, I feel no obligation to compare and contrast my work to others:-)
I started with an idea of what I'd like to hear. One of my motivations was to explore some automated updates we run at work. So, I was hoping to capture the initial DNS and ARP traffic as the update discovered the systems it would contact. Then I was hoping to capture the ssh and other traffic of the actual update.
To Packet or Stream
One of the simplest things to do would simply be to model network packets. For DNS I chose that approach. I was dubious that a packet-based model would capture the aspects of TCP streams I typically care about. I care about the source and destination (both address and port) of course. However I also care about how much traffic is being carried over the stream and the condition of the stream. Are there retransmits? Are there a bunch of unanswered SYNs? But I don't care about the actual distribution of packets. Also, a busy TCP stream can generate thousands of packets a second. I doubted my ability to distinguish thousands of sounds a second at all, especially while trying to convey enough information to carry stream characteristics like overall traffic volume.
So, for TCP, I decided to model some characteristics of streams rather than individual packets.
For DNS, I decided to represent individual requests/replies.
I came up with something clever for ARPP. There, I model the request/reply as an outstanding request. A lot of unanswered ARPs can be a sign of a scan or a significant problem. The mornful sound of a TCP stream trailing off into an unanswered ARP as the cache times out on a broken network is certainly something I'd like to capture. So, I track when an ARP request is sent and when/if it is answered.
Sound or Music
I saw two approaches. First, I could use some sound to represent streams. As an example, a running diesel engine could make a great representation of a stream. The engine speed could represent overall traffic flow. There are many opportunities for detuning the engine to represent various problems that can happen with a stream. Perhaps using stereo separation and slightly different fundamental frequencies I could even represent a couple of streams and still be able to track them.
However, at least with me as a listener, that's not going to scale to a busy network. The other option I saw was to try and create melodic music with various musical phrases modified as conditions within the stream or network changed. That seemed a lot harder to do, but humans are good at listening to complicated music.
I ended up deciding that at least for the TCP streams, I was going to try and produce something more musical than sound. I was nervous: I kept having visions of a performance of "Peter and the Wolf" with different instruments representing all the characters that somehow went dreadfully wrong.
As an aside, the decision to approach music rather than sound depended heavily on what I was trying to capture. If I'm modeling more holistic properties of a system--for example, total network traffic without splitting into streams--I think parameterized sounds would be a better approach.
The decision to approach things musically affected the rest of the modeling. Somehow I was going to need to figure out notes to play. I'd already rejected the idea of modeling packets, so I wouldn't simply be able to play notes when a packet arrived.
Energy Decay
As I played with various options, I realized that the critical challenge would be figuring out how to focus the listener's attention on the important aspects of what was going on. Clutter was the great enemy. My job would be figuring out how to spend sound wisely. When something interesting happened, that part of the model should get more focus--more of the listener's energy.
Soon I found myself thinking a lot about managing the energy of network streams. I imagined streams getting energy when something happened, and spending that energy to convey that interesting event to the listener. Energy needed to accumulate fast enough that even low-traffic streams could be noticed. Energy needed to be spent fast enough that old events were not taking listener focus from new, interesting things going on. However, if the energy were spent slow enough, then network events could be smoothed out to give a better picture of the stream rather than individual packets.
This concept of managing some decaying quantity and managing the rate of decay proved useful at multiple levels of the model.
Two Layer Model
I started with a python script that parses tcpdump output. It associates a packet with a stream and batches packets together to avoid overloading other parts of the system.
The output of this script are stream events. Events include a source and destination address, a stream ID, traffic in each direction, and any special events on the stream.
For DNS, the script just outputs packet events. For ARP, the script outputs request start, reply, and timeout events. There's some initial support for UDP, but so far that doesn't make sound.
Right now, FINs are modeled, but SYNs and the interesting TCP conditions aren't directly modeled. If you get retransmissions you'll notice because packet flow will decrease. However, I'd love to explicitly sound retransmissions. I also think a window filling as an application fails to read is important. I imagine either narrowing a band-pass filter to clamp the audio bandwidth available to a stream with a full window. Or perhaps taking it the other direction and adding an echo.
The next layer down tracks the energy of each stream. But that, and how I map energy into music, is the topic of the next post.

Reproducible builds folks: Reproducible Builds: week 91 in Stretch cycle

What happened in the Reproducible Builds effort between Sunday January 15 and Saturday January 21 2017: Media Coverage Upcoming Events Toolchain development and fixes Ximin Luo continued work on data formats, code, and test cases for SOURCE_PREFIX_MAP. He also continued to talk with the rustc team on the topic. Chris Lamb submitted a patch to implement SOURCE_DATE_EPOCH for wordwarvi, a game which gave extra points to people who built it from source within one hour. This fixes Debian #786593. Launchpad bug 1657704 was filed for them to start accepting buildinfo files. Bugs filed Reviews of unreproducible packages 10 package reviews have been added, 149 have been updated and 153 have been removed in this week, adding to our knowledge about identified issues. 2 issue types have been updated: Weekly QA work During our reproducibility testing, the following FTBFS bugs have been detected and reported by: diffoscope development diffoscope 69 was uploaded to unstable by Chris Lamb. It included contributions from: Further development continued in Git, and will be released as version 70 next week: reproducible-builds.org website development tests.reproducible-builds.org Misc. This week's edition was written by Ximin Luo, Vagrant Cascadian, Holger Levsen & Chris Lamb and reviewed by a bunch of Reproducible Builds folks on IRC & the mailing lists.

Elena 'valhalla' Grandi: Preseeding a debian installation on a libreboot computer

Preseeding a debian installation on a libreboot computer

Preseeding a debian installation from the standard installer is as easy as pressing ESC at the right time and pointing it to the url of your preseed file https://wiki.debian.org/DebianInstaller/Preseed#Loading_the_preseeding_file_from_a_webserver, right?

It is, except when you're using libreboot, and you never pass through that right time , because you are skipping the installer's grub.

So, for future reference, here is the right incantation to use at the command line that you get by pressing c at the libreboot menu:


linux (usb0)/install.amd/vmlinuz auto=true url=http://webserver/path/preseed.cfg
initrd (usb0)/install.amd/initrx
boot


simple, once you've found it...

(ok, it took me less than one hour, but I don't want it to take another hour the next time)

#coreboot #libreboot #debian #preseed

Elena 'valhalla' Grandi: One Liberated Laptop

One Liberated Laptop

Immagine/fotohttp://social.gl-como.it/photos/valhalla/image/5a480cd2d5842101fc8975d927d030f3

After many days of failed attempts, yesterday @Diego Roversi finally managed to setup SPI on the BeagleBone White , and that means that today at our home it was Laptop Liberation Day!

We took the spare X200, opened it, found the point we were on in the tutorial installing libreboot on x200 https://libreboot.org/docs/install/x200_external.html, connected all of the proper cables on the clip and did some reading tests of the original bios.

Immagine/fotohttp://social.gl-como.it/photos/valhalla/image/77e61745d9c43833b7c0a4a919d17222

While the tutorial mentioned a very conservative setting (512kHz), just for fun we tried to read it at different speed and all results up to 16384 kHz were equal, with the first failure at 32784 kHz, so we settled on using 8192 kHz.

Then it was time to customize our libreboot image with the right MAC address, and that's when we realized that the sheet of paper where we had written it down the last time had been put in a safe place somewhere

Luckily we also had taken a picture, and that was easier to find, so we checked the keyboard map , followed the instructions to customize the image https://libreboot.org/docs/hcl/gm45_remove_me.html#ich9gen, flashed the chip, partially reassembled the laptop, started it up and a black screen, some fan noise and nothing else.

We tried to reflash the chip (nothing was changed), tried the us keyboard image, in case it was the better tested one (same results) and reflashed the original bios, just to check that the laptop was still working (it was).

It was lunchtime, so we stopped our attempts. As soon as we started eating, however, we realized that this laptop came with 3GB of RAM, and that surely meant "no matching pairs of RAM", so just after lunch we reflashed the first image, removed one dimm, rebooted and finally saw a gnu-hugging penguin!

We then tried booting some random live usb key https://tails.boum.org/ we had around (failed the first time, worked the second and further one with no changes), and then proceeded to install Debian.

Running the installer required some attempts and a bit of duckduckgoing: parsing the isolinux / grub configurations from the libreboot menu didn't work, but in the end it was as easy as going to the command line and running:


linux (usb0)/install.amd/vmlinuz
initrd (usb0)/install.amd/initrd.gz
boot


From there on, it was the usual debian installation and a well know environment, and there were no surprises. I've noticed that grub-coreboot is not installed (grub-pc is) and I want to investigate a bit, but rebooting worked out of the box with no issue.

Next step will be liberating my own X200 laptop, and then if you are around the @Gruppo Linux Como area and need a 16 pin clip let us know and we may bring everything to one of the LUG meetings

yes, white, and most of the instructions on the interwebz talk about the black, which is extremely similar to the white except where it isn't

wait? there are keyboard maps? doesn't everybody just use the us one regardless of what is printed on the keys? Do I *live* with somebody who doesn't? :D

the breadboard in the picture is only there for the power supply, the chip on it is a cheap SPI flash used to test SPI on the bone without risking the laptop :)

disclaimer: it worked for us. it may not work on *your* laptop. it may brick it. it may invoke a tentacled monster, it may bind your firstborn son to a life of servitude to some supernatural being. Whatever happens, it's not our fault.

(edit: added tags)

#coreboot #libreboot

28 January 2017

Sven Hoexter: Am I a target now?

While reading the Tails 2.10 changelog I stumbled upon the fact that Tails now supports exFAT. Since Tails is Debian based I just checked the image and indeed it contains the fuse-exfat package. Do I've to assume that I've now another set of crosshairs on my back just because it's one possible maintainer you could attack to place malicious code into Tails? I'm not sure, and I'm also not sure if it would change much. I've always assumed to be a target just because I'm contributing to Debian, and because I'm working in IT operations. But to be honest so far my contributions to Debian are not on crucial packages and unexpected strange looking NMUs would always raise alarm bells for everyone. BTW the exfat fuse driver package builds reproducible. Maybe a good opportunity to thank the reproducible build team for this effort!

Steve Kemp: So I've been playing with hardware

At the end of December I decided I was going to do hardware "things", and so far that has worked out pretty well. One of the reasons I decided to play with Arduinos is that I assumed I could avoid all forms of soldering. I've done soldering often enough to know I can manage it, but not quite often enough that I feel comfortable doing so. Unfortunately soldering has become a part of my life once again, as too many of the things I've been playing with have required pins soldering to them before I can connect them. Soldering aside I've been having fun, and I have deployed several "real" projects in and around my flat. Perhaps the most interesting project shows the arrival time of the next tram to arrive at the end of my street: That's simple, reliable, and useful. I have another project which needs to be documented which combineds a WeMos D1 and a vibration sensor - no sniggers - to generate an alert when the washing machine is done. Having a newborn baby around the place means that we have a lot of laundry to manage, and we keep forgetting that we've turned the washing machine on. Oops. Anyway. Hardware. More fun than I expected. I've even started ordering more components for bigger projects. I'll continue to document the various projects online, mostly to make sure I remember the basics:

27 January 2017

Rhonda D'Vine: Icona Pop

Last fall I went to a Silent Disco event. You get wireless headphones, a DJane and a DJ were playing music on different channels, and you enjoy the time with people around who can't hear what you hear. It's a pretty funny experience, and it was one of the last warm sunny days. There I heard a song that was just in the mood for the moment, and made me looking up the band to listen more closely to them. The band was Icona Pop, they have a mood enlighening pop sound that cheers you up. Here are the songs I want to present you today: Like always, enjoy!

/music permanent link Comments: 4 Flattr this

Michal Čihař: stardicter 0.11

Stardicter 0.11, the set of scripts to convert some freely available dictionaries to StarDict format, has been released today. There are mostly minor changes and it's time to push them out in official release. The most important being fixed sorting of ascii dictionaries, what did break searching in some programs. Full list of changes: As usual, you can install from pip, download source or download generated dictionaries from my website.

Filed under: Debian English StarDict SUSE 0 comments

Russ Allbery: Review: Summer in Orcus

Review: Summer in Orcus, by T. Kingfisher
Publisher: Red Wombat Studio
Copyright: 2016
ASIN: B01N26G2I0
Format: Web serial
Pages: 268
In September, Ursula Vernon started posting Summer in Orcus as a web serial, funded by her Patreon supporters. The entire story is now complete and available on-line for free, which is how I read it, but it's also available as an ebook from the expected places if you prefer to read it that way. The ebook publication lists T. Kingfisher as the author, Vernon's pen name for her books for adults. While I would have been happy to read this book as a kid, it does have one fairly gruesome chapter, which is probably the reason for that choice. Summer is eleven, and her mother loves her very much. So much so that she's never allowed to do anything even slightly risky, and she spends quite a lot of her time and emotional energy reassuring her mother, dealing with the burden of that suffocating love, and helping her through her bad days. Then, one day, a house with giant chicken feet walks into the alley behind her house. Summer in Orcus is a portal fantasy. It's the story of how Summer meets Baba Yaga and asks for her heart's desire, finds herself in the magical country of Orcus, and is desperately moved by the plight of a frog tree. It has a talking weasel and a werehouse and antelope women who are not to be trusted, and it's about Summer making friends her mother would never have approved of and learning what she's capable of, and about doing what one can to put things right. Even though it may appear that way at times, Summer in Orcus is not really a book about large things. It's not a saving the world sort of portal fantasy. And it's not really a wish fulfillment portal fantasy, because heart's desires are complicated and subtle. It's a story about being scared and tired and lost, and about making friends, and doing the things one can do rather than learning how to be a completely different person. The plot itself is not particularly complex, but the joy of this story is in all the small things. Vernon's writing is an absolute delight. Summer in Orcus is packed with sentences and paragraphs that I just want to read again and again and quote at people.
Summer had never had a father, and wasn t entirely sure what you did with one, and certainly her mother never had anything good to say about the one Summer didn t have.
Or:
The house lifted its back end up and inched forward a little, like a dog wanting to play. This must have made the floors tilt inside, because Summer heard a banging and sliding of furniture and Baba Yaga yelled, "Fool house! I ll trade you in for one with turtle feet and a three-car garage!" The house sank back down, but wiggled forward a little more, until the front door was only a few feet away.
Vernon mentions in her author notes at the end that Summer in Orcus started as a place to put a whole bunch of fragmentary ideas that she'd come up with but that didn't seem to fit into other stories, and it does have a bit of a grand tour feel to it. But unlike a lot of grand tour figures, the protagonist is not at all bland. Summer is entirely believable and very sympathetic, torn between wanting a grand adventure and being afraid of circumstance and danger entirely outside of her limited experience. She channels the reader's awe and delight, but is still very much her own person, trying to figure out who she wants to be and believe in without the stifling presence of her mother. The tour nature of the story does mean that some things weren't explored as deeply as I would have liked. I would dearly love to read more about the dogs, for instance. I also have to admit that Zultan's motives never made sense to me, even after they were explained, and I found him an odd and weirdly random character to the end. But Glorious is, well, glorious, and I utterly adored the bits with the Forester. The ending is highly unusual for a story of this sort, and I thought it was wonderful, with a great symbolic tie back to the start of the story. The aftermath is even better, including Summer standing firm against one of the tropes of portal fantasies that I dislike the most. This is a great story, with some excellent writing. If you're anything like me, once you read the first chapter you won't want to stop (and since it's all available on the web for free, there's no reason to stop). Recommended. Rating: 8 out of 10

Iustin Pop: Languages, part 1

Human languages, part 1 I do enjoy writing blog posts, but sometimes time is lacking, other times inspiration. As I was eating dinner today, I was lost in thoughts and my eyes stopped on the documentation from a certain medication for coughing (the thing almost noone reads, like EULAs). I was surprised quite surprised with te text that I said well, some blog posts on languages might be interesting . Background: My mother tongue is Romanian. While growing up and learning foreign languages, I considered only the utilitarian aspect of languages, but as I get older (not old, older! ), I find human languages more and more interesting. Back to the subject: this being Switzerland, most everything is written in German, French and Italian (in this order of frequency). German is still a foreign language to me (let's say I get by, but not nicely), French is the fancy high class cousin, and Italian Well Italian is a special case. When I first saw Italian on TV (a newscast while travelling in Italy) I was shocked at how much one can understand without learning Italian in any way (much, much more than German after years of trying). So Italian language is quite close, and usually one understands a third to half; this is both spoken (less in common language, more in official language) and in writing. In this particular case, the instructions of use say (sorry for typos, manually copying):
In casi rarissimi possono manifestarsi reazioni di ipersensibilit grave con tumefazione del viso, difficolt respiratoria (dispnea) e diminuzione della pressione arteriosa.
What was surprising here was not the list of side effects (hah), but that this short phrase is 98% identical to the translation in Romanian; not only words, but also phrase structure. I don't think I've ever seen this before:
n cazuri rare se pot manifesta reac ii de hipersensibilitate grav cu tumefac ie a fe ei, dificultate respiratorie (dispnee) i diminuare a presiunii arteriale.
Not all the words are identical, but even the one that is obviously different (it. 'del viso', ro. 'a fe ei') is easily translatable as 'visiune' in Romanian means 'to see', so the link is clear. This phrase structure is also quite a natural way to say the things in Romanian. I was then curious to see the French version, which is:
Dans de tr s rares cas, [the medicine] peut d clencher de violentes r actions d'hypersensibilit s'accompagnant d'un gonflement du visage, de d tresse respiratorie e d'une chute de tension.
French is usually quite different from Romanian that one has to learn it (for quite a while, especially for grammar) in order to be proficient in it, but here you can make also word-by-word translation (transposition?) that doesn't lose the meaning:
n cazuri tare rari, [the medicime] poate declan a violente reac ii de hypersensibilitate acompaniate de o umflare a fe ei, de ???? respiratorie i de ???? a tensiunii.
Basically here we have two non-equivalent words, and a bit more wierd phrase structure it sounds more like coloquial speech than written language but for French is also surprisingly close. You'd invert some of the adjective-noun pairs (fr. 'violentes r actions' is understandable in Romanian as 'violente reac ii', but it sounds very poetical and you'd usually write it as 'reac ii violente'). The next phrase is no longer that similar, but the one after is again obviously identical:
Se osserva effetti collaterali qui non descritti, dovrebbe informare il suo medico, il suo farmacista o il suo drogerie.
which is:
[Dac /If] se observ effecte colaterale care nu sunt descrise, trebuie informat medicul vostru, farmacistul vostru sau [xxxx - no real equivalent].
And the French is also identical, modulo again 'droguiste':
Si vouz remarquez de effets secondaires qui ne sont pas mentionn s dans cette notice, veuillez en informer votre m decin, votre pharmacien ou votre droguiste.
which is:
Dac remarca i efecte secundare care nu sunt men ionate n aceast not , informa i medicul vostru, farmacistul vostru sau al vostru [xxxx].
This is even closer; 'votre' is more similar to '[al] vostru' than 'suo', and the phrase structure is much more natural - this is exactly how you'd write it in 'native' Romanian, whereas the Italian is not (I had to add the 'if' to make it parseable). The 'vous' in 'vouz remarquez' is 'voi' in Romanian, but doesn't need to be added as it would be redundant; but it doesn't confuse the phrase. The 'veuillez en informer' doesn't have a 1:1 translation (it would be written as 'v rug m s informa i'), but is still understandable; a false friend translation would be 'vede i s informa i'/see to inform/voir informer. Why is this all surprising? Because Romanian has a significant amount of words of Slavic origin (~11% in overall vocabulary, 15% in most commonly used 2500 words) and some from other nearby countries (Turkey, Greek, some Hungarian and German). At a stretch, it's even possible to write simple but complete sentences entirely with words from Slavic origin, as I learned from this interesting youtube video. Also, our accent is almost always confused with Russian, not with Italian or French. So to get to a summary: normally you see sentence elements that are similar or identical, but not entire sentences, and definitely not phrases. What made the three languages here keep, in this particular case, not only similar but almost identical words and also almost identical phrase structure? Is it the subject (medicine)? Maybe. Is it a random fluke? If so, I don't remember seeing it before. Do I just see similarities where there are none? Possibly , but at least I thought it worth mentioning; it was quite surprising to me. Did my brain get confused by too many languages and I misinterpreted words that don't really exist (e.g. I was sure that 'vizajul' is a Romanian word, but upon checking, it isn't )? Also possible. In any case, for me it was a good subject for a blog post. Now let's not go near Spanish and definitely not near Portuguese

26 January 2017

Martin Michlmayr: Debian on Jetson TX1

Debian is now working on the NVIDIA Jetson TX1 developer kit, a development board based on the Tegra X1 chip (Tegra 210), a 64-bit ARM chip. We have a pre-built u-boot image in Debian as well as kernel and installer support. There are some minor kernel glitches but NVIDIA is very active upstream and I hope they'll get resolved soon. The Jetson TX1 developer kit makes a pretty good 64-bit ARM development platform. The board is supported in mainline u-boot and the mainline kernel and NVIDIA are pretty responsive to bug reports. Unfortunately, a proprietary blob is required for USB (and Ethernet is connected via USB). If you're interested in a good 64-bit ARM development platform, give Debian on the Jetson TX1 development kit a try.

John Goerzen: What is happening to America?

I still remember vividly my first visit to Europe, back in 2010. I had just barely gotten off a plane in Hamburg and on to a bus to Lubeck, and struck up a conversation with a friendly, well-educated German classical musician next to me. We soon started to discuss politics and religion. Over the course of the conversation, in response to his questions, I explained I had twice voted against George W. Bush, that I opposed the war in Iraq for many reasons, that I did thought there was an ethical imperative to work to defeat climate change, that I viewed health care as an important ethical and religious issue, that I thought evolution was well-established, and that I am a Christian. Finally, without any hint of insult intended, and rather a lot of surprise written all over his face, he said: Wow. You re an American, and a Christian, and you re so . normal! This, it seems to me, has a lot to do with Trump. Ouch It felt like a punch to the gut. The day after the election, having known that a man that appeared to stand for everything that honorable people are against won the election, like people all around the world, I was trying to make sense of how could this happen? As I ve watched since, as he stacks government with wealthy cronies with records nearly as colorful as his own, it is easy to feel even more depressed. Based on how Trump spoke and acted, it would be easy to conclude that the deplorables won the day that he was elected by a contingent of sexists or racists ascendent in power. But that would be too simple an explanation. This is, after all, the same country that elected Barack Obama twice. There are a many people that voted twice for a black man, and then for Trump. Why? Racism, while doubtless a factor, can t explain it all. How Trump could happen Russ Allbery made some excellent points recently:
[Many Americans are] hurt, and they re scared, and they feel like a lot of the United States just slammed the door in their faces. The status quo is not working for people. Technocratic government by political elites is not working for people. Business as usual is not working for people. Minor tweaks to increasingly arcane systems is not working for people. People are feeling lost in bureaucracy, disaffected by elections that do not present a clear alternate vision, and depressed by a slow slide into increasingly dismal circumstances. Government is not doing what we want it to do for us. And people are getting left behind. The left in the United States (of which I m part) has for many years been very concerned about the way blacks and other racial minorities are systematically pushed to the margins of our economy, and how women are pushed out of leadership roles. Those problems are real. But the loss of jobs in the industrial heartland, the inability of a white, rural, working-class man to support his family the way his father supported him, the collapse of once-vibrant communities into poverty and despair: those problems are real too. The status quo is not working for anyone except for a few lucky, highly-educated people on the coasts. People, honestly, like me, and like many of the other (primarily white and male) people who work in tech. We are one of the few beneficiaries of a system that is failing the vast majority of people in this country.
Russ is, of course, right. The Democrats have been either complicit in policies damaging to many, or ineffective in preventing them. They have often appeared unconcerned with the plight of people outside cities (even if that wasn t really the case). And it goes deeper. When s the last time you visited Kansas? I live in Kansas. The nearest paved road is about a 3-mile drive from my home. The nearest town, population 600, is a 6-mile drive. My governor whom I did not vote for cut taxes on the wealthy so much that our excellent local schools have been struggling for years. But my community is amazing, full of loving and caring people, the sort of people who you know you ll be living with for 40 years, and so you make sure you get along well with. I have visited tourist sites in Berlin, enjoyed an opera and a Broadway show in New York, taken a train across the country to Portland, explored San Francisco. I ve enjoyed all of them. Many rural people do get out and experience the world. I have been in so many conversations where I try to explain where I live to people that simply cannot fathom it. I have explained how the 18 acres I own is a very small amount where I am. How, yes, I do actually have electricity and Internet. How a bad traffic day is one where I have to wait for three cars to go past before turning onto the paved road. How I occasionally find a bull in my front yard, how I can walk a quarter mile and be at the creek on the edge of my property, how I can get to an airport faster than most New Yorkers and my kids can walk out the front door and play in a spot more peaceful than Central Park, and how all this is way cheaper than a studio apartment in a bad part of San Francisco. It is rare indeed to see visitors actually traveling to Kansas as a destination. People have no concept of the fact that my mechanic would drop everything and help me get my broken-down car to the shop for no charge, that any number of neighbors or uncles would bring a tractor and come plow the snow off my 1/4-mile driveway out of sheer kindness, that people around here really care for each other in a way you don t see in a city. There are people that I know see politics way differently than me, but I know them to be good people. They would also do anything for a person in need, no matter who they are. I may find the people that they vote for to be repugnant, but I cannot say I ve looked this person in the eyes and they are nothing but deplorable. And so, people in rural areas feel misunderstood. And they are right. Some perspectives on Trump As I ve said, I do find Trump to be deplorable, but not everyone that voted for him is. How, then, do people wind up voting for him? The New Yorker had an excellent story about a man named Mark Frisbie, owner of a welding and fab shop. The recession had been hard on his business. His wife s day-care center also closed. Health care was hard to find, and the long, slow decline had spanned politicians of every stripe. Mark and his wife supposedly did everything they were supposed to: they worked hard, were honest, were entrepreneurial, and yet he had lost his business, his family house, his health coverage, everything. He doesn t want a handout. He wants to be able to earn a living. Asked who he d vote for, he said, Is none of the above an option? The Washington Post had another insightful article, about a professor from Madison, WI interviewing people in rural areas. She said people would often say: All the decisions are made in Madison and Milwaukee and nobody s listening to us. Nobody s paying attention, nobody s coming out here and asking us what we think. Decisions are made in the cities, and we have to abide by them. She pushed back, hard, on the idea that Trump supporters are ignorant, and added that liberals that push that line of thinking are only making the problem worse. I would agree; seeing all the talk about universities dis-inviting speakers that don t hew to certain political views doesn t help either. A related article talks about the lack of empathy for Trump voters. And then we have a more recent CNN article: Where Tump support and Obamacare use soar together, explaining in great detail how it can be logical for someone to be on Obamacare but not like it. We can all argue that the Republicans may have as much to do with that as anything, but the problem exists. And finally, a US News article makes this point:
His supporters realize he s a joke. They do not care. They know he s authoritarian, nationalist, almost un-American, and they love him anyway, because he disrupts a broken political process and beats establishment candidates who ve long ignored their interests. When you re earning $32,000 a year and haven t had a decent vacation in over a decade, it doesn t matter who Trump appoints to the U.N., or if he poisons America s standing in the world, you just want to win again, whoever the victim, whatever the price. According to the Republican Party, the biggest threat to rural America was Islamic terrorism. According to the Democratic Party it was gun violence. In reality it was prescription drug abuse and neither party noticed until it was too late.
Are we leaving people out? All this reminded me of reading about Donald Knuth, the famous computer scientist and something of the father of modern computing, writing about his feelings of trepidation about sharing with his university colleagues that he was working on a project related to the Bible. I am concerned about the complaints about the PC culture , because I think it is good that people aren t making racist or anti-semitic jokes in public anymore. But, as some of these articles point out, in many circles, making fun of Christians and conservatives is still one of the accepted targets. Does that really help anything? (And as a Christian that is liberal, have all of you that aren t Christians so quickly forgotten how churches like the Episcopals blazed the way for marriage equality many years ago already?) But they don t get a free pass I have found a few things, however, absolutely scary. One was an article from December showing that Trump voters actually changed their views on Russia after Trump became the nominee. Another one from just today was a study on how people reacted when showed inauguration crowd photos. NPR ran a story today as well, on how Trump is treating journalists like China does. Chilling stuff indeed. Conclusion So where does this leave us? Heading into uncertain times, for sure, but perhaps just maybe with a greater understanding of our neighbors. Perhaps we will all be able to see past the rhetoric and polarization, and understand that there is something, well, normal about each other. Doing that is going to be the only way we can really take our country back.

Joey Hess: badUSB

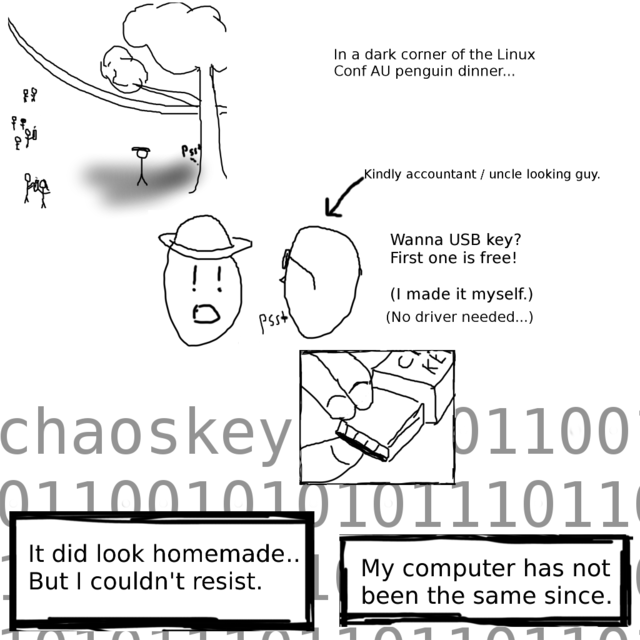
3 panel comic: 1. In a dark corner of the Linux Conf AU penguin dinner. 2. (Kindly accountant / uncle looking guy) Wanna USB key? First one is free! (I made it myself.) (No driver needed..) 3. It did look homemade, but I couldn't resist... My computer has not been the same since This actually happened.
Jan 19 00:05:10 darkstar kernel: usb 2-2: Product: ChaosKey-hw-1.0-sw-1.6.
In real life, my hat is uglier, and Keithp is more kindly looking. gimp source

25 January 2017

Urvika Gola: Outreachy- Week 4 & 5 Progress

Working with Preferences, AudioManager, RingtoneManager in Android. Sometimes the noise can get too much. Imagine all the people around you at work or in a classroom. All of them have at least one cell phones. Even if they were all to make a tiny blip, the noise would be irritating and disruptive. To avoid devices from interrupting the non-digital life, applications often provide settings that allow users to modify app volumes. My task this week was to enable/disable silent mode in Lumicall. To provide settings for your application, instead of using multiple Views, Preference APIs should be used. Each preference appears as an item in a list and provides the appropriate UI for users to modify the setting. In Lumicall, when settings menu from the menubar is selected, a preference screen is displayed showing various setting options, where I appended a Configure Silent Mode option. The UI for the preference screen is expected to be in Src->xml folder under the name preferences.xml

silentSnippet from Lumicall s preference.xml for Configure Silent Mode preference screen.
In Lumicall, whenever a SIP message comes in, RingtoneManager Class is used to generate a notification sound & AudioManager Class is used to generate sound for incoming encrypted calls. The difference between the two is that, AudioManager provides access to volume and ringer mode control. Ringer modes like, Normal, silent and vibration. Whereas RingtoneManager provides access to ringtones, notification. So to add a simple -disable/enable silent mode- functionality, I decided to use a CheckboxPreference. For the same goal, a better looking widget would be a SwitchPreference, but It does not work properly with DarkThemes which Lumicall uses. So I decided to use a simple Checkbox instead. The result of all the settings are saved as key value pairs in the default SharedPreferences file which can be retrieved to make changes in the app based on the settings modified by the user.
Every preference has a key and the result associated with it.
To fetch the result from the SharedPreferences file-
boolean silentflag=PreferenceManager.getDefaultSharedPreferences(ctx).getBoolean(org.sipdroid.sipua.ui.Settings.PREF_SILENT_MODE, org.sipdroid.sipua.ui.Settings.DEFAULT_SILENT_MODE); Note, the arguments in getBoolean function is (Key, DefaultValue). Don t forget to pass the Context object, ctx in the statement. I wasted a lot of time figuring that one out and created a non-optimal-working way which I eventually had to remove cos I figured out how to retrieve the result value. frustrated
To add a second method of setting silent mode, i.e where the user can enter his work days/time, I wanted to display an activity with required widgets .
To display an activity on a when a preference is selected, intent tags are used. (See the above snippet)
Note that the target package in the intent tags is not the package name of where the java file of the activity is to be found.It s the package name which is your applicationID. Now this activity, like any other activity in android is a combination of an xml and java file.
1. My xml file contains the widgets for user to enter two set of time value in HH:MM format. i.e.the start and end time during which user requires application notifications to be silent it also contains checkboxes for user to select multiple days of the week. 2. The java file associated with this does the following:
2.1 Comparing the Real Time with User s Specified Start and End time
2.2 Checking the current day of the week with the days marked by the user in the checkboxes I have used inbuilt Calendar class and Date class to accomplish this. All done I felt quite proud but this.. this was something that tested my patience and endurance!
As I continue my work, I will keep sharing! Please keep reading!
U


24 January 2017

Shirish Agarwal: Budget and Economics 101

The Budget The story which I wanted to share is there are few friends (from Debian as well as elsewhere) who shared that they didn t get the whole demonetisation play or what the Government is/was trying to do. As budget is just round the corner (India will be presenting its yearly budget on 1st of February), thought it is prudent to share at least some basics, ideas and theories of what goals the Finance Minister would be looking at when presenting his budget. I would NOT talk of Inflation targeting or some such exotica as those topics would require their own blog-posts altogether. I would mainly be talking a bit about Taxation and in that Personal Income Tax. I would also not use words like Receivables and like which thought bit more accurate are not used in everyday language. Just like Private Companies and increasingly public utilities, The Government of the day has two-three different aims when it is presenting a budget a. The first is to give an update about how things went last year. Did all the incomes that were projected, did it happen or was there a short-fall ? If there was a short-fall what were the reasons for the shortfall. Similarly, did all the budgeted expenditure earmarked for the year was spent and were it spent under the heads they were supposed to ? If not what went wrong there ? There is usually a tussle between Planned and Unplanned expenditure and one of the hallmarks of good governance is that unplanned expenditure is kept at minimum, while planned expenditure and projects completion or/and assets coming on-line were within the estimated time-frames. So these updates are given to the Parliament and hence public at large. The second and the more interesting part are the plans for the immediate future, 1 year down-the-line. Based on the performance last year, a bit of crystal-ball gazing of external and internal conditions of the country, the Finance Minister along with her/his colleagues of Finance Ministry. Trivia There hasn t been a female finance minister till date in India. The Finance Ministry as a whole also holds consultations with most sections of the society before sharing/putting his Fiscal Policy (Planned Expenditure) for debate and passage in form of the Budget. While the budget itself is a technical exercise, it is also a Political exercise as both the budget and the finance bill (which contains the taxation proposals) need to be passed in Lok Sabha (Lower house). After passing scrutiny of Lok Sabha (Lower House having people s representatives directly elected) and Rajya Sabha (Upper House, indirectly elected), the taxation proposals becomes the law. It isn t that simple but for our understanding, keeping it simple. This Political model of governance with two houses is modeled under the British (Westminister) model since 1947. The Government, just like any other Organization gives a similar Profit and Loss Account and a Balance Sheet.
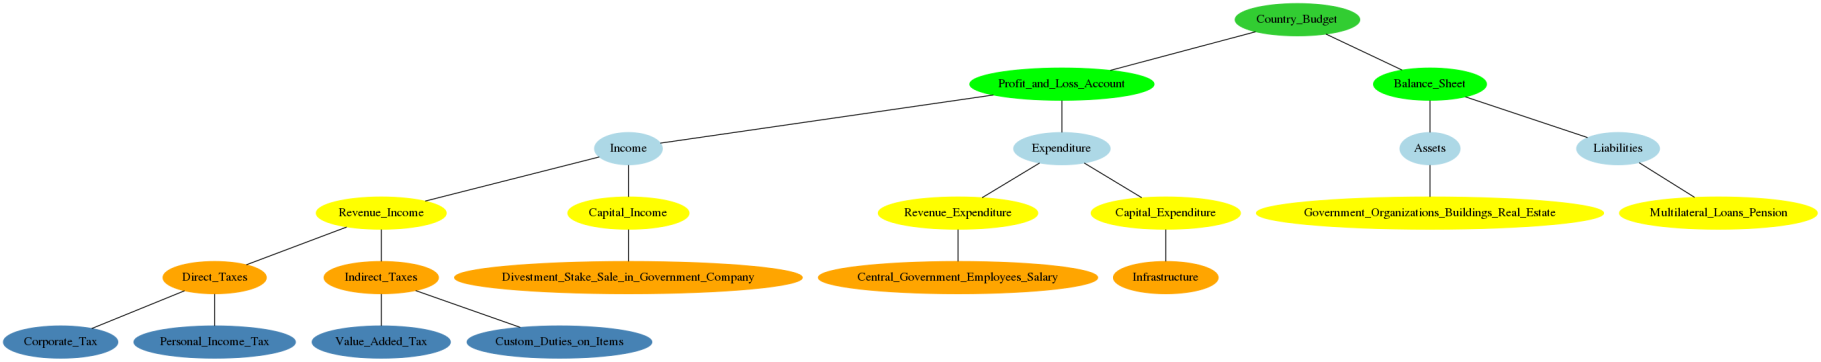
How A country's budget is made.

How A country s budget is made. A representational and simplified version of how things flow was made using Graphviz. Click on it to see image in detail.

I am a newbie to graphviz. The graph was made like this
graph Budget
subgraph tier1
node [color="limegreen",style="filled",group="tier1"]
Country_Budget

......
Country_Budget -- Profit_and_Loss_Account [type=s];
It might be possible to make the graph much better than it is currently . The Profit and Loss Account of the Government tells what Incomes it is projected to earn in the upcoming year and whatever Expenditures it hopes to do this year. The Income and Expenditure independently can be bifurcated into two, Revenue Income and Capital Income and Revenue Expenditure and Capital Expenditure.
Indian Railways EMU local train

Indian Railways EMU local train

The simplest example of such planned expenditure which comes to my mind is the Indian Railways Budget which is all planned expenditure. As can be seen even with ample funds Railways were able to spent only 50% of the total amount disbursed last year. Similarly income generation for Railways was far below the target. Examples of Revenue Income include taxes of all sorts, while Capital Income are rare, like divestment/stake sale of a company owned by the Government. These are usually one-off events. Examples of Capital Expenditure is when the Government makes a road, makes a bridge etc. Usually large expenditures come under Capital Expenditure while salaries to Government employees and routine expenditures are known as Revenue Expenditure. There was a statement by the present Government that the last 6-7 years the budgets has been more or less static as far as numbers are concerned. This hampers Government s ability to take up any new work. The Revenue income earned by the Government can again be bifurcated primarily into two Direct Taxes and Indirect Taxes.
INR 2000 Rupees

INR 2000 Rupees

Direct Taxes are those which the Government earns through Personal Income Tax and Corporate Tax. As only 1 percent of Indians pay Personal income tax, the rest Government tries to raise by Hence the Government of the day is in fix. It needs to have more money if it wants to invest into infrastructure, defence spending, social spending such as health and education and so on and so forth. It cannot Another point is that unlike China which is a Large State-backed Enterprises Export-led Economy which has its own problems, India s economy is much more consumption-based, hence any large tinkering upwards may possibly stall whatever little spending the middle-class does, similar to the stall in consumer durables which has been happening over the last few years. There are a couple of short-term solutions that the Government may do While both seem to be attractive ways, but both have their disadvantages also, both have costs associated for them. In the first one, like any other scheme, when any scheme is launched, it needs to be underwritten by GOI which means even if it s not a success they would have to service all and any obligations towards investors. Also they have to be careful how much they are borrowing as excessive borrowing for today could lead to a Greece-like meltdown situation, whether internal or external borrowers. With external borrowers they also usually like to have a guarantee that the Rupee will not slide beyond a point otherwise the Government will have to pay all and any losses but this is going beyond what I wanted to share. Printing excess money in the system could lead to loss in the value of the money itself as well as leading to inflationary pressures which leads to more problems for the poor and greater inequality between the classes among other things. So while the Government may use all of the above ways in varying degrees, the present Government had the idea that if we were to reduce black money or hidden economy (AFAIK no country can claim to completely eliminate it) we would be able to raise the finance we need without a major cost associated to it. For instance, I was reading that even in Canada, it is expected that 20% of black money/shadow economy works and that assessment is by their own taxation authorities. So While doing demonetization, it came out with an equivalent Black Money Declaration Scheme (IDS). The idea is simple, even if 1 percent of the population comes in the traditional tax net the Government of the day would be able to enhance budgets to various expenditure. Now while the idea is good in theory, implementation has been the Achilees heel. While the Government s expected something like 15% of the whole economy was black money or shadow money, almost 95% of the money in circulation came back in Banks during demonetization ( These are unofficial figures, Finance Ministry/RBI would be disclosing the real figures on 1st of February 2017 so we will know). It is suspected that 10% of money in Banks is black money. There are considerable costs to search analyze, prove in the court of law that it is so. There are and would be considerable costs to train new officers as existing Income Tax Officers are already burdened with Advance Tax being paid by Corporates and small business-man paying round the year (every 3 months), The existing Income Tax Officers already have their hands full. Also till Governments don t fix up realty sector/real-estate sector and other places where the black money/shadow economy may prevail. Hence all the training, salary, buildings where new Income Tax Officers could work, infrastructure, new buildings where suspect cases have to be tried and lawyers for those. As have shared a few times on this blog, India has almost 29 million court cases pending in the lower judiciary alone. Unless any such cases are not successfully tried within time by the Government, it would be a waste. Now whether the Government knew of these issues or not would probably be never known. Lastly, there is a voluntary part that the Government hopes, that they will by themselves join the mainstream tax-paying public. This might happen but any such happening will happen over years. People make their own choices. And unless there are not any stick and carrot approach to the Government s Policies people will tend to go back to their old ways. I would share an example from the demonetisation process which would help prove my point During demonetization, there was a great push towards doing digital transaction either via smartphones or greater usage of debit and credit cards etc. For the first 60 days till 31st December 2016, you could do digital transactions without paying any transaction fee. During that period, I used my Debit card to shop, to eat at restaurants or/and even small shops. But come 1st January 2017, the charges for digital transactions are anything between 1.5% to 3% of transactions. Naturally, I stopped using them and use them very sparingly where cash won t work. So at the end, while the Government made the whole demonetization drive to drive out shadow economy, terror financing etc. While terror financing has been hurt quite a bit, the same cannot be said of the shadow/black economy. It seems that the Government would need to close many more doors and windows before people join the mainstream. While Politically it was risky, socially it was also a bit risky move as it was uncertain how and where things will move. Venezuela tried the same thing and fell flat on its face. All said and done, if and when people become part of the tax-paying class/people, The most optimistic idea that the Government has that everybody will go cashless and it would be far easier to find out who s not paying taxes. As shared before, I don t think this will happen unless the charges for cashless is at 0.05% or something similar. Even IF people do join the mainstream, it is very much possible that the present Govt. will not enjoy fruits of this labour as fruits might come in 2018/19 or even later even if they do come. So whether the decision had the right affect or not, we may never come to know. Governments tend to tinker around with the figures as well. But I hope some idea of how things happen is known now.
Filed under: Miscellenous Tagged: #demonetization, #Government Budget, #graphviz, #Limitations, #Profit and Loss Account, #Taxation

23 January 2017

Sam Hartman: Cudos to GDB Contributors

I recently diagnosed a problem in Debian's pam-p11 package. This package allegedly permits logging into a computer using a smart card or USB security token containing an ssh key. If you know the PIN and have the token, then your login attempt is authorized against the ssh authorized keys file. This seems like a great way to permit console logins as root to machines without having a shared password. Unfortunately, the package didn't work very well for me. It worked once, then all future attempts to use it segfaulted. I'm familiar with how PAM works. I understand the basic ideas behind PKCS11 (the API used for this type of smart card), but was completely unfamiliar with this particular PAM module and the PKCS11 library it used. The segfault was in an area of code I didn't even expect that this PAM module would ever call. Back in 1994, that would have been a painful slog. Gdb has improved significantly since then, and I'd really like to thank all the people over the years who made that possible. I was able to isolate the problem in just a couple of hours of debugging. Here are some of the cool features I used: Anyway, with just a couple of hours and no instrumentation of the code, I managed to track down how a bunch of structures were being freed as an unexpected side effect of one of the function calls. Neither I nor the author of the pam-p11 module expected that (although it is documented and does make sense in retrospect). Good tools make life easier.

Matthew Garrett: Android permissions and hypocrisy

I wrote a piece a few days ago about how the Meitu app asked for a bunch of permissions in ways that might concern people, but which were not actually any worse than many other apps. The fact that Android makes it so easy for apps to obtain data that's personally identifiable is of concern, but in the absence of another stable device identifier this is the sort of thing that capitalism is inherently going to end up making use of. Fundamentally, this is Google's problem to fix.

Around the same time, Kaspersky, the Russian anti-virus company, wrote a blog post that warned people about this specific app. It was framed somewhat misleadingly - "reading, deleting and modifying the data in your phone's memory" would probably be interpreted by most people as something other than "the ability to modify data on your phone's external storage", although it ends with some reasonable advice that users should ask why an app requires some permissions.

So, to that end, here are the permissions that Kaspersky request on Android:
Every single permission that Kaspersky mention Meitu having? They require it as well. And a lot more. Why does Kaspersky want the ability to record audio? Why does it want to be able to send SMSes? Why does it want to read my contacts? Why does it need my fine-grained location? Why is it able to modify my settings?

There's no reason to assume that they're being malicious here. The reasons that these permissions exist at all is that there are legitimate reasons to use them, and Kaspersky may well have good reason to request them. But they don't explain that, and they do literally everything that their blog post criticises (including explicitly requesting the phone's IMEI). Why should we trust a Russian company more than a Chinese one?

The moral here isn't that Kaspersky are evil or that Meitu are virtuous. It's that talking about application permissions is difficult and we don't have the language to explain to users what our apps are doing and why they're doing it, and Google are still falling far short of where they should be in terms of making this transparent to users. But the other moral is that you shouldn't complain about the permissions an app requires when you're asking for even more of them because it just makes you look stupid and bad at your job.

comment count unavailable comments

22 January 2017

Shirish Agarwal: Debian contributions and World History

Beware, this would be slightly longish. Debian Contributions In the last couple of weeks, was lucky to put up a patch against debian-policy which had been bothering me for a long-long time. The problem statement is simple, man-pages historically were made by software engineers for software-engineers. The idea, probably then was you give the user some idea of what the software does and the rest the software engineer would garner from reading the source-code. But over period of time, the audience has changed. While there are still software engineers who use GNU/Linux for the technical excellence, the man-pages have not kept up with this new audience who perhaps are either not technically so sound that or they do not want to take the trouble to reading the source-code to understand how things flow. An example or examples in a man-page gives us (the lesser mortals) some insight as how the command works, how the logic flows. A good example of a man-page is the ufw man-page
EXAMPLES
Deny all access to port 53: ufw deny 53 Allow all access to tcp port 80: ufw allow 80/tcp Allow all access from RFC1918 networks to this host: ufw allow from 10.0.0.0/8
ufw allow from 172.16.0.0/12
ufw allow from 192.168.0.0/16 Deny access to udp port 514 from host 1.2.3.4: ufw deny proto udp from 1.2.3.4 to any port 514 Allow access to udp 1.2.3.4 port 5469 from 1.2.3.5 port 5469: ufw allow proto udp from 1.2.3.5 port 5469 to 1.2.3.4 port 5469
Now if we had man-pages like the above which give examples, then the user at least can try to accomplish whatever s/he is trying to do. I truly believe not having examples in a man-page kills 50% of your audience and people who could potentially use your tool. Personal wishlist The only thing (and this might be my failure) is we need a good way to search through a man-page. The only way I know is using / and try to give a pattern. Lots of times it fails because I, the user doesn t know the exact keyword which the documenter was using. What would be nice, great if we do have some sort of parser where I tell it, $this is what I m looking for and the parser tries the pattern + all its synonyms and whatever seems to be most relevant passage from the content, in this case a manpage it tells me. It would make my life a lot easier while at the same time force people to document more and more. I dunno if there has been any research or study of the relationship between good documentation and popularity of a program. I know there are lots of different tiny bits which make or break a program, one of which would definitely be documentation and in that a man-page IF it s a command-line tool. A query on Quora gives some indication https://www.quora.com/How-comprehensible-do-you-find-Unix-Linux-Man-pages although the low response rate tells its own story. there have been projects like man2html and man2pdf and others which try to make the content more accessible to people who are not used to the man-page interface but till you don t have Examples the other things can work only so far. Also if anybody talks about X project which claims to solve this problem they will have to fight manpages who have been around like forever. As can be seen in the patch, did some rookie mistakes as can be seen. I also filed a lintian bug at the same time. Hope the patch does get merged at some point in debian-policy and then a check introduced in lintian in some future release. I do agree with anarcat s assertion that it should be at the level of the manpage missing level. I am no coder but finding 14,000 binary packages without a manpage left me both shocked and surprised. I came to know about manpage-alert from the devscripts package to know which all binary packages that have been installed but not have man-pages. I hope to contribute a manpage or two if I across a package I m somewhat comfortable with. I have made a beginning of sorts by running manpage alert and putting the output in a .txt file which I would grep through manually and see if something interesting jumps at me. The learning garnered from putting the patch to the debian package resulted in another patch but this time for an upstream project altogether. As can be seen all are just baby-steps that even a non-coder can take. Another couple of bugs I filed which were fixed were of a sim called unknown-horizons . A 2D realtime strategy simulation. I had filed three bugs, two of which were fixed in 2 days, the 3rd I hope is also fixed soonish. Lastly, I spent most of the week-end poring over packages who have left files in /etc/bash_completion.d/ . I spent almost 4-5 odd hours as each package in question as well as entries found in /etc/bash-completion.d/$filename I had to find which package it belonged to first

[$] dpkg -S /etc/bash_completion.d/git-prompt
git: /etc/bash_completion.d/git-prompt
I know that dpkg-query also does the same
[$] dpkg-query -S /etc/bash_completion.d/git-prompt
git: /etc/bash_completion.d/git-prompt
But I am used to plain dpkg although do know that dpkg-query can do lot more intimate searching in various ways than dpkg can. Once the package name was established, first simulate the purge [$] sudo aptitude -s purge git

[sudo] password for shirish:
The following packages will be REMOVED:
git p
0 packages upgraded, 0 newly installed, 1 to remove and 14 not upgraded.
Need to get 0 B of archives. After unpacking 29.5 MB will be freed.
The following packages have unmet dependencies:
libgit-wrapper-perl : Depends: git but it is not going to be installed
git-extras : Depends: git (>= 1.7.0) but it is not going to be installed
bup : Depends: git but it is not going to be installed
git-remote-gcrypt : Depends: git but it is not going to be installed
git-svn : Depends: git (> 1:2.11.0) but it is not going to be installed
Depends: git ( 1:2.11.0) but it is not going to be installed
Depends: git (= 1:1.8.1) but it is not going to be installed
git-core : Depends: git (> 1:1.7.0.2) but it is not going to be installed
The following actions will resolve these dependencies:
Remove the following packages:
1) bup [0.29-2 (now, testing, unstable)]
2) fdroidserver [0.7.0-1 (now, testing, unstable)]
3) git-annex [6.20161012-1 (now, testing)]
4) git-core [1:2.11.0-2 (now, testing, unstable)]
5) git-extras [4.2.0-1 (now, testing, unstable)]
6) git-remote-gcrypt [1.0.1-1 (now, testing, unstable)]
7) git-repair [1.20151215-1 (now, unstable)]
8) git-svn [1:2.11.0-2 (now, testing, unstable)]
9) gitk [1:2.11.0-2 (now, testing, unstable)]
10) libgit-wrapper-perl [0.047-1 (now, testing, unstable)]
11) python3-git [2.1.0-1 (now, testing, unstable)]
12) svn2git [2.4.0-1 (now, testing, unstable)] Leave the following dependencies unresolved:
13) devscripts recommends libgit-wrapper-perl
14) dh-make-perl recommends git
15) fdroidserver recommends git
16) git-annex recommends git-remote-gcrypt (>= 0.20130908-6)
17) gplaycli recommends fdroidserver
18) python-rope recommends git-core
Accept this solution? [Y/n/q/?] q
Abandoning all efforts to resolve these dependencies.
Abort.
Then I made a note of all the packages being affected, saw purging all of them wouldn t call others (the Package dependency Hell), made the purge and then reinstalled anew. The reason I did this is that many a times during upgrade, either during update/upgrade sometimes the correct action doesn t happen. To take the git s example itself, there were two files git-extras and git-prompt which were in /etc/bash_completion.d/ both of which were showing their source as git. Purging git and installing git afresh removed git-extras file and git-prompt is the only one remaining. While blogging about the package, did try to grep through changelog.Debian.gz and changelog.gz in git

[shirish@debian] - [/usr/share/doc/git] - [10046]
[$] zless changelog.gz
and similarly

[shirish@debian] - [/usr/share/doc/git] - [10046]
[$] zless changelog.Debian.gz
But failed to find any mention of the now gone git-extras. Doing this with all the packages took considerable time as didn t want to deal with any potential fallout later on. For instance, ufw (uncomplicated firewall) also had an entry in /etc/bash_completion.d/, hence before purging ufw, took backup of all the rules I have made, did a successful simulation

[$] sudo aptitude -s purge ufw gufw


The following packages will be REMOVED:
gufw p ufw p
0 packages upgraded, 0 newly installed, 2 to remove and 14 not upgraded.
Need to get 0 B of archives. After unpacking 4,224 kB will be freed.
Note: Using 'Simulate' mode.
Do you want to continue? [Y/n/?] y
Would download/install/remove packages.
purged the packages, reinstalled it and then re-added all the rules. Doing it all for various sundry packages, had to do it manually as there is no one size fits all solution. A sensitive one was grub which still has an entry in /etc/bash_completion.d/grub. Doing it wrong could have resulted in a non-bootable situation. There are workarounds for that, but it would have taken quite a bit of time, energy, notes and bit of recall factor what I did the last time something like that happened. Doing it manually, being present meant I could do it rightly the first time. So, was it worth it It would be if the package maintainers do the needful and the remaining entries are moved out of /etc/bash_completion.d/ to /usr/share/bash-completions and some to my favourite /usr/share/zsh/vendor-completions/ for instance

[shirish@debian] - [/usr/share/zsh/vendor-completions] - [10064]
[$] ll -h _youtube-dl
-rw-r--r-- 1 root root 3.2K 2016-12-01 08:48 _youtube-dl But trying to get all or even major packages to use zsh-completions would be hard work and would take oodles of time and this concerns upstream stuff, also very much outside what I was sharing. World History Before, during and even after South-African experience, I was left wondering why India and South Africa, two countries who had similar histories at least the last couple of hundred years or more, the final result of Independence was so different for both the countries. It took me quite sometime to articulate that in a form of question , while the answers were interesting, from what little I know of India itself, if I were an Englishman I would never leave Hindustan . What the people answering failed to take into account was that in that era it was Hindustan or un-divided India.
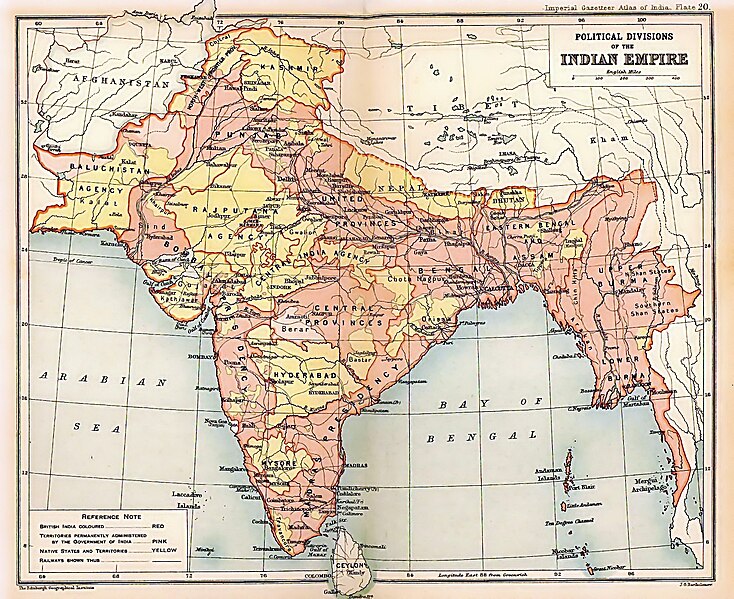
Pre-partition map of India

Pre-partition map of India

This map can be found at https://commons.wikimedia.org/wiki/File:British_Indian_Empire_1909_Imperial_Gazetteer_of_India.jpg and is part of quite a few Indian articles. I would urge people to look at the map in-depth. Except for the Central India Agency and Central India Provinces, most of the other regions were quite comfortable weather-wise. Hence I can t help but feel the assertion that Britishers didn t like India (as to live here) slightly revolting. See the excerpt/take on Dale Kennedy s The Magic Mountains: Hill Stations and the British Raj. Berkeley: University of California Press, 1996. xv + 264 pp. . A look at the list of hill stations of divided India is enough to tell that there were lot of places which either were founded by the Britishers or they chose to live there. And this is not all, there are supposed to lot of beautiful places even in Pakistan, especially in North East Frontier, Swat for instance. While today it s infamous for Taliban and Islamic Terrorism, there was a time it was known for its beauty.
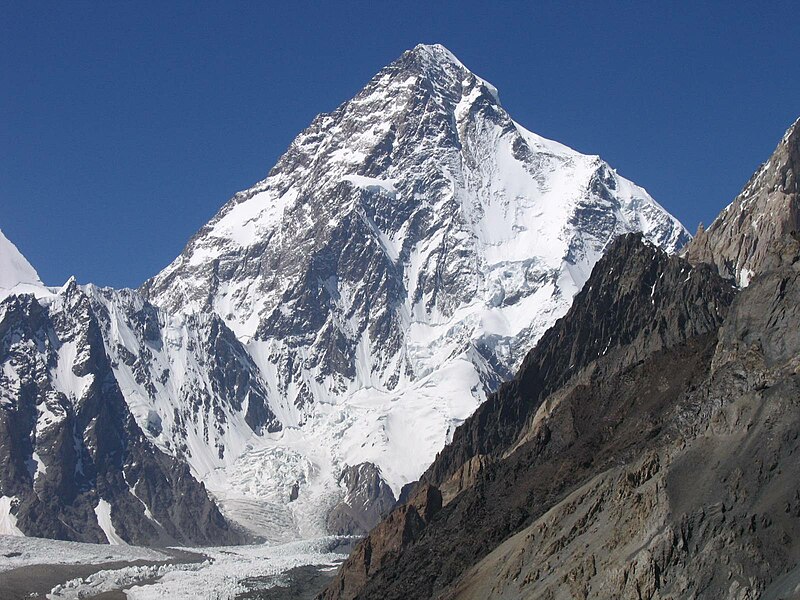
The second most difficult mountain in the world - K2, Pakistan

The second most difficult mountain in the world K2, Pakistan

Trivia After Everest, K2 is the smaller one although whatever I have read of people s accounts, most people who ascended all 14 8,000 metre peaks say K2 is technically more tougher than Everest and after Everest has the highest casualty rate. Also places like the disputed North half of Pakistan Occupied Kashmir, Gilgit Baltistan, Extreme northern Punjab of Pakistan , Northern half of Khyber-Pakhtunkhawa province and Northern Balochistan all of these places would have been more than conducive to the Britishers as it is near to the British climate (snow and pleasant weather all year round). It really is a pity that Pakistan chose to become a terrorist state where it could have become one of the more toured places of Asia. I really feel nauseous and sad at the multiple chances that Pakistan frittered away, it could have been something else.
Filed under: Miscellenous Tagged: #bash-completion, #British Raj, #contributions, #debian, #debian-policy, #Debian-QA, #Hill Stations, #India Independance Movement, #lintian, #obsolete-conffiles, #unknown-horizons, #weather, #World History, adequate, Pakistan, tourism

Lars Wirzenius: Improving debugging via email, followup

Half a year ago I wrote a blog post about debugging over email. This is a follow-up. The blog post summarised: Based on further thinking and feedback, I add: I've not written any code to help with this remote debugging, but it's something I will start experimenting with in the near future. Further ideas welcome.

19 January 2017

Matthew Garrett: Android apps, IMEIs and privacy

There's been a sudden wave of people concerned about the Meitu selfie app's use of unique phone IDs. Here's what we know: the app will transmit your phone's IMEI (a unique per-phone identifier that can't be altered under normal circumstances) to servers in China. It's able to obtain this value because it asks for a permission called READ_PHONE_STATE, which (if granted) means that the app can obtain various bits of information about your phone including those unique IDs and whether you're currently on a call.

Why would anybody want these IDs? The simple answer is that app authors mostly make money by selling advertising, and advertisers like to know who's seeing their advertisements. The more app views they can tie to a single individual, the more they can track that user's response to different kinds of adverts and the more targeted (and, they hope, more profitable) the advertising towards that user. Using the same ID between multiple apps makes this easier, and so using a device-level ID rather than an app-level one is preferred. The IMEI is the most stable ID on Android devices, persisting even across factory resets.

The downside of using a device-level ID is, well, whoever has that data knows a lot about what you're running. That lets them tailor adverts to your tastes, but there are certainly circumstances where that could be embarrassing or even compromising. Using the IMEI for this is even worse, since it's also used for fundamental telephony functions - for instance, when a phone is reported stolen, its IMEI is added to a blacklist and networks will refuse to allow it to join. A sufficiently malicious person could potentially report your phone stolen and get it blocked by providing your IMEI. And phone networks are obviously able to track devices using them, so someone with enough access could figure out who you are from your app usage and then track you via your IMEI. But realistically, anyone with that level of access to the phone network could just identify you via other means. There's no reason to believe that this is part of a nefarious Chinese plot.

Is there anything you can do about this? On Android 6 and later, yes. Go to settings, hit apps, hit the gear menu in the top right, choose "App permissions" and scroll down to phone. Under there you'll see all apps that have permission to obtain this information, and you can turn them off. Doing so may cause some apps to crash or otherwise misbehave, whereas newer apps may simply ask for you to grant the permission again and refuse to do so if you don't.

Meitu isn't especially rare in this respect. Over 50% of the Android apps I have handy request your IMEI, although I haven't tracked what they all do with it. It's certainly something to be concerned about, but Meitu isn't especially rare here - there are big-name apps that do exactly the same thing. There's a legitimate question over whether Android should be making it so easy for apps to obtain this level of identifying information without more explicit informed consent from the user, but until Google do anything to make it more difficult, apps will continue making use of this information. Let's turn this into a conversation about user privacy online rather than blaming one specific example.

comment count unavailable comments

Next.

Previous.