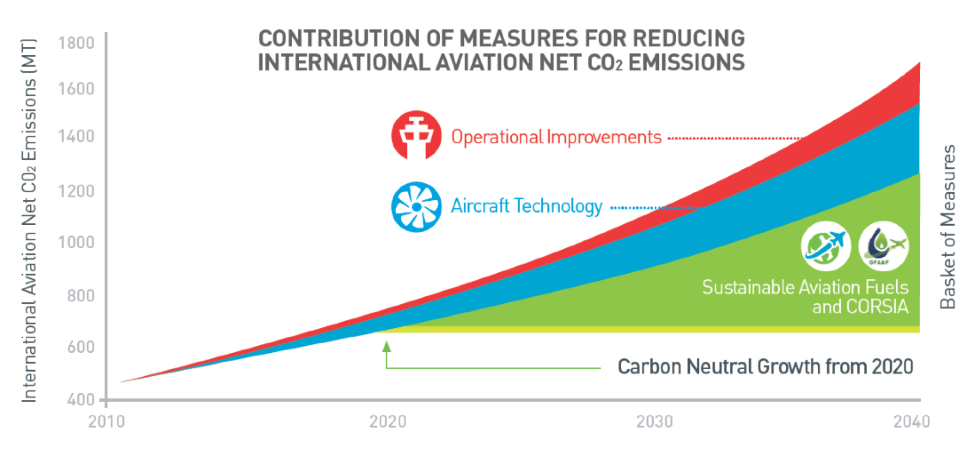
If you have to choose one year when you won't fly, this year, 2020, is the one to choose. Why? Because CORSIA. What the heck is CORSIA? CORSIA is not a novel virus, but "Carbon Offsetting and Reduction Scheme for International Aviation". In a nutshell, the aviation industry says they will freeze their co2 emissions from growing. Actually, aviation emissions are still going to grow. The airlines will just pay someone else to reduce emissions with the same amount aviation emissions rise - the "Offsetting" word in CORSIA. If that sounds like greenwashing, well it pretty much is. But that was expected. Getting every country and airline abroad CORSIA would not have been possible if the scheme would actually bite. So it's pretty much a joke.
What does it have to do with *this* Year? The first phase of CORSIA will start next year, so the emissions are frozen to year 2020 levels. Due to certain recent events, lots of flights have already been cancelled - which means the reference year aviation emissions are already a lot less than the aviation industry was expecting. By avoiding flying this year, the aviation emissions are going to be frozen at an even lower level. This will increase cost of co2 offsetting for airlines, and the joke is going to be on them. So consider skipping business travel and taking your holiday trip this year with something else than a plane. Wouldn't recommend a cruise ship, tho...
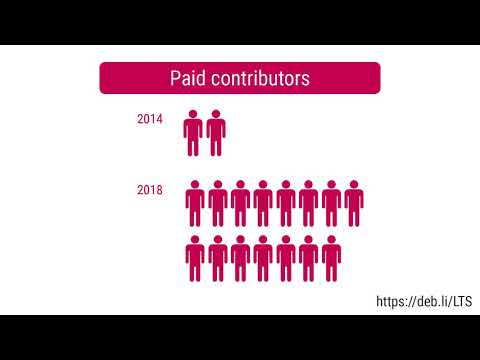
Just like we did for Debian 7 Wheezy, some of the paid Debian LTS contributors will continue to maintain Debian 8 Jessie after its 5 years of support as part of Freexian s Extended LTS service.
This service works differently than regular LTS:
No comment Liked this article? Click here. My blog is Flattr-enabled.
I have a Raspberry Pi at my parents home. They have internet access
via some ISP using Carrier Grade NAT (CGN). Hence their home router is
not reachable via IPv4 from the outside, they do have IPv6 and the
devices can also be made accessible via IPv6 via the local router.
Did that, was able to access my Raspberry Pi over IPv6 and SSH from
the outside. So doing backup of that Raspberry Pi with BackupPC from
the outside was a walk in the park.
Unfortunately the IPv6 prefix seems to change occasionally and the
router only allows to configure explicit IPv6 addresses in firewall
rules so after a prefix change the configured rules no more
match the devices IPv6 addresses. Meh.
So there were multiple possibilities to work around these
restrictions and access a devices behind the router:
ssh-ping
~backuppc/.ssh/config:
Host sherpa_via_tor
Hostname abcdefghijklmnop.onion
ProxyCommand /bin/nc.openbsd -X 5 -x localhost:9050 %h %p
These lines basically configure an alias hostname for ssh
which then connects via SOCKS5 to the Tor daemon instead of doing DNS
lookup and connection itself. It also configures the actual hostname
(a Tor .onion hostname) to connect to.
/etc/backuppc/sherpa.pl:
$Conf ClientNameAlias = 'sherpa_via_tor'; $Conf PingCmd = '/usr/bin/ssh-ping -c 1 $host'; $Conf NmbLookupFindHostCmd = "";These lines configure a few things in BackupPC:
.ssh/config.ssh-ping instead of standard ping as
command to test connectivity. (ICMP neither works over SOCKS5 nor
over Tor. And we configured the connection only for SSH
anyways.).ssh/known_hosts file also for the .onion hostname.
And the Tor Hidden Service needs to be configured on the target
device.
But that s left as exercise for the reader. There s a lot of
documentation about that on the internet, including slides and video recordings of
talks and live demos I gave about this topic in German.
Ah, and in case you might think that s unfair and misuse of the
resources of the Tor Project: No, I explicitly asked and they said
more or less any additional traffic helps to make it more difficult to
analyse Tor traffic or to track Tor users and is hence
welcome.
Addendum: The last direct full backup of that Raspberry Pi
(5.5 GB) took around 32 minutes. The first full backup over Tor (8.7
GB) took 341 minutes. Seems much slower, but there might be other
factors as well: Most backups which ran last night were running at
only 0.85 MB/s to 1 MB/s, probably because too many backups were
running in parallel after a recent backup server downtime with file
system check the backup server was probably the bottleneck.
The backup of the Raspberry Pi over Tor ran at 0.42 MB/s, so about
half the speed of the other backups. (Will probably add some more
notes if I have more statistics over time.)
Welcome to gambaru.de. Here is my monthly report (+ the first week in March) that covers what I have been doing for Debian. If you re interested in Java, Games and LTS topics, this might be interesting for you.
Debian Games
@ sign
looks when compared to my previous font, Liberation Mono:
Liberation Mono
Fira Mono
.Xresources (no, I haven't switched to Wayland):
! font settings
Emacs*font: Fira mono
rofi*font: Fira mono 12
! Symbola is to get emojis to display correctly, apt install fonts-symbola
!URxvt*font: xft:Monospace,xft:Symbola
URxvt*font: xft:Fira mono,xft:Symbola
I also dropped this script in ~/.local/share/fonts/download.sh, for
lack of a better way, to download all the fonts I'm interested in:
#!/bin/sh
set -e
set -u
wget --no-clobber --continue https://practicaltypography.com/fonts/charter.zip
unzip -u charter.zip
wget --no-clobber --continue https://github.com/adobe-fonts/source-serif-pro/releases/download/3.001R/source-serif-pro-3.001R.zip
unzip -u source-serif-pro-3.001R.zip
wget --no-clobber --continue https://github.com/adobe-fonts/source-sans-pro/releases/download/3.006R/source-sans-pro-3.006R.zip
unzip -u source-sans-pro-3.006R.zip
wget --no-clobber --continue https://github.com/adobe-fonts/source-code-pro/releases/download/2.030R-ro%2F1.050R-it/source-code-pro-2.030R-ro-1.050R-it.zip
unzip -u source-code-pro-2.030R-ro-1.050R-it.zip
wget --no-clobber --continue -O Fira-4.202.zip https://github.com/mozilla/Fira/archive/4.202.zip true
unzip -u Fira-4.202.zip
Update: I forgot to mention one motivation behind this was to work
around a change in the freetype interpreter, discussed in bug
866685 and my upgrades
documentation.
h1, h2, h3, h4, h5, body
/*
* Charter: Butterick's favorite, freely available, found on https://practicaltypography.com/free-fonts.html
* Palatino: Mac OS
* Palatino Linotype: Windows
* Noto serif: Android, packaged in Debian
* Liberation serif: Linux fallback
* Serif: fallback
*/
font-family: Charter, Palatino, "Palatino Linotype", "Noto serif", "Liberation serif", serif;
/* Charter is available from https://practicaltypography.com/charter.html under the liberal Bitstream license */
I have also decided to outline headings by making them slanted, using
the beautiful italic version of Charter:
h1, h2, h3, h4, h5
font-style: italic;
I also made the point size larger, if the display is large enough:
/* enlarge body point size for charter for larger displays */
@media (min-device-width: 750px)
body
font-size: 20px;
line-height: 1.3; /* default in FF is ~1.48 */
Modern display (including fonts) have a much higher resolution and the
point size on my website was really getting too small to be
readable. This, in turn, required a change to the max-width:
#content
/* about 2.5 alphabets with charter */
max-width: 35em;
I have kept the footers and "UI" elements in sans-serif though, and
kept those aligned on operating system defaults or "system fonts":
/* some hacking at typefaces to get some fresh zest in here
* fallbacks from:
* https://en.wikipedia.org/wiki/List_of_typefaces_included_with_Microsoft_Windows
* https://en.wikipedia.org/wiki/List_of_typefaces_included_with_macOS
*/
.navbar, .footer
/*
* Avenir: Mac, quite different but should still be pretty
* Gill sans: Mac, Windows, somewhat similar to Avenir (indulge me)
* Noto sans: Android, packaged in Debian
* Open sans: Texlive extras AKA Linux, packaged in Debian
* Fira sans: Mozilla's Firefox OS
* Liberation sans: Linux fallback
* Helvetica: general fallback
* Sans-serif: fallback
*/
font-family: Avenir, "Gill sans", "Noto sans", "Open sans", "Fira sans", "Liberation sans", Helvetica, sans-serif;
/* Fira is available from https://github.com/mozilla/Fira/ under the SIL Open Font License */
/* alternatively, just use system fonts for "controls" instead:
font-family: -apple-system, BlinkMacSystemFont, "Segoe UI", "Roboto", "Oxygen", "Ubuntu", "Cantarell", "Fira Sans", "Droid Sans", "Helvetica Neue", sans-serif;
gitlab uses: -apple-system, BlinkMacSystemFont, "Segoe UI", Roboto, "Noto Sans", Ubuntu, Cantarell, "Helvetica Neue", sans-serif, "Apple Color Emoji", "Segoe UI Emoji", "Segoe UI Symbol", "Noto Color Emoji"
*/
I've only done some preliminary testing of how this will look
like. Although I tested on a few devices (my phone, e-book tablet, an
iPad, and of course my laptop), I fully expect things to break on
your device. Do let me know if things look better or worse. For
future comparison, my site is well indexed in the Internet
Wayback Machine and can be used to look at the site before the
change. For example, compare the previous article here with its
earlier style.
The changes to the theme are of course available in my custom ikiwiki
bootstrap theme (see in particular commits 0bca0fb7 and
d1901fb8), as usual.
Enjoy, and let me know what you think!
PS: I considered just setting the Charter font in CSS and not adding
it as a @font-face. I'm still considering that option and might do
so if the performance cost is too big. The Fira mono font is
actually set like this for the preformatted sections of the site, but
because it's more common (and it's too big) I haven't added it as a
font-face. You might want to download the font locally to benefit from
the full experience as well.
PPS: As it turns out, an earlier version of this post featured exactly
that: a non-webfont version of Charter, which works fine if you have a
good Charter font available. But it looks absolutely terrible if, like
many Linux users, you have the nasty bitmap font shipped with
xfonts-100dpi and xfonts-75dpi. So I fixed the webfont and
it's unlikely this site will be able to load reasonably well in Linux
until those packages are removed or bitmap font rendering is disabled.
COVID-19 Infographic Datapack, Regularly updated
European Centre for Disease Prevention and Control infographics
COVID-19 Italia - Monitoraggio situazione
Real-time tracking of pathogen evolution
Community sharing resources, verified information, and support initiatives, on COVID-19
Live world statistics on population, government and economics, society and media, environment, food, water, energy and health.
Your friends and colleagues are talking about something called Bayes s Theorem or Bayes s Rule, or something called Bayesian reasoning. They sound really enthusiastic about it, too, so you google and find a web page about Bayes s Theorem and... It s this equation. That s all. Just one equation. The page you found gives a definition of it, but it doesn t say what it is, or why it s useful, or why your friends would be interested in it. It looks like this random statistics thing. Why does a mathematical concept generate this strange enthusiasm in its students? What is the so-called Bayesian Revolution now sweeping through the sciences, which claims to subsume even the experimental method itself as a special case? What is the secret that the adherents of Bayes know? What is the light that they have seen? Soon you will know. Soon you will be one of us. While there are a few existing online explanations of Bayes s Theorem, my experience with trying to introduce people to Bayesian reasoning is that the existing online explanations are too abstract. Bayesian reasoning is very counterintuitive. People do not employ Bayesian reasoning intuitively, find it very difficult to learn Bayesian reasoning when tutored, and rapidly forget Bayesian methods once the tutoring is over. This holds equally true for novice students and highly trained professionals in a field. Bayesian reasoning is apparently one of those things which, like quantum mechanics or the Wason Selection Test, is inherently difficult for humans to grasp with our built-in mental faculties. Or so they claim. Here you will find an attempt to offer an intuitive explanation of Bayesian reasoning an excruciatingly gentle introduction that invokes all the human ways of grasping numbers, from natural frequencies to spatial visualization. The intent is to convey, not abstract rules for manipulating numbers, but what the numbers mean, and why the rules are what they are (and cannot possibly be anything else). When you are finished reading this, you will see Bayesian problems in your dreams.
Continuiamo a lavorare, studiare, socializzare grazie a Jitsi Meet
Everywhere I worked in the past, the only feedback that was asked of
employees was during a yearly evaluation meeting. These meetings always felt to me
like talking to Santa Claus and his Knecht Ruprecht. I was asked: Were you a good
employee last year? If yes, we might give you a raise. If no, admit all
your mistakes now, even if we already know everything, ho ho ho. And don't you talk about your feelings, or your
well-being, or say anything about the organization's (invisible)
hierarchies, otherwise we will put you on the "naughty list", and that's it with candy. The
yearly evaluation set aside, there was no other place to give feedback (except by escalating a matter by involving the Labour Court, if you happen to work in France, or going on strike, also mostly part of French culture).
Feedback allows to reflect on work processes, to situate oneself, and to get closure.
How surprised was I when, some years ago, I received an email from a
collaborator asking me: kindly for just few paragraphs (doesn t have to be
anything long) to hear from you about the process, your work, challenges
you had, or anything else you want to mention there.. Wow!apt-patterns(7) for
more details.
apt(8) now waits for the dpkg locks - indefinitely, when connected
to a tty, or for 120s otherwise.
satisfy command has been added to apt(8) and apt-get(8)
src: to the
name of the package, e.g.:
Package: src:apt
Pin: version 2.0.0
Pin-Priority: 990
Will pin all binaries of the native architecture produced by the source
package apt to version 2.0.0. To pin packages across all architectures,
append :any.
This year s FOSDEM conference was a lot of fun one of the things I always enjoy most about this particular conference (besides having some of the outstanding food you can get in Brussels and meeting with friends from the free software world) is the ability to meet a large range of new people who I wouldn t usually have interacted with, or getting people from different communities together who otherwise would not meet in person as each bigger project has their own conference (for example, the amount of VideoLAN people is much lower at GUADEC and Akademy compared to FOSDEM). It s also really neat to have GNOME and KDE developers within reach at the same place, as I care about both desktops a lot.
An unexpected issue
This blog post however is not about that. It s about what I learned when talking to people there about AppStream, and the outcome of that. Especially when talking to application authors but also to people who deal with larger software repositories, it became apparent that many app authors don t really want to deal with the extra effort of writing metadata at all. This was a bit of a surprise to me, as I thought that there would be a strong interest for application authors to make their apps look as good as possible in software catalogs.
A bit less surprising was the fact that people apparently don t enjoy reading a large specification, reading a long-ish intro guide with lots of dos and don ts or basically reading any longer text at all before being able to create an AppStream MetaInfo/AppData file describing their software.
Another common problem seems to be that people don t immediately know what a reverse-DNS ID is, the format AppStream uses for uniquely identifying each software component. So naturally, people either have to read about it again (bah, reading!
) or make something up, which occasionally is wrong and not the actual component-ID their software component should have.
The MetaInfo Creator
It was actually suggested to me twice that what people really would like to have is a simple tool to put together a MetaInfo file for their software. Basically a simple form with a few questions which produces the final file. I always considered this a nice to have, but not essential feature, but now I was convinced that this actually has a priority attached to it.
So, instead of jumping into my favourite editor and writing a bunch of C code to create this make MetaInfo file form as part of appstreamcli, this time I decided to try what the cool kids are doing and make a web application that runs in your browser and creates all metadata there.
So, behold the MetaInfo Creator! If you click this link, you will end up at an Angular-based web application that will let you generate MetaInfo/AppData files for a few component-types simply by answering a set of questions.
The intent was to make this tool as easy to use as possible for someone who basically doesn t know anything about AppStream at all. Therefore, the tool will:
Also, if you want to create a form for a new component type, please submit a patch as well.
C developer s experience notes for Angular, TypeScript, NodeJS
This section is just to ramble a bit about random things I found interesting as a developer who mostly works with C/C++ and Python and stepped into the web-application developer s world for the first time.
For a project like this, I would usually have gone with my default way of developing something for the web: Creating a Flask-based application in Python. I really love Python and Flask, but of course using them would have meant that all processing would have had to be done on the server. One the one hand I could have used libappstream that way to create the XML, format it and validate it, but on the other hand I would have had to host the Python app on my own server, find a place at Purism/Debian/GNOME/KDE or get it housed at Freedesktop somehow (which would have taken a while to arrange) and I really wanted to have a permanent location for this application immediately. Additionally, I didn t want people to send the details of new unpublished software to my server.
TypeScript
I must say that I really like TypeScript as a language compared to JavaScript. It is not really revolutionary (I looked into Dart and other ways to compile $stuff to JavaScript first), but it removes just enough JavaScript weirdness to be pleasant to use. At the same time, since TS is a superset of JS, JavaScript code is valid TypeScript code, so you can integrate with existing JS code easily. Picking TS up took me much less than an hour, and most of its features you learn organically when working on a project. The optional type-safety is a blessing and actually helped me a few times to find an issue. It being so close to JS is both a strength and weakness: On the one hand you have all the JS oddities in the language (implicit type conversion is really weird sometimes) and have to basically refrain from using them or count on the linter to spot them, but on the other hand you can immediately use the massive amount of JavaScript code available on the web.
Angular
The Angular web framework took a few hours to pick up there are a lot of concepts to understand. But ultimately, it s manageable and pretty nice to use. When working at the system level, a lot of complexity is in understanding how the CPU is processing data, managing memory and using the low-level APIs the operating system provides. With the web application stuff, a lot of the complexity for me was in learning about all the moving parts the system is comprised of, what their names are, what they are, and what works with which. And that is not a flat learning curve at all. As C developer, you need to know how the computer works to be efficient, as web developer you need to know a bunch of different tools really well to be productive.
One thing I am still a bit puzzled about is the amount of duplicated HTML templates my project has. I haven t found a way to reuse template blocks in multiple components with Angular, like I would with Jinja2. The documentation suggests this feature does not exist, but maybe I simply can t find it or there is a completely different way to achieve the same result.
NPM Ecosystem
The MetaInfo Creator application ultimately doesn t do much. But according to GitHub, it has 985 (!!!) dependencies in NPM/NodeJS. And that is the bare minimum! I only added one dependency myself to it. I feel really uneasy about this, as I prefer the Python approach of having a rich standard library instead of billions of small modules scattered across the web. If there is a bug in one of the standard library functions, I can submit a patch to Python where some core developer is there to review it. In NodeJS, I imagine fixing some module is much harder.
That being said though, using npm is actually pretty nice there is a module available for most things, and adding a new dependency is easy. NPM will also manage all the details of your dependency chain, GitHub will warn about security issues in modules you depend on, etc. So, from a usability perspective, there isn t much to complain about (unlike with Python, where creating or using a module ends up as a fight the system event way too often and the question which random file do I need to create now to achieve what I want? always exists. Fortunately, Poetry made this a bit more pleasant for me recently).
So, tl;dr for this section: The web application development excursion was actually a lot of fun, and I may make more of those in future, now that I learned more about how to write web applications. Ultimately though, I enjoy the lower-level software development and backend development a bit more.
Summary
Check out the MetaInfo Creator and its source code, if you want to create MetaInfo files for a GUI application, console application, addon or service component quickly.
Welcome to the February 2020 report from the Reproducible Builds project.
One of the original promises of open source software is that distributed peer review and transparency of process results in enhanced end-user security. However, whilst anyone may inspect the source code of free and open source software for malicious flaws, almost all software today is distributed as pre-compiled binaries. This allows nefarious third-parties to compromise systems by injecting malicious code into ostensibly secure software during the various compilation and distribution processes.
The motivation behind the reproducible builds effort is to provide the ability to demonstrate these binaries originated from a particular, trusted, source release: if identical results are generated from a given source in all circumstances, reproducible builds provides the means for multiple third-parties to reach a consensus on whether a build was compromised via distributed checksum validation or some other scheme.
In this month s report, we cover:
If you are interested in contributing to the project, please visit our Contribute page on our website.
Omar Navarro Leija, a PhD student at the University Of Pennsylvania, published a paper entitled Reproducible Containers that describes in detail the workings of a new user-space container tool called DetTrace:
All computation that occurs inside a DetTrace container is a pure function of the initial filesystem state of the container. Reproducible containers can be used for a variety of purposes, including replication for fault-tolerance, reproducible software builds and reproducible data analytics. We use DetTrace to achieve, in an automatic fashion, reproducibility for 12,130 Debian package builds, containing over 800 million lines of code, as well as bioinformatics and machine learning workflows.There was also considerable discussion on our mailing list regarding this research and a presentation based on the paper will occur at the ASPLOS 2020 conference between March 16th 20th in Lausanne, Switzerland.
The many virtues of Reproducible Builds were touted as benefits for software compliance in a talk at FOSDEM 2020, debating whether the Careful Inventory of Licensing Bill of Materials Have Impact of FOSS License Compliance which pitted Jeff McAffer and Carol Smith against Bradley Kuhn and Max Sills. (~47 minutes in).
Nobuyoshi Nakada updated the canonical implementation of the Ruby programming language a change such that filesystem globs (ie. calls to list the contents of filesystem directories) will henceforth be sorted in ascending order. Without this change, the underlying nondeterministic ordering of the filesystem is exposed to the language which often results in an unreproducible build.
Vagrant Cascadian reported on our mailing list regarding a quick reproducible test for the GNU Guix distribution, which resulted in 81.9% of packages registering as reproducible in his installation:
$ guix challenge --verbose --diff=diffoscope ...
2,463 store items were analyzed:
- 2,016 (81.9%) were identical
- 37 (1.5%) differed
- 410 (16.6%) were inconclusive
Jeremiah Orians announced on our mailing list the release of a number of tools related to cross-compilation such as M2-Planet and mescc-tools-seed. This project attemps a full bootstrap of a cross-platform compiler for the C programming language (written in C itself) from hex, the ultimate goal being able to demonstrate fully-bootstrapped compiler from hex to the GCC GNU Compiler Collection. This has many implications in and around Ken Thompson s Trusting Trust attack outlined in Thompson s 1983 Turing Award Lecture.
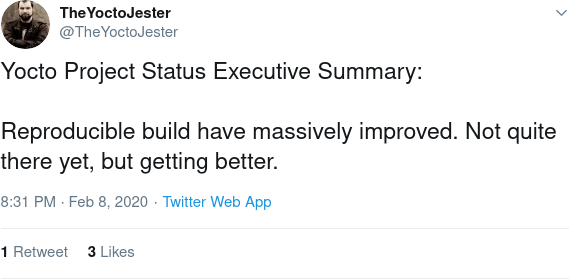
Twitter user @TheYoctoJester posted an executive summary of reproducible builds in the Yocto Project:
Finally, Reddit user tofflos posted to the /r/Java subreddit asking about how to achieve reproducible builds with Maven and Chris Lamb noticed that the Linux kernel documentation about reproducible builds of it is available on the kernel.org homepages in an attractive HTML format.
Chris Lamb created a merge request for the core debian-installer package to allow all arguments and options from sources.list files (such as [check-valid-until=no] , etc.) in order that we can test the reproducibility of the installer images on the Reproducible Builds own testing infrastructure. (#13)
Thorsten Glaser followed-up to a bug filed against the dpkg-source component that was originally filed in late 2015 that claims that the build tool does not respect permissions when unpacking tarballs if the umask is set to 0002.
Matthew Garrett posted to the debian-devel mailing list on the topic of Producing verifiable initramfs images as part of a wider conversation on being able to trust the entire software stack on our computers.
59 reviews of Debian packages were added, 30 were updated and 42 were removed this month adding to our knowledge about identified issues. Many issue types were noticed and categorised by Chris Lamb, including:
openstack_pkg_tools_python_shebang_and_dependenciesbuild_path_in_code_generated_by_dgbus_codegenrandom_argument_handling_in_javatools_jh_buildfortran_captures_build_path
In openSUSE, Bernhard M. Wiedemann published his monthly Reproducible Builds status update as well as provided the following patches:
python-rpm-macros (do not save time-based .pyc files for tests)solfege (filesystem ordering issue sent upstream via email; package is orphaned upstream)DVDStyler (zip timestamps, submitted upstream)python-pikepdf (recreate unreproducible .pyc files)
diffoscope is our in-depth and content-aware diff-like utility that can locate and diagnose reproducibility issues. It is run countless times a day on our testing infrastructure and is essential for identifying fixes and causes of nondeterministic behaviour.
Chris Lamb made the following changes this month, including uploading version 137 to Debian:
sng image utility appears to return with an exit code of 1 if there are even minor errors in the file. (#950806)classes2.dex, classes3.dex from .apk files extracted by apktool. (#88)str.format if we are just returning the string. [ ]Command.VALID_RETURNCODES. [ ]Vcs-Git to specify the debian packaging branch. [ ]
reprotest is our end-user tool to build same source code twice in widely differing environments and then checks the binaries produced by each build for any differences. This month, versions 0.7.13 and 0.7.14 were uploaded to Debian unstable by Holger Levsen after Vagrant Cascadian added support for GNU Guix [ ].
There was more work performed on our documentation and website this month. Bernhard M. Wiedemann added a Java Gradle Build Tool snippet to the SOURCE_DATE_EPOCH documentation [ ] and normalised various terms to unreproducible [ ].
Chris Lamb added a Meson.build example [ ] and improved the documentation for the CMake [ ] to the SOURCE_DATE_EPOCH documentation, replaced anyone can with anyone may as, well, not everyone has the resources, skills, time or funding to actually do what it refers to [ ] and improved the pre-processing for our report generation [ ][ ][ ][ ] etc.
In addition, Holger Levsen updated our news page to improve the list of reports [ ], added an explicit mention of the weekly news time span [ ] and reverted sorting of news entries to have latest on top [ ] and Mattia Rizzolo added Codethink as a non-fiscal sponsor [ ] and lastly Tianon Gravi added a Docker Images link underneath the Debian project on our Projects page [ ].
rdiff-backup fixed, build date in Python manpageclick-man fixed, toolchain, build date in Python manpagerpm report filesystem-order related nondeterminismpython-enaml report nondeterministic .enamlc compiler outputk9s datepython-xcffib fix a test with a race conditionsnakemake.designate.pynwb.python-oslo.reports.mate-desktop (forwarded upstream).javatools.xavs2.snapd-glib (forwarded upstream).openstack-pkg-tools.python-django (Always build the documentation in English)python_example (sort glob / readdir)autogen.autoconf.m4.intltool.binutils-dev.yodl-doc.gdb-source.automake-1.15.libtool.
We operate a fully-featured and comprehensive Jenkins-based testing framework that powers tests.reproducible-builds.org. This month, the following changes were made by Holger Levsen:
builtin-pho database of .buildinfo files. This has resulted in so that we now know that Debian bullseye contains 4,557 source packages for the amd64 architecture without corresponding .buildinfo files and 25,668 source packages with .buildinfo files. [ ][ ][ ][ ][ ]buildinfo@ to the root user. [ ]devscripts from buster-backports [ ].i386 architecture, to allow the latter to catch up a bit. [ ]
In addition, Mattia Rizzolo added an Apache web server redirect for buildinfos.debian.net [ ] and reverted the reshuffling of arm64 architecture builders [ ]. The usual build node maintenance was performed by Holger Levsen, Mattia Rizzolo [ ][ ] and Vagrant Cascadian.
#reproducible-builds on irc.oftc.net.
rb-general@lists.reproducible-builds.org
This month s report was written by Bernhard M. Wiedemann, Chris Lamb and Holger Levsen. It was subsequently reviewed by a bunch of Reproducible Builds folks on IRC and the mailing list.
I was assigned 20 hours of work by Freexian's Debian LTS initiative
and worked 19.25 hours this month, so I will carry over 0.75 hours to
March.
I prepared and, after review, released Linux 3.16.82. I then
rebased the Debian package onto that, but haven't yet sent a
request for testing. I have started preparing and testing the
next update to Linux 3.16.
I backported the Linux 4.9 package that was included in the stretch
point release (Debian 9.12) and uploaded it to jessie. I prepared

DLA
2114-1 covering this update.
I also replied to questions from LTS contributors and users, sent to
the lts-security alias or on the public mailing list.
Beef Chili Serves 5-7. Active time: 20m. Total time: 90m. Ingredients:Cooked beans two days in a row in order to deliver this masterpiece pic.twitter.com/VzIlPKKosJ e. hashman (@ehashdn) March 3, 2020
Frequently Asked Questions Q: Why wait until basically the end to add salt?before and after pic.twitter.com/CgkeCDPOaO e. hashman (@ehashdn) March 3, 2020
Sealioning (also spelled sea-lioning and sea lioning) is a type of trolling or harassment which consists of pursuing people with persistent requests for evidence or repeated questions, while maintaining a pretense of civility and sincerity.[1][2][3][4] It may take the form of "incessant, bad-faith invitations to engage in debate".[5]
Tone policing (also tone trolling, tone argument, and tone fallacy) is an ad hominem (personal attack) and antidebate tactic based on criticizing a person for expressing emotion. Tone policing detracts from the validity of a statement by attacking the tone in which it was presented rather than the message itself.
"A brawler who tattoos a message onto his knuckles does not throw every punch with the weight of First Amendment protection behind him," the brief stated. "Conduct like this does not constitute speech, nor should it. A deliberate attempt to cause physical injury to someone does not come close to the expression which the First Amendment is designed to protect."
It s no secret that times are changing. It used to be that men were men, jokes were jokes, and all facts came from one white guy in a suit who you trusted because he looked like your dad. Now I know I could get in a lot of trouble for just saying this, but I don t care because someone has to tell the truth: These days, you can t say anything racist at all without being called a racist.
Russia's neighbor has developed a plan for countering misinformation. Can it be exported to the rest of the world?
So, I wrote my BIFF Response but Marvin wrote me another angry email. Actually, he wrote 6 more this week, so what s up with that? Why didn t he stop after my first email?
The BIFF Response Method will teach you how to respond to angry emails, texts, or social media posts while maintaining your dignity and personal power.
Map of conflict
I've been practising Non-Violent Communication (NVC) for several years. It helps me to better understand my feelings and needs. The concepts of NVC can also help to look at conflicts. I would like to introduce a way to look at conflict using the basic concepts of NVC:
Here is my monthly update covering what I have been doing in the free software world during February 2020 (previous month):
warnings.warn method over logging.warning [...] and to document missing archive keyword argument to the get_bugs call [...].
libmate-desktop library component of the MATE Desktop Environment I submitted a pull request to make the build reproducible in/around various dialogs. [...]
python_example, an example pybind11 module built with a Python-based build system, I suggested sorting the extension sources to ensure a reproducible build in any projects based on this template. [...]
snapd component of the Snappy package manager. Here, I opened a pull request to make the build reproducible. [...]
For the Tails privacy-oriented operating system, I uploaded the following packages to Debian:
0.1.8-5):
dh-python to Build-Depends. (#952366)sphinxdoc:Depends to binary package dependencies. (#832588)tool:pytest section in setup.cfg over plain "pytest".dh-systemd with debhelper version 9.20160709, specify Rules-Requires-Root: no, use secure URL in debian/copyright, update Vcs-Git & Vcs-Browser and bump the package's Standards-Version to 4.5.0.0.2-9):
One of the original promises of open source software is that distributed peer review and transparency of process results in enhanced end-user security. However, whilst anyone may inspect the source code of free and open source software for malicious flaws, almost all software today is distributed as pre-compiled binaries. This allows nefarious third-parties to compromise systems by injecting malicious code into ostensibly secure software during the various compilation and distribution processes.
The motivation behind the Reproducible Builds effort is to provide the ability to demonstrate these binaries originated from a particular trusted source release: if identical results are generated from a given source in all circumstances, reproducible builds provides the means for multiple third-parties to reach a consensus on whether a build was compromised via distributed checksum validation or some other scheme.
The initiative is proud to be a member project of the Software Freedom Conservancy, a not-for-profit 501(c)(3) charity focused on ethical technology and user freedom.
Conservancy acts as a corporate umbrella allowing projects to operate as non-profit initiatives without managing their own corporate structure. If you like the work of the Conservancy or the Reproducible Builds project, please consider becoming an official supporter.
This month, I:
libmate-desktop library component of the MATE Desktop Environment I submitted a pull request to make the build reproducible in/around various dialog boxes, etc. [...]
snapd component of the Snappy package manager. Here, I opened a pull request to make the build reproducible. [...]
python_example, an example pybind11 module built with a Python-based build system, I suggested sorting the extension sources to ensure a reproducible build in any projects based on this template. [...]
debian-installer package to allow all arguments from sources.list files (such as [check-valid-until=no]) in order that we can test the reproducibility of the installer images on the Reproducible Builds own testing infrastructure. (#13)
openstack-pkg-tools to fix a curious issue where packages built differently if they built "too fast" for example, if we built for both Python 3.7 and Python 3.8 but the installation of the latter occurs within the same wall clock second of the former, the Python 3.8 version will not overwrite the Python 3.7 version and lead to a shebang of #!/usr/bin/python3.7, whilst if it does not occur within the same second, the shebang will be overwritten
to #!/usr/bin/python3.8. (#952762)
#include directives), designate (embedded build path), javatools (nondeterminstic parsing of command-line variables), mate-desktop (build timestamps), msgpack-c (embeds build path), pynwb (embedded timestamps in test files), python-oslo.reports (nondeterminstic/random numbers), snapd-glib (embedded build path) & xavs2 (embedded timestamps).
Meson.build example to the SOURCE_DATE_EPOCH documentation [...], replacing instances of "anyone can" with "anyone may" [...], correcting/improving the logic to skip commits when generating drafts [...][...][...], etc.
In our tooling, I also made the following changes to diffoscope, our in-depth and content-aware diff utility that can locate and diagnose reproducibility issues, including uploading version 137 to Debian:
sng image utility will return 1 if there are even minor errors in the file. (#950806)classes2.dex, classes3.dex from .apk files. (#88)str.format if we are just returning the string. [...]Command.VALID_RETURNCODES. [...]hsd, a blockchain-based top-level domain DNS protocol implementation that underpins Handshake and worked on some initial packaging. (#952472)
Debian LTS
This month I have worked 18 hours on Debian Long Term Support (LTS) and 12 hours on its sister Extended LTS project.
cacti (CVE-2020-8813), golang-go.crypto (CVE-2020-9283), netty, nodejs (CVE-2019-15605), nova (CVE-2015-9543), ntp, otrs2 (CVE-2019-11358)), php-horde-data (CVE-2020-8518), proftpd-dfsg, python-bleach (CVE-2020-6802), python-django, python-pysaml2, qtbase-opensource-src (CVE-2015-9541), ruby-rack, salt, sudo, systemd (CVE-2020-1712), waitress (CVE-2020-5236), wpa (CVE-2019-5061) & yara
1.10.7-2+deb9u8 to Debian stretch and 1.11.28-1~deb10u1 for Debian buster to address CVE-2020-7471, a potential SQL injection vulnerability.
2.2.10-1) New upstream security release. (#950581)
6.0~rc1-2 Add support for Transport Layer Security added in Redis 6.x (#951255) and add a comment regarding why we export a MAKEFLAGS variable in debian/rules.
5.0.7-2:
2.13+dfsg-2) Fix a regression in handling of CVE-2015-1197 with respect to the --no-absolute-filenames argument by reverting part of an upstream commit. (#946267 #946469)
0.14.0-6) Set the Bug-Database, Bug-Submit, Repository and Repository-Browse upstream metadata fields and rely on pre-initialised dpkg-architecture variables in debian/rules.
1.5.22-1 New upstream release.1.5.22-2 Apply a patch to fix build failures on the s390x architecture. (#950777)20.0.4-2 Set the upstream metadata fields (Repository, Repository-Browse, etc.), bump Standards-Version to 4.5.0.20.0.4-3 Specify that the gunicorn binary package provides the httpd-wsgi3 virtual package. (#952706)4.0.23-2:
future=+lfs to DEB_BUILD_MAINT_OPTIONS to support operating on large files. (#949665)gitlab-ci.yml.Rules-Requires-Root: no and bump the Standards-Version to 4.5.0.4.0.23-3 Drop quotes from DEB_BUILD_MAINT_OPTIONS export line. (#951037)
4.7.6-1) on behalf of Alexandre Rossi.
sbuild is a tool used by those maintaining packages in Debian, and
derived distributions such as Ubuntu. When used correctly, it can
catch a lot of categories of bugs before packages are uploaded. It
does this by building the package in a clean environment, and then
running the package through the Lintian, piuparts, adequate and
autopkgtest tools. However, configuring sbuild so that it makes use
of all of these tools is cumbersome.
In response to this complexity, I wrote a module for the
Propellor configuration management system to prepare a system such
that a user can just go ahead and run the sbuild(1) command.
This module is useful on one s development laptop if you need to
reinstall your OS, you don t have to look up the instructions for
setting up sbuild again. But it s also useful on throwaway build
boxes. I can instruct propellor to provision a new virtual machine to
build packages with sbuild, and all the different tools mentioned
above will be connected together for me.
I just uploaded Propellor version 5.1.0 to Debian unstable. The
version overhauls the API and internals of the Sbuild module to take
better advantage of Propellor s design. I won t get into those
details in this post. What I d like to do is demonstrate how you can
set up sbuild on your own machines, using Propellor.
Getting started with Propellor
apt-get install propellor, and then propellor --init.
You ll be offered two setups, options A and B. I suggest starting
with option B.
If you never use Propellor for anything other than provisioning
sbuild, you can stick with option B. If this tutorial makes you want
to check out more features of Propellor, you might consider switching
to option A and importing your old configuration.
Open ~/.propellor/config.hs. You will see something like this:
-- The hosts propellor knows about.
hosts :: [Host]
hosts =
[ mybox
]
-- An example host.
mybox :: Host
mybox = host "mybox.example.com" $ props
& osDebian Unstable X86_64
& Apt.stdSourcesList
& Apt.unattendedUpgrades
& Apt.installed ["etckeeper"]
& Apt.installed ["ssh"]
& User.hasSomePassword (User "root")
& File.dirExists "/var/www"
& Cron.runPropellor (Cron.Times "30 * * * *")
iris, so I might replace the above with this:
-- The hosts propellor knows about.
hosts :: [Host]
hosts =
[ iris
]
-- My laptop.
iris :: Host
iris = host "iris.silentflame.com" $ props
& osDebian Testing X86_64
& are the properties of the host
iris. Here, I ve removed all properties except the osDebian
property, which informs propellor that iris runs Debian testing and
has the amd64 architecture.
The effect of this is that Propellor will not try to change anything
about iris. In this tutorial, we are not going to let Propellor
configure anything about iris other than setting up sbuild.
(The osDebian property is a pure info property, which means that
it tells Propellor information about the host to which other
properties might refer, but it doesn t itself change anything about
iris.)
Telling Propellor to configure sbuild
First, add to the import lines at the top of config.hs the lines:
import qualified Propellor.Property.Sbuild as Sbuild
import qualified Propellor.Property.Schroot as Schroot
-- The hosts propellor knows about.
hosts :: [Host]
hosts =
[ iris
]
-- My laptop.
iris :: Host
iris = host "iris.silentflame.com" $ props
& osDebian Testing X86_64
& Apt.useLocalCacher
& sidSchrootBuilt
& Sbuild.usableBy (User "spwhitton")
& Schroot.overlaysInTmpfs
& Cron.runPropellor (Cron.Times "30 * * * *")
where
sidSchrootBuilt = Sbuild.built Sbuild.UseCcache $ props
& osDebian Unstable X86_64
& Sbuild.update period Daily
& Sbuild.useHostProxy iris
Apt.useLocalCacher set up apt-cacher-ng and points apt on iris
at the cacher. This is the most efficient way to share a cache of
packages between apt on iris, and apt within the sbuild chroot.sidSchrootBuilt builds the sbuild schroot. Unfortunately, we have
to use a where clause because of Haskell s rules about operator
precedence. But it s just a simple substitution: imagine that &
Sbuild.built ... replaces & sidSchrootBuilt.
osDebian specifies that this is a Debian unstable chroot. You
can easily change this, or add another chroot, for building
stable backports, etc.Sbuild.UseCcache enables ccache for builds in this chroot.
You can replace this with Sbuild.NoCcache when building a
package which is broken by ccache, which happens from
time-to-time.Sbuild.update updates the chroot once per day.Sbuild.useHostProxy iris causes Propellor to propagate iris s
apt proxy into the chroot, so that apt in the chroot will also
use iris s apt cacher.Sbuild.usableBy adds spwhitton to the right group, so that he is
allowed to invoke sbuild(1).Schroot.overlaysInTmpfs configures sbuild to install build
dependencies and build packages in tmpfs. You can omit this
property on machines with low amounts of memory.Cron.runPropellor sets up a cron job to re-run propellor once per
hour. This is needed to ensure that things like Sbuild.update
actually happen. It will also normalise sbuild configuration files,
replace chroots that you accidently deleted, etc.propellor iris.silentflame.com.
In this configuration, you don t need to worry about whether the
hostname iris.silentflame.com actually resolves to your laptop.
However, it must be possible to ssh root@localhost.
This should be enough that spwhitton can:
$ sbuild -A --run-lintian --run-autopkgtest --run-piuparts foo.dsc
Further configuration
It is easy to add new schroots; for example, for building backports:
...
& stretchSchrootBuilt
...
where
...
stretchSchrootBuilt = Sbuild.built Sbuild.UseCcache $ props
& osDebian (Stable "stretch") X86_64
& Sbuild.update period Daily
& Sbuild.useHostProxy iris
where
sidSchrootBuilt = Sbuild.built Sbuild.UseCcache $ props
& osDebian Unstable X86_64
& Sbuild.update period Daily
& Apt.mirror "https://foo.mirror/debian/"
& Apt.installed ["apt-transport-https"]
Next.