Search Results: "ag"

7 March 2007

Thijs Kinkhorst: Package deal

Today are provincial elections in The Netherlands, one of the least visible governments in this country, so it's hard to decide what would be a good choice. Add to that that the chosen members will in turn choose the (national) Senate. I have never been fond of package deals. I do not necessarily vote for the same party on the provincial level as I do nationally, because these two layers deal with distinctly different classes of decisions. After casting my vote I returned home with a little doubt of whether I'd made the right choice, until I realised which 9 parties I didn't vote for. The fact that my vote did not go to the parties that I don't trust our province or senate with is far more useful than the relatively small difference between the candidates I considered.

Ross Burton: WANTED

This may sound a little strange but does anyone have linux-image-2.6.20-6-generic and the matching restricted modules packages for Ubuntu Feisty? They've fallen out of the Ubuntu archive, the morgue doesn't exist any more, and newer kernels don't work with Scratchbox. Thanks! NP: Oneiric, Boxcutter

Andrew Pollock: [tech] iLO shenanigans

One of the many things I'm working on in my copious amounts of spare time is setting up the server that HP donated Linux Australia after I think linux.conf.au 2006. Said server has iLO, which facilitates remote power management and remote console, both things I want to have working on this server before it goes into production. Jon's been madly poking holes in his firewall for me so I could access the iLO stuff. I'm already liking it better than Dell's BMC, because it has things like SSH, although the whole thing hasn't been without some adventures. I fiddled around via the web interface and added an account for myself and an SSH key. Then I tried to SSH in, and promptly got stuff like
buffer_get_ret: trying to get more bytes 4 than in buffer 0
buffer_get_int: buffer error
straight after what looked like a successful connection, and then the SSH connection got terminated. I did a pile of Google searching, and found people had to disable environment variable sending, and agent forwarding to get this to stop happening. Interestingly, I can't find a way to disable SendEnv on a per-host basis with OpenSSH, if it's been set in /etc/ssh/ssh_config, which is kind of annoying. So after solving the problem of gaining SSH access to the iLO, I then battled with the remote console. The host already had a throwaway Linux installation on it, but the remote console kept freaking out about the console being in graphics mode. I figured this was because it was using a frame-buffer. No problem, I just needed to boot with vga=normal. Problem was, GRUB was configured with hiddenmenu so I had 3 seconds to hit Escape before it charged off and booted up. Not that big a deal you'd think, except to get out of the remote console and back to the iLO prompt, you have to hit Escape (, so the iLO eats Escape keys for breakfast. After having a bit of debate with some mainly Red Hat-oriented sysadmins on #sage-au, it turned out that RHEL has a patch so that GRUB accepts any key, not just Escape to present the menu. That was no use to me, as the box wasn't running RHEL. And all I was asking for was if anyone had any iLO experience, no whether or not "any key" was the equivalent of Escape. Sheesh. It turned out that I needed to press Escape twice in that initial 3 seconds, with probably sufficient pause between the two presses for it to register properly, in order for an Escape character to be sent to GRUB. Fun.

Eddy Petrișor: suspend-to-*

Christian is talking about problems with suspend-to-RAM and suspend-to-disk and the major cause of issue being the non-free Conexant HSF modem driver.

Since I got my new laptop I had my share of issues with suspend-to-*.

At the beginning everything worked fine, out of the box. Then (I think) I realized that my video card (damned ATI) was not working in accelerated mode, so I decided to fix that and since the card is too new to be even listed as existing on radeon driver's support page, I had to use fglrx.

Then I made the DRI work but suspend-to-ram ceased to work (after a few testing->experimental; experimental--> upstream updates, both ways); I started using the experimental driver (8.31.5-1) which proved to be stable enough (this time) just for suspend-to-disk, if it had dri enabled, or suspend-to-ram, if not having DRI enabled.

I even made a patch to help the maintainer update faster the package (I added a get-orig-source rule in debian/rules).

Now I have ported the patches in the debian package and updated it to 8.33.6 and I am running that. Problems include: consoles are not accessible, but suspend-to-ram and dri work. I will submit a bug with the patch to updated fglrx package.

I expect that I'll try soon to update to 8.34.8 in the hope that I will get all the things working: suspend-to-*, consoles, dri.

Uwe Hermann: LinuxBIOS with X11 server, completely in Flash ROM

LinuxBIOS and X11 screenshot 1
LinuxBIOS and X11 screenshot 2 Now, this is one cool project (and video) from Alan Carvalho de Assis (and friends), as announced on the LinuxBIOS mailing list: LinuxBIOS with X Server Inside (YouTube video). The setup: LinuxBIOS + a Linux kernel + BusyBox + a tiny X11 server (Kdrive) + the Matchbox window manager + rxvt. All of this in a normal BIOS chip (2 MB), without any hard drive connected (who needs hard drives when you can fit everything in the BIOS just fine)... The thing boots into BusyBox in less than 6 seconds, then in ca. 2 seconds into X11 + rxvt. There's probably even room for improvement there... It seems there will be an OGG Theora version of the video soon, and I hope a small HOWTO about the project, too. More LinuxBIOS-related screenshots and videos are available in the wiki btw., and a bunch more will follow soon...

Bastian Venthur: Etch Won t Ship Wordpress

So the security team decided to kick Wordpress from Etch since they assume it won’t be sanely maintainable over the course of 30-36 months. This practice surprises me a bit, especially since upstream plans to support the 2.0.x series until 2010 and the package is currently very well maintained by Kai Hendry. So what’s the problem? Is it manpower? I guess not, since Kai even offered to provide security updated packages when they become available, which was rejected with a friendly “EOD for me.“. Anyway, since my blog will become unsupported soon, I need to switch to something else. So dear lazyweb, what is the next best alternative to WP available in Etch? I need good comment spam protection and an option to import my old wordpress entries.

6 March 2007

John Goerzen: Re-Examining Darcs & Mercurial

I recently wrote an article or two about distributed version control systems.

I've been using Darcs since 2005. I switched to Darcs, in fact, 10 days after the simultaneous founding announcements of git and Mercurial.

Overall, I have been happy. I continue to believe that it is the most distributed of the distributed VCSs, which is a Good Thing.

However, I have lately started having trouble with Darcs hanging while working on my Debian packages. My post to the Darcs user list drew out a few other people whith this problem, which is a design flaw of Darcs.

So I revisited the VCS landscape. I re-examined git, Mercurial, and bzr. I eventually decided to give Mercurial a try. I avoided git because I write some code that is portable to Windows, and git isn't (or isn't very well). Also, git is complex to pick up for me, and I certainly don't want to force something complex onto my contributors. bzr seemed to still have some strange behaviors that it's had for awhile, and I couldn't find even one advantage of it over Mercurial. So off I went with Mercurial.

I quickly learned a bit of a philosophical difference from Darcs to Mercurial.

Darcs avoids conflicts at all costs. Mercurial makes handling conflict easy and, in many cases, automatic.

It is exactly this Darcs behavior that permits both is excellent "darcs send" feature (still unmatched in any other VCS), but also causes its hang problems.

I found Mercurial quite pleasant to work with, and *fast*. It seems to be edging out git in speed tests sometimes these days.

It is easy to get started with Mercurial. The mq system -- similar to quilt or other patch-management programs -- is really quite an amazing hybrid between patch management and version control. I frankly don't see any need for other patch-management tools anymore.

Mercurial has a "patchbomb" feature where you can select a range of changesets to send off, and it will generate nice emails with one changeset per email, and send them to your selected destination, optionally with an introductory message. The normal way of interacting with other Mercurial users is via the hg export/import commands, which send around simple unified diffs plus some additional header information, optionally in the git extended diff format.

I am happy with Mercurial and am in the process of converting my Debian repositories from Darcs to Mercurial. I'm going to keep my personal code in Darcs for the moment because "darcs send" is still easier than "hg email", but that may change before long, depending on how my experience goes.

I'd encourage others to give Mercurial a try. The community is also very nice and helpful.

I have contributed patches to Tailor to make it make exact copies of Darcs repos into Mercurial, which are now in its Darcs repo. There is also a thread on the Mercurial list with some of my initial questions/concerns coming from a Darcs perspective.

Enrico Zini: why-free-software

A reminder on why we do Free Software Some months ago I needed to find out if proper forward-only cursors were implemented in the ODBC driver for MySQL. I didn't go very far with the documentation, but I've been diving in its source code and within 30 minutes I knew everything there was to know about the subject. Now, after years I haven't touched proprietary software at all, I've been asked to port dballe to use the Oracle ODBC driver. I had a similar problem: find out how to use scrollable cursors with Oracle's ODBC driver. The release notes (a file called ODBCRelnotesUS.htm that I probably can't put online without their consent) say that they're implemented since ages, but SQLSetStmtAttr always tells me that the driver does not support it. Maybe I have to enable it somewhere? Maybe it's a bug? I could have found out with one hour browsing this driver's source code, but that wasn't available. Instead, I had to spend a whole day of trial and error, google searching with all sort of keyword combinations, looking at strings output on the .so libraries, and in the end I still don't know. That porting project is now stuck indefinitely, and my customers had to pay for a full day of fruitless work. So, here's the reminder: If you base on 3rd party proprietary software, you can't provide a serious service.

Gunnar Wolf: Suspend to RAM and video cards not noticing

My dear comment-hating Bubulle, you forced me into writing yet another weblog entry :)
I have not yet worked it out completely, but it might be that your problems with suspend to RAM your Dell machine are related to having the Composite or AIGLX extensions loaded. This is just an hypothesis, and might be just wrong, but: So... Christian, have you tried the plainest X configuration? Have you tried maybe switching to one of the virtual consoles before suspending? Or maybe even shutting down your X session?
I hope this helps you chase down your problem. Do not worry, though - I don't want to be hugged/kissed to death by a cheese-eating translation-loving Frenchman.

Edd Dumbill: Using sparklines to aid conference proposal selection

In a recent article I explained some of the mechanics behind putting together the schedule for XTech 2007. We've just added new visualization features to Expectnation that make proposal choice easier, and I thought I'd show some examples from the XTech 2007 review voting. Sparklines, devised by Edward Tufte, are thumbnail sketches of data that succinctly convey patterns. When Nat Torkington used sparklines to show reviewer voting patterns for OSCON program committee, it seemed a helpful addition to make to Expectnation. The profile of each reviewer is interesting — are they a harsh marker, or liberal with the top grades? — but sparklines really come into their own when drawn per proposal. Here are some small screenshots from this year's XTech voting, anonymized of course.
High flyers High scoring chart Reviewers are pretty unanimous about this proposal, as 4.0 is the top grade in our scoring system. The lack of variance suggests that I ought to ensure that all the assigned reviewers put in their scores — this could be just one person voting.  High scoring chart High scoring chart These next two are the pretty typical distribution for highly graded proposals: mostly top marks and a few average ones.  Middle rankingSome of the more interesting trends show up when the scoring isn't biased to either the top or bottom ends of the scale.  Medium scoring chartThe reviewers are unanimous about this paper's soundness. It's not made anyone go "wow", but there's nothing to grumble about either.  Medium scoring chartThis proposal clearly polarises opinion, and is such stands a better chance than the unanimous 3.0 above. Perhaps the subject matter or approach is controversial or timely.


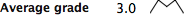

Medium scoring chartAnother proposal that divides the reviewers' opinions. It's also worth me checking here that I don't either have a pathologically strict reviewer, or at the other end, a reviewer with a wild passion for the cause this paper advocates.  Low scoring The quality of submissions is usually so good that I don't give low graded proposals much attention, but the sparklines could alert me to potential oversights. Low scoring chartThis proposal seems to polarise opinion between "rubbish" and "ok", so it's interesting to me to check out the subject matter and see if I'm missing something with potential.  Low scoring chart Low scoring chart These proposals were not received at all well.In summary, I'm delighted to find a solid practical application for sparklines. My thanks to Nat Torkington for the inspiration. 


Joerg Jaspert: New notebook ordered

So, the new notebook I want to have is ordered now. Now i only need to wait until it arrived. GOD, I HATE TO WAIT Can someone please do some magic to get us 24h into future? :) It finally is a HP nw9440, with 2G RAM, a 17” display and some additional stuff like extra battery pack, backpack, docking station and care pack. Not that cheap, but really nice. Tomorrow I have it, the guy from the shop said its on stock. All of what I want. And as we have a good relation with that shop I can trust that info. If only it would already be tomorrow. :)

Marc 'Zugschlus' Haber: EasyRSA on Debian for an OpenVPN CA

After asking for useable CA Software, I have finally settled on using EasyRSA. This is what I did to come across the packaging shortcomings of EasyRSA in Debian. Storing your CA Be sure that your CA is stored in a secure place. Don’t store it online, and make it accessible only to yourself. In my opinion, storing the the CA in a cryptoloop container file on a small 32 MB USB stick is a good idea. Cryptloop is rather easy today and available in the stock Linux kernel. I commonly use grml-crypt to manage the crypto loopback stuff:
sudo grml-crypt start /media/usb4/cryptoloop $MOUNTPOINT
Gotcha: don’t confuse sudo’s “password” prompt with grml-crypt’s “Enter LUKS passphrase” prompt, the cryptoloop password won’t bring you anywhere on the sudo prompt. Preparing the CA directory For the CA, create a dedicated directory in the mounted cryptoloop file system. You’re originally supposed to copy the entire EasyRSA directory tree in there, but I’d recommend to only link the files from your system’s EasyRSA directory to automatically take advantage of distribution updates. You’ll need at least these links:
lrwxrwxrwx 1 mh mh   56 Dec 25 23:23 openssl.cnf -> /usr/share/doc/openvpn/examples/easy-rsa/2.0/openssl.cnf
lrwxrwxrwx 1 mh mh   52 Dec 25 23:22 pkitool -> /usr/share/doc/openvpn/examples/easy-rsa/2.0/pkitool
lrwxrwxrwx 1 mh mh   60 Dec 25 23:23 whichopensslcnf -> /usr/share/doc/openvpn/examples/easy-rsa/2.0/whichopensslcnf
ln -s /usr/share/doc/openvpn/examples/easy-rsa/2.0/openssl.cnf .
ln -s /usr/share/doc/openvpn/examples/easy-rsa/2.0/pkitool .
ln -s /usr/share/doc/openvpn/examples/easy-rsa/2.0/whichopensslcnf .
Configuring your CA The only thing you cannot link is the vars file which contains your CA’s local settings:
export EASY_RSA=“$(pwd)”
export OPENSSL=“openssl”
export PKCS11TOOL=“pkcs11-tool”
export GREP=“grep”
export KEY_CONFIG=$($EASY_RSA/whichopensslcnf $EASY_RSA)
export KEY_DIR=“$EASY_RSA/keys”
# Issue rm -rf warning
echo NOTE: If you run ./clean-all, I will be doing a rm -rf on $KEY_DIR
export KEY_SIZE=1024
export CA_EXPIRE=3650
export KEY_EXPIRE=3650
export KEY_COUNTRY=“DE”
export KEY_PROVINCE=“”
export KEY_CITY=“”
export KEY_ORG=“Zugschlus.de”
export KEY_EMAIL=“mh+easyrsa-mh-openvpn@zugschlus.de”
export PKCS11_MODULE_PATH=“dummy”
export PKCS11_PIN=“dummy”
Comments have been removed from this file. Better copy the file from /usr/share/doc/openvpn/examples/easy-rsa/2.0/vars and edit it to your needs. I added the two PKCS11 variables since you won’t otherwise be able to issue certificate requests. Creating the CA Next, decide on a shell instance where you will do most operations, and source vars in there. Next, run /usr/share/doc/openvpn/examples/easy-rsa/2.0/clean-all. If you do this in a directory of an already-in-use EasyRSA CA, you’ll need to restore your backup. To actually initialize the CA, run pkitool --initca --pass. If you do not give the --pass parameter, you’ll create a CA that can issue certificates without asking for a passphrase, which might not be a brilliant idea. Choose a reasonably secure pass phrase. Creating Certificates - the simple and suboptimal way You can now simply proceed to create an arbitrary number of pairs of “private” keys and associated certificate by simply calling pkitool <clientname> and/or pkitool --server <servername>. Depending on your security policy, you can mandate the private keys to be protected by a passphrase (adding --pass to the command lines), but you’ll have the expense of being asked for the passphrase every time you start a new openvpn daemon. Creating Certificates the Right Way I have put the “private” in quotes since the keys created this way are not really private: The key was created on the box hosting the CA, was stored on the local (crypted) file system and needs to be moved to the target system via a secure channel. Doing so the right way is harder than expected, so it is usually the better way to keep the private key really private by creating it directly on the target system. On the target system, you need OpenVPN installed, and openssl. After the certificate was created, you can remove openssl again. Creating a private key is part of a key-pair generation process that also leaves a certificate request. The contents of the certificate request is public, and you can safely move it to the CA box and convert it to a certificate by signing the request. You only need to make sure that nobody exchanges your target system’s certificate request for her own before you sign it as you might end up certifying a wrong identity. For the rest of this document we’re going to assume that you have ssh access to the target system and have verified the ssh host key, so that you can be reasonably sure to be connected to the right system. To create a certificate request, you can use this script, which I have called create-easyrsa-cert-req:
#!/bin/bash
set -u
TMPDIR=“/tmp”
export OPENSSL=“openssl”
export PKCS11TOOL=“pkcs11-tool”
export GREP=“grep”
export KEY_CONFIG=“/usr/share/doc/openvpn/examples/easy-rsa/2.0/openssl.cnf”
export KEY_DIR=“$TMPDIR/keys.$$”
mkdir -p $KEY_DIR
export KEY_SIZE=1024
export KEY_EXPIRE=3650
export KEY_COUNTRY=“DE”
export KEY_PROVINCE=“”
export KEY_CITY=“”
export KEY_ORG=“Zugschlus”
export KEY_OU=“$(hostname --fqdn)”
export KEY_EMAIL=“mh+$(hostname)-ovpn-cert@zugschlus.de”
export DEBUG=1
umask 077
if [ “$ 1:-foo ” != “server” ]; then
  /usr/share/doc/openvpn/examples/easy-rsa/2.0/pkitool --csr $(hostname)
else
  /usr/share/doc/openvpn/examples/easy-rsa/2.0/pkitool --csr --server $(hostname)
fi
mv $TMPDIR/keys.$$/* .
rm -rf $TMPDIR/keys.$$
When called without parameters, it creates a certificate request for an OpenVPN client certificate, and when you call it with “server” as parameter, it will create a server certificate request. In any case, it will leave two files in the current directory. They are named after the current host name, and have the extensions .csr and .key. The .key file is your private key. keep it private! The .csr file is the certificate request which you can now move to the keys subdirectory of your CA directory via scp or other means such as an USB stick. To do the actual signing, invoke pkitool --sign <hostname> and enter the CA passphrase. You can ignore the error message that there was no .key file to chmod. Gotcha, when signing a server certificate, use pkitool --server --sign <hostname>. Move Certificate to the target host You can now move the certificate to the target system. Since you’re probably going to need the root certificate and the certificate revocation list as well, you can move the .key file (if created on the CA system), the .crt file, and ca.crt to the target system. These files are public, so there is no need for a secure channel. Revoking Certificates Since an OpenVPN server’s only means of authentication is to check whether the certificate presented by a client is signed by the “right” CA, the only way to revoke VPN access is to revoke the certificate. This is also done on the CA system by calling /usr/share/doc/openvpn/examples/easy-rsa/2.0/revoke-full <client-name>. This creates a crl.pem file which contains a list of all revoked certificates. You need to have a mechanism to distribute that list to all systems that might need it, and it is recommended to have this automated. Remember, if you do not distribute the .crl file, the systems are not going to know about revoked certificates.

Marc 'Zugschlus' Haber: Best-of-Mailing-Lists

Mailing lists of big and successful open source projects are these days flooded with clueless requests from newbies which obviously have not spent a second getting acquainted with the tool or with the basics of the underlying protocols. I’m going to publish some of the “best” of these messages in irregular intervals her, tagges with “best-of-mailing-list”. All articles tagged appropriately can be seen as blog entries. There is also an RSS feed.

Marc 'Zugschlus' Haber: DPotW: swaks

Description: SMTP command-line test tool
 swaks (Swiss Army Knife SMTP) is a command-line tool written in Perl
 for testing SMTP setups; it supports STARTTLS and SMTP AUTH (PLAIN,
 LOGIN, CRAM-MD5, SPA, and DIGEST-MD5). swaks allows to stop the SMTP
 dialog at any stage, e.g to check RCPT TO: without actually sending a
 mail.
 .
 If you are spending too much time iterating “telnet foo.example 25”
 swaks is for you.
A very important tool which makes debugging e-mail a breeze. A must for every mail admin.

Matt Brown: Dublin Bound!

I’ve accepted a job with Google and we’re shifting to Dublin! Back in January, Kat and I decided that it was about time we put thoughts into action, and booked some one-way plane tickets to get ourselves to Europe. Our plan is to spend at least a couple of years (more if I have my way) exploring the other side of the world and generally broadening our horizons. We leave NZ on the 31st of March flying on Emirates to Singapore. We plan to spend a couple of weeks in Malaysia visiting some of Kat’s extended family (who I’ve never met), followed by 3 nights in Singapore, a night in Dubai, finally ending up in London at Heathrow Airport on the 17th of April. Soon after we booked the flights I started applying for Jobs in Europe, as the prospect of converting NZD to EUR or GBP to live on is not at all attractive. I was immediately rejected by the first place I applied to (Data Connection) because I didn’t have straight A-grades in high school! (The recruiter said they didn’t even bother to look at my University Degree!). Luckily that wasn’t the only job that I had applied for! A day or two after hearing back from Data Connection, I received a call from one of the Google recruiters in Dublin, following up on the CV that I’d sent through via their website a week or two earlier. The rest, as they say, is history. I had a couple of phone interviews, followed by a whistle stop trip to Dublin (photos here) for 4 hours of onsite interviews, a week or two of waiting and finally an offer. I’ve just accepted the offer, and sometime after the 17th of April, I’ll be starting as a Linux/Unix Systems Administrator for Google in Dublin, Ireland! Moving to Dublin to work for Google seems to be somewhat of a trend these days, and I’m looking forward to catching up with all the other Debian people who have recently posted similar news. The realities of shifting across the world in less than a month are starting to sink in now! We left our apartment this weekend just gone, and we’re staying with my parents for a few weeks while we get all our household stuff into storage and sort out what we’re taking to Dublin with us. It’s a big job packing up a house and it’s scary looking at the amount of stuff we’ve accumulated over just two short years! Luckily we have some exciting opportunities to look forward and keep us motivated!

MJ Ray: Business: Links: 2003-03-06

Web Hosting - A Market for Lemons
This is a really irritating problem for hired webmasters. Too often, my prospective customers go and buy from someone else who has a slicker sales team but does a terrible job. Then what can you do? I'm honest with them about the flaws if they ask, but it'll be months before they have the money to fix their mistake - or sometimes years before they can escape their contract lock-in. Depressingly, this ends with "we find that there really aren't any good solutions to the lemons problem".
RIMU Rules
Tip from a coop ISP about a global hosting provider.
xinit considered harmful
Warning about a bad machine supplier.
Web Hosting Chat - The Number 1 in Web Hosting discussion Forums - powered by vBulletin
Possible information source about web hosting
Project Management Source: Ten Golden Rules
If I tried a little harder, I could probably make a top 10 top 10s.
10 Stupid Mistakes Made by the Newly Self-Employed
I think I've done half of these.
10 Business Lessons From a Snarky Entrepreneur
A more positive list from the same author.
10 Ways to Relaxify Your Workspace
Could I even do Top 10 Steve Pavlina Top 10s?
problog: work from home
Oh OK, here's a different author. Are all of these positives, though?
Little Known Ways to Brand on the Cheap: 99 Tips for Poor Web Startups
I keep returning to this list. Lots of good ideas.
Digit news - Most B-to-B Web sites fail
and we need those good ideas, as the statistics are horrible.
A Cambridge Co-operator: Fairtrade Fortnight
This is nearly over. Rush to your local co-op, co-operative food, co-op scottish or Welcome to get a big discount now.
Co-operatives' merger to create group to rival Sainsbury's Guardian Unlimited Business
Soon we'll be bigger than Sainsbury's.
Co-operative Bank February 07 eNews
Where some of the profits from the co-op group goes...
A Cambridge Co-operator: Phone Co-op Annual Results
A different co-op which I'm also in.
VoIP for Business 2007 - Welcome to the essential business communications experience!
Interesting, but I still can't get my office VoIP phone to work reliably...
Are .com and .net domains best? @ Problogger
The masses say .com, but my three .uk domains are going fine for my target audience. I wonder about .coop and .eu, but there's not much incentive yet.
Margaret Hodge announces Companies Act Implementation timetable Small Business Service
Argh a confusing consultation. Is it worth replying?

Gustavo Franco: Debian, get a life

"Second Life runs on 2,000 Intel and AMD servers in two co-location facilities in San Francisco and Dallas. The company has a commitment to open source, with servers running Debian Linux and the MySQL database. Linden Lab chose Debian Linux because the software is suited to scaling massively with a small IT staff, said Linden Lab CTO Cory Ondrejka. MySQL allows the server farms to scale horizontally, by adding large numbers of low-power servers as needed, rather than vertically, which would have required Second Life to run on a few, powerful systems, Miller said."
Joe Miller is VP of platform and technology development for Linden Lab.
Source: http://www.informationweek.com/news/showArticle.jhtml?articleID=197800179

We know that, but sometimes we spend more time and effort with pointless discussions. Discussions are good, don't get me wrong, but they need to start and end. Get a life, go squash some bugs, package something NEW and upload to experimental, write documentation or tell the word who else is using Debian. Debian is bigger than our own egos and debates.

Don't you care that Second Life uses Debian? Aren't you a Second Life user? I'm not a Second Life user, but if Joe Miller come out and tell the word that they use something else, a lot will go and say 'look, Debian is better than that, but the world don't care let us keep fighting'. Debian aims to be a universal operating system, and the universe is bigger than OFTC and lists.debian.org.

Alexander Schmehl: Conflict finder script - The next generation

I got some feedback for the script which tries to find conflicting packages I hacked together after the Chemnitzer Linux-Tage. Seems to be a useful tool, so it might be nice to add it to devscripts? Some criticized, that it won't work perfectly, since I only check against files mentioned in Contents-.gz where files / folder created in a maintainer scripts are not listed. I know that, but I don't know a useful way to solve the problem. It's better than nothing, and maybe I'll find later a way to add support for installation time created files. Thanks to Kevin Mark and Marc Bockschmidt who pointed me to some improvements for the script, which reduced the time the script takes dramatically! While my first hack needed for a simple package nearly 15 minutes, the new one is down to one or two minutes. Thanks! So please test it a bit; feedback is alway welcome. You can find the latest version at http://www.schmehl.info/tmp/conflicts". Special thanks to Alexander Wirt and Thomas Viehmann who did proof of concept rewrites in perl and python. Alexanders perl version is quite fast... but needs a huge amount of memory. Thomas' python version is very elegant! You don't need to understand python to understand his script. Nice done, but could need some further improvements; since it takes as much time nearly as my bash script. And since I hope it might be interesting for devscripts maintainer, and I'm not sure if they would like to add a dependency on python, I think my bash script has - for now - the lead :)) The script could still need some improvements. For example tweaking the code a bit; I'm sure many of the things I do with pipes from awk to another awk to sort (or something like that) can be cone my awk itself. I Just don't kno how. And instead of fetching the Contents-.gz from the main server, the script could tread it from the users prefered mirror... and maybe even support for other downloaders than wget.

Rapha&#235;l Hertzog: Alioth and OpenID

Stratus seeks for comments from Alioth admins. Yes I’d like to see OpenID integration with Gforge. The upstream situation is a bit difficult, so I don’t think that you’ll have official opinion from them. In my case, I want OpenID integration because it would be cool to offer a standard wiki and be able to define ACL on some pages which refer to the Alioth accounts that people are used to use. In the longer term, we have other web services which are going to need authentication (DWTT, new version of the PTS, …) in order to provide customized content and it would be great to rely on OpenID for that part. I’m waiting your patches! ;-) And next time you want an opinion from the Alioth admins, please mail us instead of hoping that we won’t miss your blog entry in planet.debian.org.

Christian Perrier: My suspend to disk works again

There are days like this where you get inspiration. Since about January (strange that one cannot never remember the beginning of such annoyances), neither suspend-to-ram nor suspend-to-disk were working anymore on my Dell latitude X1. Suspend to RAM indeed stopped working back in August 2006 for an unknown reason. The laptop indeed goes into sleep mode but, when waking up, the video card is not restored properly. A quite common problem, unfortunately. Why it suddenly stopped working is hard to explainn but as my laptop runs unstable and, usually, the latest Debian kernel, there may be an explanation somewhere betwwen kernel stuff and Xorg stuff. Since then, I had suspend to disk working pretty well until it suddenly stopped working back in January. The system was printing "Snapshotting system" on the screen and that's all. So, since then, I keep my laptop ON all the time, which is pretty bad when travelling (and I travel a lot all day long as I use public transportation with 3 connections morning and evening). Moreover, I cannot even completely close it because some moron at Dell has decided to hardcode in the BIOS that the laptop should enter suspend to RAM when the LID is closed. So, closing the laptop means....no more screen when opening it up. As a consequence, during last weeks, I had my laptop hald-closed in my bag with some random device inserted between the screen and the keyboard to prevent it to be entirely closed. Absolutely stupid. However, this morning, the Holy Grace touched me. I finally remembered that, for last New Year's Eve week-end, I did setup the Conexant HSF modem drivers on the laptop because I was staying at my mom's place with nothing but a phone line to get my mail. And, definitely, this was the explanation. As soon as I unload the Conexant driver before going to suspend to disk mode, the suspend to disk magically works again. Dammit. Once again a proof that Thou Shalt Never Use Non-Free Drivers. I'm now again a happy suspend to disk user. If someone, some day, can bring me back a working suspend to RAM, I'll hug kiss her him to death.

Next.

Previous.


