Search Results: "ron"

29 January 2017

Elena 'valhalla' Grandi: One Liberated Laptop

One Liberated Laptop

Immagine/fotohttp://social.gl-como.it/photos/valhalla/image/5a480cd2d5842101fc8975d927d030f3

After many days of failed attempts, yesterday @Diego Roversi finally managed to setup SPI on the BeagleBone White , and that means that today at our home it was Laptop Liberation Day!

We took the spare X200, opened it, found the point we were on in the tutorial installing libreboot on x200 https://libreboot.org/docs/install/x200_external.html, connected all of the proper cables on the clip and did some reading tests of the original bios.

Immagine/fotohttp://social.gl-como.it/photos/valhalla/image/77e61745d9c43833b7c0a4a919d17222

While the tutorial mentioned a very conservative setting (512kHz), just for fun we tried to read it at different speed and all results up to 16384 kHz were equal, with the first failure at 32784 kHz, so we settled on using 8192 kHz.

Then it was time to customize our libreboot image with the right MAC address, and that's when we realized that the sheet of paper where we had written it down the last time had been put in a safe place somewhere

Luckily we also had taken a picture, and that was easier to find, so we checked the keyboard map , followed the instructions to customize the image https://libreboot.org/docs/hcl/gm45_remove_me.html#ich9gen, flashed the chip, partially reassembled the laptop, started it up and a black screen, some fan noise and nothing else.

We tried to reflash the chip (nothing was changed), tried the us keyboard image, in case it was the better tested one (same results) and reflashed the original bios, just to check that the laptop was still working (it was).

It was lunchtime, so we stopped our attempts. As soon as we started eating, however, we realized that this laptop came with 3GB of RAM, and that surely meant "no matching pairs of RAM", so just after lunch we reflashed the first image, removed one dimm, rebooted and finally saw a gnu-hugging penguin!

We then tried booting some random live usb key https://tails.boum.org/ we had around (failed the first time, worked the second and further one with no changes), and then proceeded to install Debian.

Running the installer required some attempts and a bit of duckduckgoing: parsing the isolinux / grub configurations from the libreboot menu didn't work, but in the end it was as easy as going to the command line and running:


linux (usb0)/install.amd/vmlinuz
initrd (usb0)/install.amd/initrd.gz
boot


From there on, it was the usual debian installation and a well know environment, and there were no surprises. I've noticed that grub-coreboot is not installed (grub-pc is) and I want to investigate a bit, but rebooting worked out of the box with no issue.

Next step will be liberating my own X200 laptop, and then if you are around the @Gruppo Linux Como area and need a 16 pin clip let us know and we may bring everything to one of the LUG meetings

yes, white, and most of the instructions on the interwebz talk about the black, which is extremely similar to the white except where it isn't

wait? there are keyboard maps? doesn't everybody just use the us one regardless of what is printed on the keys? Do I *live* with somebody who doesn't? :D

the breadboard in the picture is only there for the power supply, the chip on it is a cheap SPI flash used to test SPI on the bone without risking the laptop :)

disclaimer: it worked for us. it may not work on *your* laptop. it may brick it. it may invoke a tentacled monster, it may bind your firstborn son to a life of servitude to some supernatural being. Whatever happens, it's not our fault.

(edit: added tags)

#coreboot #libreboot

28 January 2017

Noah Meyerhans: Call for testing: Stretch cloud images on AWS

Following up on Steve McIntyre's writeup of the Debian Cloud Sprint that took place in Seattle this past November, I'm pleased to announce the availability of preliminary Debian stretch AMIs for Amazon EC2. Pre-generated images are available in all public AWS regions, or you can use FAI with the fai-cloud-images configuration tree to generate your own images. The pre-generated AMIs were created on 25 January, shortly after Linux 4.9 entered stretch, and their details follow:
ami-6d017002 ap-south-1
ami-cc5540a8 eu-west-2
ami-43401925 eu-west-1
ami-870edfe9 ap-northeast-2
ami-812266e6 ap-northeast-1
ami-932e4aff sa-east-1
ami-34ce7350 ca-central-1
ami-9f6dd8fc ap-southeast-1
ami-829295e1 ap-southeast-2
ami-42448a2d eu-central-1
ami-98c9348e us-east-1
ami-57361332 us-east-2
ami-03386563 us-west-1
ami-7a27991a us-west-2
As with the current jessie images, these use a default username of 'admin', with access controlled by the ssh key named in the ec2 run-instances invocation. They're intended to provide a reasonably complete Debian environment without too much bloat. IPv6 addressing should be supported in an appropriately configured VPC environment. These images were build using Thomas Lange's FAI, which has been used for over 15 years for provisioning all sorts of server, workstation, and VM systems, but which only recently was adapted for use generating cloud disk images. It has proven to be well suited to this task though, and image creation is straightforward and flexible. I'll describe in a followup post the steps you can follow to create and customize your own AMIs based on our recipes. In the meantime, please do test these images! You can submit bug reports to the cloud.debian.org metapackage, and feedback is welcome via the debian-cloud mailing list or #debian-cloud on IRC.

27 January 2017

Russ Allbery: Review: Summer in Orcus

Review: Summer in Orcus, by T. Kingfisher
Publisher: Red Wombat Studio
Copyright: 2016
ASIN: B01N26G2I0
Format: Web serial
Pages: 268
In September, Ursula Vernon started posting Summer in Orcus as a web serial, funded by her Patreon supporters. The entire story is now complete and available on-line for free, which is how I read it, but it's also available as an ebook from the expected places if you prefer to read it that way. The ebook publication lists T. Kingfisher as the author, Vernon's pen name for her books for adults. While I would have been happy to read this book as a kid, it does have one fairly gruesome chapter, which is probably the reason for that choice. Summer is eleven, and her mother loves her very much. So much so that she's never allowed to do anything even slightly risky, and she spends quite a lot of her time and emotional energy reassuring her mother, dealing with the burden of that suffocating love, and helping her through her bad days. Then, one day, a house with giant chicken feet walks into the alley behind her house. Summer in Orcus is a portal fantasy. It's the story of how Summer meets Baba Yaga and asks for her heart's desire, finds herself in the magical country of Orcus, and is desperately moved by the plight of a frog tree. It has a talking weasel and a werehouse and antelope women who are not to be trusted, and it's about Summer making friends her mother would never have approved of and learning what she's capable of, and about doing what one can to put things right. Even though it may appear that way at times, Summer in Orcus is not really a book about large things. It's not a saving the world sort of portal fantasy. And it's not really a wish fulfillment portal fantasy, because heart's desires are complicated and subtle. It's a story about being scared and tired and lost, and about making friends, and doing the things one can do rather than learning how to be a completely different person. The plot itself is not particularly complex, but the joy of this story is in all the small things. Vernon's writing is an absolute delight. Summer in Orcus is packed with sentences and paragraphs that I just want to read again and again and quote at people.
Summer had never had a father, and wasn t entirely sure what you did with one, and certainly her mother never had anything good to say about the one Summer didn t have.
Or:
The house lifted its back end up and inched forward a little, like a dog wanting to play. This must have made the floors tilt inside, because Summer heard a banging and sliding of furniture and Baba Yaga yelled, "Fool house! I ll trade you in for one with turtle feet and a three-car garage!" The house sank back down, but wiggled forward a little more, until the front door was only a few feet away.
Vernon mentions in her author notes at the end that Summer in Orcus started as a place to put a whole bunch of fragmentary ideas that she'd come up with but that didn't seem to fit into other stories, and it does have a bit of a grand tour feel to it. But unlike a lot of grand tour figures, the protagonist is not at all bland. Summer is entirely believable and very sympathetic, torn between wanting a grand adventure and being afraid of circumstance and danger entirely outside of her limited experience. She channels the reader's awe and delight, but is still very much her own person, trying to figure out who she wants to be and believe in without the stifling presence of her mother. The tour nature of the story does mean that some things weren't explored as deeply as I would have liked. I would dearly love to read more about the dogs, for instance. I also have to admit that Zultan's motives never made sense to me, even after they were explained, and I found him an odd and weirdly random character to the end. But Glorious is, well, glorious, and I utterly adored the bits with the Forester. The ending is highly unusual for a story of this sort, and I thought it was wonderful, with a great symbolic tie back to the start of the story. The aftermath is even better, including Summer standing firm against one of the tropes of portal fantasies that I dislike the most. This is a great story, with some excellent writing. If you're anything like me, once you read the first chapter you won't want to stop (and since it's all available on the web for free, there's no reason to stop). Recommended. Rating: 8 out of 10

26 January 2017

John Goerzen: What is happening to America?

I still remember vividly my first visit to Europe, back in 2010. I had just barely gotten off a plane in Hamburg and on to a bus to Lubeck, and struck up a conversation with a friendly, well-educated German classical musician next to me. We soon started to discuss politics and religion. Over the course of the conversation, in response to his questions, I explained I had twice voted against George W. Bush, that I opposed the war in Iraq for many reasons, that I did thought there was an ethical imperative to work to defeat climate change, that I viewed health care as an important ethical and religious issue, that I thought evolution was well-established, and that I am a Christian. Finally, without any hint of insult intended, and rather a lot of surprise written all over his face, he said: Wow. You re an American, and a Christian, and you re so . normal! This, it seems to me, has a lot to do with Trump. Ouch It felt like a punch to the gut. The day after the election, having known that a man that appeared to stand for everything that honorable people are against won the election, like people all around the world, I was trying to make sense of how could this happen? As I ve watched since, as he stacks government with wealthy cronies with records nearly as colorful as his own, it is easy to feel even more depressed. Based on how Trump spoke and acted, it would be easy to conclude that the deplorables won the day that he was elected by a contingent of sexists or racists ascendent in power. But that would be too simple an explanation. This is, after all, the same country that elected Barack Obama twice. There are a many people that voted twice for a black man, and then for Trump. Why? Racism, while doubtless a factor, can t explain it all. How Trump could happen Russ Allbery made some excellent points recently:
[Many Americans are] hurt, and they re scared, and they feel like a lot of the United States just slammed the door in their faces. The status quo is not working for people. Technocratic government by political elites is not working for people. Business as usual is not working for people. Minor tweaks to increasingly arcane systems is not working for people. People are feeling lost in bureaucracy, disaffected by elections that do not present a clear alternate vision, and depressed by a slow slide into increasingly dismal circumstances. Government is not doing what we want it to do for us. And people are getting left behind. The left in the United States (of which I m part) has for many years been very concerned about the way blacks and other racial minorities are systematically pushed to the margins of our economy, and how women are pushed out of leadership roles. Those problems are real. But the loss of jobs in the industrial heartland, the inability of a white, rural, working-class man to support his family the way his father supported him, the collapse of once-vibrant communities into poverty and despair: those problems are real too. The status quo is not working for anyone except for a few lucky, highly-educated people on the coasts. People, honestly, like me, and like many of the other (primarily white and male) people who work in tech. We are one of the few beneficiaries of a system that is failing the vast majority of people in this country.
Russ is, of course, right. The Democrats have been either complicit in policies damaging to many, or ineffective in preventing them. They have often appeared unconcerned with the plight of people outside cities (even if that wasn t really the case). And it goes deeper. When s the last time you visited Kansas? I live in Kansas. The nearest paved road is about a 3-mile drive from my home. The nearest town, population 600, is a 6-mile drive. My governor whom I did not vote for cut taxes on the wealthy so much that our excellent local schools have been struggling for years. But my community is amazing, full of loving and caring people, the sort of people who you know you ll be living with for 40 years, and so you make sure you get along well with. I have visited tourist sites in Berlin, enjoyed an opera and a Broadway show in New York, taken a train across the country to Portland, explored San Francisco. I ve enjoyed all of them. Many rural people do get out and experience the world. I have been in so many conversations where I try to explain where I live to people that simply cannot fathom it. I have explained how the 18 acres I own is a very small amount where I am. How, yes, I do actually have electricity and Internet. How a bad traffic day is one where I have to wait for three cars to go past before turning onto the paved road. How I occasionally find a bull in my front yard, how I can walk a quarter mile and be at the creek on the edge of my property, how I can get to an airport faster than most New Yorkers and my kids can walk out the front door and play in a spot more peaceful than Central Park, and how all this is way cheaper than a studio apartment in a bad part of San Francisco. It is rare indeed to see visitors actually traveling to Kansas as a destination. People have no concept of the fact that my mechanic would drop everything and help me get my broken-down car to the shop for no charge, that any number of neighbors or uncles would bring a tractor and come plow the snow off my 1/4-mile driveway out of sheer kindness, that people around here really care for each other in a way you don t see in a city. There are people that I know see politics way differently than me, but I know them to be good people. They would also do anything for a person in need, no matter who they are. I may find the people that they vote for to be repugnant, but I cannot say I ve looked this person in the eyes and they are nothing but deplorable. And so, people in rural areas feel misunderstood. And they are right. Some perspectives on Trump As I ve said, I do find Trump to be deplorable, but not everyone that voted for him is. How, then, do people wind up voting for him? The New Yorker had an excellent story about a man named Mark Frisbie, owner of a welding and fab shop. The recession had been hard on his business. His wife s day-care center also closed. Health care was hard to find, and the long, slow decline had spanned politicians of every stripe. Mark and his wife supposedly did everything they were supposed to: they worked hard, were honest, were entrepreneurial, and yet he had lost his business, his family house, his health coverage, everything. He doesn t want a handout. He wants to be able to earn a living. Asked who he d vote for, he said, Is none of the above an option? The Washington Post had another insightful article, about a professor from Madison, WI interviewing people in rural areas. She said people would often say: All the decisions are made in Madison and Milwaukee and nobody s listening to us. Nobody s paying attention, nobody s coming out here and asking us what we think. Decisions are made in the cities, and we have to abide by them. She pushed back, hard, on the idea that Trump supporters are ignorant, and added that liberals that push that line of thinking are only making the problem worse. I would agree; seeing all the talk about universities dis-inviting speakers that don t hew to certain political views doesn t help either. A related article talks about the lack of empathy for Trump voters. And then we have a more recent CNN article: Where Tump support and Obamacare use soar together, explaining in great detail how it can be logical for someone to be on Obamacare but not like it. We can all argue that the Republicans may have as much to do with that as anything, but the problem exists. And finally, a US News article makes this point:
His supporters realize he s a joke. They do not care. They know he s authoritarian, nationalist, almost un-American, and they love him anyway, because he disrupts a broken political process and beats establishment candidates who ve long ignored their interests. When you re earning $32,000 a year and haven t had a decent vacation in over a decade, it doesn t matter who Trump appoints to the U.N., or if he poisons America s standing in the world, you just want to win again, whoever the victim, whatever the price. According to the Republican Party, the biggest threat to rural America was Islamic terrorism. According to the Democratic Party it was gun violence. In reality it was prescription drug abuse and neither party noticed until it was too late.
Are we leaving people out? All this reminded me of reading about Donald Knuth, the famous computer scientist and something of the father of modern computing, writing about his feelings of trepidation about sharing with his university colleagues that he was working on a project related to the Bible. I am concerned about the complaints about the PC culture , because I think it is good that people aren t making racist or anti-semitic jokes in public anymore. But, as some of these articles point out, in many circles, making fun of Christians and conservatives is still one of the accepted targets. Does that really help anything? (And as a Christian that is liberal, have all of you that aren t Christians so quickly forgotten how churches like the Episcopals blazed the way for marriage equality many years ago already?) But they don t get a free pass I have found a few things, however, absolutely scary. One was an article from December showing that Trump voters actually changed their views on Russia after Trump became the nominee. Another one from just today was a study on how people reacted when showed inauguration crowd photos. NPR ran a story today as well, on how Trump is treating journalists like China does. Chilling stuff indeed. Conclusion So where does this leave us? Heading into uncertain times, for sure, but perhaps just maybe with a greater understanding of our neighbors. Perhaps we will all be able to see past the rhetoric and polarization, and understand that there is something, well, normal about each other. Doing that is going to be the only way we can really take our country back.

24 January 2017

Jonathan McDowell: Experiments with 1-Wire

As previously mentioned, at the end of last year I got involved with a project involving the use of 1-Wire. In particular a DS28E15 device, intended to be used as a royalty tracker for a licensed piece of hardware IP. I d no previous experience with 1-Wire (other than knowing it s commonly used for driving temperature sensors), so I took it as an opportunity to learn a bit more about it. The primary goal was to program a suitable shared key into the DS28E15 device that would also be present in the corresponding hardware device. A Maxim programmer had been ordered, but wasn t available in stock so had to be back ordered. Of course I turned to my trusty Bus Pirate, which claimed 1-Wire support. However it failed to recognise the presence of the device at all. After much head scratching I finally listened to a co-worker who had suggested it was a clock speed issue - the absence of any option to select the 1-Wire speed in the Bus Pirate or any mention of different speeds in the documentation I had read had made me doubt it was an issue. Turns out that the Bus Pirate was talking standard 1-Wire and the DS28E15 only talks overdrive 1-Wire, to the extent that it won t even announce its presence if the reset pulse conforms to the standard, rather than overdrive, reset time period. Lesson learned: listen to your co-workers sooner. A brief period of yak shaving led to adding support to the Bus Pirate for the overdrive mode (since landed in upstream), and resulted in a search request via the BP interface correctly finding the device and displaying its ROM ID. This allowed exploration of the various commands the authenticator supports, to verify that the programming sequence operated as expected. These allow for setting the shared secret, performing a SHA256 MAC against this secret and a suitable nonce, and retrieving the result. Next problem: the retrieved SHA256 MAC did not match the locally computed value. Initially endianness issues were suspected, but trying the relevant permutations did not help. Some searching found an implementation of SHA256 for the DS28E15 that showed differences between a standard SHA256 computation and what the authenticator performs. In particular SHA256 normally adds the current working state (a-g) to the current hash value (h0-h7) at the end of every block. The authenticator does this for all but the final block, where instead the hash value is set to the working state. I haven t been able to find any documentation from Maxim that this is how things are calculated, nor have I seen any generic implementation of SHA256 which supports this mode. However rolling my own C implementation based on the code I found and using it to compare the results retrieved from the device confirms that this is what s happening. So at this point we re done, right? Wait for the proper programming hardware to turn up, write the key to the devices, profit? Well, no. There was a bit of a saga involving the programmer (actually programmers, one with at least some documentation that allowed the creation of a Python tool to allow setting the key and reading + recording the ROM ID for tracking, and one with no programming documentation that came with a fancy GUI for manually doing the programming), but more importantly it was necessary to confirm that the programmed device interacted with the hardware correctly. Initial testing with the hardware was unsuccessful. Again endianness issues were considered and permutations tried, but without success. A simple key constructed to avoid such issues was tried, and things worked fine. There was a hardware simulation of both components available, so it was decided to run that and obtain a capture of the traffic between them. As the secret key was known this would then allow the random nonce to be captured, and the corresponding (correct) hash value. Tests could then be performed in software to determine what the issue was & how to generate the same hash for verification. Two sets of analyzer software were tried, OpenBench LogicSniffer (OLS) and sigrok. As it happened both failed to correctly decode the bitstream detected as 1-Wire, but were able to show the captured data graphically, allowing for decoding by eye. A slight patch to OLS to relax the timing constraints allowed it to successfully decode the full capture and provided the appropriate data for software reproduction. The end issue? A 256 bit number (as defined in VHDL) is not the same as 32 element byte array Obvious when you know what the issue is! So? What did I learn, other than a lot about 1-Wire? Firstly, don t offhandedly discount suggestions that you don t think make sense. Secondly, having a tool (in this case the Bus Pirate) that lets you easily play with a protocol via a simple interface is invaluable in understanding it. Thirdly, don t trust manufacturers to be doing something in a normal fashion when they claim to be using a well defined technology. Fourthly, be conscious about all of the different ways bitstreams can be actually processed in memory. It s not just endianness. Finally, spending the time to actually understand what s going on up front can really help when things don t work as you d expect later on - without the yak shaving to support Overdrive on the BP I wouldn t have been able to so quickly use the simulation capture to help diagnose the issue.

Shirish Agarwal: Budget and Economics 101

The Budget The story which I wanted to share is there are few friends (from Debian as well as elsewhere) who shared that they didn t get the whole demonetisation play or what the Government is/was trying to do. As budget is just round the corner (India will be presenting its yearly budget on 1st of February), thought it is prudent to share at least some basics, ideas and theories of what goals the Finance Minister would be looking at when presenting his budget. I would NOT talk of Inflation targeting or some such exotica as those topics would require their own blog-posts altogether. I would mainly be talking a bit about Taxation and in that Personal Income Tax. I would also not use words like Receivables and like which thought bit more accurate are not used in everyday language. Just like Private Companies and increasingly public utilities, The Government of the day has two-three different aims when it is presenting a budget a. The first is to give an update about how things went last year. Did all the incomes that were projected, did it happen or was there a short-fall ? If there was a short-fall what were the reasons for the shortfall. Similarly, did all the budgeted expenditure earmarked for the year was spent and were it spent under the heads they were supposed to ? If not what went wrong there ? There is usually a tussle between Planned and Unplanned expenditure and one of the hallmarks of good governance is that unplanned expenditure is kept at minimum, while planned expenditure and projects completion or/and assets coming on-line were within the estimated time-frames. So these updates are given to the Parliament and hence public at large. The second and the more interesting part are the plans for the immediate future, 1 year down-the-line. Based on the performance last year, a bit of crystal-ball gazing of external and internal conditions of the country, the Finance Minister along with her/his colleagues of Finance Ministry. Trivia There hasn t been a female finance minister till date in India. The Finance Ministry as a whole also holds consultations with most sections of the society before sharing/putting his Fiscal Policy (Planned Expenditure) for debate and passage in form of the Budget. While the budget itself is a technical exercise, it is also a Political exercise as both the budget and the finance bill (which contains the taxation proposals) need to be passed in Lok Sabha (Lower house). After passing scrutiny of Lok Sabha (Lower House having people s representatives directly elected) and Rajya Sabha (Upper House, indirectly elected), the taxation proposals becomes the law. It isn t that simple but for our understanding, keeping it simple. This Political model of governance with two houses is modeled under the British (Westminister) model since 1947. The Government, just like any other Organization gives a similar Profit and Loss Account and a Balance Sheet.
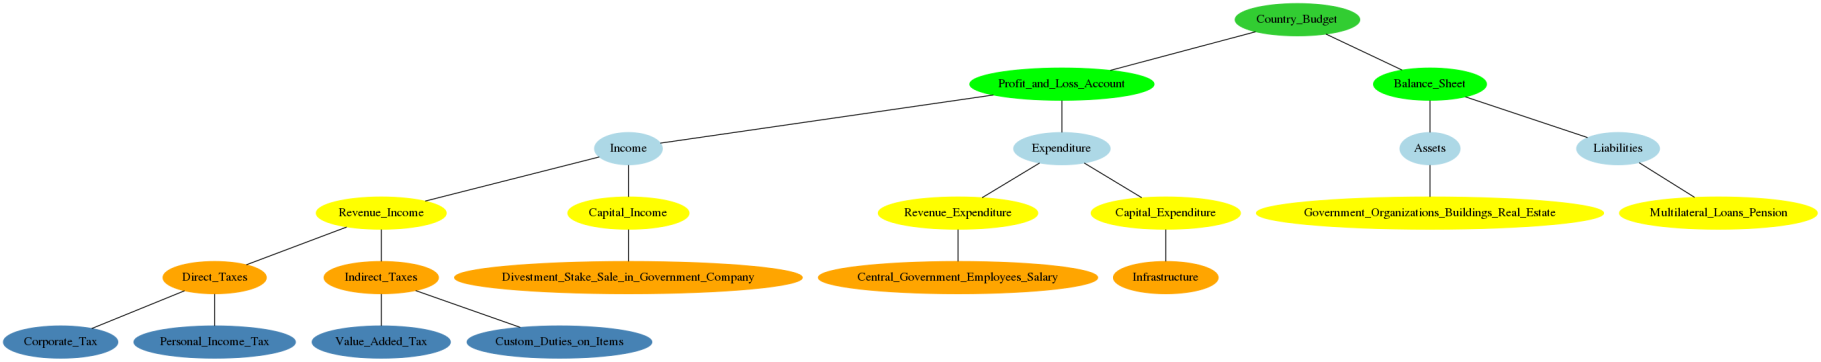
How A country's budget is made.

How A country s budget is made. A representational and simplified version of how things flow was made using Graphviz. Click on it to see image in detail.

I am a newbie to graphviz. The graph was made like this
graph Budget
subgraph tier1
node [color="limegreen",style="filled",group="tier1"]
Country_Budget

......
Country_Budget -- Profit_and_Loss_Account [type=s];
It might be possible to make the graph much better than it is currently . The Profit and Loss Account of the Government tells what Incomes it is projected to earn in the upcoming year and whatever Expenditures it hopes to do this year. The Income and Expenditure independently can be bifurcated into two, Revenue Income and Capital Income and Revenue Expenditure and Capital Expenditure.
Indian Railways EMU local train

Indian Railways EMU local train

The simplest example of such planned expenditure which comes to my mind is the Indian Railways Budget which is all planned expenditure. As can be seen even with ample funds Railways were able to spent only 50% of the total amount disbursed last year. Similarly income generation for Railways was far below the target. Examples of Revenue Income include taxes of all sorts, while Capital Income are rare, like divestment/stake sale of a company owned by the Government. These are usually one-off events. Examples of Capital Expenditure is when the Government makes a road, makes a bridge etc. Usually large expenditures come under Capital Expenditure while salaries to Government employees and routine expenditures are known as Revenue Expenditure. There was a statement by the present Government that the last 6-7 years the budgets has been more or less static as far as numbers are concerned. This hampers Government s ability to take up any new work. The Revenue income earned by the Government can again be bifurcated primarily into two Direct Taxes and Indirect Taxes.
INR 2000 Rupees

INR 2000 Rupees

Direct Taxes are those which the Government earns through Personal Income Tax and Corporate Tax. As only 1 percent of Indians pay Personal income tax, the rest Government tries to raise by Hence the Government of the day is in fix. It needs to have more money if it wants to invest into infrastructure, defence spending, social spending such as health and education and so on and so forth. It cannot Another point is that unlike China which is a Large State-backed Enterprises Export-led Economy which has its own problems, India s economy is much more consumption-based, hence any large tinkering upwards may possibly stall whatever little spending the middle-class does, similar to the stall in consumer durables which has been happening over the last few years. There are a couple of short-term solutions that the Government may do While both seem to be attractive ways, but both have their disadvantages also, both have costs associated for them. In the first one, like any other scheme, when any scheme is launched, it needs to be underwritten by GOI which means even if it s not a success they would have to service all and any obligations towards investors. Also they have to be careful how much they are borrowing as excessive borrowing for today could lead to a Greece-like meltdown situation, whether internal or external borrowers. With external borrowers they also usually like to have a guarantee that the Rupee will not slide beyond a point otherwise the Government will have to pay all and any losses but this is going beyond what I wanted to share. Printing excess money in the system could lead to loss in the value of the money itself as well as leading to inflationary pressures which leads to more problems for the poor and greater inequality between the classes among other things. So while the Government may use all of the above ways in varying degrees, the present Government had the idea that if we were to reduce black money or hidden economy (AFAIK no country can claim to completely eliminate it) we would be able to raise the finance we need without a major cost associated to it. For instance, I was reading that even in Canada, it is expected that 20% of black money/shadow economy works and that assessment is by their own taxation authorities. So While doing demonetization, it came out with an equivalent Black Money Declaration Scheme (IDS). The idea is simple, even if 1 percent of the population comes in the traditional tax net the Government of the day would be able to enhance budgets to various expenditure. Now while the idea is good in theory, implementation has been the Achilees heel. While the Government s expected something like 15% of the whole economy was black money or shadow money, almost 95% of the money in circulation came back in Banks during demonetization ( These are unofficial figures, Finance Ministry/RBI would be disclosing the real figures on 1st of February 2017 so we will know). It is suspected that 10% of money in Banks is black money. There are considerable costs to search analyze, prove in the court of law that it is so. There are and would be considerable costs to train new officers as existing Income Tax Officers are already burdened with Advance Tax being paid by Corporates and small business-man paying round the year (every 3 months), The existing Income Tax Officers already have their hands full. Also till Governments don t fix up realty sector/real-estate sector and other places where the black money/shadow economy may prevail. Hence all the training, salary, buildings where new Income Tax Officers could work, infrastructure, new buildings where suspect cases have to be tried and lawyers for those. As have shared a few times on this blog, India has almost 29 million court cases pending in the lower judiciary alone. Unless any such cases are not successfully tried within time by the Government, it would be a waste. Now whether the Government knew of these issues or not would probably be never known. Lastly, there is a voluntary part that the Government hopes, that they will by themselves join the mainstream tax-paying public. This might happen but any such happening will happen over years. People make their own choices. And unless there are not any stick and carrot approach to the Government s Policies people will tend to go back to their old ways. I would share an example from the demonetisation process which would help prove my point During demonetization, there was a great push towards doing digital transaction either via smartphones or greater usage of debit and credit cards etc. For the first 60 days till 31st December 2016, you could do digital transactions without paying any transaction fee. During that period, I used my Debit card to shop, to eat at restaurants or/and even small shops. But come 1st January 2017, the charges for digital transactions are anything between 1.5% to 3% of transactions. Naturally, I stopped using them and use them very sparingly where cash won t work. So at the end, while the Government made the whole demonetization drive to drive out shadow economy, terror financing etc. While terror financing has been hurt quite a bit, the same cannot be said of the shadow/black economy. It seems that the Government would need to close many more doors and windows before people join the mainstream. While Politically it was risky, socially it was also a bit risky move as it was uncertain how and where things will move. Venezuela tried the same thing and fell flat on its face. All said and done, if and when people become part of the tax-paying class/people, The most optimistic idea that the Government has that everybody will go cashless and it would be far easier to find out who s not paying taxes. As shared before, I don t think this will happen unless the charges for cashless is at 0.05% or something similar. Even IF people do join the mainstream, it is very much possible that the present Govt. will not enjoy fruits of this labour as fruits might come in 2018/19 or even later even if they do come. So whether the decision had the right affect or not, we may never come to know. Governments tend to tinker around with the figures as well. But I hope some idea of how things happen is known now.
Filed under: Miscellenous Tagged: #demonetization, #Government Budget, #graphviz, #Limitations, #Profit and Loss Account, #Taxation

23 January 2017

Sam Hartman: Cudos to GDB Contributors

I recently diagnosed a problem in Debian's pam-p11 package. This package allegedly permits logging into a computer using a smart card or USB security token containing an ssh key. If you know the PIN and have the token, then your login attempt is authorized against the ssh authorized keys file. This seems like a great way to permit console logins as root to machines without having a shared password. Unfortunately, the package didn't work very well for me. It worked once, then all future attempts to use it segfaulted. I'm familiar with how PAM works. I understand the basic ideas behind PKCS11 (the API used for this type of smart card), but was completely unfamiliar with this particular PAM module and the PKCS11 library it used. The segfault was in an area of code I didn't even expect that this PAM module would ever call. Back in 1994, that would have been a painful slog. Gdb has improved significantly since then, and I'd really like to thank all the people over the years who made that possible. I was able to isolate the problem in just a couple of hours of debugging. Here are some of the cool features I used: Anyway, with just a couple of hours and no instrumentation of the code, I managed to track down how a bunch of structures were being freed as an unexpected side effect of one of the function calls. Neither I nor the author of the pam-p11 module expected that (although it is documented and does make sense in retrospect). Good tools make life easier.

22 January 2017

Shirish Agarwal: Debian contributions and World History

Beware, this would be slightly longish. Debian Contributions In the last couple of weeks, was lucky to put up a patch against debian-policy which had been bothering me for a long-long time. The problem statement is simple, man-pages historically were made by software engineers for software-engineers. The idea, probably then was you give the user some idea of what the software does and the rest the software engineer would garner from reading the source-code. But over period of time, the audience has changed. While there are still software engineers who use GNU/Linux for the technical excellence, the man-pages have not kept up with this new audience who perhaps are either not technically so sound that or they do not want to take the trouble to reading the source-code to understand how things flow. An example or examples in a man-page gives us (the lesser mortals) some insight as how the command works, how the logic flows. A good example of a man-page is the ufw man-page
EXAMPLES
Deny all access to port 53: ufw deny 53 Allow all access to tcp port 80: ufw allow 80/tcp Allow all access from RFC1918 networks to this host: ufw allow from 10.0.0.0/8
ufw allow from 172.16.0.0/12
ufw allow from 192.168.0.0/16 Deny access to udp port 514 from host 1.2.3.4: ufw deny proto udp from 1.2.3.4 to any port 514 Allow access to udp 1.2.3.4 port 5469 from 1.2.3.5 port 5469: ufw allow proto udp from 1.2.3.5 port 5469 to 1.2.3.4 port 5469
Now if we had man-pages like the above which give examples, then the user at least can try to accomplish whatever s/he is trying to do. I truly believe not having examples in a man-page kills 50% of your audience and people who could potentially use your tool. Personal wishlist The only thing (and this might be my failure) is we need a good way to search through a man-page. The only way I know is using / and try to give a pattern. Lots of times it fails because I, the user doesn t know the exact keyword which the documenter was using. What would be nice, great if we do have some sort of parser where I tell it, $this is what I m looking for and the parser tries the pattern + all its synonyms and whatever seems to be most relevant passage from the content, in this case a manpage it tells me. It would make my life a lot easier while at the same time force people to document more and more. I dunno if there has been any research or study of the relationship between good documentation and popularity of a program. I know there are lots of different tiny bits which make or break a program, one of which would definitely be documentation and in that a man-page IF it s a command-line tool. A query on Quora gives some indication https://www.quora.com/How-comprehensible-do-you-find-Unix-Linux-Man-pages although the low response rate tells its own story. there have been projects like man2html and man2pdf and others which try to make the content more accessible to people who are not used to the man-page interface but till you don t have Examples the other things can work only so far. Also if anybody talks about X project which claims to solve this problem they will have to fight manpages who have been around like forever. As can be seen in the patch, did some rookie mistakes as can be seen. I also filed a lintian bug at the same time. Hope the patch does get merged at some point in debian-policy and then a check introduced in lintian in some future release. I do agree with anarcat s assertion that it should be at the level of the manpage missing level. I am no coder but finding 14,000 binary packages without a manpage left me both shocked and surprised. I came to know about manpage-alert from the devscripts package to know which all binary packages that have been installed but not have man-pages. I hope to contribute a manpage or two if I across a package I m somewhat comfortable with. I have made a beginning of sorts by running manpage alert and putting the output in a .txt file which I would grep through manually and see if something interesting jumps at me. The learning garnered from putting the patch to the debian package resulted in another patch but this time for an upstream project altogether. As can be seen all are just baby-steps that even a non-coder can take. Another couple of bugs I filed which were fixed were of a sim called unknown-horizons . A 2D realtime strategy simulation. I had filed three bugs, two of which were fixed in 2 days, the 3rd I hope is also fixed soonish. Lastly, I spent most of the week-end poring over packages who have left files in /etc/bash_completion.d/ . I spent almost 4-5 odd hours as each package in question as well as entries found in /etc/bash-completion.d/$filename I had to find which package it belonged to first

[$] dpkg -S /etc/bash_completion.d/git-prompt
git: /etc/bash_completion.d/git-prompt
I know that dpkg-query also does the same
[$] dpkg-query -S /etc/bash_completion.d/git-prompt
git: /etc/bash_completion.d/git-prompt
But I am used to plain dpkg although do know that dpkg-query can do lot more intimate searching in various ways than dpkg can. Once the package name was established, first simulate the purge [$] sudo aptitude -s purge git

[sudo] password for shirish:
The following packages will be REMOVED:
git p
0 packages upgraded, 0 newly installed, 1 to remove and 14 not upgraded.
Need to get 0 B of archives. After unpacking 29.5 MB will be freed.
The following packages have unmet dependencies:
libgit-wrapper-perl : Depends: git but it is not going to be installed
git-extras : Depends: git (>= 1.7.0) but it is not going to be installed
bup : Depends: git but it is not going to be installed
git-remote-gcrypt : Depends: git but it is not going to be installed
git-svn : Depends: git (> 1:2.11.0) but it is not going to be installed
Depends: git ( 1:2.11.0) but it is not going to be installed
Depends: git (= 1:1.8.1) but it is not going to be installed
git-core : Depends: git (> 1:1.7.0.2) but it is not going to be installed
The following actions will resolve these dependencies:
Remove the following packages:
1) bup [0.29-2 (now, testing, unstable)]
2) fdroidserver [0.7.0-1 (now, testing, unstable)]
3) git-annex [6.20161012-1 (now, testing)]
4) git-core [1:2.11.0-2 (now, testing, unstable)]
5) git-extras [4.2.0-1 (now, testing, unstable)]
6) git-remote-gcrypt [1.0.1-1 (now, testing, unstable)]
7) git-repair [1.20151215-1 (now, unstable)]
8) git-svn [1:2.11.0-2 (now, testing, unstable)]
9) gitk [1:2.11.0-2 (now, testing, unstable)]
10) libgit-wrapper-perl [0.047-1 (now, testing, unstable)]
11) python3-git [2.1.0-1 (now, testing, unstable)]
12) svn2git [2.4.0-1 (now, testing, unstable)] Leave the following dependencies unresolved:
13) devscripts recommends libgit-wrapper-perl
14) dh-make-perl recommends git
15) fdroidserver recommends git
16) git-annex recommends git-remote-gcrypt (>= 0.20130908-6)
17) gplaycli recommends fdroidserver
18) python-rope recommends git-core
Accept this solution? [Y/n/q/?] q
Abandoning all efforts to resolve these dependencies.
Abort.
Then I made a note of all the packages being affected, saw purging all of them wouldn t call others (the Package dependency Hell), made the purge and then reinstalled anew. The reason I did this is that many a times during upgrade, either during update/upgrade sometimes the correct action doesn t happen. To take the git s example itself, there were two files git-extras and git-prompt which were in /etc/bash_completion.d/ both of which were showing their source as git. Purging git and installing git afresh removed git-extras file and git-prompt is the only one remaining. While blogging about the package, did try to grep through changelog.Debian.gz and changelog.gz in git

[shirish@debian] - [/usr/share/doc/git] - [10046]
[$] zless changelog.gz
and similarly

[shirish@debian] - [/usr/share/doc/git] - [10046]
[$] zless changelog.Debian.gz
But failed to find any mention of the now gone git-extras. Doing this with all the packages took considerable time as didn t want to deal with any potential fallout later on. For instance, ufw (uncomplicated firewall) also had an entry in /etc/bash_completion.d/, hence before purging ufw, took backup of all the rules I have made, did a successful simulation

[$] sudo aptitude -s purge ufw gufw


The following packages will be REMOVED:
gufw p ufw p
0 packages upgraded, 0 newly installed, 2 to remove and 14 not upgraded.
Need to get 0 B of archives. After unpacking 4,224 kB will be freed.
Note: Using 'Simulate' mode.
Do you want to continue? [Y/n/?] y
Would download/install/remove packages.
purged the packages, reinstalled it and then re-added all the rules. Doing it all for various sundry packages, had to do it manually as there is no one size fits all solution. A sensitive one was grub which still has an entry in /etc/bash_completion.d/grub. Doing it wrong could have resulted in a non-bootable situation. There are workarounds for that, but it would have taken quite a bit of time, energy, notes and bit of recall factor what I did the last time something like that happened. Doing it manually, being present meant I could do it rightly the first time. So, was it worth it It would be if the package maintainers do the needful and the remaining entries are moved out of /etc/bash_completion.d/ to /usr/share/bash-completions and some to my favourite /usr/share/zsh/vendor-completions/ for instance

[shirish@debian] - [/usr/share/zsh/vendor-completions] - [10064]
[$] ll -h _youtube-dl
-rw-r--r-- 1 root root 3.2K 2016-12-01 08:48 _youtube-dl But trying to get all or even major packages to use zsh-completions would be hard work and would take oodles of time and this concerns upstream stuff, also very much outside what I was sharing. World History Before, during and even after South-African experience, I was left wondering why India and South Africa, two countries who had similar histories at least the last couple of hundred years or more, the final result of Independence was so different for both the countries. It took me quite sometime to articulate that in a form of question , while the answers were interesting, from what little I know of India itself, if I were an Englishman I would never leave Hindustan . What the people answering failed to take into account was that in that era it was Hindustan or un-divided India.
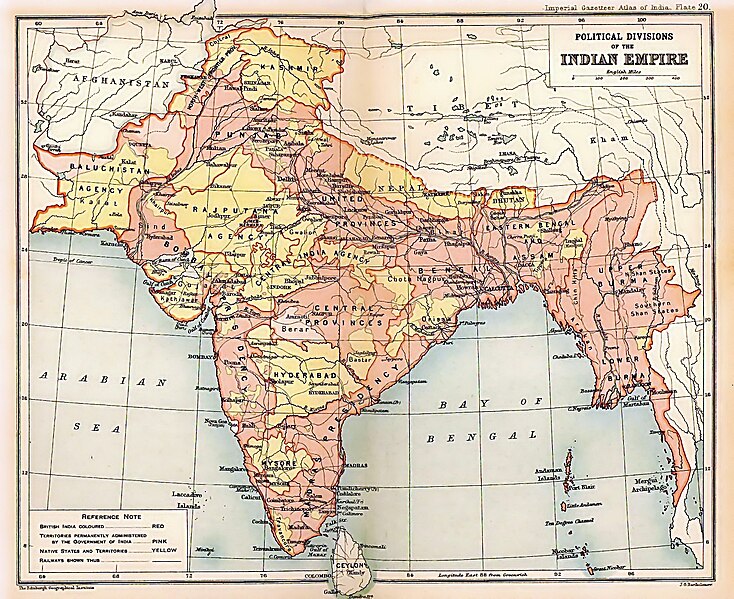
Pre-partition map of India

Pre-partition map of India

This map can be found at https://commons.wikimedia.org/wiki/File:British_Indian_Empire_1909_Imperial_Gazetteer_of_India.jpg and is part of quite a few Indian articles. I would urge people to look at the map in-depth. Except for the Central India Agency and Central India Provinces, most of the other regions were quite comfortable weather-wise. Hence I can t help but feel the assertion that Britishers didn t like India (as to live here) slightly revolting. See the excerpt/take on Dale Kennedy s The Magic Mountains: Hill Stations and the British Raj. Berkeley: University of California Press, 1996. xv + 264 pp. . A look at the list of hill stations of divided India is enough to tell that there were lot of places which either were founded by the Britishers or they chose to live there. And this is not all, there are supposed to lot of beautiful places even in Pakistan, especially in North East Frontier, Swat for instance. While today it s infamous for Taliban and Islamic Terrorism, there was a time it was known for its beauty.
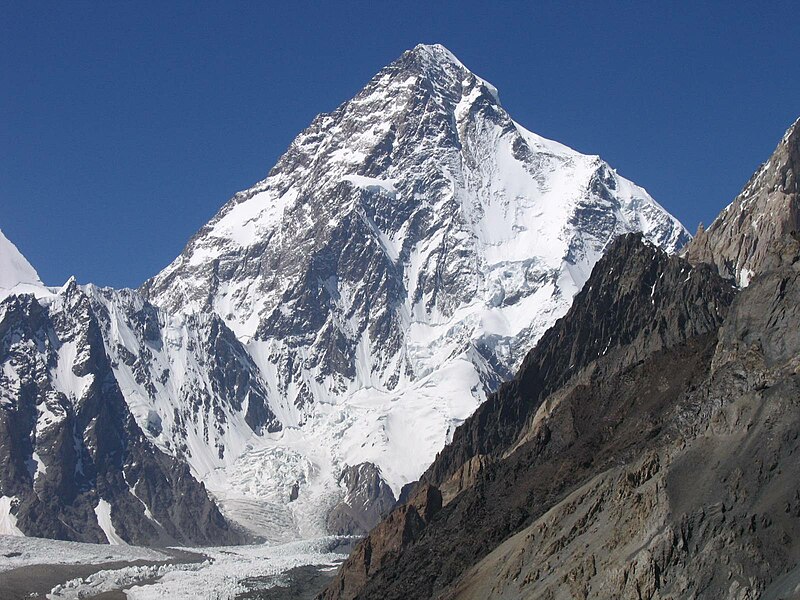
The second most difficult mountain in the world - K2, Pakistan

The second most difficult mountain in the world K2, Pakistan

Trivia After Everest, K2 is the smaller one although whatever I have read of people s accounts, most people who ascended all 14 8,000 metre peaks say K2 is technically more tougher than Everest and after Everest has the highest casualty rate. Also places like the disputed North half of Pakistan Occupied Kashmir, Gilgit Baltistan, Extreme northern Punjab of Pakistan , Northern half of Khyber-Pakhtunkhawa province and Northern Balochistan all of these places would have been more than conducive to the Britishers as it is near to the British climate (snow and pleasant weather all year round). It really is a pity that Pakistan chose to become a terrorist state where it could have become one of the more toured places of Asia. I really feel nauseous and sad at the multiple chances that Pakistan frittered away, it could have been something else.
Filed under: Miscellenous Tagged: #bash-completion, #British Raj, #contributions, #debian, #debian-policy, #Debian-QA, #Hill Stations, #India Independance Movement, #lintian, #obsolete-conffiles, #unknown-horizons, #weather, #World History, adequate, Pakistan, tourism

18 January 2017

Reproducible builds folks: Reproducible Builds: week 90 in Stretch cycle

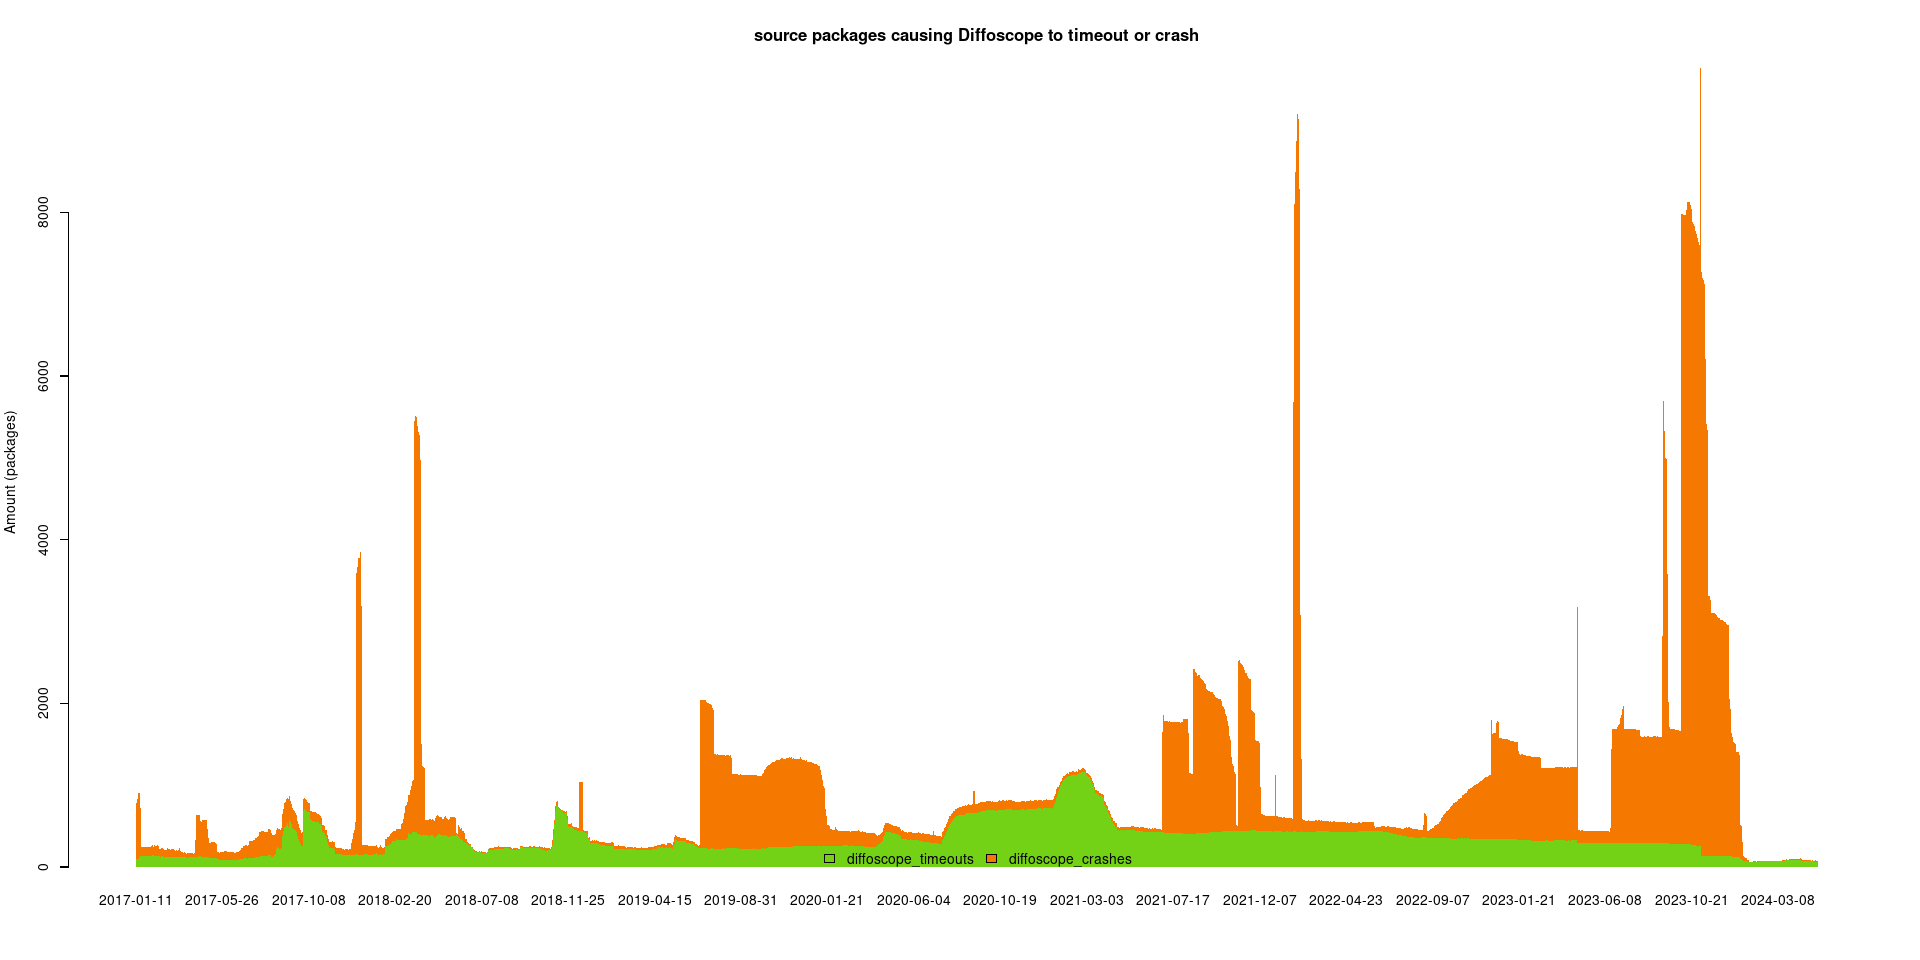
What happened in the Reproducible Builds effort between Sunday January 8 and Saturday January 14 2017: Upcoming Events Reproducible work in other projects Reproducible Builds have been mentioned in the FSF high-priority project list. The F-Droid Verification Server has been launched. It rebuilds apps from source that were built by f-droid.org and checks that the results match. Bernhard M. Wiedemann did some more work on reproducibility for openSUSE. Bootstrappable.org (unfortunately no HTTPS yet) was launched after the initial work was started at our recent summit in Berlin. This is another topic related to reproducible builds and both will be needed in order to perform "Diverse Double Compilation" in practice in the future. Toolchain development and fixes Ximin Luo researched data formats for SOURCE_PREFIX_MAP and explored different options for encoding a map data structure in a single environment variable. He also continued to talk with the rustc team on the topic. Daniel Shahaf filed #851225 ('udd: patches: index by DEP-3 "Forwarded" status') to make it easier to track our patches. Chris Lamb forwarded #849972 upstream to yard, a Ruby documentation generator. Upstream has fixed the issue as of release 0.9.6. Alexander Couzens (lynxis) has made mksquashfs reproducible and is looking for testers. It compiles on BSD systems such as FreeBSD, OpenBSD and NetBSD. Bugs filed Chris Lamb: Lucas Nussbaum: Nicola Corna: Reviews of unreproducible packages 13 package reviews have been added and 13 have been removed in this week, adding to our knowledge about identified issues. 1 issue type has been added: Weekly QA work During our reproducibility testing, the following FTBFS bugs have been detected and reported by: diffoscope development Bugs in diffoscope in the last year Many bugs were opened in diffoscope during the past few weeks, which probably is a good sign as it shows that diffoscope is much more widely used than a year ago. We have been working hard to squash many of them in time for Debian stable, though we will see how that goes in the end reproducible-website development tests.reproducible-builds.org Misc. This week's edition was written by Ximin Luo, Chris Lamb and Holger Levsen and reviewed by a bunch of Reproducible Builds folks on IRC & the mailing lists.

Michael Stapelberg: manpages.debian.org has been modernized

https://manpages.debian.org has been modernized! We have just launched a major update to our manpage repository. What used to be served via a CGI script is now a statically generated website, and therefore blazingly fast. While we were at it, we have restructured the paths so that we can serve all manpages, even those whose name conflicts with other binary packages (e.g. crontab(5) from cron, bcron or systemd-cron). Don t worry: the old URLs are redirected correctly. Furthermore, the design of the site has been updated and now includes navigation panels that allow quick access to the manpage in other Debian versions, other binary packages, other sections and other languages. Speaking of languages, the site serves manpages in all their available languages and respects your browser s language when redirecting or following a cross-reference. Much like the Debian package tracker, manpages.debian.org includes packages from Debian oldstable, oldstable-backports, stable, stable-backports, testing and unstable. New manpages should make their way onto manpages.debian.org within a few hours. The generator program ( debiman ) is open source and can be found at https://github.com/Debian/debiman. In case you would like to use it to run a similar manpage repository (or convert your existing manpage repository to it), we d love to help you out; just send an email to stapelberg AT debian DOT org. This effort is standing on the shoulders of giants: check out https://manpages.debian.org/about.html for a list of people we thank. We d love to hear your feedback and thoughts. Either contact us via an issue on https://github.com/Debian/debiman/issues/, or send an email to the debian-doc mailing list (see https://lists.debian.org/debian-doc/).

Jonathan Dowland: RetroPie, NES Classic and Bluetooth peripherals

I wanted to write a more in-depth post about RetroPie the Retro Gaming Appliance OS for Raspberry Pis, either technically or more positively, but unfortunately I don't have much positive to write. What I hoped for was a nice appliance that I could use to play old games from the comfort of my sofa. Unfortunately, nine times out of ten, I had a malfunctioning Linux machine and the time I'd set aside for jumping on goombas was being spent trying to figure out why bluetooth wasn't working. I have enough opportunities for that already, both at work and at home. I feel a little bad complaining about an open source, volunteer project: in its defence I can say that it is iterating fast and the two versions I tried in a relatively short time span were rapidly different. So hopefully a lot of my woes will eventually be fixed. I've also read a lot of other people get on with it just fine. Instead, I decided the Nintendo Classic NES Mini was the plug-and-play appliance for me. Alas, it became the "must have" Christmas toy for 2016 and impossible to obtain for the recommended retail price. I did succeed in finding one in stock at Toys R Us online at one point, only to have the checkout process break and my order not go through. Checking Stock Informer afterwards, that particular window of opportunity was only 5 minutes wide. So no NES classic for me! My adventures in RetroPie weren't entirely fruitless, thankfully: I discovered two really nice pieces of hardware.
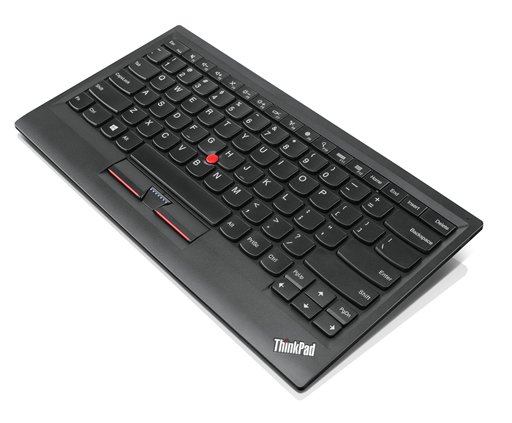
ThinkPad Keyboard ThinkPad Keyboard
The first is Lenovo's ThinkPad Compact Bluetooth Keyboard with TrackPoint, a very compact but pleasant to use Bluetooth keyboard including a trackpoint. I miss the trackpoint from my days as a Thinkpad laptop user. Having a keyboard and mouse combo in such a small package is excellent. My only two complaints would be the price (I was lucky to get one cheaper on eBay) and the fact it's bluetooth only: there's a micro-USB port for charging, but it would be nice if it could be used as a USB keyboard too. There's a separate, cheaper USB model.
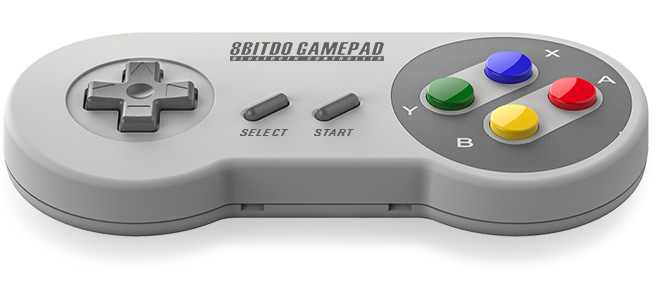
8bitdo SFC30 8bitdo SFC30
The second neat device is a clone of the SNES gamepad by HK company 8bitdo called the SFC30. This looks and feels very much like the classic Nintendo SNES controller, albeit slightly thicker from front to back. It can be used in a whole range of different modes, including attached USB; Bluetooth pretending to be a keyboard; Bluetooth pretending to be a controller; and a bunch of other special modes designed to work with iOS or Android devices in various configurations. The manufacturer seem to be actively working on firmware updates to further enhance the controller. The firmware is presently closed source, but it would not be impossible to write an open source firmware for it (some people have figured out the basis for the official firmware). I like the SFC30 enough that I spent some time trying to get it working for various versions of Doom. There are just enough buttons to control a 2.5D game like Doom, whereas something like Quake or a more modern shooter would not work so well. I added support for several 8bitdo controllers directly into Chocolate Doom (available from 2.3.0 onwards) and into SDL2, a popular library for game development, which I think is used by Steam, so Steam games may all gain SFC30 support in the future too.

17 January 2017

Arturo Borrero Gonz lez: Debian is a puzzle: difficult

Debian is a puzzle Debian is very difficult, a puzzle. This surprising statement was what I got last week when talking with a group of new IT students (and their teachers). I would like to write down here what I was able to obtain from that conversation. From time to time, as part of my job at CICA, we open the doors of our datacenter to IT students from all around Andalusia (our region) who want to learn what we do here and how we do it. All our infraestructure and servers are primarily built using FLOSS software (we have some exceptions, like backbone routers and switches), and the most important servers run Debian. As part of the talk, when I am in such a meeting with a visiting group, I usually ask about which technologies they use and learn in their studies. The other day, they told me they use mostly Ubuntu and a bit of Fedora. When I asked why not Debian, the answer was that it was very difficult to install and manage. I tried to obtain some facts about this but I failed in what seems to be a case of bad fame, a reputation problem which was extended among the teachers and therefore among the students. I didn t detect any branding biasing or the like. I just seems lack of knowledge, and bad Debian reputation. Using my DD powers and responsabilities, I kindly asked for feedback to improve our installer or whatever they may find difficult, but a week later I have received no email so far. Then, what I obtain is nothing new: I myself recently had to use the Ubuntu installer in a laptop, and it didn t seem that different to the Debian one: same steps and choices, like in every other OS installation. Please, spread the word: Debian is not difficult. Certainly not perfect, but I don t think that installing and using Debian is such a puzzle.

Ritesh Raj Sarraf: Linux Tablet-Mode Usability

In my ongoing quest to get Tablet-Mode working on my Hybrid machine, here's how I've been living with it so far. My intent is to continue using Free Software for both use cases. My wishful thought is to use the same software under both use cases.
  • Browser: On the browser front, things are pretty decent. Chromium has good support for Touchscreen input. Most of the Touchscreen use cases work well with Chromium. On the Firefox side, after a huge delay, finally, Firefox seems to be catching up. Hopefully, with Firefox 51/52, we'll have a much more usable Touchscreen browser.
  • Desktop Shell: One of the reason of migrating to GNOME was its touch support. From what I've explored so far, GNOME is the only desktop shell that has touch support natively done. The feature isn't complete yet, but is fairly well usable.
    • Given that GNOME has touchscreen support native, it is obvious to be using GNOME equivalent of tools for common use cases. Most of these tools inherit the touchscreen capabilities from the underneath GNOME libraries.
    • File Manager: Nautilus has decent support for touch, as a file manager. The only annoying bit is a right-click equivalent. Or in touch input sense, a long-press.
    • Movie Player: There's a decent movie player, based on GNOME libs; GNOME MPV. In my limited use so far, this interface seems to have good support. Other contenders are:
      • SMPlayer is based on Qt libs. So initial expectation would be that Qt based apps would have better Touch support. But I'm yet to see any serious Qt application with Touch input support. Back to SMPlayer, the dev is pragmatic enough to recognize tablet-mode users and as such has provided a so called "Tablet Mode" view for SMPlayer (The tooltip did not get captured in the screenshot).
      • MPV doesn't come with a UI but has basic management with OSD. And in my limited usage, the OSD implementation does seem capable to take touch input.
  • Books / Documents: GNOME Documents/Books is very basic in what it has to offer, to the point that it is not much useful. But since it is based on the same GNOME libraries, it enjoys native touch input support. Calibre, on the other hand, is feature rich. But it is based on (Py)Qt. Touch input is told to work for Windows. For Linux, there's no support yet. The good thing about Calibre is that it has its own UI, which is pretty decent in a Tablet-Mode Touch workflow.
  • Photo Management: With compact digital devices commonly available, digital content (Both Photos and Videos) is on the rise. The most obvious names that come to mind are Digikam and Shotwell.
    • Shotwell saw its reincarnation in the recent past. From what I recollect, it does have touch support but was lacking quite a bit in terms of features, as compared to Digikam.
    • Digikam is an impressive tool for digital content management. While Digikam is a KDE project, thankfully it does a great job in keeping its KDE dependencies to a bare minimum. But given that Digikam builds on KDE/Qt libs, I haven't had any much success in getting a good touch input solution for Tablet Mode. To make it barely usable in Table-Mode, one could choose a theme preference with bigger toolbars, labels and scrollbars. This helps in making a touch input workaround use case. As you can see, I've configured the Digikam UI with Text alongside Icons for easy touch input.
  • Email: The most common use case. With Gmail and friends, many believe standalone email clients are no more a need. But there always are users like us who prefer emails offline, encrypted emails and prefer theis own email domains. Many of these are still doable with free services like Gmail, but still.
    • Thunderbird shows its age at times. And given the state of Firefox in getting touch support (and GTK3 port), I see nothing happening with TB.
    • KMail was something I discontinued while still being on KDE. The debacle that KDEPIM was, is something I'd always avoid, in the future. Complete waste of time/resource in building, testing, reporting and follow-ups.
    • Geary is another email client that recently saw its reincarnation. I recently had explored Geary. It enjoys similar benefits like the rest applications using GNOME libraries. There was one touch input bug I found, but otherwise Geary's featureset was limited in comparison to Evolution.
    • Migration to Evolution, when migrating to GNOME, was not easy. GNOME's philosophy is to keep things simple and limited. In doing that, they restrict possible flexibilities that users may find obvious. This design philosophy is easily visible across all applications of the GNOME family. Evolution is no different. Hence, coming from TB to E was a small unlearning + newLearning curve. And since Evolution is using the same GNOME libraries, it enjoys similar benefits. Touch input support in Evolution is fairly good. The missing bit is the new Toolbar and Menu structure that many have noticed in the newer GNOME applications (Photos, Documents, Nautilus etc). If only Evolution (and the GNOME family) had the option of customization beyond the developer/project's view, there wouldn't be any wishful thoughts.
      • Above is a screenshot of 2 windows of Evoluiton. In its current form too, Evolution is a gem at times. For my RSS feeds, they are stored in a VFolder in Evolution, so that I can read them when offline. RSS feeds are something I read up in Tablet-mode. On the right is an Evolution window with larger fonts, while on the left, Evoltuion still retains its default font size. This current behavior helps me get Table-Mode Touch working to an extent. In my wishful thoughts, I wish if Evolution provided flexibility to change Toolbar icon sizes. That'd really help easily touch the delete button when in Tablet Mode. A simple button, Tablet Mode, like what SMPlayer has done, would keep users sticky with Evolution.
My wishful thought is that people write (free) software, thinking more about usability across toolkits and desktop environments. Otherwise, the year of the Linux desktop, laptop, tablet; in my opinion, is yet to come. And please don't rip apart tools, in porting them to newer versions of the toolkits. When you rip a tool, you also rip all its QA, Bug Reporting and Testing, that was done over the years. Here's an example of a tool (Goldendict), so well written. Written in Qt, Running under GNOME, and serving over the Chromium interface. In this whole exercise of getting a hybrid working setup, I also came to realize that there does not seem to be a standardized interface, yet, to determine the current operating mode of a running hybrid machine. From what we explored so far, every product has its own way to doing it. Most hybrids come pre-installed and supported with Windows only. So, their mode detection logic seems to be proprietary too. In case anyone is awaer of a standard interface, please drop a note in the comments.

Categories:

Keywords:

Like:

16 January 2017

Raphaël Hertzog: Freexian s report about Debian Long Term Support, December 2016

A Debian LTS logoLike each month, here comes a report about the work of paid contributors to Debian LTS. Individual reports In December, about 175 work hours have been dispatched among 14 paid contributors. Their reports are available: Evolution of the situation The number of sponsored hours did not increase but a new silver sponsor is in the process of joining. We are only missing another silver sponsor (or two to four bronze sponsors) to reach our objective of funding the equivalent of a full time position. The security tracker currently lists 31 packages with a known CVE and the dla-needed.txt file 27. The situation improved a little bit compared to last month. Thanks to our sponsors New sponsors are in bold.

No comment Liked this article? Click here. My blog is Flattr-enabled.

Maria Glukhova: APK, images and other stuff.

2 more weeks of my awesome Outreachy journey have passed, so it is time to make an update on my progress. I continued my work on improving diffoscope by fixing bugs and completing wishlist items. These include:

Improving APK support I worked on #850501 and #850502 to improve the way diffoscope handles APK files. Thanks to Emanuel Bronshtein for providing clear description on how to reproduce these bugs and ideas on how to fix them. And special thanks to Chris Lamb for insisting on providing tests for these changes! That part actually proved to be little more tricky, and I managed to mess up with these tests (extra thanks to Chris for cleaning up the mess I created). Hope that also means I learned something from my mistakes. Also, I was pleased to see F-droid Verification Server as a sign of F-droid progress on reproducible builds effort - I hope these changes to diffoscope will help them!

Adding support for image metadata That came from #849395 - a request was made to compare image metadata along with image content. Diffoscope has support for three types of images: JPEG, MS Windows Icon (*.ico) and PNG. Among these, PNG already had good image metadata support thanks to sng tool, so I worked on .jpeg and .ico files support. I initially tried to use exiftool for extracting metadata, but then I discovered it does not handle .ico files, so I decided to use a bigger force - ImageMagick s identify - for this task. I was glad to see it had that handy -format option I could use to select only the necessary fields (I found their -verbose, well, too verbose for the task) and presenting them in the defined form, negating the need of filtering its output. What was particulary interesting and important for me in terms of learning: while working on this feature, I discovered that, at the moment, diffoscope could not handle .ico files at all - img2txt tool, that was used for retrieving image content, did not support that type of images. But instead of recognizing this as a bug and resolving it, I started to think of possible workaround, allowing for retrieving image metadata even after retrieving image content failed. Definetely not very good thinking. Thanks Mattia Rizzolo for actually recognizing this as a bug and filing it, and Chris Lamb for fixing it!

Other work

Order-like differences, part 2 In the previous post, I mentioned Lunar s suggestion to use hashing for finding order-like difference in wide variety of input data. I implemented that idea, but after discussion with my mentor, we decided it is probably not worth it - this change would alter quite a lot of things in core modules of diffoscope, and the gain would be not really significant. Still, implementing that was an important experience for me, as I had to hack on deepest and, arguably, most difficult modules of diffoscope and gained some insight on how they work.

Comparing with several tools (work in progress) Although my initial motivation for this idea was flawed (the workaround I mentioned earlier for .ico files), it still might be useful to have a mechanism that would allow to run several commands for finding difference, and then give the output of those that succeed, failing if and only if they all have failed. One possible case when it might happen is when we use commands coming from different tools, and one of them is not installed. It would be nice if we still used the other and not the uninformative binary diff (that is a default fallback option for when something goes wrong with more clever comparison). I am still in process of polishing this change, though, and still in doubt if it is needed at all.

Side note - Outreachy and my university progress In my Outreachy application, I promised that if I am selected into this round, I will do everything I can to unload the required time period from my university time commitements. I did that by moving most of my courses to the first half of the academic year. Now, the main thing that is left for me to do is my Master s thesis. I consulted my scientific advisors from both universities that I am formally attending (SFEDU and LUT - I am in double degree program), and as a result, they agreed to change my Master s thesis topic to match my Outreachy work. Now, that should have sounded like an excellent news - merging these activities together actually mean I can allocate much more time to my work on reproducible builds, even beyond the actual internship time period. That was intended to remove a burden from my shoulders. Still, I feel a bit uneasy. The drawback of this decision lies in fact I have no idea on how to write scientific report based on pure practical work. I know other students from my universities have done such things before, but choosing my own topic means my scientific advisors can t help me much - this is just out of their area of expertise. Well, wish me luck - I m up to the challenge!

15 January 2017

Dirk Eddelbuettel: Rcpp 0.12.9: Next round

Yesterday afternoon, the nineth update in the 0.12.* series of Rcpp made it to the CRAN network for GNU R. Windows binaries have by now been generated; and the package was updated in Debian too. This 0.12.9 release follows the 0.12.0 release from late July, the 0.12.1 release in September, the 0.12.2 release in November, the 0.12.3 release in January, the 0.12.4 release in March, the 0.12.5 release in May, the 0.12.6 release in July, the 0.12.7 release in September, and the 0.12.8 release in November --- making it the thirteenth release at the steady bi-montly release frequency. Rcpp has become the most popular way of enhancing GNU R with C or C++ code. As of today, 906 packages on CRAN depend on Rcpp for making analytical code go faster and further. That is up by sixthythree packages over the two months since the last release -- or about a package a day! Some of the changes in this release are smaller and detail-oriented. We did squash one annoying bug (stemming from the improved exception handling) in Rcpp::stop() that hit a few people. Nathan Russell added a sample() function (similar to the optional one in RcppArmadillo; this required a minor cleanup by for small number of other packages which used both namespaces 'opened'. Date and Datetime objects now have format() methods and << output support. We now have coverage reports via covr as well. Last but not least James "coatless" Balamuta was once more tireless on documentation and API consistency --- see below for more details.
Changes in Rcpp version 0.12.9 (2017-01-14)
  • Changes in Rcpp API:
    • The exception stack message is now correctly demangled on all compiler versions (Jim Hester in #598)
    • Date and Datetime object and vector now have format methods and operator<< support (#599).
    • The size operator in Matrix is explicitly referenced avoiding a g++-6 issues (#607 fixing #605).
    • The underlying date calculation code was updated (#621, #623).
    • Addressed improper diagonal fill for non-symmetric matrices (James Balamuta in #622 addressing #619)
  • Changes in Rcpp Sugar:
    • Added new Sugar function sample() (Nathan Russell in #610 and #616).
    • Added new Sugar function Arg() (James Balamuta in #626 addressing #625).
  • Changes in Rcpp unit tests
    • Added Environment::find unit tests and an Environment::get(Symbol) test (James Balamuta in #595 addressing issue #594).
    • Added diagonal matrix fill tests (James Balamuta in #622 addressing #619)
  • Changes in Rcpp Documentation:
    • Exposed pointers macros were included in the Rcpp Extending vignette (MathurinD; James Balamuta in #592 addressing #418).
    • The file Rcpp.bib move to directory bib which is guaranteed to be present (#631).
  • Changes in Rcpp build system
    • Travis CI now also calls covr for coverage analysis (Jim Hester in PR #591)

Thanks to CRANberries, you can also look at a diff to the previous release. As always, even fuller details are on the Rcpp Changelog page and the Rcpp page which also leads to the downloads page, the browseable doxygen docs and zip files of doxygen output for the standard formats. A local directory has source and documentation too. Questions, comments etc should go to the rcpp-devel mailing list off the R-Forge page.

This post by Dirk Eddelbuettel originated on his Thinking inside the box blog. Please report excessive re-aggregation in third-party for-profit settings.

Mehdi Dogguy: Debian from 10,000 feet

Many of you are big fans of S.W.O.T analysis, I am sure of that! :-) Technical competence is our strongest suit, but we have reached a size and sphere of influence which requires an increase in organisation.

We all love our project and want to make sure Debian still shines in the next decades (and centuries!). One way to secure that goal is to identify elements/events/things which could put that goal at risk. To this end, we've organized a short S.W.O.T analysis session at DebConf16. Minutes of the meeting can be found here. I believe it is an interesting read and is useful for Debian old-timers as well as newcomers. It helps to convey a better understanding of the project's status. For each item, we've tried to identify an action.

Here are a few things we've worked on:
During next DebConf, we can review the progress that has been made on each item and discuss new ones. In addition to this session acting as a health check, I see it as a way for the DPL to discuss, openly and publicly, about the important changes that should be implemented in the project and imagine together a better future.

In the meantime, everyone should feel free to pick one item from the list and work on it. :-)

14 January 2017

Jamie McClelland: What's Up with WhatsApp?

Despite my jaded feelings about corporate Internet services in general, I was suprised to learn that WhatsApp's end-to-end encryption was a lie. In short, it is possible to send an encrypted message to a user that is intercepted and effectively de-crypted without the sender's knowledge. However, I was even more surprised to read Open Whisper Systems critique of the original story, claiming that it is not a backdoor because the WhatsApp sender's client is always notified when a message is de-crypted. The Open Whisper Systems post acknowledges that the WhatsApp sender can choose to disable these notifications, but claims that is not such a big deal because the WhatsApp server has no way to know which clients have this feature enabled and which do not, so intercepting a message is risky because it could result in the sender realizing it. However, there is a fairly important piece of information missing, namely: as far as I can tell, the setting to notify users about key changes is disabled by default. So, using the default installation, your end-to-end encrypted message could be intercepted and decrypted without you or the party you are communicating with knowing it. How is this not a back door? And yes, if the interceptor can't tell whether or not the sender has these notifications turned on, the interceptor runs the risk of someone knowing they have intercepted the message. Great. That's better than nothing. Except that there is strong evidence that many powerful governments on this planet routinely risk exposure in their pursuit of compromising our ability to communicate securely. And... not to mention non-governmental (or governmental) adversaries for whom exposure is not a big deal. Furthermore a critical reason for end-to-end encrption is so that your provider does not have the technical capacity to intercept your communications. That's simply not true of WhatsApp. It is true of Signal and OMEMO, which requires the active participation of the sender to compromise the communication. Why in the world would you distribute a client that not only has the ability to surpress such warnings, but has it enabled by default? Some may argue that users regularly dismiss notifications like "fingerprint has changed" and that this problem is the achilles heal of secure communications. I agree. But... there is still a monumental difference between a user absent-mindedly dismissing an important security warning and never seeing the warning in the first place. This flaw in WhatsApp is a critical reminder that secure communications doesn't just depend on a good protocol or technology, but on trust in the people who design and maintain our systems.

13 January 2017

Elena 'valhalla' Grandi: Modern XMPP Server

Modern XMPP Server

I've published a new HOWTO on my website 'http://www.trueelena.org/computers/howto/modern_xmpp_server.html':

http://www.enricozini.org/blog/2017/debian/modern-and-secure-instant-messaging/ already wrote about the Why (and the What, Who and When), so I'll just quote his conclusion and move on to the How.

I now have an XMPP setup which has all the features of the recent fancy chat systems, and on top of that it runs, client and server, on Free Software, which can be audited, it is federated and I can self-host my own server in my own VPS if I want to, with packages supported in Debian.


How

I've decided to install https://prosody.im/, mostly because it was recommended by the RTC QuickStart Guide http://rtcquickstart.org/; I've heard that similar results can be reached with https://www.ejabberd.im/ and other servers.

I'm also targeting https://www.debian.org/ stable (+ backports); as I write this is jessie; if there are significant differences I will update this article when I will upgrade my server to stretch. Right now, this means that I'm using prosody 0.9 (and that's probably also the version that will be available in stretch).

Installation and prerequisites

You will need to enable the https://backports.debian.org/ repository and then install the packages prosody and prosody-modules.

You also need to setup some TLS certificates (I used Let's Encrypt https://letsencrypt.org/); and make them readable by the prosody user; you can see Chapter 12 of the RTC QuickStart Guide http://rtcquickstart.org/guide/multi/xmpp-server-prosody.html for more details.

On your firewall, you'll need to open the following TCP ports:


The latter two are needed to enable some services provided via http(s), including rich media transfers.

With just a handful of users, I didn't bother to configure LDAP or anything else, but just created users manually via:

prosodyctl adduser alice@example.org

In-band registration is disabled by default (and I've left it that way, to prevent my server from being used to send spim https://en.wikipedia.org/wiki/Messaging_spam).

prosody configuration

You can then start configuring prosody by editing /etc/prosody/prosody.cfg.lua and changing a few values from the distribution defaults.

First of all, enforce the use of encryption and certificate checking both for client2server and server2server communications with:


c2s_require_encryption = true
s2s_secure_auth = true


and then, sadly, add to the whitelist any server that you want to talk to and doesn't support the above:


s2s_insecure_domains = "gmail.com"


virtualhosts

For each virtualhost you want to configure, create a file /etc/prosody/conf.avail/chat.example.org.cfg.lua with contents like the following:


VirtualHost "chat.example.org"
enabled = true
ssl =
key = "/etc/ssl/private/example.org-key.pem";
certificate = "/etc/ssl/public/example.org.pem";


For the domains where you also want to enable MUCs, add the follwing lines:


Component "conference.chat.example.org" "muc"
restrict_room_creation = "local"


the "local" configures prosody so that only local users are allowed to create new rooms (but then everybody can join them, if the room administrator allows it): this may help reduce unwanted usages of your server by random people.

You can also add the following line to enable rich media transfers via http uploads (XEP-0363):


Component "upload.chat.trueelena.org" "http_upload"

The defaults are pretty sane, but see https://modules.prosody.im/mod_http_upload.html for details on what knobs you can configure for this module

Don't forget to enable the virtualhost by linking the file inside /etc/prosody/conf.d/.

additional modules

Most of the other interesting XEPs are enabled by loading additional modules inside /etc/prosody/prosody.cfg.lua (under modules_enabled); to enable mod_something just add a line like:


"something";

Most of these come from the prosody-modules package (and thus from https://modules.prosody.im/ ) and some may require changing when prosody 0.10 will be available; when this is the case it is mentioned below.


@Gruppo Linux Como @LIFO

11 January 2017

Dirk Eddelbuettel: R / Finance 2017 Call for Papers

Last week, Josh sent the call for papers to the R-SIG-Finance list making everyone aware that we will have our nineth annual R/Finance conference in Chicago in May. Please see the call for paper (at the link, below, or at the website) and consider submitting a paper. We are once again very excited about our conference, thrilled about upcoming keynotes and hope that many R / Finance users will not only join us in Chicago in May 2017 -- but also submit an exciting proposal. We also overhauled the website, so please see R/Finance. It should render well and fast on devices of all sizes: phones, tablets, desktops with browsers in different resolutions. The program and registration details still correspond to last year's conference and will be updated in due course. So read on below, and see you in Chicago in May!

Call for Papers R/Finance 2017: Applied Finance with R
May 19 and 20, 2017
University of Illinois at Chicago, IL, USA The ninth annual R/Finance conference for applied finance using R will be held on May 19 and 20, 2017 in Chicago, IL, USA at the University of Illinois at Chicago. The conference will cover topics including portfolio management, time series analysis, advanced risk tools, high-performance computing, market microstructure, and econometrics. All will be discussed within the context of using R as a primary tool for financial risk management, portfolio construction, and trading. Over the past eight years, R/Finance has included attendees from around the world. It has featured presentations from prominent academics and practitioners, and we anticipate another exciting line-up for 2017. We invite you to submit complete papers in pdf format for consideration. We will also consider one-page abstracts (in txt or pdf format) although more complete papers are preferred. We welcome submissions for both full talks and abbreviated "lightning talks." Both academic and practitioner proposals related to R are encouraged. All slides will be made publicly available at conference time. Presenters are strongly encouraged to provide working R code to accompany the slides. Data sets should also be made public for the purposes of reproducibility (though we realize this may be limited due to contracts with data vendors). Preference may be given to presenters who have released R packages. Financial assistance for travel and accommodation may be available to presenters, however requests must be made at the time of submission. Assistance will be granted at the discretion of the conference committee. Please submit proposals online at http://go.uic.edu/rfinsubmit. Submissions will be reviewed and accepted on a rolling basis with a final deadline of February 28, 2017. Submitters will be notified via email by March 31, 2017 of acceptance, presentation length, and financial assistance (if requested). Additional details will be announced via the conference website as they become available. Information on previous years' presenters and their presentations are also at the conference website. We will make a separate announcement when registration opens. For the program committee:
Gib Bassett, Peter Carl, Dirk Eddelbuettel, Brian Peterson,
Dale Rosenthal, Jeffrey Ryan, Joshua Ulrich

Next.

Previous.