Search Results: "zed"

13 May 2010

Aigars Mahinovs: Hacker Neo caught in Latvia

A scandal has been brewing in Latvia over the last half year and yesterday the activity spiked shocking the media and some IT people in the country. I ll go back and explain what happened first, what is happening now and why this could have a heavy impact on IT and journalists in Latvia. At the end of last year, there were rumours that the IT system of Latvia s Internal Revenue System was hacked and millions of documents had been downloaded by multiple organizations. Shortly thereafter more details on the glaring security hole became public (after it was closed). There is a full electronic interface to give all reports to the IRS electronically (at http://eds.vid.gov.lv) and as part of that system you could also view and export monthly report summaries about your organization into XML and PDF files. After the system checked that you are authorized to access the report, you were redirected to the URL to actually download the report by report ID (as a single param in a GET request). Unfortunately, report IDs were predicable and the script that gave the reports for download did not check if you were authorized to get that report. It did not even check if were logged into the system. There were suspicions that the authorization was disabled on purpose to allow to leak data on purpose, but apparently it was an error of forgetting to disable debug code in production environment. The error was discovered only because the firewall administrator noticed an unexplained stable increase of traffic, especially during night hours when typically the traffic fully stopped. Apparently a single hacker (who later identified himself as Neo to the press) discovered the flaw and wrote a script to just try all possible report ids and get as much data out as possible. This had been going on for months, before someone noticed. After the flaw was discovered and a bit of time passed, Neo made his first move he published the list of top salaries in a governmental company, that clearly showed that the top leadership of this company failed to cut their salary by 40%, like everyone elses during harsh budget cuts of 2009. He stripped the names and ids of the specific employees, but named the company which made it pretty easy to figure out who was who. The society was outraged that the top managers in a government owned company failed to comply with the strict pay cut that everyone else in government had to endure. But after a few weeks the outrage subsided and no action followed from the government or law enforcement. Neo continued to release documents detailing salaries of top managers in different Latvian government companies. And each time after short outrage, nothing happened. Neo gave an interview where he said that he was disappointed in the passivity of the Latvian people in face of such blatant injustices. After a few month Neo went silent, promising to return before parliamentary elections this fall. However, this week a new development shocked everyone in the middle of the night two police SWAT teams went into action: one detained Ilm rs Poik ns, a researcher in artificial intelligence at the University of Latvia s Computer Science department and another raided the home of a Latvian TV journalist Ilze Nagle who interviewed Neo. Poik ns confessed of being Neo the next day and was released (with travel restrictions, pending trial) today. Politicians reacted immediately opposition demanded the resignation of the Interior Minister over such blatant disregard of freedom of press and another politician (who is also a famous lawyer) Aleksejs Loskutovs volunteered to defend Neo pro-bono (on Twitter, no less). Almost all Latvian online media have the arrest of Neo and the raid on the home of a journalist as main stories of the day. As a legal titbit, we also know that Neo is being charged with breaking statutes 145 and and 244p2 of the criminal law. Statute 145 is hard to find applicable in this situation as talks about actions done by people authorized (..) to access [private] information . Statute 244p2 will also be hard to pin down as it mentions influencing system resources of (an IT system) and if such action caused severe harm . It looks like the first part talks about at least a DoS attack (which did not happen in this case) and also there was no measurable harm from these leaks. Also Neo was careful to strip all personally identifying information (such as names, social security numbers and addresses of the employees in question), so it will be hard to pin him on that. Also no actual breaking or other modification of an IT system occurred. And no specialized software was used beyond a trivial script such as :
for i in range(0,7000000):
    wget('https://eds.vid.gov.lv/getRep.aspx?id='+str(i))
A lot of commentators on the Internet likened the situation to walking trough an unlocked door and stealing something. I think that analogy is very incorrect there was no door, and nothing went missing after the action. I came up with a different analogy there was this corridor with a lot of doors in IRS, locked steel doors. You were instructed to go to a room with a specified number and given a key to that room to unlock it and see your secret info. However, that corridor opened out to the street on one end, oh and also the walls of the rooms with all the secrets were transparent. So Neo walked into the corridor, looked at some of the secrets, wrote them down (to remember them better) and then went out and discussed the worst examples abuses of power he saw. In the end IRS had to learn their lesson if you have to put naked photos of yourself on the Internet (or something equally embarrassing), then make damn sure you password protect that, but if you don t then don t cry that someone hacked you and stole you pictures. What other people think:
http://freespeechlatvia.blogspot.com/2010/05/neo-released-under-restrictions.html We ll see how the story develops soon.

11 May 2010

Torsten Werner: Ubuntu Developer Summit

That is my second day at the UDS in Brussels. I have attended some sessions about server and cloud yesterday. The Ubuntu people are better organized than the Debian people during Debconf. They are collaboratively preparing the sessions in Launchpad and make notes with the Gobby editor during the session. Gobby allows group editing via Internet. The release date helps to keep the focus on stuff that can be done within the time frame and helps to concentrate on getting results.

It will probably be only 5 months for Maverick because Mark asked for a release on 10.10.10 which is an interesting date after removing the dots and converting it to a decimal number. I am comparing it to Debian: Toy Story 3 will be shown in cinemas soon and the Squeeze character is promoting the film. Will we use such a coincidence for more public attention and will will we release our Squeeze soon? I am afraid that it won't happen.

Our last session yesterday was about Tomcat packaging improvements. Debian and Ubuntu are using and maintaining identical packages of tomcat6 using the alioth infrastructure of the pkg-java team. Some of our plans are:

10 May 2010

Romain Beauxis: Ubuntu, the firm and its employees

This post is not meant to be offensive in any way. I would just like to write down things that came to my mind recently. It all started when I was considering applying for the right to upload the package I maintain into Ubuntu. Looking at the procedure, I realized that this needs to be present during an IRC meeting at a given date online. This stopped me immediately. I am working most of my day-time and, given the time zone I am living now, this was not an option. But, since I had registered to the corresponding mailing list, I started receiving mails of other applicants that where trying to arrange things with their work and private life to be able to participate. Now, today, I stumbled upon these notes of Mark's presentation in Bruxelles, relayed by a friend that is not either working for Ubuntu. Reading it gave me a strong taste of management-oriented presentation, with all this sort of "yeah we want our product in every box next year" propaganda. Not like Steve Ballmer, fortunately, but not far perhaps. So, yeah, there is something that makes me uncomfortable with Ubuntu. I am really happy by its success and I will continue to recommend it to friends around me. However, I wonder if, in a way, Ubuntu is not a model of commercial company where a minimal core of developers are actually payed, while a second layer of developers are fan-boys that are willing to participate as if there were employees but without being actually payed, and a third layer being the open-source developers whose work is actually what makes 90% of the core of the OS. A very good illustration is at the end of the note from Mark's presentation. It reads:
Somebody asks about advertising Ubuntu, looks like there are no plans for the moment to actually advertise Ubuntu across traditional media. Mark uses the Ubuntu Manual as an example of how Ubuntu gets advertised and will reach the mainstream, Mark points out myself and the room applauds the Ubuntu Manual Project! Woohoo!
Now, guess what:
About Us We are a group of individuals trying to promote the use of Ubuntu and its variants. This is a private web site that is not connected in any official or financial way with Ubuntu, Canonical PL or Ubuntu.com. Official Ubuntu guides and downloads are freely available at www.ubuntu.com. Ubuntu is a registered trademark of Canonical PL
Source: http://ubuntumanual.org/about-us

6 May 2010

Debian News: Brief Updates: Chromium browser, KDE and GNOME updates, DebConf sponsoring and Ben NanoNote

5 May 2010

Ritesh Raj Sarraf: Debian Developer

Finally, I am proud to be officially part of one of the most successful and well organized Free/Open project, the Debian project.I would like to thank everyone who have worked with me. I would also like to thank my Advocate Giridhar and my AM Pablo. It was and is really awesome working with you guys.

4 May 2010

Alastair McKinstry: EGU 2010 - Monday

I'm at the European Geosciences Union (EGU) General Assembly, 2010, the biggest gethering of European geoscientists, in Vienna, May 2-7. This is my first time here and its huge: over 9000 participants. Merely finding the talks and posters is a challenge (they supply a USB stick with the abstracts and agendas as they can't print them all! The first day I spent mostly at the exoplanet stream (and putting up my own poster). Some neat stuff on show: summaries by Borucki on Keplers findings (on the Hot Jupiters they found :" these things glow like a blast furnace; forget life"). He points out that when they look for Earth sized planets, radial velocity confirmation would take 1000s of hours on 10M telescopes - so it won't happen. hmm. Steve Unwin on SIM: neat astrometric mission for planet hunting and galaxy measurement. A targeted mission list, unlike the Gaia survey; to fly in 2016 if the Decadal survey says yes. 20% of time available under the general observer program, so get proposals ready ? Nestest poster idea: Anomalous night-time temps on Mars, Gonzales et al.. Finding hot spots on Arsia Mons, a volcano. Explained by air rising from 100km long lava tubes. We've seen pit entrances to caves on Mars with HiRISE, etc. here they model heat output from a pit entrace/exit and imply 100km caves. Oh to go exploring... Tinetti points out that we lack proper spectra, both experimental and theoretical, for high temperature and pressure gases such as methane, etc. Hmm, I know a group in Galway that might be able to help ... Helmut Lammer raised an interesting point at the poster session, that many groups ignore the stellar wind when looking at H2 atmospheres around exoplanets. Theis grossly inflates the apparent H2 atmosphere. Without taking this into acount it would be easy to mistake H2 detections with a Neptune-like atmosphere. He points to a 1.7M UV telescope that the Russians are planning to launch that would help do UV measurements when Hubble is gone. Lena Noack gave a talk on convection in tidally-locked planets (with related poster Low-lid formation on Super-Earths and implications for the habitability of Super-Earths and Sub-Earths). They argue that no covection can be expected in the mantle, and hence no geodynamo or magnetosphere. This could be a problem for holding an atmosphere. Time to check for planetary magnetic fields. Break out the polarimeter ? Oh, and it seems that That Damned Volcano is closing Irish airspace on Tuesday. Might be an idea to go to the meeting about it. Hope it clears by Friday ... Tags ,

2 May 2010

Dominique Dumont: Improve config file upgrades Ep 01

Hello The GSoC project Krzysztof and I are working aims to facilitate configuration upgrade during package upgrades. Most of the cases, this upgrade should not require any input from the user, even if the user had previously customized his configuration file. Currently configuration upgrade may ask questions to the user which may be hard to answer for most non-technical users. For more details see PackageConfigUpgrade on Debian wiki. (If you are not familiar with upgrade issues, you might want to read this page.) At the 2 extremes of upgrade tools, we have: Each tool has its own advantages and drawbacks. On the plus side of diff3 tools : On the other hand, here are the issues with diff3 based tools: For more details on diff3 issues, see Benjamin Pierce s paper (thanks to David Lutterkort from Augeas for the info) On the other end of the spectrum, Config::Model pros are: But, Config::Model main problem is: diff3 tools is lackluster for users. While Config::Model puts too much strain on packagers because it requires configuration models where all parameters are defined and declared in the model. For fast evolving projects, this can be a huge recurrent task (been there, done that for Xorg) . (Well, this recurrent task is a problem until doc, implementation and config model can be extracted from a single meta-description But I digress, this may be a project for GSoC 2011 :-p ) So, this GSoC project (for 2010) aims to find a compromise between these 2 extreme cases. On Config::Model, I ve always had a drawer statement whenever I was asked why Config::Model does not handle unknown parameter:
a configuration file cannot be validated if an unknown parameter can t be distinguished from a user typo.
This stance is fine for casual user interaction on a stable system: an unknown parameter is most likely an error. And the user must be warned of his error as soon as possible. For a stable distro release, packagers should have the time to provide complete models, so basing upgrade on complete models should be possible (famous last words ?). On the other hand, a lot of configuration upgrades will be done on unstable systems where software evolve quite fast, where models will likely fall behind software evolutions. Another shorcoming of my drawer statement is that it assumes user interaction where erroneous input is more likely. In case of configuration upgrades, there should be no user interaction. And we can assume that the config file to be upgraded was used (and thus validated) by the old version of the software. So unknown parameters should be tolerated and managed as best as possible. Now, the big question is: how ? In all attempts I ve seen in managing upgrades that goes beyond diff3 tools, the configuration is stored as structured data. Sometimes this structure can be infered from the configuration file syntax (shell vars, INI files, YAML, XML), sometimes not (sshd config file). In the latter case, some structural knowledge must be built in the upgrade tool. Currently, Config::Model is designed to bring a complete description of the structure and semantics of a configuration file. This is perceived as bringing too much structural and semantic knowledge ( too semantic ). So the maintenance cost is perceived as too important. That may be right or wrong, but that does not matter. Perception is more important here. So, let s figure out a way to reduce the amount of work required to perform upgrades (you may want to read a little bit more on configuration model creation before going on ) One possibility would be to support configuration models that allow unknown leaves in nodes. Such a model would provide a kind of fallback leaf description. Something like: this parameter is unknown, let s assume it s a simple string value . Let s consider sshd_config example to see how such a behavior would pan out for some upgrade scenarios. sshd model is made of 2 main classes:
- Sshd
- SshdMatchElement The second one contains all parameters allowed in a Match class (in fact, Match parameter is the only one in sshd that defines a new hierarchical level. All other parameters are simple leaves). Now let s consider typical upgrade scenarios from old version (with old models) to a more modern version. Let s assume that the model is lagging behind and the model does not follow sshd evolutions. So Config::Model will face 3 upgrade cases (extracted from sshd config history):
  1. Unexpected parameter that are actually simple leaf parameters. E.g. introduction of ClientAliveInterval.
  2. Obsolete parameters that should be migrated. E.g KeepAlive is renamed into TCPKeepAlive
  3. New structural parameters (introduction of Match element)
So what would happen with a model allowing unknown parameters but lacking specific instructions for these upgrades:
  1. ClientAliveInterval value would be kept. :-)
  2. KeepAlive would be kept as is.TCPKeepAlive would also be kept. No migration is performed, but the configuration would be good. As long as sshd supports the old parameter, we re good. :-/
  3. Without knowledge of the structure brought by Match parameters, Config::Model would consider that parameter in Match block would duplicate parameters in the main block and remove the duplicate. User data may be lost. :-(
So, there s not silver bullet. Let s resume what we ve learnt: Next step is to figure out what would happen if the same strategy is applied to other types of configuration files. But that will be for another blog. All the best

Julien Blache: forked-daapd: now with AirTunes v2 streaming

I ve been working on this for a few months now; it s taken quite some time because I wanted to do it right and deliver something better than what already existed in the OpenSource world as far as that particular technology was (not) concerned. So here it is:

AirTunes v2 UDP streaming forked-daapd can now do streaming to multiple AirTunes devices (as well as the local soundcard) and can be controlled from Remote (and, ideally, from anything that speaks DACP). I m releasing this early while the paint is still wet and not everything works on the DACP-side of things. Case in point, while playing a song or an album is supported, playing a playlist isn t. There s some work needed on this particular feature, and it ll get there eventually. There have been a couple of other changes in the codebase in recent weeks too; details after the jump. Implementing AirTunes v2 has been quite fun and, in addition to releasing the forked-daapd code today, I ve also taken the time to write down my findings about the protocol so others can experiment with it. This documentation is by no means exhaustive nor complete as far as the protocol goes; if you find out anything I haven t, let me know so I can update this document. Let s review the recent changes in the forked-daapd codebase over the past few weeks. AirTunes v2 You can now use Remote from your iSomething together with your AirTunes devices and forked-daapd to listen to your library. As mentioned above, playing a playlist is not supported; I have a few things to sort out before this can work and I suspect this will bring changes not only to the DACP interface but also to other parts of the code. So, stay tuned. forked-daapd supports synchronized playback to multiple AirTunes devices together with the local soundcard if so desired. You can expect the AirTunes devices to be in sync with each other, but the soundcard will usually run in circles around them. It looks like AirTunes plays sound a bit slower than 44.1 kHz; not a big deal, though, as AirTunes will catch up periodically and the desync, while it can be noticeable, isn t big (ie we re not talking seconds, not even one full second). Make sure your network can handle the load, as streaming to a single AirTunes device requires in excess of 1.6 Mbps (1.8 Mbps is actually closer to the real thing). Local audio output is supported via ALSA and OSS4, although note that the OSS4 code hasn t been very well tested. I intend to test and debug it fully at a later date, but feel free to beat me to it and send patches. Also note that, while there is code for FreeBSD in the player/streaming part of forked-daapd, it doesn t work well at all. The streaming code needs a timer with a higher resolution than kqueue/kevent has to offer, and I haven t found anything as capable as timerfd. So it s there, but it s broken. Read on about FreeBSD support. Metadata scanning Several fixes and enhancements have been made to the filescanner so it picks more and better metadata. Format-specific tagnames have been added to work around ffmpeg s limitations. Using a recent enough ffmpeg version (anything after mid-december 2009) will work best, especially for MP3 files. SQLite concurrency fixes The database code has been reworked to handle concurrency on the database. Issues with locked tables (or the whole database) were noticed pretty easily with big libraries when accessing forked-daapd during the library update after startup. On uniprocessor machines, this was even easier to hit. This, however, comes with new requirements for SQLite3: you ll now need SQLite3 v3.5.0 at least and it must be built with the unlock notify API enabled. Not all distributions ship SQLite3 with the unlock notify API enabled, so you may need to do a rebuild. Debian, for instance, doesn t; this is #579266. A word about FreeBSD support I m giving up on FreeBSD support. The streaming code doesn t work on FreeBSD due to timer issues, and I don t intend to fix it. I also don t intend to invest much time in porting future features to FreeBSD; if I can make it work, then fine, otherwise, too bad. Someone needs to step up if there s interest in having forked-daapd work on FreeBSD.

1 May 2010

Sean Finney: Nouveau, Gallium3D, and Compiz on Debian

update: 20100503: It's been brought to my attention that there might have been a regression in one of the libraries, mesa, maybe, so that master might not be as reliable a reference point for this guide. so, just in case, here are the commit hashes that were used from the different projects: for the non-git-savvy: git checkout -b mybranch <hash> we now return to your regular broadcasting... A week or two ago I figured it was about time that I took the plung and tried out the latest nouveau drivers from experimental on my laptop. Unfortunately, it meant bidding adieu to compiz (apart from the bling it does actually provide some pretty damned useful features). I thought I'd give it a shot at least for a while on principal, since I've always had to think of the nvidia drivers as a necessary evil, and their lack of proper xrandr support is really, really annoying. Since then I haven't noticed any problems, apart from the following message after every suspend/resume:
[  931.213239] Uhhuh. NMI received for unknown reason 80 on CPU 0.
[  931.213240] You have some hardware problem, likely on the PCI bus.
[  931.213242] Dazed and confused, but trying to continue

No idea what's causing it, but otherwise the system is stable and functional. If anyone knows what can be done about this, I'd appreciate hearing from you. My graphics card, by the way:
01:00.0 VGA compatible controller: nVidia Corporation G72M [Quadro NVS 110M/GeForce Go 7300] (rev a1)

In the time since then, the nouveau driver has made its way into unstable, and a lot of distros (ubuntu, fedora, ...) are even using it as the default driver. So before going any further with the 3d/compiz stuff, I highly recommend that you get the packaged version working first. This will not only make sure that the basic driver works, but it will also make recovery/rollback a lot easier. Since it's all packaged in the standard repositories, it's not much harder than installing a few packages and editing a few files... so come on give it a try :) Getting the 2d driver working in Debian sid Really, this is so easy it's hardly worth writing up, but i'm running with the -v flag this morning... Make sure you don't have any reference to nvidia in /etc/modules or other places that might cause it to be automatically loaded. Then remove the proprietary glx bindings, which would otherwise interfere with the nouveau driver.
sudo apt-get remove nvidia-glx

Next, you'll need to install a kernel that includes updated drm support. Normally this would require a kernel >= 2.6.33.1, but the debian kernel maintainers have graciously backported this code to the 2.6.32-4 kernel package. note this isn't the default kernel version in testing/unstable at the time of writing so you have to explicitly install it along with the nouveau driver.
sudo apt-get install linux-image-2.6.32-4-amd64 xserver-xorg-video-nouveau

If you are already running this kernel and using the proprietary nvidia drivers, via module-assistant or otherwise, you /might/ need to uninstall them first. On my system I left them installed in the old kernel version but did not install them on the new kernel version. Required xorg configuration I don't believe that nouveau is picked by default if available at the time of writing, so you have to have the following in your xorg.conf:
sudo sh -c "cat > /etc/X11/xorg.conf" << EOF
Section "Device"
    Identifier     "nVidia Corporation G72M [Quadro NVS 110M/GeForce Go 7300]"
    Driver         "nouveau"
EndSection
EOF

This was all I needed to do, apart from rebooting into the new kernel. For those who don't want to venture outside the packaging system, this is about as far as you can go for the time being. Though really, if you're bothering to read this far along, you're probably more interested in what comes next :) Getting 3d working (without voiding your distro warranty) So I thought I'd give the 3d-accelerated gallium a go. Their wiki page certainly makes one think twice, but at this point I was seriously fiending to get my bling back (well, the compiz scale plugin, anyway) and figured it wouldn't hurt too much to try. Via google and trawling around in various forums I found a number of how-to documents for getting Gallium3d on debian/ubuntu systems, but most of them recommended doing things in a way that wasn't easily reversible and that could totally hose your system in a not-so-hypothetical worst-case scenario. It's pretty hard to roll back a make install done into /usr, for example, and subsequent package upgrades can leave your system even worse off as they will probably clobber half of what you just did, leaving the other half totally broken. And if you have a laptop which requires the gui for networking (i.e. network-manager), then fixing/rolling-back the changes is not entirely trivial, since you'd likely have to re-download the various drm/mesa/xorg packages. So enter the tried and true unix utility stow (apt-get install stow, of course). stow is a utility that lets you install software into arbitrary folders, and then manage the system-wide installation of the software via a farm of symlinks pointing at the installed location. It's probably more well known among the sysadmin crowd than the desktop user crowd, but it's incredibly useful for the task at hand as it will let us easily install multiple copies of different software in a way that's very easy to update and/or roll-back. RTFM stow(1) for more information. So, on to the juicy stuff... Install needed software, remove problematic packages, setup, etc At least on my system, I had to remove libdrm-dev to keep things from accidentally linking against it instead of the updated version that we install later on below. There's probably a way to override this with CFLAGS but I figure this is simpler.
sudo apt-get remove libdrm-dev
sudo apt-get install stow build-essential xorg-dev git-core libtool mesa-common-dev automake autoconf 
mkdir ~/nouveau

Compile a linux-2.6.34 RC kernel
cd ~/nouveau
git clone git://git.kernel.org/pub/scm/linux/kernel/git/torvalds/linux-2.6.git
cd linux-2.6
git remote add -f nouveau git://anongit.freedesktop.org/nouveau/linux-2.6
git checkout -b nouveau-master nouveau/master
make menuconfig

Enable device drivers -> staging drivers -> nouveau. Make any other changes you might want to make (I just took defaults for everything else).
make deb-pkg

The linux-firmware-free debian package ships some of the same stuff from the generated linux-firmware-image package. I decided to opt for the upstream firmware, though I'm not sure that this is necessary:
sudo apt-get remove linux-firmware-free
sudo dpkg -i ~/nouveau/linux-image*.deb ~/nouveau/linux-firmware-image*.deb
sudo update-grub

Install a copy of dri2proto
cd ~/nouveau
git clone git://anongit.freedesktop.org/xorg/proto/dri2proto
cd dri2proto
./autogen.sh --prefix=/usr/local/stow/dri2proto-20100428
sudo mkdir -p /usr/local/stow/dri2proto-20100428
sudo make install
sudo stow -d /usr/local/stow dri2proto-20100428

Install a cutting-edge version of libdrm
cd ~/nouveau
git clone git://anongit.freedesktop.org/git/mesa/drm/
cd drm
./autogen.sh --prefix=/usr/local/stow/drm-20100428 --disable-intel --disable-radeon --enable-nouveau-experimental-api
make
sudo mkdir -p /usr/local/stow/drm-20100428
sudo make install
sudo stow  -d /usr/local/stow  drm-20100428

Likewise for mesa
cd ~/nouveau
git clone git://anongit.freedesktop.org/git/mesa/mesa
cd mesa
./autogen.sh --prefix=/usr/local/stow/mesa-20100428  --enable-debug --enable-glx-tls --disable-asm --with-dri-drivers= --enable-gallium-nouveau --disable-gallium-intel --disable-gallium-radeon --disable-gallium-svga --with-state-trackers=glx,dri --with-demos=xdemos,demos,trivial,tests
make
sudo mkdir -p /usr/local/stow/mesa-20100428 
sudo make install
sudo stow -d /usr/local/stow mesa-20100428

And now the xorg driver...
cd ~/nouveau
git clone git://anongit.freedesktop.org/git/nouveau/xf86-video-nouveau/
cd xf86-video-nouveau
./autogen.sh --prefix=/usr/local/stow/xf86-video-nouveau-20100428
make
sudo mkdir -p /usr/local/stow/xf86-video-nouveau-20100428
sudo make install
sudo stow -d /usr/local/stow xf86-video-nouveau-20100428

Configuration Configure xorg to look in alternate location for xorg modules and set up DRI
sudo sh -c "cat > /etc/X11/xorg.conf" << EOF
Section "Files"
    ModulePath "/usr/local/lib/xorg/modules,/usr/lib/xorg/modules"
EndSection
Section "ServerFlags"
    Option "GlxVisuals" "all"
Endsection
Section "Device"
    Identifier     "nVidia Corporation G72M [Quadro NVS 110M/GeForce Go 7300]"
    Driver         "nouveau"
EndSection
EOF

I've /heard/ that disabling TV out is a necessity on some cards, though I haven't seen this myself:
sudo sh -c "cat > /etc/modprobe.d/nouveau.conf" << EOF
# not entirely sure this is necessary, but heard it helped with vsync
options nouveau tv_disable=1
EOF

Finally, the one thing that can not be done in /usr/local is making the nouveau DRI driver available. From what I could tell the path that mesa uses to find the DRI libraries is hard-coded (corrections welcome). Since you won't already have this file (otherwise, why would you be following along here?), just drop in a symlink to the file in /usr/local:
sudo ln -s /usr/local/lib/dri/nouveau_dri.so /usr/lib/dri/

Finally, reboot, and hope for the best :) Riding the bleeding edge: how to upgrade later on Again, stow really shows its usefullness here. Using drm as an example case, upgrading an individual component would look something like:
cd ~/nouveau/drm
git clean -dfx
git pull
today= date +%Y%m%d 
./autogen.sh --prefix=/usr/local/stow/drm-$today --disable-intel --disable-radeon --enable-nouveau-experimental-api
make
sudo mkdir -p /usr/local/stow/drm-$today
sudo make install
sudo stow -d /usr/local/stow -D drm-20100428
sudo stow -d /usr/local/stow  drm-$today

Note how the old version is still installed, so you can switch components around pretty freely. Abort! Abort!: How to roll back changes In case your system becomes totally unusable, or you've decided that you just want to go back to the safe and cozy world of what's provided by the debian packages, simply do the following: Assuming that you're using the nouveau driver from unstable, this should be all that is necessary. Conclusion Overall impression I am very, very happy with the resulting setup. I was led to believe that this whole thing was much more unstable and unusable than it actually is! While there are certainly some glitches and missing features, I feel comfortable enough using it that I don't have plans to switch back. But if I find myself in a situation where I can't use the new setup, rolling back shouldn't be a problem either. I figure I'm happy with what I have now and it will only get better. What works, at least to a "kinda works" level. What still doesn't work Further reading, references Thanks A couple shoutouts to those who helped me with this on the way: Feedback / Corrections Unforunately, I've had to disable comments for the time being due to overwhelming quantities of spam. So please drop me a line via email or on IRC (seanius on oftc/freenode).

27 April 2010

Sylvain Le Gall: 32 year old

... or as some fellow DD said, one year ago: "j'ai 1000 ans". So what happened during last year, the DVCS way:

$> cd "Sylvain Le Gall"
$> darcs whatsnew
hunk life.txt 0
+ Yvain, my son, talks and walks, this is quite amazing to see your
+ child growing up.  My wife is pregnant, release expected in July
+ ;-)
+ 
+ I traveled quite a lot this year: Spain, Tunisia, Belgium,
+ Roscoff and Huelgoat (Brittany) 
hunk debian.txt 0
+ I went to Debconf 9 and attended Debcamp before. I met a lot of
+ very interesting people there. I spent the Debcamp time to
+ implement Zack proposal to compute OCaml package dependencies
+ using dh-ocaml. It WORKS ;-) It was a pleasure to work with Mehdi
+ Dogguy and Stephane Glondu on this subject.
+ 
+ The dh-ocaml work allowed me to be the co-author, with Stephane
+ and Mehdi, of Zack's article on the subject. 
+ My first publication!
+ 
+ I went to FOSDEM 2010 and helped attend the Debian booth. Quite a
+ nice experience I was there with my good old Open Brick NG (need
+ to blog about it one day).
+ 
+ Found some time to enable the LLVM OCaml bindings in LLVM Debian
+ package.
+ 
+ Voted for the first  OCaml-aware DPL! (NB: this was not the
+ reason for my vote)
hunk work.txt 0
+ I worked on extending a tool that I delivered before. OCaml is
+ quite a good language when it comes to do maintenance. You can
+ extend something and have dozens of compiler errors where your
+ changes propagate. Once every error has been corrected, your
+ changes are OK. Of course, this requires to use OCaml types,
+ pattern matching and a bit of unit testing.
+ 
+ I was delighted when Jun Furuse ask me if he can organize 
+ OCaml Meeting 2010 in Japan. The first OCaml Meeting spin-off. 
+ 
+ OASIS has been growing quite a lot since the year before and got
+ enough importance. Thus I decided to give a talk about it at CAML
+ Consortium in December and then at OCaml Meeting 2010. 
+ 
+ I decided to have some English training. I was missing some oral
+ fluency.
+ 
+ I organized the OCaml Meeting 2010 in April. It was quite a lot
+ of work, especially to prepare my own presentation, but the
+ meeting was a success and probably my best birthday gift with the
+ OCaml Hacking Day organized just after.
$> darcs record -a
What is the patch name? "32 year old"
Unfortunately, this release is late. My birthday was on April 16th, but it was OCaml Meeting this day, which was my top level priority at this time. See you next year!

Ingo Juergensmann: Johan Schl ter: "Child pornography is great"

For many activists in net-politics it is apparent that the fight against child pornography is just an excuse for establishing a EU-wide content filtering infrastructure. This infrastructure for content filtering can be used to filter other content than child pornography as well. For example politicians in Germany already requested blocking gambling sites, Nazi sites, left extremistic political sites and others, when we had that kind of discussion last year over here. The proposal of a law putting up stop pages in front of child pronography sites by former minister for family Ursula "Zensursula" von der Leyen passed the parliament, but shortly after last years parliament elecetion all political parties didn't want that law anymore.
EU commissioner Cecilia "Censilia" Malmstr m introduced a similar proposal for a EU-wide blocking iinitiative a short while ago, as you might now. Christian Engstr m, member of the EU parliament of the swedish Pirate Party, wrote today on his blog that content right industry welcomes child pornography as a way to introduce content filter and blocking infrastructure:

Child pornography is great, the speaker at the podium declared enthusiastically. It is great because politicians understand child pornography. By playing that card, we can get them to act, and start blocking sites. And once they have done that, we can get them to start blocking file sharing sites .

The venue was a seminar organized by the American Chamber of Commerce in Stockholm on May 27, 2007, under the title Sweden A Safe Haven for Pirates? . The speaker was Johan Schl ter from the Danish Anti-Piracy Group, a lobby organization for the music and film industry associations, like IFPI and others.

[...]

Start with child porn, which everybody agrees is revolting, and find some politicians who want to appear like they are doing something. Never mind that the blocking as such is ridiculously easy to circumvent in less than 10 seconds. The purpose at this stage is only to get the politicians and the general public to accept the principle that censorship in the form of filters is okay. Once that principle has been established, it is easy to extend it to other areas, such as illegal file sharing. And once censorship of the Internet has been accepted in principle, they can start looking at ways to make it more technically difficult to circumvent.


If you already have not, then please act now and contact your local EU representive and kindly ask to refuse this directive of Malmstr m and enlighten them by supplying arguments such those MOGIS (MissbrauchsOpfer Gegen InternetSperren, abuse survivors against internet blocking) put up on their webpage (English and other languages).

The abuse of childs and the documentation of such abuse (child pornography is a bad term anyway) needs to be stopped! But access blocking is the wrong direction. Better take care of a more effective criminal prosecution. Documentation of child abuse needs to get removed from the web and the producers needs to get arrested.

So, please act now!

P.S.: there's a nice video on http://cleanternet.org/

25 April 2010

Jan Wagner: 3DSupply with new Website?

Jesus shirtYesterday, my co-worker notified my about a promotion of 3DSupply and I recognized, that they have new design and you have also the choise to select from various models and colors for your shirts. I like the new site much more than the old.
For just speading they word, they offer to give a shirt (or any other item < 20 Eur) for free. So it seems to be a good idea to equip my dear wife, which is a teacher of catholic religion, with a new Jesus shirt.
Update: Today I got a reply from 3DSupply, stating that they deny the shirt request, cause I don t have 10 posts in the last 6 month. As this is unfortunately true, due my always limited time, I can t find this hard requirement in their terms. Looks like my blog doesn t match their minimal requirements and I m advised to equip my girls somewhere else with geekware. :o)

Matt Zimmerman: Ten TED talks I took in today

Starting about a year ago, I started following the release of videos from TED events. If one looked interesting, I would download the video to watch later. In this way, I accumulated a substantial collection of talks which I never managed to watch. I spent a Saturday evening working my way through the list. These are my favorites out of this batch.

24 April 2010

Adam Rosi-Kessel: Green Lemonade Success

My most successful Green Lemonade to date:
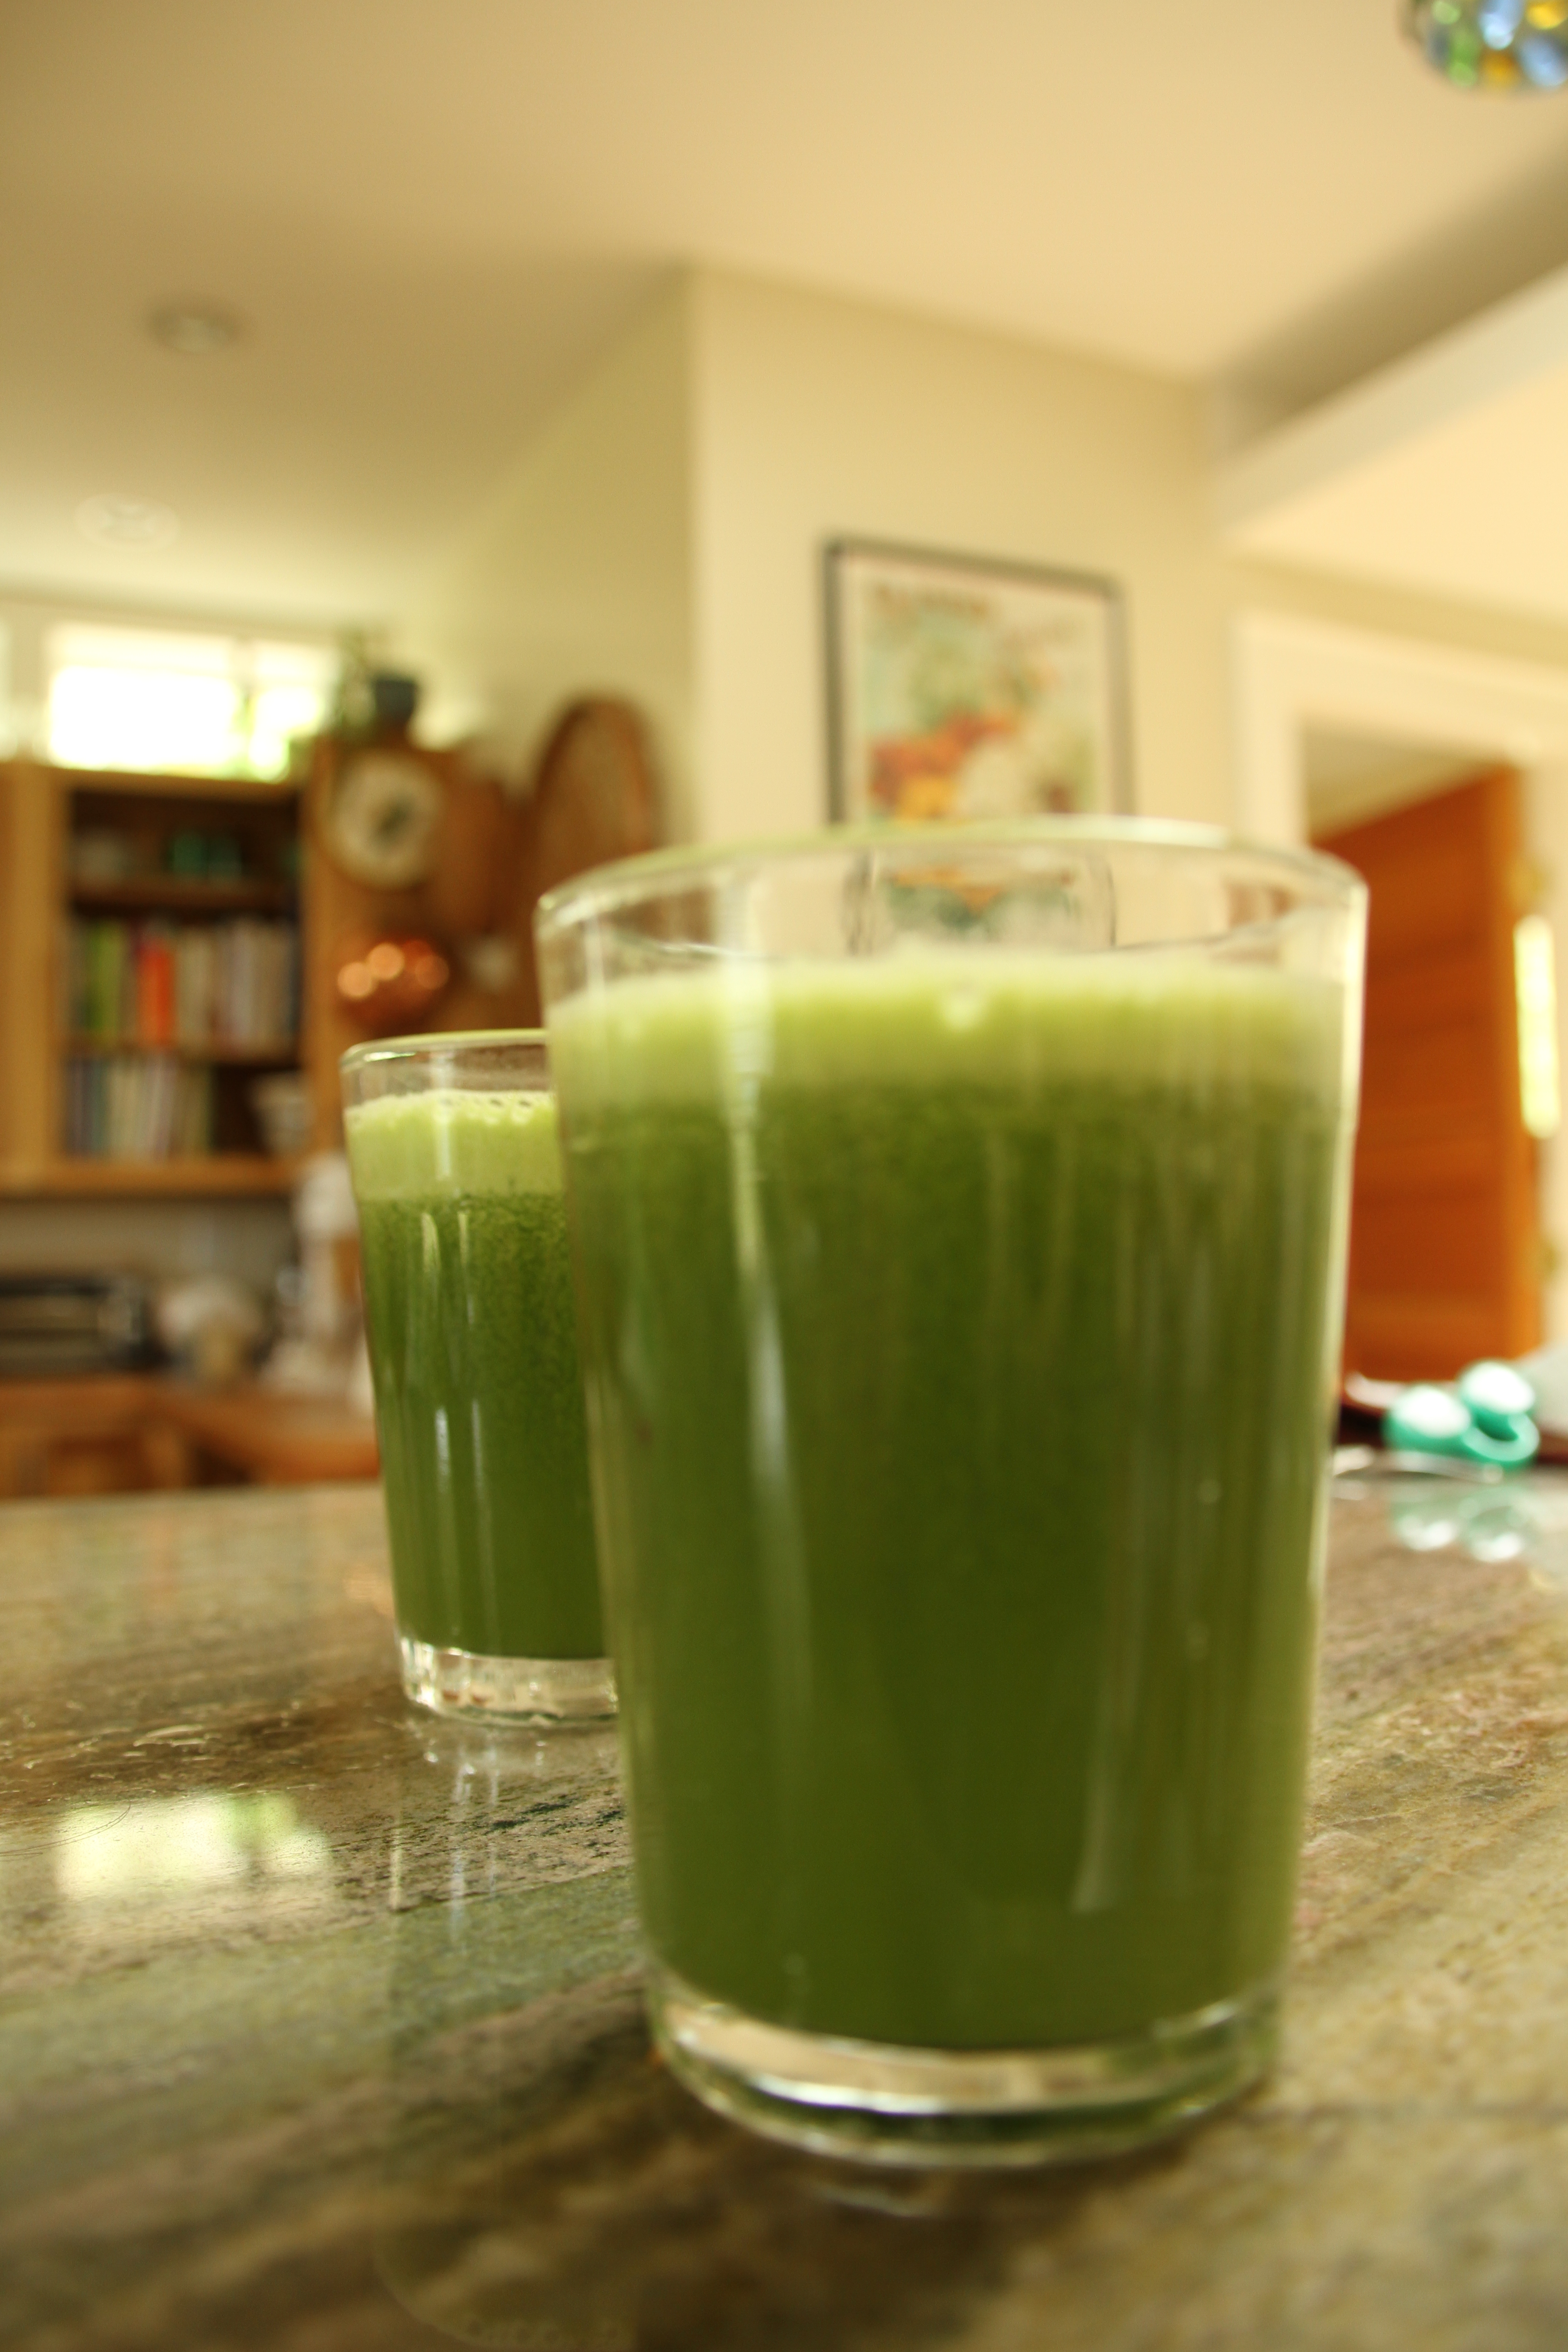
Green Lemonade

Green Lemonade

Approximate recipe: Juice and consume. I have heard from green-juice skeptics before. It may be hopeless for some poor souls. But don t knock it until you ve tried it.

23 April 2010

Jan Wagner: [selfnote] Find the DUN Channel of your bluetooth device

In the last days, I replaced my Nokia E90 with a Nokia N97 mini. As I m using my mobile from time to time to hook up to the internet when traveling, I thought I just need to replace the MAC in my /etc/bluetooth/rfcomm.conf and that s it. As always Murphy striked back. After debugging for hours I realized the DUN channel seems depending on the model. You can discover your DUN channel something like:

# hcitool scan
Scanning
3C:F7:2A:1A:4D:2A Cycophone
# sdptool browse 3C:F7:2A:1A:4D:2A \
grep -9 Service Name: Dial-Up Networking \
tail -10 grep Channel
Channel: 22 So your /etc/bluetooth/rfcomm.conf should now look like:


rfcomm0
bind yes;
device 3C:F7:2A:1A:4D:2A;
channel 22;
comment Cycophone ;

22 April 2010

Matt Zimmerman: On Cloud

If you re convinced that cloud is a useless buzzword, being used to describe everything under the sun, old and new, then well, you re right that is, except for the useless part. It s true that this word is being (ab)used in many different products, services and technologies, which do not seem to relate to each other in any concrete way. Cloud in the abstract is being defined in many different ways, based on different fundamental characteristics of cloud technology . Nonetheless, there is something genuinely important going on here, and this is my view of what it s about. The hype Countless business which only had web sites or web applications in 2008 now call them cloud services . They aren t delivering any new benefits to their users, and they haven t redesigned their infrastructure. What do they mean by this? Cloud is defined, some say, by where your data is kept, and cloud means storing your data on remote servers instead of internal ones. Millions of Gmail and Flickr users have been in the cloud without even knowing it, and so has everyone who reads their mail over IMAP, or uses voicemail. In short, cloud is just data that is somewhere else.

Credit: jurvetson

Last September, I watched a presentation on Cloud computing where Symantec pitched their anti-virus product as having something like three different cloud computing technologies. These, it turned out, all involved downloading files over the Internet. In this view, cloud is essentially about the network, derived from our habit of using a drawing of a cloud in our network diagrams for so many years. Wikipedia currently shares this view, as its Cloud computing article opens with Cloud computing is Internet-based computing . No Internet, no cloud. Maybe cloud is just SaaS, and any service provided on a pay-per-use basis over the Internet is a cloud service. It would seem that cloud is about paying for things, especially on a utility basis. The cloud is computing by the hour; it s something you buy. Others maintain that cloud is just virtualization, so if you re using KVM or VMWare, you ve got a cloud already. In this view, cloud is about operating systems, and whether they re running on real or virtual hardware. Cloud means deploying applications as virtual appliances, and creating new servers entirely in software. If your servers only have one OS on them, then they re not cloud-ready. If this vagueness and contradiction irritates you, then you re not alone. It bugs me, and a lot of other people who are getting on with developing, using and providing technology and services. Cloud is not just a new name for these familiar technologies. In fact, it isn t a technology at all. I don t think it even makes sense to categorize technologies as cloud and non-cloud , though some may be more cloudy than others. Nonetheless, there is some meaning and validity in each of these interpretations of cloud. So what is it? A different perspective

Credit: TangYauHoong

Cloud is a transition, a trend, a paradigm shift. It isn t something which exists or not: it is happening, and we won t understand its essential nature until it s over. Simon Wardley explains this, in presentation format, much better than I could in this blog post, so if you haven t already, I suggest that you take 14 minutes of your time and go and watch him do his thing. This change doesn t have a clear beginning or an end. Early on, it was a disconnected set of ideas without any identity. We re now somewhere in the middle of the bell curve, with enough insight to give it a name, and sufficient momentum to guess at what happens next. In the end, it will be absorbed into the way things are . What s going on? So, what is actually changing? The key trends I see are:
  1. People and organizations are becoming more comfortable relying on resources which do not exist in any particular place. Rather than storing precious metals under our beds, we entrust our finances to banks, which store our data and provide us with services which let us use our money . In computing terms, we re no longer enamored with keeping all of our programs and our data on our hard drive: as it turns out, it s not very safe there after all, and in some ways we can actually exercise more control over programs and data out there than in here . We can no longer hoard our gold, or drive off would-be thieves with a pistol, but that wasn t a productive way to spend our energies anyway. While we can t put our hands on our money, we can know exactly what s happening with it from minute to minute, and use it in a variety of ways at a moment s notice.
  2. IT products are ceding ground to services. In many cases, we no longer need to build software, or even buy it: we can simply use it. As computing needs become better understood, and can be met by commodity products, it becomes more feasible to develop services to meet them on-demand. This is why we see a spike in acronyms ending in aaS . Simon explains the progression in detail in his talk, linked above.
  3. Hardware, software and data are being reorganized according to new models, in order to provide these services effectively. Architectural patterns, such as hardware/OS/framework/application are giving way to new ones, like hardware/OS/IaaS/OS/PaaS/SaaS/Internet/web browser/OS/hardware . These are still evolving, and the lines between them are blurry. It s a bit early to say what the dominant patterns will be, but system, network, data and application architecture are all being transformed. No single technology or architecture defines cloud, but virtualization (at the infrastructure level) and the web (at the application level) both seem to resonate strongly with cloudy design patterns.
These trends are reinforcing and accelerating each other, driving information technologies and businesses in a common direction. That, in a nutshell, is what cloud is all about. So what? This transformation is disruptive in many different ways, but the angles which most interest me at the moment are: I d like to explore some of these topics in future posts.

Gunnar Wolf: A FLISOL critic

Once again, I was invited by several different groups to be present at FLISOL, a quite interesting phenomenon: FLISOL (Latin-american Free Software Installation Festival) is s very large-scale, very loosely coordinated thing put together for five years already in over 200 cities in basically every Latin American country. Go to the FLISOL page, it is quite interesting to try to understand it! Now, I don't like FLISOL. I managed to avoid it in 2005 and 2006; in 2007, I was present at a FLISOL, although I didn't know beforehand it was the reason for the conference I was invited to. In 2008 and 2009 I took part for reasons I should not go into right now. This year, again, I will not be part of any of its activities (regardless of rumors to the contrary I was invited to be present at a panel on ACTA, but I have not followed the topic enough to be aware of anything besides the very basic aspects, I have no authority to speak about it; I told the organizers I would like to be there as part of the audience, but not present the topic. And I am quite work-stressed, so I doubt I'll make it). Why am I against FLISOL? FLISOL itself, as I said, is a positive and interesting phenomenon, and I have enjoyed the conference cycles which often happen together with it. What I am against is installfests In my opinion, in the stage we are at today, instead of promoting Free Software, an install-fest just works against it. Free Software Linux-based distributions at least is widely known already, as a concept, even though most people dare not come anywhere close to it. Few people outside our already consolidated groups recognize programs such as the Mozilla and OpenOffice suites as being also Free Software, and valuable, quality alternatives for their everyday needs in the environments they currently use. If we need to show how to install and understand the GNU/Linux ecosystem to people who have not got close, it is not IMHO to end users. Installing a GNU/Linux system is easy enough for anybody interested in doing it, or at least, for him to request a one-on-one help session, handholding and understanding the basic ideas. We need, in any case, for the computer corner shop technicians to be somewhat acquinted, at least with the basics, at least with one popular distribution (and with the fact that there are many, and that they are different). People who have not had the curiosity and courage to try to install Linux by themselves do not need to be evangelized (a verb that should be out of our vocabularies by now, as that phase in our movement should be over by now) End users have simple needs: Things should work, and be as surprise-free as possible. They don't want to depend on a specific time-starved person (or even on a small group of people, all of which have a sanctity delirium/aura). When they go to technical support, they expect the problem to be solved Not even understanding what was wrong. End users are willing to pay a small fee to anybody to help them solve their problems. The key word is anybody. If we (myself, or me and my 10 friends who were there at the gathering, or any sufficiently defined small group) are the only support point for the OS, it is no good. Online support forums are not good either, in my experience, as the end user will prefer just lugging the computer to the nearest technician and get it fixed. Even if fixed means just installing one more readily-available package (not to mention, of course, when an update breaks something). I have witnessed, after an install fest, people walk very happy with their new system as a new toy. After a week or two, they cannot install the latest virus^Wscreen saver, or a legitimate program they need for their work. As it does not work, they take the computer to the technician... Who will end up formatting his system and installing something more usual. On the other hand, some people prefer installing a dual-boot system That guarantees the user will feel he is carrying some kind of moral superiority on his computer, and will often remember he has something Not Evil. This will often happen, of course, at boot time When they see GRUB at boot time, and rush to select Windows before That Strange Thing starts up. Anyway... Go ahead, install Free Software, enjoy the day. The conference cycles are usually interesting, and are the best part of it all I'm not saying you should stop doing it. But I'd urge you to take the focus away from the mass-installs, which become often just lost work (even detrimental to furthering Free Software). Try to see things as a non-technically-interested user would. Try to design ways to get corner shop technicians interested. Maybe that can be useful in the long run.

21 April 2010

Julien Blache: rEFIt on x64: finally fixed

When I got my Mac Mini, one of the very first things I did was to test the Debian build of rEFIt on the machine, given the EFI firmware is x64 on the newer machines whereas it s ia32 on my MacBookPro; it was the very first time I could test the x64 build. And the results weren t good: some images couldn t be loaded, and it all seemed to be random. Disabling optimization in both GNU EFI and rEFIt for the x64 builds helped somewhat, at least it made rEFIt reliable enough to be usable. Now, with this new release, I started getting error messages, requiring a key press before the menu would be displayed. It s annoying but it s also very helpful as I now had an error message to work with, and even if the error message wasn t reliable, it would still point me to some part of the code. The message was: Invalid argument. On x64, the use of a call wrapper is mandatory because the EFI x64 calling convention doesn t match the calling convention of the ELF executables we re building and later disguising as EFI executables. The call wrapper has always been the prime suspect in this issue, it d be an obvious candidate for anyone looking at this issue. Today, digging into the issue with some new data, I realized what the problem was: when using the call wrapper, all arguments need to be of the UINT64 type. That s the type the call wrapper uses when extracting the arguments from its va_list. Introduce some more macros on top of the call wrapper, build, test: voila, it s fixed! That was tricky one. Let s sum it up for the search engines: all the arguments to the EFI interface called through uefi_call_wrapper() in GNU EFI need to be cast to UINT64. rEFIt 0.14-1, available in unstable in a couple hours. Next, I ll see if I can reenable optimization in both GNU EFI and rEFIt.

20 April 2010

Biella Coleman: On Internet Punditry and Engendering Change

One day a very well known Internet theorist writes a rant on women. The rant generates controversy, controversy lands theorist on WYNC on the media , despite the fact the he does not really work on the politics of gender. If this is so, why then give him more air time and focus on the NPR show? There are three lessons that precipitate from this social fact that are worth highlighting: 1.The fact that NPR chose him to pontificate and not a woman nullifies Shirky s thesis that behavior is one of the most important factors in keeping women behind, unless of course NPR asked a bunch of women but they were too meek to be on the air (not likely). If they wanted to keep the star power that is Shirky, the very least they could have done is had a woman respond. The solutions to get more women in the limelight are so easy to implement but they do require some thoughtfulness and foresight. 2.So what I am saying, it is about networks and Shirky, isn t he a theorist of networks and behavior? It seems to be to more controversial, he really did not address how important networks are for the politics of visibility, instead he focused on individual behavior. If famous highly networked folks, most of them men, don t highlight women in their blog posts, their twitter feeds, and don t invite them to conferences, it is going to make very little difffernce whether a woman is meek or confident. So if there are more guys that are visible, which is certainly the case, it is as much their job to help engender change, not so much by pontificating but acting. 3. I realized that though I first thought his rant was a reflection of his personality (at least his public persona, I am sure he is a nice guy), in fact the rant is valuable to an anthropologist interested in digital media because it is an auto-ethnographic snapshot of web 2.0 punditry culture. It often comes across as smarmy and snarky, which is due in part, to how difficult it is to get your message heard in the sea of many voices. Just like there is an aesthetic of audaciousness in a lot of Internet memeology, for example, the pundits too must often act in extreme ways to get attention which might inf fact be one of the reasons why they are reluctant to share the stage once they have worked hard to get there.

Next.

Previous.
