I'm buying rather too many books at the moment and not reading enough of
them (in part because I got back into Minecraft and in part because I got
a bit stuck on a few difficult books). I think I've managed to get myself
unstuck again, though, and have started catching up on reviews.
2020. It's kind of a lot. And I'm not even that heavily affected.
Katherine Addison The Angel of the Crows (sff)
Marie Brennan A Natural History of Dragons (sff)
Kacen Callender Queen of the Conquered (sff)
Jo Clayton Diadem from the Stars (sff)
Jo Clayton Lamarchos (sff)
Jo Clayton Irsud (sff)
Clifford D. Conner The Tragedy of American Science (nonfiction)
Kate Elliott Unconquerable Sun (sff)
Rory Fanning & Craig Hodges Long Shot (nonfiction)
Michael Harrington Socialism: Past & Future (nonfiction)
Nalo Hopkinson Brown Girl in the Ring (sff)
Kameron Hurley The Stars Are Legion (sff)
N.K. Jemisin Emergency Skin (sff)
T. Kingfisher A Wizard's Guide to Defensive Baking (sff)
T. Kingfisher Nine Goblins (sff)
Michael Lewis The Fifth Risk (nonfiction)
Paul McAuley War of the Maps (sff)
Gretchen McCulloch Because Internet (nonfiction)
Hayao Miyazaki Nausica of the Valley of the Wind (graphic novel)
Annalee Newitz The Future of Another Timeline (sff)
Nick Pettigrew Anti-Social (nonfiction)
Rivers Solomon, et al. The Deep (sff)
Jo Walton Or What You Will (sff)
Erik Olin Wright Stardust to Stardust (nonfiction)
Of these, I've already read and reviewed
The Fifth Risk (an
excellent book).
Teaching consent is ongoing, but it starts when children are very young. It involves both teaching children to pay attention to and respect others' consent (or lack thereof) and teaching children that they should expect their own bodies and their own space to be respected---even by their parents and other relatives. And if children of two or four can be expected to read the nonverbal cues and expressions of children not yet old enough to talk in order to assess whether there is consent, what excuse do full grown adults have?
Personal boundaries are guidelines, rules or limits that a person creates to identify reasonable, safe and permissible ways for other people to behave towards them and how they will respond when someone passes those limits.[1] They are built out of a mix of conclusions, beliefs, opinions, attitudes, past experiences and social learning.[2][3] This concept or life skill has been widely referenced in self-help books and used in the counseling profession since the mid-1980s.[4]
Final call to participate in the LTS survey
After 6 years of existence, we, the Debian LTS contributors, wanted to run a survey
to learn more about how Debian LTS is used and perceived. Please
take
a few minutes to participate in the survey at https://surveys.debian.net/...!
Also, please hurry up, the survey will close at the end of July 27th on
Samoa,
which is in roughly 48h from now.
Stephen was a paladin. Then his god died.
He was a berserker, an unstoppable warrior in the service of his god.
Now, well, he's still a berserker, but going berserk when you don't have a
god to control the results is not a good idea. He and his brothers were
taken in by the Temple of the Rat, where they serve as guards, watch out
for each other, and try to get through each day with an emptiness in their
souls where a god should be.
Stephen had just finished escorting a healer through some of the poorer
parts of town when a woman runs up to him and asks him to hide her. Their
awkward simulated tryst is sufficient to fool the two Motherhood priests
who were after her for picking flowers from the graveyard. Stephen then
walks her home and that would have been the end of it, except that neither
could get the other out of their mind.
Despite first appearances, and despite being set in the same world and
sharing a supporting character, this is not the promised sequel to
Swordheart (which is apparently still
coming). It's an entirely different paladin story. T. Kingfisher (Ursula
Vernon's nom de plume when writing for adults) has a lot of
things to say about paladins! And, apparently, paladin-involved romances.
On the romance front, Kingfisher clearly has a type. The general shape of
the story will be familiar from Swordheart and
The Wonder Engine: An independent and
occasionally self-confident woman with various quirks, a hunky paladin who
is often maddeningly dense, and a lot of worrying on both sides about
whether the other person is truly interested in them and if their personal
liabilities make a relationship a horrible idea. This is not my preferred
romance formula (it provokes the occasional muttered "for the love of god
just talk to each other"), but I liked this iteration of it better than
the previous two, mostly because of Grace.
Grace is a perfumer, a trade she went into by being picked out of a lineup
of orphans by a master perfumer for her sense of smell. One of
Kingfisher's strengths as a writer is showing someone get lost in their
routine day-to-day competence. When mixed with an inherently fascinating
profession, this creates a great reading experience. Grace is also an
abuse survivor, which made the communication difficulties with Stephen
more interesting and subtle. Grace has created space and a life for
herself, and her unwillingness to take risks on changes is a deep part of
her sense of self and personal safety. As her past is slowly revealed,
Kingfisher puts the reader in a position to share Stephen's anger and
protectiveness, but then consistently puts Grace's own choices, coping
mechanisms, and irritated refusal to be protected back into the center of
the story. She has to accept some help as she gets entangled in the
investigation of a highly political staged assassination attempt, but both
that help and the relationship come on her own terms. It's very
well-done.
The plot was enjoyable enough, although it involved a bit too much of
constantly rising stakes and turns for the worst for my taste, and the
ending had a touch of deus ex machina. Like Kingfisher's other
books, though, the delight is in the unexpected details. Stephen knitting
socks. Grace's frustrated obsession with why he smells like gingerbread.
The beautifully practical and respectful relationship between the Temple
of the Rat and Stephen's band of former paladins. (After only two books
in which they play a major role, the Temple of the Rat is already one of
my favorite fantasy religions.) Everything about Bishop Beartongue.
Grace's friend Marguerite. And a truly satisfying ending.
The best part of this book, though, is the way Grace is shown as a
complete character in a way that even most books with well-rounded
characterization don't manage. Some things she does make the reader's
heart ache because of the hints they provide about her past, but they're
also wise and effective safety mechanisms for her. Kingfisher gives her
space to be competent and prickly and absent-minded. She has a complete
life: friends, work, goals, habits, and little rituals. Grace meets
someone and falls in love, but one can readily imagine her not falling in
love and going on with her life and that result wouldn't be tragic. In
short, she feels like a grown adult who has made her own peace with where
she came from and what she is doing. The book provides her an opportunity
for more happiness and more closure without undermining her independence.
I rarely see this in a novel, and even more rarely done this well.
If you haven't read any of Kingfisher's books and are in the mood for
faux-medieval city romance involving a perfumer and a bit of political
skulduggery, this is a great place to start. If you liked
Swordheart, you'll probably like Paladin's Grace; like me,
you may even like it a bit more. Recommended, particularly if you want
something light and heart-warming.
Rating: 8 out of 10
I have been using the community editions of IntelliJ and PyCharm for a while now for Python or Perl projects. But it started to annoy me that for Debian packaging bits it would revert into a fancy version of notepad. Being fed up with it, I set down and spent the last week studying how to write a plugin to fix this.
After a few prototypes, I have now released IDEA-debpkg v0.0.3 (Link to JetBrain s official plugin listing with screenshots). It provides a set of basic features for debian/control like syntax highlighting, various degree of content validation, folding of long fields, code completion and CTRL + hover documentation. For debian/changelog, it is mostly just syntax highlighting with a bit of fancy linking for now. I have not done anything for debian/rules as I noted there is a Makefile plugin, which will have to do for now.
The code is available from github and licensed under Apache-2.0. Contributors, issues/feature requests and pull requests are very welcome. Among things I could help with are:
Icons both for the plugin and for the file types. Currently it is just colored text, which is as far as my artistic skills got with the space provided.
Color and text formatting for syntax highlighting.
Reports of papercut or features that would be very useful to prioritize.
Review of the CTRL + hover documentation. I am hoping for something that is help for new contributors but I am very unlikely to have gotten it right (among other because I wrote most of it to get it done rather than getting it right )
I hope you will take it for spin if you have been looking for a bit of Debian packaging support to your PyCharm or other IDEA IDE. Please do file bugs/issues if you run into issues, rough edges or unhelpful documentation, etc.
Following on from the blog post the other day in some sense: someone has asked on the debian-user list: "I do not understand from the given page (https://www.debian.org/CD/verify) how to use .sign files and gpg in order to check verify the authenticity of debian cds. I understand the part with using sha256sum or sha512sum or md5sum to check whether the files were downloaded correctly."
Distributed with the CD and other media images on Debian CD mirrors, there are files like MD5SUM, MD5SUM.sign, SHA256SUM, SHA256SUM.sign and so on.
SHA512SUM is a plain text list of the SHA512SUMs for each of the files in the directory. SHA512SUM.sign is the GPG-signed version of that file. This allws for non-repudiation - if the signature is valid, then the plain text file has been signed by the owner of that key. Nothing has tampered with the checksums file since it was signed.
After downloading the SHA1SUM, SHA256SUM and SHA512SUM files and the corresponding .sign files from, say, the prime Debian CD mirror at
gpg --verify SHA512SUMS.sign SHA512SUMS gpg: Signature made Sun 10 May 2020 00:16:52 UTC gpg: using RSA key DF9B9C49EAA9298432589D76DA87E80D6294BE9B gpg: Good signature from "Debian CD signing key " [unknown] gpg: WARNING: This key is not certified with a trusted signature! gpg: There is no indication that the signature belongs to the owner. Primary key fingerprint: DF9B 9C49 EAA9 2984 3258 9D76 DA87 E80D 6294 BE9B
My own key isn't in the Debian CD signing key ring - but this does now show me that this is a good signature from the primary key fingerprint as given.
Repeating the exercise from the other day and producing a Debian amd64 netinst file using jigdo, I can now check the checksum on the local .iso file against the checksum file distributed by Debian. If they match, it's a good sign that the CD I've generated is bit for bit identical. For my locally generated file:
When did I start writing Free Software, now called Open Source? That s a tricky question. Does the time start with the first file edited, the first time it compiles or perhaps even some proto-program you use to work out a concept for the real program formed later on.
So using the date you start writing, especially in a era before decent version control systems, is problematic. That is why I use the date of the first release of the first package as the start date. For me, that was Monday 24th July 1995.
axdigi and before
My first released Free Software program was axdigi which was a layer-2 packet repeater for hamradio. This was uploaded to some FTP server, probably UCSD in late July 1995. The README is dated 24th July 1995.
There were programs before this. I had written a closed-source (probably undistributable) driver for the Gracilis PackeTwin serial card and also some sort of primitive wireshark/tcpdump thing for capturing packet radio. Funny thing is that the capture program is the predecessor of both axdigi and a system that was used by a major Australian ISP for their internet billing system.
Choosing Free Software
So you have written something you think others might like, what software license will you use to distribute it? In 1995 it wasn t that clear. This was the era of strange boutique licenses including ones where it was ok to run the program as a hamradio operator but not a CB radio operator (or at least they tried to work it that way).
A friend of mine and the author of the Linux HAM HOWTO amongst other documents, Terry Dawson, suggested I use GPL or another Free Software license. He explained what this Free Software thing was and said that if you want your program to be the most useful then something like GPL will do it. So I released axdigi under the GPL license and most of my programs since then have used the same license. Something like MIT or BSD licenses would have been fine too, I was just not going to use something closed or hand-crafted.
That was a while ago, I ve written or maintained many programs since then. I also became a Debian maintainer (23 years so far) and adopted both procps and psmisc which I still maintain as both the Debian developer and upstream to this day.
What Next?
So it has been 25 years or a quarter of a century, what will happen next? Probably more of the same, though I m not sure I will be maintaining Free Software by the end of the next 25 years (I ll be over 70 then). Perhaps the singularity will arrive and writing software will be something people only do at Rennie Festivals.
Come to the Festival! There is someone making horseshoes! Other there is a steam engine. See this other guy writing computer programs on a thing called keyboard!
A new minor release of the anytime package arrived on CRAN overnight. This is the nineteenth release, and it comes just over six months after the previous release giving further indicating that we appear to have reached a nice level of stability.
anytime is a very focused package aiming to do just one thing really well: to convert anything in integer, numeric, character, factor, ordered, format to either POSIXct or Date objects and to do so without requiring a format string. See the anytime page, or the GitHub README.md for a few examples.
This release mostly plays games with CRAN. Given the lack of specification for setups on their end, reproducing test failures remains, to put it mildly, somewhat challenging . So we eventually gave up and weaponed up once more and now explicitly test for the one distribution where tests failed (when they clearly passed everywhere else). With that we now have three new logical predicates for various Linux distribution flavours, and if that dreaded one is seen in one test file the test is skipped. And with that we now score twelve out of twelve OKs. This being a game of cat and mouse, I am sure someone somewhere will soon invent a new test
The full list of changes follows.
Changes in anytime version 0.3.8 (2020-07-23)
A small utility function was added to detect the Linux distribution used in order to fine-tune tests once more.
At DebConf 17 in Montreal, I gave a talk about Ayatana Indicators [1] and the project's goal to continue the by then already dropped out of maintenance Ubuntu Indicators in a separate upstream project, detached from Ubuntu and its Ubuntu'isms.
Stalling
The whole Ayatana Indicators project received a bit of a show stopper by the fact that the IDO (Indicator Display Object) rendering was not working in vanilla GTK-3 without a certain patch [2] that only Ubuntu has in their GTK-3 package. Addressing GTK developers upstream some years back (after GTK 3.22 had already gone into long term maintenance mode) and asking for a late patch acceptance did not work out (as already assumed). Ayatana Indicators stalled at a level of 90% actually working fine, but those nice and shiny special widgets, like the calendar widget, the audio volume slider widgets, switch widgets, etc. could not be rendered appropriately in GTK based desktop environments (e.g. via MATE Indicator Applet) on other distros than Ubuntu.
I never really had the guts to sit down without a defined ending and find a patch / solution to this nasty problem. Ayatana Indicators stalled as a whole. I kept it alive and defended its code base against various GLib and what-not deprecations and kept it in Debian, but the software was actually partially broken / dysfunctional.
Taking the Dog for a Walk and then It Became all Light+Love
Several days back, I received a mail from Robert Tari [3]. I was outside on a hike with our dog and thought, ah well, let's check emails... I couldn't believe what I read then, 15 seconds later. I could in fact, hardly breathe...
I have known Robert from earlier email exchanges. Robert maintains various "little" upstream projects, like e.g. Caja Rename, Odio, Unity Mail, etc. that I have looked into earlier regarding Debian packaging. Robert is also a Manjaro contributor and he has been working on bringing Ayatana Indicators to Manjaro MATE. In the early days, without knowing Robert, I even forked one of his projects (indicator-notification) and turned it into an Ayatana Indicator.
Robert and I also exchanged some emails about Ayatana Indicators already a couple of weeks ago. I got the sense of him maybe being up to something already then. Oh, yeah!!!
It turned out that Robert and I share the same "love" for the Ubuntu Indicators concept [4]. From his email, it became clear that Robert had spent the last 1-2 weeks drowned in the Ayatana IDO and libayatana-indicator code and worked him self through the bowels of it in order to understand the code concept of Indicators to its very depth.
When emerging back from his journey, he presented me (or rather: the world) a patch [5] against libayatana-indicator that makes it possible to render IDO objects even if a vanilla GTK-3 is installed on the system. This patch is a game changer for Indicator lovers.
When Robert sent me his mail pointing me to this patch, I think, over the past five years, I have never felt more excited (except from the exact moment of getting married to my wife two-to-three years ago) than during that moment when my brain tried to process his email. "Like a kid on Christmas Eve...", Robert wrote in one of his later mails to me. Indeed, like a "kid on Christmas Eve", Robert.
Try It Out
As a proof of all this to the Debian people, I have just done the first release of ayatana-indicator-datetime and uploaded it to Debian's NEW queue. Robert is doing the same for Manjaro. The Ayatana Indicator Sound will follow after my vacation.
For fancy widget rendering in Ayatana Indicator's system indicators, make sure you have libayatana-indicator 0.7.0 or newer installed on your system.
Credits
One of the biggest thanks ever I send herewith to Robert Tari! Robert is now co-maintainer of Ayatana Indicators. Welcome! Now, there is finally a team of active contributors. This is so delightful!!!
References
Like each month, here comes a report about the work of paid contributors to Debian LTS.
Individual reports
In June, 202.00 work hours have been dispatched among 12 paid contributors. Their reports are available:
Abhijith PA did 8h (out of 14h assigned), thus carrying over 6h to July.
Evolution of the situation
June was the last month of Jessie LTS which ended on 2020-06-20. If you still need to run
Jessie somewhere, please read the
post
about keeping Debian 8 Jessie alive for longer than 5 years.
So, as (Jessie) LTS is dead, long live the new LTS, Stretch LTS! Stretch has received its
last point release, so regular
LTS operations can now continue.
Accompanying this, for the first time, we have prepared a small
survey about our users
and contributors, who they are and why they are using LTS. Filling out the survey should take
less than 10 minutes. We would really appreciate if you could participate in the
survey online!
On July 27th 2020 we will close the survey, so please don t hesitate and participate now! After that, there will be a followup with the results.
The security tracker for Stretch LTS currently lists 29 packages with a known CVE and the dla-needed.txt file has 44 packages needing an update in Stretch LTS.
Thanks to our sponsors
New sponsors are in bold. We welcome CoreFiling this month!
Long story short, a fast solution for the issue with EGLSetBlobFuncANDROID is
to remove libraspberrypi-dev from your sysroot and do a full rebuild. There
will be some changes to the configure results, so please review them - if
they are relevant for you - before proceeding with your work.
That got me unstuck! dpkg --purge libraspberrypi-dev in the sysroot, and
we're back in the game.
While Qt5's build has proven extremely fragile, I was surprised that some
customization from Raspberry Pi hadn't yet broken something.
In the end, they didn't disappoint.
More i386 issues
The run now stops with a new 32bit issue related to v8 snapshots:
qt-everywhere-src-5.15.0/qtwebengine/src/core/release$/usr/bin/g++-pie-Wl,--fatal-warnings-Wl,--build-id=sha1-fPIC-Wl,-z,noexecstack-Wl,-z,relro-Wl,-z,now-Wl,-z,defs-Wl,--as-needed-m32-pie-Wl,--disable-new-dtags-Wl,-O2-Wl,--gc-sections-o"v8_snapshot/mksnapshot"-Wl,--start-group@"v8_snapshot/mksnapshot.rsp"-Wl,--end-group-ldl-lpthread-lrt-lz/usr/bin/ld:skippingincompatible//usr/lib/x86_64-linux-gnu/libz.so when searching for -lz/usr/bin/ld:skippingincompatible//usr/lib/x86_64-linux-gnu/libz.a when searching for -lz/usr/bin/ld:cannotfind-lzcollect2:error:ldreturned1exitstatus
Attempted solution: apt install zlib1g-dev:i386.
Alternative solution (untried): configure Qt5 with -no-webengine-v8-snapshot.
It builds!
Installation paths
Now it tries to install files into debian/tmp/home/build/sysroot/opt/qt5custom-armhf/.
I realise that I now need to package the sysroot itself, both as a build-dependency
of the Qt5 cross-compiler, and as a runtime dependency of the built cross-builder.
Conclusion
The current work in progress, patches, and all, is at
https://github.com/Truelite/qt5custom/tree/master/debian-cross-qtwebengine
It blows my mind how ridiculously broken is the Qt5 cross-compiler build, for a
use case that, looking at how many people are trying, seems to be one of the
main ones for the cross-builder.
We encourage our community to celebrate around the world the 27th Debian
anniversary with organized DebianDay events. This year due to the COVID-19
pandemic we cannot organize in-person events, so we ask instead that contributors,
developers, teams, groups, maintainers, and users promote The Debian Project and Debian
activities online on August 16th (and/or 15th).
Communities can organize a full schedule of online activities throughout the day.
These activities can include talks, workshops, active participation with
contributions such as translations assistance or editing, debates, BoFs, and
all of this in your local language using tools such as Jitsi for capturing
audio and video from presenters for later streaming to YouTube.
If you are not aware of any local community organizing a full event or you don't
want to join one, you can solo design your own activity using OBS and
stream it to YouTube. You can watch an OBS tutorial here.
Don't forget to record your activity as it will be a nice idea to upload it
to Peertube later.
Please add your event/activity on the DebianDay wiki page and let us know about
and advertise it on Debian micronews. To share it, you have several options:
Follow the steps listed here for Debian Developers.
Contact us using IRC in channel #debian-publicity on the OFTC network, and ask us there.
Send a mail to debian-publicity@lists.debian.org
and ask for your item to be included in micronews. This is a publicly archived list.
Answer: it sends the password typed into sudo to the other endpoint of netcat.
I can reproduce this with both nc.traditional and nc.openbsd.
One might be tempted to just put sudo in front of everything, but it'll mean
that only nc will run as root:
# This is probably not what you want
sudo nc localhost 12345   tar xf -
The fix that I will never remember, thanks to twb on IRC, is to close nc's
stdin:
<&- nc localhost 12345 sudo tar xf -
Or flip the table and just use sudo -s:
$ sudo -s
# nc localhost 12345   tar xf -
Updates
Harald Koenig suggested two alternative spellings that might be easier to remember:
nc localhost 12345 < /dev/null   sudo tar xf -
< /dev/null nc localhost 12345   sudo tar xf -
And thinking along those lines, there could also be the disappointed face variant:
: nc localhost 12345 sudo tar xf -
Matthias Urlichs suggested the approach of
precaching sudo's credentials, making the rest of the command lines more
straightforward (and TIL: sudo id):
There's one more problem with a plain tar nc tar without redirection or
extra parameteres: it doesn't know when to stop. So the best way to use it, I
believe, is:
tar c nc -Nnc -d tar x
The -N option terminates the sending end of the connection, and the -d
option tells the receiving netcat to never read any input. These two
parameters, I hope, should also fix your sudo/password problem.
Hope it helps!
I worked with the CD release team over the weekend for the final release of Debian Stretch. One problem: we have media images which we cannot test because the team does not have the hardware. I asked questions on the debian-cd mailing list about the future of these and various other .iso images.
Could we replace some DVDs and larger files with smaller jigdo files so that people can download files to build the DVD locally?
People asked me:
How do you actually use jigdo to produce a usable media image?
What advantages does jigdo bring over just downloading a large .iso image?
Why jigdo?
Downloading large files on a slow or lossy link is difficult.
Downloading large (several GB) files via http can be unreliable.
Jigdo can be quicker than trying to download one large file and failing.
There are few CD mirrors worldwide: jigdo can use a local Debian mirror.
The transport mechanism is http - no need for a particular port to be opened.
Using jigdo
Jigdo uses information from a template file to reconstruct an .iso file by downloading Debian packages from a mirror. The image is checksummed and verified at the end of the complete download. if the download is interrupted, you can import the previously downloaded part of the file.
It's a command line application - the GUI never really happened - but it is fairly easy to use. apt install jigdo-file then find the .jigdo file and .template files that you need for the image from a CD mirror: https://cdimage.debian.org/debian-cd/current/amd64/jigdo-cd/
If you only have this file, jigdo-lite will download the template later but you can save the template in the same directory and save time. The jigdo file is only 25k or so and the template is 4.6M rather than 336M. I copied them into my home directory to build there. The process does not need root permissions.
Run the command jigdo-lite This prompts you for a .jigdo file to use. By default, this uses http to fetch the file from a distant webserver.
(If the files are local, you can use the file:/// syntax.For example: file:///home/amacater/debian-10.4.0-amd64-netinst.jigdo)
jigdo-lite then reads the .jigdo file and outputs some information about the .iso
It offers the chance to reload any failed download, then prompts for a mirror name. The download pulls in small numbers of files at a time, saves to a temporary directory and will checksum the eventual .iso file.
This will work for any larger file including the 16GB .iso distributed only as a .jigdo
For i386 and AMD, the images are bootable when copied to a USB stick. Use dd to write them and verify the copy.
Plug in a USB that can be overwritten.
Use dmesg as root to work out which device this is.
Change to the directory in which you have your .iso image.
Write the image to the stick in 4M blocks and display progress with the syntax of the command below (all one line if wrapped).
I had a draft of this article for about two months, but never really managed to polish and finalize it, partially due to some nasty hacks needed down the road. Thankfully, one of my wishes was heard and I had now the chance to revisit the post and try a few things out. Sadly, my wish was granted only partially and the result is still not beautiful, but read yourself ;-)
UPDATE: I've published a follow up post on building documentation for Ansible Collections using antsibull, as my wish was now fully granted.
As part of my day job, I am maintaining the Foreman Ansible Modules - a collection of modules to interact with Foreman and its plugins (most notably Katello). We've been maintaining this collection (as in set of modules) since 2017, so much longer than collections (as in Ansible Collections) existed, but the introduction of Ansible Collections allowed us to provide a much easier and supported way to distribute the modules to our users.
Now users usually want two things: features and documentation. Features are easy, we already have plenty of them. But documentation was a bit cumbersome: we had documentation inside the modules, so you could read it via ansible-doc on the command line if you had the collection installed, but we wanted to provide online readable and versioned documentation too - something the users are used to from the official Ansible documentation.
Building HTML from Ansible modules
Ansible modules contain documentation in form of YAML blocks documenting the parameters, examples and return values of the module. The Ansible documentation site is built using Sphinx from reStructuredText. As the modules don't contain reStructuredText, Ansible hashad a tool to generate it from the documentation YAML: build-ansible.py document-plugins. The tool and the accompanying libraries are not part of the Ansible distribution - they just live in the hacking directory. To run them we need a git checkout of Ansible and source hacking/env-setup to set PYTHONPATH and a few other variables correctly for Ansible to run directly from that checkout.
It would be nice if that'd be a feature of ansible-doc, but while it isn't, we need to have a full Ansible git checkout to be able to continue.The tool has been recently split out into an own repository/distribution: antsibull. However it was also a bit redesigned to be easier to use (good!), and my hack to abuse it to build documentation for out-of-tree modules doesn't work anymore (bad!). There is an issue open for collections support, so I hope to be able to switch to antsibull soon.
Anyways, back to the original hack.
As we're using documentation fragments, we need to tell the tool to look for these, because otherwise we'd get errors about not found fragments.
We're passing ANSIBLE_COLLECTIONS_PATHS so that the tool can find the correct, namespaced documentation fragments there.
We also need to provide --module-dir pointing at the actual modules we want to build documentation for.
Ideally, when antsibull supports collections, this will become antsibull-docs collection without any need to have an Ansible checkout, sourcing env-setup or pass tons of paths.
Until then we have a Makefile that clones Ansible, runs the above command and then calls Sphinx (which provides a nice Makefile for building) to generate HTML from the reStructuredText.
You can find our slightly modified templates and themes in our git repository in the docs directory.
Publishing HTML documentation for Ansible Modules
Now that we have a way to build the documentation, let's also automate publishing, because nothing is worse than out-of-date documentation!
We're using GitHub and GitHub Actions for that, but you can achieve the same with GitLab, TravisCI or Jenkins.
First, we need a trigger. As we want always up-to-date documentation for the main branch where all the development happens and also documentation for all stable releases that are tagged (we use vX.Y.Z for the tags), we can do something like this:
Now that we have a trigger, we define the job steps that get executed:
steps:-name:Check out the codeuses:actions/checkout@v2-name:Set up Pythonuses:actions/setup-python@v2with:python-version:"3.7"-name:Install dependenciesrun:make doc-setup-name:Build docsrun:make doc
At this point we will have the docs built by make doc in the docs/_build/html directory, but not published anywhere yet.
As we're using GitHub anyways, we can also use GitHub Pages to host the result.
Configure git to have a proper author name and email, as otherwise you get ugly history and maybe even failing commits
Fetch all branch names, as the checkout action by default doesn't do this.
Setup Python, Sphinx, Ansible etc.
Build the documentation as described above.
Switch to the gh-pages branch from the commit that triggered the workflow.
Remove any existing documentation for this tag/branch ($GITHUB_REF contains the name which triggered the workflow) if it exists already.
Move the previously built documentation from the Sphinx output directory to a directory named after the current target.
Generate a simple index of all available documentation versions.
Commit all changes, but don't fail if there is nothing to commit.
Push to the gh-pages branch which will trigger a GitHub Pages deployment.
Pretty sure this won't win any beauty contest for scripting and automation, but it gets the job done and nobody on the team has to remember to update the documentation anymore.
You can see the results on theforeman.org or directly on GitHub.
Azure Kubernetes Service provides a nice way to set up Kubernetes
cluster in the cloud. It s quite practical as AKS is setup by default
with a rich monitoring and reporting environment. By default, all
container logs are collected, CPU and disk data are gathered.
I used AKS to setup a cluster for my first client as a
freelance. Everything was nice until my client asked me why logs
collection was as expensive as the computer resources.
Ouch
My first reflex was to reduce the amount of logs produced by all our
containers, i.e. start logging at warn level instead of info
level. This reduced the amount of logs quite a lot.
But this did not reduce the cost of collecting logs, which looks like
to a be a common issue.
Thanks to the documentation provided by Microsoft, I was able to find
that ContainerInventory data table was responsible of more than 60%
of our logging costs.
What is ContainerInventory ? It s a facility to monitor the content
of all environment variables from all containers.
Wait What ?
Should we be worried about our database credentials which are, legacy
oblige, stored in environment variables ?
Unfortunately, the query shown below confirmed that, yes, we should:
the logs aggregated by Azure contains the database credentials of my
client.
ContainerInventory
  where TimeGenerated > ago(1h)
Having credentials collected in logs is lackluster from a security
point of view.
And we don t need it because our environment variables do not change.
Well, it s now time to fix these issues.
We re going to:
disable the collection of environment variables in Azure, which
will reduce cost and plug the potential credential leak
renew all DB credentials, because the previous credentials can be
considered as compromised (The renewal of our DB passwords is quite
easy with the script I provided to my client)
pass credentials with files instead of environment variables.
In summary, the service provided by Azure is still nice, but beware of
the default configuration which may contain surprises.
I m a freelance, available for hire. The https://code-straight.fr site
describes how I can help your projects.
All the best
Sorry for not being on blog for sometime, the last few months have been brutal. While I am externally ok, because of the lockdown I sensed major hearing loss. First, I thought it may be a hallucination or something but as it persisted for days, I got myself checked and found out that I got 80% hearing loss in my right ear. How and why I don t know. Is this NIHL or some other kind of hearing loss is yet to be ascertained. I do live what is and used to be one of the busiest roads in the city, now for last few months not so much. On top of it, you have various other noises.
Tinnitus
I also experienced Tinnitus which again I perceived to be a hallucination but found it s not. I have no clue if my eiplepsy has anything to do with hearing loss or both are different. I did discover that while today we know that something like Tinnitus exists, just 10-15 years back, people might mistake it for madness. In a way it is madness because you are constantly hearing sound, music etc. 24 7 , that is enough to drive anybody mad.
During this brief period, did learn what an Otoscope is . I did get audiometry tests done but need to get at least a second or if possible also a third opinion but those will have to wait as the audio clinics are about 8-10 kms. away. In the open-close-open-close environment just makes it impossible to figure out the time, date and get it done. After that is done then probably get a hearing device, probably a Siemens Signia hearing aid. The hearing aids are damn expensive, almost 50k per piece and they probably have a lifetime of about 5-6 years, so it s a bit of a expensive proposition. I also need a second or/and third opinion on the audiometry profile so I know things are correct. All of these things are gonna take time.
Pandemic Situation in India and Testing
Coincidentally, was talking to couple of people about this. It is sad to see that we have the third highest number of covid cases at 1/10th the tests we are doing vis-a-vis U.S.A. According to statistical site ourworldindata , we seem to be testing 0.22 per thousand people compared to 2.28 people per thousand done by United States. Sadly it doesn t give the breakup of the tests, from what I read the PCR tests are better than the antibody tests, a primer shares the difference between the two tests. IIRC, the antibody tests are far cheaper than the swab tests but swab tests are far more accurate as it looks for the virus s genetic material (RNA) . Anyways coming to the numbers, U.S. has a population of roughly 35 crores taking a little bit liberty from numbers given at popclock . India meanwhile has 135 crore or almost four times the population of U.S. and the amount of testing done is 1/10th as shared above. Just goes to share where the GOI priorities lie . We are running out of beds, ventilators and whatever else there is. Whatever resources are there are being used for covid patients and they are being charged a bomb. I have couple of hospitals near my place and the cost of a bed in an isolation ward is upward of INR 100k and if you need a ventilator then add another 50k . And in moment of rarity, the differences between charges of private and public are zero. Meaning there is immense profiteering happening it seems in the medical world. Heck, even the Govt. is on the act where they are charging 18% GST on sanitizers. If this is not looting then I dunno what is.
Example of Medical Bills people have to pay.
China, Nepal & Diplomacy
While everybody today knows how China has intruded and captured quite a part of Ladakh, this wasn t the case when they started in April. That time Ajai Shukla had shared this with the top defence personnel but nothing came of it. Then on May 30th he broke/shared the news with the rest of the world and was immediately branded anti-national, person on Chinese payroll and what not. This is when he and Pravin Sawnhey of Force Magazine had both been warning of the same from last year itself. Pravin, has a youtube channel and had been warning India against Chinese intentions from 2015 and even before that. He had warned repeatedly that our obsession with the Pakistan border meant that we were taking eyes of the border with China which spans almost 2300 odd kms. going all the way to Arunachal Pradesh. A good map which shows the conflict can be found at dw.com which I am sharing/reproducing below India-China Border Areas Copyright DW.com 2020
Note:- I am sharing a neutral party s rendering of the border disputes or somebody who doesn t have much at stake as the two countries have so that things could be looked at little objectively.
The Prime Minister on the other hand, made the comment which made galvanising a made-up word into verb . It means to go without coming in. In fact, several news sites shared the statement told by the Prime Minister and the majority of people were shocked. In fact, there had been reports that he gave the current CDS, General Rawat, a person of his own choosing, a peace of his mind. But what lead to this confrontation in the first place ? I think many pieces are part of that puzzle, one of the pieces are surely the cutting of defense budget for the last 6 years, Even this year, if you look at the budget slashes done in the earlier part of the year when he shared how HAL had to raise loans from the market to pay salaries of its own people. Later he shared how the Govt. was planning to slash the defence budget. Interestingly, he had also shared some of the reasons which reaffirm that it is the only the Govt. which can solve some of the issues/conundrum
First, it must recognize that our firms competing for global orders are up against rivals that are being supported by their home governments with tax and export incentives and infrastructure that almost invariably surpasses India s. Our government must provide its aerospace firms with a level playing field, if not a competitive advantage. The greatest deterrent to growth our companies face is the high cost of capital and lack of access to funds. In several cases, Indian MSMEs have had to turn down offers to build components and assemblies for global OEM supply chains simply because the cost of capital to create the shop floor and train the personnel was too high. This resulted in a loss of business and a missed opportunity for creating jobs and skills. To overcome this, the government could create a sector specific A&D Fund to provide low cost capital quickly to enable our MSMEs to grab fleeting business opportunities. Ajai Shukla, blogpost 13th March 2020 .
And then reporting on 11th May 2020 itself, CDS Gen. Rawat himself commented on saving the budget, they were in poor taste but still he shared what he thought about it. So, at the end of it one part of the story. The other part of the story probably lies in India s relations with its neighbors and lack of numbers in diplomats and diplomacy. So let me cover both the things one by one .
Diplomats, lack of numbers and hence the hands we are dealth with
When Mr. Modi started his first term, he used the term Maximum Governance, Minimum Government but sadly cut those places where it indeed needs more people, one of which is diplomacy. A slightly dated 2012 article/opinion shared writes that India needs to engage with the rest of the world and do with higher number. Cut to 2020 and the numbers more or less remain the same . What Mr. Modi tried to do is instead of using diplomats, he tried to use his charm and hugopolicy for lack of a better term. 6 years later, here we are. After 200 trips abroad, not a single trade agreement to show what he done. I could go on but both time and energy are not on my side hence now switching to Nepal
Nepal, once friend, now enemy ?
Nepal had been a friend of India for 70 odd years, what changed in the last few years that it changed from friend to enemy ? There had been two incidents in recent memory that changed the status quo. The first is the 2015 Nepal blockade . Now one could argue it either way but the truth is that Nepal understood that it is heavily dependent on India hence as any sovereign country would do in its interest it also started courting China for imports so there is some balance.
The second one though is one of our own making. On December 16, 2014 RBI allowed Nepali citizens to have cash upto INR 25,000/- . Then in 2016 when demonetization was announced, they said that people could exchange only upto INR 4,500/- which was far below the limit shared above. And btw, before people start blaming just RBI for the decision, FEMA decisions are taken jointly by the finance ministry (FE) as well as ministry of external affairs (MEA) . So without them knowing the decision could not have been taken when announcing it. The result of lowering of demonetization is what made Nepal move more into Chinese hands and this has been shared by number of people in numerous articles in different websites. The wire interview with the vice-chairman of Niti Ayog is pretty interesting. The argument that Nepal show give an estimate of how much old money is there falls flat when in demonetization itself, it was thought of that around 30-40% was black money and would not be returned but by RBI s own admissions all 99.3% of the money was returned. Perhaps they should have consulted Prof. Arun Kumar of JNU who has extensivelywritten and studied the topic before doing that fool-hardy step. It is the reason that since then, an economy which was searing at 9% has been contracting ever since, I could give a dozen articles stating that, but for the moment, just one will suffice. The slowing economy and the sharp divisions between people based on either outlook, religion or whatever also encouraged China to attack us. This year is not good for India. The only thing I hope Indians and people all over do is just maintain physical distances, masks and somehow survive till middle of next year without getting infected when probably most of the vaccine candidates have been trialed, results are in and we have a ready vaccine. I do hope that at least for once, ICMR shares data even after the vaccine is approved, whichever vaccine. Till later.
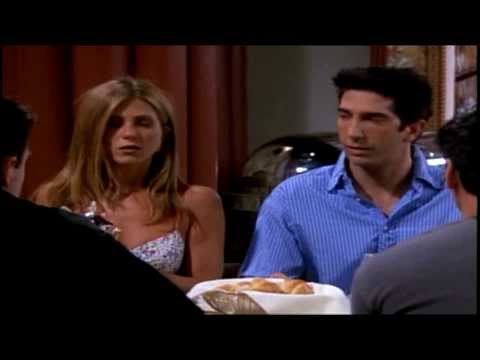
By now everyone must have seen the versions of comedy shows with the laugh track edited out. The removal of the laughter doesn't just reveal the artificial nature of television and how it conscripts the viewer into laughing along; by subverting key conversational conventions, it reveals some of the myriad and subtle ways humans communicate with one another:
Although the show's conversation is ostensibly between two people, the viewer serves as a silent third actor through which they and therefore we are meant to laugh along with. Then, when this third character is forcibly muted, viewers not only have to endure the stilted gaps, they also sense an uncanny loss of familiarity by losing their 'own' part in the script.
A similar phenomenon can be seen in other art forms. In Garfield Minus Garfield, the forced negative spaces that these pauses introduce are discomfiting, almost to the level of performance art:
But when the technique is applied to other TV shows such as The Big Bang Theory, it is unsettling in entirely different ways, exposing the dysfunctional relationships and the adorkable mysogny at the heart of the show:
Once you start to look for it, the ur-elements of the audience, response and timing in the way we communicate are everywhere, from the gaps we leave so that others instinctively know when you have finished speaking, to the myriad of ways you can edit a film. These components are always present, it is only when one of them is taken away that they become more apparent. Today, the small delays added by videoconferencing adds an uncanny awkwardness to many of our everyday interactions too. It is said that "comedy is tragedy plus timing", so it is unsurprising that Zoom's undermining of timing leads, by this simple calculus of human interactions, to feelings of... tragedy.
Leaving aside the usual comments about Pavlovian conditioning and the shows that are the exceptions, complaints against canned laughter are the domain of the pub bore. I will therefore only add two brief remarks. First, rather than being cynically added to artificially inflate the lack of 'real' comedy, laugh tracks were initially added to replicate the live audience of existing shows. In other words, without a laugh track, these new shows might have ironically appeared almost as eerie as the fan edits cited above are today.
Secondly, although laugh tracks are described as "false", this is not entirely correct. After all, someone did actually laugh, even if it was for an entirey different joke. In his Simulacra and Simulation, cultural theorist Jean Baudrillard might have poetically identified canned laughter as a "reflection of a profound reality", rather than an outright falsehood. One day, when this laughter becomes entirely algorithmically generated, Baudrillard would describe it as "an order of sorcery", placing it metaphysically on the same level as the entirely pumpkin-free Pumpkin Spiced Latte.
For a variety of reasons I recently decided to try interacting with various social media platforms in new ways. One way of loosening my addiction to this pornography of the amygdala was to hide the number of replies, 'likes' and related numbers:
The effect of installing this extension was immediate. I caught my eyes darting to where the numbers had been and realised I had been subconsciously looking for the input and perhaps even the outright validation of the masses. To be sure, these numbers can be relevant and sometimes useful, but they do implicitly involve delegating part of your responsibility of thinking for yourself to the vox populi, or the Greek chorus of the 21st century.
Like many of you reading this, I am sure I told myself that the number of 'likes' has no bearing on whether I should agree with something, but hiding the numbers reveals much of this might have been a convenient fiction; as an entire century of discoveries in behavioural economics has demonstrated, all the pleasingly-satisfying arguments for rational free-market economics stand no chance against our inherent buggy mammalian brains.
Tying a few things together, when attempting to doomscroll through social media without these numbers, I realised that social media without the scorecard of engagement is almost exactly like watching these shows without the laugh track.
Without the number of 'retweets', the lazy prompts to remind you exactly when, how and for how much to respond are removed, and replaced with the same stilted silences of those edited scenes from Friends. At times, the existential loneliness of Garfield Minus Garfield creeps in too, and there is more than enough of the dysfunctional, validation-seeking and parasocial 'conversations' of The Big Bang Theory. Most of all, the whole exercise permits a certain level of detached, critical analysis, allowing one to observe that the platforms often feel like a pre-written script with your 'friends' cast as actors, all perpetuated on the heady fumes of rows INSERT-ed into a database on the other side of the world.
I'm not quite sure how this will affect my usage of the platforms, and any time spent away from these sites may mean fewer online connections at a time when we all need them the most. But as the Karal Marling, professor at the University of Minnesota wrote about artificial audiences: "Let me be the laugh track."
And we're getting a lot closer. Last edits to the wiki for the testing page. Tests marked as passed. There are a bunch of architectures where the media images are still to be built and the source media will still need to be written as well.
It's been a really good (and fairly long day). I'm very glad indeed that I'm not staying up until the bitter end. It's always fun - I'm also very glad that, as it panned out, we didn't end up also doing the next Buster point release this weekend - it would have been a massive workload.
So Stretch passes to LTS, Jessie has passed to ELTS - and we go onwards and upwards to the next point release - and then, in due course, to Bullseye when it's ready (probably the first quarter of next year?).
As ever, thanks due to all involved - the folks behind the scenes who maintain cdimage.debian.org, to Sledge, RattusRattus, Isy and schweer. Done for about a fortnight or so until the next Buster release.
A new version of drat arrived on CRAN today. This is a follow-up release to 0.1.7 from a week ago. It contains a quick follow-up by Felix Ernst to correct on of the tests which misbehaved under the old release of R still being tested at CRAN.
drat stands for drat R Archive Template, and helps with easy-to-create and easy-to-use repositories for R packages. Since its inception in early 2015 it has found reasonably widespread adoption among R users because repositories with marked releases is the better way to distribute code.
As your mother told you: Friends don t let friends install random git commit snapshots. Rolled-up releases it is. drat is easy to use, documented by five vignettes and just works.
The NEWS file summarises the release as follows:
Changes in drat version 0.1.8 (2020-07-18)
The archive pruning test code was corrected for r-oldrel (Felix Ernst in #105 fixing #104).
 Final call to participate in the LTS survey
After 6 years of existence, we, the Debian LTS contributors, wanted to run a survey
to learn more about how Debian LTS is used and perceived. Please
 Please do file bugs/issues if you run into issues, rough edges or unhelpful documentation, etc.
 A new minor release of the
 At DebConf 17 in Montreal, I gave a talk about Ayatana Indicators [1] and the project's goal to continue the by then already dropped out of maintenance Ubuntu Indicators in a separate upstream project, detached from Ubuntu and its Ubuntu'isms.
Stalling
The whole Ayatana Indicators project received a bit of a show stopper by the fact that the IDO (Indicator Display Object) rendering was not working in vanilla GTK-3 without a certain patch [2] that only Ubuntu has in their GTK-3 package. Addressing GTK developers upstream some years back (after GTK 3.22 had already gone into long term maintenance mode) and asking for a late patch acceptance did not work out (as already assumed). Ayatana Indicators stalled at a level of 90% actually working fine, but those nice and shiny special widgets, like the calendar widget, the audio volume slider widgets, switch widgets, etc. could not be rendered appropriately in GTK based desktop environments (e.g. via MATE Indicator Applet) on other distros than Ubuntu.
I never really had the guts to sit down without a defined ending and find a patch / solution to this nasty problem. Ayatana Indicators stalled as a whole. I kept it alive and defended its code base against various GLib and what-not deprecations and kept it in Debian, but the software was actually partially broken / dysfunctional.
Taking the Dog for a Walk and then It Became all Light+Love
Several days back, I received a mail from Robert Tari [3]. I was outside on a hike with our dog and thought, ah well, let's check emails... I couldn't believe what I read then, 15 seconds later. I could in fact, hardly breathe...
I have known Robert from earlier email exchanges. Robert maintains various "little" upstream projects, like e.g. Caja Rename, Odio, Unity Mail, etc. that I have looked into earlier regarding Debian packaging. Robert is also a Manjaro contributor and he has been working on bringing Ayatana Indicators to Manjaro MATE. In the early days, without knowing Robert, I even forked one of his projects (indicator-notification) and turned it into an Ayatana Indicator.
Robert and I also exchanged some emails about Ayatana Indicators already a couple of weeks ago. I got the sense of him maybe being up to something already then. Oh, yeah!!!
It turned out that Robert and I share the same "love" for the Ubuntu Indicators concept [4]. From his email, it became clear that Robert had spent the last 1-2 weeks drowned in the Ayatana IDO and libayatana-indicator code and worked him self through the bowels of it in order to understand the code concept of Indicators to its very depth.
When emerging back from his journey, he presented me (or rather: the world) a patch [5] against libayatana-indicator that makes it possible to render IDO objects even if a vanilla GTK-3 is installed on the system. This patch is a game changer for Indicator lovers.
When Robert sent me his mail pointing me to this patch, I think, over the past five years, I have never felt more excited (except from the exact moment of getting married to my wife two-to-three years ago) than during that moment when my brain tried to process his email. "Like a kid on Christmas Eve...", Robert wrote in one of his later mails to me. Indeed, like a "kid on Christmas Eve", Robert.
Try It Out
As a proof of all this to the Debian people, I have just done the first release of

 Like
 This is part of a series of posts on compiling a custom version of Qt5 in order
to develop for both amd64 and a Raspberry Pi.
The previous rounds of attempts ended in
 We encourage our community to celebrate around the world the 27th Debian
anniversary with organized

 I used AKS to setup a cluster for my first client as a
 Ouch
 My first reflex was to reduce the amount of logs produced by all our
 Should we be worried about our database credentials which are, legacy
 And we don t need it because our environment variables do not change.
Well, it s now time to fix these issues.
 We re going to:
 Sorry for not being on blog for sometime, the last few months have been brutal. While I am externally ok, because of the lockdown I sensed major hearing loss. First, I thought it may be a hallucination or something but as it persisted for days, I got myself checked and found out that I got 80% hearing loss in my right ear. How and why I don t know. Is this
 Example of Medical Bills people have to pay.
 India-China Border Areas Copyright DW.com 2020
 By now everyone must have seen the versions of comedy shows with the laugh track edited out. The removal of the laughter doesn't just reveal the artificial nature of television and how it conscripts the viewer into laughing along; by subverting key conversational conventions, it reveals some of the myriad and subtle ways humans communicate with one another:


 A new version of