Search Results: "ag"

25 September 2007

MJ Ray: maildelayline - sending emails at a given future time

I'm pretty sure someone in one of my syndicators was looking for software to send emails in the future from anywhere, but I'm damned if I can find the message. At the time, I was using a homebrew system involving shell scripts and mailx, so I wasn't much help. I'll upload a proper release soon, but I'm happy to upload a second hack of maildelayline here. It requires recent bash, sed, at and a sendmail-like executable. I've deliberately kept it simple to try to make it easier to debug and I dislike needing to install too much for such a simple task. Make a temporary directory, edit the top of the script, then install it on a pipe mail alias (I'd keep the address secret and improbable, like RUbAHy8961: " /path/to/maildelayline" and then save the address in my address book) and send it an email. At the start of the email body, write a pseudo-header with the time, like
"X-Send-At: now + 7 hours"
and follow it with the To:, Cc:, Bcc: and any other headers. Some headers (like from, message-id and threading ones) are kept from the original message, but the Date and Received headers are among those removed. Don't put the X-Send-At in the email header unless you know what you're doing - usually, put it in the body. The X-Send-At field can be any time that your at program understands. If you confuse it, or forget to give it a time, then you should get a bounce message that says something like "garbled time" among other errors. maildelayline is similar to Leave A Message or FutureMe but it sends mail to anyone, autonomously on your own server, from emails instead of a web form. I think it will resend MIME attachments as long as the pseudo-header is in a plain text/plain part and not quoted-printable or base64 or something. It is named after delay lines, which I believe are mostly used in audio effects to repeat a sound after a time delay. Please leave a comment if you find this useful, or if you have an improvement.

MJ Ray: What is needed to start Open Social Networking?

Since the closure of SoFlow and adding myself to LinkedIn, I've been thinking a bit about Professional Associations and using Social Networks (SNs) for business. I've not worked out my answers, so this is a "dear lazyweb, what pieces of this jigsaw am I missing?" post. Much of the recent mainstream news has been about the legal problems of SNs - for example, see BBC: Web networkers 'at risk of fraud' (which was also in items on a recent Click show on BBC World and News24) and BBC: Facebook site faces fraud claim - or about how they could Save The World, like BBC: Social net offers new perspective I think there's a bigger problem which will stop SNs making a deep-change to online activity. Each time a SN like SoFlow closes, it wastes some resources of its members. I'm starting to side with other developers in being tired of seeing my input turn to bitrot, through buggy software or buggy business models. I'm not alone: see Gunnar Wolf: On social networks for example. A good idea seems to be on Slashdot: It's Time for Social Networks to Open Up but how? Each SN seems to guard its dark corners as vital elements of its business model. Should we look to our Professional Associations to create new Open Social Networks (OSNs)? After all, SNs aren't the core money-makers for professional associations. But, the biggest problem with Professional Associations is picking a trustworthy one - one which will do what it says on the tin, instead of taking your subscription, then undermining you. Consider the British Computer Society and its OSSG License: how many of its members really wanted another software copyright licence? Fortunately, it was spotted - Volunteer brickbat thrower needed in London (Tuesday 24th 6pm) - and the Report from BCS OSSG meeting on a new FS license suggests the negative feedback was loud and clear, so hopefully we won't see that again. If I was a BCS member, I'd probably not renew after helping to fund that harmful activity. librarian.net: choosing your battles and choosing your professional associations talks a little about some library associations as a sort of case study which many will recognise as familiar, but there's an interesting comment from Blake there:
"I think there's an association out there for everyone."
Is there? What association is out there for liberal hackers and webmasters? I don't think I've found it yet. So, should we be looking at ourselves, rather than existing professional associations? Can we do Open Social Networks peer-to-peer in a meaningful way? Are we already doing it with blog feeds? How should we expand on that? Although I disagree with the conclusion that using another Social Network site with an uncertain business model is How to succeed with social networking, the article also mentions that
"social networking is in its infancy and that it will not really get underway until we have portable profiles and interconnectivity"
In other words, it's our revolution - let's steal it back. (Update: 2007-09-27: 1 comment)

Julien Danjou: Random news

Wouhou, yesterday was quite a productive day. First, I've released mod_defensible 1.4 which is just one line different from 1.3 but fix a huge bug (RC in Debian) with udns 0.0.9. Already uploaded to sid. Second, I've updated greylistd in Debian and I've set myself as maintainer after 5 NMU in something like 1 year. Then, I've pushed some updates to awesome. I may release 1.2 in the week, since it seems bug free and has some useful new features. We're now quite close to Xmonad functionalities as far as I can tell. And the beat goes on

Ross Burton: Network Manager 0.7

Over the weekend I spent some time hacking on Poky, integrating Network Manager. Because I'm hardcore I went for NM from trunk, instead of 0.6, as apparently its approaching stability and feature completeness. This afternoon I finally fixed enough stupid problems (/sbin/ip wasn't executable for instance, thanks install -s) that it connected to the office wireless and let me browse to Google. NM in Poky Thanks to Dan Williams for answering my stupid questions about Network Manager.

Norbert Tretkowski: Useless Ubuntu patches

While updating the Debian package of xchat-gnome to the latest upstream release, I also wanted to check if the package in Ubuntu includes some patches relevant for Debian. Ubuntu unfortunately doesn't forward small patches relevant for Debian to it's bug tracking system, but provides one big patch on http://patches.ubuntu.com/ instead...

-rw-r--r-- 1 tretkowski tretkowski 1375182 2007-09-21 18:12 xchat-gnome_1:0.18-0ubuntu2.patch

That's the patch between 1:0.18-0ubuntu2 from Ubuntu gutsy and 1:0.17-2, the current xchat-gnome package in unstable. Quite useless, if you ask me. Who really want's to read a 1.4M patch?

David Nusinow: More Code And Less User Support For A While

While it's cute that atoponce wants to blame #debian for his problems, what he neglects to mention is that I spent some time with him in #debian finding his bug and telling him that his best bet was to watch that bug report because that's the most up to date information available on the problem. Furthermore, I told him how to add a "me too" to the report so that he would be taken care of. I also googled him up a wiki page that explained what GLcore was better than I ever could. And I tried to do it as politely and respectfully as I could.

I'm not sure what more people want from the channel. The #debian policy is that "if you're running sid, you're on your own." The reason is that it's your machine and you're responsible for it. The fact that Aaron chooses to blame other people for his decision to run a development version of a package (and then to not downgrade it when it becomes too problematic) is the kind of frustrating attitude that makes me want to stay away from being active in user support.

Fortunately, #debian is actually a very good channel on the whole, especially in comparison to the past, where some individuals really were just plain mean spirited. It's full of knowledgeable users who are generally willing to help you find a solution to your Debian problem. Sure, they're wrong sometimes, everyone is. And no matter how knowledgeable you are, you're not going to be able to predict that the next upgrade will hose some random guy's system. If you want to run unstable, be prepared for what's in store and learn how to downgrade.

Russell Coker: Census

I’m just completing Jeff and Pia Waugh’s Australian Open Source Industry & Community Census [1]. There are some things that can be improved with that survey in particular and surveys in general. It seems to be assumed that everyone is trying to work full-time. I admit that there are probably few people who have decided that they don’t need as much money as they would earn in full-time work and reduced their work hours to match their financial needs (as I have done). Surveys that just ask a for a figure of how much is earned add to the pressure to earn as much as possible, which isn’t what’s best for most people. I have the impression that the questions about “how long have you been doing X” assume that doing so is contiguous. If that’s the case then asking “when did you first do X” and giving a drop-down list-box of the last 20 years to select from would probably be better (more precise and remove confusion). Debian wasn’t listed as a Linux distribution! It only has Ubuntu, RHEL, Fedora, and SUSE. The question mixing kernels and distributions was a little strange. It gives BSD as a kernel option but no BSD option in user-space, so apparently it’s assumed that there is only one user-space/distribution for BSD (there have been some attempts to release Debian with the various BSD kernels). Also it wasn’t clear what you have to do regarding the kernel to select it (is the couple of hundred lines of patches I submitted to the Linux kernel adequate to let me list it?). There were a bunch of questions that would get very predictable answers. Do you want to have access to official government web-sites and documents with free software? I guess that they want to get a large number of people requesting such things. Incidentally much of that is in the Greens IT policy… Immediately below the buttons on the screen to go to the Next and Previous pages there is a link to clear the form and exit. When doing something difficult like sys-admin work it’s expected that a command to wipe out your work will be immediately next to something innocuous, but for something that generally doesn’t require much concentration (such as filling out a survey) it would be good to have the dangerous options a little further away. At the end of the survey there are questions about whether you want to be contacted about events held by various companies. I think that it would be better to have an RSS feed of such events that we can poll when we have spare time. I’m sure that the PR people running the events are happy when they see a good number of people signed up to their mailing list. But if you actually want to get people to sign up without prior contact the best thing to do is have it on a web site with an RSS feed (either a blog or a CMS) so that it can be polled, syndicated, and googled.

Joerg Jaspert: Password Manager

Dear Lazyweb, im looking for a “password management” application that does not suck. Any suggestions? I am currently using fpm for some low-security passwords and a gpg encrypted textfile for some more important ones. (And having some really important ones only in my head, stored nowhere else). While it works its not really comfortable or fun to use. Now, I would want an app where i can trust its encryption (while I do have my harddisks crypted the file should still be encrypted), so usage of GPG would be nice. It should also be able to group passwords, like fpm can. I do not care about any kind of “URL launcher”, thats a feature i never use. Most important - it should be able to merge its dataset. Use case: I want to use it on multiple systems and have it synchronize the data itself. The sync can be a process I manually have to start, I dont care. But trying to keep the datafiles in sync and hope I never accidently overwrite them just does not work. I also dont care about X or not (as long its not one of the gnome or kde integrated keyring things), as long as I can easily get the password out of it into a copy/paste buffer, without displaying it… Suggestions?

David Moreno Garza: On Ahmadinejad s visit to the US

Shamelessly stolen from Metroblogging NYC.

Michal Čihař: Uploading photos to minilab

I was looking for some easier solution than using web forms, but no minilab seems to support Linux here. Windows applications I tried so far does not seem to work in Wine, so this is also not an option. Only thing that seems to work is Picassa, but it is quite big tool to make just uploading photos and it is anyway some beast using Wine. So the only option was to write something myself. Using cURL from Python is quite easy so I hacked simple script to upload photos to minilab using PycURL. It currently supports only Droxi, but it might be later extended to support others. The code is also now a bit fragile as it does almost none error checking, but I was able to upload first set of photos to minilab and continue order in browser. You can download my proof of concept code at Photo uploader page, but don't expect anything clever from it, but it should basically work :-).

Masayuki Hatta: ghostscript 8.61.dfsg.1~svn8187-1 uploaded

So, brand-new packages are now in the NEW queue. Sorry it took soooo long time(my life has been hectic these days). I guess it might take another long time to make them entered into the archive, so I give you some apt-line:
deb http://people.debian.org/~mhatta/debian/ghostscript/ ./
deb-src http://people.debian.org/~mhatta/debian/ghostscript/ ./
Tell me if something goes wrong in the process of transition. One of the reason I was reluctant to upload them (while Ubuntu has already did almost 2 month ago) was, the CJKV support in GPL Ghostscript 8.60 is notably regressed from the level of ESP Ghostscript 8.15.1. Seems Till Kamppeter once merged some key CJKV patches into the mainline SVN repository, but later they were revoked. Until recently, I didn't realize why Till used a rather peculiar old SVN snapshot 8187 for Ubuntu (the current SVN revision is something like 8249), but now it's clear for me. I could choose to apply those revoked patches to the 8.60 source by myself, but as you might know I'm a lazy bastard, so I simply follow the Ubuntu path, with some Debian-specific tweaks. Well, let's hope this issue will be fixed before the official 8.61 is released...or I'll try, hopefully.

Tag this post with del.icio.us!

Otavio Salvador: live-helper support to syslinux vesa menu got merged

Since some time, I’ve been working on live-helper support for syslinux vesa menu due our need for it here at O.S. Systems. Since I got it to work, my focus has changed and I’ve forgotten this code for some time but some days ago, another project at the company required it and then I wanted to forward port it to lastest code. Initial code has been ported and then merged by Daniel on his GIT tree and today I went to try it and did some more changes on it that got it in a very good shape (not yet merged but available on my GIT tree) and I thought that would be nice to share it here so more people can try it and shout if find something is broken on it.

24 September 2007

Jordi Mallach: GNOME 2.20 for Debian

My lack of posts lately left Planet readers without yet another yay, GNOME 2.20 released post. I'm sure nobody missed it. However, I can report what's going on in Debian regarding its packaging. The executive summary is: the GNOME team rocks, and having much of GNOME 2.20 available in sid on the very same day it was officially announced was possible thanks to the incredible work done by lool, Np237, slomo and other restless team members, who spent the summer tracking GNOME 2.19 releases and packaging them in experimental. To get a better view on what's left to do, you can use the 2.20 status page, which you'll see shows lots of green at this point. Some of the outstanding blockers are gtksourceview and the new epiphany-webkit binary stuck in NEW, which block gedit and epiphany, and of course, the initial mess that the buildds need to sort out to get the dependencies installed. The rest of red bits will continue trickling in unstable in the next few days. Beware of the new behaviour in control-center, which will by default use the DPI value provided by X. Some X drivers are still buggy and can provide bad values, which will cause bad font displays. If you're hit by this, you can force a DPI value in control-center, which should fix the issue. Also, you can read the relevant thread in our mailing list. Enjoy 2.20! Update: yeah, ftpmasters rock too, and epiphany hit incoming just a few hours after posting this entry. Yay ephy-webkit!

Ross Burton: Icon Madness

Last week I had to use Vicky's laptop briefly, which sadly runs Windows XP. I was greated with this monstrosity: The baby Jesus is beyond crying. For the curious, from left to right there is battery charge, wireless network status, InstallShield Update Manager, Java Updates, Windows Updates, Lastfm Scrobbler, Lenovo Client Security Password Manager, Bluetooth network connection (never used), Wired LAN network connection (never used), volume, ThinkVantage Access Connections wireless status, IBM Message Centre, Epson printer status, ThinkVantage Access Connections, Adobe Photo Downloader, GoogleTalk, Bluetooth status, QuickTime, Windows Security Alerts. After 30 minutes of removing software and disabling some more, I finally got this down to seven icons. I wish there was a way to disable Windows from showing the status of every network connection though. NP: Sketches of Spain, Miles Davis
Adeodato Sim : Dear Lazyweb, an RSS reader that with new != unread count?

I’m looking (or I’m desperate) for an RSS reader which differentiates between new and unread articles, and can show a count that only includes new articles for each feed. My current reader, Akregator, sort of fulfills the first requirement, but not the second. If you know of one, please let me know. I’m willing to give it a try even if it’s written for another desktop environment than my own, or in a language that I don’t like. If I can’t find one, I will try to go back to rss2email and Mutt. But I really, really, really dislike the management of feeds with rss2email. I would love to have it read a simple text file where feeds are listed in groups, each group has a keyword to add as an email header, and I’m free to add/delete/move feeds in the text file with changes being effective in the next r2e run. Any suggestions on this side?

Masayuki Hatta: CAPTCHA installed

I got fed up with comment spams, so finally I made some time and installed Bill Ward's excellent Captcha plugin for Blosxom. Seems it works nicely. I'd better migrate PyBlosxom or such, maybe someday...

Tag this post with del.icio.us!

Aigars Mahinovs: FON not giving me my own Internet

Unfortunately I will have to disconnect my FONera and buy a real WiFi router to replace it because that small box is a glitchy piece of crap compared to every other WiFi router out there. The killer: if the LaFonera can not connect the FON authentication servers, then it thinks that there is no network available and does not let me use my Internet. There is even no way to force it to pass connections to outside which is required in many cases such as partial network failures (when you can not get to FON servers for some reason, but rest of the Internet works just fine) and for web signup pages that some ISP’s use to login users to their network. And you can not use another PC for that, because it records the MAC address. The box frequently freezes and the DNS server stops responding. I can continue working by editing my local DNS server settings to the DNS of my ISP, but that is no way to work! The damn thing has no idea about uPNP which is a must nowadays for peer-to-peer transactions. And lastly there is absolutely no way for me to fix any of this because the FON keeps a tight lock on the firmware. In the time when all good software and community projects go to the open side, the FON moves further and further to the dark side and that is disturbing. I consider this a permanent failure on FON’s part that negates my ability to hold my side of the Fonera promise. It would be so much easier if I could ssh into the thing - ping stuff, traceroute stuff, put some kind of flag file to say that network in fact is there, release or refresh the DHCP lease or even restart the damn thing remotely. Nothing of this is available.

Stefano Zacchiroli: vim-addons-completion

vim-addons: now with super completion power Just uploaded vim-addon-manager 0.3. The best news is that it has grown bash completion powers. After some round trips with the bug (and patch) reporter we managed to achieve a rather smart completion (e.g. vim-addons install<TAB> will complete only with the addons that you can install, excluding those which are already installed and taking into account whether or not you're asking to install a personal or system-wide addon). Cool. PS Thanks for the patch Antonio!

Russell Coker: Blogger is Not for Serious Blogging

When I started blogging I used Blogger [1]. After some time I decided that it did not offer me the freedom I desired. I could not easily make changes (I could have created new themes, but it would have taken an unreasonable amount of work). I currently use Wordpress, it’s still a lot of work to change themes, but at least it’s CSS and PHP coding which can be used for other things. Blogger offers no statistics on web use (I tried adding support for Google Analytics but couldn’t get it to work properly), what I want is Webalizer or something similar (which is easy to do when running your own server). Blogger is a reasonable way of starting blogging, but if you use it then you want to make it easy to change to something that you own. Blogger has a feature of using a DNS name in a domain that you own for the name of your blog (which is much less obvious than it once was), I regret not using that feature as I still have my old posts on blogger and don’t want to break the links. Blogger has in the past had problems with time-stamps on posts, when I used blogger I had some complaints that my posts were staying at the top of Planet listings for unreasonable amounts of time (I never tracked this down before switching to my own platform). Hosting your own blog is not as difficult as you might expect (initially at least). It becomes difficult when you want to install lots of plug-ins, but then any blogging solution would be difficult if you want to do that. The Wordpress [2] package in Debian works well and has good support for multiple Wordpress blogs. There is a separate product named Wordpress-MU [3] which is designed for people who want to run a service in competition with Blogger, some people recommend that you use Wordpress-MU if you want to set up blogs for several people. I disagree. If you are setting up blogs for a small number of people then you can use the standard Wordpress package and create a file named /etc/wordpress/config-whatever.example.com.php which contains the configuration for whatever.example.com and then create a new Wordpress blog by using the web-based interface to do the rest. It would not be difficult to create the configuration file in question with an M4 script if you have a moderate number of blogs to host (maybe a hundred or so). I think that it’s only if you want to host thousands of blogs that you need the features of Wordpress-MU. Note that MU is not as well packaged as the base Wordpress and has some rough edges. Last time I tried to set up MU I was not successful. This is not to say that Wordpress is inherently the best program, there are many other free software blogging platforms out there. Wordpress is the one that I use and am happy to recommend but if your requirements differ from mine then another platform may be better for you. I also suggest that Wordpress be used as the base-line for comparing blogging software. Blogger does not require significant resources. A virtual host with 256M of RAM should be more than adequate to run Wordpress plus MySQL. Such virtual hosts are getting quite cheap nowadays, and one such host could easily be shared by a number of bloggers. My blog uses about 1.2G of data transfer per month. vpsland.com offers virtual hosts starting at 150G per month data transfer with 192M of RAM being the minimum. Prices start at $US15 per month. While I can’t compare vpsland.com to other virtual hosting providers (having never used any other such service) I can say that they work reasonably well and I have a client who is happy with them. So it seems that a minimal plan with vpsland.com would host 20 blogs with the same traffic as mine (with RAM being the limiting factor) and a slightly larger plan (with more RAM and more bandwidth) that costs $US30 or $US40 per month could handle 100 or more blogs that are similar to mine. If you get together with some friends and share a virtual server then blogging would not be expensive. Incidentally I had previously read a blog comment about people being hesitant to share servers with their friends (as they apparently would rather grant some unknown people at a faceless corporation the ability to snoop on them than people that they know). The advantage of a blog server in this regard is that everything is public anyway! If you have good technical skills then I recommend using Wordpress as your first blogging platform. If you find that you don’t like it for some reason then you can convert to another platform if you own the domain. If you are setting up a blog for a less technical user then Wordpress is also a good choice. My sister uses Wordpress, not that she made much of a choice (I had set up a Blogger account for her some time ago which she never used - I guess that could be considered as a choice to not use Blogger) but that I set up a Wordpress blog for her and she seemed to like using it.

Benjamin Mako Hill: Lamp Stores

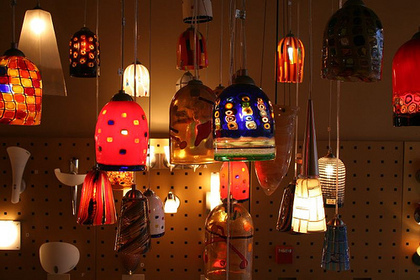
I have an intense, unexplainable, uneasiness around lamp stores. Perhaps it's even a fear. /copyrighteous/images/lamp_store.jpg Something about so many lamps, so close together. It seems unnatural. Very Wrong.
Next.

Previous.