Search Results: "ema"

9 January 2016

Guido G nther: Debian Fun in December 2015

Debian LTS December was the eighth month I contributed to Debian LTS under the Freexian umbrella. It was a bit of a funny month since most of the time most open CVEs were already taken care of by other team members (which is nice) but it resulted in me not releasing a single DLA which feels weird. Nevertheless in total I spent nine hours working on: On unpaid time I introduced some usertags for tracking our non DLA related activities (although it seems I'm currently the only user). Other Debian stuff

8 January 2016

Norbert Preining: Fighting with IPv6

During the last weeks I finally got my hands dirty with IPv6. A comment on my blog and an email informed me that my server (hosting this blog) is not reachable via IPv6, albeit it has an IPv6 address. That said, I tried to get that running and fell into several holes, due to firewalls, my home provider not doing IPv6, and not the least due to my own ignorance of IPv6. ipv6-pain Fortunately, with the help of some good souls and the technical support I finally got IPv6 connectivity on both my server, as well as at home, up. Server So my server is still running wheezy, which is a bit old, but upgrading with lots of hand-installed stuff is a bit a pain. The network interface was configured via a static IPv4 address, and no traces of IPv6 for now. Simple minded as I am, I assumed that this is the problem and started playing around with all kind of IPv6 configurations in the interfaces file, from using dhcp, and static configuration. The static configuration somehow worked out, but I never got a proper default route set. So I was really puzzled. In addition, at home I don t have IPv6, my provider is not distributing IPv6, so I couldn t test it (but on this a bit later). Fortunately, the good soul from the Netherland Filip B., did a lot of testing and also send permanent suggestions and analysis of the IPv6 situation, I am very much indebted to him. Anyway, his last advice about the problem with the default route was contacting the technical support of my provider, who within a very short time sent me an answer which made it clear to me: My firewall was blocking some ports that are necessary for IPv6 route autonegotiation. As firewall I use ferm, kind of a meta iptables language. In my server s setup the firewall blocks most of the ip traffic outside the expected servers, as well as does rate limit checks on ssh connections (those script kiddies). And while I have had some of the icmpv6 types allowed, it seemed that was insufficient. The solution at the end was to open icmpv6-type s 1-4, 133-137, 141, 142, 148, 149, as well as 130-132 from link-local adresses (fe80::/10). After having changed my ferm.conf, even removing everything related to IPv6 from the interfaces file and rebooting finally provided the server with an IPv6 address and a proper route. Wow, first step done. For Apache, fortunately I am doing already wildcard definitions, so no change was necessary and voil , the server is reachable via IPv6. Home As already mentioned, my provider at home does not provide IPv6 addresses. In addition, the DNS server of the provider is also very, well, peculiar about resolving IPv6 (i.e., AAAA records). Trying to get the AAAA record for ipv6.google.com works without a problem:
$ host -t AAAA ipv6.google.com
ipv6.google.com is an alias for ipv6.l.google.com.
ipv6.l.google.com has IPv6 address 2404:6800:4002:803::1003
but trying this with my own server, or for that matter any other server, resulted in no answer (preining.info has no AAAA record). Well, that didn t help. Despite these problems, I tried to get an IPv6 address via 6-in-4 tunneling (tunnelbroker), but that didn t work either, probably due to some reverse lookup and the fact that between the world and me there is a cable modem and a wlan router that all on top of the slightly funny infrastructure here in Japan, where you have to rent lines from NTT, but use a different company as Internet provider. I finally found the solution that worked for me, and that is installing miredo, available in Debian. Installation of the package, and starting the miredo service with systemctl start miredo (or /etc/init.d/miredo start) gave me in an instant a working IPv6 connectivity. ping6 worked on IPv6 addresses. Still, I couldn t fix the DNS lookup problem, so for the time being I have added IPv6 addresses for my own server in /etc/hosts, and by using the SixOrNot Firefox plugin I can actually check that it works. Conclusion It is 2016, and we are still far from end-to-end IPv6, and I have to admit that also my IPv6 knowledge is quite meager, and that I only recently have started to grasp some understanding. The good point was that Debian wheezy already works out of the box with IPv6 (if one is not as clumsy as me and blocks the necessary ports), including web servers and mail servers. I have also contacted my provider (AsahiNet) in the hope that they can update their DNS server, and learned that they are planning to roll out IPv6 addresses in the near future whatever that might mean in Japan, maybe next century?

7 January 2016

Elena 'valhalla' Grandi: Smartphones, ownership and hope for the fate of humanity

Smartphones, ownership and hope for the fate of humanity
Do you own your phone or does it own you? DanielPocock.com


I have conflicting opinions about this article.

Usually I carry a dumb phone, so I'm not completely disconnected, but I'm mostly self-limited to "useful" communications by the fact that I have to pay for calls and SMSs. It also has a few useful features like showing the time , an alarm clock and a led torch, but that's it.

I also carry a smartphone, but I've never been able to trust it with my personal data, so there is no email on it and no communication software. It's also always offline to preserve battery, unless I'm actually using it for something (usually maps). It does have an offline wikipedia reader, which is the second thing I use it more often for. About half of the time I try to use it, however, it is off because I forgot to charge it, unless I've planned in advance to use it (which usually means I'm also carrying a laptop and will need to tether it).

So I guess that I should be agreeing with the article that offline life is better, and that we shouldn't depend on phones in our daily life, and mostly I do.

On the other hand, I'm not so sure that all of the people who seem to be interacting with a phone are actually disconnected from the local reality.

More than once I've experienced the use of smartphones as part of a local interaction: one typical case involves people having a conversation IRL and checking some fact on the internet and then sharing the results with the rest of the local group.

Actually, most of the time I've seen a smartphone being used at our table while eating with friends or collegues it was being passed around to show something to the people at the table, or at the very least being read aloud from, so it was part of the local experience, not a way to disconnect from it.

I'm sure that there are cases of abuse, but I still have hope that most of the connected humanity is managing to find a good balance between online and offline.

I don't want to go back carrying a wrist watch. I remember them as something unconfortable that ended up hitting stuff as I moved my hands, and I'd rather have my wrists free while I type, thanks. Pocket watches, OTOH...

the main exception involved one young adult in the middle of significantly older relatives, which is a somewhat different issue, and one that I believe predated smartphones (IIRC in my case similar situations involved trying to be somewhere else by reading a book).

Francois Marier: Streamzap remotes and evdev in MythTV

Modern versions of Linux and MythTV enable infrared remote controls without the need for lirc. Here's how I migrated my Streamzap remote to evdev.

Installing packages In order to avoid conflicts between evdev and lirc, I started by removing lirc and its config:
apt purge lirc
and then I installed this tool:
apt install ir-keytable

Remapping keys While my Streamzap remote works out of the box with kernel 3.16, the keycodes that it sends to Xorg are not the ones that MythTV expects. I therefore copied the existing mapping:
cp /lib/udev/rc_keymaps/streamzap /home/mythtv/
and changed it to this:
0x28c0 KEY_0
0x28c1 KEY_1
0x28c2 KEY_2
0x28c3 KEY_3
0x28c4 KEY_4
0x28c5 KEY_5
0x28c6 KEY_6
0x28c7 KEY_7
0x28c8 KEY_8
0x28c9 KEY_9
0x28ca KEY_ESC
0x28cb KEY_MUTE #  
0x28cc KEY_UP
0x28cd KEY_RIGHTBRACE
0x28ce KEY_DOWN
0x28cf KEY_LEFTBRACE
0x28d0 KEY_UP
0x28d1 KEY_LEFT
0x28d2 KEY_ENTER
0x28d3 KEY_RIGHT
0x28d4 KEY_DOWN
0x28d5 KEY_M
0x28d6 KEY_ESC
0x28d7 KEY_L
0x28d8 KEY_P
0x28d9 KEY_ESC
0x28da KEY_BACK # <
0x28db KEY_FORWARD # >
0x28dc KEY_R
0x28dd KEY_PAGEUP
0x28de KEY_PAGEDOWN
0x28e0 KEY_D
0x28e1 KEY_I
0x28e2 KEY_END
0x28e3 KEY_A
The complete list of all EV_KEY keycodes can be found in the kernel. The following command will write this mapping to the driver:
/usr/bin/ir-keytable w /home/mythtv/streamzap -d /dev/input/by-id/usb-Streamzap__Inc._Streamzap_Remote_Control-event-if00
and they should take effect once MythTV is restarted.

Applying the mapping at boot While the na ve solution is to apply the mapping at boot (for example, by sticking it in /etc/rc.local), that only works if the right modules are loaded before rc.local runs. A much better solution is to write a udev rule so that the mapping is written after the driver is loaded. I created /etc/udev/rules.d/streamzap.rules with the following:
# Configure remote control for MythTV
# https://www.mythtv.org/wiki/User_Manual:IR_control_via_evdev#Modify_key_codes
ACTION=="add", ATTRS idVendor =="0e9c", ATTRS idProduct =="0000", RUN+="/usr/bin/ir-keytable -c -w /home/mythtv/streamzap -D 1000 -P 250 -d /dev/input/by-id/usb-Streamzap__Inc._Streamzap_Remote_Control-event-if00"
and got the vendor and product IDs using:
grep '^[IN]:' /proc/bus/input/devices
The -D and -P parameters control what happens when a button on the remote is held down and the keypress must be repeated. These delays are in milliseconds.

Daniel Pocock: Do you own your phone or does it own you?

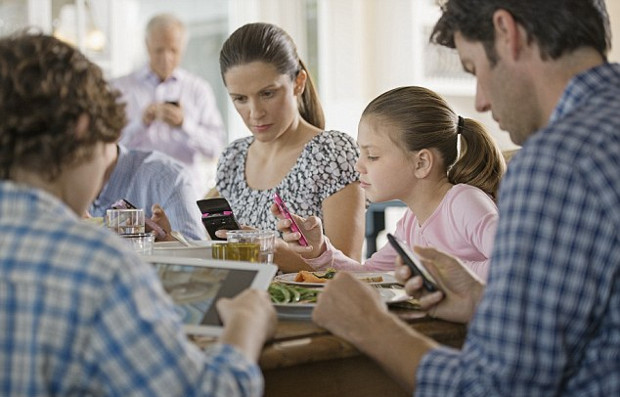
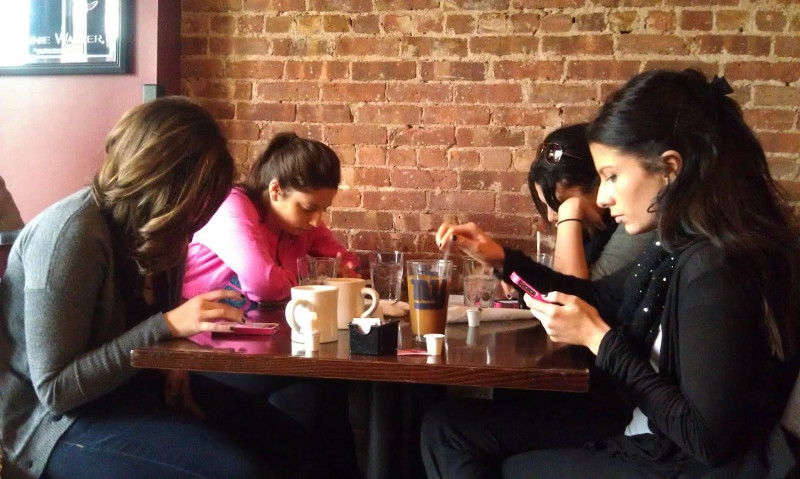
Have you started thinking about new year's resolutions for 2016? Back to the gym or giving up sugary drinks? Many new year's resolutions have a health theme. Unless you have a heroin addiction, there may not be anything else in your life that is more addictive and has potentially more impact on your health and quality of life than your mobile phone. Almost every week there is some new report about the negative impact of phone use on rest or leisure time. Children are particularly at risk and evidence strongly suggests their grades at school are tanking as a consequence. Can you imagine your life changing for the better if you switched off your mobile phone or left it at home for one day per week in 2016? If you have children, can you think of anything more powerful than the example you set yourself to help them stay in control of their phones? Children have a remarkable ability to emulate the bad habits they observe in their parents. Are you in control? Turning it off is a powerful act of showing who is in charge. If you feel you can't live without it, then you are putting your life in the hands of the people who expect an immediate answer of their calls, your phone company and the Silicon Valley executives who make all those apps you can't stop using. As security expert Jacob Appelbaum puts it, cell phones are tracking devices that also happen to make phone calls. Isn't that a chilling thought to reflect on the next time you give one as Christmas gift? For your health, your children and your bank balance Not so long ago we were having lunch in a pizza restaurant in Luzern, a picturesque lakeside town at the base of the Swiss Alps. Luzern is a popular first stop for tourists from all around the world. A Korean family came along and sat at the table next to us. After ordering their food, they all immediately took out their mobile devices and sat there in complete silence, the mother and father, a girl of eight and a boy of five, oblivious to the world around them and even each other, tapping and swiping for the next ten minutes until their food arrived. We wanted to say hello to them, I joked that I should beep first, initiating communication with the sound of a text message notification. Is this how all holidays will be in future? Is it how all families will spend time together? Can you imagine your grandchildren and their children sharing a meal like this in the year 2050 or beyond? Which gadgets does Bond bring to Switzerland? On Her Majesty's Secret Service is one of the more memorable Bond movies for its spectacular setting in the Swiss Alps, the location now transformed into a mountain-top revolving restaurant visited by thousands of tourists every day with a comfortable cable car service and hiking trails with breathtaking views that never become boring. Can you imagine Bond leaving behind his gun and his skis and visiting Switzerland with a smartphone instead? Eating a pizza with one hand while using the fingertips of the other to operate an app for making drone strikes on villains, swiping through Tinder for a new girl to replace the one who died (from boredom) in his previous "adventure" and letting his gelati melt while engrossed in a downhill ski or motorcycle game in all the glory of a 5.7" 24-bit colour display? Of course its absurd. Would you want to live like that yourself? We see more and more of it in people who are supposedly in Switzerland on the trip of a lifetime. Would you tolerate it in a movie? The mobile phone industry has paid big money to have their technology appear on the silver screen but audience feedback shows people are frustrated with movies that plaster the contents of text messages across the screen every few minutes; hopefully Bond movies will continue to plaster bullets and blood across the screen instead. Time for freedom How would you live for a day or a weekend or an entire holiday without your mobile phone? There are many small frustrations you may experience but the biggest one and the indirect cause of many other problems you will experience may be the inability to tell the time. Many people today have stopped wearing a watch, relying instead upon their mobile phone to tell the time. Without either a phone or a watch, frustration is not far away. If you feel apprehension just at the thought of leaving your phone at home, the lack of a watch may be a subconcious factor behind your hesitation. Trying is better than reading Many articles and blogs give opinions about how to buy a watch, how much to spend and what you can wear it with. Don't spend a lot of time reading any of it, if you don't know where to start, simply go down to the local high street or mall and try them. Start with the most glamorous and expensive models from Swiss manufacturers, as these are what everything else is compared to and then perhaps proceed to look more widely. While Swiss brands tend to sell through the stores, vendors on Amazon and eBay now distribute a range of watches from manufacturers in Japan, China and other locations, such as Orient and Invicta, at a fraction of the price of those in the stores. You still need to try a few first to identify your preferred style and case size though. Google can also turn up many options for different budgets.

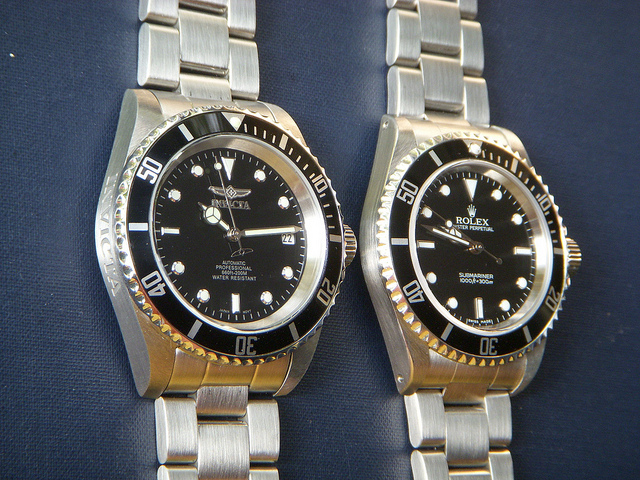
Copying or competition? Similarity of Invicta (from Amazon) and Rolex Submariner You may not know whether you want a watch that is manually wound, automatically wound or battery operated. Buying a low-cost automatic model online could be a good way to familiarize yourself before buying anything serious. Mechanical watches have a smoother and more elegant second-hand movement and will survive the next Carrington event but may come to grief around magnets - a brief encounter with a low-cost de-gausser fixes that. Is it smart to buy a smart watch? If you genuinely want to have the feeling of complete freedom and control over technology, you may want to think twice about buying a smart watch. While it may be interesting to own and experiment with it some of the time, being free from your phone means being free from other electronic technology too. If you do go for a smart watch (and there are many valid reasons for trying one some of the time), maybe make it a second (or third) watch. Smart watches are likely to be controversial for some time to come due to their impact in schools (where mobile phones are usually banned) and various privacy factors. Help those around you achieve phone freedom in 2016 There will be further blogs on this theme during 2016, each looking at the pressures people face when with or without the mobile phone. As a developer of communications technology myself, you may be surprised to see me encouraging people not to use it every waking minute. Working on this technology makes me more conscious of its impact on those around me and society in general. A powerful factor to consider when talking about any communications technology is the presence of peer pressure and the behavior of those around you. Going phone-free may involve helping them to consider taking control too. Helping them out with a new watch as a gift (be careful to seek advice on the style that they are likely to prefer or ensure the purchase can be exchanged) may be an interesting way to help them engage with the idea and every time they look at the time, they may also be reminded of your concern for their freedom.

6 January 2016

Stig Sandbeck Mathisen: Thoughts on Puppet 4 related packages

It s been a while since I ve looked at the puppet 4 packaging. During this time, a lot of things have happened.

puppet Puppet 4 is out. I ve done some packaging tests, and they are promising.

puppet-agent Puppet Labs released puppet-agent recently, with instructions. It looks like an umbrella project for building and bundling puppet, facter, augeas, ruby, and everything else to install on puppet managed nodes. It downloads a lot of software over HTTP or git, and verifies at least some of it with md5 checksums. I don t think this is needed for Debian.

puppet-server This really needs packaging. There are probably lots of dependencies not packaged yet. I am not familiar with any of the build tools.

puppetdb Needs packaging. There are probably lots of dependencies not packaged yet. I am not familiar with any of the build tools.

vim-puppet This has moved outside the puppet repository. Both puppetlabs and rodjek have vim modes for puppet. I ve grown very fond of rodjek s vim-puppet.

puppet-el This has moved outside the puppet repository. Both puppetlabs and lunaryorn have emacs modes for puppet.

puppet modules There are a lot of puppet modules in the team VCS.

Steinar H. Gunderson: IPv6 non-alternatives: DJB's article, 13 years later

With the world passing 10% IPv6 penetration over the weekend, we see the same old debates coming up again; people claiming IPv6 will never happen (despite several years now of exponential growth!), and that if they had only designed it differently, it would have been all over by now. In particular, people like to point to a 2002 3 article by D. J. Bernstein, complete with rants about how Google would never set up useless IPv6 addresses (and then they did that in 2007 I was involved). It's difficult to understand exactly what the article proposes since it's heavy on calling people idiots and light on actual implementation details (as opposed to when DJB's gotten involved in other fields; e.g. thanks to him we now have elliptical curve crypto that doesn't suck, even if the reference implementation was sort of a pain to build), but I will try to go through it nevertheless and show how I cannot find any way it would work well in practice. One thing first, though: Sorry, guys, the ship has sailed. Whatever genius solution DJB may have thought up that I'm missing, and whatever IPv6's shortcomings (they're certainly there), IPv6 is what we have. By now, you can not expect anything else to arise and take over the momentum; we will either live with IPv6 or die with IPv4. So, let's see what DJB says. As far as I can see, his primary call is for a version of IPv6 where the address space is an extension of the IPv4 space. For sake of discussion, let's call that IPv4+ , although it would share a number of properties with IPv6. In particular, his proposal requires changing the OS and other software on every single end host out there, just as IPv6; he readily admits that and outlines how it's done in rough terms (change all structs, change all configuration files, change all databases, change all OS APIs, etc.). From what I can see, he also readily admits that IPv4 and IPv4+ hosts cannot talk to each other, or more clearly, we cannot start using the extended address space before almost everybody has IPv4+ capable software. (E.g., quote: Once these software upgrades have been done on practically every Internet computer, we'll have reached the magic moment: people can start relying on public IPv6 addresses as replacements for public IPv4 addresses. ) So, exactly how does the IPv4 address space fit into the IPv4+ address space? The article doesn't really say anything about this, but I can imagine only two strategies: Build the IPv4+ space around the IPv4 space (ie., the IPv4 space occupies a little corner of the IPv4+ space, similar to how v4-mapped addresses are used within software but not on the wire today, to let applications do unified treatment of IPv4 addresses as a sort of special IPv6 address), or build it as a hierarchical extension. Let's look at the former first; one IPv4 address gives you one IPv4+ addresses. Somehow this seems to give you all the disadvantages of IPv4 and all the disadvantages of IPv6. The ISP is not supposed to give you any more IPv4+ addresses (or at least DJB doesn't want to contact his ISP about more also saying that the fact that automatic address distribution does not change his argument), so if you have one, you're stuck with one. So you still need NAT. (DJB talks about proxies , but I guess that the way things evolved, this either actually means NAT, or it talks about the practice of application-level proxies such as Squid or SOCKS proxies to reach the Internet, which really isn't commonplace anymore, so I'll assume for the sake of discussion it means NAT.) However, we already do NAT. The IPv4 crunch happened despite ubiquitous NAT everywhere; we're actually pretty empty. So we will need to hand out IPv4+ addresses at the very least to new deployments, and also probably reconfigure every site that wants to expand and is out of IPv4 addresses. ( Site here could mean any organizational unit, such as if your neighborhood gets too many new subscribers for your ISP's local addressing scheme to have enough addresses for you.) A much more difficult problem is that we now need to route these addresses on the wire. Ironically, the least clear part of DJB's plan is step 1, saying we will extend the format of IP packets to allow 16-byte addresses ; how exactly will this happen? For this scheme, I can only assume some sort of IPv4 option that says the stuff in the dstaddr field is just the start and doesn't make sense as an IPv4 address on its own; here are the remaining 12 bytes to complete the IPv4+ address . But now your routers need to understand that format, so you cannot do with only upgrading the end hosts; you also need to upgrade every single router out there, not just the end hosts. (Note that many of these do routing in hardware, so you can't just upgrade the software and call it a day.) And until that's done, you're exactly in the same situation as with IPv4/IPv6 today; it's incompatible. I do believe this option is what DJB talks about. However, I fail to see exactly how it is much better than the IPv6 we got ourselves into; you still need to upgrade all software on the planet and all routers on the planet. The benefit is supposedly that a company or user that doesn't care can just keep doing nothing, but they do need to care, since they need to upgrade 100% of their stuff to understand IPv4+ before we can start even deploying it alongside IPv4 (in contrast with IPv6, where we now have lots of experience in running production networks). The single benefit is that they won't have to renumber until they need to grow, at which point they need to anyway. However, let me also discuss the other possible interpretation, namely that of the IPv4+ address space being an extension of IPv4, ie. if you have 1.2.3.4 in IPv4, you have 1.2.3.4.x.x.x.x or similar in IPv4+. (DJB's article mentions 128-bit addresses and not 64-bit, though; we'll get to that in a moment.) People keep bringing this up, too; it's occasionally been called BangIP (probably jokingly, as in this April Fool's joke) due to the similarity with how explicit mail routing would work before SMTP became commonplace. I'll use that name, even though others have been proposed. The main advantage of BangIP is that you can keep your Internet core routing infrastructure. One way or the other, they will keep seeing IPv4 addresses and IPv4 packets; you need no new peering arrangements etc.. The exact details are unclear, though; I've seen people suggest GRE tunneling, ignoring problems they have through NAT, and I've seen suggestions of IPv4 options for source/destination addresses, also ignoring that someting as innocious as setting the ECN bits has been known to break middleboxes left and right. But let's assume you can pull that off, because your middlebox will almost certainly need to be the point that decapsulates BangIP anyway and converts it to IPv4 on the inside, presumably with a 10.0.0.0/8 address space so that your internal routing can keep using IPv4 without an IPv4+ forklift upgrade. (Note that you now lose the supposed security benefit of NAT, by the way, although you could probably encrypt the address.) Of course, your hosts will need to support IPv4+ still, and you will need some way of communicating that you are on the inside of the BangIP boundary. And you will need to know what the inside is, so that when you communicate on this side, you'll send IPv4 and not IPv4+. (For a home network with no routing, you could probably even just do IPv4+ on the inside, although I can imagine complications.) But like I wrote above, experience has shown us that 32 extra bits isn't enough. One layer of NAT isn't doing it, we need two. You could imagine the inter-block routability of BangIP helping a fair bit here (e.g., a company with too many machines for 10.0.0.0/8 could probably easily get more addresses for more external IPv4 addresses, yielding 10.0.0.0/8 blocks), but ultimately, it is a problem that you chop the Internet off in two distinct halves that work very differently. My ISP will probably want to use BangIP for itself, meaning I'm on the outside of the core; how many of those extra bits will they allocate for me? Any at all? Having multiple levels of bang sounds like pain; effectively we're creating a variable-length address. Does anyone ever want that? From experience, when we're creating protocols with variable-length addresses, people just tend to use the maximum level anyway, so why not design it with 128-bit to begin with? (The original IP protocol proposals actually had variable-length addresses, by the way.) So we can create our 32/96 BangIP , where the first 32 bits are for the existing public Internet, and then every IPv4 address gives you a 2^96 addresses to play with. (In a sense, it reminds me of 6to4, which never worked very well and is now thankfully dead.) However, this makes the inside/outside-core problem even worse. I now need two very different wire protocols coexisting on the Internet; IPv4+ (which looks like regular IPv4 to the core) for the core, and a sort of IPv4+-for-the-outside (similar to IPv6) outside it. If I build a company network, I need to make sure all of my routers are IPv4+-for-the-outside and talk that, while if I build the Internet core, I need to make sure all of my connections are IPv4 since I have no guarantee that I will be routable on the Internet otherwise. Furthermore, I have a fixed prefix that I cannot really get out of, defined by my IPv4 address(es). This is called hierarchical routing , and the IPv6 world gave it up relatively early despite it sounding like a great idea at first, because it makes multihoming a complete pain: If I have an address 1.2.3.4 from ISP A and 5.6.7.8 from ISP B, which one do I use as the first 32 bits of my IPv4+ network if I want it routable on the public Internet? You could argue that the solution for me is to get an IPv4 PI netblock (supposedly a /24, since we're not changing the Internet core), but we're already out of those, which is why we started this thing to begin with. Furthermore, if the IPv4/IPv4+ boundary is above my immediate connection to the Internet (say, ISP A doesn't have an IPv4 address, just IPv4+), I'm pretty hosed; I cannot announce an IPv4 netblock in BGP. The fact that the Internet runs on largely the same protocol everywhere is a very nice thing; in contrast, what is described here really would be a mess! So, well. I honestly don't think it's as easy to just do extension instead of alternative when it comes to the address spaces. We'll just need to deal with the pain and realize that upgrading the equipment and software is the larger part of the job anyway, and we'll need to do that no matter what solution we go with. Congrats on reaching 10%! Now get to work with the remaining 90%.

Daniel Pocock: Want to use free software to communicate with your family in Christmas 2016?

Was there a friend or family member who you could only communicate with using a proprietary, privacy-eroding solution like Skype or Facebook this Christmas? Would you like to be only using completely free and open solutions to communicate with those people next Christmas? Developers Even if you are not developing communications software, could the software you maintain make it easier for people to use "sip:" and "xmpp:" links to launch other applications? Would this approach make your own software more convenient at the same time? If your software already processes email addresses or telephone numbers in any way, you could do this. If you are a web developer, could you make WebRTC part of your product? If you already have some kind of messaging or chat facility in your website, WebRTC is the next logical step. If you are involved with the Debian or Fedora projects, please give rtc.debian.org and FedRTC.org a go and share your feedback. If you are involved with other free software communities, please come to the Free-RTC mailing list and ask how you can run something similar. Everybody can help Do you know any students who could work on RTC under Google Summer of Code, Outreachy or any other student projects? We are particularly keen on students with previous experience of Git and at least one of Java, C++ or Python. If you have contacts in any universities who can refer talented students, that can also help a lot. Please encourage them to contact me directly. In your workplace or any other organization where you participate, ask your system administrator or developers if they are planning to support SIP, XMPP and WebRTC. Refer them to the RTC Quick Start Guide. If your company web site is built with the Drupal CMS, refer them to the DruCall module, it can be installed by most webmasters without any coding. If you are using Debian or Ubuntu in your personal computer or office and trying to get best results with the RTC and VoIP packages on those platforms, please feel free to join the new debian-rtc mailing list to discuss your experiences and get advice on which packages to use. Everybody is welcome to ask questions and share their experiences on the Free-RTC mailing list. Please also come and talk to us at FOSDEM 2016, where RTC is in the main track again. FOSDEM is on 30-31 January 2016 in Brussels, attendance is free and no registration is necessary. This mission can be achieved with lots of people making small contributions along the way.

4 January 2016

Bernd Zeimetz: open-vm-tools updated

In January 2014 the open-vm-tools package was orphaned and I took the chance to take over the maintenance. Unfortunately the package is still not 100% in the shape I d like to see it, but I m getting closer. I have to say Thank You for a lot of good bug reports, especially for those use cases which are hard to test/reproduce for me (running Debian in a Windows-based VMware Workstation Player for example .). At conova communications GmbH, the company I work for, we are using the package on all of our Debian VMs, both for customer and internal use. It is essential for us to have properly working open-vm-tools - not only to be able to shutdown the VM from VMware vCenter, but also because tools like vSphere Data Protection and Veeam depend on it. Good thing is that I can work on and test the package at work and breakages are detected early and fast normally. Getting a good contact to the VMware upstream was easy and the developers there are helpful and reply pretty fast to their emails. Also as it seems there are finally real commits showing up in the open-vm-tools github repository again, not only huge single commits with a full release. It is not only nice to see that they are moving into the right direction again, but also this is really helpful in fixing (urgent) bugs before the next release of open-vm-tools - or to backport a fix to the versoin in stable/oldstable. Since a few days we have open-vm-tools 10.0.5-3227872 in If you are using VMware ESX 5.5 or newer, you should upgrade to the backports versions. Same if you use a recent VMware player version. Please note that since 10.0.0 the open-vm-dkms package is only necessary if you need the legacy vmxnet module. This is only the case if you are using very old VM hardware versions. vmxnet3 is shipped in the Debian kernel, so you don t need to compile extra modules to use it. The vmhgfs module was replaced by a fuse-based implementation. If you d like to help maintaining the package, please send bugs/patches via the Debian BTS or even better - send pull requests for pkg-open-vm-tools. The repository is mirrored to git.bzed.at in case you want to avoid github.

Mike Gabriel: MATE 1.12 landed in Debian unstable

Yesterday, I did a bundle upload of all MATE 1.12 related packages to Debian unstable. Packages are currently building for the 22 architectures supported by Debian, build status can be viewed on the DDPO page of the Debian MATE Packaging Team [1] Again a big thanks to the packaging team. Martin Wimpress amongst others did a fabulous job in bumping all packages towards the 1.12 release series before the Christmas holidays. Over the holidays, I was able to review his work (99% perfect) and upload all binary packages to a staging repository. @Martin Wimpress: It is really time that we make a DM (Debian Maintainer) out of you!!! After testing all MATE 1.12 packages on a Debian unstable system, I decided to do a bundle upload yesterday. Lessons learned about bundling Debian uploads It absolutely makes sense to hold back package uploads of a project like the MATE desktop until all relevant packages are reviewed, pre-built and tested. When releasing MATE packages via the team's packaging Git [2], there are normally two actions to be taken on a package release: When reviewing so many Git projects, it is always problematic that people commit something else during the review phase. Especially, if the review work involves many packages (i.e., Git packaging repos) and requires several days or even weeks to get finished. read more

3 January 2016

Russ Allbery: control-archive 1.7.0

First new release in a while. There haven't been a lot of changes to Usenet hierarchies. The primary change is more aggressive dropping of control messages for reserved hierarchies, mostly to suppress pointless email to news administrators. There were also the following hierarchy updates: These changes are already live on the ftp.isc.org control.ctl file. You can get the latest version from the control-archive distribution page.

Russ Allbery: podlators 4.04

Now that I've fixed the major test suite problems with podlators, failure reports are now (mostly) useful. There's still the occasional failure to create a directory for temporary files, which I think is just a problem with the testing system, but Windows test failures revealed an actual test suite bug. This release also merges the changes made for merging podlators into blead Perl, which were relatively minor, and changes the package metadata to point to GitHub as the repository. That seems to be the growing convention in the Perl community and makes it easier for people to submit pull requests. I'm still maintaining my own public repository, but Git makes it easy to replicate things in multiple places. (Bug tracking will remain in the CPAN RT.) You can get the latest release from the podlators distribution page.

Benjamin Mako Hill: Access Without Empowerment (LibrePlanet 2015 Keynote)

At LibrePlanet 2015 (the FSF s annual conference), I gave a talk called Access Without Empowerment as one of the conference keynote addresses. As I did for my 2013 LibrePlanet talk, I ve edited together a version that includes the slides and I ve posted it online in WebM and on YouTube.
Here s the summary written up in the LibrePlanet program:
The free software movement has twin goals: promoting access to software through users freedom to share, and empowering users by giving them control over their technology. For all our movement s success, we have been much more successful at the former. I will use data from free software and from several related movements to explain why promoting empowerment is systematically more difficult than promoting access and I will explore how our movement might address the second challenge in the future.
In related news, registration is open for LibrePlanet 2016 and that it s free for FSF members. If you re not an FSF member, the FSF annual fundraiser is currently going on so now would be a great time to join.

2 January 2016

Steve Kemp: Restoring my system .. worked

A while back I wrote about some issues with converting a two-disk RAID system to a one-disk system, but just to recap: In the end we bought a small form-factor PC, with only a single drive and I moved one of the two drives from the old machine into it. Then converted it to run happily with only a single drive, and not email every day to say "device missing". So there things stood, we had a desktop with a single drive, and I ensured that I took full daily backup via attic. Over Chrismas the two-year old drive failed. To the extent I couldn't even get it to be recognized by the BIOS, and thus couldn't pull data off it. Time to test my backups in anger! I bought a new drive, installed a minimal installation of the Jessie release of Debian onto the system, and then ran:
 cd /
 .. restore latest backup ..
Two days later I'd pulled 1.3Tb over the network, and once I fixed up grub, /etc/fstab, and a couple of niggles it all just worked. Rebooted to make sure the temporary.home hostname, etc, was all gone and life was good. Restored backup! No errors! No data-loss! Perfect! The backup-script I use every day was very very good at making sure nothing was missed:
attic create --stats --checkpoint-interval=7200 attic@$ remote :/attic/storage::$ host -$(date +%Y-%m-%d-%H)
  --exclude=/proc      \
  --exclude=/sys       \
  --exclude=/run       \
  --exclude=/dev       \
  --exclude=/tmp       \
  --exclude=/var/tmp   \
  --exclude=/var/log   \
  /
In other news I published my module for controlling the new smart lights I've bought

1 January 2016

Russ Allbery: 2015 Book Reading in Review

2015 was another very busy year, but one of stabilization, rebuilding, and recovery. I got through the ramp-up period with my new job, found a better role inside the company for my personal talents and preferences, and ended the year on a professional high note. I also moved, to a place I like much better. It was a year for taking things as they come, focusing on priorities, letting other things slip, and being realistic about how much I can do. All of that, plus quite a lot of company, a business trip, and a few other unexpected distractions, meant less reading than I would have preferred. However, I did catch up completely on review writing, which is another happy sign of stabilization. Reviews came in spotty bursts, but they did come. The only explicit reading goal I'm making for 2016 is to read more than I did in 2015. I'm still working out the best priorities and schedule for me, and finding the best work/life balance points, so a predictable reading schedule will have to wait a while longer. The below statistics are confined to the books I reviewed in 2015, but thanks to significant catch-up work, I've only read one book that I have not yet reviewed (and I finished that one on December 31st). That book will be counted in 2016. Once again, the year saw two 10 out of 10 books, and once again, my favorite book of the year was written by Ann Leckie. The conclusion of the Imperial Radch trilogy, Ancillary Mercy, is as good or better than the start. The second book of the trilogy, Ancillary Sword, was also among my 2015 reviews and got 9 out of 10. I highly recommend the entire trilogy, beginning with Ancillary Justice (my book of the year in 2014), to anyone who hasn't read it. The second 10 out of 10 was non-fiction: Randall Munroe's What If? collection, featuring some material from the web site feature that accompanies xkcd and some original material. These are longer essays exploring interesting bits of science, math, and guesswork in the context of hypothetical questions that usually become surprisingly destructive. As the review says, try a few samples from the web site and see if this is your thing. I loved it. Despite my continuing low reading totals, this was a year full of fiction stand-outs. Becky Chambers's The Long Way to a Small, Angry Planet was the surprise of the year for me: a heart-warming, delightful story of chosen family. Jo Walton's My Real Children was less of a surprise because I already knew she is an excellent writer, but it was probably the best-written book I read all year. In turns sad, thoughtful, and determined, it's slice-of-life fiction so good that it overcame my normal dislike of that subject matter. Other fiction highlights are parts of series: the first two Steerswomen books by Rosemary Kirstein (The Steerswoman and The Outskirter's Secret), which dance between fantasy and scientific discovery, and Seanan McGuire's One Salt Sea, the best of all the October Daye books I've read. In non-fiction, the other book that stands out is Jenny Lawson's Let's Pretend This Never Happened. This combination of memoir and stand-up comedy in book form is one of the funniest things I've read, and it mixes that humor with self-awareness and generous openness. It's a book about being a little crazy and a lot anxious, finding ways to cope by laughing at yourself, and inviting the rest of the world to join in. Finally, Sydney Padua's The Thrilling Adventures of Lovelace and Babbage straddles the line between fiction and non-fiction, but certainly deserves a place in the year-end round-up. Full of great art, humor, steampunk, footnotes galore, and numerous forms of geekery, it's a collection I've been waiting for since Padua's very occasional comic got its moment of Internet fame. The full analysis includes some additional personal reading statistics, probably only of interest to me.

Bdale Garbee: Term Limited

I woke up this morning and realized that for the first time since 17 April 2001, I am no longer a member of the Debian Technical Committee. My departure from the committee is a consequence of the Debian General Resolution "limiting the term of the technical committee members" that was passed amending the Debian Constitution nearly a year ago. As the two longest-serving members, both over the term limit, Steve Langasek and I completed our service yesterday. In early March 2015, I stepped down from the role of chairman after serving in that role for the better part of a decade, to help ensure a smooth transition. Don Armstrong is now serving admirably in that role, I have the utmost respect for the remaining members of the TC, and the process of nominating replacements for the two now-vacant seats is already well underway. So, for the Debian project as a whole, today is really a non-event... which is exactly as it should be! Debian has been a part of my life since 1994, and I sincerely hope to be able to remain involved for many years to come!

Thorsten Alteholz: My Debian Activities in December 2015

FTP assistant Due to Christmas, I only marked 254 packages for accept and rejected 17 of them. I had to send 14 emails to maintainers. Squeeze LTS This was my eighteenth month that I did some work for the Squeeze LTS initiative, started by Raphael Hertzog at Freexian. As other members of the LTS team had to give back some hours of their workload, this month my initial workload of 18.25h had been increased to 21.25h. Altogether I uploaded those DLAs: I also started to work on CVEs for packages t-coffee and pitivi, only to recognize that the versions in Squeeze are not affected. Further I prepared patches for passenger and srtp but I could not test them yet, so an upload will be in January. This month I also experienced something strange. Due to the upload of the new version of mysql, I had to process a package for squeeze-lts in NEW. I seldom see a package, that creates so much red output from lintian. I assume this always happens when an old package will be checked by the latest lintian and is a good sign for all the development within Debian. I also tested Raphaels patch for #796784 and could confirm that everything works as expected. Unfortunately the php5 upload must be delayed until Januar. This month I also had another week of frontdesk duties. Other stuff The Advent season is over and the Debian Med Advent Calendar is full to bursting. The incredible number of 150 bugs have been closed this year! Due to the GSL transition a new upload of all meep packages had to be done and all in all I could close #748822, #807210, #807212, #807213, #807214, #807215 and #807747.

31 December 2015

Chris Lamb: Free software activities in December 2015

Here is my monthly update covering a large part of what I have been doing in the free software world (previously):
Debian My work in the Reproducible Builds project was also covered in more depth in Lunar's weekly reports (#31, #32, #33, #34).
LTS

This month I have been paid to work 12 hours on Debian Long Term Support (LTS). In that time I did the following:
  • Issued DLA 363-1 for libphp-phpmailer fixing a header injection vulnerability.
  • Issued DLA 365-1 for foomatic-filters correcting a shell injection vulnerability.
  • Issued DLA 369-1 for pygments fixing an issue shell injection vulnerability.
  • Issued DLA 374-1 for cacti to fix an SQL injection vulnerability.
  • Did some futher investigation of CVE-2011-5325 in busybox.

Uploads
  • python-django (1.9) New upstream release.
  • redis (3.0.6) New upstream stable release. I additionally backported this package to Debian stable.
  • redis (3.2~rc1) Uploaded upstream's "testing/next" branch to experimental for testing.
  • gunicorn (19.4.1) New upstream release.


Patches contributed

I also filed FTBFS bugs against acpid, android-platform-frameworks-base, antlr3, artemis, beignet, bisonc++, bobcat, bustle, cargo, checkbox-ng, code2html, cplay, datanommer.commands, dcmtkpp, debci, diffutils, diod, django-restricted-resource, docker-libkv, doomsday, dvdauthor, dwww, elasticsearch, elki, flask-script, freeipa, fso-frameworkd, funny-manpages, ggcov, ghc-mod, gmpc-plugins, gparted, gs-collections, guacamole-server, guncat, haskell-concrete-typerep, haskell-geniplate, haskell-nats, haskell-x509-util, hawtbuf, heimdal, htsjdk, inspircd, jboss-xnio, jenkins-winstone, jpeginfo, jruby-openssl, kaffeine, kdbg, ktp-accounts-kcm, kuser, libcommons-cli-java, libcommons-openpgp-java, libconfig-model-lcdproc-perl, libdata-faker-perl, libexplain, libgettext-commons-java, libgtk2-ex-printdialog-perl, libmoops-perl, libnet-frame-perl, libsendmail-milter-perl, libupnp, libuv, libvpx, liwc, m4, maven2, meep-mpich2, nagios-plugin-check-multi, natlog, netpipe, ocserv, ogre-1.8, orthanc-dicomweb, perspectives-extension, php-mail, php-pinba, phpseclib, pkg-haskell-tools, plastimatch, plexus-compiler, plexus-compiler-1.0, python-acme, python-crontab, python-cs, python-csscompressor, python-debian, python-distutils-extra, python-django-compressor, python-django-openstack-auth, python-django-tagging, python-pygit2, python-pyramid, python-pywcs, python-releases, python-shade, python-statsd, python-tasklib, python-tasklib, python-webm, python-websockets, regina-normal, rinetd, roboptim-core, rpm2html, rpm2html, ruby-factory-girl, ruby-fogbugz, ruby-i18n-inflector, ruby-loofah, ruby-protected-attributes, ruby-rack-contrib, ruby-rufus-scheduler, ruby-sanitize, ruby-sidetiq, ruby-sinatra, scsh-0.6, shogun, sleekxmpp, slugimage, spatial4j, sqwebmail-de, trac-announcer, ttt, txaws, umbrello, wine-gecko-2.21, xboxdrv, xfonts-wqy, xserver-xorg-video-openchrome, yorick & yoshimi.

Rapha&#235;l Hertzog: My Free Software Activities in December 2015

My monthly report covers a large part of what I have been doing in the free software world. I write it for my donators (thanks to them!) but also for the wider Debian community because it can give ideas to newcomers and it s one of the best ways to find volunteers to work with me on projects that matter to me. Debian LTS This month I have been paid to work 21.25 hours on Debian LTS. During this time I worked on the following things: Distro Tracker I put a big focus on tracker.debian.org work this month. I completed the switch of the mail interface from packages.qa.debian.org to tracker.debian.org and I announced the change on debian-devel-announce. The changes resulted in a few problems that I quickly fixed (like #807073) and some other failures seen only by me and that were generated by weird spam messages (did you know that a subject can t have a newline character but that it can be encoded and folded over multiple lines?). Related to that I fixed some services so that they send their mails to tracker.debian.org directly instead of relying on the old emails (they get forwarded for now but it would be nice to be able to get rid of that forward). I updated (with the help of Lucas Nussbaum) the service that forwards the Launchpad bugs to the tracker, I sent a patch to update the @packages.debian.org aliases (not yet applied), I updated the configuration of all git commit notice scripts in the Alioth collab-maint and python-modules project (many remain to be done). I asked Ubuntu s Merge-O-Matic to use the new emails as well (see LP 1525497). DAK and the Debian BTS still have to be updated, as of yet nobody reacted to my announce last but not least I updated many wiki pages which duplicated the instructions to setup the commit notice sent to the PTS. While on a good track I opted to tackle the long-standing RC bug that was plaguing tracker.debian.org (#789183), so I updated the codebase to rely on Twitter s bootstrap v4 instead of v2. I had to switch to something else for the icons since glyphicons is no longer provided as part of bootstrap and the actual license for the standalone version was not suitable for use. I opted for Github s Octicons. I made numerous little improvements while doing that (closing some bugs in the process) and I believe that the result is more pleasant to use. I also did a lot of bug triage and fixed a few small issues like the incomplete architecture list (#793547), or fixing a page used only by people with javascript disabled that was not working. Or the invalid links for packages still using CVS (ugh, see #561228). Misc packaging Django. After having added DEP-8 tests (as part of my LTS work, see above), I discovered that the current version in unstable did not pass its test suite so I filed the issue upstream (ticket 26016) and added the corresponding patch. And I encouraged others to update python-bcrypt in Debian to a newer version that would have worked with Django 1.9 (see #803096). I also fixed another small issue in Django (see ticket 26017 with my pull request that got accepted). I asked the release managers to consider accepting the latest 1.7.x version in jessie (see #807654) but I have gotten zero answer so far. And I m not the only one waiting an answer. It s a bit of a sad situation we still have a few weeks until the next point release but for once I do it in advance and I would love to have timely feedback. Last but not least, I started the maintaining the current LTS release (1.8.x) in jessie-backports. Tryton. I upgraded to Tryton 3.8 and discovered an issue that I filed in #806781. I sponsored 5 new tryton modules for Matthias Behrle (who is DM) as well as one security upload (for CVE-2015-0861). Debian Handbook. I uploaded a new version to Debian Unstable and requested (to the release managers) the permission to upload a backport of it to jessie so that jessie has a version of the package that documents jessie and not wheezy contrary to my other Django request, this one should be non-controversial but I also have had zero answer so far, see #807515. Misc. I filed #808583 when sbuild stopped working with Perl 5.22. I handled #807860 on publican, I found the corresponding upstream ticket and discovered a work around with the help of upstream (see here). Kali related work I reported a bug to #debian-apt about apt miscalculating download size (ending up with 18 EB!) which resulted in a fix here in version 1.1.4. Installing a meta-package that needed more than 2GB was no longer possible without this fix and we have a kali-linux-all metapackage in that situation that gets regularly installed in a Jenkins test. I added captcha support to Distro Tracker and enabled this feature on pkg.kali.org. I filed #808863 against uhd-host because it was not possible to install the package in a systemd-nspawn s managed chroot where /proc is read-only. And we started using this to test dist-upgrade from one version of Kali to the next Thanks See you next month for a new summary of my activities.
No comment Liked this article? Click here. My blog is Flattr-enabled.

30 December 2015

Bits from Debian: Debian lamenta el dec s de l'Ian Murdock

Ian Murdock Amb el cor compungit, Debian lamenta la p rdua d'Ian Murdock, ferm partidari del programari lliure i de codi obert, pare, fill i l'"ian" a Debian. L'Ian va comen ar el projecte Debian l'agost de 1993, i va publicar les primeres versions m s tard el mateix any. Debian es convertiria en el sistema operatiu universal pel m n, que funciona en tot tipus de dispositius, des de sistemes encastats fins a l'estaci especial. L'Ian es va centrar en crear una distribuci i una cultura de comunitat que fessin el correcte, ticament o t cnica. Publicar quan estigui a punt i la ferma posici sobre la llibertat de programari s n les regles d'or en el m n del programari lliure i de codi obert. La seva devoci per fer el correcte va guiar la seva feina, tant a Debian com els seg ents anys, sempre treball per assolir el millor futur possible. El somni de l'Ian est viu, la comunitat de Debian continua incre blement activa, amb milers de desenvolupadors que treballen innumerables hores per proporcionar un sistema operatiu segur i fiable. Els pensaments de la comunitat de Debian s n amb la fam lia de l'Ian en aquests moments tant durs. La seva fam lia ens ha demanat privacitat en aquests moments dif cils i volem respectar-ho. Des de Debian i des de la comunitat de Linux en general podem enviar mostres de condol a in-memoriam-ian@debian.org; seran guardades i arxivades.

Next.

Previous.