
Search Results: "ag"

25 June 2008

Adrian von Bidder: Sometimes providers do get better...

Christian, I used to block quite aggressively (essentially blocking all IPs sending me spam for a few months) and remember seeing free.fr very, very often. Apparently this was before the block outgoing port 25 policy — I just had a grep through my log and see almost no spam coming in from free.fr. So, as I've said just recently, this is a note to all ISP: please, please, please block port 25! (ISP who don't offer unblocking will obviously lose the techie clients, but that's their own thing to decide...)

24 June 2008

Clint Adams: Eli and the wolves of Bristol

The West Virginian is huddled over his bong, swirling the ice cubes around his glass of cream sherry. There is a montage on the television, set to some factory-produced pop song sung by a no-talent teen who was thrust into major stardom with the help of comb filters and clever marketing. He is not watching the montage; he is thinking about Chris Wallace and nepotism. He will stand in the end.

Russell Coker: Links June 2008

Paul Graham has recently published an essay titled How To Disagree [1]. One form that he didn’t mention is to claim that a disagreement is a matter of opinion. Describing a disagreement about an issue which can be proved as a matter of opinion is a commonly used method of avoiding the need to offer any facts or analysis. Sam Varghese published an article about the Debian OpenSSL issue and quoted me [2]. The Basic AI Drives [3] is an interesting papar about what might motivate an AI and how AIs might modify themselves to better achieve their goals. It also has some insights into addiction and other vulnerabilities in human motivation. It seems that BeOS [4] is not entirely dead. The Haiku OS project aims to develop an open source OS for desktop computing based on BeOS [5]. It’s not nearly usable for end-users yet, but they have vmware snapshots that can be used for development. On my Document Blog I have described how to debug POP problems with the telnet command [6]. Some users might read this and help me fix their email problems faster. I know that most users won’t be able to read this, but the number of people who can use it will surely be a lot greater than the number of people who can read the RFCs… Singularity tales is an amusing collection of short stories [7] about the Technological Singularity [8]. A summary of the banana situation [9]. Briefly describes how “banana republics” work and the fact that a new variety of the Panama disease is spreading through banana producing countries. Given the links between despotic regimes and banana production it’s surprising that no-one is trying to spread the disease faster. Maybe Panama disease could do for South America what the Boll weevil did for the south of the US [10]. Jeff Dean gives an interesting talk about the Google server architecture [11]. One thing I wonder about is whether they have experimented with increasing the chunk size over the years. It seems that the contiguous IO performance of disks has been steadily increasing while the seek performance has stayed much the same, and the dramatic increases in the amount of RAM you can get for any given amount of money over the last few years have been amazing. So it seems that now it’s possible to read larger chunks of data in the same amount of time and more easily store such large chunks in memory.

Romain Francoise: Updated Debian Vcs-* statistics

Not much has changed since my previous post, Subversion and Git are still growing.

Zack has a similar graph with a logarithmic y-axis which shows that arch is losing users. Who would have thought? :)

Steve Kemp: Sorry I'm late. Work was murder.

I've spent a few hours recently looking at building RPM packages of GNU/Linux kernels, which has been a frustrating process. There are many many online guides which give the impression that this is actually a pretty complex process. For example How To Compile A Kernel - The CentOS Way guide. (Did I mention how bad most of the howtoforge guides are recently?) So, after fiddling around for an afternoon and getting lost I decided to abandon the process. Here is a tested process for building a binary RPM kernel package:
cd linux-2.6.24.7/
make rpm
Yes this works just fine upon a Centos 5.x machine - I'm used to using make-kpkg to make a Debian kernel package, but it seems that if you just visit kernel.org and download the latest version you can build a RPM without any extra effort thanks to native support. Cool. Now I need to work out how to create, host, and update a YUM repository. That looks fiddly and annoying too. XML. Eww. Any guides are most welcome - ultimately I need to package and host a "recent" kernel for Centos 4.x, Centos 5.x and Fedora Core 6-9 - each for i386 + amd64. ObQuote: Spiderman

Pablo Lorenzzoni: Ruby security advisory and fix

Debian 4.0 version of Ruby is open to the, now widely known, Ruby security vulnerabilities. The bug is reported as 487238 in Debian s BTS, and is closed, since the version now in sid (version 1.8.7.22-1) is already fixed. Users of stable can apply the patch provided by Daniel Franke (it doesn t seem to fix all, but goes a long way). Apparently, this brought up (again) the rants over full disclosure. Indeed, what is vulnerable is not that hard to find, as Zed Shaw showed us, so, why not talk about it in a plain and bold form? Why just provide the CVE numbers and ask for everybody to upgrade? Zed goes more deep about the quality of C code, but that is not the issue I want to talk about As a Free and Open Source Software supporter (and developer), I can see the benefits of full disclosure. As a not-full-time webmaster, I can see the benefits of not having a proof-of-concept piece of code attached to the vulnerability report. Of course, there s a lot of things a webmaster can do to prevent having a machine completely compromised in case a security advisory is published with a proof-of-concept code in it (think about chrooting, randomized memory protection, security libraries, grsecurity, SELinux, etc) and my machines, although vulnerable to the bug, would not be fully compromised if exploited. I guess one should be prepared to whatever comes from the Internet Full disclosure, in this sense, have more pros than cons, IMHO. For instance it was not clear if Debian 4.0 were vulnerable There were no security advisory coming from Debian (and there s still not), and it is not promptly obvious if the version packaged is affected. I know that at least I wanted to run a proof-of-concept to check if my server is vulnerable or not before going all the way into packaging a fix (or backporting the sid version), and it was not until I read Matasano Chargen Blog that I could test older versions. But different people have different ideas

Matthew Garrett: Power management design philosphy

One of the traditional problems with power management has been balancing power savings against reduced functionality. The two traditional approaches to this have been to have sane defaults or to let the user tweak them, with a hybrid approach being to have sane defaults and an "advanced" box that lets users set their own parameters.

Both of these options suck.

The problem with sane defaults is that power management is an area where the "sane default" genuinely does differ between users. Usage patterns will determine the appropriate spindown period for a hard drive. AHCI's ALPM will disable hotswap detection, which is fine for home users but a pain if people want to rip out a failed RAID element. ALPM also introduces a small amount of latency (on the order of a seek in the most aggressive mode), which is entirely irrelevant for almost everyone but is a pain if you're trying to offer i/o latency guarantees. PCI-E link power management adds small quantities of latency. Letting the CPU run to full speed whenever it wants to is good for power management but potentially bad for thermal management. Screensaver timeouts vary depending on whether you're watching a movie or not.

The problem with leaving everything tweakable is that you're asking users to make choices about things but not giving them the information they need to make those choices. Whether you get a power saving from hard drive spindown depends on whether the drive is idle for long enough to save the power you'll spend spinning it back up. Get it wrong and you'll be putting your drive under extra load, reducing performance and consuming more power than you were to begin with. If you limit the maximum speed of your CPU to keep it cool, you'll be wasting power and performance even when it's well below the thermal limits. Disabling ALPM because you might want to change a RAID device at some stage means you're consuming power despite generally not needing to use the additional functionality.

But while these options both suck in different ways, they share one fundamental failure. They both imply static configuration. The correct power management policy depends on the way that a machine is being used at a specific instant in time, and no matter how many power management profiles you add there's no way for a user to switch between them fast enough to obtain a decent power/performance ratio.

Adaptive power management adopts a different strategy. Rather than define a static policy (or several static policies), the hardware is monitored to determine the best power management settings. An example of this is the ondemand CPUfreq governor. Rather than attempt to provide a static configuration, the processor frequency is automatically changed to meet demand while also keeping the overall power consumption as low as possible. This patch adds a thermal component to its policy, preventing the machine from overheating. Result? No requirement to provide tunables to userspace.

Something similar is achievable with hard-drive spindown. By simply monitoring how often reads or writes actually hit disk, it's possible to automatically adjust the spindown period to obtain decent power savings while reducing the number of spinups. This approach is imperfect - in an ideal world we'd know to spin the drive up before it's needed, but that simply isn't possible. However, the user is almost certainly unable to make a better guess. It's not realistic for a user to be able to predict whether or not a given page is still in cache or has been evicted. Nothing is lost by providing a dynamic policy, and another unnecessary tunable has vanished.

The difficult part of an adaptive policy comes when roles are switched in ways that don't correspond to changse in hardware status. One of the most common cases is that of screensaver settings when the user is watching a video. It's not practical for the kernel or a system daemon to predict this case, so we have two choices:.One of these choices involves the user having to explicitly state something that's obvious - playing a video automatically implies the desire to adopt a different power management policy, and so asking the user to manually adjust that is ridiculous.

The loss of hotswap notifications when ALPM is enabled? Simply reenable it if SMART starts complaining or the RAID set becomes degraded or a filesystem is unmounted or any of the other things that will have to be done before a drive can be safely removed. Latency an issue? Let userspace tell you what its latency requirements are. When we get down to it, the only settings that we can't infer are things like idle-time-to-suspend, screensaver settings and default brightnesses. Which, curiously, are about the only things that Mac OS exposes[1].

The problem we face is that we don't currently have interfaces to let applications tell us what their requirements are. This is theoretically straightforward, but getting it right is important. Beyond latency and screensaver issues, what constraints do applications want to impose? How can we expose an interface to those constraints? This is the sort of thing we'll be looking at at the Linux Plumbers Conference, so if you have ideas about what they'd need to look like then sign up. Or, even better, submit a paper and be part of the process that gets Linux's power consumption as close to the theoretical minimum as possible.

[1] My Vista system gives me 25 options which can be set for each of AC and battery.

Romain Beauxis: ov51x-jpeg: a tale of hardware and kernel tricks..

The plot..
Some years ago, when I started using linux, I felt the need for video chat, and hence intended to buy a webcam..
Unfortunately, while most of usb hardware is standard, such as the usb mass storage class, this is not at all the case for video, although it is starting to get better with the usb video device class which is more and more used by modern webcams.
So, at this time, each webcam would have its own communication protocol, and each driver had to implement a different way (...)

Uwe Hermann: DIY secure pseudo-DDNS setup using ssh

Here's a quick HOWTO for setting up your own secure pseudo-dynamic DNS (DDNS) server. It's not a "real" DDNS service, i.e. you won't be able to use standard DNS tools or protocols to talk to the server, but it covers 98% of all functionality I expect from a service such as DynDNS or similar ones: It tells me the IP address of a certain box which doesn't have a static IP address (e.g. my home-server). Requirements You'll need: Setup On the homeserver: On the publicserver: The script Finally, here's the content of the updateip script:
  #!/bin/sh
  # Update IP address.
  echo $SSH_CLIENT   cut -d " " -f 1 > /home/user/homeserverip.txt
So to summarize: the homeserver's user simply executes the updateip script on the remote publicserver, which in turn abuses the $SSH_CLIENT environment variable which contains the public IP the ssh connection was coming from (which is exactly what we're looking for). We store that IP in the homeserverip.txt file, which will always contain the latest-known IP address of the homeserver (because of the cronjob). Getting the current homeserver IP address You can now retrieve the current IP address of your homeserver easily from anywhere (i.e. from your laptop when you're in another, possibly hostile network) in order to connect to your homeserver:
  $ ssh -x user@publicserver cat /home/user/homeserverip.txt
To make this a bit more convenient you can add a shell alias (e.g. into ~/.bashrc):
  alias homeserverip='ssh -x user@publicserver cat /home/user/homeserverip.txt'
Or, to conveniently login to your homeserver as user:
  alias homeserverlogin='ssh -x user@ ssh -x user@publicserver cat /home/user/homeserverip.txt '
Conclusion, advantages This may not be the most elegant solution, and it has a number of drawbacks when compared to services such as DynDNS, but it's sufficient for me and it also has some advantages: Personally I'm currently using this mechanism for two things, more might follow: So far it works pretty nicely. Update 2008-06-24: Various fixes and simplifications. SSH key must be password-less. Don't run cronjob once per minute, that's overkill.

Matthew Garrett: Intel power saving

It's sometimes surprising where power goes in a laptop. One of the things busily consuming power is the digital link between the graphics hardware and the TFT, which is busily updating your screen 50 or 60 times a second. That's kind of unfortunate, because most of the time nothing's actually changed. Unlike CRTs, TFTs don't have the same requirement for rapid updates to maintain an image - reducing the vertical refresh rate (within reason) won't result in any reduction in image quality. What it will do is result in jerky movement and blurring, though, so doing this by default is a problem.

The obvious way to handle this would be to downclock the display when it's idle and upclock it again when it's active. Doing so gives the benefit of reduced power consumption when not much is going on (most of the time) and not impairing image quality. Programming clocks takes a noticable amount of time, and doing it while they're controlling the display results in nasty screen flicker. Thankfully, Intel hardware has two sets of clocks per output. One can be programmed at high frequency, and the other at low frequency. On pre-965 chipsets, we can then simply flick between them whenever the screen becomes idle or active - the clocks are already set up and the hardware waits for the next vblank before actually performing the switch, so there's no blurring or flicker. 965 theoretically does all of this in hardware, but I haven't actually tested that yet. In principle the patch sets it up, but...

The savings seem to be on the order of 0.5W or so, though that'll probably depend on your screen resolution. Patch against current git is here, and a precompiled version of the driver for 32-bit is here. The most likely problem is screen flicker when idle, so if anyone sees that then let me know and we'll see if it can be tuned.

Biella Coleman: Lost in Translation

I bet this rings familiar to many readers of this blog.

Russell Coker: Solving Rubik s Cube and IO Bandwidth

Solving Rubiks Cube by treating disk as RAM: Gene Cooperman gave an interesting talk at Google about how he proved that Rubik’s Cube can be solved in 26 moves and how treating disk as RAM was essential for this. The Google talk is on Youtube [1]. I recommend that you read the ACM paper he wrote with Daniel Kunkle first before watching the talk. Incidentally due to the resolution of Youtube it would have been good if the notes had less than 10 lines per screen. Here is the main page for the Rubiks Cube project with source and math [2], note that I haven’t been interested enough to read the source but I’m including the link for reference. The main concept is that modern disks can deliver up to 100MB/s (I presume that’s from the outer tracks, I suspect that the inner tracks wouldn’t deliver that speed) for contiguous IO. Get 50 disks running at the same speed and you get 5GB/s for contiguous IO which is a typical speed for RAM. Of course that RAM speed is for a single system while getting 50 disks running at that speed will require either a well-tuned system from SGI (who apparently achieved such speeds on a single process on a single system many years ago - but I can’t find a reference) or 5+ machines from anyone else. The configuration that Gene describes apparently involves a network of machines with one disk each, he takes advantage of hardware purchased for other tasks (where the disks are mostly wasted). I believe that SGI sells Altix machines which can have enough RAM to store all that data. It is NUMA RAM, even the “slow” access to RAM on another NUMA node should be a lot faster in most cases for sequential access and when there are seeks the benefits of NUMA RAM over disk will be dramatic. Of course the cost of a large NUMA installation is also significant, while a set of 50 quad-core machines with 500G disks is affordable by some home users.

Philipp Kern: Hooked up on TV series

Some months ago I didn't think that I would stick to an English TV series, not in any way dubbed or subtitled. But my girlfriend got me totally hooked up with both House, M.D. (Hugh Laurie is just hilarious) and 24. I got my own pick, too: Futurama. At least watching those American series improves my listening comprehension, although I still miss quite a lot of puns and jokes due to the missing subtitles and due to my missing knowledge of English sayings. But it works out somehow, she's explaining some of them to me, and I still enjoy it and have fun.

Julien Danjou: Debian maintenance team are great

A few months ago, I decided to move my libcgi-session-perl package to the pkg-perl project. This seemed the right thing to do since I just do not do Perl anymore, anyway. And now that's the second time that I notice someone has uploaded a new upstream release in my back. WTF, this guy did my job! That's awesome. :-)

23 June 2008

Obey Arthur Liu: Daniel Burrows on cwidget-gtk

Sometimes people propose other solutions to have the Aptitude-gtk project done, like :

I d have thought that the most interesting way of doing aptitude-gtk would be to write a gtk backend for libcwidget. -Karellen
As this might be of interest to more people, I’ll repost Daniel Burrows‘ response :
Although I can see where you re coming from, a GTK+ backend to cwidget would have no significant upsides and significant downsides. The main upside to doing that from a practical point of view is that you would have only one piece of driver code for the GTK+ and curses interfaces. You wouldn t have to rewrite the entire interface from scratch to create a GUI frontend. But this is just an illusory benefit. cwidget is a terminal interface library and aptitude s curses frontend is a terminal-based UI. From a practical point of view, this means that aptitude regularly assumes that, for instance, to clear out a line it s sufficient to output $WIDTH space characters (ASCII 32) with the desired background style. A port of cwidget to GTK+ would have to introduce new, interface-independent abstractions for all operations like this and eliminate all direct use of terminal-based assumptions, at a significant cost in complexity for both cwidget and the aptitude frontend. In order to transition to these new conventions, I believe you would have to rewrite large portions of both cwidget *and* aptitude in order to make the interface abstraction layer work. (remember: the justification for doing this is to avoid having to rewrite aptitude!) Furthermore, while this approach avoids reimplementing aptitude s curses interface (sort of, except where it doesn t see above), it does so at the cost of requiring you to reimplement all of cwidget, for GTK+. I just did a quick line count (with wc -l ): in all of cwidget there are 23,390 lines of code, while aptitude s curses frontend has around 23,359 lines of code (some of which are actually shared with the other frontends but are in the curses directory due to the historical organization of the code tree). Not only is a rewrite of cwidget more involved, but the amount of code you d have to replace is comparable to the amount implicated in a rewrite of aptitude itself! Finally, even if these costs weren t enough to eliminate the idea, it s not at all clear to me that a GTK+ backend for cwidget is even desirable. Although aptitude has some superficial similarities to a GUI program, the process of designing an interface to run in a terminal (where the available input mechanisms are relatively restricted and all output is to a character-cell grid) is rather different from the process of designing a GUI. GUI programs can t rely on some simplifying assumptions that terminal programs can, and at the same time they have a lot more options available to them (just to name a few: graphics, multiple windows, differing text sizes and rotated text). Trying to force everything through an abstraction designed for terminal output would require you to either
  1. eschew those options,
  2. provide abstract GUI components that somehow fell back to terminal rendering in a terminal, or
  3. add ways for the frontend to extend the abstract widgets with custom functionality.
1. is not an option because I (and, I think, Arthur) want to design a good GTK+ package manager, not a good GTK+ imitation of a console package manager. 2. and 3. amount, in my strong opinion, to writing two separate interfaces but intertwining their implementations in a mass of maintenance-resistant and extension-resistant spaghetti code. At the end of the day, I think that having two separate frontends (sharing backend logic where appropriate, of course) is a far cleaner and more maintainable design, and also easier to create.
As I said earlier, I intend to go a little farther than just making a GTK+ “skin” over the curses interface. Think less like gvim and emacs and more like maybe ddd. I should also add that the cwidget library is used by no major programs except Aptitude so few others would benefit from a GTK+ backend. As the cwidget library homepage says:
cwidget was originally an internal user interface library for the aptitude package manager. This means, on the one hand, that cwidget is known to work in the real world for a real application; on the other hand, it means that the feature set of cwidget is coextensive with the requirements of aptitude.

Christian Perrier: On random blacklisting of mail servers

Yesterday, I again got a stupid thing like:
: host YYYYYYYYYYY.de[AA.BB.CC.DDa] said: 550
    5.7.0 ... We don't accept mail from SPAM-friendly
    providers (in reply to RCPT TO command)
That's insane. Do people really want to communicate? This was about a bug in a Debian package and the above is the address used by the maintainer in his package. Dude, when you put your name in a package, please accept that people will want to send you mail and will want to be able to do so *easily*. The original mail was sent from my home server, hosted on a fixed IP address of the French ISP provider Free. The address has reverse DNS resolution and my system never sent spam or never was used to send spam. Free has a policy to block outboind port 25 for its customers unless they explicitely request to open it...which is IMHO the best compromise to avoid thousands of zombie Windows computers to send out spam. Blocking random blocks of IP addresses because they are "used by ISP customers" or because "one should us one's ISP mail server" is nonsense. This is not the Internet I knew and this is not the Internet I want. I don't see any reason why my home server would be worse than Free mail servers. I know what spam is. I receive tons of it and I had to take measures to limit and filter it. These measures never involved such stupid blocking by IP address and silly blacklisting. I use the Internet to communicate and I want people to be able to reach me, not going through weird ways to find their route to my precious mail address. That was the random rant of the day. I know many people will maybe comment on why Filtering Is Good or why I Shouldn't Be Sending Mail Directly But Use My ISP. Feel free to do so but also think about it: aren't we using mail to freely communicate? Blocking IP addresses randomly is just the poor man's solution to spam.

Russell Coker: TED - Defining Words

I recently joined the community based around the TED conference [1]. The TED conference is expensive ($6000US) and has a long waiting list (the 2009 conference is sold out) so it seems quite unlikely that I will ever attend one. But signing up to the web site is easy and might offer some benefit. One thing that interested me was that part of the sign-up process requests that you select up to 10 words from the list above to describe yourself. Some of the words seem almost mandatory for anyone who is interested in what TED has to offer (I find it difficult to imagine someone declaring that they are not an “activist” or a “change agent” while wanting to be involved with TED in any way). The range of words also seems quite strange, there are some professions mixed with educational status, marital status, and religion. The way it is laid out would tend to encourage people to make a decision as to which aspects of their life are more important, is career, marital status, or religion more important? Given the nature of TED I’m wondering whether the intentionally did a bad job of that part of the site design to encourage people to think about these issues. It seems to me that a better way of doing this would be to provide a few suggestions and allow people to fill in text fields with their own values. Even defining marital status can require many choices and there is no limit to the number of religions and careers. If you try to make a comprehensive list then you will end up doing what British Airways did with their frequent flyer membership application page [2]. Even disregarding the choices of spelling (EG Admiral vs Admiraal and Brig Gen vs Brig General vs Brigadier General) the British Airways list is unreasonably long, and I doubt that anyone who deserves the title “Her Magesty” or “His Holyness” is going to be interested in frequent flyer points. Also I wonder which of the entries in the TED list would be most commonly accepted by the free software community. It seems that activist and technologist would be quite popular. Here is the list in text form for those who can’t get the picture above:

Activist, Agnostic, Architect, Artist, Atheist, Athlete, Blogger, Brainstormer, Buddhist, Business adviser, Business leader, Business mentor, Care taker, Change Agent, Christian, Clergy, Concerned citizen, Connector, Consultant, Designer, Doctor, Educator/Teacher, Engineer, Entrepreneur, Environmentalist, Event planner, Explorer, Filmmaker, Finance professional, Foodie, Gay, Global soul, Hindu, Idea generator, Industrialist, Inventor, Investor, Jewish, Job-seeker, Journalist, Lawyer, Life mentor, Marketer, Musician, Muslim, Parent, Performer, Philanthropist, Photographer, Policy maker, Potential employer, Producer, Project manager, Promoter, Public servant, Real Estate professional, Sales specialist, Scientist, Single, Social entrepreneur, Startup, Student, Technologist, Web guru, World traveler, and Writer/Editor.

Benjamin Mako Hill: Property!

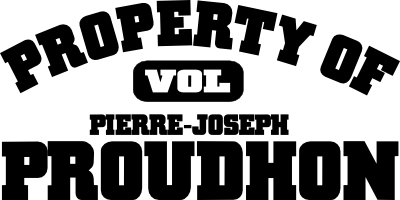
I've always been bothered by those "Property Of Blank University" t-shirts that used to actually be the loaned (or stolen) property of college athletic departments but have now become popular enough that you can find them, for sale, in nearly any university store or gift shop in the US. Few people would assume that somebody with a "Property of" shirt had stolen their clothing. In fact, it's often impossible to find the shirts except on sale anymore -- and rarely from universities themselves. Here's my response. /copyrighteous/images/property_of_pj.png For those that don't know (and that's certainly many), Pierre-Joseph Proudhon is the nineteenth century French anarchist and mutualist most famous for saying, "La propri t , c'est le vol!" In English: "Property is theft!" You can buy my t-shifts (red on black, where possible), in my Printfection store. Source SVG is here. Please share variations in a comment.
Michal Čihař: Server has been moved

This night, long delayed operation has been done and server which gives you this page has been moved to another server room. It should bring a bit better conditions for server and you should not notice this except short outage in this night till all DNS caches on the way will will update their records. This is a theory and lets see what problems will appear tomorrow morning ;-).

Steve Kemp: There is something evil there

So I've had a hectic few days, and I'm getting close to having caught up with the things that I've been sitting on whilst I've been away.
ObRandom: Several people, independantly, have told me within the past few days that "whilst" is not a real word. it is. End of ..
Some interesting things I've been working upon recently include a fun little firewall tool. Once upon a time I wrote a firewall script which worked like this:
firewall/
 -- incoming.d
     -- smtp
     -- ssh
     -- www
 -- outgoing.d
     -- ssh
     -- smtp
     -- dns
     -- icmp
When you executed the magic firewall script it would scan the incoming.d directory, and for each file it found lookup the relevant port in /etc/services. These port numbers would then be opened. And at the end you'd just have a "-j DROP". After a long phone conversation to a colleague on Thursday/Friday of last week I've now reworked this idea anew. There is still the notion of filenames referring to what is allowed for a pair of directories (incoming.d/ + outgoing.d/) but even more flexability and no hardwired use of /etc/servvices. I guess some ideas are just too simple to give up ..? Anyway there are a plethora of different firewall applications of varying sophistication and complexity in the world. I don't really want to go out of my way to promote this one - but at the same time it might be a useful idea for somebody? The next (work) job I have is determining how to make a "kernel" + "kernel-dev" RPM package based on Debian sources. Joy. Actually the more I look around the more fiddly, annoying, and troublesome I suspect this is going to be. Sigh. ObQuote: The Grudgy

Next.

Previous.

