Search Results: "sesse"

19 February 2006

Martin F. Krafft: Re: Technical classics

< Sesse> madduck: you'll have to counter-blog :-)
< madduck> mh.
< Sesse> madduck: my degree isn't in computing, it's in signal processing
< Sesse> so I don't have all the programming and db books
< madduck> mine is in procrastination.
Sesse, I see your list and raise you:
  • Computer architecture: "Structured computer organization" by Tanenbaum
  • C++: "The C++ Programming Language" by Stroustrup, and I also include "Modern C++ Design" by Alexandrescu, an excellent book and companion to the Gamma et al. "GoF" book you quote for design patterns.
  • Compilers: Aho et al. Compilers: principles, techniques, and tools. Great book.
  • Database management systems: Elmasri and Navathe
  • Operating systems: Tanenbaum, but I also liked Silberschatz and Galvin's "Operating System Concepts"
  • Unix programming: the Stevens books
  • Programming in general: Abelson & Sussman's "Structure and Interpretation of Computer Programs" -- possibly the book that had the most influence on me.
Also, for crytography, I would put "Contemporary Cryptography" by Oppliger in there, despite its price. I have worked with Oppliger so I may be biased, but I found his book to be very in-depth and yet understandable, possibly more so than Schneier's. And it's more up to date. Update: Now I am really curious what the classic for UML would be. Seems like all the UML books are either too spec-like, or too lofty.

17 February 2006

Martin F. Krafft: Pet peeves: cookies and redirects

If you design your website so that it requires cookies, you ought to be punched (c.f. Sesse). When I surf the web, I usually choose to deny cookies for this reason; should I find out that cookies are actually needed, the excellent Cookie Button Firefox extension allows me to rethink my choice. If you implement redirect chains like ticketcorner.ch to www.ticketcorner.ch to www.ticketcorner.com to www2.ticketcorner.com, you ought to be kicked and battered, especially if those are implemented with meta refresh instead of HTTP redirect. If you set a cookie from www.ticketcorner.com with cookie domain .ticketcorner.com and require that on www2.ticketcorner.com, you should be slaughtered. And Firefox should certainly have a better means to edit cookie restrictions outside of the current domain than to require me to go to the preferences and click a hundred times until I can browse a huge list of cookie exceptions (no search) for a the entry, remove it, reload the page, and cast another vote. I have not found an extension to do this...

16 February 2006

Steve Kemp: Back to reality

Steinar H. Gunderson
It doesn’t matter which shell I use for completion. (And this goes to the other people who mailed me to tell me that Zsh rulez!) The problem is that packages of Zsh and Bash both offer several completion routines which are not sufficient for me. (e.g. one missing one is completion for the various bittorrent scripts.) So I need to install my own routines for those. I also wrote custom completion routines for in-house tools, and my own personal scripts in ~/bin/. Since these are not available by default in either the bash package or the zsh package I must install them manaully upon each host I wish to use, in order to have an identical setup. And that manual installation is what my new package makes easy. (Or will when it is complete!)
Security Team Meeting
Security issue meeting on IRC went well, although I left rather abruptly since my bed was calling my name.

7 February 2006

Clint Adams: Allison

She called him because she had had a big fight with her boyfriend and asked if she could stay with him if she needed to. He told her that she could. He cleaned his place like a man possessed. No one had ever seen him that driven before and no one would see it ever again. When she made up with her boyfriend and decided to stay at home, the embers of hope within him died. Normally he dated women who were contrary. They liked to fight with him and he liked to whimper and whine. There was a great deal of manipulative behavior on both sides, and a lot of emotion and intensity. He did not fight or squabble with her, but he loved her deeply. She got married shortly before he did. He married a girl with whom there was almost no passion at all. Some people cried at that wedding.

Clint Adams: He wore a hat

It was wintertime somewhere in the Ozarks, in the days before the Soft Scape. A young boy named Timmy was born unto a poor family that already had one son. When that brother was killed in an accident, the parents boxed up all his possessions and hid them deep within the attic, not wishing to be reminded of his former existence. Some said that it was the only healthy option open to them, and some said that it was an ill-fitting tribute. In any case, Timmy barely even found out that he had had a brother, and any memories he developed of him were false. As Timmy grew, he sprouted hair, and learned to speak, and learned to pray. Every night, before going to sleep, he petitioned God, Please keep mommy and daddy safe. If he had had a brother still, he would have prayed for him too. The years went by, and Timmy went to school, and someone surprised him with the claim that he had once had a brother. He asked his parents about this when he got home, and they rather loudly instructed him not to discuss such things. He dropped the matter, but remained perplexed and afraid to ask any more questions. It was a long time before his explorations of the attic yielded the discovery that precipitated a great big scene. When his father saw that he had retrieved some of his brother's possessions, he beat him, and his mother screamed that if he ever went up to the attic again, she would cut off his pee-pee , and everyone was upset for quite some time. Mistaking this parental love for abuse, he drew away from them, and began to wander and drift. In the summer of his fifteenth year, he learned that love was a hobo's hand. Then, that winter, he left his parents' house for the last time. Finding himself overwhelmed by the eternal struggle for food and shelter, he started turning tricks for small change. This proved to be a dangerous occupation, and Timmy's life was rife with anxiety for quite some time. Presently, Timmy came to a little town, and in that little town lived a fireman and his wife. The fireman felt that it was time to experiment, and and inquired if Timmy would accomodate him. Timmy was more than happy to oblige for a reasonable fee, and the fireman was more than happy to continue to pay it. His wife was less than happy about the whole affair, for she felt that it reflected poorly on her as a woman, and she feared that if word got out, she would be the laughingstock of the town. Timmy was unconcerned with such issues. Some said that he was morally bankrupt, and some said that he was a practical businessman. In truth, though, the money became utterly unimportant to him, as he spiraled toward a psychotic breakdown. He had developed a fantasy wherein the fireman would leave his wife and take Timmy away, maybe to somewhere like Alabama, where no one would oppress them. As he obsessed and clung to this dream, he pulled farther away from reality and other human beings. The fireman was relatively unconcerned, but the fireman's wife grew more worried by subtle nuances that she noticed over time. You must stop this! she insisted. Give me my space! he insisted. The ongoing argument devolved into citations of marriage vows and Biblical passages, which were conveniently inconclusive. The fireman's wife was a God-fearing woman, and she knew that she could not violate 'til death do us part without being struck down, and that she could not invoke the old 'til death do us part loophole without violating thou shalt not kill and being likewise smitten. Thus she was at an impasse. Some said that she was a victim of a bad situation, and some said that it was her own fault for letting it happen. Timmy's relationship with God was much more complex, though now almost completely forgotten. He had also almost completely forgotten the existence of the fireman's wife, else he might have thought to plot against her. This memory lapse was abruptly corrected when the fireman's wife threatened Timmy. Timmy was upset and distraught and threatened her back. The fireman announced that he was tired of them both, and moved to Alabama on his own. Some said that it was irony, and some said that it was an owmen of things to come.

6 February 2006

Joey Hess: summer

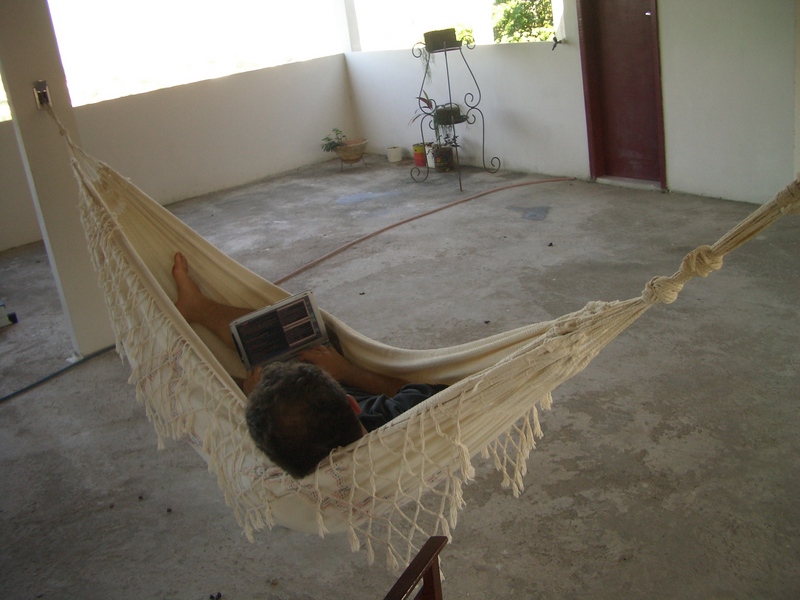
Yes Sesse, I have been known to enjoy summer (when I'm not busy merging slides at the last minute with my co-speakers). joey-hammock Though winter is nice too, and it seems to have finally gotten here.

5 February 2006

Martin F. Krafft: Encrypting ~

It's about time I encrypt my home directory. So far, I've found two tools for the job: dmcrypt and encfs. dmcrypt links in between the VFS layer and the data store. For an encrypted partition or image, it creates a device under /dev/mapper, which you then mount. Think cryptoloop. Encryption covers the whole scale of symmetric encryption, but I didn't find anything related to public key crypto. I am also not entirely clear yet on why a damaged block on the storage medium doesn't screw the encryption block (partially) stored on it, as well as all following ones, given a chaining mode like CBC for instance. However, as this thread shows, I am wrong and technology is right (and works), and I still just don't get it. It feels like another Monty Hall problem to me (which I also never really understood to the point of being able to convince someone else thinking 50/50 is the answer of the alleged 2/3). So then there's encfs, a FUSE-filesystem that seems (I have not tried it) to create a virtual directory for an existing one, transparently encrypting filenames and contents as they are written to the existing directory (via the virtual one), and decrypting them when requested through the virtual one. So it's a 1-to-1 mapping, which has its pro's and con's. encfs seems equally strong on the symmetric crypto side, but seems to lack public key support. For each, there's a proper PAM module: libpam-mount can mount a cryptoloop filesystem upon login (though the README says it cannot do so for OpenSSH logins. If that's right, well, one candidate less...). On the other hand, there's libpam-encfs, which creates the virtual directory on login (and removes it on logout). I can well imagine how any of the PAM modules would do their job just fine on a machine where xdm is the primary/only login method. However, what about SSH? What happens if I log in through xdm, then SSH, then quit X? How do you solve the problem? I am curious and will blog about the things I hear... Update: After rereading my thread, I am understanding, I think. We're talking encrypted block devices (or loop devices). It's not difficult at this stages to tie IV chains in with storage blocks. I am still curious why my 8M file was still all zeroes after changing the cryptotext. Update2: Sesse points out that CBC uses the ciphertext of the previous block as an IV, not the plaintext. So if some block gets corrupted, that messes up the next one's plaintext, but not its ciphertext, so the one after that is OK. Thanks.

16 January 2006

Ross Burton: Weakness

On the whole I'm an organic, fresh, free-range, no-MSG, tree-hugging leftie kind of guy. I prefer Marks and Spencer's Red Leicester and Spring Onion crisps as they contain potato, oil, cheese and onion. When I buy chicken it's free-range. Eggs are always free-range, and the fact that the supermarkets still sell "value" eggs upsets me. This weekend in a "top 10" conversation, I discovered that I have several weaknesses: More MSG, artificial flavourings and additives than you can shake a stick at. Please say I'm not alone... or am I just weak-willed? In other news, Henry is three months old today. He is all jabbed up now so can finally leave the house, walks are fun (for certain definitions of fun that is) as he continually pulls on the lead and is obsessed with cars driving past. So far we're averaging two random people talking to us about Henry on every walk...

8 January 2006

Andrew Pollock: [life] First Christmas abroad

(I love the term "abroad". It sounds so English.) Well that happened. We had Michael and another Andrew from work who started two weeks before us and his wife come over for what Michael was calling "linner" (the inverse of "brunch"). Sarah cooked up an absolute storm. We had roast turkey, roast potato, pumpkin and sweet potato, steamed broccoli, cauliflower and asparagus, and Yorkshire puddings. We had so many types of gravy we completely forgot about the cranberry sauce. Michael managed to track down a plum pudding (this country seems obsessed with pumpkin pie) and we had something approximating custard (something else this country doesn't seem to do) with it. A very good feast was had by all, and six hours later we were done. Back to unpacking boxes. Brought to you by some kind neighbour's open access point.

1 January 2006

Joshua Kwan: For posterity: Md is a flaming idiot!

Abridged to remove irrelevant conversation…
< Czesiu> Btw, udev recommends at least 2.6.12 kernel, which is not shipped
in Debian.
< Md> so far the upgrade procedure is “upgrade your kernel, reboot,
upgrade udev”
< Md> Czesiu: yeah, nobody had told me this yet, you know?
< dilinger> you can either go the lvm route, and make up some kernel APIs to
match again, or you can go the ndiswrapper route and make some incredibly
strict dependencies so that people are sure to upgrade kernels and udev
in parallel.  both solutions suck.
< Czesiu> Md: you sound quite sarcastic :)
< wildfire> why not just have a udev-compat; which conflicts which newer
kernels; and make udev conflict with older ones
< Md> dilinger: a future udev version will refuse to install on anything
older than 2.6.12, so this will reduce the potential for brokeness
< Md> the /dev/input/mice problem has been unexpected, if it cannot be fixed
I will make the next package require 2.6.12
< dilinger> the best solution, imo, is to have udev 0.5x and 0.62 allowed
to be installed in parallel, and have a wrapper script that determines which
to use when it’s run
< wildfire> hmm, dilinger, that does sound pretty clean
< Md> dilinger: the configuration syntax is subtly different too. this is
not really possible
< Md> wildfire: yes, until you start looking at how to implement it 
< dilinger> Md: sure it is; /etc/udev05x for the old version or something
< dilinger> /etc/udev for the new version
< wildfire> md, but that’s someone else problem ;-)
< Md> dilinger: keeping them in sync is hell
< dilinger> no kidding, but that’s what maintaining stuff like this requires
< Md> so far, it appears to be too much complex to be justified
< Md> if upgrades will happen to be more complex than we currently know then
I will reconsider this
< dilinger> are you kidding?  i think the number of people whose systems
are breaking is pretty good justification
< Md> dilinger: only because the package currently is not refusing to run
on older kernels
< idnar> Md: but if the package fails to run, isn’t that likely to cause
breakage too, since your /dev won’t look like it normally does?
< Md> idnar: it will refuse to be installed or upgraded, like it’s currently
happening if you are using a kernel < 2.6.8
< dilinger> Md: what about doing something insane w/ devfs/
< dilinger> and devfsd
< Md> dilinger: ?
< idnar> Md: ah
< dilinger> depend upon devfsd, if the kernel is older than 2.6.12, have it
mount devfs over /dev and run devfsd instead of runing udev
< Md> different configuration syntax, different semantics, no HAL/hotplug
support. basically, I can’t see why you could think about this
< dilinger> because it would allow things to *work*
< dilinger> even if it doesn’t have the same config syntax
< dilinger> it could spit out a big warning upon startup
< idnar> suddenly switching the user to devfs would likely cause all sorts
of unknown breakage
< Md> if the kernel is older than 2.6.12 people will not be able to install
a newer udev, so this is not relevant
< Md> please try to look at the whole picture
< dilinger> people are going to want to reboot into older kernels and have
their /dev in a sane state
< dilinger> the running kernel isn’t the only one they may be using
< Clint> yeah, i’m not using the running kernel
< Md> dilinger: then udev will automatically disable itself. the current
experience shows that users are not bothered by this
< dilinger> Clint: quiet over there :P
< dilinger> Md: the user experiences around here don’t seem to match what
you’re saying, otherwise i wouldn’t even be mentioning it
< Md> again, this is not how future versions will work
< dilinger> let me put it another way
< dilinger> it would be a very good idea to future proof udev against such
incompatabilities now
< Md> tell greg k-h, now me :-)
< dilinger> because i’m sure things will break again
< Md> anyway, you persuaded me. I will upload right now an updated package
which refuses to be installed with old kernels
< Md>   * Kernels older than 2.6.12 are not supported anymore.
< Md>     If detected, the package will refuse to be installed.
< Md>     If the running kernel is downgraded after the package has been
< Md>     installed udev will disable itself at boot time.
< Sesse> Md: whoa
< joshk> that’s ridiculously stupid if you as me
< Md> this is what was going to happen in a few releases anyway
< Clint> joshk: coredump immediately
< Md> BTW, I suggest that concerned people read this before continuing
http://sourceforge.net/mailarchive/message.php?msg_id=12236847
< joshk> breaking support for anything but the very latest kernel (which
isn’t even in debian yet!) is dumb. you break everyone’s desktop because
hal stops working
< joshk> (one particular example)
< Md> joshk: people can keep the old udev until the upgrade, nothing breaks
< Sesse> Md: *g*
< joshk> don’t grin at Md, it makes him think we’re in agreement

26 December 2005

Andrew Pollock: [life] First Christmas abroad

(I love the term "abroad". It sounds so English.) Well that happened. We had Michael and another Andrew from work who started two weeks before us and his wife come over for what Michael was calling "linner" (the inverse of "brunch"). Sarah cooked up an absolute storm. We had roast turkey, roast potato, pumpkin and sweet potato, steamed broccoli, cauliflower and asparagus, and Yorkshire puddings. We had so many types of gravy we completely forgot about the cranberry sauce. Michael managed to track down a plum pudding (this country seems obsessed with pumpkin pie) and we had something approximating custard (something else this country doesn't seem to do) with it. A very good feast was had by all, and six hours later we were done. Back to unpacking boxes. Brought to you by some kind neighbour's open access point.

2 December 2005

David Pashley: OOP Strikes Back

Steinar, you missed my point. I explicitly said not to get bogged down in my example. The point is that changing the internal details of your class shouldn't result in your users being forced to change their code. As I said, exposing your implementation tightly couples your code and your users. As Matthew pointed out, you shouldn't have sets and gets for every item in your class. You should have a clearly thought out api that isn't tied to the internal detail. Exposing internal, either through making data public or blindly creating gets and sets for private data members is just bad OO design. An addition to my example that makes things little cleared would be a subclass that validated the words you could use. With a public variable I couldn't enforce that, but I could override my setter to add validation.

1 December 2005

Matthew Palmer: OOP and the Get/Set issue

Steinar, your comments on the limited utility of Get/Set methods both struck a chord and touched a nerve with me. On the one hand, I completely agree that people need to spend more time writing methods that do something useful to an object rather than just exposing public methods. For example, how often have you seen something like this (in faintly python-inspired syntax):
 obj.count += 1
 [...]
 obj.count -= 1
 [...]
 if obj.count == 0:
 	obj.destroy
Instead of the far more descriptive (and well-encapsulated):
 obj.register_user()
 [...]
 obj.unregister_user()
 [...]
 obj.destroy_if_unused()
(or any one of a thousand other similar idioms). This is a contrived example, of course, and a real example would involve doing at least a dozen operations on an object's public attributes from another class (which results in class-associated logic being located in other classes in the system) instead of putting it in a method and calling that (thus keeping all of the logic with the data it's manipulating -- which is the point of OOP). Anyone who writes code like the first example above and calls it OOP is kidding themselves. Of course, you could make the code even more ridiculous with getter/setters:
 obj.setCount(obj.getCount()+1)
 [...]
 obj.setCount(obj.getCount()-1)
 [...]
 if obj.GetCount() == 0:
 	obj.destroy
Incidentally, if you ever see anyone turn the first example into the last example and say they're "improving encapsulation", please do the programming world a favour and kill them. kthx. On the other hand, Steinar, you say "I'm not denying that getters and setters for a few variables might make sense", which clouds the issue immensely. The idea of routing attribute access through a method is immensely useful. It even has it's own name -- the Uniform Access Principle. A few examples are in order (you might already have thought of these, Steinar, but who knows who reads my dribblings!): In my real-life case, there were few enough places to change all of the calls to a method, and since it's all written in Python I could have played __getattr__ games to get back to a method if I'd had to, but it would have been messy. But imagine a system written in a language that doesn't (somehow) support the Uniform Access Principle, and which was widely deployed (possibly even used by programs outside of our direct control) so the users of the class couldn't be adapted easily. Nightmare. Now, the real solution to the problem is to only use languages which support the UAP (Python can be hacked to do it; Ruby is, IMHO, almost a case-study in How To Do It; and there are other good languages out there). But, in ass-backwards languages that can't transparently map attribute accesses to method calls, I'd rather deal with getX()/setX() everywhere than have to try and perform the necessary gymnastics to later support dynamic value generation from what-was-previously-an-attribute. If, on the other hand, your post was primarily targeted at said ass-backwards languages, or programmers who cargo-cult manual getter/setters everywhere, let me join you in your derision. <grin>
David Pashley: Accessors vs. public member variables

Steinar, you use accessor rather than public data members because you may need to change the behaviour of the class to do something when you set a member variable. If you have all your data public, you can't do this. If you force people to go via a function, you can make changes to the class without affecting its users. You have a similar issue with inherited classes.

David Pashley: Accessors vs. public member variables

Steinar, you use accessor rather than public data members because you may need to change the behaviour of the class to do something when you set a member variable. If you have all your data public, you can't do this. If you force people to go via a function, you can make changes to the class without affecting its users. You have a similar issue with inherited classes.

David Pashley: Return of Accessors vs. public member variables

Steinar, Imagine a Word class:
class WordA  
   public:
      char * word;
 ;
class WordB  
   private:
      char * word;
   public:
      void setWord(char * w)   word = w;  
      char * getWord()   return word;  
 ;
WordA worda; 
worda.word = "WordA";
WordB wordb;
wordb.setWord("WordB");
printf("%s %s", worda.word, wordb.getWord());
Fine, this works well. Now imagine that you want to change word from a char * to a std::string to stop you dealing with pointers. For the WordBclass you only need to change the getWord function. You don't need to change any of your class's users. For the WordA class, you have a problem because you can't automatically convert from a std::string to a char *, so all your users have to change from object.word to object.word.c_str().
class WordA  
   public:
      std::string word;
 ;
class WordB  
   private:
      std::string word;
   public:
      void setWord(char * w)   word = w;  
      char * getWord()   return word.c_str();  
 ;
WordA worda; 
worda.word = "WordA";
WordB wordb;
wordb.setWord("WordB");
printf("%s %s", worda.word.c_str(), wordb.getWord());
This is the punishment you get for exposing the internal details of your class to your users. Please ignore any specific mistakes in my examples; the principles work the same with different types.

30 November 2005

Martin F. Krafft: OOP

But Steinar, it does... or what would you do if you had to limit the domain of a member variable so that e.g. it must not be set to an even number. If you have users of your class accessing public members everywhere, you are going to have a really hard time. Unless, of course, you use a proper language such as Python, which allows you to define implicit accessors for member variables.

28 November 2005

Wouter Verhelst: Belpic Backports

My belpic backports have now been added to the backports.org pending directory, until the dak setup there is finished (at which point they'll be accepted into the 'real' bpo archive). Oh, and Yes, you're right; sorry. So, for those not familiar with the thing, belpic is a little piece of software which was written by the Belgian Government in the context of the electronic id card project; it allows Belgian citizens to read out the information and X.509 keys on their ID card, so that they can use it to identify themselves, make signatures, and thusly do other generally interesting stuff, such as using the government's tax-on-web application.

23 November 2005

Antti-Juhani Kaijanaho: Constitutions and countries

Some people think that only countries have constitutions. I find that strange, since both write at Planet Debian; surely, Debian is not a country! [Update: As hinted in the comments, I did not get MJR's posting. My bad. Let it be known here that he expresses roughly the same argument I presented above.] In fact, the European Union is a country. It has a bicameral parliament (the council of ministers is sufficiently upper-house-like to qualify as one IMHO), a currency it governs, a passport, and it is the highest authority inside its borders. It is an unusual country in that its meber states have broad powers, but it is a country nonetheless. It possesses all four of the defining properties of statehood according to the Montevideo convention: The state as a person of international law should possess the following qualifications: (a) a permanent population; (b) a defined territory; (c) government; and (d) capacity to enter into relations with the other states. The first three are uncontroversial, and though the fourth is weak, it is present. (Okay, that last paragraph is controversial, and I know the arguments are not airtight, but I do believe the case is valid.)

12 November 2005

Steve Kowalik: Ubuntu

For some reason, I have been obsessed with Ubuntu over the last few days. I have no idea why, and frankly, wish I did. I also have no idea if it's a brief infatuation such as my foray into running FreeBSD, or a lasting love affair, such as I have with Debian.

I ran a Breezy live CD on my workstation, and I was fairly impressed, so I am actually planning on installing it on a machine - either my laptop, or my workstation, I haven't decided yet.

In other related news, my wife and I had our house warming party today! It all turned out well, with a good turn out, and everyone was very impressed with the house.

Next.

Previous.