Search Results: "ag"

2 April 2009

Rob Bradford: GNOME 3.0

I really like the 3.0 plan. There are two extra areas in particular that i d like to see us attack: Firstly (the smaller of the two) i d like to see a revamping of the Evolution client libraries, ECal & EBook, in particular ECalComponent is horrible. The work that Chris and I have been doing on libjana is showing some of the direction that such a library for accessing calendaring could go. This requires an ABI & API break to do this effectively (hence being a 3.0 thing.) Ross has also been doing sterling work on the server side of things by migrating the eds-dbus fork into the mainline. This is now basically just waiting on the migration to git and a double review of the calendaring code. The second and more significant thing that I care about is that I think we need to bring web services closer into the desktop. I ve been persuaded that desktop applications are not dead but I think we need compelling, transparent and easy ways to integrate with cloud services. In particular we are entering an age of almost always on connectivity. Many people already find little use for their computers if they are not connected to the Internet. However since the omnipresent and omni-reliable 3G/wireless/wimax utopia is not yet with us we live in a world where we get connectivity in bursts as we travel, socialise and live. Our platform should cunningly pull down interesting content when the user is on cheap and reliable connectivity which they can then peruse when offline or on an expensive and unreliable connection. A project that Ross and I have been working on at Intel to bring social networks to the desktop/mobile is called Mojito. I ll cover this in more detail soon.
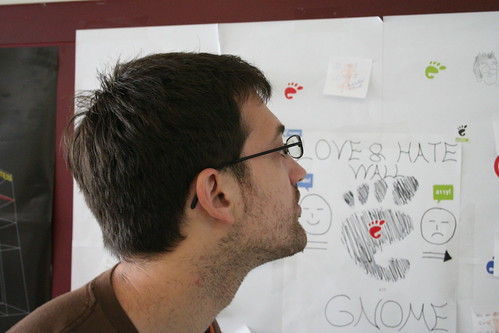
Ross inspecting the wall
Our hero: Ross Burton

Ana Beatriz Guerrero Lopez: KDE 4.2 in unstable is coming

It was 2 years ago when we started working in KDE 4 packages, and exactly 20 months ago when we started uploading KDE 4.0.0 beta 1 to experimental. Finally, we are working in packages that are targeted to unstable \o/. As announced in the users mailing list, we will be uploading KDE 4.2.2 to unstable in the next days, so look carefully at what you update :) We have worked very hard in providing a smooth upgrade, but given the change is so big, some new (little!) problems will be discovered. One of the most problematic points is we were using .kde4 to store user data and settings of KDE 4 and now it is time to switch back to the default .kde. There are several possible migration cases here and for allow users select the case they prefer, a migration wizard tool named Kaboom has been created inside the Debian KDE team. Be aware that there will be some inconsistencies in unstable the following days after KDE 4.2.2 reaches the archive. So please, be patient. We are still testing and we are not uploading until we think it is good to go, so next days could become 2 weeks. Again, be patient :) If you want to keep using KDE 3.5.10 for a few weeks more, just do not upgrade yet. But if you want to keep using KDE 3.5.10 for months, maybe you should consider become a Lenny user. If you have questions, doubts and/or suggestions, you can check our Debian KDE Team website where we try to add information and the archive of the Debian KDE users mailing list. Time for a personal note. KDE 4.2 is a huge change from KDE 3.5, and it is normal if you do not fully like it in the beginning. But I do think most of users of KDE 3 will feel very comfortable in KDE 4 after some days using it. You just need to discover the new ways of doing some tasks. Also, once KDE 4.2 is sitting in unstable, a lot of third party applications (specially plasma widgets) for KDE 4 will be finally uploaded to the Debian archive, making KDE 4 even better.

Filip Van Raemdonck: Some like it hot others just are

This week brought some really nice weather. Too nice already for some people, it would seem.<br /> While most people would likely enjoy a ride home on a sunny afternoon, for certain hotheaded ones the temperature appears to set their brains and blood boiling and remove the inhibitions for juvenile behaviour.<br /> Driving home I encountered a truck driver hanging out of his window having a heated argument with a car driver standing straight up through his sunroof. I couldn't hear what they were arguing about, as it happened a few cars before where I stood, but in the meantime they were blocking the two lane drive. I'd almost be surprised if it wasn't one or the other accusing his adversary of doing exactly that, blocking his trajectory.<br /> Luckily the scene didn't take too long and they drove on before others could join in on the argument.<br /> <br /> One pattern that I've observed so far in all incidents of traffic aggression that I witnessed, is that at least one of the parties was accompanied by a female passenger. I have to wonder if female company is in fact an influencing factor
Jan Wagner: The Crisis of Credit Visualized


The Crisis of Credit Visualized from Jonathan Jarvis on Vimeo.

Marc 'Zugschlus' Haber: LV naming, UUIDs, file systems labels

In the last few weeks, I spent quite some time wondering about how to arrange the hard disk layout of my productive systems in the future. This article outlines my thoughts and would like to ask the lazyweb for comments. I try to keep my Debian servers as identically as possible, making it possible to talk non-linux persons remotely through the system without having to worry about this particular box configuration. I have been especially worrying about: On my current systems, I usually have the root file system on /dev/hda1, with /dev/hda2 being a PV which is the only PV of a VG vg0, which in turn has LVs named home, var and usr. This setup has a bunch of disadvantages. Thankfully, there is a number of possible solutions: I am pondering about a solution, but suspect that this is totally overengineered. Did I miss something? Is this a realistic solution? How do you handle this issue? Comments to this article will be open for quite a while.

MJ Ray: A Question of Debian ClamAV, Freshclam and Volatile

I m not a big fan of virus-scanning on the mailservers (I think you should bolt your email-sending computers right down so that viruses and spambots can t send email), but it seems to be a necessity these days. So, I was a bit late starting on mailserver-antivirus and mainly pay attention to it when it goes badly wrong. I ve got clamav installed where needed, but recently I m seeing clamav hang, eat CPU and cause postfix to defer all emails while logging nothing useful. Often this seems to be soon after freshclam kicks in. Anyone else seen this problem? Moreover, anyone managed to narrow it down and fix it? On some systems, instead of having freshclam, we have clamav-data from volatile which seems to work better, but are they missing out on anything by doing that? Does it lag a bit behind and download a bit more? Is there a third option, either another way of feeding clamav, or an alternative debian package, which you think people should consider?

MJ Ray: Cooperatives-SW Board and Housing Enquiry, Bristol, 6 April 2009

With our AGM in Plymouth rescheduled until June or July, the Cooperatives-SW board will meet in Bristol on Monday. Cooperatives-SW aims to represent co-operative and mutual enterprises in the region. As with previous meetings, if you d like to meet up beforehand, let me know through this blog, identi.ca or email. Bristol is near HQ, so I expect I ve met most people there who want to talk to me. The meeting is just before a co-operative and mutual housing hearing. Places will be limited so please contact CDA (Brave Ltd) on 0117 989 2536 if you would like to reserve one.

1 April 2009

Sandro Tosi: Suggestion for personal backup solution

So, I bought this 1TB disk to backup mine (1x750GB + 1x75GB). Now what I need to find is a backup solution to use it.

What I'm looking for is not a damn complex program, with servers+clients+daemons+agents+satellites (it's just for my box), but something that allows me to:
Ok, they are a lot or requirements, almost in importance order.

What do you have to suggest to me about it?

I , by myself, am considering backuppc, amanda and bacula, while the latter seems a lot complex.

I wait for your reply :)

Nicolas Valc rcel: Guadalinex-Edu Beta Announcement

Guadalinex-EDU: New educational distribution based in Jaunty

Guadalinex Edu is a new GNU / Linux distribution developed by the Advanced Center for ICT Schools Management (CGA), initially created for use by the educational community of Andalucia, Spain which will be available for teachers and students within the domestic sphere. Guadalinex Edu distribution is equivalent to the future Guadalinex V6 citizen but oriented to the educational sector.

Looking for the highest possible level of stability in the distribution, the CGA will be releasing a beta version of the distribution, installable by anyone who wants it. The aim is to involve the educational community in the stabilization and development of Guadalinex Edu, before its deployment in local schools.

Guadalinex Edu Beta 1 is fully functional, but should not forget that this is a beta version which may contain errors from both: the applications included by the CGA in the distribution, and errors coming from the base distribution where it must be installed (Jaunty Jackalope Ubuntu 9.04), so it is not recommended for use in production computers and, in any case, it is recommend making a backup of important data before installation.

Within an ICT Center, Guadalinex Edu will take advantage of the network infrastructure and servers from the center to offer:

For domestic users, Guadalinex Edu is offered as a meta package to be installed on Ubuntu Jaunty and offers tons of applications like:

Plus all the benefits of Guadalinex:

And Ubuntu:

Installation instructions for home users are available here(In spanish)

If you have a Launchpad account, you can add comments and report bugs at the following addresses (if you do not have an account, you can register with Launchpad for one)

Comments:
https://launchpad.net/guadalinexedu/+addquestion

Bug reports:
https://bugs.launchpad.net/guadalinexedu

Original link in spanish here

Francois Marier: Safer synergy setup for laptop-desktop keyboard sharing

Synergy is a very useful piece of software for anybody wanting to share a mouse and keyboard between two networked computers.

Here is the setup I use to:
First of all, I've got the following ~/.synergy.conf on both of my laptop and desktop machines:
section: screens
mylaptop:
mydesktop:
end
section: links
mylaptop:
right = mydesktop
mydesktop:
left = mylaptop
end
section: options
keystroke(alt+shift+space) = switchInDirection(left)
keystroke(alt+space) = switchInDirection(right)
end

With this, I am ready to start the server on my desktop machine:
synergys -a localhost
Now, in order to encrypt the synergy client/server traffic, I create an ssh tunnel between the two machines:
ssh -f -N -L localhost:24800:localhost:24800 mydesktop
Then I start the synergy client on my laptop. However, some recent problems have convinced me to have a more robust alternative to simply starting the client like this:
synergyc localhost
As recommended by a few helpful people on #debian-devel, I decided to use the supervise tool (part of the daemontools package) to automatically restart the synergy client if it crashes. Here is how I do it:
supervise ~/.synergyc &
This command refers to a ~/.synergyc directory containing a single run script. That shell script consists of:
#!/bin/sh
xset r rate 500 30
/usr/bin/synergyc --no-daemon localhost

(The xset call is necessary since synergyc crashes seem to reset the repeat flag of X for some reason...)

The only problem I still need to fix in my setup is the potential password leak in the next few seconds after the synergy client crashes. Such a crash has already caused me to accidentally type my laptop password into a desktop IRC window the other day :(

Ideally, I would like the synergy server to swallow the first second or two of keyboard input after its client suddenly drops out. This could eliminate quite a few embarrassing wrong windows.

Julian Andres Klode: python-apt 0.7.10 released


I have just uploaded a version of python-apt 0.7.10 to unstable ( my first upload of python-apt, all previous uploads were done by Michael Vogt). This release is mainly a bugfix release, but also brings new features like apt.package.Version.uri and apt.package.Version.fetch_binary().I also added a Breaks: debdelta (<< 0.28~) because debdelta 0.27 is not working anymore since python-apt 0.7.9 and I expect that this problem will be fixed in 0.28, which could then use the new apt.package.Version.uri API to fetch the uris of the packages). Here is the changelog: python-apt (0.7.10) unstable; urgency=low
  • Build-Depend on python-debian, use it to get version number from changelog
  • Depend on libjs-jquery, and remove internal copy (Closes: #521532)
  • apt/package.py:
    • Introduce Version. uri,uris,fetch_binary()
  • debian/control:
    • Remove mdz from Uploaders (Closes: #521477), add myself.
    • Update Standards-Version to 3.8.1
    • Use $ binary:Version instead of $ Source-Version
    • Fix spelling error: python -> Python
  • debian/copyright: Switch to machine-interpretable copyright
  • Fix documentation building
    • doc/source/conf.py: Only include directories for current python version.
    • debian/control: Build-Depend on python-gtk2, python-vte.
    • setup.py: If pygtk can not be imported, do not build the documentation.
  • Breaks: debdelta (<< 0.28~) to avoid more problems due to the internal API changes from 0.7.9.
Julian Andres Klode <jak@debian.org> Wed, 01 Apr 2009 15:24:29 +0200 Have fun. Posted in Debian

Gerfried Fuchs: Twitter: "technically wrong"

It's quite interesting. Twitter has this snippet in its registration page: By clicking on 'Create my account' above, you confirm that you are over 13 years of age and accept the Terms of Service. At least currently when you click it leads you to a page that says: Something is technically wrong. I'm very happy to accept that, but I have this strange feeling that it's not what they intended to have there...

Stefano Zacchiroli: ocaml autoconf 1.0

1st release of ocaml-autoconf A couple of months ago, I joined an effort by Richard Jones to give a decent shape to autoconf macros for OCaml. The situation was a tad annoying before, because we had unofficial ocaml.m4 files floating around, which have diverged one from another, with unclear licensing terms, incompatible features, ecc. So we started a project on the ocamlforge to coordinate all this, injected the best we could find around, add docs, polish features, and contacted copyright owner to uniform licensing terms (to a 3-clause BSD). Yesterday we finally released ocaml-autoconf 1.0. Rich's blog post on the subject contains a nice how to to kick start your OCaml project using autotools up to automake. A brief feature overview is in order: Enjoy, and give us feedback (bug reports, feature requests, ...) using our tracker.

Andrew Pollock: [life] Rollerblading to work

I've moved buildings again, and am now the closest to home physically possible, which makes self-powered commuting less of a drag. Sarah's restarting her Certified Nursing Assistant course, in an accelerated mode this time, and started clinicals this week, which is at a skilled nursing facility in the opposite direction to work, so I rollerbladed to work today and yesterday. I managed to convince my phone to get a GPS lock today, so I used the very cool Android app, GPS Tracker, which when enabled, will report to InstaMapper's website as well as record a track. Here is today's commute in. GPS tracking powered by InstaMapper.com

Gustavo Noronha Silva: Joining Collabora

In other news, I am now working for Collabora! It is a great opportunity for me, and I will do my best to be on par with the great people that are now my colleagues. I have had the pleasure of working with Marco Barisione, and Pierre-Luc on WebKitGTK+, for some time, and some (most? =)) of them are also fellow Debian and GNOME developers, so I feel at home. Contributing to WebKitGTK+ and Epiphany is something I do as part of my job too, now, and I m not planning on dropping my volunteer contributions =). I have actually landed some patches, and worked on the 1.1.4 release with my @collabora.co.uk address already, and I hope the future holds more opportunity for such contributions!

31 March 2009

Kenshi Muto: Debian GNU/Linux device driver check & report version 2.0

I updated Web service 'Debian HCL - Debian GNU/Linux device driver check & report page' is an easy tool to check and see the support status of your hardware on GNU/Linux, with many improved features. Integrating the check page and submitted reports is convenience. The vendor tree view will make easier to find models what you'd like to see. Although Searching isn't implemented yet, I think new URL structure is friendly to search engine crawlers. I'll put Google search form on the page after Google crawls. Handling your submission is semi-automatic periodically. So please don't submit again and again even it won't be shown soon. :) This service is localized in English, Japanese, French, Spanish, Spanish-Argentina, Italian, Polish, German, and Portguese at this time, by using your Web browser language information. Because I introduced the GNU gettext system for internationalizing, it's easy to translate and update the translations. You can take template.pot file and translate in your language. If you'd like to translate in your language, please tell me. Have a fun!

Martin Meredith: vim, cherokee, etckeeper

Ok, so, today, I started using vim. I ve never really had the time before to learn how to use it. I think the most I d learned before today was just how to get out of vim if I ever accidentally got into it. Now, however, I m quite happy to do basic editing of files with it. I ve got to say, I m impressed with it s code highlighting features. I hope to eventually switch to vim permanently, but I m not that confident with it yet - my first command was nano ~/.vimrc *chuckles* Anyway, next comes cherokee. I m actually loving this webserver. It s so simplistic, yet so powerful, and it s admin interface is a dream. If anyone out there is interested in having a lightweight server, have a look at cherokee before you go and install lighttpd ! The most exciting new thing that I ve been using of late is etckeeper. (ok, maybe exciting isn t the word - but I like it!). This hooks into a RCS and basically keeps a track of your /etc/ folder. It will automagically commit changes made to it when using apt-get (or similar) and I ve actually set mine up to have bound branches. Meaning that my /etc/ is kept on a remote server. All my machines are now using etckeeper (with the exception of the eeePC, which is tucked away in a corner with a network lead plugged into the back, being used as a playground machine) and I m happy that if I ever have a hard disk crash, I can always get my configuration back from my server in a simple manner (which is massively useful for stuff like X). Anyway, just some stuff I ve been playing with of late. It seems I m switching more and more to the command line :D
Maybe I should start using w3m instead of Firefox?

Manoj Srivastava: Manoj: Fighting FUD: Working with openssl

Unfortunately, there is so much FUD associated with doing your own certificates, either based on how complex the operation is (which led to my previous supervisor insisting I use something like tinyca), and now to my employer succumbing to the FUD and shelling out several hundreds, perhaps several thousands, of dollars a year for something we could well have handled in house. Public key infrastructure, in the form of the X509 standard, is the underpinning of most of the secured communications over the net these days. The big winner in the transport protocols, TLS, and its predecessor, SSL, support X509 certificates. There are several ways of getting your own services their own X509 certs; one of which I am exploring below. One may, or course, opt to get a commercially signed certificate, and various companies are eager to do just that for you. They also charge about $400 per annum per certificate for the privilege of doing so. While there is some marginal benefit of doing so (some web browsers come with the commercial public certificate built in, allowing for an out of band distribution of the public cert), the benefit accrued is in the order or pennies, in my opinion, not hundreds of dollars, unless you are providing banking or retail services, where the end users might be justified in being paranoid. Why is there so much FUD your own certificates? Especially about how hard it is do to your own? As you can see below, it only takes three commands you have to master in order to set up your own private certifying authority, and sign your own certificates. The only marginal issue is that the user needs to verify your certificate out of band (if, really, they want to bother). Most people just accept the certificate, in my experience. The sole benefit that commercial entities provide is that they verify the identity of the person asking for the certificate, with varying degrees of diligence. For a Class 1 cert the CA usually just verifies that the email address of the requester was confirmed. For $400/year. For a Class two cert, they look up the company in a credit bureau records. A class 3 certs does an ID check with a notary public present, or a government issued ID. So, a class 3 cert is somewhat less diligent than becoming a Debian developer. Or getting your key signed at a Debian conference. As to the security aspects, or wondering whether to trust the information present on a designated web site, I have no idea how it helps verify any of those things in any way. So the web site is run by a person with a government provided ID, and who has a few hundred dollars to burn. So what? Me, I just sign my own certificates. And I think most small business web sites and mail servers are perfectly well served by using their own certificates. And there are just three simple commands that enable them to do this, in the Linux world. So what are these three commands? Gory practical details and recipes hidden here In conclusion, creating your own certifying authority is trivial, and certainly not worth several hundreds of dollars every year, and the functionality provided is identical.

Alastair McKinstry: With Speed and Violence: Why Scientists fear Tipping Points in Climate Change, by Fred Pearce

I bought With Speed and Violence: Why Scientists fear Tipping Points in Climate Change to investigate the concept of tipping points in climate change: how real are they, and what ones might exist. A lot of points are labelled 'tipping points', such as the melting of the Arctic; but, if we successfully reduced CO2 to pre-industrial levels, would they revert, or would we have passed a point of no return?

read more

Tags , ,

Sven Mueller: Link collection 2009/03

Well, I normally despise of thinks like this link collection, but I thought I might add it anyway, since these are useful links for me and if I don t post them here, I m likely to forget where to find them in the near future:
  1. Sean Finney has a nice post about storing the list of parameters a (shell) script got in a way that it can be restored later. Quite handy if your script walks through the arguments parsing them (and consuming them while doing so) but you want to be able to display them in a helpful way if the parsing fails at some point.
  2. A while ago, Ingo J rgensmann had a post that helps retrieving files from lost+found after a filesystem check, provided that you run his helper script on a regular basis. The same approach can also be used if you have a backup of all files, but lost the sorting work you did after the backup was done. This is possible because running the script can be done more often then you would normally do backups.
  3. He also has a small post about mtr oddities when IPv6 comes into play
  4. Adeodato Sim wrote about databases and when timestamps that store the timezone information really are more useful then timestamps that don t.
  5. Adeodato also has a short post on using ssh as a socks proxy, which can be quite handy if you are behind a firewall.
Update: Fixed link to Ingo s file retrieval from lost+found article. Thanks to Patrick Schoenfeld who pointed me at the wrong link.
Also thanks to the anonymous poster who found an alternative way to store and (in a way) restore commandline parameters. The solution doesn t work in an as general way as that by Sean Finney et al., but it is much shorter and therefore interesting for where it can be used (when you control how commandline parameters are processed). See comments on this post for details.

Next.

Previous.