Search Results: "ed"

20 May 2010

Wouter Verhelst: Dear lazyweb,

Can I instruct inkscape somehow that I do not want antialiasing to be used when I ask it to export a bitmap? Reason being that for what I'm trying to do, I need to limit the amount of colors used, and anti-aliasing adds quite a number of values that I don't want to be added. Thanks,

Michal Čihař: Playing with numbers and social networks

I'we just launched website (well it's quite pretentious name for few pages), which shows debts for politics when they were in government in Czech Republic. We're still not in situation like in Greece, but it can quite easily happen that we would be in few years and it's good to show some numbers describing what was happening in past. It took just few hours of coding yesterday evening using Django. Domain has been registered and it is online now. While doing such thing, I decided to make more fun for me and publish the link just on social networks (Identi.ca, Twitter, Facebook, LinkedIn) and follow if (and how) the link will spread. So no, you will not find link in this blog post :-).

Aigars Mahinovs: So, what is Microsoft Azure and how it compares to Amazon s AWS

We had a Microsoft salesperson stop at our offices today to tell people about wonders of cloud computing and Microsoft s Azure will save us all. The following is a short and non-exhaustive list of what Azure does not do according to their own experts: The Microsoft presenter also repeatedly engaged in shady tactics when presenting his information: So to summarize, Microsoft has build a cloud of Windows-like machines which can run your programs (as long as they are in .Net or Silverlight) and which does not have even a third of the features of such de-facto market leader as Amazon AWS. They try giving away their product for free and only get 14k applications in 6+ months. Note: Amazon has at least 300 000 public applications and God only knows how many more private ones. They will grow, due to companies locked-into Microsoft s way of thinking buying into their marketing, but if you have a head on your shoulders, you should avoid it as a trap, which it actually is. All that can be done on Azure, can also be done on Amazon. The opposite is not always true. In addition, if you will want have a mixed environment with both Windows and Linux servers, you will not be able to deploy Linux servers to Azure (or they will be very slow) and you ll have to put your Linux servers into Amazon (or another) cloud and pay double traffic fees for every byte of traffic between your own servers. Microsoft Azure prices are exactly the same as Amazon EC2 prices with Windows instances. However on Amazon you actually get fully capable Windows Server instances. And if you don t need Windows, you can get a much better price on Amazon. The only companies that can safely use Azure are companies that only have Windows servers AND plan to only have Windows servers for the foreseeable future. Knowing how dominant Linux is in the server market and how many Windows-only shops actually have a few Linux servers in the back room, there is very little future for Azure, until they wise up and make Linux instances first class citizens in their cloud. If not because their customers need them, then because their customers think that they at least might need them in the future. Update: Amazon now released a Reduced Redundancy storage for S3 that provides the exacts same level of storage guarantees that regular Microsoft Azure SLA (99.9%) for two thirds of the price, and also Amazons now explicitly says that their regular S3 is Designed for 99.999999999% Durability , which is worlds above what Microsoft provides. Now in this case Amazon again is cheaper than MS. Also Amazon bandwidth prices are 33% lower compared to Azure. In Azia the difference is simply staggering (0.45$ vs 0.19$ per Gb).

Dirk Eddelbuettel: RcppArmadillo 0.2.0 (and 0.2.1)

With the Rcpp 0.8.0 release on Monday, Romain, Doug and I were able to follow-up with a new RcppArmadillo release. RcppArmadillo uses Rcpp (and a few dozen lines of 'glue') to provide a transparent interface from R to Conrad Sanderson's impressive Armadillo library for linear algebra. This new release offers a number of key improvements: While we had tested this quite rigourously, the combination of some last minute changes that were meant to be stylistic-only, some troubles with the tests and builds at CRAN that were not apparent in all our tests (hint: do not yet use dynamic help features referencing other packages even if you have a Depends: on them) and an upcoming travel deadline meant that we missed a gotcha on Windows---so release 0.2.1 had to follow a few hours after the short-lived 0.2.0. More information is on the RcppArmadillo page. Questions, comments etc should go to the rcpp-devel mailing list off the R-Forge page.

Kees Cook: openoffice presenter console

During the Lucid development sprint, Pete showed me the glory that is the OpenOffice presenter console. Since then I ve switched laptops, and I figured I need to document for myself, and maybe others, how to have your OOo presentation on one screen (e.g. the projector) and the presentation notes, clock, etc, on another (e.g. the main laptop display). First, install openoffice.org-presenter-console , and once you have your displays configured, launch OpenOffice and select Slide Show / Slide Show Settings . From here, you can configure the displays under Multiple displays . So nice. :) UPDATE: corrected my typo. thank you! :)

19 May 2010

Dominique Dumont: Improve config upgrade Ep 02 Minimal model for OpenSsh s sshd_config

Hello Currently Config::Model can upgrade /etc/ssh/sshd_config file because Sshd model is complete. All 80 parameters mentioned in sshd_config man pages are described there. The whole model (including doc is about 1000 lines long). If one just want configuration upgrade capability, requiring a complete model is too much work. The aim of this GSoC project is to find a way to provide upgrades at a reasonable cost. Ep 01 focused on what feature was missing from Config::Model to provide a model that could handle unknown parameters in most cases to enable upgrades without a complete model. This covered the use case of an unmaintained model facing software evolution. Now, let s go on with the OpenSsh example and let s see what would be the minimal model that would enable upgrades from older sshd_config version to a more recent one. (Note that this blog is based on upgrade requirements mentioned in sshd_config man page). This will cover the use case of a maintained model targeted for upgrades. From last blog, we know that this minimal model must feature: Let s tackle the structure of this minimal model by re-using the current model structure. We will need 2 classes:
  1. Sshd: to handle all leaf parameters a the the Match parameter
  2. Sshd::MatchElement: to handle parameters within a Match block
Sshd::MatchElement will need to handle unknown leaf parameters (exceptd Match parameters), so its declaration should be like: 'Sshd::MatchElement' =>
accept =>
match_not => '/Match/i'' ,
type => 'leaf',
value_type => 'string'


Note that there s no element declaration. The accept structure means that Config::Model will accept any parameter that does not contain match in its name and will handle it as a string parameter. (Note that this feature is not yet implemented in Config::Model) Now, we must declare the main class: Sshd. It will feature the a wider accept statement and element declarations for the following parameters: Here we go: Any unknown parameter will be accepted by Sshd configuration class: accept =>
type => 'leaf',
value_type => 'string'
,
Here are the element that require a special treatment: Match just refer to the class declared above
Match =>
type => 'hash',
index_type => 'uniline',
cargo =>
type => 'node',
config_class_name => 'Sshd::MatchElement'
,
KeepAlive is the obsolete parameter. Parameter with status 'deprecated' are handled by Config::Model but will not be written back in the configuration file. Hence re-using the deprecated information elsewhere is more than recommended.
KeepAlive =>
type => 'leaf',
value_type => 'enum',
status => 'deprecated',
choice => [ 'no', 'yes' ]
,
Here's the new parameter. It's value is computed from KeepAlive.
TCPKeepAlive =>
type => 'leaf',
value_type => 'enum',
choice => [ 'no', 'yes' ],
migrate_from =>
formula => '$keep_alive',
variables => keep_alive => '- KeepAlive'
,
,
Now that we have the model, we must figure out how to read and write value with minimal coding efforts. Due to the mismatch between the syntax of the file (flat structure) and the actual structure (special Match parameter), a dumb parser/writer cannot be used. A parser that takes into account Match is required. Either dedicated Perl code (like the parser/writer delivered with Config::Model::OpenSsh) or use Augeas and its sshd lenses. In summary, we ve seen that the model required to perform upgrades is about 30 lines instead of the 1000 lines required for a complete model. On the other hand, the syntax of sshd_config makes the parser and writer harder to write. But, normally, this parser/writer should not evolve during the life of OpenSsh project. Now the question that I cannot answer is: Can a packager handle the extra work to maintain this minimal model ? Feedback is welcome here ;-) Next episode will study how upgrades based on Config::Model can be applied on files with other syntaxes. All the best

Daniel Kahn Gillmor: NYC SYEP still requires Microsoft Software

A year ago, i wrote about how New York City's Summer Youth Employment Program (SYEP) requires the use of Internet Explorer to apply online (and it even appears to require IE just to download the PDF of the application!) Sadly, the situation has not changed, a year later. Today, I'm writing to Dan Garodnick, Chair of The City Council's Committee on Technology (and the rest of the committee members), Carole Post, Commissioner of DoITT (the city's Department of Information Technology and Telecommunications), and Jeanne B. Mullgrav, Commissioner of DYCD (the Department of Youth and Community Development, which runs SYEP). Here's what i wrote:
For the last two years at least, the DYCD's Summer Youth Employment Program
(SYEP) has been only available to users of Internet Explorer:
 https://application.nycsyep.com/
Internet Explorer (IE) is only made by Microsoft, and is only available for
people running Microsoft operating systems.  Users of other operating systems,
such as GNU/Linux, Macintosh, or others cannot access the SYEP application
process.  Even users of Windows who care about their online security or simply
desire a different web browsing experience might prefer to avoid Internet
Explorer.
Not only is the online form inaccessible from browsers other than IE, even
retrieving a copy of the PDF to print out and fill in manually is unavailable
for web browsers other than IE.
What is the city's policy is on access to government sites?  Is it city policy
to mandate a single vendor's software for access to city resources?  Should NYC
youth be required to purchase software from Microsoft to be able to apply
for the Summer Youth Employment Program?
The sort of data collection needed by such an application is a mainstay of the
standards-based web, and has been so for over 15 years now.  There is no reason
to require particular client on an open platform.  I can point you toward
resources who would be happy to help you make the system functional for users
of *any* web browser, if you like.
I raised this issue over a year ago (see nyc.gov correspondence #1-1-473378926,
and a public weblog posted around the same time [0]), and got no effective
remedy.  It's worrisome to see that this is still a problem.
Please let me know what you plan to do to address the situation.
Regards,
	--dkg
[0] https://www.debian-administration.org/users/dkg/weblog/47
Feel free to send your own message to the folks above (especially helps if you live in or near NYC) Finally, Carole Post, the head of DoITT will also be present at a panel tonight in Soho, which i'm unfortunately be unable to attend. If you go there, you might ask her about the situation.Tags: policy

Julien Danjou: Announcing muse-blog

Digging into the fabulous world of Emacs and Lisp, I wanted to use it to build my personal Web site and my blog. I already moved from ikiwiki to Emacs Muse for my HTML pages some weeks ago. Muse provides an extension to maintain a journal, called muse-journal. Unfortunately, it was far to fulfill all my needs, and I decided that it would be a good exercise to write a better extension. Consequently, I started to wrote my own extension, which I named muse-blog. And this is now what is used to build this blog. :-)

Petter Reinholdtsen: Pieces of the roaming laptop puzzle in Debian

Today, the last piece of the puzzle for roaming laptops in Debian Edu finally entered the Debian archive. Today, the new libpam-mklocaluser package was accepted. Two days ago, two other pieces was accepted into unstable. The pam-python package needed by libpam-mklocaluser, and the sssd package passed NEW on Monday. In addition, the libpam-ccreds package we need is in experimental (version 10-4) since Saturday, and hopefully will be moved to unstable soon. This collection of packages allow for two different setups for roaming laptops. The traditional setup would be using libpam-ccreds, nscd and libpam-mklocaluser with LDAP or Kerberos authentication, which should work out of the box if the configuration changes proposed for nscd in BTS report #485282 is implemented. The alternative setup is to use sssd with libpam-mklocaluser to connect to LDAP or Kerberos and let sssd take care of the caching of passwords and group information. I have so far been unable to get sssd to work with the LDAP server at the University, but suspect the issue is some SSL/GnuTLS related problem with the server certificate. I plan to update the Debian package to version 1.2, which is scheduled for next week, and hope to find time to make sure the next release will include both the Debian/Ubuntu specific patches. Upstream is friendly and responsive, and I am sure we will find a good solution. The idea is to set up the roaming laptops to authenticate using LDAP or Kerberos and create a local user with home directory in /home/ when a usre in LDAP logs in via KDM or GDM for the first time, and cache the password for offline checking, as well as caching group memberhips and other relevant LDAP information. The libpam-mklocaluser package was created to make sure the local home directory is in /home/, instead of /site/server/directory/ which would be the home directory if pam_mkhomedir was used. To avoid confusion with support requests and configuration, we do not want local laptops to have users in a path that is used for the same users home directory on the home directory servers. One annoying problem with gdm is that it do not show the PAM message passed to the user from libpam-mklocaluser when the local user is created. Instead gdm simply reject the login with some generic message. The message is shown in kdm, ssh and login, so I guess it is a bug in gdm. Have not investigated if there is some other message type that can be used instead to get gdm to also show the message. If you want to help out with implementing this for Debian Edu, please contact us on debian-edu@lists.debian.org.

Martín Ferrari: Je ne veux pas travailler

That's a phrase I fully adhere to (I don't want to work), but that's not the point. There's a catchy song that I like a lot, it's sung in French and sounds like an old song (most places say it's an Edith Piaf's song). The chorus goes "Je ne veux pas travailler, je ne veux pas d jeuner...", and one would imagine that that's indeed the title. But nothing of this is true, once again the Internets is full of fail. The band who performs the song is called Pink Martini, two of them are the authors of it, and they are from Oregon. It was recorded in 1997 (some audio filters did the magic), and it's called "Sympathique". It also seems that it was a big success, but probably not in my part of the world. I thought that somebody should set this straight somewhere, as I couldn't find anybody speaking of this confusion. Having settled that, I invite you to listen to this wonderful song, and sing along that you don't wanna work (forget about the rest of the lyrics, it's a love song :-)). Tags: Planet Debian, Planet Lugfi, M sica

Russell Coker: Google Chrome and SE Linux

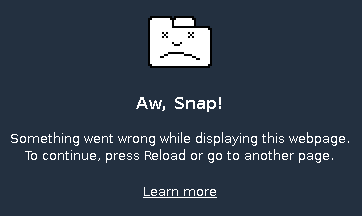
Google Chrome saying aw snap when it crashes [107108.433300] chrome[12262]: segfault at bbadbeef ip 0000000000fbea18 sp 00007fffcf348100 error 6 in chrome[400000+27ad000] When I first tried running the Google Chrome web browser [1] on SE Linux it recursively displayed the error message in the above picture, it first displayed the error and then displayed another error while trying to display a web page to describe the error. The kernel message log included messages such as the above message, it seems that some pointers are initialised to the value 0xbbadbeef to make debugging easier and more amusing. V8 error: V8 is no longer usable (v8::V8::AddMessageListener()) When I ran Chrome from the command-line it gave the above error message (which was presumably somewhere in the 8MB ~/.xsession-errors file generated from a few hours of running a KDE4 session). type=AVC msg=audit(1274070733.648:145): avc: denied execmem for pid=12833 comm= chrome scontext=unconfined_u:unconfined_r:unconfined_t:s0-s0:c0.c1023 tcontext=unconfined_u:unconfined_r:unconfined_t:s0-s0:c0.c1023 tclass=process
type=SYSCALL msg=audit(1274070733.648:145): arch=c000003e syscall=9 success=no exit=-131938567594024 a0=7fd863b41000 a1=40000 a2=7 a3=32 items=0 ppid=1 pid=12833 auid=4294967295 uid=1001 gid=1001 euid=1001 suid=1001 fsuid=1001 egid=1001 sgid=1001 fsgid=1001 tty=pts4 ses=4294967295 comm= chrome exe= /opt/google/chrome/chrome subj=unconfined_u:unconfined_r:unconfined_t:s0-s0:c0.c1023 key=(null)
type=ANOM_ABEND msg=audit(1274070733.648:146): auid=4294967295 uid=1001 gid=1001 ses=4294967295 subj=unconfined_u:unconfined_r:unconfined_t:s0-s0:c0.c1023 pid=12833 comm= chrome sig=11 V8 is the Google Javascript system which compiles JavaScript code and thus apparently needs read/write/execute access to memory [2]. In /var/log/audit/audit.log I saw the above messages (which would have been in the kernel message log as displayed by dmesg if I didn t have auditd running). The most relevant parts are that execmem access was requested and that it was by system call 9. From linux/x86_64/syscallent.h in the strace source I discovered that system call 9 on the AMD64 architecture is sys_mmap. Does anyone know a good way to discover which system call has a given number on a particular architecture without reading strace source code? Attempts to strace the Google Chrome process failed, Chrome gave the error Failed to move to new PID namespace after clone() failed. Clone was passed the flag 0 20000000 which according to /usr/include/linux/sched.h is CLONE_NEWPID. It seems that programs which create a new PID namespace (as Google Chrome does) can t be straced as the clone() call fails. It s a pity that Chrome doesn t have an option to run without using this feature, losing the ability to strace it really decreases my ability to find and report bugs in the program I m sure that the Google developers want people like me to be able to help them find bugs in their code without undue effort. Anyway the solution to this problem to allow it to run on the SE Linux Targeted configuration is to run the command chcon -t unconfined_execmem_exec_t /opt/google/chrome/chrome which causes the Chrome browser to run in the domain unconfined_execmem_t which is allowed to do such things. Of course we don t want Chrome processes to run unconfined, I think that the idea I had in 2008 for running Chrome processes in different SE Linux contexts is viable and should be implemented [3]. As a general rule if you are running a program from the command-line on SE Linux with the Targeted configuration (the default and most common configuration) then any time you see an execmem failure logged to the kernel message log or the audit subsystem then you can change the context of the program to unconfined_execmem_exec_t to make the problem go away. Note that this isn t necessarily a good thing to do, sometimes it s best to change the program to not require such access. But it seems that in this case the design of V8 requires write/execute memory access to pre-compile JavaScript code.

John Goerzen: Time to learn a new language

I have something of an informal goal of learning a new programming language every few years. It s not so much a goal as it is something of a discomfort. There are so many programming languages out there, with so many niches and approaches to problems, that I get uncomfortable with my lack of knowledge of some of them after awhile. This tends to happen every few years. The last major language I learned was Haskell, which I started working with in 2004. I still enjoy Haskell and don t see anything displacing it as my primary day-to-day workhorse. Yet there are some languages that I d like to learn. I have an interest in cross-platform languages; one of my few annoyances with Haskell is that it can t (at least with production quality) be compiled into something like Java bytecode or something else that isn t architecture-dependent. I have long had a soft spot for functional languages. I haven t had such a soft spot for static type checking, but Haskell s type inference changed that for me. Also I have an interest in writing Android apps, which means some sort of Java tie-in would be needed. Here are my current candidates: Of some particular interest to me is that Haskell has interpreters for Scheme, Lua, and JavaScript as well as code generators for some of these languages (though not generic Haskell-to-foo compilers). Languages not in the running because I already know them include: OCaml, POSIX shell, Python, Perl, Java, C, C++, Pascal, BASIC, Common Lisp, Prolog, SQL. Languages I have no interest in learning right now include Ruby (not different enough from what I already know plus bad experiences with it), any assembly, anything steeped in the Microsoft monoculture (C#, VB, etc.), or anything that is hard to work with outside of an Emacs or vim environment. (If your language requires or strongly encourages me to use your IDE or proprietary compiler, I m not interested that means you, flash.) Brief Reivews of Languages I Have Used To give you a bit of an idea of where I m coming from:

Bernd Zeimetz: new css for bzed.de

After more than a year of using ikiwiki to run bzed.de I thought it would be a good time replace the darkish-brown style by something bright. Also I wanted to get righ of the massive changes I had to do on the template files to make the old layout work. Unfortunately I hit one of the - in my opinion - major problems in the ikiwiki templates again: You can't rely on all <div>s being available on all pages, which is quite annoying when you need them to style the page with CSS. So I had to make a tiny change to page.tmpl:
diff --git a/templates/page.tmpl b/templates/page.tmpl
index 8a9911f..dbf78a0 100644
--- a/templates/page.tmpl
+++ b/templates/page.tmpl
@@ -111,8 +111,8 @@
 <TMPL_VAR CONTENT>
 <TMPL_IF HTML5></section><TMPL_ELSE></div></TMPL_IF>
-<TMPL_IF COMMENTS>
 <TMPL_IF HTML5><section id="comments"><TMPL_ELSE><div id="comments"></TMPL_IF>
+<TMPL_IF COMMENTS>
 <TMPL_VAR COMMENTS>
 <TMPL_IF ADDCOMMENTURL>
 <div class="addcomment">
@@ -121,8 +121,8 @@
 <TMPL_ELSE>
 <div class="addcomment">Comments on this page are closed.</div>
 </TMPL_IF>
-<TMPL_IF HTML5></section><TMPL_ELSE></div></TMPL_IF>
 </TMPL_IF>
+<TMPL_IF HTML5></section><TMPL_ELSE></div></TMPL_IF>
 <TMPL_IF HTML5><footer id="footer" class="pagefooter"><TMPL_ELSE><div id="footer" class="pagefooter"></TMPL_IF>
 <TMPL_IF HTML5><nav id="pageinfo"><TMPL_ELSE><div id="pageinfo"></TMPL_IF>
Everything else is a bit of CSS in local.css and some images. There are still various things which could be optimized, but there are more important things to do now :).

18 May 2010

Bernd Zeimetz: deb.li - the Debian ShortURL Service - status update

Although my progress in adding new features is not too fast (hint: patches and help is welcome), I'm quite happy with the progress of deb.li. As mentioned on my last post on debian-devel@l.d.o, I've spent some time to migrate it to the new, but very well written microframework Flask, which is based on Werkzeug, the probably most advanced WSGI utility module. The migration also allowed me to clean up several pieces of messy code which were necessary to work around some issues in python-bottle. Also I've started to bring the layout and CSS into a nice shape. The templates are finished already, just a bit CSS is missing now. Last but not least - the ciabot git script in the example clients is finished and used in a few git based projects on alioth.debian.org now. Just link /var/lib/gforge/chroot/home/users/bzed/godebian-client/ciabot.py to hooks/update and set your CIA project name by running git config hooks.cia-project your-project-name. As usual - comments, bugreports and patches are welcome!

Bernd Zeimetz: deb.li - the Debian ShortURL Service - beta test

After several other Debian developers convinced me that a ShortURL service, which is under control of a Debian Developer would be useful for them, I've spent some time to write the necessary code for it. And if it will be used regulary, I'll ask DSA if they want to host it on a proper machine. So I'm happy to announce the public beta test of deb.li (also available under go.debian.net)! Please note that neither the content of the pages nor the CSS is finished... :) As this should not become just another random, spammer-attracting ShortURL service, I will not provide a web based form to add new URLs. Instead new URLs have to be added via a simple JSON-RPC based interface. Other ways to add new URLs will be added on request (or by sending patches ;)), at least an email-gateway similar to db.debian.org is planned. The small piece of documentation which exists so far is available at wiki.debian.org/deb.li And if you want to give it a try now, log into alioth.debian.org and have a look into
/var/lib/gforge/chroot/home/users/bzed/godebian-client
- the usage is documented in the README file and should be pretty straight forward. I hope it will be useful - comments, bugreports and patches are welcome!

Bernd Zeimetz: gimp-plugin-registry package updated

Yesterday I finally found the time to update gimp-plugin-registry, the (hopefully!) largest and best collection of plugins for The GIMP. As usual here comes a short summary of the changes: Hope you like my work, suggestions and bug reports are welcome as usual!

Stefano Zacchiroli: debian maintainers list

on DMs and the packages they maintain The notion of Debian Maintainer (DM) has been with Debian for about 3 years. As of now, Debian has approximately 120 DMs, which maintain a significant part of the packages in the archive. I'm hereby happy to evilly spoil that Enrico Zini has just set up an index of Debian Maintainers and of the packages they maintain. The index is linked from the people section of our website as a symbolic step in giving more credit to DMs. Now, if anyone would like to setup a nice graph for the statistics page, which monitors the evolution of DMs (and DDs?), that would be useful.
Any idea on how to do that retroactively too?

Wouter Verhelst: Can I have my Debian back?

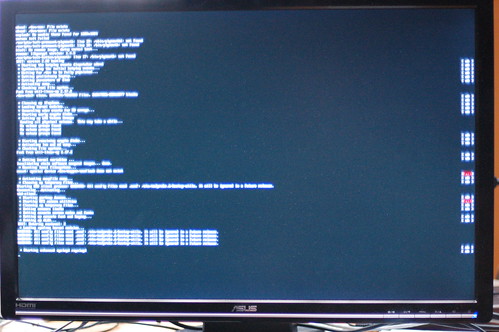
So someone thought it might be a good idea to switch the default from the time-honoured Debian style ("booting foo... ok") to the RedHat style ("<left-align>booting foo... <right-align>[ok]"). I don't think the switch adds any value (it's not like it looked bad or anything in the past); in fact, I think it's a bad idea. And I even have a technical reason. On my 26" 1920x1200 screen (when the i950 driver detects it properly and actually sets the framebuffer to that resolution), the output looks like this: bootscreen Now imagine you get to see that screen for about two to five seconds. Please tell me which two initscripts failed. And no, you cannot use a ruler. Bonus points for if you manage to do so while the text is also moving upwards, which tends to happen when systems boot. Also note that because kernel mode-settings has become the default, a lot more people are going to be using framebuffers. Am I the only one who thinks this is a bad idea?

Sune Vuorela: The Debian-KDE specific things II

I wrote a bit ago a blog post about what debian kde is missing of distribution specific things Some of the more important things includes: Installer
I don t think it is the most important thing. Wether or not the graphical installer is using gtk or qt is not that important. I would love to see it happen, but it is not something I feel like putting my time in. Others are most welcome.
It will give the advantage of giving the installer the possibility to use the framebuffer directly. Modules and firmwares and such
Someone is saying that ubuntu has something called jockey that does this exact thing, with a KDE and a Gnome frontend. Unfortunately, it is python, so it is something I will really avoid. I m hoping that me mentioning it here will make someone into python&debian pick it up and bring it to debian.
It is apparantly some nice magic around discover-data. Debconf frontend that fits
A lot of work has been put into proper perl-qt bindings and they will hopefully be ready for kde4.5, which is unfortunately a series too late for Squeeze :/. But when that has happened, we just need some perl guy to adapt the old frontend to debconf. Reportbug interface
There is already a tool called reportbug-ng that is a qt interface to reporting bugs. All in all, it looks like we are quite far already. We just need to get the last bits put together. Someone: pickup jockey. And note that the comment field isn t a place to report bugs. They will be removed.

Sam Hartman: Moonshot: Federated Authentication Beyond the Web

Recently, I ve been working on an exciting project with JaNet(UK) on a project to bring federated authentication to non-web applications. I ve worked on authentication projects a lot, although this is the first federation project I ve worked on. The big difference appears to be an emphasis on credential independence: the subject (person trying to authenticate) and service will not share a common credential type. Within their organization, the subject and their identity provider share a credential. Then, the federation has some credential mechanism such that the user s organization and the service share some (probably completely different) type of credential. The other emphasis is on providing personalization. For web applications, there are a lot of options to achieve this: Information Card, Open ID, SAML, and OAuth all provide solutions in this space. However there are not good options for non-web applications. If you out-source your mail and chat infrastructure but want to use your own chat client or IMAP client, then you will not get the same federation benefits you can get with the web. If you re using usernames and passwords and don t mind the potential problems with your out-sourcing provider being able to impersonate all your users, you can simply synchronize usernames and passwords. Within an enterprise, you can do better using Kerberos. JaNet(UK) runs the UK Access Federation, which is a SAML-based web single-sign-on federation. In order to better meet the needs of their customers they d like to expand this offering to non-web applications. This demand is apparently shared across the European academic community. I suspect there is also some demand in the US academic community and in enterprise situations. With the web, it turns out that you have a convenient platform for interactions with the identity provider: you can simply direct a web browser to the identity provider and need not specify the user interaction with the web browser at all. This is seen as a significant branding and usability advantage. With other environments, it becomes necessary to specify the interaction with the identity provider. Consider an automated client that wishes to examine a mail box and provide advanced mail sorting or aggregation. That automated client cannot directly use a web browser. OAuth solves this issue with an enrollment step that does typically involve a web browser that produces a consumer key and an authentication step that does not. However for non-web clients it seems like avoiding reliance on the browser authentication will be important. It turns out we already have widely used technologies that do this: the Extensible Authentication Protocol (EAP) mediates the interaction between a subject and identity provider for obtaining network access. It also turns out that we have fairly good technologies for abstract security services within non-web applications: thanks to Kerberos and Active Director, many application protocols and a fair number of applications support GSS-API. JaNet(UK) proposes to combine these technologies with SAML in order to produce a solution for federation beyond the web. I prepared a feasibility analysis of this proposal. At a technical level, the proposal is sound. There s a lot of standardization and implementation work, but there appears to be sufficient motivation to form the seeds of a standards activity and put together a proof-of-concept implementation. However, the big question is Will anyone use it? In particular, to be useful beyond fairly small communities, support from client vendors and application framework vendors will be needed. It s taken massive money and around 20 years to get Kerberos support to a point where it is effective within an enterprise. Moonshot can leverage that work to a large extent, but moonshot may also have greater usability and penetration goals. It s interesting that I m advocating EAP for application layer authentication. When I was a Security AD, I made a strong statement that EAP must only be used for network access. I ve been fairly consistent about that since then. I think there are two huge problems with using EAP for application authentication. The first is that EAP only authenticates the home realm; it does not authenticate what service you re going to. So you might try to connect to your e-mail and end up giving something access to your stored files and pictures instead. That is, EAP has a phishing exposure in the federated context. If the only thing you can get by using EAP is network access, that exposure is only moderate. However in a fully federated environment that is a huge exposure. Moonshot will address this problem by using EAP channel binding and by doing the necessary work to make that a viable solution. The second concern is that interoperability is reduced when you have multiple authentication approaches for the same problem. If EAP is going to be used for application authentication, we need to understand how it relates to the rest of the application authentication metasystem. Moonshot proposes such a relationship, addressing my objection. Moonshot is designed to work well with the objectives of the Identity Metasystem and its laws of identity. It uses a different technology, but does have an approach for dealing with claims-based identity and hopefully will have a user experience very similar to the identity metasystem. It uses a different underlying technology. However one of the main beliefs behind the identity metasystem is that is the user experience and universal interoperability that is important, not any specific technology. In its domain, the technologies Moonshot selects will be a better fit than a web services stack. It s strange not to be working on Kerberos; Moonshot uses some Kerberos technology, but its core is definitely not today s Kerberos. In some ways it is fun to be working on something new. There s one aspect of Kerberos I really miss: Moonshot has nothing like tickets. There s no place to remember state or exchange to directly involve the client in what the server learns. My analysis talks about ways to make Moonshot more like Kerberos; there are some potential advantages, but so far, the tradeoffs do not justify changes. We re hoping to have a bar BOF at IETF 77 and a BOF in the summer at IETF 78.

Next.

Previous.