
Do you use
GPG or
PGP to sign or encrypt your
emails and/or files?
This is a reminder to those who answered yes: make sure you have
a revocation certificate, as well as backups of your private/public
key pair, ideally in multiple
safe locations.
It s always a good idea to keep backups. But what is more
important with GPG is the revocation certificate. That s your
emergency brake. If someone ever gains control over your key, this
is the
only way for you to minimise (further) abuse of
your key and your identity.
However, even a revocation certificate won t be able to
prevent all abuse, by nature of the design of the GPG Web of Trust.
You also need to exercise utmost care in protecting your key and
making sure third parties cannot gain control over it. Do not keep
it on machines you don t trust, and make sure to use a safe,
non-guessable passphrase!
With GnuPG, generating a revocation certificate is as easy as
this; replace
$KEYID with your 8 or 16 digit
hexadecimal key ID:
gpg --gen-revoke $KEYID > $KEYID.revoke.asc
and store it away. Do
not import it until you need to
revoke your key!
In my case, the process was this; lines requiring my input are
prefixed with an arrow ( ):
  sec  1024D/330C4A75 2001-06-20 Martin F. Krafft <mail@martin-krafft.net>
  Create a revocation certificate for this key? (y/N) y
  Please select the reason for the revocation:
    0 = No reason specified
    1 = Key has been compromised
    2 = Key is superseded
    3 = Key is no longer used
    Q = Cancel
  (Probably you want to select 1 here)
  Your decision? 1
  Enter an optional description; end it with an empty line:
  >
  Reason for revocation: Key has been compromised
  (No description given)
  Is this okay? (y/N) y
  You need a passphrase to unlock the secret key for
  user: "Martin F. Krafft <mail@martin-krafft.net>"
  1024-bit DSA key, ID 330C4A75, created 2001-06-20
  ASCII armored output forced.
  Revocation certificate created.
  Please move it to a medium which you can hide away; if Mallory gets
  access to this certificate he can use it to make your key unusable.
  It is smart to print this certificate and store it away, just in case
  your media become unreadable.  But have some caution:  The print system of
  your machine might store the data and make it available to others!
I then printed the file, put it in the safe, stored it on a
removable disk and hid it away. Even though I exercise great care
over my key material, I can now sleep better at night, knowing that
I can at least minimise any damage done by an attacker who
compromises my key.
Also, that way I can make sure to declare unused keys as such,
since there is no other way to revoke a published key for which
you ve lost the private key or forgotten its passphrase. I ve left
such traces in my past and wish I had known what I was doing at the
time:
A8FA196E,
C22D1C01,
1EF0975C.
This is your chance to do it right. Make yourself a revocation
certificate
now (along with backups)! And always exercise
care and keep your key secure.
NP:
Mono:
One More Step and You Die
 Just got home from a wonderful concert by
Brad Mehldau at the
CSO. This was long overdue as I kept reading
about Mehldau. And even though he performs quite regularly around here, I
had never seen him. Big mistake.
The first set was performed as a (strictly acoustic) trio with Larry Grenadier on
bass and Jeff Ballard on drums.
After several compositions by Mehldau and a brazilian samba piece, the first
set closed with a rendition of 'Holland' from Sufjan Stevens' album
Michigan
which was truly beautiful. The second set had Mehldau performing solo, again
with several compositions of his own as well as one from Neil Young's classic 'The
Needle and the Damage Done' leading two two pieces from the Sound of Music
including an amazing, yet really different 'My favourite things' that just
hushed a piece of the central melody along with a strond rhythmic
element. Lovely. And then
to cap it all off, four encores.
Highly recommended.


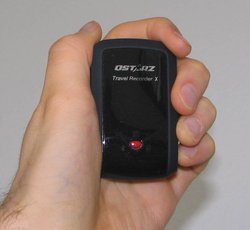 Spring has arrived in Europe and I'm looking forward to spending more
time outdoors. While I was pondering some plans, I thought it would be
nice to have a GPS. I've never used a GPS before but it seems it will
allow me to combine outdoors activities such as walking and hiking with
geek things. In particular, I'm interested in tracking where I'm going
(what route, what distance, what speed, etc), geotagging photos and
possibly contributing to OpenStreetMap. Since last week, I have a
Qstarz BT-Q1000X (Travel Recorder X), a GPS logger and receiver, and
I've been playing around with it a bit. This device uses the new MTK II
chip, which gives good accuracy and long battery time.
I've created a new gps category in which I'll share my
experience using a GPS in general and specifically the Qstarz BT-Q1000X.
I've also created a
 (The much-delayed part 2 in an ongoing series: shiny things in
telepathy-glib)


 Dear readers,
I m looking for a simple CMS, that would be usable by a non-programmer to write a simple website with less than 10 pages, not updated too frequently.
Requirements:
 Trying out simpleopal again, since my bug was closed.
It was January the last time I tried using iax, and
things were in a miserable state.
 I purchased my tickets and I'll be flying from Bucharest directly to Madrid on the 22nd and I'll be returning on the 30th. If somebody wants to fly with me on the same flights (although only the return seems more possible), please contact me privately*.

 Last few months since
 What seems like eons ago, I ordered one of those