Search Results: "ag"

18 May 2009

Marco d'Itri: Supporting unsupported USB devices

Some common classes of USB devices are supported by the same drivers because they share an identical or almost identical hardware design, but since each manufacturer uses its own Vendor and Product IDs the drivers need to be updated for each one. Some popular examples are 3G modems and devices which present a serial interface. As an interim solution until the kernel can be updated, the Linux device model provides a sysfs parameter called new_id which can be used to notify a driver that it should recognize a VID/PID pair as supported. The following example uses udev to add support for the Sheevaplug to ftdi_sio, the driver for the widely used USB to UART chips manufactured by FTDI. First we need a rule to automatically load the driver when the device is plugged in: udev cannot load it by itself since it does not know about the Sheevaplug VID and PID:
# if no driver has claimed the interface yet, load ftdi_sio
ACTION=="add", SUBSYSTEM=="usb", ENV DEVTYPE =="usb_interface", \
        ATTRS idVendor =="9e88", ATTRS idProduct =="9e8f", \
        DRIVER=="", \
        RUN+="/sbin/modprobe -b ftdi_sio"
And then we instruct udev to add the new VID and PID after the driver has been loaded:
# add the sheevaplug VID and PID to the list of devices supported by ftdi_sio
ACTION=="add", SUBSYSTEM=="drivers", \
        ENV DEVPATH =="/bus/usb-serial/drivers/ftdi_sio", \
        ATTR new_id ="9e88 9e8f"
While we are configuring udev we can also make it create a symlink for the console interface, since the FTDI chip in the Sheevaplug provides two serial interfaces: interface 0 is connected the JTAG lines and interface 1 to the serial console:
# create a convenience symlink for the console device
ACTION=="add", KERNEL=="ttyUSB*", \
        ATTRS interface =="SheevaPlug JTAGKey FT2232D B", \
        ATTRS bInterfaceNumber =="01", \
        SYMLINK+="sheevaplug"
This last rule shows an important misfeature of udev: while the keys ending in "S" can match nodes at any level of the devices chain, the matched nodes must be all at the same level. In this case this means that a single rule cannot have keys matching both the interface number and the VID and PID: this would require multiple rules and GOTO directives, so my rule matches the interface node which is available at the same level.

Ingo Juergensmann: IPv6 enabled WWW certification program

The IPv6 Forum offers a free WWW certification program and logo for IPv6 enabled sites. You can find there a ISP certification program as well.

Well, it's not a big deal. No rocket science. But I think it might somewhat help to raise awareness level for IPv6. When people see some IPv6 ready logos all around the web, they will probably start to wonder what this is all about and want to have that stuff as well. Ok, not the average Planet Debian reader, but others... ;)

There's just some caveats:
  1. At least when you use Serendipity and the HTML Nugget plugin you have to turn of "Perform Markup Transformations". Otherwise the plugin will insert some newlines in the script code that make it fail.

  2. Currently the script doesn't work with HTTPS, but that's being worked on and should be fixed in the next version.

  3. The script displays a rather wide (>200 px) logo with statistics of IPv6 visitors. The width may break your theming. But I was told by some gently IPv6 Forum staff that this can be changed.


So, please support IPv6 and participate in that certification program. It doesn't hurt you, but might help spreading IPv6!

17 May 2009

Joerg Jaspert: Weekend work

A good weekend work:
Day changed to 16 Mai 2009
NEW queue: 216
Now:
8 new source packages / 8 new packages in total.
Little statistic: Today: 23 reject, 104 accept. Yesterday: 11 reject, 107 accept At the end today both Mark and Mike helped or it would have stopped somewhere around 20. We also had a new trainee check his first few packages and generally getting it right. Working together in NEW, 3 people at the same time, even during (most of) dinstall - something that feels weird to an oldtimer like me. Until recently NEW always was just one person due to various problems you can manage to get when 2 people deal with one package. Or when a package gets copied into the accepted queue at the wrong time. (And some others) So I recently went and modified our tools to allow NEW to be done by multiple people. We now take locks per source package, do not copy directly into the accepted queue and only block during a very short timeframe of dinstall now. Something like 10 til 20 minutes instead of up to two hours (multiply that by four and you get 8 hours which we had been locked out of NEW in the past. Now its less than one (two) hour(s) a day). Whats left in NEW today is stuff waiting for various things to happen, like uploads of rejected dependencies, replies from the maintainer to our questions, such things. Saturday we also removed the last 2 of the first 3 ftptrainees (trainees, not slaves as that function got called earlier. Somehow someone somewhere found that a little offending. Tsk. :) ). All of them had less time for FTPTeam work than any existing team member, so not much point in adding any of them or continuing the training. At the same time we added one new trainee, lets see how that goes. As written above the first steps did work out good, but there is a lot to learn. :)

Martin F. Krafft: Switzerland opts for biometric passports

Switzerland voted today for the introduction of biometric passports, with 50.1% for and 49.9% against, one of the closest votes since 1848 (according to NZZ). While the news don t fill me with glee there are too many unanswered questions around the digital passports one aspect of the decision surprised and even shocked me. I do not like biometric passports, because I like to know when my data are consumed, and by whom. The German government assures that only authorised parties can access those data, and published information about the security features of the German biometric passports, but I am unconvinced that those are adequate to protection for the 10 years of validity of the passport. Furthermore, I could find absolutely no information on who the authorised parties are, or which regulations cover who will become authorised in the near future. If that was properly addressed, e.g. by leaving it up to me and only me to decide who gets access, then the digital passport could actually be a good step forward, streamlining border control and making travel easier. But there is a completely different avenue of concern, no matter who gives permission to whom to consume whose data: how are they used, and where, and how long are they stored, and for what? Again, I cannot find any regulations. Instead, my question to the German Department of the Interior was answered (!) along the lines of it being up to each country to decide themselves over the use and storage of the data. In this light, it makes little difference that the German procedure for the digital passport does not permit the issuing bureau to store the data, while Switzerland s strategy is to build a central database of all these personal details (this is what shocked me). It might make you wonder what use the Swiss government is hoping for, and you might feel uncomfortable with your government building up an even tighter database of its people. But I d much rather have my data stored in Switzerland than consumed and stored every time I enter another country, because when I compare the style of governance of Switzerland to pretty much anything else out there, I am glad I get to live here (even though I am not Swiss and cannot vote). Yet, it s a worrying step in a direction of the glass human , of a society in which personal privacy is unknown and everything is part of the system. These are totalitarian visions, and it s doubtful whether we ll ever actually get there (so far, I don t think any state has come up with the information management strategies required to properly store, make use, and read sense out of the massive amounts of information), but the trend is clearly visible. In the end, however, what worries me the most is how relaxed people treat their personal information these days. Look at the infamous social networking sites, or other Web 2.0 gimmicks and you really start to wonder how headless people can be these days. I cannot immediately paint a scenario where it might be dangerous to push all kinds of information about yourself to the masses, but the mere idea of that is scary in and of itself. I d prefer to have the choice with whom to share what data. The biometric passports, despite the advantages they might bring, are one step away from that, because they empower the government to make that choice for you. I don t consider that progress at all. Update: NZZ reports that the issue is not closed. In the cantons of Grishuna and Lucerne, people are challenging the vote and a recount or even re-vote seems possible. I will post an update as soon as I know more. Then, I would also like to address some replies I ve received over the real problems behind the digital passports, because it cannot be just the central data storage it s not like your government doesn t already have all that, and I can t imagine how your fingerprint could be used against you.
Holger Levsen: Appropriate talk about porn: it's abuse

Russel, I agree that some porn sites are facing interesting technical challenges, but I wouldn't suggest using them as example for anything, just like a talk about the challenges of torture is always inappropriate in a human society.

Porn is, except for self made porn and some other corner cases, abuse and oppression. Simple as that.

And please, before you try to argue against that simple statement, read the lyrics of no answer for a dancer from one of my favorite bands, consolidated, and think for more than ten minutes. If we were living in really free societies, porn could be fun.

Which reminds me of a quote from Rebecca L. Eisenberg: "A truly radical view of pornography recognizes that we are what we consume -- and if we are going to alter the face of society, and destroy Victorian and religious notions like gender altogether -- as I believe we must -- we must be willing to evaluate and change every aspect of our lives, including the images we feed ourselves as we fuck, as terrifying as it sounds. Like it or not, revolution is a scary concept." The complete text where this quote is from can be found online on her webpage.

P.S: If you hear me playing "the internet is for porn" (this musicalsong) or remember me doing so - can you now see the great irony? I would have hoped you've seen it before. Or at least wondered, what the hell I was doing.

Russell Coker: Appropriate Talks about Porn

There is currently some discussion about a talk which used pornographic imagery and jokes to illustrate points about Ruby programming [1]. A similar event happened in 2006 here is the description of the event from the author - which includes an unreserved apology [2]. It seems to me that the current discussion focusing on what is inappropriate for a public lecture is the wrong way to do it as there is a vast range of inappropriate material. I suggest that instead a white-list of appropriate references to porn in lectures will be more effective - if nothing else it makes for a much smaller list. Here is a first draft of such a list:

  1. Pornographic web sites handle a lot of traffic. There are significant technical problems that need to be solved. A lecture from an employee of an Internet porn company which covers the solutions to those technical problems would be of interest to many system administrators. Of course such a lecture should not promote the Internet porn company or show any samples of their products.

  2. Digital processing of images is an interesting topic. Having a digital editor from a magazine such as Vogue describe in detail how they do their job would be really interesting. There is a lot of overlap between the range of pictures displayed in Vogue and those displayed on porn sites. Having an employee of a porn company demonstrate how they touch up the picture of a fully clothed model would be an interesting technical topic, but of course it would be totally inappropriate to make any specific mentions of how the parts of the picture which are not PG-13 rated are edited. Even showing a picture of a porn star might be controversial, but I m sure that the same work could be reproduced with a photo of someone who has a more respectable career. Touching up a picture of RMS to make him look like a politician would make for a challenge for the presenter and an interesting lecture.

  3. The image known as Lenna is a photograph of a Playboy model named Lena that is widely used to test image compression [3]. While the image remains controversial, it seems to me that it would be impossible to give a complete and factual account of the history of image compression without mentioning it.

  4. The police have great discretionary powers to determine which crimes should be actively investigated. Senior police decide how many resources to assign to each case. I believe that in many jurisdictions the police will assign a much lower priority to a hacking case if the victim is running a porn service. Rumor has it that porn sites put a lot more effort into system security than most Internet services, partly due to not having as much protection from the police as other industries and partly because their customers don t want to be identified. I would be very interested in attending a presentation about practical computer security by a system administrator from a porn site. As an aside I m always interested in talking to people who do security work, so I would like to have a chat with someone who does such work for a porn site.

  5. A few years ago I attended a lecture about the security implications of porn surfing. It had some scary statistics on the number of porn sites that try to deploy malware on the computers of the people who view porn, and it made a good business case for banning porn at work without reference to HR issues (which is very relevant for the jurisdictions where viewing porn at work is not considered to be a social problem). I would like to see a new version of that talk with statistics based on more recent research, my theory is that modern porn sites are more toxic than the old ones due to the general increase in criminal activity on the net - but I have no evidence to support it.

Of course in all cases jokes about porn are not acceptable, mentions of porn need to be strictly on the basis of historical analysis or the description of technical and legal issues which are relevant to the audience. Delivering a talk about porn without inappropriate jokes would take a great deal of effort, but it can be done (and I ve seen it done once). For these five cases (and the few others that will probably be suggested in comments) it would probably be best if the conference organisers viewed the talk first to ensure that there was no misunderstanding about what is appropriate. I think that comparing a short list of specific cases where porn can reasonably be mentioned in a public lecture with the vast number of potential inappropriate references illustrates the probability of a random porn reference being acceptable. The probability of making a random porn reference that is appropriate is probably slightly less than that of winning the lottery.

Gunnar Wolf: Politicians time once again

It is time for stupid, empty politicians slogans once again in my dear country. And, as always, while we had lively, controversial presidential elections three years ago (and I won't rant this time on why so many Mexicans still believe the current president can only be called a de facto president), the mid-term elections... Fail to get any attention and cause only bored reactions. I am writing today mostly because I stumbled upon Francisco's post on why the Mexican Ecologist Green Party (PVEM) campaign does not impress him. As many, many other people with strong political opinions I know, I will go to the voting booth next July 5th, as I have done every time since I was of age - But I will most probably void my ballot, as I have found nobody worth my vote. And even if I am (and have always been) a leftist person, none of the four so-called leftist parties inspire the smallest bit of confidence. But hell, even the rightist or centrist parties fail to inspire confidence to their voters - After the 2006 electoral fiasco, we got a political system nobody believes in. And all analysts seem to concur that we moved from the most complete presidential regime to an utter partidocracy, where all of the (strong enough) parties cover each other's back not to lose the respective privileges (largely, money, but also law-making faculties and influence, which of course translates to impunity). Worth a very special mention is the crown jewel of political clowns in Mexico - PVEM, the Mexican Ecologist Green Party. A party that gets the gold medal for the most corrupt in our country (which is no small feat). A party where the National Party Presidents to date have only been father and son. And it is alarming because it is the only party apparently gathering more voters than they had before. But also, because of its utter pragmatism and lack of respect for anything they might once have stood for. I still remember on the 1994 elections, the first time they participated in general elections, their slogan was don't vote for a politician Vote for an ecologist... Little did the society know by then they were worse off than our oft-hated politicians. Can you imagine a so-called ecologist party that is expelled of the Global Greens as its behaviour is completely antithetical to anything a green party stands for? A party that promotes reinstating the death penalty (which was abolished from our Constitution, after decades of not being applied, less than a decade ago)? Or they say that, if a given medicine is not available at the Social Security hospitals, the government should pay the citizen so he can go and buy it at a drug store? (of course, if a needed medicine is not available at the Social Security it is most probably because the government is underfunded, not because the lazy administrators don't want to buy the medicines. And yes, with those two retrograde, stupid and -thankfully- completely unfeasible promises they have doubled their probable voters outcome in the past couple of months. The campaigns are only officially starting now. They are all really pathetic. A voter turnout of ~30% is expected. But yes, I am a politized person and just cannot help inviting everybody who has the right to go and vote. If there is somebody worth voting for in your district, please vote for him/her. However... Together with many people I admire, together with many of my friends, together with the people who still believe it is possible to make something out of this forsaken country's politic system... I invite you to void your ballots. Hopefully they will be enough so they must be heard this time.

16 May 2009

Wouter Verhelst: Belpic 3.5.2 has been released.

... and this time, with the source. Finally; it's been about a year since 3.5.0 came out without any source. That's not to say it's going to be in the archive tomorrow; they changed the build system (again), and the source has been overhauled to such an extent that it basically isn't even the same software anymore. I'll have to re-learn everything, make sure it builds properly, and hope to do so by the time squeeze releases. Yes, I realize that squeeze is still far away from release. Sigh. Perhaps this is a good project for debcamp...

Andrew Pollock: [tech] Deciding between the Lenovo T400 and X301

I'm in the market for a new laptop. I've got almost 4 years out of my Dell D610 (which I've been despising from not long after purchasing) and decided that I'll never buy from Dell again. I used to be very down on ThinkPads because of the placement of the Escape key, but since I've been using one at work for the last 3.5 years, I've gotten used to the Escape key location, and found the laptops themselves to otherwise be very solid and well supported by Linux. So Lenovo it is. Next question: T400 or X301? I've seen both, and the X301 is very sexy in terms of thickness, weight, and having all the latest bells and whistles, but boy, is it expensive. I did a side-by-side comparison between a T400 decked out the way I wanted, and an X301 decked out the best I could choose, and I've opted for the T400. The main problems I had with the X301 were that there was no choice of processor, and the processor available seemed significantly slower than what I could get in the T400, and of course the cost. I seemed to be paying nearly $1000 more for a slower processor, just to get something extra thin and light, with LED backlighting and an SSD disk. What finally swayed me to spending less money and getting an arguably "better" laptop was if I paid less now, I'd be more comfortable possibly getting something in less than 4 years time down the track. So if it came down to the X301 for 4 years or the T400 for 2 years, the T400 seemed like a better deal. What will hopefully end up happening is I'll end up using the T400 for four years and not end up hating it by the end of that time. Here's what I ended up going with: All of that plus a 2 year warranty and an additional 90W AC adapter came out at $1,240 (they have a 15% off discount code thing running until tomorrow, which brought the price down a bit) I'm particularly excited about not having a proprietary graphics chipset. I'm particularly unexcited about it including Windows Vista Home Basic. Drat, enumerating all of the options made me just realise that I seem to have omitted the 5-in-1 media reader from the final order. Oh well. That was largely just a nice-to-have anyway. Sarah tends to do all of the photo management on her laptop. I doubt this will get to me before Thursday, so I should have it waiting for me by the time I get back from Barcelona.

Joey Hess: one of those days

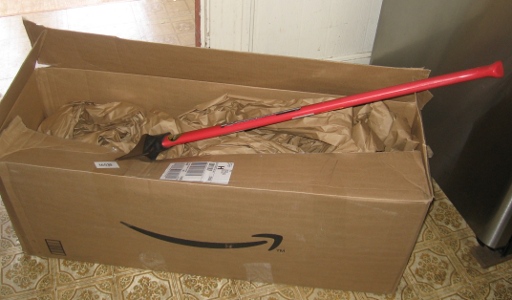
Some spring days just seem full to bursting with unusual experiences. I spent the night at the yurt and in just four hours today: big red axe Thanks to Iain M from Melbourne who writes, "We have never met. I have used your software and gained insight from your blog, over the years. So thanks. Also, I have never bought someone an axe before. This is cool." I forgot I had that in my wishlist, but now I can split wood with ease, when I run out of Amazon packaging material to burn.
Steve Kemp: Humans don't drink blood.

I've said it multiple times, but all mailing list managers suck. Especially mailman. (On that topic SELinux is nasty, Emacs is the one true editor, and people who wear furry boots are silly.) Having setup some new domains I needed a mailing list manager, and had to re-evaluate the available options. Mostly I want something nice and simple, that doesn't mess around with character sets, that requires no fancy deamons, and has no built in archiving solution. Really all we need is three basic operations: Using pipes we can easily arrange for a script to be invoked for different options:

# Aliases for 'list-blah' mailing list.
#
^list-blah-subscribe$:   " /sbin/skxlist --list=list-blah --domain=example.com --subscribe"
^list-blah-unsubscribe$: " /sbin/skxlist --list=list-blah --domain=example.com --unsubscribe"
^list-blah$:             " /sbin/skxlist --list=list-blah --domain=example.com --post"
The only remaining concerns are security related. The most obvious concern is that the script named will be launched by the mailserver user (Debian-exim in my case). That suggests that any files it creates (such as a list of email addresses - i.e. list members) will be owned by that user. That can be avoided with setuid-fu and having the mailing list manager be compiled. But compiled code? When there are so many lovely Perl modules out there? No chance! In conclusion, if you're happy for the exim user to own and be able to read the list data then you can use skxlist. It is in live use, allows open lists, member-only lists, and admin-only lists. It will archive messages in a maildir, but they are ignored for you to use if you see fit. List options are pretty minimal, but I do a fair amount of sanity checking and I see no weaknesses except for the use of the Debian-exim UID. ObFilm: Blade

Erich Schubert: Adobe GoLive question

Is there any way to provide an alternate CSS stylesheet for GoLive CS2 only, not for regular browsers? Because there are some things in that layout that are too difficult for the GoLive renderer, it doesn't display them right. The pages are still editable (just plain XHTML), it's just not looking right in GoLive (advanced CSS).The site already has alternate stylesheets for browsers such as the broken Internet Explorers, so if I could convince GoLive to use their stylesheet it might be looking a lot better in the editor, too ...I am aware that GoLive CS2 has been abandoned in favor of DreamWeaver. Still it's going to be used in a project I help with the web templates.(Other options would be Kompozer and Amaya, but none of them seem really fit for production use: Amaya was just removed from Debian because it had some security issues and the maintainers had the impression the code was such a mess that there will be much more such issues. And Kompozer seemed to be a mostly dead branch of a Gecko hack (although there has been a new alpha release this year) ... is there some reliable opensource non-source HTML editor that I'm missing?)P.S. Sorry, no comments in this blog. Use Email: erich AT debian ORG

Kartik Mistry: Indic Developers Meet 2009


* I reach Pune yesterday, had nice dinner with Gora, Ramky, Shantanu, Karaunakar, Both Raviji and Chacha Chaudhari :) Beer before and after dinner gave me awesome feeling during dream too! Met ankit/kushal and l10n folks after long time! Currently enjoying interesting session on Indic OCR using Tesseract by Debayan. Entire schedule is here. * Wiki Updates:
Development Track: http://www.indlinux.org/wiki/index.php/Development_track
Localization Track: http://www.indlinux.org/wiki/index.php/Localisation_track

Jaldhar Vyas: Classic Spock > Emo Spock

The original plan was to see the new Star Trek film on Mothers Day being the incurable romantic that I am but it didn't work out so we ended up going today instead. Overall we liked the film. It's best not to think about the plot too deeply or it will implode like red matter. (Red matter??? Are my children the scientists of the future? "I hereby name this new element Ballerinium") Anyway lots of jokes and explosions to keep your mind away from those kind of thoughts. As the title of this post suggests, I am not too fond of what they did with the Spock character. (Uhura Spock? Highly illogical.) The new Kirk is spot on as the green-alien-banging douchebag (amirite Uhura?) we know and love. And Chekhov, Scottie, and McCoy were great. The bad guy wasn't really that bad I thought. I hope they make the aliens badder and more alien in the inevitable sequels.

Antti-Juhani Kaijanaho: This is Alue

I have made a couple of references in my blog to the new software suite I am writing, which I am calling Alue. It is time to explain what it is all about. Alue will be a discussion forum system providing a web-based forum interface, a NNTP (Netnews) interface and an email interface, all with equal status. What will be unusual compared to most of the competition is that all these interfaces will be coequal views to the same abstract discussion, instead of being primarily one of these things and providing the others as bolted-on gateways. (I am aware of at least one other such system, but it is proprietary and thus not useful to my needs. Besides, I get to learn all kinds of fun things while doing this.) I have, over several years, come across many times the need for such systems and never found a good, free implementation. I am now building this software for the use of one new discussion site that is being formed (which is graciously willing to serve as my guinea pig), but I hope it will eventually be of use to many other places as well. I now have the first increment ready for beta testing. Note that this is not even close to being what I described above; it is merely a start. It currently provides a fully functional NNTP interface to a rudimentary (unreliable and unscalable) discussion database. The NNTP server implements most of RFC 3977 (the base NNTP spec IHAVE, MODE-READER, NEWNEWS and HDR are missing), all of RFC 4642 (STARTTLS) and a part of RFC 4643 (AUTHINFO USER the SASL part is missing). The article database is intended to support with certain deliberate omissions the upcoming Netnews standards (USEFOR and USEPRO), but currently omits most of the mandatory checks. There is a test installation at verbosify.org (port 119), which allows anonymous reading but requires identification and authentication for posting. I am currently handing out accounts only by invitation. Code can be browsed in a Gitweb; git clone requests should be directed to git://git.verbosify.org/git/alue.git/. There are some tweaks to be done to the NNTP frontend, but after that I expect to be rewriting the message filing system to be at least reliable if not scalable. After that, it is time for a web interface.

Marco d'Itri: Installing Debian on the Sheevaplug

This document explains how to use deboostrap --foreign to build from scratch and install a minimal Debian system on the Sheevaplug (but it is equally applicable to many other embedded systems). The only piece missing to be able to install from bare metal is a working kernel and initramfs pair, so this document assumes that you already have a kernel which can mount the root file system from a USB key. For the Sheevaplug, the factory kernel in the internal NAND flash will work fine. The Debian kernel package puts us in a chicken and egg situation: it cannot mount the root without an initramfs (because all drivers are modular), but we cannot build one until we can boot the system. I suppose that, as an exercise of style, somebody could create a minimal initramfs with busybox and the kernel modules needed to mount the root and then mount it manually, but if you really lack a working kernel then it's probably faster to boot the file system image for the first time using qemu and the "versatile" debian-installer target. The first step is to run the first stage of debootstrap on another system (which does not need to be ARM), to build a temporary root file system. I use the --variant and --include options to build the smallest possible system with network support, but they can be omitted.
debootstrap \
         --foreign --arch=armel \
         --variant=minbase \
         --include=linux-image-2.6-kirkwood,module-init-tools,udev,netbase,
                   net-tools,ifupdown,iproute,whiptail,vim-tiny \
         sid ./target/ http://ftp.it.debian.org/debian/
As usual when using debootstrap, some manual configuration is needed:
cd target/
echo bokassa.mi.bofh.it > etc/hostname
vi etc/network/interfaces
vi etc/resolv.conf
echo LANG=C > etc/default/locale
echo '127.0.0.1 localhost' > etc/hosts
cat <<END > etc/fstab
/dev/root / ext3 noatime 0 1
tmpfs /tmp tmpfs defaults 0 0
#/tmp /var/tmp none bind 0 0
END
I took some hints from http://wiki.debian.org/ReadonlyRoot to reduce writes to the flash file system:
# the blkid cache is evil anyway
ln -s /dev/null etc/blkid.tab
# this link will be created anyway by the package
ln -s /var/lib/initscripts/nologin etc/nologin
# it's better to not use a static mtab with modern kernels
ln -s /proc/mounts etc/mtab
# unless you plan to use multiple removable network interfaces, persistent
# interface names are not needed
: > etc/udev/rules.d/75-persistent-net-generator.rules
Two small workarounds are needed:
# if this is not set then the preinst of linux-image-* will die trying
# to ask a debconf question in the debootstrap second stage
echo 'do_initrd = yes' > etc/kernel-img.conf
# a workaround for bug #520742
: > etc/udev/disabled
Now you can format a USB pen drive and copy the root file system on it:
mke2fs /dev/sdb1
tune2fs -i 0 -c 0 /dev/sdb1
mount /dev/sdb1 /mnt/
rsync -aH target/ /mnt/
umount /mnt/
After powering the plug press a key to get to the U-Boot prompt and use the factory kernel to boot from USB:
setenv bootargs console=ttyS0,115200 root=/dev/sda1 rootdelay=10 panic=10 init=/bin/bash
run bootcmd
Then you can run the second stage of debootstrap, finish the bare minimal configuration and start init:
./debootstrap/debootstrap --second-stage
# disable the gettys for /dev/tty[1-6], which do not exist
vi /etc/inittab
# and add one for the serial console
echo 'T0:2345:respawn:/sbin/getty -L ttyS0 115200 linux' >> /etc/inittab
# do not forget to set the root password or you will not be able to login...
vi /etc/shadow
rm /etc/udev/disabled
exec /bin/bash
mount / -o ro,remount
exec /sbin/init
Congratulations, now you can login on the system and start to install the packages you like:
echo 'deb http://ftp.it.debian.org/debian/ unstable main' > /etc/apt/sources.list
echo 'APT   Install-Recommends "false";  ;' > /etc/apt/apt.conf.d/no-recommends
apt-get update
# dash is much faster
apt-get install dash
dpkg-divert --add /bin/sh
ln -sf dash /bin/sh
# I do not like these, YMMV
rm /vmlinuz /initrd.img
rmdir /selinux /srv
# the kernel is able to read the time from the RTC by itself, and this
# will allow using a read only root
echo HWCLOCKACCESS=no >> /etc/default/rcS
# faster boot
echo CONCURRENCY=shell >> /etc/default/rcS
# useless on this platform
mv /etc/rcS.d/S01glibc.sh /etc/rcS.d/K01glibc.sh
dpkg-reconfigure tzdata
apt-get install openssh-server screen iptables wget less
U-Boot requires that the kernel and initramfs have a special header:
apt-get uboot-mkimage
cd /boot/
mkimage -A arm -O linux -T kernel  -C none -a 0x00008000 -e 0x00008000 \
  -n Linux-2.6.29-2 -d vmlinuz-2.6.29-2-kirkwood uImage
mkimage -A arm -O linux -T ramdisk -C gzip -a 0x00000000 -e 0x00000000 \
  -n initramfs -d initrd.img-2.6.29-2-kirkwood uInitrd
Now you can reboot and configure u-boot to boot from the USB device. This is the variables scheme I like and it is not mandatory in any way, so I recommend that you read and understand the existing configuration before modifying it (some lines have been broken for readability):
setenv bootargs_nand $(bootargs)
setenv bootcmd_nand $(bootcmd)
setenv bootargs_root root=/dev/sda1
setenv bootargs_misc 'ro panic=10
  mtdparts=nand_mtd:0x400000@0x100000(uImage),0x1fb00000@0x500000(rootfs)'
setenv bootcmd_usb 'usb start; ext2load usb 0:1 0x00200000 /boot/uImage;
  ext2load usb 0:1 0x01100000 /boot/uInitrd'
setenv bootcmd 'setenv bootargs $(console) $(bootargs_root) $(bootargs_misc)
  $(bootargs_more); run bootcmd_usb; bootm 0x00200000 0x01100000'
Since now you are not using anymore the Marvell kernel tree it is mandatory to set these two variables and reboot:
setenv mainlineLinux yes
setenv arcNumber 2097
saveenv
reset
Installation to SD is identical, but requires an updated version of U-Boot with SD support. Due to a kernel bug which prevents autoloading the driver you will need to add mvsdio and mmc_block to /etc/initramfs-tools/modules and rebuild the initramfs. (Yes, the naming theme I use at home is "african dictators"...)

15 May 2009

Philipp Kern: Infinote-based Gobby hits Karmic

Gobby 0.5 (or to be more precise 0.4.92) just hit the Karmic Koala. Below you can see a screenshot of the new version (just click on it to get a large version). It is sadly not protocol compatible to the old version but it features local undo and redo! Furthermore it's not yet stable on-the-wire wise. The software itself is fairly stable but it could be a bit bumpy if the server protocol version goes out of date. Gobby 0.4.92 thumbnail If you want to try it out on earlier versions, I offer backports in the Infinote PPA for Intrepid and up. I hope to get to Hardy soon, sadly it needs some more backports. There is a public server available on gobby.0x539.de if you want to try it out (connections are encrypted, but all contents are public and can be deleted by everybody, wiki-like; so please be considerate and non-destructive). On local networks Gobby will look for servers through Avahi. That said Gobby is not yet able to host servers by itself, like the old version did. You have to install the infinoted server. You can do this on any computer, even on the local network and take advantage of Avahi. If you want encrypted connections you need to create certificates but if an unencrypted session is acceptable you can get an ad-hoc server by invoking infinoted --security-policy=no-tls without further configuration. It will persist content across invocations, too. Thanks to Greg Heynes, there will also be a KDE client for Gobby, called... Kobby! The first time someone actually uses the fact that the software uses a library for interoperability. Interesting that it's done now when the library's C instead of C++ (which obby was written in), with Qt being C++ anyway. I'm not yet aware of packages but I really hope that we can release with both. If you encounter problems, please report them to our Trac (preferred) or Launchpad.

Bdale Garbee: Altus Metrum Logo

Thanks to my wife Karen's graphic design skills, and Keith's SVG-foo, the Altus Metrum group of projects now has a logo!

Jordi Mallach: 31

So, today I turn 31. Fortunately I've had a year to learn that the thirties change nothing, and looking back, I can easily say I've enjoyed one of the best years I remember. Today, a bit of protesting in the Pla a de l'Ajuntament against the old menaces of the Valencian Botanical Garden, and just after that, beer time around the Cedre area. The amount of email, Facebook stuff and calls I've been getting today since I woke up is impressive. Thanks everyone! ;)

Neil Williams: svn-buildpackage

I'm adopting svn-buildpackage and I've made a few commits via collab-maint already. So #528733 is now mine.

I expect to be working with Jan and anyone else who wants to work on the svn-inject and svn-upgrade functionality that I don't use personally. For this reason, I've re-opened #377467 as an RFH.

I use svn-bp for a lot of my own packages and I'm not going to use git if I can possibly avoid it (quite possibly, ever). The current collab-maint changelog is already long enough so I won't be making many changes prior to the first upload to close the ITA. However, once that is done, I'll be looking at Jan's 0.7 branch code and gradually working through the rest of the bugs.

It's not as if I have a huge amount of time available for svn-bp, so things will take time, but it can't stay orphaned.

Next.

Previous.

