Search Results: "ed"

12 June 2010

Bernd Zeimetz: styling changes in ikiwiki 3.20100610

Some minutes before the release of 3.20100610 we convinced Joey in #ikiwiki to commit the following changes: We hope that nobody wants to hit us with a bat now :-)

11 June 2010

Bernd Zeimetz: merkaartor 0.16.0 available in unstable

Merkaartor 0.16.0 was uploaded to Debian/unstable several days ago and should be available on all architectures now. Merkaartor As usual please help testing the new version - upstream and me will try to fix all bugs as fast as possible. Below follows the long list of new features, for the full list of changes see the CHANGELOG.

Petter Reinholdtsen: Automatic upgrade testing from Lenny to Squeeze

The last few days I have done some upgrade testing in Debian, to see if the upgrade from Lenny to Squeeze will go smoothly. A few bugs have been discovered and reported in the process (#585410 in nagios3-cgi, #584879 already fixed in enscript and #584861 in kdebase-workspace-data), and to get a more regular testing going on, I am working on a script to automate the test. The idea is to create a Lenny chroot and use tasksel to install a Gnome or KDE desktop installation inside the chroot before upgrading it. To ensure no services are started in the chroot, a policy-rc.d script is inserted. To make sure tasksel believe it is to install a desktop on a laptop, the tasksel tests are replaced in the chroot (only acceptable because this is a throw-away chroot). A naive upgrade from Lenny to Squeeze using aptitude dist-upgrade currently always fail because udev refuses to upgrade with the kernel in Lenny, so to avoid that problem the file /etc/udev/kernel-upgrade is created. The bug report #566000 make me suspect this problem do not trigger in a chroot, but I touch the file anyway to make sure the upgrade go well. Testing on virtual and real hardware have failed me because of udev so far, and creating this file do the trick in such settings anyway. This is a known issue and the current udev behaviour is intended by the udev maintainer because he lack the resources to rewrite udev to keep working with old kernels or something like that. I really wish the udev upstream would keep udev backwards compatible, to avoid such upgrade problem, but given that they fail to do so, I guess documenting the way out of this mess is the best option we got for Debian Squeeze. Anyway, back to the task at hand, testing upgrades. This test script, which I call upgrade-test for now, is doing the trick:
#!/bin/sh
set -ex
if [ "$1" ] ; then
    desktop=$1
else
    desktop=gnome
fi
from=lenny
to=squeeze
exec < /dev/null
unset LANG
mirror=http://ftp.skolelinux.org/debian
tmpdir=chroot-$from-upgrade-$to-$desktop
fuser -mv .
debootstrap $from $tmpdir $mirror
chroot $tmpdir aptitude update
cat > $tmpdir/usr/sbin/policy-rc.d <<EOF
#!/bin/sh
exit 101
EOF
chmod a+rx $tmpdir/usr/sbin/policy-rc.d
exit_cleanup()  
    umount $tmpdir/proc
 
mount -t proc proc $tmpdir/proc
# Make sure proc is unmounted also on failure
trap exit_cleanup EXIT INT
chroot $tmpdir aptitude -y install debconf-utils
# Make sure tasksel autoselection trigger.  It need the test scripts
# to return the correct answers.
echo tasksel tasksel/desktop multiselect $desktop   \
    chroot $tmpdir debconf-set-selections
# Include the desktop and laptop task
for test in desktop laptop ; do
    echo > $tmpdir/usr/lib/tasksel/tests/$test <<EOF
#!/bin/sh
exit 2
EOF
    chmod a+rx $tmpdir/usr/lib/tasksel/tests/$test
done
DEBIAN_FRONTEND=noninteractive
DEBIAN_PRIORITY=critical
export DEBIAN_FRONTEND DEBIAN_PRIORITY
chroot $tmpdir tasksel --new-install
echo deb $mirror $to main > $tmpdir/etc/apt/sources.list
chroot $tmpdir aptitude update
touch $tmpdir/etc/udev/kernel-upgrade
chroot $tmpdir aptitude -y dist-upgrade
fuser -mv
I suspect it would be useful to test upgrades with both apt-get and with aptitude, but I have not had time to look at how they behave differently so far. I hope to get a cron job running to do the test regularly and post the result on the web. The Gnome upgrade currently work, while the KDE upgrade fail because of the bug in kdebase-workspace-data I am not quite sure what kind of extract from the huge upgrade logs (KDE 167 KiB, Gnome 516 KiB) it make sense to include in this blog post, so I will refrain from trying. I can report that for Gnome, aptitude report 760 packages upgraded, 448 newly installed, 129 to remove and 1 not upgraded and 1024MB need to be downloaded while for KDE the same numbers are 702 packages upgraded, 507 newly installed, 193 to remove and 0 not upgraded and 1117MB need to be downloaded I am very happy to notice that the Gnome desktop + laptop upgrade is able to migrate to dependency based boot sequencing and parallel booting without a hitch. Was unsure if there were still bugs with packages failing to clean up their obsolete init.d script during upgrades, and no such problem seem to affect the Gnome desktop+laptop packages.

Norbert Tretkowski: DRBD source dropped from Debian unstable

OK, not really... DRBD 8.3.7 is an official part of the Linux kernel since 2.6.33, and thanks to Dann Frazier we also have a backport of that patch in Debian's 2.6.32 kernel as well.

Until yesterday, the DRBD source package in Debian built a -utils and a -source package, the latter was now dropped. From now on, users no longer need to recompile the DRBD module after a kernel upgrade.

David Watson: Photo Scope android app released

I have now released an android app I have been working on recently. Photo Scope allows you to take photos with your phone and keep track of where each one was taken, so you can return when you have your camera or maybe when the weather is better and take the perfect shot. You can take a look here for more details.

MJ Ray: Koha in Book Industry Communication

Our co-op has joined Book Industry Communication as an associate member, mainly in order to voice experiences of the Koha community and ourselves about RFID tag standardisation and related sustainable development. I want us to give the Free and Open Source Software library world and our charity and academic clients more input in developing this big change to libraries. Even so, it wasn t an easy decision to join. I still believe that RFID standards development would be better done in an open forum, but there doesn t seem to be a perfect choice and I don t think we can create one. BIC already has cross-sector support and seems much more open than the so-called RFID Alliance . Pragmatism was enough, this time, and so far BIC seems friendly and welcoming. I see that a larger service provider co-operative, OCLC (UK), is also a member, so hopefully that means it s safe for co-ops. I think most of the readers of this will be free software developers, koha users and/or members of other co-ops. So, I ask you, what do you think of this move? Leave me a comment on our blog or email me if you prefer to keep it private.

Rapha&#235;l Hertzog: About the Debian Community Poll

While I find the idea interesting, several of the questions can t be correctly answered because the proposed choices are not realistic or too limited. On the question of the usage of money, I believe we should spend money to fund important projects but I don t want to fund people having important positions in Debian and doing important work . What should I reply? (Granted, there s the other item but that doesn t help getting a clear picture of the answers) On the question Do you prefer time based releases instead of the it s ready when it s ready releases? , it is putting two concepts in opposition when the release managers recently proposed a third way that combines both: time based freezes and release when it s ready . This is what I want and I can t adequately express it either in the current poll. Partagez cet article / Share This

Jan Hauke Rahm: MiniDebConf in Berlin, now

Good morning everyone, after quite some time of organization, we got the MiniDebConf running in Berlin. Yesterday at 9.30, Zack had the pleasure of opening the event which seems to be reflected in the press already. After that, we had nice talks, one every hour from 10 to 6 with mine being the last one of the day at 5 p.m. Yes, I did it :) Slides, links, and all that stuff will follow in a later post, or more official announcements. Right now I m preparing myself to get back to the fairground. The second day starts with another bunch of talks at 10 and I m excited to meet different people again and hear more interesting talks. The BSP went well. :) Actually, we didn t really fix many bugs, I guess. A few maintainers stayed after the event as well as a couple of users completely new to packaging. Thus, it was more like a small social event bit it was really fun. And of course the HackLab is still open today, so we have every chance to fix more bugs This just as a small input from where we stand. More is to come some time later, probably after the weekend, we ll see

10 June 2010

David Welton: Ok, first one on the block: leenooks.com

The problem with selling off these sites is that I am a bit attached to them emotionally. Leenooks.com is a cool domain, I think - it's how Linus pronounces Linux, supposedly. It's also one of the first sites I put together: the original version was done in Perl with CGI back in ... '97? The current incarnation runs on DedaWiki a wiki I put together that is built with Ruby on Rails.
The idea behind the site was that, rather than keep track of all the hardware out there that works well with Linux, let's focus on the stuff you really want to avoid as that is a smaller set of things, and hopefully one that, one day, will be empty! It seems to have been fairly popular over the years, and has helped pay for the server it runs on. However, "popular" doesn't necessarily translate into "oodles of money", and especially now that I have a daughter who is a lot of fun to play with, I need to cut back on my "spare time" projects. So this one is the first one up on the auction block. I fervently hope that whoever acquires it can dedicate a bit more time and energy to making it do what it does, only better.

Rog rio Brito: A version of xpdf with the poppler backend available

Well, it s been some time since I last wrote here and things are quite hectic, due to some real-life happenings. Announcement For those people that are insterested in a small PDF viewer, based on an actively maintained backend, and that doesn t bring your computer to a halt when you try to zoom your documents when you need to see some details, then you might want to give this version of xpdf a try. I already received some reports for some bugs and fixed them, with one of them being a problem related by a kind user of Gentoo. Motivation Some people have asked me why this even needs to exist in the first place and I agree that it would be better if it didn t: I would love to spend my time actually using my computers rather than fixing my computers for better tasks (read: studying Mathematics, etc). The upstream maintainer of xpdf uses it as one source of income and keeps it running across many system (even legacy ones). I imagine that this one of the reasons why he tries to keep xpdf almost self contained, with many parts that could be delegated to other libraries, and with some abstraction code that makes the code compile even in the presence of very broken compilers. Of course, this means, in part, that as long as you take more duties, maintaing the code becomes more and more complex. He told me that he doesn t offer an open development tree because he wants to give his customers some advantages over the public version and his reasons are perfectly justifiable, of course. He also manifested the interest of possibly basing xpdf on a more modern toolkit and, when I asked him what that would be, he mentioned that, perhaps, it would be Qt. The development of xpdf will, quite probably, take newer directions. Unfortunately, xpdf has not seen a new upstream release since 2007-02-27. It did, though, have some patchlevel updates released. Taking care of the maintainance of the code is a high concern for distributions. Some people, though, would like to keep it simple (me included). Unfortunately, some efforts to maintain it had not had the necessary coordination and duplication of effort has occured. Proposal I am willing to become a patch aggregator for the code in xpdf with a poppler backend. I would love to give it some refactoring too, drop some of the legacy code that is not used (and only serves to make the code hard to read), and adopt some good coding style standard (I particularly like the one from the Linux Kernel with the proper adaptations for C++). I have already contacted the people at Gentoo, and I would love to get people from Fedora, Ubuntu, and Suse involved also. Alas, the last time I tried to mail their mailing lists, I got messages telling me that my messages were rejected or waiting for moderation, because I was not a subscriber. I never heard back, since. I appreciate it if you could help spread the word. Thanks.
Lior Kaplan: Israeli projects for improvement of government services go open source

In an business open source conference held today (June 10th) in Tel Aviv, Michael Eitan, Minister of Improvement of Government Services, said that projects under his responsibility will go open source to improve transparency. More info at TheMarker (in Hebrew, English version by Google translate). A pilot with a focus group should begin soon for testing the changes.
Filed under: Israeli Community

Russell Coker: Logging Shell Commands

In response to my previous post about logging in directly as root [1] it was suggested that using sudo is the only way to log the commands that are entered as root. One reason for doing this is if you don t trust the people who are granted root access and you want to log all commands to a remote server that is run by different people. I wonder whether it is really possible to run systems with untrusted sysadmins, if someone can apply patches etc then they can surely install a trojan and then wait a while before activating it to make things more difficult for anyone who is analysing the logs. One of the many issues is that even the restricted version of vim permits the :r and :w commands, so one could start vim from sudo with an innocuous file as the target of the edit operation and then read and write some critical file such as /etc/shadow. I expect that someone has written an editor which has a restricted mode that doesn t allow reading/writing files other than the one specified on the command-line, and if not it surely wouldn t be difficult to patch vim (or your favorite editor) to have such a mode of operation. But there are always other programs that can access files other than the ones specified on their command-line. It seems that using the auditctl interface to log access to certain critical files (EG read access to /etc/shadow and write access to everything under /etc, /bin, /sbin, and /usr) would be a necessary part of an effective auditing strategy and that sudo would only comprise a small part of a useful configuration. There are other viable ways of logging everything that is done as root which offer benefits over sudo. Ways of Logging Shell Commands The Korn shell supports doing all the logging you might desire as part of a shell function [2]. Bash can have a similar shell function to do the logging, but when a command is entered the previous command is logged [3], this means that any single bash command that unsets this will never be logged. It might be possible to solve this if you know more about Bash than I do. I wonder if the Korn shell function has the same issue. This is still probably useful for some situations when you want to track what honorable sysadmins do, but of little benefit for tracking hostile sysadmins (tracking hostile sysadmins is actually possible). You can put code in a file such as /etc/bash.bash_logout to log the commands elsewhere, but even trivial things such as kill -9 $$ can defeat that so it s only useful when the sysadmin is trusted. The Sudoshell project exists to log all data that is entered in a shell [3]. One deficiency of this for the people who don t trust the root user is that it logs the data to files on disk, but it shouldn t be difficult to rewrite sudoscriptd to write directly to another machine over the network. Also one benefit of this for auditing is that it captures all the output of the commands as well (which can be a little inconvenient to decipher when curses programs are run. The web site also describes some of the problems with trying to use sudo directly for everything (such as pipelines). If you compile Bash version 4.1 with the SYSLOG_HISTORY macro enabled (which can be done by editing the file config-top.h) then it will log all commands to syslog. RootShell.be has a short post about this which mentions the security issues, some commands take passwords as parameters and these passwords could be exposed to the network [5]. Of course the best option is to just avoid such commands. Thanks to Chris Samuel for pointing out the Bash logging feature. Conclusion If you use sudo for auditing root access then you lose some shell functionality. Sudo also only logs the commands that are executed you don t get logging of output. It seems that depending on the exact needs either a modified version of Sudoshell or the logging that can be compiled in to Bash would be the way to go depending on the exact requirements. The main benefit of using sudo for logging would be that some distributions of Linux are configured that way by default but it seems unlikely that someone would go to the effort of running a separate logging server that the regular sysadmin team can t touch and then configure their servers in a default manner.

Dirk Eddelbuettel: Rcpp 0.8.2

A bug fix release Rcpp version 0.8.2 is now on CRAN and Debian. It contains some fixes for Sun compiler, but no user-visible changes and complements the Rcpp 0.8.1 release made Tuesday. Our thanks to Brian Ripley for help with the portability tests for that platform. It will be good to get an autobuilder for pre-emptive testing for that platform too as we make quite some use of the win-builder servive in Dortmund. The full NEWS entry for this release follows below:
0.8.2   2010-06-09
    o   Bug-fix release for suncc compiler with thanks to Brian Ripley for
        additional testing.
As always, even fuller details are in Rcpp Changelog page and the Rcpp page which also leads to the downloads, the browseable doxygen docs and zip files of doxygen output for the standard formats. A local directory has source and documentation too. Questions, comments etc should go to the rcpp-devel mailing list off the R-Forge page

Torsten Werner: Debian Community Poll

I have prepared a poll for users of the Debian operating system at http://tinyurl.com/3y33ska. We had the idea for the poll during the preparation of the MiniDebConf that is currently taking place in Berlin. Please spread the link and fill out the form yourself. Visitors of the MiniDebConf have the option to fill out the form on paper.

Alexander Reichle-Schmehl: Nice quote from a user

asked during the opening keynote of the Debian MiniDebconf in Berlin: Hi, I'm a long Debian user and Developer and would like to help. But I have a Problem: Everything works!

Dirk Eddelbuettel: RcppArmadillo 0.2.2

Following the Rcpp 0.8.1 release we made yesterday, we released RcppArmadillo release 0.2.2 this morning. RcppArmadillo uses Rcpp (and some 'glue' code) to provide a transparent interface from R to Conrad Sanderson's impressive Armadillo library for linear algebra. This release works well with the most recent inline release 0.3.5. One can now employ inlined R code as we generalized how/which headers are included and how library / linking information is added thanks a plugin mechanism. This is the first RcppArmadillo version to provide such a plugin, We also updated the included Armadillo headers to its most recent release 0.9.10, added some more operators and provide a utility function RcppArmadillo:::CxxFlags() to provide include directory information on the fly. An example of the direct inline approach for the fastLm function:
library(inline)
library(RcppArmadillo)
src <- '
	Rcpp::NumericVector yr(ys);			// creates Rcpp vector from SEXP
	Rcpp::NumericMatrix Xr(Xs);			// creates Rcpp matrix from SEXP
	int n = Xr.nrow(), k = Xr.ncol();

	arma::mat X(Xr.begin(), n, k, false);   	// reuses memory and avoids extra copy
	arma::colvec y(yr.begin(), yr.size(), false);

	arma::colvec coef = arma::solve(X, y);      	// fit model y ~ X
	arma::colvec res = y - X*coef;			// residuals

	double s2 = std::inner_product(res.begin(), res.end(), res.begin(), double())/(n - k);
							// std.errors of coefficients
	arma::colvec std_err = arma::sqrt(s2 * arma::diagvec( arma::inv(arma::trans(X)*X) ));

	return Rcpp::List::create(Rcpp::Named("coefficients") = coef,
				  Rcpp::Named("stderr")       = std_err,
				  Rcpp::Named("df")           = n - k
				  );
'
fun <- cxxfunction(signature(ys="numeric", Xs="numeric"), src, plugin="RcppArmadillo")
This creates a compiled function fun which, by using Armadillo, regresses a vector ys on a matrix Xs (just how the fastLmPure() function in the package does) --- yet is constructed on the fly using cxxfunction from inline. More information is on the RcppArmadillo page. Questions, comments etc should go to the rcpp-devel mailing list off the R-Forge page.

9 June 2010

Sylvain Le Gall: Waiting for her in ~1month

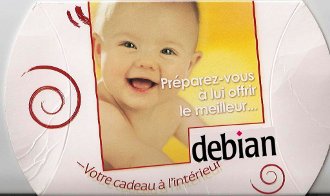
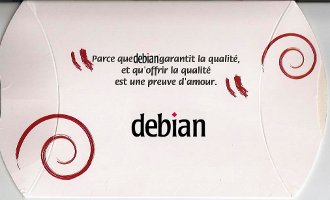
My wife is pregnant and we are expecting our second baby's arrival in about a month. Last time, she came back from her preparation lessons with a adverstisement "baby shower" gift pack. One of them catch my attention: English translation: be prepared to offer him the best... English translation: because Debian guarantee the quality and offering the quality is a proof of love OK, the swirl is the other way and I made a 5 minutes GIMP modification to cut-and-paste the Debian logo. But the message is here! Remember me: For those interested, the real thing is a soap by NUK(R).
David Welton: A Minor Erlang Rant

In an earlier post, I compared node.js to Erlang: http://journal.dedasys.com/2010/04/29/erlang-vs-node-js - which admittedly has a whiff of apples and oranges about it. Still, though, I think there's something to it. Node.js is creating lots of buzz for itself these days. Some of that will turn into actual production use, and at that point actual companies will have a vested interest in seeing the system improved. Currently, it is not as 'good' as Erlang. Erlang's VM has a built in scheduler, so you simply don't have to worry about manually creating bite-sized chunks of processing that feed into one another, it all "just works". For instance, my current Erlang project involves reading from twitter's stream, and distributing that to IRC and the web. It's pretty simple, works well, and is quite robust. I haven't had the best of days though, and one little annoyance of the many I dealt with today really caught my eye. I need to do an HTTP POST in Erlang, and:
  1. The documentation does not have examples.
  2. Here's an example of how to do a POST:
    http:request( post, "http://scream-it.com/win/tests/posttest.cfm", [], "application/x-www-form-urlencoded", "x=2&y=3&msg=Hello%20World" , [], [] ).
  3. Aside from being ugly and not very leggible, you'll note that he's passing the parameters as a string, and also has to manually include the "x-www-form-urlencoded" header.
  4. To create that string, you'd want to url encode it. Actually, ideally, you'd just pass in a list of key/value pairs and let the library module handle it.
  5. However, there's nothing in the http module that does that.
  6. If you look through various bits of Erlang code on the web, you'll note many, many versions of url encoding and decoding, because the http module makes no mention of how one might go about doing so.
  7. It turns out, that the edoc_lib module does have a uri encode function!
  8. That isn't documented in its own man page.
  9. And certainly isn't linked to in the http page.
So, in 2010, doing an HTTP POST in Erlang is still a pain in the neck. I'd be happy to put my money where my mouth is and submit a patch (at least one for the documentation), but you have to wonder why no one has fixed the problem so far - maybe they're not very accepting of patches?

Thibaut Girka: Second week of GSoC

Hi, already two weeks (and a half)! Now, this time, I haven't made as much progress I would have wanted, but here is what have been done during this week (and a half): What I've been doing As a result, the Debian Installer works on the FreeRunner, you can install Debian on the FR using it, but it won't setup anything for the bootloader. Oh, and another important thing is that the GIT repos are now up and running! You can try the prebuilt image or build it yourself. Note that you'll probably want to use a custom repo with the modified udebs. An alternative is to modify pkg-lists/netboot/network-console/armel/s3c24xx.cfg to include them in the image. What's coming next Well, nothing is sure, but I may:

Russell Coker: Mailing List Meta-Discussions

It seems that most mailing lists occasionally have meta-discussions about what is on-topic, the few that don t are the ones that have very strong moderation authoritarian moderators who jump on the first infraction and clearly specify the rules. I don t recall the list of acceptable topics for any mailing list including also discussions about what is on-topic . As this is the Internet I m sure that someone will immediately point out an example of such a list, but apart from the counter-example that someone will provide it seems obvious that for the majority of mailing lists a meta-discussion is not strictly on topic. Regardless of a meta-discussion not being on-topic I don t think there s anything wrong with such a discussion on occasion. But if a meta-discussion is to be based on the volume of off-topic messages it would be nice if the people who advocate such a position could try and encourage the discussion in a way that reduced the number of messages. Replying to lots of messages is not a good strategy if your position is that there are too many messages. If a meta-discussion is going to be about moving off-topic discussions to other forums that are more appropriate then it would be nice to have the meta-discussion move to another forum if possible. My previous post which advocates creating a separate mailing list for chatty messages was an attempt to move a discussion to a different forum [1]. Anyone who believes that such discussions don t belong on a list such as debian-private is free to commit their thoughts to some place that they consider more appropriate and provide the URL to any interested parties. I think that it s worth noting that the only comment on my previous post is one that describes how to filter mail to split the traffic from the debian-private list into different mailboxes. I had hoped that other people would write blog posts advocating their positions which would allow us to consider the merits of various ideas without the he-said-she-said element of mailing list discussions. Most mailing lists have a policy against profanity and some go further and ban personal abuse. Therefore it seems hypocritical to advocate a strict interpretation of the rules in regard to what is on-topic while also breaking the rules regarding profanity or personal abuse. I don t think it s asking a lot to suggest that the small minority of messages that someone writes on the topic of a list meta-discussion should obey the set of rules that they advocate I m not suggesting that someone should obey all the rules all the time, just when they are trying to enforce them. Also you can argue that a list policy against profanity doesn t preclude sending profane messages off-list, but if the off-list messages are for the purpose of promoting the list rules it still seems hypocritical to use profanity. It is a fair point that off-topic discussions and jokes can distract people from important issues and derail important discussions. It would be good if people who take such positions would implement them in terms of meta-discussions. If the purpose of a meta-discussion is to avoid distraction from important issues then it seems like a really good idea to try and avoid distraction in the meta-discussion thread. I wonder whether a meta-discussion can provide anything other than a source of lulz for all the people who don t care about the issue in question. The meta-discussions in the Debian project seem to always result in nothing changing, not even when the majority of people who comment agree that the current situation is not ideal. When an almost identical meta-discussion happens regularly it seems particularly pointless to start such a discussion for the purpose of reducing off-topic content. Revisiting an old discussion can do some good when circumstances change or when someone has some new insight. I know that it s difficult to avoid being sucked into such discussions, when I was diagnosed with AS [2] I decided to try and minimise my involvement in such discussions but I haven t been as successful at doing so as I had hoped.

Next.

Previous.