During his DebConf15 keynote, Jacob Appelbaum
observed
that those listening on the Internet lines would have good reason to
believe a computer have a given security hole if it download a
security fix from a Debian mirror. This is a good reason to always
use encrypted connections to the Debian mirror, to make sure those
listening do not know which IP address to attack. In August, Richard
Hartmann observed that encryption was not enough, when it was possible
to interfere download size to security patches or the fact that
download took place shortly after a security fix was released, and
proposed
to always use Tor to download packages from the Debian mirror. He
was not the first to propose this, as the
apt-transport-tor
package by Tim Retout already existed to make it easy to convince apt
to use
Tor, but I was not
aware of that package when I read the blog post from Richard.
Richard discussed the idea with Peter Palfrader, one of the Debian
sysadmins, and he set up a Tor hidden service on one of the central
Debian mirrors using the address vwakviie2ienjx6t.onion, thus making
it possible to download packages directly between two tor nodes,
making sure the network traffic always were encrypted.
Here is a short recipe for enabling this on your machine, by
installing
apt-transport-tor and replacing http and https
urls with tor+http and tor+https, and using the hidden service instead
of the official Debian mirror site. I recommend installing
etckeeper before you start to have a history of the changes
done in /etc/.
apt install apt-transport-tor
sed -i 's% http://ftp.debian.org/%tor+http://vwakviie2ienjx6t.onion/%' /etc/apt/sources.list
sed -i 's% http% tor+http%' /etc/apt/sources.list
If you have more sources listed in /etc/apt/sources.list.d/, run
the sed commands for these too. The sed command is assuming your are
using the ftp.debian.org Debian mirror. Adjust the command (or just
edit the file manually) to match your mirror.
This work in Debian Jessie and later. Note that tools like
apt-file only recently started using the apt transport
system, and do not work with these tor+http URLs. For
apt-file you need the version currently in experimental,
which need a recent apt version currently only in unstable. So if you
need a working
apt-file, this is not for you.
Another advantage from this change is that your machine will start
using Tor regularly and at fairly random intervals (every time you
update the package lists or upgrade or install a new package), thus
masking other Tor traffic done from the same machine. Using Tor will
become normal for the machine in question.
On
Freedombox, APT
is set up by default to use
apt-transport-tor when Tor is
enabled. It would be great if it was the default on any Debian
system.
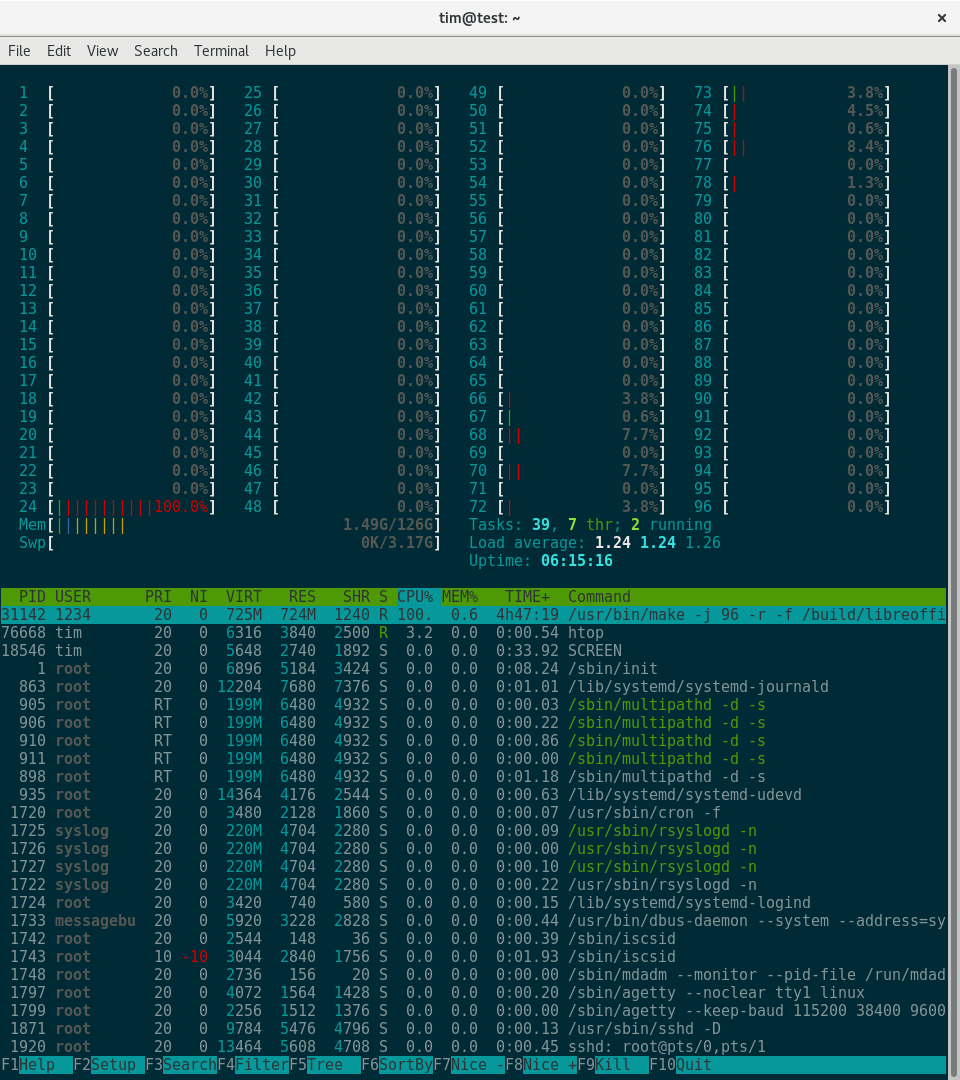 Final build time: around 12 hours, compared to 2hr 55m on the official arm64 buildd.
Most of the Libreoffice build appeared to consist of "touch /some/file"
repeated endlessly - I have a suspicion that the I/O performance might be low
on this server (although I have no further evidence to offer for this). I
think the next thing to try is building on a tmpfs, because the server has
128GB RAM available, and it's a shame not to use it.