Chris Lamb: Free software activities in February 2021
 Here is my monthly update covering what I have been doing in the free software world during February 2021 (previous month):
- Reviewed and merged a number of contribution from Peter Law to my django-cache-toolbox library for Django-based web applications, including: support always fetching some relations when loading a model (#27), allow use of custom
auth.Usermodel. (#29), avoid some more database calls (#30), wrap some collections in tuples for compatibility (#32) and cope with only some of our related models actually being loaded (#33).
- As part of my role of being the assistant Secretary of the Open Source Initiative and a board director of Software in the Public Interest, I attended their respective monthly meetings and participated in various licensing and other discussions occurring on the internet, as well as the usual internal discussions, etc.
- Opened a pull request to fix the relative target of manpage links in Roger Wesson's mocassin library. [...]
Reproducible Builds The motivation behind the Reproducible Builds effort is to ensure no flaws have been introduced during compilation process by promising identical results are always generated from a given source, therefore allowing multiple third-parties to come to a consensus on whether a build was compromised. The project is proud to be a member project of the Software Freedom Conservancy. Conservancy acts as a corporate umbrella allowing projects to operate as non-profit initiatives without managing their own corporate structure. If you like the work of the Conservancy or the Reproducible Builds project, please consider becoming an official supporter. This month, I:
-
Filed an upstream pull request to fix relative symlink targets of manpage links in
mocassin. [...] -
In Debian:
-
Submitted 5 patches to fix specific reproducibility issues in
crossfire,golang-github-revel-revel,golang-github-viant-toolbox,python-aiosqlite&zmk. - Kept isdebianreproducibleyet.com up to date. [...]
-
Submitted a patch to fix reproducibility-related toolchain issue in
kjs: Please make the opcodes.h file reproducible. (#983046)
-
Submitted 5 patches to fix specific reproducibility issues in
-
Categorised a large number of packages and issues in the Reproducible Builds
notes.gitrepository as well as wrote a script to automatically-classify a number of issues [...]. - Drafted, published and publicised our monthly report for January.
167 and 168 to Debian:
-
Bug fixes:
- Don't call
difflib.Differ.comparewith very large inputs; it is at least O(n^2) and makes diffoscope (appear to) hang. [...] - Don't rely on
dumpimagereturning an appropriate exit code; check that the file actually exists. [...] - Don't rely on
magic.Magicto have an identical API between file'smagic.pyand PyPI'spython-magiclibrary. [...]
- Don't call
- Revamp temporary file handling:
-
Testsuite improvements:
- Strip newlines when determining Black version to avoid
requires black >= 20.8b1 (18.9b0\n detected)in test output. [...] - Fix
weakref-related handling in Python 3.7 (i.e. Debian buster). [...] - If our temporary directory does not exist anymore, recreate it. [...]
- Fix FIT-related tests in Debian buster [...] and
fit_expected_diff[...]. - Gnumeric is back in testing so re-add to (test)
Build-Depends. [...] - Mark
test_apk.py::test_android_manifestas being allowed to fail for now. [...] - Add
u-boot-toolsto (test) Build-Depends so salsa.debian.org pipelines test the new U-Boot FIT comparator. [...] - Move to
assert_diffutility in a number of tests. [...][...]
- Strip newlines when determining Black version to avoid
-
Codebase improvements:
- Correct capitalisation of 'jQuery'. [...]
- Update my copyright years. [...]
- Tidy imports in
diffoscope.comparators.fit. [...] - Don't use
Inheriting PATH of X, usePATH is Xin logging messages. [...] - Drop unused
Config.aclandConfig.xattrattributes [...] and set a defaultConfig.extended_filesystem_attributes. [...]
Debian Uploads
-
python-django:2.2.18-1New upstream security release. (#981562)2.2.19-1New upstream security release. (#983090)3.2~alpha1-2Apply security fix from upstream. (#983090)3.2~beta1-1New upstream beta release.
-
redis:6.0.10-4New upstream release, fixing cluster access to unaligned memory on ARM architectures with hard alignment requirements (such asarmhfandarm64). (#982504)6.0.11-1New upstream release, incorporating security fixes. (#983446)6.2~rc3-1New upstream release candidate.6.2.0-1New upstream stable release, incorporating security fixes. (#983446)
-
gunicorn(20.1.0-1) New upstream release. -
xtrlock(2.15) Also support theXK_KP_Enterkey (i.e. the Enter on the numeric keypad) to submit a password. (#982634)
adminer (4.7.9-1) for Alexandre Rossi.
Debian LTS
This month I have worked 18 hours on Debian Long Term Support (LTS) and 12 hours on its sister Extended LTS project.
- Frontdesk duties, responding to user/developer questions, reviewing others' packages, participating in mailing list discussions, and attending our monthly development meeting. etc.
-
Updated the
lts-cve-triage.pytool to configure Python paths early due to transitive imports in an included library. [...] -
Investigated and triaged:
avahi(CVE-2021-26720),gdk-pixbuf(CVE-2021-20240),libraw(CVE-2020-24870),python3.5(CVE-2021-3177),qemu(CVE-2020-15469,CVE-2020-15859,CVE-2020-25084etc.),rails(CVE-2021-22880&CVE-2021-22881),stunnel4(CVE-2021-20230&CVE-2021-20231) &zeromq3(CVE-2021-20237) -
Issued DLA 2555-1 for
nettyas it was discovered that there was an insecure temporary file issue that could have lead to disclosure of arbitrary local files. -
Issued DLA 2562-1 to address a remote code execution vulnerability in
mumble, a VoIP client commonly used for group chats. The exploit could have been been triggered by a maliciously crafted URL on the server list. -
Issued DLA 2563-1, DLA 2565-1 and ELA-366-1 for
opensslto prevent an issue where "Digital EnVeloPe" EVP-related calls could cause applications to behave incorrectly or even crash (CVE-2021-23840) and address to an issue in the X.509 certificate parsing caused by the lack of error handling while ingesting the 'issuer' field. -
Issued DLA 2568-1 and ELA-369-1 as it was discovered that there was a buffer overflow attack in the
bind9DNS server, caused by an issue in the GSSAPI ("Generic Security Services") security policy negotiation. -
Issued DLA 2540-1, DLA 2569-1 and ELA-354-1 for
python-djangoto address a potential directory-traversal (CVE-2021-3281) and a cache-poisoning issue (CVE-2021-23336). -
Issued DLA 2576-1 for
redisas it was reported that there were a number of integer overflow.


 I have written my first Rust crate:
 Linux draws a distinction between code running in kernel (kernel space) and applications running in userland (user space). This is enforced at the hardware level - in x86-speak[1], kernel space code runs in ring 0 and user space code runs in ring 3[2]. If you're running in ring 3 and you attempt to touch memory that's only accessible in ring 0, the hardware will raise a fault. No matter how privileged your ring 3 code, you don't get to touch ring 0.
 As my contributions to Debian continue to grow in number, I find myself
uploading to the archive more and more often.
Although I'm pretty happy with my current sbuild-based workflow, twice in the
past few weeks I inadvertently made a binary upload instead of a source-only
one.

 I ve mentioned in the past my
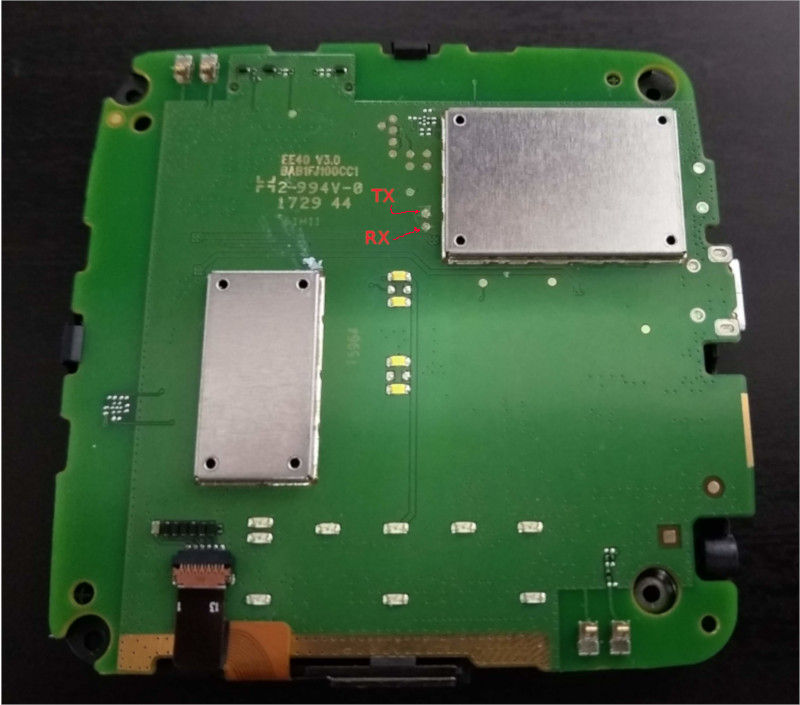 My mistake was going poking around trying to figure out where the updates are downloaded from - I know I m running a slightly older release than what s current, and the device can do an automatic download + update. Top tip; don t run

 Like
 This is more or less a followup to
 We first see Buffalo Bill at the thirty-two minute mark. (Or, more tellingly, he sees us.) Delaying the viewer's introduction to the film's villain is the mark of a secure and confident screenplay, even if it was popularised by the budget-restricted Jaws (1975) which hides the eponymous shark for one hour and 21 minutes.
 The messenger turns to watch Starling run off to Crawford. Are his eyes involuntarily following the movement or he is impressed by Starling's gumption? Or, almost two decades after John Berger's male gaze, is he simply checking her out? The film, thankfully, leaves it to us.
 The cold open of Hannibal (2001) makes for a worthy comparison. The audience remembers they loved the dialogue between Starling and Lecter, so it is clumsily mentioned. We remember Barney too, so he is shoehorned in as well. Lacking the confidence to introduce new signifiers to its universe, Red Dragon (2002) aside, the hollow, 'clip show' feel of Hannibal is a taste of the zero-calorie sequels to come in the next two decades.
 Dr. Lecter's upright stance when we meet him reminds me of the third act of Alfred Hitchcock's Notorious (1946), another picture freighted with meaningful stairs. Stanley Kubrick's The Killing (1956) began the now-shopworn trope of concealing a weapon in a flower box.
 Thrilled to announce that a new package of mine just made it to
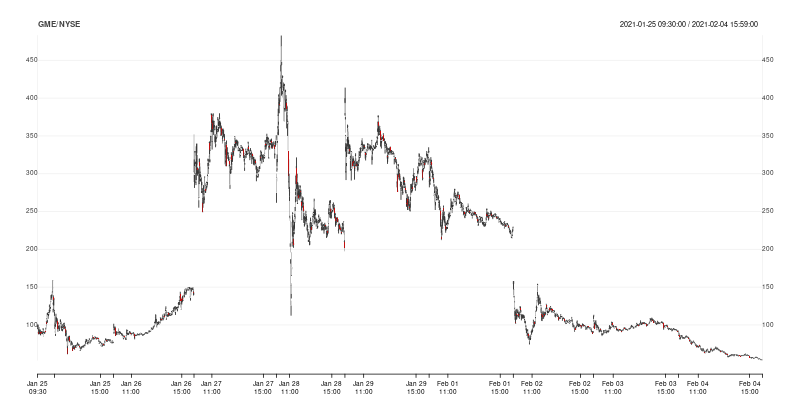 You will need an API key to have up to 800 daily accesses for free, higher-performance plans (including websocket access) are available for paying customers too. I have only used the free API so far myself.
I plan to add quote and price support this weekend, and generalize the time series access to returning lists of objects as the API does in fact support multi-security access. As always, feedback is welcomed. Please post comments and suggestions at the

 I started to write C 25 years ago now, with many different tools over the year. As many open source developers, I spent most of my life working with the GNU tools out there.As I've been using an Apple computer over the last years, I had to adapt to this environment and learn the tricks of the trade. Here are some of my notes so a search engine can index them and I'll be able to find them later.