Search Results: "ed"

10 February 2011

Russell Coker: LCA2011, Harassment, etc

The conference LCA 2011 had an anti-harassment policy [1] which was violated by a keynote speech. The speaker and the conference organisers apologised, but of course the matter didn t end there.Discussion continued on the lca-chat list (for conference delegates) [2], on the Linux-aus list (for members of Linux Australia the parent body of the LCA conference) [3], and in some blog posts.There is also some discussion on an LWN article that is linked from an ITWire article [4].I think that the policy was reasonable and from all the descriptions it seems to have worked reasonably well. With such things there are always possibilities to tweak things, so probably there will be future policies which are better in some ways, but it seemed to do the job. The way that the LCA organisers handled the situation was appropriate. In the discussion there were some comments with logical failures that I think need further analysis, I ll summarise them one per paragraph with the heading being a para-phrase of the claim.Is it Offensive?A particularly relevant blog post is Skud s post about avoiding the use of the word offense [5]. In the various discussions about the speech in question most of the people who disapprove of the erotic images don t use the word offense , this is presumably due in part to the influence of Skud s post. This hasn t stopped people claiming that the debate is about whether the images are offensive, I m not sure if this is a deliberate straw-man attack or just cluelessness.The anti-harassment policy does use the word offensive in two places, I think that this was a mistake but it doesn t detract from the overall meaning of the document.Is it Harassment?There was some discussion about whether the actions in question were harassment. Wordnet s definition of harassment includes the act of tormenting by continued persistent attacks and criticism . It seems unlikely that any of the people in the audience who objected to the erotic content in the lecture slides had never seen unwanted erotic material before. So I think that it s worth considering this incident as just another entry in a list of similar incidents that some of the delegates have experienced, and thus as a continuation of persistent attacks IE harassment. Melissa McEwan s post about the variety of harassment that she has received from men is worth reading in this regard [6].I think that a reasonable analogy here is the school bullying campaigns that were experienced by many members of the Linux community when they were younger. School bullying in most cases is not about a small number of extreme incidents, but about a large number of small incidents each of which when considered independently can be rationalised as something that isn t significant (excusing such incidents independently is what allows bullying to be rife in most schools). In many cases of high school bullying the victim is blamed for supposedly over-reacting after a reaction is compared to some small incident at the end of a long harassment campaign, some of the criticism of the Geek Feminists seems to echo this pattern.It seems to me that some of the more dismissive comments which demonstrated a lack of regard for the experiences of other people can reasonably be considered as harassment too (which is also something that Melissa McEwan mentions). Note that I am specifically not advocating that the discussion be shut down, merely that the people who claim that it s only the (supposed) opinion of the majority that matters are part of the problem. However the fact that the apology for the talk received applause from the majority of the audience seems to indicate that the majority is in fact in favor of the anti-harassment policy.Derald Wing Sue, Ph.D. and David P. Rivera (a doctoral candidate in counseling psychology) have written a couple of interesting short articles about this for Psychology Today. Bullying and Microaggressions describes bullying as more than physical violence and also discusses adult bullies [7]. The Power to Define Reality describes the way that the experiences of people who lack power can have the reality of their experiences denied [8] this one really relates to some of the discussions about harassment.But it s Legal!It has been claimed that the legal system works well in Australia and that Australian law should be the only necessary guide to content. A trivial counter-case that was noted in the discussion is the fact that pure sales presentations are not accepted at LCA and such presentations are certainly legal! There is a good precedent for prohibiting things that are legal as part of the conference speaker agreement.More generally the legal system changes slowly and still infringes on what many people in our community regard as basic human rights. There is no reason why an Australian conference should have as it s standards the bare minimum that is required by Australian law.It was pointed out that workplace social norms translate well between cultures, they are usually more stringent than Australian law requires and Australian workplace law is a lot more stringent than the laws relating to conferences and other public events. It seems to me that a presentation which would result in a visit from HR if given at the office shouldn t be regarded as suitable for a conference such as LCA.But there is a Balance of Men and Women in Erotic Pictures!The complaints are not about a lack of balance in the erotic material, but it s presence there at all. Defending the slides on the basis that there was a supposed balance of male and female misses the point that most people just want no erotic material in presentations at conferences.Also it seems to me that if there are pictures which aren t offensive then the way to demonstrate this would be to publish them and say look, they aren t offensive . If it takes 600 words in a blog post to justify the use of some images then that alone seems to be evidence that the images were poorly chosen.But the talk was EffectiveSome of the people who have commented on this issue mentioned that they couldn t remember what was said when the images in question were displayed. When images from the talk are remembered and the main content of the talk isn t that seems to be a failure of the talk.When a major sponsor of the conference complains and requests that the talk video never be published that also seems like a major failure of the talk.I think that the effective talks are ones that educate people and inspire them to do something positive and useful. A talk that inspires a discussion about whether the speaker deserves censure doesn t seem effective.There are claims that there is no way the talk could have made the point as well if it wasn t for the images in question. But I can t believe that someone who is capable enough to get awarded a keynote speaking position at a conference such as LCA is incapable of finding other images to make the same point.But Similar Images are on MTVWhen people want MTV content they can watch MTV.Why Can t we just try Educating Men?It was claimed that education works in dealing with such issues in corporate environments and sporting clubs. My observation of the corporate environment is that such training must be extremely rare in Australia, the Netherlands, and probably the UK due to the fact that none of my employers have done it. I have heard first-hand reports of diversity training from people who work in the US. I expect that the fact that people who fail diversity training in a corporate environment get a meeting with HR is a major factor in it s effectiveness.The long email discussions and blog comment threads when these incidents happen could theoretically be used as training. But when you have some men using multiple mailing lists and dozens of posts arguing without appearing to learn it seems clear that they are not about to learn anything no matter what education is offered. It seems to me that you could broadly divide the free software community into two groups, those who want to learn how to do things better (but who are unlikely to make gross errors anyway), and those who won t learn.Besides, having a keynote speaker at a major conference apologise should be educational.But Clueless Nerds Hit on GirlsI don t know why every discussion about the treatment of women ends up getting a mention of this supposed issue.But Women Could make False AccusationsIn any classification system you have to make some sort of balance between false-positives and false-negatives. If the aim is to get zero false-positives then the incidence of false-negatives will increase. So if the aim was to never ever have a false accusation brought against a man for sexual harassment then the vast majority of real harassment cases would result in no action at all.I don t think it s reasonable to expect that most women who are mistreated should suffer in silence just to reduce the possibility that men might be falsely accused.The Rape Statistics cited in the discussion may be InaccurateThere is no possible way of interpreting rape statistics to make it not be a serious problem, now matter how you analyse the available information it happens far too often and has a significant impact on the victim. Also the suggested reinterpretation of the statistics didn t contradict the claim that it is likely that there are multiple rape victims attending LCA. So interpreting the statistics in a different way to get different numbers doesn t change anything. Trying to diminish the significance of rape generally doesn t support any other arguments that you might make.There are things that you can just discuss for the heck of it and things which should be discussed with care (if at all) to avoid needlessly hurting people. In these sorts of discussions the right thing to do is to avoid debating the numbers as much as possible.I think that the numbers produced by RAINN [9] are as good as we can get.But I am very supportive of women in our communityIf you spend all your time arguing with women and don t listen to what they have to say then you really aren t supporting them.ConclusionAfter publishing this post I ll email the URL to a few of the men who helped inspire it, I will explain how disappointed I am and how I expect better from them. I encourage others to do the same.Also when such discussions happen I encourage men to vote in favor of the positions advocated by women. Writing a message that addresses points in the debate can be difficult and if the debate is rapid then you may find that every point that you might make has been made by someone else. But in that case just posting to agree with the women can really mean a lot.

Charles Plessy: Chain reaction

Now that maintain several dozens of packages in Debian, I think twice before uploading a new one. Does it have a future, a public ? Some of the packages I prepare are available on git.debian.org, and are listed in Debian Med's tasks pages. It would not take me long to finish most of them, but that does not take into account the time others will spend on it. They will make our archive bigger and our quality tests longer to execute. Somebody will translate their description. Somebody else will perhaps write a security patch someday, or a patch to make the package compilable with a new version of GCC. All in all, each package has a footprint in Debian's ecosystem. That footprint starts early, as soon as the package is sent to the NEW queue. For instance, I kept by mistake some old content in the copyright file of clustalw, that was recently freed and has to go through the NEW queue to be transferred from the non-free to the main area of our archive. That costed a small of exchange of emails, that could have been avoided. Our packages should be perfect, but that is difficult to achieve alone. For that reason, I proposed two years ago a package review system, that functions like a chain reaction. The principle is simple. After uploading to the NEW queue, download two neighbor packages and check their copyright file. The errors found can be corrected by their maintainer before the the FTP team inspects it, which save their time. For instance, after uploading tabix, I found an error in mediathekview, that was corrected. That compensates for my mistake with clustalw. If each person receiving a package review does a review of two other packages, that will create a chain reaction that will clean the queue from the simplest mistakes, leaving only the really problematic cases. As Torsten noted recently, the NEW queue is getting long. So how about trying to help ?

9 February 2011

Jonathan Wiltshire: Point Release Security Co-ordinator

In Bits from the Security Team a few weeks ago, Thijs Kinkhorst wrote:
Since a couple of years we ve been handing off security issues of minor or
theoretical impact but for which a fix would be desirable at some point, like
certain classes of denial-of-service attacks, off to stable point updates.
We re looking for a person that wants to coordinate this: monitor the Security
Tracker for issues classified as such by the Security Team, converse with
maintainers to get such updates done and coordinate with the stable release
managers on this.
I m happy to confirm, now that it s been announced, that I am that person: point release security co-ordinator. Affected packages If your package fulfils these criteria: it is a candidate for updating in stable or oldstable, and you ll probably receive a mail from me at some point asking you to do so. You can pre-empt this mail of course, by backporting your fix to the affected versions and contacting the release team to get your fix into stable, without waiting for me. In such a case, please drop me a note with the details so I can tick your off on my hit^W candidate list. Making a stable/oldstable upload This is documented in the Developer s Reference, but to summarise:
  1. Prepare your fix, targetting stable or oldstable, and build it in an up-to-date chroot for that release
  2. Send a diff of the new package to the release team, asking for permission to upload
  3. Upload as normal, and wait for it to be included in the next point release. Meanwhile, notify the security team of your upload, if it fixes a CVE.
Tracking candidate packages I m going to start off tracking filed bugs for SPU candidates and OSPU candidates with usertags in the BTS, under my own address. In time that might be merged into an address used by the security team, but for now I m still finding a good workflow so it s much easier this way.
Comments
Point Release Security Co-ordinator is a post from: jwiltshire.org.uk Flattr

Steve Kemp: Random tools I would use - and pictures

So previously I talked about pictures. Having spent a while playing with some new lighting ideas I'll present three recent images:

Now that's out of the way lets talk software. There are two specific things I think would be useful to me right now:
Opportunistic "cron"
I've got a few jobs that don't take long to run, and I schedule for once a day when my systems are idle. It'd be nice to have some long-running daemon which could trigger these odd-jobs (which do things like update my list of mutt mailboxes) when the system has been idle for >30 minutes, or some similar criterion. Ideally I'd say "Run this job when the system is idle, but if the system is never idle run it once a day, or once an hour regardless".
Content-aware tracking software
I use rsync to archive images across a number of systems. Imagine I rename a few images locally, I have to re-rsync even though ideally all I need to do is rename the contents remotely. The issue is remembering what I've changed. So given:
~/Images/Stolen-Souls/2011.02/
~/Images/Stolen-Souls/2011.02/02-Borcsa
~/Images/Stolen-Souls/2011.02/02-Camilla
~/Images/Stolen-Souls/2011.02/06-Indigo
~/Images/Stolen-Souls/2011.02/07-Rosa
If I rename "06-Indigo" then it's trivial to ssh to the remote host and do the same job. But what if I rename a bunch of individual files? Ideally I'd be able to run something like:
~$ tool --snapshot ~/Images/
~$ mv Images/old.jpg Images/new.jpg
~$ tool --show-changes ~/Images
mv Images/old.jpg Images/new.jpg
I half believe git can do something like this, but it seems like you should be able to index the filename+SHA1+size to ~/.snapshot, then later do the same thing and output a list of "mv" commands.
Anyway; I'm drunk. I'm probably not making sense, and I need to sleep. Goodnight. ObQuote: "Hello Mr. Svenning how have you been?" - Mallrats

Matthew Garrett: LCA 2011

I'm both back from LCA 2011 and also over the associated brutal jetlag, so if you sent me mail and I still haven't replied then it's fallen down some sort of cliff and you should probably shout at me until I do something about it. LCA was, as usual, excellent. Especially given that the original venue was the same distance above the river as the now somewhat misleadingly described dry dock on the opposite bank.

I did a bunch of talks this year, and they're now all online, so without further ado:

Enterprise power management - a discussion of power management with a focus on enterprise users, given at the plumbers miniconf. LWN did a writeup here, and every time I say "Tera" you should pretend that I'm saying "Giga". I have no good excuse.

Linux license compliance - about the poor observance of the GPL's conditions by vendors, given at the business miniconf. A useful example presented itself in the form of a GPL-violating Android tablet that I bought in literally the first store I went into in Australia this year. Probably also the last appearance of my Knuth t-shirt, because it appears to have several holes in places where it shouldn't.

Making laptops work in Linux - talking about identifying how laptop-specific functionality is wired up, with an emphasis on reverse-engineering ACPI methods to figure out how to make things work. This one was my presentation at the main conference.

The organisers and volunteers deserve incredible gratitude for the way the conference was managed, especially considering that the CBD was underwater a week and a half earlier.

Alexander Reichle-Schmehl: WOW! We are on the front page of the taz!

The taz (short for die tageszeitung) is one of the major German daily newspapers. And they currently feature the Squeeze release on their frontpage! The article is very good (and well investigated), managing to explain some technical details quite well, and...
It's currently the most read article! Wow! Update: The online version of the austrian newspaper der Standard has also an article about the Squeeze release!

Alexander Wirt: Using psql with readline

If you want to use psql with libreadline instead of libedit there is a small, nifty, trick:
LD_PRELOAD=/lib/libreadline.so.5 psql

Alexander Wirt: squeeze-backports and lenny-backports-sloppy started

The backports team is proud to announce the next generation of backports:
squeeze-backports. From now on all contributors will be able to upload
backports of packages available in wheezy (testing) to squeeze-backports.
Additionally the previously announced lenny-backports-sloppy is now officially
open for uploads.

To ensure the basic principle that a system consisting of lenny plus
lenny-backports can be upgraded to squeeze proper, the handling of the
lenny-backports branch has changed. From now on uploads to lenny-backports
need manual approval from a backports team member similar to the handling of
the proposed-updates queue within the regular archive. Feel free to upload
packages here, especially security updates to previously backported versions,
but please ensure the versions are lower than those in stable /
stable-security.

If you feel the need of newer versions for lenny than which are available in
squeeze, please do upload them to lenny-backports-sloppy. The rules for this
suite are practically the same as for squeeze-backports: Do base your uploads
on packages available in testing (wheezy) and build them in the appropriate
environment.

Please remember when using lenny-backports-sloppy you can't easily upgrade to a
plain squeeze. This suite is specificly meant to contain newer versions than
squeeze. While the aim is to only carry packages that will also be provided in
squeeze-backports for upgrade possibilities, we can't guarantee that, so be
careful.

User visible change to squeeze-backports

As the apt maintainers had been so kind to introduce a new archive wide option
in squeeze, the usage of backports.debian.org is easier than ever before: In
the past you had to explicitly configure pinning for the backports repository
to enjoy the full feature set including upgrades to new versions of packages
you had installed from there. As this is cumbersome, errorprone and a nuisance
this new setting got introduced. With this feature backports get handled in a
way that updates for packages installed from squeeze-backports will happen out
of the box.

And last but definitely not least, let us send a big "thank you" to all
contributors that backports.debian.org enjoys to have - you made it possible to
serve more than 1400 binary packages through 837 source backports since
lenny-backports got kicked into life. Keep up the good work.

Thank you very much!

Michal Čihař: Another new theme for phpMyAdmin

Today we've got new submission for phpMyAdmin theme contest and I must say it really looks great. The new theme is called pmahomme after it's author Mike Homme: pmahomme theme It's now also available on the demo server, so don't hesitate and try it there. Looking forward for other submissions to our contest.

Filed under: English Phpmyadmin 0 comments Flattr this!

Richard Darst: whiteboard.debian.net

A while ago (early 2009), I created whiteboard.debian.net as a way to do real-time editing collaboration. While working for DebConf, I really wanted to be able to collaboratively edit text with people, and all of the web-based solutions I found at the time were non-free. Thus, I took mobwrite and wrote a very thin wrapper around it. Mobwrite is where all the cleverness is (and mobwrite is way beyond my expertise, by the way). Mobwrite is Apache licensed, so you can use it in other places, too.Thus, whiteboard.debian.net was begun. It was never publicized very much. It has no authentication required and no history (the "static link" does provide limited recovery for mistakes, though). Here is a test whiteboard; open it in two tabs and watch the text areas sync. Any whiteboard is created if you go to a valid URL.I just deployed a slightly newer version of whiteboard. You can now see an options page for each whiteboard, and it can render in several lightweight markup languages (good for drafting+previewing things). If you have other options to add there, let me know.If you are interested in collaborative text editing, there are some other options. There is a Debian titanpad, an "open" instance of now-open-sourced Etherpad, and it has history support. Use titanpad.com and you don't have to log in. Here is a test pad. For a non-web application, Gobby exists. Use gobby-0.5 for smart undo history if everyone uses squeeze or above.Is whiteboard still relevant in light of the options above that store history? I'm sure it depends, but for now, whiteboard works well for a low-overhead scratch space and for cases where you don't want to have a history trail. I also tend to use it as a simple pastebin or a personal notepad when I don't want to worry about having traces left behind. In short, it is so minimal you don't have to think about starting one up for something. I have found that collaborative writing really helps to get things done, thus, I hope that whiteboard (or a similar tool) can be useful to you.

MJ Ray: SPI February 2011

The regular monthly board of SPI (Software in the Public Interest, the contributor-run non-profit which supports debian, drupal and many other projects not beginning with the letter d) is on IRC this evening at 20:30 UTC in #spi on irc.oftc.net. If you need an Internet Relay Chat client, check what s available in your package manager, or you could do worse than adding Chatzilla to Iceweasel or Firefox. The agenda has been posted and the reports really ought to be included by the time this blog post appears. Come along and see FOSS project support infrastructure do its thing, then maybe chat a bit afterwards.

8 February 2011

Joey Hess: mapping git repositories

Git has lots of tools to map the history of a git repository. But, I have not been able to find tools to map networks of git repositories. Possibly noone has done it because such networks tend to be pretty centralized really, with low levels of (visible) interconnection, and so not that interesting, like this network of all known branches of ikiwiki. Soon after I started using git-annex, I realized the repositories using it would tend to be more interconnected, and less centralized, and generally a more complex, rich fabric than I'd seen in my use of git before. So I've built "git annex map", which uses graphviz to spit out fun maps like this. (Green nodes are trusted drives; red nodes are not currently available.)
Previously: git tube map

Cyril Brulebois: Debian XSF News #4

Here comes the forth Debian XSF News issue! I usually try to keep the items sorted chronologically (but grouped by topic when possible), so if you re wondering about the current status of X in unstable, make sure you read the last entry.

Christoph G hre: Squeeze finally landed

Half a year after I found three Squeezes in my luggage, some more of these cute green guys landed at FOSDEM.

Thanks to Gavin for the fun and all involved Debian people for Squeeze!
landed squeezes

Mike Hommey: Knowing how much disk seeks hurt

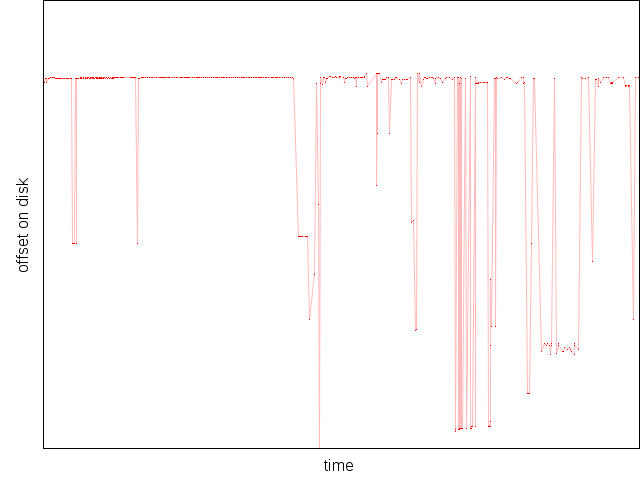
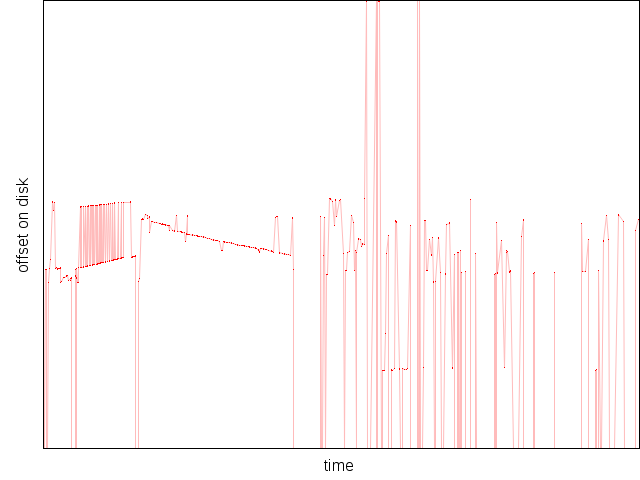
We all know disk seeks hurt. But we usually don t have a precise idea how much. How about getting that idea? Here is a little experiment I ran a few days ago. I took the output from the systemtap script tracking I/O I wrote, on a Firefox startup after boot. Each line of that output, which gives a timestamp (which we don t care about here), a file name, and an offset, represents a 4096 bytes read (one page). The first set of data points I got is how much time it takes to reproduce this read pattern after a reboot, and how that compares to Firefox startup time. For what it s worth, I did group following reads, to avoid doing too many system calls, and also avoided kernel readahead by using direct I/O, meaning I would only read exactly what the kernel reads when Firefox normally starts. All the following tests were done under the usual conditions (see previous posts), but I limited the tests to the x86-64 architecture, because all that really matters is the disk. I ll mention, however, that the amount of data read in these tests is 34,729,984 bytes, and that the original I/O pattern looks like this: Zooming around the main location where most I/O happen, we can see the pattern is still bumpy: This somehow looks familiar, doesn t it? We already know for a fact that even these patterns that, on the whole disk, look like pretty much insignificant, have an important impact on startup time. Try to imagine what kind of difference could be observed if we were reordering all these reads. Anyways, back to that I/O simulation, we first need to see how far it is from the actual Firefox startup. We would rather that simulated I/O + warm startup/hot cache end up close to the real thing. However, we need to keep in mind, as we saw in a previous post, that CPU scaling, when mixed with I/O, has an influence on startup time. Warm startup not involving I/O, the CPU can run at maximum speed the whole time. As such, for a fair comparison, we need to compare to cold startup time with the CPU forced at maximum speed, which we saw is faster than startup time with CPU scaling.
Average time (ms)
Simulated cold startup 2,764.26 0.42%
Warm startup 250.74 0.18%
Simulated cold + warm 3015
Real cold startup 3087.47 0.31%
Difference 72.47 (2.35%)
Close enough, I d say. The difference is most probably caused by metadata reads and a few other things, that isn t in the systemtap script scope. Now we know our simulated I/O is close to reality, what happens if we reorder all these reads according to the position on disk?
Average time (ms) Corresponding transfer rate
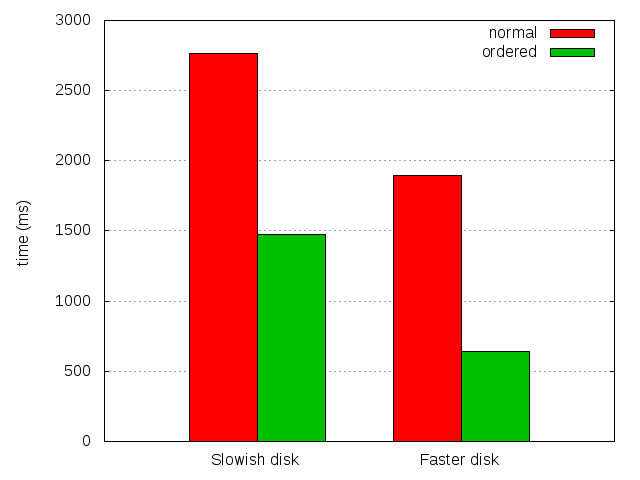
Simulated I/O 2,764.26 0.42% 12.56 MB/s
Reordered I/O 1,473.34 0.43% 23.57 MB/s
Difference 1,290.92 (46.7%) n/a
That s almost twice as fast ! And the disk doesn t even have a big throughput (around 30MB/s). Let s see what it does with a disk with a bigger throughput (85MB/s).
Average time (ms) Corresponding transfer rate
Simulated I/O 1,898.66 0.16% 18.29 MB/s
Reordered I/O 644.0 0.15% 53.93 MB/s
Difference 1,254.66 (66.08%) n/a
That s almost three times as fast ! The faster the disk, the bigger the improvement we can get by reordering and grouping I/O, which is not unexpected, but here we can see how much having to go back and forth on the disk hurt badly. Obviously, the numbers from the faster disk can t be directly compared to the ones from the slower disk, because the data was not arranged the same way on the disk, and file system fragmentation, as well as how the file system is filled also have their own share to add to the problem. And because it s more impressive to see on a graph than in a result table: Disks seeks hurt. Badly.

Michal Čihař: phpMyAdmin translation status

As we're slowly heading towards phpMyAdmin 3.4, it is good time to look at current translations state. There are few which are already at 100%, so they are in best possible shape: Some languages really miss just few messages, so they will hopefully get to 100% soon: And there is huge progress in Russian, which will at this pace get to 100% this week. Was your language not listed? You can help it being better!

Filed under: English Phpmyadmin 0 comments Flattr this!

Julien Danjou: Announcing Org-contacts

When I started to use Emacs, I got hooked by many stuff like Gnus and Org-mode. One thing I quickly started to hate is how the Lisp code can be old and unmaintained. That especially applies to BBDB, which has been unmaintained for years, and has very very very old and obsolete code. Therefore I've decided to develop my own BBDB replacement based on my lovely Org-mode. It's called org-contacts, and it allows you to handle your contact like anything you would handle in Org. This way you can manage them the way you want, without any preset fields or any assumptions like BBDB has. I had the chance to present it at the Paris OrgCamp a couple of weeks ago, and due to the enthusiastic audience I had, I'm now releasing it to the wide Internet. Flattr this

Paul Wise: Looking towards Debian wheezy

So Debian squeeze has finally been released and it is time to look toward to what we might work on or want to happen for the next release, codenamed Debian wheezy. An informal discussion on IRC mentioned libburnia libraries and apps, finishing DEP5, objnam, wayland, multiarch, Matthew Palmer plans to work on netcfg, ifupdown and the KDE team plan to remove Qt3/KDE3. I personally plan to work on catching up with my packages, the removal of defoma, boosting the Debian games team, improving collaboration with derivatives, changes to the Debian wiki, reviewing more packages mentioned on debian-mentors and more. I am really excited to see the cross-distro collaboration of Enrico Zini and others in bringing application management to Linux distributions, the multiarch work by Steve Langasek and others and hopefully optimistic about the recent discussions of automated post-install testing. I probably will not work on almost all of these but I would like to see multiarch, cross compiliation, widespread systemd integration, netconf revival, porting to phones/tablets, OEM mode and media for d-i, partitioning improvments for d-i, widespread automated post-install testing, expansion of daca, deployment of debexpo, widespread adoption of PET, automated removal of bad packages, better pro-active security measures, building all packages on buildds, migration away from Debian-specific stuff in favour of cross-distro solutions, addition of new UI experiences (like MeeGo, Android, Unity, QtMoko), addition of new APIs for portability (like Android, Khronos, MacOS/iOS stuff), more interesting/weird ports, merging derivatives into Debian, better integration of Debian Pure Blends, removing non-free packages where free alternatives exist, ex-developers and MIA folks returning to Debian, expansion of the backports repository, fixes for lots of bugs and probably other things I forgot. What are you going to work on? What do you wish you could work on? What work are you hoping others will do? What work are you excited about that others are doing?

Stefano Zacchiroli: ZOMG a Debian release

mythbustering a Debian release This is no news anymore, but in case you don't know yet: Debian 6.0 "Squeeze" has been released the past week-end. If you haven't yet downloaded Squeeze, stop reading this blog post right here and jump to: to choose your ISO; or check the release notes for upgrade instructions from Debian 5.0 "Lenny". Done?
Cool!
I hope you are now enjoying Squeeze as much as I've enjoyed being part of its development cycle which: I'm still shaked by the events, given the release happened in a sort of split context: the teams working on the final phases of the release (release team, ftp-masters, webmasters, cd, DSA, etc.) were "at home" hacking frantically on it, while many EU-based Debian people (including yours truly) were at FOSDEM representing Debian to the community with booth, talks, and answering the recurrent question so, have you released yet? . At FOSDEM, I've been personally submerged by congratulation messages that are not really for me, but rather for the Debian community at large. So: congratulations folks! People out there be them Debian users, users of some derivative, or Free Software enthusiasts in general seem to really love what we have achieved with Squeeze! The people that need to be thanked for this result are way too many, so I won't try to name names. Nonetheless, I've a few personal kudos to deliver to: I'm overwhelmed by happiness about all that and I'll cherish it forever as a souvenir of what a community of volunteers, driven by common ideals, can achieve. Now let's party and then roll up our sleeves for Wheezy, which is already open for development.
PS I've talked again at FOSDEM about the relevance of Debian in the Free Software ecosystem. I've the impression the message is getting through: check out the very nice article Why Debian matters more than ever by Zonker.

Lars Wirzenius: Growing the Debian development community

In an article about gender issues among American atheists, Sharon Moss and Lyz Liddell give a list of things to consider to be better community, not just for women:
  • Be a leader. Take responsibility for the tone of your group. If potential new members are being made to feel uncomfortable and aren t coming back, you re doing it wrong. As a leader, it is your job to prioritize the comfort of your attendees in programs, group dynamics, and communications. Try to put yourself in other members shoes and also ask for feedback.
  • Promote a sense of community. Take the time to socialize and get to know each other. If you re group isn t primarily a social group, thinking about adding some social time. Go to breakfast before the protest, compose your letters to the editor over coffee, or grab a pizza and beer after that lecture. When you know each other, you have each others backs. Being a jerk isn t tolerated.
  • Moderate discussions. Make sure everyone has the opportunity to participate- new people, quiet people, etc. Don t let conversation be dominated by one or two people who must win.
  • Embrace and accept different ways of communicating. Whether someone is an aggressive debater or not, make sure they re still welcome. The other atheist in the room isn t your enemy.
  • Encourage subgroups. Every event your group hosts doesn t need to appeal to your entire membership. Many women appreciate women-only space to express their nonbelief and to connect with other atheist women. Here at the Humanist Community of Central Ohio, we started a subgroup book club called Reasonable Women. When it grew to have about 25 regular members and was beginning to be a little too large and unwieldy to function as a book club, we created a second group, Heathen Chicks, which is just a social group that meets at a local cafe. It isn t just about creating women only space, for us, this has been a way to draw more women into other events our group hosts.
  • Foster women in leadership. Groups with women in leadership positions tend to have more women. Encourage women in your group to be visible in leadership.
These should work pretty well for Debian as well. I mean for the project in general, for getting all kinds of new people in, and getting them to stay, not just women, even if the gender imbalance is perhaps the biggest glaring problem we have. As a concrete suggestion, maybe it would be a good idea to continue the Debian party line that Joey set up for the squeeze release. We already have IRC, but having an audio chat with your Debian peers might be a nice addition. Specifically a social one, instead of something intended to boost productivity.

Next.

Previous.